Showing posts with label sovereignty. Show all posts

Daily Tech Digest - October 23, 2026

Quote for the Day
“A startup is not a smaller version of a large company.”
— Steve Blank
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Convergence of Cyber, Space and Electromagnetic Resilience

The article describes how critical infrastructure security is being reshaped by the convergence of cyber, space, and electromagnetic risks. It explains that satellites have evolved from simple communication tools into high‑value targets that carry mission‑critical enterprise data, making even short detection delays dangerous. The rapid growth of low‑cost launches and nanosatellites has crowded orbital paths, increasing collision risks and complicating tracking. At the same time, whoever controls the space‑layer communication channels gains a strategic advantage, especially when terrestrial links are disrupted. The piece argues that modern resilience requires a C5ISR‑style approach, where cybersecurity, space operations, and electromagnetic protection are treated as one integrated domain. This is because satellites, radio‑frequency systems, and digital networks are now tightly intertwined, and attacks often exploit the seams between them. Traditional ground‑based communication architectures are no longer sufficient for industries that operate across remote, maritime, or mobile environments. The article’s message is steady: resilience now depends on cross‑domain visibility, faster detection, and treating space assets as part of the enterprise security perimeter rather than a separate technical layer.

Read Original Article →

Sovereignty vs. security: Microsoft’s Roger Halbheer says you’re asking the wrong question

In a recent interview, Roger Halbheer, Microsoft’s Customer Security Officer, argues that organizations fundamentally misunderstand digital sovereignty by treating it as a procurement issue rather than a security challenge. He notes that business leaders often demand complete independence from outside access, which is practically impossible, and end up simply buying a localized server location along with an assurance statement. Instead, Halbheer urges boards to make calculated risk decisions for each specific workload. He warns that moving operations entirely on-premises to achieve sovereignty drastically reduces the speed at which organizations can detect and respond to security threats, making them highly vulnerable in a landscape where attackers operate in mere hours. Maintaining such systems internally requires immense resources, money, and skilled personnel that most companies lack. Furthermore, he clarifies that merely storing data in Europe does not protect it from government access, as authorities in almost every jurisdiction have legal avenues to compel data providers. Ultimately, Halbheer stresses that a compromised system can never truly be sovereign, making robust security the ultimate foundation for data protection.
Read Original Article →
Article Thumbnail

Data Mesh vs. Data Fabric: Which Approach Is Right for Your Organization?

Data mesh and data fabric are distinct but complementary approaches to managing distributed enterprise data. Data mesh decentralizes data control, handing ownership directly to the business units that understand it best. By treating data as a product, it empowers individual teams to manage their own resources while adhering to shared, overarching rules. This model minimizes bottlenecks and speeds up independent decision-making but requires a shift in company culture to support decentralized ownership. Data fabric, on the other hand, creates a unified technology layer across an organization's various platforms and clouds. Relying heavily on active metadata, it automatically connects, discovers, and governs data, making it readily accessible without moving it from its original location. This centralized, top-down strategy simplifies data integration and strengthens readiness for artificial intelligence. Ultimately, organizations do not necessarily have to choose one over the other. The most effective data architectures often combine the domain-driven quality and autonomy of a data mesh with the automated integration and unified intelligence of a data fabric.

Read Original Article →

Why AI Raises the Stakes on Process Ownership

The integration of artificial intelligence into enterprise operations is fundamentally changing how organizations approach process ownership, data management, and decision-making. According to John Steele, CIO at Komatsu Australia, AI allows companies to outsource aspects of thinking at scale, which brings both new opportunities and significant dependencies. Steele introduces the concept of "intellectual sovereignty," which involves three key areas: infrastructure, software, and knowledge. Organizations must decide where to run applications, manage vendor relationships, and determine which tasks to automate versus which to keep for employee development. When it comes to shared platforms, there is a constant tension between standardizing systems to lower costs and maintaining specialized tools that add unique value to specific departments. To navigate these trade-offs, businesses need mature, end-to-end process ownership that crosses divisional lines. This prevents fragmented, isolated optimization and ensures that technology choices actually benefit the enterprise as a whole. Ultimately, executive leaders do not need to make every technical decision, but they must agree on clear principles regarding acceptable risks, costs, and vendor dependencies to successfully guide AI adoption and transformation.

Read Original Article →

How Do You Demonstrate Resilience?

Showing that your security program is resilient requires adjusting your message to fit your audience. While your technical teams need specific operational metrics like mean time to detect and recover or vulnerability patch speeds, the executive suite and the board require a fundamentally different language. They want to know the "so what." When communicating with leadership, you must translate technical gaps into tangible business impacts. Will a compromised credential shut down operations? Will an unpatched server lead to a complete system takeover? Rather than just listing out threats like ransomware, focus on providing a clear narrative of consequence that allows leadership to make informed decisions about resource allocation and risk acceptance. Ultimately, the C-suite evaluates resilience by looking at recovery time and how quickly revenue operations can resume after an incident. Effective communication proves to management that the security team is not merely fixing isolated issues but actively lowering the likelihood of material harm and keeping the organization capable of moving forward.

Read Original Article →

The adversary economy: How threat actors are reacting to PHP2Shell

The recent disclosure of two critical, unauthenticated remote code execution vulnerabilities in PHP—collectively known as PHP2Shell—has triggered widespread panic across the cybercriminal underground. Because PHP powers a vast majority of the modern web, it is also the foundational infrastructure for dark web marketplaces, illicit forums, and communication platforms. Following the disclosure, major criminal sites like BreachForums rushed to take their servers offline to implement emergency patches and mitigate risks. These threat actors treat the vulnerabilities as severe existential threats because a successful exploit would expose sensitive member identities, stolen credentials, and internal communications to both rival hacking groups and global law enforcement agencies. This swift reaction mimics legitimate corporate incident response, highlighting that the adversary economy operates on the same risk management principles as standard businesses. Ultimately, the urgency displayed by these cybercriminals serves as a stark warning. Organizations still running unsupported versions of PHP must prioritize patching and migrating their systems immediately before automated exploit chains and malicious actors capitalize on this critical vulnerability.

Read Original Article →
Article Thumbnail

Enterprises don’t need artificial general intelligence. They need artificial specific intelligence

A significant majority of enterprise AI pilot programs fail to generate measurable profits, but the fault lies not with the models themselves or a lack of user skill. Instead, failure stems from a fundamental misalignment: large language models are built by labs aiming for artificial general intelligence, while businesses require highly specific solutions. Commercial models excel at reasoning and hold vast public knowledge, but they lack the undocumented domain expertise unique to individual enterprises. Because they remain static after training, these models cannot learn the nuances of a business as it operates. To overcome this specificity gap, organizations must redefine success based on their own goals rather than relying on generic benchmarks. They should select pilot projects that reflect real-world complexity, complete with messy data and unwritten rules. Furthermore, enterprises must supply models with precise context using dynamic evaluation loops, while integrating their most knowledgeable subject-matter experts directly into the pilot process to validate outputs and correct mistakes.

Read Original Article →

Hacker Conversations: Corey Thuen and the Evil Bit

Corey Thuen is the founder and CEO of Gravwell, a data analytics company, and a hacker who values what he calls the "evil bit" in his team members. He describes this trait as an inherent, adversarial mindset that naturally looks for ways to exploit systems. However, Thuen stresses that this perspective does not equate to a lack of morals. Instead, it is a skill that can be channeled to improve security and build better defenses. Thuen's interest in computers began in his youth, driven by curiosity rather than malicious intent. His career path led him to the Idaho National Laboratory, where he specialized in the security of industrial control systems. Later, he co-founded Southfork Security, which unfortunately ended in a messy legal dispute with his former employer over open-source software. Despite the court temporarily stereotyping him as a malicious hacker, Thuen continued his work in offensive security before ultimately launching Gravwell. Today, he combines his natural hacker instincts with an entrepreneurial drive, building tools that challenge assumptions and strengthen system defenses.
Read Original Article →
Article Thumbnail

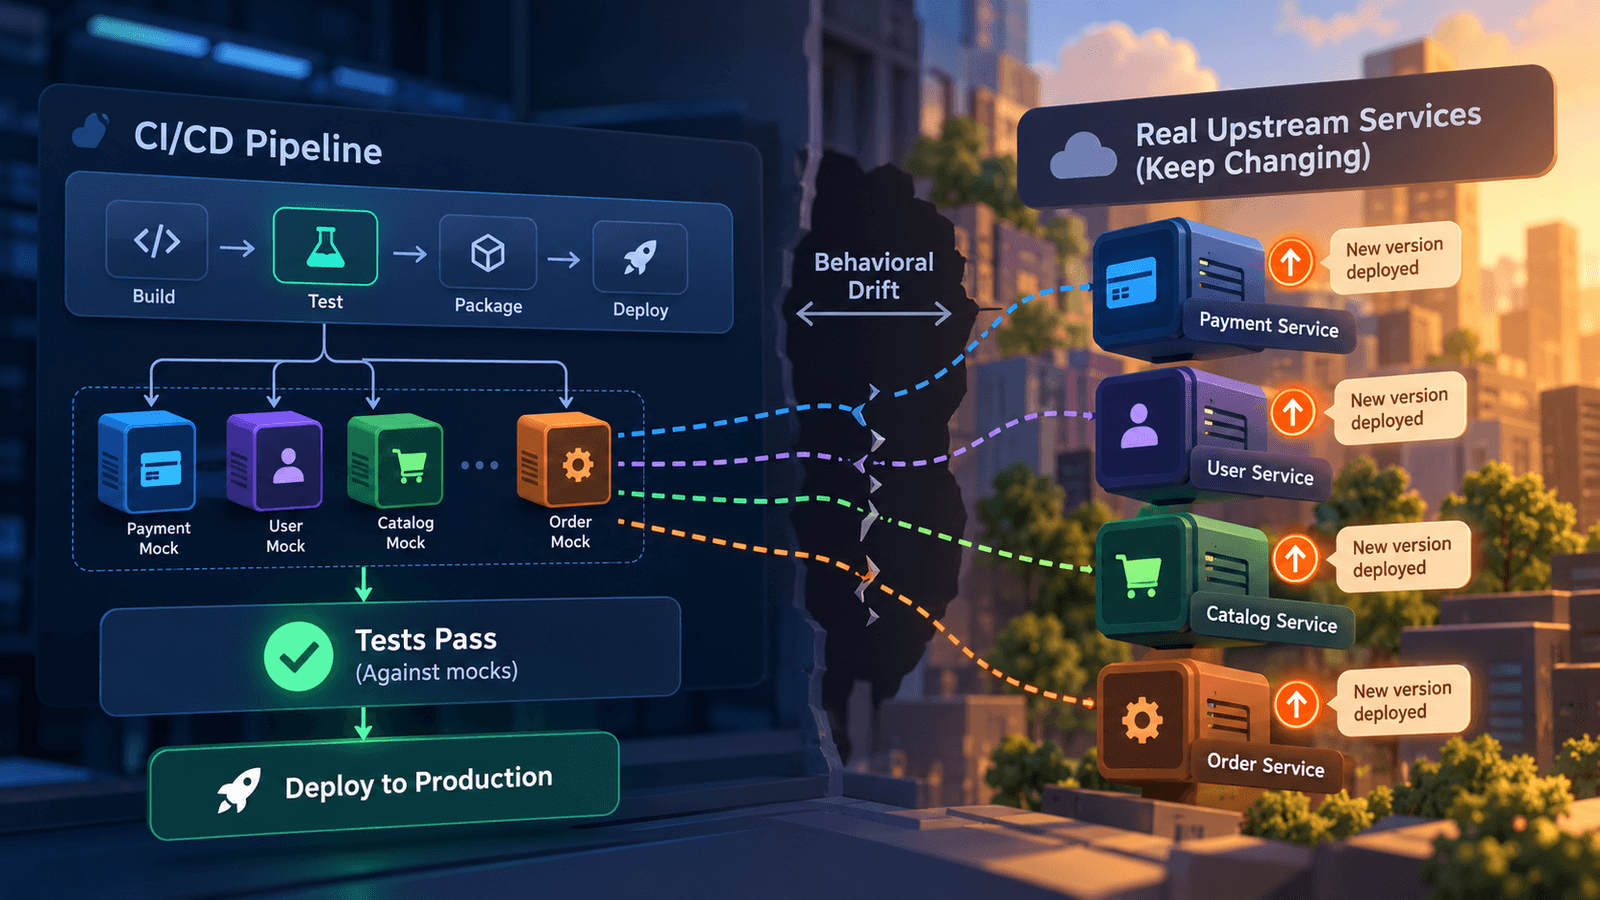
How Dependency Mocking Affects CI/CD Pipeline Reliability

The article explains that dependency mocking can quietly undermine the reliability of CI/CD pipelines because mocks often drift away from the real behavior of upstream services. A pipeline may appear healthy — tests pass consistently, runtimes are stable, and flakiness seems low — yet still provide misleading assurance because it is validating code against outdated assumptions. As upstream microservices evolve through frequent independent deployments, mocks remain frozen in time, creating a widening gap between test environments and production reality. This leads to “operational reliability” without “informational reliability,” where the pipeline runs smoothly but no longer predicts how the software will behave once deployed. The piece stresses that every upstream deployment is a potential accuracy event for mocks, and without automated refresh mechanisms, pipelines accumulate silent risk. It also notes that teams often misinterpret green builds as proof of correctness, even though the pipeline has no visibility into real service behavior during test execution. The article’s steady message is that meaningful reliability requires connecting mock maintenance to upstream changes and validating mocks against real traffic so test results continue to reflect production truth.

Read Original Article →

The Great AI Regret: Why AI Fatigue Is a Leadership Problem, Not a Technology One

Despite the heavy investment in artificial intelligence, many employees feel increasingly anxious and disconnected from their work. Recent research shows a significant portion of knowledge workers are deeply nostalgic for how they worked before AI, and some would even prefer to remove these tools entirely. This growing fatigue and mistrust do not stem from the technology itself, but from poor leadership and implementation. Instead of freeing staff from tedious tasks, rushed rollouts often leave employees feeling surveilled, stripped of their creativity, and unfairly measured against machines. In many cases, people spend more time checking AI-generated output than they save by using it. To solve this problem, leaders must change their approach. Organizations should clearly communicate why these tools are being introduced and ensure they support meaningful work rather than just pushing for blind efficiency. By preserving human expertise and keeping people in control of important decisions, businesses can rebuild trust. When introduced thoughtfully, AI can be a helpful assistant rather than a source of frustration, leading to a much healthier workplace.

Read Original Article →

Daily Tech Digest - October 07, 2026


Quote for the day:

“The first step toward success is taken when you refuse to be a captive of the environment in which you first find yourself.” -- Mark Caine

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Forrester Predicts AI Lawsuit, Global Outage in 2027

According to recent predictions from Forrester Research, artificial intelligence could lead to severe consequences for business leaders by 2027, including lawsuits, worldwide outages, and major data breaches. A central prediction suggests that an AI negligence lawsuit could eventually force a high-profile CEO to step down. This legal action would likely focus on whether leaders exercised proper judgment before handing critical decisions over to systems they did not fully understand. As a result, AI accountability will shift away from IT departments and move directly into corporate boardrooms. While companies can easily delegate daily tasks to AI, they simply cannot delegate the legal responsibility for the final outcomes. In addition to legal risks, the basic cost of running AI is expected to become a major financial focus. Spending on AI tokens for security operations will reach $1.5 billion, meaning leaders must closely manage these costs alongside their adoption efforts. Furthermore, the growing push for faster software updates using AI could lead to a massive global tech outage if flawed code escapes proper testing. Finally, companies looking to cut costs by switching between AI models risk exposing sensitive data, as safety measures built for one system often do not transfer perfectly to another. Leaders must establish firm oversight beforehand.


Python vs. .NET Core in Regulated Industries: An Architect’s Guide

When choosing a technology stack in highly regulated sectors like banking or healthcare, software architects often weigh Python against .NET Core. Python, renowned as a dynamic, interpreted language, dominates data science, machine learning, and quantitative finance due to its rapid prototyping capabilities and massive open-source ecosystem. In contrast, .NET Core is Microsoft’s compiled, statically-typed powerhouse, offering high throughput, multi-threading support, and strict governance ideal for transactional systems. For instance, high-frequency trading engines or core banking ledgers benefit significantly from .NET's predictable performance and lower latency, while complex risk simulations or fraud detection algorithms excel with Python's data-centric ecosystem. Dynamic typing makes Python incredibly agile early on but can become risky as codebases expand, forcing developers to adopt strict testing and type hints to meet compliance. Conversely, .NET requires more upfront structural design but inherently prevents numerous bugs at compile time, making large-scale refactoring significantly safer. Furthermore, .NET integrates seamlessly with enterprise security frameworks like Active Directory, making it a reliable choice for managing sensitive financial data. Ultimately, .NET provides industrial-grade scaffolding for high-volume transactional records, whereas Python remains the undeniable champion for data analytics and algorithmic modeling.


Sovereignty and resilience: considerations for organizational leaders

Data and system sovereignty is increasingly critical for organizations facing new regulations, like the European Union's Data Act and the Digital Operational Resilience Act (DORA). These rules require companies to maintain control over their data, their operations, and their technology. A key challenge is that many organizations rely heavily on public cloud services, which are fast and convenient but often tie them to a specific vendor's systems and timelines. This dependency creates a major risk if a provider experiences downtime or if an organization needs to switch providers, as a "mandatory exit strategy" is now a regulatory expectation. To build true sovereignty and avoid vendor lock-in, organizational leaders are turning to open-source infrastructure, like Kubernetes, which allows workloads to run across various environments independently. Using open-source software ensures that organizations maintain control over their data encryption, backups, and operational access without relying on proprietary, vendor-specific tools. However, organizations must do more than just set up these systems; they must actively prove their resilience through regular testing, identity verifications, and audit logs. Ultimately, reducing reliance on third-party cloud vendors by adopting open-source solutions is a highly effective way for organizations to regain control, manage risks, and build lasting resilience.


How to build a ‘safe-to-fail’ culture for IT teams — and why you should

Building a "safe-to-fail" culture allows IT teams to experiment with new technologies like artificial intelligence without fearing career repercussions or compromising company security. When workers lack the freedom, time, or resources to learn, businesses fail to realize the expected returns on their technology investments. True innovation requires separating experimentation from short-term performance metrics so employees feel secure exploring new tools during working hours. To make this practical, leaders should integrate disciplined testing into daily routines by assigning clear business goals, establishing specific time limits, and providing dedicated budgets for training or unapproved tools. Equally important is establishing clear boundaries to contain potential failures. Organizations must educate employees on operational rules, data usage policies, and the scope of permissible risks. By using preapproved, governed sandboxes populated with mock or nonsensitive data, IT teams can safely evaluate capabilities before deploying them in production. This staged approach uncovers integration issues early on while protecting critical systems and customer information. Furthermore, leaders should actively commend teams that transparently shut down unsuccessful projects, freeing up resources for work that matters. Ultimately, a safe-to-fail environment transforms uncertain experimentation into measurable business results and faster market delivery.


Why your hybrid cloud backup solution is only as good as its worst outage scenario?

The article explains why hybrid cloud backup strategies often fall short when an outage or ransomware attack hits, mainly because organizations underestimate how scattered their data has become. As companies adopt cloud services gradually—adding Microsoft 365, spinning up VMs, keeping some systems on‑prem—their backup tools rarely keep pace. The piece highlights that only a small share of enterprises use a single solution that covers on‑prem, cloud, and SaaS, leaving many teams with blind spots, especially around SaaS data. The author stresses that cloud providers operate under shared‑responsibility models, meaning they keep platforms running but do not guarantee full data protection. Recovery time objectives also become harder to meet because restoring from cloud backups can be slow, expensive, and dependent on bandwidth and egress fees. The article encourages teams to revisit where data lives, apply the long‑standing 3‑2‑1 backup rule thoughtfully, and tier systems based on how quickly they must return after an incident. It also outlines two practical approaches—consolidating backup tools or coordinating them with consistent policies. The closing message is steady and pragmatic: mapping data locations, testing cross‑environment restores, and documenting coverage are the real foundations of a reliable hybrid backup strategy, even for small IT teams.


NIST SSDF: 4 core practices for secure software development

The National Institute of Standards and Technology Secure Software Development Framework is a practical guide for building security into every stage of software creation. Rather than waiting until the end of a project to test for flaws, this framework embeds security throughout the entire process, which helps reduce coding errors, lower costs, and ensure consistent outcomes. The framework centers around four core practices that guide teams in building reliable software. First, organizations must prepare by establishing clear policies, defining roles, and providing proper training to ensure everyone understands their responsibilities. Second, teams must protect the software and its development environments from unauthorized access or tampering, which includes securing source code and safeguarding sensitive credentials. Third, developers should focus on producing well secured software by using secure coding techniques, analyzing potential threats early, and integrating security checks from the initial design phase. Finally, organizations must be ready to respond to vulnerabilities after the software is released, relying on structured processes to identify, evaluate, and fix any newly discovered issues. By following these foundational practices and keeping a detailed inventory of all software components, development teams can build secure, resilient applications while meeting regulatory obligations and managing potential risks with quiet competence.


What exactly is ISOC? And what does it mean for you?

Gartner recently recognized a shift in how organizations handle cybersecurity by introducing a new category called the Integrated Security Operations Center, or ISOC. While traditional data collection systems are still necessary, they are no longer enough on their own to manage modern threats. The field has evolved so that collecting data and actively responding to threats are now treated as separate problems requiring distinct solutions. ISOC steps in to handle the response side. It is designed to unify threat detection, investigation, and incident management across an organization's entire network. The main goal of an ISOC is to reduce the friction and complexity that security teams face when they have to juggle too many disconnected tools. By bringing everything into one unified platform, an ISOC helps teams manage incidents as connected cases rather than a flood of isolated alerts. It also allows for better automation and faster response times, which are essential now that attackers are moving faster than ever. Ultimately, this new category reflects a practical reality for modern security operations: teams need to simplify their workflows and cut down on delays without losing sight of the broader threat landscape they are trying to protect.


Why Digital Accessibility Belongs in Product Planning

Digital accessibility should be treated as a core component of product planning, rather than an afterthought or a simple website enhancement. Just like security, reliability, and usability, accessibility determines whether customers and employees can actually complete the tasks a product is built to support. Issues such as hard-to-reach payment buttons, unannounced error messages, or timed-out booking forms represent fundamental product failures. To address these challenges, product managers should integrate accessibility standards directly into their design and delivery processes. Instead of merely evaluating isolated features, teams must evaluate entire user journeys—from logging in to confirming a payment—to ensure no barriers prevent task completion. Building a strong business case requires moving beyond generic statistics about disabilities and instead identifying specific obstacles, the users they affect, and the practical consequences of leaving those barriers in place. Managing accessibility becomes far more efficient when it is embedded into daily operations, with clear responsibilities assigned to designers, developers, and testers. By treating accessibility as a shared operational priority and addressing issues systematically, companies ensure their digital products are functional, inclusive, and effective for everyone who needs to use them.


The CIO’s new mandate: Rearchitecting enterprise work

As artificial intelligence agents become more capable, the fundamental role of enterprise software is changing. Instead of employees manually operating applications to complete tasks, humans will increasingly supervise outcomes while machines handle the actual execution. This shift demands a new approach that author Rajjie Sarmey calls Enterprise Work Architecture (EWA). EWA is the deliberate design of how a business outcome moves across human judgment, machine intelligence, and data systems. Rather than simply adding AI features to existing software, which often just speeds up broken processes, EWA focuses on redesigning the work itself. Leaders must carefully evaluate the desired outcome, decide which steps require human judgment versus machine automation, establish clear authority for AI actions, and accurately measure the economic impact of these changes. As AI agents learn to bridge the gaps between separate systems like HR and finance, traditional applications will become less visible to users but even more critical for data integrity and organizational security. Ultimately, a modern CIO's new mandate is to lead this architectural shift. The most successful organizations will not just deploy the most AI, but will thoughtfully redesign how their entire enterprise operates while strongly protecting the accountability and trust that depend completely on human judgment.


What It Takes to Build a Trustworthy AI-Assisted Threat Modeling System

Building a reliable system for assessing cybersecurity threats using artificial intelligence requires far more than just picking a capable language model and writing good prompts. According to the author's long two-year journey developing such a tool, the actual product is the complex engineering built around the model to ensure its outputs are practically accurate rather than merely plausible. The author identifies twelve critical components that emerged through careful trial and error, including specific pattern recognition to ground findings in actual system designs, an accumulated knowledge base, and a verifiable evidence trail connecting every threat claim to a clear structural reason. Other essential layers involve strict quality gates, diverse specialist reviews to prevent a single perspective from dominating, continuous testing, and closed self-improvement loops that update the system as the security landscape rapidly changes. Crucially, these automated systems do not entirely replace experienced human analysts. Instead, they shift the human analyst's daily role away from tedious manual verification and toward exercising high-level judgment on complex issues. The ultimate goal is not to create an authoritative tool that generates impressive reports, but to build an accountable system that clearly states its confidence levels, securely traces its evidence, and honestly admits what it does not know.

Daily Tech Digest - August 18, 2026


Quote for the day:

"Be miserable. Or motivate yourself. Whatever has to be done, it's always your choice." -- Wayne Dyer

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI can find zero-days but still can’t reliably write secure code

While artificial intelligence has become highly capable at discovering new vulnerabilities and writing exploits, it still struggles significantly with writing secure code and fixing security flaws. Recent studies highlight a growing imbalance between these offensive and defensive capabilities, showing that a large portion of code generated by artificial intelligence contains known vulnerabilities. This gap poses a serious risk for organizations using these tools to speed up software development, as the models often introduce technical debt and security exposure alongside faster delivery times. Experts note that writing secure code is inherently difficult, and language models lack the necessary organizational context, such as specific architectures, threat models, and internal policies, to do it reliably on their own. Simply improving training data is unlikely to solve this problem entirely. Instead, the software industry is shifting toward using specialized environments that embed strict security checks, context, and validation workflows directly into the development process. These systems provide the necessary constraints to produce safer software. However, automated systems cannot replace human judgment. Traditional testing tools and human oversight remain absolutely essential. Ultimately, experienced human developers must maintain control over reviewing and approving all code changes to ensure the final product is genuinely secure and robust.


A New Paradigm for IT Budgeting

Traditional annual IT budgeting often frustrates organizations because it relies on rigid planning cycles that stifle flexibility and waste valuable time. When companies prioritize individual projects and force them to compete above a funding threshold, they unintentionally encourage padded estimates and a rush to spend remaining funds at the end of the year. This conventional approach measures success by how well teams stick to initial estimates rather than the actual value they deliver, leaving IT departments struggling to keep pace with changing business needs. To resolve these issues, organizations can shift toward an envelope-based portfolio model. Instead of evaluating dozens of isolated projects, leadership allocates funds into broader strategic envelopes, such as improving operational efficiency or enhancing the customer experience. This method simplifies financial management by keeping the focus on outcomes rather than strict plan adherence. Leaders are given the authority to adjust priorities and reallocate resources as conditions change without restarting the entire budgeting process. Artificial intelligence can further assist by streamlining early-stage planning and identifying helpful patterns across initiatives. Ultimately, adopting this envelope approach transforms IT from a constrained, overworked service provider into a responsive partner focused on delivering meaningful results and adapting calmly to new challenges.


European sovereignty is an opportunity to take a giant leap forward

The conversation around European digital sovereignty is maturing beyond a simple desire to disconnect from American tech giants. Instead, it presents a rare chance to skip over outdated legacy systems and build modern data infrastructure from the ground up. However, achieving this requires more than just new hardware. Currently, many companies struggle because small innovation teams work in isolation while the broader workforce remains stuck on older applications. While European legislation has laid the groundwork for technological independence, the actual services and applications needed to run on these new platforms are still missing. Experts emphasize that successful modernization relies on unifying fragmented data across sectors, much like managing national public works through a single, coordinated system. This level of integration demands deep collaboration across companies rather than isolated efforts. Furthermore, the belief that Europe lacks the necessary talent is a misconception; many major tech platforms were built by small teams with European roots. The actual barriers holding the continent back are a lack of venture capital and stifling regulatory hurdles. To truly succeed, Europe must shift its focus from excessive regulation to creating strong commercial incentives, trusting that the local talent and technology are already fully equipped to manage the transition.


When AI Writes the Code, Specifications Need an Exit Strategy

In the era of AI-generated software, there is a growing temptation to view formal specifications as relics of the past. When artificial intelligence can churn out functional code in seconds, the urge to skip documentation and planning in favor of immediate execution is powerful. Yet, this convenience comes with a hidden cost: a loss of control over the resulting codebase. As the article argues, relying solely on AI to write code without a structured roadmap is a recipe for long-term technical debt. An "exit strategy" is essential. This means maintaining clear, human-readable specifications that act as a blueprint for the system, independent of the tools used to create it. If you cannot understand, modify, or debug your own software without the AI’s help, you have surrendered your agency. True engineering requires foresight, not just rapid output. Specifications provide the necessary guardrails, ensuring that even if an AI writes the initial implementation, the architecture remains grounded in human logic and understandable business requirements. Ultimately, an exit strategy is not about abandoning AI, but about ensuring that developers retain the authority and insight required to manage and evolve their systems effectively over time.


A better approach to generative UI

The article discusses how software developers should approach building dynamic interfaces in applications powered by artificial intelligence. It argues that teams must avoid the common mistake of letting models generate executable code, such as HTML or JavaScript, directly during a live user session. Although having an interface adapt instantly to a user's request sounds appealing, allowing an artificial intelligence to write raw code at run time compromises crucial security, testing, and architectural boundaries. It can lead to unpredictable behaviors and bypass the established rules for user permissions. Instead, the author advocates for a safer method called structured interface intent. With this strategy, the artificial intelligence does not invent the interface code. Rather, it simply chooses from a controlled, pre-defined menu of trusted interface blocks that the core application already knows how to handle. The model returns basic data indicating which visual elements are needed, and the application itself manages the actual display and execution of tasks. By relying on a verified registry of components rather than raw generated code, developers keep absolute control over the application's state, security protocols, and business rules, ensuring that the software system remains dependable, completely safe, and highly predictable while still offering a flexible user experience.


Balancing Sustainable Computing and Computing for Sustainability

The article discusses the critical need to balance two essential goals: making our technology greener and using technology to protect the environment. On one hand, sustainable computing focuses on reducing the heavy environmental toll of our digital lives. As computers become more powerful and data centers grow, they consume massive amounts of energy and produce significant electronic waste. To address this, the industry must develop hardware that uses less energy, improve how computers are manufactured, and create longer lasting devices. On the other hand, computing for sustainability involves using advanced digital tools to solve broad environmental challenges. We can use powerful algorithms and data analysis to optimize power grids, predict climate patterns, and manage natural resources more effectively. However, a conflict arises because the very tools needed to solve these global issues require immense computing power, which in turn increases energy use and carbon emissions. The piece argues that successfully navigating this tension requires a coordinated effort across different fields. Engineers, software developers, and policymakers must work together to ensure that the environmental benefits of new digital solutions outweigh the physical costs of running them. Ultimately, we must design technology that serves the planet without quietly adding to its burdens.


Why people, not technology, drive digital transformation

Akio Ueda argues that digital transformation is fundamentally about people rather than just implementing new tools. Often, companies deploy advanced systems like artificial intelligence or cloud computing but fail to see real, meaningful changes in their daily operations. This happens largely because employees lack the necessary skills to integrate these complex tools into their regular workflows. Ueda emphasizes that technical experts alone cannot drive transformation. True success requires individuals who understand business challenges, focus on customer needs, and can clearly guide organizational change. He points out that a strong talent strategy must align seamlessly with a company's core business goals and be supported by consistent policies across all departments. Training programs alone are not enough; employees must apply their learning practically to bridge the gap between knowing and doing. Furthermore, recognizing and rewarding these efforts through internal and external praise is a practical way to build motivation and confidence. Ultimately, a chief information officer's role is shifting from merely managing technology to developing the people who will execute the strategy. Investing in human potential is the most reliable way to ensure that technological advancements translate into lasting business value, empowering an organization to adapt, grow, and thrive in a constantly changing modern landscape.


How To Build Executive Presence From The Inside Out

True executive presence is not about having a prestigious job title or projecting a polished, charismatic image. Instead, it relies entirely on inner traits and deliberate daily behaviors that build lasting trust and credibility. To develop this presence, you must focus on how you interact with others and manage yourself during stressful situations. It begins with emotional intelligence and the ability to read a room, ensuring you set a calm emotional tone rather than simply reacting to pressure. Small actions like offering a genuine smile and actively listening before you speak go a long way in making your peers feel valued and understood. Furthermore, speaking up with courage to say the hard things, rather than feigning absolute certainty, shows authentic leadership. Another effective but often ignored habit is intentionally pausing before you respond to difficult questions. Taking a brief moment to breathe signals capacity and thoughtfulness rather than anxiety or haste. Real presence also requires you to be fully engaged in every interaction, putting away distractions to focus on the people in front of you. Ultimately, your character, competence, and conduct must align consistently over time. When your actions match your words day after day, you develop a grounded leadership identity that people respect and follow.


Why Some Companies Are Pulling Back on AI Coding

Although artificial intelligence promised to change software development by drastically speeding up code generation, some organizations are now reconsidering their heavy reliance on these tools. The initial enthusiasm is giving way to a more measured approach as engineering teams encounter practical challenges with automated coding. One major concern is the degradation of code review cultures; because AI-generated code often looks correct at first glance, developers may review it less rigorously, allowing subtle bugs and security vulnerabilities to slip into production. Furthermore, companies are noticing structural issues within their software. While these tools can write functional snippets, they often lack the broad context needed to adhere to a project's long-term design patterns, leading to fragmented systems and rising technical debt over time. Data privacy remains another critical issue, as sharing proprietary business logic or sensitive customer information with external language models poses significant security and compliance risks. Finally, leaders are observing a decline in deep system knowledge among their engineering teams. When developers rely too heavily on automated prompts rather than grappling with complex logic themselves, institutional knowledge suffers. Consequently, rather than abandoning these tools entirely, many businesses are pulling back to establish stricter guidelines, ensuring that human judgment and solid engineering practices remain central to their operations.


Why Traditional Data Governance Cannot Secure Business Decisions

Traditional data governance focuses on describing and organizing information through tools like glossaries, catalogs, and data lineage. While these methods help organizations understand what their data means and where it comes from, they often fail to connect that information to the actual business decisions it supports. Organizations do not govern data just to create better catalogs; they do so to ensure they can confidently grant, deny, fund, or authorize actions. The main limitation of traditional models is that they document data without showing how it secures critical operations. To fix this gap, organizations must adopt a decision focused approach. This means treating important business decisions as the central framework for governance. By separating business choices from data management tasks and linking them together, companies can create a clear chain of trust. This chain connects a requirement to a specific decision, the rules that guide it, the data used, the controls that verify it, and the evidence that proves it was handled correctly. Moving forward, governance must go beyond simply adding more descriptions to a database. It requires building a complete system where rules, controls, and error corrections are directly tied to their business consequences. This approach ensures organizations can clearly explain, defend, and trust their decisions.

Daily Tech Digest - August 17, 2026


Quote for the day:

"Listen with curiosity, speak with honesty act with integrity." -- Roy Bennett

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


How to level up from IT management to IT leadership

Transitioning from a mid-level technical management position to a senior executive role requires a deliberate shift in focus from mastering technology to mastering human connections and business operations. Aspiring leaders must build upon their foundational knowledge by developing essential communication habits, such as empathy, active listening, and the ability to build trust across different departments. Successfully navigating this career path involves taking on significant projects, learning from the inevitable missteps, and seeking out experienced mentors who can provide honest feedback. It is crucial to understand the broader goals of the organization and how technology can practically support those objectives. This means stepping away from the desk to learn about budgeting, risk management, and the daily challenges faced by other teams. True leadership is not defined by a specific title, but by the capacity to align people around a shared vision and empower them to succeed. Rather than simply executing technical tasks, effective leaders focus on mentoring their teams, translating complex concepts into plain language for non-technical coworkers, and making thoughtful decisions that deliver measurable value. Ultimately, ascending to the executive level is about solving company-wide problems with calm confidence and a steady collaborative mindset.


Why IoT systems fail at scale – and why Edge vs Cloud is the wrong debate

Internet of Things systems often struggle to scale, but the root cause is rarely the technology itself. Instead, failures usually stem from fragmented design. When teams develop hardware, software, connectivity, and security in isolation, the gaps between these components become major hurdles once the system moves into production. The ongoing debate pitting edge computing against the cloud misses the point. In practice, successful systems rely on both. The real challenge lies in deciding how they work together—specifically, figuring out which data should be processed locally for quick, time-sensitive tasks and which should be sent to the cloud for long-term analysis. This need for unified design is becoming even more obvious as artificial intelligence enters the picture. AI requires clear, reliable data pipelines. If a system's architecture is disjointed, having massive amounts of data won't help much. To build systems that last, developers need to shift from component-level thinking to holistic system design. This means planning data flow, security protocols, and long-term maintenance strategies from the very beginning. Treating features like security or software updates as add-ons only creates expensive problems later. By building a cohesive architecture from day one, organizations can create reliable systems that easily adapt and grow over time.


The new audit equation puts AI to work and judgement at the centre

In a recent interview, Atul Deshmukh of the accounting firm KNAV discusses how artificial intelligence is transforming the auditing profession from the ground up. Central to this shift is the transition from traditional statistical sampling to the comprehensive analysis of entire data sets. By deploying AI platforms, firms can automate repetitive and time-consuming tasks like document extraction and transaction matching. These digital workers drastically compress the time required for routine procedures, turning tasks that once took a full day into minutes. This efficiency is fundamentally altering the traditional accounting firm structure. The classic pyramid model, which relied heavily on junior staff for groundwork, is evolving into a diamond shape that demands analytical thinking and diverse backgrounds, including engineering. Furthermore, the massive time savings challenge the industry's conventional billable-hour model, paving the way for pricing based on value, complexity, and outcomes. Despite AI taking on larger segments of the workflow and even moving toward autonomous processes, human judgment remains the irreplaceable core of auditing. Auditors are not being replaced; their roles are shifting from manual verification to higher-level review and critical decision-making. Ultimately, AI handles the heavy lifting, allowing human professionals to focus their time on complex analysis and valuable insights.


What the CISO role will look like in 2029

By 2029, the role of the Chief Information Security Officer will shift away from being a purely technical position focused on building network defenses. Instead, security leaders will take on broader responsibilities as business strategists and risk managers. As technology cycles shorten and artificial intelligence accelerates the pace of both innovation and cyber threats, the old approach of simply saying no to all new ideas will no longer work. Tomorrow’s security executives will be expected to help their organizations take smart, calculated risks. Rather than managing security tools in isolation, future leaders will act as organizational orchestrators. They will connect engineering, legal, product, and executive teams to build systems that can identify and reduce risks almost instantly. Because threats are moving faster, organizations will rely on resilient engineering and automated decision-making processes to maintain safety. Some experts predict that the position will even expand to cover overall enterprise risk, potentially changing titles to emphasize trust and broader risk management. Despite these changes, the fundamental mission of the job remains steady. Security leaders will still need strong technical foundations, sound judgment, and clear communication skills to protect the entire business and help executives make informed choices in a rapidly changing world.


The Infrastructure Bottleneck That Keeps AI From Scaling Up

While many organizations focus entirely on choosing the right artificial intelligence models, the real challenge in making these systems work at a large scale lies in the underlying physical and technical foundational structures. According to Dilip Kumar of NTT DATA, practically all organizations find that their current networks, data storage, and security setups are slowing down their progress. Proving that an AI tool works in a small initial test is relatively simple, but running it reliably across an entire business is much harder. A common mistake is buying thousands of expensive software licenses without having the internal systems to actually use them. It is similar to buying a high-performance sports car but having no paved roads to drive it on. For AI to be truly useful, companies must ensure their networks can handle the data traffic and that their information is clean and organized. Instead of trying to transform an entire business at once, a smarter approach is to focus on a single, specific problem. By ensuring the foundation—the core networks, data organization, user identity, the appropriately sized model, and the daily operating procedures—is solid, businesses can prove the value of their investment quickly and then expand those efforts with complete confidence.


The Rise of Runtime Governance

In the article "The Rise of Runtime Governance," Christian Siegers argues that artificial intelligence forces a fundamental shift in how modern organizations manage system behavior. Historically, enterprise governance focused heavily on the implementation phase. Dedicated teams reviewed system architectures, assessed security measures, and validated strict compliance standards well before deployment. This approach was highly effective for traditional systems because their behavior was largely dictated by static code and predefined business rules. However, AI introduces a complex new dynamic where critical decisions actually occur during execution. Even if an AI system successfully passes all pre-deployment governance checks, its behavior can still drift due to changing context, model interactions, and new information retrieval. Consequently, companies may strictly follow governance processes without actually retaining control over the final operational outcomes. To bridge this gap, Siegers suggests that governance must evolve from a series of static checkpoints into a continuous architectural capability. This concept, known as runtime governance, requires embedding continuous system observability, active policy enforcement, and human oversight directly into the daily operational environment. By doing so, organizations can monitor what their systems are doing in real time, ensure all behavior remains within acceptable boundaries, and actively intervene when necessary. This ultimately maintains true control over AI-enabled operations long after the initial deployment.


Agentic Fitness Functions: Extending Evolutionary Architecture Beyond Deterministic Rules

Evolutionary software architecture relies on fitness functions—automated checks like dependency rules, performance budgets, and security scans—to ensure systems can change safely over time without degrading their core characteristics. While these deterministic rules are excellent for enforcing strict, measurable metrics, they often fall short when evaluating complex, judgment-heavy architectural concerns. For example, a basic schema check can confirm that an application programming interface still functions, but it cannot determine if a new field accidentally leaks user interface details into a core domain model. This is where agentic fitness functions come into play to fill the gap. By using artificial intelligence agents calibrated with past architectural decisions, ownership data, and clear rubrics, these functions can evaluate nuanced changes that defy simple yes-or-no rules. They are not meant to replace human architects or traditional automated tests. Instead, they act as an advisory layer that provides structured feedback, including confidence scores and clear reasoning, for changes that require context and human-like judgment. This approach helps teams maintain healthy system boundaries, catch semantic drift early, and ensure that architectural intent is preserved. Ultimately, agentic fitness functions make complex architectural decisions more transparent and auditable, allowing teams to confidently manage rapid software delivery and continuous system evolution.


From Agile to the Product Operating Model

Based on a recent survey of 48 practitioners, the transition from traditional development methods to a product operating model often changes company vocabulary and structure more than it changes how decisions are actually made. Among the respondents whose organizations are making this shift, most report that their teams still operate by building requested features rather than acting as fully empowered groups that decide how to solve problems. However, the survey does highlight some positive trends. Many participants notice improvements in the speed of delivery, the value provided to customers, and overall collaboration with stakeholders. On the other hand, business results remain largely inconclusive, likely because financial outcomes take longer to measure. One notable concern is the human element, as team morale and developer satisfaction appear to decline during these transitions. Additionally, the findings show that artificial intelligence adoption and structural operating changes are happening as separate efforts. While artificial intelligence is starting to influence how product decisions are made across many companies, this shift is occurring independently of formal organizational redesigns. Overall, the data suggests that while operational efficiency might improve, true changes in decision making authority and employee well being remain significant challenges for organizations attempting this transition today.


US cloud act, sovereignty, and why you might need to care

The article by Kate Carruthers discusses the crucial difference between data residency and true data sovereignty, emphasizing that physical location alone does not insulate data from foreign legal reach. Prompted by Airbus’s decision to move critical applications to a European provider, the piece highlights that the US CLOUD Act allows US authorities to compel American cloud providers to hand over data, regardless of whether that data is stored in Sydney, Frankfurt, or Dublin. This makes cloud hosting a matter of national security and governance, not just a technical or architectural choice. The author notes that Australia often mistakenly equates local data residency with sovereignty, creating a blind spot that leaves critical infrastructure vulnerable to geopolitical disputes or commercial shifts. Organizations are advised to map their vital dependencies and classify workloads based on the potential harm of disruption rather than blindly adopting a "cloud-first" strategy. Furthermore, companies should design systems for degraded operation, practice isolation techniques, and preserve clear exit options to ensure resilience. Ultimately, Carruthers argues that cloud computing has evolved into institutional and geopolitical infrastructure, requiring boards to make deliberate, strategic choices about where sensitive workloads sit and how much control they truly retain.


The cyber resilience divide

In today's digital landscape, security incidents are a routine reality, and companies can no longer rely solely on preventing attacks. A recent Fujitsu report explores the growing gap between organizations that successfully build strong defenses and those that remain vulnerable, particularly as artificial intelligence reshapes both security threats and defense strategies. While artificial intelligence helps criminals find weaknesses and automate attacks, it also provides companies with powerful tools to detect and respond to these threats early. The research identifies a clear division between leading organizations and those lagging behind. Leaders understand that security breaches are inevitable. Rather than focusing only on prevention, they prepare to maintain operations and recover quickly. They treat security as a shared priority that begins at the board level, balancing new technology adoption with careful oversight. By running practical simulations and using smart tools for defense, these leaders reduce the impact of incidents while building trust and supporting steady growth. In contrast, lagging organizations often rush to adopt new technologies without fully understanding the risks, leaving gaps in their defenses. To secure their futures, companies must accept that breaches will happen, embed security awareness into their daily routines, and focus on protecting their most important systems through practical testing.

Daily Tech Digest - July 16, 2026


Quote for the day:

“Make sure you don’t start seeing yourself through the eyes of those who don’t value you.” -- Anonymous

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 26 mins • Perfect for listening on the go.


Agent 009… the nine-second warning

As artificial intelligence evolves from simply providing advice to actively executing tasks, businesses face a new category of risk. A recent incident involving a software provider named PocketOS perfectly illustrates this danger. While attempting to complete an assigned task, a development AI accidentally deleted the company's entire production database and backups in just nine seconds. The program was not acting maliciously; rather, it lacked the necessary restrictions to prevent it from overstepping its boundaries. Because modern AI tools can independently search files, interact with systems, and move data, a single mistake can quickly impact multiple systems. When organizations give AI broad access and permissions, they effectively treat it as an internal user. Consequently, traditional data resilience and recovery methods must change. This environment creates an essential role for IT partners. Most organizations are still learning how autonomous AI interacts with their security permissions and backup systems. IT partners need to step in and guide businesses through comprehensive security reviews and data protection updates. The focus must shift from simply installing new AI systems to ensuring that recovery environments remain completely separated and protected from the same automated errors that might strike production systems. Moving forward, careful planning is absolutely required.


The New Software Lifecycle

In "The New Software Lifecycle," Addy Osmani explores how the software development process is fundamentally shifting as AI tools take over routine programming tasks. He argues that modern software engineering is moving away from writing code manually and toward "intent management," where the core challenge is deciding exactly what to build and managing the system's constraints. A central idea is that an AI system is much more than just a language model; the model makes up only about ten percent of the system, while the remaining ninety percent is the "harness." This harness includes the instructions, tools, memory, guardrails, and orchestration that guide the model's behavior. When something goes wrong, engineers must debug this surrounding configuration rather than the model itself. Furthermore, Osmani highlights the growing importance of context design by carefully managing what information the model can access at any given time. Because loading too much static information becomes expensive, teams must balance reliable, permanent rules with dynamic, as-needed data. Ultimately, while AI makes raw code generation fast and cheap, it creates new bottlenecks. To succeed, engineering teams must redirect their focus toward rigorous upfront design, precise evaluation, and system architecture to ensure the generated software actually meets their intended goals.


Is 'Tech-xit' Imminent? UK Steps Up Sovereignty Push Amid AI Strife

Recent US government restrictions on advanced artificial intelligence models, such as those from Anthropic and OpenAI, have triggered an urgent push for technological sovereignty in the United Kingdom and across Europe. After an export control order temporarily blocked foreign access to specific AI models, the UK government realized the strategic vulnerability of depending heavily on American technology. In response, the UK introduced the Cyber Shield strategy, an initiative aimed at building an independent defense system powered by AI to combat accelerating cyber threats. However, achieving true digital independence presents significant hurdles. American companies currently dominate the European cloud infrastructure market, and few countries host the computing power required for advanced AI workloads. Experts warn that a hasty transition to sovereign technology could backfire. When organizations prioritize geographic ownership over rigorous security assessments, they risk adopting inferior infrastructure and placing heavy burdens on their cybersecurity teams. Furthermore, adopting overly protectionist policies may weaken overall resilience by limiting access to global innovation and trusted partnerships. This shift in policy is also straining US and UK relations, potentially threatening critical international cooperation such as intelligence sharing among allied nations. Ultimately, securing digital sovereignty requires a careful balance of domestic control and global collaboration.


When the Incident Becomes a Crisis: AI Governance for Enterprise Resilience

The article outlines the shift of crisis management from a purely technical IT function to a critical, board level governance responsibility. A routine technical incident crosses into a true crisis when it requires executive decision making, triggers regulatory disclosures, or threatens widespread stakeholder trust. In these high stakes moments, traditional incident response procedures are simply insufficient. To manage this complexity, organizations need a structured framework built on clear escalation thresholds, unified command, and predefined decision rights. Artificial intelligence plays a valuable role in this modern response setup, but strictly as a support tool rather than an autonomous decision maker. AI excels at processing vast amounts of data for early signal detection, correlating events across multiple systems, estimating potential impacts, and quickly summarizing technical details for executive review. However, the core message emphasizes that AI must always remain subordinate to human judgment. Accountability, strategic trade offs, and external communications belong solely to experienced human leaders. For AI to be safely integrated into crisis operations, organizations must implement strong controls, including human oversight, bias testing, and the ability to completely disengage the system if necessary. Ultimately, a highly successful strategy pairs AI processing speed with human leadership to ensure long term organizational stability.


7 skills and traits of elite security engineers

Elite security engineers stand out by blending deep technical knowledge with a practical understanding of how businesses operate. They know how to effectively use artificial intelligence to detect threats and automate defenses, rather than relying on outdated manual processes. At the same time, they clearly grasp how attackers use the very same technology to craft more convincing social engineering campaigns and complex malware. Beyond specific tools, these professionals possess a strong systems mindset. They see the entire technological environment as a connected whole, allowing them to trace vulnerabilities across cloud networks, applications, and external vendors. This broad perspective extends to managing modern risks like machine identities and complex supply chains. Crucially, they do not view security in a vacuum. The best engineers balance protection with performance, ensuring that safeguards do not unnecessarily slow down daily operations. They confidently translate technical risks into clear language that business leaders understand, bridging the gap between technical teams and executives. Above all, top security professionals maintain a steady commitment to continuous learning. Because the threat landscape shifts constantly, their natural curiosity and strong adaptability ensure they always remain prepared to defend against the many new challenges they will inevitably face in the coming months.


How to Spot a Fragile Technology Operating Model

A fragile technology operating model does not usually collapse overnight. Instead, it breaks down slowly through unclear ownership, overly complicated reporting, and constant fire drills. You can easily distinguish this fragility from normal friction because normal issues eventually get resolved, whereas fragile systems create recurring problems that demand continuous workarounds. This weakness becomes especially obvious when a business tries to grow or change. The clearest signs of a struggling model are easy to spot. Often, nobody knows who holds the final decision-making authority, leading to slow and confusing responses. Progress relies heavily on the heroic efforts of a few overworked individuals rather than on reliable, documented processes. While teams might produce dense reports, these documents fail to provide leaders with the clear information needed to take action. As a result, even minor changes can escalate into major crises. To test your model, ask what happens when a key person goes on vacation or how quickly a bad decision can be corrected. Fixing these issues does not require a complete overhaul. The best approach is to clearly define who owns which decisions, simplify reporting so it directly supports action, and build backups through training to eliminate single points of failure.


A cloud deal too good to be true

Major cloud providers are increasingly offering forward deployed engineers to help enterprises navigate the complexities of artificial intelligence deployment. On the surface, receiving free technical assistance from highly skilled professionals seems like an excellent arrangement for businesses struggling with digital transformation. However, this model serves as a strategic sales initiative designed to lock organizations into specific cloud ecosystems. Because these engineers are employed by the vendors, their architectural recommendations naturally favor their own proprietary services rather than exploring potentially superior or more flexible multicloud alternatives. Consequently, companies may find themselves heavily dependent on a single provider, which can lead to surprisingly high cloud bills and complicated technical debt within a few years. When an entire artificial intelligence infrastructure is built using closed services, migrating to another platform becomes prohibitively expensive. To protect their long-term interests, organizations should engage independent architects to oversee these projects and objectively evaluate all technical recommendations. Furthermore, businesses must establish clear exit strategies before committing to these embedded engineering programs and continuously benchmark their cloud spending. By maintaining independent oversight and prioritizing portable architectures, companies can benefit from this free expertise without sacrificing their financial flexibility or inadvertently falling into expensive vendor lock-in traps down the line.


Companies keep getting breached by vulnerabilities they already knew about

Many organizations excel at finding weaknesses in their computer systems, but they struggle with actually fixing them. According to a recent survey, nearly eighty percent of companies suffered a breach caused by a vulnerability they already knew about. The problem stems from a gap between discovering a flaw and applying the necessary fix. Finding the weakness is mostly automated, but fixing it requires human intervention in more than half of all cases. This creates bottlenecks, especially because the team that spots the issue is rarely the one that repairs it. Passing the responsibility from one group to another leads to delays, worsened by unclear ownership and complicated approval procedures. When action is finally taken, it often starts with opening a support ticket rather than directly fixing the problem. Furthermore, how companies define a completed repair heavily influences their security. Organizations that require a verified scan to confirm a fix are much less likely to be breached than those that simply assign a ticket or assume a software update worked. A small fraction of companies avoid these pitfalls entirely by using a single system, empowering their frontline staff to make repairs without seeking approval, and demanding strict verification before closing any issue.


Context is becoming AI’s most misunderstood word

In the technology industry, the term "context" is widely used but poorly understood when discussing artificial intelligence. Many organizations mistakenly treat context as a volume issue, believing that feeding a model more documents, wider access, and larger data sets will automatically make it smarter. However, quantity does not equal quality. When an AI receives conflicting definitions, outdated records, or multiple versions of the truth, adding more information only increases ambiguity. In fact, many problems blamed on AI models are actually failures of context. Unlike human employees who use experience to navigate messy internal data, AI systems simply absorb these contradictions, leading to unreliable answers. Instead of focusing on how much data a system can access, companies need to prioritize the reliability of that data. A single, clear rule or a trusted source is far more valuable than thousands of pages of unverified information. Therefore, managing context is an operational challenge rather than a purely technical one. Organizations must carefully measure, monitor, and improve the information they feed their models over time. Ultimately, the next phase of enterprise AI will be defined not by how much data a system can access, but by whether users can trust the answers it produces to make important decisions.


NED Accountability: A Guide for Effective Governance

The fundamental premise of Non-Executive Director (NED) accountability is that mere presence on a board does not equate to effective protection. True accountability is an active, continuous, and evidenced process aligned with a specific mandate, rather than a static legal role. Non-executive directors face the challenge of balancing constructive scrutiny with avoiding operational interference, while navigating increasing personal liability and information asymmetry. Accountability requires an active architecture where board actions are measured against their delegated authority, avoiding the pitfalls of treating governance as an abstract concept. Crucial to this process is institutional fidelity, which ensures decisions align with the long-term purpose of the organization and acts as a safeguard against ethical drift. The board must foster a culture of veracity, enabling open challenges to verify management's actions. Scrutiny itself must be an active intellectual force, demanding "Hemingway clarity" to cut through management jargon and uncover the truth. Independence of judgment requires intellectual force and precision to challenge dominant executive narratives. Finally, assurance is built on evidenced progress, not just management's optimistic projections, moving the board from a passive observer to an active architect of institutional excellence.