Showing posts with label CxO. Show all posts

Daily Tech Digest - October 10, 2026


Quote for the day:

“Most new jobs won’t come from our biggest employers. They will come from our smallest. We’ve got to do everything we can to make entrepreneurial dreams a reality.” -- Ross Perot

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Security Awareness Training Isn’t Dead, but It Needs a Rethink
While enterprise security awareness training remains a standard practice, its effectiveness in preventing modern cyberattacks is increasingly debated. Many experts note that traditional training programs fall short because they prioritize compliance over genuine behavior change, often forcing employees to complete generic, repetitive courses just to check a legal or insurance box. This approach leaves workers poorly equipped to handle today’s highly sophisticated, AI-driven threats, such as flawless deepfakes and hyper-personalized phishing messages that arrive at machine speed. Attackers hold a distinct advantage through asymmetry—they only need a single distracted employee to succeed, whereas defenders must be perfect every time. To remain relevant, security training needs a fundamental rethink. Experts argue that awareness should not be the sole line of defense; it must complement robust security architecture, engineering controls, and reliable verification processes. Furthermore, training programs should evolve from annual lectures into continuous, behavior-based learning that offers context-specific guidance at the exact moment a user makes a decision. By incorporating behavioral nudges and treating employees as an intelligent, active sensor network rather than the weakest link, organizations can build a cultural bedrock of secure habits that catch the threats technology inevitably misses.


The Unknown Present: The Governance Problem Nobody Owns

Traditional governance systems usually ask one basic question: was a system approved? For decades, audits, certifications, and compliance checks have been used to prove that a product or process met specific requirements at a single point in time. However, as organizations rely more on highly connected technologies, artificial intelligence, and constantly updating software, this historical approach is no longer enough. The article introduces a concept called the "Unknown Present," which describes the gap between a past approval and the current reality of a system. Just because a system was safe and compliant yesterday does not automatically mean the same conditions exist today when an important decision is actually made. Modern systems change too fast for old assumptions to hold up. Consequently, the real challenge for leaders and regulators is moving from simple compliance to proving continuous trustworthiness. Organizations must gather reliable evidence showing that a system remains safe at the exact moment it is being used, rather than just relying on an outdated certificate. Ultimately, the future of governance will depend not just on proving that requirements were met in the past, but on proving that the foundation of trust remains completely solid throughout the entire period of use.


‘It’s A Trap!’ How IT Pros Can Avoid the Hidden Pitfalls of AI

While many enterprises adopt artificial intelligence expecting greater efficiency and simpler workflows, a significant majority of IT professionals find that the technology is actually making their jobs more demanding. The core issue is the "reviewer trap," which occurs when organizations attach AI to outdated legacy processes or feed it unclean data. As a result, IT staff must spend excessive time reviewing the outputs to correct errors and hallucinations, creating a heavy cognitive load that often leads to burnout and a sense of growing digital debt. Fragmented implementations across different departments only worsen the situation, as context-switching drains mental energy and reduces decision-making capabilities. This phenomenon, known as AI brain-fry, ultimately causes workers to miss critical errors or lose their own skills by relying too heavily on automated tools. To avoid these hidden pitfalls, IT teams must rethink their foundational data governance rather than simply applying AI to old processes. Success requires building structural guardrails directly into workflows, treating the technology like a smart intern that needs strategic oversight rather than constant micromanagement. By starting small with low-stakes tasks and gradually improving context frameworks, organizations can harness AI's true value without overwhelming their staff.


What continuous offensive security testing is and how to implement it
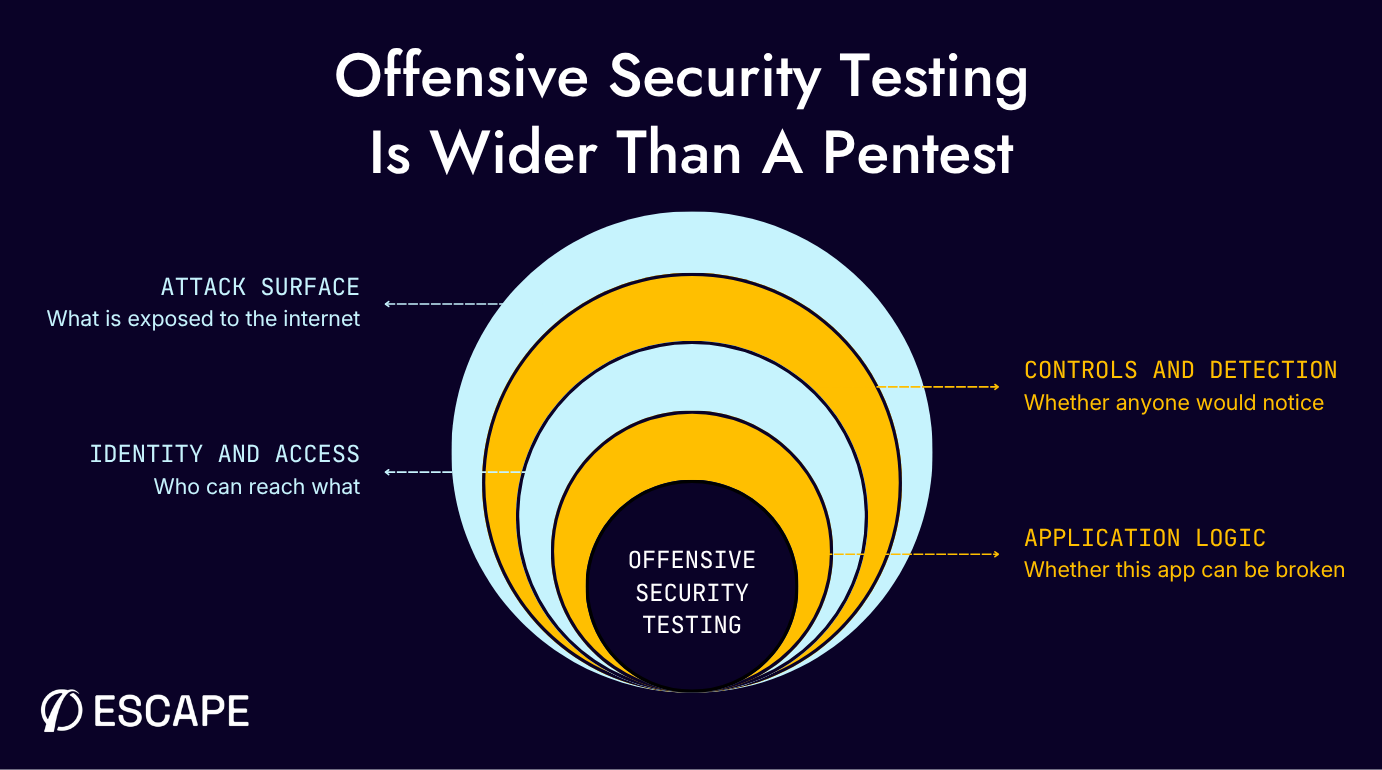
Continuous offensive security testing (COST), as defined by Gartner, is a proactive approach to cybersecurity that goes beyond annual penetration testing. Rather than relying on a fixed schedule, COST is triggered by meaningful changes in an environment—such as new internet-facing assets, production releases, relevant threat intelligence, or updates to security controls. It encompasses vulnerability assessment, penetration testing, and red teaming to evaluate a system precisely as an adversary would. A core principle of this model is strict validation; a finding is only considered valid once it has been successfully reproduced within the organization's own environment, ensuring the vulnerability is genuinely reachable and not just a theoretical risk flagged by a scanner. This emphasis on proof prevents security and engineering teams from being overwhelmed by noisy, unverified alerts. Prioritization tools like EPSS or CISA's KEV catalog provide useful context, but they do not replace the need for local validation. To implement COST effectively, organizations should establish clear triggers, define a shared standard of evidence, tier responses based on business impact, and route validated, actionable proof directly to the teams responsible for the fix, ultimately turning these findings into automated regression tests for future builds.


When building an AI-native security program, start with outcomes

The article by Israel Barak advises resource-constrained security teams to adopt artificial intelligence by focusing on specific business outcomes rather than generic technology roadmaps. Often, small security teams struggle to balance quality, consistency, and cost, which ultimately leads to noticeable gaps in necessary daily tasks. To begin, teams should identify the critical systems, data, and processes the business absolutely needs to operate, establishing a clear boundary for protection. Next, they must pinpoint tasks that should happen continuously but are currently falling behind due to limited time, skills, or budget. Practical examples include managing security posture, updating detection rules, interpreting fresh threat intelligence, or investigating routine alerts. Instead of attempting a massive system overhaul, leaders should choose one specific operational task where the team struggles to keep pace, apply artificial intelligence to that single constraint, and set clear rules and expectations. Success should not be measured by simply counting the number of queries or alerts processed, but rather by evaluating if the tool actually improved the quality, speed, and efficiency of the final outcome. By tying these tools to practical, everyday problems, security teams can effectively reduce manual workload, handle potential threats more consistently, and thoroughly protect the business without needing a massive increase in staff.


Business Intelligence Observability: The Missing Layer of Modern Analytics
While organizations heavily monitor their data infrastructure and pipelines, the business intelligence (BI) layer itself often lacks proper oversight. Traditional monitoring confirms that systems are running and data is delivered, but it fails to answer whether the analytical platform reliably supports sound business decisions. A dashboard might load successfully but perform slower over time, or a report might consume extensive computing power without clear ownership or actual usage. This gap highlights the need for BI observability, a broader operational discipline that continuously measures the health of analytical assets beyond basic technical status. BI observability evaluates five key dimensions: reliability, performance, capacity, adoption, and governance. By shifting the focus from mere technical uptime to actual business impact, data teams can proactively identify deteriorating performance, inefficient resource use, and abandoned reports before users report an issue. This level of transparency is especially critical as organizations adopt enterprise AI, which relies on the exact same governed datasets and semantic models as human decision-makers. Treating business intelligence as a fully observable operational system ensures that both human teams and AI assistants have a trusted, efficient foundation for making timely decisions.


India to release AI regulation consultation paper in 30 days: Vaishnaw

The Indian government plans to release a consultation paper on artificial intelligence regulation within thirty days, focusing on a techno-legal framework rather than relying solely on traditional legislation. Union Minister Ashwini Vaishnaw shared this timeline, highlighting the need to manage AI risks such as deepfakes, financial fraud, and accountability without stifling innovation. This approach combines clear rules with technical safeguards to help organizations monitor AI behavior, restrict unauthorized access, and handle harmful outputs responsibly. A major focus of the upcoming framework is determining accountability when advanced or autonomous AI systems make errors, especially since these systems often rely on multiple technology providers. The government is also looking to streamline how it procures AI services, considering a structured empanelment process for startups and tech companies looking to work on public-sector projects. Alongside these regulatory efforts, India is expanding its domestic AI infrastructure through the IndiaAI Mission, which includes adding thousands of graphics processing units to support computing and inference capabilities. For enterprise technology leaders, this forthcoming regulatory clarity should help establish consistent standards for evaluating AI tools, managing risks, and ensuring proper human oversight as AI adoption expands across public services and business operations.


Why the Chief Data and AI Officer Role Keeps Struggling: Rethinking Executive Leadership for the AI Era

The Chief Data and AI Officer (CDAIO) role frequently struggles because organizations incorrectly treat it as a traditional functional leadership position. Functional executives, like a CFO or COO, are directly accountable for specific departmental operations and outcomes. When the CDAIO is framed this way, their work often devolves into running a technical services department that merely fulfills project requests, delivering disconnected AI models and dashboards rather than driving genuine, widespread business integration. This creates a structural divide between business and technology, making sustainable AI adoption nearly impossible. Instead, the CDAIO should be recognized as a capability leader. Rather than owning a specific business function, their true mission is to build an enterprise-wide capability system—encompassing governance, data literacy, stewardship, and cross-functional coordination. Their goal is to empower every department to effectively leverage data and AI in their daily operations. Success in this role should not be measured by the raw output of AI models or dashboards produced, but by metrics that reflect organizational maturity, such as the number of embedded data experts, active stewards, and the actual utilization rates of AI tools. By shifting from functional ownership to capability building, the CDAIO can truly help the entire enterprise succeed.

Why Tabletop Exercises Expose More Than Technical Weaknesses

While vulnerability scans and penetration tests are excellent at identifying specific security flaws, organizations must conduct tabletop exercises to truly understand how they will respond during an actual cyberattack. These simulated events deliberately expose the nontechnical weaknesses that often go unnoticed on paper, particularly critical gaps in communication, process, and coordination. By throwing untested, unannounced scenarios at decision-makers, organizations can evaluate whether teams agree on incident severity, who actually has the clear authority to shut down systems, and when to involve the board or insurance representatives. A successful exercise is not meant to be flawless; rather, it is designed to create realistic pressure that tests muscle memory and reveals conflicting assumptions across different departments. Executives learn to trust their security teams instead of micromanaging the incident response. To be fully prepared, businesses should run these drills at least annually and conclude each session with a strict action plan that assigns specific owners and concrete deadlines to every identified gap. As threats become more complex due to artificial intelligence, these exercises will also need to adapt dynamically. Ultimately, resolving the deeper governance issues requires ongoing cross-departmental agreement, ensuring the entire organization is genuinely prepared to act quickly and securely.


When AI Meets Quantum: The Next Great Leap in Computing

The article examines three very different ways AI and quantum computing intersect, separating hype from what is actually happening. It first tackles the popular claim that quantum computers will dramatically accelerate AI. The author explains why this is unlikely in the near term: loading real‑world data into quantum states is so costly that it often cancels out any theoretical speedup. While some niche cases in chemistry and materials science show promise, the broader “quantum‑boosted AI” narrative remains mostly aspirational. The second, more grounded convergence runs in the opposite direction—AI is helping quantum hardware mature. Because quantum processors drift, generate noise, and require constant calibration, machine‑learning models are already tuning control pulses, decoding error‑correction signals, and stabilizing qubits more effectively than traditional methods. The third intersection is the most urgent: the cryptographic risk posed by future fault‑tolerant quantum machines. Even though such machines do not exist yet, attackers can harvest encrypted data today and decrypt it later. This threatens AI systems that rely on signatures, secure channels, and provenance trails. The article stresses the need for crypto‑agility, hybrid key exchange, and honest inventories of where cryptography is embedded. It closes with a steady reminder that the real “AI‑quantum leap” is not flashy acceleration but ensuring AI systems remain trustworthy when quantum computers finally arrive.

Daily Tech Digest - August 10, 2026


Quote for the day:

“Change is the end result of all true learning.” -- Leo Buscaglia

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


7 key trends defining the cybersecurity market today

The cybersecurity market is currently shaped by seven major trends that highlight a clear shift toward integration and advanced technologies. First, venture capital investment has reached record highs, heavily favoring startups that focus on artificial intelligence. As a direct result, entirely new product categories are rapidly emerging to address distinct vulnerabilities, such as securing large language models and governing artificial intelligence systems. Meanwhile, traditional market leaders are actively acquiring these specialized startups to fill gaps in their portfolios, leading to a significant surge in mergers and acquisitions. Rather than relying on scattered, standalone tools, organizations now strongly prefer integrated security platforms that consolidate functions and improve overall visibility. Additionally, the threat of quantum computing has moved from theory to reality. In response to "harvest now, decrypt later" strategies, both vendors and governments are pushing for immediate transitions to quantum-safe environments. There is also a growing reliance on outsourced managed security services, as companies seek external expertise for continuous monitoring and threat response. Finally, the need to protect sensitive information across complex, multi-cloud setups has driven the rapid rise of data security posture management tools. Together, these developments indicate a market focused on practical consolidation and preparation for complex future threats.


Secure SDLC principles explained for SaaS founders

A secure Software Development Lifecycle (SDLC) integrates security into every phase of building software, from early planning and design through to testing, release, and ongoing maintenance. For SaaS founders, the primary goal is to protect customer trust and avoid costly post-launch fixes without slowing down product delivery unnecessarily. The core principle is to build security in early rather than treating it as a bolted-on afterthought. Fixing structural flaws during the initial design phase is cheaper than addressing a data breach or emergency patch later. To make this operational, security practices must become repeatable habits, rather than relying on a single knowledgeable individual. Even small SaaS teams can establish a solid protective baseline by assigning clear ownership, requiring peer code reviews, automating basic vulnerability scans, and implementing a simple release checklist. This structured approach directly prevents common application risks such as injection flaws, broken access controls, exposed secrets, and issues hidden within third-party dependencies. By adopting DevSecOps practices, teams can easily automate routine security checks within the standard delivery pipeline. Ultimately, founders can measure their success by tracking how many high-risk issues are caught before release and how quickly problems are resolved, balancing product safety with ongoing business momentum.


Red Hat tames the open-source AI chaos.

Red Hat is actively working to bring order to the fast-moving and often chaotic open-source AI landscape. They focus on taking experimental AI projects and refining them into stable, secure tools suitable for business use. For instance, when a highly capable but risky open-source AI project called OpenClaw was released, it gave AI models the ability to act independently. Recognizing the security risks, Red Hat quickly introduced a method for companies to bring their own agents into their established IT systems. This approach ensures that AI tools operate with the necessary safety measures, such as proper isolation and clear rules for access. Drawing on years of experience in securing operating systems and building reliable platforms, Red Hat provides the structure needed to keep AI experiments safe. They restrict network access and place AI tools in contained environments to limit any potential damage from unexpected security breaches. Additionally, they help companies manage computing costs by automatically directing simple tasks to smaller, more affordable models. Red Hat views this secure management framework as a foundational operating system for AI. By prioritizing open standards and practical architecture, they offer a steady and reliable path for companies looking to adopt AI technologies without getting caught up in the surrounding industry hype.


Ask a Data Ethicist: What Use of AI Do We Need to Disclose?

In her article for Dataversity, data ethicist Katrina Ingram explores the ongoing debate around exactly how much we need to disclose when using artificial intelligence tools at work. Reflecting on early corporate policies from 2023 that demanded total transparency, she argues that a blanket requirement to always disclose everything lacks practical nuance. Ingram breaks down two opposing perspectives. The first is the strict approach, often seen in academia, which requires individuals to document every single instance of AI assistance, from basic brainstorming to editing sentences. While this level of detail supports academic integrity, Ingram points out that it is likely overkill for the corporate world. Tracking minor uses of AI for routine tasks provides little real value and risks turning harmless employee behavior into frustrating policy violations. On the other end of the spectrum is the "disclose nothing" argument, which treats AI as just another standard work tool like a word processor or a pen. However, she notes that this extreme is also problematic because AI actively generates content rather than just formatting it. Ultimately, Ingram suggests that organizations need sensible, balanced disclosure policies that distinguish between generating final public content and simply using AI to support everyday tasks.


The interconnect crisis: Why enterprise AI scaling is about to hit a wall

Enterprise AI needs differ sharply from consumer tools, prioritizing long-term reliability, data privacy, and secure on-premise infrastructure. As organizations build internal platforms and manage vast volumes of sensitive data, the cost benefits of owning hardware rather than renting cloud space are becoming clearer. While processing power is becoming cheaper and more accessible, a hidden problem threatens to slow down progress: moving data. As databases grow heavier over time, the real challenge is no longer raw processing power, but rather the speed at which data travels between storage, memory, and processors. This is the interconnect crisis. Traditional copper cables simply cannot handle the sheer volume and speed required to move information between components without severe delays. To solve this, the industry must move beyond older standards and adopt faster data transfer methods. Upgrades like advanced memory links and high-speed network protocols provide some initial relief, but the true long-term answer lies in light-based technology. Replacing standard electrical connections with photonics will allow systems to share information seamlessly. While this transition requires significant changes to hardware design, these optical solutions offer a clear path forward, ensuring that tomorrow’s computer architectures can smoothly support the increasing demands of complex software and massive data workloads.


The Corporate Network Is Fading - Here's What Replaces It

For decades, traditional enterprise networks relied on a straightforward premise: work happened exclusively inside an office building. In this older model, applications were stored in centralized, physical data centers. Employees connected through internal infrastructure, and security strategies were built entirely around defending a single, defined perimeter. Essentially, the goal was to build a wall around internal digital assets. However, how organizations operate today looks completely different from that original environment. The legacy corporate network is fading because it no longer aligns with modern reality. Today, critical applications have moved to cloud platforms rather than sitting in a basement server room. Employees are highly distributed, connecting to work from their homes, coffee shops, and airports just as often as they do from traditional desks. Additionally, businesses now collaborate heavily with external partners through shared digital systems that extend far beyond internal walls. Because work is no longer confined to a single location, the old security model simply cannot protect the modern workforce. Instead of relying on a physical network boundary, companies are replacing the traditional corporate network with flexible, decentralized approaches. Modern connectivity focuses on securing individual user identities and specific cloud applications, ensuring safe access regardless of where an employee happens to be working today.


The Decade Bet: What CIOs Are Really Locking In

The article discusses the strategic decisions technology leaders are making for the next ten years, focusing on a deliberate shift from rigid systems to adaptable foundations. Rather than tying their organizations to specific software vendors or hardware providers, Chief Information Officers are now committing to flexibility, data ownership, and secure baseline architecture. They recognize that the tools they use today will likely change, so they are investing in underlying structures that allow for easy transitions and integration of new capabilities. A major priority is ensuring information remains portable and easily accessible across different platforms, strictly protecting the company from being trapped by any single service provider. Additionally, these leaders are prioritizing fundamental security practices that will remain highly relevant regardless of future external threats. By establishing these strong, adaptable frameworks, they build environments that can calmly handle unexpected shifts in the broader market or sudden technological advancements without requiring a system overhaul. Ultimately, the true long term commitment is not to a particular application or service, but to a resilient operational model that supports steady growth and rapid adaptation. This approach safely reduces long term risks while preserving the absolute freedom to choose the best available tools as specific business needs evolve over the coming decade.


What Is the Difference Between a CDO and CIO? A View From Both Sides

The roles of Chief Data Officer (CDO) and Chief Information Officer (CIO) represent distinct but complementary areas of executive leadership. The CDO is primarily responsible for turning data into tangible business value through better decision-making, while the CIO manages the broader technology ecosystem, ensuring the reliability, security, and scale of systems that keep the business running. While a CDO focuses on driving innovation and competitive advantage, a CIO handles operational accountability, dealing with uptime, infrastructure dependencies, and risk management. Despite these practical differences, the rapid rise of artificial intelligence requires the two leaders to work together closer than ever before. Artificial intelligence initiatives need secure platforms and governance, owned by the CIO, alongside trusted data and clear business objectives, driven by the CDO. Although more CDOs are gradually transitioning into CIO roles as their exposure to engineering and platforms grows, the positions will likely remain separate in large organizations. Success ultimately depends on a shared partnership where both executives prioritize common outcomes rather than protecting their domains. Together, they balance the need for strategy and innovation with the strict discipline of operational excellence, proving that all modern organizations need both reliable technical foundations and smart data to truly thrive today.


7 Key Components for Event Cloud Threat Detection and Response Solution

As business operations increasingly span across multiple clouds, applications, and devices, securing these distributed networks has become a significant challenge. Traditional security tools designed for distinct borders often fail in these environments, leaving blind spots and causing delays in identifying risks. To effectively protect modern infrastructure, organizations need a comprehensive cloud threat detection and response solution built on seven essential components. First, teams must have clear, unified visibility across all systems, applications, and user activities. Second, this broad visibility must be paired with intelligent analytics to accurately distinguish genuine threats from routine daily activities. Third, the system needs real-time detection that connects signals across different areas to reveal actual attack paths. Fourth, security controls should focus on prevention, stopping harmful actions before they cause serious damage. Fifth, automated responses are crucial for quickly containing issues without waiting for manual approval. Sixth, a centralized control system ensures that security rules are applied consistently everywhere, reducing the chance of harmful errors. Finally, the underlying architecture must be flexible and scalable to support future growth and infrastructure changes. Together, these seven elements create a continuous loop where visibility informs intelligence, intelligence sharpens detection, and detection drives immediate, protective action across the entire organization.


Enterprise Data Warehouse Architecture Explained Simply

An enterprise data warehouse architecture provides a structured framework for businesses to collect, organize, and analyze data scattered across multiple systems. By consolidating information into a single environment, it helps organizations maintain consistent and reliable data, which improves reporting accuracy and supports better decision making across departments. A sound architecture relies on several core components working effectively together. It begins with a data source layer that pulls information from various applications, followed by an integration layer that organizes and loads the data. The information is then housed in a scalable storage layer, often using cloud platforms. Additional layers handle data processing, translate technical structures into practical business terms, and enforce strict security and governance policies. When building a data warehouse, organizations can choose from different structural patterns, such as a central hub and spoke model or a hybrid lakehouse approach, depending on their specific operational needs. Designing an effective system requires a clear understanding of practical business goals, a focus on long term scalability, and careful data modeling. Prioritizing high data quality and strong security practices ensures the system remains a trustworthy foundation. Ultimately, a properly planned data warehouse architecture allows a business to manage growing data volumes safely and efficiently while keeping internal teams aligned.

Daily Tech Digest - July 08, 2026


Quote for the day:

“Companies spend millions on firewalls and encryption, but the weakest link is always the human.” -- Kevin Mitnick

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


AI Sovereignty Is a New Test for Enterprises

As artificial intelligence transitions from a technological experiment into a primary driver of business value, organizations are facing a critical new challenge: AI sovereignty. While traditional digital sovereignty focused merely on where information was physically stored, AI sovereignty demands complete control over the entire system lifecycle. This includes actively managing data lineage, model training frameworks, inference processes, and the underlying computing infrastructure. For modern enterprises, this shift is no longer just about meeting local compliance requirements or data privacy regulations; it is a fundamental test of operational resilience and strategic independence. When companies rely too heavily on third-party global providers without establishing a sovereign framework, they risk severe vendor lock-in, operational fragility, and an inability to adapt to rapidly changing geopolitical rules. Consequently, chief information officers and business leaders must proactively embed sovereignty into their architectural designs from the start rather than treating it as an expensive afterthought. By adopting hybrid operational models that carefully balance scalable global infrastructure with strictly governed local environments, enterprises can protect sensitive data, maintain consumer trust, and confidently accelerate innovation, ultimately turning regulatory constraints into a distinct competitive advantage in a complex global market.


Why IT Keeps Getting Handed an AI Training Problem It Can't Solve Alone

When companies decide they need to train their employees on new artificial intelligence tools, they often make a classic mistake: they hand the responsibility entirely to the IT department. While IT teams know how these systems operate, knowing how to build software is entirely different from knowing how to teach adults new ways of working. This mismatch often results in generic webinars or outdated documentation, particularly because artificial intelligence changes so quickly that formal manuals become obsolete within weeks. Instead of forcing rigid courses, the most successful companies weave learning directly into everyday tasks. They stop focusing on what a tool can theoretically do and instead ask where work currently feels slow or repetitive. By introducing these tools as immediate relief for daily frustrations—and sharing practical examples in regular team meetings or chat channels—employees adopt them naturally. To make this work sustainably, IT teams should not carry the burden alone. The most effective approach requires a partnership: IT provides the technical foundation, human resources or learning professionals handle the teaching strategy, and everyday employees identify the real problems that need solving. When these groups collaborate, they build practical habits instead of forgotten training programs.


Five tips for developing data products

Creating data products is a practical strategy for organizations looking to streamline analytics and artificial intelligence projects. Just as buying pre-packaged ingredients speeds up cooking a meal, data products standardize raw information into consistent, reusable assets that save time and reduce errors. However, building these products requires careful planning. First, teams must determine when a data product is necessary, which usually happens when multiple departments rely on the same information or when ungoverned data poses security risks. Second, organizations must define strict standards for these products, tracking data lineage so users understand where the information originated and how it was modified. Third, data products need rigorous life-cycle management, requiring the same versioning, testing, and quality checks as traditional software to maintain trust. Fourth, because simply building a tool does not guarantee people will use it, product managers must actively drive adoption through dedicated change management and clear communication about business benefits. Finally, companies should measure a data product’s value not just as a technical output, but by tracking its impact on workflow efficiency, faster decision-making, and overall time-to-value. By following these steps, businesses can safely accelerate their technology initiatives.


The Data Quality Crisis Undermining Enterprise Analytics

The piece describes a familiar pattern: companies invest heavily in modern data stacks and cloud infrastructure, yet still end up with reports that people don’t trust. The core problem is messy data moving through otherwise capable systems—things like different teams using different definitions for the same metric, fields that are formatted inconsistently, and pipelines that deliver stale or partial updates. These small, everyday issues compound over time, breaking joins, skewing aggregations, and creating discrepancies that prompt users to double‑check or ignore analytics altogether. The author emphasizes that this is rarely a purely technical failure; it’s often a mix of unclear metric definitions, inconsistent transformations, and a lack of shared ownership across teams. When trust in numbers disappears, the practical value of analytics collapses, because leaders stop relying on dashboards for important decisions. The article cites industry research showing that poor data quality costs organizations millions annually and highlights real‑world examples from large enterprises where data from multiple operational systems created persistent inconsistencies. It also warns that moving to faster, more scalable platforms can simply accelerate the processing of bad data unless governance and quality controls are put in place. Finally, the author calls for pragmatic fixes: clearer definitions, stronger ownership, routine checks for freshness and consistency, and investment in processes that prevent small errors from becoming systemic.


6 ways to make AI accountability stick

As artificial intelligence systems shift from simply offering advice to independently completing tasks in production environments, traditional software governance is no longer sufficient. Organizations are finding that when an AI system makes an error, the lack of clear responsibility often leads to confusion. To prevent this, IT leaders must make accountability an enforceable part of daily operations. First, companies should assign direct ownership to individuals at the very beginning of a project, rather than relying on vague shared responsibility. Second, foundational governance rules must be integrated into normal workflows before scaling up AI deployments. Third, strong data governance is essential; knowing exactly where data comes from allows teams to trace the root cause of any mistakes. Fourth, companies need broad monitoring that tracks not just the AI model itself, but how it interacts with other internal systems and workflows. Fifth, organizations must build clear stopping points where the system pauses and asks a human for permission or guidance. Finally, leaders should manage AI systems more like human employees than traditional software, providing ongoing oversight and regular performance reviews to ensure they continue operating safely and accurately over time.


CDO to CEO Progression: Skills, Mindsets, and Lessons for the Journey

Transitioning from a chief data officer to a chief executive officer is rarely about acquiring new technical abilities. Instead, it requires a fundamental shift in how you view leadership, business strategy, and your role within an organization. Because data officers naturally work across various departments, they already develop essential executive skills, such as aligning diverse teams and balancing competing priorities. However, to be considered for the top role, data professionals must change how they communicate their value. Rather than highlighting technical achievements, they should focus entirely on business impact and outcomes. A strong foundation in business operations allows leaders to shape critical decisions rather than just report on them. Moving into the executive seat also means taking responsibility for profit and loss, where evaluating broad trade-offs becomes necessary. You move from asking if a project is possible to deciding if it is the right move for the company right now. Finally, while numbers are important, relying solely on reports is a mistake. Direct conversations with employees and customers provide the necessary context that dashboards often miss. Ultimately, this leap becomes a natural progression when leaders broaden their focus from data systems to enterprise-wide strategy.


Agents are now users, but is your architecture ready?

As AI agents increasingly act on behalf of humans to manage workflows, they are fundamentally changing who or what uses software. Instead of clicking through visual dashboards, these agents interact directly with APIs. Because of this, software architecture must adapt. Organizations now need a surface visible to agents, which means creating clear, machine readable capabilities rather than just polishing user interfaces. This transition challenges traditional software development because AI models do not behave predictably. While traditional software always gives the same output for a specific input, AI outputs vary. Consequently, development practices must evolve in three main areas. First, testing must shift from static unit tests to continuous evaluations that measure behavior over time. Second, observability needs to track agent actions, such as recognizing when an agent is stuck in an infinite loop, rather than just monitoring basic system health. Finally, safety guardrails must move from the interface level down to centralized control planes that manage access and identity. To prepare for this change, engineering teams should evaluate their current API capabilities. By focusing on a small set of securely managed tools, organizations can lay a solid foundation for safely integrating AI agents into their daily operations.


Why clarity is the missing link in AI adoption

Organizations often treat artificial intelligence adoption as a simple productivity upgrade, pushing new tools onto teams that are already overworked and stressed by constant change. While employees may see the potential benefits, they frequently experience what researchers call "FOBO"—feeling optimistic but overwhelmed. Without clear guidance, this rapid technological shift leads to uneven adoption, hidden workplace experiments, and widespread hesitation because people fear making mistakes or losing their jobs. To fix this, leaders must move beyond vague announcements and provide genuine clarity by focusing on three essential elements. First, they need to set a clear direction by naming the specific business problem the technology is meant to solve, such as reducing administrative tasks or speeding up response times. Second, leaders must establish clear priorities by highlighting two or three main use cases, which protects teams from scattered, performative adoption. Finally, companies need practical guardrails—simple, easily understood boundaries that allow employees to experiment safely without navigating dense, legalistic policies. Ultimately, treating clarity as a daily leadership discipline reduces unnecessary confusion and fear. It transforms a noisy mandate into a focused, human-centered process that empowers people to work with calm confidence.


The hidden risk in global infrastructure deployment

For data center operators expanding internationally, hardware regulatory compliance is no longer a final administrative step; it is a critical operational risk that must be addressed at the earliest stages of design and procurement. As global standards for electrical safety, electromagnetic compatibility, and energy efficiency become increasingly strict, infrastructure that fails to meet these requirements can lead to delayed deployments, costly redesigns, and diminished trust among partners. To avoid these issues, compliance must be engineered into servers and network appliances from the start. This requires careful attention to component selection, power distribution, thermal management, and circuit shielding during the hardware development process. Rather than viewing regional regulations as an obstacle, organizations should treat them as a foundation for reliable expansion. By embedding compliance directly into the supply chain and collaborating closely with testing laboratories, operators can ensure their systems are legally and safely deployable across different jurisdictions. Hardware that inherently meets international standards simplifies procurement and reduces friction in complex projects. Developing deep regulatory expertise helps data center providers mitigate operational risks, protect capital investments, and confidently scale their physical infrastructure across borders without encountering unexpected regulatory roadblocks.


When the sensor starts thinking: SnortML, agentic AI, and the evolving architecture of intrusion detection

The evolution of intrusion detection is shifting from purely signature based models to systems that analyze context using SnortML and agentic AI. SnortML introduces native machine learning to Snort 3, running in parallel with classical signature matching. Rather than relying solely on predefined rules, it evaluates network traffic, primarily HTTP requests, to determine if structural byte patterns resemble exploits like SQL injection. This allows the system to catch unseen variants that bypass traditional signatures. However, because SnortML evaluates individual packets, it remains blind to multistep attacks and broader temporal context. This limitation necessitates the integration of agentic AI. Unlike conventional automation or playbooks, agentic AI maintains state across complex investigations. It autonomously queries external systems, correlates signals across multiple data sources, and builds comprehensive context before recommending a response. In this modern architecture, SnortML acts as the highly precise wire level sensor, while agentic AI serves as the orchestration layer that synthesizes isolated events into a coherent threat narrative. Together, they create a robust defense mechanism. While challenges remain in model explainability and standardized coordination, this combination effectively addresses the growing need for scalable security operations in network defense architectures.

Daily Tech Digest - May 30, 2026


Quote for the day:

“Any fool can write code that a computer can understand. Good programmers write code that humans can understand.” -- Martin Fowler

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


AI-Driven Bug Tsunami Prompts Exploitability Questions

The article outlines how artificial intelligence has driven a massive increase in software bug reports, pushing the Common Vulnerabilities and Exposures system toward another record year. While major platforms like Chrome and GitHub have seen a large number of reported flaws, security researchers emphasize that most of these automated findings present very little real threat. Historically, fewer than two percent of all reported vulnerabilities are actually exploitable, and current telemetry indicates that only a tiny fraction are ever widely used by attackers. A primary issue is that automated tools often generate reports that lack necessary context regarding severity, practical reachability, and real world impact, creating an unnecessary administrative burden for software maintainers who must sort through low quality duplicates. In response, open source projects like the Linux kernel and platforms like GitHub have tightened their guidelines, now requiring functional proof of concept demonstrations before prioritizing a bug or issuing rewards. Furthermore, even advanced models like Anthropic’s Mythos, despite their ability to chain minor bugs into serious exploits, have not altered underlying risks significantly. Traditional security measures and defense in depth principles remain effective. By ensuring systems are built with multiple layers of security, organizations can ensure a single software flaw will not compromise an entire product.


AI and connected systems are forcing CIOs and COOs to rethink OT security

Historically, organizations kept operational technology, such as factory equipment and utility infrastructure, isolated from corporate IT networks to maintain security and safety. However, the search for efficiency has pushed companies to introduce connected sensors, cloud data, and artificial intelligence into these industrial spaces. While this change offers clear business advantages, it also creates significant cyber risks. Older operational equipment was never designed for internet connectivity, making standard software updates or sudden network shutdowns highly impractical. Furthermore, the integration of autonomous artificial intelligence systems complicates defense strategies because they constantly exchange data with outside networks while relying on legacy internal frameworks. To address these vulnerabilities, chief information officers and chief operating officers must move away from isolated management practices and embrace shared responsibility. This coordination is essential because typical corporate security tactics, like instantly isolating a compromised system, can disrupt manufacturing schedules or cause physical damage on the factory floor. Instead of trying to replace decades of old equipment immediately, leadership teams should focus on improving basic operational visibility, monitoring the network access of outside contractors, and deploying stricter identity verification checks. Taking a deliberate, phased approach to securing these blended environments allows companies to manage hidden threats much more effectively while keeping critical machinery running safely.


Accelerating Data Strategy and Governance with AI

According to a Dataversity article featuring insights from Peter Aiken, many organizations fail with their data strategies because they treat them as static documents to be completed and shelved rather than ongoing processes. Consequently, a vast amount of corporate data often remains redundant or obsolete. To fix this, an effective data strategy should serve as a continuous pattern of choices that aligns information assets directly with broader business goals. Aiken suggests utilizing a cyclical method focused on addressing constraints, where teams repeatedly isolate and resolve single bottlenecks to build small, incremental advantages. Data governance teams provide the necessary routine execution, though they frequently face common hurdles like cultural resistance, confusion, or competing technology priorities. Artificial intelligence serves as a practical tool to ease these operational burdens and expand human worker capabilities. Rather than replacing professionals, AI automates tedious administrative chores such as labeling data, mapping information lineage, checking security risks, and updating quality rules. This shift reduces internal friction and allows data stewards to spend their time on important strategic planning. Ultimately, combining cyclical improvements with automated support helps companies steadily improve their data quality, mitigate security risks proactively, and turn abstract strategy documents into practical business actions.


India has already witnessed increasing cyber targeting of critical infrastructure sectors

In this interview, Vaibhav Dutta of Tata Communications discusses the growing cybersecurity risks facing India’s critical infrastructure as industries embrace digital modernization. As sectors like energy, utilities, and manufacturing integrate isolated operational technology with enterprise IT, cloud networks, and automated systems, they inadvertently widen their exposure to external threats. This shift changes the nature of these threats from basic data breaches to complex physical disruptions capable of destabilizing essential public services. India has already seen an uptick in malware and remote access exploitation targeting its power grids and manufacturing setups. Dutta points out major vulnerabilities in current industrial upgrades, particularly a severe lack of visibility over legacy equipment, insecure remote access pathways, and unprotected application programming interfaces. Furthermore, many organizations mistakenly treat security as a compliance box to check rather than a core operational necessity. To mitigate these risks, the text advocates for building safety controls directly into systems during the initial planning stages of any digital expansion. Moving forward, safeguarding these interconnected environments will require a unified approach that blends traditional computer network security with physical operational safety, relying on continuous verification models and intelligent monitoring to detect anomalies and maintain continuity even during an active cyber attack.


The AI inventory is the EU AI Act artefact most teams underestimate

The Information Age article highlights why the AI inventory required by the EU AI Act is a critical component that corporate teams routinely underestimate. Rather than treating it as a superficial list or spreadsheet of active tools, organizations should view the inventory as a map that connects every artificial intelligence application to real business processes. A weak register merely names products like chatbots or analytics software. In contrast, a truly comprehensive inventory details business and technical owners, data inputs, intended outcomes, human review steps, and clear accountability trails. This deep level of clarity helps prevent the common issue of ownerless systems, where unmonitored technology leads to gradual shifts in purpose and completely untracked updates. While creating an inventory does not automatically ensure legal compliance or replace deeper security and privacy reviews, it establishes the necessary shared baseline record that different departments require to work together effectively. Technology executives play a central role here because standard legal or compliance teams rarely notice the automated features quietly embedded inside third-party corporate software platforms. Ultimately, maintaining a clear and current register enables legal, security, and operational units to understand exactly what they own, paving the way for structured risk management as new regulations phase in.


Kindness and Critical Infrastructure: Rethinking OT Security

In episode 52 of the Hack the Planet podcast, titled "Kindness and Critical Infrastructure," host Bryson Bort interviews Andrea Haddad, an infrastructure architect working at a pharmaceutical manufacturing organization. Haddad shares her transition from traditional IT network engineering to the world of operational technology, where safety and production take top priority. She highlights a common tension between maintaining strong security and ensuring daily workplace convenience. For example, forcing factory technicians to manage multiple complex passwords for remote access often leads to frustration and risky habits, like password reuse. Furthermore, external equipment suppliers frequently push back against corporate network rules, sometimes introducing unauthorized remote connections that create visibility blind spots. Haddad notes that while theoretical frameworks like the Purdue model offer helpful blueprints for layering networks and establishing equipment standards, strict solutions cannot be imposed instantly. Instead, she argues that lasting security relies heavily on mutual listening and empathy, choosing kindness over rigid enforcement. Because production downtime causes massive financial losses, security teams must understand the real-world constraints under which plant engineers operate. Ultimately, true system protection comes from a continuous process of learning, open communication, and building a practical middle ground that safeguards equipment without disrupting daily work.


How to Ideate in Design Thinking: What Works, What's Overhyped, and What's Changing

The Eleken article highlights that coming up with fresh product ideas is often misunderstood as a rigid, workshop-heavy process that smaller teams cannot afford. In reality, effective problem-solving is simply about pushing past the first few obvious choices, which are usually the same generic concepts your competitors have already considered. Traditional group brainstorming sessions frequently fall short because the loudest voices dominate the room, participants fear judgment, and early suggestions accidentally restrict everyone’s thinking. To bypass these social limitations, teams can use practical alternatives like the bad idea challenge, which removes performance pressure by asking people to deliberately invent terrible solutions that can later be flipped into useful features. Other effective approaches include studying solutions from completely unrelated industries or using imaginary scenarios to challenge basic assumptions. Furthermore, artificial intelligence is steadily changing how teams work by quickly producing hundreds of starting layouts and options. Instead of replacing human creativity, these software tools handle the heavy lifting of initial volume, allowing designers to dedicate their time to reviewing, editing, and perfecting the best directions. Ultimately, the article suggests treating design thinking as a flexible toolkit rather than a strict textbook rulebook, matching the core principles to actual product timelines and real-world project constraints.


Cloud spend is now a governance issue. Finance and IT need a new model

The article highlights the shifting nature of cloud and AI infrastructure costs, framing them not as a purely technical or financial problem, but as a critical governance challenge. Traditional static budgeting models and retroactive approvals fail to match the reality of modern cloud consumption, where expenses fluctuate dynamically based on daily engineering decisions and varying workload demands. Consequently, companies frequently deal with wasted spending, often due to overprovisioning or unutilized cloud resources. To solve this, finance and technology departments must work together more closely, adopting a shared framework commonly known as FinOps. This collaborative approach distributes financial accountability directly to product and business teams, linking cloud costs directly to performance and measurable business value. By establishing metrics like cost allocation coverage, forecasting accuracy, and unit economics, such as the cost per transaction or model inference, finance leaders gain deeper context into what their spending actually accomplishes. This visibility creates a shared understanding between engineering and corporate finance, helping teams make better everyday design choices. Ultimately, the text argues that companies focusing merely on reducing costs will struggle, whereas organizations that actively manage the business value of their cloud investments can turn structural volatility into a distinct operational advantage.


Stragglers, Not Failures: How Adaptive Hedged Requests Reduce p99 Latency by 74 Percent

This InfoQ article discusses how adaptive hedged requests can effectively manage extreme response delays in distributed computer networks. In large systems, overall performance is often slowed down not by outright errors, but by requests that eventually finish but take far longer than usual due to temporary glitches like background garbage collection or minor network bottlenecks. While software engineering teams often use retries to fix these issues, resending a slow request can accidentally overload an already struggling back-end server. Instead, a hedged request proactively sends a duplicate backup request if the initial attempt takes too long, accepting whichever response returns first and canceling the slower peer. To avoid the pitfalls of static timing limits, which require constant manual adjustments as traffic patterns shift throughout the day, the author introduces an automated system. By using an open-source statistical tracking tool called DDSketch, this setup continuously analyzes real-time response times to establish accurate thresholds naturally. Additionally, a built-in safety mechanism uses a token bucket budget to cap duplicate traffic, ensuring that the system handles problems gracefully rather than multiplying load during genuine outages. Ultimately, this approach works best for repeatable operations that do not change database state across multi-instance environments.


From resilience to survivability: How AI forces a rethink of business continuity

The article by Zeus Kerravala explains how artificial intelligence is changing corporate business continuity, pushing organizations to move past traditional recovery plans toward a model of continuous survivability. Historically, maintaining business operations during an unexpected network outage meant relying on simple secondary backups. However, these systems often share hidden technical dependencies, such as the same cloud providers or identity management tools. Because modern AI workloads are deeply interconnected and control real-time decision-making systems, any downtime creates severe immediate consequences and steep financial losses. To address these vulnerabilities, businesses are adopting architectural independence, which involves running separate, parallel environments with isolated data pathways and distinct operational teams. This approach ensures that a failure in the primary system does not spread to the backup. Furthermore, companies must view AI as both a major security risk and a helpful recovery asset. On one hand, automated models introduce supply chain risks and potential data corruption. On the other hand, they can predict infrastructure failures and trigger self-healing protocols. Ultimately, technology and enterprise leaders are advised to thoroughly map their complex system dependencies, test for total model failures, and transition from reactive troubleshooting to building autonomous safeguards that keep essential operations running smoothly during unexpected disruptions.

Daily Tech Digest - April 17, 2026


Quote for the day:

"We don't grow when things are easy. We grow when we face challenges." -- @PilotSpeaker


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


The agent tier: Rethinking runtime architecture for context-driven enterprise workflows

The article "The Agent Tier: Rethinking Runtime Architecture for Context-Driven Enterprise Workflows" explores the evolution of enterprise software from rigid, deterministic workflows to more flexible, agentic systems. Traditionally, business logic relies on explicit branching and hard-coded rules, which often fail to handle the nuanced, context-dependent variations found in complex processes like customer onboarding or fraud detection. To address this limitation, the author introduces the "Agent Tier"—a distinct architectural layer that separates deterministic execution from contextual reasoning. While the deterministic lane maintains authoritative control over state transitions and regulatory compliance, the Agent Tier interprets diverse signals to recommend the most appropriate next actions. This system utilizes the "Reason and Act" (ReAct) pattern, allowing AI agents to interact with governed enterprise tools within a structured reasoning cycle. By decoupling adaptive reasoning from execution, organizations can manage ambiguity more effectively without sacrificing the reliability, safety, or explainability of their core operations. This two-lane approach enables incremental adoption, allowing enterprises to modernize their workflows by integrating adaptive logic into specific points of uncertainty. Ultimately, the Agent Tier provides a scalable, robust framework for building responsive, intelligent enterprise systems that maintain strict governance while navigating the complexities of modern, context-driven business environments.


Crypto Faces Increased Threat From Quantum Attacks

The article "From RSA to Lattices: The Quantum Safe Crypto Shift" explores the intensifying race to secure digital infrastructure against the looming threat of quantum computing. Central to this discussion is a landmark whitepaper from Google Quantum AI, which reveals that the quantum resources required to break contemporary encryption are approximately twenty times smaller than previously estimated. While current quantum processors possess around 1,000 qubits, the finding that only 500,000 qubits—rather than tens of millions—could compromise RSA and elliptic curve cryptography significantly accelerates the timeline for migration. Expert Chris Peikert highlights that this "lose-lose" situation for classical security stems from compounding advancements in both quantum algorithms and hardware efficiency. The urgency is particularly acute for blockchain and cryptocurrency networks, which face the "harvest now, decrypt later" risk where encrypted data is stolen today to be cracked once capable hardware emerges. Transitioning to lattice-based post-quantum cryptography remains a complex hurdle due to the larger key sizes and signature requirements that stress existing system architectures. Although a successful attack remains unlikely within the next three years, the growing probability over the next decade necessitates immediate industry-wide re-evaluation and the adoption of more resilient, crypto-agile standards to safeguard global data integrity.


The endless CISO reporting line debate — and what it says about cybersecurity leadership

In his article, JC Gaillard explores why the debate over the Chief Information Security Officer (CISO) reporting line persists into 2026, suggesting that the focus on organizational charts masks a deeper struggle with defining the CISO’s actual role. While reporting lines define authority and visibility, Gaillard argues that the core issue is whether a CISO possesses the organizational standing to influence cross-functional silos like legal, HR, and operations. Historically viewed as a technical IT function, cybersecurity has evolved into a strategic business priority, yet governance structures often lag behind. The author asserts there is no universal reporting model; success depends less on whether a CISO reports to the CEO, CIO, or COO, and more on the quality of the relationship and mutual trust with their superior. Furthermore, the supposed conflict between CIOs and CISOs is labeled as an outdated notion, as modern security must be embedded within technology architecture rather than acting as external oversight. Ultimately, the endless debate signals that many organizations still fail to internalize cyber risk as a strategic leadership challenge. Until companies bridge this governance gap by empowering CISOs with genuine influence, structural changes alone will remain insufficient for achieving true digital resilience and organizational alignment.


Building a Leadership Bench Inside IT

Developing a robust leadership bench within Information Technology (IT) departments has become a strategic imperative for modern enterprises facing rapid digital transformation. The article emphasizes that cultivating internal talent is not merely a human resources function but a critical operational necessity to ensure business continuity and organizational agility. Organizations are increasingly moving away from reactive hiring, instead focusing on identifying high-potential employees early in their careers. These individuals are nurtured through deliberate strategies, including formal mentorship programs, cross-functional rotations, and targeted soft-skills training to bridge the gap between technical expertise and executive management. A successful leadership bench allows for seamless succession planning, reducing the risks associated with sudden executive departures and the high costs of external recruitment. Furthermore, the article highlights that fostering a culture of continuous learning and empowerment encourages retention, as employees see clear pathways for advancement. By investing in diverse talent and providing opportunities for real-world decision-making, IT leaders can build a resilient pipeline that aligns technical innovation with broader corporate objectives. This proactive approach ensures that when the time comes for a leadership transition, the organization is already equipped with visionaries who understand both the underlying infrastructure and the strategic vision of the company.


Data Center Protests Are Growing. How Should the Industry Respond?

Community opposition to data center construction has evolved into an organized movement, significantly impacting the industry by halting roughly $18 billion in projects and delaying an additional $46 billion over the last two years. While some resistance is characterized as "not in my backyard" sentiment, many protesters raise legitimate concerns regarding environmental impact, resource depletion, and public health. Specifically, residents worry about overstressed power grids, excessive water consumption in drought-prone areas, and noise or air pollution from backup generators. Furthermore, the limited number of permanent operational roles compared to the massive initial construction workforce often leaves locals feeling that the economic benefits are fleeting. To navigate this increasingly hostile landscape, industry leaders emphasize that developers must move beyond mere compliance and focus on genuine community partnership. Recommended strategies include engaging with residents early in the planning process, providing transparent data on resource usage, and adopting sustainable technologies like closed-loop cooling systems or waste heat recycling. By investing in local infrastructure and creating stable career pipelines, developers can transform from perceived "takers" of energy into valued community assets. Addressing these social and environmental anxieties is now essential for securing the future of large-scale infrastructure projects in an era of rapid AI expansion.


Empower Your Developers: How Open Source Dependencies Risk Management Can Unlock Innovation

In this InfoQ presentation, Celine Pypaert addresses the pervasive nature of open-source software and outlines a comprehensive strategy for managing the inherent risks associated with third-party dependencies. She emphasizes a critical shift from reactive "firefighting" to a proactive risk management framework designed to secure modern application architectures. Central to her blueprint is the use of Software Composition Analysis (SCA) tools and the implementation of Software Bills of Materials (SBOM) to achieve deep visibility into the software supply chain. Pypaert highlights the necessity of prioritizing high-risk vulnerabilities through the lens of exploitability data, ensuring that engineering teams focus their limited resources on the most impactful threats. A significant portion of the session focuses on bridging the historical divide between DevOps and security teams by establishing clear lines of ownership and automated governance. By defining accountability and integrating security checks directly into the development lifecycle, organizations can eliminate bottlenecks and reduce friction. Ultimately, Pypaert argues that robust dependency management does not just mitigate danger; it empowers developers and unlocks innovation by providing a stable, secure foundation for rapid software delivery. This systematic approach transforms security from a perceived hindrance into a strategic enabler of technical agility and enterprise growth.


Designing Systems That Don’t Break When It Matters Most

The article "Designing Systems That Don't Break When It Matters Most" explores the critical challenges of maintaining system resilience during extreme traffic spikes. Author William Bain argues that the most damaging failures often arise not from technical bugs but from scalability limits in state management. While stateless web services are easily scaled, they frequently overwhelm centralized databases, creating significant bottlenecks. Traditional distributed caching offers some relief by hosting "hot data" in memory; however, it remains vulnerable to issues like synchronized cache misses and "hot keys" that dominate access patterns. To overcome these hurdles, Bain advocates for "active caching," a strategy where application logic is moved directly into the cache. This approach treats cached objects as data structures, allowing developers to invoke operations locally and minimizing the need to move large volumes of data across the network. To ensure robustness, teams must load test for contention rather than just volume, tracking data motion and shared state round trips. Ultimately, designing for peak performance requires prioritizing state management as the primary scaling hurdle, keeping the database off the critical path while leveraging active caching to maintain a seamless user experience even under extreme pressure.


Cyber rules shift as geopolitics & AI reshape policy

The NCC Group’s latest Global Cyber Policy Radar highlights a transformative shift in the cybersecurity landscape, where regulation is increasingly dictated by geopolitical tensions, state-sponsored activities, and the rapid adoption of artificial intelligence. No longer confined to mere technical compliance, cyber policy has evolved into a strategic extension of national security and economic interests. This shift is characterized by a rise in digital sovereignty, with governments asserting stricter control over data, infrastructure, and supply chains, often resulting in a fragmented regulatory environment for multinational organizations. Furthermore, artificial intelligence is being governed through existing cyber frameworks, increasing the scrutiny of how businesses secure these emerging tools. A significant trend involves moving cyber governance into the boardroom, placing direct accountability on senior leadership as major legislative acts like NIS2 and the EU AI Act come into force. Perhaps most notably, there is a growing emphasis on offensive cyber capabilities as a core component of national deterrence strategies, moving beyond traditional defensive measures. For global enterprises, navigating this complex patchwork of national priorities requires moving beyond basic technical standards toward integrated resilience and proactive engagement with public authorities. Boards must now understand their strategic position within a world where cyber operations and international power dynamics are inextricably linked.


Is ‘nearly right’ AI generated code becoming an enterprise business risk?

The article examines the escalating enterprise risks associated with "nearly right" AI-generated code—software that appears functional but contains subtle errors or misses critical edge cases. As organizations increasingly adopt AI coding agents, which some analysts estimate produce up to 60% of modern code, the sheer volume of output is creating a massive quality assurance bottleneck. While AI excels at basic syntax, it often struggles with complex behavioral integration in legacy enterprise ecosystems, particularly in high-stakes sectors like finance and telecommunications. Experts warn that even minor AI-driven changes can trigger cascading system failures or outages, citing recent high-profile incidents reported at companies like Amazon. Beyond operational reliability, the shift introduces significant security vulnerabilities, such as prompt injection attacks and bloated codebases containing hidden dependencies. The core challenge lies in the fact that many large enterprises still rely on manual testing processes that cannot scale to match AI’s relentless speed. Ultimately, the article argues that the solution is not just better AI, but more robust governance and automated testing. Without clear human-in-the-loop oversight and rigorous verification protocols, the productivity gains promised by AI could be undermined by unpredictable business disruptions and an expanded cyberattack surface.


Why Traditional SOCs Aren’t Enough

The article argues that traditional Security Operations Centers (SOCs) are no longer sufficient to manage the complexities of modern digital environments characterized by AI-driven threats and rapid cloud adoption. While SOCs remain foundational for threat detection, they are inherently reactive, often operating in data silos that lack critical business context. This limitation results in analyst burnout and a failure to prioritize risks based on financial or regulatory impact. To address these systemic gaps, the author proposes a transition to a Risk Operations Center (ROC) framework, specifically highlighting DigitalXForce’s AI-powered X-ROC. Unlike traditional models, a ROC is proactive and risk-centric, integrating cybersecurity with governance and operational risk management. X-ROC utilizes artificial intelligence to provide continuous assurance and real-time risk quantification, effectively translating technical vulnerabilities into strategic business metrics such as the "Digital Trust Score." By automating manual workflows and control testing, this next-generation approach significantly reduces operational costs and audit fatigue while providing boards with actionable visibility. Ultimately, the shift from a reactive SOC to a business-aligned ROC allows organizations to transform risk management from a passive reporting requirement into a strategic advantage, ensuring resilience in an increasingly dynamic and dangerous global cyber landscape.