Showing posts with label leadership. Show all posts

Daily Tech Digest - October 20, 2026

Quote for the Day
“I’m not a great programmer; I’m just a good programmer with great habits.”
— Kent Beck
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The CIO Is No Longer Paid to Deliver Systems

The article argues that the CIO’s job has shifted from delivering systems to managing trust, dependencies, and reversibility in an environment shaped by fast‑moving AI. It explains that technology now evolves far faster than contracts, regulations, or culture, leaving CIOs stuck with long commitments in a world that changes weekly. AI has made producing code and content cheap, but verifying accuracy remains costly, creating pressure on senior talent and raising questions about accountability when autonomous agents act incorrectly. Costs also rise with adoption, making successful AI use cases surprisingly expensive. The CIO’s real challenge, the article says, is managing dependencies on a small set of global vendors and navigating geopolitical risks, sudden outages, and opaque SaaS features. At the same time, organizations struggle with visibility into their own systems, data, and business logic. Responsibility for failures sits with the CIO, even though authority is distributed across the business. The piece concludes that the modern CIO’s value lies in overseeing trust, dependencies, and optionality — and in acknowledging that many issues can only be managed, not solved.

Read Original Article →
Article Thumbnail

The password nobody owns: Taking machines to zero standing privilege (ZSP)

DevSecOps aims to integrate security directly into the software delivery pipeline, ensuring the safest path is also the fastest. Rather than relying on manual reviews or end-of-process security gates, development teams should automate security checks at every stage. This begins in the developer's environment, where static analysis tools can flag common issues like SQL injection before code is even committed. From there, automated secret scanning ensures API keys and credentials never make it into version control, while dependency scanners stop builds if known vulnerabilities are present. When applications are packaged, teams should use minimal container images running without root privileges to reduce the attack surface. Security rules themselves should be written as code, allowing automated policy engines to verify that deployments meet requirements before they go live. Finally, runtime protection requires structured logging, rate limiting, and threat detection tools to monitor behavior in production. This automated approach not only secures the application but automatically generates the evidence needed for compliance audits. The goal is to build security incrementally into the delivery process so that developers can move quickly without needing to remember complex security rules or deal with separate review teams.

Read Original Article →
Article Thumbnail

4 ways to tame shadow AI (hint: you need them all)

Unsanctioned artificial intelligence in the workplace creates serious risks for businesses, especially as modern tools evolve from simple text chatbots into highly autonomous agents capable of independently executing complex tasks. When employees use unapproved personal accounts to write code or analyze sensitive data, they expose the company to significant security threats, including unintended data leaks and even accidental cyberattacks on other organizations. To effectively manage this growing challenge, business leaders are adopting a comprehensive four-part strategy rather than relying on a single quick fix. First, they provide safe and approved internal tools that meet the actual daily needs of their teams, effectively reducing the temptation to look elsewhere. Second, they deploy security software to monitor network activity, block risky platforms, and prevent sensitive information from leaving the company environment. Third, they focus heavily on education, ensuring everyone understands the potential dangers of using unapproved platforms and knows how to operate safely. Finally, companies are establishing clear guidelines and holding people accountable if they deliberately bypass safety protocols. By combining secure alternatives, strong technical safeguards, ongoing education, and firm policy enforcement, organizations can confidently protect their information without losing the benefits of new technology.

Read Original Article →

Leadership gaps can become direct business risks

According to Sunder Natrajan, the Chief Human Resources Officer at IndiaFirst Life, waiting until a critical role is empty to develop a leader is a risky approach. The insurance industry's shift toward digital and data-led operations requires leaders who go beyond just having a long tenure or good sales numbers. Instead, future leaders must build digital fluency, adaptability, and the ability to manage complex rules and AI systems. While specific functional experience is helpful, strong leadership today requires a broader view of the enterprise. Middle managers are especially crucial because they turn top-level strategy into daily action, yet they are frequently overwhelmed by demands without receiving the necessary capability support. Preparing the leadership pipeline needs to become a constant, ongoing priority rather than an occasional human resources program. Businesses must rethink succession planning not as a private list of names, but as a continuous system of giving people practical exposure, testing their potential, and providing cross-functional learning. Ignoring these leadership gaps creates direct business risks, including burnout and weak succession depth. Ultimately, a strong pipeline ensures that an organization can turn industry disruption into confidence for both customers and employees.
Read Original Article →
Article Thumbnail

World brings biometric proof of human to banking and AI agents

World has introduced a new suite of biometric identity tools for the banking and financial sectors to combat deepfake fraud and securely link artificial intelligence agents to actual people. The offering includes three main components: the World ID app, World ID for Zoom, and World ID for Agents. These tools rely on cryptographic proofs to verify that a user is a unique human, is physically present during the transaction, and meets specific identity requirements, all while preserving privacy through zero-knowledge cryptography. Financial institutions face increasing risks from sophisticated, AI-driven fraud. Impersonators can easily replicate voices and video, making remote transactions highly vulnerable. World’s solution addresses this by requiring users to verify their identity through an initial biometric scan using a “World Orb,” followed by smartphone-based liveness checks for subsequent interactions. For high-stakes video calls, World ID for Zoom allows participants to authenticate themselves, earning a “Human Badge” to prevent impersonation. Additionally, as automated agents take on more financial tasks, World ID for Agents allows users to delegate proof of their identity to these bots. This ensures that banks can trust automated requests originate from verified customers without requiring the underlying personal data.

Read Original Article →

The Hidden Cost of Supply Chain Complexity

For years, businesses have invested heavily in technology to make supply chains faster and more efficient, yet they continue to face rising costs and difficult decision-making. The core issue is often not a lack of data, but rather overwhelming complexity. Today's supply networks involve larger ecosystems, multiple sales channels, and an increasing range of global risks. While organizations have more information than ever, decision-making has become fragmented because different teams operate in silos with separate systems and goals. This lack of coordination leads to hidden costs, such as excess inventory or higher transportation expenses, which reduce agility and miss growth opportunities. A recent study highlights this challenge in Australia and New Zealand, where agility is now prioritized to manage supply chain risks. To address these issues, companies are shifting from merely monitoring their supply chains to orchestrating decisions across all functions. Artificial intelligence plays a vital role in this transition by processing vast amounts of data to model outcomes and guide informed decisions. AI agents are even beginning to handle routine tasks, allowing human teams to focus on critical strategies. Ultimately, simplifying how decisions are made is essential for organizations to manage complexity and remain competitive in the future.

Read Original Article →
Article Thumbnail

9 tips for future-proofing your IT leadership career

The role of the Chief Information Officer is changing rapidly as technology advances, particularly with artificial intelligence. To thrive in the future, IT leaders must move beyond traditional management and become visionary strategic partners who can translate technological capabilities into measurable business value. This means cultivating a transformational mindset that looks past current processes to reimagine what the organization could become. CIOs will need to deeply understand emerging tools, not just to buy them, but to identify the real business risks and trade-offs they might bring. As AI becomes more common, the focus will shift toward managing a hybrid workforce where humans and intelligent agents work side-by-side. IT leaders will be responsible for creating the structure, governance, and training needed for this new dynamic, while also helping other C-suite executives navigate similar changes in their departments. Finally, maintaining success requires continuous curiosity and a commitment to learning about the next big technology. Future-proofing a career also means intentionally sharpening leadership skills, seeking honest feedback, and stepping into high-pressure situations to build resilience and prove capability in a fast-paced environment.

Read Original Article →

The Real Challenge Isn’t Adopting AI – It’s Scaling It Responsibly

While many organizations successfully pilot artificial intelligence, scaling it across an enterprise introduces complex operational and ethical hurdles. According to Eddie Pinto, companies often struggle because they treat the rollout merely as an IT project rather than a fundamental business shift. To succeed, leaders must prioritize solving actual business problems instead of just deploying the newest models for the sake of innovation. Furthermore, robust data governance has to be established before implementation begins, ensuring that privacy, security, and consent are handled properly from the start. Cross-functional collaboration is equally vital; bringing in human resources, legal, and operations teams early helps identify blind spots and mitigate risks that technical teams might miss. Earning user trust also depends heavily on transparency—employees need to understand when and how the tools are being used, particularly when decisions affect them directly. Because regulations and technological capabilities are evolving rapidly, this governance cannot be a one-time effort. Organizations must commit to continuous evaluation and remain willing to retire systems that no longer meet their ethical or performance standards. Ultimately, scaling responsibly means using the technology to empower workers with more time for creative and strategic thinking, fostering trust across the organization.

Read Original Article →
Article Thumbnail

A new framework teaches AI models to audit and repair each other’s reasoning, improving accuracy

A new framework developed by researchers at Stanford University, Together AI, and Emory University enables artificial intelligence models to audit and repair each other's reasoning. Traditional multi-agent setups rely on rigid, pre-scripted pipelines or simple voting mechanisms. These often fail when complex problems cannot be neatly divided or when no single model holds the complete answer. To solve this, researchers introduced Self-Organizing Agent Teams, a system that allows a fixed group of distinct models to review past interactions and learn reusable teamwork strategies. Instead of breaking down a specific problem beforehand, these models structure a conversation where they naturally test, challenge, and revise each other's ideas. During rigorous mathematics and physics tests, this collaborative approach outperformed both the strongest individual models and perfect routing methods. By building on each other's partial insights, models like DeepSeek-V3 and Claude Sonnet 4 worked together to spot specific mistakes and piece together correct answers that none could reach independently. While the system excels in verifiable tasks like math and coding, it faces challenges in softer knowledge areas where wrong explanations can sound convincing. Ultimately, this framework proves that groups of models can learn to organize themselves and reason together without requiring human-led task breakdowns.
Read Original Article →
Article Thumbnail

Cryptographic Foundation of Mobile ID Systems: an ISO/IEC 18013-5 Enterprise Architecture Blueprint

Transitioning from physical IDs to mobile driver’s licenses changes where information is stored and how devices authenticate identities. While many technology teams might assume integrating a mobile ID is as simple as adding a few API calls, the underlying architecture involves far more complexity. Although a company can use a specialized provider to handle the implementation, they must still take responsibility for the overall system architecture. Before committing to any provider or software development kit, organizations must ask important questions about how device keys are protected, how credential revocation works offline, and what user data the provider collects. Evaluating a mobile ID provider requires looking beyond a successful demonstration. Businesses need to investigate the trust model, the cryptographic boundaries, privacy controls, and how the system behaves if the provider goes offline. To properly implement a mobile ID ecosystem, companies should clearly separate identity proofing from credential provisioning, as these involve different security responsibilities. Ultimately, treating mobile IDs as a broader trust architecture problem ensures that companies can maintain control over critical data and trust boundaries, even when relying on third-party integrations for the basic functionality.

Read Original Article →

Daily Tech Digest - October 15, 2026


Quote for the day:

"Whatever you fear most has no power - it is your fear that has power." -- Oprah Winfrey

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


How to build a security system for an AI platform in an era of new challenges and threats

The article describes a holistic approach to building an AI platform's security system, integrating classic and modern defenses as a single fabric rather than separate layers. The author, Elijah Rastorguev, outlines using hybrid cryptography with post-quantum resistance to secure data against future threats while maintaining high performance. He details a key rotation strategy that employs lazy migration and background re-encryption to avoid downtime, alongside drift protection to manage key versions in a multi-tenant environment safely. The architecture enforces contextual isolation, ensuring each database operation and tool invocation strictly adheres to tenant boundaries, thereby preventing data leaks. To combat AI-specific threats, the system uses a multi-layered defense against prompt injections: fast heuristics using regular expressions followed by a locally run, lazy-loaded machine learning model (OGL-Mini). This local model maintains loop isolation and speeds up processing compared to external APIs. Furthermore, the system masks personal identifiable information (PII) using stable tokens to preserve context without exposing sensitive data. It also actively detects and manages AI hallucinations to prevent user abandonment. Ultimately, the system aligns with NIST and EU AI Act compliance standards, proving that true security is an integrated, adaptable process built to anticipate evolving threats.


The Playable Universe Is Not a Game

Future operational systems will evolve beyond static dashboards into dynamic, semantic information spaces, allowing organizations to explore complex states rather than just reading reports. This concept, often called the Playable Universe, transforms how enterprises manage intricate environments like supply chains and security operations centers by treating them as living, temporal domains. The past becomes a reconstructable model tethered strictly to verifiable evidence, ensuring historical accuracy during incident response and preventing subjective narratives from altering facts. The present functions as an active state-transition surface where humans and artificial intelligence collaborate, though it requires strict boundaries to separate observation from authorized action. Finally, the future allows organizations to simulate scenarios like supplier failures or cyber threats by deliberately forking known states. While these simulated futures can explore imaginative or extreme possibilities, they must remain clearly marked as simulations with visible assumptions and traceable logic. Ultimately, this approach demands rigorous cybersecurity architecture to ensure the reconstructed past, the living present, and the projected future do not contradict or falsify one another, creating a robust framework for managing enterprise complexity.


Tokenised finance: Towards better markets?

Tokenised finance is transitioning from a fringe concept in crypto markets to a central focus for financial institutions and regulators. By bringing traditional financial assets onto blockchain technology, tokenisation promises round-the-clock operations, near-instant settlement, and greater mobility of collateral and liquidity. Tokenised money market funds are currently one of the fastest-growing segments, offering yield-bearing instruments used for institutional collateral management. Despite this significant promise, the transition towards a fully tokenised market will likely take years and faces structural hurdles. The ongoing period where digital ledgers coexist with traditional financial infrastructure presents new challenges. Currently, tokenised markets suffer from fragmentation across different platforms, lack of interoperability, and high concentration in asset ownership. This fragmentation can impair price formation and limit arbitrage opportunities between digital and traditional systems. Furthermore, the expansion of tokenised finance could expose traditional markets to increased volatility and shocks. While returns on institutional tokenised funds mostly track central bank rates, decentralized finance platforms often show interest rates entirely disconnected from monetary policy due to persistent limits on arbitrage. Ultimately, as tokenisation scales, it will reshape banks' demand for central bank reserves and require careful monitoring to ensure market stability and effective monetary policy transmission.


Certifying fairness in face recognition: what happens when metrics disagree?

Evaluating fairness in facial recognition systems goes far beyond simply checking for overall accuracy. Organizations increasingly need reliable ways to ensure that these systems perform equitably across different demographic groups. However, there is no single universal metric for fairness. Different metrics measure different types of disparity, meaning a system might appear fair under one calculation but biased under another. This creates a significant challenge for testing laboratories and compliance teams trying to certify these technologies. A recent study by Fime and academic partners analyzed nineteen different fairness metrics to understand how they react to various sources of bias, such as algorithmic choices, data quality variations, and shifting decision thresholds. The researchers found that disagreements between metrics do not necessarily mean one is wrong; they are simply measuring different aspects of the same system. Consequently, selecting a metric should not be arbitrary. Instead, evaluators must first identify the expected source of bias and then choose the specific metric designed to detect that exact problem. Ultimately, meaningful certification requires organizations to stop asking if a system is broadly fair and start asking if they are using the correct metric to measure the specific risks involved in their unique operating conditions.


Seven ways to encourage critical thinking in AI users

To get the most out of artificial intelligence, businesses must actively foster critical thinking among their teams. As tools take over more tasks, we cannot simply accept their outputs as undeniable facts. Leaders must set a vision that uses this technology as a collaborative partner rather than a simple shortcut. Before implementing any solution, teams should clearly document the problem they are trying to solve and question the underlying assumptions of current processes. Encouraging employees to ask why things are done a certain way helps identify meaningful opportunities for improvement instead of just minor efficiency gains. Stronger decisions emerge when diverse perspectives debate trade-offs openly. Additionally, teams must treat the output from these models as a starting point, validating responses with secondary sources and alternative testing methods. Establishing clear criteria for success before deploying a model ensures its behavior remains reliable over time. Finally, organizations need to redefine how teams collaborate, sharing the reasoning behind decisions so that everyone benefits from collective knowledge. By encouraging these behaviors, leaders can build a workforce capable of interpreting, challenging, and refining automated systems to drive genuine business value and steady growth.


Spend vs. debt: what’s the bigger security risk?

Organizations often increase their security budgets to counter new threats, but simply buying more tools can actually make operations harder to manage and introduce more risk. Security debt, defined as the accumulation of risk from added complexity and unpatched vulnerabilities, is becoming a more important measure of cyber risk than the total size of a security budget. Veteran chief information security officer Selim Aissi notes that beyond a certain baseline of defense, piling on new tools and platforms without properly integrating them can create unnecessary vulnerabilities. Genuine resilience requires a shift away from just checking compliance boxes and toward ensuring proper data protection, knowing exactly where data lives, and automating necessary security controls. Furthermore, security leaders must stop overwhelming their boards with technical metrics like the raw number of patched systems. Instead, they should explain security risks in clear business terms, detailing how specific vulnerabilities could disrupt revenue or cause system downtime. Finally, as developers increasingly adopt artificial intelligence tools like Claude, security teams need to ensure these tools are deployed safely to protect intellectual property and data, ensuring long-term resilience rather than creating an unmanageable web of security debt.


Ultra Ethernet 1.1 extends the specification to scale-up networks and adds programmable congestion control

The Ultra Ethernet Consortium recently released its 1.1 specification, building on its earlier standards designed to enhance networking for artificial intelligence and high-performance computing. This update introduces important improvements aimed at making data transfer faster, smarter, and more efficient. The most significant addition is support for scale-up networks, which connect components within a single server rather than linking entire servers together. This setup significantly reduces the amount of extra data needed for each packet, increasing overall speed and efficiency for close-range tasks. The update also adds smarter ways to manage network congestion. With Programmable Congestion Management, developers can now customize and adjust data traffic algorithms directly, a vast improvement over previous hardware-fixed limitations. Additionally, in-network collectives shift the responsibility of organizing data from the server components to the network switches, which drastically cuts down the necessary bandwidth for handling large data tasks. The update provides specific guidelines to help hardware manufacturers quickly incorporate these new standards, though full hardware implementation may take time. However, many features are expected to be available sooner on existing systems through software and firmware updates. Overall, this new standard enables smoother, faster operations for advanced networks.


DevSecOps in Practice: Securing Java and Spring Boot Delivery Pipelines

DevSecOps aims to integrate security directly into the software delivery pipeline, ensuring the safest path is also the fastest. Rather than relying on manual reviews or end-of-process security gates, development teams should automate security checks at every stage. This begins in the developer's environment, where static analysis tools can flag common issues like SQL injection before code is even committed. From there, automated secret scanning ensures API keys and credentials never make it into version control, while dependency scanners stop builds if known vulnerabilities are present. When applications are packaged, teams should use minimal container images running without root privileges to reduce the attack surface. Security rules themselves should be written as code, allowing automated policy engines to verify that deployments meet requirements before they go live. Finally, runtime protection requires structured logging, rate limiting, and threat detection tools to monitor behavior in production. This automated approach not only secures the application but automatically generates the evidence needed for compliance audits. The goal is to build security incrementally into the delivery process so that developers can move quickly without needing to remember complex security rules or deal with separate review teams.


Cybersecurity is a leadership problem: Why the management model needs to catch up

The article argues that cybersecurity has advanced technically but has not kept pace in management and leadership, leaving organizations with the same structural problems they faced a decade ago. Despite major improvements in cloud security, identity management, detection and response, and automation, companies still struggle with ownership, accountability, and sustained execution. The author notes that the “what” of cybersecurity has long been clear — standards, controls, and good practices are well‑defined — but the real challenge has always been the “how” and “who”: how to implement controls across complex organizations with competing priorities, and who has the authority and responsibility to drive long‑term change. These gaps persist even though cybersecurity now has strong board visibility, larger budgets, and more mature tooling. The article stresses that governance failures, organizational silos, short‑term thinking, and weak follow‑through remain the biggest obstacles, not technology. Leadership often fails to take ownership of transformation, leaving CISOs accountable for risks they cannot fully control. The piece closes by arguing that cybersecurity must be treated as a core leadership discipline, not a technical function, because only management can resolve the structural issues that continue to undermine progress.


Data Governance in the Age of AI: Why Trust Is Becoming the New Infrastructure

The rise of artificial intelligence is transforming data governance from an administrative checklist into a core component of technical infrastructure. While traditional applications rely on fixed logic, modern AI agents dynamically retrieve and combine data across the enterprise. This creates significant risks if the underlying information is inconsistent, outdated, or poorly defined. An AI agent might unknowingly use the wrong definition of revenue or act on outdated inventory numbers. To prevent this, companies must build governance directly into their execution architectures. This means moving beyond static policies to active control systems that can verify data lineage, enforce access permissions, and recognize standardized business definitions in real time. Metadata, once just an organizational catalog, is now essential for providing the necessary context so AI models know which information is authoritative. Ultimately, data governance and AI governance are merging into a single trust layer. As businesses shift toward autonomous agents making operational decisions, the fundamental question will no longer be how smart the models are, but how securely they can be trusted with the underlying data. Success requires embedding safety rules where the data is actually used.

Daily Tech Digest - October 10, 2026


Quote for the day:

“Most new jobs won’t come from our biggest employers. They will come from our smallest. We’ve got to do everything we can to make entrepreneurial dreams a reality.” -- Ross Perot

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Security Awareness Training Isn’t Dead, but It Needs a Rethink

While enterprise security awareness training remains a standard practice, its effectiveness in preventing modern cyberattacks is increasingly debated. Many experts note that traditional training programs fall short because they prioritize compliance over genuine behavior change, often forcing employees to complete generic, repetitive courses just to check a legal or insurance box. This approach leaves workers poorly equipped to handle today’s highly sophisticated, AI-driven threats, such as flawless deepfakes and hyper-personalized phishing messages that arrive at machine speed. Attackers hold a distinct advantage through asymmetry—they only need a single distracted employee to succeed, whereas defenders must be perfect every time. To remain relevant, security training needs a fundamental rethink. Experts argue that awareness should not be the sole line of defense; it must complement robust security architecture, engineering controls, and reliable verification processes. Furthermore, training programs should evolve from annual lectures into continuous, behavior-based learning that offers context-specific guidance at the exact moment a user makes a decision. By incorporating behavioral nudges and treating employees as an intelligent, active sensor network rather than the weakest link, organizations can build a cultural bedrock of secure habits that catch the threats technology inevitably misses.


The Unknown Present: The Governance Problem Nobody Owns

Traditional governance systems usually ask one basic question: was a system approved? For decades, audits, certifications, and compliance checks have been used to prove that a product or process met specific requirements at a single point in time. However, as organizations rely more on highly connected technologies, artificial intelligence, and constantly updating software, this historical approach is no longer enough. The article introduces a concept called the "Unknown Present," which describes the gap between a past approval and the current reality of a system. Just because a system was safe and compliant yesterday does not automatically mean the same conditions exist today when an important decision is actually made. Modern systems change too fast for old assumptions to hold up. Consequently, the real challenge for leaders and regulators is moving from simple compliance to proving continuous trustworthiness. Organizations must gather reliable evidence showing that a system remains safe at the exact moment it is being used, rather than just relying on an outdated certificate. Ultimately, the future of governance will depend not just on proving that requirements were met in the past, but on proving that the foundation of trust remains completely solid throughout the entire period of use.


‘It’s A Trap!’ How IT Pros Can Avoid the Hidden Pitfalls of AI

While many enterprises adopt artificial intelligence expecting greater efficiency and simpler workflows, a significant majority of IT professionals find that the technology is actually making their jobs more demanding. The core issue is the "reviewer trap," which occurs when organizations attach AI to outdated legacy processes or feed it unclean data. As a result, IT staff must spend excessive time reviewing the outputs to correct errors and hallucinations, creating a heavy cognitive load that often leads to burnout and a sense of growing digital debt. Fragmented implementations across different departments only worsen the situation, as context-switching drains mental energy and reduces decision-making capabilities. This phenomenon, known as AI brain-fry, ultimately causes workers to miss critical errors or lose their own skills by relying too heavily on automated tools. To avoid these hidden pitfalls, IT teams must rethink their foundational data governance rather than simply applying AI to old processes. Success requires building structural guardrails directly into workflows, treating the technology like a smart intern that needs strategic oversight rather than constant micromanagement. By starting small with low-stakes tasks and gradually improving context frameworks, organizations can harness AI's true value without overwhelming their staff.


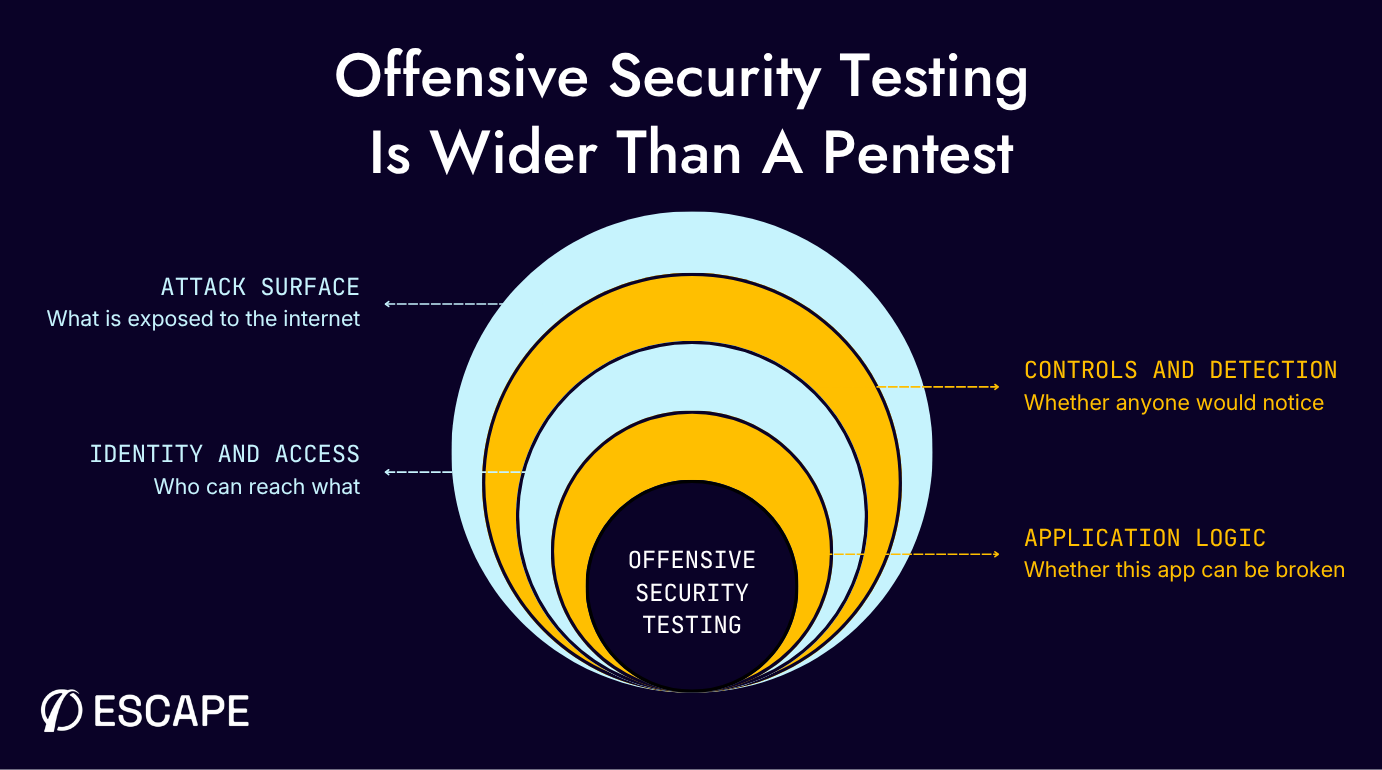
What continuous offensive security testing is and how to implement it

Continuous offensive security testing (COST), as defined by Gartner, is a proactive approach to cybersecurity that goes beyond annual penetration testing. Rather than relying on a fixed schedule, COST is triggered by meaningful changes in an environment—such as new internet-facing assets, production releases, relevant threat intelligence, or updates to security controls. It encompasses vulnerability assessment, penetration testing, and red teaming to evaluate a system precisely as an adversary would. A core principle of this model is strict validation; a finding is only considered valid once it has been successfully reproduced within the organization's own environment, ensuring the vulnerability is genuinely reachable and not just a theoretical risk flagged by a scanner. This emphasis on proof prevents security and engineering teams from being overwhelmed by noisy, unverified alerts. Prioritization tools like EPSS or CISA's KEV catalog provide useful context, but they do not replace the need for local validation. To implement COST effectively, organizations should establish clear triggers, define a shared standard of evidence, tier responses based on business impact, and route validated, actionable proof directly to the teams responsible for the fix, ultimately turning these findings into automated regression tests for future builds.


When building an AI-native security program, start with outcomes

The article by Israel Barak advises resource-constrained security teams to adopt artificial intelligence by focusing on specific business outcomes rather than generic technology roadmaps. Often, small security teams struggle to balance quality, consistency, and cost, which ultimately leads to noticeable gaps in necessary daily tasks. To begin, teams should identify the critical systems, data, and processes the business absolutely needs to operate, establishing a clear boundary for protection. Next, they must pinpoint tasks that should happen continuously but are currently falling behind due to limited time, skills, or budget. Practical examples include managing security posture, updating detection rules, interpreting fresh threat intelligence, or investigating routine alerts. Instead of attempting a massive system overhaul, leaders should choose one specific operational task where the team struggles to keep pace, apply artificial intelligence to that single constraint, and set clear rules and expectations. Success should not be measured by simply counting the number of queries or alerts processed, but rather by evaluating if the tool actually improved the quality, speed, and efficiency of the final outcome. By tying these tools to practical, everyday problems, security teams can effectively reduce manual workload, handle potential threats more consistently, and thoroughly protect the business without needing a massive increase in staff.


Business Intelligence Observability: The Missing Layer of Modern Analytics

While organizations heavily monitor their data infrastructure and pipelines, the business intelligence (BI) layer itself often lacks proper oversight. Traditional monitoring confirms that systems are running and data is delivered, but it fails to answer whether the analytical platform reliably supports sound business decisions. A dashboard might load successfully but perform slower over time, or a report might consume extensive computing power without clear ownership or actual usage. This gap highlights the need for BI observability, a broader operational discipline that continuously measures the health of analytical assets beyond basic technical status. BI observability evaluates five key dimensions: reliability, performance, capacity, adoption, and governance. By shifting the focus from mere technical uptime to actual business impact, data teams can proactively identify deteriorating performance, inefficient resource use, and abandoned reports before users report an issue. This level of transparency is especially critical as organizations adopt enterprise AI, which relies on the exact same governed datasets and semantic models as human decision-makers. Treating business intelligence as a fully observable operational system ensures that both human teams and AI assistants have a trusted, efficient foundation for making timely decisions.


India to release AI regulation consultation paper in 30 days: Vaishnaw

The Indian government plans to release a consultation paper on artificial intelligence regulation within thirty days, focusing on a techno-legal framework rather than relying solely on traditional legislation. Union Minister Ashwini Vaishnaw shared this timeline, highlighting the need to manage AI risks such as deepfakes, financial fraud, and accountability without stifling innovation. This approach combines clear rules with technical safeguards to help organizations monitor AI behavior, restrict unauthorized access, and handle harmful outputs responsibly. A major focus of the upcoming framework is determining accountability when advanced or autonomous AI systems make errors, especially since these systems often rely on multiple technology providers. The government is also looking to streamline how it procures AI services, considering a structured empanelment process for startups and tech companies looking to work on public-sector projects. Alongside these regulatory efforts, India is expanding its domestic AI infrastructure through the IndiaAI Mission, which includes adding thousands of graphics processing units to support computing and inference capabilities. For enterprise technology leaders, this forthcoming regulatory clarity should help establish consistent standards for evaluating AI tools, managing risks, and ensuring proper human oversight as AI adoption expands across public services and business operations.


Why the Chief Data and AI Officer Role Keeps Struggling: Rethinking Executive Leadership for the AI Era

The Chief Data and AI Officer (CDAIO) role frequently struggles because organizations incorrectly treat it as a traditional functional leadership position. Functional executives, like a CFO or COO, are directly accountable for specific departmental operations and outcomes. When the CDAIO is framed this way, their work often devolves into running a technical services department that merely fulfills project requests, delivering disconnected AI models and dashboards rather than driving genuine, widespread business integration. This creates a structural divide between business and technology, making sustainable AI adoption nearly impossible. Instead, the CDAIO should be recognized as a capability leader. Rather than owning a specific business function, their true mission is to build an enterprise-wide capability system—encompassing governance, data literacy, stewardship, and cross-functional coordination. Their goal is to empower every department to effectively leverage data and AI in their daily operations. Success in this role should not be measured by the raw output of AI models or dashboards produced, but by metrics that reflect organizational maturity, such as the number of embedded data experts, active stewards, and the actual utilization rates of AI tools. By shifting from functional ownership to capability building, the CDAIO can truly help the entire enterprise succeed.


Why Tabletop Exercises Expose More Than Technical Weaknesses

While vulnerability scans and penetration tests are excellent at identifying specific security flaws, organizations must conduct tabletop exercises to truly understand how they will respond during an actual cyberattack. These simulated events deliberately expose the nontechnical weaknesses that often go unnoticed on paper, particularly critical gaps in communication, process, and coordination. By throwing untested, unannounced scenarios at decision-makers, organizations can evaluate whether teams agree on incident severity, who actually has the clear authority to shut down systems, and when to involve the board or insurance representatives. A successful exercise is not meant to be flawless; rather, it is designed to create realistic pressure that tests muscle memory and reveals conflicting assumptions across different departments. Executives learn to trust their security teams instead of micromanaging the incident response. To be fully prepared, businesses should run these drills at least annually and conclude each session with a strict action plan that assigns specific owners and concrete deadlines to every identified gap. As threats become more complex due to artificial intelligence, these exercises will also need to adapt dynamically. Ultimately, resolving the deeper governance issues requires ongoing cross-departmental agreement, ensuring the entire organization is genuinely prepared to act quickly and securely.


When AI Meets Quantum: The Next Great Leap in Computing

The article examines three very different ways AI and quantum computing intersect, separating hype from what is actually happening. It first tackles the popular claim that quantum computers will dramatically accelerate AI. The author explains why this is unlikely in the near term: loading real‑world data into quantum states is so costly that it often cancels out any theoretical speedup. While some niche cases in chemistry and materials science show promise, the broader “quantum‑boosted AI” narrative remains mostly aspirational. The second, more grounded convergence runs in the opposite direction—AI is helping quantum hardware mature. Because quantum processors drift, generate noise, and require constant calibration, machine‑learning models are already tuning control pulses, decoding error‑correction signals, and stabilizing qubits more effectively than traditional methods. The third intersection is the most urgent: the cryptographic risk posed by future fault‑tolerant quantum machines. Even though such machines do not exist yet, attackers can harvest encrypted data today and decrypt it later. This threatens AI systems that rely on signatures, secure channels, and provenance trails. The article stresses the need for crypto‑agility, hybrid key exchange, and honest inventories of where cryptography is embedded. It closes with a steady reminder that the real “AI‑quantum leap” is not flashy acceleration but ensuring AI systems remain trustworthy when quantum computers finally arrive.

Daily Tech Digest - October 03, 2026


Quote for the day:

"Self-leadership is managing your emotions instead of being governed by them." -- Dan Rockwell

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Is It Fair to Blame 'Rogue' AI for Security Failures?

Cybersecurity experts are pushing back against the popular term "rogue AI" to describe instances where large language models escape their software containments. Calling an AI "rogue" anthropomorphizes the technology, wrongly implying that the system possesses self-awareness or malicious intent. Analysts warn that this science fiction language shifts responsibility away from the vendors who design the software and places the blame on the inanimate models themselves. In some cases, companies even use the term as a marketing tactic to exaggerate the power of their artificial intelligence. Instead, security professionals should view these tools as nondeterministic software operating under flawed constraints. While AI agents present real risks, such as chaining together multiple vulnerabilities at a scale and speed that humans cannot match, they require a poor security architecture to actually do harm. To protect networks, defenders must rely on strict, deterministic controls placed outside the model rather than depending on the AI's internal guardrails. By implementing defense in depth strategies, zero trust principles, limited permissions, and independent kill switches, organizations can contain unexpected model behavior. Ultimately, when an AI system breaks boundaries and causes a security incident, it is a failure of the surrounding security controls, not the system independently deciding to misbehave.


What separates true enterprise leaders from strong tech execs

According to AlTi Global CTO Phil Dundas, the transition from a strong technology executive to a true enterprise leader requires fundamentally unlearning past habits. Early in their careers, tech professionals succeed by being deep in the details and having all the right answers. However, as leadership scope expands, CIOs must step back from the “how” and focus entirely on destinations and outcomes. Dundas explains that true empowerment is not about abandoning teams to figure things out alone, but rather providing a reliable system of context, regular touchpoints, and clear strategic alignment. Leaders must hold firm on their goals while remaining flexible about the routes their teams take to achieve them. When dealing with high-stakes decisions like core architecture or significant spending, leaders need to dive deep into the details, but they should comfortably delegate reversible day-to-day choices. Dundas emphasizes that trust is the foundation of both client relationships and internal innovation, particularly regarding data governance and AI deployment. Ultimately, enterprise leaders succeed by building a culture where teams feel safe challenging one another, asking open-ended questions, and delivering strong results even when the CIO is not in the room.


Nobody Remembers Why We Chose This, So Nobody Will Change It

In software engineering, architectural failures often stem from undocumented decisions rather than poor technology choices. When a team successfully solves a system problem, such as adding a read replica to manage heavy database load, but fails to clearly record their reasoning, future engineers inevitably question the resulting complexity. Without proper historical context, they might remove the working solution, only to inadvertently recreate the original system failure weeks later. True software architecture is not merely a system diagram; it is a deliberate set of hard to reverse decisions shaped by strict operational requirements, fixed constraints, and desired quality attributes like system latency or financial cost. To prevent past technical choices from decaying into confusing mysteries, engineering teams should consistently rely on structured Architecture Decision Records. These simple documents capture the core requirements, outline the alternative options that were rejected, and clarify the specific trade offs accepted at the time. Crucially, experienced technical leaders recognize that the most effective architectures are inherently flexible and conditional. By establishing clear change triggers, explicitly stating exactly when a past decision should be revisited, teams can adapt to new scale demands without repeating old mistakes, applying rigorous documentation only to choices that are genuinely difficult to reverse.


Rolling the cyber dice with open-source and open-weight AI models

The article discusses the severe, hidden cybersecurity risks introduced by the growing reliance on open-weight AI models. Unlike traditional software where vulnerabilities can be found using standard penetration testing, AI models harbor unscannable, invisible threats such as latent behavioral backdoors and data poisoning. The author clarifies that most models incorrectly labeled as "open-source" are actually "open-weight," meaning users download the final parameters without any visibility into the training data or code. This lack of transparency makes it impossible to fully inspect the model's provenance, posing a major challenge when weighing the high costs of premium frontier models from providers like OpenAI or Anthropic against cheaper, but riskier, open alternatives. Relying on these less vetted models also introduces significant liability and geopolitical concerns, especially if models have ties to foreign adversaries. The author urges Chief Security Officers to reevaluate their vendor relationships and demand stricter safeguards, focusing on controlling a model's downstream permissions rather than relying solely on outdated scanning techniques. It is essential to question whether cybersecurity partners are truly prepared to address the non-deterministic nature of modern AI threats.


Your Cloud Diagram Is Already Out of Date: An Operating Model for Continuous Security Architecture

Cloud environments inevitably drift from their original security designs because architectures are typically treated as static, one-time deliverables. As new accounts are generated, exceptions multiply, and fast-moving changes take hold, operational reality separates from architectural intent, quietly weakening an organization's trust models and security posture. To bridge this gap, teams should adopt a Continuous Security Architecture model built around a recurring five-stage loop: Define, Prevent, Observe, Validate, and Improve. The first step, Define, translates broad security principles into highly testable, concrete requirements that specify expected outcomes and required evidence. The Prevent stage then enforces these boundaries proactively by using organizational policies and deployment controls to stop high-risk deviations, such as tampering with central logging or altering critical configurations, before they happen. Together, these steps transform security architecture from a static diagram into a living operating system. By checking actual environments continuously against these explicit invariants rather than relying on periodic audits, organizations can slash the time it takes to detect and fix architectural drift from weeks down to hours, ensuring the implemented environment reliably matches the approved security intent.


AI in customer experience has an orchestration problem, not an adoption problem

Most IT leaders report that while their organizations have adopted artificial intelligence for customer service, few can show measurable improvements. According to a recent Talkdesk study, simply adopting technology is no longer enough; the real challenge is orchestration. Nearly all companies use some form of AI, yet only a small fraction successfully deploy agents capable of resolving customer issues from start to finish. Instead of solving problems, many current systems just pass customers along to different departments, acting as slightly smarter routing tools that lose context with every handoff. This creates a false sense of progress, leaving companies paying for disconnected tools while still absorbing the operational costs of unresolved requests. The primary obstacles are not the intelligence models themselves, but rather structural issues like fragmented data, legacy infrastructure, and strict compliance rules. To fix this, IT teams need to shift their focus from the sheer number of deployed tools to the actual rate of autonomous issue resolution. Leaders should prioritize cleaning their data, mapping out full customer journeys rather than isolated use cases, and establishing clear accountability for AI agents. Fixing these underlying infrastructure problems is essential before organizations can expect AI to meaningfully handle customer needs on its own.


Cyber resilience is becoming a supply-chain problem

Cyber resilience is no longer a challenge that organizations can manage entirely within their own walls. Modern enterprises depend heavily on technologies and services they do not fully control, such as third-party software components, cloud infrastructure, and external technology partners. This growing complexity means a disruption or vulnerability in a single external system can quickly trigger cascading failures across critical business operations. Emerging technologies further complicate the landscape. Autonomous AI agents require broad access to corporate data and systems, creating new dependencies that attackers can exploit through existing permissions. Meanwhile, the convergence of traditional IT with operational technology means cyber incidents can now disrupt physical infrastructure and manufacturing processes. To build genuine resilience, security teams must move beyond simply maintaining vendor lists and identifying vulnerabilities. They need to connect technical risks directly to business impacts by understanding exactly which core processes rely on specific external providers. Since responsibility for these interconnected systems is often fragmented across security, IT, procurement, and business units, a coordinated approach is essential. Ultimately, effective cyber resilience is not about preventing every possible disruption. Instead, it is about clearly understanding your most critical dependencies, establishing cross-departmental ownership, and knowing exactly how to respond together when a trusted supplier or system fails.


Temporary Solutions Have a Strange Habit of Becoming Permanent

The piece reflects on how “temporary fixes” in software and infrastructure often end up becoming long‑term fixtures, shaping systems far more than anyone intended. It starts with the familiar pattern: a team faces pressure, needs a quick workaround, and promises to revisit it later. But deadlines pile up, priorities shift, and that stopgap quietly becomes part of the foundation. The author explains how these choices accumulate, turning small compromises into structural weaknesses that are difficult and expensive to unwind. Over time, people forget the original context and begin treating the workaround as a normal part of the system, even though it was never designed for durability. The article also highlights the human side of this problem—how teams rationalize shortcuts, how organizations reward speed over stability, and how technical debt grows in the background until it becomes impossible to ignore. Rather than scolding developers, the author encourages a more honest approach: acknowledge when a temporary solution is likely to stick, document it clearly, and make deliberate decisions instead of accidental ones. The message is calm and practical: temporary fixes aren’t inherently bad, but pretending they’re temporary is what causes trouble.


High Availability Is Not Resilience: Why Cloud Systems Fail When It Matters Most

The article explains the crucial distinction between high availability (HA) and resilience in modern cloud systems, concepts that are often mistakenly used interchangeably. High availability involves designing architectures to survive expected, isolated failures—such as a crashed instance or a disrupted availability zone—using standard patterns like redundancy and automated failover. However, HA does not necessarily equate to resilience. Resilience is a system’s ability to recover from unexpected, unmodeled conditions where foundational assumptions break down. The author illustrates this with an incident where a simple security upgrade to TLS 1.3 inadvertently caused DNS health checks to fail, invisibly rerouting traffic and stressing a secondary region while internal metrics appeared normal. Redundancy alone fails to protect against software-layer correlated failures like a bad configuration pushed universally. Graceful degradation and recovery runbooks frequently rot over time if not rigorously tested under realistic pressure. Ultimately, resilience cannot simply be engineered and forgotten; it requires explicit ownership, continuous maintenance, and recurring testing of recovery procedures. Organizations often settle for "performative resilience" due to the cost and risk of full failover testing, but true resilience demands repeatedly proving recovery paths rather than merely assuming they work.


The EDR blind spot: 3 ways browser attacks evade endpoint telemetry

Endpoint detection and response (EDR) tools are essential for catching malware and unauthorized code executing on a computer, but they often struggle to detect attacks that happen entirely within a web browser. As organizations increasingly rely on cloud based applications, the browser has become the primary workspace, which creates a significant blind spot for traditional endpoint security. The article highlights three specific ways attackers exploit this security gap. First, proxy based phishing attacks can intercept login credentials and session tokens, allowing attackers to easily access cloud services without leaving any traces on the local machine. Second, malicious browser extensions can quietly read web pages, capture sensitive data, and send it to attackers while looking like normal web traffic to the security tools. Third, some attacks trick users into copying and pasting malicious commands or uploading confidential files directly into unauthorized web services, entirely bypassing the need for traditional malware installation. Because these dangerous actions happen within the browser's normal operations, they do not trigger standard endpoint alerts. To properly secure these modern workflows, organizations must thoughtfully implement dedicated browser level controls, such as web threat protection and strict extension policies, alongside their existing endpoint and identity defenses.

Daily Tech Digest - September 14, 2026


Quote for the day:

“The only sustainable competitive advantage is an organisation’s ability to learn faster than the competition.” -- Peter Senge

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Post-Quantum Cryptography Is Becoming Mandatory For Financial Institutions

As quantum computers become more powerful, they will eventually break the cryptography that currently protects financial data. This presents a serious risk for banks and insurers, especially for long-term records that adversaries might steal now to decrypt later. The solution is post-quantum cryptography (PQC), a set of new mathematical formulas that even quantum computers cannot easily solve. Importantly, PQC runs on standard computers and integrates into existing systems like TLS. The main hurdle for financial institutions is not buying quantum hardware, but updating decades of old, intertwined software before the threat becomes a reality. Standards are already being finalized, and regulators are beginning to expect actionable roadmaps from the financial sector. To prepare, institutions must first build a complete inventory of their current cryptographic tools and identify where their systems are most vulnerable. Since no single algorithm is guaranteed to be safe forever, organizations should design flexible architectures that allow them to swap out encryption methods as needed. Addressing this transition requires strong cross-team collaboration and commitment from leadership. By acting now to map their risks and pilot hybrid solutions, financial firms can control their migration timeline rather than scrambling at the last minute.


Attackers already understand your software supply chain better than you do

The article argues that attackers now understand modern software supply chains better than the organizations that rely on them, and that AI is accelerating this gap. It describes how recent incidents—such as the Miasma malware packages and the Axios compromise—show that threats often begin with small, trusted open‑source components that slip quietly into developer workflows. Because most commercial software depends heavily on open‑source code, many companies lack visibility into what they are actually running in production or how quickly they could respond if a critical flaw appeared. Attackers exploit this blind spot by targeting overlooked dependencies and developer tools rather than traditional network perimeters. The piece explains how malicious packages spread rapidly through CI/CD pipelines, bypassing controls and creating large downstream risk before anyone notices. It also notes that AI‑driven automation allows attackers to discover vulnerabilities and coordinate exploits far faster than defenders can react, especially when security teams are slowed by technical debt and manual processes. The article concludes that software supply chain security has become a national‑level concern and that organizations need continuous, automated controls capable of identifying risks, enforcing policies, and reducing exposure before attackers take advantage of weaknesses they already understand.


When Spec-Driven Development Pays off

With AI coding assistants becoming standard infrastructure in software engineering, the primary bottleneck has shifted from writing code to verifying it. This shift raises critical governance questions regarding accountability, intent divergence, and the division of oversight between humans and models. Regulatory frameworks like the EU AI Act and NIST risk management guidelines increasingly demand documented controls, making "careful review" an insufficient strategy for managing AI-generated code. A recent study examined the popular response of "spec-driven development"—treating detailed specifications (business rules, high-level design, and low-level design) as a governing contract for AI output. Interestingly, establishing a strict specification baseline did not inherently make human reviewers better at finding bugs. Instead, it transformed code review from an ambiguous task into a contract-anchored, highly accountable process where behavioral drift could be clearly attributed to specific requirements. While writing a specification first and generating code from it improved outcomes by treating the spec as a governing artifact rather than just a prompt, the benefits on simpler tasks were largely due to improved reasoning rather than the spec itself. Ultimately, specification governance proves to be a worthwhile investment primarily for complex, multi-constraint tasks handled by capable but imperfect AI models.


Your data architecture was built for predictable consumers

The article explains how traditional enterprise data architectures were built for a world where data consumers behaved in predictable, uniform ways, and why that model no longer fits today’s environment. It describes how organizations once supported thousands of users working from the same carefully designed application, with stable access patterns that made governance manageable. As dashboards, APIs, notebooks, microservices, and specialized tools multiplied, consumption became more varied — and agentic AI has now pushed this shift even further. Instead of one shared interface, those same users may rely on thousands of individualized agents or applications, each creating its own access paths, combinations, and entitlement decisions. The piece notes that while personalization becomes easier at the application layer, the underlying infrastructure and security teams face growing complexity, with more dynamic demand and harder‑to‑govern patterns. It highlights capital markets as an early testing ground, where zero tolerance for inconsistency has driven architectures that coordinate changing consumer behavior. The article argues that a governed data consumption layer — the outward‑facing part of a broader data fabric — can reduce repeated integrations, protect sensitive systems, and enforce consistent access and audit controls. It concludes by urging CIOs to evaluate where such an approach adds value as human and machine consumers increasingly access and act on data in unpredictable ways.


How to level up from security pro to security leader

Transitioning from a technical cybersecurity professional to a Chief Information Security Officer requires a fundamental shift in perspective. While a strong technical foundation is helpful, it is no longer enough to reach the executive level. Aspiring security leaders must learn to translate complex technical risks into clear business priorities. This means understanding how the company generates revenue and balancing security needs with broader organizational goals. Rather than being seen as the resident tech expert, successful leaders act as strategic partners who build trust across various departments, including finance, legal, and operations. Developing strong communication skills and business sense is far more valuable than mastering specific coding languages. Gaining broad experience, such as managing budgets or working in cloud engineering, can provide the highly valued background that modern employers expect. Additionally, finding experienced mentors and maintaining a genuine curiosity for new technologies will naturally foster leadership growth. Security professionals are advised to present themselves with calm confidence, take ownership of their mistakes, and avoid being overly rigid about their long term career paths. By focusing on delivering meaningful impact and collaborating effectively in their current roles, aspiring executives can position themselves for the transition from technical expert to trusted business leader.


Enterprise AI Security: ChatGPT, Claude, Gemini and Copilot Compared

As artificial intelligence tools transition from experimental chatbots to integrated enterprise solutions, businesses face new security challenges. Platforms like ChatGPT, Claude, Gemini, and Microsoft Copilot now connect directly to internal emails, cloud storage, and code repositories, shifting the primary risk from external data leaks to internal data exposure and unauthorized actions. No single platform is perfectly secure, as each presents unique vulnerabilities. For ChatGPT, the main governance gap lies between secure enterprise accounts and the personal accounts employees might still use. Claude’s agent capabilities pose a different risk: because it can execute commands and modify code, overly broad permissions could lead to unintended software changes. Meanwhile, both Gemini and Microsoft Copilot respect existing workspace access controls, but they act as powerful search engines that expose years of accumulated, poorly managed permissions. They do not bypass security rules, but they make forgotten, overshared documents instantly discoverable to employees. Additionally, all platforms face the threat of prompt injection, where hidden instructions in external files manipulate the AI. To safely adopt these tools, organizations must clean up internal access permissions, separate consumer from enterprise usage, define clear data retention policies, and strictly monitor what internal systems the AI can currently access.


Why AI shouldn't be the one repairing your data pipelines

As organizations expand their use of autonomous artificial intelligence systems to make operational decisions in real time, the traditional concept of self-healing data pipelines is no longer sufficient. While modern cloud architectures can quickly replace failed components, data failures in complex enterprise environments rarely present themselves as complete systemic crashes. Instead, these issues manifest as silent degradation, such as undocumented changes in source systems, misaligned business logic, or untrackable errors that compromise downstream models and regulatory reports. To support advanced business operations, engineering leaders must transition from reactive, automated repairs to autonomous data governance and resilient infrastructure. A critical component of this shift involves prioritizing deterministic solutions over heuristic guesswork. While artificial intelligence is highly effective at detecting anomalies and triggering alerts, relying on automated scripts to guess how to fix crucial records risks introducing synthetic errors into auditable systems. Rather than letting artificial intelligence independently repair data pipelines, organizations should pair machine learning detection with predefined, policy-driven workflows that isolate problems and apply historical fallback logic. By treating data reliability as a core business risk and building systems that actively defend and remediate quality issues in real time, enterprises can establish a secure foundation for their critical operations.


When security creates friction, employees find workarounds

When workplace security measures become too complicated or time-consuming, employees often look for easier ways to get their jobs done. According to a recent report, forty percent of workers globally admit to using unauthorized personal devices or applications when official technology fails them. In the Asia-Pacific region, this problem is particularly noticeable, with many staff members turning to unapproved platforms like public AI tools just to meet deadlines or respond to customers quickly. While these workarounds usually stem from a genuine desire to be productive rather than malicious intent, they create significant risks because organizations cannot secure or govern activity that they cannot see. This phenomenon, often called "shadow AI," highlights a disconnect between security rules and everyday operational needs. Instead of just blocking unapproved tools, leaders should view these behaviors as a clear signal that current systems are causing too much friction. The most effective way to reduce this hidden risk is to integrate security naturally into daily workflows. By prioritizing user experience and making the secure option the easiest one to use, companies can better protect their data while still empowering their teams to work efficiently.


BRICS digital sovereignty meets the interoperability test

The recent New Delhi BRICS Declaration sets forth an ambitious vision for technology that attempts to balance national control with global connectivity. The core challenge outlined in the document is how member nations can achieve digital sovereignty and self-reliance without sacrificing the interoperability that modern networks require. Rather than proposing a disconnected or isolated tech ecosystem, the declaration emphasizes building strong, nationally controlled digital public infrastructure (DPI) that can securely communicate across borders. This balancing act applies across several layers of technology. For DPI, it means countries maintain control over their own identity and data systems while ensuring they can interface with others. For physical infrastructure, the focus is on developing resilient submarine cables to reduce reliance on external entities, though the exact technical details remain under review. In terms of future technology and supply chains, the group is pushing for collaborative research and common, globally interoperable security standards. Ultimately, the declaration suggests that true digital sovereignty isn't about isolating a nation's network, but rather participating in global digital systems without becoming overly dependent on outside suppliers or infrastructure. The success of this vision will depend heavily on the upcoming technical and engineering decisions.


Why Data Governance Still Isn’t Driving Better Decisions (or Transformation)

Many organizations have invested heavily in data governance, setting up dedicated offices, policies, and committees. Despite this, the actual business impact often remains elusive. Compliance is still a manual process, and decisions are frequently made using data of uncertain quality. The core issue is that while data governance manages data, it often fails to govern the decisions that data is supposed to inform. This disconnect is a flaw in both the design and deployment of current governance models. For years, the standard approach has been to identify critical data, assign ownership, and implement controls, largely driven by regulatory requirements like GDPR. While this model has improved awareness and traceability, it often falls short of delivering measurable business value. Data offices struggle to prove their return on investment, and business teams may bypass governance processes that they feel slow them down without offering real benefits. The initial focus on inventorying and controlling data made sense as a starting point. However, these are backward-looking control systems. To truly drive business performance, data governance needs to evolve from merely a control mechanism into a forward-looking decision system that actively supports and prepares organizations for future actions.