AI agents are tapping into APIs: is governance ready?
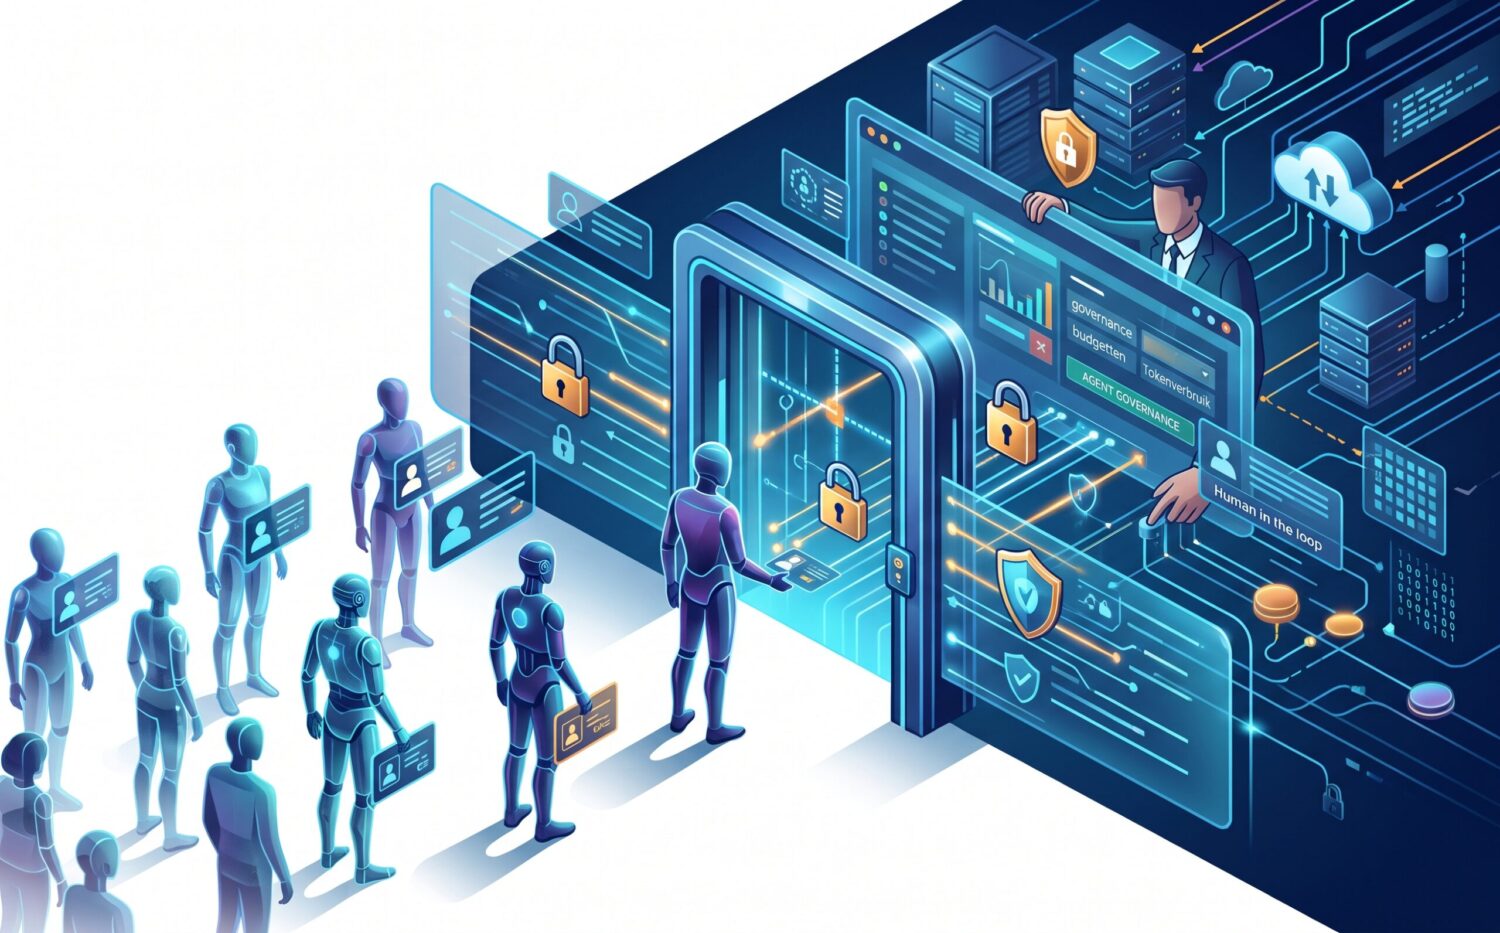
As artificial intelligence agents increasingly gain direct access to business applications and APIs, organizations face a major challenge in maintaining proper IT governance. According to Hans Bot, an enterprise architect at Yenlo, businesses must fundamentally update how they control these digital entities. Because agents now act independently on behalf of users, standard access controls are no longer sufficient. If unmanaged, these "shadow agents" can gain excessive permissions across a network, creating significant security risks. To solve this, Bot argues that every AI agent requires a distinct digital identity and credentials, much like a human employee. This allows systems to properly authenticate the agent, define the scope of its actions, and revoke its access when no longer needed. Additionally, traditional API gateways are inadequate for monitoring agents because agents exhibit behavior and consume resources rather than just passing data. This shift demands specialized management tools to evaluate an agent's effectiveness, track its usage, and implement conditional authorization for critical tasks. Ultimately, organizations must treat AI agents as an independent digital workforce that requires careful supervision and secure lifecycle management.
The Invisible Threat: Understanding the Hidden Risks of AWS Supply Chain Attacks
Amazon Web Services powers countless business operations, but relying on third-party tools and open-source software introduces hidden vulnerabilities. Supply chain attacks occur when cybercriminals infiltrate an organization’s cloud environment by compromising these external connections rather than attacking the core infrastructure directly. Even if internal security is remarkably strong, a flaw in a trusted external package or development pipeline can easily give attackers a foothold. Once inside, they can escalate privileges, move laterally across systems, expose highly sensitive data, or severely disrupt applications. A recent incident involving the data platform Qubole showed how attackers actively exploited outdated cross-account permissions to secretly access customer cloud environments and steal information. Preventing these invisible threats requires a critical shift in focus well beyond the immediate cloud setup. Organizations must actively manage their entire software supply chain by maintaining a complete inventory of software components, continuously monitoring third-party behavior, and enforcing strict access controls. Regularly reviewing permissions, securing deployment pipelines, scanning workloads for weaknesses, and evaluating vendor security practices are essential steps to ensure external connections never become the weak link in your infrastructure.
The FIPS Fallacy Behind Classified Data Protection
As artificial intelligence and connected operations push vast amounts of classified information to field devices, the risk of losing sensitive data has escalated. A dangerous misconception has emerged among security officials who rely solely on FIPS-certified encrypted drives to protect classified data at rest. While these drives meet federal standards for encryption, they only validate the cryptography itself, not the security of the overall system. If an adversary captures a device, encryption alone cannot prevent access without robust authentication measures. True data protection requires a combination of encryption and independent authentication layers, ensuring that physical possession of a device does not mean access to its contents. The National Security Agency has already outlined a comprehensive architecture for this through its Commercial Solutions for Classified program. In the past, cost and complexity deterred widespread adoption of these solutions, but today, this technology is readily available and competitively priced through standard defense suppliers. With clear policy direction and accessible technology, organizations must move beyond the false security of basic encryption and implement complete data protection architectures before a lost device turns into a national security incident.
Cybersecurity Has a Resolution Problem. Exposure Debt Is the Proof
For years, the primary goal in cybersecurity was finding vulnerabilities before attackers could exploit them. Thanks to better tools and artificial intelligence, security teams are now discovering system flaws at an unprecedented speed and scale. However, this success has created a new operational problem: organizations simply cannot fix these issues as fast as they find them. Even though teams are resolving problems quicker than before, the sheer volume of new findings is causing massive backlogs. This growing pile of known but unfixed vulnerabilities is known as exposure debt. Every unresolved issue sitting in a queue represents a real risk that attackers, who are also using artificial intelligence to speed up their own capabilities, can exploit. While improving discovery methods remains important, finding a flaw is effectively meaningless if it stays open indefinitely. Organizations need to consciously shift their focus and resources toward the later stages of the security process. By investing in better validation, clear ownership, and faster engineering responses, security leaders can ensure they are actually reducing their overall risk rather than just adding to a constant list of problems to solve.

You’ve decided to repatriate cloud workloads. Now what?
After years of shifting operations to the cloud, many organizations are now moving workloads back to their own facilities or shared data centers. This shift is not a rejection of cloud computing but a necessary rebalancing to create blended environments. Companies are making this move to regain control over security, navigate data privacy rules, and reduce the hidden costs of moving large amounts of data. Artificial intelligence applications, in particular, are returning to local servers to protect sensitive information and manage expenses. However, bringing operations back in-house introduces major hurdles. Companies face severe shortages in physical space and power capacity, making it difficult to house new equipment. They must also untangle complex networks and redesign applications that were originally built for specific cloud platforms. Furthermore, there is a significant skills gap, as many teams have lost traditional hardware expertise over the last decade. To succeed, leaders must secure physical space early and design their networks to seamlessly connect across multiple environments. They should also maintain an automated, user-friendly experience while investing heavily in training their staff to manage both physical and digital infrastructure effectively.
Maintainers don’t need more AI bug reports. They need fixes.
Open source software maintainers are currently overwhelmed by a flood of automated, poor bug reports generated by artificial intelligence. Rather than helping, these raw findings create unnecessary work, as developers must sift through false positives and duplicates to find real issues. To solve this, GitHub and Microsoft recently partnered on a pilot program called Codename MDASH, designed to rethink how artificial intelligence assists developers. Instead of simply dumping raw scan results on project leaders, the program used a careful, layered process. First, an automated system scanned six widely used open source projects to flag potential vulnerabilities. Next, an intelligent triage tool filtered out duplicates and irrelevant alerts. Crucially, human security researchers then reviewed every remaining finding by hand. As a result, the thousands of initial alerts were narrowed down to just 99 verified, private reports, each including a suggested patch. This approach worked well. By receiving a clear fix rather than a vague warning, maintainers were able to resolve more than half of the issues rapidly. The pilot demonstrates that artificial intelligence is most valuable when it provides verified solutions rather than just pointing out endless potential problems.
What IT Teams Can Learn From OT About Store Security
Recent cyberattacks on European supermarket refrigeration systems highlight a major security gap in retail: connected store equipment often lacks clear ownership. Devices like refrigeration controllers often fall into a gray area between facilities teams, IT departments, and external contractors. Because no single group owns the risk, these systems frequently run on outdated firmware and escape standard IT security checks. When attackers access these systems through exposed web interfaces, the results are devastating, leading to spoiled inventory, fires, and complex operational recovery. IT leaders can address this by adopting the Purdue model, an approach long used by operational technology (OT) teams to segment networks into distinct layers. Instead of allowing direct internet access to critical hardware, this model ensures each layer only communicates with its immediate neighbors. By combining this tiered structure with zero-trust principles to strictly manage third-party and contractor access, retailers can drastically reduce their exposure. The first practical step is simply identifying what equipment exists, who owns it, and ensuring it is no longer directly exposed to the internet.
New security needs emerge as physical access threats surpass cybercrime concerns at data centres for the first time
For the first time in nearly a decade, data center professionals are reporting that physical and human threats have finally surpassed traditional cybercrime concerns like ransomware. The explosive growth of artificial intelligence has completely transformed these facilities into high-value targets, housing critical multi-million-dollar hardware and blurring the line between physical and digital security. Insiders, whether acting with malicious intent or simply making negligent mistakes, pose the absolute greatest risk because they already possess valid access credentials. Their routine actions can easily blend in with normal daily tasks, making them very hard to detect and incredibly costly when data breaches actually occur. To directly address this growing issue, facility operators are now rapidly adopting advanced physical security measures, such as continuous biometric tracking and strict entrance controls, to verify human identity throughout an entire site. This shift is also heavily driven by the urgent need to protect essential supporting infrastructure, like water cooling and renewable energy systems, which are increasingly vital for high-density computer workloads. As new regulatory frameworks continue to tighten globally, organizations must actively integrate their physical and digital security strategies to ensure comprehensive resilience against all vulnerabilities.

Putting AI in a Cage: The Architecture of Controlled Intelligence
As artificial intelligence systems evolve from simple text generators into capable agents that can interact with APIs, modify files, and execute tasks, our approach to security must shift from focusing solely on the model to securing the entire architecture around it. An AI model is merely the reasoning engine; the real risk lies in the authority and tools granted to it. To safely harness these capabilities, we must place AI in a controlled environment built on seven essential layers: a replaceable model for intelligence, orchestration to coordinate tasks, strict least-privilege permissions, isolated execution environments like sandboxes, independent validation to verify outcomes, comprehensive observability to track actions, and human control for high-stakes decisions. By separating a system’s raw capability from its granted authority, we prevent issues like prompt injection and excessive agency from turning minor mistakes or malicious inputs into catastrophic failures. The ultimate goal is not to maximize an agent’s autonomy at the expense of safety, but to design a structured, verifiable workspace where it can perform useful work while remaining securely contained and accountable.

17 Human Capabilities Leaders Should Prioritize In The AI Era
As artificial intelligence takes on more technical and operational tasks in the workplace, smart leaders are shifting their focus to uniquely human skills that technology cannot replicate. Rather than just relying on algorithms to generate data and answers, employees must use their own judgment to interpret results, question assumptions, and make sense of ambiguity. To thrive in the AI era, leaders should prioritize developing skills like critical thinking, proactive accountability, and emotional intelligence within their teams. Empathy remains essential for building trust-based relationships, while the ability to manage conflict and disagree constructively ensures that human insight catches what algorithms might miss. Furthermore, teams need to cultivate the capacity for strategic application and discernment, shifting their value from merely producing information to evaluating it wisely. While AI accelerates speed and efficiency, it requires humans to supply context, ethical judgment, and creative problem-solving. Ultimately, the integration of AI in everyday work makes our ability to connect, lead, and think critically more important than ever for driving long-term business success.