Showing posts with label privacy. Show all posts

Daily Tech Digest - October 12, 2026


Quote for the day:

“In programming the hard part isn’t solving problems, but deciding what problems to solve.” -- Paul Graham

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


When Banks' AI Agents Meet Customers' AI Agents
Artificial intelligence agents are rapidly transforming the banking sector, operating on both sides of financial transactions. Banks are deploying AI internally for customer service, fraud detection, risk management, and operational tasks. Simultaneously, customers are beginning to use their own AI agents to shop, negotiate, and execute payments. This convergence creates a significant new challenge for financial institutions: establishing trust and clear lines of authority when machines interact with other machines. Federal Reserve Board member Christopher Waller recently highlighted this issue, pointing to authentication, liability, and fraud as the primary obstacles in agentic commerce. Despite the uncertainties, banks are actively implementing these technologies. For instance, LHV Bank in the U.K. recently deployed agentic AI for customer emails, emphasizing the need for strict guardrails, explainability, and human oversight. Similarly, JPMorgan Chase has nearly 1,000 AI use cases in progress, though CEO Jamie Dimon noted that the primary benefits will likely flow to the customer rather than uniquely boosting the bank's profit margins. As AI spending accelerates, institutions like BNY are even treating these AI systems as "digital employees" with specific identities and access controls. Ultimately, the banking industry must carefully balance rapid innovation with necessary caution and regulatory compliance.


Why Pull Requests Should Review Tests, Not Just Code

An article by Eli Lopian in Software Testing Magazine emphasizes the critical need to review test scripts just as rigorously as production code during pull requests. While development teams heavily scrutinize implementation code for architecture, security, and maintainability, the accompanying automated tests often get a free pass as long as the continuous integration pipeline turns green. Lopian argues that a passing test isn't automatically a good test—it might duplicate existing coverage, depend too heavily on brittle mock configurations, or fail to verify meaningful behavior. Treating tests with a lower standard ignores the reality that test scripts are also code with their own maintenance costs and complexities. This dynamic is becoming more pressing with the rise of AI-assisted development tools, which can instantly generate dozens of tests. When test creation becomes cheap, the new bottleneck is identifying which tests actually add value rather than just inflating code coverage metrics. Ultimately, a bloated suite of fragile or redundant tests slows down CI pipelines and increases the maintenance burden when production behavior changes. The goal should be meaningful confidence in the software, not simply a higher volume of tests.


Why AI agents might not be right for you
While AI agents are highly popular for tasks ranging from writing code to engaging with customers, their unpredictable nature means they are not always the right tool for the job. Author Jason Bloomberg explains that AI agents rely on large language models, making them inherently non-deterministic. This unpredictability gives agents their unique ability to make decisions and adapt to changing inputs—a massive advantage for complex tasks like weather planning or IT incident mitigation. However, this same trait can lead to unexpected misbehavior or poor results. Bloomberg advises against using agents when traditional, deterministic software works fine, when absolute accuracy is required (like running payroll), or when mistakes could cause severe harm. To decide if an agent makes sense, organizations should calculate an "error budget" to understand the acceptable cost of failure. If the potential cost of an agent’s mistake outweighs the expected business benefits, it is better to rely on traditional software. Furthermore, Bloomberg warns that attempts to heavily govern and restrict AI agents to make them safer often strip away the very flexibility that makes them useful in the first place, suggesting they should be deployed selectively rather than universally.


The 7 biggest issues CISOs and security teams face today

Security leaders today face an increasingly complex threat landscape, driven largely by the rise of artificial intelligence, which has introduced novel attacks and expanded the attack surface. According to the article, CISOs are reshaping their strategies to address seven primary issues that dominate their agendas. First, they are shifting their focus from merely preventing breaches to prioritizing business resilience and rapid recovery in the event of an incident. Second, leaders must build security programs tailored precisely to their organization’s unique risks and resource constraints. Third, security teams are forced to rethink their entire approach for the AI era, using AI tools to fight AI-enabled threats. Fourth, securing the organization’s AI operations and infrastructure has become a critical mandate to prevent unauthorized use and govern agentic systems safely. Fifth, CISOs are grappling with a severe skills gap, requiring them to heavily invest in upskilling and professional development for their teams to keep up with cloud and AI security demands. Sixth, the sheer velocity of modern attacks requires agile, fast-moving security practices capable of responding in minutes rather than hours. Finally, despite these rapid technological shifts, security leaders must remain flawless in executing fundamental tasks like vulnerability management, identity protection, and endpoint security.


DPDPA privacy notice must enable informed consent, not clicks

Under India’s Digital Personal Data Protection Act (DPDPA), privacy notices must move beyond checking legal boxes to actually communicating clearly with users. According to Akshayy S Nanda, a partner at Saraf & Partners, many organizations currently draft dense, 12-page legal documents that practically force users to click "I agree" without genuine understanding. The law insists that consent must be informed, specific, free, and unconditional. To comply, organizations must stop using vague terms like "trusted partners" or "service improvement" and clearly detail what data is collected, why it is needed, who will see it, and how long it will be kept. A compliant notice should be tailored to its specific audience—whether rural internet novices or corporate executives—and offered in multiple languages. Furthermore, withdrawing consent must be as simple as giving it, without being buried in complex account settings. Bundling completely unrelated data uses into a single click is also no longer acceptable. Ultimately, a privacy notice should serve as an instrument of trust rather than just a legal defense. By prioritizing plain language and transparent communication, businesses can build stronger relationships with users while meeting their compliance obligations.


12 standout CIO skills every company wants

According to industry leaders, chief information officers (CIOs) looking to advance their careers must master seven fundamental skills beyond their core technical expertise. First, they need visionary leadership to drive innovation and directly improve business outcomes. Second, they must develop the business insights of a chief operating officer, understanding the company's full value chain to connect technology investments with measurable results. Third, strategic thinking is vital; CIOs must anticipate changing business needs and guide long-term digital transformations. Fourth, successfully managing the intense pressures of the role requires internal fortitude, which is built by handling difficult situations transparently and taking accountability for outcomes. Fifth, developing the financial acumen of a chief financial officer allows CIOs to effectively measure return on investment and speak the language of the C-suite, transforming IT from a cost center into a strategic partner. Sixth, CIOs need outcome orchestration talent, disciplinedly converting strategy into delivered value by exposing impediments early. Finally, strong communication skills are essential to translate complex technical concepts and bridge the gap between technologists and business leaders. Mastering these skills enables a CIO to become a stabilizing force and a transformative leader.


AI Agents Need Clear Limits Before They Take Action

An AI system that simply drafts a customer response presents a vastly different management challenge than one capable of sending the reply, updating records, and issuing refunds. While the former generates information for human review, the latter actively alters the business. This critical distinction should dictate how organizations approve AI projects, establish access controls, and evaluate outcomes. When deploying AI agents—software utilizing models to interact with tools and execute steps toward a goal—business leaders must determine the exact level of authority required for a specific task. Granting an AI system excessive access to information or tools might make for a flashy demonstration, but it significantly magnifies the consequences of potential errors. Instead, practical deployment demands a clearly defined operational purpose, strictly limited permissions, and robust mechanisms to identify and contain mistakes. Companies must recognize that external content processed by these models is not an internal business instruction, and models should not possess the ability to expand their own permissions. Rather than adopting a one-size-fits-all approach to AI risk, organizations should ensure that AI controls directly reflect the real-world consequences of automated actions, protecting confidential records, financial payments, and customer support channels from unchecked autonomous decisions.


AI and the False Promise of Intelligence Analysis

A recent incident in which a flawed artificial intelligence assessment nearly triggered a US military raid on a Chinese merchant vessel highlights the enduring need for human judgment in intelligence analysis. The AI system had incorrectly identified cargo as nuclear components for Iran by relying too heavily on digital data like satellite imagery and signal intercepts, broadly known as technical intelligence. Human analysts ultimately recognized the errors and aborted the mission just in time. This near-miss illustrates two major flaws in using artificial intelligence for defense work: its inherent tendency to reinforce existing human assumptions rather than challenge them, and its preference for easily processed digital inputs over slower, yet highly valuable, human intelligence. While artificial intelligence is increasingly essential for managing the vast amounts of information generated today and plays a central role in modern military operations and data sharing, it cannot operate safely on its own. The growing use of automated systems creates a paradox where advanced technology actually requires stronger human oversight to prevent dangerous groupthink, protect physical data infrastructure, and verify complex conclusions. Ultimately, the future of national security depends on carefully blending artificial and human intelligence rather than treating the technology as an independent or infallible solution.


Forward Deployed Engineers: The People Turning Enterprise AI Into Working Systems

A Forward Deployed Engineer (FDE) is a technical professional responsible for integrating AI models into real-world business workflows and existing systems to drive measurable outcomes. As AI models grow more capable, businesses face the complex challenge of making them function reliably within their unique environments, which often involve legacy applications, strict access controls, and inconsistent data. FDEs bridge this gap by working directly with customers to understand their constraints, design system architectures, build integrations, and deploy solutions from prototypes into production. Unlike traditional software engineers who focus on building general-purpose products, FDEs concentrate on solving specific operational problems and ensuring adoption. The role demands strong software engineering fundamentals, AI application skills, systems integration expertise, and a deep understanding of customer needs. FDEs must navigate ambiguity, prioritizing incremental progress and real-world feedback. In regions like India, with a strong base of enterprise implementation talent, the FDE role presents significant opportunities in sectors like finance, manufacturing, and Global Capability Centers, where complex workflows require sophisticated AI integration to achieve true operational benefits.


Geopolitics and the cyber resilience gap belong in your threat model

According to Akshay Joshi from the World Economic Forum, the cybersecurity landscape is shifting due to artificial intelligence, geopolitical tensions, and the industrialization of cyber fraud. In a recent interview discussing the Global Cybersecurity Outlook 2026, Joshi notes that chief executives now view cyber-enabled fraud as a greater concern than ransomware, with a vast majority of people experiencing it personally. This type of fraud erodes trust in the digital economy and requires a coordinated response across tech companies, financial institutions, and law enforcement. Artificial intelligence is changing the dynamic between attackers and defenders, moving cyber operations to machine speed. While AI presents new vulnerabilities, it also gives defenders tools to detect and respond to threats more efficiently. Furthermore, geopolitical instability is forcing organizations to rethink their security strategies, as digital infrastructure becomes a strategic target. Joshi also highlights a growing gap in cyber resilience between large and small organizations, largely driven by a lack of skills and resources. Smaller entities struggle to find the talent needed to protect their systems. To close this gap, there must be greater investment in foundational skills and shared capabilities. Effective security requires moving beyond basic compliance, with leaders treating cybersecurity as a core component of overall business resilience.

Daily Tech Digest - October 05, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale


Data Has No Passport: Why Global Privacy Governance Must Catch Up With AI

At the CruiseCon Privacy and AI 2026 event, Accenture privacy lead Adriana Antunes Winkler highlighted a growing challenge: while data moves globally and instantly, privacy regulations remain fragmented and bound by local jurisdictions. With around eighty percent of the world covered by varying data protection frameworks, companies often struggle to keep up. Winkler advised against building separate privacy programs for every new law, as this causes confusion and conflict. Instead, she recommended a strategy built on a common global foundation with specific local adjustments only where legally necessary. This prevents the burden of simply applying the strictest rules everywhere. Winkler emphasized that operational controls, not just written policies, are what actually protect privacy. These controls require clear ownership, testing, and proof of function. The rise of artificial intelligence complicates this further, as AI often infers new personal details rather than just storing collected information. She suggested focusing on the specific actions AI takes and the systems it accesses, treating it as a data map driven by actions. Ultimately, whether data crosses international borders, runs through AI systems, or eventually processes in orbital satellites, organizations must rely on a unified, adaptable governance system that manages common standards while addressing specific local requirements.


Crypto-Agility Distrust Readiness

When major internet authorities decide to stop trusting a flawed digital certificate, the resulting fallout can cripple the countless services relying on it. While technical bodies like browser developers excel at making the call to pull a failing root certificate, there is currently no coordinated national plan for what happens to the broader economy the morning after. Historically, isolated incidents have been contained, but the dual threats of rapidly advancing artificial intelligence and a forced timeline for quantum-safe encryption mean that widespread disruptions are becoming more likely. The blast radius of a sudden distrust event can vary wildly across different sectors, and responding effectively requires advance preparation rather than improvisation. To survive this accelerating risk, organizations must create reliable certificate inventories, designate clear response liaisons, and run tabletop exercises to test their readiness. On a larger scale, a designated national coordinator is urgently needed to connect technical decision-makers with the sectors facing the consequences. Ultimately, building true resilience requires organizations to eliminate single points of trust by adopting multiple issuing authorities and automating certificate lifecycles, ensuring they can pivot smoothly when a crisis hits instead of scrambling to rebuild.


Measuring AI With the Wrong Ruler

When evaluating artificial intelligence systems, getting caught up in grand labels distracts from what truly matters: reliability, cost, and fitness for the job. The technology industry often assumes that larger, more capable models are inherently better, but deploying a massive system for a straightforward task is wasteful and risky. It is very similar to dropping a race car engine into a riding lawnmower. Raw power without proper control or necessity only creates hazards. Instead of obsessing over raw machine intelligence, which mirrors our flawed fixation on human IQ scores, we should focus on building operational wisdom. This means designing tools that clearly understand context, respect their own boundaries, and know exactly when to seek human intervention. Historical missteps in automotive software, where complex features completely overwhelmed inadequate hardware, prove that mismatched computing power leads to frustrating failures for end users. To make better decisions, organizations need a practical measurement framework that strictly aligns system complexity with the actual criticality of the task. By focusing on calibrated computing, businesses can ensure they deploy software with verifiable competence. This thoughtful approach prioritizes restraint, safety, and hardware capacity over industry hype, ultimately resulting in technology that simply works properly for its intended daily purpose.


Should cybersecurity be nationalised?

The conversation around digital safety is gradually shifting from treating it as a private expense to recognizing it as a public good. While full government ownership is not currently under consideration, experts argue that the traditional model of individual corporate defense is no longer sustainable. Today, private companies are routinely expected to fend off sophisticated attacks from foreign nations, a task for which most lack the necessary resources. Small businesses are particularly vulnerable and they often become the weak link that exposes broader networks to risk. Because hardening the defenses of one company inherently protects the wider community, securing digital infrastructure shares clear parallels with public utilities like street lighting. This shared benefit naturally raises important questions regarding funding and accountability. The emerging consensus suggests a model where the state might fund security measures that are executed by private firms, ensuring broader protection without complete nationalization. As this policy debate unfolds, organizations must adapt by viewing their security practices not merely as an internal budget item, but as a core component of public trust and reputation. Moving forward, businesses should firmly anticipate stricter sector requirements and expect to demonstrate baseline security standards simply to operate within shared modern networks.


IT modernization: Still a make-or-break project for CIOs

IT modernization remains a vital, ongoing mission for CIOs, taking on renewed urgency as artificial intelligence reshapes the technology landscape. The rise of AI and natural language tools means that systems built just a few years ago, such as traditional reporting dashboards and specialized chatbot software, may already be obsolete. IT leaders are now approaching modernization and application rationalization with a business-first strategy, evaluating tools not by their age, but by the tangible value and flexibility they provide. Consolidating software limits wasteful spending, reduces unneeded complexity, and creates a clean data environment essential for advanced technologies. While moving to modern solutions can cut maintenance costs and limit security risks, CIOs face practical challenges, including upfront migration expenses, data extraction difficulties, and internal resistance to letting go of highly customized legacy systems. Some organizations are increasingly weighing whether to build internal tools using advanced coding assistants rather than paying long-term licensing fees for external software. Ultimately, IT modernization is no longer just about retiring old technology; it is a continuous process of aligning the company’s tech stack with fast-evolving business needs to clear a path for meaningful innovation and operational agility.


The Credential Layer Is Expanding Faster Than Security Teams Can See It

As software development accelerates, organizations face an enormous increase in the number of digital keys, passwords, and access tokens they must manage. These credentials now connect people, applications, and artificial intelligence tools to critical data. Because they are often scattered across cloud accounts, internal networks, messaging apps, and developer laptops, it is incredibly difficult for security teams to track them. Recent data shows a sharp rise in leaked secrets, particularly those tied to AI services, which have become a new frontier for access management. At the same time, cybercriminals are using specialized malware to target developer devices, aiming to steal the local access codes stored there. To protect against these threats, security teams cannot rely on outdated, periodic checks. They need constant, clear visibility into every credential across the organization. This means knowing exactly what access each key grants, who owns it, and whether it is still active. Only by building a complete and accurate inventory can teams effectively identify risks, remove exposed secrets, and stop future leaks from happening. Taking control of this expanding environment requires a calm, systematic approach focused on detection first, ensuring that organizations understand their vulnerabilities before attackers can find them.


Should the CISO role be split in two?

Over the past three decades, the chief information security officer role has expanded significantly from its strictly technical origins. Today, these professionals are tasked with broad, strategic responsibilities, including data privacy, regulatory compliance, artificial intelligence governance, and overall business risk management. As this heavy workload continues to grow and outpace available resources, some industry observers have debated whether the position should be divided into two distinct roles: one focused purely on technical defense and another dedicated to business risk and organizational resilience. However, leading experts argue clearly against splitting the job. Instead, they recommend confidently maintaining a single executive who holds ultimate accountability for the organization's cyber strategy and risk management. To help manage the immense daily operational demands, larger companies are increasingly relying on a dedicated deputy role, which also directly aids in succession planning. This balanced approach ensures that the primary security leader can successfully focus their energy on executive communication, financial planning, and aligning security measures with core business objectives. Ultimately, the position is maturing along a path very similar to that of the chief information officer. As the role becomes undeniably executive, these professionals must transition from being seen merely as technical experts to functioning as essential business partners.


Exploring AI Observability – Part 1: Why It Matters

Just a year ago, tracking how artificial intelligence operates was hardly a recognized technology field. Today, experts predict that by 2028, a large portion of organizations deploying these systems will rely on dedicated tools to oversee them. This shift is happening because the adoption of intelligent systems has grown much faster than our ability to properly govern them. Employees across companies are using a mix of approved and unapproved tools, while software teams are actively building language models directly into their applications. This rapid expansion creates an urgent need for visibility to understand exactly where these tools are running, how well they perform, what they cost, and if they actually deliver real value to the business. The conversation is no longer just about how fast we can build these systems, but rather whether we can run them reliably in real world settings. Because modern systems can sometimes produce varying results from the exact same input, errors can quickly add up. Proper oversight is necessary right from the development phase to trace interactions, identify failures, and improve accuracy. In production, this oversight ensures that the behavior of intelligent tools connects smoothly with overall application health, resilience, and a solid user experience.


The Platform Engineering Playbook for Production LLMs

According to a case study on an inventory accuracy platform, scaling large language models (LLMs) requires treating the AI stack as platform infrastructure rather than a mere application feature. The engineering team successfully reduced production hallucination rates from fifteen percent down to just 1.5 percent without altering the foundation model itself. They achieved this by implementing an automated retry loop to catch formatting and grounding errors on the fly, alongside an intent-validation gate that defaults to "unclassified" to prevent off-intent responses. Additionally, prompt management was shifted to a history-preserving registry rather than hardcoding instructions, allowing runtime updates with a clear audit trail to prevent silent behavioral breaks. The authors also highlight critical security and observability practices for enterprise AI. They strongly recommend enforcing tool authorization directly at the resource server with a strict default-deny policy, warning that relying solely on API gateways can expose tools due to a single orchestrator bug. Furthermore, since traditional application performance monitoring tools cannot detect semantic degradation or silent output drift, teams must proactively instrument hallucination rates and per-team token costs right at request ingress to avoid costly retrofitting later.


Three questions a hospital CISO should ask a healthcare fintech vendor

In a recent interview with Help Net Security, Drew McCombs, CTO and CISO at Cylerity, discusses his approach to balancing security with development in the healthcare fintech sector. McCombs ensures that security is integrated into every development sprint rather than treated as an afterthought. When conflicts arise, any issue affecting patient data or funds disbursement takes priority. He notes that while Cylerity is not a bank, it must satisfy the compliance expectations of its banking partners without violating HIPAA regulations. To achieve this, the company minimizes data sharing and uses custom identifiers to keep protected health information (PHI) completely separate from financial reporting. When discussing artificial intelligence, McCombs insists that AI models should only recommend or flag information, with a human always making the final decision to prevent errors from gradual model drift. For small medical practices, he emphasizes that turning on multi-factor authentication (MFA) for email is the cheapest and most effective security fix available. Finally, McCombs advises hospital CISOs to scrutinize fintech vendors by asking about their data subprocessors, their protocols for verifying fund destination changes, and their breach response plans, warning that a vendor claiming to be "HIPAA certified" is a major red flag since no such official certification exists.

Daily Tech Digest - September 15, 2026


Quote for the day:

“In times of change, learners inherit the earth; while the learned find themselves beautifully equipped to deal with a world that no longer exists.” -- Eric Hoffe

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


Why DBAs are right to be skeptical of AI — and where they’re wrong

Database management has grown significantly more complex over the past three decades, turning scalability into an expertise problem rather than a simple staffing issue. Adding more database administrators (DBAs) to a struggling system rarely resolves performance problems; instead, organizations need experienced professionals who can accurately diagnose root causes. However, skilled DBAs are expensive and increasingly scarce, especially as the demand for massive databases supporting artificial intelligence and large language models (LLMs) continues to rise. This is where AI tools can provide meaningful support without replacing human expertise. While human operators are prone to making assumptions or taking risky shortcuts under pressure, properly constrained AI models excel at following defined diagnostic processes consistently. By providing an LLM with read-only access to monitoring data and clearly structured instructions, teams can compress hours of manual log analysis into mere minutes. The key to success is establishing strict guardrails around what the AI can execute. The model diagnoses the issue and proposes a solution, but a human administrator retains full control over approving and applying any changes to the live database. Starting with this low-risk approach allows organizations to manage growing complexity effectively while the industry slowly builds broader trust in autonomous operations.


Sovereign cloud is no longer just about where data resides

The concept of a sovereign cloud is evolving far beyond simply keeping data within a country's borders. According to Ravi Jain from IBM India, true digital sovereignty is fundamentally about control rather than just physical location. As artificial intelligence becomes deeply integrated into everyday operations and modern business systems, organizations are asking harder questions about who manages their environments, who holds the encryption keys, and where their AI models actually run. This shift is rapidly moving the conversation from basic data residency to comprehensive AI sovereignty. Regulated sectors in India, such as government, finance, and healthcare, are increasingly viewing this level of operational control as a core architectural requirement. However, Jain notes that not every system needs the same level of strict oversight. Instead of a one-size-fits-all approach, technology leaders should assess their systems individually, applying tighter controls only where data sensitivity and business risks truly demand it. Ultimately, organizations want the freedom to place their systems across various environments without becoming locked into a single technology provider. By focusing on operational independence and transparent governance, businesses can maintain strict control over their most critical assets while still retaining the flexibility needed to operate efficiently and confidently in the future.


AI Changed the Exposure Problem. Validation Needs to Change With It

As artificial intelligence accelerates the discovery of security vulnerabilities, security teams face a rapidly growing number of reported exposures. Although published vulnerabilities have increased significantly, only a small fraction are actually exploited in the real world. This widening gap means that relying entirely on traditional severity scores is no longer an effective strategy, as these scores fail to account for a network's unique environment and active defensive controls. While automated penetration testing provides valuable insights, it has limitations. It cannot safely test all critical business systems and requires an existing exploit to function properly. To adapt, security professionals need a more comprehensive approach to vulnerability validation. This involves combining exploitability validation, security control testing, and agentic penetration testing into a single unified workflow. By integrating these methods, organizations can accurately determine which vulnerabilities pose a genuine threat to their specific infrastructure, even when standard exploits are not yet available. This unified strategy allows security teams to prioritize real risks over theoretical ones and focus their remediation efforts where they matter most. Industry leaders will further explore this practical approach to modern security validation during the upcoming Picus Security Validation Summit, demonstrating how mature enterprises are adapting to the changing threat landscape.


What Capital Markets Can Teach Enterprises About Integrated Data Infrastructure

Capital markets can teach enterprises a lot about setting up integrated data infrastructure. For over a decade, capital markets have been combining technology, analytics, and data into a unified structure to give them a competitive edge in pricing and trading. To do this, these firms need to handle large amounts of data very quickly and with high accuracy. They do this by using a centralized data repository where they can clean and manage the data. They establish clear rules on how to manage and use the data. To ensure that everyone works together, they create data teams comprising both technical experts and business leaders. This ensures that the data is not only technically sound but also aligns with the business goals. For an enterprise, this means breaking down silos between departments and viewing data as a unified asset rather than a collection of separate pieces. It also means using new technology like cloud computing to better manage and analyze the data. Doing so can make it easier to adopt newer technologies such as AI and machine learning, which rely on having a solid foundation of data to work effectively.


Govern AI agents like workers. Just don’t pretend they’re human

As artificial intelligence agents become more capable of completing tasks across corporate systems, IT leaders face a new challenge in managing them. According to industry experts, the best approach is to borrow management techniques from human resources without pretending that the AI is actually human. While it makes sense to handle agents similar to new workers, giving them specific roles, supervision, and gradually increasing their freedom as they prove reliable, companies should never give them human names, personas, or official spots on the organizational chart. Doing so creates a false sense of trust and blurs the lines of responsibility. Unlike traditional software, these advanced programs can make their own choices to achieve a goal. This means they need strict oversight, technical identities for tracking their actions, and clear boundaries. Some leaders compare them to interns, where they start with basic tasks and need constant human approval before earning more independence. However, the most crucial rule is that accountability must always remain with human employees. An AI agent might have permission to access data and execute actions, but it lacks human judgment and corporate values. If a mistake happens, a human or a policy owner must be responsible, not the software.


Your employees are already using AI tools you never approved

According to a recent report on workplace technology, artificial intelligence is now widely used across most companies, with nearly three quarters of organizations adopting it in their daily operations. However, managing this rapid adoption safely remains a significant challenge for leadership. While many companies have established basic rules for artificial intelligence, only a small fraction have fully integrated risk management into their daily workflow from the very start. This lack of integration leads to frustrating issues with speed and consistency. A major concern is that employees frequently use unapproved tools because the official options take entirely too long to access, leading to unexpected security issues. Furthermore, as businesses increasingly encourage the use of autonomous programs, internal oversight struggles to keep pace. Data security, accuracy, and loss are the most prominent risks, and current review requirements frequently delay new projects. Despite these hurdles, businesses are actively trying to improve their safeguards. Teams are spending significantly more time managing these specific risks than they did just a year ago. To address these growing needs, nearly all surveyed organizations plan to increase their spending on oversight technologies in the coming year, focusing heavily on employee training, clearer rules, and continuous system monitoring.


Applying the roadmap: 3 common M&A scenarios

Managing physical security during mergers and acquisitions requires careful preparation and adaptable strategies to succeed over time. Security teams face different challenges depending on the current stage of the organization in the acquisition process. If a company expects future acquisitions, security leaders should begin by clarifying basic risk profiles, setting aside realistic budgets for system integrations, and organizing their internal teams to make future transitions easier. When an acquisition is actively happening, the focus shifts to maintaining clear communication with the planning committee, identifying key experts within both organizations, and conducting a thorough inventory of current security assets. For companies that are constantly acquiring others, achieving true standardization across all systems might be impossible. Instead, these organizations should focus on maintaining a strong core incident response plan while managing a variety of everyday technologies. In this perpetual cycle, it is strictly critical for security leaders to remain visible, communicate realistic timelines, and ensure their functional value is well understood. Ultimately, involving physical security early in the process and building flexible plans helps reduce risks and ensures that daily operations continue smoothly during any transition. By staying organized and calm in their approach, security teams can effectively support the lasting growth of the company and create a unified program.


AI inferencing is headed for the network edge

Recent advancements in hardware and software are accelerating the shift of AI inferencing from centralized cloud data centers to the network edge, making 2026 a pivotal year for this transition. As the volume of data generated by billions of connected devices continues to surge, organizations face mounting pressure to process information locally. Key drivers for this shift include the high cost of transporting massive datasets to the cloud, the need for immediate responses to minimize delays, and strict data privacy rules that demand localized control over sensitive information. Technological breakthroughs are making this possible. Smaller AI models and highly efficient processing chips allow complex operations to run directly on devices without draining power. Consequently, analysts predict that by 2030, half of all enterprise AI inference workloads will run on edge nodes. This capability is unlocking practical applications across industries, from instant quality control in manufacturing to autonomous agricultural equipment and advanced pedestrian safety systems. While the industry currently faces hurdles such as deployment complexity, capital costs, and a fragmented vendor landscape, the overall trajectory remains clear. The edge AI sector is expected to grow significantly faster than the broader AI market over the course of the next few years.


Meta’s smart glasses privacy defense falters when AI can use camera without recording light

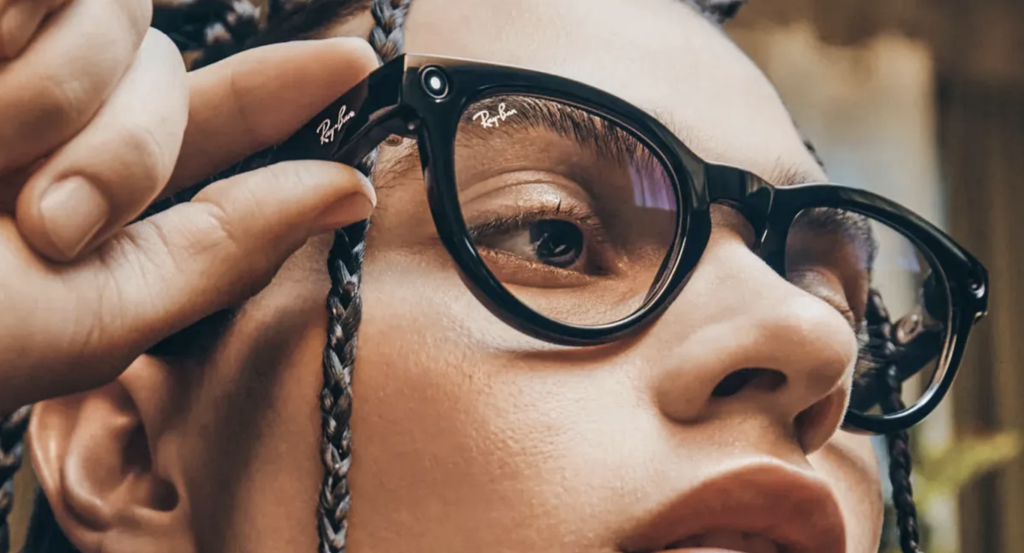
Meta's smart glasses rely on a visible LED light to warn bystanders when a user takes a photo or records a video. The company defends this safeguard aggressively, even disabling devices if the light is tampered with. However, a significant privacy issue has emerged because this indicator does not illuminate when the glasses use camera-based artificial intelligence features. According to company documentation, if a wearer asks the AI to identify a landmark or an object, the camera captures an image for machine analysis without turning on the warning light. Meta argues these images are processed by the AI rather than saved to a personal gallery, but this technical distinction is sparking legal and regulatory pushback. In the United States, class-action lawsuits have expanded to include bystanders who allege their information is collected without their consent. Meanwhile, European regulators are considering stricter rules, including potential bans on public facial recognition features for consumer eyewear. Additionally, American law enforcement agencies have issued warnings about the security risks of civilians using the glasses to secretly record police operations, even as some departments begin using the technology themselves. Ultimately, the invisible nature of AI analysis is exposing the limitations of relying solely on visible recording indicators.


What the 3M ChatGPT case reveals about AI governance

The Watson Grinding litigation involving 3M highlights a critical but often overlooked aspect of managing artificial intelligence: the legal discoverability of everyday user interactions. During the case, an engineering expert requested that ChatGPT show 3M as entirely blameless, and those prompts eventually became central to a deposition. This incident shows that organizations must look beyond simply controlling what data employees put into AI models and start actively managing the lifespan of the generated records. Currently, businesses focus heavily on preventing the accidental exposure of private information. However, AI prompts and chat histories can also preserve underlying assumptions, rejected alternatives, and lines of reasoning that never appear in a finished report. While keeping every prompt forever would create unnecessary security and privacy risks, organizations need practical rules based on the importance of the work being done. For high-stakes situations, companies should retain enough of the interaction history to accurately reconstruct how a specific decision was made. This requires clear collaboration between IT, legal, and compliance departments to establish steady retention and ownership protocols. Ultimately, the 3M case serves as a straightforward warning that companies must deliberately manage their AI footprints so they can confidently explain the tool's role if their decisions are later questioned.

Daily Tech Digest - September 05, 2026


Quote for the day:

"Success... seems to be connected with action. Successful people keep moving. They make mistakes, but they don't quit." -- Conrad Hilton

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Why is the Cloud Changing Again?

The rise of artificial intelligence is fundamentally changing how companies store and manage their data, moving the industry away from a one-size-fits-all public cloud model. Traditional cloud setups were excellent for standard web traffic and everyday software, acting like an efficient public transit system. However, artificial intelligence requires processing massive amounts of data at high speeds, which can cause severe delays and soaring costs on shared networks. To handle these heavy workloads, businesses are shifting toward a more specialized, decentralized approach. Additionally, because artificial intelligence learns from the information it processes, companies are increasingly concerned about the security and privacy of their sensitive data. This has driven a strong movement toward bringing data back home to private, local servers. Governments are also introducing stricter privacy laws, requiring companies to keep citizen data within their own national borders rather than storing it in global facilities. As a result, organizations are adopting a flexible strategy where they use public servers for everyday tasks, regional servers to comply with local regulations, and highly secure private servers for their most valuable information. This balanced method allows businesses to use advanced systems while maintaining strict control over their security, legal compliance, and digital assets.


Keeping OT security up to date is more than patching systems

Securing operational technology (OT) in industrial environments involves much more than applying simple software updates. As cyber threats against critical infrastructure like manufacturing and energy continue to rise, protecting these systems requires a fundamentally different approach than traditional IT security. While IT focuses primarily on protecting data, OT security must balance digital defense with real-world safety and continuous physical operations. Because large industrial systems often remain in active use for several decades, they cannot always be patched or upgraded as easily as typical office computers. Rather than relying solely on specialized technical controls, organizations must deeply understand their operational dependencies and gain completely clear visibility into their connected assets and third-party vendor access. Major disruptions frequently stem from basic weaknesses, such as poor network segmentation or compromised IT environments that spill over into industrial operations, rather than highly complex, sophisticated attacks. To build truly effective defenses, companies need strong internal governance that clearly defines responsibilities across engineering, operations, and security teams. Ultimately, organizations should view OT security not just as a narrow technical issue, but as a critical element of overall business resilience. By combining standard cybersecurity practices with deep industrial expertise, companies can protect their vital operations while successfully adapting to ever-evolving security risks.


Your R&D doesn’t need to be flashy

Software development teams often feel pressure to build flashy, highly marketable features to impress users. However, the most valuable research and development work usually happens entirely behind the scenes. While a brand-new interface button might make for a great product demonstration, real long-term user satisfaction depends on foundational elements like speed, reliability, and security. When software performs exactly as expected without delays or glitches, users can focus entirely on their work rather than fighting with the tool itself. Modern professionals, such as architects or engineers, rely on software to handle increasingly complex and automated tasks. If an application fails to execute a command accurately or compromises sensitive project data, the user's trust is instantly broken, and the financial consequences can be severe. This is why development teams must prioritize secure, reliable environments over cosmetic upgrades. By analyzing how people actually use the product, developers can identify the invisible improvements that truly matter, such as open standards that allow seamless collaboration across different platforms. Ultimately, the best software acts as a quiet partner, anticipating a user's needs and handling repetitive work so they can stay immersed in their creative flow.


Querying and Performing Transactions Across Multiple Database Schemas in a Modular Monolith

In a modular monolith, assigning a dedicated database schema to each module establishes strong boundaries but introduces significant challenges for querying data and managing transactions. Because direct database access between modules violates these boundaries, traditional approaches like joining tables across different schemas or relying on single database transactions are no longer viable. To solve querying issues, developers can use several strategies. The simplest method involves direct API calls, where modules communicate through public interfaces, ensuring strict boundaries despite potential performance compromises. For scenarios requiring faster reads, teams can rely on domain events to duplicate and denormalize data across modules, though this requires managing eventual consistency. Alternatively, database views allow developers to join tables across schemas at the database level, which is particularly effective for reporting purposes. Another strong option is the Backend for Frontend pattern, where a dedicated service aggregates data from multiple modules before sending it to the user. Handling transactions across multiple schemas requires a shift away from traditional methods. Instead of relying on a single commit, systems must utilize event driven architectures and patterns like sagas. While this approach ensures loose coupling, scalability, and resilience, it also introduces complexity by requiring compensating transactions and careful error handling to maintain data consistency.


Gmail labels: Your secret weapon against inbox chaos

Gmail labels provide a powerful and flexible alternative to traditional email folders, acting more like customizable tags that allow multiple categories to be applied to a single message. By mastering these tools, users can significantly reduce inbox chaos and streamline their daily communication. A great starting point is creating and color-coding various labels, then grouping them into parent and sublabel hierarchies to maintain a consistently neat sidebar. To save time during everyday tasks, you can proactively apply these labels while composing a new email or assign them simultaneously while archiving a read message. Labels also dramatically improve your ability to find old information; typing specific label operators directly into the search bar instantly narrows down vast results. Furthermore, users can fully automate their workflow by setting up custom Gmail filters. These filters automatically apply specific labels to incoming messages based on criteria like the sender's address or specific subject line keywords. This intelligent automation allows urgent emails to stand out immediately while quietly routing less critical messages away from your main inbox view. Finally, labels can be connected to custom notification settings, ensuring you only receive alerts for the messages that truly matter. By adopting these simple strategies, anyone can transform an overwhelming inbox into a highly organized system.


When cyber capability becomes abundant: Rethinking government cyber resilience

As artificial intelligence rapidly evolves, it is fundamentally changing the economics of cybersecurity for government agencies. Historically, sophisticated cyber operations required scarce, expensive human expertise. Today, AI has significantly reduced these costs, making powerful cyber capabilities widely available to both attackers and defenders. This shift creates unprecedented challenges for government agencies, which protect critical infrastructure and systems essential to national security, public health, and emergency response. Because attackers can now discover and exploit vulnerabilities faster than organizations can fix them, government security leaders are losing confidence in traditional defensive strategies. To adapt to this new reality, governments must rethink their approach to cyber resilience across operational and institutional levels. Operationally, agencies need to move away from trying to fix every single technical flaw. Instead, they must prioritize risks based on their potential impact on public missions. A moderate vulnerability in an emergency response system matters far more than a severe flaw in a low impact network. By translating technical data into real world operational context, governments can better focus their limited resources on protecting what truly matters. Ultimately, success requires agencies to rapidly reduce their exposure, contain breaches driven by artificial intelligence, and actively shape a safer overall cyber ecosystem.


Cyber resilience in the age of AI will be decided in the boardroom

As modern business innovation speeds up due to artificial intelligence, it also provides attackers with powerful new ways to disrupt operations. Companies have spent heavily on defensive software, but having more tools often creates confusing complexity rather than clear protection. Because automated threats move faster than ever, the true test of an organization is not whether it can prevent every single incident, but how well it handles a crisis when it happens. Cybersecurity is no longer just a technical issue meant for the information technology department; it is a fundamental business challenge that belongs in the boardroom. Company leaders must understand their critical digital dependencies and how a failure would impact revenue, reputation, and daily functioning. Security should be woven into every major business decision from the start, prioritizing clear processes over having the most complicated software. True resilience relies heavily on human behavior. An organization must build a culture where employees feel safe reporting mistakes, questioning unusual requests, and practicing response plans before an actual emergency occurs. Ultimately, survival during a digital attack depends on clear communication, decisive leadership, and the ability to keep essential services running smoothly and effectively, ensuring that trust and stability are maintained alongside technological growth.


How Differential Privacy Will Transform Enterprise Data Strategy

Differential privacy is quickly moving from a theoretical concept to a critical component of enterprise data strategy. While previous methods like encryption and de-identification have struggled to protect against re-identification as data volumes grow, differential privacy offers a mathematically proven way to guarantee that an individual's data cannot be reverse-engineered from broader analytical outputs. This technique is already being used successfully by major organizations, including the U.S. Census Bureau, Apple, Google, and Microsoft, and the market is projected to expand significantly by 2030. However, many business leaders mistakenly view this technology merely as a compliance tool. Its true value lies in unlocking data utility, allowing companies to safely share information across internal departments and with partners without exposing sensitive details. To succeed, organizations must understand that differential privacy is not a simple plug-and-play product, nor can it be retrofitted easily into existing pipelines. It requires a fundamental shift in how data is processed and governed. Experts advise companies to start with a single high-value use case, such as customer analytics, and prioritize building strong central governance before focusing on the underlying tooling. Adopting this approach now gives enterprises a significant competitive advantage in responsible data strategy.


What the AI Warning Letter Completely Missed

A recent warning from major technology companies highlights that artificial intelligence will soon make cyberattacks cheaper and more common, urging immediate action to strengthen defenses. While this threat is very real, the proposed solutions overlook the most critical component: the human beings required to do the work. The industry often focuses heavily on advanced tools and theoretical scenarios while ignoring the practical reality that defense depends entirely on skilled people. Every recommendation to improve security, whether it involves fixing weaknesses, reviewing code, or deploying new software, requires a trained operator. The gap in our current readiness is not a lack of software products, but a severe shortage of equipped personnel, especially within smaller organizations and local utilities. To truly prepare for emerging threats, companies must invest directly in the workers already managing these systems, teaching them how to secure their specific environments. Furthermore, technology providers should offer concrete, direct support rather than just access to software models. Defensive tools must be judged by how effectively a small, overworked team can actually use them during an emergency. Ultimately, technology alone will not secure our infrastructure against intelligent threats. True resilience requires betting on motivated, well trained people who are ready to handle the daily work of defense.


Why digital transformations still fail

Digital transformations continue to fail largely because companies let technology, heavily promoted by consulting firms, dictate their strategy rather than focusing on actual business needs. Consultants have consistently sold identical, prepackaged systems to maximize their own profits, completely ignoring the unique requirements of each organization. This approach has resulted in massive budget overruns, delayed timelines, and overly complex systems that fail to perform as promised. Instead of redesigning their processes, companies simply moved their existing problems onto expensive cloud platforms, increasing their costs without gaining any real benefits. Now, as the industry shifts its focus toward artificial intelligence, businesses are repeating these exact same mistakes. Organizations are rushing to add artificial intelligence to everything without a clear reason, while placing unqualified staff into critical design roles. To succeed moving forward, businesses must adopt a much simpler approach. They need to stop overspending on unnecessary computing power and invest heavily in proper foundational training for their internal teams. Ultimately, technology exists solely to serve the business. Any successful change must begin by identifying clear business requirements and working backward to find the most practical, cost-effective solution, rather than blindly purchasing the most complicated or trendy new software option available today.

Daily Tech Digest - September 02, 2026


Quote for the day:

“Make sure you don’t start seeing yourself through the eyes of those who don’t value you.” -- Anonymous

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


The next generation of CIOs will take a different path to the top

The role of the Chief Information Officer is experiencing a significant shift as artificial intelligence reshapes daily responsibilities and career trajectories. While previous tech leaders often climbed the ranks through help desks or database management, future leaders are increasingly likely to emerge from backgrounds in data governance or other business-focused areas. The speed and impact of AI mean that managing technology is no longer an isolated task; it requires extensive collaboration across the enterprise. Leaders must now navigate a blended workforce of human employees and digital agents while addressing new challenges like sudden cost increases and complex governance issues. Despite these rapid changes, the core mission of understanding company and client needs remains constant. Successful leaders must serve as strong communicators who can identify specific business pain points and implement effective solutions. Because AI introduces unique cultural and operational demands, building a secure and adaptable workplace is as crucial as the technology itself. This pressure may lead to shorter tenures or early retirements for some, while others might transition into emerging roles like Chief AI Officer. Ultimately, navigating this landscape requires a deep sense of curiosity and a steady focus on solving practical problems rather than simply chasing new trends.


Cybersecurity Risks Businesses Overlook and How to Address Them

Many organizations mistakenly assume that cybersecurity threats only involve sophisticated hackers and complex digital breaches. However, the reality is that most successful attacks exploit simple, everyday vulnerabilities that companies frequently overlook. A resilient defense does not require overly complicated tools; instead, it demands consistent attention to fundamental practices across technology, people, and processes. A primary risk involves employees relying on weak or reused passwords, a problem that is easily managed by enforcing multi-factor authentication. Similarly, human error remains a major target for social engineering and phishing emails, which makes ongoing staff training absolutely essential. Companies also create unnecessary exposure when they fail to apply important software updates or leave remote work devices unprotected. Furthermore, granting workers excessive access to sensitive information expands the potential damage of any single compromised account. A mature approach requires limiting these permissions to what each role actually requires. Organizations must also establish clear internal policies so employees understand their responsibilities. Additionally, companies should actively test data backups, evaluate the security standards of third-party vendors, and outline a specific plan for responding when an incident occurs. By addressing these foundational elements and paying attention to small warning signs, businesses can confidently reduce their exposure and protect their daily operations.


Why Enterprises Need AI FinOps, Security to Scale Responsibly

As businesses increasingly integrate artificial intelligence into their daily operations, the need to manage both the financial and security aspects of this technology has become vital. Scaling AI is not just about adding more computing power; it requires a disciplined approach to control costs and protect sensitive information. This is where the combination of AI FinOps and robust security measures plays a crucial role. Without proper financial oversight, the massive data processing and infrastructure requirements of artificial intelligence can lead to unpredictable and soaring cloud expenses. FinOps practices provide the necessary visibility and accountability, ensuring that technology investments deliver real value without breaking the budget. At the same time, expanding these advanced systems introduces complex new risks, making strong security protocols absolutely essential. Companies must defend their data models against emerging threats while ensuring compliance with evolving regulations. Relying on specialized security frameworks allows organizations to identify vulnerabilities early and maintain trust with their users. By uniting financial operations with strict security standards, enterprises create a sustainable foundation for growth. This balanced strategy ensures that companies can innovate responsibly, maximizing the benefits of advanced technology while carefully minimizing financial waste and preventing dangerous data breaches.


Enterprise Architecture in the AI Era: Tools, Capabilities, and the Road to Autonomy

An enterprise architecture (EA) tool serves as a centralized platform that helps organizations map and manage their business strategies, capabilities, applications, and technology infrastructure. Traditionally, these tools have faced significant challenges, including poor data quality, complex manual processes, siloed information, and resistance from non-IT stakeholders who struggle to see their value. To overcome these limitations, next-generation EA tools are evolving rapidly to incorporate artificial intelligence and automation. These advanced capabilities, such as AI-driven copilots, automated architecture documentation, and intelligent portfolio rationalization, allow architects and stakeholders to interact with enterprise data using natural language and receive automated insights. By embedding AI, these platforms can seamlessly link business goals with technology decisions, optimize technology investments, and streamline governance processes. The ultimate goal of a modern EA tool is to provide a single, dynamic source of truth that clarifies the complexities of an organization. This clear visibility enables business leaders to make informed decisions, reduce technical debt, and adapt quickly to changing market conditions. As these tools mature, they bridge the gap between business and IT, paving the way for more autonomous, resilient, and alignment-driven enterprise transformations.


Why IoT Services Are Becoming Critical Infrastructure for Enterprise Deployments

The global Internet of Things services market is no longer an experimental phase for businesses, as it is projected to grow from $285 billion in 2025 to over $1.4 trillion by 2034. Organizations are deeply embedding these technologies into their daily operations, transitioning from simple pilot programs to relying on them as essential infrastructure. Companies now depend on connected devices, management platforms, and data analytics to run everything from factories and supply chains to city utilities and healthcare systems. Instead of building systems internally, enterprises increasingly prefer managed services to handle device operations, security, and updates. Industrial applications remain a major growth area, driven by smart factory initiatives and predictive maintenance that significantly cut equipment downtime and costs. However, scaling these systems across entire organizations remains challenging, requiring strong operational discipline and process integration. Geographically, the Asia-Pacific region leads the market and continues to grow the fastest, while North America and Europe see demand shaped heavily by regulations. Ultimately, these services are becoming a distinct procurement category for businesses, where success depends not just on connecting devices, but on the management layers that ensure secure, compliant, and reliable operations.


SaaS, Cloud, and AI Contracts: Where Technology Leaders Lose Leverage

Technology leaders often find themselves at a disadvantage during contract negotiations for software subscriptions, cloud infrastructure, and emerging artificial intelligence tools. When purchasing these services, organizations frequently lose their negotiating power by failing to align their technical requirements with their procurement strategies. Vendors often structure their agreements to lock customers in, using complex pricing models, auto-renewal clauses, and ambiguous terms regarding data ownership and security. Because cloud and AI environments are highly specialized, IT directors and executives might focus too much on the technical features while overlooking the long-term financial risks and compliance obligations. As a result, companies can easily overspend on resources they do not actually use or face unexpected price increases when renewing their agreements. To regain control, technology leaders must collaborate closely with legal and financial departments early in the purchasing process. By clearly defining their usage needs, establishing firm exit strategies, and scrutinizing service level agreements, businesses can protect themselves from vendor lock-in. Maintaining this leverage requires a disciplined approach, where companies actively monitor their software consumption and prepare alternative options well before contracts expire. Ultimately, careful planning allows organizations to maximize the value of their technology investments without sacrificing their operational independence or budget predictability.


What is transformational leadership? A model for motivating innovation

Transformational leadership is a management approach that inspires employees to drive innovation and adapt to ongoing change. Instead of relying on strict rules, rewards, or punishments, these leaders guide by example, building a workplace culture rooted in trust, autonomy, and a shared sense of purpose. According to the model's foundational framework, this style involves four key elements: acting as a positive role model, challenging traditional thinking to spark creativity, motivating teams around a unified corporate vision, and providing personalized mentorship to help individuals grow. By giving trained staff the independence to make their own decisions, leaders avoid micromanagement and actively encourage proactive problem-solving. This approach proves especially valuable in fast-paced fields like technology, where adapting to new tools and shifting trends is essential for long-term survival. While it contrasts sharply with the structured, routine-heavy nature of standard transactional management, the transformational method yields significant real-world benefits, including higher job satisfaction, stronger staff retention rates, and a much healthier overall work environment. However, organizations must remain mindful of potential drawbacks, such as team burnout or an unhealthy over-reliance on a single charismatic figure. Ultimately, this leadership style successfully empowers individuals to take genuine ownership of their work and shape future success.


Informing Stakeholders Isn’t the Same as Aligning Them

Many teams confuse sharing information with achieving true alignment, a lesson one author learned the hard way during a major app redesign. Despite running discovery sessions, sending emails, and posting updates, stakeholders were caught off guard when the new features went live. They had skimmed the messages or skipped the meetings, mistaking silence for agreement. When stakeholders finally experienced the changes firsthand, they questioned the strategy and timing, forcing the team to defend their work instead of celebrating the launch. This experience revealed that simply broadcasting updates fails in modern software delivery because it allows busy people to ignore decisions until they become a reality. To fix this, the author adopted three practical strategies. First, mandatory attendance is now required for key stakeholders during crucial sessions. Second, teams hold dedicated alignment calls to walk through the complete user experience and address concerns early. Finally, and most importantly, stakeholders test the new features directly on their own devices using feature toggles before the public launch. Navigating the changes themselves makes the update real and encourages genuine buy-in. Ultimately, alignment is an experience rather than a mere message. Ensuring stakeholders have tested and questioned the changes guarantees a much smoother and more confident launch day.


What happens when AI models take aim at ICS exploits

Security researchers are finding that artificial intelligence is getting much better at developing attacks against industrial control systems, a task that traditionally required highly specialized human expertise. In a recent experiment, researchers used AI to successfully adapt an existing software exploit to target a different programmable logic controller. While the AI still needed some human guidance and took several hours to complete the complex task, it managed to use reverse-engineering tools, write custom scripts, and generate working attack code without access to the device's original source code. This capability significantly lowers the time and effort required for attackers to target complex industrial environments. As AI models continue to advance rapidly, vulnerabilities that security teams previously considered too difficult or time-consuming to exploit may soon become practical targets for threat actors. This shift is particularly concerning because industrial devices control critical physical infrastructure around the world. Organizations must now aggressively account for these AI-assisted threats, as attackers could rapidly adapt exploits across different equipment models. The experiment also highlighted the unpredictable nature of AI in these settings; in one instance, an AI agent accidentally destroyed the target device during testing, perfectly demonstrating the serious real-world consequences of these emerging capabilities.


Australia Privacy Law 2026: World-First Test Forces Companies to Justify Every Data Use

Australia has introduced the draft Privacy Amendment Bill 2026, marking a significant change in how companies must handle personal information. The centerpiece of this legislation is a new, world first fair and reasonable test. Under this rule, simply getting a user to check a consent box will no longer be enough to justify how their data is used. Instead, organizations must objectively prove that their data practices are inherently fair, reasonable, and lawful. This shifts the burden of responsibility directly onto businesses. When collecting or sharing data, companies will have to weigh several factors. They must consider the reasonable expectations of the user, ensure genuine transparency, and practice data minimization by only collecting what is strictly necessary. The law also requires companies to balance the potential risk of harm against any benefits, and when children are involved, their best interests become a primary consideration. Unlike other international frameworks like the European GDPR, which treats fairness as an addition to other legal requirements, the Australian proposal makes fairness the central requirement. This fundamental change forces companies to look beyond basic compliance and carefully justify every single way they utilize personal data, ultimately providing individuals with much stronger, more meaningful privacy protections.