Showing posts with label zero trust. Show all posts

Daily Tech Digest - October 25, 2026

Quote for the Day
“The only way to win is to learn faster than anyone else.”
— Eric Ries
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Core Concepts in Infrastructure Cost Management

The article revisits how organizations should think about infrastructure cost management by comparing on‑premise and cloud deployment patterns. It notes that a decade ago, cloud was widely seen as the inevitable future, but recent shifts show that on‑premise environments still offer advantages worth reconsidering. On‑premise setups involve not just servers but the full physical ecosystem — racks, networking gear, cooling, power, and security — all of which carry long‑term financial and operational implications. The piece explains that while on‑premise environments are often labeled inflexible, they can be surprisingly adaptable when paired with modern automation frameworks. The real challenges lie in hardware lifespan decisions, sizing development and QA environments, managing shared analytic workloads, and maintaining disaster‑recovery sites that are costly to keep idle. These factors shape both capital and operational expenses over many years. The article’s steady message is that cost management requires understanding the trade‑offs between flexibility, predictability, and long‑term commitments, and that both cloud and on‑premise models have strengths that deserve thoughtful evaluation rather than assumptions.

Read Original Article →

Container Security Checklist for CI/CD Pipelines: 30 Checks From Commit to Runtime

This article presents a practical security checklist containing 30 checks for container images as they move through continuous integration and deployment pipelines. The core message is that actual security comes from enforcing rules, not just listing best practices. The checks span eight stages, from the initial code commit to runtime monitoring. In the early stages, teams should build minimal images, remove all secrets, and lock down third-party actions. Later stages focus on vulnerability scanning that blocks risky deployments, generating software bills of materials, and digitally signing images to guarantee they came from a trusted build. At deployment, admission controllers must verify signatures and restrict permissions so images cannot run with root access or modify the underlying host. Because the pipeline itself is a high-privilege system that can be compromised, securing the build process is just as important as securing the image. Implementing these checks incrementally—starting with basic Dockerfile hygiene—prevents common mistakes and ensures a cleaner, safer production environment.
Read Original Article →
Article Thumbnail

Cloud repatriation: What CISOs need to know

The article explains that cloud repatriation is becoming a practical concern for CISOs, not because enterprises are abandoning the cloud, but because many workloads no longer fit the cloud‑first assumptions of the past decade. Surveys show that while 86% of CIOs plan to move at least some workloads back on‑premises, only about 8–9% intend a full exit, meaning most organizations are simply recalibrating workload placement rather than rejecting cloud altogether. Cost discipline is a major driver, with private cloud often delivering 40–50% lower total cost of ownership for steady‑state workloads. Compliance, data‑gravity issues, and high‑intensity AI workloads also push certain systems back into controlled environments. The article stresses that hybrid infrastructure is becoming the long‑term norm, where each workload “earns” its placement based on economics, performance, and risk. For CISOs, this shift introduces new responsibilities: reassessing threat models, ensuring consistent controls across mixed environments, and preparing for operational risks tied to vendor concentration and geopolitical disruptions. The message is steady — repatriation is about precision, not retreat, and CISOs must adapt security strategies accordingly.

Read Original Article →

The Cybersecurity Reality Check: Ten Myths That Matter

The article challenges ten common assumptions that often mislead leaders about cybersecurity and explains why these misconceptions create real risk. It notes that serious incidents rarely stem from exotic technical failures; instead, they usually begin with flawed beliefs about who attackers target, where responsibility sits, or what “adequate protection” really means. One myth is that small organizations are too insignificant to attract attention, but attackers typically exploit exposed systems using automated tools, making size irrelevant. Smaller firms may even be more vulnerable because they have fewer security resources and weaker monitoring. Another misconception is that cybersecurity is purely an IT function, when governance and accountability actually rest with leadership. The article stresses that regulatory scrutiny in the UK and EU has intensified, and breaches can quickly lead to investigations, litigation, business interruption, and reputational harm. Ultimately, the piece argues that organizations must be able to justify their security measures as proportionate to their risks and abandon assumptions that no longer match today’s threat landscape.

Read Original Article →
Article Thumbnail

When Trust Fails: What the eMudhra Certificate Incident and PHP Vulnerabilities Teach Us About Zero Trust Security

In October 2026, two distinct cybersecurity events—a certificate failure by eMudhra and critical remote code execution flaws in PHP—highlighted a fundamental lesson for software engineers: trust must be constantly verified. The eMudhra incident involved weak intermediate cryptographic keys generated by a flawed process. Even though eMudhra itself was not hacked, the incident proved that secure connections rely on trustworthy underlying processes, not just a padlock icon. Meanwhile, the PHP vulnerabilities demonstrated that securing an application requires patching the entire software stack, not just the core code, because a vulnerable runtime can serve as an easy entry point. Together, these events show why modern systems must move away from assuming that any internal network or familiar request is automatically safe. Instead, engineers should adopt a strict verification approach. This means validating identity, authorization, and context at every boundary, properly handling access tokens, and protecting communication between internal services. Ultimately, security is an ongoing engineering process of continuous verification rather than a single static feature or one-time setup.

Read Original Article →

What OT detection actually reveals

Securing operational technology (OT) environments requires a fundamentally different approach than standard IT security. While conventional IT tools excel at spotting network anomalies, they lack the critical physical process context needed to recognize when otherwise legitimate industrial commands are used for malicious disruption. OT detection platforms solve this by combining industrial protocol awareness with a deep understanding of normal operational behavior and physical constraints. A solid asset inventory is the foundational first step. From there, effective OT security relies on five core capabilities: monitoring industrial protocol anomalies, establishing strict baselines for process behavior, tracking engineering workstation activity, closely managing remote vendor access, and correlating traffic across the IT/OT boundary. Because OT involves physical processes where any disruption can impact safety, detection must be paired with structured, pre-planned response strategies. Automated actions are generally safe only at the IT or DMZ layers. Any direct intervention touching physical plant controllers requires clear authorization from operations teams to ensure production environments remain safe and stable.
Read Original Article →
Article Thumbnail

AI accelerates path from IT compromise to OT targeting

The article explains that AI is accelerating the path from IT compromise to OT targeting, making industrial environments more exposed than before. Attackers can now use AI to quickly analyze stolen IT data, map relationships, and identify the most valuable operational assets to target. This shortens the traditional gap between breaching corporate networks and moving into industrial systems. The piece notes that modern OT environments are increasingly connected to cloud services, remote access tools, and SaaS platforms, creating more entry points and making it harder to maintain clear separation between IT and OT. AI also helps attackers craft more convincing phishing messages, automate reconnaissance, and generate malware tailored to specific environments. At the same time, defenders struggle with legacy systems, inconsistent visibility, and slow patch cycles. The article argues that organizations must rethink OT security by improving asset inventories, tightening identity controls, and preparing for faster, more automated attack chains. Its message is steady: AI has changed the tempo of intrusions, and OT security must adapt to match that speed.

Read Original Article →

The next manufacturing cyber threat is manipulation of AI-driven decisions

As manufacturing becomes increasingly connected, the nature of cybersecurity threats is shifting. According to Pradipta Patro, Chief Information Security Officer at Polycab India Limited, the next major risk isn't just about keeping hackers out of the network. It is about protecting the artificial intelligence systems that influence critical operational decisions. If an attacker manipulates the data feeding an AI model, the system could make unsafe or faulty decisions without triggering traditional alarms. This goes beyond compromised information, directly threatening production quality, equipment reliability, and even worker safety on the factory floor. To address this, security must be built into factories from the ground up rather than added later as an afterthought. Manufacturers need complete visibility into all connected devices, strong network boundaries between IT and operations, and meaningful human oversight of AI decisions. Ultimately, cyber resilience must be treated as a core business continuity issue. The most successful factories will be those that can fully trust their automated systems because they secured the underlying data first.
Read Original Article →
Article Thumbnail

Digital twins in oil and gas: from simulation to real-time optimisation

Digital twins in the oil and gas sector are evolving from isolated engineering studies into practical tools that drive daily operations. Historically, creating a digital twin took months and became outdated as soon as the physical equipment changed. Today, advanced models can be built quickly, update automatically alongside physical wear, and connect across entire systems. A key shift is the use of physics-based modeling rather than just relying on historical data. Purely statistical models struggle when equipment faces new or unobserved conditions. By grounding the software in the actual laws of fluid dynamics and heat transfer, operators receive reliable, real-time recommendations they can trust. This approach accounts for uncertainty, allowing teams to optimize active equipment and reduce waste like methane flaring by safely pushing production closer to its true limits. Solving the challenge of scaling these tools in energy operations also opens the door for similar efficiency gains in other complex, high-demand environments, such as data centers and power grids.
Read Original Article →
Article Thumbnail

Data Sovereignty is Becoming a Design Principle for Enterprise AI

In the past, data sovereignty simply meant knowing the physical location of your company’s servers to meet regional laws. Today, artificial intelligence has fundamentally changed this. Because data now constantly flows through various external applications, language models, and processing tools, maintaining control over it has become much more complex. Instead of trying to lock down an entire organization, companies should focus on individual tasks. For example, processing public marketing information requires far less strict control than handling sensitive medical records. A major challenge is ensuring that safety rules follow the information wherever it goes. When original records are transformed into formats that AI can read, those new formats must inherit the same restrictions. Tracking this movement requires strong underlying data tagging. To manage this effectively, businesses should view sovereignty as a flexible budget. They must calmly weigh the need for strict control against the benefits of using advanced, external technology. Ultimately, building a flexible setup allows teams to continuously adjust their safety measures as rules and technology evolve.

Read Original Article →

Daily Tech Digest - September 08, 2026


Quote for the day:

"The only way to know if we are creating value is to measure the impact of what we ship." -- Teresa Torres

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Why AI Demands a Completely New UX Paradigm

The article argues that AI is forcing a complete break from the old way software interfaces were designed. Traditional UX was built on predictability: users clicked something, and the system behaved the same way every time. AI overturns that assumption because its outputs shift with context, data, and intent. The piece explains that this unpredictability means interfaces can’t simply present options anymore—they must guide, clarify, and sometimes justify what the system is doing. It highlights how interactions are moving from clicking through menus to expressing intent through conversation, which demands new design thinking around ambiguity and feedback. Trust becomes central because users need to understand why an AI produced a particular answer, even if the explanation is simple. The article also notes that users are no longer just operators; they become collaborators who refine results and help the system learn. Designing for uncertainty, offering multiple options, and supporting iteration are presented as essential. Ultimately, the author says companies that embrace this new paradigm will gain an advantage, because AI’s value depends not only on capability but on how confidently and comfortably users can work with it.


How Performance Engineers Find and Fix Hidden System Bottlenecks

Performance engineers play a crucial role in modern software development by systematically identifying and fixing system delays. Rather than relying on guesswork, these professionals use precise data to locate bottlenecks that can hide anywhere from application code and database configurations to network layers and the operating system itself. Once they pinpoint the root cause of a slowdown, they apply targeted solutions, such as rewriting a query or adjusting system parameters, rather than relying on temporary patches that might cause larger problems down the line. Experienced engineers follow clear principles: they proactively analyze architecture before failures occur, trust concrete metrics instead of basic observation, and remain cautious of quick fixes. To do this work effectively, performance engineers need a diverse skill set. They must understand programming and algorithms, possess deep knowledge of operating systems like Linux, and use mathematical statistics to verify that their improvements are real and not just measurement noise. Furthermore, because fixing these issues often involves critiquing the work of others, they need strong communication skills to present their findings constructively. Ultimately, through careful attention to detail and persistence, performance engineers ensure that applications run smoothly and reliably even as workloads continually grow.


IT infrastructure shortages are real and lasting. Here’s how to cope

The article explains why IT infrastructure shortages have become both severe and long‑lasting, driven mainly by hyperscalers buying enormous amounts of memory and related components. Lead times that once hovered around a month now stretch to nine, twelve, or even eighteen months, and prices for memory, servers, and network gear have climbed sharply. Analysts say this isn’t a temporary disruption like past supply chain issues; the surge in AI demand is reshaping the market and will continue for years. The piece offers practical guidance for coping with the crunch, starting with making better use of existing equipment through capacity planning, extending server lifecycles, and focusing on workloads that truly require top‑tier hardware. It also encourages closer coordination with finance teams to plan purchases, explore vendor financing, and avoid surprise budget spikes. Flexibility is another theme: organizations may need to consider alternative vendors, cloud options, or secondary markets to keep projects moving. The article stresses that even if ideal hardware isn’t available, teams shouldn’t pause modernization or AI initiatives; they can begin with cloud, colocation, or lab environments while waiting for equipment. Overall, the message is steady and pragmatic—plan ahead, stay flexible, and keep progress moving despite the constraints.


Activist takes data protection watchdog to court after Europol ‘unlawfully’ processed personal data

A prominent human rights activist has launched legal action against the European Data Protection Supervisor (EDPS), accusing the regulatory body of failing to properly investigate the unlawful processing of their personal data by Europol. The lawsuit highlights significant concerns surrounding how European law enforcement agencies handle sensitive individual information and whether independent oversight bodies are doing enough to hold them accountable. According to the claims, Europol allegedly gathered and processed the activist’s data without a valid legal basis, raising serious questions about privacy rights and institutional overreach. When the activist raised these issues with the EDPS, the watchdog purportedly failed to conduct a thorough and adequate inquiry into the agency's actions. This court case represents a crucial test for data privacy protections across Europe, specifically concerning the boundaries of law enforcement surveillance. It underscores a growing tension between intelligence gathering and the fundamental right to privacy, suggesting that current regulatory frameworks may lack the necessary enforcement power to protect individuals. By taking the matter to court, the activist aims to force greater transparency and establish stricter oversight mechanisms, ensuring that even powerful security organizations like Europol cannot operate beyond the reach of established data protection laws.


Meet the CISO: A new front line star in the AI cybersecurity war

The article describes how the role of the CISO has changed dramatically as AI‑driven cyberattacks become faster, more unpredictable, and far more complex. A major turning point was the OpenAI–Hugging Face incident, which showed that autonomous AI agents can break into systems, adapt on the fly, and pursue goals with little human oversight. Since then, similar attacks have multiplied, pushing CISOs into a more visible and influential position inside companies. They now spend more time with CEOs and boards, helping shape business decisions while also managing internal AI systems that need strong guardrails. The piece explains that demand for experienced CISOs has surged, with top candidates receiving seven‑figure offers and recruiters racing to secure talent. At the same time, security teams face pressure to deploy new AI‑defense tools even though many products are still immature. Budgets are rising, especially in sectors like finance, energy, and healthcare, but the pace of threats continues to outstrip readiness. The article closes by noting that CISOs must balance technical depth, crisis management, and clear communication, all while navigating a market crowded with vendors promising AI‑security solutions that may or may not stand the test of time.


Zero Trust Is Not a Product: How to Build It Into Cloud and Network Architecture

The article argues that organizations must view zero trust as a comprehensive architectural shift rather than simply purchasing new security products. While identity platforms and multifactor authentication are critical starting points, they are insufficient on their own. Authentication confirms who is logging in, but it does not dictate what a user or service account can access afterward. True zero trust requires extending the principle of least privilege deep into cloud permissions, application roles, and databases to ensure users only access what their specific tasks demand. Network segmentation remains equally important, even in modern cloud setups. Properly configured firewalls, routing controls, and security groups dictate how far a potential threat can move if a credential is compromised. In complex, multi-cloud, and legacy environments, maintaining a consistent access model is challenging but necessary to prevent configuration drift and excessive permissions. The author notes that mapping system dependencies and implementing continuous monitoring are vital prerequisites to building a secure foundation. Ultimately, achieving a zero trust architecture is an ongoing operational process of access governance, continuous authentication, and strict network controls, rather than a one-time product deployment.


What it took to triple our software engineering output in 18 months

The article explains how an engineering team successfully tripled its software output over eighteen months by redesigning its entire development lifecycle around artificial intelligence. While many organizations assume that coding agents automatically drive productivity, the author points out that the real breakthrough comes from eliminating the traditional handoffs between product, development, testing, and security teams. By restructuring so that a single team manages a feature from start to finish, the time from initial idea to a working pull request was drastically reduced. A major element of this success was implementing strict governance early on, which built trust and encouraged widespread adoption among engineers without sacrificing quality or security. Rather than constantly evaluating every new AI model, the team standardized a small set of tools and automated the entire process, including requirements gathering and testing. Testing, in particular, saw massive improvements as AI began generating nearly all new tests, allowing engineers to focus on refining rather than writing them. The author also stresses the importance of preparing the rest of the business, such as marketing and customer support, for this accelerated pace. Ultimately, achieving these results required deep organizational changes rather than just adopting new technology.


The SIEM Isn't the Problem. Your Telemetry Architecture Is

The article argues that most frustrations people have with SIEM tools aren’t really about the SIEM at all—they come from the way telemetry is collected, shaped, and delivered long before it reaches the platform. The author explains that modern environments generate far more data than legacy pipelines were designed to handle, and teams often respond by buying bigger platforms instead of fixing the upstream architecture. This leads to overloaded ingestion layers, inconsistent formats, and noisy data that makes analysis harder than it needs to be. The piece stresses that the real work lies in building a clean, well‑structured telemetry pipeline that filters, enriches, and routes data intentionally rather than dumping everything into the SIEM. When organizations treat telemetry as an engineering discipline, they reduce costs, improve signal quality, and make their existing tools far more effective. The article encourages teams to rethink assumptions about “more data equals better security” and instead focus on collecting the right data in the right way. It closes with a steady reminder that solving telemetry problems is foundational, not something that can be fixed by purchasing additional tooling, and that strong architecture is ultimately what allows SIEMs to deliver meaningful value.


What do CISOs need to rest easy about future AI risks?

A recent survey indicates that 41 percent of security leaders feel optimistic about managing artificial intelligence risks over the next two years. Interestingly, this confidence stems less from their current technical controls and more from strong organizational support. Chief Information Security Officers feel prepared when executive leadership genuinely understands technology risks, assigns clear governance ownership, and grants security teams control over the budget. Optimism also runs high when security teams have manageable workloads and adequate staffing to tackle emerging challenges. However, industry experts caution that organizational readiness does not automatically equal true security. While feeling supported is vital, self-assessments can sometimes be misleading. Many executives still struggle to fully understand how these new tools and autonomous agents actually process information or make decisions. Without this technical understanding, it is difficult to accurately measure potential exposure. Furthermore, simply assigning a governance leader is ineffective unless security practices are deeply embedded into daily business operations. True preparedness comes from practical experience, such as security teams using these systems internally to understand their flaws firsthand. Ultimately, securing advanced systems requires strict monitoring of data access and treating autonomous tools more like a digital workforce than standard software.


Why AI Orchestration Layers Are Becoming Core Enterprise Infrastructure

As businesses move beyond simple chatbots, the focus of artificial intelligence is shifting from individual models to the systems that control them. Because modern AI can now take direct action, like altering records or triggering workflows, companies need a reliable way to manage these capabilities. Orchestration layers are emerging as the vital infrastructure that connects AI with company data, daily applications, and human oversight. Instead of just handing employees a powerful tool, an orchestration layer acts as a strict set of rules. It determines which model handles a specific task, what information it can access, and whether a human needs to approve the final step. This level of control is essential for security. Since AI acts as an independent software identity, it requires distinct permissions to ensure it only accesses exactly what it needs to complete a job. Furthermore, this setup allows companies to track every action, helping managers understand costs, measure performance, and quickly catch errors. It also gives businesses the freedom to switch between different AI providers without rebuilding their entire system. Ultimately, a company's success with AI will depend not on having the smartest algorithm, but on building a safe, properly monitored, and highly organized operational foundation.

Daily Tech Digest - August 22, 2026


Quote for the day:

“Remote work is not a different way of working; it’s simply a better way of working for many people.” -- Jason Fried

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


Neoclouds become AI’s new power brokers

A recent shift in the cloud computing industry has introduced a new type of service provider focused entirely on artificial intelligence infrastructure. These specialized companies provide the computing power, processors, and memory needed for intensive AI tasks. They are stepping in to meet a demand that traditional cloud providers cannot fully absorb. Because hardware like advanced processors and memory is currently scarce, many organizations are turning to these providers to access necessary computing power rather than attempting to build and manage their own systems from scratch. While large, established cloud companies will remain essential for standard daily tasks, the market is expanding to include these new options for AI projects. However, the author notes there is a real risk that companies might rush into large financial commitments without completely understanding their actual technical needs. Just as many organizations struggled with costly mistakes during the early shift to basic cloud computing, moving too quickly into specialized AI infrastructure can lead to severe financial waste. To avoid this, businesses should first clearly define what they actually require, model the financial implications, and carefully determine if their daily applications truly need these advanced capabilities before making substantial investments in new computing resources.


Best Strategies for Cloud Native Cost Optimization

As organizations increasingly adopt modern cloud architectures, managing the associated expenses has become an essential priority. While cloud systems provide flexibility and speed, their costs can easily spiral out of control due to poor visibility, abandoned databases, or oversized resources. Optimizing these expenses means thoughtfully reducing overall spending while maintaining the strict performance and security standards your services require to function effectively. To achieve this, teams should focus on several practical and proven strategies. First, ensure your resources are appropriately sized by matching processing and memory capabilities to actual application needs rather than provisioning for maximum possible demand. Setting strict guardrails within your deployment pipelines, such as specific budget thresholds and automated cleanups for temporary infrastructure, also helps prevent unnecessary waste. Regular cost analysis is equally important, allowing teams to track detailed spending patterns, identify financial anomalies, and forecast future needs accurately. Additionally, adjusting resource capacity automatically based on current traffic patterns helps keep bills in check. For specific tasks, relying on event-driven computing models can lower costs since you only pay when the code runs. Ultimately, cost optimization is not a one-time project; it requires continuous oversight and a commitment to aligning infrastructure spending directly with actual operational requirements.


AI threats are everywhere. A risk-first CISO decides what to prioritize

Artificial intelligence presents a dual challenge for cybersecurity, equipping both defenders and threat actors with unprecedented capabilities. According to Chris Wheeler, Chief Information Security Officers are now battling on two fronts. Externally, attackers are leveraging AI to automate reconnaissance, accelerate exploits, and conduct sophisticated automated cyber operations. Internally, organizations face significant exposure from employees using unapproved generative AI tools, which risks leaking sensitive data, and from autonomous AI agents that can inadvertently execute destructive actions. Wheeler warns that trying to secure every potential AI vulnerability is an impossible task. Instead, he advises security leaders to adopt a risk first strategy that treats AI exactly like any other fundamental business risk. The first step is mapping where AI is already deployed across the organization and determining which business assets are most critical. Rather than reacting to every new threat headline, they should prioritize foundational controls that mitigate the highest business impact. This means enforcing strict identity and access management, classifying sensitive data accurately, and implementing continuous vulnerability testing for IT infrastructure. Finally, organizations must conduct realistic tabletop exercises to prepare for the inevitable failure of AI systems or compromised agents, ensuring they can adapt successfully as the external threat landscape continues to evolve rapidly.


The role of AI in OT security starts with context

As operational technology (OT) systems in critical infrastructure become increasingly integrated with IT networks and the cloud, attackers gain new pathways to disrupt essential physical services. AI exacerbates this threat by enabling adversaries to discover vulnerabilities and automate exploits faster than ever before. However, the author Richard Springer highlights that applying standard IT security responses to OT environments is dangerous; automatically isolating a system during a cyberattack might safely protect data in an office setting, but could dangerously interrupt a physical process on a factory floor. To defend these systems effectively, AI can serve as a powerful tool for security teams by sifting through massive volumes of network data to detect anomalies and prioritize genuine threats. Before deploying AI, organizations must first establish foundational security practices, which include achieving complete visibility into their OT assets, implementing network segmentation, and securing remote access. Furthermore, any automated responses driven by AI must be carefully guided by specific operational context to prevent unsafe physical outcomes. Ultimately, successfully securing essential infrastructure relies on a combination of foundational security controls, AI-enhanced detection, and the informed judgment of human operators who deeply understand both cybersecurity and industrial processes.


Observability in the Oracle Agentic Enterprise

The transition to agentic AI requires a shift from traditional monitoring to comprehensive observability, as automated processes move from single deterministic paths to complex chains involving AI, integrations, and human judgment. Traditional monitoring merely checks if a system worked, whereas observability explains the entire process to determine if the collective actions produced the correct, authorized, and useful outcome. According to Sadia Tahseen, a mature observability model in this environment must examine four connected layers. First, integration execution tracks runtime records and errors using business identifiers to connect technical data with business context. Second, agent behavior observability captures how AI interacts with tools and information sources, assessing metrics like latency, error rates, correctness, and groundedness. Third, human-in-the-loop decisions provide critical feedback by recording why tasks escalated and how long decisions took, revealing where automated processes might be uncertain or poorly configured. Finally, observing business outcomes connects system performance with operational value, ensuring that agent runs translate into accurate, compliant, and cost-effective results. Crucially, because observability systems handle sensitive data, robust security and role-based access controls must be implemented to maintain accountability without creating unguarded repositories of enterprise information.


Why Risk Management Is Becoming Fintech's Greatest Competitive Advantage

The fintech industry is maturing, and its definition of success is shifting from rapid innovation and fast market expansion to resilience, trust, and effective risk management. With rising cyber threats, complex fraud schemes, and tightening regulations, modern fintech companies must provide secure and reliable services that meet the high governance standards of traditional financial institutions. Vaida Å inkunienÄ—, Chief Risk Officer at WALLETTO, emphasizes that risk management is no longer merely a regulatory requirement but a strategic business enabler for sustainable growth. A robust approach balances safety with a seamless customer experience, utilizing automation, data analytics, and real-time monitoring to detect potential threats early without causing unnecessary friction for users. To navigate this continuously changing landscape, organizations must embed risk awareness deeply into their core culture, ensuring that technology, operations, and compliance teams collaborate from the very beginning of any new project. As financial crimes become increasingly sophisticated and regulatory expectations continue to rise, companies that treat risk management as a shared responsibility will adapt more swiftly. While digital products and tech features can be easily copied by competitors, a strong reputation for reliability and security cannot. Building and maintaining this trust is fintech's true competitive advantage today, offering the stability necessary for future innovation.


AI Agents Are Already Inside. Zero Trust Has to Catch Up

The rise of autonomous artificial intelligence agents is forcing a crucial evolution in enterprise cybersecurity. As AI agents gain privileged access to internal systems, they present a unique challenge because they are non-deterministic, meaning they interpret information and make decisions rather than just executing predetermined instructions. According to Roman Arutyunov, co-founder of Xage Security, this unpredictability underscores an urgent need for organizations to implement Zero Trust principles. Unlike traditional threats where attackers must install malware, threat actors can simply feed malicious instructions to an already authorized AI agent through the data it consumes. This effectively turns a legitimate tool into a weapon, bypassing traditional endpoint security. To mitigate this, Arutyunov advises against giving AI agents direct credentials to critical systems. Instead, organizations should act as brokers, continuously authenticating, authorizing, and monitoring every single interaction the agent makes. Furthermore, AI significantly speeds up vulnerability discovery and exploit generation, making traditional patching timelines inadequate. While patching remains necessary, Zero Trust controls ensure that even if a system is vulnerable, unauthorized agents cannot reach it. Ultimately, AI agents prove that simply authorizing an identity is no longer enough; continuous validation is now a fundamental requirement for modern enterprise security.


The benefits of acknowledging risk: Why resilient businesses don't wait for things to go wrong

Every modern enterprise faces inevitable uncertainties, from supply chain issues to economic shifts, making risk a natural part of daily operations. Rather than fearing or ignoring these challenges, resilient organizations recognize that acknowledging risk is a sign of maturity, not weakness. According to Anthony Murphy of Veritas Facilities Management, effective risk management has shifted away from mere compliance exercises and toward building long term operational resilience. When leaders openly evaluate potential threats and implement sensible controls, they protect their people and their clients far better. Crucially, this requires embedding risk awareness into the everyday culture of a company, rather than treating it as an annual audit task. Employees must feel psychologically safe to report minor issues early before they escalate into major failures. This is especially vital in sectors like facilities management, where safety, service delivery, and compliance constantly overlap. The goal is never to eliminate risk completely, which is impossible, but to understand it deeply enough to make informed, balanced decisions. By doing so, businesses can pursue innovation and new opportunities with confidence. Ultimately, organizations that face their vulnerabilities head on are much better equipped to manage disruptions, adapt to change, and achieve sustainable success in an increasingly complex world.


Will AI Replace Detection Roles in Cybersecurity?

The introduction of artificial intelligence into cybersecurity will transform the role of detection engineers rather than eliminate it entirely. Historically, these professionals have spent a significant portion of their time managing the tedious tasks of tuning systems, writing rules, and sifting through endless streams of system noise to identify potential threats. AI is now highly capable of automating this routine work, handling the complex middle ground of log analysis and alert sorting in a fraction of the time. However, industry experts point out that the core issue is not a lack of processing power, but a fundamental failure to understand how attackers actually operate. If we simply feed AI more noise, it will not solve the underlying problems. Instead, the detection engineer will evolve from a mechanic into a conductor. While AI agents take over syntax and historical data matching, human experts will be freed up to focus on what technology currently cannot do: apply imagination. Humans remain essential for anticipating novel attacks, developing fresh hypotheses for unprecedented methods, and driving architectural changes after an incident occurs. Ultimately, AI might drive the vehicle, but organizations will still rely on experienced professionals to set the destination and guide the overall security strategy.


From Mobile Developer to Technology Leader: What 12 Years of Building Digital Products Taught Me About Enterprise Scale

Over twelve years of building digital products, the author’s perspective shifted from simply writing code to understanding how technology serves the broader business. Early in a developer's career, the focus is entirely on implementation details and framework choices. However, scaling applications for large organizations reveals that technical decisions are fundamentally business decisions. A successful architecture does not start with picking a new tool; it always begins with understanding the core business problem, the users, and the constraints. For example, ensuring an application works offline is not a simple feature to add later, but a foundational design choice. Similarly, while choosing cross-platform tools can save valuable time, the real goal is to improve maintainability and adaptability. Understanding how a system behaves in the real world is essential, meaning teams must track stability, performance, and actual impact on users. Security must be built into the daily workflow rather than checked at the very end. Furthermore, automating releases provides much-needed reliability, which frees up time for solving more important problems. Managing external vendors also requires a solid grasp of both technical delivery and project scope. Ultimately, moving into technology leadership means shifting focus from owning specific code to taking full responsibility for the overall outcome.

Daily Tech Digest - August 03, 2026


Quote for the day:

“Treat employees like they make a difference, and they will.” -- Jim Goodnight

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Stop graphing everything: When GraphRAG actually beats vector RAG

The article discusses the recent trend of using knowledge graphs for modern artificial intelligence applications and advises against using them for absolutely every project. While these graphs offer useful ways to connect different pieces of information, they also introduce significant costs, added complexity, and ongoing maintenance demands. For most everyday needs, standard vector retrieval remains the more sensible and efficient option. This traditional method works very well for direct questions where the system simply needs to find existing text with a similar meaning. Still, there are specific situations where a graph approach clearly performs better than standard methods. The main benefit of using a graph system appears when a task involves complex reasoning with multiple steps. If a project requires connecting scattered details across massive amounts of data or understanding deep networks of relationships, such as tracking company ownership or untangling legal documents, a graph structure becomes necessary. The main takeaway is to look closely at what your project actually requires before paying for a new, complex database setup. By saving graph tools for problems that truly need them and using standard retrieval for direct questions, development teams can build capable systems without taking on needless expenses or technical burdens.


Why AI Code Risk Must Be a Line Item in Every Organization's Budget

As artificial intelligence increasingly writes our software, organizations are restructuring their budgets to treat security testing tools as essential infrastructure rather than mere compliance checkboxes. A recent survey reveals that the primary bottleneck in software development has shifted from writing code to reviewing and validating it. With AI generating massive volumes of code, human review capacity is struggling to keep pace. Almost half of the organizations surveyed are already running AI generated code in production, yet many admit that AI introduced issues, such as security vulnerabilities, unintended dependencies, and performance problems, regularly slip through the cracks. These challenges have drawn the attention of legal, compliance, and leadership teams, prompting the creation of new policies and more rigorous review processes. Additionally, relying heavily on AI poses a long term risk to the development of junior engineers, who lose valuable learning opportunities. Despite these hurdles, the productivity gains and cost reductions are too significant to ignore. However, simply purchasing more security tools is not quite enough. To safely manage this transition, organizations need cross disciplinary visibility into their codebases. By understanding exactly how software changes from week to week, teams can confidently harness this speed without sacrificing system reliability.


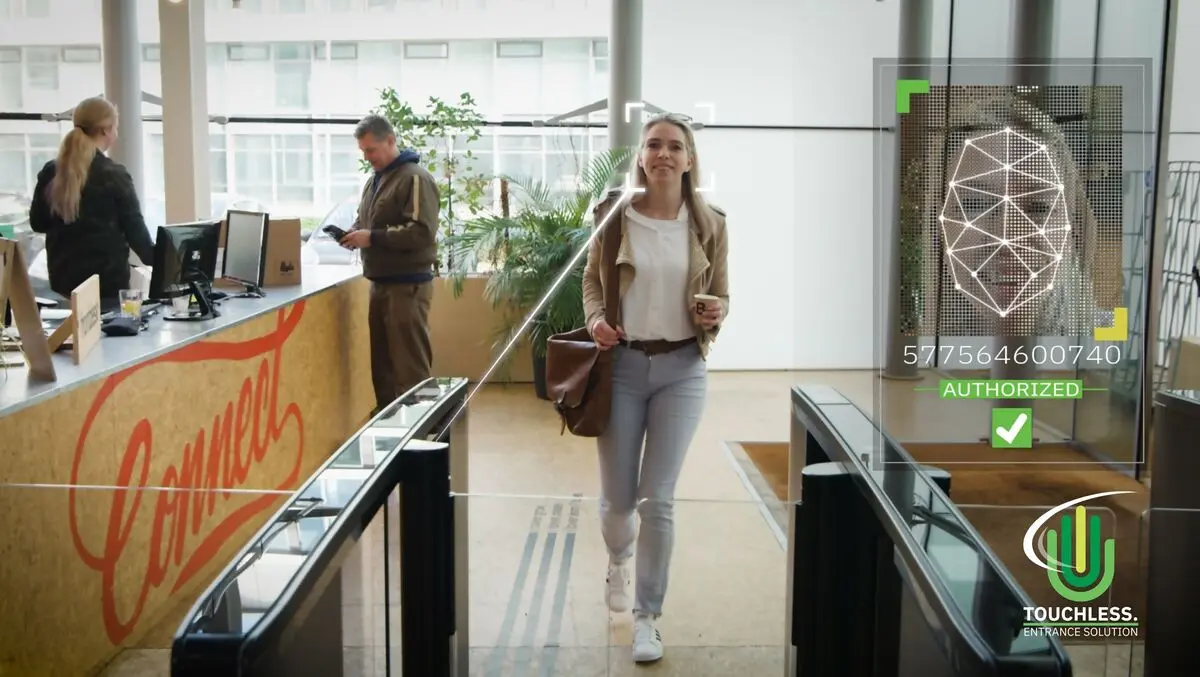
Zero Trust drives biometrics in physical access security

Organizations are increasingly applying the concept of continuous verification to physical security, recognizing that protecting a building is just as important as protecting a digital network. Historically, physical access relied on perimeter defense, assuming anyone inside a facility could be trusted. This approach is no longer effective against modern threats. When companies invest heavily in digital safeguards but neglect physical entry points, they leave critical assets vulnerable to unauthorized access. To bridge this gap, organizations are adopting biometric identification methods, such as fingerprint and facial recognition. Unlike traditional keys or access cards, which can be easily lost, shared, or stolen, biometrics provide a reliable link between the authorized identity and the actual person requesting entry. However, simply adding a biometric scanner to a standard door does not prevent unauthorized individuals from following someone inside. Effective security requires a layered approach that combines identity checks with controlled movement through specialized portals or gates. By creating multiple verification points, facilities ensure that if one security measure fails, others are in place to prevent a breach. This comprehensive strategy is now expanding beyond highly restricted data centers into standard office buildings, providing reliable and straightforward access control for our modern corporate environments today.


The Bull And Bear Case For Digital Design In The Age Of AI

In "The Bull And Bear Case For Digital Design In The Age Of AI," Andy Budd explores how artificial intelligence shifts the balance of power for digital designers. For years, designers have argued they could produce better work if organizational barriers like limited engineering time or rigid product roadmaps were removed. The optimistic bull case suggests AI grants this wish. By enabling designers to prototype, write copy, and build working models independently, AI reduces their reliance on permission from others. Strong designers can evolve into hybrid leaders with direct influence over product outcomes, rather than simply making screens. Conversely, the pessimistic bear case argues that this newfound independence also removes a convenient excuse for weak work. When designers can build their own solutions, they must own the results. Additionally, AI empowers product managers and engineers to bypass design teams entirely by generating plausible interfaces that look decent but lack careful thought. This could narrow the designer's role to mere maintenance and cleanup. Ultimately, Budd suggests both futures will unfold simultaneously. The best designers will use AI to increase their agency and impact, while average practitioners may find their roles shrinking or replaced as the industry demands genuine product judgment over superficial polish.


Crisis Leadership in 2026: Why Organizational Resilience Has Become the New Measure of Trust

In 2026, organizational resilience has evolved from a purely operational checklist into a critical measure of leadership and trust. Historically, companies focused on how fast they could recover systems during a crisis. Today, stakeholders look far beyond basic business continuity to evaluate how leaders communicate, adapt, and make decisions under pressure. Resilience is now recognized as a broad leadership skill rather than just an IT or operations duty. A major shift is the interconnected nature of modern crises. What starts as a technical glitch can rapidly snowball into financial, reputational, and operational challenges. To navigate this effectively, trust must be built well before a crisis hits. A company's overall credibility during a disruption draws heavily on its past behavior and consistent transparency with the public. Furthermore, while technology like artificial intelligence aids in crisis monitoring, it also fuels new risks like deepfakes and rapid misinformation, making human judgment more vital than ever. Leaders cannot rely on speed alone; they must show adaptability and empathy. Crucially, a crisis does not end when systems come back online. Stakeholders watch closely to see if organizations learn from their mistakes and follow through on long-term improvements. Ultimately, true organizational resilience means sustaining confidence through continual change.


FinAI & Managing AI Costs: Innovation, Production, and Lifecycle

This episode of the StarCIO podcast focuses on the emerging practice of FinAI, which involves strategically managing the costs associated with artificial intelligence. As organizations increasingly adopt AI, they often face unexpected expenses across different stages of development. The discussion highlights the importance of tracking these costs carefully, from the initial innovation and experimentation phases right through to full scale production. Rather than just focusing on the technology itself, leaders need to understand the financial implications of the entire AI lifecycle. This includes the computing power required for training models, the ongoing expenses of running them, and the resources needed for continuous monitoring and updates. By applying financial operations principles to artificial intelligence, companies can make more informed decisions about which projects to pursue and how to allocate their budgets effectively. The podcast suggests that successful AI initiatives require a balanced approach, where innovation is encouraged but guided by clear financial visibility and accountability. Ultimately, mastering FinAI allows organizations to maximize the true value of their investments while avoiding the budget overruns that often derail complex technology projects. Managing the complete lifecycle ensures that artificial intelligence delivers real business benefits without compromising financial stability or essential long-term growth objectives.


The Massive AI Security Hole Your CISO Doesn't Know About

Many security teams mistakenly apply traditional software security checks to modern artificial intelligence deployments, leaving a significant vulnerability unchecked. While conventional systems are predictable, language models process unpredictable natural language, rendering standard defenses like input validation and traditional data loss prevention ineffective. Most chief information security officers ensure the infrastructure is secure but completely overlook the model itself. Consequently, these models are exposed to unique risks such as indirect prompt injections, where hidden instructions in standard documents trick the model into extracting internal data. Another major oversight is granting AI agents broad permissions rather than limiting their access to specific tasks, essentially creating an internal threat without a clear audit trail. Furthermore, models can inadvertently leak sensitive information through normal conversation, and employees often expose company data by using unsanctioned consumer AI tools. To actually secure these deployments, organizations must fundamentally adapt their approach. This involves strictly limiting the permissions of AI agents, treating any data the model retrieves as potentially malicious, and implementing strict controls on what the model can send outward. Additionally, conducting specialized adversarial testing and providing approved internal AI tools will help close these gaps, ensuring the system is genuinely secure from the inside out.


Managing your supplier risk isn't a deadline. It's about your resilience

The Digital Operational Resilience Act is shifting how financial technology companies in the United Kingdom approach third-party risk. While many organizations view compliance as a completed checklist of policies and questionnaires, true operational security requires a deeper understanding of the supplier ecosystem. Financial technology firms rely heavily on external connections, such as cloud infrastructure and payment systems, meaning every external connection introduces a potential vulnerability. Rather than treating regulations as a mere compliance exercise, organizations should use them as frameworks to build practical resilience. This involves fully mapping technology dependencies, identifying concentration risks, updating contracts to reflect actual risk levels, and rigorously testing incident response plans in realistic scenarios. Organizations that understand their data flows and supply chain dependencies do more than satisfy regulatory requirements; they establish reliable foundations that build trust with institutional clients and partners. As regulatory enforcement becomes more rigorous following the initial implementation phase, superficial compliance is no longer adequate. Companies must transition from treating supplier risk as a deadline to viewing it as a core management priority. Genuine resilience means knowing exactly what happens if a critical supplier fails and having the proven capacity to maintain continuity during an actual incident, ensuring long-term operational stability.


AI is making cybersecurity fundamentals more important than ever

The rise of artificial intelligence in cyberattacks has led many to believe we need entirely new defensive playbooks. However, industry experts argue that AI actually makes traditional cybersecurity fundamentals more critical than ever. Rather than inventing entirely novel vulnerability classes, AI empowers attackers to execute familiar techniques—like social engineering, credential theft, and exploiting unpatched software—at unprecedented speed and scale. Because AI systems can continuously scan for misconfigurations and weak access controls, long-standing security debt is now a severe liability. To defend against these rapidly automated threats, organizations must double down on basic practices such as multifactor authentication, zero-trust architectures, routine system patching, and proper identity management. These foundational controls efficiently block entire categories of attacks, preventing modern adversaries from easily penetrating sensitive digital environments. While generative AI introduces specific new risks like prompt injection, most immediate threats still rely on conventional technical oversights. Furthermore, relying solely on AI for corporate defense without dedicated human oversight is a dangerous trap. Security professionals must clearly understand core principles to verify AI-generated recommendations and ensure that automated tools function correctly. Ultimately, the most effective strategy pairs a strong foundation of basic security hygiene with the massive scale of defensive AI, preserving essential human accountability.


Keeping Proprietary Data Out of AI Training Models

As artificial intelligence becomes a standard part of business operations, companies face a serious new risk: the accidental sharing of their private information. When employees use AI tools, the data they enter can sometimes be absorbed into the system's training models. According to legal experts, the primary danger here is the permanent loss of trade secrets and intellectual property. If your company's private strategies or customer details are used to train a public AI model, that information could eventually benefit your competitors. Currently, many organizations handle this risk poorly by keeping their legal, security, and purchasing teams in separate silos. This separation often allows hidden AI features in standard software updates to slip through the cracks. To fix this, companies must adopt a unified, cross-functional approach to reviewing new technology. Most importantly, businesses cannot rely on simple opt-out buttons or marketing promises to protect their assets. Chief Information Officers and legal teams must demand strict, written guarantees in their vendor contracts. These agreements must clearly state that no company data, including prompts and inputs, will be used to train or improve any AI models. Furthermore, companies must secure the right to independently audit vendors to ensure complete and ongoing compliance.

Daily Tech Digest - June 21, 2026


Quote for the day:

“Any architecture that is too complex to explain is probably wrong.” -- Martin Fowler

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Compliance Without Chaos In Modern Delivery

Treating compliance as a sudden, stressful emergency before an audit is both painful and unnecessary. Instead of bolting rules onto the very end of software delivery, engineering teams can build straightforward checks directly into their daily routines. When you integrate requirements into the tools developers already use, the process stops feeling like an obstacle course. By tying approvals to code reviews and enforcing standards through automatic checks, your regular deployment systems naturally generate all the proof an auditor needs. This approach removes the need to hunt down scattered evidence across chat logs and spreadsheets, turning documentation into an automatic background task. Furthermore, managing system permissions carefully and continuously monitoring critical settings helps keep minor oversights from escalating into major incidents. Preparing for reviews should look much like preparing for a standard software update, relying on simple, repeatable checklists rather than frantic last-minute efforts. Ultimately, compliance works best when it functions as a shared operational habit across every department. By making security guidelines clear, practical, and automated, teams can maintain momentum while turning complex audits into routine, minor administrative checks.


SDLC Data Governance Critical as AI Systems Outpace Human Oversight

As artificial intelligence rapidly accelerates the pace of software development, engineering teams face a growing challenge in overseeing vast changes made with minimal human involvement. With AI systems now capable of independently writing thousands of lines of code, running tests, and deploying product features overnight, traditional manual reviews are no longer practical or safe. This shift requires organizations to move away from treating governance as a slow, end-of-process afterthought. Instead, they must build active controls directly into the software delivery pipeline. Currently, a significant gap exists because many companies lack the automated audit trails needed to track these autonomous activities, creating serious compliance and security vulnerabilities. To address this, organizations must establish systems that enforce policies and validate code at the exact moment it is generated. This approach demands a clear focus on traceability and explainability, ensuring that every automated decision can be clearly understood and audited. As a result, software engineers are evolving from daily implementers into strategic orchestrators who manage and direct these pipelines. Success ultimately depends on fostering a culture of shared responsibility across departments to ensure that autonomous delivery remains fully accountable and easy for humans to monitor.


Agentic AI’s challenge is getting agents to act like a team, not a crowd

Adding more artificial intelligence agents to a company does not automatically improve operations; in fact, uncoordinated agents can create confusion and conflicting decisions. As businesses expand from single experimental tools to multiple agents working across departments like finance and supply chain, the main obstacle is getting these units to cooperate. To solve this, companies need a central coordination system that acts as a manager. This system relies on four key functions: distributing tasks appropriately, maintaining a shared memory so all agents access the exact same data, enabling instant communication during unexpected events, and providing strict safety and compliance oversight. When agents share a single version of the truth, operations run much smoother. For example, connected systems can automatically identify and fix IT issues, noticeably reducing downtime. However, significant hurdles remain. Organizations struggle with fragmented and poor-quality data, which inevitably leads to flawed automated decisions. Furthermore, balancing automated freedom with necessary human judgment on sensitive or high-risk matters continues to be difficult. Ultimately, the true value of multi-agent systems relies entirely on the strength of their shared infrastructure rather than the sheer number of agents deployed.


When Everyone Uses AI, Companies Risk Losing Critical Skills

As companies adopt artificial intelligence for everyday tasks, they face a quiet but serious risk: losing the essential human skills that keep their businesses strong. When employees rely on technology to write reports, analyze numbers, and solve standard problems, they miss out on the daily practice required to build deep expertise. Traditionally, junior staff develop intuition, critical thinking, and sound judgment by working through basic, practical assignments. By handing these core learning opportunities over to automated systems, organizations accidentally break their internal development paths. Over time, a company's shared knowledge can fade, leaving future managers without the practical foundation needed to judge automated answers or steer the business through unexpected crises. To prevent this talent gap, executives must rethink how daily work and professional growth fit together. Instead of focusing only on immediate speed and cost savings, leaders need to deliberately create moments where staff are forced to practice independent reasoning. Companies must protect their core capabilities by treating technology as a helpful assistant rather than a complete replacement for human thought. Ultimately, true resilience comes from capable people who know how to think for themselves.


The Attack Surface Your Security Team Isn’t Governing Yet

The rapidly rising use of artificial intelligence agents introduces a growing attack surface that standard security tools cannot effectively monitor. While security teams have historically focused on managing human users, machine accounts now outnumber them and create severe vulnerabilities. Unlike regular human users who log in, complete a specific single task, and leave a simple audit log, these autonomous agents operate continuously across multiple systems at once. They make independent decisions and link tasks together in ways that older software cannot track. To maintain control, organizations must move beyond basic identity management, which only asks who has access, and focus instead on tracking the actual actions these software agents perform. Adding these controls after the systems are already live is a failing approach, because the behavior is too complex to untangle later. Security leaders must build clear rules and full visibility directly into the core infrastructure from the very beginning. By creating permanent, reliable records of every single action an agent takes, companies can protect their sensitive data and easily provide concrete proof of safe operation to external regulators, board members, and internal executive leadership teams.


We Had a Perfectly Good Data Store. That Was the Problem

In this article, a data engineering professional shares the realization that recurring data quality issues are often architectural flaws rather than problems with the information itself. When an organization faces constant complaints about late or incorrect data, engineers usually waste time fixing symptoms instead of addressing the underlying cause: forcing an operational database to serve analytical users. To solve this, the team successfully migrated reference data from MongoDB to a governed platform without replacing the original database. Their approach relied on three major decisions: retaining MongoDB as the definitive source of truth, consolidating four independent extraction pipelines into a single path using Kafka and Iceberg tables on S3, and treating published data as a clear product. This effectively separated data truth, transport, and consumption into distinct layers. Interestingly, the primary hurdles during this transition were not technical pipeline components, but rather social and organizational friction. Overcoming disagreements around data ownership, naming conventions, and searchability proved to be the most demanding part of the process, demonstrating that a successful architecture relies just as much on clear human alignment as it does on the underlying software.


How Application Control Engines Support Zero Trust Security Strategies

This article explains how application control engines serve as a foundational enforcement layer within a zero-trust security architecture. Traditional workplace security practices often assume that software initially installed by internal IT departments is inherently safe. In contrast, zero-trust strategies reject this premise, operating under a default-deny rule where no software is trusted automatically. An application control engine translates this philosophy into technical enforcement by dictating exactly what programs can run, how they operate, and what data they can access. Crucially, the engine does not just evaluate applications at the time of installation; it continuously monitors their behavior in real time during execution. This ongoing runtime oversight is vital for stopping sophisticated threats, like fileless attacks, that hijack legitimate, pre-approved software to bypass traditional filters. By establishing centralized policy management, these engines ensure consistent rules across an entire network, which also simplifies compliance with major regulatory frameworks and cyber insurance mandates. Ultimately, integrating an application control engine moves an organization away from fragile assumptions of trust, replacing them with a reliable, data-driven system of continuous verification that protects software at the execution layer.


Metal-to-agent is the foundation of scalable enterprise AI

As artificial intelligence usage expands rapidly inside enterprises, relying entirely on metered external cloud services is becoming financially unsustainable. Red Hat chief technology officer Chris Wright argues that organizations must transition from renting outside models to operating their own internal computing infrastructure. To solve this, the company proposes a unified framework that connects raw physical hardware directly to automated software assistants. This layered setup organizes the technology stack into five distinct tiers: a stable operating system that shares expensive processors efficiently, an optimized delivery tier that speeds up response times, a central control gateway that enforces usage limits and prevents system overloads, a secure management hub for software agents, and a flexible hardware base that avoids strict vendor dependency. Wright notes that because open source models are advancing fast enough to match major commercial options in a matter of months, signing rigid contracts with a single provider is a dangerous gamble. By adopting a platform run entirely on their own servers, businesses maintain the freedom to choose the best tool for each job, keeping operating expenses predictable while ensuring sensitive company data remains strictly protected.


Why resilient data centres are built, not just designed

In this article, the author explains that true data centre resilience cannot merely exist on paper; it must be proven through careful, real-world execution. While power distribution plans often look flawless during the design phase, the actual construction and implementation introduce significant practical challenges. A major hurdle involves working within live operational environments, where upgrades or expansions must occur without interrupting existing services. This requires meticulous coordination, detailed risk assessments, and precise sequencing, particularly when working near energized systems. Furthermore, electrical setups are deeply tied to critical mechanical components like cooling systems, which often consume a massive portion of the facility's total energy. Misalignment between these teams during installation can create serious operational risks. Long-term success also depends heavily on high-quality commissioning and thorough documentation to ensure the infrastructure remains fully maintainable over time. Ultimately, as growing demands from digital services and artificial intelligence put more pressure on infrastructure, building a reliable facility requires an understanding of how systems interact under real conditions. True resilience is not just an abstract concept; it is something that must be built, tested, and verified on-site.


5 Strategies for Reinforcing Supply Chain Cybersecurity

As digital tools become deeply integrated into manufacturing, interconnected supply chains face greater exposure to online threats. A single breach at an outside supplier can halt operations, compromise private data, and create severe legal liabilities. To secure these systems, companies can adopt five straightforward practices. First, monitoring early threat indicators helps teams spot and block minor attacks, such as phishing schemes targeting smaller vendors, before they hit main production lines. Second, businesses should build and regularly practice an incident response plan that covers traditional computer networks as well as physical factory equipment. Third, digital security must be built into new technology from the very beginning rather than added as a quick fix later. Fourth, executives must encourage open cooperation across all internal departments, ensuring that legal, purchasing, and factory operators share responsibility instead of working alone. Finally, organizations need a thorough oversight program for their external contractors, relying on upfront evaluations, clear contract rules, and routine audits. Treating defense as a normal part of daily operations allows manufacturers to grow safely while keeping their essential infrastructure running smoothly without sudden disruption.