Showing posts with label Board Oversight. Show all posts

Daily Tech Digest - November 20, 2026

Quote for the Day
“Crisis is the ultimate test of leadership.”
— John Chambers
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

AI coding agents need a safe place to work; Eclipse is building the sandbox to give it to them

As AI coding tools evolve from simple assistants into autonomous agents that execute commands and modify software, they require more freedom to be productive. However, unrestricted access poses significant risks, such as exposing credentials or making unintended changes to systems. To address this problem, the Eclipse Foundation recently introduced Eclipse Enclave 1.0, an open source sandbox that provides a safe, isolated environment for AI coding agents to operate. Instead of forcing developers to supervise every single action, which defeats the entire purpose of automation, Enclave allows these agents to work independently within strictly defined boundaries. Developers can grant access only to the specific files, tools, and web resources needed for a particular task, keeping sensitive information like API keys completely out of reach. The platform even supports running multiple agents in parallel on entirely separate tasks without any interference. Originally built as an internal tool by EclipseSource, this vendor neutral infrastructure successfully shifts the developer role from constant supervision to higher level planning and review. While sandboxing cannot eliminate every risk associated with autonomous code generation, Enclave offers a practical framework to manage those risks while remaining independent.

Read Original Article →

CISO Conversations: Patti Degnan – Part of the Job Is Deciding What Not to Do

Patti Degnan’s journey to becoming the Chief Information Security Officer at Glow, an AI-powered endpoint security firm, began unexpectedly after her identity was stolen in 2006. This personal incident sparked a deep interest in data privacy, leading her through internal audit roles and eventually into senior security leadership positions at companies like Symantec and Notion. Degnan firmly believes that effective cybersecurity leadership requires a strong desire to lead and the ability to align security strategies with overall business goals. While technical knowledge is highly valuable, she argues that a CISO does not need to be a hands-on developer; instead, they must excel at communicating complex technical risks to non-technical stakeholders across the organization. When building her teams, she prioritizes a candidate's ability to take real ownership of problems rather than simply collecting certifications. Addressing the widespread issue of industry burnout, Degnan emphasizes that a crucial part of leadership is deciding what not to do. By setting clear priorities, automating routine tasks with artificial intelligence, and encouraging necessary time off, she helps her team maintain the personal resilience required to manage constant security challenges.

Read Original Article →
Article Thumbnail

Why Visibility Without Action is Failing OT/IoT Security

For years, securing operational technology and connected devices relied on a simple idea: if you can see it, you can secure it. However, simply identifying a vulnerable device creates a dangerous gap between discovering a problem and actually fixing it. Today's automated threats move far too quickly for manual responses. Relying on alerts alone fails because security teams quickly become overwhelmed, and these specialized devices often lack standard operating systems that make updates easy. To close this gap, organizations must move beyond passive monitoring and adopt automated systems that handle routine security tasks like patching, updating passwords, and renewing certificates. These systems can work directly with the devices at scale, effectively blocking threats before they take hold. Yet, because these industrial systems control physical environments where a faulty update could halt production or cause damage, complete automation is too risky. A qualified human professional must always remain in the loop to carefully review and approve these critical changes. Ultimately, simply watching your network is no longer enough; true security requires automated action firmly guided by human judgment to protect physical operations safely.

Read Original Article →

Is Coding with AI Actually Faster and Cheaper?

Recent studies reveal that coding with artificial intelligence indeed accelerates development, though the overall impact on software delivery is more measured than hype suggests. Research tracking over half a million developers shows a massive jump in code commits, but a much smaller increase in actual software releases. While individual programmers generally complete tasks faster using these tools, the time saved during the initial coding phase often shifts into the review, testing, and auditing stages. Consequently, building software feels less stressful and somewhat quicker, but it is not an overnight revolution that drastically slashes production timelines. Regarding costs, the financial benefit largely depends on the capability of the AI model being used. Economic simulations demonstrate that highly capable agents offset the price of their tokens by producing fewer errors and reducing the need for human supervision. In contrast, cheaper but less effective models can quickly become expensive due to the necessary retries and bug fixes. Ultimately, capable AI tools do make coding faster and more cost-effective, yet the full expense of securely delivering and maintaining enterprise software has not dramatically collapsed across the broader tech industry.

Read Original Article →
Article Thumbnail

Why Strong Board Governance Requires Knowing When To Hit The Brakes

Effective board governance comes down to knowing precisely when to accelerate and when to hit the brakes. While many board members default to either cheerleading risky moves to please founders or stalling progress under the guise of risk management, exceptional directors master tempo control. To navigate high-stakes decisions effectively, boards should rely on three key principles: reversibility, information asymmetry, and the difference between trajectory and inflection. If a decision is easily reversible or simply speeds up a proven strategy, the board should accelerate the process. Conversely, if a move represents a permanent pivot or management lacks the necessary on-the-ground expertise, the board must intervene and force a deliberate pause to evaluate risks. For instance, rushing an aggressive international expansion without proper local knowledge can drain capital, whereas a strategic pause for thorough diligence can turn potential failure into a durable revenue stream. Ultimately, a board member’s true value lies not in asking the most questions, but in discerning strategic inflection points from mere noise, protecting capital while ensuring the enterprise scales with confidence and discipline.

Read Original Article →

A game you cannot win unless you have a quantum computer

Google researchers have successfully demonstrated "quantum contextuality" on a large scale, proving that quantum computers can solve specific problems impossible for classical systems. To illustrate this, they use a "magic square" puzzle where two players must fill a grid following contradictory rules. In classical physics, players lose because a pre-determined table cannot satisfy all conditions. However, using entangled qubits on Google's Willow quantum processor, the system won the game 98.3% of the time, easily beating the absolute classical limit of 88.9%. This happens because in quantum mechanics, the answers do not exist before measurement; instead, they are generated at the moment they are observed based on their context. The researchers tested these contextual properties across systems of up to 105 qubits, proving that this phenomenon survives as quantum computers scale up in size. Beyond solving theoretical games, these tests provided a highly sensitive benchmark for identifying subtle hardware errors that standard tests miss. This research confirms that contextuality, rather than just entanglement alone, is a fundamental engine driving the computational advantage of quantum machines, paving the way for more accurate quantum algorithms in fields like chemistry and materials science.
Read Original Article →
Article Thumbnail

How to Secure IT/OT Convergence Without Breaking Operations

As manufacturing environments increasingly connect their information technology and operational technology systems, securing this overlap has become a serious challenge. Most cyberattacks that reach factory floors actually begin in the standard IT network, exploiting pathways created by integrated tools or third-party vendor access. The core issue is that these two environments operate with entirely different priorities and timelines. Standard IT focuses on speed and regular updates, while operational systems prioritize continuous uptime and safety, often relying on legacy equipment that runs for decades and cannot accept modern software patches. Because standard security controls do not translate well to factory floors, companies must adopt frameworks designed specifically for physical operations. This involves prioritizing process safety, implementing strict network segmentation, and managing remote access with time-limited, closely monitored sessions rather than open connections. Using digital certificates helps authenticate connected devices, ensuring only trusted equipment accesses the network. Furthermore, new global compliance standards are shifting how companies buy equipment, requiring manufacturers to embed security features directly into the design phase. By understanding these distinct operational constraints, organizations can better protect their critical infrastructure without disrupting daily production.

Read Original Article →

Chaos, then control: the maturity model most AI rollouts skip over

When engineering teams roll out new artificial intelligence tools, they often notice a strange gap: a few people achieve massive productivity gains, while most just use the tools like a fancy autocomplete. According to a five-stage maturity model, this happens because leaders skip the messy but essential middle steps of a proper rollout. The process should start by letting chaos reign as people experiment, followed by discovering what actually works, codifying those discoveries into shared practices, scaling them across the entire group, and only then reorganizing the team around the new reality. Unfortunately, eager to show quick financial returns, many organizations simply buy the software licenses, wait for the dust to settle, and immediately try to restructure roles based on guesses. To truly succeed, leaders need to pause and closely study their most adventurous engineers during the initial rollout. By identifying their successful habits and translating them into a clear, shared set of daily practices, companies can actively teach the rest of the team how to improve. That unglamorous middle work is the only reliable way to turn scattered individual wins into lasting team-wide success.

Read Original Article →
Article Thumbnail

Your liveness check passed. Was there ever a camera?

Passing a biometric identity check does not always mean a real person is sitting in front of a camera. While many security systems are built to catch someone holding a printed photo or mask up to a lens, criminals are now bypassing cameras entirely. By feeding fake videos or doctored images directly into the verification software, they can open fraudulent accounts with ease. These injection attacks require a different type of testing and defense than traditional physical spoofs. For smaller banks and businesses without dedicated fraud teams, it is crucial to ask technology vendors directly about their specific protections against these camera bypass methods. Instead of relying solely on the facial image, organizations should examine the broader context of the session, such as device data and location signals. Staff should be given clear guidelines on what to look for when a system flags a suspicious entry, rather than being expected to spot artificial images by eye alone. Placing temporary limits on new accounts can also reduce risk. Ultimately, treating a passed facial scan as absolute proof of physical presence is a blind spot that modern security programs must correct.

Read Original Article →

Learning the language of machine learning

MIT Associate Professor Jacob Andreas is working to make artificial intelligence more transparent by teaching machine learning models to explain their own internal processes using everyday human language. Currently, many neural networks operate as "black boxes," meaning their decision-making is difficult to audit or understand. Andreas and his research group are addressing this by developing techniques that allow AI systems to accurately describe what they have learned from their training data. Instead of relying on external tools to decipher a model's behavior, his approach trains the models to talk about themselves and their reasoning directly. His team also focuses on building systems that can learn from simple descriptions rather than millions of examples, similar to how humans learn from a single recipe. Because the field of AI evolves rapidly, often reinventing itself every few years, Andreas continuously updates his courses so students understand the foundational mechanics behind the technology. Ultimately, his research aims to build trustworthy, interpretable AI systems that can honestly communicate their capabilities and limitations, helping to establish a clearer scientific understanding of how models behave in the real world.

Read Original Article →

Daily Tech Digest - November 07, 2026

Quote for the Day
“An approximate answer to the right question is worth far more than a precise answer to the wrong one.”
— John W. Tukey
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The post-quantum future of web privacy

The Cloudflare blog post explores the transition of web privacy protocols—specifically Privacy Pass—into a post-quantum world through a new technology called MOLE (Moderation Of unLinkable Endorsements). Privacy Pass currently uses classical cryptography (like RSA and elliptic curves) to issue anonymous tokens that allow users to access websites without solving CAPTCHAs or sacrificing their identity. While these tokens are unconditionally private against all attackers, a future quantum computer could forge them and bypass site security measures like rate limiting. To address this, the industry is developing MOLE to handle automated traffic while maintaining strict user privacy. The challenge in upgrading to post-quantum cryptography is the massive increase in data size; for instance, post-quantum ML-DSA-44 signatures are nearly forty times larger than current ECDSA signatures. Because drop-in replacements are not feasible right now, systems will need to be re-engineered to handle heavier cryptographic loads. Ultimately, MOLE and recent breakthroughs in blind signature design offer a promising pathway to secure, seamless, and fully private web authentication long after quantum computers become a reality.

Read Original Article →

The boardroom blind spot: you're measuring compliance, not culture

The boardroom blind spot lies in confusing compliance metrics with actual workplace culture. While corporate boards carry a clear mandate to oversee organizational culture and manage psychosocial risks, they often rely on lagging indicators like headcount, absenteeism, and turnover rates. These data points, typically extracted from standard Human Resource Information Systems, capture transactions and historical events rather than revealing why employees are disengaged or if leaders truly hold their teams' trust. This reliance on compliance-driven data creates a governance gap, masking underlying cultural decay until it erupts into costly turnover or a public crisis. To bridge this gap, modern organizations are pairing core compliance systems with purpose-built employee experience platforms. By tracking real-time insights, boards and executives can capture genuine human intelligence regarding psychological safety and cultural cohesion before problems escalate. Effectively overseeing culture means moving past mere workforce maintenance to active workforce engagement. Ultimately, evaluating whether existing tools actually measure employee sentiment or merely record transactions is no longer just an operational decision—it is a critical governance responsibility.

Read Original Article →
Article Thumbnail

Identity as an Architectural Concern: Enterprise IAM Beyond Authentication

The article emphasizes that as organizations scale, particularly in regulated environments like financial services, identity and access management (IAM) must be integrated directly into a system's core architecture rather than bolted on as an afterthought. For a single application, setting up basic single sign-on (SSO) and authenticating tokens might suffice. However, enterprise systems face complex governance challenges, such as tracking who approved specific access rights and verifying if those rights remain valid months later during an audit. Traditional flat Role-Based Access Control (RBAC) often struggles with these complex relationship queries. The author explains that shifting to a graph-based data model (like Neo4j queried via GraphQL) is far more effective for managing entities like people, service accounts, and resources. In a graph, ownership and access validity are straightforward traversals rather than cumbersome table joins. Designing the data schema early to capture timestamped events for every grant and revocation ensures that critical questions—such as who had access on a specific past date—can be answered efficiently, ultimately reducing the time needed to manage and revoke credentials.

Read Original Article →

The Next Target for Data Breach Lawsuits – Law Firms That Represent Breached Parties

The The Next Target for Data Breach Lawsuits – Law Firms That Represent Breached Parties examines whether lawyers advising companies after data breaches could themselves become targets of lawsuits from affected customers. It draws an important distinction between a law firm being sued because its own systems exposed personal information and being sued for advice given to a breached client about notification and disclosure. Existing legal precedent generally holds that lawyers owe duties to their clients, not automatically to third parties affected by their clients’ actions. This creates a significant hurdle for customers attempting to claim malpractice against outside breach counsel. However, law firms that receive and store personal information may still face ordinary data-security claims if their own handling of that information is challenged. The article warns that expanding liability for breach-response advice could complicate attorney-client relationships, increase insurance and legal costs, and make lawyers more cautious when advising on difficult notification decisions. Its central point is that future lawsuits may increasingly name breach lawyers as defendants, but plaintiffs will still need to establish why those lawyers owed them an independent legal duty.

Read Original Article →
Article Thumbnail

Master Data Management: The Foundation of Enterprise Data Architecture and Security

Modern organizations often struggle with highly inconsistent data that is scattered across many different systems like human resources, billing, and customer management. When the exact same customer or employee is tracked differently in each independent system, it creates confusion that goes far beyond simple record keeping. This inconsistency can easily lead to improper access grants and real security risks if critical updates, such as department changes, fail to reach every application. Master Data Management addresses this exact problem not just by centralizing storage, but by establishing a single, authoritative understanding of core business entities. It clearly establishes who owns the data, where it originally came from, and what relationships exist between different records. This clarity is essential for a reliable enterprise architecture and strong internal security. Instead of applying security controls blindly, identity and access management systems can rely on this accurate, consolidated information to enforce appropriate permissions and data protection rules across the board. By providing proper context and consistent metadata, Master Data Management ensures that applications apply the right security measures, ultimately serving as the reliable foundation needed to keep organizational information completely secure.

Read Original Article →
Article Thumbnail

Study Maps 24 Problems Where Quantum Computers Could Gain an Edge

A recent study has identified 24 computational problems where quantum computers could significantly outperform standard computing methods. However, the researchers emphasize that achieving this theoretical edge in real-world scenarios requires meeting strict mathematical and operational conditions. The compiled list spans diverse fields, including chemistry, optimization, number theory, and data analysis. While quantum algorithms might need far fewer steps to solve complex challenges, such as calculating a molecule's lowest energy state or solving systems of linear equations, practical hurdles remain. Time-consuming tasks like preparing initial data, correcting errors, and extracting usable results can quickly erase any expected speed gains. Furthermore, a meaningful improvement requires the quantum machine to solve problems at a rate exponentially or cubically faster than standard computers to offset the high operating costs of early error-corrected hardware. The study divides these 24 problems into two stages based on their readiness for practical application, providing a realistic roadmap for scientists and industry specialists. Ultimately, the research cautions that translating mathematical advantages into affordable, useful solutions for pressing business and scientific challenges requires overcoming significant hardware and data processing barriers.

Read Original Article →
Article Thumbnail

The CIO’s trust paradox: Your team may be more honest with AI than with you

The CIO’s trust paradox: Your team may be more honest with AI than with you argues that AI is creating a new challenge for workplace trust: employees may be more willing to raise concerns with an AI assistant than with their managers. Research cited in the article suggests psychological safety alone is not enough. Strong teams also need accountability, while trust in AI depends partly on people’s ability to handle uncertainty and judge when AI should be trusted or questioned. The more troubling possibility is that an employee may openly challenge a flawed idea when talking to AI, yet remain silent when the same issue appears in a meeting with senior leaders. In that situation, the organization possesses valuable insight but never receives it. The author urges CIOs to look beyond AI adoption figures and employee sentiment surveys and examine whether dissent actually influences decisions. Organizations should also provide safe ways for employees to move concerns discovered through AI conversations into human decision processes without monitoring private conversations. The central message is that leaders should ask not only whether employees trust AI, but whether they trust colleagues and managers enough to repeat what they tell AI.

Read Original Article →

How technical debt hinders AI rollouts and what to fix first

Technical debt often prevents organizations from successfully rolling out artificial intelligence initiatives, turning expected modernization into costly and disconnected infrastructure islands. For years, enterprises have allowed legacy systems and fragmented tools to coexist, leading to outdated security, siloed data, and inefficient resource allocation. When companies try to implement AI on top of this unstable foundation, they typically face escalating deployment times, decreased feature stability, and significant security risks from unmonitored AI agents carrying overly broad permissions. The resulting complexity forces organizations to manage and secure separate platforms simultaneously. To fix this, IT leaders must assess how their existing technical debt impacts their specific AI goals and plan the financial cost of modernization directly into their AI business cases. Priority should be given to integrating siloed data sources and establishing strict identity and access guardrails for AI agents. By piloting small, focused projects that address these foundational issues rather than attempting massive overhauls, businesses can clear the critical roadblocks, minimize infrastructure churn, and build a secure path for scalable, productive AI adoption.

Read Original Article →
Article Thumbnail

Enterprise FinOps: How CIOs Can Reduce Total Technology Cost by 30% or More

To achieve significant cost savings in technology, modern business leaders must expand their focus beyond simple cloud management and adopt a comprehensive financial operations strategy across their entire technology portfolio. With the rapid expansion of software subscriptions, independent contractors, and artificial intelligence experiments, hidden expenses easily accumulate in isolated departments. The primary culprits of this financial waste are duplicate software tools, unused premium licenses, unsupervised departmental purchases, and contractors who remain on payroll long after their initial projects end. To counter this, technology leaders need clear visibility into how every asset is consumed and what tangible value it delivers. By tracking software usage, renegotiating vendor contracts, adjusting service level agreements to match actual needs, and hosting artificial intelligence models on internal infrastructure where practical, organizations can uncover substantial inefficiencies. Addressing these hidden expenses allows leaders to safely reduce the massive budgets typically required just to keep basic systems running. Ultimately, recovering up to thirty percent of these everyday operational costs frees up essential capital, allowing the business to invest heavily in necessary modernization, new capabilities, and sustainable future growth.

Read Original Article →
Article Thumbnail

Can blockchain rewire India’s cross-border payment infrastructure?

Blockchain holds the potential to significantly improve India’s cross-border payment infrastructure, primarily by transforming back-office operations rather than creating new front-end experiences. Currently, international transactions rely on multiple intermediaries, messaging networks like SWIFT, and separate ledgers, which lead to slow reconciliations and delayed settlements. By introducing a shared, synchronized distributed ledger, blockchain could enable banks to reconcile transactions in real time, dramatically shrinking the delays caused by failed payments. Experts suggest that if countries adopt compatible blockchain standards, connecting their financial systems would become much more seamless. However, technology alone cannot solve the economic challenges of internationalizing the rupee or reducing dependency on the US dollar. While blockchain offers a faster and more efficient pipe for moving money, true global adoption requires robust bilateral trade, stronger exports, and comprehensive regulatory frameworks. Governments and participating institutions must still agree on validation rules, legal rights for tokenized assets, and dispute resolution mechanisms across jurisdictions. Ultimately, the success of blockchain in international finance will depend less on the code itself and more on whether regulators can build the legal foundation it needs to operate securely.

Read Original Article →

Daily Tech Digest - October 09, 2026


Quote for the day:

"An inch of movement will bring you closer to your goals than a mile of intention." -- Vala Afshar

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 29 mins • Perfect for listening on the go.


Making the Case to the Board for Post-Quantum Readiness

When presenting post-quantum readiness to the board, technology leaders must avoid technical physics jargon and instead frame the conversation entirely around business exposure. Directors do not need a lesson on qubits; they need to understand which critical services and data are vulnerable and what the transition will cost. A primary concern is the “harvest now, decrypt later” tactic, where attackers steal encrypted sensitive data today to break it when quantum capabilities mature. Because sensitive information retains its value for decades, the threat is immediate. Leaders should avoid predicting an exact date for when quantum computers will break current encryption. The focus should remain on the long lead time required for migration, which can span up to fifteen years. To secure board approval, leaders should ask for funding in manageable stages. The initial request should focus on discovery, giving the team about eighteen months to assess vulnerable cryptography, identify critical services, and map third-party dependencies before proposing a massive enterprise-wide budget. Waiting only increases the final price tag and risk. Ultimately, framing this as a staged, no-regrets investment builds trust and ensures the organization strengthens its overall security foundation regardless of when the quantum threat fully materializes.


AWS’s repeated problems with AI agent controls illustrates the autonomous agent dilemma

Recent security vulnerabilities in AWS AgentCore highlight a fundamental dilemma for enterprise technology leaders: the very autonomy that makes artificial intelligence agents useful also makes them inherently dangerous. Cybersecurity researchers from Palo Alto Networks and Zenity Labs repeatedly found that attackers could use simple prompt injections to trick these agents into handing over plain text credentials. Because agents require tools like shell commands and network access to function, they operate in the same environments where sensitive data is stored. In one severe example, researchers compromised a single agent and gained the ability to extract source code, access other agents, read private conversations, and persistently poison memory. This memory poisoning is particularly concerning because, unlike stolen credentials that can simply be rotated, altered memories quietly steer future actions and are incredibly difficult to detect. While AWS has worked to patch these specific entry points, the underlying issue is that the agents functioned exactly as designed by fulfilling the requests they received. This means the responsibility falls heavily on organizations. Technology teams must therefore strictly enforce proper access limits, closely monitor all agent behavior, and carefully control the potential damage to prevent a single compromised agent from exposing the entire network environment.
The article explores what manufacturing plants truly need to make prescriptive AI effective, drawing on eight audience questions answered by experts from Siemens and Infinite Uptime. A central theme is that most plants still struggle with data quality and availability, yet waiting for perfect data before deploying AI is unrealistic. The experts argue that physics‑informed models, combined with targeted sensor retrofits, allow plants to start generating reliable insights quickly, even in brownfield environments with decades‑old equipment. They explain that prescriptive AI works best when multiple sensing methods—such as vibration, thermal imaging, and machine vision—are combined to capture different failure modes. The discussion also breaks down how diagnosis should progress: anomaly detection first, then classification, and finally linking those classifications to documentation and automated “therapy” suggestions. Several questions focus on practical economics, including when it’s cheaper to replace a part than predict its failure and how much algorithm audits typically cost. The experts emphasize building quantitative decision models rather than relying on rules of thumb. The article closes by stressing data trust and security, noting that companies must use controlled environments for LLMs and treat AI‑generated data with the same rigor as physical products. The overall message is steady and pragmatic: prescriptive AI succeeds when physics, data, and human judgment work together.


The Clock Starts Before the Restore: Measuring Recovery Time and Data Recovery Capability

The article argues that organizations often measure disaster recovery performance in a way that hides the real delays that occur before anyone starts restoring systems. It opens with an anecdote from the 1970s, where a team could technically recover from a failure in five minutes but took more than thirty minutes to decide to act. The author explains that this gap still exists today because most recovery tests measure only the restoration phase, not the time spent detecting issues, triaging them, and making the decision to declare an incident. To fix this, he introduces the idea of Recovery Time Capability (RTC)—a single clock that starts at the first sign of trouble and ends when the service is verified as working again. RTC breaks recovery into six segments, each with its own time budget and owner, making it clear where delays occur. He also defines Data Recovery Capability (DRC), which measures how long it takes to make data whole and trusted, especially in “cold case” scenarios where replicas are damaged and data must be restored from immutable vaults. The article closes with practical steps: timestamp every segment, test decision‑making with unannounced exercises, measure cold‑case recovery annually, and report gaps clearly to the board. The message is steady and pragmatic—real recoveries fail in the early minutes and the long data‑repair hours, not in the scripted tests we usually run.


I audited an award-winning AI project. The case study left out the cloud bill

The article highlights the hidden financial realities of enterprise artificial intelligence projects when they transition from a pilot phase into full daily production. During an audit of a celebrated document automation workflow, the author uncovered a massive discrepancy between perceived success and actual operational expenses. In the pilot phase, the system drastically reduced turnaround times for vendor agreements, earning internal praise while a central innovation fund quietly absorbed the computing costs. However, once the project went live and expenses shifted to the departmental budget, a harsh reality surfaced. Processing a single document surged to cost between twelve and fourteen dollars in cloud consumption and model access fees, compared to just eighty cents under the previous manual human workflow. This staggering cost increase occurred because real world documents are often messy, featuring handwritten notes, poor scans, and conflicting formatting. These inconsistencies forced the automated pipeline to trigger multiple expensive retrieval passes and secondary checks. Furthermore, roughly forty percent of the documents required human intervention to fix errors, which ultimately doubled the original manual processing time. Ultimately, falling base model prices do not guarantee cheaper business processes, as complex workflows can easily turn a predictable payroll expense into an unpredictable consumption meter.


From digital insurance to intelligent insurance: Why AI is becoming the new operating layer

The article explains how AI is shifting insurance from a digital‑first model to an intelligent‑first one, where technology becomes part of the business rather than a support function. Sriram Naganathan of HDFC ERGO describes how underwriting, pricing, fraud detection, claims, and customer service are increasingly shaped by machine learning, generative AI, and agentic systems. The company’s digital foundation—where most policies and service interactions already happen online—has made it possible to layer intelligence on top of existing processes. Examples include GenAI tools that simplify policy explanations and AI‑guided motor claims assessments using smartphone photos. The piece stresses that AI should assist human decision‑making, not replace it, especially in high‑value or sensitive claims where context and empathy matter. It also highlights the shift from data scarcity to the challenge of converting large volumes of historical information into actionable intelligence. Governance, explainability, and trust emerge as essential themes as AI begins influencing pricing, underwriting, and fraud decisions. The article notes a move toward smaller, specialised models and internally built capabilities that embed institutional knowledge. It closes by arguing that the future is not autonomous insurance but augmented insurance—where AI reduces friction and improves accuracy while humans provide judgment, oversight, and empathy when it matters most.


India is defining ‘DPI 2.0’ as it shifts beyond identity and payments

The article explains how India is shaping “DPI 2.0,” the next phase of its digital public infrastructure, by moving beyond identity and payments toward sector‑wide digital systems built on open standards, user control, and AI‑enabled services. It traces how DPI 1.0—Aadhaar, UPI, DigiLocker, and Direct Benefit Transfer—created shared public rails that proved reliable at national scale. DPI 2.0 extends this model into areas such as commerce through ONDC, financial data through Account Aggregator, healthcare via ABDM, and agriculture through AgriStack. A central theme is giving people more control over their data, supported by the Digital Personal Data Protection Act, while ensuring interoperability across ecosystems. The article highlights India’s push to integrate AI into DPI so services can operate in local languages and through voice, making them more inclusive. It also acknowledges past failures, such as authentication errors, and notes that cybersecurity, algorithmic accountability, offline access, and digital literacy are now core priorities. Internationally, India promotes open protocols rather than proprietary platforms, allowing countries like Indonesia to adapt the model to their own needs. The piece closes by noting governance tensions at home, where DPI lacks a clear legal definition, raising questions about safeguards for population‑scale systems. Overall, DPI 2.0 is presented as an evolution focused on trust, interoperability, and intelligent public services.


How to Turn Data Governance into a Decision System

Data governance programs often focus exclusively on managing the data itself, prioritizing tasks like documenting definitions, mapping lineage, and improving quality scores. However, treating data as an isolated asset misses its true purpose, which is enabling better organizational choices. To maximize value, organizations must transition from merely governing data to actively governing the conditions that make data driven decisions trustworthy. This involves bridging two distinct value chains. The standard path from data to wisdom drives operational and strategic business choices, while a parallel path from metadata to wisdom provides the necessary context to trust those choices. By focusing on critical, high impact decisions rather than generic data inventories, organizations can completely reverse their traditional governance logic. Instead of finding uses for available data, teams identify the essential decisions they need to protect and then work backward to determine the specific data, rules, and controls required. Consequently, priority is determined by business impact rather than abstract maturity scores. Fixing a missing definition or uncontrolled transformation matters because it directly protects a regulatory outcome or commercial offer. Ultimately, this approach transforms data governance from a routine compliance exercise into a robust decision system, giving business leaders the concrete evidence they need to act with absolute clarity and reliability.


AI changed my role before it changed my software

Tony Timbol shares how building an AI-assisted application completely shifted his perspective on software development. While attempting to convert a cumbersome, spreadsheet-based agile assessment tool into a lightweight app using an AI platform, his initial attempts failed. He realized the issue was not the AI but his approach: he was treating the tool like a programmer rather than a collaborator. When he shifted his focus from specifying coding details to clearly defining outcomes, user journeys, and behaviors, the AI quickly generated a functioning prototype. This experience taught Timbol that AI accelerates the coding process but fundamentally relocates the challenging parts of software engineering rather than eliminating them. While AI can write code rapidly, it cannot handle crucial architectural choices, make strategic compromises, manage system integrations like email notifications or authentication, or understand genuine user needs. As execution becomes faster and easier through AI, the true bottleneck shifts to human judgment and product strategy. Timbol concludes that the future of software development involves humans acting as product leaders who frame the right problems, recognize sound architectural decisions, and provide the essential context that machines lack to build secure and maintainable products.


PCI SSC calls for human approval of AI agent actions involving cardholder data

The article outlines new guidance from the PCI Security Standards Council on how to use AI safely in payment environments, emphasizing that AI systems must be tightly controlled, monitored, and never allowed to act independently on sensitive cardholder data. The Council stresses that organizations should clearly define each AI system’s purpose, permissions, and data access before deployment, using a “least agency” approach that limits what the system can do. A human must remain accountable for all AI‑generated output, and certain actions—especially those involving cleartext payment data—should always require explicit human approval. The guidance warns against combining sensitive data access, external communications, and unrestricted input in a single AI agent, recommending separation of duties and strong identity‑management controls. It also calls for thorough adversarial testing, continuous monitoring, and documented shutdown and rollback procedures for AI systems operating with partial autonomy. The Council advises keeping high‑impact secrets, such as passwords and cryptographic keys, out of AI systems entirely and using tokenized or encrypted data whenever possible. It also highlights the growing risk of AI‑assisted attacks, urging organizations to harden legacy systems, validate AI‑generated code, and maintain strict patching processes. Finally, the guidance reminds companies to assess external AI providers carefully, prohibit training on customer data, and ensure clear incident‑response expectations.

Daily Tech Digest - September 27, 2026


Quote for the day:

"The distance between insanity and genius is measured only by success." -- Bruce Feirstein

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Digital Twin Technology: A Comprehensive Guide

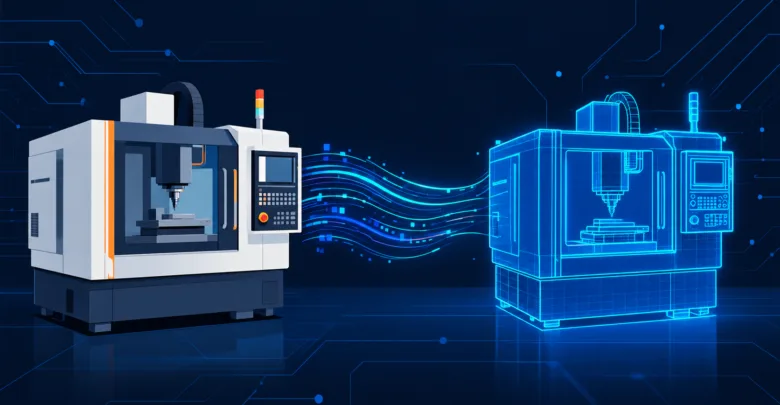
A digital twin is a dynamic, data-driven virtual replica of a physical object, process, or system. Unlike a static 3D model or a traditional one-time simulation, a digital twin continuously receives real-time data from sensors attached to its physical counterpart. This steady flow of information ensures the digital version mirrors the actual, current behavior of the real-world entity rather than just its original design specifications. The technology relies on three core components: the physical entity equipped with sensors, the virtual model, and the continuous data connection linking them. By maintaining this active connection, organizations can run highly accurate simulations, test new scenarios, and predict failures without risking the actual physical asset. The applications are broad and scalable, ranging from tracking a single component like an engine bearing to managing complex networks like a manufacturing production line or an entire modern city's infrastructure. While the technology offers incredibly powerful predictive capabilities, building an effective digital twin comes with several practical challenges. Organizations must manage data quality, handle complex modeling requirements, and navigate security concerns carefully. Because of this inherent complexity, experts recommend starting with a single, well-defined use case before attempting to scale up to larger, interconnected systems.


Three Hidden Traps That Shape Software Engineering Decisions

Engineering leaders face more than just technical challenges; they must also navigate human behaviors and cognitive biases that heavily influence software design and quality. The article outlines three common traps that developers and technical leaders fall into. The first is the "status quo bias," where teams stick to familiar tools or methods simply because "we've always done it this way," often ignoring newer, more suitable options for current requirements. The second trap is "complexity bias," which tempts engineers to overengineer solutions by adding unnecessary layers, abstractions, or services under the false assumption that complex designs are inherently more robust. This often leads to systems that are harder to maintain and prone to failure. Finally, the "broken windows" effect describes how an environment of poor code quality or neglected technical debt silently lowers a team's engineering standards. When developers see messy code or ignored warnings, they are more likely to introduce new shortcuts, gradually degrading the entire system. Recognizing and naming these biases helps teams pause, ask the right questions, and make more deliberate, evidence-based decisions rather than relying on flawed mental shortcuts.


How can boards gain confidence in their organization’s AI adoption?

Many corporate boards believe that establishing policies and risk frameworks is the key to governing artificial intelligence. However, Michael Covington argues that effective AI governance is impossible without first achieving comprehensive visibility into where and how AI is actually being used within the organization. Just as with the adoption of SaaS, cloud computing, and mobile technologies, companies are rushing to implement AI policies while lacking a basic inventory of their AI assets. Currently, over 70% of organizations deploy AI, yet more than 80% feel exposed to AI-related risks because adoption has vastly outpaced governance. This visibility gap is particularly dangerous because AI capabilities are increasingly embedded into routine software updates, meaning new tools can enter the corporate environment without any formal procurement or approval processes. This unchecked expansion poses risks beyond just security, potentially leading to unauthorized data access or widespread system disruptions. To solve this, leadership must treat AI like any other core technology asset. By integrating AI tracking into existing hardware, software, and cloud service inventories, boards can achieve continuous visibility. This foundational step transforms AI from an unmanaged liability into a measurable asset, allowing security, compliance, and finance teams to govern its usage with confidence.


The Factory Can Survive the Cyberattack. Can It Survive the Recovery?

Manufacturers have spent years investing in their ability to detect cyber threats, but detecting an attack is really only the beginning of the battle. In a factory setting, recovering from a cyber incident is far more complex than simply restoring digital assets or standard computer applications. It requires carefully bringing operational technology, such as programmable logic controllers and industrial machinery, back online in the correct sequence to avoid further issues. A technically successful software restoration can still result in operational failure if physical processes are restarted incorrectly or unsafely. To build true recovery readiness, manufacturers must map production dependencies outward from the physical process rather than inward from the network. This means identifying which critical operations must return first and defining the specific utilities, vendors, and human approvals required to support them. Organizations should assign recovery authority across tech, operations, and management teams ahead of time to prevent decision bottlenecks during an emergency. Finally, factories must practice realistic recovery scenarios where ideal conditions, such as the availability of key personnel or clean backups, are deliberately removed. Ultimately, a resilient manufacturer treats operational recovery as a designed and measured production capability, ensuring a safe, controlled return to dependable operations across the entire plant.


Why Enterprise AI ROI Is An Architecture Problem

Many companies struggle to see a positive financial return from their artificial intelligence efforts because of flawed system architecture, rather than the raw cost of the intelligence itself. Most organizations mistakenly build these capabilities by attaching them to disjointed legacy systems, forcing every new project to recreate rules and data connections from scratch. This fragmentation scatters information and makes proving economic value nearly impossible. To solve this and improve financial outcomes, businesses must adopt four core architectural changes. First, they should mandate a shared knowledge foundation to centralize enterprise data, eliminating the need to repeatedly rebuild integrations for each new tool. Second, they need to route tasks to the appropriate model based on complexity; simple tasks should use smaller, less expensive models, reserving advanced systems only for complex, high-value reasoning. Third, companies should prioritize groups of specialized tools over a single, massive program. Breaking tasks down into narrower, focused parts reduces the data processed at each step, significantly cutting costs and improving speed. Finally, organizations must build security and compliance directly into the core platform rather than adding them to individual applications, ensuring controls remain reusable and highly transparent. Ultimately, centralized architecture lowers deployment costs and clarifies actual value for the overall business.


Website Tracking Technologies Face Growing Litigation and Regulatory Scrutiny

Many companies use website tracking technologies like pixels, software development kits, session replay scripts, and chat tools to better understand how visitors interact with their pages. Working quietly behind the scenes, these tools gather data when a person clicks a button, views a product, or fills out a form. They then share this activity with third-party analytics and advertising companies. For years, businesses have relied on these insights to measure website traffic, track the effectiveness of marketing campaigns, and personalize the user experience. However, this routine data collection has recently become the center of a rapidly expanding wave of legal and regulatory action. Because these tools frequently transmit visitor information automatically and often before a user formally agrees to share their data, they have drawn severe scrutiny from privacy advocates and government agencies. Regulators and plaintiffs' attorneys are now scrutinizing exactly what information gets shared, with whom, and whether proper consent was obtained. In many recent lawsuits, these common marketing tools are being classified as wiretapping and eavesdropping devices that unlawfully disclose personal information. Ultimately, while tracking technologies provide businesses with valuable insights into customer behavior, they are now introducing substantial legal risks that demand careful oversight and strict compliance.


Clean Architecture: 5 Layers Every Developer Should Understand in 2026

Clean Architecture provides a structured way to build software by firmly separating core business rules from external details like databases, user interfaces, and frameworks. This approach relies on a central principle called the Dependency Rule, which dictates that source code dependencies must only point inward. The architecture is typically divided into five distinct layers to manage these boundaries. At the very center are Entities, which represent pure, framework-independent business logic that rarely changes. Surrounding them are Use Cases, which define application-specific rules and coordinate data flow without knowing about the database or web framework. Next are Interface Adapters, such as controllers and presenters, which carefully translate data between the inner core and the outside world. Further out is the Infrastructure layer, containing concrete implementations like third-party libraries and database adapters. Finally, the outermost layer consists of Frameworks and Drivers, which act as the basic glue holding the application together at startup. By strictly enforcing this inward dependency throughout the codebase, developers can ensure their applications remain completely testable and highly adaptable over time. This clear structure allows teams to comfortably swap out databases or web interfaces down the line without ever risking the fundamental logic that makes the product work.


The duality nobody priced in: The changing landscape of enterprise tech architecture and Agentic AI era

Enterprise technology is currently undergoing its most significant architectural shift in thirty years, driven primarily by the transition to agentic artificial intelligence. For decades, traditional enterprise systems were designed to standardize business processes, keeping core operations highly structured while placing customizations and early AI tools safely at the outer edges. Generative AI fundamentally breaks this familiar pattern by moving from transaction-driven operations to intent-driven software. Instead of following rigid, pre-defined rules, agentic applications accept a specific goal and determine their own path, effectively shifting business logic into a complex central orchestration layer. While this promises considerably faster software production, it introduces substantial new challenges in data governance, cost management, system testing, and operational oversight. Organizations now face a choice in how to integrate this technology: replacing old automation, layering agents over existing systems, running them in parallel, or embedding them deeply into core frameworks. Ultimately, true success requires much more than just launching rapid prototypes to showcase capabilities. The enterprises that will thrive in the coming decade are those that resist the urge to rush and instead focus on building robust architectural foundations, carefully balancing the speed of new technology with necessary operational reliability and long-term security.


With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

The rapid adoption of AI agents is exposing significant blind spots in traditional SOC 2 compliance frameworks. Originally designed with human actors in mind, SOC 2 controls rely on foundational assumptions that do not apply to machine identities. Because the framework does not explicitly mandate treating AI agents as a distinct class of users, organizations can pass audits while harboring unrecognized security risks. Specifically, four core assumptions are now breaking down. First, unlike human users who require formal approval before account creation, agents are often spawned automatically or indirectly. Second, determining the true owner of an agent is frequently a matter of guesswork rather than a clear record. Third, because AI agents often operate using borrowed human credentials, access logs cannot reliably distinguish between human and machine activity. Finally, traditional least-privilege principles limit an agent's reach but fail to explain its actual intended purpose. These gaps weaken critical controls, such as offboarding processes that overlook active agents tied to former employees, and change management where agents bypass genuine segregation of duties. To maintain true security, organizations must look beyond the compliance checklist, intentionally track machine identities, and match an agent's access directly to its specific purpose.


Your architecture diagram is not your resilience

An architecture diagram represents a system as it was intended to be, but it cannot prove whether that system is truly resilient today. Microsoft emphasizes that resilience is no longer a one-time project you can set and forget. Instead, it is an ongoing property you must actively maintain. Over time, architectures drift as systems change. For instance, a database might support failover, but an application's connection string could remain pinned to a single region. Because diagrams lack timestamps and operational reality, they often fail to capture this drift. Furthermore, the nature of dependencies is evolving. While traditional disaster recovery focuses on infrastructure, modern systems increasingly depend on AI models and inference endpoints. These dependencies introduce new risks, as AI can produce varying responses and may become unavailable or capacity-constrained. To manage these shifts, organizations must move beyond relying on static diagrams and adopt a continuous validation approach. Microsoft recommends designing resilience from the beginning, defining clear recovery objectives, and understanding your actual blast radius. Tools like the Azure Infrastructure Resiliency Manager and fault injection through Azure Chaos Studio can help teams test failover paths and measure their posture, ensuring that their intended resilience matches reality.