Showing posts with label database. Show all posts

Daily Tech Digest - September 05, 2026


Quote for the day:

"Success... seems to be connected with action. Successful people keep moving. They make mistakes, but they don't quit." -- Conrad Hilton

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Why is the Cloud Changing Again?

The rise of artificial intelligence is fundamentally changing how companies store and manage their data, moving the industry away from a one-size-fits-all public cloud model. Traditional cloud setups were excellent for standard web traffic and everyday software, acting like an efficient public transit system. However, artificial intelligence requires processing massive amounts of data at high speeds, which can cause severe delays and soaring costs on shared networks. To handle these heavy workloads, businesses are shifting toward a more specialized, decentralized approach. Additionally, because artificial intelligence learns from the information it processes, companies are increasingly concerned about the security and privacy of their sensitive data. This has driven a strong movement toward bringing data back home to private, local servers. Governments are also introducing stricter privacy laws, requiring companies to keep citizen data within their own national borders rather than storing it in global facilities. As a result, organizations are adopting a flexible strategy where they use public servers for everyday tasks, regional servers to comply with local regulations, and highly secure private servers for their most valuable information. This balanced method allows businesses to use advanced systems while maintaining strict control over their security, legal compliance, and digital assets.


Keeping OT security up to date is more than patching systems

Securing operational technology (OT) in industrial environments involves much more than applying simple software updates. As cyber threats against critical infrastructure like manufacturing and energy continue to rise, protecting these systems requires a fundamentally different approach than traditional IT security. While IT focuses primarily on protecting data, OT security must balance digital defense with real-world safety and continuous physical operations. Because large industrial systems often remain in active use for several decades, they cannot always be patched or upgraded as easily as typical office computers. Rather than relying solely on specialized technical controls, organizations must deeply understand their operational dependencies and gain completely clear visibility into their connected assets and third-party vendor access. Major disruptions frequently stem from basic weaknesses, such as poor network segmentation or compromised IT environments that spill over into industrial operations, rather than highly complex, sophisticated attacks. To build truly effective defenses, companies need strong internal governance that clearly defines responsibilities across engineering, operations, and security teams. Ultimately, organizations should view OT security not just as a narrow technical issue, but as a critical element of overall business resilience. By combining standard cybersecurity practices with deep industrial expertise, companies can protect their vital operations while successfully adapting to ever-evolving security risks.


Your R&D doesn’t need to be flashy

Software development teams often feel pressure to build flashy, highly marketable features to impress users. However, the most valuable research and development work usually happens entirely behind the scenes. While a brand-new interface button might make for a great product demonstration, real long-term user satisfaction depends on foundational elements like speed, reliability, and security. When software performs exactly as expected without delays or glitches, users can focus entirely on their work rather than fighting with the tool itself. Modern professionals, such as architects or engineers, rely on software to handle increasingly complex and automated tasks. If an application fails to execute a command accurately or compromises sensitive project data, the user's trust is instantly broken, and the financial consequences can be severe. This is why development teams must prioritize secure, reliable environments over cosmetic upgrades. By analyzing how people actually use the product, developers can identify the invisible improvements that truly matter, such as open standards that allow seamless collaboration across different platforms. Ultimately, the best software acts as a quiet partner, anticipating a user's needs and handling repetitive work so they can stay immersed in their creative flow.


Querying and Performing Transactions Across Multiple Database Schemas in a Modular Monolith

In a modular monolith, assigning a dedicated database schema to each module establishes strong boundaries but introduces significant challenges for querying data and managing transactions. Because direct database access between modules violates these boundaries, traditional approaches like joining tables across different schemas or relying on single database transactions are no longer viable. To solve querying issues, developers can use several strategies. The simplest method involves direct API calls, where modules communicate through public interfaces, ensuring strict boundaries despite potential performance compromises. For scenarios requiring faster reads, teams can rely on domain events to duplicate and denormalize data across modules, though this requires managing eventual consistency. Alternatively, database views allow developers to join tables across schemas at the database level, which is particularly effective for reporting purposes. Another strong option is the Backend for Frontend pattern, where a dedicated service aggregates data from multiple modules before sending it to the user. Handling transactions across multiple schemas requires a shift away from traditional methods. Instead of relying on a single commit, systems must utilize event driven architectures and patterns like sagas. While this approach ensures loose coupling, scalability, and resilience, it also introduces complexity by requiring compensating transactions and careful error handling to maintain data consistency.


Gmail labels: Your secret weapon against inbox chaos

Gmail labels provide a powerful and flexible alternative to traditional email folders, acting more like customizable tags that allow multiple categories to be applied to a single message. By mastering these tools, users can significantly reduce inbox chaos and streamline their daily communication. A great starting point is creating and color-coding various labels, then grouping them into parent and sublabel hierarchies to maintain a consistently neat sidebar. To save time during everyday tasks, you can proactively apply these labels while composing a new email or assign them simultaneously while archiving a read message. Labels also dramatically improve your ability to find old information; typing specific label operators directly into the search bar instantly narrows down vast results. Furthermore, users can fully automate their workflow by setting up custom Gmail filters. These filters automatically apply specific labels to incoming messages based on criteria like the sender's address or specific subject line keywords. This intelligent automation allows urgent emails to stand out immediately while quietly routing less critical messages away from your main inbox view. Finally, labels can be connected to custom notification settings, ensuring you only receive alerts for the messages that truly matter. By adopting these simple strategies, anyone can transform an overwhelming inbox into a highly organized system.


When cyber capability becomes abundant: Rethinking government cyber resilience

As artificial intelligence rapidly evolves, it is fundamentally changing the economics of cybersecurity for government agencies. Historically, sophisticated cyber operations required scarce, expensive human expertise. Today, AI has significantly reduced these costs, making powerful cyber capabilities widely available to both attackers and defenders. This shift creates unprecedented challenges for government agencies, which protect critical infrastructure and systems essential to national security, public health, and emergency response. Because attackers can now discover and exploit vulnerabilities faster than organizations can fix them, government security leaders are losing confidence in traditional defensive strategies. To adapt to this new reality, governments must rethink their approach to cyber resilience across operational and institutional levels. Operationally, agencies need to move away from trying to fix every single technical flaw. Instead, they must prioritize risks based on their potential impact on public missions. A moderate vulnerability in an emergency response system matters far more than a severe flaw in a low impact network. By translating technical data into real world operational context, governments can better focus their limited resources on protecting what truly matters. Ultimately, success requires agencies to rapidly reduce their exposure, contain breaches driven by artificial intelligence, and actively shape a safer overall cyber ecosystem.


Cyber resilience in the age of AI will be decided in the boardroom

As modern business innovation speeds up due to artificial intelligence, it also provides attackers with powerful new ways to disrupt operations. Companies have spent heavily on defensive software, but having more tools often creates confusing complexity rather than clear protection. Because automated threats move faster than ever, the true test of an organization is not whether it can prevent every single incident, but how well it handles a crisis when it happens. Cybersecurity is no longer just a technical issue meant for the information technology department; it is a fundamental business challenge that belongs in the boardroom. Company leaders must understand their critical digital dependencies and how a failure would impact revenue, reputation, and daily functioning. Security should be woven into every major business decision from the start, prioritizing clear processes over having the most complicated software. True resilience relies heavily on human behavior. An organization must build a culture where employees feel safe reporting mistakes, questioning unusual requests, and practicing response plans before an actual emergency occurs. Ultimately, survival during a digital attack depends on clear communication, decisive leadership, and the ability to keep essential services running smoothly and effectively, ensuring that trust and stability are maintained alongside technological growth.


How Differential Privacy Will Transform Enterprise Data Strategy

Differential privacy is quickly moving from a theoretical concept to a critical component of enterprise data strategy. While previous methods like encryption and de-identification have struggled to protect against re-identification as data volumes grow, differential privacy offers a mathematically proven way to guarantee that an individual's data cannot be reverse-engineered from broader analytical outputs. This technique is already being used successfully by major organizations, including the U.S. Census Bureau, Apple, Google, and Microsoft, and the market is projected to expand significantly by 2030. However, many business leaders mistakenly view this technology merely as a compliance tool. Its true value lies in unlocking data utility, allowing companies to safely share information across internal departments and with partners without exposing sensitive details. To succeed, organizations must understand that differential privacy is not a simple plug-and-play product, nor can it be retrofitted easily into existing pipelines. It requires a fundamental shift in how data is processed and governed. Experts advise companies to start with a single high-value use case, such as customer analytics, and prioritize building strong central governance before focusing on the underlying tooling. Adopting this approach now gives enterprises a significant competitive advantage in responsible data strategy.


What the AI Warning Letter Completely Missed
A recent warning from major technology companies highlights that artificial intelligence will soon make cyberattacks cheaper and more common, urging immediate action to strengthen defenses. While this threat is very real, the proposed solutions overlook the most critical component: the human beings required to do the work. The industry often focuses heavily on advanced tools and theoretical scenarios while ignoring the practical reality that defense depends entirely on skilled people. Every recommendation to improve security, whether it involves fixing weaknesses, reviewing code, or deploying new software, requires a trained operator. The gap in our current readiness is not a lack of software products, but a severe shortage of equipped personnel, especially within smaller organizations and local utilities. To truly prepare for emerging threats, companies must invest directly in the workers already managing these systems, teaching them how to secure their specific environments. Furthermore, technology providers should offer concrete, direct support rather than just access to software models. Defensive tools must be judged by how effectively a small, overworked team can actually use them during an emergency. Ultimately, technology alone will not secure our infrastructure against intelligent threats. True resilience requires betting on motivated, well trained people who are ready to handle the daily work of defense.


Why digital transformations still fail

Digital transformations continue to fail largely because companies let technology, heavily promoted by consulting firms, dictate their strategy rather than focusing on actual business needs. Consultants have consistently sold identical, prepackaged systems to maximize their own profits, completely ignoring the unique requirements of each organization. This approach has resulted in massive budget overruns, delayed timelines, and overly complex systems that fail to perform as promised. Instead of redesigning their processes, companies simply moved their existing problems onto expensive cloud platforms, increasing their costs without gaining any real benefits. Now, as the industry shifts its focus toward artificial intelligence, businesses are repeating these exact same mistakes. Organizations are rushing to add artificial intelligence to everything without a clear reason, while placing unqualified staff into critical design roles. To succeed moving forward, businesses must adopt a much simpler approach. They need to stop overspending on unnecessary computing power and invest heavily in proper foundational training for their internal teams. Ultimately, technology exists solely to serve the business. Any successful change must begin by identifying clear business requirements and working backward to find the most practical, cost-effective solution, rather than blindly purchasing the most complicated or trendy new software option available today.

Daily Tech Digest - June 28, 2026


Quote for the day:

"Hard work beats talent when talent doesn't work hard." -- Tim Notke

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 17 mins • Perfect for listening on the go.


Ford learned the hard way that AI can't replace experienced engineers

Ford recently discovered that artificial intelligence cannot substitute for the nuanced judgment of experienced engineers. In an effort to modernize its manufacturing and engineering systems, the automaker integrated AI to accelerate decision making and streamline vehicle development. Executives assumed that automated systems and adjusted design requirements would naturally yield high quality products. However, this approach backfired. As veteran engineers left the company, their undocumented institutional knowledge was excluded from the datasets used to train Ford’s AI models. Consequently, the technology struggled to identify and prevent defects, contributing to quality control issues and leading the industry in vehicle recalls. To resolve these challenges, Ford rehired and promoted over 350 seasoned engineers. Rather than replacing human expertise, AI now serves as a supportive tool. These veteran engineers are currently guiding how data is collected, interpreted, and fed into the AI systems to rebuild a reliable foundation. Furthermore, Ford created a dedicated software quality assurance team and introduced automated AI driven testing to catch defects early in the development cycle. This transition reflects a balanced strategy where the company relies on both advanced computing power and decades of practical automotive experience to prevent problems before they occur.


Where AI meets OT: Cybersecurity for a physical world

Integrating artificial intelligence into operational technology requires a careful approach because, unlike business software, industrial systems have physical consequences. While artificial intelligence offers clear benefits for manufacturing, such as improved maintenance and quality control, it introduces unique risks when connected to machines and factory floors. Industrial environments often rely on older, existing systems and operate on strict schedules with limited downtime, making new technology harder to test and implement safely. Furthermore, software models can become inaccurate over time as physical equipment naturally ages, which means these tools require ongoing checks against actual physical outcomes rather than just historical data. The level of risk also depends on how much control the system has. An advisory tool leaves the final decision to a human, whereas a system that directly alters machinery settings requires far stricter oversight. True human oversight means operators must fully understand the technology's recommendations and know when to override them. Adding these new digital connections also expands the cybersecurity risk, as attackers could manipulate the data feeding the models. Ultimately, these tools hold steady value for industrial operations, but they must be introduced with strong discipline, clear operating limits, and reliable backup plans.


How to Build a Powerful LLM Knowledge Base

Building a knowledge base powered by large language models is a practical, reliable way to store and retrieve your personal or company information, leading to better decision-making and clearer team alignment. To create an effective system, you must start by identifying all your daily information sources, such as meeting notes, project management tools, and coding assistants. The critical step is fully automating the collection process; requiring any manual entry virtually guarantees that valuable context will eventually be forgotten and lost. Once your data is automatically synced into the system on a regular schedule, you can use a coding agent to extract insights. You can do this actively by directly asking your agent questions when you need specific answers. Alternatively, you can configure your agent to passively draw on the knowledge base while it works on routine tasks. This passive retrieval can be managed either through a centralized index file or via an embedding-based search that pulls relevant information as needed. Ultimately, consistently capturing and accessing your unique, everyday context creates a distinct long-term advantage, ensuring that valuable insights are preserved and always ready to assist you in your daily work.


Is the CIO Role Merging Into the Business?

For decades, the role of the Chief Information Officer followed a predictable path, slowly shifting from managing basic operations to supporting broader strategy. However, recent trends indicate that this steady progression is becoming obsolete. The middle ground is collapsing, forcing a clear divide in the profession. On one hand, some leaders remain stuck in traditional management, treating technology as a separate, functional necessity. On the other hand, a new breed of technology executives is emerging as true enterprise operators who share responsibility for revenue and actively shape commercial models. In the most effective organizations, technology is no longer just a supporting layer; it is the central system for making decisions. As companies embed artificial intelligence deeply into their core operations and bring critical capabilities inside the firm, the person leading technology must also architect these decision-making systems. Consequently, the traditional boundary between technology leadership and business leadership is rapidly fading. Instead of simply elevating the position to a more strategic level, the core responsibilities are dissolving directly into the business itself. Ultimately, the future landscape will be defined not by better technology departments, but by whether the conventional title needs to exist at all.


Deep dive: Do underwater data centers make sense?

The article evaluates the practicality of underwater data centers as an alternative to land-based facilities, which struggle with high energy consumption and space limitations. Traditional data centers use tremendous amounts of power, largely just to keep servers cool. Submerging these facilities allows companies to use the ocean as a natural cooling system, significantly reducing energy requirements. Beyond energy savings, placing data centers offshore brings them closer to coastal populations. This proximity shortens the distance data travels, leading to faster loading times for end users. Research also indicates that underwater servers are surprisingly reliable. Because they are sealed in a nitrogen-rich environment without human foot traffic or temperature swings, hardware fails much less frequently. Despite these benefits, the underwater model has distinct disadvantages. Routine maintenance is virtually impossible; broken servers cannot be quickly swapped out. Furthermore, researchers are still studying how the continuous release of heat might alter local marine ecosystems. There are also valid concerns regarding the physical security of underwater cables. While the approach provides clear advantages in efficiency and speed, these formidable logistical and environmental challenges complicate the decision of whether underwater data centers are a sensible long-term investment.


5 T-SQL features that should already exist (2026 SQL Server wish list)

In a recent article by Edward Pollack on Simple Talk, the author reflects on the state of Microsoft SQL Server in 2026 and outlines five practical features he believes should be natively supported in T-SQL and the platform. While SQL Server remains a highly mature database system, Pollack highlights specific areas where daily tasks for developers and database administrators could be made far more efficient. First, he argues for the native ability to import data from compressed file formats, specifically Apache Parquet, which would eliminate the need to deal with cumbersome plain text files like CSV. Second, he requests native support for arrays, providing a straightforward alternative to using text strings or XML to store lists of values. Third, he advocates for an "OVERLAPS" function to simplify complex date logic into a single line of code. Fourth, Pollack points out that the current licensing model is overly complicated and suggests it should be as transparent as the monthly estimates provided for Azure SQL. Finally, he suggests expanding cloud blob storage integration so that files and scripts can be managed centrally in the cloud rather than on local drives.


Shaping a lasting AI strategy in a fast-changing world

As artificial intelligence becomes a standard tool in business, simply having access to the technology is no longer enough to stand out. Because most companies will use the same core platforms and models, a well-defined strategy is what will truly set an organization apart. The current landscape is marked by more capable and affordable systems that act as helpful assistants rather than outright replacements for human workers. Development teams are already showing how humans and these tools can work together effectively. To succeed, leaders need to shift their focus from the technology itself to how it supports their long-term goals over the next three to five years. This requires answering difficult questions about the company's future direction, understanding current weaknesses, and identifying the specific skills needed for tomorrow. Decision-makers must also practice restraint, choosing a few reliable platforms and focusing on clear priorities rather than chasing every new trend. By thoughtfully integrating these tools into daily workflows and supporting human decision-making, businesses can improve their customer experience and operations. Ultimately, the tools are just the vehicle; a steady, clear strategy is the route that determines long-term success.


The Unglamorous Side of Rust Web Development

In 2026, Rust remains a powerful choice for web development, offering excellent performance and safety. However, developers still face notable friction before their code even compiles. The current ecosystem often requires teams to assemble their own setups from scratch, lacking the complete, ready-to-use frameworks seen in other programming languages. Several specific challenges slow down the daily development process. Asynchronous programming in Rust provides great flexibility, but it complicates debugging and creates lengthy, hard-to-read error traces. Database management is another hurdle, as developers frequently have to write and maintain the same database structure in multiple places instead of using a single unified approach. Additionally, error handling across different tools remains inconsistent. The heavy reliance on generated code and complex type systems significantly increases compilation times, making it harder for developers to test small changes quickly. Despite these hurdles, the community is actively working on solutions. New frameworks are emerging to provide more complete starting points and reduce repetitive setup tasks. Ultimately, while Rust requires a larger initial investment of time and effort compared to simpler alternatives, its long-term reliability and speed make it a sensible choice for projects where stability is a core requirement.


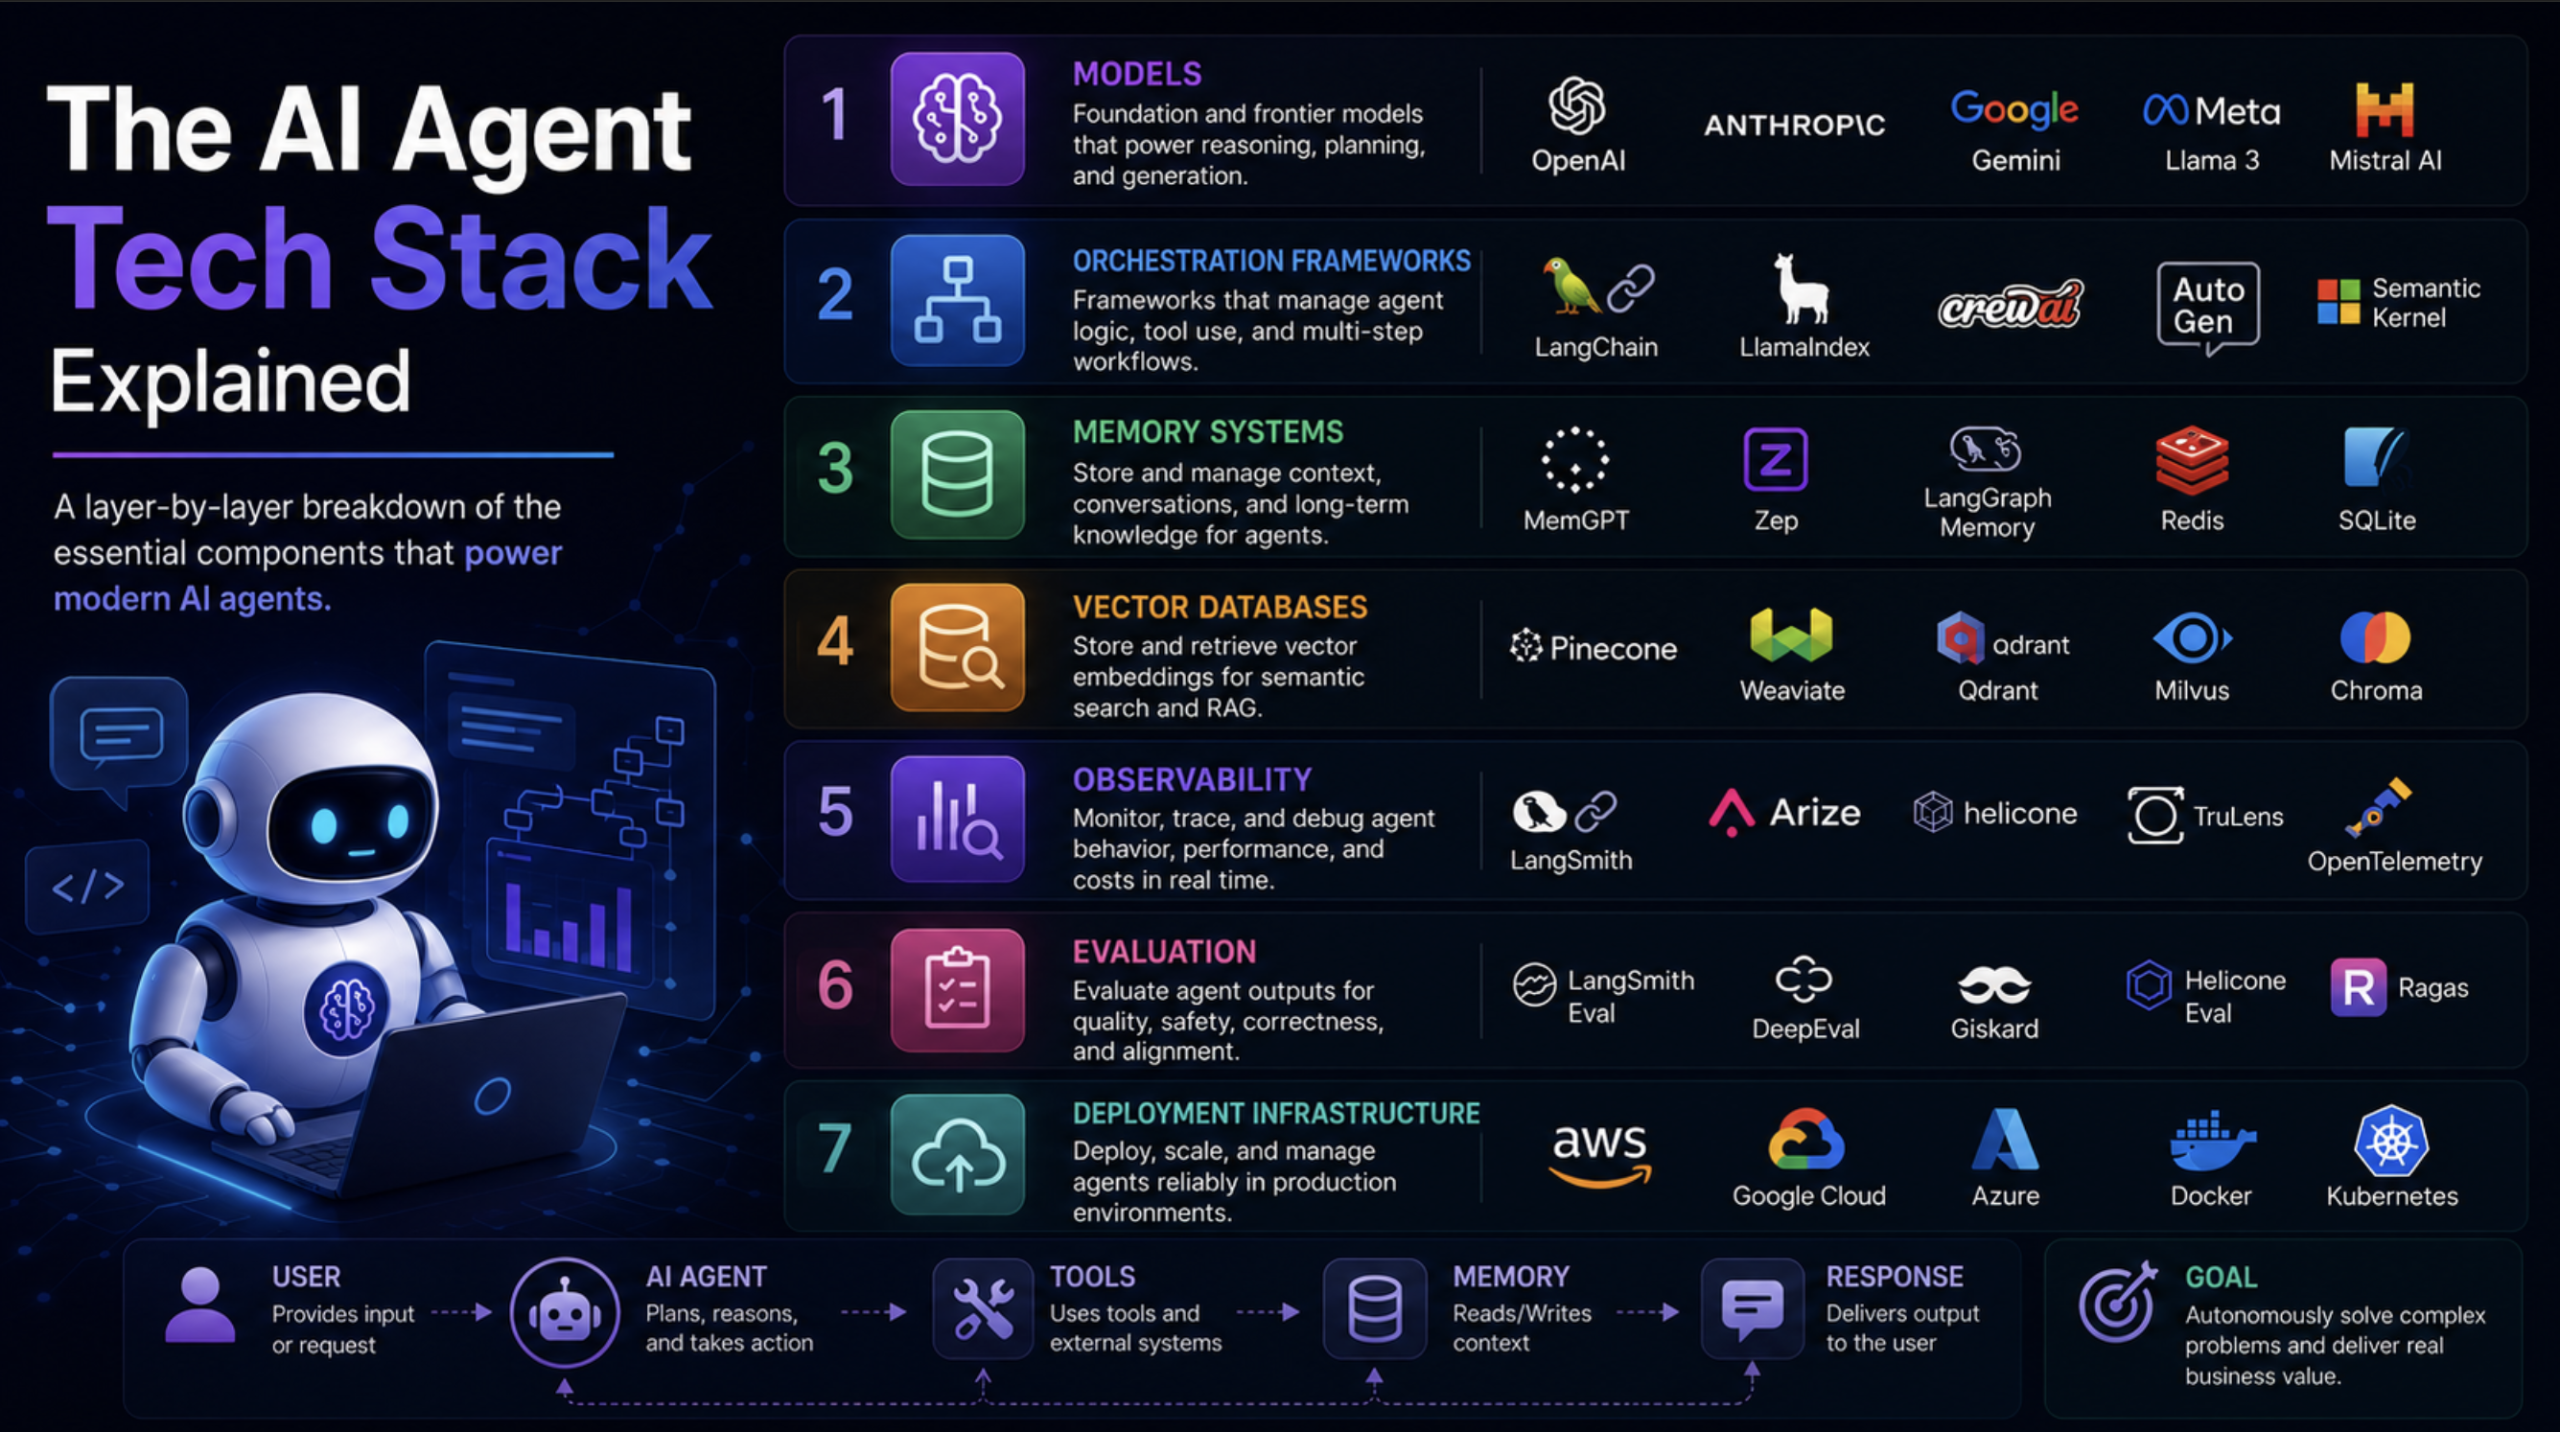
The AI Agent Tech Stack Explained

The article outlines the seven fundamental layers required to build and deploy functional artificial intelligence agents. It moves beyond basic models to explain the complete technical infrastructure needed for real-world applications. The guide begins with the foundation model, which acts as the central brain for reasoning. The second layer is the orchestration framework, serving as a nervous system to manage actions and control flow. Next, the third layer covers memory systems that provide essential context by tracking working, episodic, semantic, and procedural information. The fourth layer focuses on vector databases and document retrieval, allowing agents to access private information securely. The remaining layers detail tool integrations for performing outside actions, observability platforms for monitoring performance, and the final deployment infrastructure necessary for hosting. By breaking down the architecture into these distinct components, the text clarifies that successful systems rely heavily on a well-connected technology stack rather than just a single language model. It provides a clear, practical roadmap for software engineers and technical leads who want to understand how to assemble these exact pieces, whether they are building a simple prototype or scaling an application for production.

A Case for a Human-Centric AI Legislative Framework in India

In "A Case for a Human-Centric AI Legislative Framework in India," the author argues that India’s current approach to governing artificial intelligence is insufficient for protecting its citizens. While the Ministry of Electronics and Information Technology recently suggested relying on existing laws and self-regulation to foster innovation, the article points out that AI is fundamentally different from traditional software. Because AI programs operate as highly complex systems, relying on outdated frameworks like the Information Technology Act leaves users vulnerable to fraud, manipulation, and bias. Furthermore, the author critiques recent amendments for placing unreasonable takedown burdens on tech companies without providing clear state-defined guardrails. By comparing India’s strategy with the European Union’s user-focused risk models and China’s strict algorithm rules, the article advocates for a new Artificial Intelligence Regulation Act. This proposed legislation would introduce a risk-based grading system, establish an independent AI ombudsperson, and mandate transparency in training data. It even suggests giving citizens a copyright over their own faces to prevent unauthorized data usage. Ultimately, the piece makes a strong case that responsible innovation requires specific, human-centric laws to ensure safety and accountability for all users today.

Daily Tech Digest - June 27, 2026


Quote for the day:

"When you want to succeed as bad as you want to breathe, then you’ll be successful." -- Eric Thomas

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


‘Botsitting’: The AI time-savings killer only governance can stop

While artificial intelligence promises to free up employees for valuable tasks, a recent study reveals that workers lose more than half their saved time to “botsitting.” Digital workers save roughly eleven hours a week using these tools, but spend over six hours managing them—providing missing context, checking outputs, fixing mistakes, rewriting prompts, and correcting inaccurate answers. As a result, businesses are missing out on the full return on their investments. A core issue is poor governance and a lack of training. Employees often use AI for simple tasks like drafting emails, distrusting it for complex work. Moreover, there is “coordination neglect,” where an individual’s productivity gains create unexpected work for others downstream. For instance, when workers pass along unchecked, AI-generated content, teammates must spend unbudgeted time cleaning up the mess. Experts warn that simply implementing tools without clear guidelines on verification processes and data context leads to inefficiency. To truly benefit from these technologies, organizations must focus on proper deployment, establish clear oversight, and define quality standards rather than merely counting how often tools are used. Reliable outcomes require thoughtful management, not just fast adoption.


The database that refused to die: How Postgres survived its own creators

Postgres, one of the world's most widely used database systems, began its life with an uncertain future. Created by database pioneer Michael Stonebraker in the 1980s as a successor to Ingres, the project was essentially abandoned by its creator in the mid-1990s. Instead of fading into obscurity, Postgres was rescued by a dedicated community of independent open-source volunteers. These contributors preserved Stonebraker's foundational, highly adaptable architecture—which allowed for complex, user-defined data types rather than just basic strings and numbers—while adding standard SQL capabilities. Today, this collaborative rescue effort has established Postgres as a cornerstone of modern cloud computing infrastructure. Its enduring success stems from its foundational design philosophy. While proprietary database systems traditionally optimize their software to suit the specific needs of massive enterprise clients, Postgres was built to handle the diverse workloads of general users. By seamlessly accommodating complex data formats like geographic information and computer-aided design files, it solved real-world problems for a broad audience. Ultimately, the survival and widespread adoption of Postgres demonstrate the power of open-source software, proving that community-driven development can outlast even the original creators to become a resilient industry standard.


Why private AI is the smarter bet

Although many businesses initially assumed artificial intelligence would naturally live in the public cloud, reality is forcing a shift toward private, on-premises systems. According to the article, this transition stems from growing concerns about uncontrolled costs, security vulnerabilities, and operational fit. As companies move from small experiments to organization-wide implementation, the pay-per-token pricing models of public cloud providers risk becoming massive utility bills that wipe out business gains. Consequently, the future of enterprise AI leans toward a hybrid model. Rather than relying entirely on giant public models, businesses are discovering that smaller, specialized AI models can handle tasks better while running closely to their own private data. This approach offers better control over predictable workloads and eliminates surprise expenses. Furthermore, keeping AI in-house strengthens security and data governance. Using public AI tools raises the real danger of employees inadvertently exposing sensitive or proprietary information. While building and managing private AI networks requires significant investment, skill, and discipline, the long-term benefits of controlled costs, tight security, and owned infrastructure make it a much smarter choice for major production workloads.


AI Cost, Security Pressures Push Enterprises Toward Private Cloud, Broadcom Says

According to a recent report from Broadcom, organizations are increasingly moving their artificial intelligence operations away from public cloud services and toward private cloud setups. As businesses shift from merely testing artificial intelligence to running real-world applications, they are discovering that private networks offer better handling of costs, security, and data control. The study reveals that over half of surveyed enterprises now plan to run their active intelligence systems on private infrastructure. Meanwhile, public cloud usage for these specific tasks has dropped notably over the past year. Interestingly, cost management has now surpassed security as the primary concern with public platforms, as business leaders face unpredictable pricing for computing power and data storage. Because of this, more than eighty percent of companies are either moving or considering moving their systems back in-house. While public networks remain useful for basic testing and flexible storage, the heavy demands of daily production require a more stable environment. Strict data privacy rules further encourage this transition. Ultimately, businesses are finding that dedicated internal systems provide the financial predictability and reliable protection necessary to safely grow their technological capabilities.


How to Modernize Legacy Applications Without Disrupting Business

Upgrading older software systems is a pressing challenge for modern organizations. Delaying these updates can hinder new capabilities, consume vital budgets with maintenance costs, and create risks as experienced programmers retire. However, many companies hesitate because poorly planned upgrades often cause severe business interruptions. To avoid taking systems offline, experts recommend a gradual approach rather than attempting a risky, sudden replacement. This method relies on careful planning and proven structural designs. For example, organizations can build new services around the existing system, slowly routing traffic to the new components as they are tested and proven. Another reliable method involves running both the old and new systems at the same time to ensure they produce identical results before fully switching over. It is also important to use a translation layer to prevent the flaws of the old data formats from infecting the new setup. A successful upgrade generally follows a structured path: assessing current dependencies, planning the target design, running a small initial pilot, scaling the effort across other applications, and maintaining ongoing oversight. By strictly adhering to these methods, businesses can confidently update their technology and maintain continuous daily operations.


Data Lakehouse Architecture Layers: AI Needs More Than Just Infrastructure

Organizations have invested heavily in data lakehouses to store and process large amounts of information for analytics and artificial intelligence. While these setups handle storage and compute well, they often fall short in practical application. Data remains scattered across different cloud environments and operational systems, meaning business teams and AI models still struggle to access reliable information without technical assistance. The fundamental issue is no longer about where data is kept, but how it is connected and understood. AI tools, in particular, require more than just raw data; they need clear context and strict governance to function accurately and safely. To solve this, a new logical layer is emerging in data architecture. Instead of replacing the lakehouse, this access layer sits on top of it. It connects distributed information, applies consistent rules, and provides clear meaning to the data without requiring it to be moved or duplicated. By pairing traditional storage with this new governance layer, businesses create a stronger foundation. This approach reduces friction, ensures that both human users and systems have the context they need, and allows organizations to focus on practical outcomes rather than managing complex infrastructure.


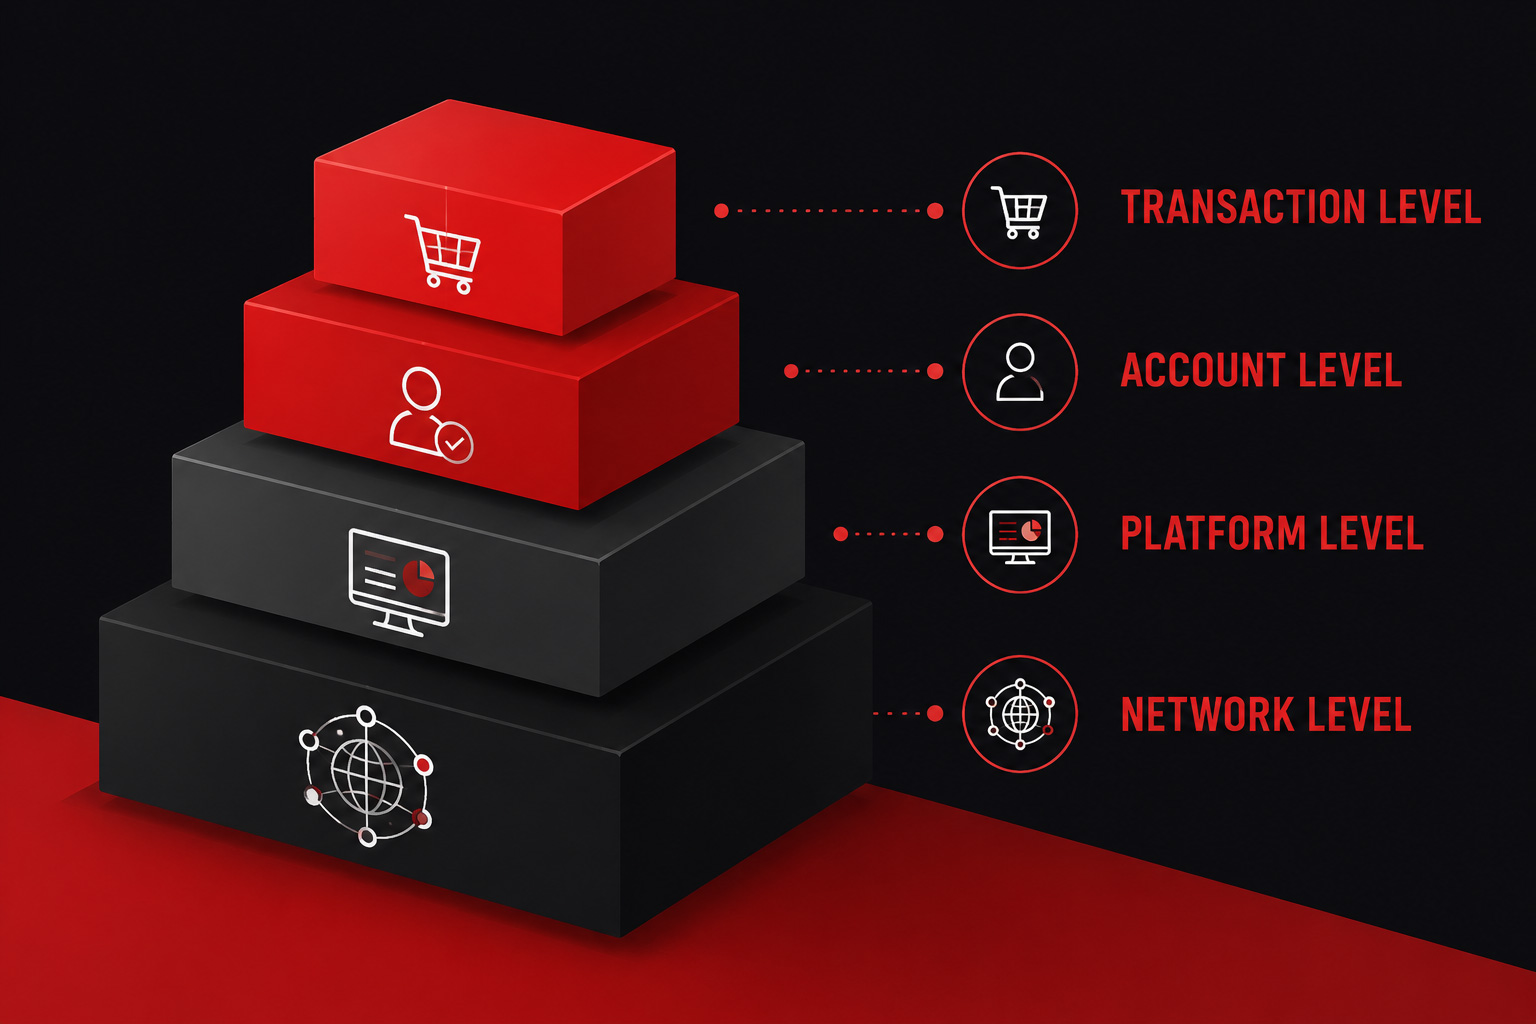
The Four Elevations of Effective Fraud Prevention

Effective fraud prevention requires more than just checking individual steps; it demands a layered approach to monitor customer behavior comprehensively. To build a resilient defense, organizations should evaluate activities across four key elevations. First is the transaction level, which looks at single interactions like logins or purchases. While important, relying on this alone can miss larger patterns because attackers frequently change their tactics. The second elevation is the account level, where monitoring a user's behavior over time helps distinguish normal activity from suspicious anomalies, such as sudden changes to contact information or unusual transfer requests. The third elevation expands to the platform level, allowing teams to analyze trends across all grouped accounts. This broad view helps quickly spot coordinated attacks or fraud rings sharing the same devices or geographic locations. Finally, the network level involves collaborating with external data providers to share insights across different companies, ensuring that a threat detected by one organization is immediately known to others. By integrating these four perspectives, businesses can confidently identify complex fraud schemes early, reduce false alarms for legitimate users, and secure their operations without disrupting the everyday customer experience.


Bridging the gap between leadership's AI enthusiasm and employee pushback

Corporate leaders and everyday employees often view artificial intelligence through entirely different lenses. While executives and board members see AI as a path to efficiency, cost reduction, and innovation, employees frequently view the technology with caution. Many workers worry that AI will result in job losses, create mentally exhausting workloads, enable invasive workplace surveillance, and harm the environment. Chief Information Officers (CIOs) find themselves caught in the middle and must bridge this divide. If IT leaders ignore workforce anxieties and force AI integration, they risk damaging company morale, losing valuable talent, and wasting money on tools that employees simply refuse to use. To resolve this tension, CIOs need to look beyond basic financial metrics and instead measure actual employee sentiment and tool usage. Having open, honest conversations with staff about their fears is essential. By creating a culture where workers feel safe sharing their concerns, companies can build trust and ease anxiety. Rather than rolling out technology blindly, leaders should clearly communicate the company's AI strategy and empower early adopters to guide their peers, ensuring the transition supports both business goals and the well-being of the team.


AI Works, Pull Requests Don’t: How AI Is Breaking the SDLC and What To Do About It

In the presentation "AI Works, Pull Requests Don't," Michael Webster examines how the rise of artificial intelligence coding assistants is severely straining traditional software development lifecycles. While AI tools initially act as powerful amplifiers that can increase development speed by three to five times, this burst in productivity is often temporary. Developers and AI agents are generating massive amounts of code, sometimes adding twenty-five times more code than they delete. As a result, human reviewers are overwhelmed by enormous pull requests, creating significant bottlenecks in the review process and leading to a steady accumulation of technical debt. Drawing on queuing theory, Webster explains that delays inevitably occur when the rate of incoming code surpasses the team's capacity to process and review it. To resolve these challenges, engineering teams must adapt their validation pipelines. He recommends implementing test impact analysis, a method that runs only the tests affected by recent code changes rather than the entire test suite. By relying on automated validation tools to quickly verify AI-generated output, teams can successfully maintain software stability, reduce testing costs, and manage the high volume of code without sacrificing overall quality.


Hackers Exploit Weak Credentials and Internet-Facing PLCs to Breach Water Utilities

Water and wastewater utilities across the United States and Europe are facing increasing threats from state-sponsored groups affiliated with Iran, Russia, and China. Rather than relying on complex software, these attackers exploit fundamental security oversights, like internet-exposed control systems, default passwords, and inadequate network separation. This shift indicates that targeting civilian infrastructure has become a deliberate method to test emergency responses, create public anxiety, and position adversaries for future conflicts. For instance, Iranian-linked groups have used factory credentials to access unprotected systems, while Russian-affiliated actors actively disrupted operations by overflowing water tanks in Texas and opening floodgates in Norway. Meanwhile, Chinese groups take a quieter approach, establishing long-term access within utility networks to maintain leverage for potential disputes. To counter these vulnerabilities, security experts advise facility operators to implement basic defenses immediately. These include removing physical control systems from direct internet exposure, enforcing strict login requirements, replacing default passwords, and firmly separating industrial equipment from standard computer networks. By addressing these entry points, utilities can effectively reduce their risk of compromise and safely protect vital public water resources from further interference.

Daily Tech Digest - June 23, 2026


Quote for the day:

“Growth is painful. Change is painful. But nothing is as painful as staying stuck.” -- N.R. Narayana Murthy

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Your AI strategy may be training employees to stop thinking

Relying too heavily on artificial intelligence for routine writing and summarizing is quietly wearing away the critical thinking skills that businesses depend on. Researchers warn that as employees repeatedly use automated tools to generate content, the original context and factual accuracy of that information begin to break down. Over time, errors multiply, outputs become generic, and staff members lose trust in their own daily processes. Correcting these automated mistakes often demands so much human review that it completely wipes out any initial time savings. To protect the quality of their work, companies need to establish clear boundaries. Instead of allowing workers to use automated tools for broad tasks like writing generic reports or crafting standard job applications, managers should require structured, factual information that relies on genuine human experience. Using tailored internal data rather than generic public systems also helps keep facts straight. By pairing genuine human judgment with automated efficiency, businesses can use technology to organize actual human knowledge rather than replace the thinking process entirely. Setting these practical limits ensures that automated tools actually support staff rather than encouraging them to stop thinking altogether.


Loop Engineering

The recent O'Reilly Radar article by Jonas Steinberger and Addy Osmani introduces loop engineering, which marks a major shift in how developers interact with artificial intelligence. Rather than relying on traditional prompt engineering, where a human types instructions and waits for responses one step at a time, loop engineering focuses on building systems that correct themselves and operate independently. In this new model, the artificial intelligence is simply one part of a larger machine built to plan tasks, utilize tools, evaluate its own work, and fix mistakes without constant human oversight. Developers are no longer just conductors of single tasks; they become orchestrators who manage entire automated workflows. The authors explain that the core of this method is the surrounding code that enforces rules, budget limits, and safety checks to ensure the intelligence stays on track. By setting firm boundaries, such as a maximum number of steps or cost caps, developers prevent the system from getting trapped in endless errors. Finally, the authors caution against blindly trusting the system, warning that developers risk losing their understanding of how the code actually functions if they surrender too much control.


Why open infrastructure will define the AI era

Software engineers increasingly rely on paid artificial intelligence tools to assist with writing code, which introduces the risk of becoming trapped within the closed systems of a few large technology corporations. Building an entire strategy on proprietary platforms forces companies to accept the shifting rules, sudden policy changes, and rising prices of specific vendors, creating expensive and fragile technical dependencies. In response to these challenges, a growing movement toward open foundations is gaining momentum across the software industry, mirroring the historical development of the early internet and operating systems like Linux. By adopting publicly accessible models, shared communication standards, and neutral management tools, organizations retain the practical freedom to swap out individual parts as their needs change. This open approach prevents businesses from being locked into the network of a single provider and eliminates the need to rebuild systems completely whenever a vendor alters its direction. Connecting different layers of technology through universal agreements provides essential stability and flexibility. Ultimately, historical patterns in computing suggest that open systems succeed because they grant organizations lasting control and independence, ensuring they do not pay endless rent for basic operational tools.


The Hidden Engineering Challenge Behind Successful GenAI Deployment

While many organizations invest in generative artificial intelligence pilots, very few successfully transition these into scalable business operations. The primary hurdle is rarely the model itself, but rather the operational and systems engineering challenges required for safe, effective deployment. Pilots often fail because they rely on controlled datasets that do not easily translate to complex enterprise systems, leading to errors and risks. To overcome this, organizations must shift their focus from simply selecting the best model to building a resilient infrastructure. This involves adopting a comprehensive, multidimensional evaluation framework that measures performance at the component, task, and broader business outcome levels. Additionally, a robust foundation requires five essential layers: data, orchestration, training, observability, and security. Relying on flexible, open-source frameworks allows companies to adapt quickly and build reusable systems. Strategically, businesses should begin with human-assisted augmentation rather than full automation, ensuring strict safeguards and continuous human oversight. By fostering cross-functional collaboration among engineering, product, and subject matter experts, companies can align technical implementations with shared business goals. Ultimately, achieving sustainable value depends entirely on rigorous planning, structured implementation, and maintaining dependable operational guardrails rather than merely chasing the largest models.


6 security leader tips for mastering business risk

As cybersecurity increasingly dictates financial health, Chief Information Security Officers must expand their focus beyond technology to manage broader company risks. The article outlines six practical steps for security leaders making this transition. First, they should partner directly with colleagues in finance, legal, and operations to understand the company’s actual risk tolerance. Second, security strategies must support overarching business goals, ensuring that protective measures do not inadvertently hinder operations or harm employee satisfaction. Third, leaders need to build strong internal relationships through routine conversations to learn what genuinely worries their fellow executives. Fourth, crisis simulations should test real business dilemmas, such as whether to pay a ransom or when to disclose a breach, rather than stopping at technical fixes. Fifth, security chiefs should study the business itself by reading annual reports and earnings transcripts, or by pursuing formal corporate governance education. Finally, cyber risks must be quantified in actual financial figures and placed on the central enterprise risk register alongside legal and market threats. By speaking the language of revenue and probability rather than technical jargon, security professionals can secure the executive support necessary to protect the entire organization.


The Cost of ‘Good Enough’ SQL in a High-Volume Database Environment

In high-volume database environments, settling for "good enough" SQL queries can become surprisingly expensive. While a query might pass testing and return accurate results, minor inefficiencies like a suboptimal join or an unnecessary table scan are magnified exponentially in production. Because these queries are executed thousands or millions of times, small flaws accumulate into massive resource drains. This multiplier effect leads to increased CPU consumption, higher software licensing costs, and slower overall system performance. The problem often starts during development, where time pressures, overreliance on automated tools, and a lack of deep database expertise cause developers to prioritize immediate functionality over long-term efficiency. As data volumes grow and concurrency increases, what was once an acceptable access path can become a major bottleneck. To prevent these hidden taxes from dragging down the system, organizations must stop treating SQL performance as an afterthought. Instead, teams should adopt a continuous and intentional approach to database management. By thoroughly reviewing queries for actual efficiency, carefully designing indexes, and prioritizing performance just as highly as functionality, companies can ensure their database workloads remain stable, predictable, and cost-effective as they scale.


Scrum That Actually Works for DevOps Teams

Applying standard Scrum to infrastructure and operations teams often fails because rigid two week cycles ignore the daily reality of unexpected outages, urgent security patches, and routine support requests. Rather than abandoning the framework completely, teams can adapt it into a practical tool by stripping away strict rituals and keeping only what helps them coordinate and finish work. The first step is cleaning up the task backlog. Instead of a messy pile of vague technical chores, tasks should be written as clear outcomes that explain why the work matters, with only the next few weeks planned in detail. Next, teams must practice honest capacity planning. Because platform engineers routinely handle urgent interruptions, scheduling total uninterrupted project focus is unrealistic. By explicitly setting aside a time buffer for reactive support and maintenance based on past data, teams avoid the recurring frustration of missed targets. In addition, sprint goals should be broad enough to survive sudden disruptions. Finally, daily meetings should remain short and focused entirely on helping team members solve immediate problems, rather than serving as tedious status reports for management. These straightforward adjustments create a balanced workflow that accommodates daily chaos without unnecessary stress.


'Lack of support' as Australia lags behind on blockchain

Australia's digital investment sector is growing steadily, with rising interest in converting physical assets, such as mining resources, into digital shares to make them easier to manage and trade. However, the nation risks losing ground to international peers like Singapore due to prolonged regulatory delays and complicated government grant processes. Industry experts, including Black Tie CEO Caroline Macdonald, note that modern investors increasingly demand transparent, immediate control over their portfolios rather than relying strictly on traditional fund managers. While digital asset systems already contribute one percent of the national gross domestic product, widespread public adoption remains constrained by overly complex user interfaces. To overcome these practical barriers, companies are deploying hybrid platforms that pair standard, familiar website designs with secure underlying ledgers. Additionally, businesses are focusing on practical applications of artificial intelligence to educate clients rather than chasing temporary industry trends. Because the basic infrastructure has proven its stability, the primary challenge is no longer proving whether the systems actually function. Instead, the immediate focus has shifted toward securing clearer federal guidance, refining the daily user experience, and ensuring the country remains a competitive destination for international talent and investment capital.


From Block-Based Programming to Vibe Coding

The evolution of how we write software is moving toward higher levels of abstraction, shifting from visual methods to natural language commands. For years, visual systems that use interlocking shapes helped beginners learn the logic of software development without worrying about precise typing or grammar rules. These tools successfully opened the door for many people to understand foundational concepts like loops and conditionals. Now, the approach known as vibe coding takes this accessibility a step further by allowing users to describe what they want a program to do using ordinary text. Instead of dragging and dropping shapes, individuals can instruct artificial intelligence to draft the actual lines of code based on their plain language descriptions. This transition changes the developer's role from writing every detail to guiding and refining the output generated by the system. While this method lowers the barrier to entry and speeds up the creation process, it also introduces new responsibilities. Users must carefully review the generated results to ensure accuracy, security, and reliability. Ultimately, this progression reflects a broader trend of making software creation more intuitive, focusing more on the underlying purpose of the program rather than the mechanical steps required to build it.


The ICS Exploit Pipeline Is Built for Destruction, Not Theft

Industrial control systems face a severe mismatch between how companies measure risk and how attackers actually operate. Today, corporate risk models borrow heavily from traditional information technology, focusing on the financial fallout of stolen data records and regulatory fines. However, recent data reveals that the vulnerability pipeline for industrial hardware is overwhelmingly built to break physical infrastructure rather than steal from it. In fact, flaws that exclusively enable equipment destruction outnumbered pure data theft vulnerabilities five to one last year. When attackers target power grids, water plants, or factories, they rarely use complex, custom software to cause damage. Instead, they exploit basic network weaknesses, such as stolen passwords or bypassed login screens, to gain access to the control room. Once inside, they simply use the machinery’s native operating commands to trigger emergency shutdowns or override safety switches. Because traditional risk calculators were never designed to evaluate a ruined turbine or a halted assembly line, they systematically leave organizations exposed. To defend these environments effectively, companies must stop treating physical operations like standard data networks and begin evaluating their security based on actual machinery downtime, physical repair costs, and human safety.

Daily Tech Digest - June 01, 2026


Quote for the day:

“The best architectures, requirements, and designs emerge from self‑organizing teams.” -- Martin Fowler

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Why AI can’t match human creative work

This Computerworld article explores why AI-generated content struggles to match the real effectiveness of human creativity, despite its overwhelming volume in today's digital marketplace. Recent industry studies in advertising and search engine optimization highlight a clear pattern: even when typical audiences cannot consciously distinguish between human and machine outputs, they consistently prefer human-created work. In advertising, human-made campaigns perform significantly better in driving sales and boosting long-term brand health because they can forge genuine emotional connections and break new ground rather than simply remixing existing data. Similarly, comprehensive data from web search results reveals that human-written articles overwhelmingly secure top rankings compared to those entirely generated by software algorithms. While automated tools have allowed an unprecedented flood of synthetic blogs, music, videos, and social media posts into the mainstream, this automated material rarely captures meaningful audience attention or real engagement. For instance, although AI-produced episodes make up a very substantial share of new podcast uploads, they currently account for less than one percent of actual listening time. Ultimately, the author concludes that while modern technology serves as a practical assistant for formatting, outlining, or brainstorming, standalone human talent remains completely indispensable for producing work that truly resonates, engages readers, and achieves tangible long-term business results.


TSA seeks biometric identity management support

The Transportation Security Administration is looking for industry assistance to modernize and maintain its internal identity management and background check systems. Through a draft work statement issued by its Enrollment Services and Vetting Programs office, the agency intends to upgrade how it processes biographical and biometric information. This initiative does not create new public-facing data collection routines; instead, it optimizes existing programs that screen pilots, commercial flight students, maritime personnel, hazardous materials drivers, and PreCheck applicants. A major focus of this comprehensive update is moving away from traditional, one-time background checks toward continuous, automated tracking. To do this, the agency plans to expand its use of the Federal Bureau of Investigation's recurrent vetting service and automate the evaluation of text-based criminal records. Additionally, the project outlines plans to integrate existing systems more deeply with Department of Homeland Security biometric databases over the next three to five years. To improve data accuracy and operational speed, the selected contractor will use data science tools, including basic machine learning, to detect data anomalies and help staff review cases more efficiently. The proposed contract includes a twelve-month base period followed by four optional one-year extensions, with all services based at the agency's Virginia headquarters.


Why ‘human in the loop’ falls short – and what to do about it

In this SiliconANGLE column, Jason Bloomberg explains why the common practice of keeping a human in the loop to oversee artificial intelligence operations is deeply flawed. While tech companies often pitch human oversight as a safety net against autonomous systems making mistakes, this method struggles to hold up under real-world pressure. On an individual level, people tend to trust automated systems too much, suffer from mental fatigue during repetitive tasks, or simply wave approvals through without checking. In corporate groups, it often leads to finger-pointing, blame-shifting, or superficial compliance. Furthermore, software systems function in mere seconds, whereas human business workflows require meetings and lengthy procedural delays, creating a massive gap in actual response times. To fix these flaws, tech providers usually suggest limiting software capabilities or building detailed tracking tools, but these heavy-handed changes slow down operations and frustrate commercial goals. Bloomberg suggests flipping the entire setup by focusing on automation in the loop instead. Rather than forcing human workers to become cogs inside an automated pipeline, software should exist purely to assist human day-to-day operations. This perspective ensures people retain ultimate responsibility, prevents software from making critical business decisions, and allows systems to grow safely without overwhelming human operators or clashing with long-term strategic plans.


Why Moving Off the Cloud Is the Easy Part and What Comes Next Is Where Things Get Hard

In this article, Eli Lahr explains that while rising costs and unpredictable performance prompt many organizations to move their digital workloads off public cloud providers, the actual migration is rarely the primary challenge. Instead, the real difficulty emerges afterward, during regular day-to-day operations. Moving away from large, centralized cloud platforms forces companies to manage internal infrastructure details that were previously handled automatically by the provider. This structural transition introduces unfamiliar administrative responsibilities, hidden technical skill gaps, and the intricate task of safely running applications across fragmented environments, including a combination of traditional on-premises hardware, local data centers, and remaining cloud components. Rather than treating this shift as a basic technology relocation, successful organizations choose to approach it as a comprehensive corporate strategy revision. They bring together their engineering, security, and financial departments early in the process to determine exactly where each distinct application belongs according to its unique performance needs, actual long-term expenses, and strict data compliance rules. Lahr recommends explicitly whiteboarding critical workloads to map out their exact structural dependencies, real monthly costs, and detailed response plans for late-night system outages or sudden traffic spikes. Ultimately, establishing precise benchmarks for baseline expenses, execution speed, and overall availability helps ensure companies achieve genuine long-term predictability.


6 critical security gaps every CISO must address

The CSO Online article highlights six essential security shortcomings that corporate security leaders need to address. First, a narrow perspective remains common; many leaders treat cybersecurity purely as a technical IT issue instead of focusing on broader business resilience and downstream operational continuity. Second, a noticeable lag exists between the swift automation used by digital attackers and the slower, more traditional response times of corporate defense teams. Similarly, security operations frequently struggle to match the rapid pace of general business changes, adoptions, and market expansions. Internal talent issues have also evolved significantly; the primary challenge is no longer just finding enough individuals to hire, but ensuring that current employees have the specific, updated skills required to handle an evolving environment. This skills gap is heavily compounded by the rapid growth of artificial intelligence, where top-down corporate initiatives and unauthorized employee tools are vastly outstripping proper security frameworks and oversight. Finally, aging tech infrastructure creates a significant vulnerability, as out-of-date systems cannot support modern security controls, leaving them exposed to easy exploitation. Rather than attempting to block every single threat, professionals are advised to use objective, risk-based prioritization to protect core company workflows and preserve long-term stability.


The Pitfalls of Defaulting to a Single Database: Why "Good Enough" Isn't Always a Good Strategy

When building software systems, it is incredibly common for modern engineering teams to default to a single database because it feels familiar, comfortable, and entirely sufficient for early stage development. However, accepting a "good enough" data architecture often introduces severe technical challenges as an organization scales. Forcing highly diverse data workloads, such as rapid transactional processing, complex analytical reporting, and unstructured document storage, into one general purpose engine creates major performance bottlenecks. No single database system can optimally handle every distinct data requirement, which forces teams to make design compromises that ultimately drag down the performance of the entire platform. Furthermore, relying on a single shared repository creates a precarious single point of failure. If that central data layer experiences an unexpected outage or suffers a performance slowdown from a poorly optimized query, every connected application and service grinds to a sudden halt. This structural centralization tightly couples unrelated services, making future software changes cumbersome and risky. Instead of settling for a monolithic database structure out of convenience, organizations achieve far greater resilience by matching distinct operational tasks with appropriate, specialized storage technologies. Choosing targeted databases minimizes resource friction, streamlines backend infrastructure management, and ensures individual services remain completely independent and stable.
The article examines how advanced artificial intelligence systems have dismantled traditional timeline safety margins for enterprise cyber defense. Historically, while AI could exploit known security flaws, it struggled to identify them independently. However, the release of Anthropic’s Claude Mythos Preview changed this dynamic by autonomously discovering thousands of zero-day vulnerabilities across major operating systems and browsers at a minimal compute cost. Consequently, the window between vulnerability disclosure and real-world exploitation has collapsed to less than ten hours, rendering traditional, calendar-based patching schedules obsolete. To address this risk, security teams are advised to replace standard severity scoring with a more dynamic, three-layer prioritization filter that integrates real-time exploitation data from federal databases and predictive scoring systems. Additionally, the proliferation of AI-driven developer platforms creates massive security risks because a single compromised host can easily expose high-value credentials across an entire corporate ecosystem. Because formal safety and authorization standards are still years away from implementation, organizations must move away from human-speed response intervals. Securing modern networks requires implementing event-driven patching for core services, conducting proactive asset discovery scans, and strictly auditing authorization boundaries to match the accelerated operational speed of automated adversaries.


Why Data “Spring Cleaning” Is Critical for AI Execution

In a Dataversity article, Michael Curry explains why enterprise data management must transition from a seasonal chore into a continuous operational discipline to support successful AI deployment. Many organizations today struggle with fragmented sources, redundant datasets, and brittle information pipelines. While these data inefficiencies were manageable during early experimental phases, they now directly block modern automation models from scaling properly. Artificial intelligence systems demand highly reliable, context-rich, and easily accessible internal records; without them, models deliver late insights or inaccurate outputs, which quickly destroys user trust. Survey data indicates that a large majority of technology leaders worry about basic quality and accessibility rather than the structural complexity of the algorithm itself. To resolve these operational bottlenecks, companies must modernize infrastructure and routinely clean their digital environments using automated classification, systematic deduplication, and regular platform profiling. Furthermore, businesses must rethink their legacy core systems, which house highly valuable data, by establishing secure, real time access instead of abandoning those platforms entirely. Ultimately, expanding these tools from isolated test pilots into broad enterprise execution requires strict data governance, clear ownership, and standardized business definitions. Because corporate information landscapes shift constantly, keeping foundations clean is a permanent obligation that directly determines if advanced tech projects succeed or stall.


Digital Twins Are Broken, AI Might Finally Fix Them

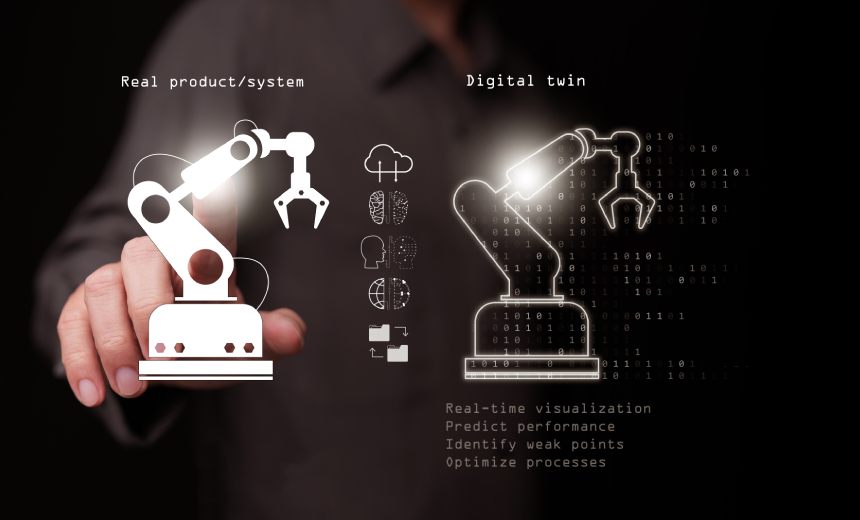
For nearly two decades, digital twins struggled to live up to their initial promises. Most companies used them merely as advanced visualization tools or static engineering models that quickly became disconnected from the physical equipment they represented. Building and maintaining these simulations was highly expensive, and fragmented data across separate corporate departments further limited their actual utility. However, the broader availability of practical artificial intelligence is changing how factories and industrial plants operate. By cleanly integrating live data feeds, modern digital twins can continuously learn from everyday operational events, environmental shifts, and machinery maintenance histories rather than remaining static. This shift allows large companies to simulate factory updates and test potential facility modifications safely without pausing active assembly lines. Beyond basic mirroring, newer setups enable virtual models to accurately predict system failures and automate adjustments directly back into real-world workflows. This ongoing progression also encourages organizations to dismantle the traditional divisions between their plant-floor operational systems and standard corporate IT networks. Ultimately, these tools working together allow manufacturers to bypass previous technical limitations. Instead of managing passive digital replicas, businesses can now run responsive systems that analyze data and optimize physical environments in real time, finally capturing real value from their data investments.


Data discovery gaps that catch enterprises off guard

In an interview with Help Net Security, Schellman CEO Avani Desai highlights a significant disconnect between what organizations believe they know about their own sensitive files and what automated discovery tools actually find. Even companies with advanced compliance dashboards and extensive data catalogs frequently overlook hidden information sitting in abandoned cloud storage, old testing setups, and legacy environments that teams assumed were turned off years ago. This lack of visibility becomes especially problematic during corporate mergers, where overlooked and heavily duplicated files can stall integration work and lead to unexpected, costly cleanups. Desai points out that while synthetic data is currently marketed heavily as a simple shortcut for basic security habits, confidential computing remains underappreciated despite its crucial ability to protect information while it is actively being processed. Interestingly, smaller firms often manage compliance and technical updates much better than large enterprises because they operate with less internal bureaucracy, fewer outdated computer systems, and far clearer lines of individual responsibility. Ultimately, mapping out company information cannot be treated as a fixed, one-off task. Desai suggests the real test of a company's readiness is knowing exactly who is responsible for continuously updating that data map after any routine system change, software update, or cloud migration takes place.