Showing posts with label Sustainability. Show all posts

Daily Tech Digest - August 18, 2026


Quote for the day:

"Be miserable. Or motivate yourself. Whatever has to be done, it's always your choice." -- Wayne Dyer

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI can find zero-days but still can’t reliably write secure code

While artificial intelligence has become highly capable at discovering new vulnerabilities and writing exploits, it still struggles significantly with writing secure code and fixing security flaws. Recent studies highlight a growing imbalance between these offensive and defensive capabilities, showing that a large portion of code generated by artificial intelligence contains known vulnerabilities. This gap poses a serious risk for organizations using these tools to speed up software development, as the models often introduce technical debt and security exposure alongside faster delivery times. Experts note that writing secure code is inherently difficult, and language models lack the necessary organizational context, such as specific architectures, threat models, and internal policies, to do it reliably on their own. Simply improving training data is unlikely to solve this problem entirely. Instead, the software industry is shifting toward using specialized environments that embed strict security checks, context, and validation workflows directly into the development process. These systems provide the necessary constraints to produce safer software. However, automated systems cannot replace human judgment. Traditional testing tools and human oversight remain absolutely essential. Ultimately, experienced human developers must maintain control over reviewing and approving all code changes to ensure the final product is genuinely secure and robust.


A New Paradigm for IT Budgeting

Traditional annual IT budgeting often frustrates organizations because it relies on rigid planning cycles that stifle flexibility and waste valuable time. When companies prioritize individual projects and force them to compete above a funding threshold, they unintentionally encourage padded estimates and a rush to spend remaining funds at the end of the year. This conventional approach measures success by how well teams stick to initial estimates rather than the actual value they deliver, leaving IT departments struggling to keep pace with changing business needs. To resolve these issues, organizations can shift toward an envelope-based portfolio model. Instead of evaluating dozens of isolated projects, leadership allocates funds into broader strategic envelopes, such as improving operational efficiency or enhancing the customer experience. This method simplifies financial management by keeping the focus on outcomes rather than strict plan adherence. Leaders are given the authority to adjust priorities and reallocate resources as conditions change without restarting the entire budgeting process. Artificial intelligence can further assist by streamlining early-stage planning and identifying helpful patterns across initiatives. Ultimately, adopting this envelope approach transforms IT from a constrained, overworked service provider into a responsive partner focused on delivering meaningful results and adapting calmly to new challenges.

European sovereignty is an opportunity to take a giant leap forward

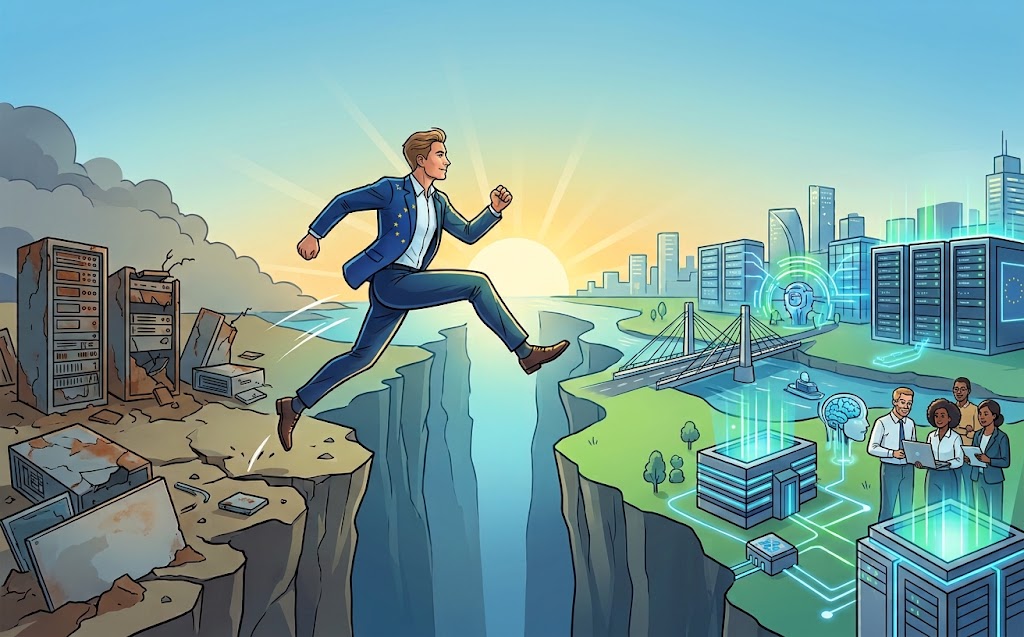
The conversation around European digital sovereignty is maturing beyond a simple desire to disconnect from American tech giants. Instead, it presents a rare chance to skip over outdated legacy systems and build modern data infrastructure from the ground up. However, achieving this requires more than just new hardware. Currently, many companies struggle because small innovation teams work in isolation while the broader workforce remains stuck on older applications. While European legislation has laid the groundwork for technological independence, the actual services and applications needed to run on these new platforms are still missing. Experts emphasize that successful modernization relies on unifying fragmented data across sectors, much like managing national public works through a single, coordinated system. This level of integration demands deep collaboration across companies rather than isolated efforts. Furthermore, the belief that Europe lacks the necessary talent is a misconception; many major tech platforms were built by small teams with European roots. The actual barriers holding the continent back are a lack of venture capital and stifling regulatory hurdles. To truly succeed, Europe must shift its focus from excessive regulation to creating strong commercial incentives, trusting that the local talent and technology are already fully equipped to manage the transition.


When AI Writes the Code, Specifications Need an Exit Strategy

In the era of AI-generated software, there is a growing temptation to view formal specifications as relics of the past. When artificial intelligence can churn out functional code in seconds, the urge to skip documentation and planning in favor of immediate execution is powerful. Yet, this convenience comes with a hidden cost: a loss of control over the resulting codebase. As the article argues, relying solely on AI to write code without a structured roadmap is a recipe for long-term technical debt. An "exit strategy" is essential. This means maintaining clear, human-readable specifications that act as a blueprint for the system, independent of the tools used to create it. If you cannot understand, modify, or debug your own software without the AI’s help, you have surrendered your agency. True engineering requires foresight, not just rapid output. Specifications provide the necessary guardrails, ensuring that even if an AI writes the initial implementation, the architecture remains grounded in human logic and understandable business requirements. Ultimately, an exit strategy is not about abandoning AI, but about ensuring that developers retain the authority and insight required to manage and evolve their systems effectively over time.


A better approach to generative UI

The article discusses how software developers should approach building dynamic interfaces in applications powered by artificial intelligence. It argues that teams must avoid the common mistake of letting models generate executable code, such as HTML or JavaScript, directly during a live user session. Although having an interface adapt instantly to a user's request sounds appealing, allowing an artificial intelligence to write raw code at run time compromises crucial security, testing, and architectural boundaries. It can lead to unpredictable behaviors and bypass the established rules for user permissions. Instead, the author advocates for a safer method called structured interface intent. With this strategy, the artificial intelligence does not invent the interface code. Rather, it simply chooses from a controlled, pre-defined menu of trusted interface blocks that the core application already knows how to handle. The model returns basic data indicating which visual elements are needed, and the application itself manages the actual display and execution of tasks. By relying on a verified registry of components rather than raw generated code, developers keep absolute control over the application's state, security protocols, and business rules, ensuring that the software system remains dependable, completely safe, and highly predictable while still offering a flexible user experience.


Balancing Sustainable Computing and Computing for Sustainability

The article discusses the critical need to balance two essential goals: making our technology greener and using technology to protect the environment. On one hand, sustainable computing focuses on reducing the heavy environmental toll of our digital lives. As computers become more powerful and data centers grow, they consume massive amounts of energy and produce significant electronic waste. To address this, the industry must develop hardware that uses less energy, improve how computers are manufactured, and create longer lasting devices. On the other hand, computing for sustainability involves using advanced digital tools to solve broad environmental challenges. We can use powerful algorithms and data analysis to optimize power grids, predict climate patterns, and manage natural resources more effectively. However, a conflict arises because the very tools needed to solve these global issues require immense computing power, which in turn increases energy use and carbon emissions. The piece argues that successfully navigating this tension requires a coordinated effort across different fields. Engineers, software developers, and policymakers must work together to ensure that the environmental benefits of new digital solutions outweigh the physical costs of running them. Ultimately, we must design technology that serves the planet without quietly adding to its burdens.


Why people, not technology, drive digital transformation

Akio Ueda argues that digital transformation is fundamentally about people rather than just implementing new tools. Often, companies deploy advanced systems like artificial intelligence or cloud computing but fail to see real, meaningful changes in their daily operations. This happens largely because employees lack the necessary skills to integrate these complex tools into their regular workflows. Ueda emphasizes that technical experts alone cannot drive transformation. True success requires individuals who understand business challenges, focus on customer needs, and can clearly guide organizational change. He points out that a strong talent strategy must align seamlessly with a company's core business goals and be supported by consistent policies across all departments. Training programs alone are not enough; employees must apply their learning practically to bridge the gap between knowing and doing. Furthermore, recognizing and rewarding these efforts through internal and external praise is a practical way to build motivation and confidence. Ultimately, a chief information officer's role is shifting from merely managing technology to developing the people who will execute the strategy. Investing in human potential is the most reliable way to ensure that technological advancements translate into lasting business value, empowering an organization to adapt, grow, and thrive in a constantly changing modern landscape.


How To Build Executive Presence From The Inside Out

True executive presence is not about having a prestigious job title or projecting a polished, charismatic image. Instead, it relies entirely on inner traits and deliberate daily behaviors that build lasting trust and credibility. To develop this presence, you must focus on how you interact with others and manage yourself during stressful situations. It begins with emotional intelligence and the ability to read a room, ensuring you set a calm emotional tone rather than simply reacting to pressure. Small actions like offering a genuine smile and actively listening before you speak go a long way in making your peers feel valued and understood. Furthermore, speaking up with courage to say the hard things, rather than feigning absolute certainty, shows authentic leadership. Another effective but often ignored habit is intentionally pausing before you respond to difficult questions. Taking a brief moment to breathe signals capacity and thoughtfulness rather than anxiety or haste. Real presence also requires you to be fully engaged in every interaction, putting away distractions to focus on the people in front of you. Ultimately, your character, competence, and conduct must align consistently over time. When your actions match your words day after day, you develop a grounded leadership identity that people respect and follow.


Why Some Companies Are Pulling Back on AI Coding

Although artificial intelligence promised to change software development by drastically speeding up code generation, some organizations are now reconsidering their heavy reliance on these tools. The initial enthusiasm is giving way to a more measured approach as engineering teams encounter practical challenges with automated coding. One major concern is the degradation of code review cultures; because AI-generated code often looks correct at first glance, developers may review it less rigorously, allowing subtle bugs and security vulnerabilities to slip into production. Furthermore, companies are noticing structural issues within their software. While these tools can write functional snippets, they often lack the broad context needed to adhere to a project's long-term design patterns, leading to fragmented systems and rising technical debt over time. Data privacy remains another critical issue, as sharing proprietary business logic or sensitive customer information with external language models poses significant security and compliance risks. Finally, leaders are observing a decline in deep system knowledge among their engineering teams. When developers rely too heavily on automated prompts rather than grappling with complex logic themselves, institutional knowledge suffers. Consequently, rather than abandoning these tools entirely, many businesses are pulling back to establish stricter guidelines, ensuring that human judgment and solid engineering practices remain central to their operations.


Why Traditional Data Governance Cannot Secure Business Decisions

Traditional data governance focuses on describing and organizing information through tools like glossaries, catalogs, and data lineage. While these methods help organizations understand what their data means and where it comes from, they often fail to connect that information to the actual business decisions it supports. Organizations do not govern data just to create better catalogs; they do so to ensure they can confidently grant, deny, fund, or authorize actions. The main limitation of traditional models is that they document data without showing how it secures critical operations. To fix this gap, organizations must adopt a decision focused approach. This means treating important business decisions as the central framework for governance. By separating business choices from data management tasks and linking them together, companies can create a clear chain of trust. This chain connects a requirement to a specific decision, the rules that guide it, the data used, the controls that verify it, and the evidence that proves it was handled correctly. Moving forward, governance must go beyond simply adding more descriptions to a database. It requires building a complete system where rules, controls, and error corrections are directly tied to their business consequences. This approach ensures organizations can clearly explain, defend, and trust their decisions.

Daily Tech Digest - July 24, 2026


Quote for the day:

“Do the thing you fear to do and keep on doing it… that is the quickest way yet discovered to conquer fear.” -- Dale Carnegie

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


Google’s AI and computing chief talks about its shapeshifting data centers

Google is rapidly upgrading its data center infrastructure to meet the massive computing demands of a new era of artificial intelligence agents. In a recent interview, Mark Lohmeyer, Google’s vice president of AI and computing, explained that modern AI has shifted from simple chat interfaces to complex agent driven tasks, increasing inference workloads dramatically. To support this rapid growth while keeping costs manageable, Google is investing heavily in advanced hardware and software technologies. Energy efficiency remains a top priority, achieved through widespread liquid cooling and the new highly efficient Axion based processor. The company has also introduced its eighth generation Tensor Processing Unit, featuring distinct systems optimized separately for training and inference workloads. To ensure maximum flexibility, Google is improving software compatibility so that applications can easily shift between these TPUs and traditional graphics processors. Additionally, Google is transforming its Kubernetes engine into an agile orchestration tool capable of spinning compute resources up and down almost instantly. To tie everything together, the new Virgo network architecture allows millions of processors to connect seamlessly, while upgraded storage systems deliver massive bandwidth and low latency. Ultimately, these targeted upgrades allow Google to deliver scalable, high performance computing power that keeps pace with fast evolving industry requirements.


Should we still design code for humans?

When artificial intelligence takes over the heavy lifting of writing software, it is natural to wonder if we still need to structure code for human eyes. The short answer is a definitive yes. Even as AI accelerates how quickly we can build systems, it does not remove the need for clarity, precision, and careful organization. Programming languages were created to strike a necessary balance, allowing people to express complex logic safely while giving machines exact instructions to execute. Natural language is simply too vague to serve as the sole blueprint for reliable software. Instead of making human-readable code obsolete, AI makes good design more important than ever. If a system is built on messy or confusing foundations, AI tools will simply amplify those flaws at a much faster rate. Well-organized code with clear names and logical boundaries helps both human developers and AI assistants understand the underlying intent of the system. Ultimately, developers are shifting from merely typing lines of code to acting as essential reviewers and stewards of system integrity. Maintaining high standards for code quality ensures that human developers can confidently verify, adapt, and trust the software that runs our critical infrastructure, keeping control securely in human hands.


Continuous authentication is the new trust infrastructure

The traditional "authenticate once" model is no longer sufficient in a landscape where AI-driven threats like deepfakes and sophisticated phishing compromise digital security. Relying on a single checkpoint—like a password or initial biometric scan—assumes that trust established at login remains secure throughout a session, a premise attackers exploit by hijacking active sessions or using malware. To counter this, organizations are shifting toward continuous authentication, treating digital identity as a persistent profile that must be consistently validated. Rather than granting permanent trust after an initial check, this approach continuously evaluates risk using a blend of explicit signals, like biometric checks, and passive signals, such as user behavior and location. When risk indicators rise, the system dynamically requires additional, strong authentication to re-establish trust. This continuous model bridges the gap between verification—proving identity at onboarding—and authentication, ensuring the same user remains present in all subsequent interactions. By eliminating disjointed security checkpoints across various channels, continuous authentication acts as the essential infrastructure for maintaining trust, ensuring that identity security adapts in real time to evolving threats.


Why climate-tech is emerging as an important segment within India’s enterprise technology landscape

Climate technology in India has transitioned from a side conversation about sustainability into a core component of mainstream enterprise technology. Once viewed simply as a compliance task or public relations effort, it is now an essential infrastructure decision for modern businesses. This shift is supported by strong investment, with the sector drawing roughly $12.8 billion in funding, indicating a mature market driven by genuine commercial traction rather than just experimental grants. Several practical factors are accelerating this change, primarily the need for national energy security and the introduction of stricter policies, such as the upcoming carbon trading market. As a result, tools like carbon accounting software, energy management systems, and emissions monitoring are no longer isolated to sustainability offices; they sit firmly on the desks of chief information and technology officers. Organizations are increasingly seeking to secure their own resources, such as water and energy, to build independence from strained public systems. For business leaders, the message is clear: climate technology should be integrated directly into their standard digital planning rather than treated as a separate project. Companies that adopt these systems early will gain a lasting structural advantage over those who wait until regulations force them to change.


The new value architecture of the AI-native SaaS era

The article explains how artificial intelligence is fundamentally changing the software industry, specifically the software as a service business model. Traditionally, companies sold software access based on how many employees needed to use it, known as seat pricing. Now, because artificial intelligence functions more like an automated worker than just a passive tool for humans, the focus is shifting toward measuring what the software actually accomplishes. This means pricing and success metrics are moving toward a credit system, where customers pay for the specific amount of work the artificial intelligence performs or the computing power it requires. Furthermore, artificial intelligence costs more to run per task compared to traditional software, which makes older profit measures completely outdated and inaccurate. As a result, software businesses must track new financial indicators, such as how quickly customers use their purchased credits and the actual profit made after covering artificial intelligence computing expenses. Investors are also adapting how they value these companies, looking closely at reliable, committed credit income versus unpredictable daily usage. Ultimately, software providers need to embrace these new financial tracking methods to properly price their products, understand their true operational costs, and clearly demonstrate their long-term stability to investors in a rapidly changing market.


The automotive software vulnerabilities hiding in your dashboard

Modern vehicles increasingly rely on established operating systems like Linux, Android, and QNX, transforming cars into rolling computers. While this shift enables quick updates and app ecosystems, it also introduces years of publicly documented software vulnerabilities. Researchers at Télécom SudParis developed a specialized scanner named VERA to evaluate these operating systems within current vehicles. Their analysis revealed a wide variation in known flaws. For example, Automotive Grade Linux showed over a thousand vulnerabilities, whereas highly certified systems had significantly fewer. However, the researchers emphasize that a high vulnerability count is not necessarily a definitive measure of risk. A documented flaw only matters if the vulnerable code is active and reachable by an attacker under specific conditions. To demonstrate this, the team tested identical attacks across different platforms, finding that success depended heavily on which specific defenses were enabled rather than the theoretical severity of the bug. Furthermore, standard security scanners often struggle with automotive software, generating numerous false alarms. By filtering out irrelevant components that a secured vehicle would never expose, the new scanner provides a more accurate assessment. Ultimately, while modern cars inherit the flaws of general computing, the practical challenge lies in identifying which bugs are genuinely exploitable.


Reselling unused cloud instances is no longer easy

Many organizations are purchasing large amounts of reserved cloud capacity, particularly for artificial intelligence projects, only to discover they have overcommitted and cannot easily unload the excess. In the past, companies could rely on a secondary resale market, such as the official marketplace provided by Amazon Web Services, to sell their unused reservations to other businesses and recover some of their costs. However, AWS shut down this official resale channel in January 2024, leaving many customers completely locked into their ongoing financial commitments. Today, the available options for handling excess capacity are far more limited and complex. Companies can attempt to modify their existing reservations if their provider allows it, navigate riskier independent brokers, or try to optimize their current usage to reduce future waste. None of these alternatives fully solve the initial problem of overspending. Because major cloud providers tightly control these contracts and can change their policies at any time, relying on the ability to resell unused space as a safety net is no longer a realistic strategy. Moving forward, businesses must focus on accurate forecasting, careful capacity planning, and responsible financial management rather than simply assuming they can always sell their way out of a poor purchasing decision.


When the Responder Is the Threat — Ransomware Negotiators, Insider Trust, and Incident Response Ethics

The article examines the insider threat posed by compromised incident response professionals during ransomware attacks, highlighted by a recent Department of Justice case. In April 2026, a former ransomware negotiator pleaded guilty to assisting the BlackCat ransomware group by secretly feeding them victims' confidential negotiation strategies and insurance policy limits. This betrayal allowed the attackers to maximize their extortion demands, proving that trust can easily be weaponized in chaotic breach environments. To prevent such compromises, organizations must treat ransomware response as a highly secure, restricted access operation rather than an unmanaged crisis. A key recommendation is enforcing strict segregation of duties. No single individual should control negotiations, forensic investigations, legal strategy, and payment logistics. Sensitive details, particularly cyber insurance limits and payment ceilings, should only be disclosed to team members who absolutely require them. Furthermore, all communications with threat actors must be carefully logged, monitored, and reviewed to prevent unauthorized side deals. Companies are strongly advised to vet incident response vendors well before an attack occurs. Engagement contracts should explicitly prohibit conflicts of interest and unauthorized information sharing. Ultimately, while organizations rely heavily on specialized experts during a security emergency, that reliance must be balanced with rigorous access controls and continuous oversight.


Multi-Agent AI for Production Security Operations: An A2A and MCP Architecture in a 5G Core

This article outlines a multiple agent AI architecture designed for production security operations, specifically within a top tier telecommunications 5G core. The primary challenge in modern security centers is not just triage, but the inability of engineering teams to write detection rules fast enough to keep pace with evolving threats. To solve this, the author proposes a system of specialized AI agents coordinated through an open protocol and integrated into the environment using the Model Context Protocol. A key component of this architecture is its reliance on classical anomaly detection to filter raw telemetry before it reaches the language models. This approach bounds inference costs and ensures the AI processes only genuinely novel samples. Furthermore, a dedicated reviewer agent enforces safety constraints as code and provides a clear escalation path to human operators. The author explicitly rejects using a single monolithic language model, which is too unpredictable for production, as well as simply bolting generative AI onto existing security tools. Implementing this collaborative strategy has significantly improved operational efficiency, reducing the time needed to detect and respond to threats by forty percent and cutting the human effort required to create new detection rules from three hours to just fifteen minutes.


After the AI Rush, Can Data Centers Reclaim Sustainability?

The rapid expansion of generative AI temporarily sidelined the data center industry's longstanding focus on environmental sustainability, shifting priorities toward raw performance and massive scale. Before the AI boom, operators actively improved efficiency through better cooling, reduced water use, and robust renewable energy commitments. However, the immense power requirements of modern AI infrastructure forced many providers to admit that reaching their ambitious net zero targets would become significantly more difficult. Now, the industry is facing a necessary course correction driven by hard economics, community opposition, and strict physical grid constraints. Heightened public scrutiny and regulatory pauses on new facility builds mean that operators can no longer afford to ignore their environmental footprint if they want to keep growing. Sustainability is returning not just as a corporate ideal, but as an absolute business necessity. Because power availability is the ultimate bottleneck, any energy wasted on inefficient cooling is power that simply cannot be monetized for computing. As a result, data centers are prioritizing advanced water conservation and strict energy efficiency measures to secure local permitting approvals and control operating costs. Ultimately, the next phase of data center growth requires operators to seamlessly integrate environmental stewardship with economic pragmatism to successfully maintain their expansion in the AI era.

Daily Tech Digest - July 15, 2026


Quote for the day:

“Always treat your employees exactly as you want them to treat your best customers.” -- Stephen R. Covey

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 17 mins • Perfect for listening on the go.


AI incidents need a new playbook. Here’s how to build one

Traditional security incident response playbooks are ill-equipped to handle modern AI incidents. While conventional cybersecurity focuses on malicious intrusions and breaches of confidentiality or availability, AI failures often happen simply because a probabilistic model behaves poorly. Issues like hallucinations and bias can occur without any external attack, meaning standard response metrics often miss the core problem entirely until it causes real-world harm. To address this significant gap, organizations must build dedicated AI playbooks that accurately account for both internal model errors and externally induced attacks, such as data poisoning. A mature AI incident response strategy requires a few foundational elements to be truly effective. First, organizations need an AI Bill of Materials to track the underlying components and data within every production system. Second, accessible model cards must be available to provide responders with immediate context on a model's limits. Third, a designated data scientist must be on the incident call tree to analyze real-time behavior. Finally, teams must establish pre-defined rollback thresholds to trigger safe containment or fallback switches without causing unnecessary business disruption. By rewriting detection triggers and involving legal teams early to manage liability risks, companies can proactively secure their AI systems before an incident ever occurs.


Trust Under Attack: Why Resilience and Not Compliance Will Define The Next Generation of Enterprise Security

In a recent interview, Pranay Modi, Chief Information Security Officer at MAS Financial Services, outlines a practical vision for the future of enterprise cybersecurity. He challenges the common belief that people are the weakest link in security; instead, they are simply the most frequent targets. By building a supportive culture where reporting mistakes is safe and security processes are straightforward, organizations can turn their workforce into a powerful defense network. Modi advises that as threats become harder to predict, companies should focus on fundamental, lasting capabilities. These include clear visibility into all digital assets, strict identity management for both humans and machines, and recovery plans that are regularly practiced rather than just documented on paper. He also highlights the growing importance of managing third-party risks and ensuring company boards truly understand their cyber exposure. Crucially, Modi warns against confusing compliance with actual security. Passing an audit is merely a starting point, not a guarantee of safety. He emphasizes that while the daily tasks of cybersecurity can be handed off, the ultimate responsibility for protecting a company's digital trust rests firmly with its executive leadership. The goal is no longer just preventing attacks, but ensuring the organization remains resilient when disruptions inevitably occur.


Why the most dangerous code test failures are invisible

Code testing is essential for modern software quality, but the most dangerous bugs are the ones that remain completely invisible. According to quality assurance engineer Mikhail Golikov, while teams often celebrate catching obvious errors, the true risk lies in failures that never trigger an alarm. These quiet failures typically fall into three main categories: tests that exist but are never executed, unreliable tests that teams learn to ignore, and untested behavior documented only in production logs. Unexecuted tests act as mere documentation rather than actual safety checks. Unreliable or flaky tests are even worse because they condition engineers to dismiss real failures as background noise, effectively lowering the overall trust of the team in their systems. Furthermore, failing to turn real world production logs into test cases leaves a massive gap between what software does in reality and what developers actually monitor. The core issue across all these structural problems is a sheer lack of system visibility, rather than a lack of modern tools. True software quality is not simply defined by having a high total volume of tests or the absence of visible bugs. Instead, it requires the unglamorous work of making sure every failure becomes impossible to ignore, ensuring that real problems reliably turn into clear signals.


The New Face of Fraud: Identity, AI and Digital Trust

This article discusses the changing nature of digital fraud, emphasizing that cybercriminals are shifting their focus from attacking systems to compromising user identities. As digital transactions grow faster and more common, attackers find it easier to blend in using stolen credentials rather than breaking into systems. The author explains that account takeover is a major threat because it allows attackers to bypass alerts and mimic normal behavior, making fraud harder to spot until the damage is done. Phishing attacks are also becoming more personalized and effective, with criminals using AI to craft targeted messages that trick users into giving up their credentials. Once inside, attackers can operate as trusted users. To combat this, the article highlights the importance of identity-centric security. Organizations need to treat every login as a trust decision and continuously verify identities. The piece also notes India's regulatory efforts, such as using AI and shared intelligence to detect fraudulent activities early. For businesses, practical steps include identifying high-risk periods, strengthening identity governance, and testing their response times. Ultimately, the future of fraud prevention lies in combining identity intelligence, AI-driven detection, and behavioral analytics to catch risks before they result in financial loss.


Microsoft’s Secure Boot has been broken for a decade and no one noticed until now

The Ars Technica article discusses a significant security flaw in Microsoft's Secure Boot system that has existed for a decade. ESET researchers found 11 outdated UEFI shim bootloaders signed by Microsoft that allow attackers to bypass Secure Boot entirely. This bypass works on nearly any UEFI-based machine that trusts the Microsoft Corporation UEFI CA 2011 certificate, regardless of the operating system. These forgotten shims are typically used to establish a chain of trust for Linux distributions and other third-party boot software. However, because they are old versions (0.9 and below) they contain known vulnerabilities. Attackers can exploit these flaws by bringing a vulnerable shim to a target system, replacing the existing bootloader, and executing malicious code during the boot sequence. This allows the installation of powerful bootkits like Bootkitty or BlackLotus, which operate below the operating system level and are notoriously difficult to detect and remove. Microsoft addressed this issue by revoking the affected shim certificates in its June 2026 Patch Tuesday update. The revocation prevents these specific vulnerable binaries from being trusted, but the incident highlights the ongoing challenges of managing trust and revocation within the UEFI Secure Boot ecosystem.


‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets

Security researchers from Tel Aviv University, Technion, and Intuit have identified a new cyber threat called "HalluSquatting," which exploits the tendency of generative AI models to hallucinate false information. As developers increasingly rely on AI coding agents to independently write code or install software packages, these assistants sometimes generate incorrect, invalid resource names instead of the intended ones. Hackers can predict these hallucinated names, register them, and attach malicious code to them. When the AI coding assistant unknowingly retrieves the fake package, it installs malware directly into the developer's system, potentially creating large botnets. This method resembles typosquatting, but rather than waiting for humans to mistype a web address, attackers rely on AI agents to make the mistake for them. The technique targets the growing trend of independent applications that execute tasks with little human oversight on modern development teams. In tests against popular AI coding tools like GitHub Copilot and Google Gemini CLI, researchers found that models hallucinated false repository names 85 percent of the time, highlighting a notable security weakness. Ultimately, HalluSquatting bypasses traditional security barriers by blending AI prompt manipulation with conventional malware strategies, representing a serious challenge as AI tools become integrated into software engineering environments.


The Shadow Insider: How AI Agents Are Becoming the New Insider Risk Nobody Is Monitoring

The article discusses a growing security challenge in modern workplaces: the rise of artificial intelligence assistants as a new type of insider risk. Traditionally, security teams have focused on monitoring human employees, contractors, and vendors who have legitimate access to sensitive company systems. However, organizations are now deploying autonomous software agents that perform tasks like reading emails, summarizing documents, and updating customer records. These agents operate as digital workers with their own identities and permissions, often acting without direct human oversight. The main issue is not that these agents are intentionally harmful, but that they quickly accumulate access to multiple systems simultaneously, creating a complex web of permissions. Over time, an agent designed for a simple task might gain access to confidential financial reports or legal documents simply because new tasks require more information. This gradual expansion of access often goes unnoticed because these machine identities do not follow normal human work patterns, making many traditional security monitoring tools completely ineffective. To address this serious problem, security teams must treat every software agent as a managed identity with strict, narrow permissions and closely monitor their behavior beyond basic login events to ensure they firmly remain aligned with their original purpose.


Prompt Privacy Is the New Endpoint Security Problem

As organizations adopt large language models, a new security challenge has emerged: protecting the privacy of prompts. While artificial intelligence offers significant advantages by allowing users to complete tasks using natural language, these inputs often include sensitive information such as trade secrets, credentials, or personal data. If employees submit confidential details into a model without proper safeguards, the information might be retained or used for future training, leading to accidental data exposure. Furthermore, attackers are actively exploiting this vulnerability through prompt injections, where they carefully craft instructions to manipulate the model into revealing hidden system rules, altering its intended behavior, or executing unauthorized commands. This problem extends to modern artificial intelligence agents and browsers, which effectively function as a new type of network endpoint. Because these agents operate autonomously and hold active user sessions, hidden malicious instructions on websites can trick them into compromising systems or authorizing transactions. Traditional security tools are generally unequipped to handle these specific threats. To address these risks, security teams must treat prompts as highly sensitive data. Organizations can better protect their networks by rigorously filtering both inputs and outputs, enforcing strict access privileges for artificial intelligence agents, and closely monitoring all system interactions over time.


'Yellow Teams' Are Defining the Future of AI Security

As the capabilities of artificial intelligence grow, organizations are increasingly relying on "yellow teams" to build robust defenses against emerging threats. Composed primarily of engineers and developers, these specialized teams work closely with both offensive red teams and defensive blue teams to understand and test the limits of advanced AI models, such as Claude Mythos and GPT-5.5. A central responsibility of yellow teams involves developing "harnesses." These are dedicated software frameworks that wrap around an AI model to firmly restrict its permissions, define operational rules, and guide its actions. This essential step focuses the AI's capabilities and ensures it fully understands the specific network context, which drastically reduces false positives during routine security testing. With these carefully refined tools, companies are uncovering a significant number of software vulnerabilities. To handle this influx of information, blue and yellow teams are integrating more deeply than before. Yellow teams are taking a proactive approach by incorporating AI directly into the software development process. This helps engineering departments identify exactly which coding practices need adjustment to prevent security flaws from recurring. By bridging the gap between security analysis and daily engineering work, yellow teams provide a highly practical strategy to protect systems against future attacks.


The neocloud approach to sustainability

The neocloud model offers a practical alternative to massive, centralized data centers by distributing computing resources closer to where people actually use them. Instead of building giant facilities that place heavy, sudden demands on local power grids and water supplies, this approach relies on a network of smaller, interconnected sites. By doing so, it avoids the severe strain that huge building projects often place on communities and utilities. A key environmental benefit of this distributed method is its incremental use of electricity and water. Rather than drawing millions of gallons of water daily for cooling or requiring massive new power plants, these localized centers allow resource consumption to grow gradually and sustainably. Processing data closer to the source also cuts down on the energy required to transmit information over long distances, which inherently improves response times and reliability for users. Furthermore, this localized strategy helps keep data within specific regions, addressing privacy and security concerns without sacrificing performance. Ultimately, spreading out the physical infrastructure makes the growth of advanced computing far more manageable. It aligns technological progress with environmental limits, proving that we can meet modern computing needs without placing an overwhelming burden on our natural resources or local infrastructure.

Daily Tech Digest - April 01, 2026


Quote for the day:

"If you automate chaos, you simply get faster chaos. Governance is the art of organizing the 'why' before the 'how'." — Adapted from Digital Transformation principles


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Why Culture Cracks During Digital Transformation

Digital transformation is frequently heralded as a panacea for modern business efficiency, yet Adrian Gostick argues that these initiatives often falter because leaders prioritize technological implementation over cultural integrity. When organizations undergo rapid digital shifts, the "cracks" in culture emerge from a fundamental misalignment between new tools and the human experience. Employees often face heightened anxiety regarding job security and skill relevance, leading to a pervasive sense of uncertainty that stifles productivity. Gostick emphasizes that the failure is rarely technical; instead, it stems from a lack of transparent communication and psychological safety. Leaders who focus solely on ROI and software integration neglect the emotional toll of change, resulting in disengagement and burnout. To prevent cultural collapse, management must actively bridge the gap by fostering an environment of gratitude and clear purpose. This necessitates involving team members in the transition process and ensuring that digital tools enhance, rather than replace, human connection. Ultimately, the article posits that culture acts as the essential operating system for any technological upgrade. Without a resilient foundation of trust and recognition, even the most sophisticated digital strategy is destined to fail, proving that people remain the most critical component of successful corporate evolution.


Most AI strategies will collapse without infrastructure discipline: Sesh Tirumala

In an interview with Express Computer, Sesh Tirumala, CIO of Western Digital, warns that most enterprise AI strategies are destined for failure without rigorous infrastructure discipline and alignment with business outcomes. Rather than focusing solely on advanced models, Tirumala emphasizes that AI readiness depends on a foundational architecture encompassing security, resilience, full-stack observability, scalable compute platforms, and a trusted data backbone. He argues that AI essentially acts as an amplifier; therefore, applying it to a weak foundation only industrializes existing inconsistencies. To achieve scalable value, organizations must shift from fragmented experimentation to disciplined execution, ensuring that data is connected and governed end-to-end. Beyond technical requirements, Tirumala highlights that the true challenge lies in organizational readiness and change management. Leaders must be willing to redesign workflows and invest in human capital, as AI transformation is fundamentally a people-centric evolution supported by technology. The evolving role of the CIO is thus to transition from a technical manager to a transformation leader who integrates intelligence into every business decision. Ultimately, infrastructure discipline separates successful enterprise-scale deployments from those stuck in perpetual pilot phases, making a robust foundation the most critical determinant of whether AI delivers real, sustained value.


IoT Device Management: Provisioning, Monitoring and Lifecycle Control

IoT Device Management serves as the critical operational backbone for large-scale connected ecosystems, ensuring that devices remain secure, functional, and efficient from initial deployment through decommissioning. As projects scale from limited pilots to millions of endpoints, organizations utilize these processes to centralize control over distributed assets, bridging the gap between physical hardware and cloud services. The management lifecycle encompasses four primary stages: secure provisioning to establish device identity, continuous monitoring for telemetry and health diagnostics, remote maintenance via over-the-air (OTA) updates, and responsible retirement. These capabilities offer significant benefits, including enhanced security through credential management, reduced operational costs via remote troubleshooting, and accelerated innovation cycles. However, the field faces substantial challenges, such as maintaining interoperability across heterogeneous hardware, managing power-constrained battery devices, and supporting hardware over extended lifespans often exceeding a decade. Looking forward, the industry is evolving with the adoption of eSIM and iSIM technologies for more flexible connectivity, alongside a shift toward zero-trust security architectures and AI-driven predictive maintenance. Ultimately, robust device management is indispensable for mitigating security risks and ensuring the long-term reliability of IoT investments across diverse sectors, including smart utilities, industrial manufacturing, and mission-critical healthcare systems.


Enterprises demand cloud value

According to David Linthicum’s analysis of the Flexera 2026 State of the Cloud Report, enterprise cloud strategies are undergoing a fundamental shift from simple cost-cutting toward a focus on measurable business value and ROI. After years of grappling with unpredictable billing and wasted resources—estimated at 29% of current spending—organizations are maturing by establishing Cloud Centers of Excellence (CCOEs) and dedicated FinOps teams to ensure centralized accountability. This trend is further accelerated by the rapid adoption of generative AI, which has seen extensive usage grow to 45% of organizations. While AI offers immense opportunities for innovation, it introduces complex, usage-based pricing models that demand early and rigorous governance to prevent financial sprawl. To maximize cloud investments, the article recommends doubling down on centralized governance, integrating AI oversight into existing frameworks, and treating FinOps as a continuous operational discipline rather than a one-time project. Ultimately, the industry is moving past the chaotic early days of cloud adoption into an era where every dollar spent must demonstrate a tangible return. By aligning technical innovation with strategic business goals, mature enterprises are finally extracting the true value that cloud and AI technologies originally promised, turning potential liabilities into competitive advantages.


The external pressures redefining cybersecurity risk

In his analysis of the evolving threat landscape, John Bruggeman identifies three external pressures fundamentally redefining modern cybersecurity risk: geopolitical instability, the rapid advancement of artificial intelligence, and systemic third-party vulnerabilities. Geopolitical tensions are no longer localized; instead, battle-tested techniques from conflict zones frequently spill over into global networks, particularly endangering operational technology (OT) and critical infrastructure. Simultaneously, AI has triggered a high-stakes arms race, lowering entry barriers for attackers while expanding organizational attack surfaces through internal tool adoption and potential data leakage. Finally, the concept of "cyber inequity" highlights that an organization’s security is often only as robust as its weakest vendor, with over 35% of breaches originating within partner networks. To navigate these challenges, Bruggeman advocates for elevating OT security to board-level oversight and establishing dedicated AI Risk Councils to govern internal innovation. Rather than aiming for absolute prevention, successful leaders must prioritize resilience and proactive incident response planning, operating under the assumption that external partners will eventually be compromised. By integrating these strategies, organizations can better withstand pressures that originate far beyond their immediate control, shifting from a reactive posture to one of coordinated defense and long-term business continuity.


Failure As a Means to Build Resilient Software Systems: A Conversation with Lorin Hochstein

In this InfoQ podcast, host Michael Stiefel interviews reliability expert Lorin Hochstein to explore how software failures serve as critical learning tools for architects. Hochstein distinguishes between "robustness," which targets anticipated failure patterns, and "resilience," the ability of a system to adapt to "unknown unknowns." A central theme is "Lorin’s Law," which posits that as systems become more reliable, they inevitably grow more complex, often leading to failure modes triggered by the very mechanisms intended to protect them. Hochstein argues that synthetic testing tools like Chaos Monkey are useful but cannot replicate the unpredictable confluence of events found in real-world outages. He emphasizes a "no-blame" culture, asserting that operators are rational actors who make the best possible decisions with available information. Therefore, humans are not the "weak link" but the primary source of resilience, constantly adjusting to maintain stability in evolving socio-technical systems. The discussion highlights that because software is never truly static, architects must embrace storytelling and incident reviews to understand the "drift" between original design assumptions and current operational realities. Ultimately, building resilient systems requires moving beyond binary uptime metrics to cultivate an organizational capacity for handling the inevitable surprises of modern, complex computing environments.


How AI has suddenly become much more useful to open-source developers

The ZDNET article "Maybe open source needs AI" explores the growing necessity of artificial intelligence in managing the vast landscape of open-source software. With millions of critical projects relying on a single maintainer, the ecosystem faces significant risks from burnout or loss of leadership. Fortunately, AI coding tools have evolved from producing unreliable "slop" to generating high-quality security reports and sophisticated code improvements. Industry leaders, including Linux kernel maintainer Greg Kroah-Hartman, highlight a recent shift where AI-generated contributions have become genuinely useful for triaging vulnerabilities and modernizing legacy codebases. However, this transition is not without friction. Legal complexities regarding copyright and derivative works are emerging, exemplified by disputes over AI-driven library rewrites. Furthermore, maintainers are often overwhelmed by a flood of low-quality, AI-generated pull requests that can paradoxically increase their workload or even force projects to shut down. Despite these hurdles, organizations like the Linux Foundation are deploying AI resources to assist overworked developers. The article concludes that while AI offers a potential lifeline for neglected projects and a productivity boost for experts, careful implementation and oversight are essential to navigate the legal and technical challenges inherent in this new era of software development.


Axios NPM Package Compromised in Precision Attack

The Axios npm package, a cornerstone of the JavaScript ecosystem with over 400 million monthly downloads, recently fell victim to a highly sophisticated "precision attack" that underscores the evolving threats to the software supply chain. Security researchers identified malicious versions—specifically 1.14.1 and 0.30.4—which were published following the compromise of a lead maintainer’s account. These versions introduced a malicious dependency called "plain-crypto-js," which stealthily installed a cross-platform remote-access Trojan (RAT) capable of targeting Windows, Linux, and macOS environments. Attributed by Google to the North Korean threat actor UNC1069, the campaign exhibited remarkable operational tradecraft, including pre-staged dependencies and advanced anti-forensic techniques where the malware deleted itself and restored original configuration files to evade detection. Unlike typical broad-spectrum attacks, this incident focused on machine profiling and environment fingerprinting, suggesting a strategic goal of initial access brokerage or targeted espionage. Although the malicious versions were active for only a few hours before being removed by NPM, the breach highlights a significant escalation in supply chain exploitation, marking the first time a top-ten npm package has been successfully compromised by North Korean actors. Organizations are urged to verify dependencies immediately as the silent, traceless nature of the infection poses a fundamental risk to developer environments.


Financial groups lay out a plan to fight AI identity attacks

The rapid advancement of generative AI has significantly lowered the cost of creating deepfakes, leading to a dramatic surge in sophisticated identity fraud targeting financial institutions. A joint report from the American Bankers Association, the Better Identity Coalition, and the Financial Services Sector Coordinating Council highlights that deepfake incidents in the fintech sector rose by 700% in 2023, with projected annual losses reaching $40 billion by 2027. To combat these AI-driven threats, the groups have proposed a comprehensive plan focused on four primary initiatives. First, they advocate for improved identity verification through the adoption of mobile driver's licenses and expanding access to government databases like the Social Security Administration's eCBSV system. Second, the report urges a shift toward phishing-resistant authentication methods, such as FIDO security keys and passkeys, to replace vulnerable legacy systems. Third, it emphasizes the necessity of international cooperation to establish unified standards for digital identity and wallet interoperability. Finally, the plan calls for robust public education campaigns to raise awareness about deepfake risks and modern security tools. By modernizing identity infrastructure and fostering collaboration between government and industry, policymakers can better protect the national economy from the escalating dangers posed by automated AI exploitation.


Beyond PUE: Rethinking how data center sustainability is measured

The article "Beyond PUE: Rethinking How Data Center Sustainability is Measured" emphasizes the growing necessity to evolve beyond the traditional Power Usage Effectiveness (PUE) metric in evaluating the environmental impact of data centers. While PUE has historically served as the industry standard for measuring energy efficiency by comparing total facility power to actual IT load, it fails to account for critical sustainability factors such as carbon emissions, water consumption, and the origin of the energy used. As the data center sector expands, particularly under the pressure of AI and high-density computing, a more holistic approach is required to reflect true operational sustainability. The article advocates for the adoption of multi-dimensional KPIs, including Water Usage Effectiveness (WUE), Carbon Usage Effectiveness (CUE), and Energy Reuse Factor (ERF), to provide a more comprehensive view of resource management. Furthermore, it highlights the importance of Lifecycle Assessment (LCA) to address "embodied carbon"—the emissions generated during the construction and hardware manufacturing phases—rather than just operational efficiency. By shifting the focus from simple power ratios to integrated metrics like 24/7 carbon-free energy matching and circular economy principles, the industry can better align its rapid growth with global climate targets and responsible resource stewardship.

Daily Tech Digest - March 09, 2026


Quote for the day:

"A positive attitude will not solve all your problems. But it will annoy enough people to make it worth the effort" -- Herm Albright


Is AI Killing Sustainability?

This article examines the paradoxical relationship between the rapid growth of artificial intelligence and environmental goals. On one hand, AI's massive computational needs are driving a surge in energy consumption, with global spending projected to reach $2.52 trillion this year. This expansion is fueling an exponential rise in data center power requirements, potentially consuming as much electricity as 22% of U.S. households by 2028. However, the author argues that AI also serves as a critical tool for boosting sustainability. By analyzing vast datasets, AI can optimize supply chains, automate waste management, and enhance energy efficiency in buildings by up to 30%. The piece provides six strategic tips for organizations to utilize AI for greenhouse gas reduction, including predictive environmental risk monitoring, accurate emission reporting, and improved renewable energy integration. Despite these benefits, a tension exists between corporate "green" ambitions and financial constraints, often leading to a "lite green" approach where cost-cutting takes priority over true environmental innovation. Ultimately, while AI's infrastructure poses a significant threat to climate targets, its potential to identify high-ROI decarbonization opportunities offers a path toward reconciling technological advancement with ecological preservation, provided that organizations move beyond superficial commitments toward mature, outcome-driven strategies.


PQC roadmap remains hazy as vendors race for early advantage

The transition to post-quantum cryptography (PQC) is evolving from a theoretical concern into an urgent operational risk, prompting major security vendors to race for early market advantages. As mainstream players like Palo Alto Networks, Cisco, and IBM join specialized firms, the focus has shifted toward structured readiness offerings centered on discovery, inventory, and migration planning. A significant hurdle for organizations remains the lack of visibility into cryptographic sprawl across infrastructure, making it difficult to identify vulnerabilities in legacy algorithms like RSA. The urgency is further fueled by the “harvest now, decrypt later” threat model, where adversaries collect encrypted data today for future decryption by capable quantum computers. While NIST has finalized several PQC standards, experts suggest that the expected moment of cryptographic compromise could arrive as early as 2029, making immediate preparation essential. Despite the marketing push, some observers question whether these PQC offerings represent a new category of security tools or simply a necessary enforcement of long-overdue security hygiene, such as comprehensive asset mapping and certificate tracking. Ultimately, the migration to quantum-safe environments requires a phased approach and a commitment to crypto-agility, ensuring that enterprises can adapt to evolving cryptographic standards before legacy systems become insurmountable liabilities in a post-quantum world.


Tech Debt “For Later” Crashed Production 5 Years Later

This Devrim Ozcay’s article critiques the pervasive hype surrounding AI in DevOps, specifically addressing the gap between marketing promises and production realities. The author argues that while "autonomous remediation" and "predictive incident detection" are often touted as revolutionary, they frequently fail in complex, high-stakes environments. These tools often rely on simple logic or pattern matching, and general-purpose models like ChatGPT can be dangerous during active incidents by providing confident but entirely incorrect root cause hypotheses. Instead of relying on AI for critical judgment, the article suggests leveraging it for "assembly" tasks that alleviate the mechanical burden on engineers. This includes filtering log noise, reconstructing incident timelines from disparate sources, and drafting initial postmortem reports. By automating these time-consuming, repetitive processes, teams can reduce the duration of post-incident documentation from hours to minutes. Ultimately, the article advocates for a balanced approach where AI handles the data organization while human engineers retain sole responsibility for interpretation and decision-making. This shift allows practitioners to focus on high-leverage problem-solving rather than tedious transcription, ensuring that incident response remains both efficient and reliable without succumbing to the unrealistic expectations often presented at tech conferences.


What Is Sampling in LLMs and How Does It Relate to Ethics?

This article explores the technical mechanisms behind how AI models choose their words and the subsequent moral responsibilities of developers. Sampling is the process by which an LLM selects the next token from a probability distribution. Techniques such as temperature, Top-K, and Top-P (nucleus sampling) are used to balance creativity with accuracy. Higher temperature settings introduce more randomness, which can foster innovation but also increases the likelihood of "hallucinations" or the generation of biased and harmful content. Conversely, lower settings make the model more deterministic and reliable for factual tasks but can lead to repetitive and uninspired responses. From an ethical standpoint, the choice of sampling strategy is never neutral. It requires a delicate balance between providing a diverse range of perspectives and ensuring the safety and truthfulness of the output. The author emphasizes that organizations must transparently define their sampling parameters to mitigate risks like misinformation. Ultimately, ethical AI development hinges on understanding these technical levers, as they directly influence how a model perceives and interacts with human values, necessitating a cautious approach to model tuning that prioritizes user safety and informational integrity.


AI Won't Fix Cybersecurity, But It Could Rebalance It

The article explores the nuanced role of artificial intelligence in cybersecurity, debunking the myth that it serves as a total panacea while highlighting its potential to rebalance the long-standing asymmetric advantage held by attackers. Traditionally, cybercriminals have enjoyed a lower barrier to entry and a higher success rate because defenders must be perfect across every surface, whereas attackers only need to succeed once. With the advent of generative AI, malicious actors are leveraging the technology to craft sophisticated phishing campaigns, automate vulnerability discovery, and democratize complex malware creation. Conversely, AI empowers defenders by automating routine monitoring, identifying anomalous patterns at machine speed, and bridging the significant talent gap within the industry. This technological shift creates a perpetual arms race where AI functions as a force multiplier for both sides. Rather than eliminating threats, AI recalibrates the battlefield, allowing security teams to process vast datasets and respond to incidents with unprecedented agility. However, the human element remains indispensable; strategic oversight and critical thinking are essential to guide AI tools. Ultimately, while AI will not "fix" the inherent vulnerabilities of digital infrastructure, it offers a vital mechanism to shift the strategic advantage back toward those safeguarding the digital frontier.


AI Is Not Here to Replace People, It’s Here to Replace Waiting

In this insightful interview, Aliaksei Tulia, the Chief Technical Officer at CoinsPaid, argues that the true purpose of artificial intelligence in the financial sector is not to displace human judgment but to eliminate the friction of waiting. Tulia emphasizes that AI acts as a powerful catalyst for efficiency and speed within the digital payment ecosystem by automating repetitive, high-volume tasks that traditionally create operational bottlenecks. By handling routine duties such as document summarization, log scanning, and boilerplate coding, AI allows for a significant compression of cycle times while maintaining necessary human oversight. The article highlights how CoinsPaid integrates these intelligent tools to enhance consistency and visibility, ensuring that the platform remains robust without sacrificing control. Furthermore, the discussion explores the essential division of labor where technology manages data-heavy routine processes, freeing professionals to focus on high-level strategic decisions, complex problem-solving, and improving the overall customer experience. This pragmatic approach represents a shift where AI handles the disciplined "first pass," allowing people to dedicate their expertise to tasks requiring creativity and accountability. Ultimately, Tulia envisions a future where AI-driven automation defines industry standards, proving that the technology’s primary value lies in its ability to streamline operations for a global audience.


Dynamic UI for dynamic AI: Inside the emerging A2UI model

The article "Dynamic UI for Dynamic AI: Inside the Emerging A2UI Model" explores the transformative shift from traditional graphical user interfaces to Agent-to-User Interfaces. As AI agents become increasingly autonomous, the standard chat-based "command line" is no longer sufficient for managing complex workflows. A2UI represents a fundamental paradigm shift where the interface is dynamically generated by the AI to match the specific context and requirements of a task. Unlike static SaaS platforms with fixed menus, A2UI allows agents to create ephemeral, highly functional components—such as interactive charts, data tables, or specialized dashboards—on demand. This movement is powered by advancements like Vercel’s AI SDK and features like Anthropic’s Artifacts, which allow for real-time rendering of code and UI. The goal is to bridge the gap between human intent and machine execution by providing a rich, interactive medium that transcends simple text responses. By embracing generative UI, developers are enabling a more fluid collaboration where the software adapts to the user, rather than the user being forced to navigate rigid software structures. This evolution signals the end of "one-size-fits-all" application design, ushering in a future where every interaction produces a bespoke, temporary interface tailored specifically to the immediate problem.


AI Use at Work Is Causing “Brain Fry,” Researchers Find, Especially Among High Performers

The Futurism article "AI Use at Work Is Causing 'Brain Fry'" highlights a concerning trend where artificial intelligence, despite its promises of productivity, is significantly damaging employee mental health. A study of 1,500 workers conducted by Boston Consulting Group and the University of California, Riverside, introduced the term "AI brain fry" to describe the cognitive exhaustion resulting from excessive interaction with AI tools. Approximately 14 percent of employees—predominantly high performers in fields like software development and finance—reported symptoms such as mental "static," brain fog, and headaches. This fatigue is largely driven by information overload, rapid task-switching, and the constant, draining necessity of overseeing multiple AI agents. Rather than lightening the load, these tools often force users to work harder to manage the technology than to solve actual problems. The consequences are severe for both individuals and organizations; the research found a 33 percent increase in decision fatigue and a higher likelihood of employees quitting their jobs. Ultimately, the piece argues that while AI is marketed as a way to supercharge efficiency, it often acts as a "burnout machine" that compromises cognitive capacity and leads to costly errors or paralysis in professional environments.


Submarine cables move to the center of critical infrastructure security debate

The article examines the escalating strategic significance of submarine cables, which facilitate the vast majority of international data traffic but are increasingly vulnerable to geopolitical tensions and physical threats. A new sector report highlights how high-profile incidents, such as the 2024 Baltic Sea cable severing, have transitioned these underwater assets from ignored infrastructure into critical security priorities. Beyond intentional sabotage or "grey-zone" activities, the industry faces significant resilience challenges, including an annual average of two hundred cable faults primarily caused by commercial fishing and anchoring. This vulnerability is exacerbated by a critical shortage of specialized repair vessels and experienced personnel, complicating rapid incident response. Furthermore, the shift in ownership dynamics, where cloud hyperscalers are now primary investors, creates commercial friction with traditional operators while reshaping infrastructure architecture. Technological advancements, particularly AI-driven distributed acoustic sensing, are transforming cables into active monitoring tools, yet technical solutions alone remain insufficient. The report concludes that long-term security depends on improved international coordination and unified governance frameworks between governments and private entities. Ultimately, protecting these vital conduits requires a holistic approach that integrates technical controls, organizational readiness, and cross-border cooperation to match the scale of modern digital dependency and evolving global risks.


How DevOps Broke Accessibility

In this article on DevOps Digest, the author explores the unintended consequences that the rapid adoption of DevOps practices has had on web accessibility. While DevOps has revolutionized software development by emphasizing speed, continuous integration, and frequent deployments, these very priorities have often sidelined the inclusive design and rigorous accessibility testing required for users with disabilities. The shift-left mentality, which aims to catch bugs early, frequently fails to incorporate accessibility checks into the automated pipeline, leading to a "move fast and break things" culture that disproportionately affects those relying on assistive technologies. Furthermore, the reliance on automated testing tools—which can only detect about 30% of accessibility issues—creates a false sense of security among development teams. This technical debt accumulates quickly in fast-paced environments, making retroactive fixes costly and complex. The article argues that for DevOps to truly succeed, accessibility must be integrated as a core pillar of the development lifecycle, rather than being treated as an afterthought. Ultimately, the piece calls for a cultural shift where developers and stakeholders prioritize human-centric design alongside technical efficiency to ensure the digital world remains open and equitable for every user regardless of their physical or cognitive abilities.