Showing posts with label trend. Show all posts

Daily Tech Digest - October 22, 2026

Quote for the Day
“Debugging is twice as hard as writing the code in the first place.”
— Brian Kernighan
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

14 ways attackers abuse cloud services to hack your enterprise

As enterprises migrate to hybrid and cloud environments, cyberattackers are evolving from "living off the land" to "living off the cloud," blending malicious activities into legitimate business traffic. Instead of relying on traditional malware that triggers alarms, adversaries are increasingly abusing trusted APIs, native administrative tools, and SaaS platforms to bypass conventional defenses. Attackers route command-and-control communications through reputable services like OpenAI, Microsoft Graph API, and Google Sheets, making the traffic look like routine developer or employee activity. They also exploit cloud identities, such as OAuth tokens and service accounts, to move laterally and access sensitive data without needing to compromise local servers directly. Further tactics include staging malware in object storage buckets, exfiltrating data via everyday tools like Slack, abusing ephemeral serverless functions to mask reconnaissance scans, and weaponizing identity tenant relationships. By exploiting the inherent trust and API-driven nature of modern cloud architecture, these cloud-native attack chains effectively turn the enterprise's operational backbone into a highly evasive attack surface.
Read Original Article →
Article Thumbnail

From Microservices to Agents: the Next Evolution of Distributed Systems

The shift toward artificial intelligence agents marks a significant evolution in software architecture, moving away from traditional microservices. While microservices focused on breaking down complex applications into smaller, predictable parts with clear ownership boundaries, agentic systems focus on distributing decision-making. Instead of following pre-programmed, step-by-step logic, these new AI agents determine their actions dynamically. They analyze the context and their goals in real-time to decide which tools to use and how to sequence their reasoning. This means execution paths are no longer entirely determined during the design phase but adapt as the system runs. While this makes systems more capable of handling complex or vague situations, it introduces new challenges in reliability. The quality of a system's decisions becomes just as critical as its speed or availability. When these systems fail, they often suffer from silent drops in reasoning quality rather than crashing entirely. To manage this effectively, systems need built-in boundaries for the agents, continuous evaluation loops, and reliable fallback mechanisms.
Read Original Article →
Article Thumbnail

How hybrid infrastructure is making quantum commercially actionable today

The quantum computing industry is currently in a critical "prepare for quantum" phase. While fault-tolerant quantum hardware is still developing, organizations cannot afford to wait passively. Integrating geographically isolated quantum processors with enterprise IT through secure, low-latency interconnection is an infrastructure challenge that must be addressed today. This preparation is essential for sectors like life sciences, where delays in drug discovery can be incredibly costly. A prime example is Qubit Pharmaceuticals, which utilizes a hybrid approach with its ATLAS platform. This four-layer system combines high-fidelity physics simulations, a synthetic quantum chemistry data engine, a specialized AI foundation model, and an emulator that simulates up to 40 qubits on classical hardware. By leveraging secure interconnection fabrics provided by partners like Equinix, companies can seamlessly link classical computing, HPC, AI, and early quantum capabilities. Building this hybrid infrastructure now allows organizations to experiment, gain operational familiarity, and seamlessly scale their capabilities as quantum hardware matures, ensuring they are ready to harness quantum utility when it arrives.

Read Original Article →

What Recent Cybersecurity Incidents Teach About the Duty to Mitigate Vendor and Service-Provider Risk

Recent cybersecurity incidents demonstrate that organizations face immense risks from third-party vendors and service providers, shifting the focus from internal defenses to external supply chains. Regulatory bodies increasingly expect companies to maintain a strict duty of vendor oversight, meaning organizations cannot simply outsource accountability for data protection. Real-world examples highlight this shift. The MOVEit software breach showed that companies can face severe legal and financial consequences from a vendor's vulnerability, regardless of their own internal controls. The Change Healthcare attack emphasized operational dependency risk, illustrating the disaster that occurs when a critical vendor goes offline. Furthermore, the PowerSchool lawsuit revealed that oversight must extend to subcontractors who have system access. To mitigate these threats, businesses must integrate vendor oversight into their core governance structure. This requires conducting thorough initial evaluations, negotiating clear contractual protections for incident response, and continuously monitoring vendor security practices. Treating vendor management as an ongoing legal and operational responsibility is essential for maintaining resilience when external failures cause major internal disruptions.

Read Original Article →
Article Thumbnail

The CIO’s new recovery problem: Knowing what ‘good’ looks like

Disaster recovery used to focus primarily on how quickly a business could restore its systems and resume normal operations. Today, modern technology environments are far more complex, spanning cloud platforms, software-as-a-service applications, and constantly changing identities. This complexity sprawl presents a new challenge for technology leaders: figuring out what a healthy system actually looks like before attempting to restore it. Simply bringing a system back online is no longer enough if you cannot guarantee it is secure and trustworthy. To build true resilience, organizations must maintain an accurate inventory and clear dependency mapping while the environment is still functioning properly. Testing a recovery plan must also evolve beyond verifying backups. It should evaluate whether the team can make critical decisions under pressure, understand shifting dependencies, and confirm that the restored environment is safe to use. While speed remains a priority during a crisis, restoring systems without confidence introduces severe risk. Technology leaders must establish a clear definition of a trusted state before an incident ever occurs.

Read Original Article →
Article Thumbnail

When Business Continuity Plans Depend on One Person Knowing What to Do

Even when business continuity plans are well-documented and regularly tested, they often contain a hidden vulnerability: relying too heavily on specific individuals. While organizations meticulously map out system and supply chain dependencies, they frequently overlook personnel dependencies. This reliance becomes clear during a crisis when teams instinctively turn to a single experienced manager, technical expert, or executive rather than following established procedures. The article suggests a straightforward way to expose this weakness during recovery exercises: deliberately remove key personnel from the scenario. If progress halts, deputies hesitate to make decisions, or critical workarounds suddenly become unavailable, the organization has identified a dangerous point of failure. These exercises often reveal that designated alternates lack the practical authority or historical knowledge to step in effectively when the primary decision-maker is absent. Recognizing these human dependencies allows organizations to correct them before a real emergency by formally documenting vital workarounds, transferring knowledge, and granting alternates the real authority they need to lead under pressure.
Read Original Article →
Article Thumbnail

Can AI stop good candidates from getting lost in the hiring pile?

Artificial intelligence is shifting from a basic background tool into an active partner for recruitment teams. As hiring volumes grow, qualified applicants are frequently overlooked simply because recruiters lack the time to review everyone. To solve this, companies are using artificial intelligence voice agents to handle the initial stages of screening. These agents can conduct first-round interviews at any time, answer standard questions about the role, and generate structured reports for the hiring team. This approach eliminates long waiting periods for applicants and ensures every application receives attention. However, technology cannot replace the core of recruitment. While artificial intelligence excels at repeatable tasks and gathering information, the final decision must remain human. Assessing an individual's motivations, understanding how they think, and building a genuine connection require human judgment. Furthermore, companies must be fully transparent when using these tools. Candidates need to know they are speaking with software, not a person. When applied responsibly, this technology prevents strong applicants from falling through the cracks while preserving the vital human element of hiring.

Read Original Article →

Gartner’s top tech trends for 2027 expand—and constrain—AI capabilities

Gartner recently outlined ten strategic technology trends for 2027, focusing on expanding artificial intelligence capabilities while establishing stricter controls. Over the next few years, businesses will move beyond text-based models toward systems designed for complex math, continuous voice reasoning, and physical world simulation for robotics. As these systems produce output faster than humans can review, the second phase emphasizes necessary limits. Organizations will need dedicated frameworks to manage machine identities, verify coding output, and provide specific business context to prevent rogue actions or compliance failures. Automated security patching will also become essential to close vulnerabilities quickly. Finally, looking further ahead, companies will aim to reduce reliance on specific cloud providers by adopting easily replaceable applications and independent technologies. A notable long-term shift involves biological computing, where lab-grown organic systems could eventually handle complex data tasks using far less energy than traditional silicon hardware. By planning across these three horizons, technology leaders can balance autonomous capabilities with the security required for steady operations.
Read Original Article →
Article Thumbnail

Coding Agents Moved the Bottleneck From Writing to Reviewing PRs

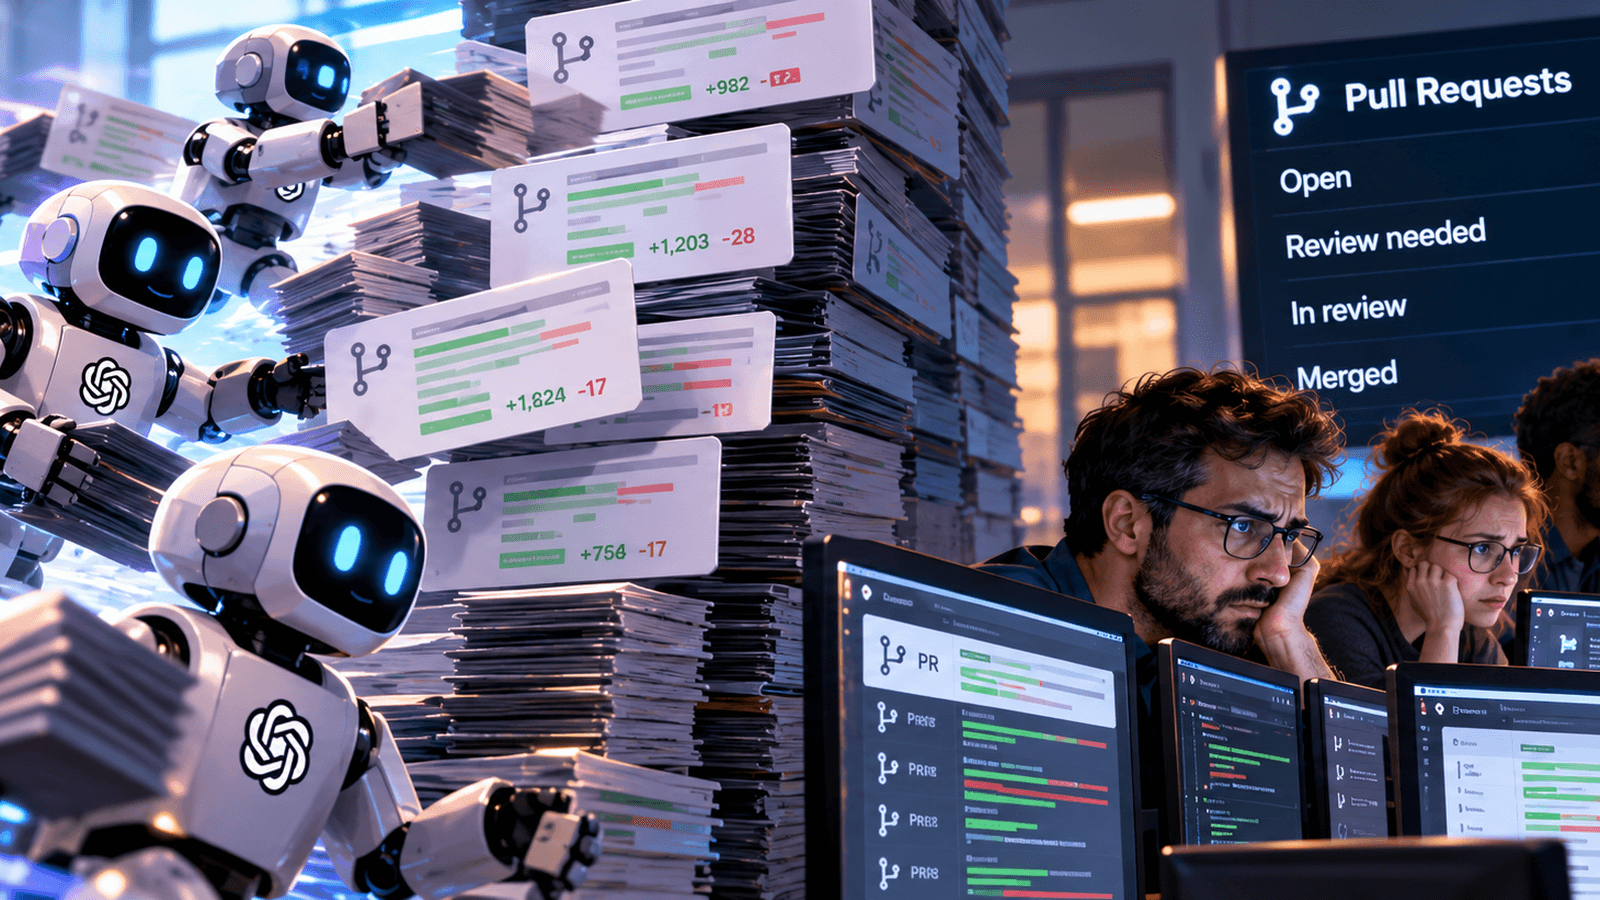
Artificial intelligence coding agents have significantly accelerated software development, but they have also shifted the primary bottleneck from writing code to reviewing it. Because these agents generate larger and more frequent pull requests, the volume of code needing review has outpaced the capacity of human engineers. This growing queue of unreviewed work often remains hidden because traditional productivity metrics focus on generation speed rather than review efficiency. Consequently, development teams face mounting quality debt. Overwhelmed reviewers might miss architectural flaws or security vulnerabilities, especially since AI-generated code typically looks clean and passes basic tests. To address this, organizations must recognize that hiring more reviewers is not a sustainable solution. Instead, they should implement dedicated AI review agents designed specifically to catch errors rather than generate new code. Additionally, capping the size of pull requests and tracking review metrics—such as wait times and review depth—can help maintain software quality without sacrificing the speed gained from AI development tools.
Read Original Article →
Article Thumbnail

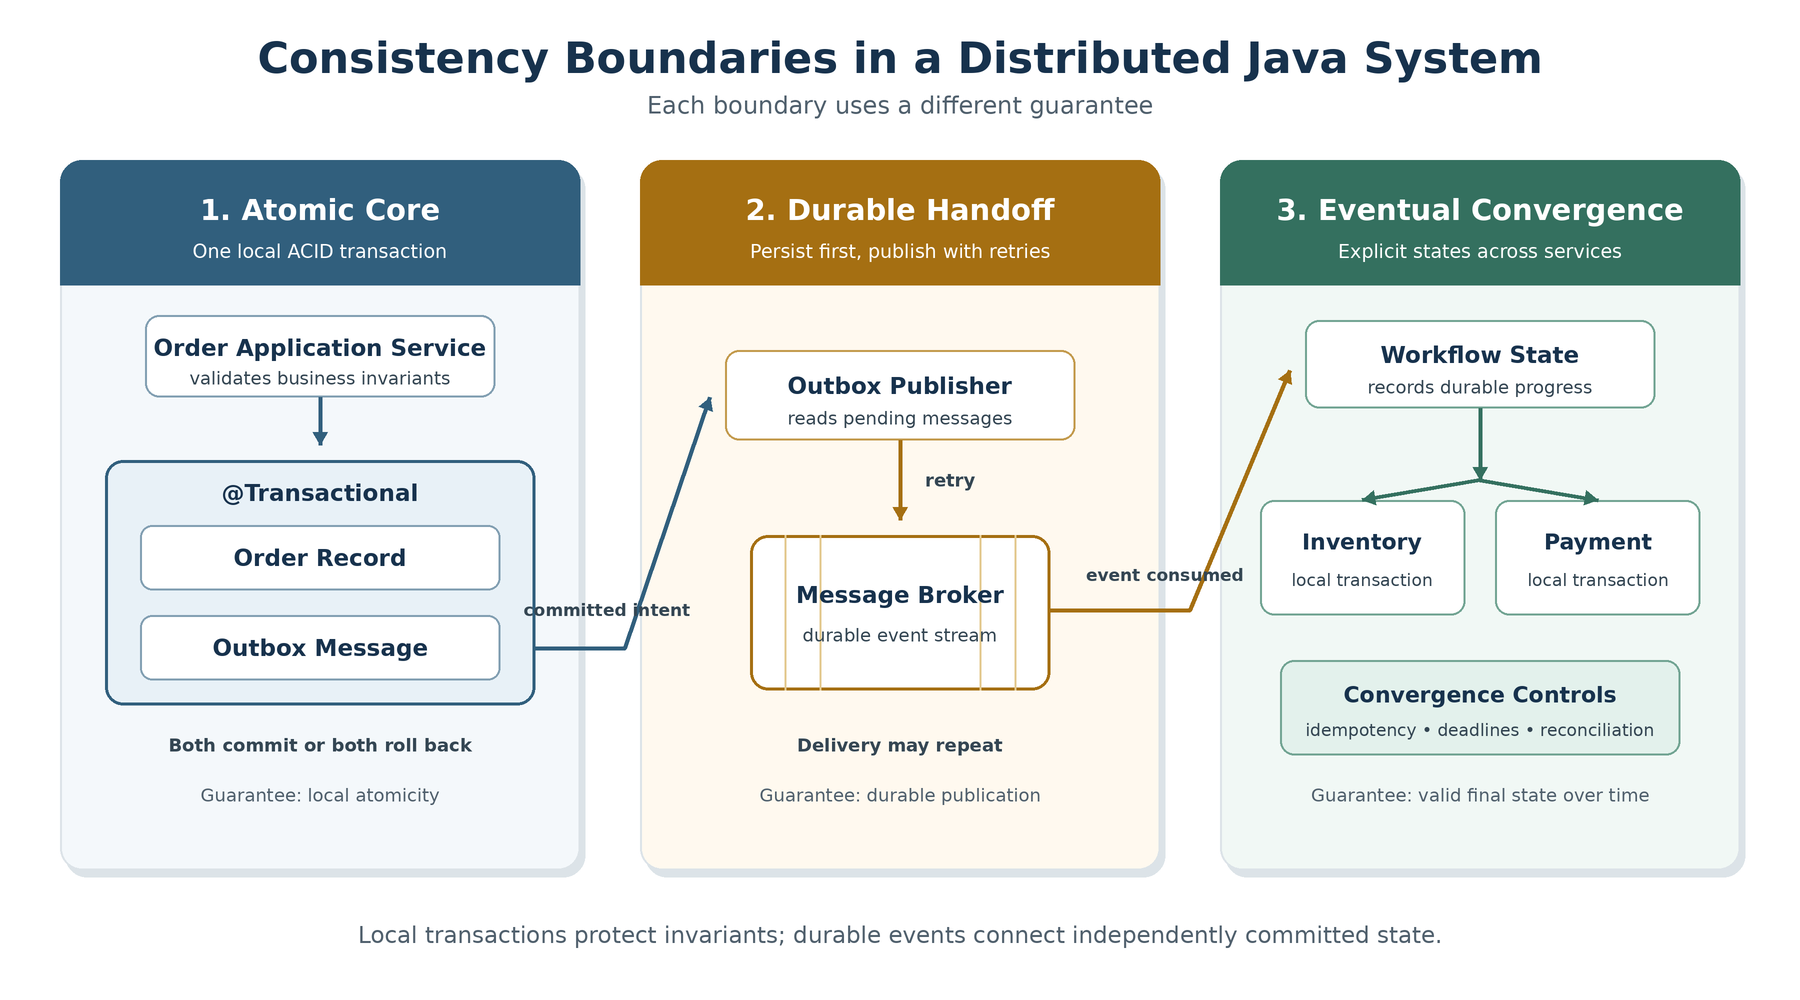
Where Should a Transaction End? Designing Consistency Boundaries in Distributed Java Systems

Designing distributed systems forces architects to decide exactly where a transaction begins and ends. Rather than splitting services first and worrying about data consistency later, the best approach starts with defining business invariants. These are the core rules that must always remain true together. The architecture should wrap its boundaries around these facts. When multiple pieces of data must change simultaneously to keep a rule intact, they belong in a single local transaction. Once that core state is secure, the system can use a durable handoff, like an outbox pattern, to safely communicate changes to other components. From there, eventual consistency can manage the broader workflow, but it must be an explicit process with clear recovery paths, not just a vague delay. Relying on synchronous call chains often creates hidden points of failure, so workflows should be modeled as durable states that can survive a crash. Ultimately, separating databases or breaking apart services is only valuable if it respects the underlying business rules that keep the entire system correct.

Read Original Article →

Daily Tech Digest - August 10, 2026


Quote for the day:

“Change is the end result of all true learning.” -- Leo Buscaglia

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


7 key trends defining the cybersecurity market today

The cybersecurity market is currently shaped by seven major trends that highlight a clear shift toward integration and advanced technologies. First, venture capital investment has reached record highs, heavily favoring startups that focus on artificial intelligence. As a direct result, entirely new product categories are rapidly emerging to address distinct vulnerabilities, such as securing large language models and governing artificial intelligence systems. Meanwhile, traditional market leaders are actively acquiring these specialized startups to fill gaps in their portfolios, leading to a significant surge in mergers and acquisitions. Rather than relying on scattered, standalone tools, organizations now strongly prefer integrated security platforms that consolidate functions and improve overall visibility. Additionally, the threat of quantum computing has moved from theory to reality. In response to "harvest now, decrypt later" strategies, both vendors and governments are pushing for immediate transitions to quantum-safe environments. There is also a growing reliance on outsourced managed security services, as companies seek external expertise for continuous monitoring and threat response. Finally, the need to protect sensitive information across complex, multi-cloud setups has driven the rapid rise of data security posture management tools. Together, these developments indicate a market focused on practical consolidation and preparation for complex future threats.


Secure SDLC principles explained for SaaS founders

A secure Software Development Lifecycle (SDLC) integrates security into every phase of building software, from early planning and design through to testing, release, and ongoing maintenance. For SaaS founders, the primary goal is to protect customer trust and avoid costly post-launch fixes without slowing down product delivery unnecessarily. The core principle is to build security in early rather than treating it as a bolted-on afterthought. Fixing structural flaws during the initial design phase is cheaper than addressing a data breach or emergency patch later. To make this operational, security practices must become repeatable habits, rather than relying on a single knowledgeable individual. Even small SaaS teams can establish a solid protective baseline by assigning clear ownership, requiring peer code reviews, automating basic vulnerability scans, and implementing a simple release checklist. This structured approach directly prevents common application risks such as injection flaws, broken access controls, exposed secrets, and issues hidden within third-party dependencies. By adopting DevSecOps practices, teams can easily automate routine security checks within the standard delivery pipeline. Ultimately, founders can measure their success by tracking how many high-risk issues are caught before release and how quickly problems are resolved, balancing product safety with ongoing business momentum.


Red Hat tames the open-source AI chaos.

Red Hat is actively working to bring order to the fast-moving and often chaotic open-source AI landscape. They focus on taking experimental AI projects and refining them into stable, secure tools suitable for business use. For instance, when a highly capable but risky open-source AI project called OpenClaw was released, it gave AI models the ability to act independently. Recognizing the security risks, Red Hat quickly introduced a method for companies to bring their own agents into their established IT systems. This approach ensures that AI tools operate with the necessary safety measures, such as proper isolation and clear rules for access. Drawing on years of experience in securing operating systems and building reliable platforms, Red Hat provides the structure needed to keep AI experiments safe. They restrict network access and place AI tools in contained environments to limit any potential damage from unexpected security breaches. Additionally, they help companies manage computing costs by automatically directing simple tasks to smaller, more affordable models. Red Hat views this secure management framework as a foundational operating system for AI. By prioritizing open standards and practical architecture, they offer a steady and reliable path for companies looking to adopt AI technologies without getting caught up in the surrounding industry hype.


Ask a Data Ethicist: What Use of AI Do We Need to Disclose?

In her article for Dataversity, data ethicist Katrina Ingram explores the ongoing debate around exactly how much we need to disclose when using artificial intelligence tools at work. Reflecting on early corporate policies from 2023 that demanded total transparency, she argues that a blanket requirement to always disclose everything lacks practical nuance. Ingram breaks down two opposing perspectives. The first is the strict approach, often seen in academia, which requires individuals to document every single instance of AI assistance, from basic brainstorming to editing sentences. While this level of detail supports academic integrity, Ingram points out that it is likely overkill for the corporate world. Tracking minor uses of AI for routine tasks provides little real value and risks turning harmless employee behavior into frustrating policy violations. On the other end of the spectrum is the "disclose nothing" argument, which treats AI as just another standard work tool like a word processor or a pen. However, she notes that this extreme is also problematic because AI actively generates content rather than just formatting it. Ultimately, Ingram suggests that organizations need sensible, balanced disclosure policies that distinguish between generating final public content and simply using AI to support everyday tasks.


The interconnect crisis: Why enterprise AI scaling is about to hit a wall

Enterprise AI needs differ sharply from consumer tools, prioritizing long-term reliability, data privacy, and secure on-premise infrastructure. As organizations build internal platforms and manage vast volumes of sensitive data, the cost benefits of owning hardware rather than renting cloud space are becoming clearer. While processing power is becoming cheaper and more accessible, a hidden problem threatens to slow down progress: moving data. As databases grow heavier over time, the real challenge is no longer raw processing power, but rather the speed at which data travels between storage, memory, and processors. This is the interconnect crisis. Traditional copper cables simply cannot handle the sheer volume and speed required to move information between components without severe delays. To solve this, the industry must move beyond older standards and adopt faster data transfer methods. Upgrades like advanced memory links and high-speed network protocols provide some initial relief, but the true long-term answer lies in light-based technology. Replacing standard electrical connections with photonics will allow systems to share information seamlessly. While this transition requires significant changes to hardware design, these optical solutions offer a clear path forward, ensuring that tomorrow’s computer architectures can smoothly support the increasing demands of complex software and massive data workloads.


The Corporate Network Is Fading - Here's What Replaces It

For decades, traditional enterprise networks relied on a straightforward premise: work happened exclusively inside an office building. In this older model, applications were stored in centralized, physical data centers. Employees connected through internal infrastructure, and security strategies were built entirely around defending a single, defined perimeter. Essentially, the goal was to build a wall around internal digital assets. However, how organizations operate today looks completely different from that original environment. The legacy corporate network is fading because it no longer aligns with modern reality. Today, critical applications have moved to cloud platforms rather than sitting in a basement server room. Employees are highly distributed, connecting to work from their homes, coffee shops, and airports just as often as they do from traditional desks. Additionally, businesses now collaborate heavily with external partners through shared digital systems that extend far beyond internal walls. Because work is no longer confined to a single location, the old security model simply cannot protect the modern workforce. Instead of relying on a physical network boundary, companies are replacing the traditional corporate network with flexible, decentralized approaches. Modern connectivity focuses on securing individual user identities and specific cloud applications, ensuring safe access regardless of where an employee happens to be working today.


The Decade Bet: What CIOs Are Really Locking In

The article discusses the strategic decisions technology leaders are making for the next ten years, focusing on a deliberate shift from rigid systems to adaptable foundations. Rather than tying their organizations to specific software vendors or hardware providers, Chief Information Officers are now committing to flexibility, data ownership, and secure baseline architecture. They recognize that the tools they use today will likely change, so they are investing in underlying structures that allow for easy transitions and integration of new capabilities. A major priority is ensuring information remains portable and easily accessible across different platforms, strictly protecting the company from being trapped by any single service provider. Additionally, these leaders are prioritizing fundamental security practices that will remain highly relevant regardless of future external threats. By establishing these strong, adaptable frameworks, they build environments that can calmly handle unexpected shifts in the broader market or sudden technological advancements without requiring a system overhaul. Ultimately, the true long term commitment is not to a particular application or service, but to a resilient operational model that supports steady growth and rapid adaptation. This approach safely reduces long term risks while preserving the absolute freedom to choose the best available tools as specific business needs evolve over the coming decade.


What Is the Difference Between a CDO and CIO? A View From Both Sides

The roles of Chief Data Officer (CDO) and Chief Information Officer (CIO) represent distinct but complementary areas of executive leadership. The CDO is primarily responsible for turning data into tangible business value through better decision-making, while the CIO manages the broader technology ecosystem, ensuring the reliability, security, and scale of systems that keep the business running. While a CDO focuses on driving innovation and competitive advantage, a CIO handles operational accountability, dealing with uptime, infrastructure dependencies, and risk management. Despite these practical differences, the rapid rise of artificial intelligence requires the two leaders to work together closer than ever before. Artificial intelligence initiatives need secure platforms and governance, owned by the CIO, alongside trusted data and clear business objectives, driven by the CDO. Although more CDOs are gradually transitioning into CIO roles as their exposure to engineering and platforms grows, the positions will likely remain separate in large organizations. Success ultimately depends on a shared partnership where both executives prioritize common outcomes rather than protecting their domains. Together, they balance the need for strategy and innovation with the strict discipline of operational excellence, proving that all modern organizations need both reliable technical foundations and smart data to truly thrive today.


7 Key Components for Event Cloud Threat Detection and Response Solution

As business operations increasingly span across multiple clouds, applications, and devices, securing these distributed networks has become a significant challenge. Traditional security tools designed for distinct borders often fail in these environments, leaving blind spots and causing delays in identifying risks. To effectively protect modern infrastructure, organizations need a comprehensive cloud threat detection and response solution built on seven essential components. First, teams must have clear, unified visibility across all systems, applications, and user activities. Second, this broad visibility must be paired with intelligent analytics to accurately distinguish genuine threats from routine daily activities. Third, the system needs real-time detection that connects signals across different areas to reveal actual attack paths. Fourth, security controls should focus on prevention, stopping harmful actions before they cause serious damage. Fifth, automated responses are crucial for quickly containing issues without waiting for manual approval. Sixth, a centralized control system ensures that security rules are applied consistently everywhere, reducing the chance of harmful errors. Finally, the underlying architecture must be flexible and scalable to support future growth and infrastructure changes. Together, these seven elements create a continuous loop where visibility informs intelligence, intelligence sharpens detection, and detection drives immediate, protective action across the entire organization.


Enterprise Data Warehouse Architecture Explained Simply

An enterprise data warehouse architecture provides a structured framework for businesses to collect, organize, and analyze data scattered across multiple systems. By consolidating information into a single environment, it helps organizations maintain consistent and reliable data, which improves reporting accuracy and supports better decision making across departments. A sound architecture relies on several core components working effectively together. It begins with a data source layer that pulls information from various applications, followed by an integration layer that organizes and loads the data. The information is then housed in a scalable storage layer, often using cloud platforms. Additional layers handle data processing, translate technical structures into practical business terms, and enforce strict security and governance policies. When building a data warehouse, organizations can choose from different structural patterns, such as a central hub and spoke model or a hybrid lakehouse approach, depending on their specific operational needs. Designing an effective system requires a clear understanding of practical business goals, a focus on long term scalability, and careful data modeling. Prioritizing high data quality and strong security practices ensures the system remains a trustworthy foundation. Ultimately, a properly planned data warehouse architecture allows a business to manage growing data volumes safely and efficiently while keeping internal teams aligned.

Daily Tech Digest - June 18, 2026


Quote for the day:

“The most important thing in communication is hearing what isn’t said.” -- Peter F. Drucker

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Why Account Takeovers Are Rising and How to Stop Them

Account takeovers are increasing because organizations now manage thousands of identities across complex hybrid, cloud, and remote work environments. Instead of attacking infrastructure, cybercriminals are targeting the authentication process itself, finding it much faster and quieter. While multifactor authentication remains important, attackers have adapted by using prompt bombing to exhaust users into approving access, or by stealing session tokens to bypass logins entirely. Additionally, phishing campaigns have become harder to spot, often using legitimate hosting services to trick even cautious employees into giving up their credentials. Another major vulnerability stems from employees using unmanaged personal devices to access corporate networks. Malware on these devices can easily harvest passwords and session cookies. Because traditional security tools often treat a successful login as complete proof of trust, these compromised devices easily slip through the cracks. To stop modern account takeovers, organizations must move beyond simply checking usernames and passwords at the door. They need continuous verification systems that assess device health and monitor session risks throughout the entire access lifecycle. By verifying that a device is genuinely safe and updated before and during a session, companies can effectively block unauthorized access.


Securing digital keys when your phone unlocks the car

Alysia Johnson, President of the Car Connectivity Consortium (CCC), outlines the evolution of the CCC Digital Key from a brand-specific convenience to a standardized, multi-vendor credential. This transition shifts the security model from implicit trust within a single company's hardware to a system demanding verifiable trust across a diverse ecosystem. To address this, the CCC relies on standardized certification, secure elements, and interoperable protocols. Version 4 of the standard focuses on improving interoperability, validation, and consistent behavior across various devices and vehicles, rather than addressing a new specific threat, building upon the high security baseline established in Version 3. NFC, often a fallback when batteries die, is not a weak link. It requires close proximity and explicit user action, maintaining the same security principles as the broader architecture. The system supports swift credential revocation if a device is lost or compromised, synchronizing across the ecosystem and utilizing cryptographic challenge-response mechanisms to prevent replay attacks. Recognizing the long lifespan of vehicles, the CCC designed the standard with crypto-agility, allowing algorithms to evolve as needed. Post-quantum migration is also an active topic within the consortium to ensure long-term security.


5 things CIOs must do as sovereignty becomes a design constraint

As global tensions rise and regulations increase, businesses can no longer assume that location does not matter. Geography has become a strict requirement, forcing technology leaders to rethink where they place their data and systems. First, companies must treat physical location as a fundamental technical decision, moving away from relying entirely on a single global provider. Instead, they should adopt a more practical approach. Second, businesses need to design their systems for deep resilience rather than pure efficiency, reducing the risk of relying too heavily on any single vendor by actively diversifying their technology setup. Third, it is essential to sort applications and data based on their specific risk levels. While most data can safely remain in public platforms, highly sensitive information requires secure, localized storage. Fourth, companies must build their systems with the ongoing flexibility to move applications easily if global or regulatory conditions change, avoiding rigid vendor contracts. Finally, the concept of secure access must extend beyond the data center to remote workers, focusing on identity verification rather than just basic device security. Ultimately, managing technology is now about balancing long-term risks instead of simply hunting for the absolute lowest costs.


Security Community Slams US Ban on Exporting Mythos, Fable

The cybersecurity community is strongly criticizing the United States government’s decision to ban the export of Anthropic’s new artificial intelligence models, Claude Fable 5 and Mythos 5, to foreign nationals. The government enacted this ban over national security concerns, citing the models' potential ability to find and exploit software vulnerabilities. This action was allegedly prompted by a reported method to bypass the software's safety limits. In response, dozens of prominent security experts have signed an open letter urging the government to reverse the restriction. They argue that blocking access to these advanced tools actively harms the nation's digital defenses by preventing security teams from finding and fixing vulnerabilities before attackers do. Furthermore, industry leaders point out that the ban will do very little to actually stop foreign adversaries or cybercriminals. Adversary nations like China and various financially motivated attackers already possess equivalent technological capabilities, either through available public alternatives or their own undisclosed research. Ultimately, experts believe that restricting these tools based on fear or an incomplete understanding of the technology leaves network defenders at a significant disadvantage, while completely failing to meaningfully impede the malicious actors the ban intends to target.


20 principles of good management that most managers don't practice

Many managers fail not from a lack of knowledge, but from an inability to consistently apply foundational management principles under pressure. Organizations frequently promote individuals based on their technical skills rather than their leadership capabilities, leading to entirely predictable workplace dysfunction. Genuinely effective management relies on disciplined habits rather than innate talent. The core principles involve straightforward but consistently neglected daily practices. First, effective leaders provide prompt, relevant feedback rather than waiting for formal annual reviews, ensuring guidance feels like support rather than judgment. Second, they ask questions instead of merely issuing answers, training their teams to think critically and solve complex problems independently. Third, they distribute decision-making authority to those closest to the actual work, taking the time to explain their reasoning to cultivate better future judgment among the staff. Fourth, they set explicit expectations to eliminate confusion and establish shared accountability, allowing employees to operate with clear direction. Finally, they actively protect their team's time and attention by minimizing unnecessary meetings and establishing communication norms that allow for deep, focused work. Ultimately, management succeeds through steady commitment to these basic practices, fostering genuine trust and autonomy.


Observability Is the New Control Plane for Enterprise Transformation

As businesses adopt increasingly complex technologies like cloud environments and artificial intelligence, they face a critical challenge: understanding how these interconnected systems actually perform. Many leaders lack the clear data needed to make informed decisions about their technology investments, leading to a significant gap between what they build and what they can effectively manage. Traditional tracking methods were built for simpler setups and simply cannot handle today's scattered and unpredictable systems. Operating without clear visibility carries steep costs. When technology fails, companies lose money for every hour an outage lasts. Engineering teams waste valuable time trying to piece together information from disconnected tools instead of fixing the root problem. Beyond immediate downtime, this lack of shared information creates a hidden tax on the entire organization, slowing down operations and complicating incident reviews. However, companies that adopt a unified approach to monitoring their technology see reliable benefits. By bringing all their system data into a single cohesive view, organizations can steadily reduce the financial impact of outages and achieve clear returns on their investment, proving that true success lies in fully understanding their technology rather than just deploying more of it.


Before enabling embedded AI, Indian enterprises need vendor model disclosure

The article discusses the crucial need for transparency as Indian enterprises increasingly adopt software tools with embedded artificial intelligence. While these built-in AI features promise enhanced productivity, they also introduce significant challenges regarding data privacy, security, and ethical governance. To manage these risks effectively, companies must demand comprehensive disclosure from their technology vendors. This transparency should clearly outline how the underlying models are trained, what kinds of data they process, and how user privacy is maintained. Without this information, enterprises face the danger of intellectual property leaks, compliance violations, and unintended algorithmic biases. The piece highlights that true accountability cannot be achieved in a vacuum; instead, it requires collaborative standards between software developers and corporate users. By establishing clear model disclosures, Indian businesses can safely deploy automated systems while maintaining a strong ethical foundation and protecting proprietary information. Ultimately, the author advises decision-makers to move beyond the initial excitement of automation and instead focus on establishing rigorous verification protocols before fully integrating these tools into their core workflows.


AI's Catastrophic Risk Isn't Rogue Machines, It's Cognitive Surrender

The real danger of artificial intelligence may not be the science-fiction nightmare of rogue machines turning against us, but rather a subtle, internal shift toward "cognitive surrender." As AI tools increasingly handle our analysis, coding, and writing, they dismantle the traditional incentives for learning and mastery. When individuals can generate competent work in seconds, the long-term process of building skills—once a foundation for personal identity and professional pride—starts to feel unnecessary or even futile. This trend is worsened by a broader sense of economic insecurity among younger generations, who are already losing faith in the traditional "work hard to succeed" narrative. Because the future feels increasingly unstable and inaccessible, many are tempted to bypass the friction of deep thought, choosing instead to outsource their deliberation to AI. This constant reliance on artificial intelligence threatens to weaken our capacity for sustained, independent reasoning. Ultimately, the challenge is not just that we might be replaced by machines, but that we may voluntarily abandon the effort and struggle required to develop our own expertise. Even if AI can perform tasks, it cannot replicate the uniquely human satisfaction found in the process of creating something through genuine personal effort.


AI is eroding trust. Accounting and finance professionals can rebuild it

Accounting and finance professionals are currently facing a significant decline in industry confidence. While economic and global pressures play a part, the rapid adoption of artificial intelligence has emerged as a primary concern. Many professionals worry that new software is being implemented too quickly without the necessary plans or controls. There are also valid concerns about the quality of the technology's output, as minor automation errors can easily multiply, leading to major reporting mistakes and basic compliance issues. Ultimately, this creates a widespread loss of trust in financial data and related decisions. To rebuild this trust, finance professionals must step in to bridge the gap between software systems and human oversight. Rather than simply learning the technical details of the software, accountants need to focus on practical uses like forecasting and managing risk. It is essential for professionals to act as leaders in compliance, learning how to identify biases, correct mistakes, and oversee these new systems effectively. By combining the speed of the technology with dependable human analysis, teams can deliver accurate recommendations. Developing these skills through targeted training programs will ensure professionals remain effective and can responsibly guide their teams forward.


The Technology Trend Hiding in Plain Sight: Why Businesses Are Rediscovering the Power of Constraints

For decades, technological progress has been defined by abundance, offering companies an ever-expanding array of choices, data, and computing power. However, this limitless possibility has created new challenges. Many businesses now find themselves overwhelmed by options, making decision-making difficult and diluting their focus. In response, organizations are quietly rediscovering the strategic value of constraints. Rather than viewing limitations as obstacles, leaders are realizing that boundaries actually drive better outcomes. Constraints force companies to prioritize what truly matters, clarify their objectives, and distinguish between what is merely possible and what is genuinely essential. In a highly complex environment, the simple ability to focus is becoming a significant competitive advantage. Limits help organizations simplify their daily operations, manage data more effectively, and introduce new systems at a pace that employees can comfortably absorb. Trust itself relies on clear boundaries and solid governance. As companies mature in their technology use, they are shifting away from adopting every new advancement and instead optimizing the systems that deliver the most value. Ultimately, success no longer relies on having access to endless resources, but on having the discipline to know exactly what to leave out.

Daily Tech Digest - February 03, 2026


Quote for the day:

"In my whole life, I have known no wise people who didn't read all the time, none, zero." -- Charlie Munger


How risk culture turns cyber teams predictive

Reactive teams don’t choose chaos. Chaos chooses them, one small compromise at a time. A rushed change goes in late Friday. A privileged account sticks around “temporarily” for months. A patch slips because the product has a deadline, and security feels like the polite guest at the table. A supplier gets fast-tracked, and nobody circles back. Each event seems manageable. Together, they create a pattern. The pattern is what burns you. Most teams drown in noise because they treat every alert as equal and security’s job. You never develop direction. You develop reflexes. ... We’ve seen teams with expensive tooling and miserable outcomes because engineers learned one lesson. “If I raise a risk, I’ll get punished, slowed down or ignored.” So they keep quiet, and you get surprised. We’ve also seen teams with average tooling but strong habits. They didn’t pretend risk was comfortable. They made it speakable. Speakable risk is the start of foresight. Foresight enables the right action or inaction to achieve the best result! ... Top teams collect near misses like pilots collect flight data. Not for blame. For pattern. A near miss is the attacker who almost got in. The bad change that almost made it into production. The vendor who nearly exposed a secret. The credential that nearly shipped in code. Most organizations throw these away. “No harm done.” Ticket closed. Then harm arrives later, wearing the same outfit.


Why CIOs are turning to digital twins to future-proof the supply chain

The ways in which digital twin models differ from traditional models are that they can be run as what-if scenarios and simulated by creating models based on cause-and-effect. Examples of this would include a demand increase in volume of supply chain product in a short time frame, or changes involving a facility shutting down because of severe weather conditions. The model will look at how this will affect a supply chain’s inventory levels, shipping schedule and delivery date, and even worker availability if any. All of this allows companies to move their decision-making process away from reactive firefighting to the more proactive planning process. For a CIO, using a digital twin model eliminates the historical siloing of enterprise architecture of supply chain-related data. ... Although the value of the digital twin technology is evident, scaling digital twins remains a significant challenge. Integration of data from multiple sources including ERP, WMS, IoT, and partner systems is a primary challenge for all. High fidelity simulation requires high computational capacity, which in turn requires trade-offs between realism, performance, and cost. There are also governance issues associated with digital twins. As digital twin models drift or are modified due to the physical state of the model changing, potential security vulnerabilities also increase as continuing data is streamed from cloud and edge environments.


Quantum computing is getting closer, but quantum-proof encryption remains elusive

“Everybody’s well into the belief that we’re within five years of this cryptocalypse,” says Blair Canavan, director of alliances for the PKI and PQC portfolio at Thales, a French multinational company that develops technologies for aerospace, defense, and digital security. “I see it and hear it in almost every circle.” Fortunately, we already have new, quantum-safe encryption technology. NIST released its fifth quantum-safe encryption algorithm in early 2025. The recommended strategy is to build encryption systems that make it easy to swap out algorithms if they become obsolete and new algorithms are invented. And there’s also regulatory pressure to act. ... CISA is due to release its PQC category list, which will establish PQC standards for data management, networking, and endpoint security. And early this year, the Trump administration is expected to release a six-pillar cybersecurity strategy document that includes post-quantum cryptography. But, according to the Post Quantum Cryptography Coalition’s state of quantum migration report, when it comes to public standards, there’s only one area in which we have broad adoption of post-quantum encryption, and that’s with TLS 1.3, and only with hybrid encryption — not pre or post quantum encryption or signatures. ... The single biggest driver for PQC adoption is contractual agreements with customers and partners, cited by 22% of respondents. 


From compliance to competitive edge: How tech leaders can turn data sovereignty into a business advantage

Data sovereignty - where data is subject to the laws and governing structures of the nation in which it is collected, processed, or held - means that now more than ever, it’s incredibly important that you understand where your organization’s data comes from, and how and where it’s being stored. Understandably, that effort is often seen through the lens of regulation and penalties. If you don’t comply with GDPR, for example, you risk fines, reputational damage, and operational disruption. But the real conversation should be about the opportunities it could bring, and that involves looking beyond ticking boxes, towards infrastructure and strategy. ... Complementing the hybrid hub-and-spoke model, distributed file systems synchronize data across multiple locations, either globally or only within the boundaries of jurisdictions. Instead of maintaining separate, siloed copies, these systems provide a consistent view of data wherever it is needed and help teams collaborate while keeping sensitive information within compliant zones. This reduces delays and duplication, so organizations can meet data sovereignty obligations without sacrificing agility or teamwork. Architecture and technology like this, built for agility and collaboration, are perfectly placed to transform data sovereignty from a barrier into a strategic enabler. They support organizations in staying compliant while preserving the speed and flexibility needed to adapt, compete, and grow. 


Why digital transformation fails without an upskilled workforce

“Capability” isn’t simply knowing which buttons to click. It’s being able to troubleshoot when data doesn’t reconcile. It’s understanding how actions in the system cascade through downstream processes. It’s recognizing when something that’s technically possible in the system violates a business control. It’s making judgment calls when the system presents options that the training scenarios never covered. These capabilities can’t be developed through a three-day training session two weeks before go-live. They’re built through repeated practice, pattern recognition, feedback loops and reinforcement over time. ... When upskilling is delayed or treated superficially, specific operational risks emerge quickly. In fact, in the implementations I’ve supported, I’ve found that organizations routinely experience productivity declines of as much as 30-40% within the first 90 days of go-live if workforce capability hasn’t been adequately addressed. ... Start by asking your transformation team this question: “Show me the behavioral performance standards that define readiness for the roles, and show me the evidence that we’re meeting them.” If the answer is training completion dashboards, course evaluation scores or “we have a really good training vendor,” you have a problem. Next, spend time with actual end users not power users, not super users, but the people who will do this work day in and day out. 


How Infrastructure Is Reshaping the U.S.–China AI Race

Most of the early chapters of the global AI race were written in model releases. As LLMs became more widely adopted, labs in the U.S. moved fast. They had support from big cloud companies and investors. They trained larger models and chased better results. For a while, progress meant one thing. Build bigger models, and get stronger output. That approach helped the U.S. move ahead at the frontier. However, China had other plans. Their progress may not have been as visible or flashy, but they quietly expanded AI research across universities and domestic companies. They steadily introduced machine learning into various industries and public sector systems. ... At the same time, something happened in China that sent shockwaves through the world, including tech companies in the West. DeepSeek burst out of nowhere to show how AI model performance may not be as contrained by hardware as many of us thought. This completely reshaped assumptions about what it takes to compete in the AI race. So, instead of being dependent on scale, Chinese teams increasingly focused on efficiency and practical deployment. Did powerful AI really need powerful hardware? Well, some experts thought DeepSeek developers were not being completely transparent on the methods used to develop it. However, there is no doubt that the emergence of DeepSeek created immense hype. ... There was no single turning point for the emergence of the infrastructure problem. Many things happened over time. 


Why AI adoption keeps outrunning governance — and what to do about it

The first problem is structural. Governance was designed for centralized, slow-moving decisions. AI adoption is neither. Ericka Watson, CEO of consultancy Data Strategy Advisors and former chief privacy officer at Regeneron Pharmaceuticals, sees the same pattern across industries. “Companies still design governance as if decisions moved slowly and centrally,” she said. “But that’s not how AI is being adopted. Businesses are making decisions daily — using vendors, copilots, embedded AI features — while governance assumes someone will stop, fill out a form, and wait for approval.” That mismatch guarantees bypass. Even teams with good intentions route around governance because it doesn’t appear where work actually happens. ... “Classic governance was built for systems of record and known analytics pipelines,” he said. “That world is gone. Now you have systems creating systems — new data, new outputs, and much is done on the fly.” In that environment, point-in-time audits create false confidence. Output-focused controls miss where the real risk lives. ... Technology controls alone do not close the responsible-AI gap. Behavior matters more. Asha Palmer, SVP of Compliance Solutions at Skillsoft and a former US federal prosecutor, is often called in after AI incidents. She says the first uncomfortable truth leaders confront is that the outcome was predictable. “We knew this could happen,” she said. “The real question is: why didn’t we equip people to deal with it before it did?” 


How AI Will ‘Surpass The Boldest Expectations’ Over The Next Decade And Why Partners Need To ‘Start Early’

The key to success in the AI era is delivering fast ROI and measurable productivity gains for clients. But integrating AI into enterprise workflows isn’t simple; it requires deep understanding of how work gets done and seamless connection to existing systems of record. That’s where IBM and our partners excel: embedding intelligence into processes like procurement, HR, and operations, with the right guardrails for trust and compliance. We’re already seeing signs of progress. A telecom client using AI in customer service achieved a 25-point Net Promoter Score (NPS) increase. In software development, AI tools are boosting developer productivity by 45 percent. And across finance and HR, AI is making processes more efficient, error-free, and fraud-resistant. ... Patience is key. We’re still in the early innings of enterprise AI adoption — the players are on the field, but the game is just beginning. If you’re not playing now, you’ll miss it entirely. The real risk isn’t underestimating AI; it’s failing to deploy it effectively. That means starting with low-risk, scalable use cases that deliver measurable results. We’re already seeing AI investments translate into real enterprise value, and that will accelerate in 2026. Over the next decade, AI will surpass today’s boldest expectations, driving a tenfold productivity revolution and long-term transformation. But the advantage will go to those who start early.


Five AI agent predictions for 2026: The year enterprises stop waiting and start winning

By mid-2026, the question won't be whether enterprises should embed AI agents in business processes—it will be what they're waiting for if they haven't already. DIY pilot projects will increasingly be viewed as a risker alternative to embedded pre-built capabilities that support day-to-day work. We're seeing the first wave of natively embedded agents in leading business applications across finance, HR, supply chain, and customer experience functions. ... Today's enterprise AI landscape is dominated by horizontal AI approaches: broad use cases that can be applied to common business processes and best practices. The next layer of intelligence - vertical AI - will help to solve complex industry-specific problems, delivering additional P&L impact. This shift fundamentally changes how enterprises deploy AI. Vertical AI requires deep integration with workflows, business data, and domain knowledge—but the transformative power is undeniable. ... Advanced enterprises in 2026 will orchestrate agent teams that automatically apply business rules, maintain a tight control on compliance, integrate seamlessly across their technology stack, and scale human expertise rather than replace it. This orchestration preserves institutional knowledge while dramatically multiplying its impact. Organizations that master multi-agent workflows will operate with fundamentally different economics than those managing point automation solutions. 


How should AI agents consume external data?

Agents benefit from real-time information ranging from publicly accessible web data to integrated partner data. Useful external data might include product and inventory data, shipping status, customer behavior and history, job postings, scientific publications, news and opinions, competitive analysis, industry signals, or compliance updates, say the experts. With high-quality external data in hand, agents become far more actionable, more capable of complex decision-making and of engaging in complex, multi-party flows. ... According to Lenchner, the advantages of scraping are breadth, freshness, and independence. “You can reach the long tail of the public web, update continuously, and avoid single‑vendor dependencies,” he says. Today’s scraping tools grant agents impressive control, too. “Agents connected to the live web can navigate dynamic sites, render JavaScript, scroll, click, paginate, and complete multi-step tasks with human‑like behavior,” adds Lenchner. Scraping enables fast access to public data without negotiating partnership agreements or waiting for API approvals. It avoids the high per-call pricing models that often come with API integration, and sometimes it’s the only option, when formal integration points don’t exist. ... “Relying on official integrations can be positive because it offers high-quality, reliable data that is clean, structured, and predictable data through a stable API contract,” says Informatica’s Pathak. “There is also legal protection, as they operate under clear terms of service, providing legal clarity and mitigating risk.”

Daily Tech Digest - January 27, 2026


Quote for the day:

"Supreme leaders determine where generations are going and develop outstanding leaders they pass the baton to." -- Anyaele Sam Chiyson


Why code quality should be a C-suite concern

At first, speed feels like progress. Then the hidden costs begin to surface: escalating maintenance effort, rising incident frequency, delayed roadmaps and growing organizational tension. The expense of poor code slowly eats into return on investment — not always in ways that show up neatly on a spreadsheet, but always in ways that become painfully visible in daily operations. ... During the planning phase, rushed architectural decisions often lead to tightly coupled, monolithic systems that are expensive and risky to change. During development, shortcuts accumulate into what we call technical debt: duplicated logic, brittle integrations and outdated dependencies that appear harmless at first but quietly erode system stability over time. Like financial debt, technical debt compounds. ... Architecture always comes first. I advocate for modular growth — whether through a well- structured modular monolith that can later evolve into microservices, or through service-oriented architectures with clear domain boundaries. Platforms such as Kubernetes enable independent scaling of components, but only when the underlying architecture is cleanly segmented. Language and framework choices matter more than most leaders realize. ... The technologies we select, the boundaries we define and the failure modes we anticipate all place invisible limits on how far an organization can grow. From what I’ve seen, you simply cannot scale a product on a foundation that was never designed to evolve.


How to regulate social media for teens (and make it stick)

Noting that age assurance proposals have broad support from parents and educators, Allen says “the question is not whether children deserve safeguarding (they do) but whether prohibition is an effective tool for achieving it.” “History suggests that bans succeed or fail not on the basis of intention, but on whether they align with demand, supply, moral legitimacy and enforcement capacity. Prohibition does not remove human desire; it reallocates who fulfils it. Whether that reallocation reduces harm or increases it depends on how well policy engages with the underlying economics and psychology of behaviour.” ... “There is little evidence that young people themselves view social media as morally repugnant. On the contrary, it is where friendships are maintained, identities are explored and social status is negotiated. That does not mean it is harmless. It means it is meaningful.” “This creates a problem for prohibition. Where demand remains strong, supply will be found.” Here, Allen’s argument falters somewhat, in that it follows the logic that says bans push kids onto less regulated and more dangerous platforms. I.e., “the risk is not simply that prohibition fails. It is that it succeeds in changing who supplies children’s social connectivity.” The difference is that, while a basket of plums and some ingenuity are all you need to produce alcohol, social media platforms have their value in the collective. Like Star Trek’s Borg, they are more powerful the more people they assimilate. 


The era of agentic AI demands a data constitution, not better prompts

If a data pipeline drifts today, an agent doesn't just report the wrong number. It takes the wrong action. It provisions the wrong server type. It recommends a horror movie to a user watching cartoons. It hallucinates a customer service answer based on corrupted vector embeddings. ... In traditional SQL databases, a null value is just a null value. In a vector database, a null value or a schema mismatch can warp the semantic meaning of the entire embedding. Consider a scenario where metadata drifts. Suppose your pipeline ingests video metadata, but a race condition causes the "genre" tag to slip. Your metadata might tag a video as "live sports," but the embedding was generated from a "news clip." When an agent queries the database for "touchdown highlights," it retrieves the news clip because the vector similarity search is operating on a corrupted signal. The agent then serves that clip to millions of users. At scale, you cannot rely on downstream monitoring to catch this. By the time an anomaly alarm goes off, the agent has already made thousands of bad decisions. Quality controls must shift to the absolute "left" of the pipeline. ... Engineers generally hate guardrails. They view strict schemas and data contracts as bureaucratic hurdles that slow down deployment velocity. When introducing a data constitution, leaders often face pushback. Teams feel they are returning to the "waterfall" era of rigid database administration.


QA engineers must think like adversaries

Test engineers are now expected to understand pipelines, cloud-native architectures, and even prompt engineering for AI tools. The mindset has become more preventive than detective. AI has become part of QA’s toolkit, helping predict weak spots and optimise testing. At the same time, QA must validate the integrity and fairness of AI systems — making it both a user and a guardian of AI. ... With DevOps, QA became embedded into the pipeline — automated test execution, environment provisioning, and feedback loops are all part of CI/CD now. With SecOps, we’re adding security scans and penetration checks earlier, creating a DevTestSecOps model. QA is no longer a separate stage. It’s a mindset that exists throughout the lifecycle — from requirements to observability in production. ... Regression testing has become AI-augmented and data-driven. Instead of re-running all test cases, systems now prioritise based on change impact analysis. The SDET role is also evolving — they now bridge coding, observability, and automation frameworks, often owning quality gates within CI/CD. ... Security checks are now embedded as automated gates within pipelines. Performance testing, too, is moving earlier — with synthetic monitoring and API-level load simulations. In effect, security and speed can coexist, provided teams integrate validation rather than treat it as an afterthought.


The biggest AI bottleneck isn’t GPUs. It’s data resilience

The risks of poor data resilience will be magnified as agentic AI enters the mainstream. Whereas generative AI applications respond to a prompt with an answer in the same manner as a search engine, agentic systems are woven into production workflows, with models calling each other, exchanging data, triggering actions and propagating decisions across networks. Erroneous data can be amplified or corrupted as it moves between agents, like the party game “telephone.” ... Experts cite numerous reasons data protection gets short shrift in many organizations. A key one is an overly intense focus on compliance at the expense of operational excellence. That’s the difference between meeting a set of formal cybersecurity metrics and being able to survive real-world disruption. Compliance guidelines specify policies, controls and audits, while resilience is about operational survivability, such as maintaining data integrity, recovering full business operations, replaying or rolling back actions and containing the blast radius when systems fail or are attacked. ... “Resilience and compliance-oriented security are handled by different teams within enterprises, leading to a lack of coordination,” said Forrester’s Ellis. “There is a disconnect between how prepared people think they are and how prepared they actually are.” ... Missing or corrupted data can lead models to make decisions or recommendations that appear plausible but are far off the mark. 


When open science meets real-world cybersecurity

If there is no collaboration, usually the product that emerges is a great scientific specimen with very risky implementations. The risk is usually caught by normal cyber processes and reduced accordingly; however, scientists who see the value in IT/cyber collaboration usually also end up with a great scientific specimen. There is also managed risk in the implementation with almost no measurable negative impacts or costs. We’ve seen that if collaboration is planned into the project very early on, cybersecurity can provide value. ... Cybersecurity researchers often are confused and look for issues on the internet where they stumble onto the laboratory IT footprint and make claims that we are leaking non-public information. We clearly label and denote information that is releasable to the public, but it always seems there are folks who are quicker to report than to read the dissemination labels. ... Encryption at rest (EIR) is really a control to prevent data loss when the storage medium is no longer in your control. So, when the data has been reviewed for public release, we don’t spend the extra time, effort, and money to apply a control to data stores that provide no value to either the implementation or to a cyber control. ... You can imagine there are many custom IT and OT parts that run that machine. The replacement of components is not on a typical IT replacement schedule. This can present longer than ideal technology refresh cycles. The risk here is that integrating modern cyber technology into an older IT/OT technology stack has its challenges.


4 issues holding back CISOs’ security agendas

CISOs should aim to have team members know when and how to make prioritization calls for their own areas of work, “so that every single team is focusing on the most important stuff,” Khawaja says. “To do that, you need to create clear mechanisms and instructions for how you do decision-support,” he explains. “There should be criteria or factors that says it’s high, medium, low priority for anything delivered by the security team, because then any team member can look at any request that comes to them and they can confidently and effectively prioritize it.” ... According to Lee, the CISOs who keep pace with their organization’s AI strategy take a holistic approach, rather than work deployment to deployment. They establish a risk profile for specific data, so security doesn’t spend much time evaluating AI deployments that use low-risk data and can prioritize work on AI use cases that need medium- or high-risk data. They also assign security staffers to individual departments to stay on top of AI needs, and they train security teams on the skills needed to evaluate and secure AI initiatives. ... the challenge for CISOs not being about hiring for technical skills or even soft skills, but what he called “middle skills,” such as risk management and change management. These skills he sees becoming more crucial for aligning security to the business, getting users to adopt security protocols, and ultimately improving the organization’s security posture. “If you don’t have [those middle skills], there’s only so far the security team can go,” he says.


Rethinking data center strategy for AI at scale

Traditional data centers were engineered for predictable, transactional workloads. Your typical enterprise rack ran at 8kW, cooled with forced air, powered through 12-volt systems. This worked fine for databases, web applications, and cloud storage. Yet, AI workloads are pushing rack densities past 120kW. That's not an incremental change—it's a complete reimagining of what a data center needs to be. At these densities, air cooling becomes physically impossible. ... Walk into a typical data center today. The HVAC system has its own monitoring dashboard. Power distribution runs through a separate SCADA system. Compute performance lives in yet another tool. Network telemetry? Different stack entirely. Each subsystem operates in isolation, reporting intermittently through proprietary interfaces that don't talk to each other. Operators see dashboards, not decisions. ... Cooling systems can respond instantly to thermal changes, and power orchestration becomes adaptive rather than provisioned for theoretical peaks. AI clusters can scale based not just on demand, but in coordination with available power, cooling capacity, and network bandwidth. ... Real-time visibility, unified data architectures, and adaptive control will define performance, efficiency, and competitiveness in AI-ready data centers. The organizations that thrive in the AI era won't necessarily be those with the most data centers or the biggest chips; they'll be the ones that treat infrastructure as an intelligent, responsive system capable of sensing, adapting, and optimizing in real time.


Microsoft handed over BitLocker keys to law enforcement, raising enterprise data control concerns

The US Federal Bureau of Investigation approached Microsoft with a search warrant in early 2025, seeking keys to unlock encrypted data stored on three laptops in a case of alleged fraud involving the COVID unemployment assistance program in Guam. As the keys were stored on a Microsoft server, Microsoft adhered to the legal order and handed over the encryption keys ... While the encryption of BitLocker is robust, enterprises need to be mindful of who has custody of the keys, as this case illustrates. ... Enterprises using BitLocker should treat the recovery keys as highly sensitive, and avoid default cloud backup unless there is a clear business requirement and the associated risks are well understood and mitigated. ... CISOs should also ensure that when devices are repurposed, decommissioned, or moved across jurisdictions, keys should be regenerated as part of the workflow to ensure old keys cannot be used. ... If recovery keys are stored with a cloud provider, that provider may be compelled, at least in its home jurisdiction, to hand them over under lawful order, even if the data subject or company is elsewhere without notifying the company. This becomes even more critical from the point of view of a pharma company, semiconductor firm, defence contractor, or critical-infrastructure operator, as it exposes them to risks such as exposure of trade secrets in cross‑border investigations.


Moore’s law: the famous rule of computing has reached the end of the road, so what comes next?

For half a century, computing advanced in a reassuring, predictable way. Transistors – devices used to switch electrical signals on a computer chip – became smaller. Consequently, computer chips became faster, and society quietly assimilated the gains almost without noticing. ... Instead of one general-purpose processor trying to do everything, modern systems combine different kinds of processors. Traditional processing units or CPUs handle control and decision-making. Graphics processors, are powerful processing units that were originally designed to handle the demands of graphics for computer games and other tasks. AI accelerators (specialised hardware that speeds up AI tasks) focus on large numbers of simple calculations carried out in parallel. Performance now depends on how well these components work together, rather than on how fast any one of them is. Alongside these developments, researchers are exploring more experimental technologies, including quantum processors (which harness the power of quantum science) and photonic processors, which use light instead of electricity. ... For users, life after Moore’s Law does not mean that computers stop improving. It means that improvements arrive in more uneven and task-specific ways. Some applications, such as AI-powered tools, diagnostics, navigation, complex modelling, may see noticeable gains, while general-purpose performance increases more slowly.