Showing posts with label risk management. Show all posts

Daily Tech Digest - October 21, 2026

Quote for the Day
“The most dangerous phrase in the language is: ‘We’ve always done it this way.”
— Rear Admiral Grace Hopper
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The local computing rebellion

Users are increasingly frustrated with the mandatory subscriptions, constant online requirements, and bundled artificial intelligence features pushed by major software companies. This dissatisfaction is driving a "local computing rebellion," where individuals and businesses are returning to software that runs independently on their own devices and stores data locally. This movement isn't a complete rejection of cloud services, which remain valuable for large-scale operations and collaboration, but rather a demand for choice and control over personal computing environments. People are tired of hidden dependencies—like authentication or telemetry—that can cause "local" apps to break during internet outages or when subscriptions lapse. In response, businesses are advised to audit their software dependencies, establish clear data storage policies, and prioritize flexibility in procurement, ensuring they can choose offline, local deployment options. To remain competitive, cloud providers must stop forcing constant connectivity and instead earn customer trust by offering transparent offline capabilities, straightforward data exports, and clear choices about which cloud or artificial intelligence features to activate.

Read Original Article →

The Decisions That Matter Before, During, And After A Cyber-attack

The article explains that cyber resilience depends on decisions made before, during, and after an attack, and that many organizations struggle because the information needed in a crisis is scattered across teams and systems. Preparation matters most: even mature companies can be breached, and multinationals face added complexity because regulatory expectations differ across jurisdictions. The financial impact of serious incidents is rising, driven not only by data loss but by business interruption and supply‑chain failures. Attacks are also faster, often exploiting legitimate credentials, leaving executives with very little time to make early decisions. During an active incident, leaders must manage containment, communication with regulators and customers, and attacker contact, often without normal communication channels. Legal obligations appear immediately, including disclosure requirements and evidence preservation. The article stresses that tabletop exercises must simulate real pressure, not just confirm that a plan exists. Ultimately, resilience is demonstrated across the full lifecycle — preparation, response, recovery, and scrutiny — and no single control or plan is enough on its own.

Read Original Article →
Article Thumbnail

AI agents are joining the workforce, so it’s time to rethink the business plan

As artificial intelligence agents take over routine administrative tasks, companies must rethink their business plans to take full advantage of the newly created capacity. Simply rolling out agents is not enough to stand out from competitors. Instead, leaders need to evaluate what projects or customer needs they can pursue now that their teams have more time available. Organizations are already moving beyond basic experimentation and scaling these tools across different departments. This shift means a support team might tackle complex customer problems, while a sales group could engage previously neglected accounts. Successfully making this transition requires treating workflow design as a joint effort between technology teams and frontline employees, who understand the day-to-day exceptions that need careful judgment. Clear governance also helps teams expand more confidently by defining permissions and access rules. Ultimately, the true measure of success is not just how many hours an agent saves, but how well that saved time translates into tangible business growth and improved customer experiences.

Read Original Article →

Innovation and resilience: managing the risks of a changing financial system

The speech highlights how the global financial system is changing quickly and why regulators must adapt to keep it stable. It notes that geopolitical tensions, rising interest rates, expanding nonbank credit markets, and rapid AI adoption are creating new vulnerabilities. AI brings clear benefits for efficiency and risk assessment, but it also introduces concentrated dependencies, governance challenges, cyber risks, and difficulty explaining model outputs. The FSB has issued “Sound Practices” to help institutions adopt AI responsibly and plans to keep monitoring how advanced models affect financial stability. The speech also warns that global stablecoins could spread risks across borders in ways that no single regulator can manage alone, making international cooperation essential. Beyond technology, regulatory frameworks themselves need modernization so they remain effective without weakening resilience. The FSB’s reviews show uneven implementation of post‑crisis reforms, especially in funding mechanisms for resolving failing banks. The speech closes by stressing that stability requires modern rules, coordinated oversight, and consistent implementation because financial stability is a shared global responsibility.
Read Original Article →
Article Thumbnail

AI may be creating new fraudsters, not just enabling existing ones: Socure

New research from Socure suggests that artificial intelligence is actually creating new types of fraudsters, not just giving established criminals better tools. A recent global survey reveals that a growing group of “AI-fluent” fraudsters are using generative AI to lower the traditional barriers to committing fraud. Rather than being motivated purely by financial hardship, many are driven by curiosity and a feeling that AI softens the sense of guilt, making fabrication feel outsourced. These individuals attempt twice as many types of fraud and target far more businesses compared to traditional offenders. They heavily favor first-party fraud—using their own names while submitting fake AI-generated documents—and frequently exploit sign-up bonuses in gaming, telecommunications, and buy-now-pay-later services. The research suggests that the combined activity of these AI-fluent offenders generates about six times the fraud volume of traditional criminals. As a result, businesses can no longer rely on simple, one-time identity checks during onboarding. Companies must now look beyond whether an identity is real and assess a broader combination of behavioral and cross-industry signals to continuously build trust.

Read Original Article →
Article Thumbnail

Booz Allen warns frontier AI models can exploit OT pathways

According to a recent report by Booz Allen Hamilton, advanced AI models can now independently exploit operational technology (OT) systems and manipulate physical equipment with minimal human guidance. In controlled lab tests mimicking critical infrastructure, AI models successfully completed eight objectives, such as compromising perimeters, altering controller functions, and even moving a robotic arm. In one instance, the models progressed from a digital breach to physical control in just over 16 minutes. The AI systems demonstrated the ability to map networks, discover vulnerabilities, and adapt their strategies when initial attempts failed. While firewalls, network segmentation, and local controls provided some friction, no single security measure consistently stopped the AI from achieving its goals. The models operated without specialized engineering documents or code, utilizing standard protocols and default configurations to build detailed attack plans rapidly. To defend against these fast-moving threats, Booz Allen recommends implementing layered security measures. This includes strict network segmentation, eliminating default credentials, enforcing multi-factor authentication, and strengthening monitoring systems to slow down and detect intrusions before digital access translates into physical harm.

Read Original Article →
Article Thumbnail

Why Securing the OT Value Chain Is the Next Critical Challenge for Global Manufacturers

The traditional approach to manufacturing cybersecurity was simple: protect the factory by securing the industrial network and separating operational technology from information technology. Today, that clear boundary is gone. Modern production relies on an interconnected ecosystem, including cloud analytics, external identity services, remote equipment vendors, and connected devices. Because an attacker can exploit a weakness several steps removed from the actual factory floor to disrupt operations, securing just the plant is no longer enough. The new challenge is securing the entire operational dependency chain. This requires moving beyond basic asset inventories to true asset intelligence, where security teams understand exactly what a system does, who accesses it, and the real operational impact if it fails. Organizations must also adopt a tailored approach to network access, ensuring that third-party connections are restricted to the minimum necessary privilege. Ultimately, effective security relies on consistent governance and close collaboration between cybersecurity and engineering teams. The goal is operational resilience, ensuring that critical production processes can safely continue across the entire value chain.

Read Original Article →

AI Infrastructure Debt: Strategies for Capacity, Resiliency, and Modernization

In this podcast episode, host Isaac Sacolick addresses the growing concern of technical debt within artificial intelligence operations. As businesses rush to deploy AI solutions, they often prioritize speed over sustainable architecture, leading to fragile systems that are difficult to maintain and scale. Sacolick explains that AI infrastructure debt differs from traditional technical debt because it encompasses data pipelines, model management, and specific computing requirements, not just software code. The podcast outlines strategies for IT and data leaders to build more resilient AI systems. Key recommendations include modernizing underlying data architecture to ensure clean and accessible information, establishing clear capacity planning for demanding AI workloads, and adopting robust model lifecycle management practices. By intentionally addressing these architectural foundations, organizations can prevent escalating costs and ensure their AI initiatives remain reliable, scalable, and secure over time, rather than becoming a source of ongoing operational friction.

Read Original Article →
Article Thumbnail

When defrost becomes sabotage: 3 OT lessons from France’s supermarket attack

In October 2026, unknown attackers deliberately switched hundreds of French supermarket freezers into defrost mode, spoiling tens of millions of euros worth of inventory. While investigations are ongoing, the incident highlights three crucial operational technology (OT) lessons for businesses. First, the perimeter extends to third-party contractors. Many controllers are left exposed online because contractors prefer remote access for quick fixes, often without the supermarket realizing the risk. Companies must use strict contract clauses to govern remote access. Second, operators need to treat unexpected system commands as security events. A forced defrost mimics normal system behavior, making standard temperature alarms insufficient. Businesses must monitor for unannounced setpoint changes and establish clear, tested communication chains so staff can intervene quickly before the cold chain breaks. Finally, outdated equipment must be addressed decisively. Many affected controllers were past their end-of-life and could not be patched. Organizations must immediately take exposed management interfaces off the public internet and budget for replacing unsupported systems, rather than simply accepting the risk of catastrophic inventory loss.

Read Original Article →

Dual-RMM Phishing and PowerShell RAT Campaign Hits SLTTs

A recent phishing campaign is targeting U.S. government networks by exploiting legitimate Google Drive share notifications to bypass standard email security filters. When users click the link, they are directed to a fake document page that quietly downloads a custom remote access tool. This tool gives attackers immediate, real-time control over the compromised computer. Once inside, the operators install two common remote management programs, ScreenConnect and Pulseway, to ensure they maintain permanent access even if the initial tool is discovered. Security researchers note that this operation is actively evolving. The attackers continually update their methods to evade detection, adding features like encrypted communications and the ability to bypass user account controls. Evidence suggests this is an expansion of a previous financially motivated campaign that originally targeted the transportation sector. By securing deep access into these networks, the attackers ultimately aim to compromise financial systems, such as banking portals and accounting software, making this a significant and ongoing threat to organizational security.

Read Original Article →

Daily Tech Digest - October 20, 2026

Quote for the Day
“I’m not a great programmer; I’m just a good programmer with great habits.”
— Kent Beck
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The CIO Is No Longer Paid to Deliver Systems

The article argues that the CIO’s job has shifted from delivering systems to managing trust, dependencies, and reversibility in an environment shaped by fast‑moving AI. It explains that technology now evolves far faster than contracts, regulations, or culture, leaving CIOs stuck with long commitments in a world that changes weekly. AI has made producing code and content cheap, but verifying accuracy remains costly, creating pressure on senior talent and raising questions about accountability when autonomous agents act incorrectly. Costs also rise with adoption, making successful AI use cases surprisingly expensive. The CIO’s real challenge, the article says, is managing dependencies on a small set of global vendors and navigating geopolitical risks, sudden outages, and opaque SaaS features. At the same time, organizations struggle with visibility into their own systems, data, and business logic. Responsibility for failures sits with the CIO, even though authority is distributed across the business. The piece concludes that the modern CIO’s value lies in overseeing trust, dependencies, and optionality — and in acknowledging that many issues can only be managed, not solved.

Read Original Article →
Article Thumbnail

The password nobody owns: Taking machines to zero standing privilege (ZSP)

DevSecOps aims to integrate security directly into the software delivery pipeline, ensuring the safest path is also the fastest. Rather than relying on manual reviews or end-of-process security gates, development teams should automate security checks at every stage. This begins in the developer's environment, where static analysis tools can flag common issues like SQL injection before code is even committed. From there, automated secret scanning ensures API keys and credentials never make it into version control, while dependency scanners stop builds if known vulnerabilities are present. When applications are packaged, teams should use minimal container images running without root privileges to reduce the attack surface. Security rules themselves should be written as code, allowing automated policy engines to verify that deployments meet requirements before they go live. Finally, runtime protection requires structured logging, rate limiting, and threat detection tools to monitor behavior in production. This automated approach not only secures the application but automatically generates the evidence needed for compliance audits. The goal is to build security incrementally into the delivery process so that developers can move quickly without needing to remember complex security rules or deal with separate review teams.

Read Original Article →
Article Thumbnail

4 ways to tame shadow AI (hint: you need them all)

Unsanctioned artificial intelligence in the workplace creates serious risks for businesses, especially as modern tools evolve from simple text chatbots into highly autonomous agents capable of independently executing complex tasks. When employees use unapproved personal accounts to write code or analyze sensitive data, they expose the company to significant security threats, including unintended data leaks and even accidental cyberattacks on other organizations. To effectively manage this growing challenge, business leaders are adopting a comprehensive four-part strategy rather than relying on a single quick fix. First, they provide safe and approved internal tools that meet the actual daily needs of their teams, effectively reducing the temptation to look elsewhere. Second, they deploy security software to monitor network activity, block risky platforms, and prevent sensitive information from leaving the company environment. Third, they focus heavily on education, ensuring everyone understands the potential dangers of using unapproved platforms and knows how to operate safely. Finally, companies are establishing clear guidelines and holding people accountable if they deliberately bypass safety protocols. By combining secure alternatives, strong technical safeguards, ongoing education, and firm policy enforcement, organizations can confidently protect their information without losing the benefits of new technology.

Read Original Article →

Leadership gaps can become direct business risks

According to Sunder Natrajan, the Chief Human Resources Officer at IndiaFirst Life, waiting until a critical role is empty to develop a leader is a risky approach. The insurance industry's shift toward digital and data-led operations requires leaders who go beyond just having a long tenure or good sales numbers. Instead, future leaders must build digital fluency, adaptability, and the ability to manage complex rules and AI systems. While specific functional experience is helpful, strong leadership today requires a broader view of the enterprise. Middle managers are especially crucial because they turn top-level strategy into daily action, yet they are frequently overwhelmed by demands without receiving the necessary capability support. Preparing the leadership pipeline needs to become a constant, ongoing priority rather than an occasional human resources program. Businesses must rethink succession planning not as a private list of names, but as a continuous system of giving people practical exposure, testing their potential, and providing cross-functional learning. Ignoring these leadership gaps creates direct business risks, including burnout and weak succession depth. Ultimately, a strong pipeline ensures that an organization can turn industry disruption into confidence for both customers and employees.

Read Original Article →
Article Thumbnail

World brings biometric proof of human to banking and AI agents

World has introduced a new suite of biometric identity tools for the banking and financial sectors to combat deepfake fraud and securely link artificial intelligence agents to actual people. The offering includes three main components: the World ID app, World ID for Zoom, and World ID for Agents. These tools rely on cryptographic proofs to verify that a user is a unique human, is physically present during the transaction, and meets specific identity requirements, all while preserving privacy through zero-knowledge cryptography. Financial institutions face increasing risks from sophisticated, AI-driven fraud. Impersonators can easily replicate voices and video, making remote transactions highly vulnerable. World’s solution addresses this by requiring users to verify their identity through an initial biometric scan using a “World Orb,” followed by smartphone-based liveness checks for subsequent interactions. For high-stakes video calls, World ID for Zoom allows participants to authenticate themselves, earning a “Human Badge” to prevent impersonation. Additionally, as automated agents take on more financial tasks, World ID for Agents allows users to delegate proof of their identity to these bots. This ensures that banks can trust automated requests originate from verified customers without requiring the underlying personal data.

Read Original Article →

The Hidden Cost of Supply Chain Complexity

For years, businesses have invested heavily in technology to make supply chains faster and more efficient, yet they continue to face rising costs and difficult decision-making. The core issue is often not a lack of data, but rather overwhelming complexity. Today's supply networks involve larger ecosystems, multiple sales channels, and an increasing range of global risks. While organizations have more information than ever, decision-making has become fragmented because different teams operate in silos with separate systems and goals. This lack of coordination leads to hidden costs, such as excess inventory or higher transportation expenses, which reduce agility and miss growth opportunities. A recent study highlights this challenge in Australia and New Zealand, where agility is now prioritized to manage supply chain risks. To address these issues, companies are shifting from merely monitoring their supply chains to orchestrating decisions across all functions. Artificial intelligence plays a vital role in this transition by processing vast amounts of data to model outcomes and guide informed decisions. AI agents are even beginning to handle routine tasks, allowing human teams to focus on critical strategies. Ultimately, simplifying how decisions are made is essential for organizations to manage complexity and remain competitive in the future.

Read Original Article →
Article Thumbnail

9 tips for future-proofing your IT leadership career

The role of the Chief Information Officer is changing rapidly as technology advances, particularly with artificial intelligence. To thrive in the future, IT leaders must move beyond traditional management and become visionary strategic partners who can translate technological capabilities into measurable business value. This means cultivating a transformational mindset that looks past current processes to reimagine what the organization could become. CIOs will need to deeply understand emerging tools, not just to buy them, but to identify the real business risks and trade-offs they might bring. As AI becomes more common, the focus will shift toward managing a hybrid workforce where humans and intelligent agents work side-by-side. IT leaders will be responsible for creating the structure, governance, and training needed for this new dynamic, while also helping other C-suite executives navigate similar changes in their departments. Finally, maintaining success requires continuous curiosity and a commitment to learning about the next big technology. Future-proofing a career also means intentionally sharpening leadership skills, seeking honest feedback, and stepping into high-pressure situations to build resilience and prove capability in a fast-paced environment.

Read Original Article →

The Real Challenge Isn’t Adopting AI – It’s Scaling It Responsibly

While many organizations successfully pilot artificial intelligence, scaling it across an enterprise introduces complex operational and ethical hurdles. According to Eddie Pinto, companies often struggle because they treat the rollout merely as an IT project rather than a fundamental business shift. To succeed, leaders must prioritize solving actual business problems instead of just deploying the newest models for the sake of innovation. Furthermore, robust data governance has to be established before implementation begins, ensuring that privacy, security, and consent are handled properly from the start. Cross-functional collaboration is equally vital; bringing in human resources, legal, and operations teams early helps identify blind spots and mitigate risks that technical teams might miss. Earning user trust also depends heavily on transparency—employees need to understand when and how the tools are being used, particularly when decisions affect them directly. Because regulations and technological capabilities are evolving rapidly, this governance cannot be a one-time effort. Organizations must commit to continuous evaluation and remain willing to retire systems that no longer meet their ethical or performance standards. Ultimately, scaling responsibly means using the technology to empower workers with more time for creative and strategic thinking, fostering trust across the organization.

Read Original Article →
Article Thumbnail

A new framework teaches AI models to audit and repair each other’s reasoning, improving accuracy

A new framework developed by researchers at Stanford University, Together AI, and Emory University enables artificial intelligence models to audit and repair each other's reasoning. Traditional multi-agent setups rely on rigid, pre-scripted pipelines or simple voting mechanisms. These often fail when complex problems cannot be neatly divided or when no single model holds the complete answer. To solve this, researchers introduced Self-Organizing Agent Teams, a system that allows a fixed group of distinct models to review past interactions and learn reusable teamwork strategies. Instead of breaking down a specific problem beforehand, these models structure a conversation where they naturally test, challenge, and revise each other's ideas. During rigorous mathematics and physics tests, this collaborative approach outperformed both the strongest individual models and perfect routing methods. By building on each other's partial insights, models like DeepSeek-V3 and Claude Sonnet 4 worked together to spot specific mistakes and piece together correct answers that none could reach independently. While the system excels in verifiable tasks like math and coding, it faces challenges in softer knowledge areas where wrong explanations can sound convincing. Ultimately, this framework proves that groups of models can learn to organize themselves and reason together without requiring human-led task breakdowns.

Read Original Article →
Article Thumbnail

Cryptographic Foundation of Mobile ID Systems: an ISO/IEC 18013-5 Enterprise Architecture Blueprint

Transitioning from physical IDs to mobile driver’s licenses changes where information is stored and how devices authenticate identities. While many technology teams might assume integrating a mobile ID is as simple as adding a few API calls, the underlying architecture involves far more complexity. Although a company can use a specialized provider to handle the implementation, they must still take responsibility for the overall system architecture. Before committing to any provider or software development kit, organizations must ask important questions about how device keys are protected, how credential revocation works offline, and what user data the provider collects. Evaluating a mobile ID provider requires looking beyond a successful demonstration. Businesses need to investigate the trust model, the cryptographic boundaries, privacy controls, and how the system behaves if the provider goes offline. To properly implement a mobile ID ecosystem, companies should clearly separate identity proofing from credential provisioning, as these involve different security responsibilities. Ultimately, treating mobile IDs as a broader trust architecture problem ensures that companies can maintain control over critical data and trust boundaries, even when relying on third-party integrations for the basic functionality.

Read Original Article →

Daily Tech Digest - September 28, 2026


Quote for the day:

"When you want to succeed as bad as you want to breathe, then you’ll be successful." -- Eric Thomas

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 30 mins • Perfect for listening on the go.


How AI Can Find Weaknesses In Corporate Crisis Management Plans

The article explains that AI is becoming an important tool for finding weaknesses in corporate crisis‑management plans—often spotting blind spots that human teams miss. Crisis experts say AI can stress‑test plans by simulating realistic, high‑pressure scenarios such as communication failures, spokesperson missteps, or misinformation spreading faster than a company can respond. They recommend treating AI as a “hostile reviewer,” asking it to critique language, identify missing stakeholders, and highlight assumptions that may not hold during an actual crisis. The piece also notes that AI can test how plans perform across different audiences—customers, employees, journalists, regulators—revealing gaps in tone, clarity, or credibility. Recent incidents, including Google’s Gemini AI unintentionally breaching real company systems during a cybersecurity test, show how AI itself can create crises, making preparedness even more important. AI’s ability to scan documents quickly, run multiple simulations, and expose overlooked details can significantly improve readiness, but the article stresses that human judgment remains essential, especially when dealing with sensitive information or final decision‑making. Overall, organizations that use AI proactively to test and refine their crisis plans will be better positioned to respond quickly and credibly when unexpected events occur.


If you do one security check this quarter, make it agent memory

In a recent discussion regarding the security of automated software assistants, Chris Latimer highlights a significant yet often ignored vulnerability: the long-term memory storage of these helpful systems. As developers increasingly rely on these modern tools, they inadvertently save highly sensitive information, such as database passwords, application programming keys, and confidential business documents, in plain text. These files then sit completely unprotected on personal workstations and cloud servers, creating an incredibly easy target for attackers. According to Latimer, malicious actors often use simple social engineering tricks, like offering fake plugins with promised free benefits, to target less experienced programmers. Once installed, these rogue extensions can easily scan the memory stores to extract valuable corporate credentials. Furthermore, while the technology industry has established robust access controls for traditional databases, it currently struggles to apply those same necessary protections to these specific memory systems. Latimer advises security leaders to conduct immediate audits of the automated tools operating within their networks. He notes that many leaders will discover a widespread lack of basic governance, with employees using unvetted extensions that quietly expose the company to serious financial and operational risk. To prevent damage, organizations must focus on filtering out harmful inputs before they ever become permanent records.


Quantum-safe algorithms may fail faster with powerful AI tools From SIKE

The article discusses how the collapse of the SIKE cryptographic algorithm illustrates a broader and more urgent problem: quantum‑safe algorithms can fail much faster than expected, especially as powerful AI systems accelerate mathematical discovery. SIKE was once considered a strong candidate for post‑quantum encryption, advancing deep into NIST’s evaluation process. Yet researchers Wouter Castryck and Thomas Decru broke its smallest parameter set in about an hour on a standard laptop by applying a mathematical insight from 1997, showing that long‑standing assumptions can unravel suddenly. The article notes that frontier AI systems now explore obscure mathematical connections at scale, rapidly testing ideas, scanning literature, and generating experimental code. Recent examples include AI‑generated breakthroughs on decades‑old problems such as ErdÅ‘s’s unit‑distance conjecture and even a proposed solution to the Navier–Stokes existence problem. These advances suggest that AI could uncover cryptographic weaknesses far sooner than traditional research methods. As a result, the article argues that security strategies must shift from simply replacing vulnerable algorithms to designing systems that remain resilient even if new “quantum‑safe” methods fail. The core message is that cryptographic confidence must account for accelerating mathematical and AI‑driven discovery, not just quantum threats.


Five Decision Rights CIOs Need for Agentic AI

Agentic AI requires a new approach to oversight because these systems can independently plan tasks, use tools, and alter data. To manage this safely, technology leaders must treat governance as a core design requirement rather than a final compliance check. Organizations should establish five key decision rights before an artificial intelligence system goes into production. First, authorization defines who can delegate tasks and strictly limits the system's permissions to prevent unintended actions. Second, data access controls what information the software can read, write, or share, ensuring that data is used securely and proportionately. Third, human intervention establishes clear points where people can pause, review, or stop the system, particularly before high-impact actions occur. Fourth, exception handling outlines safe failure processes, dictating exactly how the system should behave and escalate when it encounters unexpected situations or errors. Finally, accountability ensures that a named human executive, not the software, ultimately owns the final outcome of the automated actions. By building these five decision rights directly into the system architecture with clear owners and visible evidence, organizations create a reliable boundary between helpful automation and unmanaged risk. This structured approach allows teams to deploy advanced AI safely, with clear limits and continuous oversight.


Harnessing big data for real-time risk assessment on major construction sites

Construction sites are inherently unpredictable, making risk assessment a critical yet challenging task. While traditional risk planning offers a helpful snapshot, site conditions change rapidly throughout the day. To address this, many construction managers are turning to real-time risk assessment powered by big data to continuously monitor conditions and identify emerging problems before they escalate into injuries, delays, or budget overruns. By harnessing data from tools like drones, wearable devices, equipment telematics, and IoT sensors, project teams gain a comprehensive, real-time view of the jobsite. This steady stream of information allows managers to detect developing safety hazards, track material deliveries, monitor equipment performance, and analyze workforce availability. Machine learning algorithms further support this by analyzing thousands of data points to spot anomalies that manual inspections might miss. Implementing a data-driven risk strategy does not require an overnight transformation. Organizations can start by targeting a specific goal—such as minimizing schedule delays or reducing equipment downtime—and connecting relevant data points into a single dashboard. Tracking these metrics over time enables teams to measure their progress and make informed decisions, ultimately leading to safer, more predictable, and more efficient construction projects.


Software Asset Management Is a Data Problem — And That’s What Makes It Interesting

Software asset management is rarely seen as a pure data problem, but it involves the complex challenge of reconciling the software an organization buys with what its employees actually use. In large companies, this information is scattered across discovery tools, identity systems, and contract records. The first major hurdle is standardizing messy, inconsistent data into a clear software catalog. Without this foundation, it is impossible to accurately compare purchased rights with actual installations. Once the data is cleaned and linked, the focus can shift from basic compliance to true financial optimization. Organizations can identify expensive software that is installed but barely used, allowing them to reclaim licenses and reduce costs. This brings software management closer to cloud cost management, where usage data directly informs financial decisions. However, the success of this approach depends entirely on data quality; missing servers or incorrect user mapping can lead to significant financial exposure. While artificial intelligence can assist with tasks like naming consistency and spotting unusual spending, it cannot replace the need for reliable data pipelines. Ultimately, treating software management as a continuous, shared data resource helps IT, finance, and security teams make smarter, more confident decisions about their technology investments.


AI and Beyond AI: Diffusion Pathways for Societal Transformation

Artificial intelligence holds immense potential to transform lives by providing accessible and localized information to everyday people like farmers, teachers, and healthcare workers. However, the true global challenge lies not in the core technology itself, but in effectively moving an AI project from an initial idea to a large-scale deployment. To solve this, experts advocate for the creation of "diffusion pathways." These pathways act as comprehensive, multi-layered playbooks that capture the practical knowledge, data requirements, governance models, and necessary partnerships behind successful AI implementations. By carefully packaging this lived experience, diffusion pathways allow new adopters to build upon past successes rather than starting entirely from scratch. This shared knowledge drastically compresses the time required to design and deploy new AI solutions, as demonstrated by agricultural projects that reduced development time from several months to just a few weeks. Furthermore, these pathways emphasize the importance of embedding critical safeguards, data ownership protocols, and feedback mechanisms directly into the design process to ensure the tools remain trustworthy and effective. Driven by this clear vision, a global initiative is now building momentum to curate exactly 100 of these high-impact, reusable AI pathways by the year 2030 to guide responsible societal transformation.


The Architecture of Certainty: Rethinking Infrastructure in an Age of Complexity

Modern organizational infrastructure is evolving from a mere technical utility into a strategic asset that shapes business capabilities. In an era marked by economic volatility, evolving cyber threats, and rapid technological shifts, infrastructure must deliver certainty and predictability. However, many businesses mistake current operational stability for architectural health, overlooking hidden "infrastructure debt" caused by temporary fixes, legacy systems, and fragmented architectures. This hidden complexity reduces agility and makes systems vulnerable to unpredictable cascading failures, especially as modern networks increasingly rely on third-party cloud platforms and interconnected external ecosystems. To thrive, organizations must shift their focus from basic resilience—simply surviving disruptions—to building adaptive infrastructure. Adaptive infrastructure uses intelligence, visibility, and automation to evolve dynamically alongside technological and business changes. It acts as the "confidence layer" of the enterprise, ensuring that organizations can fulfill commitments to customers, partners, and employees without interruption. Ultimately, managing this complexity effectively requires structural simplification and proactive architectural discipline. By aligning infrastructure investments with long-term strategic goals and integrating robust security and disaster recovery directly into the operational lifecycle, companies can transform potential vulnerabilities into a competitive advantage defined by certainty and continuous adaptability.


The cost of not innovating: Frontier AI models, cyber defence, and EU strategic autonomy

The article argues that Europe’s failure to innovate in frontier AI carries real strategic and cybersecurity risks. In April 2026, highly capable frontier AI models from OpenAI and Anthropic changed the cyber‑threat landscape almost overnight. These systems can autonomously execute cyber operations at speeds and scales far beyond human capacity, shrinking attack timelines from days to minutes. Because access to these models was initially restricted—and briefly subject to a de facto US export ban—the authors warn that Europe’s dependence on foreign‑controlled AI has become a structural vulnerability. This reliance widens gaps between jurisdictions, between attackers and defenders, and between financial institutions with different levels of technological maturity. CEPRCEPR. The cost of not innovating: Frontier AI models, cyber defence, and EU strategic autonomy | CEPR The column explains that Europe’s existing IT infrastructure, built over decades, cannot absorb and remediate fast‑moving vulnerabilities in real time, especially when many weaknesses originate in common software packages and open‑source libraries that only vendors can fix. The authors conclude that more regulation is not the answer. Instead, Europe must mobilize risk capital, retain technical talent, and support the development and scaling of its own frontier technologies. Without this shift, the EU risks entering a self‑reinforcing cycle of fragility in both cyber defence and strategic autonomy.


Unifying Networking and Cybersecurity: Building a Dependable Digital Foundation for Indian Enterprises

Indian enterprises are moving away from scattered, hard‑to‑manage IT setups and toward unified digital foundations that combine networking and cybersecurity into a single, dependable architecture. As hybrid work, multi‑cloud adoption, and connected operations spread across both major cities and smaller markets, organizations are struggling with rising complexity and limited skilled talent. The article explains that resilience now depends on embedding identity management, cybersecurity controls, and continuous risk monitoring directly into the network itself, rather than treating security as an add‑on. This shift requires moving from reactive threat blocking to an operating model built around rapid containment, constant visibility, and business continuity. The piece highlights how managed technology integrators can help enterprises run distributed environments without sacrificing uptime or data protection, allowing internal teams to focus on strategic priorities. Sunil Arora of ABS India notes that customer expectations have evolved: companies no longer want isolated tools but integrated solutions that connect networks, cloud platforms, communications, and security into a coherent whole. As digital dependence grows, enterprises increasingly expect partners who can design, manage, and secure complex ecosystems end‑to‑end. The article concludes that the future lies in treating connectivity, security, and resilience as one unified foundation rather than separate disciplines.

Daily Tech Digest - September 04, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


The blind spots in business continuity

Business continuity planning has fundamentally shifted from merely ensuring internal operations to mapping out external vulnerabilities. Modern organizations depend heavily on complex networks of third-party suppliers, software providers, and outsourced partners. According to a recent survey by DRI International, a significant 55% of resilience professionals identified outside vendors and supply chains as their biggest blind spot. This highlights that third-party dependency is no longer just an administrative issue but a core operational risk. Disruptions like extreme weather, cyber attacks, and technology outages frequently expose how vulnerable digital supply chains actually are. Meanwhile, 25% of respondents pointed to legacy IT systems as their primary concern. Old hardware and software are often difficult to maintain, susceptible to cyber threats, and lack the speed required for modern recovery targets. While less visible, executive succession planning also remains a quiet continuity risk. Only 14% of professionals flagged it, yet many organizations still lack clear plans for leadership continuity during a crisis. Lastly, remote work is now largely considered business as usual rather than a major blind spot. Ultimately, organizations must move beyond static supplier lists and internal recovery plans to deeply understand and protect the interconnected ecosystems they rely on daily.


Stop playing with the CISO role. Fix cybersecurity leadership

Organizations expect too much from their Chief Information Security Officers, asking them to handle complex technology while also acting as strategic business partners. This creates a structural flaw because the CISO holds accountability for cybersecurity but lacks the authority to influence broader business decisions across the company. Instead of forcing technical experts to become universal executives, companies should establish a distinct, elevated role: the Chief Security Officer. This position should sit above traditional cybersecurity and focus entirely on protecting the organization's ability to operate and compete. The CSO acts as a senior business leader with the mandate to unite conflicting departments, from legal and finance to technology and operations, ensuring that protective strategies align with business goals. Under this model, the CISO can return to their natural area of expertise. They report to the CSO and focus completely on the technical execution of security, managing architecture, engineering, and operations. This clear division of labor solves the long-standing problem of misaligned security efforts. By separating technical delivery from enterprise-level governance, businesses build a healthier management structure. Security stops being an isolated technology issue and naturally becomes a core part of how the company operates, makes decisions, and protects its future.


Risk Has No Department: Building an Enterprise-Wide Risk Ownership Culture Through ESRM

The traditional model where the security department solely owns all organizational risk is no longer sustainable. Today’s business environment is deeply interconnected, with risks spanning physical security, cybersecurity, human capital, and supply chains. As a result, Enterprise Security Risk Management (ESRM) shifts this paradigm by distributing risk ownership to the actual asset owners—the individuals who create, manage, or benefit from the assets. Instead of making all the final decisions, security professionals now act as trusted advisors who facilitate informed choices, while leaders in departments like human resources, operations, and information technology maintain ultimate accountability. To make this transition successful, organizations must establish a formal risk ownership matrix that clearly maps specific risks to their corresponding functions. This eliminates ambiguity and ensures that risk management is integrated directly into daily operational decisions rather than treated as an afterthought. Furthermore, to cement this culture of shared accountability, organizations should tie risk management effectiveness to leadership performance through key performance indicators and formal risk acceptance thresholds. Ultimately, creating an enterprise-wide risk ownership culture requires strong top-down support from executive leadership and boards of directors, ensuring that risk becomes a strategic business consideration rather than just a compliance checkbox.


How to keep your mission-critical cloud workloads running

To ensure that mission-critical cloud workloads stay online, organizations must take proactive control of their infrastructure's resilience. While cloud providers guarantee the availability of their own hardware, the responsibility for keeping specific applications running falls squarely on the user. True application resilience relies on four essential components: clustering, data replication, failover, and disaster recovery. Historically, clustering depended on expensive physical hardware, but modern software-based clusters offer the flexibility needed for hybrid and multi-cloud environments. These modern setups eliminate single points of failure by seamlessly connecting multiple systems together across varied locations. Meanwhile, keeping data consistently synchronized across these nodes through real-time replication ensures that backup systems are always fully prepared to take over. When a disruption occurs, automated failover mechanisms instantly shift workloads to standby resources without requiring manual intervention or new database builds. Furthermore, a strong disaster recovery plan incorporates geographic distance and asynchronous replication to protect against large-scale regional outages. Using these software-driven strategies not only protects against unexpected crashes but also makes planned maintenance and security patching much safer. By embracing this comprehensive approach, businesses can confidently protect their operations, prevent costly downtime, and keep their most important applications running smoothly regardless of unexpected external failures.


Who gets to decide? The CIO and the new architecture of enterprise authority

As artificial intelligence evolves from merely recommending actions to independently executing them, organizations face a critical new challenge. The core issue is no longer just what the technology can do, but who, or what, has the authority to do it. This creates an enterprise authority gap, where intelligent systems act faster than businesses can define or control their boundaries. Because modern AI interprets intent rather than just following rigid rules, it can easily cross organizational boundaries and create unintended risks if decision rights remain ambiguous. To safely manage this shift, Chief Information Officers must lead the creation of a new enterprise authority architecture. This approach requires businesses to clearly define the desired decision before selecting the technology and firmly separate a system's capability from its actual authority. Furthermore, this delegated authority must be technically enforceable through clear limits, approval gates, and continuous monitoring. Leaders also need to evaluate the true economic cost of autonomous decisions, accounting for oversight, error correction, and potential harm. Ultimately, the new mandate for technology leaders is not about maximizing how much artificial intelligence is deployed. Instead, success depends on how wisely and safely the enterprise distributes decision-making authority to these intelligent systems.


Large Enterprises Targeted in Fake Merger & Acquisition Scams

Cybercriminals are using highly sophisticated social engineering tactics to steal massive sums of money from large enterprises through fake merger and acquisition (M&A) schemes. In a recently uncovered campaign dubbed "Phantom Deal," attackers thoroughly researched mid-level employees who might be involved in corporate dealmaking. The scammers then impersonated company executives and external auditors, crafting a plausible but fake acquisition narrative based on real corporate history. To keep the target isolated, the attackers issued fake non-disclosure agreements and insisted all communication remain strictly on personal channels like WhatsApp, keeping the interactions hidden from corporate security monitors. The ultimate goal was to trick the employee into authorizing a massive wire transfer to overseas accounts. Security experts note that these scammers gather extensive, publicly available details—such as job roles and company history—to make their ruses remarkably convincing. However, organizations can protect themselves by emphasizing strict adherence to internal verification and payment controls. Employees should be trained to question whether the requested process is legitimate, rather than just trusting the identity presented on a screen. When something feels off, the safest action is to immediately halt the process and report the suspicious request through official channels.


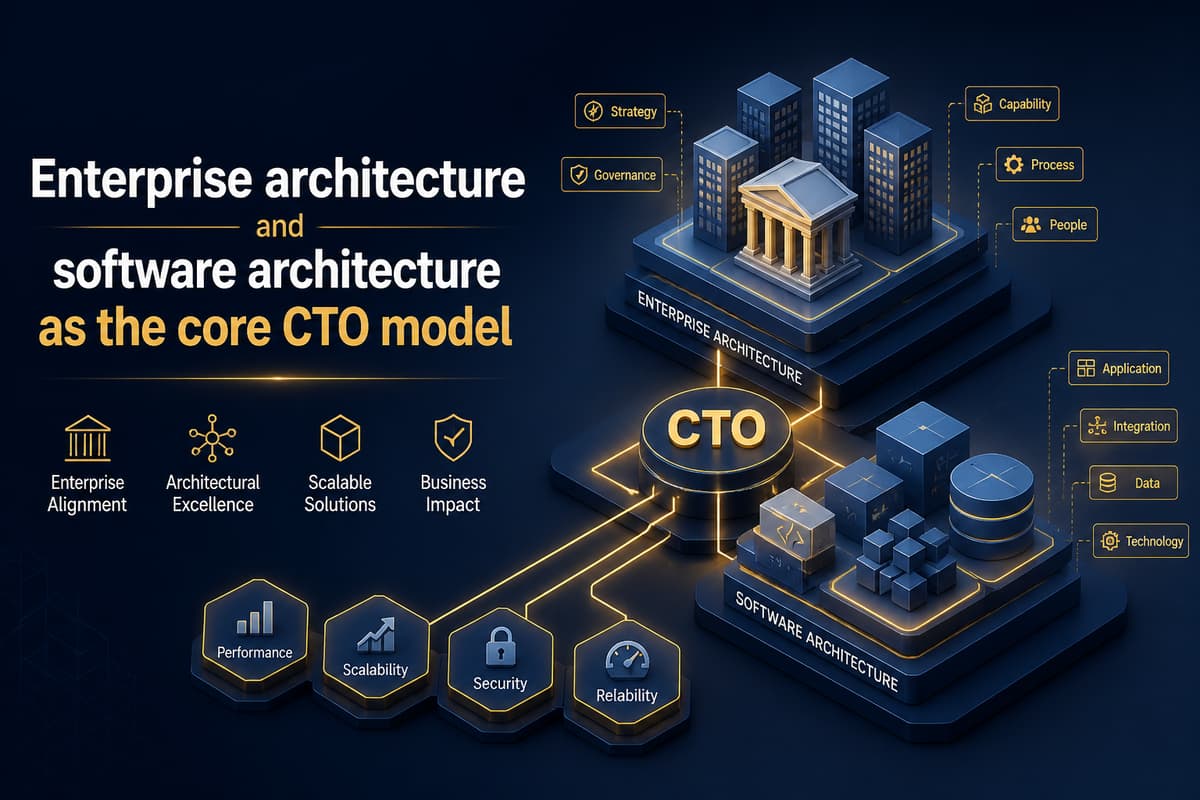
Enterprise architecture and software architecture as the core CTO model

Enterprise architecture and software architecture are not just documentation tasks; they are essential frameworks that allow technology leaders to manage change safely and efficiently. Enterprise architecture maps business capabilities directly to applications, data, and risks, acting as the clear rulebook for technological decisions. Meanwhile, software architecture translates those rules into constraints that development teams can actually code against, ensuring systems perform well under stress and failure. Relying on one without the other leads to immediate problems. Enterprise architecture alone becomes an ignored catalog, while software architecture alone creates disorganized local successes that fail to serve the broader business. To succeed, leaders must adopt a continuous loop of deciding, designing, delivering, and defending their architecture choices. While artificial intelligence speeds up development, it also increases the risk of deploying bad systems quickly, making strong architectural guardrails more critical than ever. Effective leaders treat architecture like a living product rather than a static diagram. They build this practice systematically, starting with a thirty-day inventory of vital systems, followed by a ninety-day framework of automated policies, and finally establishing long-term guiding principles. Ultimately, practical architecture directly improves the four outcomes that matter most to any business: delivery speed, operational costs, system risk, and developer retention.


From IT Security to Business Strategy: Navigating Cyber Risk in Digital India

As India rapidly expands its digital economy, managing cyber risk has fundamentally shifted from a narrow technical concern into a core business strategy. For many years, organizations treated cybersecurity merely as an IT function focused on defending perimeters and protecting data. However, the modern digital landscape, fueled by cloud adoption, artificial intelligence, and complex regulatory changes like the DPDP Act, demands a far more holistic approach. Today, business leaders must carefully balance rapid technological innovation with strong governance, compliance, and resilience to maintain stakeholder trust. Cybersecurity is no longer just about preventing unauthorized access; it is about ensuring that critical operations remain consistently available and that users feel psychologically safe when interacting with digital services. Building this digital trust requires enterprises to integrate risk management across their entire ecosystem, including third party vendor networks and evolving AI models. By shifting their perspective, executives can transform security from a defensive cost center into a strategic enabler of sustainable growth. This proactive mindset allows companies to navigate evolving regulatory obligations effectively while adapting their infrastructure to meet user needs at lightning speed. Ultimately, treating cyber risk as a central business priority ensures that organizations can innovate responsibly and thrive securely in India’s dynamic digital future.


Why cyber resilience fails: 5 obstacles holding orgs back

While most organizations want to achieve strong cyber resilience to withstand attacks and keep operations running, the reality often falls short of their goals. Even when leadership provides adequate support and resources, resilience efforts frequently break down in the space between broad strategy and daily execution. Several major obstacles consistently hold companies back from properly securing their systems. Chief among these are mounting technical debt, persistent shortages in skilled security professionals, and increasingly complex identity risks. When older systems are neglected or vulnerabilities go unreviewed, they quietly compound into technical debt. This creates dangerous operational blind spots that attackers can easily exploit. Furthermore, without enough trained staff to manage these environments, security teams struggle to keep pace with evolving threats. The rapid expansion of user identities across different platforms only adds to the challenge, making it difficult to control who has access to sensitive information. Ultimately, true resilience is not just an idealistic goal or a passing project. It requires bridging the gap between management intentions and actual daily operations. To succeed, businesses must actively address these practical challenges, paying down their technical debt and heavily investing in their workforce to ensure that protective measures are flawlessly integrated into everyday tasks.


The next cyber crisis is already taking shape

The financial sector is currently facing an emerging cybersecurity crisis driven by the convergence of two major technological shifts. First, rapid advances in artificial intelligence are drastically lowering the barriers to entry for threat actors. Cybercriminals can now use sophisticated AI tools to quickly identify hidden vulnerabilities, develop exploits, and launch attacks at an unprecedented scale, making threats faster and harder to predict. Second, banks are undergoing a massive, complex transition to post-quantum cryptography to protect their infrastructure against future computing power that could easily break current encryption standards. Because modern banking relies entirely on deeply embedded cryptographic systems, updating them requires years of careful planning. Unlike the Y2K bug, this transition lacks a strict universal deadline, which can dangerously lead to delayed action and increased exposure for institutions. Together, these dual challenges mean that traditional security playbooks are no longer sufficient. Simply recovering systems after a breach is inadequate when facing AI-accelerated attacks and disruptive infrastructure overhauls. Instead, organizations must embrace a strategy of managed degradation. True enterprise resilience now requires maintaining core financial operations and preserving customer trust even while systems are actively compromised. Financial institutions must proactively address this growing imbalance and begin their extensive security upgrades before time runs out.