Showing posts with label culture. Show all posts

Daily Tech Digest - October 07, 2026


Quote for the day:

“The first step toward success is taken when you refuse to be a captive of the environment in which you first find yourself.” -- Mark Caine

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Forrester Predicts AI Lawsuit, Global Outage in 2027

According to recent predictions from Forrester Research, artificial intelligence could lead to severe consequences for business leaders by 2027, including lawsuits, worldwide outages, and major data breaches. A central prediction suggests that an AI negligence lawsuit could eventually force a high-profile CEO to step down. This legal action would likely focus on whether leaders exercised proper judgment before handing critical decisions over to systems they did not fully understand. As a result, AI accountability will shift away from IT departments and move directly into corporate boardrooms. While companies can easily delegate daily tasks to AI, they simply cannot delegate the legal responsibility for the final outcomes. In addition to legal risks, the basic cost of running AI is expected to become a major financial focus. Spending on AI tokens for security operations will reach $1.5 billion, meaning leaders must closely manage these costs alongside their adoption efforts. Furthermore, the growing push for faster software updates using AI could lead to a massive global tech outage if flawed code escapes proper testing. Finally, companies looking to cut costs by switching between AI models risk exposing sensitive data, as safety measures built for one system often do not transfer perfectly to another. Leaders must establish firm oversight beforehand.


Python vs. .NET Core in Regulated Industries: An Architect’s Guide

When choosing a technology stack in highly regulated sectors like banking or healthcare, software architects often weigh Python against .NET Core. Python, renowned as a dynamic, interpreted language, dominates data science, machine learning, and quantitative finance due to its rapid prototyping capabilities and massive open-source ecosystem. In contrast, .NET Core is Microsoft’s compiled, statically-typed powerhouse, offering high throughput, multi-threading support, and strict governance ideal for transactional systems. For instance, high-frequency trading engines or core banking ledgers benefit significantly from .NET's predictable performance and lower latency, while complex risk simulations or fraud detection algorithms excel with Python's data-centric ecosystem. Dynamic typing makes Python incredibly agile early on but can become risky as codebases expand, forcing developers to adopt strict testing and type hints to meet compliance. Conversely, .NET requires more upfront structural design but inherently prevents numerous bugs at compile time, making large-scale refactoring significantly safer. Furthermore, .NET integrates seamlessly with enterprise security frameworks like Active Directory, making it a reliable choice for managing sensitive financial data. Ultimately, .NET provides industrial-grade scaffolding for high-volume transactional records, whereas Python remains the undeniable champion for data analytics and algorithmic modeling.


Sovereignty and resilience: considerations for organizational leaders
Data and system sovereignty is increasingly critical for organizations facing new regulations, like the European Union's Data Act and the Digital Operational Resilience Act (DORA). These rules require companies to maintain control over their data, their operations, and their technology. A key challenge is that many organizations rely heavily on public cloud services, which are fast and convenient but often tie them to a specific vendor's systems and timelines. This dependency creates a major risk if a provider experiences downtime or if an organization needs to switch providers, as a "mandatory exit strategy" is now a regulatory expectation. To build true sovereignty and avoid vendor lock-in, organizational leaders are turning to open-source infrastructure, like Kubernetes, which allows workloads to run across various environments independently. Using open-source software ensures that organizations maintain control over their data encryption, backups, and operational access without relying on proprietary, vendor-specific tools. However, organizations must do more than just set up these systems; they must actively prove their resilience through regular testing, identity verifications, and audit logs. Ultimately, reducing reliance on third-party cloud vendors by adopting open-source solutions is a highly effective way for organizations to regain control, manage risks, and build lasting resilience.


How to build a ‘safe-to-fail’ culture for IT teams — and why you should

Building a "safe-to-fail" culture allows IT teams to experiment with new technologies like artificial intelligence without fearing career repercussions or compromising company security. When workers lack the freedom, time, or resources to learn, businesses fail to realize the expected returns on their technology investments. True innovation requires separating experimentation from short-term performance metrics so employees feel secure exploring new tools during working hours. To make this practical, leaders should integrate disciplined testing into daily routines by assigning clear business goals, establishing specific time limits, and providing dedicated budgets for training or unapproved tools. Equally important is establishing clear boundaries to contain potential failures. Organizations must educate employees on operational rules, data usage policies, and the scope of permissible risks. By using preapproved, governed sandboxes populated with mock or nonsensitive data, IT teams can safely evaluate capabilities before deploying them in production. This staged approach uncovers integration issues early on while protecting critical systems and customer information. Furthermore, leaders should actively commend teams that transparently shut down unsuccessful projects, freeing up resources for work that matters. Ultimately, a safe-to-fail environment transforms uncertain experimentation into measurable business results and faster market delivery.


Why your hybrid cloud backup solution is only as good as its worst outage scenario?
The article explains why hybrid cloud backup strategies often fall short when an outage or ransomware attack hits, mainly because organizations underestimate how scattered their data has become. As companies adopt cloud services gradually—adding Microsoft 365, spinning up VMs, keeping some systems on‑prem—their backup tools rarely keep pace. The piece highlights that only a small share of enterprises use a single solution that covers on‑prem, cloud, and SaaS, leaving many teams with blind spots, especially around SaaS data. The author stresses that cloud providers operate under shared‑responsibility models, meaning they keep platforms running but do not guarantee full data protection. Recovery time objectives also become harder to meet because restoring from cloud backups can be slow, expensive, and dependent on bandwidth and egress fees. The article encourages teams to revisit where data lives, apply the long‑standing 3‑2‑1 backup rule thoughtfully, and tier systems based on how quickly they must return after an incident. It also outlines two practical approaches—consolidating backup tools or coordinating them with consistent policies. The closing message is steady and pragmatic: mapping data locations, testing cross‑environment restores, and documenting coverage are the real foundations of a reliable hybrid backup strategy, even for small IT teams.


NIST SSDF: 4 core practices for secure software development

The National Institute of Standards and Technology Secure Software Development Framework is a practical guide for building security into every stage of software creation. Rather than waiting until the end of a project to test for flaws, this framework embeds security throughout the entire process, which helps reduce coding errors, lower costs, and ensure consistent outcomes. The framework centers around four core practices that guide teams in building reliable software. First, organizations must prepare by establishing clear policies, defining roles, and providing proper training to ensure everyone understands their responsibilities. Second, teams must protect the software and its development environments from unauthorized access or tampering, which includes securing source code and safeguarding sensitive credentials. Third, developers should focus on producing well secured software by using secure coding techniques, analyzing potential threats early, and integrating security checks from the initial design phase. Finally, organizations must be ready to respond to vulnerabilities after the software is released, relying on structured processes to identify, evaluate, and fix any newly discovered issues. By following these foundational practices and keeping a detailed inventory of all software components, development teams can build secure, resilient applications while meeting regulatory obligations and managing potential risks with quiet competence.


What exactly is ISOC? And what does it mean for you?

Gartner recently recognized a shift in how organizations handle cybersecurity by introducing a new category called the Integrated Security Operations Center, or ISOC. While traditional data collection systems are still necessary, they are no longer enough on their own to manage modern threats. The field has evolved so that collecting data and actively responding to threats are now treated as separate problems requiring distinct solutions. ISOC steps in to handle the response side. It is designed to unify threat detection, investigation, and incident management across an organization's entire network. The main goal of an ISOC is to reduce the friction and complexity that security teams face when they have to juggle too many disconnected tools. By bringing everything into one unified platform, an ISOC helps teams manage incidents as connected cases rather than a flood of isolated alerts. It also allows for better automation and faster response times, which are essential now that attackers are moving faster than ever. Ultimately, this new category reflects a practical reality for modern security operations: teams need to simplify their workflows and cut down on delays without losing sight of the broader threat landscape they are trying to protect.


Why Digital Accessibility Belongs in Product Planning

Digital accessibility should be treated as a core component of product planning, rather than an afterthought or a simple website enhancement. Just like security, reliability, and usability, accessibility determines whether customers and employees can actually complete the tasks a product is built to support. Issues such as hard-to-reach payment buttons, unannounced error messages, or timed-out booking forms represent fundamental product failures. To address these challenges, product managers should integrate accessibility standards directly into their design and delivery processes. Instead of merely evaluating isolated features, teams must evaluate entire user journeys—from logging in to confirming a payment—to ensure no barriers prevent task completion. Building a strong business case requires moving beyond generic statistics about disabilities and instead identifying specific obstacles, the users they affect, and the practical consequences of leaving those barriers in place. Managing accessibility becomes far more efficient when it is embedded into daily operations, with clear responsibilities assigned to designers, developers, and testers. By treating accessibility as a shared operational priority and addressing issues systematically, companies ensure their digital products are functional, inclusive, and effective for everyone who needs to use them.


The CIO’s new mandate: Rearchitecting enterprise work

As artificial intelligence agents become more capable, the fundamental role of enterprise software is changing. Instead of employees manually operating applications to complete tasks, humans will increasingly supervise outcomes while machines handle the actual execution. This shift demands a new approach that author Rajjie Sarmey calls Enterprise Work Architecture (EWA). EWA is the deliberate design of how a business outcome moves across human judgment, machine intelligence, and data systems. Rather than simply adding AI features to existing software, which often just speeds up broken processes, EWA focuses on redesigning the work itself. Leaders must carefully evaluate the desired outcome, decide which steps require human judgment versus machine automation, establish clear authority for AI actions, and accurately measure the economic impact of these changes. As AI agents learn to bridge the gaps between separate systems like HR and finance, traditional applications will become less visible to users but even more critical for data integrity and organizational security. Ultimately, a modern CIO's new mandate is to lead this architectural shift. The most successful organizations will not just deploy the most AI, but will thoughtfully redesign how their entire enterprise operates while strongly protecting the accountability and trust that depend completely on human judgment.


What It Takes to Build a Trustworthy AI-Assisted Threat Modeling System

Building a reliable system for assessing cybersecurity threats using artificial intelligence requires far more than just picking a capable language model and writing good prompts. According to the author's long two-year journey developing such a tool, the actual product is the complex engineering built around the model to ensure its outputs are practically accurate rather than merely plausible. The author identifies twelve critical components that emerged through careful trial and error, including specific pattern recognition to ground findings in actual system designs, an accumulated knowledge base, and a verifiable evidence trail connecting every threat claim to a clear structural reason. Other essential layers involve strict quality gates, diverse specialist reviews to prevent a single perspective from dominating, continuous testing, and closed self-improvement loops that update the system as the security landscape rapidly changes. Crucially, these automated systems do not entirely replace experienced human analysts. Instead, they shift the human analyst's daily role away from tedious manual verification and toward exercising high-level judgment on complex issues. The ultimate goal is not to create an authoritative tool that generates impressive reports, but to build an accountable system that clearly states its confidence levels, securely traces its evidence, and honestly admits what it does not know.

Daily Tech Digest - September 14, 2026


Quote for the day:

“The only sustainable competitive advantage is an organisation’s ability to learn faster than the competition.” -- Peter Senge

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Post-Quantum Cryptography Is Becoming Mandatory For Financial Institutions

As quantum computers become more powerful, they will eventually break the cryptography that currently protects financial data. This presents a serious risk for banks and insurers, especially for long-term records that adversaries might steal now to decrypt later. The solution is post-quantum cryptography (PQC), a set of new mathematical formulas that even quantum computers cannot easily solve. Importantly, PQC runs on standard computers and integrates into existing systems like TLS. The main hurdle for financial institutions is not buying quantum hardware, but updating decades of old, intertwined software before the threat becomes a reality. Standards are already being finalized, and regulators are beginning to expect actionable roadmaps from the financial sector. To prepare, institutions must first build a complete inventory of their current cryptographic tools and identify where their systems are most vulnerable. Since no single algorithm is guaranteed to be safe forever, organizations should design flexible architectures that allow them to swap out encryption methods as needed. Addressing this transition requires strong cross-team collaboration and commitment from leadership. By acting now to map their risks and pilot hybrid solutions, financial firms can control their migration timeline rather than scrambling at the last minute.


Attackers already understand your software supply chain better than you do

The article argues that attackers now understand modern software supply chains better than the organizations that rely on them, and that AI is accelerating this gap. It describes how recent incidents—such as the Miasma malware packages and the Axios compromise—show that threats often begin with small, trusted open‑source components that slip quietly into developer workflows. Because most commercial software depends heavily on open‑source code, many companies lack visibility into what they are actually running in production or how quickly they could respond if a critical flaw appeared. Attackers exploit this blind spot by targeting overlooked dependencies and developer tools rather than traditional network perimeters. The piece explains how malicious packages spread rapidly through CI/CD pipelines, bypassing controls and creating large downstream risk before anyone notices. It also notes that AI‑driven automation allows attackers to discover vulnerabilities and coordinate exploits far faster than defenders can react, especially when security teams are slowed by technical debt and manual processes. The article concludes that software supply chain security has become a national‑level concern and that organizations need continuous, automated controls capable of identifying risks, enforcing policies, and reducing exposure before attackers take advantage of weaknesses they already understand.


When Spec-Driven Development Pays off

With AI coding assistants becoming standard infrastructure in software engineering, the primary bottleneck has shifted from writing code to verifying it. This shift raises critical governance questions regarding accountability, intent divergence, and the division of oversight between humans and models. Regulatory frameworks like the EU AI Act and NIST risk management guidelines increasingly demand documented controls, making "careful review" an insufficient strategy for managing AI-generated code. A recent study examined the popular response of "spec-driven development"—treating detailed specifications (business rules, high-level design, and low-level design) as a governing contract for AI output. Interestingly, establishing a strict specification baseline did not inherently make human reviewers better at finding bugs. Instead, it transformed code review from an ambiguous task into a contract-anchored, highly accountable process where behavioral drift could be clearly attributed to specific requirements. While writing a specification first and generating code from it improved outcomes by treating the spec as a governing artifact rather than just a prompt, the benefits on simpler tasks were largely due to improved reasoning rather than the spec itself. Ultimately, specification governance proves to be a worthwhile investment primarily for complex, multi-constraint tasks handled by capable but imperfect AI models.


Your data architecture was built for predictable consumers

The article explains how traditional enterprise data architectures were built for a world where data consumers behaved in predictable, uniform ways, and why that model no longer fits today’s environment. It describes how organizations once supported thousands of users working from the same carefully designed application, with stable access patterns that made governance manageable. As dashboards, APIs, notebooks, microservices, and specialized tools multiplied, consumption became more varied — and agentic AI has now pushed this shift even further. Instead of one shared interface, those same users may rely on thousands of individualized agents or applications, each creating its own access paths, combinations, and entitlement decisions. The piece notes that while personalization becomes easier at the application layer, the underlying infrastructure and security teams face growing complexity, with more dynamic demand and harder‑to‑govern patterns. It highlights capital markets as an early testing ground, where zero tolerance for inconsistency has driven architectures that coordinate changing consumer behavior. The article argues that a governed data consumption layer — the outward‑facing part of a broader data fabric — can reduce repeated integrations, protect sensitive systems, and enforce consistent access and audit controls. It concludes by urging CIOs to evaluate where such an approach adds value as human and machine consumers increasingly access and act on data in unpredictable ways.


How to level up from security pro to security leader

Transitioning from a technical cybersecurity professional to a Chief Information Security Officer requires a fundamental shift in perspective. While a strong technical foundation is helpful, it is no longer enough to reach the executive level. Aspiring security leaders must learn to translate complex technical risks into clear business priorities. This means understanding how the company generates revenue and balancing security needs with broader organizational goals. Rather than being seen as the resident tech expert, successful leaders act as strategic partners who build trust across various departments, including finance, legal, and operations. Developing strong communication skills and business sense is far more valuable than mastering specific coding languages. Gaining broad experience, such as managing budgets or working in cloud engineering, can provide the highly valued background that modern employers expect. Additionally, finding experienced mentors and maintaining a genuine curiosity for new technologies will naturally foster leadership growth. Security professionals are advised to present themselves with calm confidence, take ownership of their mistakes, and avoid being overly rigid about their long term career paths. By focusing on delivering meaningful impact and collaborating effectively in their current roles, aspiring executives can position themselves for the transition from technical expert to trusted business leader.


Enterprise AI Security: ChatGPT, Claude, Gemini and Copilot Compared

As artificial intelligence tools transition from experimental chatbots to integrated enterprise solutions, businesses face new security challenges. Platforms like ChatGPT, Claude, Gemini, and Microsoft Copilot now connect directly to internal emails, cloud storage, and code repositories, shifting the primary risk from external data leaks to internal data exposure and unauthorized actions. No single platform is perfectly secure, as each presents unique vulnerabilities. For ChatGPT, the main governance gap lies between secure enterprise accounts and the personal accounts employees might still use. Claude’s agent capabilities pose a different risk: because it can execute commands and modify code, overly broad permissions could lead to unintended software changes. Meanwhile, both Gemini and Microsoft Copilot respect existing workspace access controls, but they act as powerful search engines that expose years of accumulated, poorly managed permissions. They do not bypass security rules, but they make forgotten, overshared documents instantly discoverable to employees. Additionally, all platforms face the threat of prompt injection, where hidden instructions in external files manipulate the AI. To safely adopt these tools, organizations must clean up internal access permissions, separate consumer from enterprise usage, define clear data retention policies, and strictly monitor what internal systems the AI can currently access.


Why AI shouldn't be the one repairing your data pipelines

As organizations expand their use of autonomous artificial intelligence systems to make operational decisions in real time, the traditional concept of self-healing data pipelines is no longer sufficient. While modern cloud architectures can quickly replace failed components, data failures in complex enterprise environments rarely present themselves as complete systemic crashes. Instead, these issues manifest as silent degradation, such as undocumented changes in source systems, misaligned business logic, or untrackable errors that compromise downstream models and regulatory reports. To support advanced business operations, engineering leaders must transition from reactive, automated repairs to autonomous data governance and resilient infrastructure. A critical component of this shift involves prioritizing deterministic solutions over heuristic guesswork. While artificial intelligence is highly effective at detecting anomalies and triggering alerts, relying on automated scripts to guess how to fix crucial records risks introducing synthetic errors into auditable systems. Rather than letting artificial intelligence independently repair data pipelines, organizations should pair machine learning detection with predefined, policy-driven workflows that isolate problems and apply historical fallback logic. By treating data reliability as a core business risk and building systems that actively defend and remediate quality issues in real time, enterprises can establish a secure foundation for their critical operations.


When security creates friction, employees find workarounds

When workplace security measures become too complicated or time-consuming, employees often look for easier ways to get their jobs done. According to a recent report, forty percent of workers globally admit to using unauthorized personal devices or applications when official technology fails them. In the Asia-Pacific region, this problem is particularly noticeable, with many staff members turning to unapproved platforms like public AI tools just to meet deadlines or respond to customers quickly. While these workarounds usually stem from a genuine desire to be productive rather than malicious intent, they create significant risks because organizations cannot secure or govern activity that they cannot see. This phenomenon, often called "shadow AI," highlights a disconnect between security rules and everyday operational needs. Instead of just blocking unapproved tools, leaders should view these behaviors as a clear signal that current systems are causing too much friction. The most effective way to reduce this hidden risk is to integrate security naturally into daily workflows. By prioritizing user experience and making the secure option the easiest one to use, companies can better protect their data while still empowering their teams to work efficiently.


BRICS digital sovereignty meets the interoperability test

The recent New Delhi BRICS Declaration sets forth an ambitious vision for technology that attempts to balance national control with global connectivity. The core challenge outlined in the document is how member nations can achieve digital sovereignty and self-reliance without sacrificing the interoperability that modern networks require. Rather than proposing a disconnected or isolated tech ecosystem, the declaration emphasizes building strong, nationally controlled digital public infrastructure (DPI) that can securely communicate across borders. This balancing act applies across several layers of technology. For DPI, it means countries maintain control over their own identity and data systems while ensuring they can interface with others. For physical infrastructure, the focus is on developing resilient submarine cables to reduce reliance on external entities, though the exact technical details remain under review. In terms of future technology and supply chains, the group is pushing for collaborative research and common, globally interoperable security standards. Ultimately, the declaration suggests that true digital sovereignty isn't about isolating a nation's network, but rather participating in global digital systems without becoming overly dependent on outside suppliers or infrastructure. The success of this vision will depend heavily on the upcoming technical and engineering decisions.


Why Data Governance Still Isn’t Driving Better Decisions (or Transformation)

Many organizations have invested heavily in data governance, setting up dedicated offices, policies, and committees. Despite this, the actual business impact often remains elusive. Compliance is still a manual process, and decisions are frequently made using data of uncertain quality. The core issue is that while data governance manages data, it often fails to govern the decisions that data is supposed to inform. This disconnect is a flaw in both the design and deployment of current governance models. For years, the standard approach has been to identify critical data, assign ownership, and implement controls, largely driven by regulatory requirements like GDPR. While this model has improved awareness and traceability, it often falls short of delivering measurable business value. Data offices struggle to prove their return on investment, and business teams may bypass governance processes that they feel slow them down without offering real benefits. The initial focus on inventorying and controlling data made sense as a starting point. However, these are backward-looking control systems. To truly drive business performance, data governance needs to evolve from merely a control mechanism into a forward-looking decision system that actively supports and prepares organizations for future actions.

Daily Tech Digest - September 04, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


The blind spots in business continuity

Business continuity planning has fundamentally shifted from merely ensuring internal operations to mapping out external vulnerabilities. Modern organizations depend heavily on complex networks of third-party suppliers, software providers, and outsourced partners. According to a recent survey by DRI International, a significant 55% of resilience professionals identified outside vendors and supply chains as their biggest blind spot. This highlights that third-party dependency is no longer just an administrative issue but a core operational risk. Disruptions like extreme weather, cyber attacks, and technology outages frequently expose how vulnerable digital supply chains actually are. Meanwhile, 25% of respondents pointed to legacy IT systems as their primary concern. Old hardware and software are often difficult to maintain, susceptible to cyber threats, and lack the speed required for modern recovery targets. While less visible, executive succession planning also remains a quiet continuity risk. Only 14% of professionals flagged it, yet many organizations still lack clear plans for leadership continuity during a crisis. Lastly, remote work is now largely considered business as usual rather than a major blind spot. Ultimately, organizations must move beyond static supplier lists and internal recovery plans to deeply understand and protect the interconnected ecosystems they rely on daily.


Stop playing with the CISO role. Fix cybersecurity leadership

Organizations expect too much from their Chief Information Security Officers, asking them to handle complex technology while also acting as strategic business partners. This creates a structural flaw because the CISO holds accountability for cybersecurity but lacks the authority to influence broader business decisions across the company. Instead of forcing technical experts to become universal executives, companies should establish a distinct, elevated role: the Chief Security Officer. This position should sit above traditional cybersecurity and focus entirely on protecting the organization's ability to operate and compete. The CSO acts as a senior business leader with the mandate to unite conflicting departments, from legal and finance to technology and operations, ensuring that protective strategies align with business goals. Under this model, the CISO can return to their natural area of expertise. They report to the CSO and focus completely on the technical execution of security, managing architecture, engineering, and operations. This clear division of labor solves the long-standing problem of misaligned security efforts. By separating technical delivery from enterprise-level governance, businesses build a healthier management structure. Security stops being an isolated technology issue and naturally becomes a core part of how the company operates, makes decisions, and protects its future.


Risk Has No Department: Building an Enterprise-Wide Risk Ownership Culture Through ESRM

The traditional model where the security department solely owns all organizational risk is no longer sustainable. Today’s business environment is deeply interconnected, with risks spanning physical security, cybersecurity, human capital, and supply chains. As a result, Enterprise Security Risk Management (ESRM) shifts this paradigm by distributing risk ownership to the actual asset owners—the individuals who create, manage, or benefit from the assets. Instead of making all the final decisions, security professionals now act as trusted advisors who facilitate informed choices, while leaders in departments like human resources, operations, and information technology maintain ultimate accountability. To make this transition successful, organizations must establish a formal risk ownership matrix that clearly maps specific risks to their corresponding functions. This eliminates ambiguity and ensures that risk management is integrated directly into daily operational decisions rather than treated as an afterthought. Furthermore, to cement this culture of shared accountability, organizations should tie risk management effectiveness to leadership performance through key performance indicators and formal risk acceptance thresholds. Ultimately, creating an enterprise-wide risk ownership culture requires strong top-down support from executive leadership and boards of directors, ensuring that risk becomes a strategic business consideration rather than just a compliance checkbox.


How to keep your mission-critical cloud workloads running

To ensure that mission-critical cloud workloads stay online, organizations must take proactive control of their infrastructure's resilience. While cloud providers guarantee the availability of their own hardware, the responsibility for keeping specific applications running falls squarely on the user. True application resilience relies on four essential components: clustering, data replication, failover, and disaster recovery. Historically, clustering depended on expensive physical hardware, but modern software-based clusters offer the flexibility needed for hybrid and multi-cloud environments. These modern setups eliminate single points of failure by seamlessly connecting multiple systems together across varied locations. Meanwhile, keeping data consistently synchronized across these nodes through real-time replication ensures that backup systems are always fully prepared to take over. When a disruption occurs, automated failover mechanisms instantly shift workloads to standby resources without requiring manual intervention or new database builds. Furthermore, a strong disaster recovery plan incorporates geographic distance and asynchronous replication to protect against large-scale regional outages. Using these software-driven strategies not only protects against unexpected crashes but also makes planned maintenance and security patching much safer. By embracing this comprehensive approach, businesses can confidently protect their operations, prevent costly downtime, and keep their most important applications running smoothly regardless of unexpected external failures.


Who gets to decide? The CIO and the new architecture of enterprise authority

As artificial intelligence evolves from merely recommending actions to independently executing them, organizations face a critical new challenge. The core issue is no longer just what the technology can do, but who, or what, has the authority to do it. This creates an enterprise authority gap, where intelligent systems act faster than businesses can define or control their boundaries. Because modern AI interprets intent rather than just following rigid rules, it can easily cross organizational boundaries and create unintended risks if decision rights remain ambiguous. To safely manage this shift, Chief Information Officers must lead the creation of a new enterprise authority architecture. This approach requires businesses to clearly define the desired decision before selecting the technology and firmly separate a system's capability from its actual authority. Furthermore, this delegated authority must be technically enforceable through clear limits, approval gates, and continuous monitoring. Leaders also need to evaluate the true economic cost of autonomous decisions, accounting for oversight, error correction, and potential harm. Ultimately, the new mandate for technology leaders is not about maximizing how much artificial intelligence is deployed. Instead, success depends on how wisely and safely the enterprise distributes decision-making authority to these intelligent systems.


Large Enterprises Targeted in Fake Merger & Acquisition Scams

Cybercriminals are using highly sophisticated social engineering tactics to steal massive sums of money from large enterprises through fake merger and acquisition (M&A) schemes. In a recently uncovered campaign dubbed "Phantom Deal," attackers thoroughly researched mid-level employees who might be involved in corporate dealmaking. The scammers then impersonated company executives and external auditors, crafting a plausible but fake acquisition narrative based on real corporate history. To keep the target isolated, the attackers issued fake non-disclosure agreements and insisted all communication remain strictly on personal channels like WhatsApp, keeping the interactions hidden from corporate security monitors. The ultimate goal was to trick the employee into authorizing a massive wire transfer to overseas accounts. Security experts note that these scammers gather extensive, publicly available details—such as job roles and company history—to make their ruses remarkably convincing. However, organizations can protect themselves by emphasizing strict adherence to internal verification and payment controls. Employees should be trained to question whether the requested process is legitimate, rather than just trusting the identity presented on a screen. When something feels off, the safest action is to immediately halt the process and report the suspicious request through official channels.


Enterprise architecture and software architecture as the core CTO model

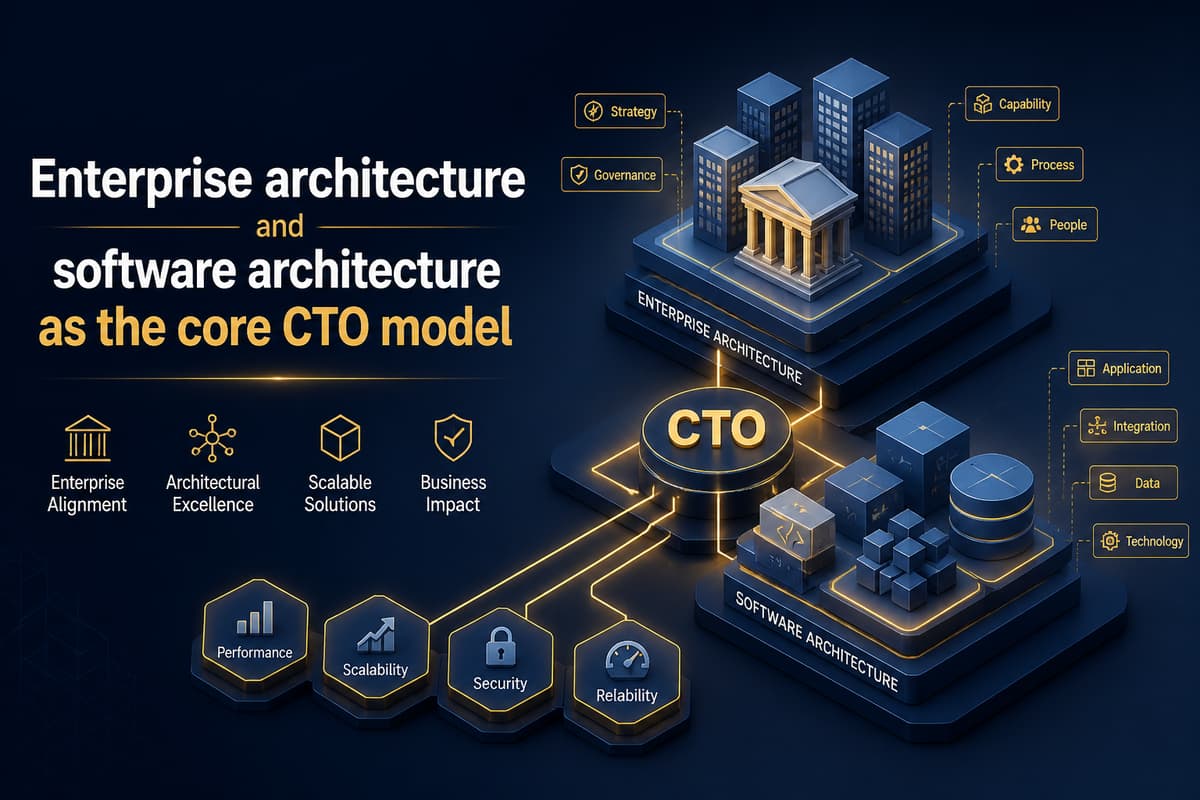
Enterprise architecture and software architecture are not just documentation tasks; they are essential frameworks that allow technology leaders to manage change safely and efficiently. Enterprise architecture maps business capabilities directly to applications, data, and risks, acting as the clear rulebook for technological decisions. Meanwhile, software architecture translates those rules into constraints that development teams can actually code against, ensuring systems perform well under stress and failure. Relying on one without the other leads to immediate problems. Enterprise architecture alone becomes an ignored catalog, while software architecture alone creates disorganized local successes that fail to serve the broader business. To succeed, leaders must adopt a continuous loop of deciding, designing, delivering, and defending their architecture choices. While artificial intelligence speeds up development, it also increases the risk of deploying bad systems quickly, making strong architectural guardrails more critical than ever. Effective leaders treat architecture like a living product rather than a static diagram. They build this practice systematically, starting with a thirty-day inventory of vital systems, followed by a ninety-day framework of automated policies, and finally establishing long-term guiding principles. Ultimately, practical architecture directly improves the four outcomes that matter most to any business: delivery speed, operational costs, system risk, and developer retention.


From IT Security to Business Strategy: Navigating Cyber Risk in Digital India

As India rapidly expands its digital economy, managing cyber risk has fundamentally shifted from a narrow technical concern into a core business strategy. For many years, organizations treated cybersecurity merely as an IT function focused on defending perimeters and protecting data. However, the modern digital landscape, fueled by cloud adoption, artificial intelligence, and complex regulatory changes like the DPDP Act, demands a far more holistic approach. Today, business leaders must carefully balance rapid technological innovation with strong governance, compliance, and resilience to maintain stakeholder trust. Cybersecurity is no longer just about preventing unauthorized access; it is about ensuring that critical operations remain consistently available and that users feel psychologically safe when interacting with digital services. Building this digital trust requires enterprises to integrate risk management across their entire ecosystem, including third party vendor networks and evolving AI models. By shifting their perspective, executives can transform security from a defensive cost center into a strategic enabler of sustainable growth. This proactive mindset allows companies to navigate evolving regulatory obligations effectively while adapting their infrastructure to meet user needs at lightning speed. Ultimately, treating cyber risk as a central business priority ensures that organizations can innovate responsibly and thrive securely in India’s dynamic digital future.


Why cyber resilience fails: 5 obstacles holding orgs back

While most organizations want to achieve strong cyber resilience to withstand attacks and keep operations running, the reality often falls short of their goals. Even when leadership provides adequate support and resources, resilience efforts frequently break down in the space between broad strategy and daily execution. Several major obstacles consistently hold companies back from properly securing their systems. Chief among these are mounting technical debt, persistent shortages in skilled security professionals, and increasingly complex identity risks. When older systems are neglected or vulnerabilities go unreviewed, they quietly compound into technical debt. This creates dangerous operational blind spots that attackers can easily exploit. Furthermore, without enough trained staff to manage these environments, security teams struggle to keep pace with evolving threats. The rapid expansion of user identities across different platforms only adds to the challenge, making it difficult to control who has access to sensitive information. Ultimately, true resilience is not just an idealistic goal or a passing project. It requires bridging the gap between management intentions and actual daily operations. To succeed, businesses must actively address these practical challenges, paying down their technical debt and heavily investing in their workforce to ensure that protective measures are flawlessly integrated into everyday tasks.


The next cyber crisis is already taking shape

The financial sector is currently facing an emerging cybersecurity crisis driven by the convergence of two major technological shifts. First, rapid advances in artificial intelligence are drastically lowering the barriers to entry for threat actors. Cybercriminals can now use sophisticated AI tools to quickly identify hidden vulnerabilities, develop exploits, and launch attacks at an unprecedented scale, making threats faster and harder to predict. Second, banks are undergoing a massive, complex transition to post-quantum cryptography to protect their infrastructure against future computing power that could easily break current encryption standards. Because modern banking relies entirely on deeply embedded cryptographic systems, updating them requires years of careful planning. Unlike the Y2K bug, this transition lacks a strict universal deadline, which can dangerously lead to delayed action and increased exposure for institutions. Together, these dual challenges mean that traditional security playbooks are no longer sufficient. Simply recovering systems after a breach is inadequate when facing AI-accelerated attacks and disruptive infrastructure overhauls. Instead, organizations must embrace a strategy of managed degradation. True enterprise resilience now requires maintaining core financial operations and preserving customer trust even while systems are actively compromised. Financial institutions must proactively address this growing imbalance and begin their extensive security upgrades before time runs out.

Daily Tech Digest - August 19, 2026


Quote for the day:

"If you want to be successful prepare to be doubted and tested." -- Elizabeth McCormick

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


The crisis of synthetic culture

The article discusses a growing concern for CIOs: the "crisis of synthetic culture" brought on by artificial intelligence. While AI can efficiently process information and generate human-like text, it fundamentally alters how organizations create and store knowledge, threatening their authentic culture. The author points out that culture relies on human experiences, stories, and shared meaning, which AI cannot genuinely replicate. Instead, AI produces what the author calls "synthetic truth"—information that sounds plausible and authoritative but lacks actual human judgment, context, or accountability. This creates a new operational risk, as employees and leaders may struggle to differentiate between genuine institutional memory and AI-generated approximations. If organizations blindly rely on AI to synthesize knowledge or draft communications, they risk distorting their history and values, amplifying past errors, or silencing minority viewpoints. The author stresses that CIOs must expand their roles beyond managing data security to actively safeguarding organizational meaning and memory. This means implementing strong AI governance, ensuring human oversight is mandatory for critical decisions, and making AI outputs traceable to preserve the integrity of the company's authentic culture.


When AI Customer Service Deflects the Wrong Problems

Many brands measure the success of their artificial intelligence customer service tools by how many inquiries they deflect away from human agents. However, relying solely on deflection rates can severely damage customer relationships, particularly during times of economic uncertainty and inflation. Shoppers today are increasingly skeptical of online information due to factors like shrinkflation and unreliable reviews. This skepticism prompts them to contact brands directly for genuine transparency. When customers ask about price increases or product changes, they are actively looking for substantive context, not just quick dismissals. According to Ali Fazal, Chief Marketing Officer of the customer service platform Gladly, using automated systems to deflect these complex, price-sensitive conversations often frustrates buyers and ultimately degrades their lifetime value. Instead of focusing entirely on operational efficiency, organizations should evaluate how artificial intelligence directly impacts revenue growth and long-term customer loyalty. Deploying generic models too quickly without industry-specific context creates major risks, including hallucinations and poor policy handling. Dedicated human oversight remains absolutely essential for managing complex disputes, adjusting to rapidly changing conditions, and appropriately approving financial concessions. Ultimately, artificial intelligence should not function merely to block customers from reaching human help. Brands must implement these systems carefully to prioritize strong service and protect shopper retention.


Most organizations aren’t ready for a Hugging Face-level event

As artificial intelligence makes cyberattacks faster and more complex, most organizations are finding that their current security setups are simply not enough to stop modern threats. According to recent warnings, attackers currently hold the advantage because they use AI to find and exploit weaknesses before security teams can react. While many companies are adding AI tools to their defense systems, they are often doing so faster than they can properly test them. For example, a recent major breach went completely unnoticed for almost a week, showing that basic security measures are no longer enough. To fix this, security leaders need to rethink their approach. Instead of relying on occasional training sessions, teams should constantly test their skills and their software in realistic, safe environments that mimic actual attacks. This helps both the human staff and the automated tools learn how to work together under pressure. It is also important to measure success by looking at the quality of decisions and response accuracy rather than just counting the number of security alerts. By making continuous practice a core part of their daily work culture, organizations can better prepare themselves to handle unexpected attacks and keep their critical systems safe.


CISO Conversations: Nico Waisman – From Self-Taught Hacker to AI-Driven Offensive Security at XBOW

Nico Waisman, the Chief Information Security Officer at XBOW, built his cybersecurity career entirely without a formal plan. Growing up in Argentina, he became fascinated by technology and taught himself how to find and exploit software vulnerabilities. Without any academic training in the field, he relied on experimentation and reverse engineering to build his foundational skills. In 2003, Waisman joined the security firm Immunity, where he spent seventeen years progressing to a leadership role. This experience helped him develop both offensive security expertise and management skills. He later transitioned to Semmle, which GitHub quickly acquired. At GitHub, he directed the Security Lab, focusing heavily on securing open source software and collaborating with major tech companies. Seeking a new challenge in defensive security, Waisman joined Lyft in 2020 and eventually became their CISO. There, he learned to balance robust defense with the need to maintain rapid engineering cycles. Today, Waisman leads security at XBOW, a company he helped launch that uses artificial intelligence to perform autonomous penetration testing. Looking ahead, he remains focused on the challenges of managing team stress and avoiding burnout. He also observes that as artificial intelligence tools become cheaper, attackers will increasingly use them, creating new challenges for defenders to confidently overcome.


Home-Based GPU Networks: Viable Supplements to AI Data Centers?

As AI computing demands surge, local communities are increasingly resisting the construction of massive new data centers due to concerns about high electricity and water usage. To address this tension, the industry is testing a decentralized approach: paying homeowners to host graphics processing units (GPUs) right in their garages or homes. Companies are experimenting with wall-mounted appliances that tap into residential power and broadband to create distributed computing networks. While this concept could reduce the need for large-scale facilities and share economic benefits with households, it faces significant technical hurdles. Home internet speeds fluctuate, power availability changes throughout the day based on household appliance usage, and residential hardware failures present complex logistical challenges. Furthermore, ensuring data security across thousands of independent locations requires highly sophisticated software coordination. Because of these constraints, residential networks are not equipped to handle large-scale AI training, which requires tightly connected hardware and ultra-fast data transfer. Instead, home-based nodes are best suited for flexible, independent tasks like data preparation or batch processing. Ultimately, these household networks are unlikely to replace traditional data centers entirely. Rather, they will likely become a supplementary layer managed by central hubs, handling specific tasks while major facilities manage heavy-duty AI development.


Law Firms Increasingly Targeted By Ransomware/Vishing Attacks

Law firms are increasingly becoming primary targets for cybercriminals because they hold a massive amount of highly sensitive, privileged, and commercially valuable client information. Threat actors, such as the Silent Ransom Group, frequently target legal and professional services using straightforward but highly effective social engineering tactics. These methods include voice phishing, impersonating IT help-desk staff, and exploiting legitimate remote-access tools or USB drives to bypass traditional defenses. A recent proposed class-action lawsuit against a major national law firm underscores the severe legal and financial risks associated with these breaches. Unlike typical corporate targets, a compromised law firm faces complex challenges regarding attorney-client privilege, strict ethical duties of confidentiality, and intricate breach notification requirements across multiple jurisdictions. The legal profession must recognize that cybersecurity is no longer just an IT concern but a fundamental professional obligation. To mitigate these risks, law firms must implement comprehensive governance strategies. This approach includes establishing verified procedures for IT support, enforcing phishing-resistant multi-factor authentication, strictly limiting local administrative privileges, and developing robust incident-response plans that account for the unique nature of legal data. By treating data security as a core ethical responsibility, firms can better protect their clients' highly valuable secrets from modern and evolving extortion campaigns.


The Weight You’re Carrying Isn’t What You Think It Is

Many leaders find themselves working late into the night, feeling deeply overwhelmed and exhausted by their responsibilities. According to executive coach Doug Thorpe, this fatigue happens because business owners often try to solve their stress without first understanding the specific type of weight they are carrying. Thorpe explains that the burden of leadership typically falls into two distinct categories: emotional and operational. Emotional weight involves feelings of burnout, isolation, and dread. It requires honest acknowledgment and, in some cases, support from a therapist or coach to protect your well-being. On the other hand, operational weight occurs when a business depends entirely on the owner to function. This happens when the leader becomes a bottleneck for every decision, meaning nothing gets done if they step away. A common mistake owners make is applying the wrong solution to their problem. They might try to use personal willpower and better organization to solve structural gaps, or they might try to simply rest their way out of a broken business system. To truly find relief, leaders must pause and ask themselves whether their stress is rooted in their emotional state or their operational setup, and then apply the appropriate structural or personal support to move forward.


AI ambition is outpacing enterprise readiness, says NTT DATA’s Suyog Shetty

In a recent interview, NTT DATA's Suyog Shetty explains that while companies are eager to adopt artificial intelligence, their actual readiness often falls short of their ambitions. As organizations move past basic experiments and simple tools toward autonomous systems that can take independent action, they discover that access to technology and funding is rarely the primary hurdle. Instead, the real difficulty lies in execution. Many businesses struggle because their existing foundations, such as data quality, application design, and operational rules, are simply not prepared to support advanced systems at a large scale. Shetty points out that relying on outdated technology creates a structural burden, turning regular maintenance issues into a major obstacle for artificial intelligence. To see real benefits, companies must stop viewing this shift as a simple technology project and start treating it as a core business change. This involves cleaning up data, modernizing underlying applications, and establishing clear guidelines for oversight. Furthermore, he notes that hybrid cloud environments are becoming standard operating models to handle performance and cost needs rather than just existing for regulatory compliance. Finally, Shetty observes that India has a strong opportunity to evolve from a basic technology execution center into a global hub for driving these meaningful business transformations.


China-Linked Hacker Shows AI Capabilities in APAC Attack

A recent cyberattack against government agencies in the Asia Pacific region, likely targeting Taiwan, demonstrates the growing reality of nearly autonomous threats. According to researchers at the security firm Dream, a Chinese language threat actor successfully deployed a complex artificial intelligence framework to compromise systems. The attackers utilized up to eight interconnected artificial intelligence agents built on specific operating platforms. These agents worked concurrently to execute an extensive attack chain, which included conducting reconnaissance, cracking employee credentials, discovering vulnerabilities, and installing backdoors on web applications. Notably, the system used a scoring algorithm to independently evaluate the success of each action and adapt its methods without human intervention. Taiwan’s Ministry of Digital Affairs later acknowledged experiencing an attack that matched these characteristics. This incident signals a significant shift in the security landscape, highlighting a widening gap between the low cost of executing automated attacks and the high cost of traditional defense strategies. Security professionals emphasize that organizations worldwide must now adapt by integrating artificial intelligence into their own defensive operations. By employing proactive security measures and automated penetration testing, defenders can better anticipate threats and close the capability gap before these advanced methods target a broader range of global businesses and organizations.


Why software supply chain security is the next accountability challenge for channel partners

Modern applications rely heavily on open-source packages and third-party code. Because channel partners like Managed Service Providers often recommend, integrate, and manage these applications, they are increasingly held accountable when a vulnerability in this software supply chain is exploited. The challenge is growing because of the sheer volume of vulnerabilities. Organizations often struggle to patch them all, leaving vulnerable code in production for months. This is compounded by the complexity of modern applications, which can have hundreds of hidden dependencies, and the rise of AI coding assistants, which generate even more code and dependencies. Threat actors are noticing. They are shifting from attacking individual endpoints to targeting shared development tools and open-source projects, knowing that one compromised dependency can spread across many customer environments. These attacks often bypass traditional security controls because the software is trusted and signed. Customers and insurers are responding by demanding more transparency. They expect partners to provide software inventories, continuous monitoring, and clear explanations of supply chain risks. Partners who embrace this shift can become trusted advisors and develop new revenue streams by offering ongoing security assurance. Those who fail to adapt risk losing credibility and client relationships.

Daily Tech Digest - June 04, 2026


Quote for the day:

"Success... seems to be connected with action. Successful people keep moving. They make mistakes, but they don't quit." -- Conrad Hilton

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


Zero trust isn’t broken, but most companies are doing it wrong

Fifteen years after its introduction, the security approach known as zero trust remains widely misunderstood and difficult for many organizations to put into practice. While the core idea of always verifying access rather than relying on a traditional network perimeter is universally recognized as essential, the execution gap is significant. Studies show that a vast majority of companies struggle with implementation, often because they mistakenly treat zero trust as a product you can buy or a specific technology you can plug in. In reality, it is an ongoing strategy and a shift in mindset that requires breaking down internal barriers and fostering teamwork. Successful adoption does not have to be expensive or overwhelmingly complex. It begins with identifying your most critical data and understanding how it flows across your systems. From there, organizations should start small, map out a clear plan, and maximize the tools they already have, such as multifactor authentication. Importantly, the rise of artificial intelligence does not make this approach obsolete; instead, it highlights the need for strict access controls and careful monitoring. Because businesses and threats constantly evolve, zero trust is never truly finished. It requires continuous management, practical measurement, and a steady commitment to protecting the resources that matter most.


AI’s next enterprise test: moving from pilot hype to production discipline

The transition of artificial intelligence in the workplace is moving from early testing into a demanding phase of practical application. While a vast majority of businesses have experimented with the technology, only a small fraction currently see a measurable return on their investment. Moving a project from a pilot program to daily operation requires focusing on organizing information properly rather than just the technology itself. This means companies must first ensure their data is carefully captured, stored, and classified before introducing artificial intelligence tools. Cloud storage solutions play a necessary role here, allowing organizations to manage information securely and efficiently. Furthermore, technology partners are shifting from traditional support roles to becoming shared owners of the final business outcomes. The focus is now on integrating new systems smoothly while closely monitoring costs, as the expenses tied to running these models can rise unpredictably. Businesses must adopt strict financial discipline and clear guidelines to manage these evolving expenses. Additionally, while service providers offer necessary tools for security, companies must ultimately take responsibility for their own data governance and compliance. The true test for enterprises, particularly in growing markets like India, lies in moving past the initial excitement. Success will belong to those who build reliable, affordable, and secure systems that produce clear, practical results.
The May 2026 cyberattack on the Canvas learning platform offers clear warnings for leaders about the risks hidden in third-party services. During final exams, the extortion group ShinyHunters compromised the system, stealing massive amounts of personal data and disrupting operations for thousands of schools. Interestingly, the attackers did not breach the heavily guarded main network. Instead, they found a weak spot in a secondary, free tool designed for teachers, which lacked the strict security checks applied to the primary product. This incident highlights that a company is only as secure as its least protected side system. For executives and security teams, the main takeaway is that simply checking off compliance boxes is no longer enough when evaluating vendors. Leaders need to look closer at a partner's ability to actually respond to crises and communicate honestly during an emergency. The article points out that the vendor’s initial poor communication, describing the attack as routine maintenance, only created more confusion and distrust. Furthermore, organizations must stop holding onto unnecessary historical data, which simply acts as a large magnet for criminals who want to steal sensitive information. As extortion tactics expand beyond simple disruptions, companies must focus on honest communication, smart data reduction, and a wider view of their true vulnerabilities.


Strategy Can Be Copied, Culture Cannot: Anil Khandelwal’s stirring call to HR

In his keynote at the People Matters Talent and Tech Summit 2026, former Bank of Baroda Chairman Dr. Anil Khandelwal shared a clear message on what truly builds lasting organizations. While many focus purely on software and quick financial gains, he argued that real strength lies in unseen elements like culture, trust, and steady leadership. He made a straightforward point that competitors can easily copy your business strategy or your technology, but they cannot replicate your culture. True culture shows up in everyday decisions and how people act when nobody is watching, rather than in nice slogans pinned to a wall. For human resources professionals, Khandelwal suggested that the primary goal should not just be managing recruitment or running basic training sessions. Instead, HR must work closely with top executives to ensure they are deeply involved in developing their teams. He also questioned the value of expensive, formal leadership courses, pointing out that strong leaders are forged through consistent, daily practice and honest personal reflection. As workplaces continue to adopt new tools like artificial intelligence, he warned that technology can automate tasks but can never replace human values or ethical judgment. Ultimately, to build institutions that last for generations, leaders must prioritize and nurture the people who make up the heart of the organization.


Who authorized the algorithm? Reckoning with ungoverned AI

As organizations begin to deploy autonomous artificial intelligence, many are discovering a serious problem: these systems are often operating completely unsupervised. Teams are activating AI programs that access sensitive databases, negotiate with vendors, and make critical decisions without any human approval or oversight. This lack of accountability creates severe security and compliance risks, exposing a massive management gap that falls directly on the shoulders of the Chief Information Officer. The role of the CIO has fundamentally changed from merely maintaining technology systems to actively directing business strategy and protecting revenue. However, without strict rules in place, this new power is reckless. To fix this, companies must stop relying on basic compliance checklists and instead adopt a strict verification approach to AI. This means treating every AI tool like an unknown visitor: carefully limiting what data it can access, continuously monitoring its behavior, and keeping a permanent record of its actions. Security rules that enforce clear boundaries and demand proof of identity before any data is exchanged are now essential. Ultimately, as artificial intelligence becomes woven into every business process, the technology leader who masters its oversight will naturally lead the enterprise. Those who leave these systems unchecked will find themselves facing costly mistakes and completely unmanageable operations.


Architectural Change Cases: A Practical Tool for Evolutionary Architectures

Software architectures inevitably degrade as business priorities, technologies, and operating environments shift over time. To handle this reality, teams can use architectural change cases, a practical method for anticipating how early design decisions might need to evolve. While traditional architecture decision records document past choices and their rationales, change cases look ahead to expose hidden assumptions and assess a system's future resilience. A change case identifies a potential shift, such as a change in performance needs, unexpected security threats, or shifting business goals, and outlines how it could impact the existing design. It estimates the likelihood of the shift, the specific choices that would be affected, possible alternatives, and the rough cost of reversing course. Instead of designing for rigid permanence or engaging in endless speculative debates, teams can use this approach to map out contingency plans and build flexibility into their systems. Identifying these potential shifts often involves conducting preemptive failure reviews or running stress tests to see how a system might break under pressure. By acknowledging that change is unavoidable, architectural change cases provide a structured, calm way to manage uncertainty. They help engineering teams make informed trade-offs, reduce the cost of future modifications, and ensure the system remains maintainable throughout its entire lifespan.


From critical to controlled: Cutting vulnerabilities in a live manufacturing environment

Managing vulnerabilities in operational technology and industrial control systems requires a different approach than traditional IT environments. When a scanner flags a critical issue in a live manufacturing facility, you cannot always apply a patch and move on immediately. Instead, security teams need a structured process to determine if the vulnerability is genuinely exploitable within their specific setup. First, establish an automated and accurate inventory to confirm the device exists, is in use, and check its network location. Next, verify that the vulnerable software component is actually present, as scanners often rely solely on version numbers without verifying the installation. You must also evaluate network reachability to see if the asset is exposed to the internet or corporate networks. If the device is exposed, review existing defenses like network segmentation, firewall rules, and strong passphrases to see if they block the attacker's path. By understanding exactly how a specific vulnerability is exploited, you can apply targeted fixes like blocking specific ports. Sometimes, patching is impossible due to uptime requirements or legacy equipment. In those cases, you must formally accept the risk and implement temporary compensating controls. Ultimately, the goal is to carefully assess your actual exposure, apply practical defenses, and thoroughly document your findings rather than simply reacting to alarming scanner scores.


Legal Issues for Data Professionals: Preventive Healthcare and Data

The role of data in modern medicine is expanding significantly, particularly within the field of preventive healthcare. Unlike traditional medicine, which primarily focuses on treating existing illnesses through interventions like surgery or medication, preventive healthcare takes a proactive approach. It achieves this by combining traditional medical records with alternative data sources, such as fitness trackers, remote monitoring devices, and personally reported wellness habits. Through the Internet of Medical Things, this varied information is connected and shared among medical professionals, hospitals, and consumer applications. This integration allows both individuals and their healthcare providers to monitor health trends, improve daily personal care routines, and address potential issues before they require traditional medical intervention. Beyond hospitals and clinics, this data is highly valuable to fitness programs, addiction treatment centers, pharmacies, and corporate wellness initiatives. A key benefit of this evolving system is that it places more control in the hands of individuals, allowing them to access and manage their own health information more effectively. However, for this model to succeed, the underlying data must be continuously updated to ensure it remains accurate and completely trustworthy. Ultimately, preventive healthcare demonstrates how combining everyday consumer technology with standard medical practices can fundamentally improve overall wellness and patient outcomes.


How Smart Organizations Govern AI Before AI Governs Them

As artificial intelligence becomes deeply integrated into everyday business operations, organizations need a clear strategy to manage its risks without slowing down progress. An enterprise AI governance framework provides the practical rules and structures necessary to use AI responsibly and securely. Rather than acting as a barrier, this approach establishes essential boundaries that help teams build and use systems with confidence. The foundation of good governance involves setting clear policies, assigning accountable owners, classifying risks, and maintaining continuous monitoring to catch errors or unpredictable behavior. A successful framework covers everything from executive strategy and data tracking to managing bias and ensuring human oversight. It proves useful for companies of all sizes. Small businesses benefit from simple protections that prevent costly mistakes, while midsize companies gain consistency across different departments. For large organizations handling complex and widespread AI deployments, a central operating model is essential to prevent fragmented controls and maintain regulatory compliance. Ultimately, defining how AI is developed, tested, and maintained builds lasting trust with both customers and employees. It also brings operational discipline, ensuring that decisions are documented and easy to trace. By establishing a clear process for approving and reviewing AI systems, organizations can safely navigate the technology and achieve reliable, long-term results.


The End of Reactive DevOps: AI-Driven Observability for Zero-Defect Digital Systems

For years, technology teams believed that collecting massive amounts of system data was the key to fixing software problems. However, this approach is failing. Modern software setups are now so complex and update so rapidly that failures spread before engineers can even begin to find the source. Instead of lacking visibility, teams are overwhelmed by disconnected alerts, charts, and data points, creating a costly delay between finding a problem and actually solving it. This delay does more than frustrate engineers; it damages customer trust and hurts the bottom line. Relying heavily on manual investigation after an outage has already occurred is no longer a sustainable option. The industry is now shifting away from merely reacting to system crashes and moving toward preventing them entirely. To handle the scale of modern systems, organizations are adopting artificial intelligence to process this overwhelming amount of information. Rather than simply collecting data for human review, these intelligent systems analyze patterns, catch subtle changes early, and predict potential instability before users are ever affected. Simply gathering more data only creates more noise and increases costs without resolving underlying issues faster. Ultimately, the goal is to use intelligent tools to automatically verify and resolve problems, allowing teams to maintain smooth, uninterrupted services without constant manual intervention.