Showing posts with label programming. Show all posts

Daily Tech Digest - November 04, 2026

Quote for the Day
“The team owns the process — the Scrum Master owns the improvement.”
— Henrik Kniberg
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

How good is your cloud exit strategy?

The article argues that most enterprises assume they can leave a cloud provider whenever they want, but the way systems are actually built makes that far harder in practice. A cloud exit strategy isn’t about abandoning the cloud; it’s about avoiding architectural choices that quietly lock the business into one provider. The piece explains that portability is a business requirement, not just a technical ideal. If pricing changes, regulations shift, or a region goes down, the organization should have options that don’t require a multi‑year rewrite. The article highlights four areas where lock‑in usually hides: identity systems tied too tightly to a provider’s access model, data stored in proprietary formats or managed services without a clear extraction path, networking built around provider‑specific constructs, and infrastructure‑as‑code templates that encode assumptions only one cloud understands. It stresses that using native services is fine as long as the dependency is intentional and documented. The steady message is that cloud exit architecture is about flexibility — knowing what can move, what can’t, and what trade‑offs you’re accepting before they become constraints.

Read Original Article →

Industrial AI adoption outpaces security readiness, leaving OT environments exposed to emerging threats

The integration of artificial intelligence into industrial and operational technology is happening faster than the security measures needed to protect it. While many organizations are adopting AI to improve efficiency and predictive maintenance, they often lack the tools to detect when these models or the data feeding them have been compromised. Unlike traditional cyberattacks, a manipulated AI model might not trigger standard security alerts. Instead, it often looks like a routine equipment failure, a slow loss of efficiency, or a subtle change in physical processes, making it hard to identify. Attackers can exploit these systems by feeding them bad data or manipulating the models to make unsafe decisions. Because AI relies on sensor inputs that were not originally designed with modern security in mind, the physical safety of industrial plants is at risk. To safely use AI, organizations must treat these tools as advisors rather than giving them direct operational control. They should also rely on strict engineering practices, continuous monitoring, and independent safety systems to ensure reliable operations.
Read Original Article →
Article Thumbnail

Your Tools Should Answer to the Profession

Enterprise architects are often trapped by software tools that force them into proprietary data models, making it difficult to transfer work or change vendors. Instead of software companies dictating what an architecture artifact is, the profession itself should define the standards. Using the Business Technology Architecture Body of Knowledge (BTABoK), architects can rely on open models and shared formats, ensuring that their daily work remains highly accessible and transferable. When tools adopt these open standards, they no longer need to invent custom data structures that limit flexibility. Instead, software vendors can compete on practical features like better editing, deeper analysis, and smoother collaboration. To support this shift, a formal licensing and accreditation program ensures tools faithfully read and write standard formats without quietly altering them. While experimental platforms like Ergane help test and refine these open standards, the ultimate goal is a diverse market of independent tools that all speak the same language. By taking control of the standards, architects ensure their models remain readable, portable, and relevant for years, freeing teams from restrictive vendor lock-in.

Read Original Article →
Article Thumbnail

Beyond the HR File: Governing Employee Data Under India’s DPDP Act

ndia’s Digital Personal Data Protection (DPDP) Act of 2023 changes how businesses must handle employee information, clarifying that employment itself does not grant a company unlimited rights to an individual’s personal data. While the law permits organizations to process data for specific employment purposes—such as managing payroll or protecting corporate assets—it does not offer a blanket exemption for activities like using personal phone numbers for public customer service, featuring employee photographs in marketing campaigns, or circulating full resumes to prospective clients. Employers must carefully examine the true purpose of their data collection, establish clear legal boundaries, and ensure that data is only shared or retained as strictly necessary. For uses outside essential employment functions, companies must obtain specific, informed, and optional consent without pressuring staff. To stay compliant and lower risks, organizations should document their data practices, implement strong security controls, rely on business-managed communication tools, and minimize the personal details shared externally. Ultimately, safeguarding employee privacy requires treating their data with the same careful governance applied to customer information.

Read Original Article →
Article Thumbnail

Elon Musk Says Neuralink's Blindsight Will Bring Sight to the Blind

Elon Musk recently announced that Neuralink’s second product, Blindsight, is engineering-ready and aims to restore vision for the blind, including those without sight since birth. The device works by bypassing the eyes entirely, using a camera to send visual data directly to a brain implant. This implant stimulates the visual cortex to create tiny flashes of light, forming a low-resolution map of a person's surroundings. While the hardware and robotic surgical implementation represent notable engineering progress, medical experts advise caution regarding the real-world timeline and functional results. Regulatory approval for such a complex brain implant will likely take years of rigorous safety trials. Furthermore, researchers point out that previous attempts at cortical stimulation have struggled to produce useful, patterned vision beyond simple flickering lights. For patients blind since birth, the brain often repurposes the visual cortex for other senses, complicating how these signals might be perceived. Ultimately, while Blindsight brings advanced hardware to the table, solving the long-term biological and neurological challenges of artificial vision remains a significant hurdle.

Read Original Article →
Article Thumbnail

The most popular programming languages in 2026 – and some good news on developer job growth

Recent data from 2026 shows that despite the rapid rise of autonomous AI coding assistants, the core landscape of software development remains remarkably stable. According to an analysis of multiple industry surveys, the most popular programming languages have barely shifted. Python, Java, and JavaScript continue to dominate the top three spots, while legacy systems ensure languages like COBOL and Fortran maintain a persistent presence. However, the most significant finding contradicts the widespread fear of a developer replacement crisis. Since the widespread adoption of these advanced coding tools, the month-over-month growth rate for software development jobs has actually increased. In fact, current demand for developers is actively outpacing overall job market growth. The data suggests that rather than eliminating the need for human programmers, these efficiencies may be driving new demands and altering the structure of the profession. Ultimately, the fundamental tools of the trade remain the same, and the market for developers continues to expand, proving that human oversight and architectural skills are still highly valued in the industry.

Read Original Article →
Article Thumbnail

The End Of Software Archaeology: Why The Old Rules Of System Modernization No Longer Apply

Modernizing older business software systems has historically felt like archaeology. As systems age, they accumulate layers of unrecorded choices, outdated assumptions, and quick fixes that make them difficult to update without causing unexpected failures. For a long time, developers had to manually trace how these systems worked before they could safely improve them, a slow and risky process that often took up the majority of their time. However, the approach to system modernization is changing because of artificial intelligence. Instead of manually digging through old code, engineering teams can now use AI to generate detailed maps of a system's structure. These tools analyze dependencies and business context, revealing exactly how different components interact and where vulnerabilities hide. By providing a clear picture of what relies on what, AI helps organizations decide precisely which parts of a system require an update and which reliable elements they can leave alone. This targeted approach prevents the need for complete, expensive system rebuilds, allowing companies to upgrade their technology safely, efficiently, and with much greater clarity.

Read Original Article →

Future-proofing enterprise AI: The impact of post-quantum cryptography on Red Hat AI Enterprise

As the rapid growth of generative AI collides with the emerging threat of quantum computing, organizations must rethink how they protect their data. Current encryption methods are vulnerable to "harvest now, decrypt later" attacks, where malicious actors intercept and store sensitive AI models and proprietary data until quantum computers become powerful enough to break standard security. To counter this, Red Hat is integrating new post-quantum cryptography standards into its AI platform. Rather than abruptly abandoning classical encryption, this approach uses a hybrid model, combining traditional and quantum-safe algorithms to secure data in transit. This shift fundamentally protects the entire machine learning lifecycle. During data ingestion, upgraded network connections prevent surveillance. Within automated pipelines, quantum-safe digital signatures verify software components, blocking compromised code before it runs. Finally, securely signing the trained AI models ensures that these valuable assets remain tamper-proof in storage. By embedding these advanced cryptographic defenses across the architecture, organizations can confidently build and deploy artificial intelligence without exposing their most valuable intellectual property to future quantum threats.

Read Original Article →

Digital sovereignty starts with knowing your exit

Digital sovereignty is increasingly becoming a board-level priority as organizations recognize the risks of deep dependence on single technology vendors. Triggered by geopolitical events and sudden technology restrictions, business leaders are realizing that true operational resilience requires more than just securing data; it demands a clear exit strategy from key suppliers. Rather than completely avoiding major providers, organizations are urged to build flexible, modular systems that allow them to switch services if costs spike or access is restricted. Experts recommend taking an inventory of current vendor dependencies and identifying critical areas where alternative solutions are necessary. Open-source software offers a pathway to independence, as it grants organizations the right to inspect, modify, and migrate their code without being locked into proprietary constraints. Ultimately, achieving digital resilience means negotiating exit terms before signing new contracts and treating core services like cloud computing as interchangeable utilities. By planning for departure from the start, companies can ensure that staying with a vendor remains a deliberate choice rather than a costly necessity.

Read Original Article →

The rise of AI governance: Why organisations need a new generation of risk leaders

The article argues that as AI becomes deeply embedded in business decisions, organisations need a new generation of risk leaders who can oversee how these systems are designed, deployed, monitored, and challenged. Michael Sell of GARP explains that AI governance can’t sit only with technical teams; it requires shared accountability across boards, business leaders, risk functions, technology, and HR. He highlights the growing demand for roles such as AI risk managers, governance officers, assurance specialists, and model‑risk experts, along with the need to upskill existing professionals in areas like bias, data quality, security, model drift, and responsible‑AI principles. Sell stresses that oversight must span the entire AI lifecycle and that employees should feel confident questioning AI outputs rather than accepting them automatically. He also notes that leadership must develop enough literacy to understand AI risks and their impact on strategy and accountability. The article’s steady message is that organisations cannot scale AI safely without building governance talent, strengthening human judgement, and creating a culture where people can challenge machine‑generated decisions.

Read Original Article →

Daily Tech Digest - October 29, 2026

Quote for the Day
“The most expensive software is the one that doesn’t meet the needs of its users.”
— Karl Wiegers
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

When prevention fails: Why cyber resilience is the next big test of trust

The article explains that even well‑protected organizations can be thrown into chaos when a serious cyberattack disrupts basic operations, leaving leaders unsure which systems or data can still be trusted. It argues that prevention alone is no longer enough, because no control is perfect and attackers often find ways around strong defenses. Cyber resilience, therefore, becomes the next major test of trust: the ability to keep essential functions running, recover safely, and restore confidence after an incident. The piece highlights that backups are only useful if they can be accessed securely and restored without contamination, and that recovery plans must assume that some systems — including backup environments — may be compromised. Drawing on NIST guidance, it outlines four goals for resilience: anticipating threats, withstanding disruption, recovering trustworthy systems, and adapting based on lessons learned. The article’s steady message is that resilience must be designed into systems from the start, not treated as an afterthought, because the real challenge after an attack is determining what can still be relied on.

Read Original Article →

Programming Languages and Choosing a Path

Learning a programming language is about learning how to translate your logic into a format a computer can understand. An algorithm outlines the solution to a problem, while a programming language simply provides the vocabulary and rules to express that solution. Knowing the syntax of a language will not automatically make your logic correct. Behind the scenes, languages use tools like compilers or interpreters to turn human-readable instructions into actions the computer hardware can execute. When choosing your first programming language, it is important to remember that there is no universal best choice. Languages are tools built for different jobs. For example, C++ is great for competitive programming, Java offers strong structure for enterprise systems, and Python is highly readable and ideal for data tasks. Instead of getting caught up in the search for the perfect language, beginners should pick one that aligns with their immediate goals and local support system. Learn enough basics to express your logic clearly, and then focus on mastering problem-solving, which is the true core skill of programming.

Read Original Article →
Article Thumbnail

Beyond Binary Quantum Computing: Exploring Higher-Dimensional Qudits

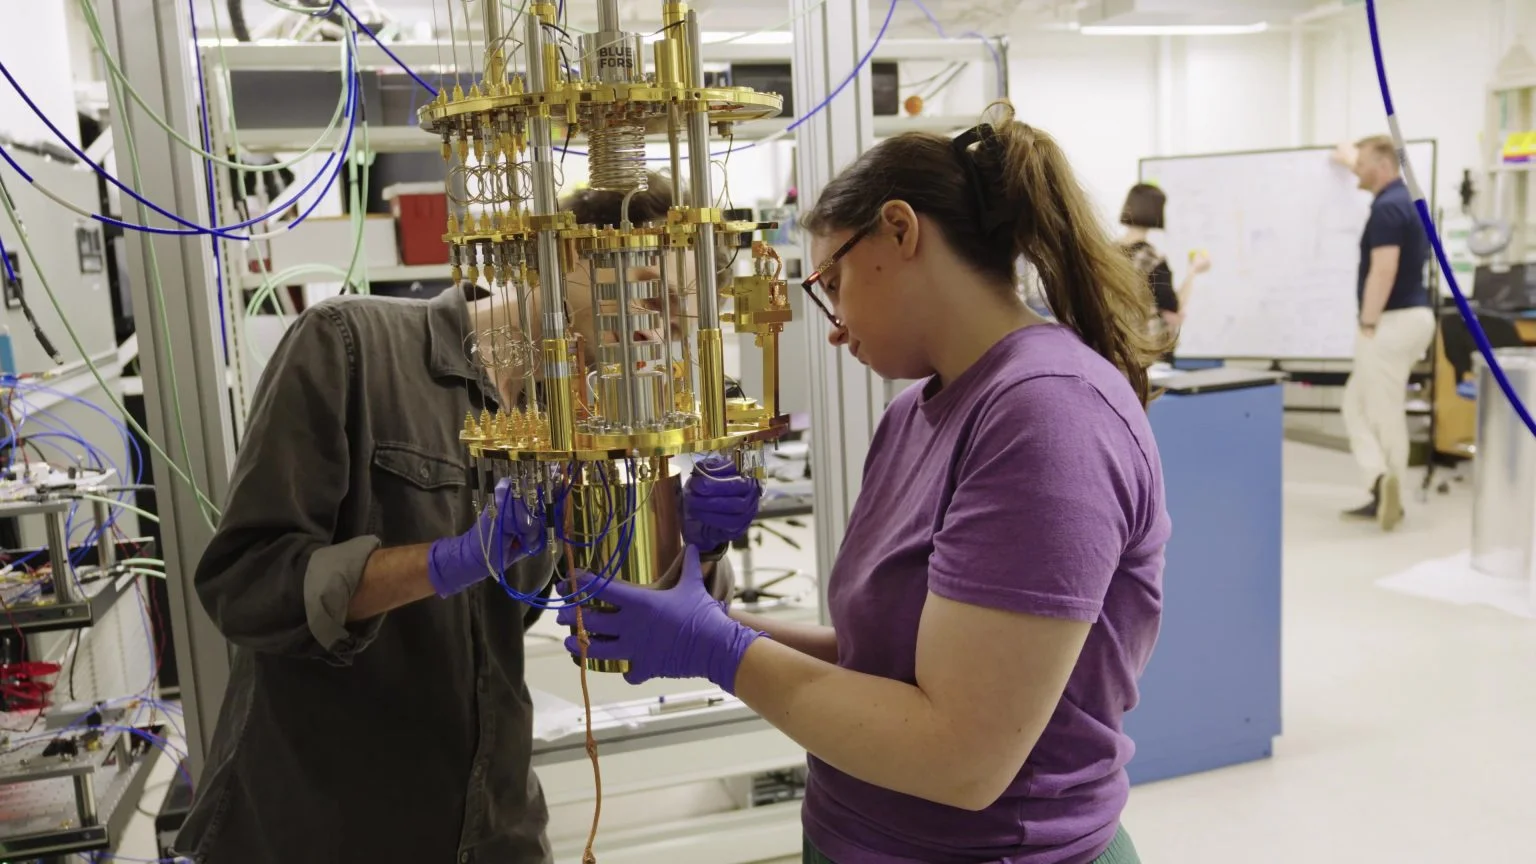
Researchers at the University of Rochester, led by Professor Machiel Blok, are exploring a new approach to quantum computing using "qudits" instead of standard qubits. While traditional quantum computers rely on binary systems with just two energy states, qudits can store information across multiple levels. This concept mimics the natural world, where atoms and molecules naturally exist in multiple states. By matching the computer's structure to the physical problem it is trying to solve, the team believes qudits could offer a much more efficient way to tackle complex challenges in chemistry and physics. To make this work, the researchers developed a new method to control all energy transitions simultaneously, essentially building a denser, high-rise structure for information rather than a sprawling, flat one. Supported by reliable cooling technology, the lab also provides practical experience for students. Ultimately, this research suggests the future of quantum computing will likely rely on a mix of different systems tailored to specific problems, rather than a single binary approach.

Read Original Article →

Why Faster Algorithms Aren't Enough to Build High-Performance Data Platforms

The article argues that high‑performance data platforms cannot be created simply by swapping in faster algorithms or adding more hardware. Performance, it says, is an architectural outcome shaped by many upstream decisions about how data is represented, moved, stored, and delivered. Faster joins or better allocators help only at the margins; they cannot fix a system that is fundamentally slow because of poor layout, excessive data movement, or inefficient memory patterns. The piece highlights that modern platforms already rely on highly optimized libraries, so the real bottlenecks often appear between those functions — for example, when unnecessary tables are materialized, when workflows shuffle large datasets across layers, or when memory allocation becomes a long‑tail problem. It also notes that parallelizing work across CPU cores is relatively easy compared to designing a pipeline that avoids hidden costs in browsers, storage formats, or intermediate transformations. The steady message is that performance emerges from dozens of coordinated design choices, and no single algorithmic improvement can compensate for weak architectural foundations.

Read Original Article →
Article Thumbnail

Why decision-making is the next frontier of modern cyber resilience

The article explains that while many organizations have strong security tools and threat visibility, they still suffer vastly different outcomes during a cyberattack. This difference comes down to decision-making. Knowing a threat exists does not automatically tell leaders how to prioritize their limited resources or which systems to fix first. Standard security models improve accountability but often fail to connect technical risks with actual business goals. To close this gap, the author suggests adopting a decision system framework that translates threat data into clear, actionable choices. This approach evaluates risks based on their real-world impact on core business functions rather than just their technical severity. By blending financial realities, trust, and business priorities into the security process, leaders can make faster, better-coordinated choices during a crisis. Ultimately, effective security is no longer just about building taller walls or spotting potential attacks; it is about having a clear, reliable method to decide exactly where to act, what to protect first, and how to recover quickly when disruptions occur.

Read Original Article →

Wazuh and AI for Enhanced SOC Workflows

As cyber threats grow more complex, Security Operations Centers face an overwhelming volume of daily alerts that can easily cause analyst fatigue and missed critical events. To manage this workload, organizations are integrating artificial intelligence to support their security teams rather than replace them. Platforms like Wazuh address this need by offering flexible AI tools that streamline threat detection and response. For cloud users, the Wazuh AI Analyst automatically reviews security data using secure cloud models to deliver scheduled, comprehensive insights on vulnerabilities and overall security posture without exposing private data. For teams with strict privacy requirements, Wazuh supports self-hosted local models like Llama 3, keeping all log data safely within the company network. Alternatively, organizations can connect external models like Claude 3.5 Haiku directly into their dashboard to provide a helpful assistant for daily tasks. By handling repetitive analysis and data correlation, these AI integrations allow human analysts to focus on making the final decisions and keeping the organization secure.

Read Original Article →
Article Thumbnail

What Should a Business Do After a Personal Data Breach in India?

The article outlines the practical steps an Indian business should take immediately after discovering a personal data breach, emphasizing that quick, organized action matters more than panic. It begins with containment: isolating affected systems, revoking compromised credentials, and stopping further data loss. The next step is verification — confirming what happened, which data was exposed, and whether the breach is still active. The article stresses that businesses must document facts carefully because regulators will expect clear evidence of what was done and when. Under the DPDP Act, organizations must notify the Data Protection Board and affected individuals when harm is likely, and the article explains that vague or delayed communication can worsen legal and reputational consequences. It also highlights the need to preserve logs, review security controls, and assess whether vendors or third‑party processors contributed to the incident. The message is steady: a breach response is both a technical and governance exercise, and businesses must combine containment, transparency, and structured follow‑up to restore trust and meet regulatory expectations.

Read Original Article →

Shadow AI vs. Shadow IT: What's the Difference?

The article explains that “shadow AI” is emerging as a distinct and faster‑moving risk compared to traditional shadow IT. Shadow IT has long referred to employees using unapproved apps or services, often exposing data by storing it in places the organization cannot monitor. Shadow AI, however, introduces a sharper problem: employees feed internal data into AI tools — sometimes through personal accounts or new AI features inside already‑approved applications — without any governance. The piece notes that one in five organizations have already seen data exposure through personal AI accounts, showing how easily risky behavior can slip past existing controls. Unlike shadow IT, where data can often be retrieved or redirected, data given to an AI model may be processed, retained, or used for training in ways the organization cannot reverse. This shifts the governance challenge from simply discovering unauthorized apps to understanding what data enters AI systems, what outputs they generate, and what actions those systems can take. The article’s steady message is that AI requires new visibility, new controls, and a more nuanced approach than legacy shadow‑IT playbooks.

Read Original Article →
Article Thumbnail

When auditors come for your AI algorithms

As artificial intelligence increasingly influences critical business operations, traditional auditing methods are falling short. Conventional audits rely on predictable, step-by-step trails, but AI models—especially large language models—are inherently variable. This unpredictability makes it difficult for CIOs to explain how an AI system reached a specific conclusion, which frustrates auditors demanding clear evidence and accountability. The core problem often stems from vague ownership across different teams, rather than the technology itself. To bridge this gap, organizations must abandon point-in-time audits in favor of continuous monitoring and a structured accountability framework. This approach involves assessing risks during system design, continuously reviewing those risks as the technology evolves, and conducting independent evaluations of the process. Rather than waiting for a massive corporate AI rollout, leaders need to act now, as AI features are already embedded in everyday enterprise software. By treating audit readiness as a core business capability rather than a compliance chore, CIOs can take proactive ownership, reduce risk, and confidently support ongoing innovation.

Read Original Article →
Article Thumbnail

Building Review Intelligence into the SDLC with AI Agents and Archetypes

As artificial intelligence evolves beyond basic code generation, AI agents are becoming active collaborators throughout the software delivery lifecycle. Instead of replacing human architects, developers, and reviewers, these agents act as helpful partners that provide vital context and consistent feedback. To truly benefit from this shift, organizations should move past generic AI prompts and develop specialized, well-defined skills for design, architecture, and code reviews. These targeted skills can be organized into reusable patterns, or archetypes, tailored to specific tasks like building new applications, upgrading older systems, or migrating to the cloud. By employing a coordinated group of agents driven by strict checklists, a central agent can organize the workflow, while specialized agents handle security, performance, and compliance. A final review agent ensures all feedback is practical and backed by evidence. Ultimately, this structured approach transforms informal AI assistance into a reliable quality assurance process, allowing engineering teams to manage the increasing speed of modern software development with clarity and confidence.

Read Original Article →

Daily Tech Digest - October 26, 2026

Quote for the Day
“If you can’t describe what you are doing as a process, you don’t know what you’re doing.”
— W. Edwards Deming
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The Migration Succeeded. The System Got Worse

Moving an application to the public cloud is often seen as an automatic upgrade, but a successful migration does not always result in a better system. One of the most common mistakes is relocating an application while leaving its primary database in an on-premises data center. This separation introduces critical network delays, meaning a system that functions fine under normal traffic can quickly suffer from connection exhaustion and severe failures during peak demand. While the cloud offers useful capabilities like flexible capacity and managed services, these benefits only matter if the entire technology stack is optimized for them. Simply moving infrastructure without addressing underlying dependencies often leads to inflated costs and new operational risks. A hybrid approach can be effective if planned deliberately, but it becomes an expensive burden when components are separated without a clear strategy. Ultimately, there is no single correct environment for every workload. Deciding whether to migrate, maintain a hybrid setup, or bring systems back in-house requires a realistic evaluation of performance, dependencies, and true operating costs.

Read Original Article →

Healthcare Data Governance: Who Decides What Gets Used?

Healthcare data governance is much more than just creating internal rules; it requires assigning clear, enforceable decision rights as patient information moves across different systems, APIs, and AI models. Rather than simply asking who owns the data, organizations should divide authority into four specific areas: legal permissions, operational approval, technical enforcement, and final accountability. This division is vital because when data is shared with payers, cloud vendors, or secondary AI tools, the original privacy policies are easily lost if someone is not explicitly responsible for enforcing them. Crucially, moving data to a cloud environment does not remove the healthcare organization's ultimate accountability. To prevent confusion and maintain compliance, organizations need a simple decision-rights matrix that clearly names the single person responsible for defining, accessing, reusing, correcting, and deleting data at every step of its journey. Ambiguity between different departments often leads to failure. Therefore, every single data handoff must have a clear owner equipped with both the responsibility and the actual power to enforce policies and correct issues.

Read Original Article →
Article Thumbnail

Identity at checkout: why payments must prove more and share less

As digital identity tools and payment systems continue to merge, payment providers face new challenges regarding customer verification and data privacy. With the European Union requiring digital identity wallets by late 2026, the traditional multi-step checkout process is shifting into a single, unified action. However, this connection risks exposing too much personal information. To protect consumer privacy and avoid the high costs of financial data breaches, payment networks must ask for only the minimum details required to approve a transaction, rather than viewing a user's entire background. At the same time, updated European rules are shifting fraud liability directly onto payment providers. If weak security checks let fraud slip through, companies will face significant financial losses through mandatory customer refunds. Over the next two years, providers need to build checkout experiences that focus on strong but easy verification. By asking for less personal data while proving identity more securely, companies can lower their financial risks and build better trust with both merchants and everyday consumers.

Read Original Article →

India’s cybersecurity talent challenge: Why more automation must be matched by better skills

As artificial intelligence takes over routine cybersecurity tasks like filtering alerts, the role of security professionals in India is fundamentally changing. Instead of simply operating tools, experts must now focus on validating AI findings, making complex judgment calls, and understanding when an automated system might be wrong. A recent report shows that most Indian enterprises struggle to find candidates with these practical, hands-on skills. To bridge this gap, organizations need to rethink how they train their teams. Standard certifications are no longer enough. Instead, companies should offer role-specific training and simulated scenarios where professionals can practice handling incomplete information and testing automated security boundaries. This shift is a major opportunity for India’s technology sector to build a workforce capable of supporting global security operations. Ultimately, the future of cybersecurity isn't just about how much we can automate, but how well humans and machines can work together to defend an increasingly complex digital landscape.

Read Original Article →
Article Thumbnail

Psychological Safety: The Overlooked Risk in Workplace AI Adoption

As organizations integrate AI into daily operations, they heavily focus on data security and privacy while frequently overlooking a crucial human element: psychological safety. Employees are adjusting rapidly to these tools, which naturally creates anxiety about job security and personal competence. If workers feel afraid to admit they do not understand a system, or remain hesitant to challenge an odd result, small mistakes can easily go unnoticed and escalate. A written corporate policy alone cannot prevent this. To use AI responsibly, leaders must actively build a workplace where people feel completely safe raising concerns. Management should encourage questions, acknowledge their own uncertainties, and demonstrate that healthy skepticism toward AI outputs is a sign of good judgment, rather than resistance to change. When leaders communicate clear expectations and actively support their teams, employees gain the confidence needed to catch errors early. Ultimately, building trust ensures that these new tools are used responsibly and effectively as a normal part of everyday work.

Read Original Article →
Article Thumbnail

Your AI Agent Has a Supervisor. Are They Qualified?

As AI systems handle more tasks in security operations, they are not replacing human analysts. Instead, analysts are shifting into supervisory roles to direct and review the technology's work. The central issue is that many companies simply add this responsibility to an analyst's existing workload without providing proper training, clear guidelines, or a defined job title. To fix this, organizations must establish AI supervision as a distinct and formal role. Supervisors need a deep understanding of security threats so they can properly set limits, question the AI's reasoning, and catch missing evidence. A supervisor's readiness should be tested through practical exercises rather than basic training completion. When evaluating success, security teams should focus on the quality of these reviews instead of how quickly tickets are closed. As AI tools gain the ability to take direct actions, like isolating systems or disabling accounts, strict human oversight becomes increasingly vital. Ultimately, a qualified human supervisor must own the final decisions to ensure accountability and maintain a secure environment.

Read Original Article →

Enterprise Deployment Architecture for Agentic AI on IIS: ChatGPT-Style UI over Agents & MCP Servers

The article outlines an architectural guide for deploying a ChatGPT-style web interface using Microsoft Internet Information Services (IIS) to front an agent powered by the Model Context Protocol (MCP). Instead of running agent interactions in a basic developer console, the paper presents a system tailored for enterprise needs, supporting 25 to 30 concurrent users. It relies on Windows Authentication and an IIS reverse proxy connecting to a long-running Python service. This design choice provides stability and avoids the overhead of launching a new process for every user request, while also eliminating the need for complex Kerberos double-hop delegation. The reference model, named ChefAI, illustrates a practical use case where restaurant staff query an assistant for real-time information, invoice generation, and technical troubleshooting. The agent connects to a local server for secure local tasks and remote HTTP servers for retrieving documents or analyzing logs. By using Server-Sent Events, the setup ensures smooth progress streaming to the chat interface, keeping the user interface completely independent of how the underlying tools are accessed or deployed.

Read Original Article →
Article Thumbnail

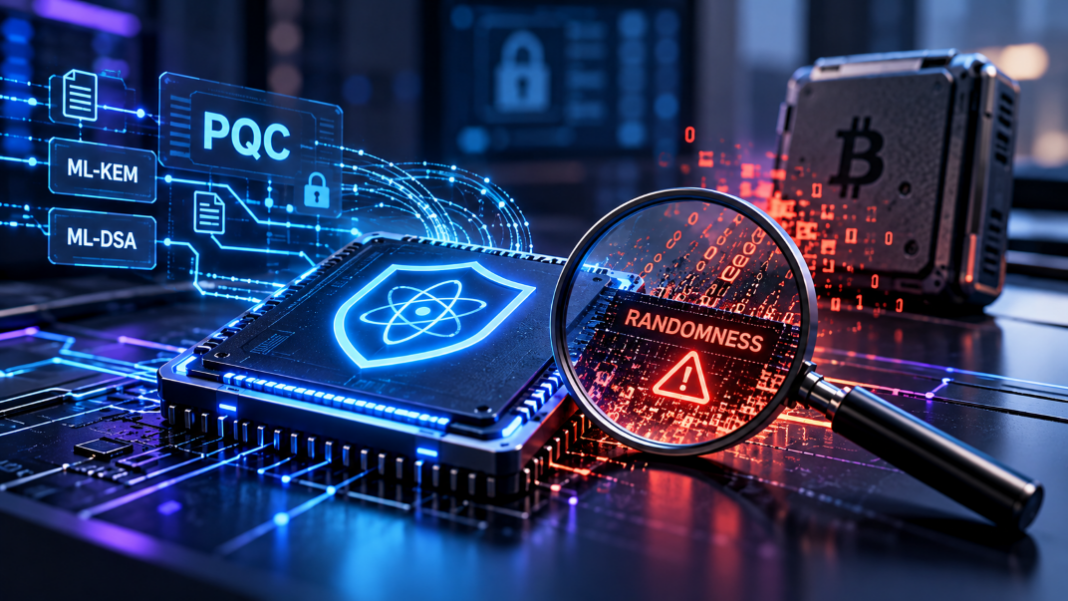
Your PQC Plan Trusts the One Thing You May Not Be Checking

As organizations prepare for post-quantum cryptography, they usually focus on mapping their current encryption tools and ensuring software flexibility. However, many migration plans overlook a critical, foundational vulnerability: the quality of their random number generators. Even the most advanced encryption algorithms will fail if the underlying randomness is predictable or generated by flawed hardware. Rather than relying solely on software upgrades, companies must trace exactly where their randomness originates and ensure it comes from verified, properly functioning sources. Upgrading safely requires identifying outdated legacy systems that cannot support new standards and adjusting procurement policies to demand quantum-resistant features immediately. Security leaders should treat this transition as a vital business continuity effort, not just an IT compliance checklist. By securing hardware-level trust, verifying random number generation, and acting early, organizations can effectively protect their most critical systems and avoid the steep financial costs of rushing to fix vulnerabilities later.

Read Original Article →
Article Thumbnail

Java vs Python in 2026: Which One Should You Learn for Backend, AI, and Data Science?

In 2026, the choice between Java and Python depends on your engineering goals rather than which language is simply more popular. Python is the primary language for artificial intelligence, machine learning, and data analytics. Its extensive ecosystem makes it the standard for researching and training models. On the other hand, Java remains the foundation for large enterprise backend systems, such as banking and retail platforms. Java provides the performance, structural safety, and mature frameworks needed to support massive, high-traffic codebases over many years. In practice, companies often use both: Python builds the AI models, while Java runs the reliable infrastructure around them. Python has an easier learning curve and gets you building faster, whereas Java requires more initial effort but teaches strict engineering fundamentals. Ultimately, if you aim to work directly with data or machine learning, start with Python. If you prefer building durable, large-scale backend architecture, focus on Java. Both offer strong career paths without the need for hype.

Read Original Article →

What Is CRQ? Cyber Risk Quantification Guide

Cyber risk quantification is a method that assigns clear financial values to potential security threats, allowing organizations to understand the real-world business impact of cyber events. Rather than viewing security solely as a technical issue, this approach translates risks into standard financial terms, making it much easier for security leaders to communicate with corporate boards and executives. By analyzing historical data alongside the frequency and severity of potential incidents, organizations can predict financial losses across both internal systems and third-party providers. This clarity helps businesses move away from subjective guesswork, enabling them to make practical decisions about where to invest their security budgets and how to prioritize protective measures. In addition to improving internal planning, putting a dollar figure on risk helps organizations negotiate better insurance terms, measure the return on their security investments, and establish a realistic tolerance for risk. Ultimately, calculating these financial impacts provides companies with the necessary insight to reduce the overall cost of security incidents and maintain steady operations.

Read Original Article →

Daily Tech Digest - October 07, 2026


Quote for the day:

“The first step toward success is taken when you refuse to be a captive of the environment in which you first find yourself.” -- Mark Caine

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Forrester Predicts AI Lawsuit, Global Outage in 2027

According to recent predictions from Forrester Research, artificial intelligence could lead to severe consequences for business leaders by 2027, including lawsuits, worldwide outages, and major data breaches. A central prediction suggests that an AI negligence lawsuit could eventually force a high-profile CEO to step down. This legal action would likely focus on whether leaders exercised proper judgment before handing critical decisions over to systems they did not fully understand. As a result, AI accountability will shift away from IT departments and move directly into corporate boardrooms. While companies can easily delegate daily tasks to AI, they simply cannot delegate the legal responsibility for the final outcomes. In addition to legal risks, the basic cost of running AI is expected to become a major financial focus. Spending on AI tokens for security operations will reach $1.5 billion, meaning leaders must closely manage these costs alongside their adoption efforts. Furthermore, the growing push for faster software updates using AI could lead to a massive global tech outage if flawed code escapes proper testing. Finally, companies looking to cut costs by switching between AI models risk exposing sensitive data, as safety measures built for one system often do not transfer perfectly to another. Leaders must establish firm oversight beforehand.


Python vs. .NET Core in Regulated Industries: An Architect’s Guide

When choosing a technology stack in highly regulated sectors like banking or healthcare, software architects often weigh Python against .NET Core. Python, renowned as a dynamic, interpreted language, dominates data science, machine learning, and quantitative finance due to its rapid prototyping capabilities and massive open-source ecosystem. In contrast, .NET Core is Microsoft’s compiled, statically-typed powerhouse, offering high throughput, multi-threading support, and strict governance ideal for transactional systems. For instance, high-frequency trading engines or core banking ledgers benefit significantly from .NET's predictable performance and lower latency, while complex risk simulations or fraud detection algorithms excel with Python's data-centric ecosystem. Dynamic typing makes Python incredibly agile early on but can become risky as codebases expand, forcing developers to adopt strict testing and type hints to meet compliance. Conversely, .NET requires more upfront structural design but inherently prevents numerous bugs at compile time, making large-scale refactoring significantly safer. Furthermore, .NET integrates seamlessly with enterprise security frameworks like Active Directory, making it a reliable choice for managing sensitive financial data. Ultimately, .NET provides industrial-grade scaffolding for high-volume transactional records, whereas Python remains the undeniable champion for data analytics and algorithmic modeling.


Sovereignty and resilience: considerations for organizational leaders

Data and system sovereignty is increasingly critical for organizations facing new regulations, like the European Union's Data Act and the Digital Operational Resilience Act (DORA). These rules require companies to maintain control over their data, their operations, and their technology. A key challenge is that many organizations rely heavily on public cloud services, which are fast and convenient but often tie them to a specific vendor's systems and timelines. This dependency creates a major risk if a provider experiences downtime or if an organization needs to switch providers, as a "mandatory exit strategy" is now a regulatory expectation. To build true sovereignty and avoid vendor lock-in, organizational leaders are turning to open-source infrastructure, like Kubernetes, which allows workloads to run across various environments independently. Using open-source software ensures that organizations maintain control over their data encryption, backups, and operational access without relying on proprietary, vendor-specific tools. However, organizations must do more than just set up these systems; they must actively prove their resilience through regular testing, identity verifications, and audit logs. Ultimately, reducing reliance on third-party cloud vendors by adopting open-source solutions is a highly effective way for organizations to regain control, manage risks, and build lasting resilience.


How to build a ‘safe-to-fail’ culture for IT teams — and why you should

Building a "safe-to-fail" culture allows IT teams to experiment with new technologies like artificial intelligence without fearing career repercussions or compromising company security. When workers lack the freedom, time, or resources to learn, businesses fail to realize the expected returns on their technology investments. True innovation requires separating experimentation from short-term performance metrics so employees feel secure exploring new tools during working hours. To make this practical, leaders should integrate disciplined testing into daily routines by assigning clear business goals, establishing specific time limits, and providing dedicated budgets for training or unapproved tools. Equally important is establishing clear boundaries to contain potential failures. Organizations must educate employees on operational rules, data usage policies, and the scope of permissible risks. By using preapproved, governed sandboxes populated with mock or nonsensitive data, IT teams can safely evaluate capabilities before deploying them in production. This staged approach uncovers integration issues early on while protecting critical systems and customer information. Furthermore, leaders should actively commend teams that transparently shut down unsuccessful projects, freeing up resources for work that matters. Ultimately, a safe-to-fail environment transforms uncertain experimentation into measurable business results and faster market delivery.


Why your hybrid cloud backup solution is only as good as its worst outage scenario?

The article explains why hybrid cloud backup strategies often fall short when an outage or ransomware attack hits, mainly because organizations underestimate how scattered their data has become. As companies adopt cloud services gradually—adding Microsoft 365, spinning up VMs, keeping some systems on‑prem—their backup tools rarely keep pace. The piece highlights that only a small share of enterprises use a single solution that covers on‑prem, cloud, and SaaS, leaving many teams with blind spots, especially around SaaS data. The author stresses that cloud providers operate under shared‑responsibility models, meaning they keep platforms running but do not guarantee full data protection. Recovery time objectives also become harder to meet because restoring from cloud backups can be slow, expensive, and dependent on bandwidth and egress fees. The article encourages teams to revisit where data lives, apply the long‑standing 3‑2‑1 backup rule thoughtfully, and tier systems based on how quickly they must return after an incident. It also outlines two practical approaches—consolidating backup tools or coordinating them with consistent policies. The closing message is steady and pragmatic: mapping data locations, testing cross‑environment restores, and documenting coverage are the real foundations of a reliable hybrid backup strategy, even for small IT teams.


NIST SSDF: 4 core practices for secure software development

The National Institute of Standards and Technology Secure Software Development Framework is a practical guide for building security into every stage of software creation. Rather than waiting until the end of a project to test for flaws, this framework embeds security throughout the entire process, which helps reduce coding errors, lower costs, and ensure consistent outcomes. The framework centers around four core practices that guide teams in building reliable software. First, organizations must prepare by establishing clear policies, defining roles, and providing proper training to ensure everyone understands their responsibilities. Second, teams must protect the software and its development environments from unauthorized access or tampering, which includes securing source code and safeguarding sensitive credentials. Third, developers should focus on producing well secured software by using secure coding techniques, analyzing potential threats early, and integrating security checks from the initial design phase. Finally, organizations must be ready to respond to vulnerabilities after the software is released, relying on structured processes to identify, evaluate, and fix any newly discovered issues. By following these foundational practices and keeping a detailed inventory of all software components, development teams can build secure, resilient applications while meeting regulatory obligations and managing potential risks with quiet competence.


What exactly is ISOC? And what does it mean for you?

Gartner recently recognized a shift in how organizations handle cybersecurity by introducing a new category called the Integrated Security Operations Center, or ISOC. While traditional data collection systems are still necessary, they are no longer enough on their own to manage modern threats. The field has evolved so that collecting data and actively responding to threats are now treated as separate problems requiring distinct solutions. ISOC steps in to handle the response side. It is designed to unify threat detection, investigation, and incident management across an organization's entire network. The main goal of an ISOC is to reduce the friction and complexity that security teams face when they have to juggle too many disconnected tools. By bringing everything into one unified platform, an ISOC helps teams manage incidents as connected cases rather than a flood of isolated alerts. It also allows for better automation and faster response times, which are essential now that attackers are moving faster than ever. Ultimately, this new category reflects a practical reality for modern security operations: teams need to simplify their workflows and cut down on delays without losing sight of the broader threat landscape they are trying to protect.


Why Digital Accessibility Belongs in Product Planning

Digital accessibility should be treated as a core component of product planning, rather than an afterthought or a simple website enhancement. Just like security, reliability, and usability, accessibility determines whether customers and employees can actually complete the tasks a product is built to support. Issues such as hard-to-reach payment buttons, unannounced error messages, or timed-out booking forms represent fundamental product failures. To address these challenges, product managers should integrate accessibility standards directly into their design and delivery processes. Instead of merely evaluating isolated features, teams must evaluate entire user journeys—from logging in to confirming a payment—to ensure no barriers prevent task completion. Building a strong business case requires moving beyond generic statistics about disabilities and instead identifying specific obstacles, the users they affect, and the practical consequences of leaving those barriers in place. Managing accessibility becomes far more efficient when it is embedded into daily operations, with clear responsibilities assigned to designers, developers, and testers. By treating accessibility as a shared operational priority and addressing issues systematically, companies ensure their digital products are functional, inclusive, and effective for everyone who needs to use them.


The CIO’s new mandate: Rearchitecting enterprise work

As artificial intelligence agents become more capable, the fundamental role of enterprise software is changing. Instead of employees manually operating applications to complete tasks, humans will increasingly supervise outcomes while machines handle the actual execution. This shift demands a new approach that author Rajjie Sarmey calls Enterprise Work Architecture (EWA). EWA is the deliberate design of how a business outcome moves across human judgment, machine intelligence, and data systems. Rather than simply adding AI features to existing software, which often just speeds up broken processes, EWA focuses on redesigning the work itself. Leaders must carefully evaluate the desired outcome, decide which steps require human judgment versus machine automation, establish clear authority for AI actions, and accurately measure the economic impact of these changes. As AI agents learn to bridge the gaps between separate systems like HR and finance, traditional applications will become less visible to users but even more critical for data integrity and organizational security. Ultimately, a modern CIO's new mandate is to lead this architectural shift. The most successful organizations will not just deploy the most AI, but will thoughtfully redesign how their entire enterprise operates while strongly protecting the accountability and trust that depend completely on human judgment.


What It Takes to Build a Trustworthy AI-Assisted Threat Modeling System

Building a reliable system for assessing cybersecurity threats using artificial intelligence requires far more than just picking a capable language model and writing good prompts. According to the author's long two-year journey developing such a tool, the actual product is the complex engineering built around the model to ensure its outputs are practically accurate rather than merely plausible. The author identifies twelve critical components that emerged through careful trial and error, including specific pattern recognition to ground findings in actual system designs, an accumulated knowledge base, and a verifiable evidence trail connecting every threat claim to a clear structural reason. Other essential layers involve strict quality gates, diverse specialist reviews to prevent a single perspective from dominating, continuous testing, and closed self-improvement loops that update the system as the security landscape rapidly changes. Crucially, these automated systems do not entirely replace experienced human analysts. Instead, they shift the human analyst's daily role away from tedious manual verification and toward exercising high-level judgment on complex issues. The ultimate goal is not to create an authoritative tool that generates impressive reports, but to build an accountable system that clearly states its confidence levels, securely traces its evidence, and honestly admits what it does not know.