Showing posts with label incident response. Show all posts

Daily Tech Digest - November 11, 2026

Quote for the Day
“The essence of strategy is choosing what not to do.”
— Michael E. Porter
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Sent or Just Written? The Outbox Problem in a Communications Outage

During a network outage, typical messaging tools often create a dangerous gray zone by simply labeling a message as "sent" the moment a user hits the button, even if it has not left the device. This false confidence can derail incident response efforts. When users are unsure if their updates went through, they tend to resend them repeatedly, leading to duplicate records. Additionally, when a device finally reconnects, stale messages can arrive looking fresh, or a sudden burst of old drafts can overwhelm the receiving team. To prevent these failures, organizations must recognize a middle state where a message is pending rather than fully delivered. While upgrading to tools that clearly display when a message is still on the device or unconfirmed is ideal, teams can also adapt their current processes. Business continuity plans should require users to include the time directly in the text of their updates, define clear rules for resending, and designate a person to acknowledge receipt. Testing these tools in airplane mode during routine drills ensures teams know exactly how their software behaves when the connection fails.

Read Original Article →

What is the difference between an HSM and a vault for key storage?

The core difference between a Hardware Security Module (HSM) and a vault lies in how they handle the exportability and processing of sensitive cryptographic data. An HSM is a dedicated, tamper-resistant hardware device designed to generate, store, and utilize keys entirely within its protected boundary. Because the private key material never leaves the hardware during signing or decryption processes, HSMs offer the highest level of assurance against memory scraping, host compromise, or accidental copying. In contrast, a vault is a broader secret-management system focused on orchestrating, centrally storing, and distributing credentials or application secrets on demand. A vault typically delivers secrets to an application over an authenticated channel, meaning the data exists temporarily in process memory. Many modern security architectures layer both solutions for maximum efficiency. Teams often use vaults as an operational control plane to manage developer workflows, automation, and general low-to-medium sensitivity secrets. They then reserve the HSM as a cryptographic trust anchor to secure non-exportable, high-value assets like root certificates and signing keys where exposure would be devastating.
Read Original Article →
Article Thumbnail

Before you automate, ask whether the process should exist: The missing question in Enterprise AI

Before adopting enterprise AI, many organizations make a critical mistake: they focus on automating existing processes without first evaluating if those processes are actually necessary. When companies rush to implement artificial intelligence, they often end up hardwiring inefficient or outdated workflows into their digital systems. This approach does not truly solve underlying business problems; it merely speeds up a broken system, creating long-term operational friction. To genuinely benefit from AI, business leaders must view automation as an opportunity for structural redesign. The essential first step is to completely map out current workflows and ask whether each step provides real value or simply exists due to legacy habits. If a process is redundant, overly complex, or fails to directly serve business goals, it should be eliminated or entirely redesigned before any software is introduced. By prioritizing process optimization over mindless automation, companies can ensure their AI investments drive meaningful efficiency, reduce operational waste, and foster a more agile enterprise. Ultimately, the best automation strategy is one that avoids automating what shouldn't be done in the first place.

Read Original Article →

What a security leader should tell the CEO about leaked credentials

In a recent interview, GitGuardian CEO Eric Fourrier discusses the evolving challenges of managing leaked credentials and the increasing personal liability facing security leaders. While holding executives accountable has forced boards to take cyber risk more seriously, it can also backfire by making employees afraid to report mistakes. This fear often leads developers to hide exposed secrets rather than properly revoking them, leaving the underlying security risk unresolved. Fourrier emphasizes that companies must separate accountability from blame, creating a culture where rapid reporting is encouraged and prioritized over punishment. When speaking to leadership, security chiefs need to confidently demonstrate that they can detect exposed credentials even in external or personal repositories, and they must track the time it takes from discovery to full revocation. Looking ahead to 2027, Fourrier warns that the rise of AI tools and autonomous agents is expanding the attack surface. As more non-engineers handle sensitive data through AI workflows, the paths for secrets to leak into public view are multiplying, requiring broader monitoring strategies to keep organizations secure.

Read Original Article →
Article Thumbnail

How AI Is Changing the Role of QA Engineers

The introduction of AI in software testing is fundamentally reshaping the role of Quality Assurance (QA) engineers, moving their core responsibility from executing tests to evaluating results. While AI tools now excel at automating repetitive tasks like test generation, locator maintenance, visual comparisons, and failure triage, they do not eliminate the need for human oversight. Instead, the focus shifts to verifying the machine’s decisions. For instance, when an AI tool automatically heals a broken locator, a QA engineer must confirm it actually targeted the correct element rather than masking a genuine issue. Furthermore, testing AI-driven features introduces unique complexities like non-deterministic outputs, hallucination, and model drift. Traditional pass/fail assertions are no longer adequate; QA teams must now build evaluation sets and scoring rules to judge acceptable model behavior. Ultimately, the notion that AI will replace testers completely misunderstands the process. As AI accelerates code generation, the volume of plausible but subtly flawed code increases. This "almost right" output demands stronger human judgment, meaning QA engineers remain essential to define what correct behavior looks like in increasingly complex systems.
Read Original Article →
Article Thumbnail

Gartner says CIOs must apply the brakes on AI to balance value and risk

Gartner is urging CIOs to slow the pace of AI adoption enough to ensure investment produces real business value without exposing organizations to poorly understood risks. The message is not to retreat from AI, but to bring greater discipline to decisions about where and how it is used. As businesses push ahead with AI initiatives, technology leaders face growing pressure to balance experimentation with governance, security, cost, and measurable outcomes. Gartner’s position suggests that enthusiasm alone is not a sufficient reason to expand AI programs. CIOs need to determine whether individual projects address genuine business needs and whether their benefits justify the resources and risks involved. This also means paying closer attention to controls and accountability rather than allowing adoption to run ahead of an organization’s ability to manage it. The broader point is that successful AI use will depend less on adopting the technology quickly and more on making deliberate choices about where it adds meaningful value. For CIOs, applying the brakes therefore means creating enough space for sound judgement while continuing to pursue worthwhile opportunities.

Read Original Article →
Article Thumbnail

Panic over cloud capacity is out of hand

The article argues that talk of cloud AI capacity being “sold out” is creating unnecessary confusion for enterprises. While demand for GPUs is high and constraints around hardware, power, regional availability, and long-term reservations are real, that does not mean organizations cannot obtain cloud resources for AI projects. Most enterprises are not training enormous models from scratch; they are running inference, building retrieval-augmented generation systems, fine-tuning smaller models, testing copilots, or experimenting with agents, each with different infrastructure requirements. The author warns that broad claims about shortages can push companies toward rushed capacity commitments or unnecessary changes to their cloud strategies. Instead, enterprises should first define the workloads they actually need to support, then confirm availability, pricing, quotas, reservation terms, lead times, and alternatives directly with providers. Architectures should also preserve flexibility by avoiding needless dependence on a single capacity option. The central message is straightforward: cloud capacity constraints deserve careful planning, but exaggerated headlines obscure important differences between workloads. Organizations will make better decisions by relying on specific facts, realistic requirements, and flexible architecture rather than reacting to market anxiety.

Read Original Article →

The Invisible Security Paradigm: Embedding Cyber Resilience into Operational Workflows

The article explains why cyber resilience in logistics must become part of everyday operations rather than remain a separate security activity. As supply chains rely more heavily on cloud platforms, APIs, connected devices, applications, partners, and third parties, cyber incidents can disrupt shipments, customer communication, operational systems, and business continuity, not simply expose data. Security leaders therefore need to move beyond compliance and prioritize risks according to exposure, exploitability, and the importance of affected assets. Strong resilience starts with clear visibility of assets, identities, data flows, and external dependencies, supported by measures such as least-privilege access, encryption, network segmentation, and tested detection and recovery capabilities. AI can help security teams analyze large volumes of information, identify unusual patterns, prioritize alerts, and speed investigations, but human judgement and reliable data remain essential. The article also stresses that security controls must fit operational realities rather than obstruct legitimate work. Ultimately, CISOs need to connect cyber risk with business continuity, customer trust, financial impact, and reputation, while making secure behaviour a normal part of everyday decision-making.
Read Original Article →
Article Thumbnail

Who Should Own Data Quality? What Changed When We Moved It

Historically, organizations assign data quality ownership to platform teams simply because they manage the technical infrastructure. However, this default approach causes significant delays. While technical teams can easily detect anomalies like sudden spikes in missing values, they lack the specific business context required to determine whether an anomaly is a genuine error, a documented rule change, or a valid edge case. To solve this problem, organizations should keep detection mechanisms centralized while shifting the responsibility for data definitions and incident resolution directly to the lines of business. When business units own the meaning of their data and have dedicated time allocated to resolve issues, incident resolution times can drop dramatically from several days to just a few hours. A successful transition also requires a thin enterprise governance layer to maintain a central definition registry, preventing individual departments from creating conflicting rules. By centralizing the detection of issues and decentralizing the judgment of those issues to the people who understand the data best, organizations build a highly responsive and accountable system that consistently maintains core data integrity without unfairly overburdening their technical teams.

Read Original Article →

Six questions to ask your MDR provider

As business technology environments grow more complex, organizations must regularly reassess their managed detection and response providers to ensure they still offer effective protection. It is no longer enough to rely on a list of features or assume that initial capabilities remain sufficient. Instead, security teams should focus on what a provider can genuinely see and address across the entire environment. This includes asking whether they can monitor machine identities, such as automated tools or system accounts, and tell the difference between normal and unusual behavior. Furthermore, a reliable provider must connect data from various systems, spanning across clouds, endpoints, and local networks, to spot threats that cross traditional boundaries. Simply collecting more data is useless without the proper context needed to interpret it. Organizations should also verify how the provider adapts to new types of attacks and exactly how artificial intelligence is applied alongside human expertise. Ultimately, the best way to evaluate a provider is to ask them to demonstrate their capabilities using a real incident. This proves they can connect subtle warning signs, understand their true meaning, and take decisive action.

Read Original Article →

Daily Tech Digest - November 03, 2026

Quote for the Day
“You can analyze the past, but you have to design the future.”
— Edward de Bono
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Nearly 1 in 5 workers laid off due to AI are asked to return, survey finds

Recent surveys reveal that many companies are reconsidering their decisions to replace human workers with artificial intelligence. According to research from SHL, nearly one in five US employees who lost their jobs to automation have been asked to return, while a separate study found that a third of organizations had to rehire staff after AI-related cuts. Experts suggest that employers moved too quickly to reduce headcount for immediate savings, only to realize that technology cannot easily replace human judgment, empathy, and contextual understanding of the business. However, bringing employees back is proving complicated because trust has been affected. Workers are returning with firmer demands, with many expecting significant pay increases, written guarantees of job security, and clear transparency regarding how AI will be used in their roles moving forward. This trend highlights a necessary shift in how businesses approach workforce planning. Rather than viewing technology purely as a tool for cutting costs, successful organizations are learning to balance the efficiency of automation with the irreplaceable experience of their human employees.

Read Original Article →

Securonix CPO on the limits of AI in security operations

In a recent interview, Simon Hunt, Chief Product Officer at Securonix, emphasizes that while artificial intelligence is a valuable tool for security teams, it cannot replace human judgment. He points out that AI is excellent at processing large volumes of data and identifying technical threats, such as a compromised account. However, it lacks the broader context needed to make sound business decisions. For example, AI does not inherently know the difference between locking an account on a quiet Sunday versus a critical Monday morning. Because of this gap in wisdom, Hunt envisions a future where security operations are heavily assisted by technology, but not entirely run by it. As automation takes over routine analytical work, human professionals will shift away from basic monitoring and focus instead on supervising the systems and handling complex exceptions. Furthermore, while these tools allow average criminals to launch stronger attacks, they also help defenders patch vulnerabilities much faster. Ultimately, organizations must maintain fundamental safety practices and rely on human oversight for final, high-stakes decisions regarding organizational risk.

Read Original Article →
Article Thumbnail

Could modular pre-planned response capabilities offer something new to the business continuity toolbox?

Traditional business continuity plans often gather all response procedures into a single, comprehensive document. While well-intentioned, these large plans tend to become rigid and difficult to navigate during a fast-paced crisis. Because they frequently contain outdated information, experienced response teams often abandon them in real-time, choosing instead to adapt and formulate new strategies as the situation unfolds. Recognizing this flaw, the author suggests shifting away from massive, overarching plans toward a more flexible approach inspired by emergency services, such as mountain rescue teams. Instead of relying on a single manual, organizations should adopt modular pre-planned response capabilities. These are self-contained, heavily practiced response units designed to handle specific operational impacts. During an emergency, a leader can simply assess the situation and activate only the necessary modules. This strategy transitions organizations from a rigid, plan-centered mindset to an agile, capability-centered model. By focusing on flexible modules rather than static documents, businesses can respond to disruptions much more effectively, ensuring their teams rely on practical, well-rehearsed actions rather than cumbersome paperwork.

Read Original Article →

Cybersecurity Awareness Month Wrap-Up: Five New Threats and Steps to Take Now

The article closes Cybersecurity Awareness Month by highlighting five fast‑evolving threats that now shape everyday risk. It explains that attackers increasingly rely on impersonation powered by AI, using convincing messages, voices, and videos to trick employees into approving payments or sharing sensitive information. Identity‑based attacks are also rising, with criminals bypassing technical defenses by persuading help desks to reset passwords or enroll new MFA devices. The piece warns that prompt‑injection attacks can manipulate AI tools directly, especially when employees use unapproved “shadow AI” and unknowingly expose confidential data. Insider threats are another concern, including cases where foreign operatives secure legitimate remote IT jobs using fabricated identities. Vendor compromise remains a major risk, as organizations often inherit incidents from third‑party providers. To respond, the article recommends updating incident‑response plans, running realistic tabletop exercises, assessing AI and identity risks, establishing legal frameworks before an incident occurs, and reviewing critical vendors. Its steady message is that modern threats often look like normal business activity, and organizations must adapt quickly to keep pace.

Read Original Article →
Article Thumbnail

NaaS hasn’t lived up to the hype. Is it still worth it?

The article explains why Network‑as‑a‑Service (NaaS) has not met early expectations, even though it still offers value in certain situations. Gartner once predicted rapid adoption, but uptake remains stuck around 1% to 5%, placing NaaS firmly in the “trough of disillusionment.” The piece shows that NaaS works well for organizations with aging infrastructure, limited staff, or a need for turnkey management — illustrated by a school that replaced its entire LAN through a vendor‑owned, fully managed deployment. However, the broader market faces obstacles. Consumption‑based pricing can be unpredictable, vendor lock‑in is a real concern, and ripping out functioning networks rarely makes financial sense. Analysts also point out that campus networking requires substantial on‑premises hardware, making it hard to deliver a true cloud‑like model. Definitions of NaaS vary widely, adding confusion and mismatched expectations. Surveys show interest in phased adoption, but fully mature deployments are rare. The steady message is that NaaS isn’t a failure — it’s simply a niche solution whose benefits depend heavily on an organization’s starting point and priorities.

Read Original Article →

From capacity, to the cost of intelligence

The article explores a major shift in the artificial intelligence industry: the focus is moving from simply buying enough hardware to figuring out the true cost of the intelligence it produces. While the price to run a single task has dropped dramatically, overall spending is soaring because companies are using AI far more heavily. The real cost of artificial intelligence is no longer just the price tag on a computer chip. Instead, it depends on the entire system working together efficiently, including how much power is used, how effectively the hardware is kept busy, and where the data is actually processed. This shift brings new challenges. For instance, as hardware becomes more powerful, it demands significantly more electricity. Finding enough power to run these advanced systems has become a bigger hurdle than securing the computer chips themselves. To build sustainable systems, the industry must prioritize complete efficiency across the entire setup, balancing cost, speed, and power, rather than just focusing on raw computing capacity.

Read Original Article →
Article Thumbnail

Seven egregious failures of modern web tech

The article lays out seven ways modern web technology has let users down, arguing that the web has become slower, heavier, and more frustrating despite decades of innovation. It points out that websites now load layers of scripts, trackers, and ads before showing meaningful content, making even simple pages feel sluggish. Basic reliability has also slipped: pages freeze, buttons don’t respond, and forms break because they depend on fragile JavaScript frameworks. The author criticizes how often sites block content with pop‑ups, cookie banners, and sign‑in walls, turning routine browsing into a negotiation. Search results have become cluttered with SEO‑driven pages that bury useful information. The article also notes that privacy has eroded, with sites collecting far more data than users realize. Accessibility remains inconsistent, leaving many people struggling with poorly designed interfaces. Finally, the piece argues that developers often chase new tools instead of building stable, lightweight experiences. Its steady message is that the web’s problems are not technical limitations but choices — and better choices could make the web fast, simple, and trustworthy again.

Read Original Article →
Article Thumbnail

Banks prepare for AI agents, but consumers hesitate to hand over control

European financial institutions are rapidly preparing for a future driven by AI agents, but their customers are not yet ready to hand over control. A recent survey by Signicat reveals a stark divide: while 79% of financial providers are prepared for AI-initiated applications, only a small fraction of consumers trust AI to act autonomously. Consumers are highly comfortable using AI as an assistant to research, compare products, or pre-fill forms. However, they draw a hard line when assistance turns into agency. Very few are willing to let AI submit applications, use their digital identity, or sign contracts on their behalf. The hesitation stems from valid concerns around security, fraud, and risk. Interestingly, digitally advanced markets like Norway and Sweden show the least comfort with autonomous AI. To bridge this trust gap, financial providers must move gradually, ensuring customers retain final approval over decisions. Ultimately, building confidence in this new landscape will require secure digital identities and continuous verification of both the customer and the AI agent acting for them.

Read Original Article →
Article Thumbnail

When AI agents agree on the data but not what it means

The article explains that AI agents can work from the same data yet still reach conflicting conclusions because data alone rarely carries the business context needed to interpret it correctly. Enterprises have spent years centralizing records into data lakes and warehouses, but in the process stripped away the policies, processes, and semantics that originally gave those numbers meaning. As organizations begin using multiple agents across a workflow, this missing context becomes a coordination problem rather than a data problem. Each agent may perform its assigned task correctly, but without shared business semantics, their combined actions can produce harmful outcomes — such as payment‑term negotiations, liquidity management, and compliance checks unintentionally stalling vendor payments. The article shows how fragmented data architectures and disconnected context sources make these failures more likely as agents hand tasks off to one another. Its steady message is that enterprises must supply agents with consistent business meaning, not just raw data, because alignment on numbers is useless if agents don’t share an understanding of what those numbers represent.

Read Original Article →
Article Thumbnail

Quantum computers are coming: Here are the problems they could tackle

The article explains that quantum computers are designed to solve a narrow set of problems that overwhelm even the fastest classical machines, especially those involving the behavior of complex molecules and materials. Because chemistry and materials science operate according to quantum mechanics, quantum computers could eventually simulate reactions and structures with far greater accuracy, opening doors to new medicines, cleaner industrial processes, better catalysts, and more efficient batteries. Researchers expect early, meaningful demonstrations once fault‑tolerant systems with a few dozen logical qubits arrive later this decade. The article also highlights the security implications: a sufficiently powerful quantum computer running Shor’s algorithm could break today’s widely used encryption, which is why governments are already pushing post‑quantum cryptography. Quantum systems may also help with certain optimization problems, though the article cautions that clear advantages are not guaranteed. Overall, it argues that quantum computers will not replace classical machines but will act as specialized partners, delivering breakthroughs in chemistry, materials, cryptography, and select optimization tasks as fault‑tolerant hardware matures through the late 2020s and 2030s.

Read Original Article →

Daily Tech Digest - October 30, 2026

Quote for the Day
“Scrum is not a methodology; it is a path to agility.”
— Ken Schwaber
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

CISO Problems That Can't Be Solved With Technology

The article highlights a blunt reality: many of the hardest problems CISOs face cannot be solved with technology alone. A panel of security leaders explains that organizations often churn through tools not because the tools are bad, but because they were never properly integrated, funded, or owned. New leaders arrive, priorities shift, and platforms get replaced before they ever reach full value. Several CISOs stress that the real issues are operational — unclear ownership, slow coordination, and misaligned reporting structures. One example describes a critical vulnerability that took an hour to fix technically but three days to close because no one had agreed in advance who should notify teams, approve downtime, or communicate with the business. The panel also criticizes vendors for pushing products without understanding customer needs, and notes that corporate politics often prevent CISOs from having a direct voice with CEOs and boards. The steady message is that security failures often stem from human systems, not technical ones, and solving them requires clearer accountability, better collaboration, and more realistic operating models.

Read Original Article →

Out-of-Band Communication: Your Incident Plan Assumes the Systems You’re Using to Respond Still Work

Most organizations mistakenly assume their standard communication tools will be safe to use during a cyberattack. In reality, when a breach occurs, attackers routinely monitor platforms like Teams, Slack, and corporate email to stay a step ahead of the defense team. If your incident responders are coordinating on compromised systems, they are essentially giving the attackers a live briefing of their recovery strategy. To prevent this, response teams need out-of-band communication—a secure channel entirely separate from the company’s primary network and identity infrastructure. However, simply switching to consumer messaging apps like Signal or WhatsApp is not a reliable backup. These apps lack proper identity verification, make it difficult to maintain accurate team access, and fail to create the secure, defensible audit trails required for regulatory reporting. A genuine out-of-band strategy requires a dedicated, independent environment that is set up and tested long before a crisis hits. By moving the entire response process off the primary network, organizations can confidently manage the incident without tipping off the adversary.

Read Original Article →
Article Thumbnail

Agents are rewriting the book on security. Can your data layer keep up?

The article argues that AI agents are reshaping security in ways that traditional data architectures are not prepared for. These agents don’t just automate tasks — they make decisions, take actions, and interact with multiple systems at once. That shift means the data layer becomes a central security concern rather than a background utility. The piece explains that most organizations still rely on fragmented data stores, inconsistent permissions, and brittle pipelines, all of which create blind spots when agents begin pulling information from many sources simultaneously. If the underlying data is incomplete, stale, or poorly governed, agents can make incorrect or risky choices at machine speed. The article also warns that agents expand the attack surface because they can be manipulated through poisoned data, misleading prompts, or compromised integrations. To keep up, organizations need unified governance, strong lineage tracking, and real‑time visibility into how data flows through agent workflows. The steady message is that AI agents change the tempo and complexity of security, and only a modern, well‑governed data layer can support them safely.

Read Original Article →

Cheap Code, Expensive Confidence

Delegating software development to AI coding assistants might generate code quickly, but building the confidence that this code actually works as intended remains a challenging and time-consuming process. When an AI builds a feature, seeing a number on a screen doesn't prove the underlying math is correct or that the right data was used. Verifying these details requires deep system knowledge and often collaborative discussions with experienced colleagues. Because of this, claiming an AI got a project "eighty percent done" is often misleading. The remaining work involves uncovering where your expectations and the AI's logic diverge, which can take longer than writing the code manually. Furthermore, leaning too heavily on AI can rob newer developers of vital learning opportunities. Working through a problem manually helps them understand how data flows through an application, a skill they need for future troubleshooting. Ultimately, teams must thoughtfully decide when to hand tasks to an AI. This choice should depend on how easily the team can verify the final result and whether a developer needs the experience of solving the problem themselves.

Read Original Article →
Article Thumbnail

The Rise of the Threat Operator: How AI Will Redefine Security Operations and Careers

As artificial intelligence takes over routine security tasks like investigating alerts and gathering evidence, the traditional role of the security analyst is fundamentally changing. Instead of getting bogged down in individual alerts, professionals are transitioning into a new role often called a threat operator. This position requires overseeing the entire defense strategy rather than just monitoring tools. Because AI can handle the repetitive technical work, human experts must now focus on understanding their organization's unique business risks and guiding the AI systems accordingly. They decide how much independence the software should have and step in when complex judgment is needed, such as balancing a security threat against the risk of taking a critical business system offline. This shift means future security professionals will need a different blend of skills. While technical knowledge remains important, the ability to interpret automated decisions, manage overall risk, and maintain accountability over the defense process is becoming essential. Ultimately, security teams are moving from operating individual software tools to managing a comprehensive, AI-supported defense system.

Read Original Article →
Article Thumbnail

A Release Review Checklist for Teams Where One Developer Does Most of the Work

When a single developer handles an entire software project, the usual safety nets of peer reviews and dedicated testing disappear. To prevent bugs from reaching users, teams should implement a straightforward release review process that a senior developer can complete in under an hour. The foundation of this method is a consistent, eight-point checklist applied to every release. First, the reviewer reads the release summary to ensure the code actually solves the requested problem. They then evaluate the structural design rather than just reading lines of code. The reviewer tests the feature from the perspective of both a brand-new user and a long-time user, deliberately trying unexpected inputs that the original developer likely missed. They also check for broken features in other parts of the application, verify that appropriate tests are included, and confirm environment configurations match production settings. Finally, the reviewer records a clear decision to release or hold the code. For this system to work, reviews must be scheduled, reviewers must have authority to halt a release, and common mistakes must be discussed.

Read Original Article →
Article Thumbnail

A JSON schema Is not an AI governance layer

True AI governance happens far below the level of industry regulations and policy debates; it ultimately comes down to the specific code that decides whether an AI agent is allowed to execute an action. While many developers rely on tools like JSON schemas to validate an agent's requests, these schemas only check the shape of the data, not its precise meaning across different systems. This limitation creates a security vulnerability known as a parser differential, where two different components read the exact same payload in slightly different ways. Simple differences in how a system handles whitespace, looks up identifiers, or processes data normalization can inadvertently alter your authorization rules. Furthermore, you cannot rely on an agent to declare its own inputs as trustworthy. Real security requires deriving trust directly at the enforcement boundary by verifying cryptographic signatures against known keys. To truly secure your AI deployments, you must go beyond basic schema validation, strictly enforce specifications, reject ambiguous data shapes, and ensure your system independently verifies the authority behind every requested action.

Read Original Article →

McKinsey's Quantum Road Map Runs Through Q-Day

A recent McKinsey report highlights the rapid advancement of quantum technology and its dual role as a massive economic opportunity and a serious security threat. The focus for security professionals is "Q-Day," the point when quantum computers become capable of breaking today’s standard encryption. This milestone is approaching faster than initially projected, with key hardware developments expected within the next five years. Because attackers are already stealing encrypted data to decode it in the future, organizations cannot afford to wait. The report urges companies to begin upgrading to new, quantum-resistant encryption methods immediately to protect their long-term data. Upgrading this security infrastructure will require significant time and financial investment, marking a shift that is non-negotiable for large enterprises. To prepare, leaders need to take inventory of their current encryption systems, secure multi-year budgets, and require their technology suppliers to provide clear transition plans. Ultimately, updating to quantum-safe security is not a distant concern but an active, ongoing necessity that requires methodical and immediate planning.

Read Original Article →
Article Thumbnail

No One Holds the Key: Threshold ECDSA, Part 1

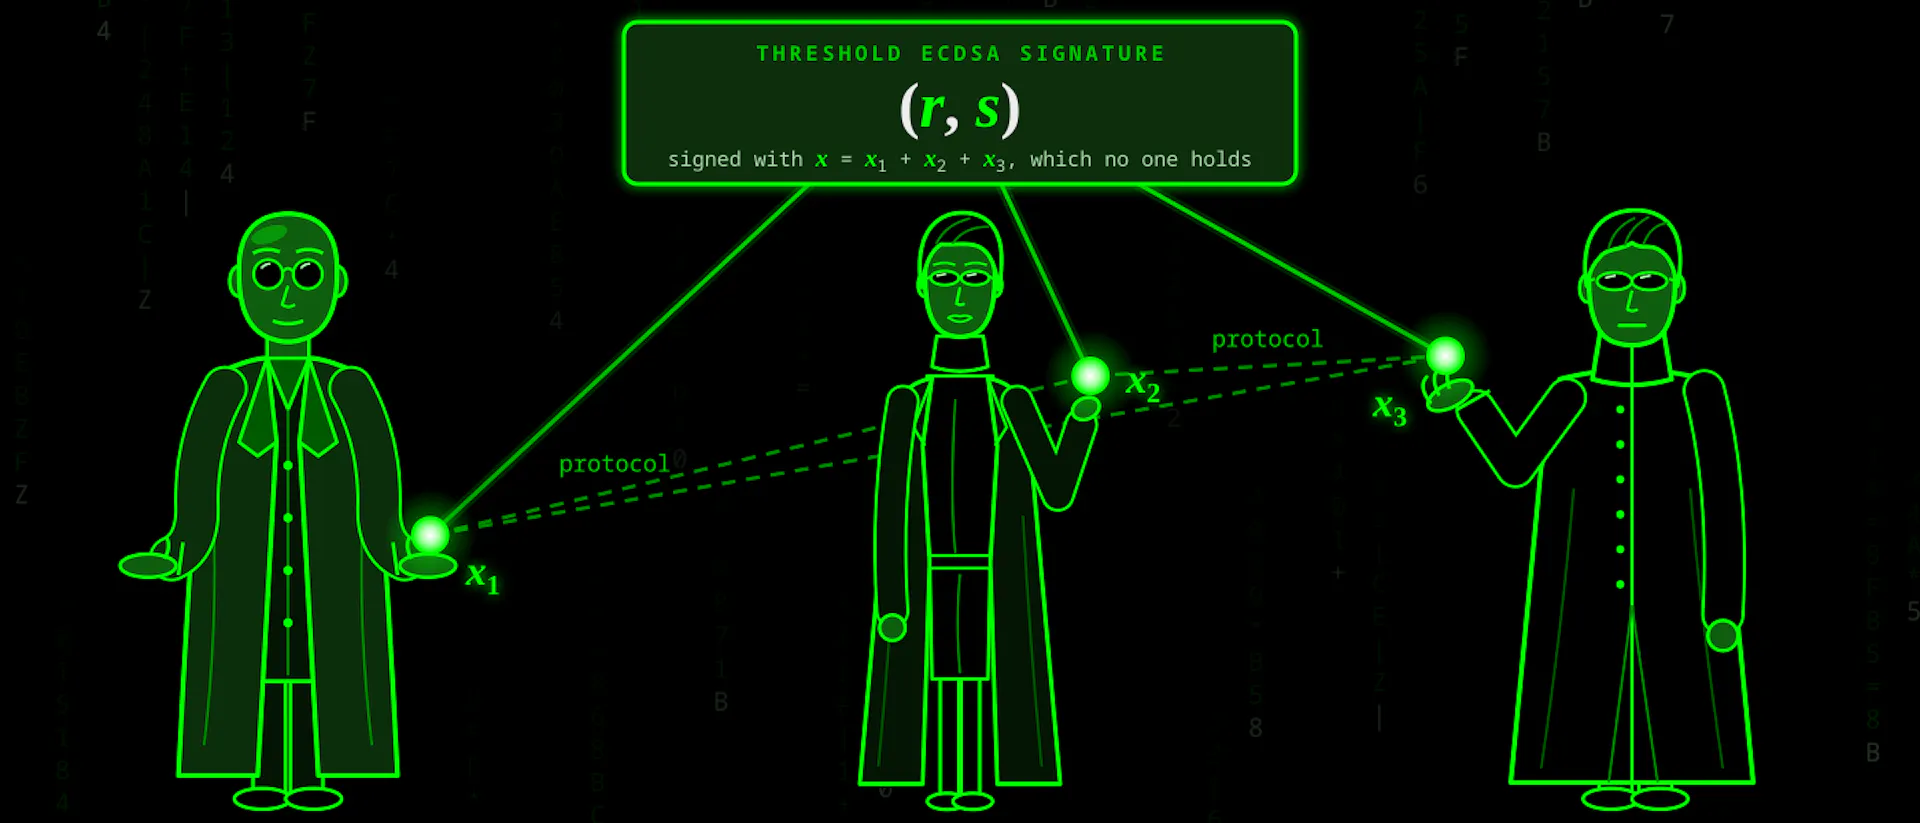
The article introduces threshold ECDSA as a way to remove single points of failure in digital signing systems. Traditional ECDSA relies on one private key held by one party, which creates an obvious risk: if that key is stolen, lost, or misused, the entire system is compromised. Threshold ECDSA changes this model by splitting the private key into multiple independent shares held by different participants. No one ever sees or reconstructs the full key, yet the group can still produce valid ECDSA signatures through a coordinated protocol. The article explains that this approach improves security for wallets, exchanges, and custodial services because attackers can no longer target a single secret. It also reduces operational fragility — losing one device or administrator doesn’t destroy access. The piece highlights that implementing threshold signing is complex, requiring careful cryptographic design to prevent leaks during collaboration. Its steady message is that threshold ECDSA offers a practical path toward stronger, more resilient key management by ensuring that “no one holds the key” in the traditional sense.

Read Original Article →
Article Thumbnail

PHP2Shell will persist in enterprise environments for years

The article explains why the PHP2Shell vulnerabilities will linger in enterprise environments for years, even though patches already exist. PHP is embedded in an enormous range of third‑party products — NAS devices, firewalls, VPN gateways, printers, building‑management systems, industrial controllers, and OT interfaces — many of which run outdated or unsupported PHP versions. Because customers cannot patch these runtimes directly, they must wait for vendors to release updates, and those updates often arrive slowly or not at all. The article shows how inconsistent versioning, backported fixes, and long‑term‑support Linux distributions make it difficult to know whether a system is truly protected. Early scans already reveal widespread exposure, and CISA has confirmed active exploitation. Even when patches are available, organizations still face the challenge of discovering every PHP instance across servers, containers, appliances, and firmware images. Until vendors deliver fixes, teams must rely on temporary mitigations such as isolating devices, tightening firewall rules, and monitoring for signs of compromise. The steady message is that PHP2Shell is less a single vulnerability and more a visibility and lifecycle problem that enterprises will be managing for a long time.

Read Original Article →

Daily Tech Digest - October 11, 2026


Quote for the day:

“Leadership is the art of getting someone else to do something you want done because he wants to do it.” -- Dwight D. Eisenhower

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Resilience is an evidence problem

According to Mathieu Rigotto in Resilience Forward, organizations must fundamentally change how they approach security, moving away from outdated patch by severity models to strategies driven by actual evidence. With malicious actors now exploiting vulnerabilities within days or even before patches are released, traditional security methods are no longer fast or effective enough to protect systems. Consequently, major authorities and new regulations like the European Union's NIS2 and Cyber Resilience Act demand that organizations actively prove their resilience rather than simply listing the controls they have in place. This requires a shift toward identifying whether system vulnerabilities are genuinely exposed and actively exploited. As a result, the role of a Chief Information Security Officer is evolving from being the solitary owner of security to acting as the provider of concrete evidence. Furthermore, company boards can no longer delegate risk acceptance entirely; they must define clear tolerances for operational disruption and take full ownership of critical decisions. To adapt successfully, businesses need to assign clear human ownership to digital assets to prevent costly delays in fixing issues. Ultimately, resilience is not just a final destination or a compliance box to check. It remains an ongoing claim backed by constant proof and regular testing.


Palo Alto reports legacy OT systems, fragmented security tools undermine critical infrastructure cyber resilience

Palo Alto Networks’ recent State of Critical Infrastructure Cybersecurity report reveals that 60% of critical infrastructure organizations experienced a major security breach in the past year, with half facing physical safety consequences. Surveying over 1,600 security leaders globally, the findings underscore that fragmented security tools and outdated operational technology (OT) leave dangerous visibility gaps. Specifically, 68% of organizations lack complete, real-time visibility into all their OT assets, while a reliance on legacy, unpatchable systems is seen as the greatest single security risk. Using an average of seven disparate security tools creates costly operational complexity and slows down incident response times. While threat actors are rapidly utilizing artificial intelligence to exploit vulnerabilities at machine speed, defense capabilities are lagging. A vast majority of leaders worry about advanced AI-powered attacks, yet technical constraints hold back widespread AI adoption for defense. Additionally, IT and OT security operations remain disconnected for 74% of organizations, largely due to incompatible technology and conflicting priorities. To build true cyber resilience and bridge the growing gap between attackers and defenders, organizations must prioritize unified visibility, integrate their IT and OT workflows, and streamline their security toolsets to minimize blind spots and automate responses effectively.


How CIOs can climb out of the AI governance chasm

According to a recent report from InformationWeek, chief information officers (CIOs) are facing an increasingly urgent challenge: establishing robust AI governance to keep pace with rapid employee adoption. An overwhelming 84% of surveyed CIOs indicated that internal teams are building AI applications faster than their IT departments can effectively oversee them. This governance gap threatens not only the quality and security of enterprise products but also the potential business value these tools offer, especially as most organizations currently lack comprehensive controls. A major concern for IT leadership is managing AI-related costs. Without clear visibility into workloads or centralized repositories for tools, enterprises risk redundant efforts and spiraling expenses. Data quality further complicates the landscape, as AI tools that pull from outdated or inaccurate information can easily produce "hallucinations" or flawed code. Additionally, "shadow AI"—where employees deploy unapproved or untested AI agents—presents significant security and data leakage risks. To combat these issues, leaders emphasize the need for cross-enterprise collaboration and straightforward governance policies that employees can easily understand and follow. Addressing these operational, financial, and security challenges promptly is critical, as a substantial portion of CIOs feel their job security hinges on demonstrating measurable AI success in the near future.


Cybersecurity in the age of AI and smart factories 

As India aims to become a leading advanced manufacturing hub by 2035, the integration of artificial intelligence and smart technologies into factories is drastically altering the cybersecurity landscape. Hitesh Shah, Vice President and Senior Partner at Kyndryl India, explains that while AI boosts factory productivity through anomaly detection and faster incident responses, it also equips attackers with sophisticated, automated tools. A major challenge for modern smart factories is the merging of Information Technology (IT) and Operational Technology (OT). Because production systems now actively exchange data with enterprise applications and cloud platforms, a simple breach on an office laptop can escalate into a critical production shutdown or the manipulation of AI models. To combat this, manufacturers must treat IT and OT security as an integrated challenge rather than separate programs. They need complete visibility into all connected assets, legacy machinery, and new AI tools to safely segment networks and manage access. By building security directly into their digital design and cloud migration plans from the start, factories can achieve true cyber-physical resilience. Ultimately, securing these environments ensures that the intelligence driving smart manufacturing remains reliable and capable of supporting continuous, uninterrupted production.


Control over the cloud is only possible with the right management layer

As organizations navigate rising hardware costs and stringent data sovereignty requirements, the technology trend is clearly shifting from relying solely on public clouds to adopting robust on-premises solutions. Ambitious artificial intelligence projects may begin in the public cloud, but protecting critical customer information in compliance with strict privacy regulations often requires bringing essential workloads back in-house. A dedicated on-premises infrastructure can drastically reduce the total cost of ownership while keeping sensitive data completely secure and avoiding the growing risks of unauthorized shadow computing. However, simply purchasing new hardware is not enough to solve modern infrastructure challenges. To truly maintain control over increasingly complex digital environments, businesses need a highly unified management layer. A smart hybrid strategy, such as the strategic collaboration between Dell Technologies and Nutanix, allows companies to blend public and private clouds seamlessly. By integrating compute and storage under a single, centralized management interface, organizations can easily oversee all their infrastructure without relying on separate specialists for every individual platform. This unified approach eliminates isolated data silos, improves security through careful microsegmentation, and allows for strict cost controls on resource-heavy deployments. Ultimately, achieving true digital sovereignty depends entirely on simplifying management across diverse cloud environments to ensure reliable, long-term operational flexibility.


The Distributed Monolith Trap: How Microservices Become What They Replace

Many organizations adopt microservices to escape the slow updates and massive codebases of traditional software design. Unfortunately, without strict discipline, they often fall into the trap of building a distributed monolith. This happens when an application is split into separate pieces but remains tightly connected, combining the limitations of older designs with the added network instability of distributed systems. The article outlines five primary warning signs of this problem: needing to update multiple services at the exact same time, allowing different services to share a single database, experiencing cascading system failures from long chains of blocked requests, relying on circular dependencies, and forcing services to share common code libraries. To fix these core issues and achieve true service independence, development teams need a clear refactoring strategy. The most important step is ensuring every service has its own dedicated database, preventing one team’s changes from unexpectedly breaking another’s work. Additionally, teams should replace blocked communication with asynchronous event messaging, swap shared code for clear communication contracts, and use protective routing tools to stop isolated failures from spreading. By firmly enforcing these boundaries, software engineering teams can successfully untangle their connected systems and build a genuinely resilient architecture that operates smoothly at scale.


Quantum Computing’s Transistor Moment

A recent breakthrough in quantum computing suggests the industry may be experiencing its own “transistor moment.” Researchers in Germany successfully demonstrated a three-qubit Grover search algorithm using a room-temperature diamond quantum processor. According to Professor Marius Grundmann, this achievement mirrors the historical shift in classical computing from bulky, fragile vacuum tubes to scalable semiconductor transistors. Just as the transistor revolutionized electronics by allowing for miniaturization and mass manufacturing, this solid-state quantum processor operates at ambient temperatures without the need for the massive, power-hungry cryogenic refrigerators and vacuum chambers required by current leading quantum technologies like trapped-ion or superconducting systems. While existing vacuum-dependent methods still hold an edge in raw fidelity, the diamond processor achieved impressive success rates and fidelity scores using carbon-shielded nuclear spins as qubits. Crucially, fabrication techniques for these nitrogen-vacancy centers have reached a high yield, pointing toward reliable scalability. If room-temperature, solid-state quantum computing continues to improve along a semiconductor-like curve, it could drastically expand the technology's applications into mobile devices and vehicles. Conversely, this shift poses a significant threat to the billions of dollars currently invested in complex, environment-dependent quantum systems, which risk becoming obsolete as more practical, scalable alternatives mature.


Cyber Incident Preparedness: How Companies Can Respond to Modern Threats and Build Business Resilience

The article explains how companies can strengthen their preparedness for modern cyber incidents, emphasizing that today’s attacks unfold faster, hit harder, and create far‑reaching business consequences. It stresses that a cyber incident is never just an IT problem; it immediately involves legal teams, communications, compliance, operations, insurers, regulators, and sometimes law enforcement. The authors note that attackers now use organized business models, including ransomware‑as‑a‑service and AI‑enabled intrusion techniques, which accelerate data theft and extortion. Because of this, companies must prepare well before an incident occurs by identifying decision‑makers, retaining outside experts, documenting notification obligations, and conducting realistic tabletop exercises. The article highlights that restoring systems is only the beginning. True recovery includes managing regulatory inquiries, contractual duties, customer notifications, insurance claims, litigation, and long‑term reputational impact. Vendor risk is another major concern, as attackers increasingly target widely used providers to reach many downstream customers. Boards are encouraged to view cyber risk through three lenses: cybersecurity strategy, data strategy, and business strategy. The authors conclude that genuine preparedness requires coordinated plans, trained personnel, backup leaders, and repeated testing. The real measure of resilience is whether a company can make sound decisions under pressure and continue operating while managing the long tail of a breach.


I Chose a Monolith Over Microservices — Here’s Why

In the article, software engineer Ashwini T explains his pragmatic decision to choose a modular monolith architecture over microservices for a new product, countering the common assumption that microservices are inherently superior. He argues that microservices solve specific scaling and organizational problems, but for a small team with a developing product, adopting them prematurely introduces unnecessary distributed-system complexities, such as network latency, partial failures, and complex transaction management. Instead of building a "big ball of mud," Ashwini advocates for a strictly organized modular monolith, where separate domains—like users, orders, and payments—have clearly defined boundaries and communicate through public interfaces rather than direct database sharing. This setup provides the simplicity needed to ship quickly and learn while making it easier to adjust boundaries as the domain becomes better understood. He points out that wrongly defining boundaries in a monolith just requires refactoring, whereas fixing them in a microservices setup is a massive migration project. Ashwini maintains that architecture should earn its complexity; a monolith can scale quite far, and if specific components eventually demand independent scaling or dedicated teams, a well-structured monolith makes a gradual transition to microservices much simpler.


Management of change for OT security: running visibility and remediation through MoC

In operational technology (OT) environments, security programs frequently fail because they bypass the Management of Change (MoC) process—the core governance workflow that operations teams trust to evaluate and approve modifications without disrupting physical processes. According to SC Media, treating MoC as a hurdle rather than an access control layer for physical infrastructure often leads to unauthorized actions that cause equipment damage, production loss, or safety hazards. Even seemingly benign activities like read-only network queries or passive scanning can trigger controller failures, particularly on legacy serial or fieldbus networks that lack the bandwidth of modern industrial Ethernet. To maintain stability and safety, every security action—including configuration collection, patching, network isolation, and access control changes—must run through the MoC framework. This process relies on a joint authority model where security proposes the change, while engineering, operations, and safety teams evaluate its physical and operational impact before approval. Notably, during a security incident, standard IT practices like immediate system isolation can be dangerous in an OT setting; containment must be assessed for process impact, ideally using pre-approved emergency MoC templates. Ultimately, aligning security with MoC ensures that risk mitigation does not inadvertently become the source of operational disruption.