Showing posts with label data sovereignty. Show all posts

Daily Tech Digest - October 25, 2026

Quote for the Day
“The only way to win is to learn faster than anyone else.”
— Eric Ries
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Core Concepts in Infrastructure Cost Management

The article revisits how organizations should think about infrastructure cost management by comparing on‑premise and cloud deployment patterns. It notes that a decade ago, cloud was widely seen as the inevitable future, but recent shifts show that on‑premise environments still offer advantages worth reconsidering. On‑premise setups involve not just servers but the full physical ecosystem — racks, networking gear, cooling, power, and security — all of which carry long‑term financial and operational implications. The piece explains that while on‑premise environments are often labeled inflexible, they can be surprisingly adaptable when paired with modern automation frameworks. The real challenges lie in hardware lifespan decisions, sizing development and QA environments, managing shared analytic workloads, and maintaining disaster‑recovery sites that are costly to keep idle. These factors shape both capital and operational expenses over many years. The article’s steady message is that cost management requires understanding the trade‑offs between flexibility, predictability, and long‑term commitments, and that both cloud and on‑premise models have strengths that deserve thoughtful evaluation rather than assumptions.

Read Original Article →

Container Security Checklist for CI/CD Pipelines: 30 Checks From Commit to Runtime

This article presents a practical security checklist containing 30 checks for container images as they move through continuous integration and deployment pipelines. The core message is that actual security comes from enforcing rules, not just listing best practices. The checks span eight stages, from the initial code commit to runtime monitoring. In the early stages, teams should build minimal images, remove all secrets, and lock down third-party actions. Later stages focus on vulnerability scanning that blocks risky deployments, generating software bills of materials, and digitally signing images to guarantee they came from a trusted build. At deployment, admission controllers must verify signatures and restrict permissions so images cannot run with root access or modify the underlying host. Because the pipeline itself is a high-privilege system that can be compromised, securing the build process is just as important as securing the image. Implementing these checks incrementally—starting with basic Dockerfile hygiene—prevents common mistakes and ensures a cleaner, safer production environment.
Read Original Article →
Article Thumbnail

Cloud repatriation: What CISOs need to know

The article explains that cloud repatriation is becoming a practical concern for CISOs, not because enterprises are abandoning the cloud, but because many workloads no longer fit the cloud‑first assumptions of the past decade. Surveys show that while 86% of CIOs plan to move at least some workloads back on‑premises, only about 8–9% intend a full exit, meaning most organizations are simply recalibrating workload placement rather than rejecting cloud altogether. Cost discipline is a major driver, with private cloud often delivering 40–50% lower total cost of ownership for steady‑state workloads. Compliance, data‑gravity issues, and high‑intensity AI workloads also push certain systems back into controlled environments. The article stresses that hybrid infrastructure is becoming the long‑term norm, where each workload “earns” its placement based on economics, performance, and risk. For CISOs, this shift introduces new responsibilities: reassessing threat models, ensuring consistent controls across mixed environments, and preparing for operational risks tied to vendor concentration and geopolitical disruptions. The message is steady — repatriation is about precision, not retreat, and CISOs must adapt security strategies accordingly.

Read Original Article →

The Cybersecurity Reality Check: Ten Myths That Matter

The article challenges ten common assumptions that often mislead leaders about cybersecurity and explains why these misconceptions create real risk. It notes that serious incidents rarely stem from exotic technical failures; instead, they usually begin with flawed beliefs about who attackers target, where responsibility sits, or what “adequate protection” really means. One myth is that small organizations are too insignificant to attract attention, but attackers typically exploit exposed systems using automated tools, making size irrelevant. Smaller firms may even be more vulnerable because they have fewer security resources and weaker monitoring. Another misconception is that cybersecurity is purely an IT function, when governance and accountability actually rest with leadership. The article stresses that regulatory scrutiny in the UK and EU has intensified, and breaches can quickly lead to investigations, litigation, business interruption, and reputational harm. Ultimately, the piece argues that organizations must be able to justify their security measures as proportionate to their risks and abandon assumptions that no longer match today’s threat landscape.

Read Original Article →
Article Thumbnail

When Trust Fails: What the eMudhra Certificate Incident and PHP Vulnerabilities Teach Us About Zero Trust Security

In October 2026, two distinct cybersecurity events—a certificate failure by eMudhra and critical remote code execution flaws in PHP—highlighted a fundamental lesson for software engineers: trust must be constantly verified. The eMudhra incident involved weak intermediate cryptographic keys generated by a flawed process. Even though eMudhra itself was not hacked, the incident proved that secure connections rely on trustworthy underlying processes, not just a padlock icon. Meanwhile, the PHP vulnerabilities demonstrated that securing an application requires patching the entire software stack, not just the core code, because a vulnerable runtime can serve as an easy entry point. Together, these events show why modern systems must move away from assuming that any internal network or familiar request is automatically safe. Instead, engineers should adopt a strict verification approach. This means validating identity, authorization, and context at every boundary, properly handling access tokens, and protecting communication between internal services. Ultimately, security is an ongoing engineering process of continuous verification rather than a single static feature or one-time setup.

Read Original Article →

What OT detection actually reveals

Securing operational technology (OT) environments requires a fundamentally different approach than standard IT security. While conventional IT tools excel at spotting network anomalies, they lack the critical physical process context needed to recognize when otherwise legitimate industrial commands are used for malicious disruption. OT detection platforms solve this by combining industrial protocol awareness with a deep understanding of normal operational behavior and physical constraints. A solid asset inventory is the foundational first step. From there, effective OT security relies on five core capabilities: monitoring industrial protocol anomalies, establishing strict baselines for process behavior, tracking engineering workstation activity, closely managing remote vendor access, and correlating traffic across the IT/OT boundary. Because OT involves physical processes where any disruption can impact safety, detection must be paired with structured, pre-planned response strategies. Automated actions are generally safe only at the IT or DMZ layers. Any direct intervention touching physical plant controllers requires clear authorization from operations teams to ensure production environments remain safe and stable.
Read Original Article →
Article Thumbnail

AI accelerates path from IT compromise to OT targeting

The article explains that AI is accelerating the path from IT compromise to OT targeting, making industrial environments more exposed than before. Attackers can now use AI to quickly analyze stolen IT data, map relationships, and identify the most valuable operational assets to target. This shortens the traditional gap between breaching corporate networks and moving into industrial systems. The piece notes that modern OT environments are increasingly connected to cloud services, remote access tools, and SaaS platforms, creating more entry points and making it harder to maintain clear separation between IT and OT. AI also helps attackers craft more convincing phishing messages, automate reconnaissance, and generate malware tailored to specific environments. At the same time, defenders struggle with legacy systems, inconsistent visibility, and slow patch cycles. The article argues that organizations must rethink OT security by improving asset inventories, tightening identity controls, and preparing for faster, more automated attack chains. Its message is steady: AI has changed the tempo of intrusions, and OT security must adapt to match that speed.

Read Original Article →

The next manufacturing cyber threat is manipulation of AI-driven decisions

As manufacturing becomes increasingly connected, the nature of cybersecurity threats is shifting. According to Pradipta Patro, Chief Information Security Officer at Polycab India Limited, the next major risk isn't just about keeping hackers out of the network. It is about protecting the artificial intelligence systems that influence critical operational decisions. If an attacker manipulates the data feeding an AI model, the system could make unsafe or faulty decisions without triggering traditional alarms. This goes beyond compromised information, directly threatening production quality, equipment reliability, and even worker safety on the factory floor. To address this, security must be built into factories from the ground up rather than added later as an afterthought. Manufacturers need complete visibility into all connected devices, strong network boundaries between IT and operations, and meaningful human oversight of AI decisions. Ultimately, cyber resilience must be treated as a core business continuity issue. The most successful factories will be those that can fully trust their automated systems because they secured the underlying data first.
Read Original Article →
Article Thumbnail

Digital twins in oil and gas: from simulation to real-time optimisation

Digital twins in the oil and gas sector are evolving from isolated engineering studies into practical tools that drive daily operations. Historically, creating a digital twin took months and became outdated as soon as the physical equipment changed. Today, advanced models can be built quickly, update automatically alongside physical wear, and connect across entire systems. A key shift is the use of physics-based modeling rather than just relying on historical data. Purely statistical models struggle when equipment faces new or unobserved conditions. By grounding the software in the actual laws of fluid dynamics and heat transfer, operators receive reliable, real-time recommendations they can trust. This approach accounts for uncertainty, allowing teams to optimize active equipment and reduce waste like methane flaring by safely pushing production closer to its true limits. Solving the challenge of scaling these tools in energy operations also opens the door for similar efficiency gains in other complex, high-demand environments, such as data centers and power grids.
Read Original Article →
Article Thumbnail

Data Sovereignty is Becoming a Design Principle for Enterprise AI

In the past, data sovereignty simply meant knowing the physical location of your company’s servers to meet regional laws. Today, artificial intelligence has fundamentally changed this. Because data now constantly flows through various external applications, language models, and processing tools, maintaining control over it has become much more complex. Instead of trying to lock down an entire organization, companies should focus on individual tasks. For example, processing public marketing information requires far less strict control than handling sensitive medical records. A major challenge is ensuring that safety rules follow the information wherever it goes. When original records are transformed into formats that AI can read, those new formats must inherit the same restrictions. Tracking this movement requires strong underlying data tagging. To manage this effectively, businesses should view sovereignty as a flexible budget. They must calmly weigh the need for strict control against the benefits of using advanced, external technology. Ultimately, building a flexible setup allows teams to continuously adjust their safety measures as rules and technology evolve.

Read Original Article →

Daily Tech Digest - October 14, 2026


Quote for the day:

“Growth is painful. Change is painful. But nothing is as painful as staying stuck.” -- N.R. Narayana Murthy

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


What is Beyond Zero? The latest Google-backed security trend explained

Google has introduced "Beyond Zero," a new security framework that evolves the well-known Zero Trust model to address the rise of artificial intelligence. As artificial intelligence agents become increasingly common in the workplace, traditional security measures struggle to keep up. Zero Trust focused primarily on verifying human access to networks and applications, but artificial intelligence agents operate with much higher speed and autonomy, performing countless tasks that require a more granular approach. Beyond Zero addresses this challenge by shifting the focus from broad access permissions to specific actions and resources. This means evaluating exactly what an agent is trying to do, what data it needs, and the context of its request, rather than just granting blanket authorization. The framework relies on five core principles: resource and action-based security, combined static and dynamic controls, enriched context for decision making, automated investigations, and immediate containment measures. Security experts suggest that businesses should view Beyond Zero as a natural evolution rather than a complete overhaul of their current systems. Organizations should start by applying these stricter controls to their most sensitive data and high-risk workflows, ensuring they understand exactly what permissions their automated systems hold and how to stop unauthorized behavior quickly.


Policy Latency Is the New Attack Surface. Breach Readiness Must Begin at the Top

As cyberattacks become faster and more automated, many organizations remain dangerously slow to respond because their internal policies cannot keep up. Today, attackers can move laterally in seconds, yet updating a security policy or granting an exception often takes weeks. This creates a critical vulnerability gap. To shift from simply trying to prevent attacks to ensuring the business survives them, organizations must start at the very top. Company boards and executives need to clearly define two key things: the maximum impact the business can absorb before failing, and the core systems that must absolutely remain operational during an incident. Governance requires a modern, streamlined policy structure to make these goals a reality. Instead of maintaining dozens of fragmented and contradictory rulebooks, companies should adopt six clear policies. This starts with a top-level Information Security Policy that declares the board's intent and survival thresholds. Beneath it sit five core policies governing acceptable use, breach readiness, digital system ownership, security operations, and data alongside artificial intelligence governance. By consolidating these rules, assigning clear human accountability, and ensuring policies are reviewed continuously, businesses can build an agile defense architecture that acts just as fast as the modern threats they face.


Building Determinism in an AI World: Why AI Agents Need Proof of Control

Security professionals are facing a major challenge as they shift from managing predictable systems to unpredictable artificial intelligence agents. Since these agents are probabilistic, they can execute the same task differently each time, creating dangerous blind spots. They might silently fail, ignore permission boundaries, or bypass security rules during complex tasks without leaving a clear log of their actions. The real issue is the verifiability gap—the inability to prove an agent actually stayed within its authorized limits rather than just taking its word for it. To solve this, the Advanced AI Society is developing Proof of Control, an emerging standard that creates a clear boundary between an agent's reasoning and a fixed, auditable record of its actions. This standard relies on cryptographic evidence to ensure every action is traceable, tamper-evident, and independently verifiable. While it does not judge the quality or fairness of the AI's output, it definitively answers whether the agent followed its assigned rules. Currently in draft form, Proof of Control will eventually integrate with existing security tools to help teams detect silent failures and unauthorized changes, ensuring trust relies on hard evidence rather than assumptions.


When Architecture Decisions Actually Apply

When feeding architectural decisions to AI coding agents, simply finding relevant documents is not enough. The author discovered through testing that agents often fail to respect architectural rules even when the correct guidance is in their context window. This happens because the system struggles to differentiate between a general suggestion and a binding rule that specifically applies to the code being changed. To solve this, engineering teams must separate relevance from authority and distinguish guidance from enforcement. Retrieval tools like semantic search are great at finding related information, but applicability determines whether a decision actually governs the specific artifact in question. Furthermore, some decisions are clear prohibitions that can be strictly enforced, like blocking a specific database tool. Other decisions are more nuanced and should serve as guidance rather than rigid, automated blockers. As teams increasingly rely on various AI coding tools, a shared and precise set of architectural rules must sit beneath these environments. The goal is not to force every architectural choice into a strict rule, but to ensure that decisions the team has already settled do not regress into mere suggestions when an agent takes over the keyboard.


Data residency in Google’s borderless Lakehouse: the cache follows the query, not the data

Google Cloud's borderless Lakehouse allows companies to query their data directly where it currently lives, whether that is in Amazon, Microsoft, or internal company servers, without ever having to move it into a central location first. This flexible approach speeds up analytics and avoids locking businesses into a single vendor. However, in order to operate quickly and efficiently, the system creates a temporary working cache of the accessed data in the specific Google Cloud region where the query runs. This cache relies entirely on Google-managed encryption keys, meaning that customer-managed keys are not currently supported. For heavily regulated industries like banking and insurance, operating in regions with strict data residency laws, this caching mechanism poses significant compliance challenges. Countries like Malaysia, which enforce rigid rules on cross-border data transfers, require organisations to actively track where their data physically sits at all times. While Google states that fast inter-cloud connections allow queries to remain within a single jurisdiction, some countries simply do not yet have a local Google Cloud region. Consequently, the businesses themselves remain entirely responsible for configuring their tools correctly to ensure that sensitive information is never accidentally cached outside of their approved legal jurisdictions.


Designing for data sovereignty: Building architectures that keep control where it belongs

The article outlines the pressing need for modern businesses to adopt data sovereignty as a fundamental design principle, rather than treating compliance as a secondary addition. While earlier tech strategies focused on expanding storage for massive amounts of data and shifting to cloud services for artificial intelligence, the primary challenge today is maintaining strict control over data jurisdiction, access, and governance. This is complicated by the fact that data residency (simply where files are stored) does not guarantee sovereignty, which must account for remote access, international backups, and cross border artificial intelligence processing. Artificial intelligence pipelines introduce even greater risks by constantly moving, copying, and transforming data, obscuring its origin and ownership. Traditional central data hubs fail in this environment, as they create duplication and make policy enforcement messy and complex. To solve this, companies should weave sovereignty directly into their data architecture from day one. This involves identifying sensitive information early, mapping data flows instead of just storage, keeping governance consistent without forcing physical centralization, and ensuring flexible deployment options. By designing adaptable frameworks that adjust to changing regulations rather than resisting them, businesses can turn compliance into an operational strength and easily maintain a confident grasp on their most vital corporate data in the future.


Why downturns can make innovation greener

Green innovation is vital for transitioning to a low-carbon economy, but many worry that economic downturns might slow its progress as companies cut back on investments. However, recent research reveals a surprising divergence: while general innovation drops during economic contractions, green innovation actually rises. By analyzing patent applications and their response to economic shocks, researchers observed that companies decrease their overall patenting but actively shift their focus toward green technologies. The core reason for this behavior lies in the timing of profits. Because the market for low-carbon solutions is expected to grow over the coming years, the value of green patents is heavily tied to future returns. This makes them less sensitive to short-term economic dips compared to non-green patents. Furthermore, when general innovation declines, the demand and wages for skilled scientists also drop. These lower research costs disproportionately benefit green projects, encouraging further investment. Ultimately, this means that temporary recessions can persistently shape the direction of technological progress. For policymakers, this suggests that offering research and development subsidies during downturns might be highly effective. It is an opportunity to get more innovation per dollar while accelerating the shift toward sustainable technologies.


Agentic AI Is Turning a Decade of Enterprise Data Debt Into Operational Risk

For years, businesses have accumulated hidden "data debt"—inconsistent definitions, outdated policies, and lingering permissions—because human workers always acted as a buffer. If two departments defined a metric differently or multiple versions of a document existed, an experienced employee would catch the discrepancy, apply the missing context, and make the right call. The process was slow, but it prevented mistakes. The arrival of agentic artificial intelligence removes this human safety net entirely. These new autonomous systems are built to interpret a goal, retrieve information, and execute actions across different platforms without stopping to ask questions. If the underlying data is ambiguous or contradictory, the agent will simply assemble what looks like a reasonable answer and proceed to act on it. An artificial intelligence system does not have to hallucinate to cause serious problems; it only needs to pull accurate information that lacks the right context, version, or effective date. Ultimately, companies do not just have an artificial intelligence challenge; they have an action-readiness problem. Deploying autonomous agents exposes years of unresolved data debt, immediately turning old inconsistencies into real operational risks.


CIOs must rethink intellectual property protection in the age of AI coding

The article explains why CIOs need to rethink intellectual property protection as generative AI and autonomous coding tools become deeply embedded in software development. It notes that developers are shifting from writing code themselves to supervising and reviewing AI‑generated outputs, which boosts productivity but creates new uncertainty around ownership. Current IP frameworks are built on human authorship, and content produced entirely by machines does not automatically qualify for copyright protection. As AI contributes a growing share of enterprise code, organisations may struggle to distinguish human‑created components from AI‑generated ones unless they establish strong governance and documentation practices early. The article warns that by 2032, more than 60% of critical corporate code may not be protected as IP because it lacks sufficient human authorship. This creates a strategic dilemma: the same AI tools that accelerate innovation can also weaken long‑term protection of proprietary assets. The piece highlights risks such as commoditisation of core software, unclear ownership of AI‑generated designs, and reduced ability to defend competitive advantages. It encourages CIOs to implement safeguards that preserve authorship records, clarify contribution boundaries, and ensure that valuable digital assets remain legally defensible as AI becomes a central part of the development lifecycle.


"Works on My Machine" Is an Architecture Problem

The "works on my machine" problem is not just a minor annoyance but a serious architectural flaw where the execution environment exists outside version control. When software behaves correctly on a developer's computer but fails elsewhere, it means the system lacks a complete, reproducible definition of its inputs. Hidden dependencies like host time zones, locales, file system behavior, native libraries, and build tools cause unpredictable behaviors if left undocumented. To build a reliable architecture, developers must make these environmental assumptions explicit and verifiable. This involves locking application dependencies and controlling the toolchain used to build the software. While containers reduce inconsistencies, they do not erase them entirely, as issues like CPU architecture differences and floating image tags remain. Therefore, the development environment itself should be treated as code and captured in version control. Production and testing environments should also be tightly defined, ensuring that default settings like time zones are explicitly set at application boundaries. By validating CPU targets, pinning base images, and making runtime identities observable, development teams can transform mysterious environment failures into traceable defects. Ultimately, a strong software architecture explicitly connects the source code to the machine it runs on.

Daily Tech Digest - September 23, 2026


Quote for the day:

"Every great story on the planet happened when someone decided not to give up, but kept going no matter what." -- Spryte Loriano

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 26 mins • Perfect for listening on the go.


Observability should start with business outcomes, not infrastructure

The article, "Observability should start with business outcomes, not infrastructure" by Vjacheslav Mikitjuk, argues that technical metrics alone are inadequate for understanding the actual performance of IT systems. The article points out that while an engineering dashboard might show a system running efficiently, it could simultaneously be experiencing a serious customer-facing failure. Therefore, IT teams need to translate technical severity into business severity to provide management with a clear picture of the impact on customers, transaction values, and overall business operations. Mikitjuk suggests that observability needs to follow a chain starting from business outcomes down to telemetry. This approach involves defining service objectives based on user experience rather than just infrastructure metrics. He emphasizes that the translation between technical and business performance should be a shared responsibility across the organization, involving business leadership, product owners, and engineering teams. Furthermore, he advises that business observability must be designed proactively during the service and product design phases, rather than being an afterthought during an incident. The article also highlights that observability priorities should be determined by business criticality, focusing efforts where degradation would have the most significant consequences. Finally, while AI can assist in interpreting data, it requires the foundational context of business goals to be truly effective.


Redefining Cyber Recovery Requirements in the Era of Modern Cyberattacks

Cyber recovery is fundamentally different from traditional disaster recovery, requiring a practical approach to combat modern threats. While disaster recovery focuses on quickly restoring the most recent backup after an outage, cyber recovery prioritizes data integrity. Because attackers often dwell inside networks for days or weeks before causing damage, the newest backup is usually infected. Therefore, IT teams must work backward to find a genuinely clean copy. This process is complicated by the fact that the vast majority of modern intrusions leave no malicious files behind. Instead, attackers use stolen credentials and existing administrative tools to move silently. As a result, standard antivirus scans on powered-off backups are no longer sufficient. To ensure a backup is truly safe, organizations must power it on and carefully observe its behavior over time to detect hidden threats. Because powering on a compromised system risks reinfecting the entire network, this behavioral analysis must happen inside a strictly isolated clean room. Solutions like VMware Cloud Foundation and Advanced Cyber Compliance automate this critical testing environment. By integrating secure, quarantined recovery workflows, organizations can confidently identify uncorrupted data and restore operations safely, moving beyond outdated backup strategies to address the reality of modern fileless attacks.


Data embassies and sovereign dispersion

Data embassies and sovereign dispersion present a new approach to managing the trade-off between data residency and resilience, moving beyond traditional data localization. Driven by geopolitical instability and cyber threats, governments—particularly smaller, highly digitized nations like Estonia—are establishing legally protected digital enclaves on foreign soil. Unlike multi-region cloud backups subject to host nation laws, genuine data embassies operate under bilateral treaties granting them diplomatic immunity. They maintain an active "digital twin" to ensure core civic services, like tax systems and central bank ledgers, run smoothly during domestic crises such as cyberattacks or power failures. Gartner anticipates that by 2029, 15% of nations in unstable regions will have formalized data embassy agreements. Estonia established the first in 2015, partnering with Luxembourg for its Tier IV data centers, setting a precedent that requires specific intergovernmental contracts. Security relies on principles like "encryption as a border," ensuring the origin state retains decryption keys. While replicating this model is challenging for private enterprises, IT leaders can adopt similar technical resilience strategies. By decoupling encryption keys from cloud providers and avoiding over-reliance on a single vendor or location, businesses can enhance their operational continuity and mitigate risks associated with physical data concentration.


How to Handle the Growing Data Complexity Challenge in Cyber Incident Response

The article explains that cyber incident response has become far more complicated than simply handling large volumes of data after a breach. Modern organizations generate information across cloud platforms, collaboration tools, mobile devices, enterprise applications, and third‑party services, creating a sprawling and interconnected data environment. Regulators now expect investigators to identify and analyze a wider range of sensitive information, from traditional personal data to device identifiers, geolocation details, and behavioral patterns. The piece highlights how today’s breaches often involve structured and unstructured data, multimedia files, and systems that store overlapping records, making it difficult to determine what truly matters. Traditional keyword‑based search methods are no longer enough, especially when investigators must uncover “unknown unknowns” hidden across diverse systems. AI‑assisted tools can help by recognizing entities, relationships, and context, but the article stresses that any AI‑driven process must remain legally defensible through documented workflows, validation, and human oversight. Notification decisions—often the hardest part—require consolidating identities, applying jurisdictional rules, and ensuring accuracy at scale. The author concludes that organizations need a disciplined, context‑aware approach to data mining, combining technology, expertise, and defensible processes to understand risk and respond confidently under tight timelines.


7 decisions that make an Azure landing zone enterprise-ready

Creating an effective, enterprise-ready Azure landing zone requires thinking beyond basic reference architectures to build a platform that supports engineering teams rather than hindering them. The article highlights seven key design decisions to achieve this balance between security and developer autonomy. First, treat the landing zone as an operating model—not just a network—by separating platform resources from application workloads using management groups and subscriptions to create clear governance boundaries. Second, opt for Azure Virtual WAN over a self-managed hub-and-spoke setup to simplify cross-region connectivity and route management. Third, integrate your security model, such as a next-generation firewall, directly into the routing architecture from day one rather than bolting it on later. Fourth, implement governance as guardrails that manage risk without turning routine engineering tasks into a constant exception process. Fifth, separate your observability tools for operational health from your SIEM tools for security monitoring to reduce noise and clarify responsibilities. Sixth, treat CI/CD networking as a core platform component, using solutions like private GitHub runners to securely deploy to isolated resources. Finally, ensure an active-active architecture truly works by making both regions fully production-ready and capable of independently supporting the workload during a failure.


AI adoption in OT security accelerates as legacy infrastructure and poor data expose readiness gaps

Many industrial organizations are eager to implement AI for operational technology (OT) security, but their current infrastructure often isn't ready. A recent survey highlights that while nearly 88% of organizations are using or planning to use AI, under 8% have deployed it across multiple functions. The main hurdles are poor data quality and the challenges of integrating AI with legacy systems. Most industrial facilities were built long before AI was a consideration, resulting in control systems that produce inconsistent data. Experts point out that legacy environments frequently lack the necessary identity and access management infrastructure and cloud connectivity required for modern AI models. This gap is especially problematic because AI depends on high-quality data and complete asset context to function accurately. Without these, AI tools can produce incorrect assumptions, leading to false positives or missed threats. Furthermore, poor data quality in OT can have serious physical consequences, including equipment damage or safety incidents. To make AI work effectively and safely in these environments, organizations must first focus on improving their architectural foundations. This includes better data normalization, consistent telemetry, and modernized security architectures that provide a stronger base for AI-enabled tools.


Operational Technology Scope Expands as Security Matures

The article describes how operational technology (OT) security has matured as industrial organizations face more frequent and costly cyber incidents. According to Honeywell’s 2026 OT Cybersecurity Benchmark Report, major attacks now cause an average of 16 hours of downtime, with losses reaching up to $500,000 per hour. As a result, companies across energy, manufacturing, healthcare, maritime, and other critical sectors are shifting from a narrow, technology‑centric mindset to a broader focus on business resilience. Leaders increasingly view OT security as essential to safety, uptime, and service continuity, especially as digital connectivity expands across industrial control systems, field devices, building management systems, IoT sensors, and medical equipment. The report shows that organizations with mature programs detect and respond to threats faster, largely because they maintain strong asset inventories and continuous monitoring. Yet visibility remains a major gap: only one‑third have integrated OT systems into a centralized SOC, and just one‑fifth continuously monitor IoT devices. Legacy systems, staffing shortages, and budget constraints add further strain. Many organizations are adopting AI for detection and monitoring, though fully autonomous decision‑making remains rare. The article concludes that resilience depends on extending security across every connected system and closing visibility gaps that still hinder effective response.


I Wasn’t Trying to Predict the Future. I Was Trying to Build One I Could Tolerate

The article is a reflective piece in which the author explains that his work with AI did not begin as an attempt to predict the future but as a practical response to a narrowing set of acceptable options. He frames his journey not as a heroic narrative but as a form of “niche construction,” a security practice focused on shaping an environment that can support more viable futures. Throughout his career in cybersecurity, supply‑chain assurance, information sharing, and industrial systems, he learned that security is rarely about protecting a single object. Instead, it is about maintaining the conditions that allow systems to survive and adapt. He illustrates this through stories of living on self‑built boats, where survival depended on constant maintenance, awareness, and the ability to respond to change. When his own circumstances tightened in 2025, he turned to a large language model as one of the few available tools and began a sustained, iterative collaboration that produced frameworks, documents, code, and new institutional structures. He describes this as building a generative set—an evolving system that creates new possibilities rather than following a fixed plan. The article concludes that meaningful security often comes from constructing environments where better futures can emerge, not from defending the present in isolation.


CISOs can no longer ignore the nation-state threat

The accelerating use of AI by nation-state actors is forcing Chief Information Security Officers (CISOs) to rethink their threat models and treat geopolitical threats as urgent enterprise risks. Historically, CISOs focused on quickly expelling adversaries from networks, while government agencies preferred to monitor them for intelligence. However, AI is now lowering the barrier to entry, allowing even amateur cybercriminals to launch sophisticated attacks that mimic nation-state activity. This shift blurs the line between national security threats and ordinary business risks. A major challenge for organizations is recognizing their own strategic value to foreign adversaries. Companies in seemingly benign industries, such as agriculture, can become targets if they possess valuable intellectual property or supply chain access. AI worsens this by compressing the time between a vulnerability's discovery and its exploitation to mere seconds, making traditional patching processes insufficient. To adapt, security leaders must recognize that AI enables faster, broader pre-positioning by attackers within organizational assets. Experts advise CISOs to prepare for fully autonomous attacks, plan to operate through compromises during major disruptions, and focus on core security controls like zero trust and multi-factor authentication. Crucially, CISOs need board-level support and funding to implement these necessary resilience measures.


AI slop is creating more work, not less. Here’s why

The rise of generative AI in the workplace was promised to boost productivity, but it is increasingly resulting in "AI slop"—low-quality, generic, and often unverified content that shifts the workload onto other employees. In a recent Today in Tech episode, host Keith Shaw and Commvault’s Chris Bevil discussed how tools that instantly generate emails, reports, and presentations create a hidden "review tax." While an executive might save time using AI to summarize a long document or draft a memo, the receiving employees must often spend significant time fact-checking, correcting context, and deciphering vague, polished-but-empty drafts. This disconnect explains why executives frequently report high productivity gains from AI, while non-managers feel bogged down by new verification processes. AI slop resembles a "first draft wearing a tie"—it looks professional and confident on the surface but lacks underlying substance or clear judgment. As this unverified content spreads rapidly across organizations, it risks becoming accepted corporate knowledge. To truly benefit from AI, companies must move beyond simply generating more content and emphasize proper governance, human review, and clear workflows to prevent productivity gains at the top from becoming a burden at the bottom.

Daily Tech Digest - September 20, 2026


Quote for the day:

“The more I read, the more I acquire, the more certain I am that I know nothing.” -- Voltaire

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


Brain-Machine Interfaces Are Advancing: What Leaders Need to Know About Neurotechnology

The convergence of artificial intelligence, smaller electronics, and advanced materials is accelerating the steady development of brain-machine interfaces, allowing for practical communication between human brains and digital systems. While this field is currently focused on healthcare, with recent clinical studies showing paralyzed patients successfully using neural interfaces to control devices and communicate independently at home, its applications will soon expand. In the near future, industries such as education, manufacturing, and assistive technology will likely adopt these emerging tools to improve human performance and overall accessibility. By the end of the decade, the technology is expected to feature more accurate signals, less invasive hardware, and better machine interpretation of brain activity. Rather than guessing which specific device will dominate the market, organizations and leaders should prepare for these predictable advancements now. This means tracking improvements in neural decoding, exploring diverse interface methods like ultrasound, and considering how neural data might fit into future product lines. Just as importantly, the widespread use of neurotechnology will create new challenges surrounding data privacy, system compatibility, and user control over sensitive neural information. Solving these practical problems will offer significant opportunities for those who calmly anticipate the steady progress of neural engineering and plan accordingly.


Opinion: Tech enables transformation, people achieve it

Daire Cunningham’s article explores why so many organizations struggle to get real value from artificial intelligence, despite the technology being widely available. He notes that while 88% of businesses use AI in some capacity, only a third have managed to scale it across their operations. The core issue, he argues, isn’t a lack of access to advanced tech, but rather the underlying condition of the organizations trying to use it. When companies rush to adopt AI, they often start by looking for a specific tool instead of identifying the actual business problem they need to solve. To succeed, leaders must work backward: map out their processes, figure out where the information is kept, and spot the real bottlenecks. A major roadblock is poor data readiness—many businesses have years of accumulated, disorganized data and permissions. AI tends to expose these underlying flaws rather than cause them. Ultimately, Cunningham believes digital transformation is about rethinking how work gets done, not just adding new software. While AI can process data faster and tackle complex tasks, human judgment and oversight remain essential. True transformation happens when a company prepares its data foundation and empowers its people to use technology responsibly.


CIOs offer guiding principles on how to achieve AI sovereignty

The article discusses the growing importance of AI sovereignty for Chief Information Officers (CIOs). This concept is centered on maintaining control over an organization’s entire AI ecosystem, which encompasses data, models, and the infrastructure hosting those models. As AI technology becomes increasingly integrated into business operations, organizations face mounting risks related to data privacy, regulatory compliance, and potential vendor lock-in. To manage these challenges effectively, CIOs recommend establishing clear guiding principles. First, it is crucial to create a comprehensive inventory of all AI resources currently in use, as you cannot manage what you do not track. Second, organizations must implement robust data and usage controls to monitor information flow and quickly identify any policy violations. This proactive approach helps secure sensitive data. Third, companies should update their incident response plans specifically to address potential AI-related breaches, ensuring they can act swiftly if issues arise. Finally, maintaining transparency and auditability is essential. Knowing who accessed data and how AI tools influence decision-making helps build trust and ensures regulatory compliance. Rather than viewing AI sovereignty as a simple compliance checklist, leaders should treat it as a fundamental strategy for the long-term success and security of the enterprise.


Children's Data Protection in the Age of EdTech and Platform Design

The digital age has made children’s data collection widespread, from location tracking and educational data to behavioral and voice information. While some of this is meant for learning or safety, the concern is that such data can be used for profiling, targeted ads, or boosting engagement without parental consent. This has made data protection laws surrounding children increasingly relevant. India's Digital Personal Data Protection (DPDP) Act, 2023 defines a child as anyone under 18, which is a higher threshold than seen in many other countries. This act requires platforms to secure verifiable parental consent before processing a child’s data and forbids processing that could harm a child’s well-being. Additionally, the DPDP Act bans the tracking, behavioral monitoring, and targeted advertising directed at children, though it provides some exceptions for safe uses in healthcare, education, or child safety. Internationally, there are variations in how children's data is handled. In the United States, COPPA applies to children under 13, while the European Union’s GDPR sets the default age at 16, though member states can adjust it to 13. The UK’s Children’s Code requires platforms that children are likely to use to have high privacy settings by default. For platforms dealing with children's data, balancing data retention limits with educational needs requires clear strategies and compliance checks.


Most enterprises are failing to translate talk into meaningful dependency mapping

The recent feature on digital sovereignty highlights a significant gap between what organizations want and what they can actually achieve. While most companies express a strong desire to regain control over their digital infrastructure, the reality is that true independence remains out of reach for many. The truth is that achieving digital sovereignty is not simply about building internal data centers or buying local software; it requires deep visibility into existing information systems and having credible exit options from major service providers. Unfortunately, most enterprises currently lack these fundamental building blocks. Over the past fifteen years, a rush toward cloud computing has left many businesses heavily dependent on a handful of dominant technology giants. This dependency makes it incredibly difficult to pivot or change providers without facing steep costs and major operational disruption. As artificial intelligence becomes central to business strategy, the stakes for retaining control over data and computing power are higher than ever before. The article suggests that instead of pursuing total independence, leaders should focus on preserving choice. By prioritizing flexible tools and establishing clear governance, organizations can gradually build resilience. Ultimately, sovereignty is about making smart decisions today that prevent complete vendor entanglement in the future.


Agentic Systems and Design Patterns

The shift toward agentic artificial intelligence marks a move from simple text generation to setups that can plan, take action, and learn from their mistakes. When building these systems, developers must first choose an overall structure. A single agent approach is easier to build and manage, making it a great starting point, though it can struggle with complex or extended tasks. Conversely, a multiple agent system uses an orchestrator to delegate work to specialists, which boosts reliability through teamwork but requires careful coordination. Beyond the basic structure, six core design patterns drive how these models function. The ReAct pattern mixes logical thinking with concrete actions in a loop, while CodeAct allows agents to write and test code to achieve their goals. Self reflection acts as an internal critic to refine outputs and fix errors. Basic tool use lets agents interact with outside software, and Agentic RAG improves how they fetch and verify information. Finally, the multiple agent workflow handles massive tasks by dividing them into smaller parallel jobs. For the best results, start with a simple single agent setup and only add complexity when the task demands it. Strong safeguards, like strict iteration limits and clear tool definitions, keep these systems reliable and easy to monitor.


What OT Resilience Actually Controls

The article from SC Media explains that recovering operational technology (OT) after a cyber incident requires a fundamentally different approach than recovering standard IT systems. While IT disaster recovery focuses on system availability—getting servers and applications back online—OT recovery requires "safe-state validation." This means ensuring the manufacturing process can be controlled safely before restarting production. The challenge is that standard IT backups often miss crucial OT engineering data, such as process configurations, device programming, and safety system logic. Without these, a restored system might appear functional but lack the specific parameters needed to operate safely. The author outlines five common failure scenarios in OT resilience, including ransomware affecting control systems, vendor platform outages, and control logic tampering. These scenarios highlight the need for specialized OT backup architectures and recovery procedures. Ultimately, true OT resilience involves validating configurations at the device, system, and process levels, often requiring specialized engineering expertise. This validation step adds time to the recovery process but is essential to prevent unsafe conditions that could lead to physical harm or environmental damage.


Achieving data sovereignty for SaaS with confidential containers and quantum-safe networking

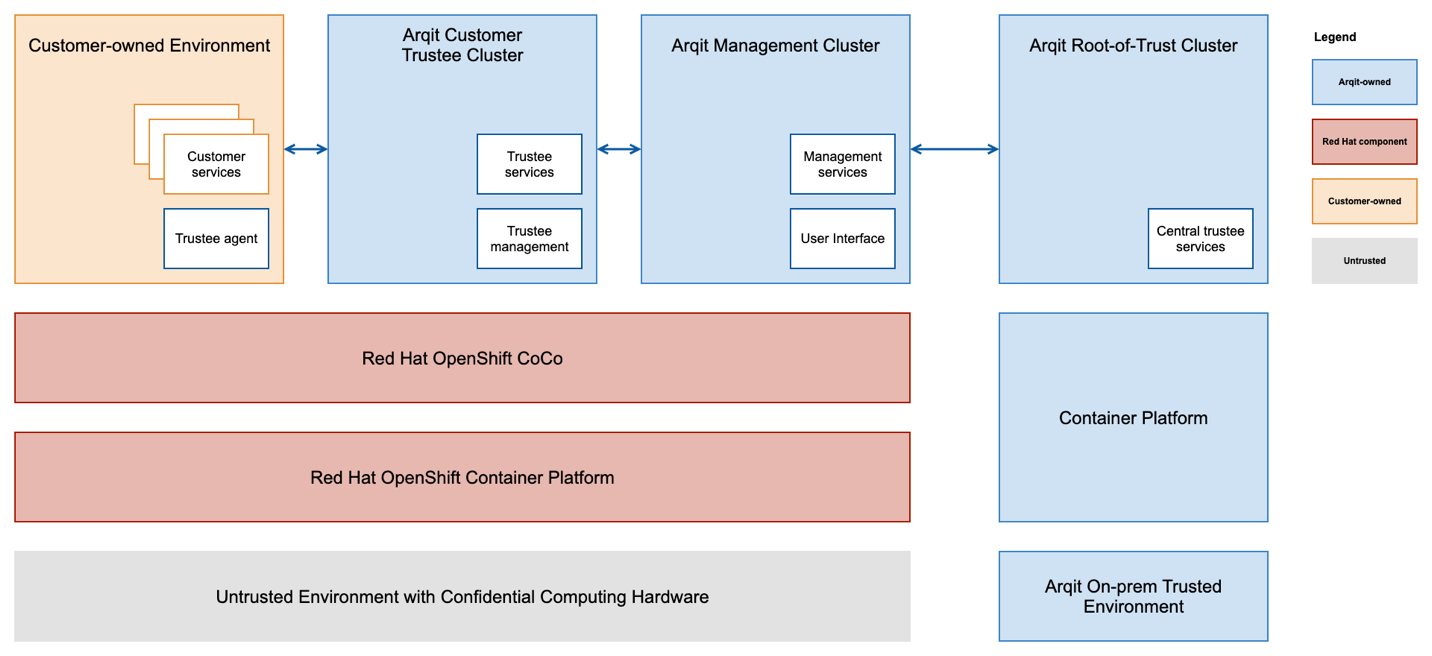
Software vendors hosting services on the public cloud face increasing pressure from customers who want to keep their data secure and private. Often, customers prefer on-premise solutions, which are harder to manage and scale for vendors. A better approach allows vendors to keep their services in the cloud while offering robust security through cryptographic controls, specifically using confidential computing. This technology secures data processed in untrusted environments by isolating it in a trusted execution environment (TEE). Red Hat and Arqit have introduced a setup that uses confidential containers and quantum-safe networking to protect data in transit. They applied this to Arqit's Encryption Intelligence (EI) platform. In this setup, services and data are isolated from the host environment, allowing customers to maintain control over their data while protecting the vendor's intellectual property. The architecture involves three clusters operating in the untrusted environment, communicating via a quantum-safe connection. Trust is established by an outer trustee in a trusted on-premise environment, which verifies the inner trustee in the cloud. This combination of confidential containers and quantum-safe protection for data in transit offers a practical alternative to on-premise deployments, providing strong assurance over data security and sovereignty for both vendors and customers.


AI-led SOC infrastructure shifts from raw data to outcomes

The article discusses a shift in how modern Security Operations Centres (SOCs) measure success in an AI-driven environment. Historically, SOCs focused on volume metrics, such as alerts processed or data ingested, but this model struggles against modern threats across distributed environments. Today, the focus is shifting to measuring outcomes like risk reduction, analyst capacity, and decision quality. The traditional volume-driven model leads to rising costs, overwhelmed analysts, and incremental improvements, failing to deliver clear returns on investment. While AI is viewed as a solution, it has struggled to deliver value when treated simply as an overlay, lacking transparency and integration. To overcome these limits, organizations must build SOCs around productivity rather than throughput, connecting technology investments with operational impact. In this model, AI isn't measured by its theoretical capability but by the work it completes alongside human analysts. A critical component is the use of "Agentic AI" as an execution layer, which coordinates investigations and decisions rather than functioning in isolation. For AI to be effective, it must also be governed to ensure actions are explainable and align with organizational policies, allowing security leaders to demonstrate responsible use and measurable security outcomes.


Data sovereignty is a control problem, not a geography problem

The article argues that data sovereignty is fundamentally about control, not geography. Many organizations assume that storing data within national borders is enough, but the author explains that this view is too narrow. True sovereignty depends on knowing who controls identities, administration, infrastructure, and legal authority over the data. Recent events have exposed how fragile digital infrastructure can be, from attacks on subsea cables to large‑scale outages like the CrowdStrike incident, which disrupted critical services worldwide and led to major financial losses. At the same time, new regulations and the rise of AI have increased the stakes, since sensitive information and intellectual property now flow through cloud‑hosted models governed by foreign jurisdictions. The article stresses that organizations often lack visibility into where their data lives, who can access it, and which laws apply. To regain sovereignty, they must demand transparency from providers, understand dependencies, and treat governance as an architectural requirement rather than an afterthought. Cost and speed still matter, but they can’t outweigh resilience and accountability. Sovereignty, the author concludes, isn’t about abandoning the cloud—it’s about ensuring organizations retain meaningful control so they can manage risk and respond confidently when incidents occur.

Daily Tech Digest - September 19, 2026


Quote for the day:

“The only true wisdom is in knowing you know nothing.” -- Socrates

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Building a pre-emptive security architecture — what is it and how can your business adopt one?

With the rise of AI-driven cybersecurity threats, conventional "detect and respond" frameworks are struggling. The speed of attacks has increased, and the volume of vulnerabilities is projected to skyrocket, leading to practitioner burnout. This has prompted a shift toward a pre-emptive security architecture. Instead of waiting to respond to an intrusion, pre-emptive security aims to stop attacks before they cause damage by placing controls directly in the attack path. It's an architectural approach, connecting security across layers—like users, applications, and data—so that a breach in one layer doesn't compromise the whole system. This strategy focuses on anticipating and preventing breaches rather than just limiting the fallout. Key elements of this approach include denying access, deceiving attackers with decoys, and disrupting emerging threats. Techniques like zero trust, secure code development, and confidential computing are central to this model. To implement it, businesses should first identify sensitive data and map out vulnerabilities. This involves understanding potential attack paths and applying the principle of least privilege. Regular penetration testing and continuous monitoring are essential to ensure these controls work without disrupting legitimate business processes. While pre-emptive measures are crucial, they are meant to enhance, not replace, existing security alerts.


Strong fundamentals make next-gen security possible

Instead of constantly chasing the newest security tools, organizations should focus their efforts on mastering five foundational practices to effectively protect their systems. First, businesses must maintain a clear, accurate inventory of all their physical and digital assets across every environment. You simply cannot protect what you do not know exists. Second, carefully managing user identities is critical. Implementing simple but strong measures like multifactor authentication or passkeys significantly lowers the chance of compromised accounts. Third, security strategies should match the specific needs and risk tolerance of the business. By identifying the most valuable data and establishing clear priorities, security teams can focus their resources exactly where they matter most. Fourth, while preventing attacks is important, organizations must also prioritize true resilience. This means keeping secure backups, writing clear recovery plans, and actively practicing those plans so employees know exactly what to do during a crisis. Finally, security professionals and business leaders need to speak the same language. By translating technical risks into clear business impacts, such as potential financial costs, teams can make better decisions together. Mastering these basic, everyday practices may not seem exciting, but it provides a much stronger defense against real threats than simply buying the latest technology.


The cloud outage that should terrify the CIO

A recent Microsoft Azure outage that simultaneously knocked out major AI services, including ChatGPT, Claude, Grok, and Copilot, serves as a stark warning for business leaders. The disruption highlights a growing, hidden vulnerability: concentrated cloud dependency. As organizations increasingly weave artificial intelligence into their core operations, they are inadvertently stacking their critical workflows on the same shared infrastructure. When a major cloud region fails, the impact is no longer limited to a single application going offline. Instead, automated business processes, financial transactions, and customer support pipelines can grind to a sudden halt, leading to massive financial losses. What makes this risk especially dangerous is that many companies are completely unaware of their true exposure. Organizations rely on countless third-party software vendors, who in turn depend on major cloud providers. This creates a chain of invisible dependencies where an outage at a provider you do not directly use can still freeze your business. To protect their operations, technology leaders must actively map their entire software dependency chains, including the artificial intelligence layer. They need to design their critical systems to smoothly switch to backup providers during failures and clearly present the financial risks of cloud downtime to their executive boards.


The Control Plane Is Not the Trust Plane

The article from Security Boulevard, titled "The Control Plane Is Not the Trust Plane," explores the evolving landscape of AI governance. The author argues that while control planes—systems designed to govern what an AI agent is permitted to do—are necessary, they are no longer sufficient. As organizations deploy more AI agents, a critical gap emerges: the need to verify history, provenance, and the actual context of an action. To address this, the author proposes a new conceptual layer: the "trust plane." A control plane answers questions about possibility, such as which identities exist and what policies apply. In contrast, the trust plane answers questions about history, focusing on why a specific action belongs to a legitimate chain of authority. It requires "evidence receipts" to understand the full context—who initiated the request, what identity was used, and what was actually accepted by the receiving system. The article emphasizes that trust should not rely on centralization, which creates single points of failure. Instead, it advocates for a distributed approach where nodes retain local identity while sharing verifiable evidence. Ultimately, as AI systems transition from tools to active participants, securing both control and trust is vital for maintaining accountability and operational integrity.


California child-safety laws expand age checks to addictive feeds, AI chatbots

California has introduced a series of new child safety laws that regulate artificial intelligence chatbots and social media platforms, establishing the state as a leader in digital age verification. These bills aim to create safer online environments for children by making device based age checks the standard. A central piece of this legislation is a new rule requiring independent safety audits and annual risk assessments for companion chatbots. This measure was inspired by a tragic case where a teenager was allegedly influenced by a chatbot to end his life. Major industry players, including the creators of ChatGPT and media advocacy groups, have voiced their support for these rules. In response, artificial intelligence providers are already implementing mandatory safety modes for users under eighteen. Additionally, the new laws ban social media platforms from offering addictive features to children under sixteen. Companies must now verify age before enabling these tools, with severe financial penalties of up to fifty thousand dollars per affected child for those who knowingly violate the rules. Finally, lawmakers clarified how age signals should be shared by operating systems, ensuring that open source developers are not unfairly burdened. As artificial intelligence continues to grow, other states are expected to adopt similar protective measures.


Enabling the next generation of AI data centers

The article describes how AI is forcing a fundamental rethink of data center design, mainly because traditional facilities were built for predictable CPU workloads and steady growth. AI training clusters, by contrast, demand far higher power density, faster deployment timelines, and more complex infrastructure coordination. The author explains that developers are now planning gigawatt‑scale campuses where power, cooling, transmission, water, and long‑term operations must be designed as one integrated system rather than separate components. Site selection has become a balancing act: inexpensive land may lack grid access, while power‑ready sites may come with long interconnection delays or higher costs. To keep projects moving, many operators are turning to hybrid or off‑grid power solutions, including gas generation, batteries, and microgrids, even though these approaches require more capital and careful permitting. Cooling is also shifting toward liquid systems and thermal storage to handle dense AI loads and reduce peak energy use. The article stresses that early permitting work and cross‑discipline alignment are now essential, because regulatory, environmental, and community constraints can shape a project as much as engineering choices. Ultimately, the piece argues that success depends on making early, realistic decisions that translate AI demand into infrastructure that can be delivered at speed and scale.


Is Your Organisation’s Data Secure?

Data security is critical, and many free, open-source tools now offer robust protection, making strong encryption accessible to organizations of all sizes. Encrypting data prevents unauthorized access by converting plaintext into unreadable ciphertext, which requires a specific key to decipher. The transparency of open-source software allows a global community of experts to continuously evaluate the code, often identifying vulnerabilities faster than with closed, proprietary systems. A comprehensive security strategy must address data in two states: at rest and in transit. Data at rest, such as information stored on hard drives or databases, is a high-value target for attackers. Encrypting this data ensures that even if physical devices are stolen, the information remains secure. Data in transit moves between systems over networks like the internet and can be intercepted. Tools like OpenSSL, Let's Encrypt, WireGuard, and OpenSSH provide essential encryption for data in transit, securing web traffic, remote access, and file transfers. Regulatory frameworks worldwide further emphasize the importance of data encryption to protect personal and financial information. By leveraging these open-source tools, organizations can build resilient defenses against data breaches.


Cybersecurity Work-Life Balance Starts With Actually Turning Off

The constant pressure of defending against relentless threats has made it incredibly difficult for cybersecurity professionals to step away from their work. Sam Van Ryder, a veteran in operational technology security, emphasizes that achieving a healthy balance requires individuals to genuinely disconnect, while employers must actively protect their team's downtime. Often, organizations talk about this balance as a benefit without creating the environment necessary for people to log off. With ongoing staffing shortages and constant alerts, the inability to rest is no longer just a personal wellness issue; it is a direct security risk. When security teams are exhausted, their judgment naturally suffers, creating the exact vulnerabilities that attackers actively look to exploit in critical systems. Recognizing this, leaders need to ensure time off is fully respected. This means no emails, no emergency messages, and no checking the daily news. If a team member tries to work on their day off, leaders should send them back to their rest. Furthermore, recovery should not be limited to an annual vacation. Regular breaks throughout the year are completely essential for maintaining a strong and focused workforce. Ultimately, the most effective way to maintain long-term security is for individuals to step back, turn everything off, and simply recharge.


Beyond Age-Gating: Regulating Platform Design for Child Safety

India's approach to child online safety currently relies on basic age restrictions and rapid content removals, but these conventional measures fail to address a much deeper issue: structural platform design. With millions of children accessing the internet daily, the conversation must shift from simply blocking entry to reforming how digital services are actually built from the ground up. Features such as recommendation algorithms, automatic video playback, and default direct messaging settings shape the online experience of a child and their exposure to risk long before content moderation even occurs. Global evidence clearly shows that simple age limits are frequently bypassed, leaving many young users vulnerable to the exact same risks. Furthermore, current safety metrics only track formal complaints rather than measuring the actual frequency of exposure to harmful material. To create a genuinely safer environment, policymakers must begin regulating platform design directly. Rather than treating safety as an afterthought, features that enable direct contact with strangers should be restricted by default. India can utilize its existing consumer protection laws to classify manipulative interfaces as unfair practices. Large digital services should be required to justify structural changes affecting minors, disable behavioral tracking, and publish independently audited data on how often children encounter harmful content online.


The DPDP cross-border transfer rules aren't live yet; so why are contracts being redrafted as if they are?

Many legal teams and companies are prematurely rewriting contracts to comply with the cross-border data transfer rules of India's Digital Personal Data Protection Act. However, these specific rules will not actually take effect until roughly May 2027. Currently, organizations are making the mistake of forcing strict European-style data protection clauses into their Indian contracts. This approach is highly counterproductive because India's legal model is vastly different. While the European system requires strict safeguards for every single transfer, India will use a much more open approach. This means that data can flow freely to any country unless the government explicitly restricts it. Because the government has not yet released a list of restricted countries, there is no solid legal basis to enforce strict transfer mechanisms right now. Including heavy compliance requirements prematurely can easily lock businesses into unnecessary legal burdens and costs. Instead of overcomplicating current agreements, legal teams should draft adaptable clauses that allow for future updates once the rules officially take effect. During this waiting period, companies should focus on understanding their data flows rather than creating rigid compliance structures. Lawyers must also be totally transparent with clients, clarifying that these contract changes are preparations for the future, not immediate legal obligations.