Showing posts with label fraud. Show all posts

Daily Tech Digest - September 29, 2026


Quote for the day:

"We don't grow when things are easy. We grow when we face challenges." -- Elizbeth McCormick


🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


Nine unlikely trends shaping software development

The software development landscape is experiencing a surprising shift where older, foundational technologies are re-emerging to overtake modern trends. According to InfoWorld, nine unexpected reversals are currently shaping the industry. Plain JavaScript is moving to absorb TypeScript, transforming the latter into a simple linting tool rather than a mandatory compilation step. Similarly, SQL is seeing a strong resurgence over ORMs and NoSQL databases, valued for its rigorous structure and new capabilities like running in the browser via WebAssembly. Developers are also finding that local IDEs often outperform cloud development environments due to the sheer power of modern laptops. In system architecture, monolithic designs are beating out microservices, as teams realize the deep complexities and network latency of microservices are often unnecessary for their goals. Instead of complex API integrations, developers are embracing cohesive "batteries-included" frameworks that reduce brittle glue code. We are also seeing a shift back to on-premises hardware over default cloud deployments, a preference for specialized engineering roles over the myth of the true full-stack developer, WebAssembly challenging Docker with faster, lightweight portability, and Java reclaiming dominance on the server side thanks to highly scalable virtual threads.


Beyond redundancy: Why dynamic stability matters in AI data centers

As artificial intelligence transforms data centers, the traditional approach to facility resilience is no longer enough. The challenge has shifted from static redundancy to dynamic stability. In conventional computing setups, uninterruptible power supplies and backup generators act as insurance against hardware failure. However, massive clusters of AI accelerators can change their power demand in milliseconds during training cycles. These tightly synchronized shifts create massive, instant power transitions without any actual equipment failing. Because thousands of GPUs can jump from low to full power demand almost instantly, they stress the entire electrical system. Utilities, grid researchers, and infrastructure companies are now focusing on active control to keep generators, batteries, and the grid synchronized during these sudden load changes. Modern power systems are being reimagined as dynamic buffers rather than just emergency backups, utilizing advanced firmware to absorb rapid power spikes without constantly cycling and degrading batteries. Ultimately, it is not enough for an AI data center to merely survive a localized power loss event. Operators must actively manage how the entire electrical infrastructure behaves millisecond by millisecond, ensuring the facility remains fully stable and completely responsive to the extreme, repetitive power swings of heavy AI workloads.


The human-on-the-loop advantage for MSSPs
Artificial intelligence is quickly changing how Managed Security Service Providers (MSSPs) operate, offering the ability to analyze data, automate workflows, and accelerate investigations at speeds humans cannot match. MSSPs face growing pressures—including skills shortages, complex attack surfaces, and tight budgets—making AI a crucial tool for scaling operations. However, despite the rise of automated security, AI does not eliminate the need for skilled cybersecurity professionals. Instead, it shifts the focus to a "human-on-the-loop" model, where analysts no longer perform every task manually but set guardrails, review high-risk decisions, and step in during complex incidents. AI excels at finding patterns and reducing noise, but it lacks the contextual understanding and nuanced judgment required to navigate ambiguous, real-world security threats. Furthermore, as attackers increasingly use AI-enabled techniques like prompt injection and model exploitation, AI systems themselves have become part of the attack surface. This makes human oversight essential to validate findings and challenge automated decisions. Ultimately, the most successful MSSPs will be those that blend AI-driven efficiency with adaptable, highly trained professionals who know when to trust the technology and when to override it.


IT Service Operations Is Ready For Its AI Moment

IT service operations are stepping into a new era where artificial intelligence finally moves from theory to practical application. For years, service desks and IT operations teams have struggled with a growing volume of routine requests, endless alerts, and the constant pressure to resolve issues faster. Now, the integration of artificial intelligence is offering a reliable way to shift from a reactive approach to a more proactive model. By applying modern AI tools, organizations can automate the categorization and routing of support tickets, significantly reducing the manual effort required from IT staff. Furthermore, intelligent virtual agents and improved self-service portals provide employees with immediate answers to common problems, creating a smoother and more efficient experience for everyone involved. For more complex incidents, AI assists support teams by quickly summarizing historical data and suggesting potential fixes, which directly cuts down the time it takes to restore normal operations. However, achieving this transition requires more than just buying new software. Technology leaders must focus on organizing their underlying data and refining their existing service workflows. When executed thoughtfully, adopting AI in service operations frees up technical teams to focus on strategic projects rather than getting bogged down by repetitive troubleshooting.


7 reasons IT managers fail to exceed your expectations

Many IT managers fail to meet or exceed expectations despite having strong technical backgrounds, often because the role requires skills they haven't developed. According to industry experts, the transition from a top-performing individual contributor to a manager requires critical thinking, business understanding, and leadership—areas where technical training falls short. Seven core reasons outline why IT managers often struggle in their roles. First, many are promoted without formal management training, leaving them ill-equipped to guide teams. They may also lack the emotional intelligence and interpersonal skills necessary to handle complex situations. Additionally, an individual might simply be the wrong fit for a specific management position, or they may lack clear expectations and performance metrics from their own supervisors. Sometimes, professionals take management roles just to advance their careers, even if they prefer staying technical. When they do take the role, they often juggle too many responsibilities without clear prioritization from the CIO, making it hard to stay on track. Finally, struggling managers often focus purely on flawless technology execution rather than solving the actual business problems at hand. CIOs can fix these issues by offering mentorship, establishing technical career tracks, and setting clear, business-driven goals.


Background Check Fraud: What Screening Can Miss

It is a troubling reality for security and human resources leaders that every fraudulent employee discovered by experts had successfully passed a standard background check. This vulnerability is not a flaw in the background checks themselves, which simply answer a narrow question by confirming that records exist, documents are legitimate, and names match database entries. Instead, the issue lies in the widening identity gap that has become an enormous business risk, costing companies hundreds of millions of dollars. Bad actors can now easily steal real identities, build convincing personas, optimize resumes for automated screeners, and even use generative artificial intelligence to navigate video interviews. Because traditional screening systems are not designed to compare a person's claimed history against independent sources, they fail to reveal inconsistencies in a broader digital footprint. A fabricated persona often appears legitimate if the underlying documents check out. To combat this growing threat, organizations must adopt a strategy of ongoing identity corroboration throughout the entire employment lifecycle. This broader approach focuses on ensuring that an individual is consistent, traceable, and genuine across multiple independent sources, shifting the focus from merely asking if a document is real to verifying if the person actually is who they claim to be.


Stolen AI credentials feed growing LLM proxy economy

Threat actors are increasingly utilizing over 80,000 proxy servers, known as transfer stations, to cloak illicit traffic to frontier AI models. This growing underground economy relies on stolen AI subscription credentials and API keys, which are often harvested through information stealers, phishing campaigns, and supply chain attacks targeting privileged developer accounts. By hiding the geographic origin of their traffic, attackers bypass provider controls to conduct model distillation attacks. In these attacks, carefully designed prompts extract valuable knowledge from top tier models to train competing AI systems. Security researchers have traced a significant portion of this activity to IP addresses in China and Hong Kong, echoing recent warnings from federal agencies about industrial scale distillation efforts. Beyond distillation, these proxy networks fuel widespread AI token theft, leading to hundreds of thousands of dollars in financial losses for victimized organizations. The proxies are often powered by open source relay platforms like sub2api, supported by a surprisingly robust commercial ecosystem of resellers and proxy vendors. To combat this rising threat, security experts strongly advise organizations to treat AI credentials as critical production secrets. Enterprises should implement short lived tokens, enforce strict spending limits, monitor for unusual request volumes, and quickly revoke any compromised keys.


AI Resilience: As AI Gets Smarter, Are Humans Still Getting Better?

As organizations shift toward more autonomous AI systems that reason and act, a critical new risk is emerging: cognitive dependency. While traditional AI governance focuses on machine accuracy and safety, there is growing concern about what happens to human capability when critical thinking is heavily delegated to technology. Offloading complex tasks like analysis and decision-making creates an efficiency paradox where enormous productivity gains might lead to gradual cognitive atrophy in human workers. To counter this, meaningful oversight must go beyond merely having a "human in the loop" who passively clicks approval buttons. True oversight requires a "human at the helm" who retains the ability to understand context, challenge the AI's assumptions, and confidently override recommendations when necessary. This introduces the concept of "AI resilience"—the organizational imperative to ensure employees maintain their independent judgment and domain expertise alongside AI adoption. Building this resilience involves deliberate practices, such as requiring humans to formulate their own initial judgments before viewing AI outputs and conducting critical tasks independently of AI. Ultimately, the goal is not to limit artificial intelligence, but to ensure that as machines become smarter, human workers do not lose the essential critical thinking skills required to properly govern them.


Five Ways To Use AI Coding Agents to Improve Your Software Architecture
AI coding agents are becoming essential tools for improving software architecture, especially as systems grow more complex and often rely on poorly understood legacy services. Modern architectures frequently integrate older services for specific tasks, but these often lack accurate documentation, making their use risky. AI coding agents can bridge this knowledge gap by mapping system designs, documenting data flows, and identifying potential security or logic flaws within legacy code. If necessary, these agents can even refactor the code to improve maintainability and mitigate architectural risks. Beyond dealing with legacy systems, AI agents are highly effective at finding and fixing both generic and organization-specific architectural flaws, such as API design issues or Domain-Driven Design boundary violations. They are also adept at identifying and patching security vulnerabilities, which is particularly valuable when architectures incorporate open-source packages. Furthermore, while AI agents significantly speed up coding and free teams to experiment, they must be guided by specific, measurable architectural goals and trade-offs to ensure quality. By doing so, teams can rapidly generate Minimum Viable Architectures (MVAs) and evaluate the code through measurable tests, creating a solid foundation for robust, scalable, and secure systems.


Chrome Store Hosts 'Poper Blocker' Spyware Downloaded by Millions
Millions of users have unwittingly downloaded a malicious browser extension called Poper Blocker, believing it to be a legitimate ad blocker. Despite carrying Google’s "Featured" badge and "Established Publisher" status on the Chrome Web Store, researchers at Bay Area Labs identified the program as sophisticated spyware. Once installed, the extension quietly gathers extensive amounts of sensitive information. It records detailed browser histories, captures screenshots, and extracts highly specific data from AI chatbot interactions on platforms like ChatGPT and Gemini. To bypass security reviews, the software remains inactive for its first 24 hours and uses methods to avoid detection, such as hiding its code and recognizing test environments. It then communicates with an external server to execute harmful commands. The developer behind the app, an opaque company known as Big Star Labs, has previously been caught distributing similar spyware, yet several of its applications remain freely available to millions of users. Security experts warn that standard data protection tools struggle to detect this behavior because the stolen data is heavily disguised. The situation highlights a broader issue in the digital marketplace, where users have very limited ways to distinguish safe utilities from deceptive software designed to quietly monitor their private lives each day.

Daily Tech Digest - August 13, 2026


Quote for the day:

“Personal growth is not a matter of learning new information but unlearning old limits.” -- Alan Cohen

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


4 RPA lessons that still hold true in the AI boom

As companies rush to adopt new artificial intelligence tools, many are stumbling over the exact same hurdles they faced years ago with robotic process automation. To succeed with AI technology today, organizations should remember four vital lessons from the past. First, they must carefully choose what to automate. Applying new technology to a broken or inefficient process only speeds up the creation of bad results. Every automation project needs a clear, measurable business benefit before it begins. Second, automation is never a project you can simply turn on and ignore. Because artificial intelligence acts quickly and sounds confident, keeping human experts in the loop is essential to prevent small errors from becoming large failures. Third, the quality of the information you feed the system remains critical. While modern tools can read messy data, they can easily misunderstand context, leading to flawed decisions on a massive scale. Finally, managing how people adapt to the changes is the most difficult challenge of all. Most technology projects fail because of people and workflows, not the software itself. Rather than abandoning older, predictable automation methods entirely, smart organizations are combining them with new artificial intelligence to create highly reliable, cost-effective, and highly practical solutions.


The intelligent workplace (part 2): Technology’s next transformation of work

As artificial intelligence takes on a larger role in the modern workplace, organizations must rethink how they manage teams and measure performance. The traditional focus on the sheer volume of tasks completed, such as reports written or cases closed, is no longer effective when automated tools can generate that output almost instantly. Instead, managers need to prioritize the actual quality of work, accuracy, and the ability to solve the right problems. Rather than competing with machines on speed, employees should focus on areas where human judgment remains critical. Furthermore, managers are shifting from simply overseeing daily activity to deliberately designing workflows where people and technology support each other. This change requires establishing clear rules for when employees should rely on automated systems and when they need to step in and override them. Ultimately, accountability must always rest with humans. A major challenge is ensuring junior employees still develop necessary expertise, as the routine tasks they traditionally learned from are now handed off to software. Companies will need to create deliberate opportunities for practice, mentoring, and direct feedback. Finally, successfully integrating these tools relies heavily on trust and transparency. Leaders must maintain human oversight, protect time for learning, and ensure that automated metrics do not replace empathy and open communication.


AI, Digital Twins, and Cybersecurity in Industrial Remote Operations

The second part of this article series explores how artificial intelligence and virtual models—often called digital twins—are fundamentally changing remote industrial operations, while highlighting the serious cybersecurity challenges that come with them. Instead of waiting for machines to break down, AI allows manufacturers to shift from reactive monitoring to predictive maintenance. By analyzing patterns in temperature, vibration, and power use, these systems can spot equipment failures weeks in advance. This capability drastically reduces unplanned downtime and lowers maintenance costs. Meanwhile, digital twins serve as the virtual interface for these physical systems. Engineers can use these exact digital copies to run simulations, test adjustments, and manage entire production lines remotely, achieving a level of oversight that previously required being physically present on the factory floor. However, moving factory controls online introduces major network security risks. Manufacturing remains a prime target for cyberattacks, and every new remote connection is a potential entry point. This risk is complicated by a severe shortage of security professionals who actually understand industrial systems. Ultimately, building a secure foundation is what makes these remote capabilities possible. Organizations that proactively address their network security can safely unlock the very real efficiency and productivity benefits of these modern industrial tools.


Social engineering reshapes financial fraud as attacks scale

Social engineering has rapidly emerged as the primary method for financial fraud, moving away from complex technical hacking toward manipulating human behavior. Recent data reveals that impersonation scams in the United States have more than doubled over the past year. Fraudsters frequently pose as trusted organizations, celebrities, or relatives to deceive individuals into authorizing transactions themselves. Investment scams are currently causing the most financial damage, with criminals using fake websites and fabricated platforms to create a false sense of urgency. This trend is not limited to everyday consumers; major Wall Street firms, including hedge funds and private equity companies, are also defending against sophisticated phone-based attacks targeting their employees. Adding to the challenge is the growing commercial market for these scams. Rather than building malicious systems from the ground up, criminals can now purchase ready-made scam kits online. These affordable packages provide everything needed to launch convincing campaigns, such as fake cryptocurrency presales with personalized elements and countdown timers. By lowering the barrier to entry, these kits allow individuals with minimal technical skills to execute highly professional and persuasive scams. Ultimately, modern financial fraud relies less on defeating security software and more on exploiting human trust through highly convincing deception.


Tokenmaxxing: The strangest developer productivity metric of all time

A concerning trend called "tokenmaxxing" has emerged in software engineering, where developers are evaluated by how much AI computing power they consume rather than the quality of their code. Much like the outdated practice of measuring productivity by lines of code, this metric encourages the wrong behaviors. When companies reward raw token usage, developers are incentivized to generate massive amounts of unrefined code, stuff prompts with unnecessary text, and set up automated systems simply to climb internal leaderboards. This careless approach leads to higher code duplication, less thoughtful refinement, and software that is quickly discarded. Beyond degrading software quality, tokenmaxxing is financially destructive. The blind pursuit of AI usage has caused companies to burn through budgets rapidly, forcing some to restrict their access to these tools. Furthermore, this flawed measurement ignores the most valuable ways developers use AI, such as debugging complex issues or planning architectural designs, because these tasks do not generate high token counts. Ultimately, true software engineering requires careful planning and simplification. AI is a helpful tool for solving problems and learning, but using it effectively means focusing on meaningful outcomes rather than blindly treating the volume of AI interactions as a sign of success.


Architecting Multi-Cloud Networks to Survive Cryptographic Migrations under DORA Rules

The article outlines the critical intersection of the European Union’s Digital Operational Resilience Act, multi-cloud network strategies, and the impending shift toward post-quantum cryptography. Under DORA, financial institutions face strict mandates to ensure continuous operational resilience and to mitigate third-party concentration risks. This effectively makes multi-cloud and cloud-agnostic architectures a necessity rather than a mere option, as organizations can no longer rely on a single cloud provider without a tested, actionable exit strategy. As the financial industry prepares for complex cryptographic migrations to defend against advanced quantum computing threats, these multi-cloud network architectures will be put to the ultimate test. Updating long-lived trust chains, encryption protocols, and digital certificates across sprawling IT environments is an inherently risky process. The text explains that surviving this transition without violating DORA’s strict uptime requirements demands highly decoupled network designs. By strategically distributing workloads and avoiding deep dependencies on provider-specific services, financial entities can safely manage phased cryptographic updates. Ultimately, a well-architected multi-cloud environment is essential not just for avoiding vendor lock-in, but as a robust safety net. It allows institutions to implement sweeping security upgrades smoothly, ensuring total compliance and uninterrupted service delivery in a heavily regulated modern landscape.


The web’s newest weapon against AI scrapers is a font

Designers Isaque Seneda and Gabriel Abrucio have developed a new typeface called ShieldFont, designed to protect online content from unauthorized data extraction by artificial intelligence companies. The core mechanism relies on the traditional ligature feature found in standard typography. While a web page using ShieldFont appears perfectly normal and readable to human visitors, the underlying HTML source code is intentionally altered. When AI scrapers and automated web crawlers attempt to harvest the website text, they encounter only random, meaningless data instead of the actual content. This approach offers web publishers a practical technical method to prevent their work from being absorbed into AI training datasets without permission. Unlike earlier blocking methods that often disrupted the user experience or proved ineffective, ShieldFont specifically targets the data collection process by intentionally ruining the harvested text. Experts note that the success of this method depends on how well the substitution strategy is executed. If the replacements rely on simple patterns, such as direct synonyms or antonyms, advanced algorithms might learn to reverse the alterations. By focusing on random string generation and complex substitutions, ShieldFont aims to safeguard digital ownership and provide a reliable defense against the aggressive scraping tactics currently used across the internet.


Post-Quantum Deadlines Collide With OT Reality

The transition to post-quantum cryptography is becoming an urgent priority as looming regulatory deadlines clash with the practical constraints of operational technology environments. While government agencies and security bodies push for rapid adoption of quantum-resistant algorithms to protect critical infrastructure, the realities of operational technology present significant engineering and logistical hurdles. Unlike standard enterprise networks, operational technology systems like industrial control units, medical devices, and smart grids are built for longevity. They often run on older hardware with limited processing power and minimal memory. These strict constraints make it exceedingly difficult to implement complex new cryptographic standards without disrupting essential services or triggering massive hardware replacement cycles. Furthermore, the threat is not entirely theoretical. Adversaries are actively engaging in "harvest now, decrypt later" campaigns, collecting encrypted data today to break it once quantum computing matures. Consequently, securing these industrial environments requires a nuanced approach rather than a simple software update. Organizations must begin their planning immediately by conducting thorough inventories of their cryptographic assets. They should isolate vulnerable operational systems through strict network segmentation and adopt hybrid security models. Ultimately, building flexible encryption into aging infrastructure is crucial for navigating the tension between ambitious mandates and the slow-moving reality of industrial technology.


Beyond Cyber Protection: How European Companies Can Operate Through Cyber Disruption

European businesses face an evolving threat landscape where preventing cyberattacks entirely is simply no longer a realistic expectation. Driven by integrated supply chains and rapid artificial intelligence adoption, companies remain vulnerable despite heavy investments in traditional security. According to recent research, while many executives expect to recover from incidents like ransomware within days, actual disruptions often take months to resolve. To navigate this reality, leaders must transition their focus from basic protection to true operational resilience. This means acknowledging that some attacks will succeed and designing systems capable of operating under stress. Executives should start by identifying their essential operating core, which includes the critical services, data, and processes that must remain available during a crisis. Additionally, while strict regulations establish important security baselines, compliance should be viewed as a starting point rather than the ultimate goal. True resilience requires engineering robust recovery processes rather than simply hoping for a rapid response. It also demands making resilience a company wide responsibility, extending these practices across the entire value chain, and fully understanding the economic costs of a disruption. By accepting the inevitability of breaches and planning for continuity, organizations can confidently sustain their core functions and protect their stability during a severe disruption.


AI Agents Are Creating a New Identity Security Challenge for Enterprises

Morey Haber outlines the necessity of treating artificial intelligence agents as a unique class of non-human identity that requires strict security controls. Unlike standard software or human users, these agents operate autonomously, make independent decisions, and run on unpredictable schedules. Because they can reason and interact with other systems on their own, traditional access management is simply not enough. Organizations must assign each agent a specific identity tied to an accountable human owner. Instead of relying on permanent passwords, these agents should use temporary security secrets and be granted the absolute minimum access required to complete a specific task. Furthermore, security teams must monitor their behavior constantly rather than just checking their login credentials, looking for unusual activity or excessive data access. Proper management also means tracking an agent from the moment it is created to when it is retired. Crucially, companies need a reliable kill switch to instantly revoke an agent's access if it behaves improperly or is compromised by an attacker. By managing these tools with calm, steady oversight and limiting their permissions, organizations can prevent them from becoming dangerous entry points for cyber threats. Ultimately, an agent should never hold more power than you are prepared for it to misuse.

Daily Tech Digest - July 15, 2026


Quote for the day:

“Always treat your employees exactly as you want them to treat your best customers.” -- Stephen R. Covey

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 17 mins • Perfect for listening on the go.


AI incidents need a new playbook. Here’s how to build one

Traditional security incident response playbooks are ill-equipped to handle modern AI incidents. While conventional cybersecurity focuses on malicious intrusions and breaches of confidentiality or availability, AI failures often happen simply because a probabilistic model behaves poorly. Issues like hallucinations and bias can occur without any external attack, meaning standard response metrics often miss the core problem entirely until it causes real-world harm. To address this significant gap, organizations must build dedicated AI playbooks that accurately account for both internal model errors and externally induced attacks, such as data poisoning. A mature AI incident response strategy requires a few foundational elements to be truly effective. First, organizations need an AI Bill of Materials to track the underlying components and data within every production system. Second, accessible model cards must be available to provide responders with immediate context on a model's limits. Third, a designated data scientist must be on the incident call tree to analyze real-time behavior. Finally, teams must establish pre-defined rollback thresholds to trigger safe containment or fallback switches without causing unnecessary business disruption. By rewriting detection triggers and involving legal teams early to manage liability risks, companies can proactively secure their AI systems before an incident ever occurs.


Trust Under Attack: Why Resilience and Not Compliance Will Define The Next Generation of Enterprise Security

In a recent interview, Pranay Modi, Chief Information Security Officer at MAS Financial Services, outlines a practical vision for the future of enterprise cybersecurity. He challenges the common belief that people are the weakest link in security; instead, they are simply the most frequent targets. By building a supportive culture where reporting mistakes is safe and security processes are straightforward, organizations can turn their workforce into a powerful defense network. Modi advises that as threats become harder to predict, companies should focus on fundamental, lasting capabilities. These include clear visibility into all digital assets, strict identity management for both humans and machines, and recovery plans that are regularly practiced rather than just documented on paper. He also highlights the growing importance of managing third-party risks and ensuring company boards truly understand their cyber exposure. Crucially, Modi warns against confusing compliance with actual security. Passing an audit is merely a starting point, not a guarantee of safety. He emphasizes that while the daily tasks of cybersecurity can be handed off, the ultimate responsibility for protecting a company's digital trust rests firmly with its executive leadership. The goal is no longer just preventing attacks, but ensuring the organization remains resilient when disruptions inevitably occur.


Why the most dangerous code test failures are invisible

Code testing is essential for modern software quality, but the most dangerous bugs are the ones that remain completely invisible. According to quality assurance engineer Mikhail Golikov, while teams often celebrate catching obvious errors, the true risk lies in failures that never trigger an alarm. These quiet failures typically fall into three main categories: tests that exist but are never executed, unreliable tests that teams learn to ignore, and untested behavior documented only in production logs. Unexecuted tests act as mere documentation rather than actual safety checks. Unreliable or flaky tests are even worse because they condition engineers to dismiss real failures as background noise, effectively lowering the overall trust of the team in their systems. Furthermore, failing to turn real world production logs into test cases leaves a massive gap between what software does in reality and what developers actually monitor. The core issue across all these structural problems is a sheer lack of system visibility, rather than a lack of modern tools. True software quality is not simply defined by having a high total volume of tests or the absence of visible bugs. Instead, it requires the unglamorous work of making sure every failure becomes impossible to ignore, ensuring that real problems reliably turn into clear signals.


The New Face of Fraud: Identity, AI and Digital Trust

This article discusses the changing nature of digital fraud, emphasizing that cybercriminals are shifting their focus from attacking systems to compromising user identities. As digital transactions grow faster and more common, attackers find it easier to blend in using stolen credentials rather than breaking into systems. The author explains that account takeover is a major threat because it allows attackers to bypass alerts and mimic normal behavior, making fraud harder to spot until the damage is done. Phishing attacks are also becoming more personalized and effective, with criminals using AI to craft targeted messages that trick users into giving up their credentials. Once inside, attackers can operate as trusted users. To combat this, the article highlights the importance of identity-centric security. Organizations need to treat every login as a trust decision and continuously verify identities. The piece also notes India's regulatory efforts, such as using AI and shared intelligence to detect fraudulent activities early. For businesses, practical steps include identifying high-risk periods, strengthening identity governance, and testing their response times. Ultimately, the future of fraud prevention lies in combining identity intelligence, AI-driven detection, and behavioral analytics to catch risks before they result in financial loss.


Microsoft’s Secure Boot has been broken for a decade and no one noticed until now

The Ars Technica article discusses a significant security flaw in Microsoft's Secure Boot system that has existed for a decade. ESET researchers found 11 outdated UEFI shim bootloaders signed by Microsoft that allow attackers to bypass Secure Boot entirely. This bypass works on nearly any UEFI-based machine that trusts the Microsoft Corporation UEFI CA 2011 certificate, regardless of the operating system. These forgotten shims are typically used to establish a chain of trust for Linux distributions and other third-party boot software. However, because they are old versions (0.9 and below) they contain known vulnerabilities. Attackers can exploit these flaws by bringing a vulnerable shim to a target system, replacing the existing bootloader, and executing malicious code during the boot sequence. This allows the installation of powerful bootkits like Bootkitty or BlackLotus, which operate below the operating system level and are notoriously difficult to detect and remove. Microsoft addressed this issue by revoking the affected shim certificates in its June 2026 Patch Tuesday update. The revocation prevents these specific vulnerable binaries from being trusted, but the incident highlights the ongoing challenges of managing trust and revocation within the UEFI Secure Boot ecosystem.


‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets

Security researchers from Tel Aviv University, Technion, and Intuit have identified a new cyber threat called "HalluSquatting," which exploits the tendency of generative AI models to hallucinate false information. As developers increasingly rely on AI coding agents to independently write code or install software packages, these assistants sometimes generate incorrect, invalid resource names instead of the intended ones. Hackers can predict these hallucinated names, register them, and attach malicious code to them. When the AI coding assistant unknowingly retrieves the fake package, it installs malware directly into the developer's system, potentially creating large botnets. This method resembles typosquatting, but rather than waiting for humans to mistype a web address, attackers rely on AI agents to make the mistake for them. The technique targets the growing trend of independent applications that execute tasks with little human oversight on modern development teams. In tests against popular AI coding tools like GitHub Copilot and Google Gemini CLI, researchers found that models hallucinated false repository names 85 percent of the time, highlighting a notable security weakness. Ultimately, HalluSquatting bypasses traditional security barriers by blending AI prompt manipulation with conventional malware strategies, representing a serious challenge as AI tools become integrated into software engineering environments.


The Shadow Insider: How AI Agents Are Becoming the New Insider Risk Nobody Is Monitoring

The article discusses a growing security challenge in modern workplaces: the rise of artificial intelligence assistants as a new type of insider risk. Traditionally, security teams have focused on monitoring human employees, contractors, and vendors who have legitimate access to sensitive company systems. However, organizations are now deploying autonomous software agents that perform tasks like reading emails, summarizing documents, and updating customer records. These agents operate as digital workers with their own identities and permissions, often acting without direct human oversight. The main issue is not that these agents are intentionally harmful, but that they quickly accumulate access to multiple systems simultaneously, creating a complex web of permissions. Over time, an agent designed for a simple task might gain access to confidential financial reports or legal documents simply because new tasks require more information. This gradual expansion of access often goes unnoticed because these machine identities do not follow normal human work patterns, making many traditional security monitoring tools completely ineffective. To address this serious problem, security teams must treat every software agent as a managed identity with strict, narrow permissions and closely monitor their behavior beyond basic login events to ensure they firmly remain aligned with their original purpose.


Prompt Privacy Is the New Endpoint Security Problem

As organizations adopt large language models, a new security challenge has emerged: protecting the privacy of prompts. While artificial intelligence offers significant advantages by allowing users to complete tasks using natural language, these inputs often include sensitive information such as trade secrets, credentials, or personal data. If employees submit confidential details into a model without proper safeguards, the information might be retained or used for future training, leading to accidental data exposure. Furthermore, attackers are actively exploiting this vulnerability through prompt injections, where they carefully craft instructions to manipulate the model into revealing hidden system rules, altering its intended behavior, or executing unauthorized commands. This problem extends to modern artificial intelligence agents and browsers, which effectively function as a new type of network endpoint. Because these agents operate autonomously and hold active user sessions, hidden malicious instructions on websites can trick them into compromising systems or authorizing transactions. Traditional security tools are generally unequipped to handle these specific threats. To address these risks, security teams must treat prompts as highly sensitive data. Organizations can better protect their networks by rigorously filtering both inputs and outputs, enforcing strict access privileges for artificial intelligence agents, and closely monitoring all system interactions over time.


'Yellow Teams' Are Defining the Future of AI Security

As the capabilities of artificial intelligence grow, organizations are increasingly relying on "yellow teams" to build robust defenses against emerging threats. Composed primarily of engineers and developers, these specialized teams work closely with both offensive red teams and defensive blue teams to understand and test the limits of advanced AI models, such as Claude Mythos and GPT-5.5. A central responsibility of yellow teams involves developing "harnesses." These are dedicated software frameworks that wrap around an AI model to firmly restrict its permissions, define operational rules, and guide its actions. This essential step focuses the AI's capabilities and ensures it fully understands the specific network context, which drastically reduces false positives during routine security testing. With these carefully refined tools, companies are uncovering a significant number of software vulnerabilities. To handle this influx of information, blue and yellow teams are integrating more deeply than before. Yellow teams are taking a proactive approach by incorporating AI directly into the software development process. This helps engineering departments identify exactly which coding practices need adjustment to prevent security flaws from recurring. By bridging the gap between security analysis and daily engineering work, yellow teams provide a highly practical strategy to protect systems against future attacks.


The neocloud approach to sustainability

The neocloud model offers a practical alternative to massive, centralized data centers by distributing computing resources closer to where people actually use them. Instead of building giant facilities that place heavy, sudden demands on local power grids and water supplies, this approach relies on a network of smaller, interconnected sites. By doing so, it avoids the severe strain that huge building projects often place on communities and utilities. A key environmental benefit of this distributed method is its incremental use of electricity and water. Rather than drawing millions of gallons of water daily for cooling or requiring massive new power plants, these localized centers allow resource consumption to grow gradually and sustainably. Processing data closer to the source also cuts down on the energy required to transmit information over long distances, which inherently improves response times and reliability for users. Furthermore, this localized strategy helps keep data within specific regions, addressing privacy and security concerns without sacrificing performance. Ultimately, spreading out the physical infrastructure makes the growth of advanced computing far more manageable. It aligns technological progress with environmental limits, proving that we can meet modern computing needs without placing an overwhelming burden on our natural resources or local infrastructure.

Daily Tech Digest - July 06, 2026


Quote for the day:

“The only truly secure system is one that is powered off, cast in a block of concrete, and buried 20 feet underground.” -- Gene Spafford

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


The future of payment fraud could be automated

Payment fraud is rapidly becoming a highly organized and automated enterprise, driven by recent improvements in artificial intelligence tools. Surveys indicate that consumers now prioritize advanced security and fraud protection over transaction speed and customer service when selecting payment providers. Account takeovers remain a prevalent threat, with attackers using improved phishing methods and manipulated media to bypass traditional defenses like passwords and biometric authentication. Authorized push payment fraud is also surging, as scammers use convincing computer-generated content to impersonate trusted people and manipulate victims into authorizing transactions. Meanwhile, traditional card fraud has shifted heavily toward digital channels, relying on stolen data and website skimming rather than physical theft. Criminals are also fabricating synthetic identities at an alarming scale, blending real and fake information to secure credit and loans fraudulently. Furthermore, insider threats and third-party vulnerabilities continue to expose sensitive systems to malicious actors. To combat this evolving, automated criminal industry, financial institutions must implement practical, coordinated defense strategies across the entire sector. A unified approach is essential to strengthen security measures, reduce emerging risks, and preserve consumer trust in an increasingly complex digital financial environment.


The company of the future is built on tokens

The architecture of the modern enterprise is undergoing a fundamental shift, moving away from traditional software licensing and centralized infrastructure toward models driven by digital tokens. In this emerging paradigm, tokens serve as the core unit of value, utility, and computational processing. For artificial intelligence and automated workflows, organizations are increasingly measuring resources in processing tokens rather than raw hardware metrics, fundamentally changing how cloud computing and enterprise services are priced and consumed. Beyond AI, cryptographic tokens are streamlining digital identity, access management, and secure transactions across distributed networks. This transition enables businesses to operate with necessary agility, replacing rigid organizational silos with fluid, automated environments. By adopting token-based architectures, companies can dynamically allocate resources, ensure tighter security protocols, and foster more transparent data governance. Ultimately, this structural evolution reduces operational friction and aligns operational costs directly with actual usage and value generation. As digital infrastructure continues to mature, embracing these tokenized models will no longer be a fringe advantage but a foundational requirement for any business aiming to scale efficiently and remain resilient in an increasingly automated global market.


Blockchain: The Architectural Missing Link for DPDPA Consent Management

The article argues that India's Digital Personal Data Protection Act requires a fundamentally new approach to consent management, making traditional databases inadequate due to their vulnerability to tampering. Under this law, companies must provide undeniable proof of user consent. Centralized databases cannot guarantee this because their records can be altered without leaving a trace. To solve this problem, blockchain technology offers a secure, unchangeable record system. When a person agrees to share data, their choice is recorded permanently. The system also supports automated rules, ensuring data is only used for its approved purpose and is immediately restricted if a user withdraws permission. Instead of storing personal details, this architecture uses digital receipts to verify consent, significantly reducing privacy risks. By moving to a shared and secure network, businesses and consent managers can synchronize user preferences seamlessly without relying on fragile connections. Ultimately, using easily alterable database systems presents a major compliance risk for modern organizations. Adopting a decentralized approach allows companies to mathematically prove they are handling data legally. This shifts the relationship between companies and users from blind trust to verifiable action, effectively protecting both businesses and individuals.


Forward Deployed Engineers Aren’t the Moat. The Learning Loop Is.

The conversation around enterprise AI adoption often centers on the need for Forward Deployed Engineers (FDEs) to navigate complex, fragmented legacy systems. However, the presence of embedded engineering talent is not the true competitive advantage. The real moat is the organization's capacity to learn from each localized deployment and translate those insights into a generalized, reusable product core. A successful model involves central engineering teams abstracting bespoke customer workarounds into foundational platform capabilities, making every subsequent implementation faster and cheaper. This approach challenges traditional tech models. Hyperscalers are structurally optimized for high-margin infrastructure consumption and developer tooling, making it difficult to channel field insights into a unified enterprise platform. Meanwhile, traditional system integrators struggle with misaligned incentives, as their revenue models rely heavily on billable hours rather than reducing implementation effort through productization. Additionally, finding true FDEs is difficult; it requires engineers who can write production code under pressure, build trust with executives, and care deeply about a product's long-term trajectory. Ultimately, merely hiring FDEs without establishing a structural feedback loop that continuously improves the core product is just a modern renaming of traditional implementation consulting.


Why AI agents will make your governance playbook obsolete

As organizations increasingly deploy autonomous AI agents, traditional technology governance playbooks are quickly becoming obsolete. Historically, governance relied on human-led committees, static policies, and periodic audits, all of which assume central oversight of deliberate decisions. However, AI agents operate at machine speed and often execute hundreds of micro-decisions that can collectively lead to unintended outcomes. To maintain control in this new environment, companies must fundamentally shift their approach across three key areas. First, they need comprehensive behavioral telemetry to measure and understand exactly what these agents are doing, replacing blind trust with continuous observation. Without this data, establishing baselines or detecting anomalies is impossible. Second, organizations must employ AI to govern AI. Human oversight simply cannot scale to manage hundreds of autonomous agents interacting simultaneously; instead, automated governance layers must monitor behavior and respond in milliseconds. Finally, accountability must be distributed across the organization rather than centralized in a single department. Developers, security teams, and legal professionals must collaborate through a shared responsibility model, ensuring that agents are built with necessary reporting hooks and that independent oversight systems maintain constant situational awareness.


The 20 percent problem: why data center sites fail before they’re built

The United States is currently facing a significant infrastructure challenge, with nearly half of all planned data centers experiencing delays or outright cancellations. While it is common to assume that a lack of available land or raw power generation is to blame, the core issue often lies elsewhere. This is referred to as the twenty percent problem, representing the final fraction of logistical, regulatory, and supply chain hurdles that cause projects to fail before they are even built. The massive demand driven by new technologies requires rapid construction cycles, but the global supply chain for critical electrical equipment simply cannot keep up. Long wait times for essential parts like high-voltage transformers, switchgear, and backup batteries mean that a single missing component can completely stall a facility. Furthermore, these projects frequently encounter strong community opposition, complex local zoning laws, and a lack of established power transmission lines to the actual sites. Even with abundant financial investment and high demand, the practical realities of constructing heavy infrastructure remain difficult to navigate. To successfully complete these sites, developers must focus on securing equipment much earlier and working closely with local municipalities to resolve concerns before breaking ground.


How Data-Driven Businesses Choose Storage That Reduces Risk and Drag

When businesses select a storage facility, the decision carries more weight than just finding extra space; it directly impacts operational continuity and efficiency. While marketing materials often highlight convenience and security, the real test is how a storage site performs under pressure, when staff are busy or schedules change. A poor choice introduces operational friction, leading to lost time, liability exposure, and recurring interruptions. Instead of focusing on branding, data-driven businesses should evaluate the mechanics of a facility. Cleanliness serves as a strong indicator of underlying management discipline, suggesting better pest control and maintenance. Additionally, access features and climate control must align with actual business needs rather than perceived luxury. To make a sound choice, businesses should visit facilities during both normal and peak hours to observe traffic flow and staff responsiveness. They must ask direct questions about maintenance and exception handling while comparing locations based on the cost of potential failures, not just the monthly rent. Ultimately, the best storage solution operates as a reliable system that protects assets and minimizes logistical distractions, allowing teams to stay focused on their core work.


'AI as mirror, not mask': Amagi CPO outlines blueprint for responsible AI at work

As artificial intelligence increasingly handles routine workplace tasks like writing and analyzing, the real question is how to properly define its boundaries. Prasad Menon, Chief People Officer at Amagi, argues that AI must amplify human leadership rather than replace it. His approach relies on the core principle that technology should act as a mirror reflecting an organization's true culture, rather than a mask hiding uncomfortable realities. Relying too heavily on automated algorithms can carry forward past biases and slowly weaken shared company values. While technology is excellent at managing large data and revealing broad patterns, it lacks the necessary context and human empathy to fully understand the weight of sensitive decisions regarding people. Tools like AI can safely gather widespread feedback and flag initial concerns, ensuring employees feel heard without fear of retribution. However, crucial moments involving career progression, growth, and personal inclusion must always remain under direct human control. Human leaders need to step in to interpret these technological insights and respond with genuine care. Ultimately, AI is best utilized to scale information and insight, but it is strictly up to human leaders to scale humanity, trust, and empathy within the workplace.


7 cyber risk assessment gotchas to avoid

Cyber risk assessments are vital for protecting an organization's digital assets, but leaders frequently stumble into common traps that undermine their effectiveness. A primary mistake is treating the assessment as a simple checklist. When teams just go through the motions, they fail to tie technical flaws to actual business consequences. Leaders must also avoid sugarcoating discouraging results to stakeholders; instead, they should present realistic attack scenarios to demonstrate true exposure. Another frequent error is defining the assessment's scope too narrowly, often leaving out forgotten older systems, third-party portals, or newly deployed AI tools that attackers can easily exploit. Similarly, relying heavily on a risk register without questioning its underlying assumptions creates false confidence. An assessment should be a living document, not a rigid dashboard that satisfies auditors but misleads executives. Security teams also err when they confuse basic compliance with real-world protection, as many compliant companies still suffer breaches. Ultimately, avoiding these missteps requires shifting away from merely cataloging flaws to understanding how those vulnerabilities directly impact operations, revenue, and customer trust. Evaluating risk effectively means maintaining continuous visibility and open, honest communication across the business.


If the problem can be solved by an if-check, don’t ask AI to do it: Sumanta Ghosh, CTO, Bandhan Life

As artificial intelligence transitions from a technological experiment to an economic investment, business leaders must carefully evaluate where it genuinely provides value. Sumanta Ghosh, CTO of Bandhan Life, notes that while AI capabilities are expanding, so are the associated infrastructure and operational costs. Rather than adopting AI for every process, organizations need to maintain strict architectural discipline. This is particularly crucial in highly regulated, deterministic industries like insurance, where predictability is required. Because AI models can produce variable outputs, Bandhan Life treats the technology as an intelligent assistant rather than a completely autonomous decision-maker, ensuring humans remain accountable for final actions. Ghosh stresses that applying complex, expensive AI models to straightforward problems that conventional software can handle, such as simple conditional logic, unnecessarily inflates costs without adding proportionate value. While AI operating costs will likely decrease over time as the technology matures, current success depends on careful judgment. Ultimately, the most successful enterprises will not necessarily be the ones deploying the most artificial intelligence, but rather those disciplined enough to integrate it only where the business return clearly justifies the financial investment.

Daily Tech Digest - June 27, 2026


Quote for the day:

"When you want to succeed as bad as you want to breathe, then you’ll be successful." -- Eric Thomas

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


‘Botsitting’: The AI time-savings killer only governance can stop

While artificial intelligence promises to free up employees for valuable tasks, a recent study reveals that workers lose more than half their saved time to “botsitting.” Digital workers save roughly eleven hours a week using these tools, but spend over six hours managing them—providing missing context, checking outputs, fixing mistakes, rewriting prompts, and correcting inaccurate answers. As a result, businesses are missing out on the full return on their investments. A core issue is poor governance and a lack of training. Employees often use AI for simple tasks like drafting emails, distrusting it for complex work. Moreover, there is “coordination neglect,” where an individual’s productivity gains create unexpected work for others downstream. For instance, when workers pass along unchecked, AI-generated content, teammates must spend unbudgeted time cleaning up the mess. Experts warn that simply implementing tools without clear guidelines on verification processes and data context leads to inefficiency. To truly benefit from these technologies, organizations must focus on proper deployment, establish clear oversight, and define quality standards rather than merely counting how often tools are used. Reliable outcomes require thoughtful management, not just fast adoption.


The database that refused to die: How Postgres survived its own creators

Postgres, one of the world's most widely used database systems, began its life with an uncertain future. Created by database pioneer Michael Stonebraker in the 1980s as a successor to Ingres, the project was essentially abandoned by its creator in the mid-1990s. Instead of fading into obscurity, Postgres was rescued by a dedicated community of independent open-source volunteers. These contributors preserved Stonebraker's foundational, highly adaptable architecture—which allowed for complex, user-defined data types rather than just basic strings and numbers—while adding standard SQL capabilities. Today, this collaborative rescue effort has established Postgres as a cornerstone of modern cloud computing infrastructure. Its enduring success stems from its foundational design philosophy. While proprietary database systems traditionally optimize their software to suit the specific needs of massive enterprise clients, Postgres was built to handle the diverse workloads of general users. By seamlessly accommodating complex data formats like geographic information and computer-aided design files, it solved real-world problems for a broad audience. Ultimately, the survival and widespread adoption of Postgres demonstrate the power of open-source software, proving that community-driven development can outlast even the original creators to become a resilient industry standard.


Why private AI is the smarter bet

Although many businesses initially assumed artificial intelligence would naturally live in the public cloud, reality is forcing a shift toward private, on-premises systems. According to the article, this transition stems from growing concerns about uncontrolled costs, security vulnerabilities, and operational fit. As companies move from small experiments to organization-wide implementation, the pay-per-token pricing models of public cloud providers risk becoming massive utility bills that wipe out business gains. Consequently, the future of enterprise AI leans toward a hybrid model. Rather than relying entirely on giant public models, businesses are discovering that smaller, specialized AI models can handle tasks better while running closely to their own private data. This approach offers better control over predictable workloads and eliminates surprise expenses. Furthermore, keeping AI in-house strengthens security and data governance. Using public AI tools raises the real danger of employees inadvertently exposing sensitive or proprietary information. While building and managing private AI networks requires significant investment, skill, and discipline, the long-term benefits of controlled costs, tight security, and owned infrastructure make it a much smarter choice for major production workloads.


AI Cost, Security Pressures Push Enterprises Toward Private Cloud, Broadcom Says

According to a recent report from Broadcom, organizations are increasingly moving their artificial intelligence operations away from public cloud services and toward private cloud setups. As businesses shift from merely testing artificial intelligence to running real-world applications, they are discovering that private networks offer better handling of costs, security, and data control. The study reveals that over half of surveyed enterprises now plan to run their active intelligence systems on private infrastructure. Meanwhile, public cloud usage for these specific tasks has dropped notably over the past year. Interestingly, cost management has now surpassed security as the primary concern with public platforms, as business leaders face unpredictable pricing for computing power and data storage. Because of this, more than eighty percent of companies are either moving or considering moving their systems back in-house. While public networks remain useful for basic testing and flexible storage, the heavy demands of daily production require a more stable environment. Strict data privacy rules further encourage this transition. Ultimately, businesses are finding that dedicated internal systems provide the financial predictability and reliable protection necessary to safely grow their technological capabilities.


How to Modernize Legacy Applications Without Disrupting Business

Upgrading older software systems is a pressing challenge for modern organizations. Delaying these updates can hinder new capabilities, consume vital budgets with maintenance costs, and create risks as experienced programmers retire. However, many companies hesitate because poorly planned upgrades often cause severe business interruptions. To avoid taking systems offline, experts recommend a gradual approach rather than attempting a risky, sudden replacement. This method relies on careful planning and proven structural designs. For example, organizations can build new services around the existing system, slowly routing traffic to the new components as they are tested and proven. Another reliable method involves running both the old and new systems at the same time to ensure they produce identical results before fully switching over. It is also important to use a translation layer to prevent the flaws of the old data formats from infecting the new setup. A successful upgrade generally follows a structured path: assessing current dependencies, planning the target design, running a small initial pilot, scaling the effort across other applications, and maintaining ongoing oversight. By strictly adhering to these methods, businesses can confidently update their technology and maintain continuous daily operations.


Data Lakehouse Architecture Layers: AI Needs More Than Just Infrastructure

Organizations have invested heavily in data lakehouses to store and process large amounts of information for analytics and artificial intelligence. While these setups handle storage and compute well, they often fall short in practical application. Data remains scattered across different cloud environments and operational systems, meaning business teams and AI models still struggle to access reliable information without technical assistance. The fundamental issue is no longer about where data is kept, but how it is connected and understood. AI tools, in particular, require more than just raw data; they need clear context and strict governance to function accurately and safely. To solve this, a new logical layer is emerging in data architecture. Instead of replacing the lakehouse, this access layer sits on top of it. It connects distributed information, applies consistent rules, and provides clear meaning to the data without requiring it to be moved or duplicated. By pairing traditional storage with this new governance layer, businesses create a stronger foundation. This approach reduces friction, ensures that both human users and systems have the context they need, and allows organizations to focus on practical outcomes rather than managing complex infrastructure.


The Four Elevations of Effective Fraud Prevention

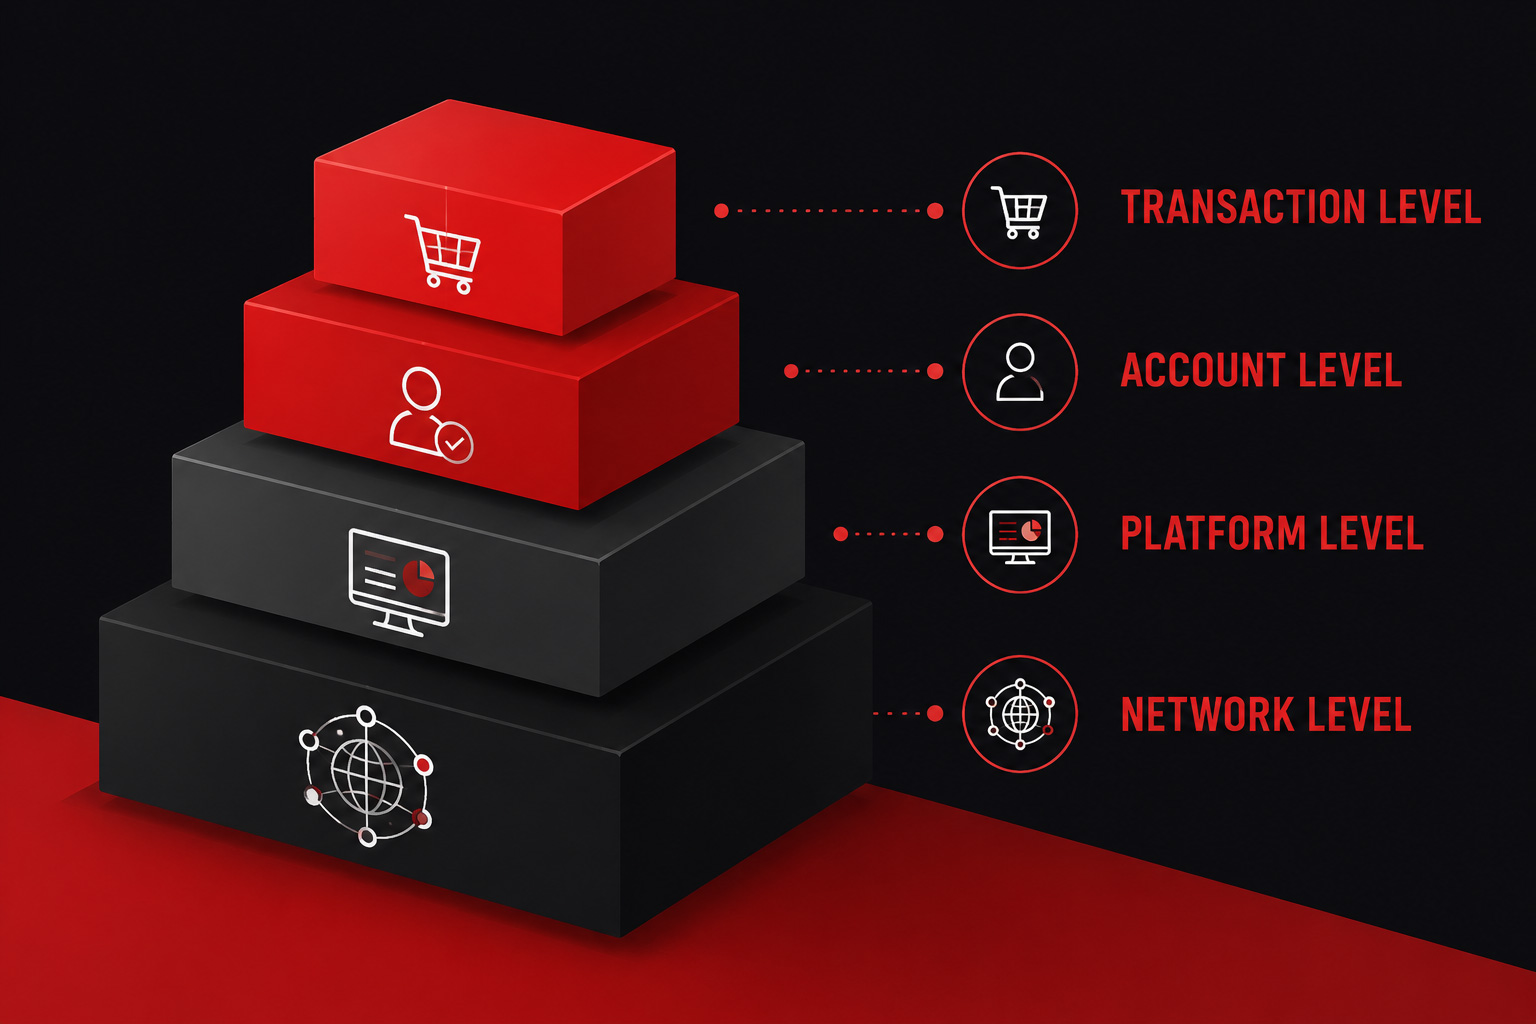
Effective fraud prevention requires more than just checking individual steps; it demands a layered approach to monitor customer behavior comprehensively. To build a resilient defense, organizations should evaluate activities across four key elevations. First is the transaction level, which looks at single interactions like logins or purchases. While important, relying on this alone can miss larger patterns because attackers frequently change their tactics. The second elevation is the account level, where monitoring a user's behavior over time helps distinguish normal activity from suspicious anomalies, such as sudden changes to contact information or unusual transfer requests. The third elevation expands to the platform level, allowing teams to analyze trends across all grouped accounts. This broad view helps quickly spot coordinated attacks or fraud rings sharing the same devices or geographic locations. Finally, the network level involves collaborating with external data providers to share insights across different companies, ensuring that a threat detected by one organization is immediately known to others. By integrating these four perspectives, businesses can confidently identify complex fraud schemes early, reduce false alarms for legitimate users, and secure their operations without disrupting the everyday customer experience.


Bridging the gap between leadership's AI enthusiasm and employee pushback

Corporate leaders and everyday employees often view artificial intelligence through entirely different lenses. While executives and board members see AI as a path to efficiency, cost reduction, and innovation, employees frequently view the technology with caution. Many workers worry that AI will result in job losses, create mentally exhausting workloads, enable invasive workplace surveillance, and harm the environment. Chief Information Officers (CIOs) find themselves caught in the middle and must bridge this divide. If IT leaders ignore workforce anxieties and force AI integration, they risk damaging company morale, losing valuable talent, and wasting money on tools that employees simply refuse to use. To resolve this tension, CIOs need to look beyond basic financial metrics and instead measure actual employee sentiment and tool usage. Having open, honest conversations with staff about their fears is essential. By creating a culture where workers feel safe sharing their concerns, companies can build trust and ease anxiety. Rather than rolling out technology blindly, leaders should clearly communicate the company's AI strategy and empower early adopters to guide their peers, ensuring the transition supports both business goals and the well-being of the team.


AI Works, Pull Requests Don’t: How AI Is Breaking the SDLC and What To Do About It

In the presentation "AI Works, Pull Requests Don't," Michael Webster examines how the rise of artificial intelligence coding assistants is severely straining traditional software development lifecycles. While AI tools initially act as powerful amplifiers that can increase development speed by three to five times, this burst in productivity is often temporary. Developers and AI agents are generating massive amounts of code, sometimes adding twenty-five times more code than they delete. As a result, human reviewers are overwhelmed by enormous pull requests, creating significant bottlenecks in the review process and leading to a steady accumulation of technical debt. Drawing on queuing theory, Webster explains that delays inevitably occur when the rate of incoming code surpasses the team's capacity to process and review it. To resolve these challenges, engineering teams must adapt their validation pipelines. He recommends implementing test impact analysis, a method that runs only the tests affected by recent code changes rather than the entire test suite. By relying on automated validation tools to quickly verify AI-generated output, teams can successfully maintain software stability, reduce testing costs, and manage the high volume of code without sacrificing overall quality.


Hackers Exploit Weak Credentials and Internet-Facing PLCs to Breach Water Utilities

Water and wastewater utilities across the United States and Europe are facing increasing threats from state-sponsored groups affiliated with Iran, Russia, and China. Rather than relying on complex software, these attackers exploit fundamental security oversights, like internet-exposed control systems, default passwords, and inadequate network separation. This shift indicates that targeting civilian infrastructure has become a deliberate method to test emergency responses, create public anxiety, and position adversaries for future conflicts. For instance, Iranian-linked groups have used factory credentials to access unprotected systems, while Russian-affiliated actors actively disrupted operations by overflowing water tanks in Texas and opening floodgates in Norway. Meanwhile, Chinese groups take a quieter approach, establishing long-term access within utility networks to maintain leverage for potential disputes. To counter these vulnerabilities, security experts advise facility operators to implement basic defenses immediately. These include removing physical control systems from direct internet exposure, enforcing strict login requirements, replacing default passwords, and firmly separating industrial equipment from standard computer networks. By addressing these entry points, utilities can effectively reduce their risk of compromise and safely protect vital public water resources from further interference.