Showing posts with label data breach. Show all posts

Daily Tech Digest - November 07, 2026

Quote for the Day
“An approximate answer to the right question is worth far more than a precise answer to the wrong one.”
— John W. Tukey
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The post-quantum future of web privacy

The Cloudflare blog post explores the transition of web privacy protocols—specifically Privacy Pass—into a post-quantum world through a new technology called MOLE (Moderation Of unLinkable Endorsements). Privacy Pass currently uses classical cryptography (like RSA and elliptic curves) to issue anonymous tokens that allow users to access websites without solving CAPTCHAs or sacrificing their identity. While these tokens are unconditionally private against all attackers, a future quantum computer could forge them and bypass site security measures like rate limiting. To address this, the industry is developing MOLE to handle automated traffic while maintaining strict user privacy. The challenge in upgrading to post-quantum cryptography is the massive increase in data size; for instance, post-quantum ML-DSA-44 signatures are nearly forty times larger than current ECDSA signatures. Because drop-in replacements are not feasible right now, systems will need to be re-engineered to handle heavier cryptographic loads. Ultimately, MOLE and recent breakthroughs in blind signature design offer a promising pathway to secure, seamless, and fully private web authentication long after quantum computers become a reality.

Read Original Article →

The boardroom blind spot: you're measuring compliance, not culture

The boardroom blind spot lies in confusing compliance metrics with actual workplace culture. While corporate boards carry a clear mandate to oversee organizational culture and manage psychosocial risks, they often rely on lagging indicators like headcount, absenteeism, and turnover rates. These data points, typically extracted from standard Human Resource Information Systems, capture transactions and historical events rather than revealing why employees are disengaged or if leaders truly hold their teams' trust. This reliance on compliance-driven data creates a governance gap, masking underlying cultural decay until it erupts into costly turnover or a public crisis. To bridge this gap, modern organizations are pairing core compliance systems with purpose-built employee experience platforms. By tracking real-time insights, boards and executives can capture genuine human intelligence regarding psychological safety and cultural cohesion before problems escalate. Effectively overseeing culture means moving past mere workforce maintenance to active workforce engagement. Ultimately, evaluating whether existing tools actually measure employee sentiment or merely record transactions is no longer just an operational decision—it is a critical governance responsibility.
Read Original Article →
Article Thumbnail

Identity as an Architectural Concern: Enterprise IAM Beyond Authentication

The article emphasizes that as organizations scale, particularly in regulated environments like financial services, identity and access management (IAM) must be integrated directly into a system's core architecture rather than bolted on as an afterthought. For a single application, setting up basic single sign-on (SSO) and authenticating tokens might suffice. However, enterprise systems face complex governance challenges, such as tracking who approved specific access rights and verifying if those rights remain valid months later during an audit. Traditional flat Role-Based Access Control (RBAC) often struggles with these complex relationship queries. The author explains that shifting to a graph-based data model (like Neo4j queried via GraphQL) is far more effective for managing entities like people, service accounts, and resources. In a graph, ownership and access validity are straightforward traversals rather than cumbersome table joins. Designing the data schema early to capture timestamped events for every grant and revocation ensures that critical questions—such as who had access on a specific past date—can be answered efficiently, ultimately reducing the time needed to manage and revoke credentials.

Read Original Article →

The Next Target for Data Breach Lawsuits – Law Firms That Represent Breached Parties

The The Next Target for Data Breach Lawsuits – Law Firms That Represent Breached Parties examines whether lawyers advising companies after data breaches could themselves become targets of lawsuits from affected customers. It draws an important distinction between a law firm being sued because its own systems exposed personal information and being sued for advice given to a breached client about notification and disclosure. Existing legal precedent generally holds that lawyers owe duties to their clients, not automatically to third parties affected by their clients’ actions. This creates a significant hurdle for customers attempting to claim malpractice against outside breach counsel. However, law firms that receive and store personal information may still face ordinary data-security claims if their own handling of that information is challenged. The article warns that expanding liability for breach-response advice could complicate attorney-client relationships, increase insurance and legal costs, and make lawyers more cautious when advising on difficult notification decisions. Its central point is that future lawsuits may increasingly name breach lawyers as defendants, but plaintiffs will still need to establish why those lawyers owed them an independent legal duty.

Read Original Article →
Article Thumbnail

Master Data Management: The Foundation of Enterprise Data Architecture and Security

Modern organizations often struggle with highly inconsistent data that is scattered across many different systems like human resources, billing, and customer management. When the exact same customer or employee is tracked differently in each independent system, it creates confusion that goes far beyond simple record keeping. This inconsistency can easily lead to improper access grants and real security risks if critical updates, such as department changes, fail to reach every application. Master Data Management addresses this exact problem not just by centralizing storage, but by establishing a single, authoritative understanding of core business entities. It clearly establishes who owns the data, where it originally came from, and what relationships exist between different records. This clarity is essential for a reliable enterprise architecture and strong internal security. Instead of applying security controls blindly, identity and access management systems can rely on this accurate, consolidated information to enforce appropriate permissions and data protection rules across the board. By providing proper context and consistent metadata, Master Data Management ensures that applications apply the right security measures, ultimately serving as the reliable foundation needed to keep organizational information completely secure.
Read Original Article →
Article Thumbnail

Study Maps 24 Problems Where Quantum Computers Could Gain an Edge

A recent study has identified 24 computational problems where quantum computers could significantly outperform standard computing methods. However, the researchers emphasize that achieving this theoretical edge in real-world scenarios requires meeting strict mathematical and operational conditions. The compiled list spans diverse fields, including chemistry, optimization, number theory, and data analysis. While quantum algorithms might need far fewer steps to solve complex challenges, such as calculating a molecule's lowest energy state or solving systems of linear equations, practical hurdles remain. Time-consuming tasks like preparing initial data, correcting errors, and extracting usable results can quickly erase any expected speed gains. Furthermore, a meaningful improvement requires the quantum machine to solve problems at a rate exponentially or cubically faster than standard computers to offset the high operating costs of early error-corrected hardware. The study divides these 24 problems into two stages based on their readiness for practical application, providing a realistic roadmap for scientists and industry specialists. Ultimately, the research cautions that translating mathematical advantages into affordable, useful solutions for pressing business and scientific challenges requires overcoming significant hardware and data processing barriers.

Read Original Article →
Article Thumbnail

The CIO’s trust paradox: Your team may be more honest with AI than with you

The CIO’s trust paradox: Your team may be more honest with AI than with you argues that AI is creating a new challenge for workplace trust: employees may be more willing to raise concerns with an AI assistant than with their managers. Research cited in the article suggests psychological safety alone is not enough. Strong teams also need accountability, while trust in AI depends partly on people’s ability to handle uncertainty and judge when AI should be trusted or questioned. The more troubling possibility is that an employee may openly challenge a flawed idea when talking to AI, yet remain silent when the same issue appears in a meeting with senior leaders. In that situation, the organization possesses valuable insight but never receives it. The author urges CIOs to look beyond AI adoption figures and employee sentiment surveys and examine whether dissent actually influences decisions. Organizations should also provide safe ways for employees to move concerns discovered through AI conversations into human decision processes without monitoring private conversations. The central message is that leaders should ask not only whether employees trust AI, but whether they trust colleagues and managers enough to repeat what they tell AI.

Read Original Article →

How technical debt hinders AI rollouts and what to fix first

Technical debt often prevents organizations from successfully rolling out artificial intelligence initiatives, turning expected modernization into costly and disconnected infrastructure islands. For years, enterprises have allowed legacy systems and fragmented tools to coexist, leading to outdated security, siloed data, and inefficient resource allocation. When companies try to implement AI on top of this unstable foundation, they typically face escalating deployment times, decreased feature stability, and significant security risks from unmonitored AI agents carrying overly broad permissions. The resulting complexity forces organizations to manage and secure separate platforms simultaneously. To fix this, IT leaders must assess how their existing technical debt impacts their specific AI goals and plan the financial cost of modernization directly into their AI business cases. Priority should be given to integrating siloed data sources and establishing strict identity and access guardrails for AI agents. By piloting small, focused projects that address these foundational issues rather than attempting massive overhauls, businesses can clear the critical roadblocks, minimize infrastructure churn, and build a secure path for scalable, productive AI adoption.
Read Original Article →
Article Thumbnail

Enterprise FinOps: How CIOs Can Reduce Total Technology Cost by 30% or More

To achieve significant cost savings in technology, modern business leaders must expand their focus beyond simple cloud management and adopt a comprehensive financial operations strategy across their entire technology portfolio. With the rapid expansion of software subscriptions, independent contractors, and artificial intelligence experiments, hidden expenses easily accumulate in isolated departments. The primary culprits of this financial waste are duplicate software tools, unused premium licenses, unsupervised departmental purchases, and contractors who remain on payroll long after their initial projects end. To counter this, technology leaders need clear visibility into how every asset is consumed and what tangible value it delivers. By tracking software usage, renegotiating vendor contracts, adjusting service level agreements to match actual needs, and hosting artificial intelligence models on internal infrastructure where practical, organizations can uncover substantial inefficiencies. Addressing these hidden expenses allows leaders to safely reduce the massive budgets typically required just to keep basic systems running. Ultimately, recovering up to thirty percent of these everyday operational costs frees up essential capital, allowing the business to invest heavily in necessary modernization, new capabilities, and sustainable future growth.
Read Original Article →
Article Thumbnail

Can blockchain rewire India’s cross-border payment infrastructure?

Blockchain holds the potential to significantly improve India’s cross-border payment infrastructure, primarily by transforming back-office operations rather than creating new front-end experiences. Currently, international transactions rely on multiple intermediaries, messaging networks like SWIFT, and separate ledgers, which lead to slow reconciliations and delayed settlements. By introducing a shared, synchronized distributed ledger, blockchain could enable banks to reconcile transactions in real time, dramatically shrinking the delays caused by failed payments. Experts suggest that if countries adopt compatible blockchain standards, connecting their financial systems would become much more seamless. However, technology alone cannot solve the economic challenges of internationalizing the rupee or reducing dependency on the US dollar. While blockchain offers a faster and more efficient pipe for moving money, true global adoption requires robust bilateral trade, stronger exports, and comprehensive regulatory frameworks. Governments and participating institutions must still agree on validation rules, legal rights for tokenized assets, and dispute resolution mechanisms across jurisdictions. Ultimately, the success of blockchain in international finance will depend less on the code itself and more on whether regulators can build the legal foundation it needs to operate securely.

Read Original Article →

Daily Tech Digest - October 29, 2026

Quote for the Day
“The most expensive software is the one that doesn’t meet the needs of its users.”
— Karl Wiegers
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

When prevention fails: Why cyber resilience is the next big test of trust

The article explains that even well‑protected organizations can be thrown into chaos when a serious cyberattack disrupts basic operations, leaving leaders unsure which systems or data can still be trusted. It argues that prevention alone is no longer enough, because no control is perfect and attackers often find ways around strong defenses. Cyber resilience, therefore, becomes the next major test of trust: the ability to keep essential functions running, recover safely, and restore confidence after an incident. The piece highlights that backups are only useful if they can be accessed securely and restored without contamination, and that recovery plans must assume that some systems — including backup environments — may be compromised. Drawing on NIST guidance, it outlines four goals for resilience: anticipating threats, withstanding disruption, recovering trustworthy systems, and adapting based on lessons learned. The article’s steady message is that resilience must be designed into systems from the start, not treated as an afterthought, because the real challenge after an attack is determining what can still be relied on.

Read Original Article →

Programming Languages and Choosing a Path

Learning a programming language is about learning how to translate your logic into a format a computer can understand. An algorithm outlines the solution to a problem, while a programming language simply provides the vocabulary and rules to express that solution. Knowing the syntax of a language will not automatically make your logic correct. Behind the scenes, languages use tools like compilers or interpreters to turn human-readable instructions into actions the computer hardware can execute. When choosing your first programming language, it is important to remember that there is no universal best choice. Languages are tools built for different jobs. For example, C++ is great for competitive programming, Java offers strong structure for enterprise systems, and Python is highly readable and ideal for data tasks. Instead of getting caught up in the search for the perfect language, beginners should pick one that aligns with their immediate goals and local support system. Learn enough basics to express your logic clearly, and then focus on mastering problem-solving, which is the true core skill of programming.

Read Original Article →
Article Thumbnail

Beyond Binary Quantum Computing: Exploring Higher-Dimensional Qudits

Researchers at the University of Rochester, led by Professor Machiel Blok, are exploring a new approach to quantum computing using "qudits" instead of standard qubits. While traditional quantum computers rely on binary systems with just two energy states, qudits can store information across multiple levels. This concept mimics the natural world, where atoms and molecules naturally exist in multiple states. By matching the computer's structure to the physical problem it is trying to solve, the team believes qudits could offer a much more efficient way to tackle complex challenges in chemistry and physics. To make this work, the researchers developed a new method to control all energy transitions simultaneously, essentially building a denser, high-rise structure for information rather than a sprawling, flat one. Supported by reliable cooling technology, the lab also provides practical experience for students. Ultimately, this research suggests the future of quantum computing will likely rely on a mix of different systems tailored to specific problems, rather than a single binary approach.

Read Original Article →

Why Faster Algorithms Aren't Enough to Build High-Performance Data Platforms

The article argues that high‑performance data platforms cannot be created simply by swapping in faster algorithms or adding more hardware. Performance, it says, is an architectural outcome shaped by many upstream decisions about how data is represented, moved, stored, and delivered. Faster joins or better allocators help only at the margins; they cannot fix a system that is fundamentally slow because of poor layout, excessive data movement, or inefficient memory patterns. The piece highlights that modern platforms already rely on highly optimized libraries, so the real bottlenecks often appear between those functions — for example, when unnecessary tables are materialized, when workflows shuffle large datasets across layers, or when memory allocation becomes a long‑tail problem. It also notes that parallelizing work across CPU cores is relatively easy compared to designing a pipeline that avoids hidden costs in browsers, storage formats, or intermediate transformations. The steady message is that performance emerges from dozens of coordinated design choices, and no single algorithmic improvement can compensate for weak architectural foundations.

Read Original Article →
Article Thumbnail

Why decision-making is the next frontier of modern cyber resilience

The article explains that while many organizations have strong security tools and threat visibility, they still suffer vastly different outcomes during a cyberattack. This difference comes down to decision-making. Knowing a threat exists does not automatically tell leaders how to prioritize their limited resources or which systems to fix first. Standard security models improve accountability but often fail to connect technical risks with actual business goals. To close this gap, the author suggests adopting a decision system framework that translates threat data into clear, actionable choices. This approach evaluates risks based on their real-world impact on core business functions rather than just their technical severity. By blending financial realities, trust, and business priorities into the security process, leaders can make faster, better-coordinated choices during a crisis. Ultimately, effective security is no longer just about building taller walls or spotting potential attacks; it is about having a clear, reliable method to decide exactly where to act, what to protect first, and how to recover quickly when disruptions occur.

Read Original Article →

Wazuh and AI for Enhanced SOC Workflows

As cyber threats grow more complex, Security Operations Centers face an overwhelming volume of daily alerts that can easily cause analyst fatigue and missed critical events. To manage this workload, organizations are integrating artificial intelligence to support their security teams rather than replace them. Platforms like Wazuh address this need by offering flexible AI tools that streamline threat detection and response. For cloud users, the Wazuh AI Analyst automatically reviews security data using secure cloud models to deliver scheduled, comprehensive insights on vulnerabilities and overall security posture without exposing private data. For teams with strict privacy requirements, Wazuh supports self-hosted local models like Llama 3, keeping all log data safely within the company network. Alternatively, organizations can connect external models like Claude 3.5 Haiku directly into their dashboard to provide a helpful assistant for daily tasks. By handling repetitive analysis and data correlation, these AI integrations allow human analysts to focus on making the final decisions and keeping the organization secure.

Read Original Article →
Article Thumbnail

What Should a Business Do After a Personal Data Breach in India?

The article outlines the practical steps an Indian business should take immediately after discovering a personal data breach, emphasizing that quick, organized action matters more than panic. It begins with containment: isolating affected systems, revoking compromised credentials, and stopping further data loss. The next step is verification — confirming what happened, which data was exposed, and whether the breach is still active. The article stresses that businesses must document facts carefully because regulators will expect clear evidence of what was done and when. Under the DPDP Act, organizations must notify the Data Protection Board and affected individuals when harm is likely, and the article explains that vague or delayed communication can worsen legal and reputational consequences. It also highlights the need to preserve logs, review security controls, and assess whether vendors or third‑party processors contributed to the incident. The message is steady: a breach response is both a technical and governance exercise, and businesses must combine containment, transparency, and structured follow‑up to restore trust and meet regulatory expectations.

Read Original Article →

Shadow AI vs. Shadow IT: What's the Difference?

The article explains that “shadow AI” is emerging as a distinct and faster‑moving risk compared to traditional shadow IT. Shadow IT has long referred to employees using unapproved apps or services, often exposing data by storing it in places the organization cannot monitor. Shadow AI, however, introduces a sharper problem: employees feed internal data into AI tools — sometimes through personal accounts or new AI features inside already‑approved applications — without any governance. The piece notes that one in five organizations have already seen data exposure through personal AI accounts, showing how easily risky behavior can slip past existing controls. Unlike shadow IT, where data can often be retrieved or redirected, data given to an AI model may be processed, retained, or used for training in ways the organization cannot reverse. This shifts the governance challenge from simply discovering unauthorized apps to understanding what data enters AI systems, what outputs they generate, and what actions those systems can take. The article’s steady message is that AI requires new visibility, new controls, and a more nuanced approach than legacy shadow‑IT playbooks.

Read Original Article →
Article Thumbnail

When auditors come for your AI algorithms

As artificial intelligence increasingly influences critical business operations, traditional auditing methods are falling short. Conventional audits rely on predictable, step-by-step trails, but AI models—especially large language models—are inherently variable. This unpredictability makes it difficult for CIOs to explain how an AI system reached a specific conclusion, which frustrates auditors demanding clear evidence and accountability. The core problem often stems from vague ownership across different teams, rather than the technology itself. To bridge this gap, organizations must abandon point-in-time audits in favor of continuous monitoring and a structured accountability framework. This approach involves assessing risks during system design, continuously reviewing those risks as the technology evolves, and conducting independent evaluations of the process. Rather than waiting for a massive corporate AI rollout, leaders need to act now, as AI features are already embedded in everyday enterprise software. By treating audit readiness as a core business capability rather than a compliance chore, CIOs can take proactive ownership, reduce risk, and confidently support ongoing innovation.

Read Original Article →
Article Thumbnail

Building Review Intelligence into the SDLC with AI Agents and Archetypes

As artificial intelligence evolves beyond basic code generation, AI agents are becoming active collaborators throughout the software delivery lifecycle. Instead of replacing human architects, developers, and reviewers, these agents act as helpful partners that provide vital context and consistent feedback. To truly benefit from this shift, organizations should move past generic AI prompts and develop specialized, well-defined skills for design, architecture, and code reviews. These targeted skills can be organized into reusable patterns, or archetypes, tailored to specific tasks like building new applications, upgrading older systems, or migrating to the cloud. By employing a coordinated group of agents driven by strict checklists, a central agent can organize the workflow, while specialized agents handle security, performance, and compliance. A final review agent ensures all feedback is practical and backed by evidence. Ultimately, this structured approach transforms informal AI assistance into a reliable quality assurance process, allowing engineering teams to manage the increasing speed of modern software development with clarity and confidence.

Read Original Article →

Daily Tech Digest - September 09, 2026


Quote for the day:

"The only way to know if we are creating value is to measure the impact of what we ship." -- Teresa Torres

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Who owns the whole life of an enterprise IT asset?

The article discusses a common weakness in how businesses manage their enterprise hardware. While organizations are typically good at assigning responsibility for specific tasks—such as purchasing, deploying, or repairing a server—they often fail to clarify who is accountable for the asset over its entire useful life. This fragmented approach means that crucial information is frequently lost between different stages and teams. For instance, a deployment configuration change might severely complicate troubleshooting years later, or a missing repair history could lead to poor decisions about whether an upgrade is actually worthwhile. When the records fail to travel with the equipment, the next team inherits the hardware without understanding its complete background. To solve this problem, enterprises need a designated owner who holds authority to coordinate across various functions and ensure the asset’s history remains intact and accessible. Every transition should be treated as a formal deliverable, leaving behind a clear record of what was changed and why. By maintaining a continuous, well-documented history, companies can make much better decisions regarding whether to retain, repair, repurpose, or eventually retire their critical IT assets. Ultimately, the business itself must retain true ownership of the outcome.


The AI Fluency Crisis: Upgrading Passive Data Catalogs to Active Context Engines

Although modern companies have built strong data infrastructures and stable pipelines, they often struggle to successfully deploy advanced artificial intelligence. This problem arises because, while the technical setup is structurally sound, it lacks the essential business context needed for the system to interpret information accurately. In other words, the challenge has moved from simply storing data to actually understanding its meaning. An AI model might have access to massive amounts of perfectly organized information, but if it misunderstands fundamental business terms—like what defines an "active customer"—its practical value quickly falls apart. Historically, organizations relied on data catalogs and business glossaries to manage these definitions. While these traditional repositories are excellent tools for human analysts who can use their own intuition and experience to interpret the information, they do not work well for artificial intelligence. Humans can read a definition, trace where the data came from, and accurately apply it to their work. AI systems, however, lack this built-in enterprise intuition, making them prone to misinterpreting data when they rely solely on passive catalogs. To succeed, companies must find ways to actively provide these systems with the vital business context they need.


EU age assurance debate intensifies as Macron seeks bloc-wide social media law

French President Emmanuel Macron is urging the European Commission to adopt an EU-wide law that establishes a minimum age for social media platforms. France recently attempted to pass its own age assurance legislation, but it was blocked by the country's Constitutional Council over free speech concerns. By appealing directly to European Commission President Ursula von der Leyen, Macron hopes a unified, bloc-wide framework will bypass this national roadblock and effectively protect children across Europe. Instead of a strict prohibition, experts suggest the EU might propose a hybrid approach combining baseline age requirements with parental consent and strict rules against addictive platform designs. This push for regulation highlights growing concerns that a lack of coordinated action will lead to fragmented national policies. However, the debate remains highly contested. Privacy groups strongly oppose mandatory digital age checks, arguing they pave the way for mass surveillance and threaten internet freedom. Some advocates argue that if age gates are used, they must rely on privacy-preserving technologies like zero-knowledge proofs. Still, proponents of the regulation maintain that the ideal of a completely unrestricted internet is outdated, arguing that legal oversight is necessary to hold major tech platforms accountable.


Implementing Chaos Engineering in Financial Payment Systems: Lessons from Enterprise ECS Deployments

Chaos engineering is increasingly essential for financial payment systems, particularly those using Amazon Elastic Container Service (ECS). Traditional chaos playbooks, designed for stateless web applications, often fail in fintech environments due to strict compliance rules and complex transaction states. While typical web experiments can be stopped cleanly, payment transactions mid-flight may become stuck in ambiguous states requiring manual intervention. Furthermore, regulatory frameworks like PCI DSS and SOC 2 require formal approval for intentional production degradation. Teams must adapt by starting experiments on non-critical services before moving to primary transaction paths. ECS introduces specific vulnerabilities, such as a dangerous startup window where newly launched tasks accept traffic before they are fully initialized. Chaos experiments should target these blind spots proactively. Additionally, real-world failure behaviors often diverge from configured settings. For instance, a sixty-second DNS time-to-live might actually produce a ninety-three-second failover window due to intermediate caching. Similarly, ECS availability zone rebalancing can cause start-stop loops during partial degradation. By treating chaos experiments as formal change requests with defined steady states and rollback conditions, engineering teams can build resilient payment systems, satisfy strict audit requirements, and uncover hidden infrastructure flaws before they cause a critical, costly outage.


The EU AI Act just gave you a breach notification clock you didn’t know about

The European Union Artificial Intelligence Act has introduced a strict new deadline for incident reporting that many technology leaders might be overlooking. Under Article 73, which went into effect in August, companies providing high-risk AI systems must report serious incidents within 15 days, and in some severe cases, within just two to ten days. Unlike traditional data breaches that trigger immediate technical alerts from unauthorized access, AI incidents often surface much later and indirectly. For example, a flawed algorithm might silently deny benefits or loans, creating a harmful pattern that goes completely unnoticed by standard security monitoring tools until customers begin complaining weeks later. This fundamentally changes how organizations must handle incident response. Most companies lack a dedicated process for determining whether an AI output directly caused a downstream harm. To adapt, businesses must designate clear owners for these complex judgment calls rather than leaving them to chance during a crisis. Additionally, security teams need to lower the threshold for opening investigations, treating business unit complaints and customer escalations with the same urgency as technical alerts. Taking these proactive steps ensures organizations remain compliant and better equipped to manage the hidden risks of artificial intelligence.


Service Account Credential Rotation: The Blast-Radius Checklist

Rotating service account credentials can be risky, often causing production breakdowns because organizations lose track of how and where machine identities are used. Unlike human accounts, machine credentials—such as API keys, passwords, and tokens—frequently pile up across pipelines, vaults, and scripts without clear ownership. This creates fear around revocation, as an unmapped dependency could cause an entire application to fail. To safely rotate credentials and understand their "blast radius," security teams must answer eight essential questions. They must verify if the credential is still valid and whether it has been exposed, which escalates the risk. They also need to check its access scope to understand potential security impacts. Teams must map every consumer relying on the credential, locate its "source of truth" in a vault, and identify duplicate copies spread across systems. Finding the current owner is critical for coordinating the change, and establishing a rollback plan ensures quick recovery if rotation breaks a live system. By answering these questions and mapping dependencies before taking action, organizations can turn a high-risk gamble into a controlled production change, minimizing downtime while effectively securing long-lived secrets.


Why observability has become essential to the CIO's job

Observability has steadily evolved from a simple troubleshooting tool for developers into an essential management resource for modern Chief Information Officers. As technology infrastructures become more complex and interconnected, observability provides a very clear picture of how systems are performing and whether technology investments are delivering real value. It allows technology leaders to make practical decisions, such as identifying unused software licenses or safely extending the lifespan of company laptops based on actual usage data. The rapid adoption of artificial intelligence introduces both new challenges and new opportunities for observability. On one hand, autonomous AI agents and applications create additional layers of complexity that require careful monitoring to ensure they operate correctly and safely. On the other hand, artificial intelligence significantly improves observability tools by automatically sifting through massive amounts of data, reducing unhelpful alerts, and highlighting genuine issues faster than traditional methods. While the fundamental goal remains the same, identifying and fixing problems quickly, the future of observability is shifting toward a more proactive approach. Eventually, artificial intelligence could function as a helpful digital assistant that anticipates system failures and resolves them before they disrupt the business, ensuring smooth operations across increasingly complicated enterprise environments.


How European enterprises can meet sovereignty demands without giving up global reach

European enterprises are currently facing a complex and vital challenge: balancing strict data sovereignty regulations with the urgent need for global scale and connectivity. As digital operations expand, companies must strictly comply with evolving local privacy laws and maintain complete control over their sensitive information. However, they must accomplish this without isolating themselves from the broader international cloud ecosystem, which is essential for modern business. To successfully navigate this tension, organizations are increasingly adopting distributed and localized infrastructure models. This strategic shift allows them to securely store sensitive data in local environments that meet all regulatory standards, while still interacting with global partners and services. Instead of relying entirely on centralized public networks, businesses are utilizing private, direct interconnections. This method safely routes data across borders, effectively bypassing the vulnerabilities of the public internet and ensuring that information stays protected. Ultimately, this approach provides a reliable path forward, giving companies the ability to enforce strict geographic boundaries and guarantee ongoing compliance. By modernizing their digital infrastructure, European businesses can safeguard their critical assets without sacrificing their competitive edge, continuing to drive innovation and support sustainable international growth in a highly connected modern global economy.


50% of CISOs see Mythos as a sign to exit the profession

Chief Information Security Officers are facing unprecedented stress, leading half of them to consider quitting due to the rapid rise of advanced artificial intelligence models like Anthropic's Mythos. A recent survey shows that pressure from company leadership to quickly adopt these tools is far outpacing the ability of security teams to manage the associated risks. Security leaders are exhausted by a landscape where attackers weaponize vulnerabilities almost instantly. Adding to this heavy burden is the increasing personal liability placed on executives when data breaches inevitably occur. Many new job candidates are now demanding liability insurance before even asking about budgets or team sizes. However, industry experts point out that while advanced technology heightens existing problems, it also offers practical solutions. Security teams can leverage artificial intelligence to improve their own defenses, provided they start with low-risk applications and avoid untested models in production. Despite the grueling demands, where anything less than total perfection is often viewed as a failure, some security professionals still find the work deeply rewarding. For these resilient leaders, defending their organizations and customers against complex modern threats remains a highly engaging and meaningful challenge that keeps them dedicated to the field.


AI Agent Security Is Recreating the Password Problem

As artificial intelligence agents become increasingly common in business operations, they are inadvertently recreating the classic password problem. Historically, passwords posed a security risk because they could be separated from the user and reused until someone detected the breach. Today, when teams give AI agents reusable credentials or standing service accounts to perform tasks, they introduce a similar vulnerability. An AI agent might retain access to sensitive systems like customer databases or financial records long after its original assignment is complete. Because these agents can independently decide which tools to call, lingering access can be easily exploited if the agent encounters malicious instructions or deeply compromised workflows. To prevent this, organizations need to stop giving AI agents permanent static secrets. Instead, security teams should implement brokered access models. In this setup, an agent must securely request temporary permission for each specific action it takes. A policy enforcement layer evaluates the request based on the delegated authority and the potential risk. Once the specific task concludes, the granted access immediately expires. By controlling permissions dynamically and closely monitoring automated actions, companies can safely utilize artificial intelligence without allowing temporary access to become a permanent and dangerous vulnerability.

Daily Tech Digest - August 29, 2026


Quote for the day:

“You may be disappointed if you fail, but you are doomed if you don’t try.” -- Beverly Sills


🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


Digital twins are evolving from passive virtual mirrors into active decision environments, making their underlying data structures more critical. As artificial intelligence agents are introduced into these environments, they must evaluate complex layers of information such as sensor data, equipment dependencies, and historical records to make sound operational decisions. However, AI agents demand more than standard data access; they require durable, long term memory. Rather than forcing information into prompt windows or attaching separate storage systems, organizations should treat agent memory as primary data within the twin itself. This approach means accurately tracking the source of every fact, its historical context, and its validity over time. Crucially, when new information contradicts an older belief, the system should not simply overwrite the past. Instead, it must retain the original data and link it to the update. Preserving this chain of reasoning creates an essential audit trail that builds trust and supports proper governance. To handle this complexity at scale, unified data foundations are necessary to seamlessly link documents, temporal states, and structured records. Ultimately, the challenge is no longer just building the digital model, but constructing the comprehensive memory around it, ensuring that human operators and machines can act with complete confidence.


AI Slop in the Enterprise: What Happens When Engineers Stop Reviewing AI-Generated Code

AI slop in enterprise software engineering refers to low-quality, AI-generated code that appears functional on the surface but introduces hidden defects, security flaws, and severe maintenance burdens. This phenomenon occurs when developers use AI tools to generate code much faster than teams can responsibly review it. Consequently, pull requests accumulate, and code is frequently merged without thorough human oversight. Because AI-generated code lacks clear human intent, reviewing it requires significantly more effort to identify subtle architectural errors, ultimately doubling review times and placing a heavy burden on senior engineers. This growing review tax leads to burnout and a divide between responsible developers and those who submit AI output without understanding it. The business impact is substantial. Studies show that while AI increases coding volume, it also introduces security vulnerabilities at a vastly accelerated rate, with nearly half of AI-generated samples containing fundamental flaws. Furthermore, unmanaged AI code can quadruple technical debt by the second year, silently embedding architectural mistakes that slow down future development. To solve this problem, enterprises must shift their focus from raw coding speed to strict governance. Solutions involve implementing visible quality metrics, enforcing architectural fit, and applying automated rule sets to verify AI output before human review even begins.


The three layers of agentic AI security: A defense-in-depth architecture for autonomous agents

The VentureBeat article outlines a comprehensive security architecture designed to address the specific risks of autonomous AI agents. Traditional security measures fall short because these agents operate independently and can inadvertently cause data leaks or execute unintended commands. To manage these new risks, the piece proposes a security model built on three distinct layers. First, the infrastructure layer establishes a secure foundation by verifying the physical and digital environments where agents run. By using methods such as hardware level trust and secure isolation, this step ensures that only authorized workloads operate, which is especially important for regulated industries like finance. Second, the network layer manages how agents communicate with other systems and data sources. Because agents generate complex and dynamic traffic patterns, traditional static network rules no longer work. Instead, organizations must adopt dynamic, strict access policies that closely control internal movement and data retrieval. Finally, the control plane acts as the central management hub for permissions and resource allocation. This layer enforces rules consistently across the entire system, preventing agents from using unauthorized tools or consuming excessive computing power. Together, these three layers provide a structured approach to securing independent AI systems, allowing organizations to maintain effective control and continuous oversight.


The Board’s Role in Crisis Management and Scenario Planning

In an era of unpredictable disruptions, a board of directors must shift from merely reacting to crises to actively preparing for them. The core responsibility of the board in crisis management is oversight and strategic guidance, rather than day-to-day execution. While senior management is tasked with implementing response plans when an emergency strikes, the board ensures that robust frameworks, ethical standards, and clear communication channels are already established. A critical tool in this proactive approach is scenario planning. By anticipating potential threats, ranging from financial downturns and operational failures to reputational damage, boards can guide management in developing practical response strategies before a crisis occurs. This involves conducting regular risk assessments and participating in crisis simulations to build organizational resilience. Scenario planning helps uncover hidden vulnerabilities and tests the effectiveness of current policies, allowing companies to respond swiftly and confidently when real challenges arise. Furthermore, effective governance during a crisis requires clear decision-making processes and an unwavering commitment to the company's long-term stability. After a crisis, the board must also lead the review process to identify lessons learned and improve future readiness. Ultimately, strong board leadership transforms crisis management from a frantic scramble into a structured, reliable process that protects the organization and its stakeholders.


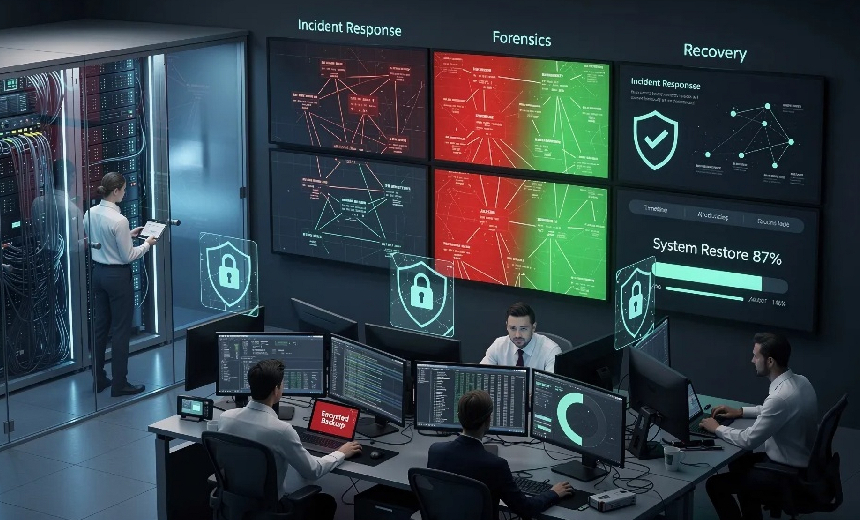
Most Organizations Declare Victory Over a Breach Too Early

When dealing with a security incident, business leaders often feel pressured to return to normal operations as quickly as possible. This pressure leads many organizations to declare victory over a breach long before the threat is fully removed. In their rush to restore services, response teams typically address the most obvious signs of an attack, such as isolating a compromised server or resetting user passwords. However, stopping the investigation at this early stage is a critical mistake. Intruders often establish hidden backdoors, create secondary accounts, or move laterally across the network well before the initial detection occurs. If responders fail to conduct a thorough forensic analysis, these hidden footholds remain active, allowing the attackers to quietly regain access days or weeks later. To effectively resolve a cyber incident, organizations must shift their focus from mere speed to complete threat eradication. This requires committing to extended monitoring and ensuring that all affected systems are deeply analyzed for residual threats. Teams should wait until they have clear evidence that the environment is genuinely secure before announcing that the crisis has passed. By taking a careful, methodical approach to recovery, companies can better protect themselves from falling victim to the exact same intruders twice.
Artificial intelligence is fundamentally changing how enterprise software is built, shifting the industry away from large, specialized teams toward smaller, highly skilled groups. At the center of this shift is the IT architect. Rather than simply overseeing design, architects are returning to direct implementation. AI tools allow them to compress the traditional software process into a single, continuous loop that includes analysis, design, coding, testing, and deployment. To succeed today, these architects must combine a deep understanding of business operations with strong technical judgment. By using AI to close the gap between an initial idea and working software, small, architecture-led teams can deliver solid results in a fraction of the time. For instance, a recent legacy system update was finished in just five months instead of the usual two years, without sacrificing basic security, data integrity, or accuracy. This newfound efficiency completely changes the underlying economics of technology development. Traditional systems integrators and major software providers that rely on large staffs and lengthy timelines will face serious market pressure. Highly experienced professionals equipped with modern tools can now build complex systems much faster and more affordably. Consequently, business leaders must rethink their approach to building and buying technology before smaller, more capable competitors outpace them.

In a recent interview at Black Hat USA 2026, Omdia analyst Theresa Lanowitz shared findings on how artificial intelligence is shifting the landscape of cybersecurity. She notes that older methods like standard penetration testing and simulated attacks are no longer enough to keep up with the speed at which threats operate today. Because of this, organizations are rethinking their defense strategies and increasing their investments in offensive security. In fact, research shows that a vast majority of companies are willing to spend more to gain continuous visibility and better track devices across their networks. However, deploying automated tools for defense introduces its own set of challenges. Companies are rightly concerned about the risks of these systems behaving unpredictably, falling victim to manipulative inputs, or simply driving up costs. To manage these risks, experts recommend establishing strict boundaries to limit the potential damage if a system goes off track. Furthermore, securing the software supply chain has become incredibly critical. While nearly all organizations recognize its importance and are investing heavily in it, less than half are documenting their software components during the build process. Ultimately, business leaders are prioritizing overall resilience to ensure they can withstand and recover from unexpected incidents.


CTEM can give your security team a contextual edge

Traditional vulnerability management relies on periodic assessments and patching, but this approach is no longer enough to keep up with fast-moving cyber threats. Many security teams are now turning to continuous threat exposure management (CTEM) to stay ahead. Unlike standard scanners that only flag software flaws, CTEM takes a much broader view of an organization's actual risk. It actively monitors for misconfigurations, identity risks, and excessive permissions across cloud environments, applications, and networks. A major advantage of this continuous model is that it focuses on validation and action. Instead of simply generating long lists of potential issues, it helps teams determine whether a vulnerability is truly exploitable under their current defenses. It also ensures specific people are assigned to fix the most critical problems, shifting the goal from counting flaws to actually closing attack paths. To work well, this approach relies heavily on automation and contextual intelligence, combining technical data with business priorities. However, adopting this new model requires significant cultural shifts. Security leaders must overcome tool fatigue, break down departmental silos, and change their teams' mindsets. Rather than just hunting for every single technical error, the focus must shift toward steadily reducing the overall risk to the core business.

Cybersecurity in manufacturing is no longer just an IT concern; it is a fundamental operational discipline. When a cyber incident strikes a factory, it halts production, impacts product quality, and compromises worker safety. Because modern facilities connect legacy machinery with cloud services, robots, and artificial intelligence, the boundaries of the factory floor have expanded. This creates new vulnerabilities, yet many companies still rely on traditional IT security methods. Standard IT practices, like aggressive scanning and immediate patching, can actually disrupt continuous manufacturing processes. Instead, protecting operational technology requires a different approach focused on system availability, using passive monitoring and protective architecture around older equipment rather than replacing it. A major challenge is the division of responsibility between IT, engineering, and plant operations, which often leaves critical decisions unresolved during an attack. To build real resilience, plant leaders need clear ownership of cyber risks, treating them with the same importance as workplace safety and product quality. By developing specific response plans before an incident occurs, teams can drastically reduce recovery time. Ultimately, manufacturers must merge technical threat knowledge with practical engineering experience to ensure that their facilities run reliably and securely in an increasingly connected world.


Security Readiness Looks Good On Paper. Investigations Say Otherwise

Organizations frequently overestimate their cybersecurity readiness, assuming that purchasing an array of security tools makes them safe. In reality, the true strength of a security program is only revealed during an actual breach, which often exposes a gap between what leaders believe and what is actually happening. Many companies buy defenses like endpoint detection or backup systems but fail to fully implement or monitor them around the clock. Attackers capitalize on these cumulative, minor weaknesses, such as delayed updates or lingering credentials, rather than relying on a single sophisticated exploit. Furthermore, detecting threats has become increasingly difficult as attackers use stealthy methods and artificial intelligence to blend their movements with normal daily operations. Instead of waiting for a breach to happen to secure funding and buy the newest marketed tools, leaders should adopt a proactive mindset. This means asking what protective measures they would wish they had in place if an attack happened tomorrow. By relying on forensic evidence from actual incidents rather than theoretical product demonstrations, companies can focus on battle-tested solutions and practical fixes. Closing the gap between perceived readiness and actual defense capabilities allows organizations to address their vulnerabilities before attackers can exploit them.