Showing posts with label biometric. Show all posts

Daily Tech Digest - October 20, 2026

Quote for the Day
“I’m not a great programmer; I’m just a good programmer with great habits.”
— Kent Beck
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The CIO Is No Longer Paid to Deliver Systems

The article argues that the CIO’s job has shifted from delivering systems to managing trust, dependencies, and reversibility in an environment shaped by fast‑moving AI. It explains that technology now evolves far faster than contracts, regulations, or culture, leaving CIOs stuck with long commitments in a world that changes weekly. AI has made producing code and content cheap, but verifying accuracy remains costly, creating pressure on senior talent and raising questions about accountability when autonomous agents act incorrectly. Costs also rise with adoption, making successful AI use cases surprisingly expensive. The CIO’s real challenge, the article says, is managing dependencies on a small set of global vendors and navigating geopolitical risks, sudden outages, and opaque SaaS features. At the same time, organizations struggle with visibility into their own systems, data, and business logic. Responsibility for failures sits with the CIO, even though authority is distributed across the business. The piece concludes that the modern CIO’s value lies in overseeing trust, dependencies, and optionality — and in acknowledging that many issues can only be managed, not solved.

Read Original Article →
Article Thumbnail

The password nobody owns: Taking machines to zero standing privilege (ZSP)

DevSecOps aims to integrate security directly into the software delivery pipeline, ensuring the safest path is also the fastest. Rather than relying on manual reviews or end-of-process security gates, development teams should automate security checks at every stage. This begins in the developer's environment, where static analysis tools can flag common issues like SQL injection before code is even committed. From there, automated secret scanning ensures API keys and credentials never make it into version control, while dependency scanners stop builds if known vulnerabilities are present. When applications are packaged, teams should use minimal container images running without root privileges to reduce the attack surface. Security rules themselves should be written as code, allowing automated policy engines to verify that deployments meet requirements before they go live. Finally, runtime protection requires structured logging, rate limiting, and threat detection tools to monitor behavior in production. This automated approach not only secures the application but automatically generates the evidence needed for compliance audits. The goal is to build security incrementally into the delivery process so that developers can move quickly without needing to remember complex security rules or deal with separate review teams.

Read Original Article →
Article Thumbnail

4 ways to tame shadow AI (hint: you need them all)

Unsanctioned artificial intelligence in the workplace creates serious risks for businesses, especially as modern tools evolve from simple text chatbots into highly autonomous agents capable of independently executing complex tasks. When employees use unapproved personal accounts to write code or analyze sensitive data, they expose the company to significant security threats, including unintended data leaks and even accidental cyberattacks on other organizations. To effectively manage this growing challenge, business leaders are adopting a comprehensive four-part strategy rather than relying on a single quick fix. First, they provide safe and approved internal tools that meet the actual daily needs of their teams, effectively reducing the temptation to look elsewhere. Second, they deploy security software to monitor network activity, block risky platforms, and prevent sensitive information from leaving the company environment. Third, they focus heavily on education, ensuring everyone understands the potential dangers of using unapproved platforms and knows how to operate safely. Finally, companies are establishing clear guidelines and holding people accountable if they deliberately bypass safety protocols. By combining secure alternatives, strong technical safeguards, ongoing education, and firm policy enforcement, organizations can confidently protect their information without losing the benefits of new technology.

Read Original Article →

Leadership gaps can become direct business risks

According to Sunder Natrajan, the Chief Human Resources Officer at IndiaFirst Life, waiting until a critical role is empty to develop a leader is a risky approach. The insurance industry's shift toward digital and data-led operations requires leaders who go beyond just having a long tenure or good sales numbers. Instead, future leaders must build digital fluency, adaptability, and the ability to manage complex rules and AI systems. While specific functional experience is helpful, strong leadership today requires a broader view of the enterprise. Middle managers are especially crucial because they turn top-level strategy into daily action, yet they are frequently overwhelmed by demands without receiving the necessary capability support. Preparing the leadership pipeline needs to become a constant, ongoing priority rather than an occasional human resources program. Businesses must rethink succession planning not as a private list of names, but as a continuous system of giving people practical exposure, testing their potential, and providing cross-functional learning. Ignoring these leadership gaps creates direct business risks, including burnout and weak succession depth. Ultimately, a strong pipeline ensures that an organization can turn industry disruption into confidence for both customers and employees.
Read Original Article →
Article Thumbnail

World brings biometric proof of human to banking and AI agents

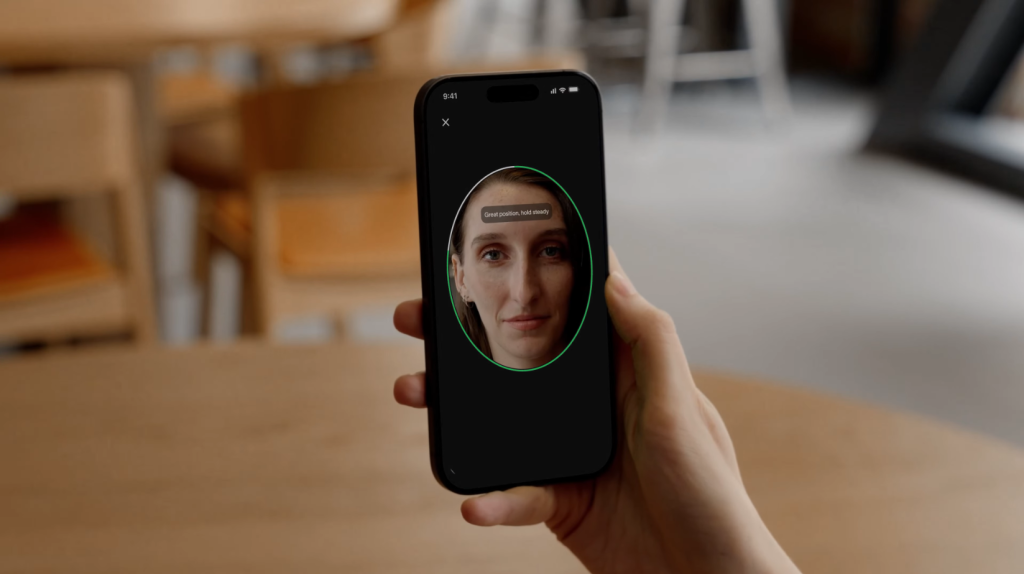
World has introduced a new suite of biometric identity tools for the banking and financial sectors to combat deepfake fraud and securely link artificial intelligence agents to actual people. The offering includes three main components: the World ID app, World ID for Zoom, and World ID for Agents. These tools rely on cryptographic proofs to verify that a user is a unique human, is physically present during the transaction, and meets specific identity requirements, all while preserving privacy through zero-knowledge cryptography. Financial institutions face increasing risks from sophisticated, AI-driven fraud. Impersonators can easily replicate voices and video, making remote transactions highly vulnerable. World’s solution addresses this by requiring users to verify their identity through an initial biometric scan using a “World Orb,” followed by smartphone-based liveness checks for subsequent interactions. For high-stakes video calls, World ID for Zoom allows participants to authenticate themselves, earning a “Human Badge” to prevent impersonation. Additionally, as automated agents take on more financial tasks, World ID for Agents allows users to delegate proof of their identity to these bots. This ensures that banks can trust automated requests originate from verified customers without requiring the underlying personal data.

Read Original Article →

The Hidden Cost of Supply Chain Complexity

For years, businesses have invested heavily in technology to make supply chains faster and more efficient, yet they continue to face rising costs and difficult decision-making. The core issue is often not a lack of data, but rather overwhelming complexity. Today's supply networks involve larger ecosystems, multiple sales channels, and an increasing range of global risks. While organizations have more information than ever, decision-making has become fragmented because different teams operate in silos with separate systems and goals. This lack of coordination leads to hidden costs, such as excess inventory or higher transportation expenses, which reduce agility and miss growth opportunities. A recent study highlights this challenge in Australia and New Zealand, where agility is now prioritized to manage supply chain risks. To address these issues, companies are shifting from merely monitoring their supply chains to orchestrating decisions across all functions. Artificial intelligence plays a vital role in this transition by processing vast amounts of data to model outcomes and guide informed decisions. AI agents are even beginning to handle routine tasks, allowing human teams to focus on critical strategies. Ultimately, simplifying how decisions are made is essential for organizations to manage complexity and remain competitive in the future.

Read Original Article →
Article Thumbnail

9 tips for future-proofing your IT leadership career

The role of the Chief Information Officer is changing rapidly as technology advances, particularly with artificial intelligence. To thrive in the future, IT leaders must move beyond traditional management and become visionary strategic partners who can translate technological capabilities into measurable business value. This means cultivating a transformational mindset that looks past current processes to reimagine what the organization could become. CIOs will need to deeply understand emerging tools, not just to buy them, but to identify the real business risks and trade-offs they might bring. As AI becomes more common, the focus will shift toward managing a hybrid workforce where humans and intelligent agents work side-by-side. IT leaders will be responsible for creating the structure, governance, and training needed for this new dynamic, while also helping other C-suite executives navigate similar changes in their departments. Finally, maintaining success requires continuous curiosity and a commitment to learning about the next big technology. Future-proofing a career also means intentionally sharpening leadership skills, seeking honest feedback, and stepping into high-pressure situations to build resilience and prove capability in a fast-paced environment.

Read Original Article →

The Real Challenge Isn’t Adopting AI – It’s Scaling It Responsibly

While many organizations successfully pilot artificial intelligence, scaling it across an enterprise introduces complex operational and ethical hurdles. According to Eddie Pinto, companies often struggle because they treat the rollout merely as an IT project rather than a fundamental business shift. To succeed, leaders must prioritize solving actual business problems instead of just deploying the newest models for the sake of innovation. Furthermore, robust data governance has to be established before implementation begins, ensuring that privacy, security, and consent are handled properly from the start. Cross-functional collaboration is equally vital; bringing in human resources, legal, and operations teams early helps identify blind spots and mitigate risks that technical teams might miss. Earning user trust also depends heavily on transparency—employees need to understand when and how the tools are being used, particularly when decisions affect them directly. Because regulations and technological capabilities are evolving rapidly, this governance cannot be a one-time effort. Organizations must commit to continuous evaluation and remain willing to retire systems that no longer meet their ethical or performance standards. Ultimately, scaling responsibly means using the technology to empower workers with more time for creative and strategic thinking, fostering trust across the organization.

Read Original Article →
Article Thumbnail

A new framework teaches AI models to audit and repair each other’s reasoning, improving accuracy

A new framework developed by researchers at Stanford University, Together AI, and Emory University enables artificial intelligence models to audit and repair each other's reasoning. Traditional multi-agent setups rely on rigid, pre-scripted pipelines or simple voting mechanisms. These often fail when complex problems cannot be neatly divided or when no single model holds the complete answer. To solve this, researchers introduced Self-Organizing Agent Teams, a system that allows a fixed group of distinct models to review past interactions and learn reusable teamwork strategies. Instead of breaking down a specific problem beforehand, these models structure a conversation where they naturally test, challenge, and revise each other's ideas. During rigorous mathematics and physics tests, this collaborative approach outperformed both the strongest individual models and perfect routing methods. By building on each other's partial insights, models like DeepSeek-V3 and Claude Sonnet 4 worked together to spot specific mistakes and piece together correct answers that none could reach independently. While the system excels in verifiable tasks like math and coding, it faces challenges in softer knowledge areas where wrong explanations can sound convincing. Ultimately, this framework proves that groups of models can learn to organize themselves and reason together without requiring human-led task breakdowns.
Read Original Article →
Article Thumbnail

Cryptographic Foundation of Mobile ID Systems: an ISO/IEC 18013-5 Enterprise Architecture Blueprint

Transitioning from physical IDs to mobile driver’s licenses changes where information is stored and how devices authenticate identities. While many technology teams might assume integrating a mobile ID is as simple as adding a few API calls, the underlying architecture involves far more complexity. Although a company can use a specialized provider to handle the implementation, they must still take responsibility for the overall system architecture. Before committing to any provider or software development kit, organizations must ask important questions about how device keys are protected, how credential revocation works offline, and what user data the provider collects. Evaluating a mobile ID provider requires looking beyond a successful demonstration. Businesses need to investigate the trust model, the cryptographic boundaries, privacy controls, and how the system behaves if the provider goes offline. To properly implement a mobile ID ecosystem, companies should clearly separate identity proofing from credential provisioning, as these involve different security responsibilities. Ultimately, treating mobile IDs as a broader trust architecture problem ensures that companies can maintain control over critical data and trust boundaries, even when relying on third-party integrations for the basic functionality.

Read Original Article →

Daily Tech Digest - April 23, 2026


Quote for the day:

“Every time you have to speak, you are auditioning for leadership.” -- James Humes

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


How To Navigate The New Economics Of Professionalized Cybercrime

The modern cybercrime landscape has evolved into a professionalized industry where attackers prioritize precision and severity over volume. According to recent data, while the frequency of material claims has decreased, the average cost per ransomware incident has surged, signaling a shift toward more efficient targeting. This new economic reality is defined by three primary trends: the rise of data-theft extortion, the prevalence of identity attacks, and the long-tail financial consequences that follow a breach. Because businesses have improved their backup and recovery systems, criminals have pivoted from simple encryption to threatening the exposure of sensitive data, often leveraging AI to analyze stolen information for maximum leverage. Furthermore, the professionalization of these threats extends to supply chain vulnerabilities, where a single vendor compromise can cause cascading losses across thousands of downstream clients. Consequently, cyber incidents are no longer isolated technical failures but material enterprise risks with financial repercussions lasting years. To navigate this environment, organizational leaders must shift their focus from mere operational recovery to robust data exfiltration prevention. CISOs, CFOs, and CROs must collaborate to integrate cyber risk into broader enterprise frameworks, ensuring that financial planning and security investments account for the multi-year legal, regulatory, and reputational exposures that now characterize the threat landscape.


How Agentic AI is transforming the future of Indian healthcare

Agentic AI represents a transformative shift in the Indian healthcare landscape, transitioning from passive data analysis to autonomous, goal-oriented systems that proactively manage patient care. Unlike traditional AI, which primarily focuses on reporting, agentic systems independently execute tasks such as triaging, scheduling, and continuous monitoring to address India’s strained doctor-to-patient ratio. By integrating these intelligent agents, medical facilities can streamline outpatient visits—from digital symptom recording to automated post-consultation follow-ups—significantly reducing the administrative burden on overworked clinicians. The technology is particularly vital for chronic disease management, where it provides timely nudges for medication adherence and identifies early warning signs before they escalate into emergencies. Furthermore, Agentic AI acts as a crucial support layer for frontline health workers in rural regions, bridging the clinical knowledge gap through real-time protocol guidance and decision support. While these advancements offer a scalable solution for public health, the article emphasizes that human empathy remains irreplaceable. Successful adoption requires robust frameworks for data privacy and ethical transparency, ensuring that physicians always retain final decision-making authority. Ultimately, by evolving from a mere tool into essential digital infrastructure, Agentic AI is poised to democratize access and foster a more responsive, patient-centric healthcare ecosystem across the diverse Indian population.


What a Post-Commercial Quantum World Could Look Like

The article "What a Post-Commercial Quantum World Could Look Like," published by The Quantum Insider, explores a future where quantum computing has moved beyond its initial commercial hype into a phase of deep integration and stabilization. In this post-commercial era, the focus shifts from the race for "quantum supremacy" toward the practical, ubiquitous application of quantum technologies across global infrastructure. The piece suggests that once the technology matures, it will cease to be a standalone industry of speculative startups and instead become a foundational utility, much like the internet or electricity today. Key impacts include a complete transformation of cybersecurity through quantum-resistant encryption and the optimization of complex systems in logistics, materials science, and drug discovery that were previously unsolvable. This transition will likely lead to a "quantum divide," where geopolitical and economic power is concentrated among those who have successfully integrated these capabilities into their national security and industrial frameworks. Ultimately, the article paints a picture of a world where quantum mechanics no longer represents a frontier of experimental physics but serves as the silent, invisible engine driving high-performance global economies and ensuring long-term technological resilience.


Continuous AI biometric identification: Why manual patient verification is not enough!

The article explores the critical transition from manual patient verification to continuous AI-powered biometric identification in modern healthcare. Traditional methods, such as verbal confirmations and physical wristbands, are increasingly deemed insufficient due to their susceptibility to human error and data entry inconsistencies, which often lead to fragmented medical records and life-threatening mistakes. To address these vulnerabilities, the industry is shifting toward a model of constant identity assurance using advanced technologies like facial biometrics, behavioral signals, and passive authentication. This continuous approach ensures real-time validation across all clinical touchpoints, significantly reducing the risks associated with duplicate electronic health records — currently estimated at 8-12% of total files. Furthermore, the integration of agentic AI and multimodal systems — combining fingerprints, voice, and device data — creates a secure identity layer that streamlines clinical workflows and protects patients from misidentification. With the healthcare biometrics market projected to reach $42 billion by 2030, the article argues that automating identity verification is no longer optional. Ultimately, by replacing episodic manual checks with autonomous, intelligent monitoring, healthcare organizations can enhance data integrity, safeguard financial interests against identity fraud, and, most importantly, ensure the highest standards of safety for the individuals in their care.


The 4 disciplines of delivery — and why conflating them silently breaks your teams

In his article for CIO, Prasanna Kumar Ramachandran argues that enterprise success depends on maintaining four distinct delivery disciplines: product management, technical architecture, program management, and release management. Each domain addresses a fundamental question that the others are ill-equipped to answer. Product management defines the "what" and "why," establishing the strategic vision and priorities. Technical architecture translates this into the "how," determining structural feasibility and sequence. Program management orchestrates the delivery timeline by managing cross-team dependencies, while release management ensures safe, compliant deployment to production. Organizations frequently stumble by treating these roles as interchangeable or asking a single team to bridge all four. This conflation "silently breaks" teams because it forces experts into roles outside their core competencies. For instance, an architect focused on product decisions might prioritize technical elegance over market needs, while program managers might sequence work based on staff availability rather than strategic value. When these boundaries blur, the result is often wasted effort, missed dependencies, and a fundamental misalignment between technical output and business goals. By clearly delineating these responsibilities, leaders can prevent operational friction and ensure that every capability delivered actually reaches the customer safely and generates measurable impact.


Teaching AI models to say “I’m not sure”

Researchers at MIT’s Computer Science and Artificial Intelligence Laboratory (CSAIL) have developed a novel training technique called Reinforcement Learning with Calibration Rewards (RLCR) to address the issue of AI overconfidence. Modern large language models often deliver every response with the same level of certainty, regardless of whether they are correct or merely guessing. This dangerous trait stems from standard reinforcement learning methods that reward accuracy but fail to penalize misplaced confidence. RLCR fixes this flaw by teaching models to generate calibrated confidence scores alongside their answers. During training, the system is penalized for being confidently wrong or unnecessarily hesitant when correct. Experimental results demonstrate that RLCR can reduce calibration errors by up to 90 percent without sacrificing accuracy, even on entirely new tasks the models have never encountered. This advancement is particularly significant for high-stakes applications in medicine, law, and finance, where human users must rely on the AI’s self-assessment to determine when to seek a second opinion. By providing a reliable signal of uncertainty, RLCR transforms AI from an unshakable but potentially deceptive voice into a more trustworthy tool that explicitly communicates its own limitations, ultimately enhancing safety and reliability in complex decision-making environments.


Are you paying an AI ‘swarm tax’? Why single agents often beat complex systems

The VentureBeat article discusses a "swarm tax" paid by enterprises that over-engineer AI systems with complex multi-agent architectures. Recent Stanford University research reveals that single-agent systems often match or even outperform multi-agent swarms when both are allocated an equivalent "thinking token budget." The perceived superiority of swarms frequently stems from higher total computation during testing rather than inherent structural advantages. This "tax" manifests as increased latency, higher costs, and greater technical complexity. A primary reason for this performance gap is the "Data Processing Inequality," where critical information is often lost or fragmented during the handoffs and summarizations required in multi-agent orchestration. In contrast, a single agent maintains a continuous context window, allowing for much more efficient information retention and reasoning. The study suggests that developers should prioritize optimizing single-agent models—using techniques like SAS-L to extend reasoning—before adopting multi-agent frameworks. Swarms remain useful only in specific scenarios, such as when a single agent’s context becomes corrupted by noisy data or when a task is naturally modular and requires parallel processing. Ultimately, the article advocates for a "single-agent first" approach, warning that unnecessary architectural bloat can lead to diminishing returns and inefficient resource utilization in enterprise AI deployments.


Cloud tech outages: how the EU plans to bolster its digital infrastructure

The recent global outages involving Amazon Web Services in late 2025 and CrowdStrike in 2024 have underscored the extreme fragility of modern digital infrastructure, which remains heavily reliant on a small group of U.S.-based hyperscalers. These disruptions revealed that the perceived redundancy of cloud computing is often an illusion, as many organizations concentrate their primary and backup systems within the same provider's ecosystem. Consequently, the European Union is shifting its strategy from mere technical efficiency to a geopolitical pursuit of "digital sovereignty." To mitigate the risks of "digital colonialism" and the reach of the U.S. CLOUD Act, European leaders are championing the 2025 European Digital Sovereignty Declaration. This framework prioritizes the development of a federated cloud architecture, linking national nodes into a cohesive, secure network to reduce dependence on foreign monopolies. Furthermore, the EU is investing heavily in homegrown semiconductors, foundational AI models, and public digital infrastructure. By establishing a dedicated task force to monitor progress through 2026, the bloc aims to ensure that European data remains subject strictly to local jurisdiction. This comprehensive approach seeks to bolster resilience against future technical failures while securing the strategic autonomy necessary for Europe’s long-term digital and economic security.


When a Cloud Region Fails: Rethinking High Availability in a Geopolitically Unstable World

In the InfoQ article "When a Cloud Region Fails," Rohan Vardhan introduces the concept of sovereign fault domains (SFDs) to address cloud resilience within an increasingly unstable geopolitical landscape. While traditional high-availability strategies focus on technical abstractions like multi-availability zone (multi-AZ) deployments to mitigate hardware failures, Vardhan argues these are insufficient against sovereign-level disruptions. SFDs represent failure boundaries defined by legal, political, or physical jurisdictions. Recent events, such as sudden cloud provider withdrawals or infrastructure instability in conflict zones, demonstrate how geopolitical shifts can trigger correlated failures across entire regions, rendering standard multi-AZ setups ineffective. To combat these risks, architects must shift their baseline for high availability from multi-AZ to multi-region architectures. This transition requires a fundamental rethink of distributed systems, moving beyond technical redundancy to include legal and political considerations in data replication and traffic management. The article advocates for the adoption of explicit region evacuation playbooks, the definition of geopolitical recovery targets, and the expansion of chaos engineering to simulate sovereign-level losses. Ultimately, achieving true resilience in the modern world necessitates acknowledging that cloud regions are physical and political assets, not just virtualized resources, requiring intentional design to survive jurisdictional partitions.


Inside Caller-as-a-Service Fraud: The Scam Economy Has a Hiring Process

The BleepingComputer article explores the emergence of "Caller-as-a-Service," a professionalized vishing ecosystem where cybercrime syndicates mirror the organizational structure of legitimate businesses. These industrialized fraud operations utilize a clear division of labor, employing specialized roles such as infrastructure operators, data analysts, and professional callers. Recruitment for these positions is surprisingly formal; underground job postings resemble professional LinkedIn ads, specifically seeking native English speakers with high emotional intelligence and persuasive social engineering skills. To establish credibility, recruiters often display verifiable "proof-of-profit" via large cryptocurrency balances to entice new talent. Once hired, callers are frequently subjected to real-time supervision through screen sharing to ensure strict adherence to malicious scripts and maximize victim conversion rates. Compensation models are equally sophisticated, ranging from fixed weekly salaries of $1,500 to success-based commissions of $1,000 per successful vishing hit. This service-driven model significantly lowers the barrier to entry for criminals, as it allows them to outsource the technical and interpersonal complexities of a cyberattack. Ultimately, the article emphasizes that the professionalization of the scam economy makes these threats more resilient and efficient, necessitating that defenders implement more robust identity verification and multi-factor authentication to protect individuals from these increasingly coordinated, data-driven vishing campaigns.

Daily Tech Digest - April 05, 2026


Quote for the day:

​"Risk management is a culture, not a cult. It only works if everyone lives it, not if it’s practiced by a few high priests." -- Tom Wilson


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Reengineering AML in the Era of Instant Payments

The transition to high-value instant payments, underscored by the Federal Reserve’s decision to raise FedNow transaction limits to $10 million, necessitates a fundamental reengineering of Anti-Money Laundering (AML) frameworks. Traditional monitoring systems, plagued by a 95% false-positive rate and designed for retrospective reviews, are increasingly inadequate for real-time rails where compliance decisions must occur within seconds. Consequently, financial institutions are shifting their controls upstream, prioritizing pre-settlement checks, robust customer due diligence, and behavioral profiling.
​This evolution moves AML from a reactive back-end function to a preventive, intelligence-led process integrated throughout the customer life cycle. Enhanced data standards like ISO 20022 further enable nuanced, risk-based decisioning by providing richer transaction context. While industry experts argue that AI-powered tools can reconcile the perceived conflict between processing speed and rigorous control, the pace of adoption remains uneven across the sector. Larger institutions are aggressively modernizing their architectures, whereas smaller firms often struggle with legacy system constraints and vendor dependencies. Ultimately, the industry is moving toward a converged model where fraud and AML functions merge to address financial crime holistically. This strategic shift ensures that security does not come at the expense of the frictionless experience demanded by modern corporate treasury and retail sectors.


Inconsistent Privacy Labels Don't Tell Users What They Are Getting

The Dark Reading article "Inconsistent Privacy Labels Don't Tell Users What They Are Getting" critiques the current effectiveness of mobile app privacy labels, such as those found on Apple’s App Store and Google Play. While originally designed to offer consumers transparency regarding data collection practices, researcher Lorrie Cranor highlights that these labels remain largely inaccurate and "not at all useful" in their present state. According to recent studies, the discrepancies between an app’s actual data handling and its public label often stem from developer misunderstandings and honest technical mistakes rather than malicious intent. However, this inconsistency creates a deceptive environment where companies appear to be prioritizing user privacy without actually doing so. To address these failings, experts advocate for the standardization of privacy reporting across platforms and the implementation of automated verification tools to assist developers. Furthermore, placing these labels more prominently within app store listings would ensure users can make informed decisions before downloading software. Ultimately, without rigorous verification and clearer presentation, the current privacy label system serves as more of a performative gesture than a functional security tool, failing to provide the level of protection and clarity that modern smartphone users require and expect from major digital marketplaces.


Cybersecurity and Operational Resilience: A Board-Level Imperative

In today's digital landscape, cybersecurity and operational resilience have evolved into critical boardroom imperatives, driven by a sophisticated threat environment and rigorous global regulations. The article highlights how sector-agnostic attacks, exemplified by the massive disruption at Change Healthcare, underscore the systemic risks posed to essential services. Contributing factors include the widespread monetization of "ransomware-as-a-service" and the emergence of AI-driven threats like deepfakes and automated phishing. Consequently, regulators in the EU and U.S. have introduced stringent frameworks—such as the NIS 2 Directive, the Digital Operational Resilience Act (DORA), and updated SEC rules—that demand proactive oversight, timely incident disclosure, and direct accountability from management bodies. Beyond mere legal compliance, boards are increasingly targeted by activist investors leveraging governance lapses as a catalyst for change. To navigate these challenges, the article advises directors to cultivate cyber expertise, rigorously oversee internal controls, and integrate AI governance into their broader strategic frameworks. Ultimately, organizations must shift from a reactive posture to a proactive, enterprise-wide resilience strategy to protect shareholders and ensure long-term stability amidst rapid technological shifts, quantum computing risks, and escalating financial losses associated with cyber breaches. This requires not only monitoring vulnerabilities but also investing in talent and technical controls that can withstand the dual pressures of legal liability and operational disruption.


Biometric data sharing infrastructure matures as border control expectations evolve

The article outlines significant advancements and challenges in the global biometric landscape as of April 2026, emphasizing the maturation of data-sharing infrastructures and evolving border control expectations. A primary focus is the centralization of digital trust, exemplified by Apple’s mandatory age verification in the UK and EU, which shifts identity assurance to the device level. Meanwhile, international travel is being streamlined by ICAO’s updated Public Key Directory, allowing airports and airlines to authenticate documents remotely via passenger smartphones. NIST has further modernized these systems by transitioning biometric data exchange standards to fully machine-readable formats. Despite these technical leaps, practical hurdles remain, such as recurring delays in implementing Entry/Exit System checks at major UK-EU borders. On a national level, digital identity programs are expanding, with Niger launching biometric cards for regional integration and Spain granting full legal status to its digital identity. Conversely, market pressures led to the closure of Australia Post's Digital iD. Finally, the rise of AI agents has sparked a debate over "proof of personhood," highlighting the urgent need for robust digital frameworks to differentiate between human users and automated entities within an increasingly complex and interconnected global digital ecosystem.


Learning to manage the cloud without losing control

In this insightful opinion piece, Vera Shulman, CEO of ProfiSea, addresses the critical challenges organizations face as they integrate generative artificial intelligence into their operations, specifically highlighting the surge in cloud spending. Shulman argues that while product teams focus on model capabilities, leadership often overlooks the strategic blind spot of runaway infrastructure costs. To prevent the estimated thirty percent of generative AI projects from failing after the proof-of-concept stage due to financial instability, she proposes a framework built on three fundamental pillars of cloud governance. First, she emphasizes token economics, suggesting that businesses must meticulously monitor token consumption and utilize retrieval-augmented generation to minimize data transfer costs. Second, Shulman advocates for a robust multi-cloud strategy to avoid vendor lock-in and provide the flexibility to route tasks to the most cost-efficient models. Finally, she stresses the necessity of automated financial management tools that can allocate resources in real-time and detect usage anomalies. Ultimately, the transition of artificial intelligence from a significant budget burden into a powerful strategic asset depends on intentionally designing cloud infrastructure around efficiency and governance. Decision-makers must shift their focus from mere model performance to ensuring their underlying systems are truly prepared for AI-centric business operations.


Multi-Agent AI Patterns for Developers: Pick the Right Pattern for the Right Problem

In "Multi-agent AI Patterns for Developers," the author examines the transition from basic prompt engineering to sophisticated agentic architectures designed for production-level reliability. The article outlines several fundamental patterns, starting with the Router, which uses a classifier to direct queries to specialized agents, and the Sequential Chain, which is ideal for linear, multi-step processes. It emphasizes the Orchestrator-Workers model for complex tasks requiring dynamic planning and delegation, alongside the Parallel/Voting pattern for achieving consensus across multiple agent outputs. A significant portion of the text is dedicated to the Evaluator-Optimizer loop, a pattern where one agent refines work based on the critical feedback of another to ensure high-quality results. By selecting patterns based on specific constraints—such as latency, cost, and reasoning depth—developers can move beyond monolithic LLM calls toward systems that handle error recovery and specialized tool usage effectively. Ultimately, the guide suggests that the future of AI development lies in these modular, collaborative frameworks, which provide the transparency and control necessary to execute intricate business logic. This strategic selection of architectures bridges the gap between experimental prototypes and robust, autonomous AI agents capable of operating within complex real-world environments.


How digital twins are redefining visibility and control in supply chain and logistics

Digital twins are revolutionizing supply chain and logistics by bridging the gap between physical operations and digital data. This technology creates a granular, real-time mirror of reality, enabling businesses to move beyond simple tracking to deep operational intelligence. By integrating warehouse and transport management systems with IoT sensors, digital twins provide a unified data backbone that identifies process risks and SLA breaches before they impact customers. This transformation shifts supply chains from reactive systems to intelligent, anticipatory ones that offer predictive insights and prescriptive models. The practical benefits include accelerated decision-making, optimized resource utilization, and significant cost reductions through smarter labor planning and routing. Furthermore, digital twins enhance service quality by providing early warning signals for potential delivery failures. However, successful implementation demands rigorous data governance and automated anomaly detection to ensure accuracy. As these models evolve, they progress toward autonomous orchestration, recommending strategic actions like inventory rebalancing and order reallocation. Ultimately, treating the digital twin as a strategic asset allows companies to achieve unprecedented precision and reliability. By fostering a shared operational truth across departments, organizations can compress planning cycles and set new benchmarks for excellence in an increasingly competitive market where customer experience is paramount.


Without controls, an AI agent can cost more than an employee

The article "Without controls, an AI agent can cost more than an employee" explores the financial risks of deploying AI agents without rigorous oversight. Industry experts, including Jason Calacanis and Chamath Palihapitiya, note that uncontrolled API usage—particularly for complex tasks like coding—can drive agent costs to $300 daily, effectively rivaling a $100,000 annual salary. This "sloppy" deployment often occurs when organizations use frontier models for broad, unmonitored tasks, leading to excessive token consumption that may only replace a fraction of human labor. Furthermore, experts emphasize that while agents can perform high-impact shipping of features, blindly trusting them with code leads to significant quality and security concerns. To mitigate these expenses, IT leaders must transition from treating AI as a fixed utility to managing it as a variable-cost resource. Key strategies include implementing hard spending caps, assigning unique API keys to teams, and utilizing smaller, fine-tuned models for specific, bounded tasks. While AI agents offer significant productivity gains, their economic viability depends on benchmarking inference costs against actual labor value. Ultimately, successful integration requires clear governance, where agents are treated with the same accountability and budgetary controls as any other department asset to ensure they remain a cost-effective tool.


The New Leadership Bottleneck Isn't Productivity—It's Judgment

In her Forbes article, Michelle Bernier argues that the primary bottleneck for leadership has shifted from productivity to judgment. As artificial intelligence continues to automate a significant majority of execution-based tasks, sheer output volume no longer serves as a competitive advantage. Instead, the modern leader's value lies in the ability to navigate uncertainty, discern which goals are worth pursuing, and protect the cognitive capacity required for high-stakes strategic thinking. ​This paradigm shift requires leaders to prioritize deep focus, as a single hour of uninterrupted deliberation now yields more organizational value than days of distracted task completion. To adapt, Bernier suggests that executives should organize their schedules around peak energy levels rather than mere calendar availability, pre-decide recurring choices through robust frameworks to preserve mental resources, and explicitly teach their teams to internalize these decision-making criteria. Ultimately, thriving in an AI-driven era is not about working harder or faster; it is about becoming ruthlessly clear on where to apply human insight and protecting the conditions that make high-level thinking possible. Leaders who fail to cultivate this deliberate quality of judgment risk remaining busy while falling behind, whereas those who master it will turn focused judgment into their most sustainable competitive asset.


Components of A Coding Agent

In "Components of a Coding Agent," Sebastian Raschka explores the architectural requirements for effective AI-driven programming assistants, moving beyond standard Large Language Models (LLMs) toward integrated agentic systems. He distinguishes between base LLMs, reasoning models, and fully-fledged agents, emphasizing that a robust "agent harness" is essential for reliable performance. The article outlines six critical building blocks: the core LLM, a planning/reasoning layer, tool integration, memory, repository context management, and feedback mechanisms. By incorporating tools like terminal access and file system interfaces, agents can move beyond text generation to active code execution and testing. Memory and repository context ensure the agent remains grounded in project-specific requirements, while feedback loops allow for reflection, auditing, and error correction. Raschka suggests that the future of coding agents lies in transitioning from a "chat-to-code" paradigm to a more structured "chat-to-spec-to-code" workflow, where intent is captured as a formal specification first. This modular approach directly addresses common industry issues like context drift and hallucinations, ensuring that the AI system operates within a deterministic framework. Ultimately, the effectiveness of a coding agent depends not just on the underlying model's intelligence, but on the sophisticated control layer and integration of these modular components.


Daily Tech Digest - March 05, 2026


Quote for the day:

"To get a feel for the true essence of leadership, assume everyone who works for you is a volunteer." -- Kouzes and Posner


CISOs Are Now AI Guardians of the Enterprise

CISOs are managing risk, talent and digital resilience that underpins critical business outcomes - a reality that demands new approaches to leadership and execution. Security leaders are quantifying and communicating ROI to executive leadership, developing the next generation of cybersecurity talent, and responsibly deploying emerging technologies - including generative and agentic AI ... While CISOs approach AI with cautious optimism, 86% fear agentic AI will increase the sophistication of social engineering attacks and 82% worry it will increase deployment speed and complexity of persistence mechanisms. "This is happening primarily because AI accelerates existing weaknesses in how organizations understand and control their data. The solution to both is not more tools, but [to implement] a strong and well-understood data governance model across the organization," said Kim Larsen, group CISO at Keepit. ... Despite the rise of AI, CISOs know that human intelligence and judgement supersede even the most intelligent tools, because of their ability to understand context. Their primary strategies include upskilling current workforces, hiring new full-time employees and engaging contractors, especially for nuanced tasks like threat hunting. "AI risk management, cloud security architecture, automation skills and the ability to secure AI-driven systems will be far more valuable in senior cybersecurity hires in 2026 than they were three years ago," said Latesh Nair


The right way to architect modern web applications

A single modern SaaS platform often contains wildly different workloads. Public-facing landing pages and documentation demand fast first contentful paint, predictable SEO behavior, and aggressive caching. Authenticated dashboards, on the other hand, may involve real-time data, complex client-side interactions, and long-lived state where a server round trip for every UI change would be unacceptable. Trying to force a single rendering strategy across all of that introduces what many teams eventually recognize as architectural friction. ... Modern server-rendered applications behave very differently. The initial HTML is often just a starting point. It is “hydrated,” enhanced, and kept alive by client-side logic that takes over after the first render. The server no longer owns the full interaction loop, but it hasn’t disappeared either. ... Data volatility matters. Content that changes once a week behaves very differently from real-time, personalized data streams. Performance budgets matter too. In an e-commerce flow, a 100-millisecond delay can translate directly into lost revenue. In an internal admin tool, the same delay may be irrelevant. Operational reality plays a role as well. Some teams can comfortably run and observe a fleet of SSR servers. Others are better served by static-first or serverless approaches simply because that’s what their headcount and expertise can support. ... When something breaks, the hardest part is often figuring out where it broke. This is where staged architectures show a real advantage. 


Safeguarding biometric data through anonymization

Biometric anonymization refers to a range of approaches that remove Personally Identifiable Information (PII) from biometric data so that an individual can no longer be identified from the data alone. If, after anonymization, the retained data or template can still perform its required function, then we have successfully removed the risk of the identifiers being compromised. An anonymized biometric template in the wrong hands then has no meaningful value, as it can’t be used to identify the individual from whom it originated. As a result, there is great interest in anonymization approaches that can meet the needs of different business applications. ... While biometrics deliver significant value across a wide range of use cases, safeguarding data privacy and meeting regulatory obligations remain top priorities for most organizations. Biometric anonymization can help reduce risk by limiting the exposure of sensitive personal data. Taken together, anonymization approaches address different dimensions of risk – from inference and reporting exposure to vulnerabilities at the template level. They are not one-size-fits-all solutions. Organizations must evaluate which method aligns with their functional requirements, risk tolerance, and compliance obligations, while ensuring that only the minimum necessary personal data is retained for the intended purpose. Anonymization is no longer a peripheral consideration. 


Security leaders must regain control of vendor risk, says Vanta’s risk and compliance director

The rise of AI technologies has made vendor networks increasingly harder to manage. Shadow supply chains (untracked vendor networks), fast-moving subcontracting, model updates, data-sharing and embedded tooling all compound the complexities. Particularly for large enterprises with a network of tens of thousands of suppliers or more, traditional vendor management relying on legacy infrastructure and manual operations is no longer adequate. This is where the Cyber Security and Resilience Bill comes in, forcing a shift toward continuous monitoring which should match the speed of AI threats. ... By implementing evidence-led reporting templates, automated control validation, and continuous monitoring of supplier security posture, businesses can provide the board with real-time assurance, not point-in-time attestations. This approach demonstrates that systemic supplier risk is actively managed without diverting disproportionate time away from frontline threat detection and response. At an operational level, leaders shouldn’t wait for the bill to be finalised to find out who their ‘critical suppliers’ are. ... Upcoming changes to the bill will likely encourage tighter contractual obligations. Businesses should get ahead of this mandate and implement measures such as incident notification service-level agreements, rights-to-audit and evidence provisions, continuous monitoring, and Software bill of Materials.


Inspiration And Aspiration: Why Feel-Good Leadership Rarely Changes Outcomes

Inspiration is fancy. It makes ideas feel noble, futures feel possible and leadership feel virtuous—all without demanding immediate action or sacrifice. We feel moved, aligned and temporarily elevated. It’s a dream we see others have achieved through their actions. Aspiration is different. It is inconvenient. It’s our own dream, our desire to see ourselves in a certain spot or a way in the future. It requires disproportionate effort, new skills and a willingness to confront the uncomfortable gap between who we are today and who we say we want to become. ... That gap between intent and impact was uncomfortable. I told myself "I can't" and then took a step back, which was the easiest thing to do. What I realized is this: Aspiration without action becomes self-deception. Inspiration without action becomes mere admiration. And leadership that relies on either one eventually stagnates. Real change happens only when inspiration and aspiration move together, dance together—not sequentially, not occasionally, but in constant unison. ... Belief does not close gaps; capability and capacity do. Until the distance between intention and reality is acknowledged, effort will always be miscalculated. This gap should evoke and cement commitment, rather than creating drag. One needs to be very careful at this stage, as most people stop here. We may get inspired by mountaineers climbing Everest, but when we do a mental assessment about ourselves, we assume we are incapable of the task of bridging the gap, and we take a step back.


Most Organizations Plan Strategically. Few Manage It That Way

The report segments respondents into two categories: “Dynamic Planners,” characterized by frequent review cycles, cross-functional integration, high portfolio visibility, and active use of scenario planning; and “Plodders,” defined by siloed operations, infrequent reassessment, and limited real-time visibility into execution data. The performance difference between them is sharp enough to be operationally relevant. Eighty-one percent of Planners’ projects deliver measurable ROI or strategic value. Among Plodders, that figure is 45%. That’s a 36-point spread. That’s not measuring financial metrics; it’s about whether projects are doing what they were supposed to do. The survey also found that 30% of projects are not delivering meaningful ROI or strategic value. That leaves nearly one in three funded initiatives operating at levels ranging from marginal to counterproductive. ... Over a third of projects across the survey population are stopped early due to misalignment or insufficient ROI. The report treats this not as a problem to fix but as a sign of mature portfolio management. Chynoweth frames it in capital terms: “Cancellation is not failure. It’s disciplined capital allocation.” Most enterprises reward launch momentum, delivery against plan, and continuation of funded initiatives. Budget cycles create sunk-cost inertia. Career incentives favor project sponsors who ship, not those who cancel. 


Malicious insider threats outpace negligence in Australia

John Taylor, Mimecast's Field Chief Technical Officer for APAC, said organisations are seeing more cases where insiders are used to bypass established security controls. "We're seeing a concerning acceleration in malicious insider threats across Australia. While negligence has traditionally been the primary insider concern, intentional betrayal is now growing at a faster rate. ..." The report described AI as a factor that can increase the speed and scale of attacks, citing more convincing social engineering messages and automated reconnaissance. It also raised the prospect of AI being used to help recruit insiders. Taylor said older assumptions about a clear boundary between internal and external users no longer match how organisations operate, particularly with distributed workforces and widespread cloud adoption. ... Governance and compliance over communications data emerged as another concern. Mimecast found 91% of Australian organisations face challenges maintaining governance and compliance across communications data, and 53% lack confidence in quickly locating data to meet regulatory or legal requirements. These issues can slow incident response by delaying investigations and limiting the ability to reconstruct timelines across messaging platforms, email, and file stores. They can also increase risk during regulatory inquiries when organisations must produce relevant records quickly. Taylor said visibility is central to improving governance, culture, and response.


AI fatigue is real and it’s time for leaders to close the organizational gap

AI has been pitched as the next great accelerant of productivity. But inside many enterprises, teams are still recovering from years’ worth of transformation programs—cloud migrations, ERP upgrades, data modernization. Adding AI to an already overloaded change agenda can feel less like innovation and more like yet another disruption to absorb. The result is a predictable backlash. Tools in the industry are dismissed as “just another license”. Expectations are sky high; lived experience is often underwhelming. And when the novelty wears off, employees revert to old behavior fast. ... A pervasive misconception is that adopting AI is mostly about selecting and deploying the right technology. But tooling alone doesn’t redesign workflows. It doesn’t train employees. It doesn’t embed new decision making patterns. Some of the highest spending organizations are seeing the least value from AI precisely because investment has been concentrated at the technology layer rather than the organizational one. Without true operational change, AI tools risk becoming surface level enhancements rather than business accelerators. ... AI is not a spectator sport. Employees must understand how to use it, when to trust it, and how it adds value to their role. Organizations that invest early in skills from prompting to automation design will see dramatically higher adoption rates. The companies scaling fastest are those that build internal capability, not dependency on a small number of specialists.


Measuring What Matters in Large Language Model Performance

The study is timely, as LLM innovation increasingly targets skills and traits that are difficult to benchmark. “There’s been a shift towards testing AI systems for more complex capabilities like reasoning, helpfulness, and safety, which are very hard to measure,” said Rocher. “We wanted to look at whether evaluations are doing a good job capturing these sorts of skills.” Historically, AI innovators focused on equipping programs with easy-to-measure skills, like the ability to play chess and other strategy games. Today’s general-purpose LLMs, including popular models like ChatGPT, feature more flexible, open-ended strengths and traits. These attributes are notoriously difficult to operationalize, or to define in a way that’s precise enough to work in AI program measurement but broad enough to encompass the many different ways that the attribute might show up in the real world. Reasoning is one such skill. While most people are able to tell what counts as good or bad reasoning on a case-by-case basis, it’s not easy to describe reasoning in general terms. ... Towards this end, “Measuring what Matters” includes a set of guidelines to promote precision, thoroughness, rigor, and transparency in benchmark development. The first two recommendations, “define the phenomenon” and “measure the phenomenon and only the phenomenon,” encourage benchmark authors to be direct and specific as they define their target phenomena. 


Hallucination is not an option when AI meets the real world

For Boeckem, the most consequential AI applications are not advisory. They are autonomous. “In industrial environments, AI doesn’t just recommend,” he says. “It acts.” That shift, from insight to action, raises the stakes dramatically. Autonomous systems operate in safety-critical environments where failure can result in physical damage, financial loss, or human harm. “When generative AI went mainstream in 2022, it was exciting,” Boeckem says. “But professional environments need AI that is grounded in reality. These systems must always know where they are, what obstacles exist, and what the consequences of an action might be.” ... Despite the growing popularity of digital twins, many enterprises struggle to make them operational. According to Boeckem, the problem is not ambition, but misunderstanding. “A digital twin must be fit for purpose,” he says. “And above all, it must be dimensionally accurate.” Accuracy is non-negotiable. A flood simulation requires a watertight model. Urban planning demands precise representations of sunlight, shadows, and surroundings. Aesthetic simulations require photorealistic textures and material properties. At the most complex end of the spectrum, Hexagon models human faces. “A human face is not static,” Boeckem explains. “It’s soft-body material. When you smile, when you’re angry, when you’re sad, it changes. If you want to do diagnosis or therapy, you have to account for that.” 

Daily Tech Digest - December 10, 2025


Quote for the day:

"Develop success from failures. Discouragement and failure are two of the surest stepping stones to success." -- Dale Carnegie


Design in the age of AI: How small businesses are building big brands faster

Instead of hiring separate agencies for naming, logo design, and web development, small businesses are turning to unified AI platforms that handle the full early-stage design stack. Tools like Design.com merge naming, logo creation, and website generation into a single workflow — turning an entrepreneur’s first sketch into a polished brand system within minutes. ... Behind the surge in AI design tools lies a broader ecosystem shift. Companies like Canva and Wix made design accessible; the current wave — led by AI-native platforms like Design.com — is more personal and adaptive. Unlike templated platforms, these tools understand context. A restaurant founder and a SaaS startup will get not just different visuals, but different copy tones, typography systems, and user flows — automatically. “What we’re seeing,” Lynch explains, “isn’t just growth in one product category. It’s a movement toward connected creativity — where every part of the brand experience learns from every other.” ... Imagine naming a company and watching an AI instantly generate a logo, color palette, and homepage layout that all reflect the same personality. As your audience grows, the same system helps you update your visual identity or tone to match new goals — while preserving your original DNA.


Henkel CISO on the messy truth of monitoring factories built across decades

On the factory floor, it is common to find a solitary engineering workstation that holds the only up-to-date copies of critical logic files, proprietary configuration tools, and project backups. If that specific computer suffers a hardware failure or is compromised by ransomware, the maintenance team loses the ability to diagnose errors or recover the production line. ... If the internet connection is severed, or if the third-party cloud provider suffers an outage, the equipment on the floor stops working. This architecture fails because it prioritizes connectivity over local autonomy, creating a fragile ecosystem where a disruption in a remote cloud environment creates a “digital brick” out of physical machinery. ... An attacker does not need sophisticated “zero-day” exploits to compromise a fifteen-year-old human-machine interface, they often just need publicly known vulnerabilities that will never be fixed by the vendor. By compromising a peripheral camera or an outdated visualization node, they gain a persistence mechanism that security teams rarely monitor, allowing them to map the operational technology network and prepare for a disruptive attack on the critical control systems at their leisure. ... A critical question for CISOs to ask is: “Can you provide a continuously updated Software Bill of Materials for your firmware, and what is your specific process for mitigating vulnerabilities in embedded third-party libraries?”


AI churn has IT rebuilding tech stacks every 90 days

Even without full production status, the fact that so many organizations are rebuilding components of their agent tech stacks every few months demonstrates not only the speed of change in the AI landscape but also a lack of faith in agentic results, Northcutt claims. Changes in the agent tech stack range from something as simple as updating the underlying AI model’s version, to moving from a closed-source to an open-source model or changing the database where agent data is stored, he notes. In many cases, replacing one component in the stack sets off a cascade of changes downstream, he adds. ... While the speed of AI evolution can drive frequent rebuilds, part of the problem lies in the way AI models are tweaked, she says. “The deeper issue is that many agent systems rely on behaviors that sit inside the model rather than on clear rules,” Hashem explains. “When the model updates, the behavior drifts. When teams set clear steps and checks for the agent, the stack can evolve without constant breakage.” ... “What works now may become suboptimal later on,” he says. “If organizations don’t actively keep up to date and refresh their stack, they risk falling behind in performance, security, and reliability.” Constant rebuilds don’t have to create chaos, however, Balabanskyy adds. CIOs should take a layered approach to their agent stacks, he recommends, with robust version control, continuous monitoring, and a modular deployment approach.


Why Losing One Security Engineer Can Break Your Defences

When tools are hard to manage – or if you need to bundle numerous tools from different vendors together – tribal knowledge builds up in one engineer’s head. It’s unrealistic to expect them to document it. Gartner recently said that organizations use an average of 45 cybersecurity tools and called for security leaders to optimize their toolsets. And in that context, losing the one person who understands how these systems actually work is not just inconvenient: it's a structural risk. And the impact this has is seen in the data from the State of AI in Security & Development report; using numerous vendors for security tools correlates with more incidents, more time spent prioritising alerts and slower remediation. In short, a security engineer has too much on their plate, and most security tools aren’t making their job any easier. ... “Organisations tend to be all looking for the same blend of technical cloud, integration, SecOps, IAM experience but with extensive knowledge in each pillar,” says James Walsh, National Lead for Cyber, Data & Cloud UK&I at Hays. “Everyone wants the unicorn security engineer whose experience spans all of this, but it comes at too high a price for lots of organisations,” he adds. Walsh notes that hiring is often driven by teams below the CISO — such as Heads of SecOps — which can create inconsistent expectations of what a ‘fully competent’ engineer should look like.


Overload Protection: The Missing Pillar of Platform Engineering

Some limits exist to protect systems. Others enforce fairness between customers or align with contractual tiers. Regardless of the reason, these limits must be enforced predictably and transparently. ... In data-intensive environments, bottlenecks often appear in storage, compute, or queueing layers. One unbounded query or runaway job can starve others, impacting entire regions or tenants. Without a unified overload protection layer, every team becomes a potential failure domain. ... Enterprise customers often face challenges when quota systems evolve organically. Quotas are published inconsistently, counted incorrectly, or are not visible to the right teams. Both external customers and internal services need predictable limits. A centralized Quota Service solves this. It defines clear APIs for tracking and enforcing usage across tenants, resources, and time intervals.  ... When overload protection is not owned by the platform, teams reinvent it repeatedly. Each implementation behaves differently, often under pressure. The result is a fragile ecosystem where: Limits are enforced inconsistently, for example, some endpoints apply resource limits, while others run requests without enforcing any limits, leading to unpredictable behavior and downstream problems; Failures cascade unpredictably, for example, a runaway data pipeline job can saturate a shared database, delaying or failing unrelated jobs and triggering retries and alerts across teams


Is your DR plan just wishful thinking? Prove your resilience with chaos engineering

At its core, it’s about building confidence in your system’s resilience. The process starts with understanding your system's steady state, which is its normal, measurable, and healthy output. You can't know the true impact of a failure without first defining what "good" looks like. This understanding allows you to form a clear, testable hypothesis: a statement of belief that your system's steady state will persist even when a specific, turbulent condition is introduced. To test this hypothesis, you then execute a controlled action, which is a precise and targeted failure injected into the system. This isn't random mischief; it's a specific simulation of real-world failures, such as consuming all CPU on a host (resource exhaustion), adding network latency (network failure), or terminating a virtual machine (state failure). While this action is running, automated probes act as your scientific instruments, continuously monitoring the system's state to measure the effect. ... Beyond simply proving system availability, chaos engineering builds trust in your reliability metrics, ensuring that you meet your SLOs even when services become unavailable. An SLO is a specific, acceptable target level of your service's performance measured over a specified period that reflects the user's experience. SLOs aren't just internal goals; they are the bedrock of customer trust and the foundation of your contractual service level agreements (SLAs).


The data center of the future: high voltage, liquid cooled, up to 4 MW per rack

Developments such as microfluidic cooling could have a profound impact on how racks and accompanying infrastructure will be built towards the future. Also, it is not all about the type of cooling, but also about the way chips communicate with each other and communicate internally. What will the impact of an all-photonics network be on cooling, for example? The first couple of stages building that type of end-to-end connection have been completed. The interesting parts for the discussion we have here are next on the roadmap for all-photonics networks: using photonics connections between and inside silicon on boards. ... However, there are many moving parts to take into account. It will need a more dynamic approach to selling space in data centers, which is usually based on the amount of watts a customer wants. Irrespective of the actual load, the data center reserves that for the customer. If data centers need to be more dynamic, so do the contracts. ... The data center of the future will be characterized by high-density computing, liquid cooling, sustainable power sources, and a more integrated role in the grid ecosystem. As technology continues to advance, data centers will become more efficient, flexible, and environmentally responsible. That may sound like an oxymoron to many people nowadays, but it’s the only way to get to the densities we need moving forward.


Vietnam integrating biometrics into daily life in digital transformation drive

Vietnam is rapidly integrating biometrics and digital identity into everyday life, rolling out identity‑based systems across public transport, air travel and banking as part of an ambitious national digital transformation drive. New deployments in Hanoi’s metro, airports nationwide and the financial sector show how VNeID and biometric verification increasingly constitute Vietnam’s infrastructure. ... Officials argue the initiative strengthens Hanoi’s ambitions as a smart city and improves interoperability across transport modes. It also introduces a unified digital identity layer for public transit, which no other Vietnamese city can yet boast. Passenger data, operations and transactions are now centralized on a single platform, enabling targeted subsidies based on usage patterns rather than flat‑rate models. The Hanoi Metro app, available on major app stores, supports tap‑and‑go access and discounted fares for verified digital identities. ... The new rules require banks to conduct face‑to‑face identity checks and verify biometric data, such as facial information, before issuing cards to individual customers. The same requirement applies to the legal representatives of corporate clients, with limited exceptions, reports Vietnam Plus. ... Foreigners without electronic identity credentials, as well as Vietnamese nationals with undetermined citizenship status, will undergo in‑person biometric collection using data from the National Population Database. 


Why 2025 broke the manager role — and what it means for leadership ahead

Managers did far more than supervise. “They became mentors, skill-builders, culture carriers and the first line of emotional support,” Tyagi said. They coached diverse teams, supported women and marginalised groups entering new roles, and navigated talent crunches by building internal pipelines. They adopted learning apps, facilitated experience-sharing sessions and absorbed the emotional load of stretched teams. ... Sustaining morale amid continual uncertainty was the most difficult task, Tyagi said. Workloads were redistributed constantly. Managers had to reassure employees while balancing performance expectations with wellbeing. Chopra saw the same tensions. Recognition and feedback remained inconsistent. Gallup research showed a gap between managers’ belief that they offered regular feedback and employees’ experience that they rarely received it. Remote work deepened disconnection. “Creating team cohesion, trust and belonging when people are dispersed remains difficult,” she said. ... Empathy dominated the management skill-set in 2025. Transparency, communication and emotional intelligence were indispensable as uncertainty persisted. Coaching and talent development grew central, especially in organisations investing in women, new hires and marginalised communities. Chopra pointed to several non-negotiables: emotional intelligence, tech literacy, outcome-focused leadership, psychological safety, coaching and ethical awareness in technology use. 


The Missing Link in AI Scaling: Knowledge-First, Not Data-First

Organizations today need to ensure data readiness to avoid failures in model performance, system trust, and strategic alignment. To succeed, CIOs must shift from a “data-first” to a “knowledge-first” approach in order to capitalize on the true benefits of AI. ... Domain-specific reasoning capabilities provide context and meaning to data, which is crucial for professional and reliable advice. A semantic layer across silos creates unified views of all data, enabling comprehensive insights that are otherwise impossible to achieve. Another benefit is its ability to support AI governance and explainability by ensuring that AI systems are not “black boxes,” but are transparent and trustworthy. Lastly, it acts as an agentic AI backbone by orchestrating a workforce of AI agents that can execute complex tasks with reliability and context. ... Shifting to a knowledge-first architecture is not just an option, but a necessity, and is a direct challenge to the conventional data-first mindset. For decades, enterprises have focused on accumulating vast lakes of data, believing that more data inherently leads to better insights. However, this approach created fragmented, context-poor data silos. This “digital quicksand” is the root of the “Semantic Challenge” because data is siloed and heterogeneous. ... A knowledge-first approach fundamentally changes the goal from simply storing data to building an interconnected, enterprise-wide, knowledge graph. This architecture is built on the principle of “things, not strings”.