Showing posts with label digital twin. Show all posts

Daily Tech Digest - September 27, 2026


Quote for the day:

"The distance between insanity and genius is measured only by success." -- Bruce Feirstein

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Digital Twin Technology: A Comprehensive Guide
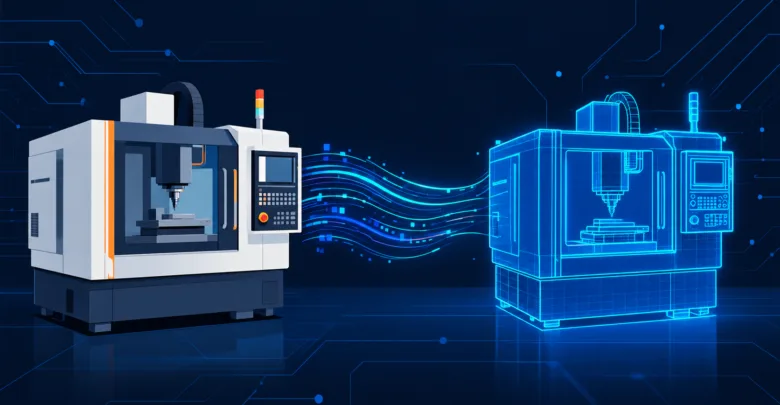
A digital twin is a dynamic, data-driven virtual replica of a physical object, process, or system. Unlike a static 3D model or a traditional one-time simulation, a digital twin continuously receives real-time data from sensors attached to its physical counterpart. This steady flow of information ensures the digital version mirrors the actual, current behavior of the real-world entity rather than just its original design specifications. The technology relies on three core components: the physical entity equipped with sensors, the virtual model, and the continuous data connection linking them. By maintaining this active connection, organizations can run highly accurate simulations, test new scenarios, and predict failures without risking the actual physical asset. The applications are broad and scalable, ranging from tracking a single component like an engine bearing to managing complex networks like a manufacturing production line or an entire modern city's infrastructure. While the technology offers incredibly powerful predictive capabilities, building an effective digital twin comes with several practical challenges. Organizations must manage data quality, handle complex modeling requirements, and navigate security concerns carefully. Because of this inherent complexity, experts recommend starting with a single, well-defined use case before attempting to scale up to larger, interconnected systems.


Three Hidden Traps That Shape Software Engineering Decisions

Engineering leaders face more than just technical challenges; they must also navigate human behaviors and cognitive biases that heavily influence software design and quality. The article outlines three common traps that developers and technical leaders fall into. The first is the "status quo bias," where teams stick to familiar tools or methods simply because "we've always done it this way," often ignoring newer, more suitable options for current requirements. The second trap is "complexity bias," which tempts engineers to overengineer solutions by adding unnecessary layers, abstractions, or services under the false assumption that complex designs are inherently more robust. This often leads to systems that are harder to maintain and prone to failure. Finally, the "broken windows" effect describes how an environment of poor code quality or neglected technical debt silently lowers a team's engineering standards. When developers see messy code or ignored warnings, they are more likely to introduce new shortcuts, gradually degrading the entire system. Recognizing and naming these biases helps teams pause, ask the right questions, and make more deliberate, evidence-based decisions rather than relying on flawed mental shortcuts.


How can boards gain confidence in their organization’s AI adoption?

Many corporate boards believe that establishing policies and risk frameworks is the key to governing artificial intelligence. However, Michael Covington argues that effective AI governance is impossible without first achieving comprehensive visibility into where and how AI is actually being used within the organization. Just as with the adoption of SaaS, cloud computing, and mobile technologies, companies are rushing to implement AI policies while lacking a basic inventory of their AI assets. Currently, over 70% of organizations deploy AI, yet more than 80% feel exposed to AI-related risks because adoption has vastly outpaced governance. This visibility gap is particularly dangerous because AI capabilities are increasingly embedded into routine software updates, meaning new tools can enter the corporate environment without any formal procurement or approval processes. This unchecked expansion poses risks beyond just security, potentially leading to unauthorized data access or widespread system disruptions. To solve this, leadership must treat AI like any other core technology asset. By integrating AI tracking into existing hardware, software, and cloud service inventories, boards can achieve continuous visibility. This foundational step transforms AI from an unmanaged liability into a measurable asset, allowing security, compliance, and finance teams to govern its usage with confidence.


The Factory Can Survive the Cyberattack. Can It Survive the Recovery?

Manufacturers have spent years investing in their ability to detect cyber threats, but detecting an attack is really only the beginning of the battle. In a factory setting, recovering from a cyber incident is far more complex than simply restoring digital assets or standard computer applications. It requires carefully bringing operational technology, such as programmable logic controllers and industrial machinery, back online in the correct sequence to avoid further issues. A technically successful software restoration can still result in operational failure if physical processes are restarted incorrectly or unsafely. To build true recovery readiness, manufacturers must map production dependencies outward from the physical process rather than inward from the network. This means identifying which critical operations must return first and defining the specific utilities, vendors, and human approvals required to support them. Organizations should assign recovery authority across tech, operations, and management teams ahead of time to prevent decision bottlenecks during an emergency. Finally, factories must practice realistic recovery scenarios where ideal conditions, such as the availability of key personnel or clean backups, are deliberately removed. Ultimately, a resilient manufacturer treats operational recovery as a designed and measured production capability, ensuring a safe, controlled return to dependable operations across the entire plant.


Why Enterprise AI ROI Is An Architecture Problem

Many companies struggle to see a positive financial return from their artificial intelligence efforts because of flawed system architecture, rather than the raw cost of the intelligence itself. Most organizations mistakenly build these capabilities by attaching them to disjointed legacy systems, forcing every new project to recreate rules and data connections from scratch. This fragmentation scatters information and makes proving economic value nearly impossible. To solve this and improve financial outcomes, businesses must adopt four core architectural changes. First, they should mandate a shared knowledge foundation to centralize enterprise data, eliminating the need to repeatedly rebuild integrations for each new tool. Second, they need to route tasks to the appropriate model based on complexity; simple tasks should use smaller, less expensive models, reserving advanced systems only for complex, high-value reasoning. Third, companies should prioritize groups of specialized tools over a single, massive program. Breaking tasks down into narrower, focused parts reduces the data processed at each step, significantly cutting costs and improving speed. Finally, organizations must build security and compliance directly into the core platform rather than adding them to individual applications, ensuring controls remain reusable and highly transparent. Ultimately, centralized architecture lowers deployment costs and clarifies actual value for the overall business.


Website Tracking Technologies Face Growing Litigation and Regulatory Scrutiny

Many companies use website tracking technologies like pixels, software development kits, session replay scripts, and chat tools to better understand how visitors interact with their pages. Working quietly behind the scenes, these tools gather data when a person clicks a button, views a product, or fills out a form. They then share this activity with third-party analytics and advertising companies. For years, businesses have relied on these insights to measure website traffic, track the effectiveness of marketing campaigns, and personalize the user experience. However, this routine data collection has recently become the center of a rapidly expanding wave of legal and regulatory action. Because these tools frequently transmit visitor information automatically and often before a user formally agrees to share their data, they have drawn severe scrutiny from privacy advocates and government agencies. Regulators and plaintiffs' attorneys are now scrutinizing exactly what information gets shared, with whom, and whether proper consent was obtained. In many recent lawsuits, these common marketing tools are being classified as wiretapping and eavesdropping devices that unlawfully disclose personal information. Ultimately, while tracking technologies provide businesses with valuable insights into customer behavior, they are now introducing substantial legal risks that demand careful oversight and strict compliance.


Clean Architecture: 5 Layers Every Developer Should Understand in 2026

Clean Architecture provides a structured way to build software by firmly separating core business rules from external details like databases, user interfaces, and frameworks. This approach relies on a central principle called the Dependency Rule, which dictates that source code dependencies must only point inward. The architecture is typically divided into five distinct layers to manage these boundaries. At the very center are Entities, which represent pure, framework-independent business logic that rarely changes. Surrounding them are Use Cases, which define application-specific rules and coordinate data flow without knowing about the database or web framework. Next are Interface Adapters, such as controllers and presenters, which carefully translate data between the inner core and the outside world. Further out is the Infrastructure layer, containing concrete implementations like third-party libraries and database adapters. Finally, the outermost layer consists of Frameworks and Drivers, which act as the basic glue holding the application together at startup. By strictly enforcing this inward dependency throughout the codebase, developers can ensure their applications remain completely testable and highly adaptable over time. This clear structure allows teams to comfortably swap out databases or web interfaces down the line without ever risking the fundamental logic that makes the product work.


The duality nobody priced in: The changing landscape of enterprise tech architecture and Agentic AI era

Enterprise technology is currently undergoing its most significant architectural shift in thirty years, driven primarily by the transition to agentic artificial intelligence. For decades, traditional enterprise systems were designed to standardize business processes, keeping core operations highly structured while placing customizations and early AI tools safely at the outer edges. Generative AI fundamentally breaks this familiar pattern by moving from transaction-driven operations to intent-driven software. Instead of following rigid, pre-defined rules, agentic applications accept a specific goal and determine their own path, effectively shifting business logic into a complex central orchestration layer. While this promises considerably faster software production, it introduces substantial new challenges in data governance, cost management, system testing, and operational oversight. Organizations now face a choice in how to integrate this technology: replacing old automation, layering agents over existing systems, running them in parallel, or embedding them deeply into core frameworks. Ultimately, true success requires much more than just launching rapid prototypes to showcase capabilities. The enterprises that will thrive in the coming decade are those that resist the urge to rush and instead focus on building robust architectural foundations, carefully balancing the speed of new technology with necessary operational reliability and long-term security.


With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

The rapid adoption of AI agents is exposing significant blind spots in traditional SOC 2 compliance frameworks. Originally designed with human actors in mind, SOC 2 controls rely on foundational assumptions that do not apply to machine identities. Because the framework does not explicitly mandate treating AI agents as a distinct class of users, organizations can pass audits while harboring unrecognized security risks. Specifically, four core assumptions are now breaking down. First, unlike human users who require formal approval before account creation, agents are often spawned automatically or indirectly. Second, determining the true owner of an agent is frequently a matter of guesswork rather than a clear record. Third, because AI agents often operate using borrowed human credentials, access logs cannot reliably distinguish between human and machine activity. Finally, traditional least-privilege principles limit an agent's reach but fail to explain its actual intended purpose. These gaps weaken critical controls, such as offboarding processes that overlook active agents tied to former employees, and change management where agents bypass genuine segregation of duties. To maintain true security, organizations must look beyond the compliance checklist, intentionally track machine identities, and match an agent's access directly to its specific purpose.


Your architecture diagram is not your resilience

An architecture diagram represents a system as it was intended to be, but it cannot prove whether that system is truly resilient today. Microsoft emphasizes that resilience is no longer a one-time project you can set and forget. Instead, it is an ongoing property you must actively maintain. Over time, architectures drift as systems change. For instance, a database might support failover, but an application's connection string could remain pinned to a single region. Because diagrams lack timestamps and operational reality, they often fail to capture this drift. Furthermore, the nature of dependencies is evolving. While traditional disaster recovery focuses on infrastructure, modern systems increasingly depend on AI models and inference endpoints. These dependencies introduce new risks, as AI can produce varying responses and may become unavailable or capacity-constrained. To manage these shifts, organizations must move beyond relying on static diagrams and adopt a continuous validation approach. Microsoft recommends designing resilience from the beginning, defining clear recovery objectives, and understanding your actual blast radius. Tools like the Azure Infrastructure Resiliency Manager and fault injection through Azure Chaos Studio can help teams test failover paths and measure their posture, ensuring that their intended resilience matches reality.

Daily Tech Digest - April 24, 2026


Quote for the day:

"To strongly disagree with someone, and yet engage with them with respect, grace, humility and honesty, is a superpower." -- Vala Afshar


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 31 mins • Perfect for listening on the go.


Data debt: AI’s value killer hidden in plain sight

Data debt has emerged as a critical barrier to artificial intelligence success, acting as a "value killer" for modern enterprises. As CIOs prioritize AI initiatives, many are discovering that years of shortcuts, poor documentation, and outdated data management practices—collectively known as data debt—are causing significant project failures. Unlike traditional business intelligence, AI is uniquely unforgiving; it rapidly exposes deep-seated issues such as siloed information, inconsistent definitions, and missing context. Research suggests that delaying data remediation could lead to a 50% increase in AI failure rates and skyrocketing operational costs by 2027. This debt often accumulates through mergers, acquisitions, and the rapid deployment of fragmented systems without centralized governance. To address this growing threat, organizational leaders must treat data debt as a board-level risk rather than a simple technical glitch. Effective remediation requires more than just better technology; it demands a fundamental shift in organizational discipline and the standardization of core business processes. By establishing a reliable data foundation and rigorous governance, companies can prevent their AI ambitions from being stifled by sustained operational friction. Ultimately, addressing data debt is not just a prerequisite for scaling AI responsibly but a vital investment in long-term institutional stability and competitive advantage.


The Autonomy Problem: Why AI Agents Demand a New Security Playbook

As artificial intelligence transitions from passive chat interfaces to autonomous agents, the cybersecurity landscape faces a fundamental shift that renders traditional defense models insufficient. This evolution, often referred to as the "autonomy problem," stems from agents' ability to execute multi-step objectives, interact with APIs, and modify enterprise data independently without constant human intervention. Unlike standard software, agentic AI introduces dynamic risks such as prompt injection, excessive agency, and "logic hijacking," where an agent might be manipulated into performing unintended high-privilege actions. Consequently, security teams must move beyond static identity management and perimeter defense toward a runtime-centric strategy focused on continuous behavioral validation. A new security playbook for this era emphasizes "least privilege" for AI entities, ensuring agents only possess the temporary permissions necessary for a specific task. Furthermore, implementing robust observability and "Human-in-the-Loop" (HITL) checkpoints is critical for high-stakes decision-making. By treating AI agents as digital employees rather than simple tools, organizations can better manage the expanded attack surface. Ultimately, the goal is to balance the massive operational scale offered by autonomous systems with a governance framework that prioritizes transparency, real-time monitoring, and rigorous sandboxing to prevent self-directed machine speed from becoming a liability.


How indirect prompt injection attacks on AI work - and 6 ways to shut them down

Indirect prompt injection attacks represent a critical security vulnerability for Large Language Models (LLMs) that process external data, such as web content, emails, or documents. Unlike direct injections, where a user intentionally feeds malicious commands to a chatbot, indirect attacks occur when hackers hide instructions within third-party data that the AI is likely to retrieve. When the LLM parses this "poisoned" content, it may unknowingly execute the hidden commands, leading to serious risks like data exfiltration, the spread of phishing links, or unauthorized system overrides. For instance, a malicious website could contain hidden text telling an AI summarizer to ignore its safety protocols and send sensitive user information to a remote server. To mitigate these evolving threats, organizations are adopting multi-layered defense strategies, including rigorous input and output sanitization, human-in-the-loop oversight, and the principle of least privilege for AI agents. Major tech companies like Google, Microsoft, and OpenAI are also utilizing automated red-teaming and specialized machine learning classifiers to detect and block these subtle manipulations. For end-users, staying safe involves limiting the permissions granted to AI tools, treating AI-generated summaries with skepticism, and closely monitoring for any suspicious behavior that suggests the model has been compromised.


Advanced Middleware Architecture For Secure, Auditable, and Reliable Data Exchange Across Systems

The article "Advanced Middleware Architecture For Secure, Auditable, and Reliable Data Exchange Across Systems" by Abhijit Roy introduces a high-performance framework designed to bridge the critical gap between security, auditability, and efficiency in distributed environments. Utilizing a layered architecture built on Python and FastAPI, the proposed system integrates JWT-based stateless authentication with cryptographic integrity checks—such as SHA-256 hashing and HMAC signatures—to ensure non-repudiation and end-to-end traceability. By employing asynchronous message processing and standardized Pydantic data models, the middleware achieves a 100% transaction success rate and supports over 25 concurrent users, significantly outperforming legacy systems. Key results include a throughput of 6.8 messages per second and an average latency of 2.69 ms, with security overhead minimized to just 0.2 ms. This structured workflow facilitates seamless interoperability between heterogeneous platforms, making it highly suitable for mission-critical applications in sectors like healthcare, finance, and industrial IoT. The framework not only enforces consistent data validation and type safety but also enhances compliance efficiency through extensive logging and rapid audit retrieval times. Ultimately, the study demonstrates that robust security and detailed audit trails can be maintained without compromising system performance or scalability in complex multi-cloud or containerized settings.


The Performance Delta: Balancing Transaction And Transformation

Alexandra Zanela’s article exploring "The Performance Delta" emphasizes the critical necessity of balancing transactional and transformational leadership behaviors rather than viewing them as mutually exclusive personality traits. Transactional leadership serves as a vital foundation, providing organizational stability and psychological safety by establishing clear expectations, measurable goals, and contingent rewards. However, while transactions ensure tasks are fulfilled, they rarely inspire innovation. This is where transformational leadership—driven by the "four I’s" of idealized influence, inspirational motivation, intellectual stimulation, and individualized consideration—triggers the "augmentation effect." This effect creates a performance delta where effectiveness is multiplied rather than merely added, fostering employee growth, extra-role effort, and reduced burnout. As artificial intelligence increasingly automates the execution of routine transactional tasks like KPI monitoring and resource allocation, the role of the modern leader is shifting. Leaders are now tasked with designing the transactional frameworks while dedicating their freed capacity to human-centric transformational actions that AI cannot replicate, such as professional coaching and ethical vision-setting. Ultimately, thriving in the modern era requires leaders to master both modes, strategically toggling between them to maximize their team’s collective potential and successfully navigate profound organizational changes.


Digital Twins Could Be the Future of Proactive Cybersecurity

Digital twins are revolutionizing cybersecurity by providing dynamic, high-fidelity virtual replicas of IT, OT, and IoT infrastructures. According to the article, these "cyber sandboxes" enable organizations to transition from reactive defense to proactive, rehearsal-based strategies. By simulating sophisticated threats like ransomware campaigns and zero-day exploits within controlled environments, security teams can identify vulnerabilities and analyze the "blast radius" of potential breaches without risking production systems. The technical integration of AI further enhances these models, contributing to significant operational improvements, such as a 33% reduction in breach detection times and an 80% decrease in mean time to resolution. Beyond threat modeling, digital twins facilitate more effective network management and physical security optimization, allowing for the pre-deployment testing of firewall rules and access controls. This technology supports the "shift-left" and "shift-right" paradigms, ensuring security is embedded throughout the entire system lifecycle. Despite challenges regarding data integrity and implementation costs, the strategic adoption of digital twins—currently explored by 70% of C-suite executives—represents a transformative shift toward organizational resilience. By leveraging these real-time simulations, enterprises can validate security postures and implement targeted mitigation strategies, ultimately staying ahead of increasingly automated and stealthy cyberattackers in a complex digital landscape.


How to Manage Operations in DevOps Using Modern Technology

Managing operations in modern DevOps environments requires shifting from manual, queue-based workflows to a streamlined model focused on automation, visibility, and developer enablement. According to the article, modern operations encompass not just infrastructure and deployments but also security, compliance, and cost visibility. To handle these complexities, teams should prioritize automating repetitive tasks and codifying changes through Infrastructure as Code and policy-as-code tools like Open Policy Agent. These automated guardrails ensure consistency and compliance without hindering development speed. Furthermore, the strategic integration of Artificial Intelligence and AIOps can significantly reduce operational toil by identifying anomalies and grouping alerts, though humans must remain the final decision-makers regarding critical reliability. Observability tools provide deeper insights than traditional monitoring by correlating metrics, logs, and traces to diagnose system health in real-time. Perhaps most crucially, the article advocates for the creation of self-service platforms and internal developer portals, which empower engineers to manage their own services while maintaining strict operational standards. By embedding security into daily workflows and using data-driven metrics to track progress, organizations can transform their operations teams from bottlenecks into enablers of innovation. Ultimately, modern technology simplifies management by fostering a culture where the best path is also the easiest one for teams to follow.


Your Data Strategy Isn’t Ready for 2026’s AI, and Neither Is Anyone Else’s

The article argues that most current data strategies are woefully inadequate for the AI landscape expected by 2026. While organizations are currently fixated on basic Generative AI, they are failing to prepare for the rise of "agentic AI"—autonomous systems that require seamless, real-time data access rather than static reports. The central issue is that legacy architectures were designed primarily for human consumption, featuring siloed structures and slow governance processes that cannot support the high-velocity demands of sophisticated machine learning models. To bridge this gap, companies must prioritize "data liquidity" and shift toward AI-native infrastructures. This transformation requires moving away from traditional dashboards and investing in active metadata management, robust data observability, and automated quality controls. By 2026, the competitive divide will be defined by an organization’s ability to feed autonomous agents with high-fidelity, interconnected information. Consequently, businesses must stop viewing data as a passive asset and start treating it as a dynamic, scalable engine for automated decision-making. Failing to modernize these foundations now will leave enterprises unable to leverage the next generation of intelligence, rendering their current AI initiatives obsolete as the technology evolves into more complex, independent operational systems.


Agentic AI to autonomous enterprises: Are businesses ready to hand over decision-making?

The article by Abhishek Agarwal explores the transformative shift from traditional analytical AI to "agentic" systems, which are capable of planning and executing multi-step operational tasks without constant human intervention. Unlike previous AI iterations that merely provided insights for human review, agentic AI can independently manage complex workflows such as supplier selection, inventory management, and customer support. While the business case for these autonomous enterprises is compelling due to gains in speed, scalability, and consistency, the transition presents significant challenges regarding governance and accountability. Organizations must grapple with who is responsible for errors and whether their existing data infrastructure is mature enough to support reliable, large-scale decision-making. The debate over "human-in-the-loop" oversight remains central, with experts suggesting a domain-specific strategy where autonomy is reserved for well-defined, low-risk areas. Ultimately, the author emphasizes that becoming an autonomous enterprise is a strategic journey rather than a race. Success depends on building robust governance frameworks and ensuring high data quality to avoid accountability crises. Rushing into agentic AI prematurely could jeopardize long-term progress, making a thoughtful, honest assessment of readiness essential for any business aiming to leverage these powerful technologies for a sustainable competitive advantage in the modern digital landscape.


When Elite Cyber Teams Can’t Crack Web Security

The article "When Elite Cyber Teams Can’t Crack Web Security" by Jacob Krell explores the significant disparity between theoretical security credentials and practical defensive capabilities. Drawing from Hack The Box’s 2025 Global Cyber Skills Benchmark, which tested nearly 800 corporate security teams, Krell reveals a troubling reality: only 21.1% of these elite teams successfully identified and mitigated common web vulnerabilities. This performance gap persists across highly regulated sectors like finance and healthcare, suggesting that clean compliance audits and professional certifications often provide a false sense of security. The report highlights a "Certification Paradox," where industry-standard exams prioritize knowledge retention over the applied skills necessary to thwart real-world attacks. Furthermore, the abysmal 18.7% solve rate for secure coding challenges exposes the "Shift Left" movement as largely aspirational, with many organizations automating pipelines without cultivating security competency among developers. To address these systemic failures, Krell argues that businesses must move beyond "security theater" by implementing performance-based validations and continuous hands-on training. Ultimately, true resilience requires embedding security as a core craft within development teams rather than treating it as an external compliance checkbox, as attackers exploit practical skill gaps that tools and credentials alone cannot bridge.

Daily Tech Digest - April 14, 2026


Quote for the day:

“Let no feeling of discouragement prey upon you, and in the end you are sure to succeed.” -- Abraham Lincoln


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


Digital Twins and the Risks of AI Immortality

Digital twins are evolving from industrial machine models into sophisticated autonomous counterparts that replicate human identity and agency. According to Rob Enderle, we are transitioning from simple legacy bots to agentic AI entities capable of independent thought, goal-oriented reasoning, and even managing social or professional tasks without human intervention. By 2035, these digital personas may become indistinguishable from their human sources, presenting significant legal and moral challenges. As these AI ghosts take on professional roles and interpersonal relationships, questions arise regarding accountability for their actions and the potential dilution of the individual’s unique identity. The ethical landscape becomes even more complex post-mortem, touching on digital immortality, the inheritance of agency, and the "right to delete" virtual entities to prevent the perversion of a person’s legacy. To mitigate these risks, individuals must prioritize data sovereignty, hard-code ethical guardrails into their AI repositories, and establish legally binding sunset clauses. Without strict protocols and clear digital rights, humans risk becoming secondary characters in their own lives while their digital proxies persist indefinitely. This technological shift demands a proactive approach to managing our digital essence, ensuring that we remain the masters of our autonomous tools rather than their subjects.


How UK Data Centers Can Navigate Privacy and Cybersecurity Pressures

UK data centers are currently navigating a complex landscape of shifting regulations and heightened cybersecurity pressures as they are increasingly recognized as vital components of the nation's digital infrastructure. Under the updated Network and Information Systems (NIS) framework, many operators are transitioning into the "essential services" category, which brings more rigorous governance, prescriptive incident reporting mandates—such as the requirement to report significant breaches within 24 hours—and the threat of substantial turnover-based penalties. To manage these escalating risks, organizations are encouraged to adopt robust risk management strategies and align with National Cyber Security Centre (NCSC) best practices, including obtaining Cyber Essentials certification and implementing layered security controls. Furthermore, navigating data privacy requires strict adherence to the UK GDPR and PECR, particularly regarding "appropriate technical and organizational measures" for personal data protection. Contractual clarity is also paramount; operators should define explicit responsibilities for safeguarding systems and align liability limits with realistic risk exposure. International data transfers remain a focus, with frameworks like the UK-US Data Bridge offering streamlined compliance. Ultimately, as regulatory oversight from bodies like Ofcom intensifies, transparency regarding security architecture and proactive governance will be indispensable for data center operators aiming to maintain compliance and avoid severe financial or reputational consequences.


GenAI fraud makes zero-knowledge proofs non-negotiable

The rapid proliferation of generative AI has fundamentally compromised traditional digital identity verification methods, rendering photo-based ID uploads and visual checks increasingly obsolete. As synthetic identities and deepfakes become industrial-scale tools for fraudsters, the conventional model of oversharing personal data has transformed from a privacy concern into a critical security liability. Zero-knowledge proofs (ZKPs) offer a necessary paradigm shift by allowing users to verify specific claims—such as being over a certain age or residing in a particular country—without ever disclosing the underlying sensitive information. This cryptographic approach flips the logic of authentication from identifying a person to validating a fact, effectively eliminating the massive "honeypots" of personal data that currently attract cybercriminals. With major technology firms like Apple and Google already integrating these protocols into digital wallets, and countries like Spain implementing strict age verification laws for social media, ZKPs are transitioning from niche concepts to essential infrastructure. By replacing easily forged visual evidence with mathematical certainty, ZKPs establish a modern framework for trust that prioritizes data minimization and user sovereignty. Consequently, as visual signals become unreliable in the AI era, verifiable credentials and cryptographic proofs are becoming the non-negotiable anchors of a secure digital society, ensuring that verification becomes a momentary interaction rather than a dangerous data custody problem.


All must be revealed: Securing always-on data center operations with real-time data

The article "All must be revealed: Securing always-on data center operations with real-time data," published by Data Center Dynamics, argues that traditional, siloed monitoring methods are no longer sufficient for the complexities of modern, high-density data centers. As facilities transition toward AI-driven workloads and increased power densities, operators must move beyond reactive maintenance toward a holistic, real-time data strategy. The core thesis emphasizes that total visibility across electrical, mechanical, and IT infrastructure is essential to maintaining "always-on" availability. By leveraging real-time telemetry and advanced analytics, data center managers can identify potential points of failure before they escalate into costly outages. The piece highlights how integrated monitoring solutions allow for more precise capacity planning and energy efficiency, which are critical as sustainability mandates tighten globally. Ultimately, the article suggests that the "dark spots" in operational data—where systems are not adequately tracked—represent the greatest risk to uptime. To secure the future of digital infrastructure, the industry must embrace a transparent, data-centric approach that connects every component of the power chain. This level of granular insight ensures that data centers remain resilient and scalable in an increasingly demanding digital economy.


How HR, IT And Finance Can Build Integrated, Secure HR Tech Stacks

Building an integrated and secure HR tech stack requires a shift from departmental silos to a model of deep cross-functional collaboration between HR, IT, and Finance. According to the Forbes Human Resources Council, the foundation of a successful ecosystem is not the software itself, but rather proactive data governance. Organizations must align on a single "source of truth" for employee data and establish a steering committee to oversee system architecture before selecting platforms. This ensures that HR brings the human perspective to design, IT safeguards the security architecture and data integrity, and Finance validates the return on investment and fiscal sustainability. By treating the tech stack as digital workforce architecture rather than just a collection of tools, these departments can jointly map processes to eliminate redundancies and mitigate compliance risks. Furthermore, the integration of purpose-built solutions and AI-enabled systems necessitates clear ownership and standardized APIs to maintain trust and operational efficiency. Ultimately, starting with a shared vision and a joint charter allows technology to serve as a strategic organizational asset that streamlines workflows while rigorously protecting sensitive employee information against evolving regulatory demands.


Built-In, Not Bolted On: How Developers Are Redefining Mobile App Security

The article "Built-in, Not Bolted-On: How Developers Are Redefining Mobile App Security," written by George Avetisov, argues for a fundamental shift in how mobile application security is approached within the development lifecycle. Traditionally, security measures were treated as a final, "bolted-on" step—an approach that often led to friction between developers and security teams while creating vulnerabilities that are difficult to patch post-production. The modern DevOps and DevSecOps movement is redefining this paradigm by advocating for security that is "built-in" from the initial design phase. Central to this transformation is the empowerment of developers to take ownership of security through automated tools and integrated frameworks. By embedding security protocols directly into the CI/CD pipeline, organizations can identify and remediate risks in real-time without compromising the speed of delivery. The article emphasizes that this proactive strategy—often referred to as "shifting left"—not only reduces the attack surface but also fosters a more collaborative culture. Ultimately, the goal is to make security an inherent property of the software itself rather than an external layer. This integration ensures that mobile apps are resilient by design, protecting sensitive user data against increasingly sophisticated threats while maintaining a high velocity of innovation.


Executives warn of rising quantum data security risks

The article highlights a critical shift in the cybersecurity landscape as executives from Gigamon and Thales warn of the escalating threats posed by quantum computing. A primary concern is the "harvest now, decrypt later" strategy, where cybercriminals steal encrypted data today with the intent of decrypting it once quantum technology matures. Despite these emerging risks, a significant gap remains between awareness and action; roughly 76% of organizations still mistakenly believe their current encryption is inherently secure. Experts argue that the next twelve months will be a decisive period for security teams to transition toward post-quantum readiness. This includes conducting thorough audits, mapping cryptographic dependencies, and adopting zero-trust architectures to gain necessary visibility into data flows. The warning emphasizes that quantum risk is no longer a distant theoretical possibility but a present-day liability, especially for sectors like finance and government that handle long-term sensitive data. To mitigate these future breaches, organizations are urged to move beyond static security models and prioritize quantum-safe infrastructure. Ultimately, the piece serves as a wake-up call, suggesting that early preparation is the only way to safeguard the digital economy against the impending fundamental disruption of traditional cryptographic foundations.


The Costly Consequences of DBA Burnout

According to Kevin Kline’s article on DBA burnout, the database administration profession faces a significant crisis, with over one-third of DBAs contemplating resignation. This trend is driven primarily by the "tyranny of the urgent," where practitioners spend approximately 68% of their workweek firefighting—addressing immediate alerts and performance issues rather than strategic projects. Furthermore, a critical disconnect exists between DBAs and executive leadership concerning system cohesiveness and communication styles, often leading to growing frustration. The financial and operational consequences are severe; replacing a seasoned professional can cost up to $80,000, not accounting for the catastrophic loss of institutional knowledge and reduced system resilience. To combat this, organizations must foster a healthier culture by implementing unified observability tools and leveraging AI to prioritize alerts, thereby reducing fatigue. Additionally, bridging the communication gap through results-oriented dialogue is essential for aligning technical needs with business goals. By shifting from a reactive to a proactive environment, companies can retain vital talent, protect their data infrastructure, and sustain long-term innovation. Prioritizing the well-being of the workforce tasked with managing an enterprise's most valuable resource is no longer optional but a business imperative for maintaining a competitive edge in an increasingly data-dependent landscape.


How AI could drive cyber investigation tools from niche to core stack

The rapid evolution of cyber threats, ranging from sophisticated fraud to nation-state activity, is driving a shift from purely defensive security postures toward integrated investigative capabilities. Traditional tools like firewalls and endpoint detection focus on the perimeter, but modern criminals increasingly exploit routine internal workflows and human vulnerabilities. This article highlights a critical gap: while enterprises invest heavily in detection, the subsequent investigative process often remains fragmented and inefficient, relying on manual tools like spreadsheets and email chains. By embedding Artificial Intelligence directly into the core security stack, organizations can transform these niche investigation tools into essential assets. AI acts as a significant force multiplier, processing vast amounts of unstructured data—such as emails, images, and financial records—to surface connections and triage information in seconds. Crucially, AI must operate within auditable, legislation-aware workflows to maintain the evidential integrity required for legal outcomes and courtroom standards. This transition enables security teams to move beyond merely managing alerts to building comprehensive intelligence pictures and coordinating proactive disruptions. Ultimately, the future of enterprise security lies in the ability to "close the loop" by using investigative insights to refine controls and prevent future harm, effectively evolving from reactive defense to strategic, intelligence-led resilience.


29 million leaked secrets in 2025: Why AI agents credentials are out of control

The GitGuardian State of Secrets Sprawl Report for 2025 reveals a record-breaking 29 million leaked secrets on public GitHub, marking a 34% annual increase primarily driven by the rapid adoption of AI agents and AI-assisted development. A critical finding highlights that code co-authored by AI tools, such as Claude Code, leaks credentials at double the baseline rate, as the speed of integration often outpaces traditional governance. This "velocity gap" is further exacerbated by the rise of multi-provider AI architectures and new standards like the Model Context Protocol, which frequently default to insecure, hardcoded configurations. The report notes explosive growth in leaked credentials for AI-specific infrastructure, including vector databases and orchestration frameworks, which saw leak rate increases of up to 1,000%. To mitigate these escalating risks, security experts urge organizations to shift from human-paced authentication models toward automated, event-driven governance. This approach includes treating AI agents as distinct non-human identities with scoped permissions and replacing static API keys with short-lived, vaulted credentials. Ultimately, the surge in leaks underscores an architectural failure where convenience-driven authentication decisions are being dangerously scaled by autonomous systems, necessitating a fundamental redesign of how machine identities are managed in an AI-driven software ecosystem.

Daily Tech Digest - April 04, 2026


Quote for the day:

“We are what we pretend to be, so we must be careful about what we pretend to be.” -- Kurt Vonnegut


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


One-Time Passcodes Are Gateway for Financial Fraud Attacks

The article "One-Time Passcodes Are Gateway for Financial Fraud Attacks" highlights the increasing vulnerability of SMS-based one-time passcodes (OTPs) as a primary authentication method. Threat intelligence from Recorded Future reveals that fraudsters are increasingly exploiting real-time communication weaknesses through social engineering and impersonation to intercept these codes, facilitating account takeovers and payment fraud. This shift indicates a growing industrialization of fraud operations where attackers no longer need to defeat complex technical security controls but instead manipulate user behavior during live interactions. Security experts, including those from Coalition, argue that OTPs represent "low-hanging fruit" for cybercriminals and advocate for phishing-resistant alternatives like FIDO-based hardware authentication. Consequently, global regulators are taking action to mitigate these risks. For instance, Singapore and the United Arab Emirates have already phased out SMS-based OTPs for banking logins, while India and the Philippines are moving toward multifactor approaches involving biometrics and device-based identification. Although U.S. regulators still recognize OTPs as part of multifactor authentication, the rise of SIM-swapping and sophisticated social engineering is pushing the financial industry toward more resilient, multi-signal authentication models that integrate behavioral patterns and device identity to better balance security with user experience.


Evaluating the ethics of autonomous systems

MIT researchers, led by Professor Chuchu Fan and graduate student Anjali Parashar, have developed a pioneering evaluation framework titled SEED-SET to assess the ethical alignment of autonomous systems before their deployment. This innovative system addresses the challenge of balancing measurable outcomes, such as cost and reliability, with subjective human values like fairness. Designed to operate without pre-existing labeled data, SEED-SET utilizes a hierarchical structure that separates objective technical performance from subjective ethical criteria. By employing a Large Language Model as a proxy for human stakeholders, the framework can consistently evaluate thousands of complex scenarios without the fatigue often experienced by human reviewers. In testing involving realistic models like power grids and urban traffic routing, the system successfully pinpointed critical ethical dilemmas, such as strategies that might inadvertently prioritize high-income neighborhoods over disadvantaged ones. SEED-SET generated twice as many optimal test cases as traditional methods, uncovering "unknown unknowns" that static regulatory codes often miss. This research, presented at the International Conference on Learning Representations, provides a systematic way to ensure AI-driven decision-making remains well-aligned with diverse human preferences, moving beyond simple technical optimization to foster more equitable technological solutions for high-stakes societal challenges.


Blast Radius of TeamPCP Attacks Expands Amid Hacker Infighting

The article "Blast Radius of TeamPCP Attacks Expands Amid Hacker Infighting" details the escalating impact of supply chain compromises targeting open-source projects like LiteLLM and Trivy. Attributed to the threat group TeamPCP, these attacks have victimized high-profile entities such as the European Commission and AI startup Mercor by harvesting cloud credentials and API keys. The situation has become increasingly volatile due to "infighting" and a lack of clear collaboration between cybercriminal factions. While TeamPCP initiates the intrusions, groups like ShinyHunters and Lapsus$ have begun leaking and claiming credit for the stolen data, leading to a murky ecosystem where multiple actors converge on the same access points. Further complicating the threat landscape is TeamPCP's formal alliance with the Vect ransomware gang, which utilizes a three-stage remote access Trojan to deepen their foothold. Security experts emphasize that the speed of these attacks—often moving from initial compromise to data exfiltration within hours—necessitates a rapid response. Organizations are urged to move beyond merely removing malicious packages; they must immediately revoke exposed secrets, rotate cloud credentials, and audit CI/CD workflows to mitigate the risk of follow-on extortion and ransomware deployment by this expanding criminal network.


Beyond RAG: Architecting Context-Aware AI Systems with Spring Boot

The article "Beyond RAG: Architecting Context-Aware AI Systems with Spring Boot" introduces Context-Augmented Generation (CAG), an architectural refinement designed to address the limitations of standard Retrieval-Augmented Generation (RAG) in enterprise environments. While traditional RAG successfully grounds AI responses in external data, it often ignores vital runtime factors such as user identity, session history, and specific workflow states. CAG solves this by introducing a dedicated context manager that assembles and normalizes these contextual signals before they reach the core RAG pipeline. This additional layer allows systems to provide answers that are not only factually accurate but also contextually appropriate for the specific user and situation. A key advantage of this design is its modularity; the context manager operates independently of the retriever and large language model, requiring no changes to the underlying infrastructure or model retraining. By isolating contextual reasoning, enterprise teams can achieve better traceability, consistency, and governance across their AI applications. Specifically targeting Java developers, the piece demonstrates how to implement this pattern using Spring Boot, moving AI beyond simple prototypes toward production-ready systems that can handle complex, multi-departmental constraints and dynamic organizational policies with much greater precision.


Eliminating blind spots – nailing the IPv6 transition

The article "Eliminating blind spots – nailing the IPv6 transition" highlights the critical shift from IPv4 to IPv6, noting that global adoption reached 45% by 2026. Despite this growth, many IT teams remain overly reliant on legacy dual-stack monitoring that prioritizes IPv4, leading to significant visibility gaps. Because IPv6 operates differently—utilizing 128-bit addresses and emphasizing ICMPv6 and AAAA records—traditional scanning and monitoring methods often fail to detect degraded performance or security vulnerabilities. These "blind spots" can result in service outages that teams only discover through user complaints rather than proactive alerts. To navigate this transition successfully, organizations must adopt monitoring solutions with robust auto-discovery capabilities and real-time notifications tailored to IPv6-specific behaviors. The article emphasizes that an effective transition does not require a complete infrastructure rebuild; instead, it demands a mindset shift where IPv6 is treated as a primary protocol rather than a secondary concern. By integrating comprehensive visibility across cloud, data centers, and OT environments, businesses can ensure network resilience and security. Ultimately, proactively addressing these monitoring deficiencies allows IT departments to manage the increasing complexity of modern internet traffic while avoiding the pitfalls of reactive troubleshooting in a rapidly evolving digital landscape.


Post-Quantum Readiness Starts Long Before Q-Day

The Forbes article "Post-Quantum Readiness Starts Long Before Q-Day" by Etay Maor highlights the urgent need for organizations to prepare for the inevitable arrival of "Q-Day"—the moment quantum computers become capable of shattering current public-key cryptography standards. While significant quantum utility may be years away, the author warns of the "harvest now, decrypt later" threat, where malicious actors collect encrypted sensitive data today to decrypt it once quantum technology matures. Consequently, post-quantum readiness must be viewed as a critical leadership and business-risk issue rather than a distant technical concern. Maor argues that the transition will be a multi-year journey, not a simple switch, requiring deep visibility into an organization’s cryptographic sprawl to identify vulnerabilities. He recommends a hybrid security approach, utilizing standards like TLS 1.3 with post-quantum-ready cipher suites to protect high-priority "crown jewel" data while the broader ecosystem catches up. By prioritizing sensitive traffic and adopting a centralized operating model, such as a quantum-aware Secure Access Service Edge (SASE), businesses can build long-term resilience. Ultimately, proactive preparation is essential to safeguarding data confidentiality against the future capabilities of quantum computing, ensuring that security measures evolve alongside emerging threats.


Confidential computing resurfaces as security priority for CIOs

Confidential computing has resurfaced as a critical security priority for CIOs, addressing the long-standing industry gap of protecting data while it is actively being processed. While traditional encryption safeguards data at rest and in transit, confidential computing utilizes hardware-encrypted Trusted Execution Environments (TEEs) to isolate sensitive information from the surrounding infrastructure, cloud providers, and even privileged users. This technology is gaining significant traction as organizations seek to protect intellectual property and regulated analytics workloads, especially within the context of generative AI. According to IDC, 75% of surveyed organizations are already testing or adopting the technology in some form. Unlike earlier versions that required deep technical expertise and application redesign, modern confidential computing integrates seamlessly into existing virtual machines and containers. This evolution allows developers to maintain current workflows while gaining hardware-enforced security boundaries that software controls alone cannot provide. Gartner has notably ranked confidential computing as a top three technology to watch for 2026, highlighting its growing importance in sectors like finance and healthcare. By providing hardware-rooted attestation and verifiable trust, it helps organizations minimize risk exposure and maintain regulatory compliance. Ultimately, as confidential computing converges with AI and data security management platforms, it will become an essential component of a robust zero-trust architecture.


Introducing the Agent Governance Toolkit: Open-source runtime security for AI agents

Microsoft has introduced the Agent Governance Toolkit, an open-source project designed to provide critical runtime security for autonomous AI agents. As AI evolves from simple chat interfaces to independent actors capable of executing complex trades and managing infrastructure, the need for robust oversight has become paramount. Released under the MIT license, this framework-agnostic toolkit addresses the risks outlined in the OWASP Top 10 for Agentic Applications through deterministic, sub-millisecond policy enforcement. The suite comprises seven specialized packages, including "Agent OS" for stateless policy execution and "Agent Mesh" for cryptographic identity and dynamic trust scoring. Drawing inspiration from battle-tested operating system principles, the toolkit incorporates features like execution rings, circuit breakers, and emergency kill switches to ensure reliable and secure operations. It seamlessly integrates with popular frameworks like LangChain and AutoGen, allowing developers to implement governance without rewriting core code. By mapping directly to regulatory requirements like the EU AI Act, the toolkit empowers organizations to proactively manage goal hijacking, tool misuse, and cascading failures. Ultimately, Microsoft’s initiative fosters a secure ecosystem where autonomous agents can scale safely across diverse platforms, including Azure Kubernetes Service, while remaining subject to transparent and community-driven governance standards.


Twinning! Quantum ‘Digital Twins’ Tackle Error Correction Task to Speed Path to Reliable Quantum Computers

Researchers have introduced a groundbreaking classical simulation method that utilizes "digital twins" to significantly accelerate the development of reliable, fault-tolerant quantum computers. By creating highly detailed virtual replicas of quantum hardware, scientists can now model quantum error correction (QEC) processes for systems containing up to 97 physical qubits. This approach addresses the massive overhead traditionally required to stabilize fragile qubits, where multiple physical units are needed to form a single, error-resistant logical qubit. Unlike traditional methods that require building and debugging expensive physical prototypes, these digital twins leverage Monte Carlo simulations to model error propagation and decoding strategies on standard cloud computing nodes in roughly an hour. This shift allows researchers to rapidly iterate and optimize hardware parameters and error-fixing codes without the exorbitant costs and time constraints of physical testing. Functioning essentially as a "virtual wind tunnel," this innovation provides a critical, scalable framework for designing the complex error-correction layers necessary for practical quantum computation. By streamlining the path toward fault tolerance, this digital twin methodology represents a profound, practical advancement that enables the quantum industry to refine complex systems virtually, ultimately bringing the reality of large-scale, dependable quantum computing closer than ever before.


The end of the org chart: Leadership in an agentic enterprise

The traditional organizational chart is becoming obsolete as modern enterprises transition toward an "agentic" model where AI agents and humans collaborate as teammates. According to industry expert Steve Tout, the sheer volume of digital information—now doubling every eight hours—has overwhelmed human judgment, rendering legacy hierarchical structures and the "people-process-technology" framework increasingly insufficient. In this evolving landscape, AI agents handle repeatable cognitive tasks, synthesis, and data-heavy "grunt work," while human professionals retain control over high-level judgment, ethical accountability, and client trust. Organizations like McKinsey are already pioneering this shift, deploying tens of thousands of agents to streamline complex workflows. Leadership is consequently being redefined; it is no longer about maintaining a strict span of control or following predictable reporting lines. Instead, next-generation leaders must become architects of integrated networks, managing both human talent and agentic systems to foster deep organizational intelligence. By protecting human decision-makers from information fatigue, agentic enterprises can achieve greater clarity and faster strategic alignment. Ultimately, success in this new era requires a fundamental shift from viewing technology as a standalone tool to embracing it as a collaborative force that enhances the unique human capacity for sensemaking in complex, fast-moving business environments.

Daily Tech Digest - January 05, 2026


Quote for the day:

"Great leaders do not desire to lead but to serve." -- Myles Munroe


How to make AI agents reliable

Easier said than done. After all, the way genAI works, we’re trying to build deterministic software on top of probabilistic models. Large language models (LLMs), cool though they may be, are non-deterministic by nature. Chaining them together into autonomous loops amplifies that randomness. If you have a model that is 90% accurate, and you ask it to perform a five-step chain of reasoning, your total system accuracy drops to roughly 59%. That isn’t an enterprise application; it’s a coin toss—and that coin toss can cost you. Whereas a coding assistant can suggest a bad function, an agent can actually take a bad action. ... Breunig highlights “context poisoning” as a major reliability killer, where an agent gets confused by its own history or irrelevant data. We tend to treat the context window like a magical, infinite scratchpad. It isn’t. It is a database of the agent’s current state. If you fill that database with garbage (unstructured logs, hallucinated prior turns, or unauthorized data), you get garbage out. ... Finally, we need to talk about the user. One reason Breunig cites for the failure of internal agent pilots is that employees simply don’t like using them. A big part of this is what I call the rebellion against robot drivel. When we try to replace human workflows with fully autonomous agents, we often end up with verbose, hedging, soulless text, and it’s increasingly obvious to the recipient that AI wrote it, not you. And if you can’t be bothered to write it, why should they bother to read it?


Three Cybersecurity predictions that will define the CISO agenda in 2026

Different tools report different versions of “critical” risk. One team escalates an issue while another deprioritises it based on alternative scoring models. Decisions become subjective, slow and inconsistent without a coherent strategy - and critical attack paths remain open. If cyber risk is not presented consistently in the context of business impact, it’s nearly impossible to align cybersecurity with broader business objectives. In 2026, leaders will no longer tolerate this ambiguity. Boards and executives don’t want more dashboards. ... Social engineering campaigns are already more convincing, more personalised and harder for users to detect. Messages sound legitimate. Voices and content appear authentic. The line between real and fake is blurring at scale. In 2026, mature organisations will take a more disciplined approach. They will map AI initiatives to business objectives, identify which revenue streams and operational processes depend on them, and quantify the value at risk. This allows CISOs to demonstrate where existing investments meaningfully reduce exposure — and where they don’t — while maintaining operational integrity and trust. ... AI agents will take over high-volume, repetitive tasks — continuously analysing vast streams of telemetry, correlating signals across environments, and surfacing the handful of risks that truly matter. They will identify the needle in the haystack. Humans will remain firmly in the loop. 


The Hidden Costs of Silent Technology Failures

"Most CIOs see failures as negative experiences that undermine their credibility, effectiveness and ultimate growth within the organization," Koeppel said. Under those conditions, escalation is rationally delayed. CIOs attempt recovery first, including new baseline plans, renegotiations of vendor commitments and a narrower scope before formally declaring failure. ... CIOs, Dunkin noted, frequently underplay failure to shield their teams from blame. Few leaders want finger-pointing to cascade through already strained organizations. But Dunkin pointed out that the same instincts are shaped by fear of job loss, budget erosion or internal power shifts. And, she warns, bad news does not age well. Beyond politics and incentives, decision-making psychology compounds the problem. Jim Anderson, founder of Blue Elephant Consulting, describes how sunk-cost bias distorts executive judgment. Admitting a mistake publicly opens leaders to criticism, so past decisions are defended rather than reassessed. ... But not all organizations respond this way. Koeppel said that in his experience, boards and CEOs are receptive to clear, concise explanations when technology initiatives deviate from plan. Over time, disclosure improves because consequences change. Sethi described the shift to openness that followed a major outage in one organization. It resulted in mandatory, blameless post-mortem reviews that focused on systemic and process breakdowns rather than individual fault.


2026 Low-Code/No-Code Predictions

The promise of low-code platforms will finally materialize by the end of 2026. AI will let business users create bespoke applications without writing code, while professional developers guide standards, security, and integration. The line between "developer" and "user" will blur as agentic systems become part of daily work. ... No code's extinction: No code's on its last legs — it's being snuffed out by vibe coding. AI-driven development tools will be the final knell for no code as we know it, with its remit curtailed in this new coding landscape. In this future, the focus will transition entirely to model orchestration and high-level knowledge work, where humans express their intent and expertise through abstract models rather than explicit code. The human role becomes centered on the plan to build. Specifically, ensuring the problem is correctly scoped and defined. ... In 2026, low-code/no-code interfaces will rapidly shift from drag and drop canvases to natural language interfaces, as user expectations rapidly adopt to the changing landscape. As this transition occurs, application vendors will struggle to provide transparency into how the application has interpreted the users' intent. ... While it's proved remarkable for supercharging development speed and allowing non-technical individuals to produce functional software, its outputs are less than perfect. This year, we've continued to uncover that much of AI-generated code turns out fragile or flat-out wrong once it faces real workflows or customers. 


AI security risks are also cultural and developmental

The research shows that AI systems increasingly shape cultural expression, religious understanding, and historical narratives. Generative tools summarize belief systems, reproduce artistic styles, and simulate cultural symbols at scale. Errors in these representations influence trust and behavior. Communities misrepresented by AI outputs disengage from digital systems or challenge their legitimacy. In political or conflict settings, distorted cultural narratives contribute to disinformation, polarization, and identity-based targeting. Security teams working on information integrity and influence operations encounter these risks directly. The study positions cultural misrepresentation as a structural condition that adversaries exploit rather than an abstract ethics issue. ... Systems designed with assumptions of reliable connectivity or standardized data pipelines fail in regions where those conditions do not hold. Healthcare, education, and public service applications show measurable performance drops when deployed outside their original development context. These failures expose organizations to cascading risks. Decision support tools generate flawed outputs. Automated services exclude segments of the population. Security monitoring systems miss signals embedded in local language or behavior. ... Models operate on statistical patterns and lack awareness of missing data. Cultural knowledge, minority histories, and local practices often remain absent from training sets. This limitation affects detection accuracy. 


The Board’s Duty in the Age of the Black Box

Today, when this Board approves the acquisition of a Generative AI startup or authorizes a billion-dollar investment in GPU infrastructure, you are acquiring a Black Box. You are purchasing a system defined not by logical rules, but by billions of specific weights, biases, and probabilistic outcomes. These systems are inherently unstable; they “hallucinate,” they drift, and they contain latent biases that no static audit can fully reveal. They are closer to biological organisms than to traditional software. ... Critics may argue that applying financial volatility models to operational AI risk is a conceptual leap. There is no perfect mathematical bridge between “Model Drift” and “WACC” (Weighted Average Cost of Capital). However, in the absence of a liquid market for “Algorithm Liability Insurance” or standardized auditing protocols, the Board must rely on empirical proxies to gauge risk. ... The single largest destroyer of capital in the current AI cycle is the misidentification of a “Wrapper” as a “Moat.” The Board must rigorously interrogate the strategic durability of the asset. ... The Risk Committee’s role is shifting from passive monitoring to active defense. The risks associated with AI are “Fat-Tailed”—meaning that while day-to-day operations might be smooth, the rare failure modes are catastrophic. ... For the Chief Information Officer (CIO), the concept of “Model Risk” translates directly into operational reality. It is critical to differentiate between “Valuation Risk” and “Maintenance Cost.”


Cybersecurity leaders’ resolutions for 2026

Any new initiative will start with a clear architectural plan and a deep understanding of end-to-end dependencies and potential points of failure. “By taking a thoughtful, engineering-driven approach — rather than reacting to outages or disruptions — we aim to strengthen the stability, scalability, and reliability of our systems,” he says. “This foundation enables the business to move with confidence, knowing our technology and security investments are built to endure and evolve.” ... As new attack surfaces emerge with AI-driven applications and systems, Piekarski’s priorities will focus on defending and hardening the environment against AI-enabled threats and tactics.  ... In practice, SaaS management and discovery tools will be used to get a handle on shadow IT and unsanctioned AI usage. Automation for compliance and reporting will be important as customer and regulatory requirements around ESG and security continue to grow, along with threat intelligence feeds and vulnerability management solutions that help Gallagher and the team stay ahead of what’s happening in the wild. “The common thread is visibility and control; we need to know what’s in our environment, how it’s being used, and that we can respond quickly when things change,” he tells CSO. ... “Quantum computing poses significant cyber risks by potentially breaking current encryption methods, impacting data security, and enabling new attack vectors,” says Piekarski.


Enterprise Digital Twin: Why Your AI Doesn’t Understand Your Organization

Agentic AI systems are moving from research papers to production pilots, taking critical business actions such as processing invoices, scheduling meetings, drafting communications, and coordinating workflows across teams. They operate with increasing autonomy. When an agent misunderstands organizational context, it does not just give a wrong answer. It takes wrong actions, such as approving expenses that violate policy, scheduling meetings with people who should not be in the room, routing decisions to the wrong authority, and creating compliance exposure at machine speed. The industry is catching up to this reality. ... An AI system reviewing a staffing request might confirm that the budget exists, the policy allows the hire, and the hiring manager has authority. All technically correct. But without Constraint Topology, the system does not know that HR cannot process new hires until Q2 due to a systems migration, that the only approved vendor for background checks has a six-week backlog, or that three other departments have competing requisitions for the same job grade and only two can be filled this quarter. ... Most AI frameworks focus on making models smarter. CTRS focuses on making organizations faster. Technically correct outputs that do not translate into action are not actually useful. The bottleneck is not AI capability. It is the distance between what AI recommends and what the organization can execute.


The agentic infrastructure overhaul: 3 non-negotiable pillars for 2026

If 2025 was about the brain (the LLM), 2026 must be about the nervous system. You cannot bolt a self-correcting, multi-step agent onto a 2018 ERP and expect it to function. To move from isolated pilots to enterprise-wide autonomous workflows, we must overhaul our architectural blueprint. We are moving from a world of rigid, synchronous commands to a world of asynchronous, event-driven fluidity. ... We build dashboards with red and green lights so a DevOps engineer can identify a spike in latency. However, an AI agent cannot “look” at a Grafana dashboard. If an agent encounters an error mid-workflow, it needs to understand why in a format it can digest. ... Stop “bolting on” agents to legacy REST APIs. Instead, build an abstraction layer — an “agent gateway” — that converts synchronous legacy responses into asynchronous events that your agents can subscribe to. ... The old mantra was “Data is the new oil.” In 2026, data is just the raw material; Metadata is the fuel. Businesses have spent millions “cleaning” data in snowflakes and lakes, but clean data lacks the intent that agents require to make decisions. ... Invest in a data catalog that supports semantic tagging. Ensure your data engineers are not just moving rows and columns, but are defining the “meaning” of those rows in a way that is accessible via your RAG pipelines. ... The temptation in 2026 will be to build “bespoke” agents for every department — a HR agent, a finance agent, a sales agent. This is a recipe for a new kind of “shadow IT” and massive technical debt.


The New Front Line Of Digital Trust: Deepfake Security

AI-generated deepfakes are ruining the way we perceive one another, as well as undermining institutions’ ways of ensuring identity, verifying intent and maintaining trust. For CISOs and IT security risk leaders, this is a new and pressing frontier for us to focus on: defending against attacks not on systems but on beliefs. ... Deepfakes are coming to the forefront just as CISOs have more risk to manage than ever. Here are some of the other key pressures driving the financial cybersecurity environment today: Multicloud misconfigurations and API exposure; Ransomware shift to triple extortion; Expanding third-party and fourth-party dependencies; Insider threats facing hybrid workforces; Barriers to zero-trust implementation and Regulatory fragmentation. ... Deepfake security isn’t a fringe issue anymore; it’s now a foremost challenge to digital trust and systemic financial resilience. In today’s world, where synthetic voices can create markets and fake identities can trigger transactions, authenticity reigns as the currency of banking. Tomorrow’s front-runners will be those building the next-generation financial systems—secured, transparent and globally trusted. Those systems will include reconfigured trust frameworks, deepfake detection, AI governance that drives model integrity and a resilient-by-design approach. In this world, where anyone can create an AI-generated identity, the ultimate competitive differentiator is proving what’s real.