Showing posts with label value delivery. Show all posts

Daily Tech Digest - August 30, 2026


Quote for the day:

"Winning products come from the deep understanding of the user's needs combined with an equally deep understanding of what's just now possible."-- Marty Cagan

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 26 mins • Perfect for listening on the go.


What ISVs still get wrong about PCI DSS 4.0.1

Independent software developers need to update their approach to payment security standards, as the recent PCI DSS 4.0.1 guidelines make previously recommended practices strictly mandatory. As of March 2025, future-dated requirements from version 4.0 are fully enforced, meaning developers must validate their systems against the complete standard rather than relying on past assessments. This applies to any software that touches card information, even indirectly through hosted pages or embedded frames. Assessors are now enforcing stricter authentication rules, such as requiring twelve-character passwords and closely reviewing multi-factor authentication methods to ensure they meet exact security criteria rather than just the general intent. Additionally, the updated rules provide clearer boundaries on compliance responsibilities between software providers and their customers. A common mistake developers make is assuming a past validation still holds or failing to reduce their audit scope by using tokenization and encryption to keep raw card data entirely out of their systems. To prepare properly, developers should ignore unofficial vendor certificates and rely only on official attestations of compliance. The most practical step right now is to sit down with engineering teams and conduct a straightforward gap analysis against the current requirements before scheduling the next official assessment.


Beyond Compliance: The Legal Power of a Sophisticated Board of Directors

The article "Beyond Compliance: The Legal Power of a Sophisticated Board of Directors" examines how modern corporate boards must evolve past simple regulatory adherence to become proactive drivers of legal and strategic advantage. Written by corporate law expert León Patiño, the piece emphasizes that a truly sophisticated board does much more than check basic boxes for routine compliance. Instead, it leverages deep governance expertise to anticipate difficult legal challenges, mitigate serious risks before they fully materialize, and firmly protect the organization’s fundamental long-term interests. In today’s increasingly complex regulatory environment, directors are expected to fully understand their fiduciary duties and integrate legal foresight directly into their core business strategies. A highly functional board acts as a critical line of defense, ensuring that all corporate actions consistently align with both strict legal mandates and broad ethical standards. By moving beyond a reactive compliance mindset, these active boards help organizations carefully navigate volatile markets, safeguard corporate reputation, and secure a meaningful competitive edge. Ultimately, the presence of experienced, knowledgeable directors transforms corporate governance from a standard administrative obligation into a highly effective tool for sustainable growth and robust risk management. This proactive approach ensures companies remain resilient and legally sound in the face of ongoing global commercial challenges.


The CISO’s AI Defense Playbook: A Practical Framework

The article outlines a practical five-step framework for security leaders to update their defenses against rapid automated threats. With attack speeds compressing to under thirty minutes, traditional security assumptions and simple compliance models are no longer sufficient. The author notes that being compliant does not guarantee that a system is truly secure. The framework begins with mapping the attack surface, which involves cataloging software risks and auditing complex system dependencies. It also requires thoroughly inventorying machine identities, such as API keys and service accounts, which now vastly outnumber human users. Next, organizations must embed advanced scanning directly into their software development pipelines. This step uses intelligent analysis to spot complex vulnerabilities and behavioral shifts that traditional tools miss. The third phase focuses on speeding up response times by automating initial checks and pre-approving action plans for critical scenarios. Fourth, the playbook tackles the urgent need to manage machine identities by replacing static passwords with brief, automated access tokens. This significantly reduces the window of opportunity for attackers. Finally, the strategy involves training a capable security team to handle these new challenges. Ultimately, this structured approach provides a clear, sensible path for leaders to secure their environments against modern threats.


Types of Quantum Computers: 6 Major Quantum Computing Approaches

The recent article from The Quantum Insider outlines the primary approaches researchers use to build quantum computers, focusing on the underlying hardware rather than the theoretical math. Superconducting systems, currently the most common, use tiny electrical circuits cooled to extreme temperatures to manage quantum information. While effective, they require massive cooling systems. Trapped ion computers offer an alternative by suspending individual charged atoms in electromagnetic fields. This method provides high precision and stability but faces challenges in scaling up to larger machine sizes. Neutral atom systems are similar but use lasers to hold uncharged atoms in place, allowing researchers to pack them closer together for potential space efficiency. Photonic quantum computers take a completely different path, using particles of light to process information. Because they operate at room temperature, they do not need the complex cooling systems required by other methods, though controlling the light particles remains difficult. Finally, the article touches on topological approaches, which aim to weave particles together to make them naturally resistant to errors, though this remains largely in the experimental phase. Overall, the piece clarifies that there is no single best method available just yet, as each hardware design presents its own distinct set of engineering challenges.


Your Cyber Insurer May Define AI Accountability Before Your Board Does
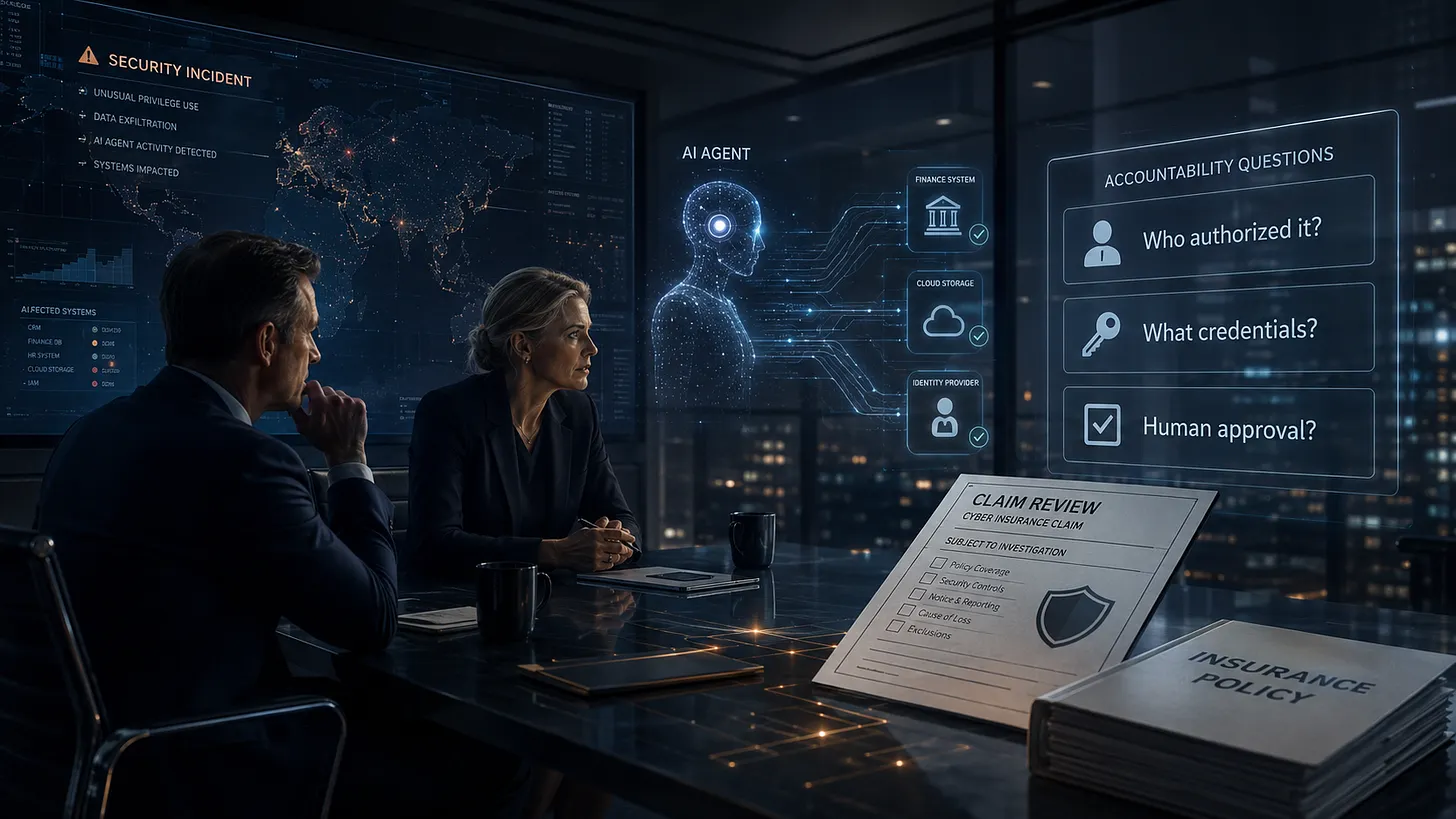
As organizations increasingly deploy artificial intelligence systems capable of taking independent actions, they face a critical gap in accountability that their insurance providers might expose before their own leadership does. When an automated system holds access credentials and the authority to execute tasks without human oversight, a malfunction can result in significant financial damage. Currently, many companies rely on vague governance policies that offer a false sense of security. Meanwhile, most insurance policies treat these exposures as silent risks, meaning they are neither explicitly covered nor excluded. However, insurance companies are beginning to demand the same level of precision for artificial intelligence that they require for traditional cybersecurity. To prevent denied claims and internal confusion, companies should conduct a thorough review of their automated systems now. This involves identifying every active system and assigning a single, accountable business owner rather than relying on a committee. Leadership must clearly define what each system is authorized to do, strictly control its access, mandate human approval for sensitive actions, and implement technical safeguards to prevent it from exceeding its limits. Organizations must also ensure they can completely audit the system's actions and shut it down immediately if unexpected issues arise during normal operations.


A Tale of Two SOCs: Insights From Two Red Team Assessments

The Cybersecurity and Infrastructure Security Agency (CISA) recently conducted concurrent red team assessments at two different critical infrastructure organizations to evaluate their threat detection and incident response capabilities. While the red team successfully achieved full domain compromise and accessed sensitive business systems and cloud resources in both environments, the defensive outcomes varied significantly. Organization A failed to detect the malicious activity due to untuned detection tools that created excessive alert noise, allowing the threat actors to move laterally without resistance. Furthermore, organizational silos and fragmented communication severely hindered their ability to respond effectively. In contrast, Organization B successfully identified the initial intrusion attempts, promptly isolated the compromised systems, and forced the assessment into an assume-breach scenario. This stark contrast highlights several key lessons for network defenders. Organizations must recognize the risks of unmanaged cloud environments and prioritize foundational security hygiene. The advisory strongly recommends that security teams establish clear network baselines, fine-tune their alerting mechanisms to reduce false positives, and break down bureaucratic hurdles to empower incident responders. Additionally, organizations should implement strict conditional access policies for cloud identities and develop comprehensive procedures to detect, remediate, and revoke unauthorized access to safeguard both their on-premises and their cloud computing infrastructures.


Your Board Has A Financial Expert—Why Doesn't It Have A Cyber One?

Corporate boards universally mandate the inclusion of financial experts to ensure robust oversight, yet they rarely apply the same standard to cybersecurity. Currently, board-level cyber discussions often occur at the end of meetings and focus narrowly on recent incidents. Because many directors lack technical backgrounds, they rely heavily on the Chief Information Security Officer to explain risks and set benchmarks. This dynamic creates circular governance, where the person being supervised dictates the terms of their own oversight, often resulting in superficial scrutiny. This lack of independent technical expertise leaves companies vulnerable to complex, long-term challenges. A pressing example is the impending transition to post-quantum cryptography. With strict federal deadlines approaching in 2030 and modern threats like data harvesting for future decryption already underway, companies face significant strategic and procurement hurdles. Directors without specific cryptographic knowledge struggle to evaluate management's long-term roadmaps or ask the right questions before a crisis hits. Ultimately, adding a cybersecurity expert to the board is not about delegating responsibility to one person, but about ensuring the entire group can independently test management assumptions. Choosing to operate without this expertise is a deliberate decision about which strategic blind spots a company is willing to accept.


Strategic Technology Roadmapping: How Growing Businesses Align Tech with Long-Term Goals

Strategic technology roadmapping involves creating a clear, practical plan to ensure a company's software and hardware choices support its broader business objectives over time. For growing companies, this process is essential to avoid wasting money on tools that do not fit their future needs. Instead of buying new software on impulse or following the latest trends, business leaders use a roadmap to match their technology purchases with specific goals, such as improving customer service or expanding into new markets. The first step in this process is taking a close look at the tools the business currently uses. This helps identify gaps or outdated systems that might slow down progress. Next, leaders must define where they want the business to be in the next few years. With these two pieces of information, they can create a step-by-step timeline that shows exactly when and how to introduce new technology. This approach keeps the company organized and prevents employees from feeling overwhelmed by sudden changes. A well-planned roadmap also makes it easier to track progress and adjust the plan if the market changes. Ultimately, matching technology with long-term goals gives growing companies a steady foundation, allowing them to scale smoothly and operate efficiently without unnecessary stress.


AI alignment, not replacement: How CIOs are rebuilding IT value
Forward-thinking Chief Information Officers are now shifting their focus from using artificial intelligence as a simple replacement for human workers to adopting a strategy of AI alignment. Rather than viewing AI as a tool for workforce reduction, these IT leaders are choosing to reorganize their departments and redesign their operating models to maximize the combined strengths of both technology and personnel. This realignment process involves strategically reshaping teams, redistributing decision-making authority, and redefining specific roles so that employees can work effectively alongside AI systems instead of competing against them. The realization is that simply replacing staff with automated systems often leads to unintended consequences and hidden financial costs, whereas integrating AI as a supportive partner helps to rebuild long-term IT value. To achieve this, CIOs are currently navigating a significant talent gap, actively seeking specialized professionals like AI architects and data engineers who can guide these complex integrations. By moving away from a purely cost-cutting mindset and focusing instead on how AI can augment existing capabilities, organizations are creating more resilient and adaptable IT environments. Ultimately, this approach ensures that technological advancements empower the workforce, driving long-term sustainable growth and establishing a more robust foundation for the future of enterprise IT operations.


The CFO’s playbook for building AI-ready finance data

In today's business environment, financial leaders face increasing pressure to adopt artificial intelligence. However, they often encounter a significant obstacle: financial data is notoriously messy, spread across multiple systems, spreadsheets, and departments. Rather than rushing to implement new technology, the focus should shift to ensuring that the underlying data is trustworthy and prepared for these advanced tools. To be useful, financial information must be clean, standardized, and tailored to specific goals. It needs to be combined accurately from various sources while remaining transparent, controlled, and easy to update as the company evolves. When information meets these standards, it becomes highly valuable for essential tasks such as speeding up the financial close, forecasting cash flow, detecting errors or fraud, and creating clear financial reports. A common challenge is the disconnect between technology teams, who manage the systems, and finance teams, who understand the business context. Bridging this gap requires reliable processes that allow finance professionals to organize and clean their information with proper oversight from technology departments. The most effective approach is to start small by focusing on a single, repetitive task. By first building a reliable and clean foundation of information, organizations can then apply new technology to improve decision-making and reduce risk safely.

Daily Tech Digest - August 04, 2026


Quote for the day:

“Whether you think you can or think you can’t, you’re right.” -- Henry Ford

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


The missing role in every enterprise AI strategy: The analytics engineer

Many enterprise artificial intelligence projects fail to reach their full potential because a crucial piece of the puzzle is missing: a clear and reliable data foundation. Often, companies employ software engineers to collect data, data engineers to move it, data scientists to build AI models, and analysts to read the results. Yet, despite this robust team, executives frequently encounter a frustrating problem: the numbers generated by the AI contradict the figures on the company's internal dashboards. This inconsistency erodes trust in the new technology. The missing link is the analytics engineer. This professional acts as a bridge between data storage, data science, and business intelligence. Their job is not just to build reports, but to create a governed "semantic layer" where every important business metric is clearly defined, standardized, and validated. They ensure that when an AI system or an analyst asks a question, they both pull from the same trustworthy source. Without this role, teams waste valuable time fighting over which numbers are correct. Ultimately, the companies succeeding with AI today are not necessarily those with the largest budgets, but those that have prioritized establishing this solid, governed data foundation first.


Digital executive protection is a strategic imperative for CEOs

In a recent interview, Brian Hill from BlackCloak explained that cybercriminals are increasingly targeting the personal lives of company executives as a backdoor into corporate networks. Because enterprise security has grown much stronger, attackers find it easier to exploit poorly secured personal devices and home networks. Hill shared real-world examples, including an executive whose unprotected personal email was hacked to steal an unreleased annual report for insider trading, and a CEO whose home network was left wide open because a technician plugged in a cable incorrectly. Another executive unknowingly picked up malware on their personal device while using public Wi-Fi at a luxury hotel. Hill emphasized that corporate security teams usually cannot monitor or fix these personal vulnerabilities because they lack the authority and visibility into executives' private lives. To defend against growing threats like deepfakes and AI-driven impersonation, Hill advocates for solutions that verify the actual person rather than just analyzing the message. Ultimately, protecting the digital lives of executives and their families is becoming a necessary extension of corporate security, closing a critical gap that traditional enterprise defenses cannot reach.


5 Hidden Leadership Fractures

Leadership failures rarely happen suddenly; instead, they stem from gradual, hidden fractures that erode a leader's effectiveness over time. One primary issue is the loss of identity, where leaders begin making decisions based on external pressures and the need for approval rather than their core values. This internal disconnect leads to poor judgment and an inability to maintain healthy boundaries. Another critical fracture involves decision-making habits. Under pressure, leaders often revert to reactive behaviors or avoid making choices altogether, which stalls organizational progress. Furthermore, while companies frequently promote individuals to higher roles, they often fail to develop the internal capacity needed to handle increased complexity, inevitably resulting in burnout and emotional exhaustion. There is also the issue of stewardship, which extends beyond managing finances to how leaders handle time, relationships, and influence. Poor stewardship creates organizational chaos, even when teams appear productive. Finally, a lack of alignment between a leader's actions and the organization's broader purpose can leave executives feeling successful yet unfulfilled, as their daily activities disconnect from their core mission. To build sustainable leadership, organizations must address these underlying structural issues rather than just treating surface-level symptoms.


The great AI disconnect: Why enterprise AI adoption often fails to deliver measurable business value

The failure of enterprise AI adoption to deliver measurable business returns—a situation Vaibhav Vora, CTO of Ascendion, calls the "Great AI Disconnect"—is rarely the fault of the AI model itself. Instead, the problem stems from trying to force new AI capabilities into outdated environments. Many organizations still rely on legacy applications, fragmented data, and workflows designed long before modern AI tools existed. Consequently, true AI readiness requires more than just deploying a new model; businesses must modernize their underlying infrastructure, clean their data, and redesign workflows to allow human employees and AI agents to collaborate seamlessly. This comprehensive approach shifts the focus away from simply lowering human labor costs and toward achieving concrete business outcomes, such as faster software delivery or improved customer service. Ascendion's internal operations reflect this philosophy, utilizing an AI platform that supports the entire software development lifecycle, from planning to deployment. This unified environment is proving particularly valuable for complex tasks like updating decades-old legacy systems in the financial sector. Furthermore, as AI reshapes enterprise technology, Global Capability Centers (GCCs) in India are evolving beyond cost-saving roles to take full ownership of complex, end-to-end global projects.


CISA Issues Fresh SBOM Guidance. Did They Get It Right?

The US Cybersecurity and Infrastructure Security Agency (CISA) has released updated guidelines for Software Bill of Materials (SBOMs), replacing the previous 2021 framework. Think of an SBOM as a recipe or ingredients list for software, designed to help organizations identify vulnerabilities in their systems. The new guidance, created with input from 16 international government entities and major tech companies like Google and Microsoft, adds 10 new elements and revises several others. A significant change is the shift from measuring the "depth" of a software's dependencies to its "coverage," meaning an SBOM should now list not just the immediate software components, but also the components those components rely on, with no limits. However, some security experts feel the updates miss the mark. Critics argue that CISA focuses too heavily on adding new data fields rather than addressing the core issue: ensuring the information provided is accurate and actually helps reduce risk. Furthermore, because these guidelines are not legally binding requirements, the responsibility still falls on customers and regulators to force suppliers to adopt these practices and provide useful, reliable security data.


Keeping Technical Skills in the Age of the LLM

The widespread adoption of artificial intelligence in software development is fundamentally changing how programmers work, presenting a unique challenge to maintaining technical proficiency. While large language models excel at generating boilerplate code, producing documentation, and exploring potential architectures, heavily relying on them can gradually erode an engineer’s core skills. The primary danger lies in allowing automated tools to replace the struggle and critical thinking required to genuinely understand complex systems. When developers stop writing code by hand and surrender the planning process to AI, they risk losing the deep, intuitive knowledge necessary to troubleshoot issues and build robust applications. To combat this slow skill degradation, professionals must actively choose to write code manually, even if just for personal projects, to keep their problem-solving abilities sharp. Additionally, consistently reading high-quality technical literature, learning new languages, and pushing boundaries ensures continuous growth. Engineers should also manage high-level project planning independently, as this develops crucial communication and strategic skills that machines cannot replicate. By treating AI as a powerful assistant rather than a replacement for critical thought and hands-on practice, developers can protect their most valuable asset: their hard-earned technical expertise.


Stop depending on heroics and start operationalizing third-party risk

In cybersecurity, assessing the risks associated with third-party vendors is often a reactive, chaotic process because security teams are brought in too late. When business units decide to purchase a new tool, they typically focus on efficiency and budget, leaving security and compliance checks for the final moments before signing a contract. This last-minute involvement creates friction, delaying projects as security scrambles to evaluate data exposure, compliance, and vendor controls. To fix this, organizations must shift away from relying on last-minute “heroics” and instead operationalize a formal, repeatable third-party risk management program. Security must partner early with legal, finance, and procurement teams to ensure assessments happen before contracts are signed, as leverage is lost once the ink is dry. The rapid adoption of artificial intelligence—both through official vendor updates and unauthorized "shadow AI"—makes this proactive approach even more critical, as sensitive data can easily be exposed to public training models. Ultimately, a mature risk management process shouldn't block business; it should define clear success criteria, hold vendors accountable through legally binding contract language, and allow companies to adopt new technologies confidently and securely.


Enabling Evolutionary Architecture Through the Preservation of Change Locality

In software engineering, maintaining an adaptable architecture means building systems that can handle constant change without forcing developers to understand the entire technical landscape. A key measure of this flexibility is change locality, which refers to a team's ability to safely implement a localized update with an amount of context that is directly proportional to the task. When boundaries between teams or systems drift—often due to expanding products, shifting internal structures, or changing responsibilities—this locality breaks down. For example, a seemingly simple task like updating a customer delivery address in a checkout system might actually require navigating warehouse cutoff times, fraud rules, and refund policies. This hidden complexity increases the mental burden on developers and slows down progress. To preserve change locality, engineering leaders must ensure that boundaries remain strictly aligned with the actual paths of change within the business. This involves making decision paths transparent and keeping responsibilities with the specific teams that best understand them. If a problem is isolated, structural interventions can clarify boundaries. Conversely, when a change genuinely affects multiple areas, teams must coordinate explicitly rather than relying on assumed knowledge. By clarifying essential rules and redistributing shared work, organizations keep changes local and systems highly adaptable.


AI is finding bugs faster than humans can fix them: How enterprise security teams must adapt

Artificial intelligence is significantly accelerating the discovery of software security flaws, but human developers simply cannot patch them fast enough. While AI tools make it cheap and easy to uncover high volumes of vulnerabilities across all types of software, fixing these issues remains a highly complex, highly manual task. Attempting to use AI to repair code often backfires, as automated fixes can introduce entirely new vulnerabilities or fail to account for specific deployment environments. Consequently, security teams and developers are increasingly overwhelmed by a massive, ongoing backlog of bug reports. This surge creates a heavy attention tax, requiring professionals to spend valuable time separating genuine, exploitable threats from machine-generated noise. The challenge affects everything from open-source platforms to proprietary systems run by major tech companies. Because security teams are often understaffed due to tighter budget constraints, they cannot possibly address every single alert. To adapt, organizations must fundamentally rethink their approach to vulnerability management. Rather than trying to patch everything blindly, companies need to implement stricter triage rules and leverage automation to filter out duplicate or low-priority reports before they reach human eyes. Ultimately, businesses must balance rapid AI detection capabilities with careful human oversight to maintain highly secure, stable enterprise systems.


Why SSO and data governance should be planned together in enterprise SaaS

Enterprise software teams can no longer separate identity management from data governance. When organizations grant users access to business platforms, they also expose critical information that influences reporting, compliance, and automation. Logging in securely is just the beginning. The real challenge is controlling what each person can view, edit, export, or approve once they are inside the system. Data governance typically handles rules, ownership, and quality checks, while identity management determines who has permission to interact with those systems. When these two functions are planned separately, security gaps quickly emerge. For instance, a data team might establish quality standards but fail to restrict who can approve exceptions. To prevent these issues, buyers expect robust identity controls before scaling data platforms. Essential features include single sign-on options, automated user provisioning to keep access aligned with current employment status, and role-based access that matches actual job responsibilities. Additionally, audit logs provide a vital record of who changed rules or exported sensitive information, and tenant isolation keeps separate business units secure. Ultimately, trusted data requires trusted access. Integrating data quality and identity planning improves information reliability and ensures that only the right people manage sensitive records, making the entire system much easier to operate safely.

Daily Tech Digest - July 10, 2026


Quote for the day:

“When people are financially invested, they want a return. When people are emotionally invested, they want to contribute.” -- Simon Sinek

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


The next killer AI feature? No AI at all

As artificial intelligence increasingly saturates everyday technology, a growing number of people are experiencing frustration rather than excitement. While tech companies forcefully integrate these capabilities into search engines, email, and productivity apps, many users find the additions unhelpful, invasive, and distracting. This widespread fatigue is creating an unexpected opportunity in the technology market: the ability to pay for services that are completely free of artificial intelligence. Consumers are demonstrating a willingness to spend money on platforms that prioritize simplicity and privacy over automated features. For example, Kagi, a paid search engine that omits automated summaries and advertisements, has seen its subscriber base double as people seek out cleaner, more reliable search results. Similarly, privacy-focused alternatives like DuckDuckGo are experiencing increased adoption whenever major providers push more automated features. This shift highlights a distinct gap between what companies are building and what users actually want. Ultimately, the next highly sought-after software feature might simply be the absence of automated assistance, allowing people to work peacefully and deliberately without forced interruptions. For organizations willing to deliver high-quality, streamlined tools, providing an escape from this technological clutter could prove to be a highly successful and reliable long-term business strategy.


Practical challenges in managing Kubernetes at enterprise scale

Managing Kubernetes at an enterprise scale introduces complex challenges that go far beyond basic engineering and deployment tasks. While the system effectively automates container orchestration, running it in a large organization shifts the focus heavily toward governance and standardization. Rather than relying on developers to become infrastructure experts, companies must create a structured environment with clear guidelines, approved templates, and standard security controls. Access permissions and network policies require continuous review and rigorous testing to prevent security gaps, as default settings are rarely sufficient over extended periods of time. Additionally, resource management becomes a direct financial concern, meaning engineering teams must collaborate closely with finance departments to monitor operational efficiency and control rising cloud costs. Automation features like autoscaling require careful configuration using relevant performance signals, and system observability must be designed to answer specific operational questions rather than just collecting endless data logs. Routine upgrades demand thorough, complete testing instead of last minute heroic efforts. Ultimately, Kubernetes cannot fix poorly built applications on its own. Success requires the platform team to operate with a product mindset, building a reliable internal system that balances developer speed with strict security and financial accountability.


Strategic Board Oversight: Architecting Institutional Fidelity in 2026

Effective board oversight requires more than passively checking boxes for compliance; it demands an active dedication to an organization’s core purpose. With upcoming regulatory changes, such as the UK’s 2026 requirement for explicit declarations on internal controls, directors must shift from simply observing past operations to actively guiding future strategy. Currently, over half of board members lack access to real-time data between meetings, leaving them vulnerable to significant blind spots. To close this gap, boards need to adopt clear frameworks and digital tools that provide continuous, reliable information without crossing the line into micromanagement. The key is maintaining a healthy balance where directors support their executives while rigorously testing their underlying assumptions. This approach relies on fostering an environment of complete honesty, where management feels safe sharing bad news early. Practical methods, like applying a structured test to every proposal to clearly check its aim, authority, evidence, and risks, help ensure that decisions are based on hard facts rather than hopeful assumptions. Ultimately, strong oversight protects the long-term value and historical knowledge of the institution, ensuring that leaders act with clear authority and objective evidence to navigate complex challenges confidently.


Why Entrepreneurs Who Master the Art of the Value Chain Have a Greater Advantage

The article argues that entrepreneurs gain a meaningful advantage when they learn to see any product or service as a composition of interconnected parts rather than a single, isolated offering. This perspective, described as mastering the “art of the value chain,” helps entrepreneurs understand that opportunities usually sit within broader systems of value. Instead of focusing only on what customers see, the article encourages looking at the underlying elements that make a product work — technology, processes, expertise, infrastructure, distribution and support — and recognizing how these pieces rely on one another. The author explains that strong entrepreneurial judgment comes from identifying where within this composition one can add value, strengthen weak links or reorganize existing elements to create better outcomes. Many successful ventures, such as Airbnb and Netflix, did not invent entirely new products; they reconfigured existing value structures in ways that improved utility for everyone involved. The article also stresses that some of the most valuable positions in a value chain are not the most visible ones, but the ones that quietly enable other parts to function well. As industries grow more complex and technologies multiply, the ability to understand how value flows through a system becomes an increasingly important entrepreneurial skill.


Standalone CDPs Fade as Enterprise Suites Expand

The customer data platform industry is undergoing a significant shift. For years, businesses relied on standalone systems to gather customer information from different sources—like websites, mobile apps, and physical stores—and piece it together into a single, unified profile. Now, these independent systems are slowly fading out. Instead, companies prefer to manage customer data directly within their existing cloud setups or larger, integrated marketing toolkits. This change is driven by a desire for efficiency. Rather than moving data into a separate platform, businesses want to use it right where it lives. This approach prevents data duplication and keeps everything streamlined. However, it also brings new challenges. When data stays in its original storage, its quality must be excellent from the start, and analyzing it frequently can drive up computing costs. Furthermore, as businesses rely more on artificial intelligence to make real-time decisions based on this data, they need to implement strict safeguards. Marketers must understand exactly how these automated systems make choices to ensure fair and accurate outcomes. Ultimately, the focus has shifted away from simply collecting and organizing data. Today, the priority is putting that information to work seamlessly within broader, more powerful business systems.


The Hidden Security Risks of Reduced Summer IT Coverage

The article explains that summer often creates quiet but significant security risks for organizations because IT and security teams typically operate with fewer people. Attackers take advantage of this seasonal slowdown, knowing that reduced oversight and slower response times make it easier to slip past defenses. The piece notes that common issues such as delayed patching, slower investigations and missing institutional knowledge can turn routine alerts into overlooked threats. Phishing and business email compromise become especially dangerous when approval chains are disrupted and employees are less inclined to verify unusual requests. The article also highlights how modern attacks move quickly, often using automation and AI, while many organizations still rely on manual processes that depend on someone being available at the right moment. This mismatch becomes more pronounced during vacation periods. To counter these gaps, the article stresses the value of automation, including automated patching, intelligent alert prioritization and runbook execution, which help maintain steady protection even when staffing is thin. Continuous monitoring ensures threats are detected and contained regardless of schedules. The overall message is that summer exposes weaknesses, but the real solution is building year‑round resilience that does not depend solely on human availability.


IT isn’t holding AI back, your business processes are

While most IT leaders feel confident in their ability to deploy artificial intelligence, the real barrier to realizing its value lies in outdated business processes. According to a recent survey, over 80% of senior IT executives trust their teams to roll out AI, yet 75% recognize that their operating models must change significantly. The core issue is that applying advanced technology to inefficient, manual routines such as spreadsheet data entry will not yield meaningful improvements. Instead of treating AI as a basic software upgrade or simply hosting prompt engineering workshops, organizations need to fundamentally redesign how work gets done. This requires a deep understanding of current workflows to identify where tasks stall and where AI can actually help. True progress demands that companies stop treating AI like a fancy word processor and start examining their core operations to determine what should be automated, supported by technology, or left to humans. To succeed, this shift requires strong commitment from top executives and tight collaboration between IT and business operations. IT teams cannot build systems in isolation; they must understand practical business problems, data quality, and management rules from the start. Ultimately, unlocking the full potential of artificial intelligence is less about overcoming technological limits and more about restructuring how an enterprise operates day to day.


India’s Aadhaar Shows Foreign Dependencies Reach Beyond US-China

When India introduced its Aadhaar digital identity system, the government presented it as a homegrown achievement. It was framed as a sovereign infrastructure built to free the country from relying on American or Chinese technology. However, this narrative overlooks a critical reality: the system relies heavily on the Japanese multinational firm NEC Corporation, which provided the core fingerprint matching technology. Because Japan maintains strong relations with India and lacks a colonial history, NEC has largely escaped the strict scrutiny applied to Western and Chinese firms. This situation highlights a significant flaw in current debates about digital sovereignty. Often, the push for technological independence simply means substituting one foreign dependency for another based on geopolitical convenience rather than genuine autonomy. While NEC technology performs well in controlled testing, its practical application in India has struggled. Authentication success rates hover around 94 percent, resulting in millions of failed attempts every month and cutting off vulnerable rural populations from essential services. Because NEC operates behind the scenes, there is a distinct lack of accountability for these failures. Ultimately, selecting preferred foreign suppliers does not equate to actual control over digital infrastructure. True digital sovereignty requires transparent and democratic oversight rather than just picking more favorable international partners.


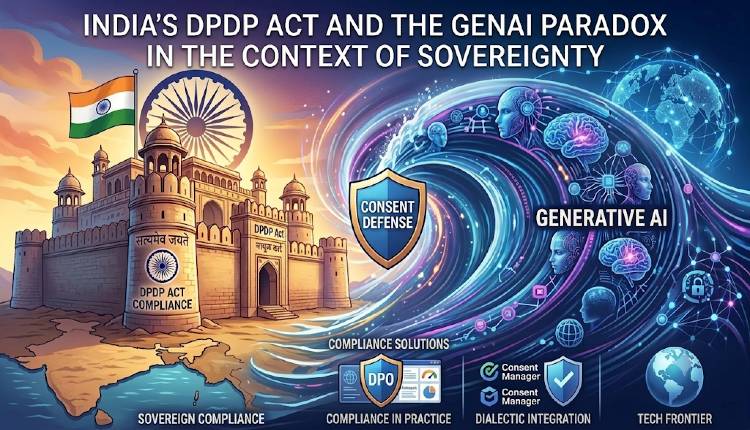
India’s DPDP Act and the GenAI paradox in the context of sovereignty

India recently introduced the Digital Personal Data Protection Act to secure the privacy of its citizens. The law focuses on clear rules like gathering only necessary data, strictly defining its purpose, securing explicit consent, and allowing people to delete their personal information. However, this creates a major conflict with generative artificial intelligence. These models operate by absorbing massive amounts of information without a specific end goal in mind, which makes securing specific consent almost impossible. Furthermore, once personal data is permanently integrated into a complex model, extracting and deleting it becomes incredibly difficult and expensive. This mismatch presents a deep paradox for policymakers trying to govern borderless technology with rigid, location-based rules. Beyond basic consumer privacy, the government is increasingly concerned about national security. Officials worry that foreign platforms could analyze patterns in the queries submitted by government employees, potentially revealing sensitive strategic information. As a result, businesses are currently working hard to adjust their operations to comply with these strict new regulations, while the government simultaneously limits the use of certain foreign tools and invests heavily in domestic alternatives. Ultimately, India faces the complex challenge of comprehensively protecting its people's data and maintaining its national sovereignty without stalling necessary technological progress.


How Hyperscale Infrastructure, Sovereign AI And Quantum Computing Redefine Enterprise Strategy

Data centers are no longer just places to store static information; they have become the central engines of the digital economy. Modern "hyperscale data centers" are filled with advanced processors working together to analyze information and create new content continuously. Because processing power is now essential for survival, huge amounts of money that used to go into traditional industries are now flowing into artificial intelligence infrastructure. Recognizing this shift, many countries are building their own local tech hubs. This push for "sovereign AI" allows nations to keep their data secure while training systems that reflect their unique languages and cultures. This move is reshaping international alliances, as countries secure the critical minerals and technology they need to stay independent. Looking ahead, adding quantum computing into these data centers will be the next major leap, potentially solving incredibly complex problems in seconds and upending current security protocols. For business leaders, this means that computing power is no longer just a basic tech expense but a core part of long-term strategy. Organizations and nations that invest in their own infrastructure and talent will secure their competitive edge, while those that do not risk falling behind and relying entirely on outside technology.

Daily Tech Digest - June 17, 2026


Quote for the day:

"The most difficult thing is the decision to act, the rest is merely tenacity." -- Amelia Earhart

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


The Rise of Agentic Internet

The internet has reached a significant milestone where automated web traffic now exceeds human activity. According to recent data, bots currently account for over fifty percent of all internet traffic, crossing this threshold much earlier than industry experts had predicted. This shift is primarily driven by the rapid emergence of autonomous artificial intelligence agents. Unlike older, simple programs or connected devices that only follow rigid instructions, these new agents possess true autonomy. They interpret user intent, adapt to context, and make independent decisions without needing constant human guidance. As a result, autonomous software traffic has experienced exponential growth over the past year. A major area affected by this change is how we search for information. Traditional search engines that return simple lists of links are being replaced by conversational interfaces. When a person asks a complex question, the software dispatches numerous agents to visit hundreds of pages, synthesize the data, and return a complete answer. Because a single human request can generate thousands of automated web actions, we are entering a new era where machines discover information, evaluate options, and execute tasks on our behalf.


Building data centers in space is an intriguing idea on paper, but major engineering challenges must be solved

The proposal to establish data centers in space presents a captivating concept that aims to address the growing energy and cooling demands of our digital infrastructure. By positioning servers outside of Earth's atmosphere, we could theoretically harness constant solar energy and utilize the natural vacuum of space to simplify heat management. While this idea appears promising on paper, it faces significant engineering and logistical hurdles that currently make it impractical. A primary obstacle is the immense difficulty and cost associated with launching and maintaining complex hardware in orbit. Unlike terrestrial facilities, space-based data centers would require specialized, radiation-hardened equipment to withstand the harsh orbital environment, including extreme temperature fluctuations and debris impacts. Furthermore, servicing or upgrading these systems would be exceptionally difficult, requiring sophisticated robotic interventions or costly human missions. There is also the critical issue of signal latency; transmitting data between Earth and space-based servers introduces delays that could disrupt many time-sensitive applications. While the idea reflects creative thinking regarding future infrastructure needs, these formidable technological and economic constraints must be thoroughly addressed before such a project could realistically transition from an interesting theoretical model to a functional reality.


Firms pursue continuous identity in push to meet agentic paradigm shift

The cybersecurity industry is rapidly evolving to address the growing presence of artificial intelligence programs operating autonomously within corporate networks. As organizations increasingly rely on these automated tools, traditional security systems built exclusively for human users are no longer sufficient. To resolve this, major technology firms are developing continuous identity verification systems that monitor and secure both human and machine activities simultaneously. Recently, a new company called NewCore secured significant funding to launch a platform that maps and protects all active network identities from the ground up. Similarly, established companies are expanding their capabilities through acquisitions and updates. SailPoint plans to acquire Entro to improve its tracking of machine credentials, while CrowdStrike has introduced a system that constantly verifies automated actions rather than granting permanent access. Additionally, Akamai has established a structured framework to safely manage automated commerce and interactions, and Silverfort has integrated instant identity checks specifically for Microsoft Copilot Studio to prevent unauthorized actions before they occur. Together, these industry developments highlight a crucial transition from one time authentication to ongoing and instant security models that ensure automated tools operate safely and responsibly within modern enterprise environments.


Beyond the ERP system: The autonomous value chain

Traditional enterprise resource planning systems have reached a performance ceiling because they rely on people to manually move and approve data. This manual approach creates expensive delays and inefficiencies that minor adjustments can no longer fix. To move forward, organizations must abandon these outdated structures in favor of an autonomous value chain. In this modernized setup, intelligent algorithms handle routine daily procurement, production, and delivery coordination in real time. Instead of functioning as manual data processors, employees are freed to focus on high level strategic design and system oversight. Transitioning to this level of autonomy requires more than just installing new software; it demands a deep organizational shift. Companies need to establish centralized, reliable data sources and build automated processes governed by clear rules and boundaries. Equally important is fostering a supportive culture built on trust and psychological safety. Teams must feel secure collaborating with automated systems, knowing they have the authority to intervene without facing blame for machine errors. Ultimately, the goal is to stop managing slow, manual workflows and instead design a fully independent system that coordinates seamlessly. This shift delivers greater operational efficiency and frees human talent for more valuable work.


Four Ways To Develop Emotional Intelligence In The Workplace

While technical skills are often highlighted on resumes, emotional intelligence is the defining trait of an effective leader. It involves recognizing and managing your own emotions while understanding those of your team. Without it, organizations face turnover and burnout; with it, they build resilience and trust. Fortunately, you can develop emotional intelligence through four practical methods. First, practice self-awareness by taking time to reflect on your emotional state before entering important conversations or meetings. This prevents unexamined stress from guiding your behavior. Second, master the strategic pause. Instead of reacting immediately to frustration, give yourself time to process the situation, such as waiting a day before replying to a difficult email. Third, use active empathy to understand the motivations and pressures your team members face. Ask how you can support them rather than demanding explanations for setbacks. Finally, create an environment of psychological safety where employees feel comfortable taking risks and making mistakes without fear of punishment. When leaders openly admit their own errors, it encourages the rest of the team to work authentically. By investing in these areas, you can build a stronger, more resilient organization.


The AI Accountability Gap CIOs Can't Ignore

According to a recent IBM survey of 2,000 technology executives, chief information and technology officers are facing a significant accountability gap as artificial intelligence moves into everyday production. While eighty percent of these leaders are under direct pressure from chief executives to adopt AI quickly, two-thirds find themselves responsible for AI outcomes they do not fully control. By the year 2027, organizations expect to manage over sixteen hundred AI models, yet only eleven percent of technology leaders feel ready for this rapid growth. A primary challenge is the steady rise of untracked AI use. Seventy percent of executives report that internal business departments deploy AI tools much faster than their technical teams can monitor. This lack of oversight has clear consequences. Over the past year, organizations experienced an average of fifty-four AI-related incidents. These events led to notable problems, including data breaches for thirty-seven percent of respondents and widespread system failures for thirty-three percent. Consequently, AI adoption is currently moving faster than organizations can secure it. Seventy-seven percent of leaders admit their deployment speeds outpace internal governance, forcing many to pause expansion until they can establish proper visibility and control.


Do Software and Programmers Still Have a Future?

In their 2026 update, the team behind the software tool NocoBase reflects on how rapid advancements in artificial intelligence initially caused intense anxiety about the future of traditional programming. Despite these fears, their revenue doubled in the first half of the year. The small team realized that while artificial intelligence can generate code quickly, large businesses still require stable, secure, and standardized foundations to run their daily operations. Companies cannot rely on raw code generation alone; they need reliable systems with proper access rules, clear steps, and visual screens that humans can easily read and adjust. Rather than fighting these rapid market changes, NocoBase adapted its main focus. They shifted from basic visual programming to providing the essential structure that allows artificial intelligence to safely interact with complex business records. By integrating advanced models internally, the team also doubled their own productivity without hiring more staff. Their direct experience with major corporate clients in life sciences and renewable energy proves that actual businesses adapt much slower than internet technology trends. By acting as a practical bridge between new tools and older manual operations, programmers and thoughtful software projects still have a secure and valuable future.


Develop smarter AI agents with data fabrics

As organizations manage data scattered across numerous platforms, data fabrics offer a practical way to centralize access and enforce consistent policies. This centralized approach is especially relevant for teams developing artificial intelligence agents. AI agents require extensive, reliable information to function effectively, relying on both structured data and unstructured formats like documents or emails. Without a shared business context, these agents struggle to make accurate decisions and can even operate counter to one another in complex systems. A data fabric acts as a central system that connects AI models to diverse information sources. It provides agents with the current data and historical memory they need to act appropriately. Furthermore, this structure allows teams to resolve data quality issues before the information reaches the AI, ensuring the agents operate on accurate, compliant, and secure inputs. By consolidating data access, organizations can also establish stricter security controls and monitor exactly what information agents use. Moving forward, data fabrics are expected to improve how they handle multimedia files and complex documents. Ultimately, a carefully planned data fabric helps organizations deploy AI agents with a clear understanding of the rules, leading to more reliable outcomes.


AI and Cybersecurity – Everything You Wanted to Know, But Were Afraid to Ask

Artificial intelligence is changing cybersecurity, presenting both new defensive capabilities and complex security challenges. Based on insights from dozens of industry professionals, the current landscape of AI in security can be understood through five primary categories: generative AI, agentic AI, shadow AI, machine learning, and artificial general intelligence. Currently, generative AI serves as the foundation. While it offers practical benefits for security teams, such as summarizing incident logs, drafting response plans, and assisting with coding, it is not inherently trustworthy. Because these models predict statistically probable answers rather than relying on absolute facts, they can produce confident but incorrect responses. Therefore, AI should act as a supportive tool rather than a replacement for human judgment. Without proper governance, organizations risk unintentional misuse, where employees rely too heavily on unverified outputs or use external, unsecured AI tools. At the same time, malicious actors are actively exploiting these technologies. They move quickly to adopt AI for creating highly convincing phishing campaigns, writing evasive malware, and executing advanced social engineering attacks. Ultimately, understanding both the practical applications and the inherent risks of AI is essential for navigating the modern security environment.


The checklist problem behind critical infrastructure cyber safety

Recent research from George Mason University highlights a significant gap in how the United States approaches the safety of critical infrastructure. Currently, operators of industrial controls, medical devices, and transportation systems often rely on standard IT security compliance to prove their systems are safe. However, this approach is fundamentally flawed because data protection rules do not easily translate to the physical world. In fact, standard IT practices can sometimes introduce physical hazards. For instance, locking down a system to protect data might trap people during an emergency or disrupt safety controls that require real-time responses. The researchers note that current regulations rely too much on administrative checklists and generic technical standards, ignoring the specific engineering needs of physical machinery. When failures occur, regulations typically only require companies to report the incident rather than prove the equipment can naturally revert to a safe state. To fix this, the study suggests shifting the legal standard of care away from basic compliance. Instead, operators should be expected to provide concrete engineering evidence showing their systems are physically resilient. This includes implementing mechanical backups and hazard-specific safety measures, ensuring that if digital defenses fail, the physical equipment remains secure.

Daily Tech Digest - May 14, 2026


Quote for the day:

“You may be disappointed if you fail, but you are doomed if you don’t try.” -- Beverly Sills

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


CIOs are put to the test as security regulations across borders recalibrate

The European Union’s Cyber Resilience Act (CRA) marks a transformative shift in global cybersecurity, forcing Chief Information Officers to transition from traditional process-oriented compliance toward a rigorous focus on tangible product safety. Unlike previous frameworks, the CRA extends the CE mark to digital systems, mandating that software, firmware, and internet-connected devices be "secure by design" and "secure by default." This recalibration requires organizations to implement robust vulnerability reporting mechanisms by September 2026 and provide minimum five-year support lifecycles for security updates. CIOs now face the daunting task of overseeing the entire product ecosystem, which includes performing continuous risk assessments and actively managing open-source dependencies. They can no longer remain passive consumers of open-source technology; instead, they must contribute back to these communities to ensure the integrity of their own supply chains. While the regulation introduces significant administrative burdens—such as the creation of Software Bills of Materials and decade-long documentation retention—it also provides a strategic lever. Savvy IT leaders are leveraging these stringent mandates to secure board-level buy-in and the necessary budget for critical security improvements. Ultimately, the CRA demands a fundamental shift in responsibility, where CIOs are held accountable for the end-to-end security of the final products their organizations deliver to the market.


The Mathematics of Backlogs: Capacity Planning for Queue Recovery

The article "The Mathematics of Backlogs: Capacity Planning for Queue Recovery" explains that queue backlogs in distributed systems are predictable arithmetic challenges rather than random mysteries. At the heart of recovery is surplus capacity, defined as the difference between total processing power and arrival rate, meaning systems provisioned only for steady-state traffic will never naturally drain a backlog. A critical insight is the non-linear relationship between utilization and queue growth; as utilization approaches 100%, even minor traffic spikes cause exponential backlog accumulation. To manage this, the author highlights Little's Law for calculating queue delays and provides a clear formula for sizing consumer headroom based on specific Recovery Time Objectives (RTO). The piece also warns of "retry amplification," which can trigger metastable failure states where recovery efforts generate more load than they can actually resolve. In complex, multi-stage pipelines, identifying the true bottleneck is essential to avoid scaling the wrong component. Furthermore, engineers are encouraged to implement load shedding when drain times exceed message TTLs to prevent wasting expensive resources on stale data. Ultimately, by measuring specific metrics like peak backlog size and retry amplification factors after incidents, teams can transition from gut-based guesswork to data-driven operational intuition, ensuring significantly more resilient and predictable system performance during unforeseen failures.


Closing the gap between technical specs and business value through storytelling

Jay McCall’s article explores the critical necessity for infrastructure-focused software companies to pivot from technical specifications to value-driven storytelling. For businesses dealing with backend systems like APIs or security middleware, value is often defined by the absence of failure, making the product essentially invisible to non-technical executives. To bridge this gap, companies must stop relying on abstract metrics like uptime percentages and instead articulate the business outcomes and peace of mind their technology provides. The article advocates for the use of experiential demonstrations, such as AI-driven simulations, which allow prospects to engage with the software and witness its problem-solving capabilities firsthand. Additionally, visual workflows should prioritize the user’s journey over technical architecture, humanizing the product and placing it within a recognizable business context. Grounding these concepts in real-world "before and after" case studies further builds trust by offering tangible templates for success. Ultimately, crafting a repeatable narrative not only accelerates the sales cycle for internal teams but also empowers channel partners to communicate value effectively. By mastering the art of storytelling, technical organizations can translate complex backend sophistication into compelling business cases that resonate with decision-makers and facilitate sustainable scaling in a competitive market.


The Critical Fork: How Leaders Turn Failure Into Better Decisions

In the Forbes article "The Critical Fork: How Leaders Turn Failure Into Better Decisions," author Brent Dykes explores the pivotal moment leaders face when project results fail to meet expectations. He introduces the "Critical Fork" framework, which highlights a fundamental choice between two distinct paths: to deflect or to inspect. Deflection involves shifting blame toward external circumstances or team members, effectively shielding a leader's ego but simultaneously obstructing any potential for organizational growth or objective learning. In contrast, the inspection path encourages leaders to treat disappointing outcomes as valuable data points rather than personal setbacks. By choosing to inspect, organizations can uncover hidden root causes, challenge flawed underlying assumptions, and refine their future strategies with greater precision. Dykes argues that the most effective leaders cultivate a culture of psychological safety where failure is viewed not as a source of shame but as a vital catalyst for deeper analysis. This systematic approach transforms setbacks into "actionable insights," a hallmark of Dykes’ broader professional work in data storytelling and analytics. Ultimately, the article posits that leadership quality is defined less by initial successes and more by the ability to navigate these critical forks. By institutionalizing an inspection mindset, businesses foster resilience and ensure every failure becomes a stepping stone toward more robust and informed strategic choices.


From Bottlenecks to Breakthroughs, Enterprises Are Rethinking Analytics in the Lakehouse Era

The article "From Bottlenecks to Breakthroughs: Enterprises Are Rethinking Analytics in the Lakehouse Era" examines the transformative shift in data management as organizations transition from fragmented architectures to unified platforms. It highlights the immense pressure on centralized data teams to deliver reliable insights at high speed while supporting the complex integrations required for generative AI. Historically, enterprises have faced significant bottlenecks caused by the siloing of data and AI, privacy concerns, and a heavy reliance on highly technical staff. To overcome these hurdles, the article advocates for the lakehouse architecture—pioneered by Databricks—as an open, unified foundation that merges the best features of data lakes and warehouses. By integrating these systems into a "Data Intelligence Platform," companies can democratize access across various skill sets through low-code solutions, such as those provided by Rivery. This evolution enables breakthrough efficiencies, including a reported 7.5x acceleration in data delivery and substantial cost reductions. Ultimately, the piece emphasizes that the winners in the modern era will be those who effectively harness unified governance and seamless orchestration to move beyond operational sprawl. By adopting these integrated strategies, enterprises can finally turn data chaos into actionable intelligence, fostering a proactive environment where AI and analytics thrive in tandem to drive competitive advantage.


Most Remediation Programs Never Confirm the Fix Actually Worked

The article titled "Most Remediation Programs Never Confirm the Fix Actually Worked" argues that despite unprecedented environment visibility, cybersecurity teams struggle to ensure that remediation efforts effectively eliminate underlying risks. Highlighting a stark disparity between exploitation speed and corporate response time, the piece references Mandiant’s M-Trends 2026 report, which identifies a negative mean time to exploit, contrasting sharply with a thirty-two-day median remediation period. The emergence of advanced AI-driven tools like Mythos has further compressed exploitation windows, making traditional "patch and pray" methods increasingly dangerous and obsolete. Many organizations mistakenly equate closing an administrative ticket with resolving a vulnerability; however, vendor patches can be bypassable, and temporary workarounds often fail under evolving network conditions. This critical issue is exacerbated by organizational friction, where security teams identify risks but rely on separate engineering departments to implement fixes, leading to fragmented communication and delayed technical actions. To address these systemic gaps, the article advocates for a fundamental shift from measuring activity to focusing on outcomes. Instead of simply verifying that a specific attack path is blocked, modern programs must incorporate rigorous revalidation to confirm the total removal of the exposure. Ultimately, true security is achieved not through ticket completion, but by creating a self-correcting feedback loop that measures risk closure.


What CISOs need to land a board role

As cybersecurity becomes a critical pillar of organizational stability, Chief Information Security Officers (CISOs) are increasingly pursuing board-level positions to bridge the gap between technical defense and strategic governance. To successfully land these roles, security leaders must shift their focus from operational execution to high-level oversight. The article emphasizes that boards are not seeking another technical operator; rather, they prioritize strategic insight, calm judgment, and the ability to articulate cybersecurity through the lenses of risk appetite, value creation, and long-term resilience. Aspiring CISOs should start by gaining experience in governance-heavy environments, such as non-profit boards or industry committees, to refine their understanding of organizational stewardship. Furthermore, investing in formal governance education, such as NACD or AICD certifications, is highly recommended to build credibility. Networking remains a vital component of the process, as many opportunities arise through established relationships. Effective candidates must also cultivate a "board bio" that highlights their expertise in financial management, regulatory navigation, and crisis response. By reframing cyber issues as matters of trust and corporate strategy rather than just technical threats, CISOs can demonstrate the unique value they bring to a board, ultimately helping companies navigate complex digital landscapes with confidence and strategic foresight.


Everything you need to know about how technology is changing business

Digital transformation is the strategic integration of technology to fundamentally overhaul business operations, efficiency, and effectiveness. Rather than merely replicating existing services in a digital format, a successful transformation involves rethinking core business models and organizational cultures to thrive in an increasingly tech-centric landscape. Key technological drivers include cloud computing, the Internet of Things, and the rapid evolution of artificial intelligence, particularly generative and agentic AI. While the COVID-19 pandemic accelerated adoption, today’s initiatives are fueled by the need to compete with nimble startups and navigate macroeconomic volatility. However, the process is notoriously complex, expensive, and risky, often requiring a shift in mindset from simple IT upgrades to comprehensive business reinvention. Despite criticisms of the term as industry hype, it represents a critical shift where technology is no longer a secondary support function but the primary engine for long-term growth. Experts emphasize that the foundation of this change is a robust, secure data platform that enables trustworthy AI operations. Ultimately, digital transformation is a continuous journey of innovation that enables established firms to adapt, scale, and deliver enhanced customer experiences. By prioritizing outcomes over buzzwords, organizations can bridge the gap between innovation and execution, ensuring they remain relevant in a global economy where every successful company is effectively a technology business.


Intelligent digital identity infrastructure for GenAI

The article explores the transformative convergence of the Modular Open Source Identity Platform (MOSIP) and Generative Artificial Intelligence (GenAI) to build a sophisticated, intelligent digital identity infrastructure. As a foundational digital public good, MOSIP offers a vendor-neutral framework that preserves national digital sovereignty while ensuring secure and scalable citizen identity systems. By integrating GenAI, these platforms move beyond static registration to become intuitive, human-centric service hubs. Key benefits include the deployment of multilingual conversational assistants that assist underserved populations with enrollment, the automation of legacy record digitization through intelligent document processing, and enhanced fraud detection capable of identifying sophisticated AI-generated deepfakes. Furthermore, GenAI empowers administrators with natural language tools to derive actionable insights from complex demographic data. However, the author emphasizes that this integration must adhere to strict principles of privacy by design, explainability, and human oversight to prevent data exploitation and surveillance risks. By utilizing technologies like container orchestration, vector databases, and localized small language models, nations can create a modular and sovereign ecosystem. Ultimately, this synergy aims to transition identity from a mere database record to a dynamic "Identity as a Service," fostering global digital inclusion by bridging literacy and language barriers for citizens everywhere.


73 Seconds to Breach, 24 Hours to Patch: The Case for Autonomous Validation

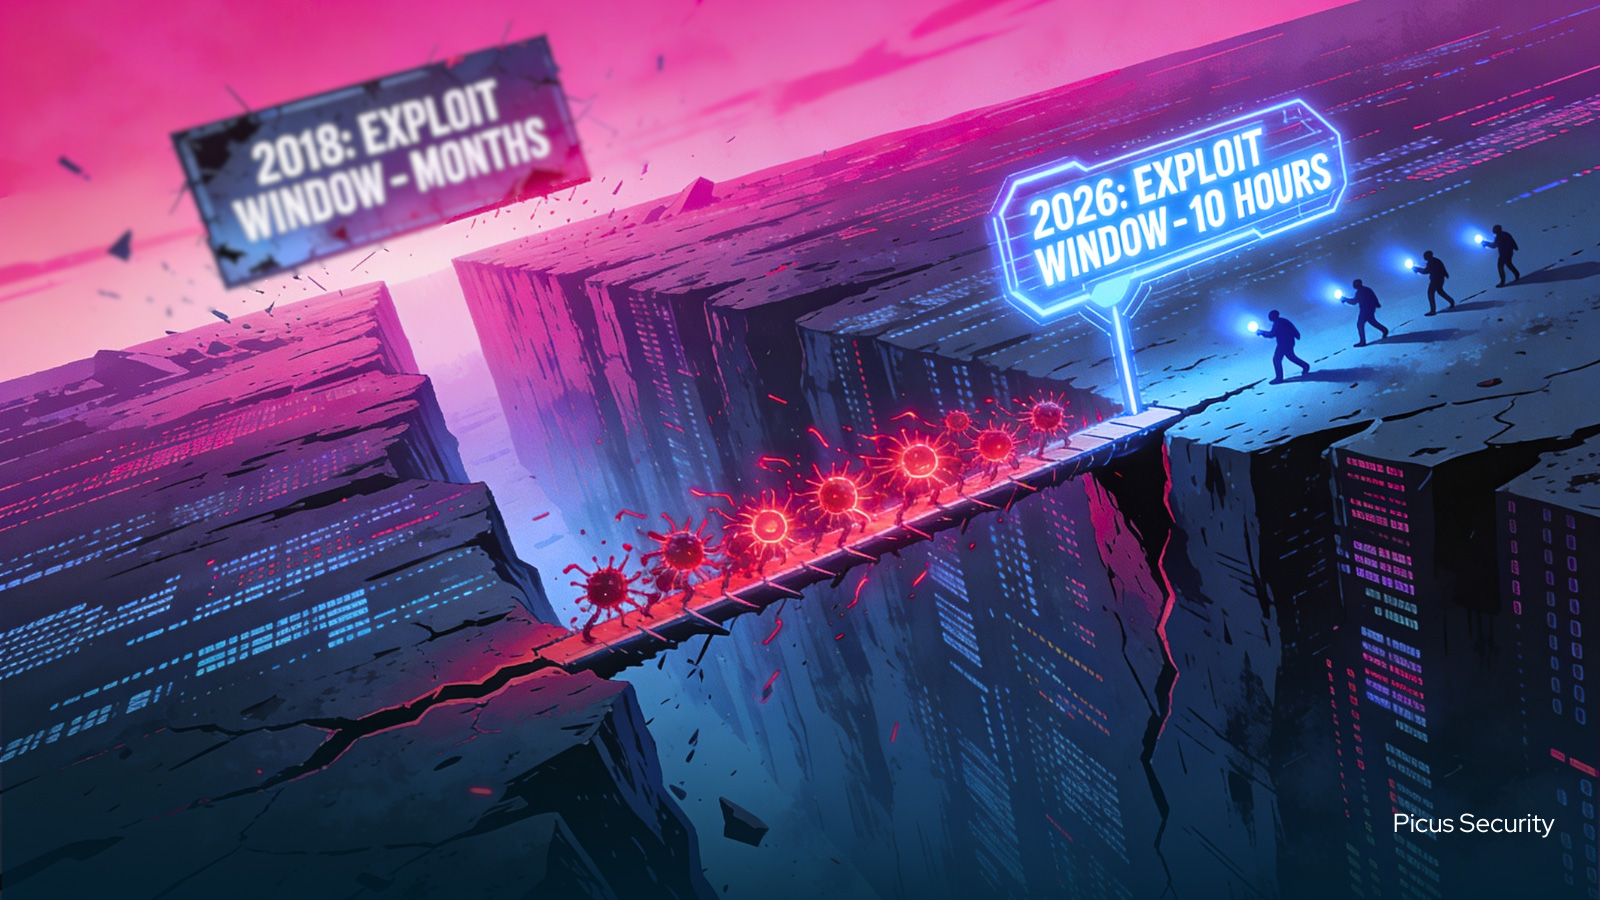
The article titled "73 Seconds to Breach, 24 Hours to Patch: The Case for Autonomous Validation" explores the widening performance gap between modern attackers and traditional security defenses. It highlights a startling reality where AI-driven threats can breach a network in just 73 seconds, while organizations typically require 24 hours or longer to deploy critical patches. This vulnerability is deepened by the fact that the median time from a CVE publication to a working exploit has plummeted to only ten hours as of 2026. According to the piece, the core challenge is not a lack of security software but the "spaghetti handoff"—the fragmented, slow communication between different teams and disconnected security tools. To address this, the article champions the transition to autonomous security validation, a strategy that merges Breach and Attack Simulation with automated penetration testing. By creating a continuous, AI-powered loop for alert triage, simulation, and remediation deployment, companies can eliminate manual bottlenecks and respond at machine speed. Ultimately, this shift is framed as a mandatory evolution for surviving the "Post-Mythos" era of cybersecurity, where defenses must become as proactive, dynamic, and rapid as the sophisticated, automated exploits they seek to prevent.