Showing posts with label cto. Show all posts

Daily Tech Digest - September 04, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


The blind spots in business continuity

Business continuity planning has fundamentally shifted from merely ensuring internal operations to mapping out external vulnerabilities. Modern organizations depend heavily on complex networks of third-party suppliers, software providers, and outsourced partners. According to a recent survey by DRI International, a significant 55% of resilience professionals identified outside vendors and supply chains as their biggest blind spot. This highlights that third-party dependency is no longer just an administrative issue but a core operational risk. Disruptions like extreme weather, cyber attacks, and technology outages frequently expose how vulnerable digital supply chains actually are. Meanwhile, 25% of respondents pointed to legacy IT systems as their primary concern. Old hardware and software are often difficult to maintain, susceptible to cyber threats, and lack the speed required for modern recovery targets. While less visible, executive succession planning also remains a quiet continuity risk. Only 14% of professionals flagged it, yet many organizations still lack clear plans for leadership continuity during a crisis. Lastly, remote work is now largely considered business as usual rather than a major blind spot. Ultimately, organizations must move beyond static supplier lists and internal recovery plans to deeply understand and protect the interconnected ecosystems they rely on daily.


Stop playing with the CISO role. Fix cybersecurity leadership

Organizations expect too much from their Chief Information Security Officers, asking them to handle complex technology while also acting as strategic business partners. This creates a structural flaw because the CISO holds accountability for cybersecurity but lacks the authority to influence broader business decisions across the company. Instead of forcing technical experts to become universal executives, companies should establish a distinct, elevated role: the Chief Security Officer. This position should sit above traditional cybersecurity and focus entirely on protecting the organization's ability to operate and compete. The CSO acts as a senior business leader with the mandate to unite conflicting departments, from legal and finance to technology and operations, ensuring that protective strategies align with business goals. Under this model, the CISO can return to their natural area of expertise. They report to the CSO and focus completely on the technical execution of security, managing architecture, engineering, and operations. This clear division of labor solves the long-standing problem of misaligned security efforts. By separating technical delivery from enterprise-level governance, businesses build a healthier management structure. Security stops being an isolated technology issue and naturally becomes a core part of how the company operates, makes decisions, and protects its future.


Risk Has No Department: Building an Enterprise-Wide Risk Ownership Culture Through ESRM
The traditional model where the security department solely owns all organizational risk is no longer sustainable. Today’s business environment is deeply interconnected, with risks spanning physical security, cybersecurity, human capital, and supply chains. As a result, Enterprise Security Risk Management (ESRM) shifts this paradigm by distributing risk ownership to the actual asset owners—the individuals who create, manage, or benefit from the assets. Instead of making all the final decisions, security professionals now act as trusted advisors who facilitate informed choices, while leaders in departments like human resources, operations, and information technology maintain ultimate accountability. To make this transition successful, organizations must establish a formal risk ownership matrix that clearly maps specific risks to their corresponding functions. This eliminates ambiguity and ensures that risk management is integrated directly into daily operational decisions rather than treated as an afterthought. Furthermore, to cement this culture of shared accountability, organizations should tie risk management effectiveness to leadership performance through key performance indicators and formal risk acceptance thresholds. Ultimately, creating an enterprise-wide risk ownership culture requires strong top-down support from executive leadership and boards of directors, ensuring that risk becomes a strategic business consideration rather than just a compliance checkbox.


How to keep your mission-critical cloud workloads running

To ensure that mission-critical cloud workloads stay online, organizations must take proactive control of their infrastructure's resilience. While cloud providers guarantee the availability of their own hardware, the responsibility for keeping specific applications running falls squarely on the user. True application resilience relies on four essential components: clustering, data replication, failover, and disaster recovery. Historically, clustering depended on expensive physical hardware, but modern software-based clusters offer the flexibility needed for hybrid and multi-cloud environments. These modern setups eliminate single points of failure by seamlessly connecting multiple systems together across varied locations. Meanwhile, keeping data consistently synchronized across these nodes through real-time replication ensures that backup systems are always fully prepared to take over. When a disruption occurs, automated failover mechanisms instantly shift workloads to standby resources without requiring manual intervention or new database builds. Furthermore, a strong disaster recovery plan incorporates geographic distance and asynchronous replication to protect against large-scale regional outages. Using these software-driven strategies not only protects against unexpected crashes but also makes planned maintenance and security patching much safer. By embracing this comprehensive approach, businesses can confidently protect their operations, prevent costly downtime, and keep their most important applications running smoothly regardless of unexpected external failures.


Who gets to decide? The CIO and the new architecture of enterprise authority

As artificial intelligence evolves from merely recommending actions to independently executing them, organizations face a critical new challenge. The core issue is no longer just what the technology can do, but who, or what, has the authority to do it. This creates an enterprise authority gap, where intelligent systems act faster than businesses can define or control their boundaries. Because modern AI interprets intent rather than just following rigid rules, it can easily cross organizational boundaries and create unintended risks if decision rights remain ambiguous. To safely manage this shift, Chief Information Officers must lead the creation of a new enterprise authority architecture. This approach requires businesses to clearly define the desired decision before selecting the technology and firmly separate a system's capability from its actual authority. Furthermore, this delegated authority must be technically enforceable through clear limits, approval gates, and continuous monitoring. Leaders also need to evaluate the true economic cost of autonomous decisions, accounting for oversight, error correction, and potential harm. Ultimately, the new mandate for technology leaders is not about maximizing how much artificial intelligence is deployed. Instead, success depends on how wisely and safely the enterprise distributes decision-making authority to these intelligent systems.


Large Enterprises Targeted in Fake Merger & Acquisition Scams
Cybercriminals are using highly sophisticated social engineering tactics to steal massive sums of money from large enterprises through fake merger and acquisition (M&A) schemes. In a recently uncovered campaign dubbed "Phantom Deal," attackers thoroughly researched mid-level employees who might be involved in corporate dealmaking. The scammers then impersonated company executives and external auditors, crafting a plausible but fake acquisition narrative based on real corporate history. To keep the target isolated, the attackers issued fake non-disclosure agreements and insisted all communication remain strictly on personal channels like WhatsApp, keeping the interactions hidden from corporate security monitors. The ultimate goal was to trick the employee into authorizing a massive wire transfer to overseas accounts. Security experts note that these scammers gather extensive, publicly available details—such as job roles and company history—to make their ruses remarkably convincing. However, organizations can protect themselves by emphasizing strict adherence to internal verification and payment controls. Employees should be trained to question whether the requested process is legitimate, rather than just trusting the identity presented on a screen. When something feels off, the safest action is to immediately halt the process and report the suspicious request through official channels.


Enterprise architecture and software architecture as the core CTO model
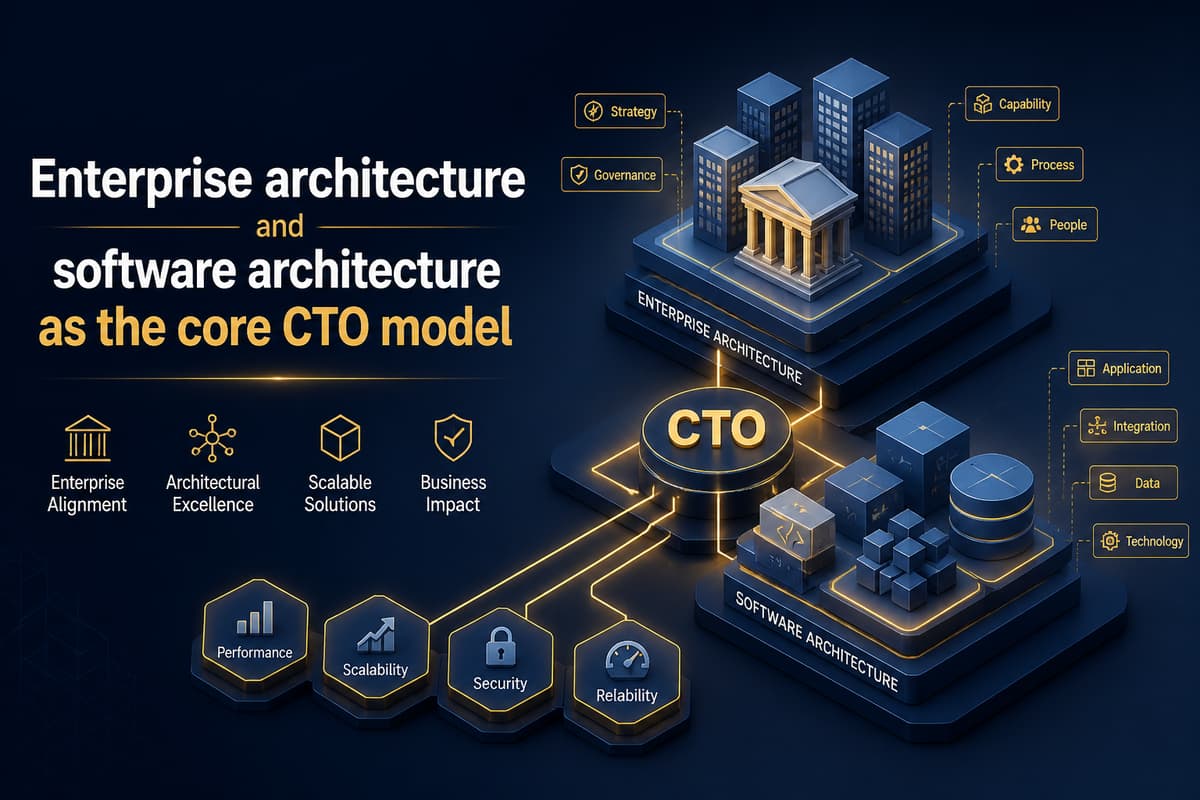
Enterprise architecture and software architecture are not just documentation tasks; they are essential frameworks that allow technology leaders to manage change safely and efficiently. Enterprise architecture maps business capabilities directly to applications, data, and risks, acting as the clear rulebook for technological decisions. Meanwhile, software architecture translates those rules into constraints that development teams can actually code against, ensuring systems perform well under stress and failure. Relying on one without the other leads to immediate problems. Enterprise architecture alone becomes an ignored catalog, while software architecture alone creates disorganized local successes that fail to serve the broader business. To succeed, leaders must adopt a continuous loop of deciding, designing, delivering, and defending their architecture choices. While artificial intelligence speeds up development, it also increases the risk of deploying bad systems quickly, making strong architectural guardrails more critical than ever. Effective leaders treat architecture like a living product rather than a static diagram. They build this practice systematically, starting with a thirty-day inventory of vital systems, followed by a ninety-day framework of automated policies, and finally establishing long-term guiding principles. Ultimately, practical architecture directly improves the four outcomes that matter most to any business: delivery speed, operational costs, system risk, and developer retention.


From IT Security to Business Strategy: Navigating Cyber Risk in Digital India

As India rapidly expands its digital economy, managing cyber risk has fundamentally shifted from a narrow technical concern into a core business strategy. For many years, organizations treated cybersecurity merely as an IT function focused on defending perimeters and protecting data. However, the modern digital landscape, fueled by cloud adoption, artificial intelligence, and complex regulatory changes like the DPDP Act, demands a far more holistic approach. Today, business leaders must carefully balance rapid technological innovation with strong governance, compliance, and resilience to maintain stakeholder trust. Cybersecurity is no longer just about preventing unauthorized access; it is about ensuring that critical operations remain consistently available and that users feel psychologically safe when interacting with digital services. Building this digital trust requires enterprises to integrate risk management across their entire ecosystem, including third party vendor networks and evolving AI models. By shifting their perspective, executives can transform security from a defensive cost center into a strategic enabler of sustainable growth. This proactive mindset allows companies to navigate evolving regulatory obligations effectively while adapting their infrastructure to meet user needs at lightning speed. Ultimately, treating cyber risk as a central business priority ensures that organizations can innovate responsibly and thrive securely in India’s dynamic digital future.

Why cyber resilience fails: 5 obstacles holding orgs back

While most organizations want to achieve strong cyber resilience to withstand attacks and keep operations running, the reality often falls short of their goals. Even when leadership provides adequate support and resources, resilience efforts frequently break down in the space between broad strategy and daily execution. Several major obstacles consistently hold companies back from properly securing their systems. Chief among these are mounting technical debt, persistent shortages in skilled security professionals, and increasingly complex identity risks. When older systems are neglected or vulnerabilities go unreviewed, they quietly compound into technical debt. This creates dangerous operational blind spots that attackers can easily exploit. Furthermore, without enough trained staff to manage these environments, security teams struggle to keep pace with evolving threats. The rapid expansion of user identities across different platforms only adds to the challenge, making it difficult to control who has access to sensitive information. Ultimately, true resilience is not just an idealistic goal or a passing project. It requires bridging the gap between management intentions and actual daily operations. To succeed, businesses must actively address these practical challenges, paying down their technical debt and heavily investing in their workforce to ensure that protective measures are flawlessly integrated into everyday tasks.


The next cyber crisis is already taking shape

The financial sector is currently facing an emerging cybersecurity crisis driven by the convergence of two major technological shifts. First, rapid advances in artificial intelligence are drastically lowering the barriers to entry for threat actors. Cybercriminals can now use sophisticated AI tools to quickly identify hidden vulnerabilities, develop exploits, and launch attacks at an unprecedented scale, making threats faster and harder to predict. Second, banks are undergoing a massive, complex transition to post-quantum cryptography to protect their infrastructure against future computing power that could easily break current encryption standards. Because modern banking relies entirely on deeply embedded cryptographic systems, updating them requires years of careful planning. Unlike the Y2K bug, this transition lacks a strict universal deadline, which can dangerously lead to delayed action and increased exposure for institutions. Together, these dual challenges mean that traditional security playbooks are no longer sufficient. Simply recovering systems after a breach is inadequate when facing AI-accelerated attacks and disruptive infrastructure overhauls. Instead, organizations must embrace a strategy of managed degradation. True enterprise resilience now requires maintaining core financial operations and preserving customer trust even while systems are actively compromised. Financial institutions must proactively address this growing imbalance and begin their extensive security upgrades before time runs out.

Daily Tech Digest - May 29, 2026


Quote for the day:

"Failure is not the opposite of success. It is part of success." -- @PilotSpeaker

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


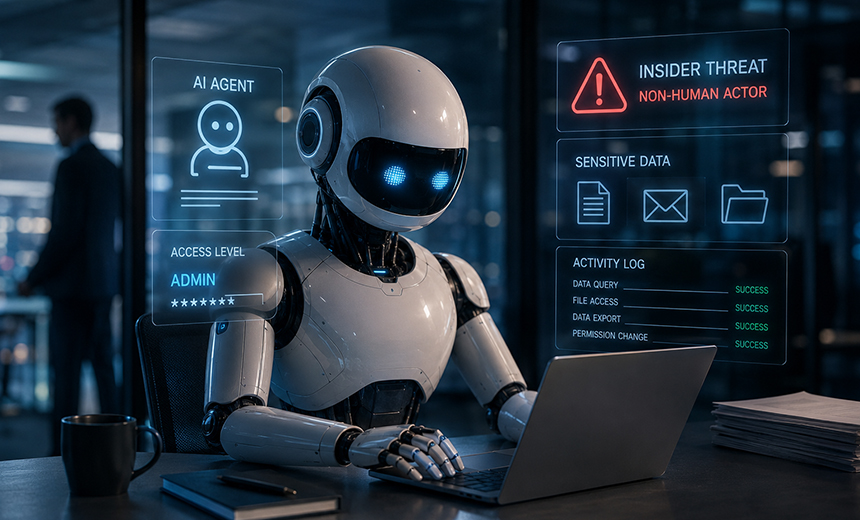
AI Agents Are the New Insiders

The article outlines how artificial intelligence systems are changing from passive tools into autonomous entities capable of making decisions and accessing sensitive data with minimal supervision. This shift introduces a new type of corporate risk: the digital insider threat. Traditionally, security strategies focused on managing human behavior, such as spotting disgruntled employees or compromised login credentials. However, automated software agents lack these biological patterns and can cause widespread problems much faster. They work at machine speed, allowing them to pull vast amounts of data simultaneously before traditional defenses register an anomaly. Furthermore, because these tools combine multiple technical skills like writing code and querying databases, a single faulty prompt or system misconfiguration can create an unexpected vulnerability. Traditional security systems fail here because they are built to monitor human working hours and typing habits, meaning they easily become overwhelmed by millions of automated logs. To address this risk, organizations need to update their approach by adopting behavioral monitoring, isolating software tasks in secure environments, and granting access permissions only when needed. Implementing strict management routines for software deployment and keeping a human in charge of final approvals for critical actions will help teams safely manage these independent tools.


The CTO’s Comprehension Debt

The article from The Serious CTO addresses a hidden challenge in software development called comprehension debt. This issue represents the growing gap between the massive volume of code teams are shipping and what they actually understand about their systems. With the rise of artificial intelligence tools, developers frequently transition from being builders to merely reviewing code they do not fully grasp. The author distinguishes comprehension debt from traditional technical debt. While technical debt involves conscious, deliberate shortcuts that developers plan to fix later, comprehension debt accumulates invisibly and unintentionally. Because code produced by machines looks clean and passes automated testing suites, it creates a false sense of security that standard tracking metrics fail to flag. These metrics track deployment frequency and overall speed rather than genuine human understanding. Consequently, teams face a new breed of legacy systems built at high speeds but impossible to maintain. When a major technical failure happens, engineers can see the error reports but cannot explain the underlying logic or design intent. Standard remedies like heavier peer reviews or more tests only mask the deeper problem. The piece concludes that organizations must treat code comprehension as a vital asset and actively maintain a clear, shared mental model of their entire core infrastructure.


What the industrialization of exploitation means for defenders

In this CSO Online article, the author explains how artificial intelligence has automated cyberattacks, transforming what used to be a battle of human skill into rapid, widespread operations. This shift allows threat actors to scan and exploit vulnerabilities across thousands of organizations simultaneously without needing deep technical expertise. Unfortunately, most corporate security departments remain stuck in an outdated mindset. Instead of building cohesive defenses, organizations frequently layer disconnected software tools that generate a confusing amount of data without offering real clarity. To counter this threat, defenders must stop treating software flaws as isolated issues on a spreadsheet and instead look at their networks through the eyes of an intruder. This means focusing on how separate weaknesses can be linked together to form a real path to critical corporate assets. Despite the rise of automated hacking tools, defenders still maintain a fundamental advantage: they already operate inside the network. By shifting their focus toward continuously mapping their environment and understanding internal security relationships, teams can pinpoint and patch the genuine entry points that matter most, rather than waste time on theoretical risks. Ultimately, staying secure requires a clear understanding of your own infrastructure to disrupt an attacker's journey before they gain a foothold.


Privacy under pressure: Challenges in the age of AI

This article details the privacy obligations healthcare organizations and their business associates face as they increasingly adopt artificial intelligence platforms while handling protected health information. Although the benefits of automated systems include increased efficiency and improved patient experiences, federal and state regulators expect providers to manage their technical frameworks closely. Enforcement agencies, such as the Department of Health and Human Services and the Department of Justice, demand thorough risk assessments tailored to unique technical vulnerabilities, such as data aggregation and cloud processing. A critical privacy threat involves sophisticated software algorithms that can reverse data anonymization and trace records back to specific individuals. Additionally, uploading sensitive medical information into public generative software applications often causes unintended leaks and severe compliance violations. To navigate these digital complexities confidently, healthcare administrators must establish comprehensive inventories of all active software tools and execute regular risk evaluations. Restricting file access based on specific user roles, encrypting sensitive medical data, and requiring multi-factor authentication are practical strategies to keep records secure. Finally, institutions should solidify external vendor contracts, conduct continual staff training sessions, and create internal governance committees to track legal shifts, ensuring that new technology safely integrates without undermining patient confidentiality.


Why software development is changing for good

In this CIO article, technology entrepreneur Nick Thompson reflects on why software development is experiencing a permanent and structural change. After a decade away from daily coding, Thompson recently found himself building a complex robotics system again, a return made possible because artificial intelligence has drastically lowered the cost of experimentation. In the past, writing software required rigid upfront planning because creating and editing code was inherently slow and expensive. Once a team spent weeks building a specific feature, changing direction was financially difficult. Today, software developers can test new ideas, review live results, and discard ineffective approaches in minutes with almost no penalty. This shift alters the developer's traditional role from a manual writer of code to a director or manager who sets the core vision, reviews automated output, and corrects architectural mistakes. Thompson emphasizes that this transition actually makes foundational system design and human experience more critical than ever. Without a clear human strategy, automated tools will simply build poorly structured programs at a faster rate. Ultimately, the value of a modern developer is no longer about memorizing syntax, but about exercising mature judgment, managing complexity, and knowing when an approach must be simplified. Experienced professionals find that their engineering instincts are becoming far more valuable than basic technical execution.


OMB cyber directive pushes centralized logging, AI-driven detection to counter cyber threats across IoT and OT systems

The United States Office of Management and Budget recently released an updated cybersecurity directive, Memorandum M-26-14, that establishes a more flexible approach to network security for federal agencies. This new mandate replaces an older framework that required organizations to store massive volumes of data, a process that proved both costly and operationally impractical for most offices. Instead, the updated guidance instructs agencies to employ a prioritized strategy focusing on continuous event monitoring alongside improved threat hunting, forensic investigation, and incident response capabilities. The regulations apply broadly across all federal networks, notably including operational technology environments and connected internet of things devices. Under this strategy, the Cybersecurity and Infrastructure Security Agency has ninety days to design a comprehensive reference architecture to guide individual agencies as they build their own structured logging plans. This updated model utilizes automated anomaly detection and advanced analytical tools to help defenders counter rapid and highly automated digital attacks. Furthermore, the directive sets clear and extended data retention standards, requiring departments to keep searchable system records for at least six months and retrievable files for one full year. Finally, agencies are expected to share these logs with federal investigators during suspected breaches to streamline security operations and enhance national defense.


Preparing for Mythos and Enhanced AI-Enabled Cyber Threats: UK Financial Services Regulator Expectations

A joint statement by the Financial Conduct Authority, the Bank of England, and HM Treasury highlights how advanced artificial intelligence software, like Anthropic's Mythos system, creates new cybersecurity challenges for the UK financial sector. Regulators warn that these advanced tools allow malicious actors to identify and exploit software flaws at an unprecedented speed and scale. Rather than introducing entirely new regulations, authorities intend to hold firms accountable using existing frameworks, meaning companies face potential supervisory actions or penalties if their defenses fall short. To prepare for these challenges, financial institutions must ensure their boards and senior executives thoroughly understand these shifting risks to guide corporate decisions effectively. Firms should also strengthen basic technical habits by keeping an accurate inventory of their computer hardware and software, mapping operational connections, and safely deleting or isolating old data. Furthermore, patching procedures and IT staffing levels must be updated so teams can fix vulnerabilities more quickly while minimizing business disruptions. Finally, risk planning should account for complex, simultaneous attacks across different systems, while vendor contracts must mandate prompt notifications and clear technical support. By reinforcing these foundational habits, companies can maintain steady security against automated threats.


Four Lessons From a Founder to Build and Scale a Cybersecurity Company That Lasts

In this article, a cybersecurity company co-founder shares four key lessons learned over seventeen years of building a resilient business from the ground up. The first lesson is to always prioritize the actual needs of customers over the personal desire to build a specific software product. Founders should have open, honest conversations with industry practitioners to understand their everyday challenges, creating long-term partnerships rather than treating people as mere sales transactions. Second, the author notes that true leadership takes time, meaning it is entirely normal not to have all the answers immediately; success lies in a leader's willingness to solve unpredictable problems as they arise while staying present and accessible to their staff. Third, long-term hiring should focus heavily on cultural alignment and adaptability rather than just checking off technical skills on a resume. Evaluating a candidate’s self-awareness and collaboration style ensures a stronger, more unified team. Finally, retaining talented employees requires keeping the daily work meaningful and maintaining a supportive internal environment. This includes creating inclusive spaces that welcome underrepresented groups and encouraging open communication across departments. Ultimately, the author emphasizes that a lasting business relies on treating both customers and employees as valued human partners, proving that professional networks and healthy workplaces are the true foundations of enduring corporate achievement.


Third-Party Risk in the Age of SaaS: The Supplier You Don’t Know Can Hurt You Most

The article explains how modern companies rely heavily on an extensive network of cloud platforms and external software applications. However, many organizations still focus their risk management solely on internal systems, creating a major operational blind spot. Because individual departments can easily purchase independent software tools using a corporate credit card, businesses face a hidden buildup of platforms operating completely outside the view of centralized technology teams. This lack of visibility hides significant vulnerabilities, particularly hidden dependencies where multiple seemingly independent software tools actually rely on the exact same underlying provider. Furthermore, external vendor risk is no longer just a computer security problem; a single vendor failure can directly halt core business functions, freeze supply chains, or stop employee payroll systems. To manage these realities, traditional annual or onboarding assessments based on simple checklists are no longer sufficient. Companies are now shifting toward continuous risk monitoring to track their external partners' operational health and safety measures on an ongoing basis. Additionally, corporate contracts are becoming practical defensive tools, with organizations requiring much clearer guidelines regarding data ownership, swift incident notifications, and subcontractor disclosures. Ultimately, a firm's actual stability is entirely defined by the daily standards of the suppliers it tracks the least.


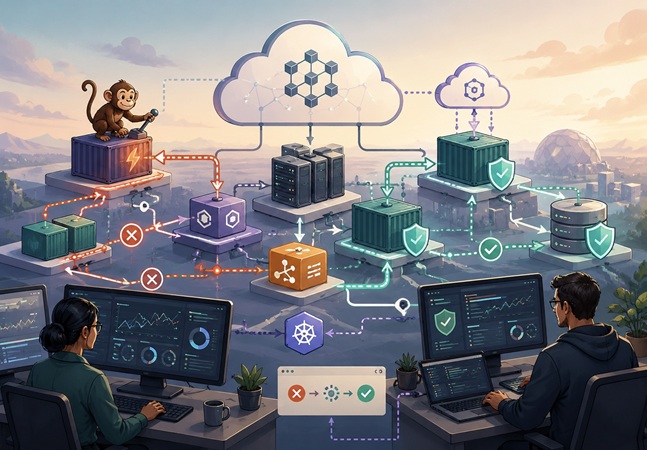
Cloud Resiliency Expert Dives Deep into Chaos Engineering and Chaos Monkey

In a recent virtual session at the Cyber Resilience for Cloud-Native Infrastructure Summit, technology author and cloud resilience expert Brien Posey discussed the practical role of chaos engineering in modern software infrastructure. Originally popularized by Netflix through its Chaos Monkey tool, which randomly shut down live servers to evaluate system survival, this practice revolves around intentionally creating controlled disruptions. As Posey noted, the primary goal of the methodology is not to cause actual damage, but to reduce a team's underlying fear of unexpected failure. Modern cloud networks rely heavily on web APIs, software containers, and various interconnected vendor dependencies, making their exact breaking points highly unpredictable. Rather than waiting to patch a live outage after the fact, engineers can use these simulated disruptions to study how both their software architectures and their response teams handle intense operational stress beforehand. However, Posey cautioned that these deliberate tests must never be performed recklessly. They require full support from company leadership, clear monitoring visibility, an immediate ability to roll back changes, a carefully restricted blast radius, and pre-defined conditions to stop the test instantly if things go wrong. Ultimately, proactively uncovering weak points helps organizations safely preserve business operations and maintain customer trust.

Daily Tech Digest - May 16, 2026


Quote for the day:

“A leader’s real power is measured not by the decisions they make, but by the decisions they enable.” -- Leadership Principle


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 17 mins • Perfect for listening on the go.


Digital twins reshape network and data center management

As demanding artificial intelligence workloads exponentially increase modern network complexity and push data center power densities past traditional physical limits, digital twins are rapidly transitioning from specialized enterprise edge cases into baseline operational tools. Unlike static design simulations, these digital twins act as continuously synchronized virtual replicas of live environments. For network management teams, these twins provide mathematically verified, current behavioral models derived from device configurations and state data, allowing engineers to safely test infrastructure updates and reduce unplanned outages by as much as seventy percent. Meanwhile, data center engineers utilize advanced computational fluid dynamics and electrical simulations within the twin to model extreme power loads, rack layouts, and cooling strategies before touching physical hardware, mitigating risks for high density systems like Nvidia clusters that exceed one hundred fifty kilowatts per rack. Integrating artificial intelligence further enhances these virtual models via natural language querying interfaces, which eliminate configuration hallucinations by grounding outputs in verified facts, and autonomous agentic workflows that independently diagnose errors or optimize cooling efficiency. Ultimately, as hybrid cloud architectures and dense processing clusters fully outpace manual oversight, the combination of artificial intelligence and digital twins delivers the essential baseline planning foundation required to maintain enterprise operational stability.


The Pipeline That Shapes the Work: On Build Systems, CI/CD, and Deployment Infrastructure

In this article, Andras Ludanyi argues that build and deployment pipelines are not neutral technical constraints but important policy documents encoded in automation that structurally dictate engineering workflows. At the core of software development is the feedback loop, and its speed acts as the central variable shaping developer behavior. Rapid feedback loops, resolving in just a few minutes, enable engineers to maintain cognitive context and continuously integrate small, low risk changes. Conversely, slow pipelines enforce costly context switching and encourage risky change batching, which expands the error diagnostic surface when failures occur. To maximize efficiency, pipelines must be intentionally designed rather than haphazardly accumulated over time. This requires utilizing structured stages, running fast static analysis and unit testing before parallelized integration tests, while deferring heavy comprehensive validation to later deployment gates. Furthermore, deployment frequency is entirely governed by pipeline friction. Smooth automation fosters routine, frequent deployments, while high friction processes breed massive, infrequent releases accompanied by extensive organizational ceremony. Finally, adopting infrastructure as code mitigates environment drift and instability by subjecting environment configurations to the same version controlled rigor as application code. Ultimately, treating the pipeline as a first class engineering artifact yields substantial compounding returns across team productivity, software quality, and system reliability.


Cyber Resilience Is Now a CEO Metric, Not a CISO KPI

Historically managed by specialized IT teams and Chief Information Security Officers (CISOs), cybersecurity has rapidly evolved into a critical enterprise-wide responsibility falling under the direct purview of Chief Executive Officers (CEOs). This fundamental paradigm shift is heavily driven by accelerated business digitization and the emergence of highly sophisticated, AI-enabled threats like advanced phishing, synthetic voice cloning, and deepfakes. Consequently, a dangerous organizational maturity gap has opened between aggressive digital adoption and lagging cyber preparedness. Modern cyber disruptions are no longer isolated technical failures; instead, they carry massive enterprise-wide consequences, including immediate operational paralysis, compounding financial liabilities, strict regulatory penalties, and severe reputational damage. Because absolute risk prevention is increasingly unrealistic in today’s volatile landscape, forward-thinking organizations must pivot from basic cybersecurity to holistic cyber resilience. This comprehensive strategy prioritizes an organization's structural capability to absorb ongoing disruptions, contain damage, maintain operational continuity, and swiftly adapt. Therefore, the contemporary CEO's mandate extends far beyond simply approving technology budgets to actively cultivating an integrated, cross-functional resilience culture. Ultimately, cyber resilience is no longer a narrow IT performance metric, but rather a defining test of corporate leadership, governance, and long-term enterprise sustainability, effectively ensuring the preservation of overall stakeholder trust.


The Strategic Impact Of Edge Computing And AI On Modern Manufacturing

In "The Strategic Impact of Edge Computing and AI on Modern Manufacturing," John Healy discusses how industrial organizations use localized data processing to optimize real-time efficiency and productivity. As automation generates unprecedented data volumes, edge computing addresses traditional cloud latency by moving compute power closer to machinery and sensors, a market projected to surpass $380 billion by 2028. By integrating artificial intelligence, edge systems amplify these operational benefits through predictive maintenance, automated equipment adjustments, and enhanced energy efficiency, which ultimately lower costs. Furthermore, keeping data local improves data governance and strengthens cybersecurity against rising industrial threats, with forecasts indicating that nearly 74% of global data will process outside traditional data centers by the early 2030s. Despite these advantages, expanding edge initiatives often stalls due to organizational fragmentation and misaligned information technology (IT) and operational technology (OT) teams. Overcoming these barriers requires shared accountability, utilizing existing industrial assets, and targeting high-value use cases like real-time quality monitoring. Ultimately, the convergence of AI and edge computing represents a structural shift that bridges traditional automation with advanced capabilities like digital twins and robotics. For instance, mobile warehouse robots rely on this localized processing to navigate dynamic environments safely. By adopting these systems, manufacturers establish a defining capability for future industrial performance.


Leadership During Crisis: How Technology Firms Can Build Cultures That Bend Without Breaking

In the fast-paced technology sector, crises are uniquely complex due to their high velocity, visibility, systemic interdependence, and heavy emotional load on engineering teams. Moving past traditional command-and-control structures, modern organizational resilience demands a shift toward building an adaptable corporate culture that bends without breaking. According to Kannan Subbiah, a resilient culture functions as an essential operating system anchored by psychological safety, radical transparency, and decentralized decision-making. Effective crisis leaders must intentionally cultivate an agile mindset where calm is contagious, prioritizing clear, actionable daily direction over absolute long-term certainty. Furthermore, maximizing employee engagement is highly critical to mitigate pervasive crisis fatigue and sustain performance under intense pressure. Communication serves as a leadership superpower, requiring managers to share updates early, maintain an empathetic and accountable tone, and completely avoid blaming individuals. When making high-stakes choices, utilizing structured frameworks helps separate critical operational signals from distracting background noise while empowering specialized teams to act autonomously. Finally, the post-crisis phase serves as the ultimate test of leadership, necessitating blameless postmortems, enhanced capabilities, and consistent actions to rebuild trust. Ultimately, the future of tech crisis management relies on an intersection of human-centered empathy, data-driven insights, and adaptive execution, proving that crises do not build leaders but reveal them.


Why DevOps Is Critical for Modern Business Resilience

In a rapidly changing business environment marked by evolving cyber threats and shifting market demands, modern business resilience relies heavily on the strategic adoption of DevOps practices. According to the article, DevOps establishes a vital cultural and technical bridge between development and operations teams, replacing siloed organizational workflows and blame games with a unified model of shared responsibility. This profound paradigm shift accelerates enterprise innovation through microservices and essential technical drivers like Continuous Integration and Continuous Delivery (CI/CD), which actively minimize human error and automate seamless code deployment. Furthermore, the proactive practice of DevSecOps embeds security protocols directly into every single stage of the software development life cycle, ensuring that critical vulnerabilities are mitigated early and cost-effectively rather than treated as a mere afterthought. To proactively preempt failures, modern organizations leverage comprehensive observability frameworks enhanced by artificial intelligence to identify backend system issues before customers ever notice. From an architectural perspective, operational resilience is heavily reinforced through active-active configurations that run critical applications simultaneously across multiple geographic cloud regions to guarantee faster disaster recovery. Ultimately, cultivating true business resilience is primarily an ongoing cultural challenge that requires leadership to foster psychological safety, continuous learning, and robust documentation, empowering agile teams to intentionally prepare for and adapt to unexpected market disruptions.


Autonomous systems are finally working. Security is next

In this article, Chris Lentricchia argues that cybersecurity is reaching a transformative 'Waymo moment,' moving from human-driven alert analysis to autonomous systems. Over the past decade, the industry heavily prioritized threat detection, which created an overwhelming volume of alerts. However, because attackers achieve lateral movement in an average of twenty-nine minutes, human-speed investigation remains the primary bottleneck. True defense requires rapidly executing the OODA loop, consisting of observation, orientation, decision, and action, which human security teams cannot accomplish given the scale of modern data. To fix this structural asymmetry, autonomous security systems must absorb the investigative sequence. Instead of requiring analysts to manually gather context from fragmented tools, autonomous platforms can compile and present a completed threat assessment instantly. Furthermore, automated remediation mechanisms can bridge the gap between decision and action by executing real-time protective measures, such as isolating compromised workloads or revoking user credentials, while maintaining human oversight. The widespread adoption of artificial intelligence accelerates interaction speeds even further, requiring continuous validation models. Ultimately, cybersecurity success will not be determined by expanded visibility or better alerts, but by the ability to autonomously complete the entire response cycle faster than modern attackers can exploit environments.


The cloud native CTO

The article "The Cloud-Native CTO: Airbnb & Pinterest," published by Data Center Dynamics, analyzes the strategic evolution of infrastructure engineering and technology leadership within modern, hyper-growth digital platforms. By exploring the cloud architecture of major systems like Airbnb and Pinterest, the piece highlights their shift entirely away from legacy physical data centers toward mature, cloud-native ecosystems built atop public hyperscalers such as Amazon Web Services. It details how these companies manage immense global scale, supporting billions of data points and millions of active users without managing on-premises server hardware. A central focus of the text is the integration of advanced machine learning, real-time personalization, and algorithmic recommendation engines directly into the core platform frameworks. These complex, data-heavy workloads require dynamic architectures relying on microservices, containerized deployments, and robust distributed database layers. Furthermore, the analysis breaks down the multi-faceted responsibilities of a modern chief technology officer, emphasizing the continuous need to balance rapid product feature deployment against rigorous cloud spend optimization, regional data compliance, and systemic reliability. Ultimately, the publication underscores that mastering a cloud-native operation demands a total organizational pivot, converting system infrastructure into a highly agile, competitive asset that continuously fuels corporate growth and technological innovation.


How Intelligent Operations Are Reshaping Manufacturing

The article outlines how manufacturing is shifting from reactive to intelligent operations to combat severe macroeconomic pressures like supply chain disruptions, rising quality demands, and labor shortages. Advanced emerging technologies, including the Industrial Internet of Things, edge artificial intelligence, 5G, and agentic AI, are converging to replace traditional digitization with smart manufacturing. Leaders from prominent corporations like Blue Star, Apollo Tyres, and Uno Minda highlight that successful transformations rely heavily on structured maturity assessments and strong data architectures rather than isolated pilot projects. For instance, unified data fabrics and internal artificial intelligence models are actively streamlining root cause analysis, quality assurance, and predictive maintenance across production environments. Furthermore, these complex strategies must seamlessly incorporate data sovereignty, robust operational technology cybersecurity, and enterprise modernization frameworks. Ultimately, manufacturing chief information officers emphasize that the most difficult aspect of achieving a resilient, intelligent factory ecosystem is not deploying the technology itself, but rather cultivating the internal talent, skills, and change management required to scale these advanced systems. Consequently, workforce readiness remains a central constraint on operations, making human capability building the definitive cornerstone of modern industrial evolution.


Vector embedding security gap exposes enterprise AI pipelines

The article introduces VectorSmuggle, an open-source research framework by Jascha Wanger of ThirdKey that exposes a significant security vulnerability in enterprise AI pipelines, specifically regarding vector embeddings used in Retrieval-Augmented Generation (RAG). As companies convert sensitive documents into high-dimensional numerical vectors, traditional Data Loss Prevention (DLP) and egress monitoring tools remain completely blind to this data format. VectorSmuggle demonstrates six steganographic methods, including adding noise, scaling, and rotating, to clandestinely hide unauthorized payloads within these embeddings. Crucially, the perturbed vectors continue to function normally for legitimate search queries, allowing data exfiltration to go entirely unnoticed. Testing across prominent embedding models from OpenAI, Nomic, Gemma, Snowflake, and MXBai revealed that while statistical detectors can catch noise-based alterations, vector rotation seamlessly evades standard anomaly detection by preserving mathematical relationships. This rotation technique can smuggle roughly 1,920 bytes per vector across popular databases like FAISS and Chroma. To counter this invisible infrastructure-layer threat, the project introduces VectorPin, a defensive mechanism that cryptographically signs embeddings upon creation to flag any subsequent tampering. Wanger warns that while most contemporary AI security efforts focus on the visible model layer, the underlying plumbing remains highly vulnerable to sophisticated data leakage.

Daily Tech Digest - March 16, 2026


Quote for the day:

"Inspired leaders move a business beyond problems into opportunities." -- Dr. Abraham Zaleznik


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Why many enterprises struggle with outdated digital systems & how to fix them

The article on Express Computer, "Why many enterprises struggle with outdated digital systems & how to fix them," explores the pervasive issue of legacy technical debt. Many organizations remain tethered to aging infrastructure that stifles innovation and hampers agility. The struggle often stems from the prohibitive costs of replacement, the immense complexity of migrating mission-critical processes, and a fundamental fear of business disruption. Governance layers and siloed ownership further exacerbate these challenges, creating compounding "enterprise debt" across processes, data, and talent. To address these bottlenecks, the author advocates for a strategic shift toward a product mindset and incremental modernization instead of high-risk, wholesale replacements. Recommended fixes include mapping system dependencies, quantifying inefficiencies, and following a clear roadmap that progresses from stabilization to systematic optimization. By decoupling tightly integrated components and establishing clear ownership, enterprises can transform their brittle legacy systems into scalable, resilient assets. Fostering a culture of continuous improvement and aligning digital transformation with core business objectives are equally vital for survival. Ultimately, the piece emphasizes that overcoming outdated digital systems is a strategic necessity in a fast-paced market, requiring a balanced approach to technical remediation and organizational change to ensure long-term competitiveness.


COBOL developers will always be needed, even as AI takes the lead on modernization projects

The article from ITPro explores the enduring necessity of COBOL developers amidst the rise of artificial intelligence in legacy modernization projects. While AI is increasingly being marketed as a "silver bullet" for converting ancient COBOL codebases into modern languages like Java, industry experts argue that these digital transformations cannot succeed without human domain expertise. COBOL remains the backbone of global financial and administrative systems, housing decades of intricate business logic that AI often fails to interpret accurately. The piece emphasizes that while generative AI can significantly accelerate code translation and documentation, it lacks the contextual understanding required to define what a successful transformation actually looks like. Consequently, veteran developers are essential for overseeing AI-driven migrations, identifying potential risks, and ensuring that the logic preserved in the legacy system is correctly replicated in the new environment. Rather than replacing the workforce, AI acts as a collaborative tool that shifts the developer's role from manual coding to strategic orchestration. Ultimately, the survival of critical infrastructure depends on a hybrid approach that combines the speed of machine learning with the deep-seated knowledge of COBOL specialists, proving that legacy expertise is more valuable than ever in the modern era.


The CTO is dead. Long live the CTO

In the article "The CTO is dead. Long live the CTO" on CIO.com, Marios Fakiolas argues that the traditional role of the Chief Technology Officer as a technical gatekeeper and "human compiler" has become obsolete due to the rise of advanced AI. Modern Large Language Models can now design complex system architectures in minutes, outperforming humans in handling multidimensional constraints and technical interdependencies. Consequently, the new era demands a "multiplier" who shifts focus from providing technical answers to architecting systems that enable continuous organizational intelligence. Today’s CTO is measured not by architectural purity, but by tangible business outcomes such as gross margin, ROI, and operational velocity. This evolution requires leaders to move beyond their "AI comfort zone" of fancy demos and instead tackle difficult structural challenges like cost optimization and team restructuring. The author emphasizes that the modern leader must lead from the front, ruthlessly killing legacy "darlings" and designing for impermanence rather than static stability. Ultimately, the successful CTO must transition from being a bottleneck to becoming an orchestrator of AI agents and human expertise, ensuring that the entire organization can pivot rapidly without trauma. By embracing this proactive mindset, technology leaders can transcend the gatekeeping era and drive meaningful innovation in a fierce, AI-driven market.


When insider risk is a wellbeing issue, not just a disciplinary one

In the article "When insider risk is a wellbeing issue, not just a disciplinary one" on Security Boulevard, Katie Barnett argues for a paradigm shift in how organizations manage insider threats. Moving beyond traditional framing—which often focuses on malicious intent and punitive disciplinary measures—the author highlights that many security incidents are actually the byproduct of employee stress, fatigue, and disengagement. In a modern work environment characterized by digital isolation and economic uncertainty, personal strains such as financial pressure or burnout can erode professional judgment, making individuals more susceptible to manipulation or unintentional policy violations. The piece emphasizes that relying solely on technical controls and monitoring is insufficient; these tools do not address the underlying human factors that lead to risk. Instead, Barnett advocates for a proactive approach where wellbeing is treated as a core pillar of organizational resilience. This involves training managers to recognize early behavioral warning signs, fostering a supportive culture where staff feel safe raising concerns, and creating interdepartmental cooperation between HR and security teams. Ultimately, the article posits that by integrating support and psychological safety into the security strategy, organizations can prevent incidents before they escalate, strengthening their overall security posture through empathy rather than just compliance.


What it takes to win that CSO role

In the CSO Online article "What it takes to win that CSO role," David Weldon explores the transformation of the Chief Security Officer position into a high-stakes C-suite role requiring board-level accountability. No longer a back-office function, the modern CSO operates at the critical intersection of technology, regulatory exposure, revenue continuity, and brand trust. Achieving success in this position demands a shift from being a "cost center" to a "trust center," where security is positioned as a strategic business enabler that supports revenue growth rather than just a preventative measure. Key requirements include deep expertise in identity and access management and a sophisticated understanding of emerging threats like shadow AI, data poisoning, and model risk. Beyond technical prowess, financial acumen is non-negotiable; aspiring CSOs must translate security investments into business value, such as reduced insurance premiums or contractual leverage. Communication is paramount, as the role involves constant negotiation and the ability to translate complex risks for non-technical stakeholders. Ultimately, winning the role requires aligning accountability with authority and demonstrating the operating depth to maintain business resilience during sustained outages. By evolving from a "no" person to a "how" person, successful CSOs ensure that security becomes a foundational pillar of organizational success and customer confidence.


Human-Centered AI Is Becoming A Leadership Imperative

In his Forbes article, "Human-Centered AI Is Becoming A Leadership Imperative," Rhett Power argues that while artificial intelligence offers unprecedented industrial opportunities, its successful implementation depends entirely on a shift from technical obsession to human-centric leadership. Power contends that unchecked AI deployment often fails because it ignores the social and cognitive arrangements necessary for technology to thrive. To bridge the widening gap between technological promise and actual business value, leaders must adopt three foundational principles: prioritizing desired business outcomes over specific tools, evolving training to support role-specific enablement, and treating human-centered design as a core competitive advantage. Power identifies a new leadership paradigm where executives must serve as visionary guides who align AI with human values, ethical guardians who ensure transparency and bias mitigation, and human advocates who prioritize employee experience. By focusing on augmenting rather than replacing human expertise, organizations can transform AI into a seamless collaborative partner that drives long-term resilience and innovation. Ultimately, the article emphasizes that the true value of AI lies in its ability to extend the reach of human judgment, making the integration of empathy and ethical oversight a non-negotiable requirement for modern executive accountability in a rapidly evolving digital landscape.


Employee Experience 2.0: AI as the Performance Engine of the Work Operating System

In the article "Employee Experience 2.0: AI as the Performance Engine of the Work Operating System," Jeff Corbin outlines an essential evolution in workplace management. While the first version of the Employee Experience (EX 1.0) focused on cross-departmental alignment between HR, IT, and Communications, the author argues that human capacity alone is no longer sufficient to manage the modern digital workspace. EX 2.0 introduces artificial intelligence as a "performance layer" that transforms the work operating system from a static framework into a self-optimizing engine. AI addresses critical challenges such as "digital friction"—where employees waste nearly 30% of their day searching through disconnected systems like SharePoint and ServiceNow—by acting as an automated editor for content governance. Beyond cleaning up data, AI-driven EX 2.0 enables hyper-personalization of communications and provides predictive analytics that can identify turnover risks or workflow bottlenecks before they escalate. By integrating AI as a core architectural component, organizations can move beyond manual coordination to create a frictionless environment that boosts engagement and productivity. Ultimately, the piece calls for leaders to upgrade their governance models, positioning AI not just as a tool, but as a collaborative partner that ensures the employee experience remains agile and effective in a technology-driven era.


The Next Era of UX and Analytics, and Merging Conversational AI with Design-to-Code

The article "The Transformation of Software Development: Smarter UI Components, the Next Era of UX and Analytics" explores the profound shift from static, reactive user interfaces to proactive, intelligent systems. Modern software development is evolving beyond standard component libraries toward "smarter" UI elements that leverage embedded analytics and machine learning to adapt to user behavior in real-time. This transformation allows digital interfaces to anticipate user needs, personalize layouts dynamically, and optimize complex workflows without manual intervention. By integrating sophisticated telemetry directly into front-end components, developers gain granular, actionable insights into performance and engagement, effectively bridging the gap between user experience and technical execution. This evolution significantly impacts the modern DevOps lifecycle, as development teams move from building isolated features to orchestrating continuous learning environments. The article further highlights that these intelligent components reduce the cognitive load for end-users by surfacing relevant information and simplifying intricate navigations. Ultimately, the synergy between advanced data analytics and front-end engineering is setting a new industry standard for digital excellence, where personalization and efficiency are core to the process. Organizations that embrace this era of "smarter" components will deliver highly tailored experiences that drive superior retention and user satisfaction in an increasingly competitive market.


Certificate lifespans are shrinking and most organizations aren’t ready

The article "Certificate lifespans are shrinking and most organizations aren't ready," featured on Help Net Security, outlines the critical challenges businesses face as TLS certificate validity periods compress from one year down to 47 days. John Murray of GlobalSign emphasizes that this rapid shift, driven by browser requirements, necessitates a complete overhaul of traditional manual certificate management. To avoid operational disruptions and outages, organizations must prioritize "discovery" as the foundational step, utilizing tools like GlobalSign's Atlas or LifeCycle X to inventory every certificate and platform. This proactive approach is not only vital for managing shorter lifecycles but also serves as essential preparation for the eventual migration to post-quantum cryptography. Murray suggests that manual spreadsheets are no longer sustainable; instead, businesses should adopt automation protocols like ACME and shift toward flexible, SAN-based licensing models to remove procurement friction. While larger enterprises may have dedicated PKI teams, mid-market and smaller organizations are at a higher risk of being caught off guard. By establishing automated renewal pipelines and closing the specialized knowledge gap in PKI expertise, companies can build a resilient security posture. Ultimately, the window for preparation is closing, and integrating automated lifecycle management is now a strategic imperative rather than a future luxury.


Agoda CTO on why AI still needs human oversight

In the Tech Wire Asia article, Agoda’s Chief Technology Officer, Idan Zalzberg, discusses the essential role of human oversight in an era dominated by artificial intelligence. While AI tools have significantly accelerated developer workflows and boosted productivity—with early experiments at Agoda showing a 27% uplift—Zalzberg emphasizes that these technologies remain supplementary. The primary challenge lies in the inherent unpredictability and non-deterministic nature of generative AI, which differs from traditional software by producing inconsistent outputs. Consequently, Agoda maintains a strict policy where human engineers remain fully accountable for all code, regardless of its origin. Quality control remains rigorous, utilizing the same static analysis and automated testing frameworks applied to human-written scripts. Zalzberg notes that the evolution of the engineering role shifts focus toward critical thinking, strategic decision-making, and "evaluation"—a statistical method for assessing AI performance. Beyond technical management, the article highlights how cultural attitudes toward risk influence AI adoption rates across different regions. Ultimately, Zalzberg argues that AI maturity is defined by a balanced approach: leveraging the speed of automation while ensuring that sensitive decisions—such as pricing or critical architecture—are governed by human judgment and a centralized gateway to manage security and costs effectively.

Daily Tech Digest - January 30, 2026


Quote for the day:

"In my experience, there is only one motivation, and that is desire. No reasons or principle contain it or stand against it." -- Jane Smiley


Crooks are hijacking and reselling AI infrastructure: Report

In a report released Wednesday, researchers at Pillar Security say they have discovered campaigns at scale going after exposed large language model (LLM) and MCP endpoints – for example, an AI-powered support chatbot on a website. “I think it’s alarming,” said report co-author Ariel Fogel. “What we’ve discovered is an actual criminal network where people are trying to steal your credentials, steal your ability to use LLMs and your computations, and then resell it.” ... How big are these campaigns? In the past couple of weeks alone, the researchers’ honeypots captured 35,000 attack sessions hunting for exposed AI infrastructure. “This isn’t a one-off attack,” Fogel added. “It’s a business.” He doubts a nation-state it behind it; the campaigns appear to be run by a small group. ... Defenders need to treat AI services with the same rigor as APIs or databases, he said, starting with authentication, telemetry, and threat modelling early in the development cycle. “As MCP becomes foundational to modern AI integrations, securing those protocol interfaces, not just model access, must be a priority,” he said.  ... Despite the number of news stories in the past year about AI vulnerabilities, Meghu said the answer is not to give up on AI, but to keep strict controls on its usage. “Do not just ban it, bring it into the light and help your users understand the risk, as well as work on ways for them to use AI/LLM in a safe way that benefits the business,” he advised.


AI-Powered DevSecOps: Automating Security with Machine Learning Tools

Here's the uncomfortable truth: AI is both causing and solving the same problem. A Snyk survey from early 2024 found that 77% of technology leaders believe AI gives them a competitive advantage in development speed. That's great for quarterly demos and investor decks. It's less great when you realize that faster code production means exponentially more code to secure, and most organizations haven't figured out how to scale their security practice at the same rate. ... Don't try to AI-ify your entire security stack at once. Pick one high-pain problem — maybe it's the backlog of static analysis findings nobody has time to triage, or maybe it's spotting secrets accidentally committed to repos — and deploy a focused tool that solves just that problem. Learn how it behaves. Understand its failure modes. Then expand. ... This is non-negotiable, at least for now. AI should flag, suggest, and prioritize. It should not auto-merge security fixes or automatically block deployments without human confirmation. I've seen two different incidents in the past year where an overzealous ML system blocked a critical hotfix because it misclassified a legitimate code pattern as suspicious. Both cases were resolved within hours, but both caused real business impact. The right mental model is "AI as junior analyst." ... You need clear policies around which AI tools are approved for use, who owns their output, and how to handle disagreements between human judgment and AI recommendations.


AI & the Death of Accuracy: What It Means for Zero-Trust

The basic idea is that as the signal quality degrades over time through junk training data, models can remain fluent and fully interact with the user while becoming less reliable. From a security standpoint, this can be dangerous, as AI models are positioned to generate confident-yet-plausible errors when it comes to code reviews, patch recommendations, app coding, security triaging, and other tasks. More critically, model degradation can erode and misalign system guardrails, giving attackers the opportunity exploit the opening through things like prompt injection. ... "Most enterprises are not training frontier LLMs from scratch, but they are increasingly building workflows that can create self-reinforcing data stores, like internal knowledge bases, that accumulate AI-generated text, summaries, and tickets over time," she tells Dark Reading.  ... Gartner said that to combat the potential impending issue of model degradation, organizations will need a way to identify and tag AI-generated data. This could be addressed through active metadata practices (such as establishing real-time alerts for when data may require recertification) and potentially appointing a governance leader that knows how to responsibly work with AI-generated content. ... Kelley argues that there are pragmatic ways to "save the signal," namely through prioritizing continuous model behavior evaluation and governing training data.


The Friction Fix: Change What Matters

Friction is the invisible current that sinks every transformation. Friction isn’t one thing, it’s systemic. Relationships produce friction: between the people, teams and technology. ... When faced with a systemic challenge, our human inclination is to blame. Unfortunately, we blame the wrong things. We blame the engineering team for failing to work fast enough or decide the team is too small, rather than recognize that our Gantt chart was fiction, which is an oversimplification of a complex dynamic. ... The fix is to pause and get oriented. Begin by identifying the core domain, the North Star. What is the goal of the system? For Fedex, it is fast package delivery. Chances are, when you are experiencing counterintuitive behavior, it is because people are navigating in different directions while using the same words. ... Every organization trying to change has that guy: the gatekeeper, the dungeon master, the self-proclaimed 10x engineer who knows where the bodies are buried. They also wield one magic word: No. ... It’s easy to blame that guy’s stubborn personality. But he embodies behavior that has been rewarded and reinforced. ... Refusal to change is contagious. When that guy shuts down curiosity, others drift towards a fixed mindset. Doubt becomes the focus, not experimentation. The organization can’t balance avoiding risk with trying something new. The transformation is dead in the water.


From devops to CTO: 8 things to start doing now

Devops leaders have the opportunity to make a difference in their organization and for their careers. Lead a successful AI initiative, deploy to production, deliver business value, and share best practices for other teams to follow. Successful devops leaders don’t jump on the easy opportunities; they look for the ones that can have a significant business impact. ... Another area where devops engineers can demonstrate leadership skills is by establishing standards for applying genAI tools throughout the software development lifecycle (SDLC). Advanced tools and capabilities require effective strategies to extend best practices beyond early adopters and ensure that multiple teams succeed. ... If you want to be recognized for promotions and greater responsibilities, a place to start is in your areas of expertise and with your team, peers, and technology leaders. However, shift your focus from getting something done to a practice leadership mindset. Develop a practice or platform your team and colleagues want to use and demonstrate its benefits to the organization. Devops engineers can position themselves for a leadership role by focusing on initiatives that deliver business value. ... One of the hardest mindset transitions for CTOs is shifting from being the technology expert and go-to problem-solver to becoming a leader facilitating the conversation about possible technology implementations. If you want to be a CTO, learn to take a step back to see the big picture and engage the team in recommending technology solutions.


The stakes rise for the CIO role in 2026

The CIO's days as back-office custodian of IT are long gone, to be sure, but that doesn't mean the role is settled. Indeed, Seewald and others see plenty of changes still underway. In 2026, the CIO's role in shaping how the business operates and performs is still expanding. It reflects a nuanced change in expectations, according to longtime CIOs, analysts and IT advisors -- and one that is showing up in many ways as CIOs become more directly involved in nailing down competitive advantage and strategic success across their organizations. ... "While these core responsibilities remain the same, the environment in which CIOs operate has become far more complex," Tanowitz added. Conal Gallagher, CIO and CISO at Flexera, said the CIO in 2026 is now "accountable for outcomes: trusted data, controlled spend, managed risk and measurable productivity. "The deliverable isn't a project plan," Gallagher said. "It's proof that the business runs faster, safer and more cost-disciplined because of the operating model IT enables." ... In 2026, the CIO role is less about being the technology owner and more about being a business integrator, Hoang said. At Commvault, that shift places greater emphasis on governance and orchestration across ecosystems. "We're operating in a multicloud, multivendor, AI-infused environment," she said. "A big part of my job is building guardrails and partnerships that enable others to move fast -- safely," she said. 


Inside the Shift to High-Density, AI-Ready Data Centres

As density increases, design philosophy must evolve. Power infrastructure, backup systems, and cooling can no longer be treated as independent layers; they have to be tightly integrated. Our facilities use modular and scalable power and cooling architectures that allow us to expand capacity without disrupting live environments. Rated-4 resilience is non-negotiable, even under continuous, high-density AI workloads. The real focus is flexibility. Customers shouldn’t be forced into an all-or-nothing transition. Our approach allows them to move gradually to higher densities while preserving uptime, efficiency, and performance. High-density AI infrastructure is less about brute force and more about disciplined engineering that sustains reliability at scale. ... The most common misconception is that AI data centres are fundamentally different entities. While AI workloads do increase density, power, and cooling demands, the core principles of reliability, uptime, and efficiency remain unchanged. AI readiness is not about branding; it’s about engineering and operations. Supporting AI workloads requires scalable and resilient power delivery, precision cooling, and flexible designs that can handle GPUs and accelerators efficiently over sustained periods. Simply adding more compute without addressing these fundamentals leads to inefficiency and risk. The focus must remain on mission-critical resilience, cost-effective energy management, and sustainability. 


Software Supply Chain Threats Are on the OWASP Top Ten—Yet Nothing Will Change Unless We Do

As organizations deepen their reliance on open-source components and embrace AI-enabled development, software supply chain risks will become more prevalent. In the OWASP survey, 50% of respondents ranked software supply chain failures number one. The awareness is there. Now the pressure is on for software manufacturers to enhance software transparency, making supply chain attacks far less likely and less damaging. ... Attackers only need one forgotten open-source component from 2014 that still lives quietly inside software to execute a widespread attack. The ability to cause widespread damage by targeting the software supply chain makes these vulnerabilities alluring for attackers. Why break into a hardened product when one outdated dependency—often buried several layers down—opens the door with far less effort? The SolarWinds software supply chain attack that took place in 2020 demonstrated the access adversaries gain when they hijack the build process itself. ... “Stable” legacy components often go uninspected for years. These aging libraries, firmware blocks, and third-party binaries frequently contain memory-unsafe constructs and unpatched vulnerabilities that could be exploited. Be sure to review legacy code and not give it the benefit of the doubt. ... With an SBOM in hand, generated at every build, you can scan software for vulnerabilities and remediate issues before they are exploited. 


What the first 24 hours of a cyber incident should look like

When a security advisory is published, the first question is whether any assets are potentially exposed. In the past, a vendor’s claim of exploitation may have sufficed. Given the precedent set over the past year, it is unwise to rely solely on a vendor advisory for exploited-in-the-wild status. Too often, advisories or exploitation confirmations reach teams too late or without the context needed to prioritise the response. CISA’s KEV, trusted third-party publications, and vulnerability researchers should form the foundation of any remediation programme. ... Many organisations will leverage their incident response (IR) retainers to assess the extent of the compromise or, at a minimum, perform a rudimentary threat hunt for indicators of compromise (IoCs) before involving the IR team. As with the first step, accurate, high-fidelity intelligence is critical. Simply downloading IoC lists filled with dual-use tools from social media will generate noise and likely lead to inaccurate conclusions. Arguably, the cornerstone of the initial assessment is ensuring that intelligence incorporates decay scoring to validate command-and-control (C2) infrastructure. For many, the term ‘threat hunt’ translates to little more than a log search on external gateways. ... The approach at this stage will be dependent on the results of the previous assessments. There is no default playbook here; however, an established decision framework that dictates how a company reacts is key.


NIST’s AI guidance pushes cybersecurity boundaries

For CISOs, what should matter is that NIST is shifting from a broad, principle-based AI risk management framework toward more operationally grounded expectations, especially for systems that act without constant human oversight. What is emerging across NIST’s AI-related cybersecurity work is a recognition that AI is no longer a distant or abstract governance issue, but a near-term security problem that the nation’s standards-setting body is trying to tackle in a multifaceted way. ... NIST’s instinct to frame AI as an extension of traditional software allows organizations to reuse familiar concepts — risk assessment, access control, logging, defense in depth — rather than starting from zero. Workshop participants repeatedly emphasized that many controls do transfer, at least in principle. But some experts argue that the analogy breaks down quickly in practice. AI systems behave probabilistically, not deterministically, they say. Their outputs depend on data that may change continuously after deployment. And in the case of agents, they may take actions that were not explicitly scripted in advance. ... “If you were a consumer of all of these documents, it was very difficult for you to look at them and understand how they relate to what you are doing and also understand how to identify where two documents may be talking about the same thing and where they overlap.”