Showing posts with label Shadow IT. Show all posts

Daily Tech Digest - October 29, 2026

Quote for the Day
“The most expensive software is the one that doesn’t meet the needs of its users.”
— Karl Wiegers
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

When prevention fails: Why cyber resilience is the next big test of trust

The article explains that even well‑protected organizations can be thrown into chaos when a serious cyberattack disrupts basic operations, leaving leaders unsure which systems or data can still be trusted. It argues that prevention alone is no longer enough, because no control is perfect and attackers often find ways around strong defenses. Cyber resilience, therefore, becomes the next major test of trust: the ability to keep essential functions running, recover safely, and restore confidence after an incident. The piece highlights that backups are only useful if they can be accessed securely and restored without contamination, and that recovery plans must assume that some systems — including backup environments — may be compromised. Drawing on NIST guidance, it outlines four goals for resilience: anticipating threats, withstanding disruption, recovering trustworthy systems, and adapting based on lessons learned. The article’s steady message is that resilience must be designed into systems from the start, not treated as an afterthought, because the real challenge after an attack is determining what can still be relied on.

Read Original Article →

Programming Languages and Choosing a Path

Learning a programming language is about learning how to translate your logic into a format a computer can understand. An algorithm outlines the solution to a problem, while a programming language simply provides the vocabulary and rules to express that solution. Knowing the syntax of a language will not automatically make your logic correct. Behind the scenes, languages use tools like compilers or interpreters to turn human-readable instructions into actions the computer hardware can execute. When choosing your first programming language, it is important to remember that there is no universal best choice. Languages are tools built for different jobs. For example, C++ is great for competitive programming, Java offers strong structure for enterprise systems, and Python is highly readable and ideal for data tasks. Instead of getting caught up in the search for the perfect language, beginners should pick one that aligns with their immediate goals and local support system. Learn enough basics to express your logic clearly, and then focus on mastering problem-solving, which is the true core skill of programming.
Read Original Article →
Article Thumbnail

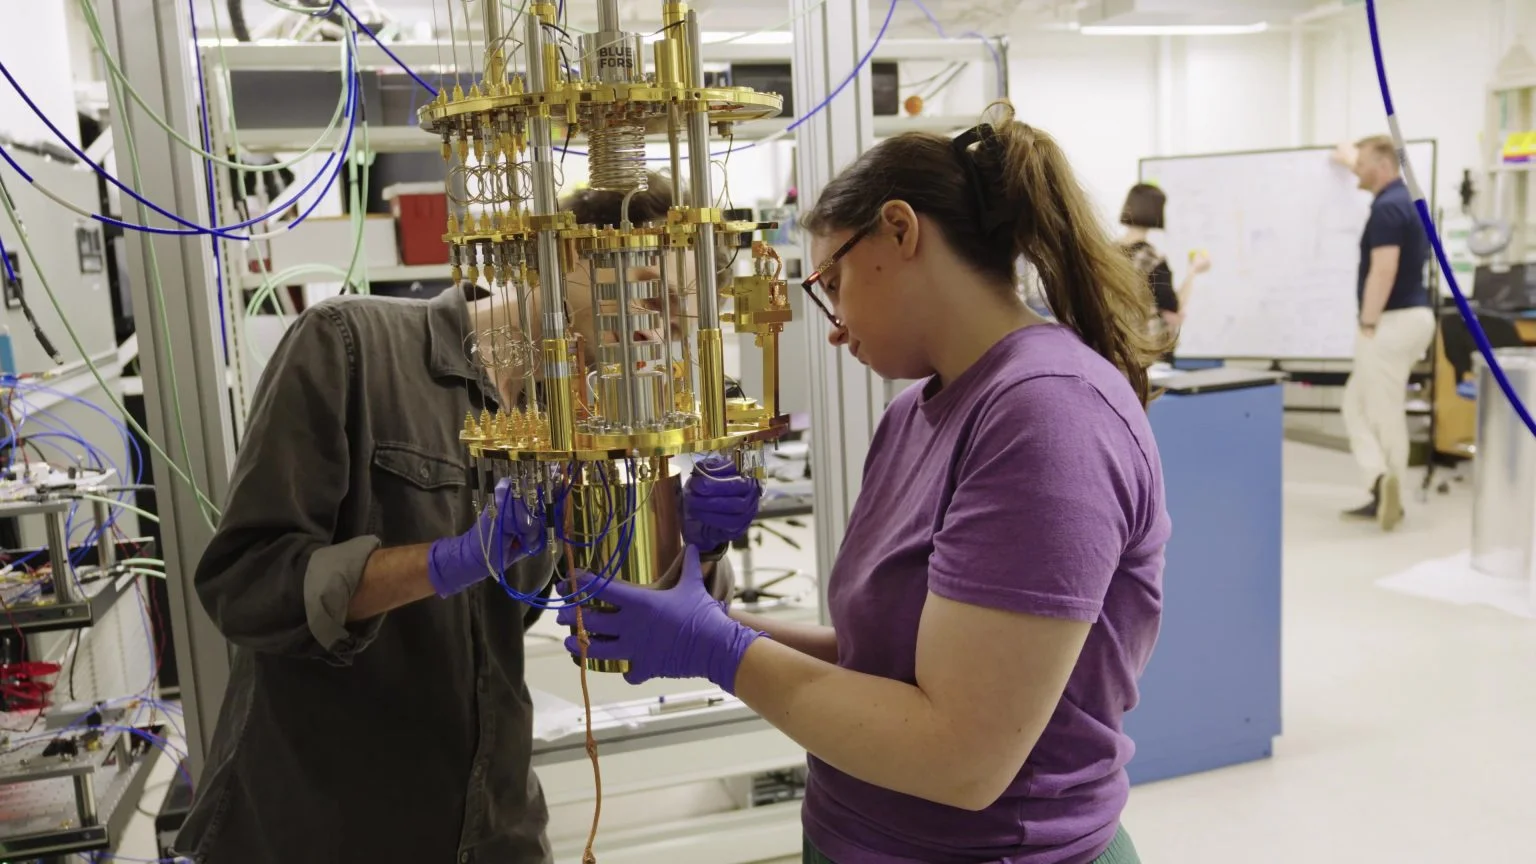
Beyond Binary Quantum Computing: Exploring Higher-Dimensional Qudits

Researchers at the University of Rochester, led by Professor Machiel Blok, are exploring a new approach to quantum computing using "qudits" instead of standard qubits. While traditional quantum computers rely on binary systems with just two energy states, qudits can store information across multiple levels. This concept mimics the natural world, where atoms and molecules naturally exist in multiple states. By matching the computer's structure to the physical problem it is trying to solve, the team believes qudits could offer a much more efficient way to tackle complex challenges in chemistry and physics. To make this work, the researchers developed a new method to control all energy transitions simultaneously, essentially building a denser, high-rise structure for information rather than a sprawling, flat one. Supported by reliable cooling technology, the lab also provides practical experience for students. Ultimately, this research suggests the future of quantum computing will likely rely on a mix of different systems tailored to specific problems, rather than a single binary approach.

Read Original Article →

Why Faster Algorithms Aren't Enough to Build High-Performance Data Platforms

The article argues that high‑performance data platforms cannot be created simply by swapping in faster algorithms or adding more hardware. Performance, it says, is an architectural outcome shaped by many upstream decisions about how data is represented, moved, stored, and delivered. Faster joins or better allocators help only at the margins; they cannot fix a system that is fundamentally slow because of poor layout, excessive data movement, or inefficient memory patterns. The piece highlights that modern platforms already rely on highly optimized libraries, so the real bottlenecks often appear between those functions — for example, when unnecessary tables are materialized, when workflows shuffle large datasets across layers, or when memory allocation becomes a long‑tail problem. It also notes that parallelizing work across CPU cores is relatively easy compared to designing a pipeline that avoids hidden costs in browsers, storage formats, or intermediate transformations. The steady message is that performance emerges from dozens of coordinated design choices, and no single algorithmic improvement can compensate for weak architectural foundations.
Read Original Article →
Article Thumbnail

Why decision-making is the next frontier of modern cyber resilience

The article explains that while many organizations have strong security tools and threat visibility, they still suffer vastly different outcomes during a cyberattack. This difference comes down to decision-making. Knowing a threat exists does not automatically tell leaders how to prioritize their limited resources or which systems to fix first. Standard security models improve accountability but often fail to connect technical risks with actual business goals. To close this gap, the author suggests adopting a decision system framework that translates threat data into clear, actionable choices. This approach evaluates risks based on their real-world impact on core business functions rather than just their technical severity. By blending financial realities, trust, and business priorities into the security process, leaders can make faster, better-coordinated choices during a crisis. Ultimately, effective security is no longer just about building taller walls or spotting potential attacks; it is about having a clear, reliable method to decide exactly where to act, what to protect first, and how to recover quickly when disruptions occur.

Read Original Article →

Wazuh and AI for Enhanced SOC Workflows

As cyber threats grow more complex, Security Operations Centers face an overwhelming volume of daily alerts that can easily cause analyst fatigue and missed critical events. To manage this workload, organizations are integrating artificial intelligence to support their security teams rather than replace them. Platforms like Wazuh address this need by offering flexible AI tools that streamline threat detection and response. For cloud users, the Wazuh AI Analyst automatically reviews security data using secure cloud models to deliver scheduled, comprehensive insights on vulnerabilities and overall security posture without exposing private data. For teams with strict privacy requirements, Wazuh supports self-hosted local models like Llama 3, keeping all log data safely within the company network. Alternatively, organizations can connect external models like Claude 3.5 Haiku directly into their dashboard to provide a helpful assistant for daily tasks. By handling repetitive analysis and data correlation, these AI integrations allow human analysts to focus on making the final decisions and keeping the organization secure.
Read Original Article →
Article Thumbnail

What Should a Business Do After a Personal Data Breach in India?

The article outlines the practical steps an Indian business should take immediately after discovering a personal data breach, emphasizing that quick, organized action matters more than panic. It begins with containment: isolating affected systems, revoking compromised credentials, and stopping further data loss. The next step is verification — confirming what happened, which data was exposed, and whether the breach is still active. The article stresses that businesses must document facts carefully because regulators will expect clear evidence of what was done and when. Under the DPDP Act, organizations must notify the Data Protection Board and affected individuals when harm is likely, and the article explains that vague or delayed communication can worsen legal and reputational consequences. It also highlights the need to preserve logs, review security controls, and assess whether vendors or third‑party processors contributed to the incident. The message is steady: a breach response is both a technical and governance exercise, and businesses must combine containment, transparency, and structured follow‑up to restore trust and meet regulatory expectations.

Read Original Article →

Shadow AI vs. Shadow IT: What's the Difference?

The article explains that “shadow AI” is emerging as a distinct and faster‑moving risk compared to traditional shadow IT. Shadow IT has long referred to employees using unapproved apps or services, often exposing data by storing it in places the organization cannot monitor. Shadow AI, however, introduces a sharper problem: employees feed internal data into AI tools — sometimes through personal accounts or new AI features inside already‑approved applications — without any governance. The piece notes that one in five organizations have already seen data exposure through personal AI accounts, showing how easily risky behavior can slip past existing controls. Unlike shadow IT, where data can often be retrieved or redirected, data given to an AI model may be processed, retained, or used for training in ways the organization cannot reverse. This shifts the governance challenge from simply discovering unauthorized apps to understanding what data enters AI systems, what outputs they generate, and what actions those systems can take. The article’s steady message is that AI requires new visibility, new controls, and a more nuanced approach than legacy shadow‑IT playbooks.
Read Original Article →
Article Thumbnail

When auditors come for your AI algorithms

As artificial intelligence increasingly influences critical business operations, traditional auditing methods are falling short. Conventional audits rely on predictable, step-by-step trails, but AI models—especially large language models—are inherently variable. This unpredictability makes it difficult for CIOs to explain how an AI system reached a specific conclusion, which frustrates auditors demanding clear evidence and accountability. The core problem often stems from vague ownership across different teams, rather than the technology itself. To bridge this gap, organizations must abandon point-in-time audits in favor of continuous monitoring and a structured accountability framework. This approach involves assessing risks during system design, continuously reviewing those risks as the technology evolves, and conducting independent evaluations of the process. Rather than waiting for a massive corporate AI rollout, leaders need to act now, as AI features are already embedded in everyday enterprise software. By treating audit readiness as a core business capability rather than a compliance chore, CIOs can take proactive ownership, reduce risk, and confidently support ongoing innovation.

Read Original Article →
Article Thumbnail

Building Review Intelligence into the SDLC with AI Agents and Archetypes

As artificial intelligence evolves beyond basic code generation, AI agents are becoming active collaborators throughout the software delivery lifecycle. Instead of replacing human architects, developers, and reviewers, these agents act as helpful partners that provide vital context and consistent feedback. To truly benefit from this shift, organizations should move past generic AI prompts and develop specialized, well-defined skills for design, architecture, and code reviews. These targeted skills can be organized into reusable patterns, or archetypes, tailored to specific tasks like building new applications, upgrading older systems, or migrating to the cloud. By employing a coordinated group of agents driven by strict checklists, a central agent can organize the workflow, while specialized agents handle security, performance, and compliance. A final review agent ensures all feedback is practical and backed by evidence. Ultimately, this structured approach transforms informal AI assistance into a reliable quality assurance process, allowing engineering teams to manage the increasing speed of modern software development with clarity and confidence.

Read Original Article →

Daily Tech Digest - May 17, 2026


Quote for the day:

“In tech, leadership isn’t about predicting the future — it’s about creating the conditions where your teams can build it.” -- Unknown

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Scale ‘autonomous intelligence’ for real growth

In an interview with Ryan Daws, Prakul Sharma, the AI and Insights Practice Leader at Deloitte Consulting LLP, explains that modern enterprises must look beyond the localized productivity gains of generative AI to scale "autonomous intelligence" for real business growth. Sharma describes an intelligence maturity curve transitioning from assisted and artificial intelligence into autonomous intelligence, where systems independently execute actions within predefined boundaries. To unlock true economic value, organizations must integrate these autonomous agents directly into critical, costly workflows like enterprise procurement. However, scaling successfully faces significant technical and structural hurdles. First, enterprises frequently lack decision-grade data, which means real-time, traceable information required for binding transactions, relying instead on outdated reporting-grade data. Second, the production gap and governance debt often stall live deployments, because shortcuts taken during small pilots become major barriers for corporate legal and compliance teams. Sharma advises leaders to conduct thorough decision audits of existing workflows to uncover operational bottlenecks and data gaps. By building pilots from the very outset as reusable platforms equipped with proper identity verification, continuous model evaluations, and robust risk frameworks, enterprises can securely transition from experimental testing to successful, widespread live deployment.


6 Technical Red Flags Product Managers Should Never Ignore

In the article "6 Technical Red Flags Product Managers Should Never Ignore," Seyifunmi Olafioye emphasizes that product managers must recognize signs of underlying technical instability, as it directly impacts delivery, scalability, and customer trust. The author identifies six major red flags that product managers should never overlook: a lack of clear understanding among the team regarding how the system works, new feature development consistently taking much longer than estimated, and resolved bugs repeatedly resurfacing in production. Additionally, product managers should be concerned if operational teams must rely heavily on manual workarounds to keep the platform functioning, if the entire project suffers from an over-reliance on a single engineer's institutional knowledge, or if internal errors are only discovered after users report them due to a lack of proper monitoring. While no system is entirely flawless, ignoring these persistent warning signs can lead to severe operational issues. The article concludes that product managers should not dictate technical fixes; instead, they must proactively initiate honest conversations with engineering leadership, ask challenging questions during planning, and prioritize long-term technical health alongside new features to ensure sustainable growth and protect the user experience.
In this article, Ed Leavens argues that Quantum Day, known as Q-Day, is the precise moment when quantum computers become advanced enough to break existing asymmetric encryption standards like RSA and ECC, presenting a far greater threat than Y2K. While Y2K had a definitive deadline and a known remedy, Q-Day has no set timeline and introduces the insidious risk of "harvest now, decrypt later" (HNDL) tactics. Under HNDL, adversaries secretly exfiltrate and stockpile encrypted data today, waiting to decrypt it once sufficiently powerful quantum technology becomes available. Furthermore, this threat compounds daily due to modern data sprawl across multiple environments. To counter this impending crisis, organizations must look beyond traditional encryption upgrades and adopt data-layer protection strategies like vaulted tokenization. This quantum-resilient approach mathematically separates original sensitive data from its representation by replacing it with non-sensitive, format-preserving tokens. Because tokens share no reversible mathematical connection with the underlying information, quantum algorithms cannot decipher them, effectively neutralizing the value of stolen payloads. Implementing vaulted tokenization requires comprehensive data discovery, strict access governance, and cross-functional organizational alignment. Ultimately, Leavens emphasizes that enterprises must act immediately to secure their data directly, rendering harvested information useless before quantum-powered breaches materialize.


The AI infrastructure bottleneck is becoming a CIO problem

The article by Madeleine Streets explores how the expanding ambitions of artificial intelligence are colliding with physical infrastructure limitations, shifting the AI bottleneck from a general tech industry challenge into a critical problem for Chief Information Officers (CIOs). While billions of dollars continue pouring into AI development, physical realities like power grid limitations, data center construction delays, permitting hurdles, and cooling requirements are struggling to match software demand. This mismatch threatens to create a more constrained operating environment where AI access becomes expensive, delayed, or regionally uneven. Consequently, this pressure exposes "AI sprawl" within organizations where uncoordinated and disconnected AI initiatives compete for the same resources without centralized governance. To mitigate these risks, experts suggest that CIOs treat AI capacity as a core operational resilience and business continuity issue. IT leaders must introduce disciplined governance by tiering AI workloads into critical, important, and experimental categories, or utilizing smaller, local models to reduce compute reliance. Furthermore, CIOs must demand greater transparency from vendors regarding capacity guarantees, regional availability, and workload prioritization during peak demand. Ultimately, enterprise AI strategies can no longer assume infinite compute availability and must instead realign their deployment ambitions with physical operational constraints.


How AI Is Repeating Familiar Shadow IT Security Risks

The rapid adoption of artificial intelligence across the corporate enterprise is triggering new governance and security risks that closely mirror past technological shifts, such as the initial emergence of shadow IT and unauthorized software as a service platform usage. Modern organizations currently face three primary vectors of vulnerability, starting with employees inadvertently leaking proprietary intellectual property, corporate source code, and confidential financial records by pasting this data into public generative AI platforms. Furthermore, software developers frequently introduce hidden backdoors or compromised dependencies into production systems by integrating unverified open source models and components that circumvent traditional software supply chain scrutiny. Compounding these operational issues is the sudden rise of autonomous AI agents that operate with dynamic decision making authority but completely lack explicitly defined ownership or documented permission boundaries within internal corporate networks. To successfully mitigate these vulnerabilities, blanket restrictive policies are typically ineffective; instead, companies must establish robust frameworks that ensure absolute visibility, accountability, and adaptive identity controls. As detailed in the SANS Institute’s new AI Security Maturity Model, managing these continuous threats requires treating artificial intelligence not as an isolated software application, but as a critical operational layer demanding proactive lifecycle validation and verification.


Six priorities reshaping the MENA boardroom in 2026

The EY report details how the 2026 macroeconomic landscape in the Middle East and North Africa (MENA) region requires corporate boardrooms to transition from traditional, periodic oversight toward integrated, forward-looking strategic leadership. Driven by overlapping pressures across geopolitics, rapid technological innovation, sustainability demands, and complex governance regulations, MENA boards face a highly volatile operating environment. To navigate this uncertainty and secure long-term value, directors must actively address six central boardroom priorities. First, boards need to develop geopolitical foresight, embedding regional shifts directly into strategic scenario planning. Second, they must manage the expanding technology and cyber assurance landscape, ensuring ethical artificial intelligence governance and robust defenses against escalating digital threats. Third, strengthening corporate integrity, fraud prevention, and independent investigation oversight remains essential for maintaining stakeholder trust. Fourth, elevating climate resilience and sustainability governance helps mitigate critical environmental risks while driving resource efficiency. Fifth, achieving financial excellence requires rigorous cost optimization and aligning internal controls across financial and sustainability reporting frameworks. Finally, adopting mature, behavioral-based board evaluations over mere procedural assessments fosters deep accountability. Ultimately, orchestrating these interconnected priorities empowers MENA leaders to fortify institutional trust and transform market disruptions into sustainable growth.


The software supply chain is the new ground zero for enterprise cyber risk. Don’t get caught short

In this article, Matias Madou highlights the rising vulnerabilities within the software supply chain as the new ground zero for enterprise cyber risks, heavily exacerbated by the rapid adoption of artificial intelligence tools. Recent highly sophisticated breaches, such as the TeamPCP supply chain attacks, have aggressively weaponized critical security and developer platforms like Checkmarx and the open-source library LiteLLM. By embedding highly obfuscated, multistage credential stealers into these trusted systems, attackers successfully moved laterally through development pipelines and Kubernetes clusters to exfiltrate highly sensitive enterprise data. Madou warns that traditional, reactive security measures are entirely insufficient against fast-moving, AI-driven threats. To mitigate these expanding dangers, organizations must redefine AI middleware as critical infrastructure, implementing rigorous monitoring of application programming interface keys and environment variables that constantly flow through these abstraction layers. Furthermore, security leaders must modernize risk management strategies by locking down dependency pipelines, enforcing strict least-privilege access, and gaining visibility into autonomous Model Context Protocol agents. Ultimately, the author urges modern enterprises to establish comprehensive internal AI governance frameworks and continuously upskill developers in secure coding standards rather than waiting for formal government legislation, thereby proactively shielding their operational workflows from devastating, cascading supply-chain compromises.


World Bank, African DPAs outline formula for trusted digital identity, DPI

During the ID4Africa 2026 Annual General Meeting, a key World Bank presentation emphasized that establishing public trust is vital for the success of digital public infrastructure and national identity systems across Africa. Experts noted that even mature digital identity networks remain vulnerable to operational failures and public mistrust due to weak data collection safeguards, frequent data breaches, and expanding cyberattack surfaces. To address these vulnerabilities, data protection authorities from nations like Liberia, Benin, and Mauritius highlighted that digital forensics, cybersecurity, and rigorous data governance must operate collectively. Although these under-resourced regulatory bodies often struggle to fund large population-scale awareness campaigns, they are pioneering localized solutions. For example, Mauritius leverages chief data officers and amicable dispute resolution mechanisms to efficiently settle compliance breaches without lengthy prosecution, while Benin relies on specialized government liaisons to ensure proper database compliance across different agencies. Furthermore, regional frameworks like the East African Community body facilitate international knowledge-sharing and joint investigative capabilities. Ultimately, achieving an ecosystem worthy of citizen and business trust requires a comprehensive formula blending careful system architecture, strictly enforced data protection, robust cybersecurity defenses, and transparent communication that effectively helps citizens understand their rights within the broader data lifecycle.


When configuration becomes a vulnerability: Exploitable misconfigurations in AI apps

The rapid deployment of artificial intelligence and agentic applications on cloud-native platforms, particularly Kubernetes clusters, often compromises cybersecurity in favor of operational speed. According to the Microsoft Defender Security Research Team, this trend has led to an increase in exploitable misconfigurations, which are scenarios where public internet access is paired with absent or weak authentication mechanisms. Rather than relying on sophisticated zero-day vulnerabilities, threat actors can leverage these low-effort attack paths to achieve high-impact compromises, including remote code execution, credential exfiltration, and unauthorized access to sensitive internal data. Microsoft identified these specific dangers across several popular AI platforms: Model Context Protocol servers frequently permitted unauthenticated interaction with corporate tools, Mage AI default setups enabled internet-accessible administrative shells, and frameworks like kagent and AutoGen Studio leaked plaintext API keys or allowed unauthorized workload deployments. To mitigate these pervasive security gaps, organizations must treat AI systems as high-impact workloads. Security teams should enforce strong authentication across all endpoints, apply strict least-privilege principles, and continuously audit infrastructure configurations. Furthermore, cloud protection tools like Microsoft Defender for Cloud can actively detect exposed services, helping defenders remediate dangerous oversights before malicious adversaries can exploit them.


Tokenized assets face trust infrastructure test, Cardano chief says

The article, titled "Tokenized assets face trust infrastructure test, Cardano chief says," by Jeff Pao, outlines a pivotal shift in the digital assets sector as financial institutions transition from tentative pilot projects to scaled, production-level tokenization. According to Cardano’s leadership, the primary challenges facing this widespread adoption are no longer the core blockchain mechanisms themselves, but rather the underlying hurdles of verification, identity, and robust auditability. These elements form a critical "trust infrastructure" that remains essential for creating compliant, institutional-grade financial networks. As real-world asset tokenization expands rapidly across global markets, traditional financial institutions require secure mechanisms like decentralized identifiers and privacy-preserving verifiable credentials to interact safely with public ledgers. By embedding accountability directly into the network architecture, digital trust frameworks turn complex compliance into seamless operational coordination, enabling institutions to efficiently manage counterparty exposure and automated settlement risks without exposing sensitive transactional data. Ultimately, the piece underscores that the long-term survival of decentralized finance relies heavily on resolving these identity and legal infrastructure gaps. Establishing a standardized trust layer will determine whether tokenized finance achieves mature stability or succumbs to institutional fragility and unresolved regulatory friction, marking a major turning point for future global capital flows.

Daily Tech Digest - December 24, 2025


Quote for the day:

"The only person you are destined to become is the person you decide to be." -- Ralph Waldo Emerson


When is an AI agent not really an agent?

If you believe today’s marketing, everything is an “AI agent.” A basic workflow worker? An agent. A single large language model (LLM) behind a thin UI wrapper? An agent. A smarter chatbot with a few tools integrated? Definitely an agent. The issue isn’t that these systems are useless. Many are valuable. The problem is that calling almost anything an agent blurs an important architectural and risk distinction. ... If a vendor knows its system is mainly a deterministic workflow plus LLM calls but markets it as an autonomous, goal-seeking agent, buyers are misled not just about branding but also about the system’s actual behavior and risk. That type of misrepresentation creates very real consequences. Executives may assume they are buying capabilities that can operate with minimal human oversight when, in reality, they are procuring brittle systems that will require substantial supervision and rework. Boards may approve investments on the belief that they are leaping ahead in AI maturity, when they are really just building another layer of technical and operational debt. Risk, compliance, and security teams may under-specify controls because they misunderstand what the system can and cannot do. ... demand evidence instead of demos. Polished demos are easy to fake, but architecture diagrams, evaluation methods, failure modes, and documented limitations are harder to counterfeit. If a vendor can’t clearly explain how their agents reason, plan, act, and recover, that should raise suspicion. 


Five identity-driven shifts reshaping enterprise security in 2026

Organizations that continue to treat identity as a static access problem will fall behind attackers who exploit AI-powered automation, credential abuse, and identity sprawl. The enterprises that succeed will be those that re-architect identity security as a continuous, data-aware control plane, one built to govern humans, machines, and AI with the same rigor, visibility, and accountability. ... Unlike traditional shadow IT, shadow AI is both more powerful and more dangerous. Employees can deploy advanced models trained on sensitive company data, and these tools often store or transmit privileged credentials, API keys, and service tokens without oversight. Even sanctioned AI tools become risky when improperly configured or connected to internal workflows. ... With AI-driven automation, sophisticated playbooks previously reserved for top-tier nation-states become accessible to countries, and non-state actors, with far fewer resources. This levels the playing field and expands the number of threat actors capable of meaningful, identity-focused cyber aggression. In 2026, expect more geopolitical disruptions driven by identity warfare, synthetic information, and AI-enabled critical infrastructure targeting. ... Machine identities have become the primary source of privilege misuse, and their growth shows no sign of slowing. As AI-driven automation accelerates and IoT ecosystems proliferate, organizations will hit a governance tipping point.2026 will force security teams to confront a tough reality. Identity-first security can’t stop with humans. 


Implementing NIS2 — without getting bogged down in red tape

NIS2 essentially requires three things: concrete security measures; processes and guidelines for managing these measures; and robust evidence that they work in practice. ... Therefore, two levels are crucial for NIS2: the technical measures and the evidence that they are effective. This is precisely where the transformation of recent years becomes apparent. Previously, concepts, measures, and specifications for software and IT infrastructures were predominantly documented in text form. ... The second area that NIS2 and the new Implementing Regulation 2024/2690 for digital services are enshrining in law is vulnerability management in the company’s own code and supply chain. This requires regular vulnerability scans, procedures for assessment and prioritization, timely remediation of critical vulnerabilities, and regulated vulnerability handling and — where necessary — coordinated vulnerability disclosure. Cloud and SaaS providers also face additional supply chain obligations ... The third area where NIS2 quickly becomes a paper tiger is the combination of monitoring, incident response, and the new reporting requirements. The directive sets clear deadlines: early warning within 24 hours, a structured report after 72 hours, and a final report no later than one month. ... NIS2 forces companies to explicitly define their security measures, processes, and documentation. This is inconvenient — ​​especially for organizations that have previously operated largely on an ad-hoc basis. 


Rethinking Anomaly Detection for Resilient Enterprise IT

Being armed with this knowledge is only the first step, though. The next challenge is detecting anomalies consistently and accurately in complex environments. This task is becoming increasingly difficult as IT environments undergo continuous digital transformation, shift towards hybrid-cloud setups, and rely on legacy systems that are well past their prime. These challenges introduce dynamic data, pushing IT leaders to rethink their anomaly detection processes. ... By incorporating seasonal patterns, user behavior, and workload types, adaptive baselines filter out the noise and highlight genuine deviations. Another factor to integrate is the overall context of a situation. Metrics rarely operate in isolation. During planned deployment, it would be anticipated for a spike in network latency. This same spike would be seen completely differently if it were to occur during steady operations. By combining telemetry with contextual signals, anomaly detection systems can separate the expected from the unexpected. ... Anomaly detection is meant to strengthen operations and improve overall resilience. However, it is not capable of delivering on this promise when teams are constantly swimming through the seas of generated alerts. By contextually and comprehensively adopting new approaches to the variety of anomalies, systems can identify root causes, uniformly correct systemic failures created from multiple metrics points, and mitigate the risk of outages.


Bridging the Gap: Engineering Resilience in Hybrid Environments (DR, Failover, and Chaos)

Resilience in a hybrid environment isn't just about preventing failure; it’s about enduring it. It requires moving beyond hope as a strategy and embracing a tripartite approach: Robust Disaster Recovery (DR), automated Failover, and proactive Chaos Engineering. ... Disaster Recovery is your insurance policy for catastrophic events. It is the process of regaining access to data and infrastructure after a significant outage—a hurricane hitting your primary data center, a massive ransomware attack, or a prolonged regional cloud failure. ... While DR handles catastrophes, Failover handles the everyday hiccups. Failover is the (ideally automatic) process of switching to a redundant or standby system upon the failure of the primary system, mostly automatic. Failover mechanisms in a hybrid environment ensure immediate operational continuity by automatically switching workloads from a failed primary system (on-premises or cloud) to a redundant secondary system with minimal downtime. This requires coordinating recovery across cloud and on-premises platforms. ... Chaos engineering is a proactive discipline used to stress-test systems by intentionally introducing controlled failures to identify weaknesses and build resilience. In hybrid environments—which combine on-premises infrastructure with cloud resources—this practice is essential for navigating the added complexity and ensuring continuous reliability across diverse platforms.


Should CIOs rethink the IT roadmap?

As technology consultancy West Monroe states: “You don’t need bigger plans — you need faster moves.” This is a fitting mantra for IT roadmap development today. CIOs should ask themselves where the most likely business and technology plan disrupters are going to come from. ... Understandably, CIOs can only develop future-facing technology roadmaps with what they see at a present point in time. However, they do have the ability to improve the quality of their roadmaps by reviewing and revising these plans more often. ... CIOs should revisit IT roadmaps quarterly at a minimum. If roadmaps must be altered, CIOs should communicate to their CEOs, boards, and C-level peers what’s happening and why. In this way, no one will be surprised when adjustments must be made. As CIOs get more engaged with lines of business, they can also show how technology changes are going to affect company operations and finances before these changes happen ... Equally important is emphasizing that a seismic change in technology roadmap direction could impact budgets. For instance, if AI-driven security threats begin to impact company AI and general systems, IT will need AI-ready tools and skills to defend and to mitigate these threats. ... Now is the time for CIOs to transform the IT roadmap into a more malleable and responsive document that can accommodate the disruptive changes in business and technology that companies are likely to experience.


Why shadow IT is a growing security concern for data centre teams

It is essential to recognise that employees use shadow IT to get their work done efficiently, not to deliberately create security risks. This should be front of mind for any IT teams and data centre consultants involved in infrastructure design and security provision. Finding blame or taking an approach that blocks everything does not work. A more effective way to address shadow IT use is to invest for the long term in a culture which promotes IT as a partner to workplace productivity, not something which is a hindrance. Ideally, this demands buy-in from senior management. Although it falls to IT teams to provide people with the tools for their jobs, providing choice, listening to employees’ requests and offering prompt solutions, will encourage the transparency so much needed for IT to analyse usage patterns, identify potential issues and address minor issues before they grow into costly problems. Importantly, this goes a long way towards embracing new technologies and avoiding employees turning to shadow IT that they find and use without approval. ... While IT teams are focused on gaining visibility and control over the software, hardware and services gainfully used by their organisations, they also need to be careful not to stifle innovation. It is here that data centre operators can share ideas on ways to best achieve this balance, as there is never going to be one model that suits every business. 


From Digitalization to Intelligence: How AI Is Redefining Enterprise Workflows

In the AI economy, digitalization plays another important role—turning paper documents into data suitable for LLM engines. This will become increasingly important as more sites restrict crawlers or require licensing, which reduces the usable pool of data. A 2024 report from the nonprofit watchdog Epoch AI projected that large language models (LLMs) could run out of fresh, human-generated training data as soon as 2026. Companies that rely purely on publicly available crawl data for continuous scaling likely will encounter diminishing returns. To avoid the looming publicly accessed data shortage, enterprises will need to use their digitized documents and corporate data to fine‐tune models for domain specific tasks rather than rely only on generic web data. Intelligent capture technologies can now recognize document types, extract key entities, and validate information automatically. Once digitized, this data flows directly into enterprise systems where AI models can uncover insights or predict outcomes. ... Automation isn’t just about doing more with less; it’s about learning from every action. Each scan, transaction, or decision strengthens the feedback loop that powers enterprise AI systems. The organizations recognizing this shift early will outpace competitors that still treat data capture as a back-office function. The winners will be those that turn the last mile of digitalization into the first mile of intelligence.


Boardrooms demand tougher AI returns & stronger data

Budget scrutiny is increasing as wider economic conditions remain uncertain and as organisations review early generative AI experiments. "AI investment is no longer about FOMO. Boards and CFOs want answers about what's working, where it's paying off, and why it matters now. 2026 will be a year of focus. Flashy experiments and perpetual pilots will lose funding. Projects that deliver measurable outcomes will move to the center of the roadmap," said McKee, CEO, Ataccama. ... "For years people have predicted that AI will hollow out data teams, yet the closer you get to real deployments, the harder that story is to believe. Once agents take over the repetitive work of querying, cleaning, documenting, and validating data, the cost of generating an insight will begin falling toward zero. And when the cost of something useful drops, demand rises. We've seen this pattern with steam engines, banking, spreadsheets, and cloud compute, and data will follow the same curve," said Keyser. Keyser said easier access to data and analysis is likely to change behaviours in business units that have not traditionally engaged with central data groups. He expects a rise in AI-literate staff across operational functions and a larger need for oversight. ... The organizations that adopt agents will discover something counterintuitive. They won't end up with fewer data workers, but more. This is Jevons paradox applied to analytics. When insight becomes easier, curiosity will expand and decision-making will accelerate.


The Blind Spots Created by Shadow AI Are Bigger Than You Think

If you think it’s the same as the old “shadow IT” problem with different branding, you’re wrong. Shadow AI is faster, harder to detect, and far more entangled with your intellectual property and data flows than any consumer SaaS tool ever was. ... Shadow AI is not malicious in nature; in fact, the intent is almost always to improve productivity or convenience. Unfortunately, the impact is a major increase in unplanned data exposure, untracked model interactions, and blind spots across your attack surface. ... Most AI tools don’t clearly explain how long they keep your data. Some retrain on what you enter, others store prompts forever for debugging, and a few had almost no limits at all. That means your sensitive info could be copied, stored, reused for training, or even show up later to people it shouldn’t. Ask Samsung, whose internal code found its way into a public model’s responses after an engineer uploaded it. They banned AI instantly. Hardly the most strategic solution, and definitely not the last time you’ll see this happen. ... Shadow AI bypasses Identity controls, DLP controls, SASE boundaries, Cloud logging, and Sanctioned inference gateways. All that “AI data exhaust” ends up scattered across a slew of unsanctioned tools and locations. Your exposure assessments are, by default, incomplete because you can’t protect what you can’t see. ... Shadow AI has changed from an occasional or unusual instance case to everyday behavior happening across all departments.

Daily Tech Digest - November 03, 2025


Quote for the day:

"With the new day comes new strength and new thoughts." -- Eleanor Roosevelt


Smaller, Smarter, Faster: AI Will Scale Differently in 2026

"Technology leaders face a pivotal year in 2026, where disruption, innovation and risk are expanding at unprecedented speed," said Gene Alvarez, distinguished vice president analyst at Gartner. "The top strategic technology trends identified for 2026 are tightly interwoven and reflect the realities of an AI-powered, hyperconnected world where organizations must drive responsible innovation, operational excellence and digital trust." The centerpiece of that thesis is the pivot from large, general-purpose LLMs to domain-specific language models, or DSLMs, and modular multiagent systems, MAS, designed to execute and audit business workflows. DSLMs promise higher accuracy, lower downstream compliance risk and cheaper inference costs; MAS promise orchestration and scale. ... The back half of Gartner's report is a sober reminder of the price of admission. First is geopatriation. This is the C-suite-level trend of yanking critical data and apps out of global public clouds and moving them to local or "sovereign" clouds. Driven by regulations like Europe's GDPR and fears over the US CLOUD Act, this market is exploding. Second, the security model is flipping. Gartner's Preemptive Cybersecurity trend predicts a massive shift, forecasting that 50% of IT security spending will move from "detection and response" to "proactive protection" by 2030, up from less than 5% in 2024. 


Today’s security leaders must adopt an asymmetric mindset

We’ve built an unbalanced view of threats. We pour resources into the risks we know how to manage — firewalls, access control, guard contracts — while neglecting the ones that move fastest and cut deepest: hybrid, cross-domain, and narrative-driven threats. Consider the Salt Typhoon campaign in 2024. State-linked actors compromised multiple U.S. telecom networks for nearly a year, breaching routers, core systems, and even National Guard networks. What began as a cyber incident rippled across national security. Or, the hybrid criminal case in which a fake recruiter on LinkedIn lured a corporate employee into downloading malware while coordinating physical intimidation. Digital, physical, and psychological tactics in one operation. ... Asymmetric actors win by exploiting tempo, surprise, and blind spots. As the former U.S. Army Asymmetric Warfare Group explained, its mission was to “identify critical asymmetric threats… through global first-hand observations,” enabling rapid adaptation in a shifting threat environment. That’s the same level of insight security leaders should demand whether from small teams or entire corporations. They don’t respect our categories. They will hit us digitally, physically, and reputationally in whatever sequence maximizes confusion and slows our response. They’ll use low-cost tools to cause high-cost damage: small moves, outsized effects.


Employees keep finding new ways around company access controls

AI, SaaS, and personal devices are changing how people get work done, but the tools that protect company systems have not kept up, according to 1Password. Tools like SSO, MDM, and IAM no longer align with how employees and AI agents access data. The result is what researchers call the “access-trust gap,” a growing distance between what organizations think they can control and how employees and AI systems access company data. The survey tracks four areas where this gap is widening: AI governance, SaaS and shadow IT, credentials, and endpoint security. Each shows the same pattern of rapid adoption and limited oversight. ... Organizations now rely on hundreds of cloud apps, most outside IT’s visibility. Over half of employees admit they have downloaded work tools without permission, often because approved options are slower or lack needed features. This behavior drives SaaS sprawl. 70% of security professionals say SSO tools are not a complete solution for securing identities. On average, only about two-thirds of enterprise apps sit behind SSO, leaving a large portion unmanaged. Offboarding gaps make the problem worse. 38% of employees say they have accessed a former employer’s account or data after leaving the company. ... Mobile Device Management remains the default control for company hardware, but security leaders see its limits. MDM tools do not adequately safeguard managed devices or ensure compliance.


Securing APIs at Scale: Threats, Testing, and Governance

API security must be approached as a fundamental element of the design and development process, rather than an afterthought or add-on. Many organizations fall short in this regard, assuming that security measures can be patched onto an existing system by deploying security devices like Web Application Firewall (WAF) at the perimeter. In reality, secure APIs begin with the first line of code, integrating security controls throughout the design lifecycle. Even minor security gaps can result in significant economic losses, legal repercussions, and long-term brand damage. Designing APIs with inadequate security practices introduces risks that compound over time, often becoming a time bomb for organizations. ... APIs are attractive targets for attackers because they expose business logic, data flows, and authentication mechanisms. According to Salt Security, 94% of organizations experienced an API-related security incident in the past year. The threats facing APIs are constantly evolving, becoming more sophisticated and targeted. ... Given the complexity and scale of API ecosystems, a proactive and comprehensive testing strategy is crucial. Relying solely on manual testing is no longer sufficient; automation is key. ... Technical controls are vital, but without a strong governance framework, API security efforts can quickly unravel. Without governance, APIs become a “wild west” of inconsistent standards, duplicated efforts, and accidental exposure. 


The Agentic evolution, How Autonomous AI is Re-Architecting the Enterprise

The rise of Agentic AI is leading to a new kind of enterprise that functions more like a living system. In this model, AI agents and humans work together as collaborators. The agents handle ongoing operations and optimize outcomes, while humans provide strategy, creativity, and oversight. Organizations that can successfully combine human intelligence with machine autonomy will lead the next era of business transformation. They will move faster, adapt quicker, and make better use of their data and resources. The Agentic Leap is not only about new technology; it represents a deeper change in how enterprises think and operate. It marks the beginning of organizations that are not only supported by AI but are actively driven and shaped by it. This traditional hierarchy of command is gradually evolving into a network of intelligent collaboration, where humans and AI systems continuously exchange information, refine strategies, and act with shared intent. In this model, humans and AI agents function as true partners. Agents operate as intelligent executors and problem-solvers, constantly monitoring data flows, identifying opportunities, and adapting operations in real time. They can handle repetitive, data-intensive tasks, freeing humans to focus on higher-order functions such as strategic planning, creative innovation, and ethical oversight. Humans, in turn, provide contextual understanding, emotional intelligence, and long-term vision qualities that anchor AI-driven actions in purpose and responsibility.


6 essential rules for unleashing AI on your software development process - and the No. 1 risk

"AI is not something you can pull out of your toolbox and expect magical things to happen," cautioned Andrew Kum-Seun, research director at Info-Tech Research Group. "At least, not right now. IT managers must be prepared to address the human, workflow, and technical implications that naturally come with AI while being honest about what AI can do today for their organization." In other words, get your AI implementation in order before you attempt to apply it to getting your software development in order. ... As Agile is meant to maintain humanity in software development, AI needs to support this vision. This must be a core component of AI-driven Agile development as well. "If leaders are unable to bridge their intent for AI with the team's concerns, they will likely see improper use of AI and, perhaps, deliberate sabotage in its implementation," said Kum-Seun. Another important step is to "keep all AI explainable by ensuring the use of AI tools that clearly cite where their suggestions come from -- no black-box code that cannot be simply verified," said Sopuch. "Human oversight is a required step. AI can write and refactor code, but humans absolutely must approve merges, product pushes, or any exceptions. Everything in the process must be logged, including prompts, outputs, and approvals so that an audit can easily take place on demand."


The AWS outage post-mortem is more revealing in what it doesn’t say

When AWS suffered a series of cascading failures that crashed its systems for hours in late October, the industry was once again reminded of its extreme dependence on major hyperscalers. The incident also shed an uncomfortable light on how fragile these massive environments have become. In Amazon’s detailed post-mortem report, the cloud giant detailed a vast array of delicate systems that keeps global operations functioning — at least, most of the time. ... “The outage exposed how deeply interdependent and fragile our systems have become. It doesn’t provide any confidence that it won’t happen again. ‘Improved safeguards’ and ‘better change management’ sound like procedural fixes, but they’re not proof of architectural resilience. If AWS wants to win back enterprise confidence, it needs to show hard evidence that one regional incident can’t cascade across its global network again. Right now, customers still carry most of that risk themselves.” ... Ellis agreed with others that AWS didn’t detail why this cascading failure happened on that day, which makes it difficult for enterprise IT executives to have high confidence that something similar won’t happen in a month. “They talked about what things failed and not what caused the failure. Typically, failures like this are caused by a change in the environment. Someone wrote a script and it changed something or they hit a threshold. It could have been as simple as a disk failure in one of the nodes. I tend to think it’s a scaling problem.”


Five Real-World Ways AI Can Boost Your Bank’s Operations

Use of artificial intelligence decisioning has already had time to prove itself, and the results have been strong, according to Daryl Jones, senior director. The fit varies from one institution to another, "but the lift, overall, has been unquestionable," said Jones. He said institutions using AI in lending decisions have generally seen healthy increases in approvals, with solid results. One caveat is that as aspects of loan decisions transition to AI, institutions have to be careful how human lenders influence the software development process. ... Technology has long been a mainstay for antifraud, according to John Meyer, managing director. "We’ve had machine learning algorithms since the 1990s," said Meyer, but today’s antifraud applications of AI go a step beyond. He explained that the old technology could evaluate a few data points "on day two," once the damage was already done. By contrast, AI-based techniques can screen and surface instances truly needing human evaluation, according to Meyer. Such applications include verifying that paper checks are genuine. Meyer noted that check fraud remains a significant issue for the banking industry in spite of the rise of digital transactions. ... Even in a modern banking office, documents can be a rat’s nest. "We had a client on the West Coast that wanted to centralize all of its operational documents," said Clio Silman, managing director. 


Context engineering: Improving AI by moving beyond the prompt

It isn’t a new practice for developers of AI models to ingest various sources of information to train their tools to provide the best outputs, notes Neeraj Abhyankar, vice president of data and AI at R Systems, a digital product engineering firm. He defines the recently coined term context engineering as a strategic capability that shapes how AI systems interact with the broader enterprise. ... Context engineering will be critical for autonomous agents trusted to perform complex tasks on an organization’s behalf without errors, he adds. ... Context engineering is an “architectural shift” in how AI systems are built, adds Louis Landry, CTO at data analytics firm Teradata. “Early generative AI was stateless, handling isolated interactions where prompt engineering was sufficient,” he says. “However, autonomous agents are fundamentally different. They persist across multiple interactions, make sequential decisions, and operate with varying levels of human oversight.” He suggests that AI users are moving away from the approach of, “How do I ask this AI a question?” to “How do I build systems that continuously supply agents with the right operational context?” “The shift is toward context-aware agent architectures, especially as we move from simple task-based agents to autonomous agentic systems that make decisions, chain together complex workflows, and operate independently,” Landry adds.


India’s Search for Digital Sovereignty

states are seeking to impose varying degrees of control over the internet. Often, these manifest as restrictions on information flows, which have consequences for civil liberties such as speech, expression, dissent, and the exchange of ideas in society. And, in a time when both geopolitical and domestic actors, state and non-state alike, cynically exploit open societies to exacerbate polarization and dehumanization, calls for greater control might seem appealing. However, it is vital that attempts to curb the concentration of power and resources of one set of actors do not merely transfer those same powers to another set. On the contrary, the goal should be to dissipate dominance, in general. ... It is not that alternative pathways to reduce concentration do not exist. Free and open source software, though not without its own challenges, is an approach that many can choose. Kailash Nadh, one of the founders of the FOSS United Foundation, has argued that for India to achieve technological self-determination, it needed to “publicly acknowledge” FOSS, and invest “time, effort and resources into” it. In late August, perhaps in a nod to the Microsoft-Nayara situation, LibreOffice positioned itself as a “Strategic Asset for Governments and Enterprises Focused on Digital Sovereignty and Privacy.” When it comes to information distribution and consumption, decentralized social networks and ideas such as “middleware” have existed for several years, but have yet to gain traction in India’s policy discourse.