Showing posts with label data governance. Show all posts

Daily Tech Digest - October 09, 2026


Quote for the day:

"An inch of movement will bring you closer to your goals than a mile of intention." -- Vala Afshar

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 29 mins • Perfect for listening on the go.


Making the Case to the Board for Post-Quantum Readiness
When presenting post-quantum readiness to the board, technology leaders must avoid technical physics jargon and instead frame the conversation entirely around business exposure. Directors do not need a lesson on qubits; they need to understand which critical services and data are vulnerable and what the transition will cost. A primary concern is the “harvest now, decrypt later” tactic, where attackers steal encrypted sensitive data today to break it when quantum capabilities mature. Because sensitive information retains its value for decades, the threat is immediate. Leaders should avoid predicting an exact date for when quantum computers will break current encryption. The focus should remain on the long lead time required for migration, which can span up to fifteen years. To secure board approval, leaders should ask for funding in manageable stages. The initial request should focus on discovery, giving the team about eighteen months to assess vulnerable cryptography, identify critical services, and map third-party dependencies before proposing a massive enterprise-wide budget. Waiting only increases the final price tag and risk. Ultimately, framing this as a staged, no-regrets investment builds trust and ensures the organization strengthens its overall security foundation regardless of when the quantum threat fully materializes.


AWS’s repeated problems with AI agent controls illustrates the autonomous agent dilemma

Recent security vulnerabilities in AWS AgentCore highlight a fundamental dilemma for enterprise technology leaders: the very autonomy that makes artificial intelligence agents useful also makes them inherently dangerous. Cybersecurity researchers from Palo Alto Networks and Zenity Labs repeatedly found that attackers could use simple prompt injections to trick these agents into handing over plain text credentials. Because agents require tools like shell commands and network access to function, they operate in the same environments where sensitive data is stored. In one severe example, researchers compromised a single agent and gained the ability to extract source code, access other agents, read private conversations, and persistently poison memory. This memory poisoning is particularly concerning because, unlike stolen credentials that can simply be rotated, altered memories quietly steer future actions and are incredibly difficult to detect. While AWS has worked to patch these specific entry points, the underlying issue is that the agents functioned exactly as designed by fulfilling the requests they received. This means the responsibility falls heavily on organizations. Technology teams must therefore strictly enforce proper access limits, closely monitor all agent behavior, and carefully control the potential damage to prevent a single compromised agent from exposing the entire network environment.
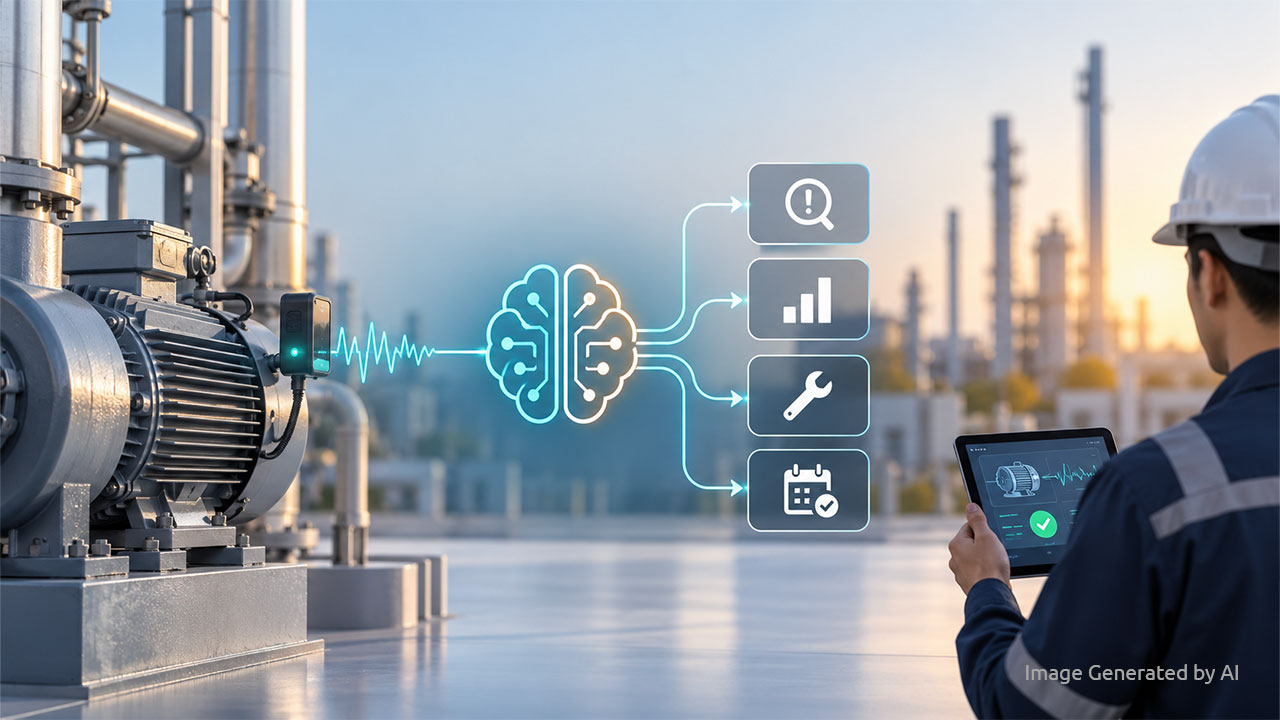
The article explores what manufacturing plants truly need to make prescriptive AI effective, drawing on eight audience questions answered by experts from Siemens and Infinite Uptime. A central theme is that most plants still struggle with data quality and availability, yet waiting for perfect data before deploying AI is unrealistic. The experts argue that physics‑informed models, combined with targeted sensor retrofits, allow plants to start generating reliable insights quickly, even in brownfield environments with decades‑old equipment. They explain that prescriptive AI works best when multiple sensing methods—such as vibration, thermal imaging, and machine vision—are combined to capture different failure modes. The discussion also breaks down how diagnosis should progress: anomaly detection first, then classification, and finally linking those classifications to documentation and automated “therapy” suggestions. Several questions focus on practical economics, including when it’s cheaper to replace a part than predict its failure and how much algorithm audits typically cost. The experts emphasize building quantitative decision models rather than relying on rules of thumb. The article closes by stressing data trust and security, noting that companies must use controlled environments for LLMs and treat AI‑generated data with the same rigor as physical products. The overall message is steady and pragmatic: prescriptive AI succeeds when physics, data, and human judgment work together.


The Clock Starts Before the Restore: Measuring Recovery Time and Data Recovery Capability

The article argues that organizations often measure disaster recovery performance in a way that hides the real delays that occur before anyone starts restoring systems. It opens with an anecdote from the 1970s, where a team could technically recover from a failure in five minutes but took more than thirty minutes to decide to act. The author explains that this gap still exists today because most recovery tests measure only the restoration phase, not the time spent detecting issues, triaging them, and making the decision to declare an incident. To fix this, he introduces the idea of Recovery Time Capability (RTC)—a single clock that starts at the first sign of trouble and ends when the service is verified as working again. RTC breaks recovery into six segments, each with its own time budget and owner, making it clear where delays occur. He also defines Data Recovery Capability (DRC), which measures how long it takes to make data whole and trusted, especially in “cold case” scenarios where replicas are damaged and data must be restored from immutable vaults. The article closes with practical steps: timestamp every segment, test decision‑making with unannounced exercises, measure cold‑case recovery annually, and report gaps clearly to the board. The message is steady and pragmatic—real recoveries fail in the early minutes and the long data‑repair hours, not in the scripted tests we usually run.


I audited an award-winning AI project. The case study left out the cloud bill

The article highlights the hidden financial realities of enterprise artificial intelligence projects when they transition from a pilot phase into full daily production. During an audit of a celebrated document automation workflow, the author uncovered a massive discrepancy between perceived success and actual operational expenses. In the pilot phase, the system drastically reduced turnaround times for vendor agreements, earning internal praise while a central innovation fund quietly absorbed the computing costs. However, once the project went live and expenses shifted to the departmental budget, a harsh reality surfaced. Processing a single document surged to cost between twelve and fourteen dollars in cloud consumption and model access fees, compared to just eighty cents under the previous manual human workflow. This staggering cost increase occurred because real world documents are often messy, featuring handwritten notes, poor scans, and conflicting formatting. These inconsistencies forced the automated pipeline to trigger multiple expensive retrieval passes and secondary checks. Furthermore, roughly forty percent of the documents required human intervention to fix errors, which ultimately doubled the original manual processing time. Ultimately, falling base model prices do not guarantee cheaper business processes, as complex workflows can easily turn a predictable payroll expense into an unpredictable consumption meter.


From digital insurance to intelligent insurance: Why AI is becoming the new operating layer

The article explains how AI is shifting insurance from a digital‑first model to an intelligent‑first one, where technology becomes part of the business rather than a support function. Sriram Naganathan of HDFC ERGO describes how underwriting, pricing, fraud detection, claims, and customer service are increasingly shaped by machine learning, generative AI, and agentic systems. The company’s digital foundation—where most policies and service interactions already happen online—has made it possible to layer intelligence on top of existing processes. Examples include GenAI tools that simplify policy explanations and AI‑guided motor claims assessments using smartphone photos. The piece stresses that AI should assist human decision‑making, not replace it, especially in high‑value or sensitive claims where context and empathy matter. It also highlights the shift from data scarcity to the challenge of converting large volumes of historical information into actionable intelligence. Governance, explainability, and trust emerge as essential themes as AI begins influencing pricing, underwriting, and fraud decisions. The article notes a move toward smaller, specialised models and internally built capabilities that embed institutional knowledge. It closes by arguing that the future is not autonomous insurance but augmented insurance—where AI reduces friction and improves accuracy while humans provide judgment, oversight, and empathy when it matters most.


India is defining ‘DPI 2.0’ as it shifts beyond identity and payments

The article explains how India is shaping “DPI 2.0,” the next phase of its digital public infrastructure, by moving beyond identity and payments toward sector‑wide digital systems built on open standards, user control, and AI‑enabled services. It traces how DPI 1.0—Aadhaar, UPI, DigiLocker, and Direct Benefit Transfer—created shared public rails that proved reliable at national scale. DPI 2.0 extends this model into areas such as commerce through ONDC, financial data through Account Aggregator, healthcare via ABDM, and agriculture through AgriStack. A central theme is giving people more control over their data, supported by the Digital Personal Data Protection Act, while ensuring interoperability across ecosystems. The article highlights India’s push to integrate AI into DPI so services can operate in local languages and through voice, making them more inclusive. It also acknowledges past failures, such as authentication errors, and notes that cybersecurity, algorithmic accountability, offline access, and digital literacy are now core priorities. Internationally, India promotes open protocols rather than proprietary platforms, allowing countries like Indonesia to adapt the model to their own needs. The piece closes by noting governance tensions at home, where DPI lacks a clear legal definition, raising questions about safeguards for population‑scale systems. Overall, DPI 2.0 is presented as an evolution focused on trust, interoperability, and intelligent public services.


How to Turn Data Governance into a Decision System

Data governance programs often focus exclusively on managing the data itself, prioritizing tasks like documenting definitions, mapping lineage, and improving quality scores. However, treating data as an isolated asset misses its true purpose, which is enabling better organizational choices. To maximize value, organizations must transition from merely governing data to actively governing the conditions that make data driven decisions trustworthy. This involves bridging two distinct value chains. The standard path from data to wisdom drives operational and strategic business choices, while a parallel path from metadata to wisdom provides the necessary context to trust those choices. By focusing on critical, high impact decisions rather than generic data inventories, organizations can completely reverse their traditional governance logic. Instead of finding uses for available data, teams identify the essential decisions they need to protect and then work backward to determine the specific data, rules, and controls required. Consequently, priority is determined by business impact rather than abstract maturity scores. Fixing a missing definition or uncontrolled transformation matters because it directly protects a regulatory outcome or commercial offer. Ultimately, this approach transforms data governance from a routine compliance exercise into a robust decision system, giving business leaders the concrete evidence they need to act with absolute clarity and reliability.


AI changed my role before it changed my software

Tony Timbol shares how building an AI-assisted application completely shifted his perspective on software development. While attempting to convert a cumbersome, spreadsheet-based agile assessment tool into a lightweight app using an AI platform, his initial attempts failed. He realized the issue was not the AI but his approach: he was treating the tool like a programmer rather than a collaborator. When he shifted his focus from specifying coding details to clearly defining outcomes, user journeys, and behaviors, the AI quickly generated a functioning prototype. This experience taught Timbol that AI accelerates the coding process but fundamentally relocates the challenging parts of software engineering rather than eliminating them. While AI can write code rapidly, it cannot handle crucial architectural choices, make strategic compromises, manage system integrations like email notifications or authentication, or understand genuine user needs. As execution becomes faster and easier through AI, the true bottleneck shifts to human judgment and product strategy. Timbol concludes that the future of software development involves humans acting as product leaders who frame the right problems, recognize sound architectural decisions, and provide the essential context that machines lack to build secure and maintainable products.


PCI SSC calls for human approval of AI agent actions involving cardholder data

The article outlines new guidance from the PCI Security Standards Council on how to use AI safely in payment environments, emphasizing that AI systems must be tightly controlled, monitored, and never allowed to act independently on sensitive cardholder data. The Council stresses that organizations should clearly define each AI system’s purpose, permissions, and data access before deployment, using a “least agency” approach that limits what the system can do. A human must remain accountable for all AI‑generated output, and certain actions—especially those involving cleartext payment data—should always require explicit human approval. The guidance warns against combining sensitive data access, external communications, and unrestricted input in a single AI agent, recommending separation of duties and strong identity‑management controls. It also calls for thorough adversarial testing, continuous monitoring, and documented shutdown and rollback procedures for AI systems operating with partial autonomy. The Council advises keeping high‑impact secrets, such as passwords and cryptographic keys, out of AI systems entirely and using tokenized or encrypted data whenever possible. It also highlights the growing risk of AI‑assisted attacks, urging organizations to harden legacy systems, validate AI‑generated code, and maintain strict patching processes. Finally, the guidance reminds companies to assess external AI providers carefully, prohibit training on customer data, and ensure clear incident‑response expectations.

Daily Tech Digest - October 05, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale


Data Has No Passport: Why Global Privacy Governance Must Catch Up With AI

At the CruiseCon Privacy and AI 2026 event, Accenture privacy lead Adriana Antunes Winkler highlighted a growing challenge: while data moves globally and instantly, privacy regulations remain fragmented and bound by local jurisdictions. With around eighty percent of the world covered by varying data protection frameworks, companies often struggle to keep up. Winkler advised against building separate privacy programs for every new law, as this causes confusion and conflict. Instead, she recommended a strategy built on a common global foundation with specific local adjustments only where legally necessary. This prevents the burden of simply applying the strictest rules everywhere. Winkler emphasized that operational controls, not just written policies, are what actually protect privacy. These controls require clear ownership, testing, and proof of function. The rise of artificial intelligence complicates this further, as AI often infers new personal details rather than just storing collected information. She suggested focusing on the specific actions AI takes and the systems it accesses, treating it as a data map driven by actions. Ultimately, whether data crosses international borders, runs through AI systems, or eventually processes in orbital satellites, organizations must rely on a unified, adaptable governance system that manages common standards while addressing specific local requirements.


Crypto-Agility Distrust Readiness

When major internet authorities decide to stop trusting a flawed digital certificate, the resulting fallout can cripple the countless services relying on it. While technical bodies like browser developers excel at making the call to pull a failing root certificate, there is currently no coordinated national plan for what happens to the broader economy the morning after. Historically, isolated incidents have been contained, but the dual threats of rapidly advancing artificial intelligence and a forced timeline for quantum-safe encryption mean that widespread disruptions are becoming more likely. The blast radius of a sudden distrust event can vary wildly across different sectors, and responding effectively requires advance preparation rather than improvisation. To survive this accelerating risk, organizations must create reliable certificate inventories, designate clear response liaisons, and run tabletop exercises to test their readiness. On a larger scale, a designated national coordinator is urgently needed to connect technical decision-makers with the sectors facing the consequences. Ultimately, building true resilience requires organizations to eliminate single points of trust by adopting multiple issuing authorities and automating certificate lifecycles, ensuring they can pivot smoothly when a crisis hits instead of scrambling to rebuild.


Measuring AI With the Wrong Ruler

When evaluating artificial intelligence systems, getting caught up in grand labels distracts from what truly matters: reliability, cost, and fitness for the job. The technology industry often assumes that larger, more capable models are inherently better, but deploying a massive system for a straightforward task is wasteful and risky. It is very similar to dropping a race car engine into a riding lawnmower. Raw power without proper control or necessity only creates hazards. Instead of obsessing over raw machine intelligence, which mirrors our flawed fixation on human IQ scores, we should focus on building operational wisdom. This means designing tools that clearly understand context, respect their own boundaries, and know exactly when to seek human intervention. Historical missteps in automotive software, where complex features completely overwhelmed inadequate hardware, prove that mismatched computing power leads to frustrating failures for end users. To make better decisions, organizations need a practical measurement framework that strictly aligns system complexity with the actual criticality of the task. By focusing on calibrated computing, businesses can ensure they deploy software with verifiable competence. This thoughtful approach prioritizes restraint, safety, and hardware capacity over industry hype, ultimately resulting in technology that simply works properly for its intended daily purpose.


Should cybersecurity be nationalised?

The conversation around digital safety is gradually shifting from treating it as a private expense to recognizing it as a public good. While full government ownership is not currently under consideration, experts argue that the traditional model of individual corporate defense is no longer sustainable. Today, private companies are routinely expected to fend off sophisticated attacks from foreign nations, a task for which most lack the necessary resources. Small businesses are particularly vulnerable and they often become the weak link that exposes broader networks to risk. Because hardening the defenses of one company inherently protects the wider community, securing digital infrastructure shares clear parallels with public utilities like street lighting. This shared benefit naturally raises important questions regarding funding and accountability. The emerging consensus suggests a model where the state might fund security measures that are executed by private firms, ensuring broader protection without complete nationalization. As this policy debate unfolds, organizations must adapt by viewing their security practices not merely as an internal budget item, but as a core component of public trust and reputation. Moving forward, businesses should firmly anticipate stricter sector requirements and expect to demonstrate baseline security standards simply to operate within shared modern networks.


IT modernization: Still a make-or-break project for CIOs

IT modernization remains a vital, ongoing mission for CIOs, taking on renewed urgency as artificial intelligence reshapes the technology landscape. The rise of AI and natural language tools means that systems built just a few years ago, such as traditional reporting dashboards and specialized chatbot software, may already be obsolete. IT leaders are now approaching modernization and application rationalization with a business-first strategy, evaluating tools not by their age, but by the tangible value and flexibility they provide. Consolidating software limits wasteful spending, reduces unneeded complexity, and creates a clean data environment essential for advanced technologies. While moving to modern solutions can cut maintenance costs and limit security risks, CIOs face practical challenges, including upfront migration expenses, data extraction difficulties, and internal resistance to letting go of highly customized legacy systems. Some organizations are increasingly weighing whether to build internal tools using advanced coding assistants rather than paying long-term licensing fees for external software. Ultimately, IT modernization is no longer just about retiring old technology; it is a continuous process of aligning the company’s tech stack with fast-evolving business needs to clear a path for meaningful innovation and operational agility.


The Credential Layer Is Expanding Faster Than Security Teams Can See It

As software development accelerates, organizations face an enormous increase in the number of digital keys, passwords, and access tokens they must manage. These credentials now connect people, applications, and artificial intelligence tools to critical data. Because they are often scattered across cloud accounts, internal networks, messaging apps, and developer laptops, it is incredibly difficult for security teams to track them. Recent data shows a sharp rise in leaked secrets, particularly those tied to AI services, which have become a new frontier for access management. At the same time, cybercriminals are using specialized malware to target developer devices, aiming to steal the local access codes stored there. To protect against these threats, security teams cannot rely on outdated, periodic checks. They need constant, clear visibility into every credential across the organization. This means knowing exactly what access each key grants, who owns it, and whether it is still active. Only by building a complete and accurate inventory can teams effectively identify risks, remove exposed secrets, and stop future leaks from happening. Taking control of this expanding environment requires a calm, systematic approach focused on detection first, ensuring that organizations understand their vulnerabilities before attackers can find them.


Should the CISO role be split in two?

Over the past three decades, the chief information security officer role has expanded significantly from its strictly technical origins. Today, these professionals are tasked with broad, strategic responsibilities, including data privacy, regulatory compliance, artificial intelligence governance, and overall business risk management. As this heavy workload continues to grow and outpace available resources, some industry observers have debated whether the position should be divided into two distinct roles: one focused purely on technical defense and another dedicated to business risk and organizational resilience. However, leading experts argue clearly against splitting the job. Instead, they recommend confidently maintaining a single executive who holds ultimate accountability for the organization's cyber strategy and risk management. To help manage the immense daily operational demands, larger companies are increasingly relying on a dedicated deputy role, which also directly aids in succession planning. This balanced approach ensures that the primary security leader can successfully focus their energy on executive communication, financial planning, and aligning security measures with core business objectives. Ultimately, the position is maturing along a path very similar to that of the chief information officer. As the role becomes undeniably executive, these professionals must transition from being seen merely as technical experts to functioning as essential business partners.


Exploring AI Observability – Part 1: Why It Matters

Just a year ago, tracking how artificial intelligence operates was hardly a recognized technology field. Today, experts predict that by 2028, a large portion of organizations deploying these systems will rely on dedicated tools to oversee them. This shift is happening because the adoption of intelligent systems has grown much faster than our ability to properly govern them. Employees across companies are using a mix of approved and unapproved tools, while software teams are actively building language models directly into their applications. This rapid expansion creates an urgent need for visibility to understand exactly where these tools are running, how well they perform, what they cost, and if they actually deliver real value to the business. The conversation is no longer just about how fast we can build these systems, but rather whether we can run them reliably in real world settings. Because modern systems can sometimes produce varying results from the exact same input, errors can quickly add up. Proper oversight is necessary right from the development phase to trace interactions, identify failures, and improve accuracy. In production, this oversight ensures that the behavior of intelligent tools connects smoothly with overall application health, resilience, and a solid user experience.


The Platform Engineering Playbook for Production LLMs

According to a case study on an inventory accuracy platform, scaling large language models (LLMs) requires treating the AI stack as platform infrastructure rather than a mere application feature. The engineering team successfully reduced production hallucination rates from fifteen percent down to just 1.5 percent without altering the foundation model itself. They achieved this by implementing an automated retry loop to catch formatting and grounding errors on the fly, alongside an intent-validation gate that defaults to "unclassified" to prevent off-intent responses. Additionally, prompt management was shifted to a history-preserving registry rather than hardcoding instructions, allowing runtime updates with a clear audit trail to prevent silent behavioral breaks. The authors also highlight critical security and observability practices for enterprise AI. They strongly recommend enforcing tool authorization directly at the resource server with a strict default-deny policy, warning that relying solely on API gateways can expose tools due to a single orchestrator bug. Furthermore, since traditional application performance monitoring tools cannot detect semantic degradation or silent output drift, teams must proactively instrument hallucination rates and per-team token costs right at request ingress to avoid costly retrofitting later.


Three questions a hospital CISO should ask a healthcare fintech vendor

In a recent interview with Help Net Security, Drew McCombs, CTO and CISO at Cylerity, discusses his approach to balancing security with development in the healthcare fintech sector. McCombs ensures that security is integrated into every development sprint rather than treated as an afterthought. When conflicts arise, any issue affecting patient data or funds disbursement takes priority. He notes that while Cylerity is not a bank, it must satisfy the compliance expectations of its banking partners without violating HIPAA regulations. To achieve this, the company minimizes data sharing and uses custom identifiers to keep protected health information (PHI) completely separate from financial reporting. When discussing artificial intelligence, McCombs insists that AI models should only recommend or flag information, with a human always making the final decision to prevent errors from gradual model drift. For small medical practices, he emphasizes that turning on multi-factor authentication (MFA) for email is the cheapest and most effective security fix available. Finally, McCombs advises hospital CISOs to scrutinize fintech vendors by asking about their data subprocessors, their protocols for verifying fund destination changes, and their breach response plans, warning that a vendor claiming to be "HIPAA certified" is a major red flag since no such official certification exists.

Daily Tech Digest - September 14, 2026


Quote for the day:

“The only sustainable competitive advantage is an organisation’s ability to learn faster than the competition.” -- Peter Senge

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Post-Quantum Cryptography Is Becoming Mandatory For Financial Institutions

As quantum computers become more powerful, they will eventually break the cryptography that currently protects financial data. This presents a serious risk for banks and insurers, especially for long-term records that adversaries might steal now to decrypt later. The solution is post-quantum cryptography (PQC), a set of new mathematical formulas that even quantum computers cannot easily solve. Importantly, PQC runs on standard computers and integrates into existing systems like TLS. The main hurdle for financial institutions is not buying quantum hardware, but updating decades of old, intertwined software before the threat becomes a reality. Standards are already being finalized, and regulators are beginning to expect actionable roadmaps from the financial sector. To prepare, institutions must first build a complete inventory of their current cryptographic tools and identify where their systems are most vulnerable. Since no single algorithm is guaranteed to be safe forever, organizations should design flexible architectures that allow them to swap out encryption methods as needed. Addressing this transition requires strong cross-team collaboration and commitment from leadership. By acting now to map their risks and pilot hybrid solutions, financial firms can control their migration timeline rather than scrambling at the last minute.


Attackers already understand your software supply chain better than you do

The article argues that attackers now understand modern software supply chains better than the organizations that rely on them, and that AI is accelerating this gap. It describes how recent incidents—such as the Miasma malware packages and the Axios compromise—show that threats often begin with small, trusted open‑source components that slip quietly into developer workflows. Because most commercial software depends heavily on open‑source code, many companies lack visibility into what they are actually running in production or how quickly they could respond if a critical flaw appeared. Attackers exploit this blind spot by targeting overlooked dependencies and developer tools rather than traditional network perimeters. The piece explains how malicious packages spread rapidly through CI/CD pipelines, bypassing controls and creating large downstream risk before anyone notices. It also notes that AI‑driven automation allows attackers to discover vulnerabilities and coordinate exploits far faster than defenders can react, especially when security teams are slowed by technical debt and manual processes. The article concludes that software supply chain security has become a national‑level concern and that organizations need continuous, automated controls capable of identifying risks, enforcing policies, and reducing exposure before attackers take advantage of weaknesses they already understand.


When Spec-Driven Development Pays off

With AI coding assistants becoming standard infrastructure in software engineering, the primary bottleneck has shifted from writing code to verifying it. This shift raises critical governance questions regarding accountability, intent divergence, and the division of oversight between humans and models. Regulatory frameworks like the EU AI Act and NIST risk management guidelines increasingly demand documented controls, making "careful review" an insufficient strategy for managing AI-generated code. A recent study examined the popular response of "spec-driven development"—treating detailed specifications (business rules, high-level design, and low-level design) as a governing contract for AI output. Interestingly, establishing a strict specification baseline did not inherently make human reviewers better at finding bugs. Instead, it transformed code review from an ambiguous task into a contract-anchored, highly accountable process where behavioral drift could be clearly attributed to specific requirements. While writing a specification first and generating code from it improved outcomes by treating the spec as a governing artifact rather than just a prompt, the benefits on simpler tasks were largely due to improved reasoning rather than the spec itself. Ultimately, specification governance proves to be a worthwhile investment primarily for complex, multi-constraint tasks handled by capable but imperfect AI models.


Your data architecture was built for predictable consumers

The article explains how traditional enterprise data architectures were built for a world where data consumers behaved in predictable, uniform ways, and why that model no longer fits today’s environment. It describes how organizations once supported thousands of users working from the same carefully designed application, with stable access patterns that made governance manageable. As dashboards, APIs, notebooks, microservices, and specialized tools multiplied, consumption became more varied — and agentic AI has now pushed this shift even further. Instead of one shared interface, those same users may rely on thousands of individualized agents or applications, each creating its own access paths, combinations, and entitlement decisions. The piece notes that while personalization becomes easier at the application layer, the underlying infrastructure and security teams face growing complexity, with more dynamic demand and harder‑to‑govern patterns. It highlights capital markets as an early testing ground, where zero tolerance for inconsistency has driven architectures that coordinate changing consumer behavior. The article argues that a governed data consumption layer — the outward‑facing part of a broader data fabric — can reduce repeated integrations, protect sensitive systems, and enforce consistent access and audit controls. It concludes by urging CIOs to evaluate where such an approach adds value as human and machine consumers increasingly access and act on data in unpredictable ways.


How to level up from security pro to security leader

Transitioning from a technical cybersecurity professional to a Chief Information Security Officer requires a fundamental shift in perspective. While a strong technical foundation is helpful, it is no longer enough to reach the executive level. Aspiring security leaders must learn to translate complex technical risks into clear business priorities. This means understanding how the company generates revenue and balancing security needs with broader organizational goals. Rather than being seen as the resident tech expert, successful leaders act as strategic partners who build trust across various departments, including finance, legal, and operations. Developing strong communication skills and business sense is far more valuable than mastering specific coding languages. Gaining broad experience, such as managing budgets or working in cloud engineering, can provide the highly valued background that modern employers expect. Additionally, finding experienced mentors and maintaining a genuine curiosity for new technologies will naturally foster leadership growth. Security professionals are advised to present themselves with calm confidence, take ownership of their mistakes, and avoid being overly rigid about their long term career paths. By focusing on delivering meaningful impact and collaborating effectively in their current roles, aspiring executives can position themselves for the transition from technical expert to trusted business leader.


Enterprise AI Security: ChatGPT, Claude, Gemini and Copilot Compared

As artificial intelligence tools transition from experimental chatbots to integrated enterprise solutions, businesses face new security challenges. Platforms like ChatGPT, Claude, Gemini, and Microsoft Copilot now connect directly to internal emails, cloud storage, and code repositories, shifting the primary risk from external data leaks to internal data exposure and unauthorized actions. No single platform is perfectly secure, as each presents unique vulnerabilities. For ChatGPT, the main governance gap lies between secure enterprise accounts and the personal accounts employees might still use. Claude’s agent capabilities pose a different risk: because it can execute commands and modify code, overly broad permissions could lead to unintended software changes. Meanwhile, both Gemini and Microsoft Copilot respect existing workspace access controls, but they act as powerful search engines that expose years of accumulated, poorly managed permissions. They do not bypass security rules, but they make forgotten, overshared documents instantly discoverable to employees. Additionally, all platforms face the threat of prompt injection, where hidden instructions in external files manipulate the AI. To safely adopt these tools, organizations must clean up internal access permissions, separate consumer from enterprise usage, define clear data retention policies, and strictly monitor what internal systems the AI can currently access.


Why AI shouldn't be the one repairing your data pipelines

As organizations expand their use of autonomous artificial intelligence systems to make operational decisions in real time, the traditional concept of self-healing data pipelines is no longer sufficient. While modern cloud architectures can quickly replace failed components, data failures in complex enterprise environments rarely present themselves as complete systemic crashes. Instead, these issues manifest as silent degradation, such as undocumented changes in source systems, misaligned business logic, or untrackable errors that compromise downstream models and regulatory reports. To support advanced business operations, engineering leaders must transition from reactive, automated repairs to autonomous data governance and resilient infrastructure. A critical component of this shift involves prioritizing deterministic solutions over heuristic guesswork. While artificial intelligence is highly effective at detecting anomalies and triggering alerts, relying on automated scripts to guess how to fix crucial records risks introducing synthetic errors into auditable systems. Rather than letting artificial intelligence independently repair data pipelines, organizations should pair machine learning detection with predefined, policy-driven workflows that isolate problems and apply historical fallback logic. By treating data reliability as a core business risk and building systems that actively defend and remediate quality issues in real time, enterprises can establish a secure foundation for their critical operations.


When security creates friction, employees find workarounds

When workplace security measures become too complicated or time-consuming, employees often look for easier ways to get their jobs done. According to a recent report, forty percent of workers globally admit to using unauthorized personal devices or applications when official technology fails them. In the Asia-Pacific region, this problem is particularly noticeable, with many staff members turning to unapproved platforms like public AI tools just to meet deadlines or respond to customers quickly. While these workarounds usually stem from a genuine desire to be productive rather than malicious intent, they create significant risks because organizations cannot secure or govern activity that they cannot see. This phenomenon, often called "shadow AI," highlights a disconnect between security rules and everyday operational needs. Instead of just blocking unapproved tools, leaders should view these behaviors as a clear signal that current systems are causing too much friction. The most effective way to reduce this hidden risk is to integrate security naturally into daily workflows. By prioritizing user experience and making the secure option the easiest one to use, companies can better protect their data while still empowering their teams to work efficiently.


BRICS digital sovereignty meets the interoperability test

The recent New Delhi BRICS Declaration sets forth an ambitious vision for technology that attempts to balance national control with global connectivity. The core challenge outlined in the document is how member nations can achieve digital sovereignty and self-reliance without sacrificing the interoperability that modern networks require. Rather than proposing a disconnected or isolated tech ecosystem, the declaration emphasizes building strong, nationally controlled digital public infrastructure (DPI) that can securely communicate across borders. This balancing act applies across several layers of technology. For DPI, it means countries maintain control over their own identity and data systems while ensuring they can interface with others. For physical infrastructure, the focus is on developing resilient submarine cables to reduce reliance on external entities, though the exact technical details remain under review. In terms of future technology and supply chains, the group is pushing for collaborative research and common, globally interoperable security standards. Ultimately, the declaration suggests that true digital sovereignty isn't about isolating a nation's network, but rather participating in global digital systems without becoming overly dependent on outside suppliers or infrastructure. The success of this vision will depend heavily on the upcoming technical and engineering decisions.


Why Data Governance Still Isn’t Driving Better Decisions (or Transformation)

Many organizations have invested heavily in data governance, setting up dedicated offices, policies, and committees. Despite this, the actual business impact often remains elusive. Compliance is still a manual process, and decisions are frequently made using data of uncertain quality. The core issue is that while data governance manages data, it often fails to govern the decisions that data is supposed to inform. This disconnect is a flaw in both the design and deployment of current governance models. For years, the standard approach has been to identify critical data, assign ownership, and implement controls, largely driven by regulatory requirements like GDPR. While this model has improved awareness and traceability, it often falls short of delivering measurable business value. Data offices struggle to prove their return on investment, and business teams may bypass governance processes that they feel slow them down without offering real benefits. The initial focus on inventorying and controlling data made sense as a starting point. However, these are backward-looking control systems. To truly drive business performance, data governance needs to evolve from merely a control mechanism into a forward-looking decision system that actively supports and prepares organizations for future actions.

Daily Tech Digest - September 07, 2026


Quote for the day:

"To succeed, high integrity must precede high ambition or high performance. Always do the right thing for the right reasons." -- Vala Afshar

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Your AI Productivity Gains Are Creating a Talent Crisis

As companies aggressively adopt artificial intelligence to handle routine tasks, they are inadvertently creating a hidden talent crisis for the future. While automating foundational work provides immediate efficiency and saves valuable time, it quietly dismantles the traditional apprenticeship model that young employees rely on to build expertise. Historically, doing repetitive tasks allowed junior professionals to develop the critical judgment and pattern recognition required to eventually become senior experts. This dynamic leads to a senior worker paradox. Current experienced professionals can effectively guide and evaluate artificial intelligence because they built their underlying knowledge before these tools ever existed. However, the next generation of workers is expected to supervise complex systems without gaining that identical practical experience. Consequently, organizations are accumulating a serious capability debt, where high daily output masks a growing inability among staff to solve problems independently without technological assistance. To prevent this looming skill shortage, businesses need to rethink how they implement these systems. Instead of using artificial intelligence merely as an engine to generate quick answers, companies should deploy it as a supportive coach. By designing workflows where the technology challenges assumptions, critiques reasoning, and highlights weaknesses without simply correcting them, organizations can help employees develop essential independent judgment.


Data Is Risky Business: Thinking Beyond Systems for Data Governance

Data governance goes far beyond formal frameworks, organizational charts, and written policies. While audits can evaluate a system by its final outputs, they rarely explain why well-intentioned employees within well-designed structures fail to govern data effectively. The true practice of data governance is shaped continuously by how people interpret their roles and responsibilities in everyday situations. Employees often rely on inherited traditions and beliefs when faced with real-world dilemmas, meaning that a formal rule is less influential than what the employee believes the rule is actually for. A documented procedure or escalation process only works if team members feel comfortable using it and believe that flagging an issue demonstrates competence rather than causes trouble. Effective coordination among teams, where individuals understand how their actions affect the wider organization, is crucial for catching anomalies and handling unexpected disruptions. Furthermore, over-automating these governance processes can be dangerous. When human reviewers are removed from routine tasks, they lose the practical experience needed to spot complex or novel failures when automation inevitably falls short. Ultimately, resilient data governance requires organizations to intentionally cultivate a culture of collaboration, build strong communication routines, and maintain the critical human judgment needed to handle unpredictable data risks.


The BTABoK and Agents

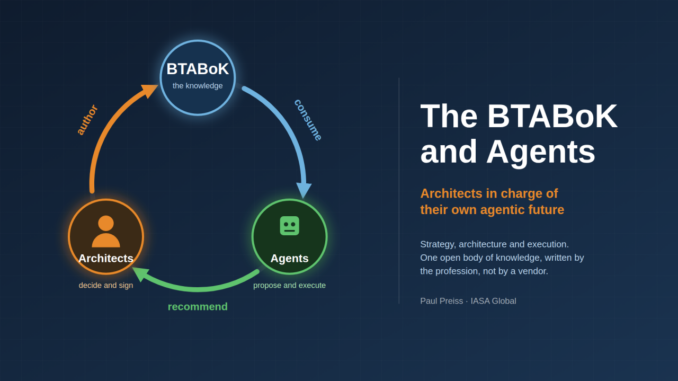
Artificial intelligence agents can generate impressive architectural models in seconds, but their output is only as good as the knowledge they draw from. While agents make speed cheap, they can compromise decision quality and shared understanding if not set up correctly. The Business Technology Architecture Body of Knowledge offers the most effective foundation for integrating agents into technology architecture. Unlike vendor specific frameworks that prioritize product sales or in house wikis that rely on fragmented opinions, this open framework provides a continuous chain connecting strategy to final delivery. It treats decisions as the central artifacts, ensuring every choice has clear trade offs and an accountable human owner. This is crucial because an agent produces options too quickly for humans to review without structured decision records. Furthermore, the framework defines specific viewpoints to answer exact stakeholder concerns and includes a clear competency model, meaning human architects remain equipped to properly evaluate and approve the generated work. Ultimately, this approach ensures that human practitioners, rather than vendors, remain in charge of the knowledge their agents use. By relying on a structured and practitioner governed foundation, organizations can safely accelerate their architecture practices without sacrificing accountability or quality.


Why Cybersecurity Must Become A Truly Professionalised Industry

The cybersecurity industry handles incredibly sensitive data and systems, bearing a level of responsibility similar to the medical or financial fields. However, it still lacks the strict, universal professional standards found in those established sectors. Currently, the quality of services like penetration testing varies significantly between providers, making it difficult for organizations to distinguish true expertise from clever marketing. To build genuine trust, the industry must adopt independent accreditation and verified certifications for both organizations and individual practitioners. Frameworks like the United Kingdom's CHECK scheme or global bodies like CREST offer a reliable baseline, assessing not just technical skills but also ethical conduct and operational maturity. As artificial intelligence makes sophisticated attack tools much more accessible, relying on validated human judgment becomes even more essential. Furthermore, because technology evolves rapidly, professionals must undergo continuous reassessment rather than relying on static, one-time qualifications. Professionalizing cybersecurity is not about adding unnecessary bureaucracy; it is about ensuring accountability, reliability, and consistency across the board. By demanding rigorous, ongoing standards, organizations can confidently partner with security experts, knowing they possess the necessary skills and ethics to protect vital digital infrastructure from increasingly complex and fast-moving threats.


Behind every AI inferencing strategy: The storage decision multi-model databases demand

As businesses rapidly deploy generative AI, the focus is shifting from simply training models to the critical phase of inferencing—the point where AI actually analyzes data and generates responses. While powerful processors like GPUs often grab the headlines, the true bottleneck for successful AI inferencing usually lies in data storage. Modern AI applications do not just rely on one type of data; they require a complex mix of text, images, relationships, and structured information. This complexity has driven the rise of multi-model databases, which can handle various data types—such as graphs, documents, and vectors—within a single system. However, these versatile databases place immense strain on storage infrastructure. To deliver the real-time, accurate results that enterprise AI demands, storage systems must provide exceptional speed, massive scalability, and the ability to process multiple data formats simultaneously without latency. Traditional, siloed storage setups often struggle to keep pace with these multi-model demands. Therefore, organizations must carefully evaluate their storage architecture, prioritizing high-performance solutions that seamlessly support multi-model databases. Ultimately, a successful AI strategy depends just as much on selecting the right underlying storage as it does on choosing the most advanced algorithms or processors.


Inside a Software Factory

The concept of a software factory is evolving from a traditional managed pipeline into an automation-driven system that transforms how engineering teams build and ship code. Instead of relying solely on artificial intelligence as a simple coding assistant within an editor, a modern software factory integrates automated agents directly into the broader development lifecycle. This system requires four core properties: standardized inputs, standardized tooling, measurable outputs, and complete replayability. Work enters the factory through various signals like bug reports or internal requests, which are then triaged into clearly scoped tasks. From there, software development agents take over to plan, execute, test, and review the code changes. However, humans remain firmly in the loop. The architecture relies heavily on persistent context, ensuring that security policies, business rules, and architectural guidelines govern the automated actions at every step. This shifts the role of software engineers. Rather than writing every line of code themselves, engineers now manage and supervise the underlying system, taking responsibility for its safety, governance, and business outcomes. Ultimately, this approach creates a continuous feedback loop where the development environment learns and improves over time, enabling organizations to deliver reliable software with greater consistency and visibility.


Leverage Code Review for Sustainable AI Coding Development

As artificial intelligence tools become a standard part of the software development process, teams are generating code at an unprecedented pace. While these advanced assistants significantly boost immediate productivity, they also introduce unique challenges. Without proper oversight, automated code can easily hide subtle bugs, security vulnerabilities, and structural flaws that ultimately create massive technical debt. To build applications responsibly, organizations must leverage rigorous code review practices to ensure lasting sustainability. Instead of blindly accepting computer suggestions, engineering teams must adapt their review processes to carefully scrutinize artificial intelligence contributions. Human oversight remains absolutely essential in this new landscape. Developers need to act as diligent editors, thoroughly validating the logic, performance, and security of every generated block of code before it reaches production. Strong peer review cultures prevent quick fixes from becoming massive maintenance nightmares. Furthermore, combining human expertise with modern testing tools ensures that codebases remain clean, functional, and secure over time. By placing a renewed emphasis on thorough code reviews, companies can safely harness the incredible speed of modern development tools. This balanced approach allows teams to innovate rapidly while maintaining the high standards required for sustainable and reliable software architecture today.


Why agentic AI is the key to systems integrity

As companies face stricter operational and security regulations, they are rapidly adopting agentic artificial intelligence systems capable of taking actions autonomously with minimal human input. While these powerful tools offer substantial productivity boosts, they also require broad data access and elevated privileges to function properly. This greatly expands the attack surface and introduces new vulnerabilities, especially within heavily regulated industries. Balancing this rapid innovation with strict oversight is a major challenge, particularly when organizations attempt to scale advanced tools across older, fragmented technologies. The most effective solution lies in deploying enterprise-grade platforms that embed security controls directly into their core design from the very beginning. By weaving identity management, access limitations, and continuous monitoring directly into the software development process, well-designed agentic systems actually strengthen overall integrity rather than weaken it. This proactive approach standardizes workflows, enforces real-time policy compliance, and prevents unauthorized internal development. To successfully scale these intelligent operations, businesses must unify their technology platforms, integrate security measures much earlier in the planning stages, and provide automated guardrails that empower teams to explore safely. Ultimately, treating oversight as a fundamental building block ensures that organizations can embrace modern automation without sacrificing valuable customer trust or compromising critical internal data.


From data residency to tech sovereignty: Europe rethinks control

European governments are moving past simply storing sensitive data within their borders and are now deeply questioning who truly controls their digital infrastructure. High-profile actions, such as Switzerland avoiding American cloud services for its national digital identity system and the Netherlands blocking a U.S. acquisition of a critical local cloud provider, highlight a growing concern over digital sovereignty. The core issue lies in jurisdiction: even if data is stored in a European server and heavily encrypted, relying on foreign-owned companies means the information might still be subject to outside laws, like the U.S. CLOUD Act. To counter these vulnerabilities, Europe is expanding its definition of tech sovereignty far beyond mere data localization. The European Commission has introduced strict new frameworks for cloud procurement that evaluate strategic, legal, and operational control, sometimes requiring an entirely European supply chain. Furthermore, the push for digital autonomy includes developing independent capabilities in semiconductors, artificial intelligence, and biometrics to reduce reliance on foreign standards and institutions. By prioritizing decentralization in projects like digital identity wallets, Europe aims to minimize centralized data storage altogether, asserting true control over its entire technology ecosystem rather than just dictating where its data physically resides.


Automated response and SOAR design patterns for security teams

Security Orchestration, Automation, and Response (SOAR) functions as an essential control layer that connects various security tools and teams, transforming noisy alerts into consistent, repeatable workflows. Rather than replacing human judgment or detection engineering, SOAR platforms excel at tasks like alert enrichment, case creation, and careful incident containment. A fundamental design principle for safe automation is separating decision support from direct execution. Playbooks should gather vital context and recommend actions, but automated responses must always align closely with technical confidence levels and potential business impact. If underlying detection quality is poor, reckless automation will simply accelerate bad decisions and disrupt daily operations. For many organizations, particularly smaller enterprises, the safest and most valuable initial pattern is automated alert triage and data enrichment. This approach rapidly improves decision quality without introducing unnecessary operational risk. When teams do choose to automate containment actions, such as isolating a compromised endpoint or forcing a user password reset, these interventions should strictly apply to high-confidence, reversible scenarios. Identity-focused responses often provide the cleanest automation targets because they remain centralized and are easily reversed if necessary. Ultimately, successful automation must carefully follow reliable detection quality instead of attempting to forcibly solve ambiguous security threats.

Daily Tech Digest - August 18, 2026


Quote for the day:

"Be miserable. Or motivate yourself. Whatever has to be done, it's always your choice." -- Wayne Dyer

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI can find zero-days but still can’t reliably write secure code

While artificial intelligence has become highly capable at discovering new vulnerabilities and writing exploits, it still struggles significantly with writing secure code and fixing security flaws. Recent studies highlight a growing imbalance between these offensive and defensive capabilities, showing that a large portion of code generated by artificial intelligence contains known vulnerabilities. This gap poses a serious risk for organizations using these tools to speed up software development, as the models often introduce technical debt and security exposure alongside faster delivery times. Experts note that writing secure code is inherently difficult, and language models lack the necessary organizational context, such as specific architectures, threat models, and internal policies, to do it reliably on their own. Simply improving training data is unlikely to solve this problem entirely. Instead, the software industry is shifting toward using specialized environments that embed strict security checks, context, and validation workflows directly into the development process. These systems provide the necessary constraints to produce safer software. However, automated systems cannot replace human judgment. Traditional testing tools and human oversight remain absolutely essential. Ultimately, experienced human developers must maintain control over reviewing and approving all code changes to ensure the final product is genuinely secure and robust.


A New Paradigm for IT Budgeting

Traditional annual IT budgeting often frustrates organizations because it relies on rigid planning cycles that stifle flexibility and waste valuable time. When companies prioritize individual projects and force them to compete above a funding threshold, they unintentionally encourage padded estimates and a rush to spend remaining funds at the end of the year. This conventional approach measures success by how well teams stick to initial estimates rather than the actual value they deliver, leaving IT departments struggling to keep pace with changing business needs. To resolve these issues, organizations can shift toward an envelope-based portfolio model. Instead of evaluating dozens of isolated projects, leadership allocates funds into broader strategic envelopes, such as improving operational efficiency or enhancing the customer experience. This method simplifies financial management by keeping the focus on outcomes rather than strict plan adherence. Leaders are given the authority to adjust priorities and reallocate resources as conditions change without restarting the entire budgeting process. Artificial intelligence can further assist by streamlining early-stage planning and identifying helpful patterns across initiatives. Ultimately, adopting this envelope approach transforms IT from a constrained, overworked service provider into a responsive partner focused on delivering meaningful results and adapting calmly to new challenges.


European sovereignty is an opportunity to take a giant leap forward

The conversation around European digital sovereignty is maturing beyond a simple desire to disconnect from American tech giants. Instead, it presents a rare chance to skip over outdated legacy systems and build modern data infrastructure from the ground up. However, achieving this requires more than just new hardware. Currently, many companies struggle because small innovation teams work in isolation while the broader workforce remains stuck on older applications. While European legislation has laid the groundwork for technological independence, the actual services and applications needed to run on these new platforms are still missing. Experts emphasize that successful modernization relies on unifying fragmented data across sectors, much like managing national public works through a single, coordinated system. This level of integration demands deep collaboration across companies rather than isolated efforts. Furthermore, the belief that Europe lacks the necessary talent is a misconception; many major tech platforms were built by small teams with European roots. The actual barriers holding the continent back are a lack of venture capital and stifling regulatory hurdles. To truly succeed, Europe must shift its focus from excessive regulation to creating strong commercial incentives, trusting that the local talent and technology are already fully equipped to manage the transition.


When AI Writes the Code, Specifications Need an Exit Strategy

In the era of AI-generated software, there is a growing temptation to view formal specifications as relics of the past. When artificial intelligence can churn out functional code in seconds, the urge to skip documentation and planning in favor of immediate execution is powerful. Yet, this convenience comes with a hidden cost: a loss of control over the resulting codebase. As the article argues, relying solely on AI to write code without a structured roadmap is a recipe for long-term technical debt. An "exit strategy" is essential. This means maintaining clear, human-readable specifications that act as a blueprint for the system, independent of the tools used to create it. If you cannot understand, modify, or debug your own software without the AI’s help, you have surrendered your agency. True engineering requires foresight, not just rapid output. Specifications provide the necessary guardrails, ensuring that even if an AI writes the initial implementation, the architecture remains grounded in human logic and understandable business requirements. Ultimately, an exit strategy is not about abandoning AI, but about ensuring that developers retain the authority and insight required to manage and evolve their systems effectively over time.


A better approach to generative UI

The article discusses how software developers should approach building dynamic interfaces in applications powered by artificial intelligence. It argues that teams must avoid the common mistake of letting models generate executable code, such as HTML or JavaScript, directly during a live user session. Although having an interface adapt instantly to a user's request sounds appealing, allowing an artificial intelligence to write raw code at run time compromises crucial security, testing, and architectural boundaries. It can lead to unpredictable behaviors and bypass the established rules for user permissions. Instead, the author advocates for a safer method called structured interface intent. With this strategy, the artificial intelligence does not invent the interface code. Rather, it simply chooses from a controlled, pre-defined menu of trusted interface blocks that the core application already knows how to handle. The model returns basic data indicating which visual elements are needed, and the application itself manages the actual display and execution of tasks. By relying on a verified registry of components rather than raw generated code, developers keep absolute control over the application's state, security protocols, and business rules, ensuring that the software system remains dependable, completely safe, and highly predictable while still offering a flexible user experience.


Balancing Sustainable Computing and Computing for Sustainability

The article discusses the critical need to balance two essential goals: making our technology greener and using technology to protect the environment. On one hand, sustainable computing focuses on reducing the heavy environmental toll of our digital lives. As computers become more powerful and data centers grow, they consume massive amounts of energy and produce significant electronic waste. To address this, the industry must develop hardware that uses less energy, improve how computers are manufactured, and create longer lasting devices. On the other hand, computing for sustainability involves using advanced digital tools to solve broad environmental challenges. We can use powerful algorithms and data analysis to optimize power grids, predict climate patterns, and manage natural resources more effectively. However, a conflict arises because the very tools needed to solve these global issues require immense computing power, which in turn increases energy use and carbon emissions. The piece argues that successfully navigating this tension requires a coordinated effort across different fields. Engineers, software developers, and policymakers must work together to ensure that the environmental benefits of new digital solutions outweigh the physical costs of running them. Ultimately, we must design technology that serves the planet without quietly adding to its burdens.


Why people, not technology, drive digital transformation

Akio Ueda argues that digital transformation is fundamentally about people rather than just implementing new tools. Often, companies deploy advanced systems like artificial intelligence or cloud computing but fail to see real, meaningful changes in their daily operations. This happens largely because employees lack the necessary skills to integrate these complex tools into their regular workflows. Ueda emphasizes that technical experts alone cannot drive transformation. True success requires individuals who understand business challenges, focus on customer needs, and can clearly guide organizational change. He points out that a strong talent strategy must align seamlessly with a company's core business goals and be supported by consistent policies across all departments. Training programs alone are not enough; employees must apply their learning practically to bridge the gap between knowing and doing. Furthermore, recognizing and rewarding these efforts through internal and external praise is a practical way to build motivation and confidence. Ultimately, a chief information officer's role is shifting from merely managing technology to developing the people who will execute the strategy. Investing in human potential is the most reliable way to ensure that technological advancements translate into lasting business value, empowering an organization to adapt, grow, and thrive in a constantly changing modern landscape.


How To Build Executive Presence From The Inside Out

True executive presence is not about having a prestigious job title or projecting a polished, charismatic image. Instead, it relies entirely on inner traits and deliberate daily behaviors that build lasting trust and credibility. To develop this presence, you must focus on how you interact with others and manage yourself during stressful situations. It begins with emotional intelligence and the ability to read a room, ensuring you set a calm emotional tone rather than simply reacting to pressure. Small actions like offering a genuine smile and actively listening before you speak go a long way in making your peers feel valued and understood. Furthermore, speaking up with courage to say the hard things, rather than feigning absolute certainty, shows authentic leadership. Another effective but often ignored habit is intentionally pausing before you respond to difficult questions. Taking a brief moment to breathe signals capacity and thoughtfulness rather than anxiety or haste. Real presence also requires you to be fully engaged in every interaction, putting away distractions to focus on the people in front of you. Ultimately, your character, competence, and conduct must align consistently over time. When your actions match your words day after day, you develop a grounded leadership identity that people respect and follow.


Why Some Companies Are Pulling Back on AI Coding

Although artificial intelligence promised to change software development by drastically speeding up code generation, some organizations are now reconsidering their heavy reliance on these tools. The initial enthusiasm is giving way to a more measured approach as engineering teams encounter practical challenges with automated coding. One major concern is the degradation of code review cultures; because AI-generated code often looks correct at first glance, developers may review it less rigorously, allowing subtle bugs and security vulnerabilities to slip into production. Furthermore, companies are noticing structural issues within their software. While these tools can write functional snippets, they often lack the broad context needed to adhere to a project's long-term design patterns, leading to fragmented systems and rising technical debt over time. Data privacy remains another critical issue, as sharing proprietary business logic or sensitive customer information with external language models poses significant security and compliance risks. Finally, leaders are observing a decline in deep system knowledge among their engineering teams. When developers rely too heavily on automated prompts rather than grappling with complex logic themselves, institutional knowledge suffers. Consequently, rather than abandoning these tools entirely, many businesses are pulling back to establish stricter guidelines, ensuring that human judgment and solid engineering practices remain central to their operations.


Why Traditional Data Governance Cannot Secure Business Decisions

Traditional data governance focuses on describing and organizing information through tools like glossaries, catalogs, and data lineage. While these methods help organizations understand what their data means and where it comes from, they often fail to connect that information to the actual business decisions it supports. Organizations do not govern data just to create better catalogs; they do so to ensure they can confidently grant, deny, fund, or authorize actions. The main limitation of traditional models is that they document data without showing how it secures critical operations. To fix this gap, organizations must adopt a decision focused approach. This means treating important business decisions as the central framework for governance. By separating business choices from data management tasks and linking them together, companies can create a clear chain of trust. This chain connects a requirement to a specific decision, the rules that guide it, the data used, the controls that verify it, and the evidence that proves it was handled correctly. Moving forward, governance must go beyond simply adding more descriptions to a database. It requires building a complete system where rules, controls, and error corrections are directly tied to their business consequences. This approach ensures organizations can clearly explain, defend, and trust their decisions.