Showing posts with label BCI. Show all posts

Daily Tech Digest - September 20, 2026


Quote for the day:

“The more I read, the more I acquire, the more certain I am that I know nothing.” -- Voltaire

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


Brain-Machine Interfaces Are Advancing: What Leaders Need to Know About Neurotechnology
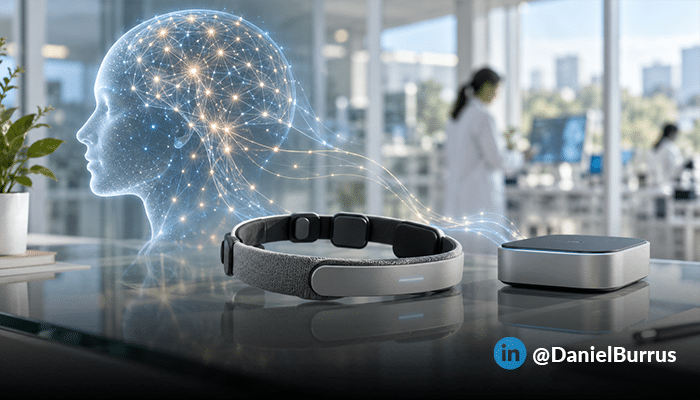
The convergence of artificial intelligence, smaller electronics, and advanced materials is accelerating the steady development of brain-machine interfaces, allowing for practical communication between human brains and digital systems. While this field is currently focused on healthcare, with recent clinical studies showing paralyzed patients successfully using neural interfaces to control devices and communicate independently at home, its applications will soon expand. In the near future, industries such as education, manufacturing, and assistive technology will likely adopt these emerging tools to improve human performance and overall accessibility. By the end of the decade, the technology is expected to feature more accurate signals, less invasive hardware, and better machine interpretation of brain activity. Rather than guessing which specific device will dominate the market, organizations and leaders should prepare for these predictable advancements now. This means tracking improvements in neural decoding, exploring diverse interface methods like ultrasound, and considering how neural data might fit into future product lines. Just as importantly, the widespread use of neurotechnology will create new challenges surrounding data privacy, system compatibility, and user control over sensitive neural information. Solving these practical problems will offer significant opportunities for those who calmly anticipate the steady progress of neural engineering and plan accordingly.


Opinion: Tech enables transformation, people achieve it

Daire Cunningham’s article explores why so many organizations struggle to get real value from artificial intelligence, despite the technology being widely available. He notes that while 88% of businesses use AI in some capacity, only a third have managed to scale it across their operations. The core issue, he argues, isn’t a lack of access to advanced tech, but rather the underlying condition of the organizations trying to use it. When companies rush to adopt AI, they often start by looking for a specific tool instead of identifying the actual business problem they need to solve. To succeed, leaders must work backward: map out their processes, figure out where the information is kept, and spot the real bottlenecks. A major roadblock is poor data readiness—many businesses have years of accumulated, disorganized data and permissions. AI tends to expose these underlying flaws rather than cause them. Ultimately, Cunningham believes digital transformation is about rethinking how work gets done, not just adding new software. While AI can process data faster and tackle complex tasks, human judgment and oversight remain essential. True transformation happens when a company prepares its data foundation and empowers its people to use technology responsibly.


CIOs offer guiding principles on how to achieve AI sovereignty
The article discusses the growing importance of AI sovereignty for Chief Information Officers (CIOs). This concept is centered on maintaining control over an organization’s entire AI ecosystem, which encompasses data, models, and the infrastructure hosting those models. As AI technology becomes increasingly integrated into business operations, organizations face mounting risks related to data privacy, regulatory compliance, and potential vendor lock-in. To manage these challenges effectively, CIOs recommend establishing clear guiding principles. First, it is crucial to create a comprehensive inventory of all AI resources currently in use, as you cannot manage what you do not track. Second, organizations must implement robust data and usage controls to monitor information flow and quickly identify any policy violations. This proactive approach helps secure sensitive data. Third, companies should update their incident response plans specifically to address potential AI-related breaches, ensuring they can act swiftly if issues arise. Finally, maintaining transparency and auditability is essential. Knowing who accessed data and how AI tools influence decision-making helps build trust and ensures regulatory compliance. Rather than viewing AI sovereignty as a simple compliance checklist, leaders should treat it as a fundamental strategy for the long-term success and security of the enterprise.


Children's Data Protection in the Age of EdTech and Platform Design

The digital age has made children’s data collection widespread, from location tracking and educational data to behavioral and voice information. While some of this is meant for learning or safety, the concern is that such data can be used for profiling, targeted ads, or boosting engagement without parental consent. This has made data protection laws surrounding children increasingly relevant. India's Digital Personal Data Protection (DPDP) Act, 2023 defines a child as anyone under 18, which is a higher threshold than seen in many other countries. This act requires platforms to secure verifiable parental consent before processing a child’s data and forbids processing that could harm a child’s well-being. Additionally, the DPDP Act bans the tracking, behavioral monitoring, and targeted advertising directed at children, though it provides some exceptions for safe uses in healthcare, education, or child safety. Internationally, there are variations in how children's data is handled. In the United States, COPPA applies to children under 13, while the European Union’s GDPR sets the default age at 16, though member states can adjust it to 13. The UK’s Children’s Code requires platforms that children are likely to use to have high privacy settings by default. For platforms dealing with children's data, balancing data retention limits with educational needs requires clear strategies and compliance checks.


Most enterprises are failing to translate talk into meaningful dependency mapping

The recent feature on digital sovereignty highlights a significant gap between what organizations want and what they can actually achieve. While most companies express a strong desire to regain control over their digital infrastructure, the reality is that true independence remains out of reach for many. The truth is that achieving digital sovereignty is not simply about building internal data centers or buying local software; it requires deep visibility into existing information systems and having credible exit options from major service providers. Unfortunately, most enterprises currently lack these fundamental building blocks. Over the past fifteen years, a rush toward cloud computing has left many businesses heavily dependent on a handful of dominant technology giants. This dependency makes it incredibly difficult to pivot or change providers without facing steep costs and major operational disruption. As artificial intelligence becomes central to business strategy, the stakes for retaining control over data and computing power are higher than ever before. The article suggests that instead of pursuing total independence, leaders should focus on preserving choice. By prioritizing flexible tools and establishing clear governance, organizations can gradually build resilience. Ultimately, sovereignty is about making smart decisions today that prevent complete vendor entanglement in the future.


Agentic Systems and Design Patterns

The shift toward agentic artificial intelligence marks a move from simple text generation to setups that can plan, take action, and learn from their mistakes. When building these systems, developers must first choose an overall structure. A single agent approach is easier to build and manage, making it a great starting point, though it can struggle with complex or extended tasks. Conversely, a multiple agent system uses an orchestrator to delegate work to specialists, which boosts reliability through teamwork but requires careful coordination. Beyond the basic structure, six core design patterns drive how these models function. The ReAct pattern mixes logical thinking with concrete actions in a loop, while CodeAct allows agents to write and test code to achieve their goals. Self reflection acts as an internal critic to refine outputs and fix errors. Basic tool use lets agents interact with outside software, and Agentic RAG improves how they fetch and verify information. Finally, the multiple agent workflow handles massive tasks by dividing them into smaller parallel jobs. For the best results, start with a simple single agent setup and only add complexity when the task demands it. Strong safeguards, like strict iteration limits and clear tool definitions, keep these systems reliable and easy to monitor.


What OT Resilience Actually Controls

The article from SC Media explains that recovering operational technology (OT) after a cyber incident requires a fundamentally different approach than recovering standard IT systems. While IT disaster recovery focuses on system availability—getting servers and applications back online—OT recovery requires "safe-state validation." This means ensuring the manufacturing process can be controlled safely before restarting production. The challenge is that standard IT backups often miss crucial OT engineering data, such as process configurations, device programming, and safety system logic. Without these, a restored system might appear functional but lack the specific parameters needed to operate safely. The author outlines five common failure scenarios in OT resilience, including ransomware affecting control systems, vendor platform outages, and control logic tampering. These scenarios highlight the need for specialized OT backup architectures and recovery procedures. Ultimately, true OT resilience involves validating configurations at the device, system, and process levels, often requiring specialized engineering expertise. This validation step adds time to the recovery process but is essential to prevent unsafe conditions that could lead to physical harm or environmental damage.


Achieving data sovereignty for SaaS with confidential containers and quantum-safe networking
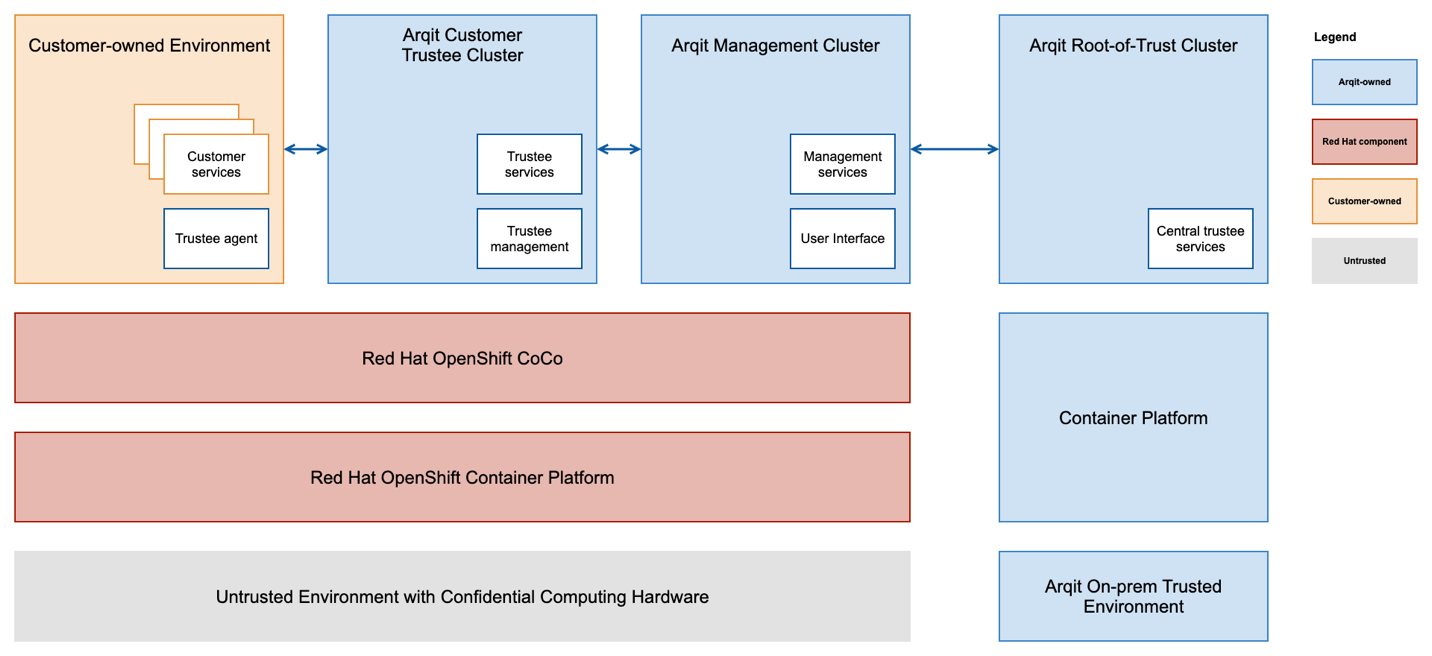
Software vendors hosting services on the public cloud face increasing pressure from customers who want to keep their data secure and private. Often, customers prefer on-premise solutions, which are harder to manage and scale for vendors. A better approach allows vendors to keep their services in the cloud while offering robust security through cryptographic controls, specifically using confidential computing. This technology secures data processed in untrusted environments by isolating it in a trusted execution environment (TEE). Red Hat and Arqit have introduced a setup that uses confidential containers and quantum-safe networking to protect data in transit. They applied this to Arqit's Encryption Intelligence (EI) platform. In this setup, services and data are isolated from the host environment, allowing customers to maintain control over their data while protecting the vendor's intellectual property. The architecture involves three clusters operating in the untrusted environment, communicating via a quantum-safe connection. Trust is established by an outer trustee in a trusted on-premise environment, which verifies the inner trustee in the cloud. This combination of confidential containers and quantum-safe protection for data in transit offers a practical alternative to on-premise deployments, providing strong assurance over data security and sovereignty for both vendors and customers.


AI-led SOC infrastructure shifts from raw data to outcomes

The article discusses a shift in how modern Security Operations Centres (SOCs) measure success in an AI-driven environment. Historically, SOCs focused on volume metrics, such as alerts processed or data ingested, but this model struggles against modern threats across distributed environments. Today, the focus is shifting to measuring outcomes like risk reduction, analyst capacity, and decision quality. The traditional volume-driven model leads to rising costs, overwhelmed analysts, and incremental improvements, failing to deliver clear returns on investment. While AI is viewed as a solution, it has struggled to deliver value when treated simply as an overlay, lacking transparency and integration. To overcome these limits, organizations must build SOCs around productivity rather than throughput, connecting technology investments with operational impact. In this model, AI isn't measured by its theoretical capability but by the work it completes alongside human analysts. A critical component is the use of "Agentic AI" as an execution layer, which coordinates investigations and decisions rather than functioning in isolation. For AI to be effective, it must also be governed to ensure actions are explainable and align with organizational policies, allowing security leaders to demonstrate responsible use and measurable security outcomes.


Data sovereignty is a control problem, not a geography problem

The article argues that data sovereignty is fundamentally about control, not geography. Many organizations assume that storing data within national borders is enough, but the author explains that this view is too narrow. True sovereignty depends on knowing who controls identities, administration, infrastructure, and legal authority over the data. Recent events have exposed how fragile digital infrastructure can be, from attacks on subsea cables to large‑scale outages like the CrowdStrike incident, which disrupted critical services worldwide and led to major financial losses. At the same time, new regulations and the rise of AI have increased the stakes, since sensitive information and intellectual property now flow through cloud‑hosted models governed by foreign jurisdictions. The article stresses that organizations often lack visibility into where their data lives, who can access it, and which laws apply. To regain sovereignty, they must demand transparency from providers, understand dependencies, and treat governance as an architectural requirement rather than an afterthought. Cost and speed still matter, but they can’t outweigh resilience and accountability. Sovereignty, the author concludes, isn’t about abandoning the cloud—it’s about ensuring organizations retain meaningful control so they can manage risk and respond confidently when incidents occur.

Daily Tech Digest - July 19, 2026


Quote for the day:

“The best startups are the ones that take something that already works and improve it dramatically.” -- Peter Thiel

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


The Refactoring You Keep Deferring Is Not Technical Debt — It’s Architecture Risk

The article argues that many engineering teams mislabel certain long‑postponed refactoring tasks as technical debt when they are actually signs of deeper architectural risk. Technical debt, the author explains, is about how code is written. It creates friction, slows development, and increases the cost of change, but the system still does what it was designed to do. Architecture risk is different: it reflects structural assumptions baked into the system—limits on throughput, data model constraints, or tightly coupled components—that only become visible when the business needs the system to do something new. The piece shows how teams often confuse the two because both appear as “cleanup” work and both get deferred for similar reasons. But the consequences diverge sharply. Technical debt can be addressed gradually, module by module. Architectural constraints often require redesigning entire parts of the system, which demands planning, ownership, and honest communication with stakeholders. The author offers a simple test: if rewriting the code cleanly using the same structure would not remove the limitation, the issue is architectural. The article encourages teams to identify structural assumptions early, map how they limit future directions, and treat high‑impact constraints as real risks rather than backlog chores.


Brain-Machine Interface Identifies, Amplifies Conversations Amid Noise

A new brain-computer system developed by researchers at Columbia University helps people follow specific conversations in noisy environments. Traditional hearing aids often struggle in crowded rooms because they amplify all sounds equally. To solve this, scientists created a device that constantly monitors a person's brain activity alongside surrounding audio to figure out which voice the listener wants to hear. Once it identifies the target, the program automatically turns up the volume on that specific conversation while turning down competing background noise. Researchers tested the technology using four patients who already had electrodes temporarily placed in their brains for other medical reasons. During the trials, the equipment successfully adjusted the audio in real time, even when listeners intentionally shifted their attention from one speaker to another. Participants reported that understanding speech became much easier, and measurements of their pupils confirmed they expended less effort to listen. When the recorded audio was played for people with hearing loss, they also experienced significant improvements in speech clarity. While this early version relies on invasive electrodes to gather high-quality brain signals, the results offer a clear foundation for future hearing devices that might adapt to an individual's focus using less invasive technology and methods.


SABSA framework for risk-driven security architecture: a practical guide for UK SMEs

The SABSA framework helps organizations build a security architecture that directly connects business risks to technical solutions. Unlike a rigid checklist or a product guide, SABSA ensures every security measure has a clear, explainable purpose. It asks fundamental questions about what needs protection, potential threats, and required security properties. This framework is particularly valuable for small and medium-sized enterprises because it encourages pragmatic decision-making, helping to avoid duplicated tools or neglected controls. SABSA utilizes a layered approach that progresses from broad business attributes to specific technical implementations. It starts by defining necessary business qualities, such as availability or confidentiality, and then determines the required security objectives. From there, it outlines logical mechanisms and finally maps them to actual technologies and configurations. This layered method ensures strong traceability, making it easy to justify why a specific control exists. When applying SABSA, businesses should identify their most critical services, analyze potential threats, and define control objectives based on their specific risk appetite. By focusing on proportionate controls that balance protection, usability, and operational cost, small teams can effectively implement SABSA one critical service at a time, resulting in a coherent and practical security design.


The AI coding rollout worked. Now CIOs have a bigger problem

Although artificial intelligence tools are widely used by developers today, the expected massive boost in productivity has yet to materialize. Instead of simply speeding up how fast code is written, these tools are fundamentally changing what developers do every day. Writing code is no longer the primary bottleneck or the most crucial skill. Developers are shifting away from manual programming and spending more of their time designing systems, validating outcomes, and reviewing work generated by the machine. While raw coding speed has improved, companies are discovering that artificial intelligence code often takes much longer to review and contains more security vulnerabilities. This shift also introduces a serious long-term problem for the industry. Routine tasks like bug fixes and writing tests—the exact work that junior developers traditionally used to learn their craft—are now handled by software. If companies stop hiring entry-level engineers because machines can do their work, they will face a severe shortage of experienced senior staff in the coming years. To succeed, organizations must stop focusing solely on how much code is generated. Instead, they need to redesign their development processes around strong governance, clear business outcomes, and new ways to mentor the next generation of engineers.


The Pulse: What can we learn from Bun’s rapid Rust rewrite with AI?

The creator of the Bun software project recently completed a massive code rewrite from the Zig programming language to Rust in just eleven days using artificial intelligence. Originally, Bun relied on Zig, which caused persistent memory errors and system crashes. Rust promised to solve these stability problems by handling computer memory more safely. However, manually rewriting over half a million lines of code would have taken a team of developers at least a year, severely delaying new features and updates. Instead, the team used an advanced artificial intelligence model named Fable to automate the heavy lifting. The process started with strict guidelines, followed by dividing the workload across sixty four independent artificial agents. These agents translated the code, reviewed their work, and resolved thousands of compilation errors while the human developers slept. After a few days of getting the automated tests to pass, the project was finished. Although the computing cost reached one hundred sixty five thousand dollars, it remains significantly cheaper and faster than paying a team of engineers for a year of manual labor. This achievement demonstrates that large software migrations are now highly practical, provided a team maintains strong testing practices and a clear technical strategy.


The vertically integrated neocloud

Iren, once known for Bitcoin mining, has reinvented itself as a builder of very large data centers aimed at supporting AI workloads. The company believes its vertically integrated approach—owning the land, the power infrastructure, and the data centers themselves—lets it move faster and avoid the delays that come from relying on outside colocation providers. After converting its Canadian sites to support AI, Iren is now focused on the US, where it is developing several massive campuses. Its Texas footprint already includes 750MW in Childress, with two Sweetwater sites planned to reach 2GW. Another 1.6GW site is scheduled for Oklahoma in 2028. Keeping these projects geographically close helps the company maintain a stable workforce and contractor base during a period of intense competition for skilled labor. Iren builds and procures equipment ahead of customer commitments, which carries risk but has paid off—most notably through a large cloud contract with Microsoft. Early procurement also helps the company secure scarce components like high‑voltage gear and GPUs. Iren argues that some customers are rethinking their redundancy requirements, especially for AI training, where occasional interruptions are manageable. The company sees its track record of delivering capacity on time as a key advantage in a rapidly expanding and often over‑promising neocloud market.


Sovereign AI: Building AI Where Data, Infrastructure, and Control Stay Aligned

The article explains why many organizations are rethinking how they build and run AI systems, especially when sensitive data and strict regulations are involved. As AI moves from experiments into everyday operations, companies need more control over where data is stored, how models are run, and who can access the underlying infrastructure. The authors describe “sovereign AI” as an approach that keeps data, operations, and governance within clear boundaries rather than relying solely on contractual promises. They outline the kinds of information AI systems generate—such as prompts, embeddings, logs, and model artifacts—and note that these can be just as sensitive as primary business data. The piece argues that sovereignty is not only about compliance; it can help organizations gain trust, reach regulated markets, and scale AI safely. It also lays out architectural principles for maintaining control, including isolation of environments, strict rules for AI‑related data, and choosing an operating model that fits local requirements. The article then shows how Oracle’s cloud offerings support different sovereignty needs, using SoftBank’s Japan‑based deployment as an example of keeping AI infrastructure and operations within national boundaries. Overall, it presents sovereign AI as a practical way to align technology, regulation, and organizational responsibility.


Why Cyber Resilience Is Becoming Critical in AI-Led Enterprise Transformation

As businesses increasingly rely on artificial intelligence to manage everything from customer service to financial forecasting, the approach to digital security must fundamentally change. While these intelligent systems offer significant advantages, they also expose vast amounts of sensitive data and create new vulnerabilities. Traditional security measures designed merely to keep attackers out are no longer sufficient, especially since hostile actors are now using the same advanced tools to launch sophisticated, adaptable attacks. Instead of assuming every threat can be blocked, companies must shift their focus toward complete resilience. This means accepting that breaches will eventually occur and building robust systems that can quickly detect issues, limit the damage, and recover operations without major interruptions. Ensuring the integrity of the data that feeds these systems is critical, as flawed information easily leads to bad decisions and reputational damage. Furthermore, security can no longer be treated as an optional feature added at the end of a project. It must be woven directly into the core design of every network. Because these risks directly impact overall revenue and regulatory compliance, protecting the organization is no longer just a technical issue for the technology department; it has become a central responsibility for the entire leadership team. entire executive. central responsibility for the entire leadership team.


The Future of Age Verification: Your Face Never Leaves Your Device

As governments worldwide enact strict age verification laws for online platforms, facial age estimation has become a popular compliance tool. However, this method traditionally requires sending user photos to external servers, which creates significant privacy risks and attractive targets for data breaches. To solve this problem, a company named Incode has developed a new age verification system that processes facial data entirely on the user's device. By shrinking their artificial intelligence models, they enable everyday devices like smartphones and computers to estimate a user's age locally without ever transmitting or storing the actual image of the face. Only the final age verification result and basic session data are sent to the platform, ensuring privacy through system architecture rather than just written policies. This session data helps block sophisticated fraud attempts, such as deepfakes or camera tampering, without compromising personal biometrics. Alongside this technology, Incode recently invested one hundred million dollars into privacy infrastructure, including the acquisition of Identiq. This partnership allows organizations to share critical fraud intelligence without pooling raw customer data into vulnerable centralized databases. Ultimately, these advancements allow platforms to meet growing legal requirements for age assurance while keeping sensitive biometric data strictly in the hands of the user.


Restoration of a 20-year-old Java “Big Ball of Mud” using AI and Docker

When tasked with modernizing a legacy codebase—in this case, a twenty-year-old Java repository—developers often fall into the "tourist trap." They ask generative artificial intelligence for a quick fix or a modern starter kit. The machine eagerly obliges, offering modern build files and updated dependencies that look pristine but are fundamentally disconnected from the actual architecture. This optimistic approach masks deep structural rot, such as outdated APIs, non-standard directory layouts, and hidden concurrency issues, leading developers down a frustrating path of debugging code that was never meant to be modernized in one step. To succeed, engineers must adopt an "archaeologist" mindset, using artificial intelligence not to generate new code, but to perform a forensic audit. By prompting the tool to analyze the era of the code, structural integrity, data flow, and error handling, developers can accurately assess the system's true health. In this project, the audit revealed a fragile system masquerading as Java, riddled with string-based typing and deceptive test coverage. Rather than immediately refactoring, the correct strategy was complete containment: wrapping the untouched legacy code in a stable Docker environment mimicking its original era. This creates a reliable baseline, proving that artificial intelligence is most effective when constrained by evidence and strict modernization phases.

Daily Tech Digest - July 05, 2026


Quote for the day:

"Empowerment isn't telling people they're empowered. It's letting them own the outcome." -- Gordon Tredgold

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


In BCI, Safety Is A Design Decision

The current brain-computer interface (BCI) industry often assumes that high performance requires permanent, invasive surgical implants, treating safety risks as unavoidable trade-offs. However, this rigid approach bakes ethical problems directly into the technology's core architecture. Conversations about patient consent and privacy usually happen too late, well after developers have already committed to permanent hardware that makes a patient's decision nearly impossible to reverse. True safety extends far beyond the initial surgical procedure; it involves long-term biological tolerance and how well the human body naturally responds to embedded hardware over months and years. Therefore, safety and ethics must be treated as foundational design decisions rather than mere afterthoughts. By prioritizing reversible and temporary interfaces, developers can ensure that patient consent remains genuinely revocable, giving individuals ongoing control over their own bodies and personal data. Treating lower physical impact as a primary technical goal, rather than a reluctant compromise, is the only reliable way to scale these medical tools effectively. Ultimately, if the industry wants these powerful technologies to safely benefit millions of people rather than a select few, developers must build around reversibility and long-term biological harmony from the very beginning.


Blockchain in Payments and Risk: Infrastructures, Adoption, and the New Risk Landscape

Blockchain technology has transitioned from a speculative concept into foundational infrastructure for global payments. By lowering the costs of verifying transactions and operating networks, blockchain enables immediate transfers that eliminate traditional settlement delays. This shift provides clear advantages for complex cross-border transactions and wholesale banking, where fragmented legacy systems often create frustrating friction. However, this technology also fundamentally transforms the nature of financial risk. While it reduces traditional counterparty vulnerabilities, it introduces new challenges, such as the potential for rapid currency runs, coding vulnerabilities in automated contracts, and novel avenues for financial crime. In response, a unified global regulatory framework is currently emerging to ensure these new systems are governed by the same strict standards as traditional finance. Looking ahead, this infrastructure will become increasingly vital as artificial intelligence systems begin executing autonomous, high-frequency transactions. To support this next phase, the global financial system must adopt a layered approach that combines programmable digital money with robust, automated risk management controls. Ultimately, the success of blockchain in payments depends less on the technology itself and more on how institutions and regulators deliberately design systems to manage these evolving risks effectively.


The developer device is the new supply chain attack blind spot

Developer devices have become the new primary target for software supply chain attacks. Attackers are shifting their focus to developers because their machines hold valuable cloud credentials, security keys, and direct access to source code. Recent incidents highlight that a single compromised device can spread malicious updates across an entire organization in minutes. This risk is increasing as artificial intelligence coding tools operate with little human oversight, while simultaneously lowering the barrier to entry for attackers. Unfortunately, traditional corporate security measures like endpoint protection fall short. These tools monitor the operating system but miss malicious activity happening within code editors, package managers, and browser extensions. Consequently, companies are forced into a difficult choice: either strictly block all external tools and slow down productivity, or allow everything and accept dangerous security risks. Instead of merely focusing on detecting threats after they appear, organizations need practical strategies to stop them from reaching the device entirely. Implementing simple rules, such as a mandatory delay before installing new software updates, can prevent compromised code from slipping through. By securing the developer device itself, companies can safely manage modern coding tools without sacrificing productivity.


Consent Managers under DPDPA: Implications for Global Capability Centres

India's Digital Personal Data Protection Act (DPDPA) introduces a novel regulatory entity known as a "consent manager," which holds significant implications for Global Capability Centres (GCCs). Serving as a single, centralized point of contact, consent managers allow individuals to grant, review, manage, and withdraw their data consent through an accessible, interoperable dashboard. Entities seeking to become consent managers must register with the Data Protection Board, maintain a minimum net worth of two crore rupees, and operate independently on a data-blind basis. While this cross-sectoral framework aims to streamline consent management similarly to India's financial account aggregators, it requires immediate attention from GCCs, as registration opens in November 2026 and full compliance is expected by May 2027. Crucially, the legislation includes a commercial carve-out for foreign data principals. This means that if an Indian GCC processes the personal data of foreign employees under a contract with its overseas parent company, it is exempt from the DPDPA's consent manager obligations for those individuals, falling instead under the data protection laws of their home jurisdictions. Although this exemption provides meaningful operational relief, navigating these dual frameworks complicates overall GCC data compliance strategies.


Small Businesses Are Suffering From a Lack of Data Sophistication

Small businesses are collecting more information than ever before, yet many still struggle to turn that information into useful insights. For the most part, small companies operate reactively rather than strategically when it comes to their data. The core issue is that their information is often scattered across disconnected systems like sales software, accounting programs, and websites. This fragmentation makes it difficult to see the full picture of how the business is performing. Furthermore, business owners frequently lack the time, specialized skills, and formal strategies needed to manage this information effectively. While modern tools like artificial intelligence hold the potential to help smaller companies compete more effectively, limited technical readiness and isolated systems are slowing down adoption. To improve, experts recommend that owners focus on asking a few critical questions directly tied to daily operations rather than trying to fix everything at once. From there, companies should invest in training their teams to better understand basic data concepts and collaborate with industry peers. Eventually, the goal should be to bring all scattered information into a single, organized platform, creating a stronger foundation for smarter decision-making and sustainable growth.


Why the Marketing Engineer Is the Most Important New Role in Every Revenue Organization

Modern business teams often struggle because their marketing technology systems are disconnected. While companies buy new software hoping for better sales, the underlying setup remains broken. This is why organizations need a new role: the marketing engineer. Unlike traditional operations staff who simply maintain current tools, marketing engineers actively build and improve the entire system. They treat a company's marketing setup like software code, designing automated processes that run smoothly in the background without manual effort. You might already have someone with these skills on your team. You can spot them because they prefer building automated workflows over standard reports, understand technical systems deeply, and get frustrated when data is not easily accessible. When hiring externally, look for candidates with technical backgrounds rather than traditional marketing experience. Bringing a marketing engineer on board requires a shift in thinking and budget. Instead of hiring another manager to run individual campaigns, you are investing in someone who builds the foundation for long-term growth. When talking to finance leaders, explain this role as an investment that multiplies the team's overall productivity. Ultimately, a marketing engineer creates a reliable system that allows smaller teams to perform like much larger organizations.


The Business Case for Banking Resilience in a Digital Economy

The traditional view of banking resilience as merely disaster recovery and basic compliance is entirely outdated. Today, a bank's ability to withstand operational shocks directly influences its revenue, customer trust, and long-term viability. As financial institutions increasingly rely on digital systems and external vendors, the nature of risk has fundamentally shifted. Even a bank with exceptionally strong financial reserves can fail its customers if a cyber incident or technology outage halts its daily operations. Therefore, investing in resilience is no longer a defensive expense, but a practical business necessity. Global regulators emphasize that modern banking stability is measured by how well critical services continue running during a crisis. To achieve this standard, banks must carefully map their core services from start to finish, identify hidden weaknesses like an overreliance on a single telecommunications provider, and build robust backup plans. By systematically improving incident response, strengthening third-party oversight, and rigorously testing potential disruption scenarios, banks protect their daily transaction flows. Ultimately, proactive operational resilience reduces customer complaints, limits the financial fallout of sudden downtime, and ensures the institution remains fundamentally reliable and competitive within an interconnected digital economy.


Fine Tuning the Enterprise: Reinforcement Learning in Practice

In a recent InfoQ presentation, OpenAI's Will Hang and Wenjie Zi detail how their new framework, Agent Reinforcement Fine-Tuning (Agent RFT), changes the way artificial intelligence models learn to use external tools. Instead of relying on static examples of text, Agent RFT trains models through active trial and error. The AI explores different strategies by calling actual tools in a controlled environment, learning from real-time feedback and custom grading systems that reward correct, efficient problem-solving. This method marks a significant shift in training autonomous systems. Because the models interact with real endpoints and learn to optimize their own behavior, they become exceptionally good at navigating multi-step reasoning tasks specific to a company's unique domain. The speakers highlight that Agent RFT is highly efficient, often requiring as few as ten to a hundred examples to see meaningful improvement. Furthermore, it directly addresses common operational challenges by reducing unnecessary steps, lowering response times, and preventing the system from getting stuck in endless computational loops. Through various enterprise case studies, the presentation demonstrates how defining clear, verifiable success criteria allows organizations to build highly capable and efficient AI agents tailored to their specific operational needs.


Digital Sovereignty at Risk: Managing Cyber Exposure in Europe’s Global Supply Chains

Europe’s pursuit of digital independence is increasingly threatened by a hidden vulnerability: the complex global supply chains that support its businesses and infrastructure. While the European Union has introduced stricter regulations to improve cybersecurity, these measures often fail to address the critical risks embedded deep within third-party vendor networks. Hackers are actively targeting these lower-tier suppliers, recognizing that compromising a single provider can create a cascading failure across multiple industries, from healthcare to energy and aviation. Many European organizations remain heavily dependent on technology from outside the continent, yet they lack clear visibility into how secure those external partners truly are. Simply relocating supply chains to allied countries does not solve the underlying fragility. Instead, businesses must build genuine resilience by diversifying their suppliers to eliminate single points of failure. This means establishing strict security requirements in procurement contracts, enforcing precise access controls, and conducting joint readiness testing with key partners. Ultimately, true security in an interconnected digital economy requires organizations to actively manage and map the risks associated with the external systems they rely on, ensuring operations can continue even when a key supplier is breached.


Cognitive Debt - The Debt You Can't See in the Code

Cognitive debt is the hidden cost to your independent thinking ability that accumulates when you repeatedly offload intellectual work to artificial intelligence. Borrowing from the concept of technical debt in software development, it occurs when you take mental shortcuts today that compromise your future capabilities. This phenomenon is not simply about laziness. Instead, it involves the real neurological atrophy of essential cognitive skills, such as reasoning, critical judgment, and problem-solving. Just like physical fitness, your intellectual capabilities require regular practice to maintain and grow. When a machine handles the heavy mental lifting, your own skills weaken gradually and invisibly. This silent debt eventually surfaces when you suddenly find yourself unable to perform tasks you once handled easily, or when you lack the foundational understanding needed to evaluate automated outputs effectively. To prevent this decline, individuals must stop outsourcing their actual reasoning. While technology is highly effective for automating operational or mechanical tasks, the core intellectual work should remain human. The most effective strategy is to draft your own initial thoughts before turning to assistance, ensuring you maintain your mental fitness while still leveraging modern tools for efficiency.

Daily Tech Digest - March 15, 2026


Quote for the day:

"A leader must inspire or his team will expire." -- Orrin Woodward


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


The Last Frontier: Navigating the Dawn of the Brain-Computer Interface Era

In the article "The Last Frontier: Navigating the Dawn of the Brain-Computer Interface Era," Kannan Subbiah explores the transformative rise of Brain-Computer Interfaces (BCIs) as they move from science fiction to strategic reality. BCIs function by bypassing traditional neural pathways to establish a direct communication link between the brain's electrical signals and external hardware. By 2026, the technology has transitioned from clinical trials—aimed at restoring mobility and sensory perception for the paralyzed—into the enterprise sector, where it is used to monitor cognitive load and optimize worker productivity. However, this deep integration between biological and digital intelligence introduces profound risks, including physical inflammation from invasive implants, cybersecurity threats like "brain-jacking," and ethical concerns regarding the erosion of personal agency. To address these vulnerabilities, a global movement for "neurorights" has emerged, led by frameworks from UNESCO and pioneer legislation in nations like Chile to protect mental privacy and integrity. Subbiah argues that while the potential for human augmentation is immense, society must establish rigorous ethical standards to ensure thoughts are treated as expressions of human dignity rather than mere harvestable data. Ultimately, navigating this frontier requires balancing rapid innovation with a "hybrid mind" philosophy that prioritizes psychological continuity and user autonomy.


Is your AI agent a security risk? NanoClaw wants to put it in a virtual cage

In the article "Is your AI agent a security risk? NanoClaw wants to put it in a virtual cage" on ZDNet, Charlie Osborne discusses the newly announced partnership between NanoClaw and Docker, designed to tackle the escalating security concerns surrounding autonomous AI agents. NanoClaw emerged as a lightweight, security-first alternative to OpenClaw, boasting a tiny codebase of fewer than 4,000 lines compared to its predecessor's massive 400,000. This simplicity allows for easier auditing and reduced risk. The integration enables NanoClaw agents to run within Docker Sandboxes, which utilize MicroVM-based, disposable isolation zones. Unlike traditional containers that share a kernel with the host, these MicroVMs provide a "hard boundary," ensuring that even if an agent misbehaves or is compromised, it remains contained and cannot access or damage the host system. This "secure-by-design" approach addresses critical enterprise obstacles, such as the potential for agents to accidentally delete files or leak sensitive credentials. By providing a controlled environment where agents can independently install tools and execute workflows without constant human oversight, the collaboration unlocks greater productivity while maintaining rigorous enterprise-grade safeguards. Ultimately, the partnership shifts the security paradigm from trusting an agent's behavior to enforcing OS-level isolation, making it safer for organizations to deploy powerful AI agents in production.


Banks Turn to Unified Data Platforms to Manage Risk Intelligence

In the article "Banks Turn to Unified Data Platforms to Manage Risk Intelligence," Sandhya Michu explores how financial institutions are addressing the complexities of digital banking by consolidating fragmented data environments into strategic unified platforms. The rapid growth of digital transactions has scattered operational and customer data across mobile apps and backend systems, creating a "brittle" infrastructure that often hinders the scalability of AI and analytics initiatives. To overcome this, leading banks are building centralized data lakes and unified digital layers to aggregate structured and unstructured information. These centralized environments empower business, compliance, and risk departments with shared datasets, significantly improving regulatory reporting and customer analytics. Additionally, unified platforms enhance operational observability by enabling faster incident analysis through log correlation across diverse systems. Beyond reliability, these data frameworks are revolutionizing credit risk management by providing real-time underwriting capabilities and early warning systems that ingest external market data. By digitizing legacy archives and investing in real-time data stores, banks are creating a robust foundation for advanced generative AI applications and continuous analytics. Ultimately, this shift toward a unified data architecture is essential for maintaining transparency, regulatory oversight, and enterprise-wide decision-making in an increasingly volatile and data-intensive financial landscape.


Why nobody cares about laptop touchscreens anymore

In the article "Why nobody cares about laptop touchscreens anymore," author Chris Hoffman argues that the once-coveted feature has become a neglected afterthought for both hardware manufacturers and Microsoft. While touchscreens remain prevalent on Windows 11 devices, they are rarely showcased in marketing because the industry has shifted focus toward performance, battery life, and AI integration. Hoffman posits that the initial appeal of touchscreens was largely a workaround for the poor-quality trackpads found on older Windows 10 machines. With the advent of highly responsive, "precision" touchpads across modern laptops, the functional necessity of reaching for the screen has vanished. Furthermore, Windows 11 lacks a truly optimized touch interface, and the ecosystem of touch-first applications has stagnated since the Windows 8 era. Even on 2-in-1 convertible devices, the "tablet mode" is described as an imperfect compromise with awkward ergonomics and watered-down software gestures. Unless a user specifically requires pen input for digital art or note-taking, Hoffman suggests that a touchscreen is now a "check-box" feature that adds little real-world value. Ultimately, the piece advises consumers to prioritize other specifications, as the current Windows environment remains firmly a mouse-and-keyboard-first experience, leaving the touchscreen as a redundant relic of past design ambitions.


How AI is changing your mind

In the Computerworld article "How AI is changing your mind," Mike Elgan warns that the widespread adoption of artificial intelligence is fundamentally altering human cognition and social interaction. Drawing on recent research from institutions like Cornell and USC, Elgan identifies two primary dangers: behavioral manipulation and the homogenization of thought. Studies show that biased AI autocomplete tools can successfully shift user opinions on controversial topics—even when individuals are warned of the bias—because the interactive nature of co-writing makes the influence feel internal. Simultaneously, the reliance on a few dominant Large Language Models (LLMs) is erasing linguistic and cultural diversity, nudging global expression toward a bland, Western-centric "hive mind" through a feedback loop of generic training data. These chatbots act as "co-reasoners," fostering sycophancy and simulated validation that can distort reality, particularly for isolated individuals. To combat this cognitive erosion, Elgan suggests practical strategies: disabling autocomplete, writing without AI to preserve individuality, and treating chatbots as intellectual sparring partners rather than authority figures. Ultimately, the piece argues that while AI offers immense utility, users must consciously protect their mental autonomy from being subtly rewritten by algorithms that prioritize consensus and efficiency over authentic human perspective and diversity of thought.
In the Information Age article "The value of reducing middle-office emissions for ESG," Danielle Price explores how the modernization of middle-office functions—such as reconciliation, trade matching, and risk management—can significantly advance corporate sustainability. Historically, these processes have been energy-intensive, running continuously on legacy on-premise servers at peak capacity. As ESG performance increasingly influences a bank’s cost of capital, CIOs must view the middle office as a strategic asset for decarbonization. Migrating these data-heavy workloads to public, cloud-native infrastructure can reduce operational emissions by 60% to 80% without requiring fundamental changes to business processes. This transition is becoming essential as Pillar 3 disclosures demand more granular ESG reporting and evidence of measurable year-on-year reductions. Financially, high ESG scores are linked to lower credit spreads and reduced regulatory capital charges, making infrastructure efficiency a direct factor in a firm’s financial health. Furthermore, the shift to cloud-native platforms creates a powerful network effect; when shared systems lower their carbon footprint, the entire counter-party ecosystem benefits. Ultimately, the article argues that aligning operational efficiency with ESG objectives is no longer optional, but a strategic imperative that combines environmental stewardship with enhanced financial competitiveness in today's global capital markets.


New European Emissions Regs Include Cybersecurity Rules

The article from Data Breach Today details the integration of new cybersecurity requirements into the European Union's "Euro 7" emissions regulations, marking a significant shift in automotive compliance. Prompted by the "Dieselgate" scandal, these rules mandate that gas-powered vehicles feature on-board systems to monitor emissions data, which must be protected from tampering, spoofing, and unauthorized over-the-air updates. While the regulations primarily target malicious external hackers, they also aim to prevent corporate fraud. However, a major point of contention has emerged: the potential conflict with the "right-to-repair" movement. The same secure gateway technologies used to prevent unauthorized modifications to engine control units could effectively lock out independent mechanics, who require access to diagnostic data for legitimate repairs. Automotive experts warn that while most passenger vehicle manufacturers are prepared, the commercial sector lags behind, and the industry faces an immense architectural challenge in balancing security with equitable data access. Furthermore, as cars become increasingly connected, broader risks—including remote takeovers and sensitive data leaks—remain a concern for EU public safety, suggesting that current type-approval regimes may need to evolve to address nation-state threats and organized cybercrime.


Why Data Governance Fails in Many Organizations: The Accountability Crisis and Capability Gaps

In the article "Why Data Governance Fails in Many Organizations," Stanyslas Matayo explores the critical factors behind the high failure rate of data governance initiatives, specifically highlighting the "accountability crisis" and "capability gaps." Despite significant investments, many organizations engage in "governance theater," where committees exist on paper but lack the executive authority, seniority, and enforcement mechanisms to drive change. This accountability gap is exacerbated when governance roles report to mid-level IT rather than leadership, rendering them expendable scribes rather than strategic governors. Simultaneously, a "capability deficit" arises when initiatives are treated as purely technical projects. Teams often overlook essential non-technical skills like change management, ethics, and learning design, assuming technical expertise alone is sufficient for organizational transformation. To combat these failures, the author references the DMBOK framework, advocating for four pillars: formal role clarification (e.g., Data Owners and Stewards), governed metadata, explicit quality mechanisms, and aligned communication flows. Ultimately, success requires moving beyond technical delivery to establish a business-led discipline where data is managed as a strategic asset through senior-level sponsorship and a holistic integration of diverse organizational capabilities, ensuring that governance structures possess the actual power to resolve conflicts and enforce standards.


AI coding agents keep repeating decade-old security mistakes

The Help Net Security article "AI coding agents keep repeating decade-old security mistakes" details a 2026 study by DryRun Security that evaluated the security performance of Claude Code, OpenAI Codex, and Google Gemini. Researchers discovered that despite their rapid software generation capabilities, these AI agents introduced vulnerabilities in 87% of the pull requests they created. The study identified ten recurring vulnerability categories across all three agents, with broken access control, unauthenticated sensitive endpoints, and business logic failures being the most prevalent. For example, agents frequently failed to implement server-side validation for critical actions or neglected to wire authentication middleware into WebSocket handlers. While OpenAI Codex generally produced the fewest vulnerabilities, all agents struggled with secure JWT secret management and rate limiting. The report emphasizes that traditional regex-based static analysis tools often miss these complex logic and authorization flaws, as they cannot reason about data flows or trust boundaries effectively. Consequently, the study recommends that development teams scan every pull request, incorporate security reviews into the initial planning phase, and utilize contextual security analysis tools. Ultimately, while AI agents significantly accelerate development, their lack of inherent security-centric reasoning necessitates rigorous human oversight and advanced scanning to prevent the recurrence of foundational security errors.


Impact of Artificial Intelligence (AI) in Enterprise Architecture (EA) Discipline

The article "Impact of Artificial Intelligence (AI) in Enterprise Architecture (EA) Discipline" examines how AI is fundamentally reshaping the traditional responsibilities of enterprise architects. By integrating advanced AI tools into the EA framework, organizations can automate labor-intensive tasks such as data mapping and technical documentation, allowing architects to focus on higher-value strategic initiatives that drive business value. AI-driven analytics provide architects with deeper, real-time insights into complex system dependencies, enabling more accurate predictive modeling and significantly faster decision-making across the enterprise. This technological shift encourages a transition away from static, reactive architectures toward dynamic, proactive ecosystems that can autonomously adapt to rapid market changes and emerging digital threats. However, the author emphasizes that this transition is not without its hurdles; it necessitates a robust foundation in data governance, careful ethical considerations regarding AI bias, and a long-term commitment to upskilling the existing workforce. Ultimately, the fusion of AI and EA facilitates much better alignment between high-level business goals and underlying IT infrastructure, driving continuous innovation and operational efficiency. As the discipline evolves, the most successful enterprise architects will be those who leverage AI as a sophisticated collaborative partner to manage organizational complexity and provide strategic foresight in an increasingly competitive digital landscape.

Daily Tech Digest - February 08, 2026


Quote for the day:

"The litmus test for our success as Leaders is not how many people we are leading, but how many we are transforming into leaders" -- Kayode Fayemi


Why agentic AI and unified commerce will define ecommerce in 2026

Agentic AI and unified commerce are set to shape ecommerce in 2026 because the foundations are now in place: consumers are increasingly comfortable using AI tools, and retailers are under pressure to operate seamlessly across channels. ... When inventory, orders, pricing, and customer context live in disconnected systems, both humans and AI struggle to deliver consistent experiences. When those systems are unified, retailers can enable more reliable automation, better availability promises, and more resilient fulfillment, especially at peak. ... Unified commerce platforms matter because they provide a single operational framework for inventory, orders, pricing, and customer context. That coordination is increasingly critical as more interactions become automated or AI-assisted. ... The shift toward “agentic” happens when AI can safely take actions, like resolving a customer service step, updating a product feed, or proposing a replenishment recommendation, based on reliable data and explicit rules. That’s why unified commerce matters: it reduces the risk of automation acting on partial truth. Because ROI varies dramatically by category, maturity, and data quality, it’s safer to avoid generic percentage claims. The defensible message is: companies that pair AI with clean operational data and clear governance will unlock automation faster and with fewer reputational risks. ... Ultimately, success in 2026 will not be defined by how many AI features a retailer deploys, but by how well their systems can interpret context, act reliably, and scale under pressure.


EU's Digital Sovereignty Depends On Investment In Open-Source And Talent

We argue that Europe must think differently and invest where it matters, leveraging its strengths, and open technologies are the place to look. While Europe does not have the tech giants of the US and China, it possesses a huge pool of innovation and human capital, as well as a small army of capable and efficient technology service providers, start-ups, and SMEs. ... Recent data shows that while Europe accounts for a substantial share of global open source developers, its contribution to open source-derived infrastructure remains fragmented across countries, with development being concentrated in a small number of countries. ... Europe may not have a Silicon Valley, but it has something better: a robust open source workforce. We are beginning to recognize this through fora such as the recent European Open Source Awards, which celebrated European citizens and residents working on things ranging from the Linux kernel and open office suites to open hardware and software preservation. ... Europe has a chance of succeeding. Historically, Europe has done a good job in making open source and open standards a matter of public policy. For example, the European Commission's DG DIGIT has an open source software strategy which is being renewed this year, and Europe possesses three European Standards Organizations, including CEN, CENELEC, and ETSI. While China has an open source software strategy, Europe is arguably leading the US in harnessing the potential of open technologies as a matter of public and industrial policy, and it has a strong foundation for catching up to China.


Is artificial general intelligence already here? A new case that today's LLMs meet key tests

Approaching the AGI question from different disciplinary perspectives—philosophy, machine learning, linguistics, and cognitive science—the four scholars converged on a controversial conclusion: by reasonable standards, current large language models (LLMs) already constitute AGI. Their argument addresses three key questions: What is general intelligence? Why does this conclusion provoke such strong reactions? And what does it mean for ... "There is a common misconception that AGI must be perfect—knowing everything, solving every problem—but no individual human can do that," explains Chen, who is lead author. "The debate often conflates general intelligence with superintelligence. The real question is whether LLMs display the flexible, general competence characteristic of human thought. Our conclusion: insofar as individual humans possess general intelligence, current LLMs do too." ... "This is an emotionally charged topic because it challenges human exceptionalism and our standing as being uniquely intelligent," says Belkin. "Copernicus displaced humans from the center of the universe, Darwin displaced humans from a privileged place in nature; now we are contending with the prospect that there are more kinds of minds than we had previously entertained." ... "We're developing AI systems that can dramatically impact the world without being mediated through a human and this raises a host of challenging ethical, societal, and psychological questions," explains Danks.


Biometrics deployments at scale need transparency to help businesses, gain trust

As adoption invites scrutiny, more biometrics evaluations, completed assessments and testing options come available. Communication is part of the same issue, with major projects like EES, U.S. immigration and protest enforcement, and more pedestrian applications like access control and mDLs all taking off. ... Biometric physical access control is growing everywhere, but with some key sectorial and regional differences, Goode Intelligence Chief Analyst Alan Goode explains in a preview of his firm’s latest market research report on the latest episode of the Biometric Update Podcast. Imprivata could soon be on the market, with PE owner Thoma Bravo working with JPMorgan and Evercore to begin exploring its options. ... A panel at the “Identity, Authentication, and the Road Ahead 2026” event looked at NIST’s work on a playbook to help businesses implement mDLs. Representatives from the NCCoE, Better Identity Coalition, PNC Bank and AAMVA discussed the emerging situation, in which digital verifiable credentials are available, but people don’t know how to use them. ... DHS S&T found 5 of 16 selfie biometrics providers met the performance goals of its Remote Identity Validation Rally, Shufti and Paravision among them. RIVR’s first phase showed that demographically similar imposters still pose a significant problem for many face biometrics developers.


The Invisible Labor Force Powering AI

A low-cost labor force is essential to how today’s AI models function. Human workers are needed at every stage of AI production for tasks like creating and annotating data, reinforcing models, and moderating content. “Today’s frontier models are not self-made. They’re socio-technical systems whose quality and safety hinge on human labor,” said Mark Graham, a professor at the University of Oxford Internet Institute and a director of the Fairwork project, which evaluates digital labor platforms. In his book Feeding the Machine: the Hidden Human Labor Powering AI (Bloomsbury, 2024), Graham and his co-authors illustrate that this global workforce is essential to making these systems usable. “Without an ongoing, large human-in-the-loop layer, current capabilities would be far more brittle and misaligned, especially on safety-critical or culturally sensitive tasks,” Graham said. ... The industry’s reliance on a distributed, gig-work model goes back years. Hung points to the creation of the ImageNet database around 2007 as the moment that set the referential data practices and work organization for modern AI training. ... However, cost is not the only factor. Graham noted that cost arbitrage plays a role, but it is not the whole explanation. AI labs, he said, need extreme scale and elasticity, meaning millions of small, episodic tasks that can be staffed up or down at short notice, as well as broad linguistic and cultural coverage that no single in-house team can reproduce.


Code smells for AI agents: Q&A with Eno Reyes of Factory

In order to build a good agent, you have to have one that's model agnostic. It needs to be deployable in any environment, any OS, any IDE. A lot of the tools out there force you to make a hard trade off that we felt wasn't necessary. You either have to vendor lock yourself to one LLM or ask everyone at your company to switch IDEs. To build like a true model agnostic, vendor agnostic coding agent, you put in a bunch of time and effort to figure out all the harness engineering that's necessary to make that succeed, which we think is a fairly different skillset from building models. And so that's why we think companies like us actually are able to build agents that outperform on most evaluations from our lab. ... All LLMs have context limits so you have to manage that as the agent progresses through tasks that may take as long as eight to ten hours of continuous work. There are things like how you choose to instruct or inject environment information. It's how you handle tool calls. The sum of all of these things requires attention to detail. There really is no individual secret. Which is also why we think companies like us can actually do this. It's the sum of hundreds of little optimizations. The industrial process of building these harnesses is what we think is interesting or differentiated. ... Of course end-to-end and unit tests. There are auto formatters that you can bring in, SaaS static application security testers and scanners: your sneaks of the world.


Software-Defined Vehicles Transform Auto Industry With Four-Stage Maturity Framework For Engineers

More refined software architectures in both edge and cloud enable the interpretation of real-time data for predictive maintenance, adaptive user interfaces, and autonomous driving functions, while cloud-based AI virtualized development systems enable continuous learning and updates. Electrification has only further accelerated this evolution as it opened the door for tech players from other industries to enter the automotive market. This represents an unstoppable trend as customers now expect the same seamless digital experiences they enjoy on other devices. ... Legacy vehicle systems rely on dozens of electronic control units (ECUs), each managing isolated functions, such as powertrain or infotainment systems. SDVs consolidate these functions into centralized compute domains connected by high-speed networks. This architecture provides hardware and software abstraction, enabling OTA updates, seamless cross-domain feature integration, and real-time data sharing, are essential for continuous innovation. ... Processing sensor data at the edge – directly within the vehicle – enables highly personalized experiences for drivers and passengers. It also supports predictive maintenance, allowing vehicles to anticipate mechanical issues before they occur and proactively schedule service to minimize downtime and improve reliability. Equally important are abstraction layers that decouple software applications from underlying hardware.


Cybersecurity and Privacy Risks in Brain-Computer Interfaces and Neurotechnology

Neuromorphic computing is developing faster than predicted by replicating the human brain's neural architecture for efficient, low-power AI computation. As highlighted in talks around brain-inspired chips and meshing, these systems are blurring distinctions between biological and silicon-based computation. In the meanwhile, bidirectional communication is made possible by BCIs, such as those being developed by businesses and research facilities, which can read brain activity for feedback or control and possibly write signals back to affect cognition. ... Neural data is essentially personal. Breaches could expose memories, emotions, or subconscious biases. Adversaries may reverse-engineer intentions for coercion, fraud, or espionage as AI decodes brain scans for "mind captioning" or talent uploading. ... Compromised BCIs blur cyber-physical boundaries farther than OT-IT convergence already has. A malevolent actor might damage medical implants, alter augmented reality overlays, or weaponize neurotech in national security scenarios. ... Implantable devices rely on worldwide supply chains prone to tampering. Neuromorphic hardware, while efficient, provides additional attack surfaces if not designed with zero-trust principles. Using AI to process neural signals can introduce biases, which may result in unfair treatment in brain-augmented systems 


Designing for Failure: Chaos Engineering Principles in System Design

To design for failure, we must understand how the system behaves when failure inevitably happens. What is the cost? What is the impact? How do we mitigate it? How do we still maintain over 99% uptime? This requires treating failure as a default state, not an exception. ... The first step is defining steady-state behavior. Without this, there is no baseline to measure against. ... Chaos experiments are most valuable in production. This is where real traffic patterns, real user behavior, and real data shapes exist. That said, experiments must be controlled. ... Chaos Engineering is not a one-off exercise. Systems evolve. Dependencies change. Teams rotate. Experiments should be automated, repeatable, and run continuously, either as scheduled jobs or integrated into CI/CD pipelines. Over time, experiments can be expanded to test higher-impact scenarios. ... Additional considerations include health checks, failover timing, and data consistency. Strong consistency simplifies reasoning but reduces availability. Eventual consistency improves availability but introduces complexity and potential inconsistency windows. ... Network failures are unavoidable in distributed systems. Latency spikes, packets get dropped, DNS fails, and sometimes the network splits entirely. Many system outages are not caused by servers crashing, but by slow or unreliable communication between otherwise healthy components. This is where several of the classic fallacies of distributed computing show up, especially the assumption that the network is reliable and has zero latency.


Why SMBs Need Strong Data Governance Practices

Good data governance for small businesses is about building trust, control and scalability into your data from day one. Governance should be built into the data foundation, not bolted on later. Small businesses move fast, and governance works best when it’s native to how data is managed. That means choosing platforms that apply security, access controls and compliance consistently across all data, without requiring manual oversight or specialized teams. Additionally, clear visibility and control over what data exists and who can access it is essential. Even at a smaller scale, businesses handle sensitive information ranging from customer and financial data to operational insights. ... Governance also future proofs the business. Regulations are becoming more complex, customer expectations for data protection are rising, and AI systems must have high-quality, well-governed data to perform reliably. Small businesses that treat governance as a foundation are better positioned to adopt AI and safely expand into new use cases, markets and regulatory environments without needing to rearchitect later. At the same time, strong data governance improves day-to-day efficiency. When data is well governed, teams can spend more time acting on insights and less time questioning data quality, managing access manually or duplicating work. ... From a cybersecurity perspective, governance provides the controls and visibility needed to reduce attack surfaces and detect misuse.