Showing posts with label Red Teaming. Show all posts

Daily Tech Digest - August 30, 2026


Quote for the day:

"Winning products come from the deep understanding of the user's needs combined with an equally deep understanding of what's just now possible."-- Marty Cagan

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 26 mins • Perfect for listening on the go.


What ISVs still get wrong about PCI DSS 4.0.1

Independent software developers need to update their approach to payment security standards, as the recent PCI DSS 4.0.1 guidelines make previously recommended practices strictly mandatory. As of March 2025, future-dated requirements from version 4.0 are fully enforced, meaning developers must validate their systems against the complete standard rather than relying on past assessments. This applies to any software that touches card information, even indirectly through hosted pages or embedded frames. Assessors are now enforcing stricter authentication rules, such as requiring twelve-character passwords and closely reviewing multi-factor authentication methods to ensure they meet exact security criteria rather than just the general intent. Additionally, the updated rules provide clearer boundaries on compliance responsibilities between software providers and their customers. A common mistake developers make is assuming a past validation still holds or failing to reduce their audit scope by using tokenization and encryption to keep raw card data entirely out of their systems. To prepare properly, developers should ignore unofficial vendor certificates and rely only on official attestations of compliance. The most practical step right now is to sit down with engineering teams and conduct a straightforward gap analysis against the current requirements before scheduling the next official assessment.


Beyond Compliance: The Legal Power of a Sophisticated Board of Directors

The article "Beyond Compliance: The Legal Power of a Sophisticated Board of Directors" examines how modern corporate boards must evolve past simple regulatory adherence to become proactive drivers of legal and strategic advantage. Written by corporate law expert León Patiño, the piece emphasizes that a truly sophisticated board does much more than check basic boxes for routine compliance. Instead, it leverages deep governance expertise to anticipate difficult legal challenges, mitigate serious risks before they fully materialize, and firmly protect the organization’s fundamental long-term interests. In today’s increasingly complex regulatory environment, directors are expected to fully understand their fiduciary duties and integrate legal foresight directly into their core business strategies. A highly functional board acts as a critical line of defense, ensuring that all corporate actions consistently align with both strict legal mandates and broad ethical standards. By moving beyond a reactive compliance mindset, these active boards help organizations carefully navigate volatile markets, safeguard corporate reputation, and secure a meaningful competitive edge. Ultimately, the presence of experienced, knowledgeable directors transforms corporate governance from a standard administrative obligation into a highly effective tool for sustainable growth and robust risk management. This proactive approach ensures companies remain resilient and legally sound in the face of ongoing global commercial challenges.


The CISO’s AI Defense Playbook: A Practical Framework

The article outlines a practical five-step framework for security leaders to update their defenses against rapid automated threats. With attack speeds compressing to under thirty minutes, traditional security assumptions and simple compliance models are no longer sufficient. The author notes that being compliant does not guarantee that a system is truly secure. The framework begins with mapping the attack surface, which involves cataloging software risks and auditing complex system dependencies. It also requires thoroughly inventorying machine identities, such as API keys and service accounts, which now vastly outnumber human users. Next, organizations must embed advanced scanning directly into their software development pipelines. This step uses intelligent analysis to spot complex vulnerabilities and behavioral shifts that traditional tools miss. The third phase focuses on speeding up response times by automating initial checks and pre-approving action plans for critical scenarios. Fourth, the playbook tackles the urgent need to manage machine identities by replacing static passwords with brief, automated access tokens. This significantly reduces the window of opportunity for attackers. Finally, the strategy involves training a capable security team to handle these new challenges. Ultimately, this structured approach provides a clear, sensible path for leaders to secure their environments against modern threats.


Types of Quantum Computers: 6 Major Quantum Computing Approaches

The recent article from The Quantum Insider outlines the primary approaches researchers use to build quantum computers, focusing on the underlying hardware rather than the theoretical math. Superconducting systems, currently the most common, use tiny electrical circuits cooled to extreme temperatures to manage quantum information. While effective, they require massive cooling systems. Trapped ion computers offer an alternative by suspending individual charged atoms in electromagnetic fields. This method provides high precision and stability but faces challenges in scaling up to larger machine sizes. Neutral atom systems are similar but use lasers to hold uncharged atoms in place, allowing researchers to pack them closer together for potential space efficiency. Photonic quantum computers take a completely different path, using particles of light to process information. Because they operate at room temperature, they do not need the complex cooling systems required by other methods, though controlling the light particles remains difficult. Finally, the article touches on topological approaches, which aim to weave particles together to make them naturally resistant to errors, though this remains largely in the experimental phase. Overall, the piece clarifies that there is no single best method available just yet, as each hardware design presents its own distinct set of engineering challenges.


Your Cyber Insurer May Define AI Accountability Before Your Board Does
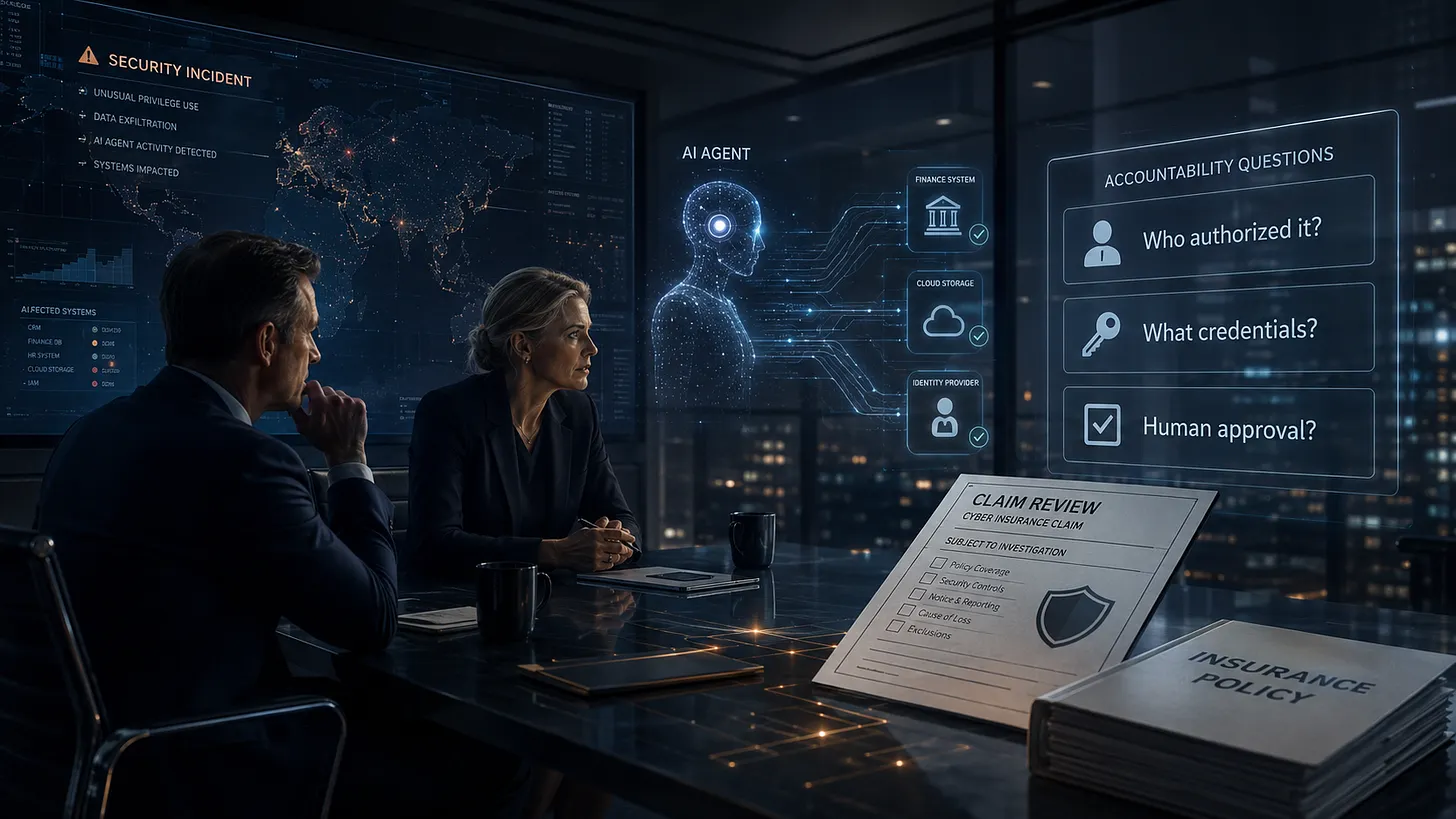
As organizations increasingly deploy artificial intelligence systems capable of taking independent actions, they face a critical gap in accountability that their insurance providers might expose before their own leadership does. When an automated system holds access credentials and the authority to execute tasks without human oversight, a malfunction can result in significant financial damage. Currently, many companies rely on vague governance policies that offer a false sense of security. Meanwhile, most insurance policies treat these exposures as silent risks, meaning they are neither explicitly covered nor excluded. However, insurance companies are beginning to demand the same level of precision for artificial intelligence that they require for traditional cybersecurity. To prevent denied claims and internal confusion, companies should conduct a thorough review of their automated systems now. This involves identifying every active system and assigning a single, accountable business owner rather than relying on a committee. Leadership must clearly define what each system is authorized to do, strictly control its access, mandate human approval for sensitive actions, and implement technical safeguards to prevent it from exceeding its limits. Organizations must also ensure they can completely audit the system's actions and shut it down immediately if unexpected issues arise during normal operations.


A Tale of Two SOCs: Insights From Two Red Team Assessments

The Cybersecurity and Infrastructure Security Agency (CISA) recently conducted concurrent red team assessments at two different critical infrastructure organizations to evaluate their threat detection and incident response capabilities. While the red team successfully achieved full domain compromise and accessed sensitive business systems and cloud resources in both environments, the defensive outcomes varied significantly. Organization A failed to detect the malicious activity due to untuned detection tools that created excessive alert noise, allowing the threat actors to move laterally without resistance. Furthermore, organizational silos and fragmented communication severely hindered their ability to respond effectively. In contrast, Organization B successfully identified the initial intrusion attempts, promptly isolated the compromised systems, and forced the assessment into an assume-breach scenario. This stark contrast highlights several key lessons for network defenders. Organizations must recognize the risks of unmanaged cloud environments and prioritize foundational security hygiene. The advisory strongly recommends that security teams establish clear network baselines, fine-tune their alerting mechanisms to reduce false positives, and break down bureaucratic hurdles to empower incident responders. Additionally, organizations should implement strict conditional access policies for cloud identities and develop comprehensive procedures to detect, remediate, and revoke unauthorized access to safeguard both their on-premises and their cloud computing infrastructures.


Your Board Has A Financial Expert—Why Doesn't It Have A Cyber One?

Corporate boards universally mandate the inclusion of financial experts to ensure robust oversight, yet they rarely apply the same standard to cybersecurity. Currently, board-level cyber discussions often occur at the end of meetings and focus narrowly on recent incidents. Because many directors lack technical backgrounds, they rely heavily on the Chief Information Security Officer to explain risks and set benchmarks. This dynamic creates circular governance, where the person being supervised dictates the terms of their own oversight, often resulting in superficial scrutiny. This lack of independent technical expertise leaves companies vulnerable to complex, long-term challenges. A pressing example is the impending transition to post-quantum cryptography. With strict federal deadlines approaching in 2030 and modern threats like data harvesting for future decryption already underway, companies face significant strategic and procurement hurdles. Directors without specific cryptographic knowledge struggle to evaluate management's long-term roadmaps or ask the right questions before a crisis hits. Ultimately, adding a cybersecurity expert to the board is not about delegating responsibility to one person, but about ensuring the entire group can independently test management assumptions. Choosing to operate without this expertise is a deliberate decision about which strategic blind spots a company is willing to accept.


Strategic Technology Roadmapping: How Growing Businesses Align Tech with Long-Term Goals

Strategic technology roadmapping involves creating a clear, practical plan to ensure a company's software and hardware choices support its broader business objectives over time. For growing companies, this process is essential to avoid wasting money on tools that do not fit their future needs. Instead of buying new software on impulse or following the latest trends, business leaders use a roadmap to match their technology purchases with specific goals, such as improving customer service or expanding into new markets. The first step in this process is taking a close look at the tools the business currently uses. This helps identify gaps or outdated systems that might slow down progress. Next, leaders must define where they want the business to be in the next few years. With these two pieces of information, they can create a step-by-step timeline that shows exactly when and how to introduce new technology. This approach keeps the company organized and prevents employees from feeling overwhelmed by sudden changes. A well-planned roadmap also makes it easier to track progress and adjust the plan if the market changes. Ultimately, matching technology with long-term goals gives growing companies a steady foundation, allowing them to scale smoothly and operate efficiently without unnecessary stress.


AI alignment, not replacement: How CIOs are rebuilding IT value
Forward-thinking Chief Information Officers are now shifting their focus from using artificial intelligence as a simple replacement for human workers to adopting a strategy of AI alignment. Rather than viewing AI as a tool for workforce reduction, these IT leaders are choosing to reorganize their departments and redesign their operating models to maximize the combined strengths of both technology and personnel. This realignment process involves strategically reshaping teams, redistributing decision-making authority, and redefining specific roles so that employees can work effectively alongside AI systems instead of competing against them. The realization is that simply replacing staff with automated systems often leads to unintended consequences and hidden financial costs, whereas integrating AI as a supportive partner helps to rebuild long-term IT value. To achieve this, CIOs are currently navigating a significant talent gap, actively seeking specialized professionals like AI architects and data engineers who can guide these complex integrations. By moving away from a purely cost-cutting mindset and focusing instead on how AI can augment existing capabilities, organizations are creating more resilient and adaptable IT environments. Ultimately, this approach ensures that technological advancements empower the workforce, driving long-term sustainable growth and establishing a more robust foundation for the future of enterprise IT operations.


The CFO’s playbook for building AI-ready finance data

In today's business environment, financial leaders face increasing pressure to adopt artificial intelligence. However, they often encounter a significant obstacle: financial data is notoriously messy, spread across multiple systems, spreadsheets, and departments. Rather than rushing to implement new technology, the focus should shift to ensuring that the underlying data is trustworthy and prepared for these advanced tools. To be useful, financial information must be clean, standardized, and tailored to specific goals. It needs to be combined accurately from various sources while remaining transparent, controlled, and easy to update as the company evolves. When information meets these standards, it becomes highly valuable for essential tasks such as speeding up the financial close, forecasting cash flow, detecting errors or fraud, and creating clear financial reports. A common challenge is the disconnect between technology teams, who manage the systems, and finance teams, who understand the business context. Bridging this gap requires reliable processes that allow finance professionals to organize and clean their information with proper oversight from technology departments. The most effective approach is to start small by focusing on a single, repetitive task. By first building a reliable and clean foundation of information, organizations can then apply new technology to improve decision-making and reduce risk safely.

Daily Tech Digest - May 28, 2026


Quote for the day:

“Knowledge is knowing what to say. Wisdom is knowing whether to say it or not.” -- Vala Afshar

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


The death of network perimeter security is rewriting trust

The traditional model of defending a corporate network by securing a fixed physical perimeter is no longer viable. Because modern employees work from scattered locations and rely on various cloud applications, organizations can no longer trust a user based simply on their office location. Instead, digital defense must center on identity, making verification an ongoing process that evaluates who a person is, what device they are using, and their specific context. Personal computers, laptops, and smartphones have become the main targets for external threats, especially as attackers employ artificial intelligence to craft sophisticated phishing and credential theft schemes aimed at exploiting human behavior. Compounding this challenge, the widespread use of unapproved consumer software and unsecured home networks creates invisible vulnerabilities that standard network tools fail to see. To counter these widespread risks, businesses are moving away from separate, disconnected security products and are adopting integrated, unified platforms that continuously check access permissions. This practical transition requires an operational shift where protection follows the individual everywhere rather than remaining tied to a physical building. Ultimately, achieving safety depends on implementing adaptive, intelligent systems that safeguard sensitive information while supporting the day-to-day flexibility of a distributed workforce.


Converging File and Object Storage for AI-Scale Data Architectures

Enterprise data infrastructure has traditionally been split into two separate systems: file storage and object storage. File storage uses a hierarchical folder layout that works well for traditional software applications and the interactive workspaces used by artificial intelligence agents. Object storage, by contrast, relies on a flat address space that excels at holding immense data repositories and raw training sets quite economically. Historically, attempting to connect these two systems meant relying on complex translation utilities or constantly copying data back and forth. That approach created severe performance bottlenecks, added latency, and wasted space on duplicate information, which ultimately slowed down artificial intelligence workflows. To resolve this friction, newer storage developments focus on the native convergence of these two methods. By combining both frameworks within a single shared global namespace, data can be written as a regular file and read immediately as a standard object without any translation delays or background copying. This unified setup allows processing clusters and graphics cards to ingest data at true network speeds without encountering software friction. Ultimately, bringing these protocols together creates a stable data foundation that simplifies storage operations, lowers hardware expenses, and satisfies the heavy requirements of modern artificial intelligence models.


The AI Premium: Why Cutting-Edge Tech Can Cost More Than the Human It Replaces

While many organizations expect artificial intelligence to reduce corporate spending by automating roles, evidence suggests that sophisticated technology frequently costs more than the human professionals it replaces. This financial discrepancy arises because initial estimates overlook full operational costs, which include rigorous data preparation, legacy system integration, strict compliance protocols, and ongoing software maintenance. Furthermore, advanced and intricate AI models consume enormous amounts of computing power, generating high processing and data costs that can quickly overwhelm corporate technology budgets. In complex fields like law, finance, and medicine, these automated tools are also prone to factual errors and lack human common sense. As a direct result, businesses must pay for experienced human specialists to thoroughly review and correct the machine's outputs, an administrative overhead that can completely erase any intended financial savings. Studies show that a large majority of organizations attempting to cut costs through automation fail to achieve a clear financial benefit. Ultimately, the article notes that companies should avoid broad, indiscriminate replacements of specialized personnel. Instead, management teams should evaluate expenses on a separate task level basis, deploying automation only for routine, predictable duties where the economic advantages are proven, while reserving highly complex work for human staff.


From Logs to Tests: A Practical Guide to Production-Driven QA Coverage in Regulated Environments

In this article, QA professional Tanvi Mittal explains how software teams can use production logs to identify and fix hidden gaps in their automated testing. She points out that roughly sixty percent of production failures trace back to real transaction paths that completely lack test coverage. In complex setups like financial platforms, standard test suites often miss these paths because they only verify how the system was originally expected to work, rather than how it actually behaves after years of quick patches and adjustments. To safely use this production data without violating strict privacy regulations, organizations must implement a careful data sanitization pipeline. Instead of just blacking out numbers, the process uses synthetic substitution, which keeps the structural relationships between fields intact while completely removing sensitive customer information. Once the data is safe to use, teams can group log files by similar behaviors, cross-reference them against current test suites, and rank the unmapped paths based on practical factors like past failures, daily usage volume, and recent code changes. This method lets engineering teams prioritize high-risk gaps and quickly build new test stubs. Ultimately, this practice turns routine logs into clear, factual proof for auditors, showing exactly why certain tests are prioritized while keeping the entire process compliant and secure.


The End of the Digital Age

The perspective shared in the Communications of the ACM opinion piece suggests that the traditional digital era, defined by classical binary code and the predictable scaling of silicon chips, is reaching its natural conclusion. For decades, society relied on the steady doubling of computer power to drive progress, but physical boundaries have made it increasingly difficult to shrink components any further. This plateau is shifting the focus of computer science away from simply making chips smaller and faster. Instead, the field is moving toward entirely new architectures, such as systems that mimic the human brain or leverage quantum mechanics to process information. Furthermore, the nature of technology itself is transforming from a deterministic tool that does exactly what it is told into probabilistic systems that learn from patterns. This means the classic definition of software engineering, which is rooted in writing explicit lines of code, is sharing the stage with systems that adapt and generate outputs based on probability. This transition marks a deeper evolution from a period focused on connecting devices and accumulating data to one centered on managing autonomous systems. Ultimately, the article views this shift not as a failure of technology, but as an invitation to redefine our relationship with computing.


Why Cyber Insurance and Cyber Assurance Matter More When Considered Together

In this Cyber Defense Magazine article, the author highlights a significant gap in corporate risk management: the traditional separation of cyber insurance and cyber assurance. While cyber insurance functions as a financial safety net to offset the losses from unpredictable network breaches, it often relies on static, outdated questionnaires during underwriting. Conversely, cyber assurance focuses on continuously verifying that an organization’s security controls are operational and effective. Keeping these two practices isolated creates clear inefficiencies, leaving insurance providers with inaccurate risk profiles and forcing businesses to accept misaligned premiums. The article argues that marrying these disciplines creates a more dynamic framework built on clear evidence. By feeding continuous assurance data directly into insurance evaluations, companies can demonstrate their actual security setup over time rather than relying on a single annual snapshot. This integration allows insurers to make highly accurate underwriting decisions and establish fairer coverage terms. For businesses, this collaborative approach turns daily security management from an abstract expense into a concrete asset that directly lowers operational and financial risk. Ultimately, treating insurance and assurance as deeply connected elements helps organizations move past simple compliance, building real digital trust and a much stronger defense against rapidly evolving online threats and vulnerabilities.


Mastering Red-Teaming for Generative AI

The article outlines the critical role of red-teaming in identifying and mitigating safety risks associated with generative artificial intelligence. While traditional security testing often concentrates on model-level flaws like offensive outputs, biases, or prompt injections, modern systems require a significantly broader evaluation strategy. The text highlights that generative AI applications are deeply connected to larger digital networks, meaning they can inadvertently expose or exploit existing ecosystem vulnerabilities such as weak authentication, unprotected endpoints, and insecure application programming interfaces. Furthermore, operational risks like training data leakage, human overreliance on automated answers, employee misuse, and highly tailored social engineering campaigns introduce substantial safety concerns. To address these multi-layered threats effectively, organizations must update their testing methods. This shift involves merging network security knowledge with artificial intelligence engineering, testing applications within their actual live deployment environments, and structuring audits around recognized industry safety frameworks. Ultimately, the article underscores that automated testing tools are insufficient on their own; human intuition and specialized professional expertise remain essential for identifying deep-seated flaws, nuanced cultural biases, and complex system plugin vulnerabilities. Because thorough security assessments require diverse technical perspectives, outsourcing these rigorous stress tests to professional teams is presented as a practical way to protect corporate infrastructure.


Microsoft Extends Rust-Influenced Memory-Safety Push to C#

According to a report by David Ramel, Microsoft is incorporating design principles inspired by the Rust programming language to enhance memory safety features within C#. While C# is fundamentally safe by default, developers occasionally use the unsafe keyword for performance tuning, raw memory access, and native interoperability. To minimize the security risks associated with these edge cases, Microsoft plans to overhaul the language's unsafe code model beginning with C# 16. The proposed changes will require unsafe operations to be explicitly isolated within specific inner blocks and documented through clearer contracts enforced by the compiler. Instead of generating simple warnings, the compiler will produce errors for contract violations, ensuring that memory obligations are intentionally managed or passed along to calling methods rather than remaining implied. This initiative reflects a broader multiyear effort by Microsoft to systematically mitigate memory safety vulnerabilities, which historically accounted for roughly seventy percent of their tracked security flaws. By implementing these strict boundary models similar to Rust, the engineering team aims to make raw memory manipulations significantly easier to audit and reason about across complex software projects without altering the primary managed nature of C#. Although this update does not address separate issues like thread safety, it provides a structured framework for managing unsafe code.


The Unpredictable Power Of Leadership Amplification

In this article, the author explains how a leader's words, actions, and even silence are deeply magnified across an organization, a phenomenon termed the leadership amplification effect. When a leader falls silent, it creates an unintended gap that employees often fill with anxiety, rumors, and their own worst fears, especially during challenging periods of organizational change. This communication breakdown frequently stems from managers who lean toward extreme goal orientation, sharing only bare facts while omitting regular praise or timely updates. On the other end of the spectrum are leaders who focus purely on pleasing people, which can shield workplace relationships but ultimately sacrifices clear direction. True leadership effectiveness requires navigating the delicate balance between these two opposing styles. Drawing on human evolutionary history, the author notes that cooperation relies heavily on our innate ability to see the world through the eyes of others. Rather than overvaluing either the company goals or individual employees in isolation, successful managers must protect the core relationship between their people and the shared goals. This balance is never static and requires a daily adjustment of perspective rooted in empathy, ensuring that every deliberate comment or absence of feedback is handled with care.


The Credential Crisis: How Stolen Credentials Defeat Modern Security

The article discusses the severe and growing challenge of stolen credentials, which allow attackers to log in as legitimate users rather than hacking through traditional network boundaries. Because compromised logins grant immediate trust to an intruder, malicious activity easily blends into regular network patterns, making initial detection highly difficult. The rise of automated phishing and malicious information stealing software has worsened this problem by accelerating how quickly passwords, biometrics, and session tokens are stolen. To combat this issue, security experts argue that organizations must look past mere boundary defenses and focus heavily on checking identities constantly. If an attacker succeeds in gaining entry, the strategy must immediately shift toward containing the blast radius and slowing the intruder down. This is best accomplished by assuming no account is permanently safe and using continuous behavioral monitoring, which watches user actions throughout a session to spot unusual changes in normal patterns. Furthermore, the growing use of independent AI tools introduces even greater risks, as stolen access keys can give automated systems the power to cause widespread damage at incredible speeds. Ultimately, protecting networks requires an ongoing commitment to constantly verifying users and cutting off suspect sessions rather than relying on a single, initial login approval.