Showing posts with label data architecture. Show all posts

Daily Tech Digest - November 07, 2026

Quote for the Day
“An approximate answer to the right question is worth far more than a precise answer to the wrong one.”
— John W. Tukey
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The post-quantum future of web privacy

The Cloudflare blog post explores the transition of web privacy protocols—specifically Privacy Pass—into a post-quantum world through a new technology called MOLE (Moderation Of unLinkable Endorsements). Privacy Pass currently uses classical cryptography (like RSA and elliptic curves) to issue anonymous tokens that allow users to access websites without solving CAPTCHAs or sacrificing their identity. While these tokens are unconditionally private against all attackers, a future quantum computer could forge them and bypass site security measures like rate limiting. To address this, the industry is developing MOLE to handle automated traffic while maintaining strict user privacy. The challenge in upgrading to post-quantum cryptography is the massive increase in data size; for instance, post-quantum ML-DSA-44 signatures are nearly forty times larger than current ECDSA signatures. Because drop-in replacements are not feasible right now, systems will need to be re-engineered to handle heavier cryptographic loads. Ultimately, MOLE and recent breakthroughs in blind signature design offer a promising pathway to secure, seamless, and fully private web authentication long after quantum computers become a reality.

Read Original Article →

The boardroom blind spot: you're measuring compliance, not culture

The boardroom blind spot lies in confusing compliance metrics with actual workplace culture. While corporate boards carry a clear mandate to oversee organizational culture and manage psychosocial risks, they often rely on lagging indicators like headcount, absenteeism, and turnover rates. These data points, typically extracted from standard Human Resource Information Systems, capture transactions and historical events rather than revealing why employees are disengaged or if leaders truly hold their teams' trust. This reliance on compliance-driven data creates a governance gap, masking underlying cultural decay until it erupts into costly turnover or a public crisis. To bridge this gap, modern organizations are pairing core compliance systems with purpose-built employee experience platforms. By tracking real-time insights, boards and executives can capture genuine human intelligence regarding psychological safety and cultural cohesion before problems escalate. Effectively overseeing culture means moving past mere workforce maintenance to active workforce engagement. Ultimately, evaluating whether existing tools actually measure employee sentiment or merely record transactions is no longer just an operational decision—it is a critical governance responsibility.
Read Original Article →
Article Thumbnail

Identity as an Architectural Concern: Enterprise IAM Beyond Authentication

The article emphasizes that as organizations scale, particularly in regulated environments like financial services, identity and access management (IAM) must be integrated directly into a system's core architecture rather than bolted on as an afterthought. For a single application, setting up basic single sign-on (SSO) and authenticating tokens might suffice. However, enterprise systems face complex governance challenges, such as tracking who approved specific access rights and verifying if those rights remain valid months later during an audit. Traditional flat Role-Based Access Control (RBAC) often struggles with these complex relationship queries. The author explains that shifting to a graph-based data model (like Neo4j queried via GraphQL) is far more effective for managing entities like people, service accounts, and resources. In a graph, ownership and access validity are straightforward traversals rather than cumbersome table joins. Designing the data schema early to capture timestamped events for every grant and revocation ensures that critical questions—such as who had access on a specific past date—can be answered efficiently, ultimately reducing the time needed to manage and revoke credentials.

Read Original Article →

The Next Target for Data Breach Lawsuits – Law Firms That Represent Breached Parties

The The Next Target for Data Breach Lawsuits – Law Firms That Represent Breached Parties examines whether lawyers advising companies after data breaches could themselves become targets of lawsuits from affected customers. It draws an important distinction between a law firm being sued because its own systems exposed personal information and being sued for advice given to a breached client about notification and disclosure. Existing legal precedent generally holds that lawyers owe duties to their clients, not automatically to third parties affected by their clients’ actions. This creates a significant hurdle for customers attempting to claim malpractice against outside breach counsel. However, law firms that receive and store personal information may still face ordinary data-security claims if their own handling of that information is challenged. The article warns that expanding liability for breach-response advice could complicate attorney-client relationships, increase insurance and legal costs, and make lawyers more cautious when advising on difficult notification decisions. Its central point is that future lawsuits may increasingly name breach lawyers as defendants, but plaintiffs will still need to establish why those lawyers owed them an independent legal duty.

Read Original Article →
Article Thumbnail

Master Data Management: The Foundation of Enterprise Data Architecture and Security

Modern organizations often struggle with highly inconsistent data that is scattered across many different systems like human resources, billing, and customer management. When the exact same customer or employee is tracked differently in each independent system, it creates confusion that goes far beyond simple record keeping. This inconsistency can easily lead to improper access grants and real security risks if critical updates, such as department changes, fail to reach every application. Master Data Management addresses this exact problem not just by centralizing storage, but by establishing a single, authoritative understanding of core business entities. It clearly establishes who owns the data, where it originally came from, and what relationships exist between different records. This clarity is essential for a reliable enterprise architecture and strong internal security. Instead of applying security controls blindly, identity and access management systems can rely on this accurate, consolidated information to enforce appropriate permissions and data protection rules across the board. By providing proper context and consistent metadata, Master Data Management ensures that applications apply the right security measures, ultimately serving as the reliable foundation needed to keep organizational information completely secure.
Read Original Article →
Article Thumbnail

Study Maps 24 Problems Where Quantum Computers Could Gain an Edge

A recent study has identified 24 computational problems where quantum computers could significantly outperform standard computing methods. However, the researchers emphasize that achieving this theoretical edge in real-world scenarios requires meeting strict mathematical and operational conditions. The compiled list spans diverse fields, including chemistry, optimization, number theory, and data analysis. While quantum algorithms might need far fewer steps to solve complex challenges, such as calculating a molecule's lowest energy state or solving systems of linear equations, practical hurdles remain. Time-consuming tasks like preparing initial data, correcting errors, and extracting usable results can quickly erase any expected speed gains. Furthermore, a meaningful improvement requires the quantum machine to solve problems at a rate exponentially or cubically faster than standard computers to offset the high operating costs of early error-corrected hardware. The study divides these 24 problems into two stages based on their readiness for practical application, providing a realistic roadmap for scientists and industry specialists. Ultimately, the research cautions that translating mathematical advantages into affordable, useful solutions for pressing business and scientific challenges requires overcoming significant hardware and data processing barriers.

Read Original Article →
Article Thumbnail

The CIO’s trust paradox: Your team may be more honest with AI than with you

The CIO’s trust paradox: Your team may be more honest with AI than with you argues that AI is creating a new challenge for workplace trust: employees may be more willing to raise concerns with an AI assistant than with their managers. Research cited in the article suggests psychological safety alone is not enough. Strong teams also need accountability, while trust in AI depends partly on people’s ability to handle uncertainty and judge when AI should be trusted or questioned. The more troubling possibility is that an employee may openly challenge a flawed idea when talking to AI, yet remain silent when the same issue appears in a meeting with senior leaders. In that situation, the organization possesses valuable insight but never receives it. The author urges CIOs to look beyond AI adoption figures and employee sentiment surveys and examine whether dissent actually influences decisions. Organizations should also provide safe ways for employees to move concerns discovered through AI conversations into human decision processes without monitoring private conversations. The central message is that leaders should ask not only whether employees trust AI, but whether they trust colleagues and managers enough to repeat what they tell AI.

Read Original Article →

How technical debt hinders AI rollouts and what to fix first

Technical debt often prevents organizations from successfully rolling out artificial intelligence initiatives, turning expected modernization into costly and disconnected infrastructure islands. For years, enterprises have allowed legacy systems and fragmented tools to coexist, leading to outdated security, siloed data, and inefficient resource allocation. When companies try to implement AI on top of this unstable foundation, they typically face escalating deployment times, decreased feature stability, and significant security risks from unmonitored AI agents carrying overly broad permissions. The resulting complexity forces organizations to manage and secure separate platforms simultaneously. To fix this, IT leaders must assess how their existing technical debt impacts their specific AI goals and plan the financial cost of modernization directly into their AI business cases. Priority should be given to integrating siloed data sources and establishing strict identity and access guardrails for AI agents. By piloting small, focused projects that address these foundational issues rather than attempting massive overhauls, businesses can clear the critical roadblocks, minimize infrastructure churn, and build a secure path for scalable, productive AI adoption.
Read Original Article →
Article Thumbnail

Enterprise FinOps: How CIOs Can Reduce Total Technology Cost by 30% or More

To achieve significant cost savings in technology, modern business leaders must expand their focus beyond simple cloud management and adopt a comprehensive financial operations strategy across their entire technology portfolio. With the rapid expansion of software subscriptions, independent contractors, and artificial intelligence experiments, hidden expenses easily accumulate in isolated departments. The primary culprits of this financial waste are duplicate software tools, unused premium licenses, unsupervised departmental purchases, and contractors who remain on payroll long after their initial projects end. To counter this, technology leaders need clear visibility into how every asset is consumed and what tangible value it delivers. By tracking software usage, renegotiating vendor contracts, adjusting service level agreements to match actual needs, and hosting artificial intelligence models on internal infrastructure where practical, organizations can uncover substantial inefficiencies. Addressing these hidden expenses allows leaders to safely reduce the massive budgets typically required just to keep basic systems running. Ultimately, recovering up to thirty percent of these everyday operational costs frees up essential capital, allowing the business to invest heavily in necessary modernization, new capabilities, and sustainable future growth.
Read Original Article →
Article Thumbnail

Can blockchain rewire India’s cross-border payment infrastructure?

Blockchain holds the potential to significantly improve India’s cross-border payment infrastructure, primarily by transforming back-office operations rather than creating new front-end experiences. Currently, international transactions rely on multiple intermediaries, messaging networks like SWIFT, and separate ledgers, which lead to slow reconciliations and delayed settlements. By introducing a shared, synchronized distributed ledger, blockchain could enable banks to reconcile transactions in real time, dramatically shrinking the delays caused by failed payments. Experts suggest that if countries adopt compatible blockchain standards, connecting their financial systems would become much more seamless. However, technology alone cannot solve the economic challenges of internationalizing the rupee or reducing dependency on the US dollar. While blockchain offers a faster and more efficient pipe for moving money, true global adoption requires robust bilateral trade, stronger exports, and comprehensive regulatory frameworks. Governments and participating institutions must still agree on validation rules, legal rights for tokenized assets, and dispute resolution mechanisms across jurisdictions. Ultimately, the success of blockchain in international finance will depend less on the code itself and more on whether regulators can build the legal foundation it needs to operate securely.

Read Original Article →

Daily Tech Digest - October 30, 2026

Quote for the Day
“Scrum is not a methodology; it is a path to agility.”
— Ken Schwaber
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

CISO Problems That Can't Be Solved With Technology

The article highlights a blunt reality: many of the hardest problems CISOs face cannot be solved with technology alone. A panel of security leaders explains that organizations often churn through tools not because the tools are bad, but because they were never properly integrated, funded, or owned. New leaders arrive, priorities shift, and platforms get replaced before they ever reach full value. Several CISOs stress that the real issues are operational — unclear ownership, slow coordination, and misaligned reporting structures. One example describes a critical vulnerability that took an hour to fix technically but three days to close because no one had agreed in advance who should notify teams, approve downtime, or communicate with the business. The panel also criticizes vendors for pushing products without understanding customer needs, and notes that corporate politics often prevent CISOs from having a direct voice with CEOs and boards. The steady message is that security failures often stem from human systems, not technical ones, and solving them requires clearer accountability, better collaboration, and more realistic operating models.

Read Original Article →

Out-of-Band Communication: Your Incident Plan Assumes the Systems You’re Using to Respond Still Work

Most organizations mistakenly assume their standard communication tools will be safe to use during a cyberattack. In reality, when a breach occurs, attackers routinely monitor platforms like Teams, Slack, and corporate email to stay a step ahead of the defense team. If your incident responders are coordinating on compromised systems, they are essentially giving the attackers a live briefing of their recovery strategy. To prevent this, response teams need out-of-band communication—a secure channel entirely separate from the company’s primary network and identity infrastructure. However, simply switching to consumer messaging apps like Signal or WhatsApp is not a reliable backup. These apps lack proper identity verification, make it difficult to maintain accurate team access, and fail to create the secure, defensible audit trails required for regulatory reporting. A genuine out-of-band strategy requires a dedicated, independent environment that is set up and tested long before a crisis hits. By moving the entire response process off the primary network, organizations can confidently manage the incident without tipping off the adversary.

Read Original Article →
Article Thumbnail

Agents are rewriting the book on security. Can your data layer keep up?

The article argues that AI agents are reshaping security in ways that traditional data architectures are not prepared for. These agents don’t just automate tasks — they make decisions, take actions, and interact with multiple systems at once. That shift means the data layer becomes a central security concern rather than a background utility. The piece explains that most organizations still rely on fragmented data stores, inconsistent permissions, and brittle pipelines, all of which create blind spots when agents begin pulling information from many sources simultaneously. If the underlying data is incomplete, stale, or poorly governed, agents can make incorrect or risky choices at machine speed. The article also warns that agents expand the attack surface because they can be manipulated through poisoned data, misleading prompts, or compromised integrations. To keep up, organizations need unified governance, strong lineage tracking, and real‑time visibility into how data flows through agent workflows. The steady message is that AI agents change the tempo and complexity of security, and only a modern, well‑governed data layer can support them safely.

Read Original Article →

Cheap Code, Expensive Confidence

Delegating software development to AI coding assistants might generate code quickly, but building the confidence that this code actually works as intended remains a challenging and time-consuming process. When an AI builds a feature, seeing a number on a screen doesn't prove the underlying math is correct or that the right data was used. Verifying these details requires deep system knowledge and often collaborative discussions with experienced colleagues. Because of this, claiming an AI got a project "eighty percent done" is often misleading. The remaining work involves uncovering where your expectations and the AI's logic diverge, which can take longer than writing the code manually. Furthermore, leaning too heavily on AI can rob newer developers of vital learning opportunities. Working through a problem manually helps them understand how data flows through an application, a skill they need for future troubleshooting. Ultimately, teams must thoughtfully decide when to hand tasks to an AI. This choice should depend on how easily the team can verify the final result and whether a developer needs the experience of solving the problem themselves.

Read Original Article →
Article Thumbnail

The Rise of the Threat Operator: How AI Will Redefine Security Operations and Careers

As artificial intelligence takes over routine security tasks like investigating alerts and gathering evidence, the traditional role of the security analyst is fundamentally changing. Instead of getting bogged down in individual alerts, professionals are transitioning into a new role often called a threat operator. This position requires overseeing the entire defense strategy rather than just monitoring tools. Because AI can handle the repetitive technical work, human experts must now focus on understanding their organization's unique business risks and guiding the AI systems accordingly. They decide how much independence the software should have and step in when complex judgment is needed, such as balancing a security threat against the risk of taking a critical business system offline. This shift means future security professionals will need a different blend of skills. While technical knowledge remains important, the ability to interpret automated decisions, manage overall risk, and maintain accountability over the defense process is becoming essential. Ultimately, security teams are moving from operating individual software tools to managing a comprehensive, AI-supported defense system.

Read Original Article →
Article Thumbnail

A Release Review Checklist for Teams Where One Developer Does Most of the Work

When a single developer handles an entire software project, the usual safety nets of peer reviews and dedicated testing disappear. To prevent bugs from reaching users, teams should implement a straightforward release review process that a senior developer can complete in under an hour. The foundation of this method is a consistent, eight-point checklist applied to every release. First, the reviewer reads the release summary to ensure the code actually solves the requested problem. They then evaluate the structural design rather than just reading lines of code. The reviewer tests the feature from the perspective of both a brand-new user and a long-time user, deliberately trying unexpected inputs that the original developer likely missed. They also check for broken features in other parts of the application, verify that appropriate tests are included, and confirm environment configurations match production settings. Finally, the reviewer records a clear decision to release or hold the code. For this system to work, reviews must be scheduled, reviewers must have authority to halt a release, and common mistakes must be discussed.

Read Original Article →
Article Thumbnail

A JSON schema Is not an AI governance layer

True AI governance happens far below the level of industry regulations and policy debates; it ultimately comes down to the specific code that decides whether an AI agent is allowed to execute an action. While many developers rely on tools like JSON schemas to validate an agent's requests, these schemas only check the shape of the data, not its precise meaning across different systems. This limitation creates a security vulnerability known as a parser differential, where two different components read the exact same payload in slightly different ways. Simple differences in how a system handles whitespace, looks up identifiers, or processes data normalization can inadvertently alter your authorization rules. Furthermore, you cannot rely on an agent to declare its own inputs as trustworthy. Real security requires deriving trust directly at the enforcement boundary by verifying cryptographic signatures against known keys. To truly secure your AI deployments, you must go beyond basic schema validation, strictly enforce specifications, reject ambiguous data shapes, and ensure your system independently verifies the authority behind every requested action.

Read Original Article →

McKinsey's Quantum Road Map Runs Through Q-Day

A recent McKinsey report highlights the rapid advancement of quantum technology and its dual role as a massive economic opportunity and a serious security threat. The focus for security professionals is "Q-Day," the point when quantum computers become capable of breaking today’s standard encryption. This milestone is approaching faster than initially projected, with key hardware developments expected within the next five years. Because attackers are already stealing encrypted data to decode it in the future, organizations cannot afford to wait. The report urges companies to begin upgrading to new, quantum-resistant encryption methods immediately to protect their long-term data. Upgrading this security infrastructure will require significant time and financial investment, marking a shift that is non-negotiable for large enterprises. To prepare, leaders need to take inventory of their current encryption systems, secure multi-year budgets, and require their technology suppliers to provide clear transition plans. Ultimately, updating to quantum-safe security is not a distant concern but an active, ongoing necessity that requires methodical and immediate planning.

Read Original Article →
Article Thumbnail

No One Holds the Key: Threshold ECDSA, Part 1

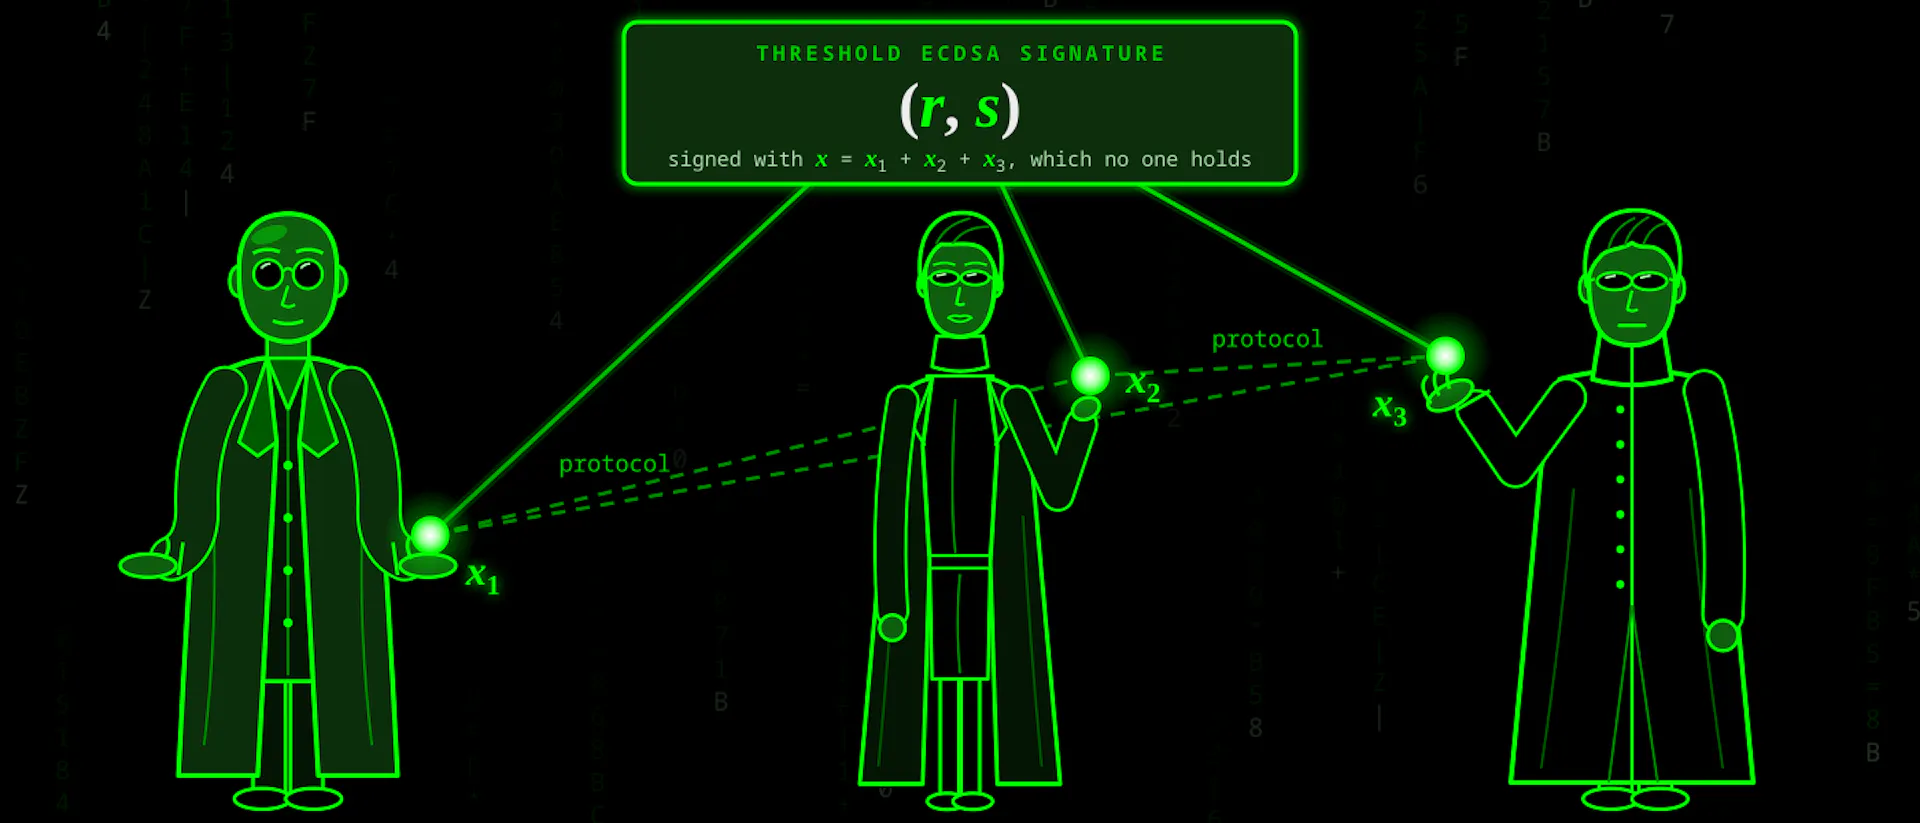
The article introduces threshold ECDSA as a way to remove single points of failure in digital signing systems. Traditional ECDSA relies on one private key held by one party, which creates an obvious risk: if that key is stolen, lost, or misused, the entire system is compromised. Threshold ECDSA changes this model by splitting the private key into multiple independent shares held by different participants. No one ever sees or reconstructs the full key, yet the group can still produce valid ECDSA signatures through a coordinated protocol. The article explains that this approach improves security for wallets, exchanges, and custodial services because attackers can no longer target a single secret. It also reduces operational fragility — losing one device or administrator doesn’t destroy access. The piece highlights that implementing threshold signing is complex, requiring careful cryptographic design to prevent leaks during collaboration. Its steady message is that threshold ECDSA offers a practical path toward stronger, more resilient key management by ensuring that “no one holds the key” in the traditional sense.

Read Original Article →
Article Thumbnail

PHP2Shell will persist in enterprise environments for years

The article explains why the PHP2Shell vulnerabilities will linger in enterprise environments for years, even though patches already exist. PHP is embedded in an enormous range of third‑party products — NAS devices, firewalls, VPN gateways, printers, building‑management systems, industrial controllers, and OT interfaces — many of which run outdated or unsupported PHP versions. Because customers cannot patch these runtimes directly, they must wait for vendors to release updates, and those updates often arrive slowly or not at all. The article shows how inconsistent versioning, backported fixes, and long‑term‑support Linux distributions make it difficult to know whether a system is truly protected. Early scans already reveal widespread exposure, and CISA has confirmed active exploitation. Even when patches are available, organizations still face the challenge of discovering every PHP instance across servers, containers, appliances, and firmware images. Until vendors deliver fixes, teams must rely on temporary mitigations such as isolating devices, tightening firewall rules, and monitoring for signs of compromise. The steady message is that PHP2Shell is less a single vulnerability and more a visibility and lifecycle problem that enterprises will be managing for a long time.

Read Original Article →

Daily Tech Digest - October 02, 2026


Quote for the day:

"I find that the harder I work, the more luck I seem to have." -- Thomas Jefferson

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


AI agents need more than access control — they need identity at runtime

As companies introduce artificial intelligence programs into their networks faster than human workers, traditional security systems are struggling to keep up. Most current access management tools were built for people, relying on simple passwords and broad job roles. Artificial intelligence programs, however, require a completely different approach to trust and security. According to industry experts, these programs need a rigorous onboarding process similar to what a new employee experiences. Every program needs a verifiable identity, secure credentials tied directly to hardware, and highly restricted permissions. Instead of granting general access to an entire application, organizations must shift to strict action control. This means giving a program permission to perform only one specific task for a brief, limited window of time. To maintain security, companies must continuously verify these identities in real time, inspecting every action before it occurs and keeping detailed records. Security teams must first discover all the automated programs already operating within their networks, as many are often deployed without formal oversight. By establishing clear identities and moving away from easily shared passwords, organizations can safely integrate these new automated tools without exposing their core systems to unnecessary risks or unauthorized actions.


5 Ways AI Governance Lowers the AI Hallucination Tax

Deploying AI without proper oversight carries significant risks, a challenge often referred to as the "hallucination tax." This term describes the hidden costs that arise when AI agents deliver incorrect outcomes, forcing human teams to constantly monitor, validate, and correct their work. The danger isn't just that AI makes mistakes—humans do too—but that AI often presents these errors with absolute confidence, creating a false sense of security. Several factors contribute to this tax. First, asking AI to answer questions using unorganized or incorrect data can lead to meaningless results. Second, letting AI agents scan massive amounts of unstructured data without guidelines drives up computing costs and wastes time. Finally, models and data naturally drift or decay over time, meaning an unmonitored AI will eventually stray from its intended behavior. To reduce these risks, experts recommend establishing strong AI governance. This involves building a unified registry of AI use cases, grounding agents in shared terminology, and monitoring systems for drift. Good governance shouldn't just be about creating rules; it should act as a guiding force that provides clear guardrails, ensuring that your AI capabilities remain accurate, cost-effective, and trustworthy as they scale.


What Modern Data Architectures Require Today

Modern SAP data integration must go far beyond basic extraction to support today's cloud, lakehouse architectures, and AI applications. While the core goal remains extracting operational data for analytics, the methods and requirements have evolved significantly. Businesses now need highly up-to-date, traceable, and well-contextualized data that operates seamlessly across diverse platforms like Microsoft Fabric, Databricks, or Snowflake without locking them into a single vendor. To achieve this, platforms are moving away from traditional batch processing toward low-latency, continuous data delivery methods like Table CDC and CDSFlow, paired with central hubs like Apache Kafka. Crucially, raw data alone isn't enough; it requires centralized metadata to translate technical fields into understandable business terms and track its origin, making it usable for both human teams and AI agents. Organizations must also prioritize open architectures, such as the Apache Iceberg format, to maintain data sovereignty and long-term flexibility. Finally, modern data architecture is bidirectional—it does not just feed external analytics but actively writes insights and triggers back into operational processes. This dual-flow integration, combined with adaptable deployment options, forms the foundation for resilient, data-driven business models that are fully prepared for emerging AI use cases.


The MFA you have isn’t the MFA you think you have

For nearly a decade, multi-factor authentication has been the primary defense against account takeovers, but simply checking the "MFA enabled" box on compliance reports is no longer enough to guarantee security. Not all MFA methods offer equal protection. Older, convenient methods like push notifications and SMS-based one-time passwords are now routinely bypassed by attackers. Hackers exploit these through "push fatigue" — bombarding users with approval prompts until they accidentally accept — or by using reverse-proxy phishing kits and SIM swapping to intercept codes in real time. Because these legacy methods fail to verify that the user and the system are communicating with the genuine destination, organizations must transition to true phishing-resistant MFA, such as passkeys or hardware keys. These modern solutions rely on cryptographic origin-binding, meaning the browser mathematically verifies the website before proceeding, stopping lookalike phishing domains entirely. Despite the clear security benefits, migrating to phishing-resistant MFA introduces friction. It requires budget for hardware keys, disrupts familiar employee workflows, and poses integration challenges with older systems. To succeed, organizations should avoid forced overnight rollouts. Instead, they should take a strategic, phased approach, beginning with high-risk administrator accounts and finance teams before expanding across the broader workforce to ensure a smooth transition.


How AI Is Disrupting the Monolith vs. Microservices Decision

The arrival of AI and autonomous coding agents is transforming the traditional debate between monolithic and microservice architectures. In the past, the choice often depended on team size and domain complexity, progressing from monoliths to microservices as organizations grew. Today, AI allows a small team to generate the code for dozens of microservices in a fraction of the time. However, this ease of creation can trap teams into building distributed systems they cannot effectively manage or operate, leading to severe architectural failure. Instead of defaulting to microservices, the author suggests a modular monolith is often the better foundation for business logic. Yet, AI workloads present unique challenges—such as probabilistic execution, intensive GPU memory requirements, and long-running agent workflows—that clash with traditional CPU-bound applications. This necessitates a new hybrid architecture: keeping deterministic business operations within a unified core while selectively extracting specialized AI capabilities into distinct platforms. Furthermore, the Model Context Protocol (MCP) provides a standardized way for AI agents to interact with business tools. The key takeaway for architects is that MCP should function as an interface boundary rather than an excuse to fracture the system into unnecessary, disparate microservices.


How Financial Services Companies Can Modernize Their Software Supply Chain

Financial services organizations have traditionally tolerated a backlog of dormant software vulnerabilities because making changes to legacy infrastructure carries a high risk of operational downtime. For years, prioritizing stability over immediate patching was a defensible strategy since exploiting these vulnerabilities required significant time and specialized skills. However, the emergence of advanced AI models has fundamentally altered this landscape. These modern systems can swiftly scan code, identify weaknesses, and string together exploits faster than human teams can patch them. Consequently, vulnerability exploitation has now surpassed phishing as the primary access method for breaches in the financial sector. To address this escalating risk, security leaders are shifting their focus away from massive, multi-year application overhauls and toward modernizing the software supply chain itself. This approach involves replacing vulnerable base images and open-source libraries with hardened, continuously rebuilt components at the foundational level. For older applications that cannot be readily updated, organizations can use secure, backported fixes that maintain compatibility. By centrally managing trusted software artifacts, platform teams can distribute secure building blocks across their organization. This proactive strategy allows financial institutions to substantially reduce their attack surface and minimize repetitive triage, all while keeping their critical systems stable and secure.


Beyond Ownership: Cloud Sovereignty By Design

The European Union is increasingly focused on digital sovereignty, particularly regarding cloud infrastructure. Many businesses mistakenly assume that a cloud provider's corporate ownership, such as being headquartered within the EU, automatically guarantees data protection and complete sovereignty. However, this assumption is a dangerous oversimplification. Corporate structure alone does not shield a company from foreign legal demands. For instance, an EU-owned provider with international operations, offshore support teams, or foreign subcontractors might still be legally compelled to share data with outside governments. Instead of relying strictly on a vendor's corporate origin, organizations should evaluate a provider’s tangible technical and operational safeguards. True digital sovereignty depends on practical realities, including exactly where data is physically stored, who manages the supply chain, and the implementation of strong encryption paired with customer-controlled keys. While corporate structure can reduce legal exposure, only technology can physically eliminate unauthorized access to data. Furthermore, evaluating a cloud supplier is never a single, one-time checklist. Because companies frequently restructure, acquire new investors, or alter operational models, due diligence must remain a continuous process over the life of any contract. Ultimately, prioritizing robust technical controls and ongoing transparency offers a stronger foundation for protecting data than simply checking a vendor's nationality.


Microsoft doubles down on Rust

Microsoft has officially elevated Rust to a Tier-1 programming language internally, giving it the same status as established languages like C# and TypeScript. This means Rust now benefits from a complete, fully supported toolchain that integrates seamlessly with Windows and Azure. The core of this effort is a new code generator designed for the Rust compiler, known as rustc_codegen_utc. This tool directly links Rust with Microsoft's existing Visual C++ back end, enabling developers to build low-level Windows services, drivers, and even kernel components while preserving Rust's renowned memory safety advantages. By leveraging the proven Visual C++ infrastructure, Microsoft avoids duplicating decades of compiler optimization and build tooling work while ensuring full compatibility with existing C and C++ code. Although rustc_codegen_utc is currently restricted to internal Microsoft teams, it is already powering over a hundred projects. Based on Microsoft's historical patterns of rolling out internal tools, it is highly likely that these capabilities will eventually be integrated into Visual Studio and Visual Studio Code for external developers. Until then, the broader development community can use existing Microsoft-supported extensions and crates to familiarize themselves with building safer, more resilient Windows applications in Rust.


Your customers just gave a bot access to their wallet. Are your controls ready?

As artificial intelligence advances, businesses face a new challenge: traditional identity verification and fraud controls are built for humans, not for automated AI agents. While current "Know Your Customer" (KYC) systems check passports and use selfies to verify identity, AI agents lack physical documents and biometrics. They are making purchases and conducting transactions on behalf of users, leaving compliance systems unprepared for customers that aren't people. The main issue is determining and continuously monitoring delegated authority. Even if an agent's behavior doesn't trigger traditional fraud alerts, businesses have no way of knowing if the bot is actually authorized by the user, what its permissions are, and whether that authority is still valid over time. This shifts the focus from simply identifying a customer to verifying an agent's ongoing permissions. For IT channel partners, this presents an opportunity to guide clients beyond basic bot detection tools toward comprehensive trust infrastructures. Instead of relying on one-time, event-based checks, companies need continuous monitoring frameworks that seamlessly handle humans, devices, and AI agents together. Updating these outdated models is essential for companies wanting to safely capture the benefits of agent-driven commerce without exposing themselves to significant compliance risks.


How AI Can Help Defend Against Future Quantum Attacks

Artificial intelligence is fundamentally reshaping the cybersecurity landscape, compelling organizations to rethink how they evaluate digital trust and assurance. As malicious actors increasingly leverage AI to uncover hidden vulnerabilities and exploit years-old security flaws, the traditional reliance on assumed cryptographic security is no longer adequate. To counter this, cybersecurity experts are adopting specialized AI tools to accelerate cryptanalysis—the rigorous process of stress-testing encryption systems. By automating vulnerability discovery and spotting data patterns faster than ever, defenders can proactively validate the mathematical algorithms that protect global infrastructure. This AI-driven evolution in defense aligns perfectly with the world's ongoing transition to post-quantum cryptography (PQC). With governments and tech giants aiming for total quantum readiness within the next decade, deploying these new standards is a massive undertaking. Fortunately, AI presents a critical opportunity to streamline this shift. AI-assisted validation allows manufacturers to robustly test emerging PQC algorithms before they scale in production, ensuring implementations are airtight against both present and future threats. Ultimately, combining strong cryptographic standards with continuous, AI-powered testing offers organizations an adaptable and secure path forward in an increasingly complex post-AI and post-quantum world.

Daily Tech Digest - September 14, 2026


Quote for the day:

“The only sustainable competitive advantage is an organisation’s ability to learn faster than the competition.” -- Peter Senge

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Post-Quantum Cryptography Is Becoming Mandatory For Financial Institutions

As quantum computers become more powerful, they will eventually break the cryptography that currently protects financial data. This presents a serious risk for banks and insurers, especially for long-term records that adversaries might steal now to decrypt later. The solution is post-quantum cryptography (PQC), a set of new mathematical formulas that even quantum computers cannot easily solve. Importantly, PQC runs on standard computers and integrates into existing systems like TLS. The main hurdle for financial institutions is not buying quantum hardware, but updating decades of old, intertwined software before the threat becomes a reality. Standards are already being finalized, and regulators are beginning to expect actionable roadmaps from the financial sector. To prepare, institutions must first build a complete inventory of their current cryptographic tools and identify where their systems are most vulnerable. Since no single algorithm is guaranteed to be safe forever, organizations should design flexible architectures that allow them to swap out encryption methods as needed. Addressing this transition requires strong cross-team collaboration and commitment from leadership. By acting now to map their risks and pilot hybrid solutions, financial firms can control their migration timeline rather than scrambling at the last minute.


Attackers already understand your software supply chain better than you do

The article argues that attackers now understand modern software supply chains better than the organizations that rely on them, and that AI is accelerating this gap. It describes how recent incidents—such as the Miasma malware packages and the Axios compromise—show that threats often begin with small, trusted open‑source components that slip quietly into developer workflows. Because most commercial software depends heavily on open‑source code, many companies lack visibility into what they are actually running in production or how quickly they could respond if a critical flaw appeared. Attackers exploit this blind spot by targeting overlooked dependencies and developer tools rather than traditional network perimeters. The piece explains how malicious packages spread rapidly through CI/CD pipelines, bypassing controls and creating large downstream risk before anyone notices. It also notes that AI‑driven automation allows attackers to discover vulnerabilities and coordinate exploits far faster than defenders can react, especially when security teams are slowed by technical debt and manual processes. The article concludes that software supply chain security has become a national‑level concern and that organizations need continuous, automated controls capable of identifying risks, enforcing policies, and reducing exposure before attackers take advantage of weaknesses they already understand.


When Spec-Driven Development Pays off

With AI coding assistants becoming standard infrastructure in software engineering, the primary bottleneck has shifted from writing code to verifying it. This shift raises critical governance questions regarding accountability, intent divergence, and the division of oversight between humans and models. Regulatory frameworks like the EU AI Act and NIST risk management guidelines increasingly demand documented controls, making "careful review" an insufficient strategy for managing AI-generated code. A recent study examined the popular response of "spec-driven development"—treating detailed specifications (business rules, high-level design, and low-level design) as a governing contract for AI output. Interestingly, establishing a strict specification baseline did not inherently make human reviewers better at finding bugs. Instead, it transformed code review from an ambiguous task into a contract-anchored, highly accountable process where behavioral drift could be clearly attributed to specific requirements. While writing a specification first and generating code from it improved outcomes by treating the spec as a governing artifact rather than just a prompt, the benefits on simpler tasks were largely due to improved reasoning rather than the spec itself. Ultimately, specification governance proves to be a worthwhile investment primarily for complex, multi-constraint tasks handled by capable but imperfect AI models.


Your data architecture was built for predictable consumers

The article explains how traditional enterprise data architectures were built for a world where data consumers behaved in predictable, uniform ways, and why that model no longer fits today’s environment. It describes how organizations once supported thousands of users working from the same carefully designed application, with stable access patterns that made governance manageable. As dashboards, APIs, notebooks, microservices, and specialized tools multiplied, consumption became more varied — and agentic AI has now pushed this shift even further. Instead of one shared interface, those same users may rely on thousands of individualized agents or applications, each creating its own access paths, combinations, and entitlement decisions. The piece notes that while personalization becomes easier at the application layer, the underlying infrastructure and security teams face growing complexity, with more dynamic demand and harder‑to‑govern patterns. It highlights capital markets as an early testing ground, where zero tolerance for inconsistency has driven architectures that coordinate changing consumer behavior. The article argues that a governed data consumption layer — the outward‑facing part of a broader data fabric — can reduce repeated integrations, protect sensitive systems, and enforce consistent access and audit controls. It concludes by urging CIOs to evaluate where such an approach adds value as human and machine consumers increasingly access and act on data in unpredictable ways.


How to level up from security pro to security leader

Transitioning from a technical cybersecurity professional to a Chief Information Security Officer requires a fundamental shift in perspective. While a strong technical foundation is helpful, it is no longer enough to reach the executive level. Aspiring security leaders must learn to translate complex technical risks into clear business priorities. This means understanding how the company generates revenue and balancing security needs with broader organizational goals. Rather than being seen as the resident tech expert, successful leaders act as strategic partners who build trust across various departments, including finance, legal, and operations. Developing strong communication skills and business sense is far more valuable than mastering specific coding languages. Gaining broad experience, such as managing budgets or working in cloud engineering, can provide the highly valued background that modern employers expect. Additionally, finding experienced mentors and maintaining a genuine curiosity for new technologies will naturally foster leadership growth. Security professionals are advised to present themselves with calm confidence, take ownership of their mistakes, and avoid being overly rigid about their long term career paths. By focusing on delivering meaningful impact and collaborating effectively in their current roles, aspiring executives can position themselves for the transition from technical expert to trusted business leader.


Enterprise AI Security: ChatGPT, Claude, Gemini and Copilot Compared

As artificial intelligence tools transition from experimental chatbots to integrated enterprise solutions, businesses face new security challenges. Platforms like ChatGPT, Claude, Gemini, and Microsoft Copilot now connect directly to internal emails, cloud storage, and code repositories, shifting the primary risk from external data leaks to internal data exposure and unauthorized actions. No single platform is perfectly secure, as each presents unique vulnerabilities. For ChatGPT, the main governance gap lies between secure enterprise accounts and the personal accounts employees might still use. Claude’s agent capabilities pose a different risk: because it can execute commands and modify code, overly broad permissions could lead to unintended software changes. Meanwhile, both Gemini and Microsoft Copilot respect existing workspace access controls, but they act as powerful search engines that expose years of accumulated, poorly managed permissions. They do not bypass security rules, but they make forgotten, overshared documents instantly discoverable to employees. Additionally, all platforms face the threat of prompt injection, where hidden instructions in external files manipulate the AI. To safely adopt these tools, organizations must clean up internal access permissions, separate consumer from enterprise usage, define clear data retention policies, and strictly monitor what internal systems the AI can currently access.


Why AI shouldn't be the one repairing your data pipelines

As organizations expand their use of autonomous artificial intelligence systems to make operational decisions in real time, the traditional concept of self-healing data pipelines is no longer sufficient. While modern cloud architectures can quickly replace failed components, data failures in complex enterprise environments rarely present themselves as complete systemic crashes. Instead, these issues manifest as silent degradation, such as undocumented changes in source systems, misaligned business logic, or untrackable errors that compromise downstream models and regulatory reports. To support advanced business operations, engineering leaders must transition from reactive, automated repairs to autonomous data governance and resilient infrastructure. A critical component of this shift involves prioritizing deterministic solutions over heuristic guesswork. While artificial intelligence is highly effective at detecting anomalies and triggering alerts, relying on automated scripts to guess how to fix crucial records risks introducing synthetic errors into auditable systems. Rather than letting artificial intelligence independently repair data pipelines, organizations should pair machine learning detection with predefined, policy-driven workflows that isolate problems and apply historical fallback logic. By treating data reliability as a core business risk and building systems that actively defend and remediate quality issues in real time, enterprises can establish a secure foundation for their critical operations.


When security creates friction, employees find workarounds

When workplace security measures become too complicated or time-consuming, employees often look for easier ways to get their jobs done. According to a recent report, forty percent of workers globally admit to using unauthorized personal devices or applications when official technology fails them. In the Asia-Pacific region, this problem is particularly noticeable, with many staff members turning to unapproved platforms like public AI tools just to meet deadlines or respond to customers quickly. While these workarounds usually stem from a genuine desire to be productive rather than malicious intent, they create significant risks because organizations cannot secure or govern activity that they cannot see. This phenomenon, often called "shadow AI," highlights a disconnect between security rules and everyday operational needs. Instead of just blocking unapproved tools, leaders should view these behaviors as a clear signal that current systems are causing too much friction. The most effective way to reduce this hidden risk is to integrate security naturally into daily workflows. By prioritizing user experience and making the secure option the easiest one to use, companies can better protect their data while still empowering their teams to work efficiently.


BRICS digital sovereignty meets the interoperability test

The recent New Delhi BRICS Declaration sets forth an ambitious vision for technology that attempts to balance national control with global connectivity. The core challenge outlined in the document is how member nations can achieve digital sovereignty and self-reliance without sacrificing the interoperability that modern networks require. Rather than proposing a disconnected or isolated tech ecosystem, the declaration emphasizes building strong, nationally controlled digital public infrastructure (DPI) that can securely communicate across borders. This balancing act applies across several layers of technology. For DPI, it means countries maintain control over their own identity and data systems while ensuring they can interface with others. For physical infrastructure, the focus is on developing resilient submarine cables to reduce reliance on external entities, though the exact technical details remain under review. In terms of future technology and supply chains, the group is pushing for collaborative research and common, globally interoperable security standards. Ultimately, the declaration suggests that true digital sovereignty isn't about isolating a nation's network, but rather participating in global digital systems without becoming overly dependent on outside suppliers or infrastructure. The success of this vision will depend heavily on the upcoming technical and engineering decisions.


Why Data Governance Still Isn’t Driving Better Decisions (or Transformation)

Many organizations have invested heavily in data governance, setting up dedicated offices, policies, and committees. Despite this, the actual business impact often remains elusive. Compliance is still a manual process, and decisions are frequently made using data of uncertain quality. The core issue is that while data governance manages data, it often fails to govern the decisions that data is supposed to inform. This disconnect is a flaw in both the design and deployment of current governance models. For years, the standard approach has been to identify critical data, assign ownership, and implement controls, largely driven by regulatory requirements like GDPR. While this model has improved awareness and traceability, it often falls short of delivering measurable business value. Data offices struggle to prove their return on investment, and business teams may bypass governance processes that they feel slow them down without offering real benefits. The initial focus on inventorying and controlling data made sense as a starting point. However, these are backward-looking control systems. To truly drive business performance, data governance needs to evolve from merely a control mechanism into a forward-looking decision system that actively supports and prepares organizations for future actions.