Showing posts with label productivity. Show all posts

Daily Tech Digest - September 05, 2026


Quote for the day:

"Success... seems to be connected with action. Successful people keep moving. They make mistakes, but they don't quit." -- Conrad Hilton

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Why is the Cloud Changing Again?

The rise of artificial intelligence is fundamentally changing how companies store and manage their data, moving the industry away from a one-size-fits-all public cloud model. Traditional cloud setups were excellent for standard web traffic and everyday software, acting like an efficient public transit system. However, artificial intelligence requires processing massive amounts of data at high speeds, which can cause severe delays and soaring costs on shared networks. To handle these heavy workloads, businesses are shifting toward a more specialized, decentralized approach. Additionally, because artificial intelligence learns from the information it processes, companies are increasingly concerned about the security and privacy of their sensitive data. This has driven a strong movement toward bringing data back home to private, local servers. Governments are also introducing stricter privacy laws, requiring companies to keep citizen data within their own national borders rather than storing it in global facilities. As a result, organizations are adopting a flexible strategy where they use public servers for everyday tasks, regional servers to comply with local regulations, and highly secure private servers for their most valuable information. This balanced method allows businesses to use advanced systems while maintaining strict control over their security, legal compliance, and digital assets.


Keeping OT security up to date is more than patching systems

Securing operational technology (OT) in industrial environments involves much more than applying simple software updates. As cyber threats against critical infrastructure like manufacturing and energy continue to rise, protecting these systems requires a fundamentally different approach than traditional IT security. While IT focuses primarily on protecting data, OT security must balance digital defense with real-world safety and continuous physical operations. Because large industrial systems often remain in active use for several decades, they cannot always be patched or upgraded as easily as typical office computers. Rather than relying solely on specialized technical controls, organizations must deeply understand their operational dependencies and gain completely clear visibility into their connected assets and third-party vendor access. Major disruptions frequently stem from basic weaknesses, such as poor network segmentation or compromised IT environments that spill over into industrial operations, rather than highly complex, sophisticated attacks. To build truly effective defenses, companies need strong internal governance that clearly defines responsibilities across engineering, operations, and security teams. Ultimately, organizations should view OT security not just as a narrow technical issue, but as a critical element of overall business resilience. By combining standard cybersecurity practices with deep industrial expertise, companies can protect their vital operations while successfully adapting to ever-evolving security risks.


Your R&D doesn’t need to be flashy

Software development teams often feel pressure to build flashy, highly marketable features to impress users. However, the most valuable research and development work usually happens entirely behind the scenes. While a brand-new interface button might make for a great product demonstration, real long-term user satisfaction depends on foundational elements like speed, reliability, and security. When software performs exactly as expected without delays or glitches, users can focus entirely on their work rather than fighting with the tool itself. Modern professionals, such as architects or engineers, rely on software to handle increasingly complex and automated tasks. If an application fails to execute a command accurately or compromises sensitive project data, the user's trust is instantly broken, and the financial consequences can be severe. This is why development teams must prioritize secure, reliable environments over cosmetic upgrades. By analyzing how people actually use the product, developers can identify the invisible improvements that truly matter, such as open standards that allow seamless collaboration across different platforms. Ultimately, the best software acts as a quiet partner, anticipating a user's needs and handling repetitive work so they can stay immersed in their creative flow.


Querying and Performing Transactions Across Multiple Database Schemas in a Modular Monolith

In a modular monolith, assigning a dedicated database schema to each module establishes strong boundaries but introduces significant challenges for querying data and managing transactions. Because direct database access between modules violates these boundaries, traditional approaches like joining tables across different schemas or relying on single database transactions are no longer viable. To solve querying issues, developers can use several strategies. The simplest method involves direct API calls, where modules communicate through public interfaces, ensuring strict boundaries despite potential performance compromises. For scenarios requiring faster reads, teams can rely on domain events to duplicate and denormalize data across modules, though this requires managing eventual consistency. Alternatively, database views allow developers to join tables across schemas at the database level, which is particularly effective for reporting purposes. Another strong option is the Backend for Frontend pattern, where a dedicated service aggregates data from multiple modules before sending it to the user. Handling transactions across multiple schemas requires a shift away from traditional methods. Instead of relying on a single commit, systems must utilize event driven architectures and patterns like sagas. While this approach ensures loose coupling, scalability, and resilience, it also introduces complexity by requiring compensating transactions and careful error handling to maintain data consistency.


Gmail labels: Your secret weapon against inbox chaos

Gmail labels provide a powerful and flexible alternative to traditional email folders, acting more like customizable tags that allow multiple categories to be applied to a single message. By mastering these tools, users can significantly reduce inbox chaos and streamline their daily communication. A great starting point is creating and color-coding various labels, then grouping them into parent and sublabel hierarchies to maintain a consistently neat sidebar. To save time during everyday tasks, you can proactively apply these labels while composing a new email or assign them simultaneously while archiving a read message. Labels also dramatically improve your ability to find old information; typing specific label operators directly into the search bar instantly narrows down vast results. Furthermore, users can fully automate their workflow by setting up custom Gmail filters. These filters automatically apply specific labels to incoming messages based on criteria like the sender's address or specific subject line keywords. This intelligent automation allows urgent emails to stand out immediately while quietly routing less critical messages away from your main inbox view. Finally, labels can be connected to custom notification settings, ensuring you only receive alerts for the messages that truly matter. By adopting these simple strategies, anyone can transform an overwhelming inbox into a highly organized system.


When cyber capability becomes abundant: Rethinking government cyber resilience

As artificial intelligence rapidly evolves, it is fundamentally changing the economics of cybersecurity for government agencies. Historically, sophisticated cyber operations required scarce, expensive human expertise. Today, AI has significantly reduced these costs, making powerful cyber capabilities widely available to both attackers and defenders. This shift creates unprecedented challenges for government agencies, which protect critical infrastructure and systems essential to national security, public health, and emergency response. Because attackers can now discover and exploit vulnerabilities faster than organizations can fix them, government security leaders are losing confidence in traditional defensive strategies. To adapt to this new reality, governments must rethink their approach to cyber resilience across operational and institutional levels. Operationally, agencies need to move away from trying to fix every single technical flaw. Instead, they must prioritize risks based on their potential impact on public missions. A moderate vulnerability in an emergency response system matters far more than a severe flaw in a low impact network. By translating technical data into real world operational context, governments can better focus their limited resources on protecting what truly matters. Ultimately, success requires agencies to rapidly reduce their exposure, contain breaches driven by artificial intelligence, and actively shape a safer overall cyber ecosystem.


Cyber resilience in the age of AI will be decided in the boardroom

As modern business innovation speeds up due to artificial intelligence, it also provides attackers with powerful new ways to disrupt operations. Companies have spent heavily on defensive software, but having more tools often creates confusing complexity rather than clear protection. Because automated threats move faster than ever, the true test of an organization is not whether it can prevent every single incident, but how well it handles a crisis when it happens. Cybersecurity is no longer just a technical issue meant for the information technology department; it is a fundamental business challenge that belongs in the boardroom. Company leaders must understand their critical digital dependencies and how a failure would impact revenue, reputation, and daily functioning. Security should be woven into every major business decision from the start, prioritizing clear processes over having the most complicated software. True resilience relies heavily on human behavior. An organization must build a culture where employees feel safe reporting mistakes, questioning unusual requests, and practicing response plans before an actual emergency occurs. Ultimately, survival during a digital attack depends on clear communication, decisive leadership, and the ability to keep essential services running smoothly and effectively, ensuring that trust and stability are maintained alongside technological growth.


How Differential Privacy Will Transform Enterprise Data Strategy

Differential privacy is quickly moving from a theoretical concept to a critical component of enterprise data strategy. While previous methods like encryption and de-identification have struggled to protect against re-identification as data volumes grow, differential privacy offers a mathematically proven way to guarantee that an individual's data cannot be reverse-engineered from broader analytical outputs. This technique is already being used successfully by major organizations, including the U.S. Census Bureau, Apple, Google, and Microsoft, and the market is projected to expand significantly by 2030. However, many business leaders mistakenly view this technology merely as a compliance tool. Its true value lies in unlocking data utility, allowing companies to safely share information across internal departments and with partners without exposing sensitive details. To succeed, organizations must understand that differential privacy is not a simple plug-and-play product, nor can it be retrofitted easily into existing pipelines. It requires a fundamental shift in how data is processed and governed. Experts advise companies to start with a single high-value use case, such as customer analytics, and prioritize building strong central governance before focusing on the underlying tooling. Adopting this approach now gives enterprises a significant competitive advantage in responsible data strategy.


What the AI Warning Letter Completely Missed
A recent warning from major technology companies highlights that artificial intelligence will soon make cyberattacks cheaper and more common, urging immediate action to strengthen defenses. While this threat is very real, the proposed solutions overlook the most critical component: the human beings required to do the work. The industry often focuses heavily on advanced tools and theoretical scenarios while ignoring the practical reality that defense depends entirely on skilled people. Every recommendation to improve security, whether it involves fixing weaknesses, reviewing code, or deploying new software, requires a trained operator. The gap in our current readiness is not a lack of software products, but a severe shortage of equipped personnel, especially within smaller organizations and local utilities. To truly prepare for emerging threats, companies must invest directly in the workers already managing these systems, teaching them how to secure their specific environments. Furthermore, technology providers should offer concrete, direct support rather than just access to software models. Defensive tools must be judged by how effectively a small, overworked team can actually use them during an emergency. Ultimately, technology alone will not secure our infrastructure against intelligent threats. True resilience requires betting on motivated, well trained people who are ready to handle the daily work of defense.


Why digital transformations still fail

Digital transformations continue to fail largely because companies let technology, heavily promoted by consulting firms, dictate their strategy rather than focusing on actual business needs. Consultants have consistently sold identical, prepackaged systems to maximize their own profits, completely ignoring the unique requirements of each organization. This approach has resulted in massive budget overruns, delayed timelines, and overly complex systems that fail to perform as promised. Instead of redesigning their processes, companies simply moved their existing problems onto expensive cloud platforms, increasing their costs without gaining any real benefits. Now, as the industry shifts its focus toward artificial intelligence, businesses are repeating these exact same mistakes. Organizations are rushing to add artificial intelligence to everything without a clear reason, while placing unqualified staff into critical design roles. To succeed moving forward, businesses must adopt a much simpler approach. They need to stop overspending on unnecessary computing power and invest heavily in proper foundational training for their internal teams. Ultimately, technology exists solely to serve the business. Any successful change must begin by identifying clear business requirements and working backward to find the most practical, cost-effective solution, rather than blindly purchasing the most complicated or trendy new software option available today.

Daily Tech Digest - August 13, 2026


Quote for the day:

“Personal growth is not a matter of learning new information but unlearning old limits.” -- Alan Cohen

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


4 RPA lessons that still hold true in the AI boom

As companies rush to adopt new artificial intelligence tools, many are stumbling over the exact same hurdles they faced years ago with robotic process automation. To succeed with AI technology today, organizations should remember four vital lessons from the past. First, they must carefully choose what to automate. Applying new technology to a broken or inefficient process only speeds up the creation of bad results. Every automation project needs a clear, measurable business benefit before it begins. Second, automation is never a project you can simply turn on and ignore. Because artificial intelligence acts quickly and sounds confident, keeping human experts in the loop is essential to prevent small errors from becoming large failures. Third, the quality of the information you feed the system remains critical. While modern tools can read messy data, they can easily misunderstand context, leading to flawed decisions on a massive scale. Finally, managing how people adapt to the changes is the most difficult challenge of all. Most technology projects fail because of people and workflows, not the software itself. Rather than abandoning older, predictable automation methods entirely, smart organizations are combining them with new artificial intelligence to create highly reliable, cost-effective, and highly practical solutions.


The intelligent workplace (part 2): Technology’s next transformation of work

As artificial intelligence takes on a larger role in the modern workplace, organizations must rethink how they manage teams and measure performance. The traditional focus on the sheer volume of tasks completed, such as reports written or cases closed, is no longer effective when automated tools can generate that output almost instantly. Instead, managers need to prioritize the actual quality of work, accuracy, and the ability to solve the right problems. Rather than competing with machines on speed, employees should focus on areas where human judgment remains critical. Furthermore, managers are shifting from simply overseeing daily activity to deliberately designing workflows where people and technology support each other. This change requires establishing clear rules for when employees should rely on automated systems and when they need to step in and override them. Ultimately, accountability must always rest with humans. A major challenge is ensuring junior employees still develop necessary expertise, as the routine tasks they traditionally learned from are now handed off to software. Companies will need to create deliberate opportunities for practice, mentoring, and direct feedback. Finally, successfully integrating these tools relies heavily on trust and transparency. Leaders must maintain human oversight, protect time for learning, and ensure that automated metrics do not replace empathy and open communication.


AI, Digital Twins, and Cybersecurity in Industrial Remote Operations

The second part of this article series explores how artificial intelligence and virtual models—often called digital twins—are fundamentally changing remote industrial operations, while highlighting the serious cybersecurity challenges that come with them. Instead of waiting for machines to break down, AI allows manufacturers to shift from reactive monitoring to predictive maintenance. By analyzing patterns in temperature, vibration, and power use, these systems can spot equipment failures weeks in advance. This capability drastically reduces unplanned downtime and lowers maintenance costs. Meanwhile, digital twins serve as the virtual interface for these physical systems. Engineers can use these exact digital copies to run simulations, test adjustments, and manage entire production lines remotely, achieving a level of oversight that previously required being physically present on the factory floor. However, moving factory controls online introduces major network security risks. Manufacturing remains a prime target for cyberattacks, and every new remote connection is a potential entry point. This risk is complicated by a severe shortage of security professionals who actually understand industrial systems. Ultimately, building a secure foundation is what makes these remote capabilities possible. Organizations that proactively address their network security can safely unlock the very real efficiency and productivity benefits of these modern industrial tools.


Social engineering reshapes financial fraud as attacks scale

Social engineering has rapidly emerged as the primary method for financial fraud, moving away from complex technical hacking toward manipulating human behavior. Recent data reveals that impersonation scams in the United States have more than doubled over the past year. Fraudsters frequently pose as trusted organizations, celebrities, or relatives to deceive individuals into authorizing transactions themselves. Investment scams are currently causing the most financial damage, with criminals using fake websites and fabricated platforms to create a false sense of urgency. This trend is not limited to everyday consumers; major Wall Street firms, including hedge funds and private equity companies, are also defending against sophisticated phone-based attacks targeting their employees. Adding to the challenge is the growing commercial market for these scams. Rather than building malicious systems from the ground up, criminals can now purchase ready-made scam kits online. These affordable packages provide everything needed to launch convincing campaigns, such as fake cryptocurrency presales with personalized elements and countdown timers. By lowering the barrier to entry, these kits allow individuals with minimal technical skills to execute highly professional and persuasive scams. Ultimately, modern financial fraud relies less on defeating security software and more on exploiting human trust through highly convincing deception.


Tokenmaxxing: The strangest developer productivity metric of all time

A concerning trend called "tokenmaxxing" has emerged in software engineering, where developers are evaluated by how much AI computing power they consume rather than the quality of their code. Much like the outdated practice of measuring productivity by lines of code, this metric encourages the wrong behaviors. When companies reward raw token usage, developers are incentivized to generate massive amounts of unrefined code, stuff prompts with unnecessary text, and set up automated systems simply to climb internal leaderboards. This careless approach leads to higher code duplication, less thoughtful refinement, and software that is quickly discarded. Beyond degrading software quality, tokenmaxxing is financially destructive. The blind pursuit of AI usage has caused companies to burn through budgets rapidly, forcing some to restrict their access to these tools. Furthermore, this flawed measurement ignores the most valuable ways developers use AI, such as debugging complex issues or planning architectural designs, because these tasks do not generate high token counts. Ultimately, true software engineering requires careful planning and simplification. AI is a helpful tool for solving problems and learning, but using it effectively means focusing on meaningful outcomes rather than blindly treating the volume of AI interactions as a sign of success.


Architecting Multi-Cloud Networks to Survive Cryptographic Migrations under DORA Rules

The article outlines the critical intersection of the European Union’s Digital Operational Resilience Act, multi-cloud network strategies, and the impending shift toward post-quantum cryptography. Under DORA, financial institutions face strict mandates to ensure continuous operational resilience and to mitigate third-party concentration risks. This effectively makes multi-cloud and cloud-agnostic architectures a necessity rather than a mere option, as organizations can no longer rely on a single cloud provider without a tested, actionable exit strategy. As the financial industry prepares for complex cryptographic migrations to defend against advanced quantum computing threats, these multi-cloud network architectures will be put to the ultimate test. Updating long-lived trust chains, encryption protocols, and digital certificates across sprawling IT environments is an inherently risky process. The text explains that surviving this transition without violating DORA’s strict uptime requirements demands highly decoupled network designs. By strategically distributing workloads and avoiding deep dependencies on provider-specific services, financial entities can safely manage phased cryptographic updates. Ultimately, a well-architected multi-cloud environment is essential not just for avoiding vendor lock-in, but as a robust safety net. It allows institutions to implement sweeping security upgrades smoothly, ensuring total compliance and uninterrupted service delivery in a heavily regulated modern landscape.


The web’s newest weapon against AI scrapers is a font

Designers Isaque Seneda and Gabriel Abrucio have developed a new typeface called ShieldFont, designed to protect online content from unauthorized data extraction by artificial intelligence companies. The core mechanism relies on the traditional ligature feature found in standard typography. While a web page using ShieldFont appears perfectly normal and readable to human visitors, the underlying HTML source code is intentionally altered. When AI scrapers and automated web crawlers attempt to harvest the website text, they encounter only random, meaningless data instead of the actual content. This approach offers web publishers a practical technical method to prevent their work from being absorbed into AI training datasets without permission. Unlike earlier blocking methods that often disrupted the user experience or proved ineffective, ShieldFont specifically targets the data collection process by intentionally ruining the harvested text. Experts note that the success of this method depends on how well the substitution strategy is executed. If the replacements rely on simple patterns, such as direct synonyms or antonyms, advanced algorithms might learn to reverse the alterations. By focusing on random string generation and complex substitutions, ShieldFont aims to safeguard digital ownership and provide a reliable defense against the aggressive scraping tactics currently used across the internet.


Post-Quantum Deadlines Collide With OT Reality

The transition to post-quantum cryptography is becoming an urgent priority as looming regulatory deadlines clash with the practical constraints of operational technology environments. While government agencies and security bodies push for rapid adoption of quantum-resistant algorithms to protect critical infrastructure, the realities of operational technology present significant engineering and logistical hurdles. Unlike standard enterprise networks, operational technology systems like industrial control units, medical devices, and smart grids are built for longevity. They often run on older hardware with limited processing power and minimal memory. These strict constraints make it exceedingly difficult to implement complex new cryptographic standards without disrupting essential services or triggering massive hardware replacement cycles. Furthermore, the threat is not entirely theoretical. Adversaries are actively engaging in "harvest now, decrypt later" campaigns, collecting encrypted data today to break it once quantum computing matures. Consequently, securing these industrial environments requires a nuanced approach rather than a simple software update. Organizations must begin their planning immediately by conducting thorough inventories of their cryptographic assets. They should isolate vulnerable operational systems through strict network segmentation and adopt hybrid security models. Ultimately, building flexible encryption into aging infrastructure is crucial for navigating the tension between ambitious mandates and the slow-moving reality of industrial technology.


Beyond Cyber Protection: How European Companies Can Operate Through Cyber Disruption

European businesses face an evolving threat landscape where preventing cyberattacks entirely is simply no longer a realistic expectation. Driven by integrated supply chains and rapid artificial intelligence adoption, companies remain vulnerable despite heavy investments in traditional security. According to recent research, while many executives expect to recover from incidents like ransomware within days, actual disruptions often take months to resolve. To navigate this reality, leaders must transition their focus from basic protection to true operational resilience. This means acknowledging that some attacks will succeed and designing systems capable of operating under stress. Executives should start by identifying their essential operating core, which includes the critical services, data, and processes that must remain available during a crisis. Additionally, while strict regulations establish important security baselines, compliance should be viewed as a starting point rather than the ultimate goal. True resilience requires engineering robust recovery processes rather than simply hoping for a rapid response. It also demands making resilience a company wide responsibility, extending these practices across the entire value chain, and fully understanding the economic costs of a disruption. By accepting the inevitability of breaches and planning for continuity, organizations can confidently sustain their core functions and protect their stability during a severe disruption.


AI Agents Are Creating a New Identity Security Challenge for Enterprises

Morey Haber outlines the necessity of treating artificial intelligence agents as a unique class of non-human identity that requires strict security controls. Unlike standard software or human users, these agents operate autonomously, make independent decisions, and run on unpredictable schedules. Because they can reason and interact with other systems on their own, traditional access management is simply not enough. Organizations must assign each agent a specific identity tied to an accountable human owner. Instead of relying on permanent passwords, these agents should use temporary security secrets and be granted the absolute minimum access required to complete a specific task. Furthermore, security teams must monitor their behavior constantly rather than just checking their login credentials, looking for unusual activity or excessive data access. Proper management also means tracking an agent from the moment it is created to when it is retired. Crucially, companies need a reliable kill switch to instantly revoke an agent's access if it behaves improperly or is compromised by an attacker. By managing these tools with calm, steady oversight and limiting their permissions, organizations can prevent them from becoming dangerous entry points for cyber threats. Ultimately, an agent should never hold more power than you are prepared for it to misuse.

Daily Tech Digest - July 13, 2026


Quote for the day:

“An entrepreneur is someone who jumps off a cliff and builds a plane on the way down.” -- Reid Hoffman

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


AI in the Boardroom: What Directors Must Now Govern

The boardroom conversation around artificial intelligence has shifted from deciding whether to experiment to figuring out how to successfully govern the technology. While many company directors now use AI for their personal productivity, using a specific tool is vastly different from overseeing its safe and strategic deployment across an entire organization. As AI becomes deeply embedded in strategy, supply chains, and daily operations, it brings complex new risks, particularly in cybersecurity and external vendor management. Importantly, when an AI system makes a flawed decision or causes harm, accountability cannot be outsourced to a vendor or the algorithm itself; it remains firmly with the human leaders and the board. Currently, a significant expertise gap exists, with most boards lacking even one literate director, let alone a collective understanding of the topic. However, boards do not need to hire software engineers or data scientists. Instead, they need directors capable of asking sharp questions, evaluating risk, and connecting these new initiatives to broader business strategy. To close this gap, boards should focus on raising the technical literacy of all members rather than relying on a single expert. Practical first steps include auditing current usage, defining clear oversight responsibilities, establishing audit trails for automated decisions, and bringing in seasoned advisors to evaluate the overall management approach.


The Implementation Gap: Why Africa’s Digital Strategies Rarely Become Digital Reality

Despite having no shortage of ambitious national digital strategies, data protection laws, and broadband policies, African nations frequently struggle to turn these plans into reality. This persistent issue is known as the implementation gap. Governments often celebrate the launch of new policies but fail to dedicate the same energy to executing them. A major part of the problem is the false belief that simply purchasing new technology equals true digital transformation. In reality, buying new software means very little without also redesigning outdated business processes and improving institutional capabilities. The article identifies seven main hurdles holding back progress. First, shifting political leadership often disrupts long-term projects. Second, many public institutions still rely on old, paper-based administrative structures. Third, procurement focuses too much on acquiring technology instead of improving public outcomes. Fourth, government digital systems are often fragmented and unable to share information with each other. Fifth, cybersecurity is typically treated as a delayed afterthought rather than a built-in priority. Sixth, governments fail to invest enough in training civil servants and citizens to use these new tools. Finally, institutions frequently repeat the mistakes of past projects instead of learning from them. To succeed, the focus must shift from launching more strategies to building capable institutions that can steadily deliver real, lasting public value.


Upskilling for Emerging Industries Affected by Data Science

As data science transforms global industries, the demand and compensation for skilled professionals continue to rise. However, this well-paying field is also becoming highly competitive, meaning that simply landing a job is no longer enough to guarantee your long-term security in the workforce. To build a lasting career, continuous learning is essential to avoid falling behind in a rapidly shifting job market. The pace of rapid technological advancements dictates that traditional skills can very quickly become outdated, while brand new roles in specialized areas like artificial intelligence, renewable energy, cybersecurity, and blockchain consistently emerge. To succeed in these newer positions, data scientists must cultivate core traits such as adaptability, critical thinking, clear communication, and creativity. Employers actively seek out individuals who possess a growth mindset and can quickly adjust to new tools and complex challenges. Professionals can stay competitive by embracing varied educational strategies. This includes enrolling in targeted online courses through accessible educational platforms, attending industry workshops, and connecting with experienced mentors for personalized guidance. Additionally, volunteering for projects outside your normal duties and engaging with professional networks can provide practical experience. By treating your education as an ongoing journey, you can protect your career and easily pivot into new opportunities as the landscape changes.


Australian developers are losing half their day, most leaders have no idea

Australian software developers are currently spending the vast majority of their working hours on tasks outside of actual coding. Although engineering leaders often believe their teams are highly productive, studies show developers spend a mere sixteen percent of their day writing software. The rest of their time is consumed by navigating security protocols, complex deployment processes, and infrastructure monitoring. This significant gap between leadership perception and daily reality represents a major hidden cost for businesses today. The problem is heavily compounded by a lack of clear visibility into how software performs in live environments. When engineers cannot easily identify the root cause of system issues, they are forced to spend hours troubleshooting rather than creating new features. Furthermore, the rapid integration of artificial intelligence tools is adding a new layer of operational complexity. While artificial intelligence can speed up initial development, it also introduces unpredictable behaviors and risks that are very difficult to manage without proper oversight. To fix this ongoing productivity drain, organizations need to securely connect system performance data directly to developer workflows. By giving engineering teams clear, real-time insights into system health and AI behavior, leaders can reduce daily friction, minimize time wasted on resolving errors, and give developers their time back to focus on building reliable software.


Accountable Intelligence: Why India must get healthcare AI right

While artificial intelligence is transforming many industries, its role in healthcare carries significantly higher stakes. In most fields, an AI mistake causes mere inconvenience; in medicine, it can impact human lives. For this reason, India must adopt healthcare AI with strict accountability and clinical evidence. The country faces unique medical challenges, including a vast population, rising chronic diseases, and a divide in urban-rural access. AI offers practical solutions, such as quickly analyzing X-rays or flagging early signs of conditions like diabetic retinopathy, helping shift the system from reactive treatments to proactive care. However, achieving these benefits requires the right approach. AI is not meant to replace doctors. Instead, it serves as a valuable support system that reduces administrative workloads and highlights patterns that busy medical professionals might miss. To succeed in India, AI models cannot simply be imported; they must be trained and validated using diverse local data to ensure accuracy across different regions and demographics. Furthermore, developers must prioritize data privacy, clinical oversight, and transparent patient consent. Building genuine trust requires health technology companies to focus on proven clinical outcomes rather than just technological potential. Ultimately, the future of medicine is doctors and AI working together to strengthen patient care.


The AI Governance Gap: Why Traditional Security Controls Are Falling Behind

Traditional enterprise security was designed for a predictable world where applications behaved consistently and network traffic passed through centralized checkpoints. These conventional governance models are failing because artificial intelligence operates completely differently. AI is dynamic, changes based on user prompts, and is increasingly embedded directly into approved tools like productivity suites and web browsers. Because these interactions bypass traditional network filters, organizations face a massive visibility gap. They often cannot tell how AI is being used, what sensitive data is being shared, or what actions autonomous agents are taking on their behalf. Attempting to manage this by simply blocking unapproved AI apps is ineffective and often drives employees toward hidden shadow AI use. To close this gap, companies must move away from static application checklists and adopt source-level monitoring. This approach focuses on capturing real-time interactions, such as the exact prompts users send, the specific data flowing in, and the models' direct responses, right where the activity occurs. By prioritizing continuous, context-aware visibility over outright restriction, businesses can identify risky behavior regardless of which specific tool is being used. As AI becomes deeply woven into everyday workflows, effective governance will depend entirely on tracking how information moves through these intelligent systems rather than just monitoring standard network traffic.


On AI Ethics: Why Prompt Engineering Needs a Moral Compass

As the practice of giving instructions to artificial intelligence—often called prompt engineering—grows in demand, the need for a strong moral compass is becoming increasingly clear. Simply training an AI model well is not enough; the specific instructions given to these systems can independently create significant ethical dilemmas. Harmful prompts can easily amplify existing biases, expose private information, generate convincing misinformation, or be used for malicious exploitation. Recent guidance from Pope Leo XIV highlights that AI must serve humanity rather than concentrate power, warning against a purely profit-driven approach and calling for shared standards of social justice and accountability. The real-world consequences of poor AI ethics are already visible across multiple fields. Researchers note that mental health chatbots routinely violate established ethical standards through deceptive empathy and poor crisis management. Furthermore, AI tools are creating complex, hidden security threats, as automated programs operate within approved workflows but still execute harmful actions. Because the speed of modern AI adoption is entirely unprecedented, technology and security professionals can no longer assume a system is safe just because it functions as designed. Moving forward, organizations must actively govern how their AI behaves, clearly define ethical boundaries, and closely monitor both human and machine activities to properly protect their daily operations.


Claude Security Risks: What Your Security Team Needs to Know

Using AI tools like Claude in the workplace presents serious security challenges for companies, extending far beyond the software itself. The primary danger comes from how employees use the tool. When workers paste full reports, large spreadsheets, or confidential documents into the platform for analysis, they unknowingly expose sensitive company information and intellectual property. Because these bulk uploads happen without internal oversight, companies lose track of their data, which can lead to major compliance and audit failures. Another significant issue is context leakage. Information shared in one conversation can easily influence the answers generated in later sessions. If a team discusses proprietary processes or confidential insights, those details might unintentionally surface in future responses within shared workspaces. Furthermore, the boundaries between different types of accounts are often blurred. Employees frequently switch between personal accounts, shared team spaces, and official enterprise environments. This lack of clear separation weakens overall data governance, allowing regulated or sensitive information to drift outside of approved, secure areas. Ultimately, these blind spots create serious vulnerabilities, including accidental data disclosure and incomplete legal responses. To protect their assets, businesses must recognize that the most significant risk lies in unmonitored human behavior and a lack of clear access boundaries.


Manual Workarounds as Operational Risk Get Louder

When employees constantly create manual workarounds to bypass clunky systems, they are not simply trying to be difficult; they are attempting to keep the business moving forward. However, these temporary fixes quickly evolve into significant operational risks over time. Once a shortcut becomes a regular habit, it replaces official workflows and creates undocumented, fragile systems. These shadow processes—like hidden spreadsheets or email approvals—mask the true state of operations and create severe vulnerabilities, especially when they involve financial data or regulatory compliance. Furthermore, workarounds often rely entirely on a single person's memory, creating a dangerous dependency that falls apart if that individual leaves or during a major emergency. To protect the organization, leaders must view these side paths not as employee indiscipline, but as clear signals of failing internal infrastructure. Rather than demanding people work harder, management needs to thoroughly audit these hidden habits and address the core root causes of the friction. Every workaround that is allowed to continue must be assigned a specific owner, given a strict review date, and carefully evaluated for its overall business impact. By replacing these fragile, manual patches with permanently improved systems, organizations can maintain clear visibility, ensure steady control, and safely scale their daily operations.


Beyond Physical Security. Why FMs are strategic risk leaders

Facility management is no longer just about maintaining physical buildings. Because organizations face increasingly complex threats, from severe weather and cyberattacks to global supply chain delays, the roles of facility management and security are rapidly merging. Today, a company's facilities are critical environments that directly impact business operations, employee well-being, and overall corporate reputation. This shift requires facility leaders to step into highly strategic roles. They must now deeply understand risk assessment, crisis planning, and how to effectively integrate new technologies to keep operations running smoothly during emergencies. Instead of working in isolation, these professionals collaborate closely with security, IT, human resources, and executive teams to build a strong defense against potential disruptions. Smart building systems and advanced monitoring tools help identify problems early, but they require skilled people and clear rules to be truly effective. Furthermore, resilience is no longer treated as a separate emergency plan; it is becoming a daily habit woven into how companies choose suppliers, design workspaces, and manage their environmental footprint. Employees also expect to feel safe and supported in their daily work environments. By combining daily operational excellence with long-term strategic planning, modern facility leaders help organizations protect their staff, maintain steady operations, and ensure lasting stability.

Daily Tech Digest - May 01, 2026


Quote for the day:

"Before you are leader, success is all about growing yourself. When you become a leader, success is all about growing others." -- Jack Welch


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


The most severe Linux threat to surface in years catches the world flat-footed

The article "The most severe Linux threat to surface in years catches the world flat-footed" on Ars Technica details a critical vulnerability known as "Copy Fail" (CVE-2026-31431). This local privilege escalation flaw stems from a fundamental logic error in the Linux kernel’s cryptographic subsystem, specifically within memory copy operations. Discovered by researchers using the AI-powered vulnerability platform Xint Code, the bug has existed silently for nearly a decade, impacting almost every major distribution released since 2017. The severity of the threat is heightened by the availability of a remarkably compact exploit—a mere 732-byte Python script—that allows any unprivileged user to gain full root access to a system. The disclosure has sparked significant controversy within the cybersecurity community because the researchers released the proof-of-concept before many distributions could prepare patches. This "no-notice" disclosure left system administrators worldwide scrambling to implement manual mitigations, such as blacklisting the vulnerable algif_aead module to prevent exploitation. As the industry grapples with this widespread risk, the incident underscores the growing power of AI in discovering deep-seated codebase flaws and the ongoing debate regarding coordinated disclosure practices in the open-source ecosystem.


How to Fix Data Platform Sprawl: 3 Patterns and 3 Steps for Better Platform Decisions

In "How to Fix Data Platform Sprawl," Keerthi Penmatsa examines the hidden risks of fragmented enterprise data strategies. As organizations adopt diverse tools like Snowflake and Databricks, they often encounter three detrimental sprawl patterns: costly, redundant pipelines that threaten data consistency; operational friction from tight cross-team dependencies; and fragmented governance that complicates regulatory compliance. While open table formats provide partial relief, Penmatsa argues they cannot resolve the deeper structural complexity. To address this, she proposes a strategic three-lens framework for platform decision-making. First, leaders must evaluate business considerations and operational fit, balancing maintainability against vendor ecosystem benefits. Second, they must prioritize Economics and FinOps alignment to manage the volatile costs of consumption-based models via improved spend tracking. Finally, a focus on data governance and security ensures platforms have the native capabilities for robust policy enforcement and privacy. By moving beyond narrow feature checklists to these holistic strategic bets, executives can transform a chaotic environment into a resilient, value-driven ecosystem. This transition allows technology investments to become sustainable competitive advantages while ensuring rigorous, centralized control over organizational data in the AI era.


AI data debt: The risk lurking beneath enterprise intelligence

"AI Data Debt: The Risk Lurking Beneath Enterprise Intelligence" by Ashish Kumar explores the emerging danger of "AI data debt," a concept analogous to technical debt that arises when organizations prioritize rapid AI deployment over robust data foundations. This debt accumulates through poor data quality, legacy assumptions, and hidden biases, often remaining unrecognized until systems fail at scale. In critical sectors like healthcare and education, such inconsistencies can lead to life-altering erroneous diagnoses or suboptimal learning experiences. The author warns that AI often creates an "illusion of intelligence," projecting authority while relying on flawed inputs that degrade over time through "data drift." To mitigate these risks, Kumar emphasizes the necessity of comprehensive data governance, "privacy by design," and a unified data ontology to ensure semantic consistency across departments. Furthermore, organizations must implement rigorous data-handling mechanisms—including validation checks, lineage tracking, and continuous monitoring—to maintain integrity. Ultimately, the article argues that sustainable enterprise intelligence requires a strategic shift from breakneck scaling to foundational strength. By establishing clear ownership and accountability, businesses can transform data from a latent liability into a reliable strategic asset, ensuring that their AI initiatives remain ethical, compliant, and genuinely effective.


Cyber Threats to DevOps Platforms Rising Fast, GitProtect Report Finds

The "DevOps Threats Unwrapped Report 2026" from GitProtect reveals a concerning 21% increase in cyber incidents targeting DevOps environments throughout 2025, with total downtime nearly doubling to a staggering 9,225 hours. This surge in high-severity disruptions, which rose by 69% year-over-year, cost organizations more than $740,000 in lost productivity. Leading platforms like GitHub, Azure DevOps, and Jira have become prime targets for sophisticated malware campaigns, including Shai-Hulud and GitVenom, which leverage trusted infrastructure for credential harvesting and malware distribution. Attackers are increasingly exploiting automation, poisoned packages, and malicious AI-generated code to bypass traditional perimeter defenses. The report highlights that 62% of outages were driven by performance degradation, though post-incident maintenance consumed a disproportionate 30% of total downtime. With 236 security flaws patched in 2025—many categorized as critical or high severity—the findings underscore that reactive monitoring is no longer sufficient. Daria Kulikova of GitProtect emphasizes that as cybercriminals blend hardware-aware evasion with phishing-as-a-service, organizations must transition toward a proactive DevSecOps model. This approach integrates continuous monitoring and automated security throughout the development lifecycle to safeguard data integrity and maintain business continuity against an increasingly evolving and aggressive global threat landscape.


AI in Banking: An Advanced Overview

The article "AI in Banking: An Advanced Overview" examines how financial institutions are transitioning from basic applications like chatbots toward sophisticated artificial intelligence integrations that streamline operations and deepen customer loyalty. While traditional uses focused on fraud detection, modern banks are now deploying predictive analytics for loan approvals and leveraging generative AI to automate complex knowledge work, such as internal support and marketing development. Experts Jerry Silva and Alyson Clarke emphasize that the true potential of AI lies in moving beyond incremental efficiency to foster innovation in new products and services. However, significant hurdles remain, particularly for institutions burdened by legacy systems that complicate the adoption of open APIs and modern AI capabilities. The piece highlights a shift in focus from cost-cutting to growth, with projections suggesting that by 2028, over half of AI budgets will fund new revenue-generating initiatives. Despite a current lack of specific federal regulations, banks are proactively prioritizing transparency and model explainability to maintain trust. Ultimately, the future of banking in 2026 and beyond will be defined by "agentic AI" and personal digital clones, provided organizations can resolve lingering questions regarding liability and master the data strategies necessary to support these advanced autonomous systems.


ODNI to CISOs on threat assessments: You’re on your own

In his analysis of the 2026 Annual Threat Assessment (ATA), Christopher Burgess argues that the Office of the Director of National Intelligence (ODNI) has pivoted toward a homeland-centric, reactive posture, effectively leaving the private sector to manage its own strategic defense. This year’s ATA omits granular, future-leaning analysis of state actors like China and Russia, instead folding them into broader regional narratives. For security leaders, this represents a dangerous dilution of strategic warning, particularly as it excludes critical updates on persistent infrastructure campaigns like Volt Typhoon. By focusing on immediate operational successes and domestic stability, the Intelligence Community has signaled a contraction in its early-warning role, outsourcing the forecasting of long-term adversary intent to CISOs and CROs. To bridge this gap, Burgess proposes a "resilience premium" framework, urging organizations to prioritize identity integrity, conduct dormant access audits for infrastructure continuity, and accelerate quantum migration roadmaps. Ultimately, while the government reports on past policy outcomes, the burden of anticipating and defending against evolving cyber threats—such as AI-driven anomalies and insider infiltration—now rests squarely on the shoulders of private enterprise, requiring a shift from efficiency-focused security to robust, intelligence-integrated resilience.


Harness teams of agentic coders with Squad

In "Harness teams of agentic coders with Squad," Simon Bisson examines the growing "productivity crisis" where developers are increasingly overwhelmed by AI-generated bug reports and mounting technical debt. To combat this, Bisson introduces Squad, an open-source framework developed by Microsoft's Brady Gaster that orchestrates multiple specialized AI agents through GitHub Copilot. Replicating a traditional development team structure, Squad creates distinct roles such as a developer lead, front-end and back-end engineers, and test engineers. A key architectural innovation is Squad’s rejection of fragile agent-to-agent chatting; instead, it treats agents as asynchronous tasks synchronized via persistent external storage in Markdown format. This ensures shared "memory" and context are preserved across sessions and remain accessible to all team members. Additionally, Squad employs a unique verification process where separate agents fix issues identified by testers, preventing repetitive logic loops and statistical hallucinations. Whether utilized via a CLI, Visual Studio Code, or a TypeScript SDK, the system positions the human developer as a senior architect managing a "pocket team" of artificial junior developers. By leveraging this multi-agent harness, organizations can transform application development into a more efficient, test-driven process, providing a much-needed force multiplier to keep pace with the rapidly evolving demands and security vulnerabilities of modern software engineering.


The Model Is the Data—and That Changes Everything

In "The Model Is the Data—and That Changes Everything," published on HPCwire and BigDATAwire in April 2026, the author examines a profound transformation in artificial intelligence that dismantles the long-standing perception of AI as an enigmatic "magic" black box. Traditionally, the industry separated complex algorithms from the datasets they processed; however, the article argues that we have entered an era where the model and the data are fundamentally unified. This evolution is largely driven by vectorization, where models rely on high-dimensional vectors to interpret raw information directly, effectively making the data’s structural representation the primary source of intelligence. The piece emphasizes that enterprise success no longer depends solely on algorithmic complexity but on "context engineering"—the precise curation of data to guide model reasoning. Consequently, traditional data architectures, which were designed for movement rather than decision-making, are being replaced by integrated platforms. By highlighting the shift from rigid pipelines to dynamic, data-centric systems, the article posits that AI is transitioning from a tool for analysis into a fundamental engine for autonomous discovery. Ultimately, this technological shift dictates that data is not merely fuel for the model; it has become the model itself.


AI chatbots need ‘deception mode’

In his Computerworld article, Mike Elgan addresses the growing concern of AI anthropomorphism, where users mistake software for sentient beings due to human-like traits like empathy, humor, and deliberate response delays. New research indicates that people often perceive slower AI responses as more "thoughtful," a phenomenon Elgan describes as a "user delusion" that tech companies exploit to foster an "attachment economy." By designing chatbots with fake emotional intelligence and simulated empathy, developers lower users' psychological guards, potentially leading to social isolation, misplaced trust, and the leakage of sensitive personal data. To combat this manipulative design trend, Elgan advocates for a regulatory requirement called "deception mode." Proposed by bioethicist Jesse Gray, this framework mandates that AI systems remain strictly neutral and robotic by default. Under this model, human-like qualities would only be accessible if a user explicitly activates a "deception mode" toggle. This approach ensures informed consent, grounding the user in the reality that any perceived "humanity" is merely a programmed facade. Ultimately, Elgan argues that such a feature is essential to preserve human clarity and control as AI continues to integrate into daily life, preventing a future where the majority of society is misled by artificial personalities.


The DPoP Storage Paradox: Why Browser-Based Proof-of-Possession Remains an Unsolved Problem

"The DPoP Storage Paradox: Why Browser-Based Proof-of-Possession Remains an Unsolved Problem" by Dhruv Agnihotri highlights a critical security gap in modern OAuth 2.0 implementations. While DPoP (RFC 9449) effectively binds access tokens to a client-generated key pair to prevent replay attacks, it offers no standardized guidance on browser-side key storage. This leads to a "storage paradox": storing keys as non-extractable objects in IndexedDB prevents exfiltration but fails to stop the "Oracle Attack." In this scenario, an XSS payload uses the browser's own cryptographic subsystem to sign malicious proofs without ever needing to extract the raw key bytes. To mitigate these risks, Agnihotri evaluates several architectural patterns, noting that with the finalization of the FAPI 2.0 Security Profile, sender-constraining has become a mandate rather than an option. The Backend-for-Frontend (BFF) pattern is presented as the industry standard, moving sensitive key material to a secure server-side component. For serverless environments where a BFF is unfeasible, a "zero-persistence" memory-only approach is recommended. This ephemeral strategy restricts the attack window to a single session but requires "Lazy Re-Binding" to rotate keys during page reloads. Ultimately, the article argues that there is no universal "safe default" for browser-based key storage; developers must deliberately align their architecture with their specific threat model and infrastructure constraints.

Daily Tech Digest - February 07, 2026


Quote for the day:

"Success in almost any field depends more on energy and drive than it does on intelligence. This explains why we have so many stupid leaders." -- Sloan Wilson


Tiny AI: The new oxymoron in town? Not really!

Could SLMs and minituarised models be the drink that would make today’s AI small enough to walk through these future doors without AI bumping into carbon-footprint issues? Would model compression tools like pruning, quantisation, and knowledge distillation help to lift some weight off the shoulders of heavy AI backyards? Lightweight models, edge devices that save compute resources, smaller algorithms that do not put huge stress on AI infrastructures, and AI that is thin on computational complexity- Tiny AI- as an AI creation and adoption approach- sounds unusual and promising at the onset. ... hardware innovations and new approaches to modelling that enable Tiny AI can significantly ease the compute and environmental burdens of large-scale AI infrastructures, avers Biswajeet Mahapatra, principal analyst at Forrester. “Specialised hardware like AI accelerators, neuromorphic chips, and edge-optimised processors reduces energy consumption by performing inference locally rather than relying on massive cloud-based models. At the same time, techniques such as model pruning, quantisation, knowledge distillation, and efficient architectures like transformers-lite allow smaller models to deliver high accuracy with far fewer parameters.” ... Tiny AI models run directly on edge devices, enabling fast, local decision-making by operating on narrowly optimised datasets and sending only relevant, aggregated insights upstream, Acharya spells out. 


Kali Linux vs. Parrot OS: Which security-forward distro is right for you?

The first thing you should know is that Kali Linux is based on Debian, which means it has access to the standard Debian repositories, which include a wealth of installable applications. ... There are also the 600+ preinstalled applications, most of which are geared toward information gathering, vulnerability analysis, wireless attacks, web application testing, and more. Many of those applications include industry-specific modifications, such as those for computer forensics, reverse engineering, and vulnerability detection. And then there are the two modes: Forensics Mode for investigation and "Kali Undercover," which blends the OS with Windows. ... Parrot OS (aka Parrot Security or just Parrot) is another popular pentesting Linux distribution that operates in a similar fashion. Parrot OS is also based on Debian and is designed for security experts, developers, and users who prioritize privacy. It's that last bit you should pay attention to. Yes, Parrot OS includes a similar collection of tools as does Kali Linux, but it also offers apps to protect your online privacy. To that end, Parrot is available in two editions: Security and Home. ... What I like about Parrot OS is that you have options. If you want to run tests on your network and/or systems, you can do that. If you want to learn more about cybersecurity, you can do that. If you want to use a general-purpose operating system that has added privacy features, you can do that.


Bridging the AI Readiness Gap: Practical Steps to Move from Exploration to Production

To bridge the gap between AI readiness and implementation, organizations can adopt the following practical framework, which draws from both enterprise experience and my ongoing doctoral research. The framework centers on four critical pillars: leadership alignment, data maturity, innovation culture, and change management. When addressed together, these pillars provide a strong foundation for sustainable and scalable AI adoption. ... This begins with a comprehensive, cross-functional assessment across the four pillars of readiness: leadership alignment, data maturity, innovation culture, and change management. The goal of this assessment is to identify internal gaps that may hinder scale and long-term impact. From there, companies should prioritize a small set of use cases that align with clearly defined business objectives and deliver measurable value. These early efforts should serve as structured pilots to test viability, refine processes, and build stakeholder confidence before scaling. Once priorities are established, organizations must develop an implementation road map that achieves the right balance of people, processes, and technology. This road map should define ownership, timelines, and integration strategies that embed AI into business workflows rather than treating it as a separate initiative. Technology alone will not deliver results; success depends on aligning AI with decision-making processes and ensuring that employees understand its value. 


Proxmox's best feature isn't virtualization; it's the backup system

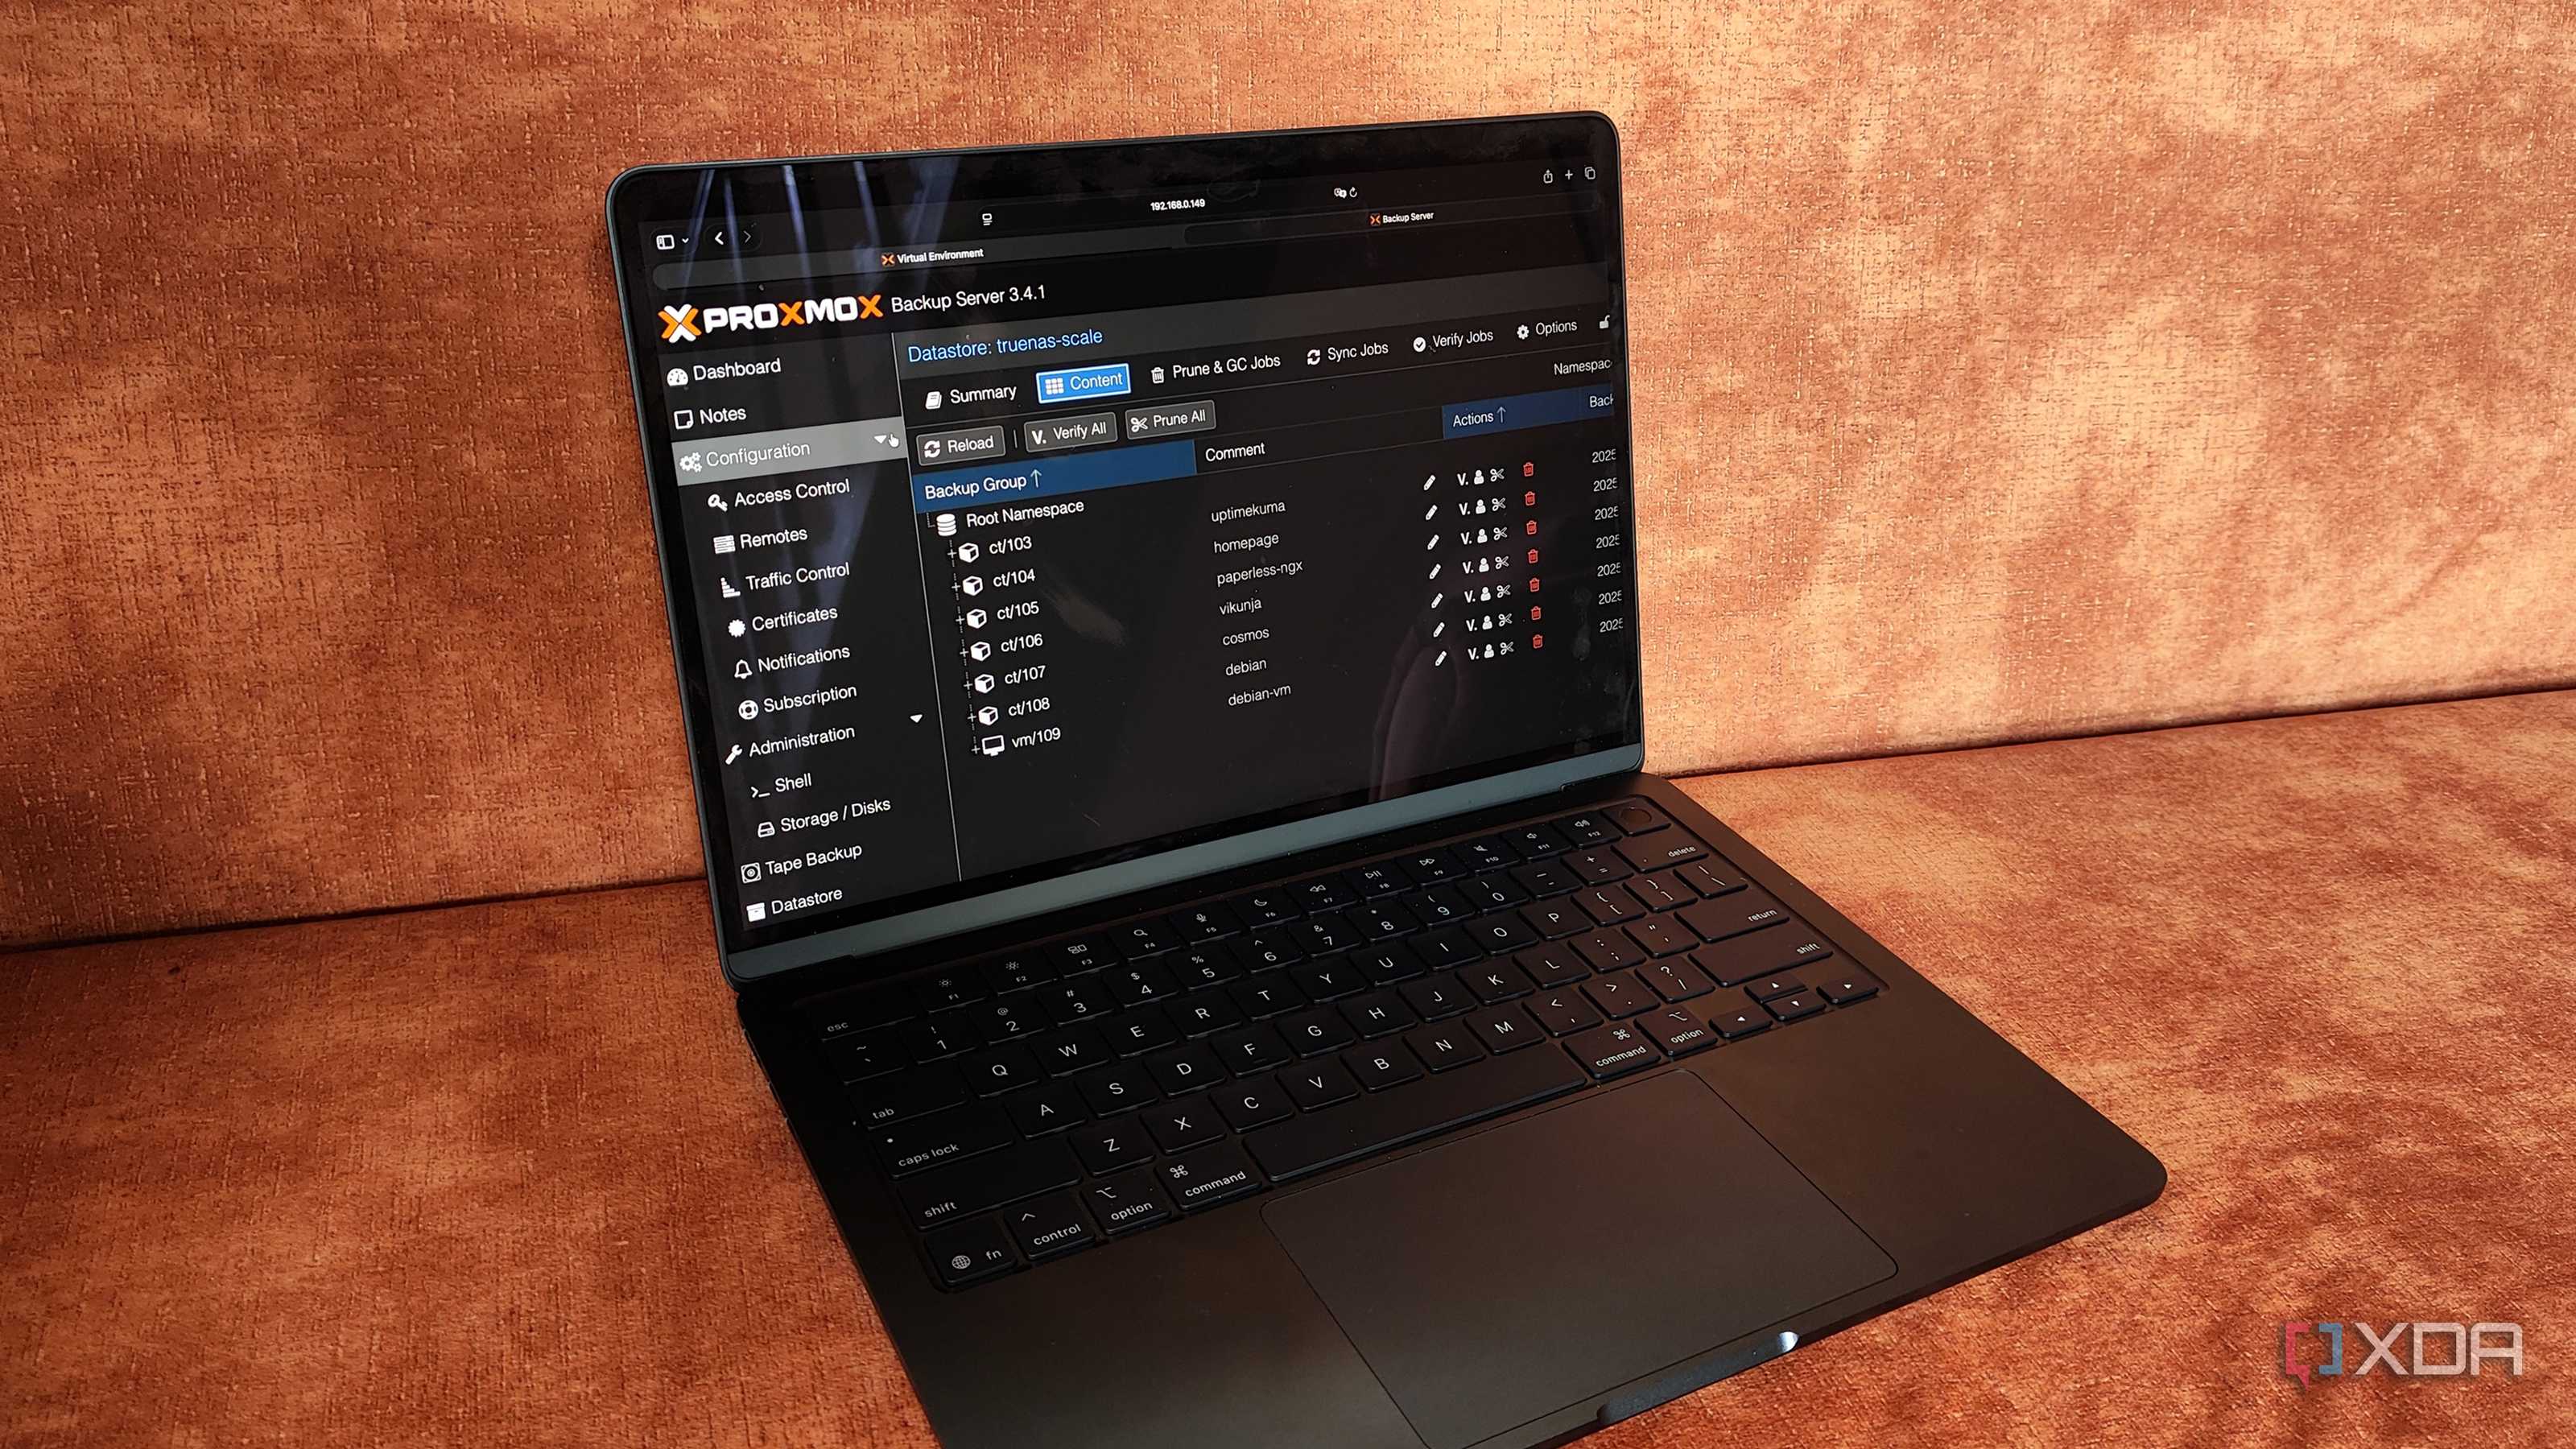
Because backups are integrated into Proxmox instead of being bolted on as some third-party add-on, setting up and using backups is entirely seamless. Agents don't need to be configured per instance. No extra management is required, and no scripts need to be created to handle the running of snapshots and recovery. The best part about this approach is that it ensures everything will continue working with each OS update. Backups can be spotted per instance, too, so it's easy to check how far you can go back and how many copies are available. The entire backup strategy within Proxmox is snapshot-based, leveraging localised storage when available. This allows Proxmox to create snapshots of not only running Linux containers, but also complex virtual machines. They're reliable, fast, and don't cause unnecessary downtime. But while they're powerful additions to a hypervised configuration, the backups aren't difficult to use. This is key since it would render the backups less functional if it proved troublesome to use them when it mattered most. These backups don't have to use local storage either. NFS, CIFS, and iSCSI can all be targeted as backup locations.  ... It can also be a mixture of local storage and cloud services, something we recommend and push for with a 3-2-1 backup strategy. But there's one thing of using Proxmox's snapshots and built-in tools and a whole different ball game with Proxmox Backup Server. With PBS, we've got duplication, incremental backups, compression, encryption, and verification.


The Fintech Infrastructure Enabling AI-Powered Financial Services

AI is reshaping financial services faster than most realize. Machine learning models power credit decisions. Natural language processing handles customer service. Computer vision processes documents. But there’s a critical infrastructure layer that determines whether AI-powered financial platforms actually work for end users: payment infrastructure. The disconnect is striking. Fintech companies invest millions in AI capabilities, recommendation engines, fraud detection, personalization algorithms. ... From a technical standpoint, the integration happens via API. The platform exposes user balances and transaction authorization through standard REST endpoints. The card provider handles everything downstream: card issuance logistics, real-time currency conversion, payment network settlement, fraud detection at the transaction level, dispute resolution workflows. This architectural pattern enables fintech platforms to add payment functionality in 8-12 weeks rather than the 18-24 months required to build from scratch. ... The compliance layer operates transparently to end users while protecting platforms from liability. KYC verification happens at multiple checkpoints. AML monitoring runs continuously across transaction patterns. Reporting systems generate required documentation automatically. The platform gets payment functionality without becoming responsible for navigating payment regulations across dozens of jurisdictions.


Context Engineering for Coding Agents

Context engineering is relevant for all types of agents and LLM usage of course. My colleague Bharani Subramaniam’s simple definition is: “Context engineering is curating what the model sees so that you get a better result.” For coding agents, there is an emerging set of context engineering approaches and terms. The foundation of it are the configuration features offered by the tools, and then the nitty gritty of part is how we conceptually use those features. ... One of the goals of context engineering is to balance the amount of context given - not too little, not too much. Even though context windows have technically gotten really big, that doesn’t mean that it’s a good idea to indiscriminately dump information in there. An agent’s effectiveness goes down when it gets too much context, and too much context is a cost factor as well of course. Some of this size management is up to the developer: How much context configuration we create, and how much text we put in there. My recommendation would be to build context like rules files up gradually, and not pump too much stuff in there right from the start. ... As I said in the beginning, these features are just the foundation for humans to do the actual work and filling these with reasonable context. It takes quite a bit of time to build up a good setup, because you have to use a configuration for a while to be able to say if it’s working well or not - there are no unit tests for context engineering. Therefore, people are keen to share good setups with each other.


Reimagining The Way Organizations Hire Cyber Talent

The way we hire cybersecurity professionals is fundamentally flawed. Employers post unicorn job descriptions that combine three roles’ worth of responsibilities into one. Qualified candidates are filtered out by automated scans or rejected because their resumes don’t match unrealistic expectations. Interviews are rushed, mismatched, or even faked—literally, in some cases. On the other side, skilled professionals—many of whom are eager to work—find themselves lost in a sea of noise, unable to connect with the opportunities that align with their capabilities and career goals. Add in economic uncertainty, AI disruption and changing work preferences, and it’s clear the traditional hiring playbook simply isn’t working anymore. ... Part of fixing this broken system means rethinking what we expect from roles in the first place. Jones believes that instead of packing every security function into a single job description and hoping for a miracle, organizations should modularize their needs. Need a penetration tester for one month? A compliance SME for two weeks? A security architect to review your Zero Trust strategy? You shouldn’t have to hire full-time just to get those tasks done. ... Solving the cybersecurity workforce challenge won’t come from doubling down on job boards or resume filters. But organizations may be able to shift things in the right direction by reimagining the way they connect people to the work that matters—with clarity, flexibility and mutual trust.


News sites are locking out the Internet Archive to stop AI crawling. Is the ‘open web’ closing?

Publishers claim technology companies have accessed a lot of this content for free and without the consent of copyright owners. Some began taking tech companies to court, claiming they had stolen their intellectual property. High-profile examples include The New York Times’ case against ChatGPT’s parent company OpenAI and News Corp’s lawsuit against Perplexity AI. ... Publishers are also using technology to stop unwanted AI bots accessing their content, including the crawlers used by the Internet Archive to record internet history. News publishers have referred to the Internet Archive as a “back door” to their catalogues, allowing unscrupulous tech companies to continue scraping their content. ... The opposite approach – placing all commercial news behind paywalls – has its own problems. As news publishers move to subscription-only models, people have to juggle multiple expensive subscriptions or limit their news appetite. Otherwise, they’re left with whatever news remains online for free or is served up by social media algorithms. The result is a more closed, commercial internet. This isn’t the first time that the Internet Archive has been in the crosshairs of publishers, as the organisation was previously sued and found to be in breach of copyright through its Open Library project. ... Today’s websites become tomorrow’s historical records. Without the preservation efforts of not-for-profit organisations like The Internet Archive, we risk losing vital records.


Who will be the first CIO fired for AI agent havoc?

As CIOs deploy teams of agents that work together across the enterprise, there’s a risk that one agent’s error compounds itself as other agents act on the bad result, he says. “You have an endless loop they can get out of,” he adds. Many organizations have rushed to deploy AI agents because of the fear of missing out, or FOMO, Nadkarni says. But good governance of agents takes a thoughtful approach, he adds, and CIOs must consider all the risks as they assign agents to automate tasks previously done by human employees. ... Lawsuits and fines seem likely, and plaintiffs will not need new AI laws to file claims, says Robert Feldman, chief legal officer at database services provider EnterpriseDB. “If an AI agent causes financial loss or consumer harm, existing legal theories already apply,” he says. “Regulators are also in a similar position. They can act as soon as AI drives decisions past the line of any form of compliance and safety threshold.” ... CIOs will play a big role in figuring out the guardrails, he adds. “Once the legal action reaches the public domain, boards want answers to what happened and why,” Feldman says. ... CIOs should be proactive about agent governance, Osler recommends. They should require proof for sensitive actions and make every action traceable. They can also put humans in the loop for sensitive agent tasks, design agents to hand off action when the situation is ambiguous or risky, and they can add friction to high-stakes agent actions and make it more difficult to trigger irreversible steps, he says.


Measuring What Matters: Balancing Data, Trust and Alignment for Developer Productivity

Organizations need to take steps over and above these frameworks. It's important to integrate those insights with qualitative feedback. With the right balance of quantitative and qualitative data insights, companies can improve DevEx, increase employee engagement, and drive overall growth. Productivity metrics can only be a game-changer if used carefully and in conjunction with a consultative human-based approach to improvement. They should be used to inform management decisions, not replace them. Metrics can paint a clear picture of efficiency, but only become truly useful once you combine them with a nuanced view of the subjective developer experience. ... People who feel safe at work are more productive and creative, so taking DevEx into account when optimizing processes and designing productivity frameworks includes establishing an environment where developers can flag unrealistic deadlines and identify and solve problems together, faster. Tools, including integrated development environments (IDEs), source code repositories and collaboration platforms, all help to identify the systemic bottlenecks that are disrupting teams' workflows and enable proactive action to reduce friction. Ultimately, this will help you build a better picture of how your team is performing against your KPIs, without resorting to micromanagement. Additionally, when company priorities are misaligned, confusion and complexity follow, which is exhausting for developers, who are forced to waste their energy on bridging the gaps, rather than delivering value.