Showing posts with label cybersecurity. Show all posts

Daily Tech Digest - October 26, 2026

Quote for the Day
“If you can’t describe what you are doing as a process, you don’t know what you’re doing.”
— W. Edwards Deming
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

The Migration Succeeded. The System Got Worse

Moving an application to the public cloud is often seen as an automatic upgrade, but a successful migration does not always result in a better system. One of the most common mistakes is relocating an application while leaving its primary database in an on-premises data center. This separation introduces critical network delays, meaning a system that functions fine under normal traffic can quickly suffer from connection exhaustion and severe failures during peak demand. While the cloud offers useful capabilities like flexible capacity and managed services, these benefits only matter if the entire technology stack is optimized for them. Simply moving infrastructure without addressing underlying dependencies often leads to inflated costs and new operational risks. A hybrid approach can be effective if planned deliberately, but it becomes an expensive burden when components are separated without a clear strategy. Ultimately, there is no single correct environment for every workload. Deciding whether to migrate, maintain a hybrid setup, or bring systems back in-house requires a realistic evaluation of performance, dependencies, and true operating costs.

Read Original Article →

Healthcare Data Governance: Who Decides What Gets Used?

Healthcare data governance is much more than just creating internal rules; it requires assigning clear, enforceable decision rights as patient information moves across different systems, APIs, and AI models. Rather than simply asking who owns the data, organizations should divide authority into four specific areas: legal permissions, operational approval, technical enforcement, and final accountability. This division is vital because when data is shared with payers, cloud vendors, or secondary AI tools, the original privacy policies are easily lost if someone is not explicitly responsible for enforcing them. Crucially, moving data to a cloud environment does not remove the healthcare organization's ultimate accountability. To prevent confusion and maintain compliance, organizations need a simple decision-rights matrix that clearly names the single person responsible for defining, accessing, reusing, correcting, and deleting data at every step of its journey. Ambiguity between different departments often leads to failure. Therefore, every single data handoff must have a clear owner equipped with both the responsibility and the actual power to enforce policies and correct issues.

Read Original Article →
Article Thumbnail

Identity at checkout: why payments must prove more and share less

As digital identity tools and payment systems continue to merge, payment providers face new challenges regarding customer verification and data privacy. With the European Union requiring digital identity wallets by late 2026, the traditional multi-step checkout process is shifting into a single, unified action. However, this connection risks exposing too much personal information. To protect consumer privacy and avoid the high costs of financial data breaches, payment networks must ask for only the minimum details required to approve a transaction, rather than viewing a user's entire background. At the same time, updated European rules are shifting fraud liability directly onto payment providers. If weak security checks let fraud slip through, companies will face significant financial losses through mandatory customer refunds. Over the next two years, providers need to build checkout experiences that focus on strong but easy verification. By asking for less personal data while proving identity more securely, companies can lower their financial risks and build better trust with both merchants and everyday consumers.

Read Original Article →

India’s cybersecurity talent challenge: Why more automation must be matched by better skills

As artificial intelligence takes over routine cybersecurity tasks like filtering alerts, the role of security professionals in India is fundamentally changing. Instead of simply operating tools, experts must now focus on validating AI findings, making complex judgment calls, and understanding when an automated system might be wrong. A recent report shows that most Indian enterprises struggle to find candidates with these practical, hands-on skills. To bridge this gap, organizations need to rethink how they train their teams. Standard certifications are no longer enough. Instead, companies should offer role-specific training and simulated scenarios where professionals can practice handling incomplete information and testing automated security boundaries. This shift is a major opportunity for India’s technology sector to build a workforce capable of supporting global security operations. Ultimately, the future of cybersecurity isn't just about how much we can automate, but how well humans and machines can work together to defend an increasingly complex digital landscape.

Read Original Article →
Article Thumbnail

Psychological Safety: The Overlooked Risk in Workplace AI Adoption

As organizations integrate AI into daily operations, they heavily focus on data security and privacy while frequently overlooking a crucial human element: psychological safety. Employees are adjusting rapidly to these tools, which naturally creates anxiety about job security and personal competence. If workers feel afraid to admit they do not understand a system, or remain hesitant to challenge an odd result, small mistakes can easily go unnoticed and escalate. A written corporate policy alone cannot prevent this. To use AI responsibly, leaders must actively build a workplace where people feel completely safe raising concerns. Management should encourage questions, acknowledge their own uncertainties, and demonstrate that healthy skepticism toward AI outputs is a sign of good judgment, rather than resistance to change. When leaders communicate clear expectations and actively support their teams, employees gain the confidence needed to catch errors early. Ultimately, building trust ensures that these new tools are used responsibly and effectively as a normal part of everyday work.

Read Original Article →
Article Thumbnail

Your AI Agent Has a Supervisor. Are They Qualified?

As AI systems handle more tasks in security operations, they are not replacing human analysts. Instead, analysts are shifting into supervisory roles to direct and review the technology's work. The central issue is that many companies simply add this responsibility to an analyst's existing workload without providing proper training, clear guidelines, or a defined job title. To fix this, organizations must establish AI supervision as a distinct and formal role. Supervisors need a deep understanding of security threats so they can properly set limits, question the AI's reasoning, and catch missing evidence. A supervisor's readiness should be tested through practical exercises rather than basic training completion. When evaluating success, security teams should focus on the quality of these reviews instead of how quickly tickets are closed. As AI tools gain the ability to take direct actions, like isolating systems or disabling accounts, strict human oversight becomes increasingly vital. Ultimately, a qualified human supervisor must own the final decisions to ensure accountability and maintain a secure environment.

Read Original Article →

Enterprise Deployment Architecture for Agentic AI on IIS: ChatGPT-Style UI over Agents & MCP Servers

The article outlines an architectural guide for deploying a ChatGPT-style web interface using Microsoft Internet Information Services (IIS) to front an agent powered by the Model Context Protocol (MCP). Instead of running agent interactions in a basic developer console, the paper presents a system tailored for enterprise needs, supporting 25 to 30 concurrent users. It relies on Windows Authentication and an IIS reverse proxy connecting to a long-running Python service. This design choice provides stability and avoids the overhead of launching a new process for every user request, while also eliminating the need for complex Kerberos double-hop delegation. The reference model, named ChefAI, illustrates a practical use case where restaurant staff query an assistant for real-time information, invoice generation, and technical troubleshooting. The agent connects to a local server for secure local tasks and remote HTTP servers for retrieving documents or analyzing logs. By using Server-Sent Events, the setup ensures smooth progress streaming to the chat interface, keeping the user interface completely independent of how the underlying tools are accessed or deployed.
Read Original Article →
Article Thumbnail

Your PQC Plan Trusts the One Thing You May Not Be Checking

As organizations prepare for post-quantum cryptography, they usually focus on mapping their current encryption tools and ensuring software flexibility. However, many migration plans overlook a critical, foundational vulnerability: the quality of their random number generators. Even the most advanced encryption algorithms will fail if the underlying randomness is predictable or generated by flawed hardware. Rather than relying solely on software upgrades, companies must trace exactly where their randomness originates and ensure it comes from verified, properly functioning sources. Upgrading safely requires identifying outdated legacy systems that cannot support new standards and adjusting procurement policies to demand quantum-resistant features immediately. Security leaders should treat this transition as a vital business continuity effort, not just an IT compliance checklist. By securing hardware-level trust, verifying random number generation, and acting early, organizations can effectively protect their most critical systems and avoid the steep financial costs of rushing to fix vulnerabilities later.

Read Original Article →
Article Thumbnail

Java vs Python in 2026: Which One Should You Learn for Backend, AI, and Data Science?

In 2026, the choice between Java and Python depends on your engineering goals rather than which language is simply more popular. Python is the primary language for artificial intelligence, machine learning, and data analytics. Its extensive ecosystem makes it the standard for researching and training models. On the other hand, Java remains the foundation for large enterprise backend systems, such as banking and retail platforms. Java provides the performance, structural safety, and mature frameworks needed to support massive, high-traffic codebases over many years. In practice, companies often use both: Python builds the AI models, while Java runs the reliable infrastructure around them. Python has an easier learning curve and gets you building faster, whereas Java requires more initial effort but teaches strict engineering fundamentals. Ultimately, if you aim to work directly with data or machine learning, start with Python. If you prefer building durable, large-scale backend architecture, focus on Java. Both offer strong career paths without the need for hype.

Read Original Article →

What Is CRQ? Cyber Risk Quantification Guide

Cyber risk quantification is a method that assigns clear financial values to potential security threats, allowing organizations to understand the real-world business impact of cyber events. Rather than viewing security solely as a technical issue, this approach translates risks into standard financial terms, making it much easier for security leaders to communicate with corporate boards and executives. By analyzing historical data alongside the frequency and severity of potential incidents, organizations can predict financial losses across both internal systems and third-party providers. This clarity helps businesses move away from subjective guesswork, enabling them to make practical decisions about where to invest their security budgets and how to prioritize protective measures. In addition to improving internal planning, putting a dollar figure on risk helps organizations negotiate better insurance terms, measure the return on their security investments, and establish a realistic tolerance for risk. Ultimately, calculating these financial impacts provides companies with the necessary insight to reduce the overall cost of security incidents and maintain steady operations.

Read Original Article →

Daily Tech Digest - October 25, 2026

Quote for the Day
“The only way to win is to learn faster than anyone else.”
— Eric Ries
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Core Concepts in Infrastructure Cost Management

The article revisits how organizations should think about infrastructure cost management by comparing on‑premise and cloud deployment patterns. It notes that a decade ago, cloud was widely seen as the inevitable future, but recent shifts show that on‑premise environments still offer advantages worth reconsidering. On‑premise setups involve not just servers but the full physical ecosystem — racks, networking gear, cooling, power, and security — all of which carry long‑term financial and operational implications. The piece explains that while on‑premise environments are often labeled inflexible, they can be surprisingly adaptable when paired with modern automation frameworks. The real challenges lie in hardware lifespan decisions, sizing development and QA environments, managing shared analytic workloads, and maintaining disaster‑recovery sites that are costly to keep idle. These factors shape both capital and operational expenses over many years. The article’s steady message is that cost management requires understanding the trade‑offs between flexibility, predictability, and long‑term commitments, and that both cloud and on‑premise models have strengths that deserve thoughtful evaluation rather than assumptions.

Read Original Article →

Container Security Checklist for CI/CD Pipelines: 30 Checks From Commit to Runtime

This article presents a practical security checklist containing 30 checks for container images as they move through continuous integration and deployment pipelines. The core message is that actual security comes from enforcing rules, not just listing best practices. The checks span eight stages, from the initial code commit to runtime monitoring. In the early stages, teams should build minimal images, remove all secrets, and lock down third-party actions. Later stages focus on vulnerability scanning that blocks risky deployments, generating software bills of materials, and digitally signing images to guarantee they came from a trusted build. At deployment, admission controllers must verify signatures and restrict permissions so images cannot run with root access or modify the underlying host. Because the pipeline itself is a high-privilege system that can be compromised, securing the build process is just as important as securing the image. Implementing these checks incrementally—starting with basic Dockerfile hygiene—prevents common mistakes and ensures a cleaner, safer production environment.

Read Original Article →
Article Thumbnail

Cloud repatriation: What CISOs need to know

The article explains that cloud repatriation is becoming a practical concern for CISOs, not because enterprises are abandoning the cloud, but because many workloads no longer fit the cloud‑first assumptions of the past decade. Surveys show that while 86% of CIOs plan to move at least some workloads back on‑premises, only about 8–9% intend a full exit, meaning most organizations are simply recalibrating workload placement rather than rejecting cloud altogether. Cost discipline is a major driver, with private cloud often delivering 40–50% lower total cost of ownership for steady‑state workloads. Compliance, data‑gravity issues, and high‑intensity AI workloads also push certain systems back into controlled environments. The article stresses that hybrid infrastructure is becoming the long‑term norm, where each workload “earns” its placement based on economics, performance, and risk. For CISOs, this shift introduces new responsibilities: reassessing threat models, ensuring consistent controls across mixed environments, and preparing for operational risks tied to vendor concentration and geopolitical disruptions. The message is steady — repatriation is about precision, not retreat, and CISOs must adapt security strategies accordingly.

Read Original Article →

The Cybersecurity Reality Check: Ten Myths That Matter

The article challenges ten common assumptions that often mislead leaders about cybersecurity and explains why these misconceptions create real risk. It notes that serious incidents rarely stem from exotic technical failures; instead, they usually begin with flawed beliefs about who attackers target, where responsibility sits, or what “adequate protection” really means. One myth is that small organizations are too insignificant to attract attention, but attackers typically exploit exposed systems using automated tools, making size irrelevant. Smaller firms may even be more vulnerable because they have fewer security resources and weaker monitoring. Another misconception is that cybersecurity is purely an IT function, when governance and accountability actually rest with leadership. The article stresses that regulatory scrutiny in the UK and EU has intensified, and breaches can quickly lead to investigations, litigation, business interruption, and reputational harm. Ultimately, the piece argues that organizations must be able to justify their security measures as proportionate to their risks and abandon assumptions that no longer match today’s threat landscape.

Read Original Article →
Article Thumbnail

When Trust Fails: What the eMudhra Certificate Incident and PHP Vulnerabilities Teach Us About Zero Trust Security

In October 2026, two distinct cybersecurity events—a certificate failure by eMudhra and critical remote code execution flaws in PHP—highlighted a fundamental lesson for software engineers: trust must be constantly verified. The eMudhra incident involved weak intermediate cryptographic keys generated by a flawed process. Even though eMudhra itself was not hacked, the incident proved that secure connections rely on trustworthy underlying processes, not just a padlock icon. Meanwhile, the PHP vulnerabilities demonstrated that securing an application requires patching the entire software stack, not just the core code, because a vulnerable runtime can serve as an easy entry point. Together, these events show why modern systems must move away from assuming that any internal network or familiar request is automatically safe. Instead, engineers should adopt a strict verification approach. This means validating identity, authorization, and context at every boundary, properly handling access tokens, and protecting communication between internal services. Ultimately, security is an ongoing engineering process of continuous verification rather than a single static feature or one-time setup.

Read Original Article →

What OT detection actually reveals

Securing operational technology (OT) environments requires a fundamentally different approach than standard IT security. While conventional IT tools excel at spotting network anomalies, they lack the critical physical process context needed to recognize when otherwise legitimate industrial commands are used for malicious disruption. OT detection platforms solve this by combining industrial protocol awareness with a deep understanding of normal operational behavior and physical constraints. A solid asset inventory is the foundational first step. From there, effective OT security relies on five core capabilities: monitoring industrial protocol anomalies, establishing strict baselines for process behavior, tracking engineering workstation activity, closely managing remote vendor access, and correlating traffic across the IT/OT boundary. Because OT involves physical processes where any disruption can impact safety, detection must be paired with structured, pre-planned response strategies. Automated actions are generally safe only at the IT or DMZ layers. Any direct intervention touching physical plant controllers requires clear authorization from operations teams to ensure production environments remain safe and stable.

Read Original Article →
Article Thumbnail

AI accelerates path from IT compromise to OT targeting

The article explains that AI is accelerating the path from IT compromise to OT targeting, making industrial environments more exposed than before. Attackers can now use AI to quickly analyze stolen IT data, map relationships, and identify the most valuable operational assets to target. This shortens the traditional gap between breaching corporate networks and moving into industrial systems. The piece notes that modern OT environments are increasingly connected to cloud services, remote access tools, and SaaS platforms, creating more entry points and making it harder to maintain clear separation between IT and OT. AI also helps attackers craft more convincing phishing messages, automate reconnaissance, and generate malware tailored to specific environments. At the same time, defenders struggle with legacy systems, inconsistent visibility, and slow patch cycles. The article argues that organizations must rethink OT security by improving asset inventories, tightening identity controls, and preparing for faster, more automated attack chains. Its message is steady: AI has changed the tempo of intrusions, and OT security must adapt to match that speed.

Read Original Article →

The next manufacturing cyber threat is manipulation of AI-driven decisions

As manufacturing becomes increasingly connected, the nature of cybersecurity threats is shifting. According to Pradipta Patro, Chief Information Security Officer at Polycab India Limited, the next major risk isn't just about keeping hackers out of the network. It is about protecting the artificial intelligence systems that influence critical operational decisions. If an attacker manipulates the data feeding an AI model, the system could make unsafe or faulty decisions without triggering traditional alarms. This goes beyond compromised information, directly threatening production quality, equipment reliability, and even worker safety on the factory floor. To address this, security must be built into factories from the ground up rather than added later as an afterthought. Manufacturers need complete visibility into all connected devices, strong network boundaries between IT and operations, and meaningful human oversight of AI decisions. Ultimately, cyber resilience must be treated as a core business continuity issue. The most successful factories will be those that can fully trust their automated systems because they secured the underlying data first.

Read Original Article →
Article Thumbnail

Digital twins in oil and gas: from simulation to real-time optimisation

Digital twins in the oil and gas sector are evolving from isolated engineering studies into practical tools that drive daily operations. Historically, creating a digital twin took months and became outdated as soon as the physical equipment changed. Today, advanced models can be built quickly, update automatically alongside physical wear, and connect across entire systems. A key shift is the use of physics-based modeling rather than just relying on historical data. Purely statistical models struggle when equipment faces new or unobserved conditions. By grounding the software in the actual laws of fluid dynamics and heat transfer, operators receive reliable, real-time recommendations they can trust. This approach accounts for uncertainty, allowing teams to optimize active equipment and reduce waste like methane flaring by safely pushing production closer to its true limits. Solving the challenge of scaling these tools in energy operations also opens the door for similar efficiency gains in other complex, high-demand environments, such as data centers and power grids.

Read Original Article →
Article Thumbnail

Data Sovereignty is Becoming a Design Principle for Enterprise AI

In the past, data sovereignty simply meant knowing the physical location of your company’s servers to meet regional laws. Today, artificial intelligence has fundamentally changed this. Because data now constantly flows through various external applications, language models, and processing tools, maintaining control over it has become much more complex. Instead of trying to lock down an entire organization, companies should focus on individual tasks. For example, processing public marketing information requires far less strict control than handling sensitive medical records. A major challenge is ensuring that safety rules follow the information wherever it goes. When original records are transformed into formats that AI can read, those new formats must inherit the same restrictions. Tracking this movement requires strong underlying data tagging. To manage this effectively, businesses should view sovereignty as a flexible budget. They must calmly weigh the need for strict control against the benefits of using advanced, external technology. Ultimately, building a flexible setup allows teams to continuously adjust their safety measures as rules and technology evolve.

Read Original Article →

Daily Tech Digest - October 22, 2026

Quote for the Day
“Debugging is twice as hard as writing the code in the first place.”
— Brian Kernighan
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

14 ways attackers abuse cloud services to hack your enterprise

As enterprises migrate to hybrid and cloud environments, cyberattackers are evolving from "living off the land" to "living off the cloud," blending malicious activities into legitimate business traffic. Instead of relying on traditional malware that triggers alarms, adversaries are increasingly abusing trusted APIs, native administrative tools, and SaaS platforms to bypass conventional defenses. Attackers route command-and-control communications through reputable services like OpenAI, Microsoft Graph API, and Google Sheets, making the traffic look like routine developer or employee activity. They also exploit cloud identities, such as OAuth tokens and service accounts, to move laterally and access sensitive data without needing to compromise local servers directly. Further tactics include staging malware in object storage buckets, exfiltrating data via everyday tools like Slack, abusing ephemeral serverless functions to mask reconnaissance scans, and weaponizing identity tenant relationships. By exploiting the inherent trust and API-driven nature of modern cloud architecture, these cloud-native attack chains effectively turn the enterprise's operational backbone into a highly evasive attack surface.

Read Original Article →
Article Thumbnail

From Microservices to Agents: the Next Evolution of Distributed Systems

The shift toward artificial intelligence agents marks a significant evolution in software architecture, moving away from traditional microservices. While microservices focused on breaking down complex applications into smaller, predictable parts with clear ownership boundaries, agentic systems focus on distributing decision-making. Instead of following pre-programmed, step-by-step logic, these new AI agents determine their actions dynamically. They analyze the context and their goals in real-time to decide which tools to use and how to sequence their reasoning. This means execution paths are no longer entirely determined during the design phase but adapt as the system runs. While this makes systems more capable of handling complex or vague situations, it introduces new challenges in reliability. The quality of a system's decisions becomes just as critical as its speed or availability. When these systems fail, they often suffer from silent drops in reasoning quality rather than crashing entirely. To manage this effectively, systems need built-in boundaries for the agents, continuous evaluation loops, and reliable fallback mechanisms.

Read Original Article →
Article Thumbnail

How hybrid infrastructure is making quantum commercially actionable today

The quantum computing industry is currently in a critical "prepare for quantum" phase. While fault-tolerant quantum hardware is still developing, organizations cannot afford to wait passively. Integrating geographically isolated quantum processors with enterprise IT through secure, low-latency interconnection is an infrastructure challenge that must be addressed today. This preparation is essential for sectors like life sciences, where delays in drug discovery can be incredibly costly. A prime example is Qubit Pharmaceuticals, which utilizes a hybrid approach with its ATLAS platform. This four-layer system combines high-fidelity physics simulations, a synthetic quantum chemistry data engine, a specialized AI foundation model, and an emulator that simulates up to 40 qubits on classical hardware. By leveraging secure interconnection fabrics provided by partners like Equinix, companies can seamlessly link classical computing, HPC, AI, and early quantum capabilities. Building this hybrid infrastructure now allows organizations to experiment, gain operational familiarity, and seamlessly scale their capabilities as quantum hardware matures, ensuring they are ready to harness quantum utility when it arrives.

Read Original Article →

What Recent Cybersecurity Incidents Teach About the Duty to Mitigate Vendor and Service-Provider Risk

Recent cybersecurity incidents demonstrate that organizations face immense risks from third-party vendors and service providers, shifting the focus from internal defenses to external supply chains. Regulatory bodies increasingly expect companies to maintain a strict duty of vendor oversight, meaning organizations cannot simply outsource accountability for data protection. Real-world examples highlight this shift. The MOVEit software breach showed that companies can face severe legal and financial consequences from a vendor's vulnerability, regardless of their own internal controls. The Change Healthcare attack emphasized operational dependency risk, illustrating the disaster that occurs when a critical vendor goes offline. Furthermore, the PowerSchool lawsuit revealed that oversight must extend to subcontractors who have system access. To mitigate these threats, businesses must integrate vendor oversight into their core governance structure. This requires conducting thorough initial evaluations, negotiating clear contractual protections for incident response, and continuously monitoring vendor security practices. Treating vendor management as an ongoing legal and operational responsibility is essential for maintaining resilience when external failures cause major internal disruptions.

Read Original Article →
Article Thumbnail

The CIO’s new recovery problem: Knowing what ‘good’ looks like

Disaster recovery used to focus primarily on how quickly a business could restore its systems and resume normal operations. Today, modern technology environments are far more complex, spanning cloud platforms, software-as-a-service applications, and constantly changing identities. This complexity sprawl presents a new challenge for technology leaders: figuring out what a healthy system actually looks like before attempting to restore it. Simply bringing a system back online is no longer enough if you cannot guarantee it is secure and trustworthy. To build true resilience, organizations must maintain an accurate inventory and clear dependency mapping while the environment is still functioning properly. Testing a recovery plan must also evolve beyond verifying backups. It should evaluate whether the team can make critical decisions under pressure, understand shifting dependencies, and confirm that the restored environment is safe to use. While speed remains a priority during a crisis, restoring systems without confidence introduces severe risk. Technology leaders must establish a clear definition of a trusted state before an incident ever occurs.

Read Original Article →
Article Thumbnail

When Business Continuity Plans Depend on One Person Knowing What to Do

Even when business continuity plans are well-documented and regularly tested, they often contain a hidden vulnerability: relying too heavily on specific individuals. While organizations meticulously map out system and supply chain dependencies, they frequently overlook personnel dependencies. This reliance becomes clear during a crisis when teams instinctively turn to a single experienced manager, technical expert, or executive rather than following established procedures. The article suggests a straightforward way to expose this weakness during recovery exercises: deliberately remove key personnel from the scenario. If progress halts, deputies hesitate to make decisions, or critical workarounds suddenly become unavailable, the organization has identified a dangerous point of failure. These exercises often reveal that designated alternates lack the practical authority or historical knowledge to step in effectively when the primary decision-maker is absent. Recognizing these human dependencies allows organizations to correct them before a real emergency by formally documenting vital workarounds, transferring knowledge, and granting alternates the real authority they need to lead under pressure.

Read Original Article →
Article Thumbnail

Can AI stop good candidates from getting lost in the hiring pile?

Artificial intelligence is shifting from a basic background tool into an active partner for recruitment teams. As hiring volumes grow, qualified applicants are frequently overlooked simply because recruiters lack the time to review everyone. To solve this, companies are using artificial intelligence voice agents to handle the initial stages of screening. These agents can conduct first-round interviews at any time, answer standard questions about the role, and generate structured reports for the hiring team. This approach eliminates long waiting periods for applicants and ensures every application receives attention. However, technology cannot replace the core of recruitment. While artificial intelligence excels at repeatable tasks and gathering information, the final decision must remain human. Assessing an individual's motivations, understanding how they think, and building a genuine connection require human judgment. Furthermore, companies must be fully transparent when using these tools. Candidates need to know they are speaking with software, not a person. When applied responsibly, this technology prevents strong applicants from falling through the cracks while preserving the vital human element of hiring.

Read Original Article →

Gartner’s top tech trends for 2027 expand—and constrain—AI capabilities

Gartner recently outlined ten strategic technology trends for 2027, focusing on expanding artificial intelligence capabilities while establishing stricter controls. Over the next few years, businesses will move beyond text-based models toward systems designed for complex math, continuous voice reasoning, and physical world simulation for robotics. As these systems produce output faster than humans can review, the second phase emphasizes necessary limits. Organizations will need dedicated frameworks to manage machine identities, verify coding output, and provide specific business context to prevent rogue actions or compliance failures. Automated security patching will also become essential to close vulnerabilities quickly. Finally, looking further ahead, companies will aim to reduce reliance on specific cloud providers by adopting easily replaceable applications and independent technologies. A notable long-term shift involves biological computing, where lab-grown organic systems could eventually handle complex data tasks using far less energy than traditional silicon hardware. By planning across these three horizons, technology leaders can balance autonomous capabilities with the security required for steady operations.
Read Original Article →
Article Thumbnail

Coding Agents Moved the Bottleneck From Writing to Reviewing PRs

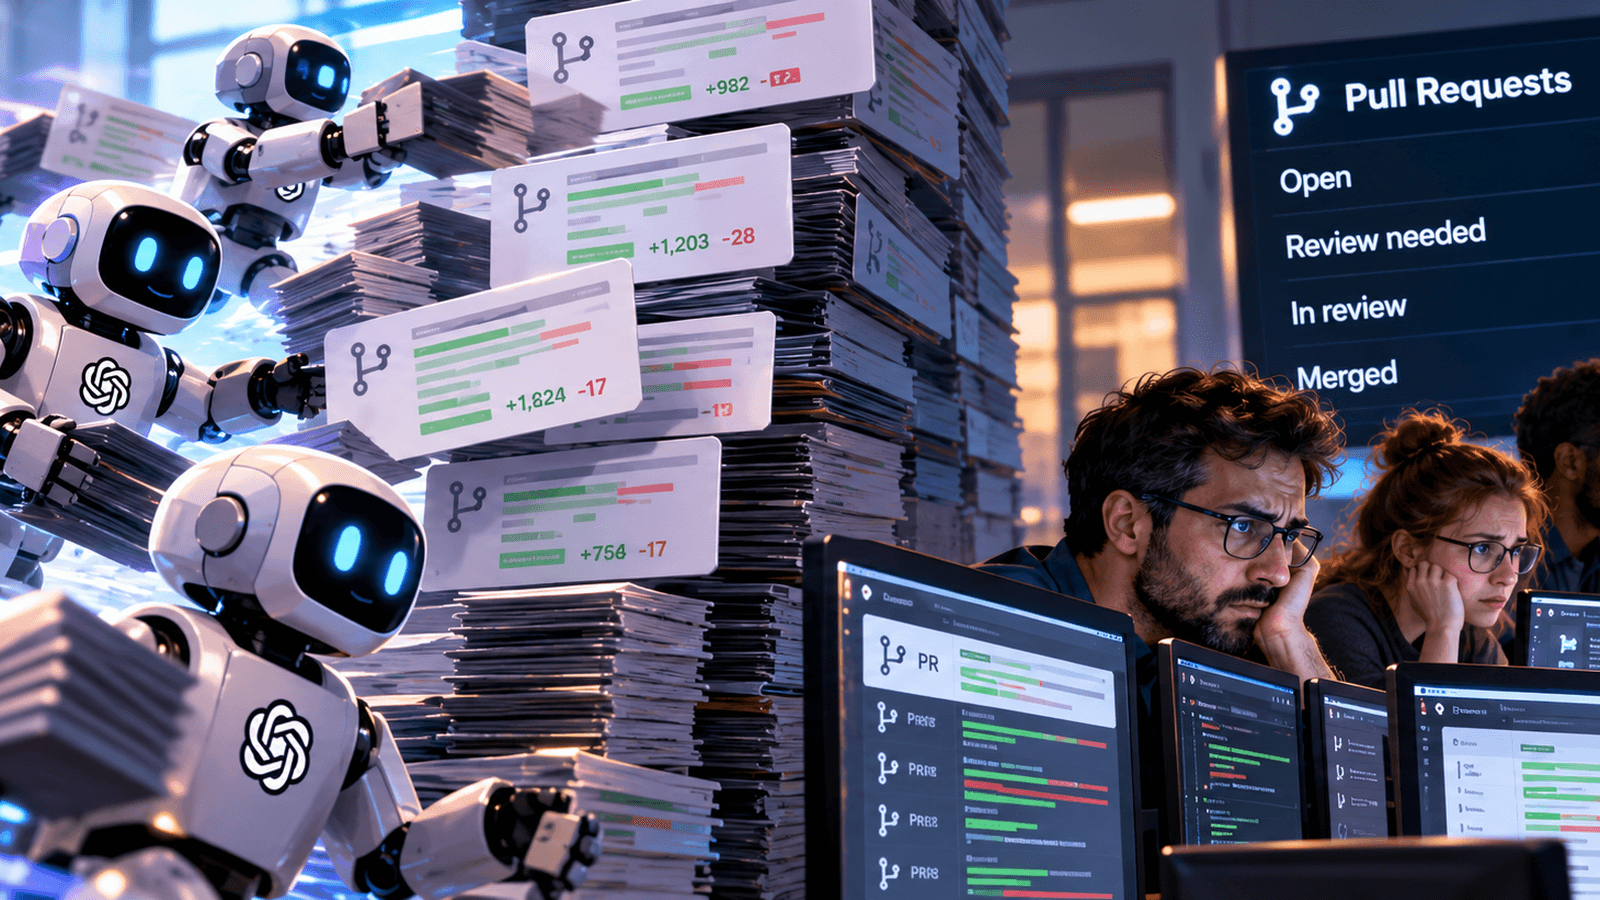
Artificial intelligence coding agents have significantly accelerated software development, but they have also shifted the primary bottleneck from writing code to reviewing it. Because these agents generate larger and more frequent pull requests, the volume of code needing review has outpaced the capacity of human engineers. This growing queue of unreviewed work often remains hidden because traditional productivity metrics focus on generation speed rather than review efficiency. Consequently, development teams face mounting quality debt. Overwhelmed reviewers might miss architectural flaws or security vulnerabilities, especially since AI-generated code typically looks clean and passes basic tests. To address this, organizations must recognize that hiring more reviewers is not a sustainable solution. Instead, they should implement dedicated AI review agents designed specifically to catch errors rather than generate new code. Additionally, capping the size of pull requests and tracking review metrics—such as wait times and review depth—can help maintain software quality without sacrificing the speed gained from AI development tools.

Read Original Article →
Article Thumbnail

Where Should a Transaction End? Designing Consistency Boundaries in Distributed Java Systems

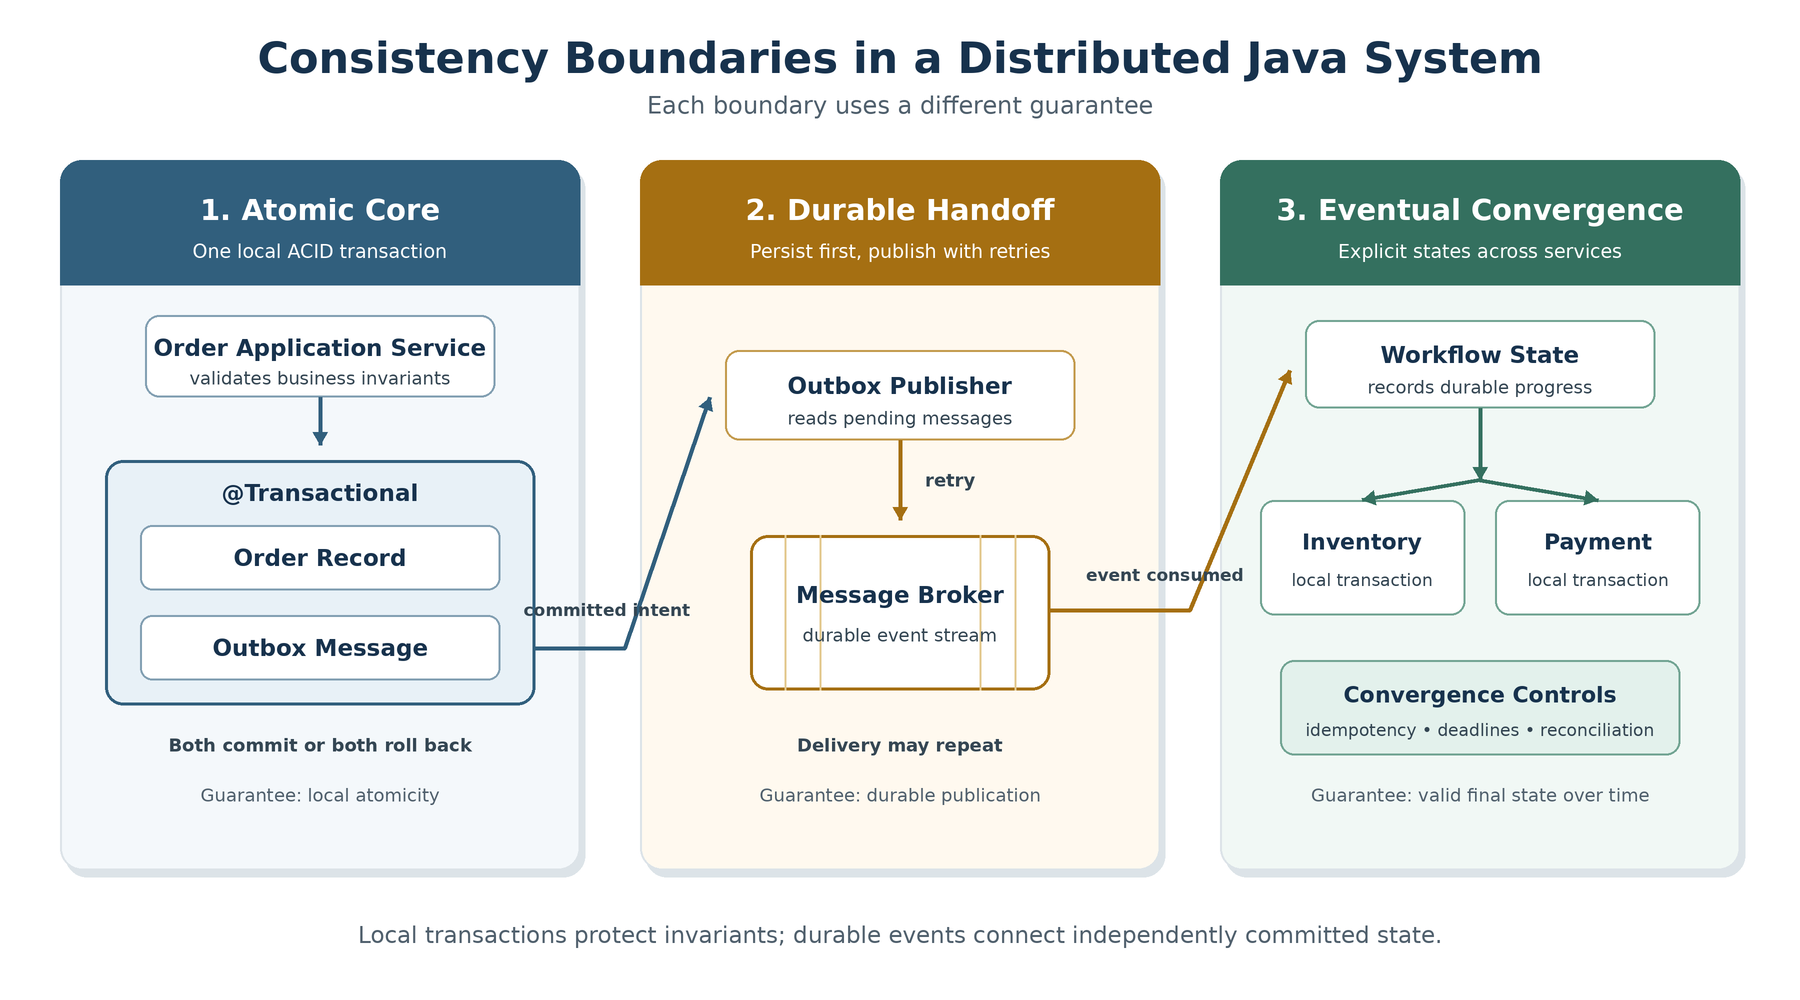
Designing distributed systems forces architects to decide exactly where a transaction begins and ends. Rather than splitting services first and worrying about data consistency later, the best approach starts with defining business invariants. These are the core rules that must always remain true together. The architecture should wrap its boundaries around these facts. When multiple pieces of data must change simultaneously to keep a rule intact, they belong in a single local transaction. Once that core state is secure, the system can use a durable handoff, like an outbox pattern, to safely communicate changes to other components. From there, eventual consistency can manage the broader workflow, but it must be an explicit process with clear recovery paths, not just a vague delay. Relying on synchronous call chains often creates hidden points of failure, so workflows should be modeled as durable states that can survive a crash. Ultimately, separating databases or breaking apart services is only valuable if it respects the underlying business rules that keep the entire system correct.

Read Original Article →

Daily Tech Digest - October 05, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale


Data Has No Passport: Why Global Privacy Governance Must Catch Up With AI

At the CruiseCon Privacy and AI 2026 event, Accenture privacy lead Adriana Antunes Winkler highlighted a growing challenge: while data moves globally and instantly, privacy regulations remain fragmented and bound by local jurisdictions. With around eighty percent of the world covered by varying data protection frameworks, companies often struggle to keep up. Winkler advised against building separate privacy programs for every new law, as this causes confusion and conflict. Instead, she recommended a strategy built on a common global foundation with specific local adjustments only where legally necessary. This prevents the burden of simply applying the strictest rules everywhere. Winkler emphasized that operational controls, not just written policies, are what actually protect privacy. These controls require clear ownership, testing, and proof of function. The rise of artificial intelligence complicates this further, as AI often infers new personal details rather than just storing collected information. She suggested focusing on the specific actions AI takes and the systems it accesses, treating it as a data map driven by actions. Ultimately, whether data crosses international borders, runs through AI systems, or eventually processes in orbital satellites, organizations must rely on a unified, adaptable governance system that manages common standards while addressing specific local requirements.


Crypto-Agility Distrust Readiness

When major internet authorities decide to stop trusting a flawed digital certificate, the resulting fallout can cripple the countless services relying on it. While technical bodies like browser developers excel at making the call to pull a failing root certificate, there is currently no coordinated national plan for what happens to the broader economy the morning after. Historically, isolated incidents have been contained, but the dual threats of rapidly advancing artificial intelligence and a forced timeline for quantum-safe encryption mean that widespread disruptions are becoming more likely. The blast radius of a sudden distrust event can vary wildly across different sectors, and responding effectively requires advance preparation rather than improvisation. To survive this accelerating risk, organizations must create reliable certificate inventories, designate clear response liaisons, and run tabletop exercises to test their readiness. On a larger scale, a designated national coordinator is urgently needed to connect technical decision-makers with the sectors facing the consequences. Ultimately, building true resilience requires organizations to eliminate single points of trust by adopting multiple issuing authorities and automating certificate lifecycles, ensuring they can pivot smoothly when a crisis hits instead of scrambling to rebuild.


Measuring AI With the Wrong Ruler

When evaluating artificial intelligence systems, getting caught up in grand labels distracts from what truly matters: reliability, cost, and fitness for the job. The technology industry often assumes that larger, more capable models are inherently better, but deploying a massive system for a straightforward task is wasteful and risky. It is very similar to dropping a race car engine into a riding lawnmower. Raw power without proper control or necessity only creates hazards. Instead of obsessing over raw machine intelligence, which mirrors our flawed fixation on human IQ scores, we should focus on building operational wisdom. This means designing tools that clearly understand context, respect their own boundaries, and know exactly when to seek human intervention. Historical missteps in automotive software, where complex features completely overwhelmed inadequate hardware, prove that mismatched computing power leads to frustrating failures for end users. To make better decisions, organizations need a practical measurement framework that strictly aligns system complexity with the actual criticality of the task. By focusing on calibrated computing, businesses can ensure they deploy software with verifiable competence. This thoughtful approach prioritizes restraint, safety, and hardware capacity over industry hype, ultimately resulting in technology that simply works properly for its intended daily purpose.


Should cybersecurity be nationalised?

The conversation around digital safety is gradually shifting from treating it as a private expense to recognizing it as a public good. While full government ownership is not currently under consideration, experts argue that the traditional model of individual corporate defense is no longer sustainable. Today, private companies are routinely expected to fend off sophisticated attacks from foreign nations, a task for which most lack the necessary resources. Small businesses are particularly vulnerable and they often become the weak link that exposes broader networks to risk. Because hardening the defenses of one company inherently protects the wider community, securing digital infrastructure shares clear parallels with public utilities like street lighting. This shared benefit naturally raises important questions regarding funding and accountability. The emerging consensus suggests a model where the state might fund security measures that are executed by private firms, ensuring broader protection without complete nationalization. As this policy debate unfolds, organizations must adapt by viewing their security practices not merely as an internal budget item, but as a core component of public trust and reputation. Moving forward, businesses should firmly anticipate stricter sector requirements and expect to demonstrate baseline security standards simply to operate within shared modern networks.


IT modernization: Still a make-or-break project for CIOs

IT modernization remains a vital, ongoing mission for CIOs, taking on renewed urgency as artificial intelligence reshapes the technology landscape. The rise of AI and natural language tools means that systems built just a few years ago, such as traditional reporting dashboards and specialized chatbot software, may already be obsolete. IT leaders are now approaching modernization and application rationalization with a business-first strategy, evaluating tools not by their age, but by the tangible value and flexibility they provide. Consolidating software limits wasteful spending, reduces unneeded complexity, and creates a clean data environment essential for advanced technologies. While moving to modern solutions can cut maintenance costs and limit security risks, CIOs face practical challenges, including upfront migration expenses, data extraction difficulties, and internal resistance to letting go of highly customized legacy systems. Some organizations are increasingly weighing whether to build internal tools using advanced coding assistants rather than paying long-term licensing fees for external software. Ultimately, IT modernization is no longer just about retiring old technology; it is a continuous process of aligning the company’s tech stack with fast-evolving business needs to clear a path for meaningful innovation and operational agility.


The Credential Layer Is Expanding Faster Than Security Teams Can See It

As software development accelerates, organizations face an enormous increase in the number of digital keys, passwords, and access tokens they must manage. These credentials now connect people, applications, and artificial intelligence tools to critical data. Because they are often scattered across cloud accounts, internal networks, messaging apps, and developer laptops, it is incredibly difficult for security teams to track them. Recent data shows a sharp rise in leaked secrets, particularly those tied to AI services, which have become a new frontier for access management. At the same time, cybercriminals are using specialized malware to target developer devices, aiming to steal the local access codes stored there. To protect against these threats, security teams cannot rely on outdated, periodic checks. They need constant, clear visibility into every credential across the organization. This means knowing exactly what access each key grants, who owns it, and whether it is still active. Only by building a complete and accurate inventory can teams effectively identify risks, remove exposed secrets, and stop future leaks from happening. Taking control of this expanding environment requires a calm, systematic approach focused on detection first, ensuring that organizations understand their vulnerabilities before attackers can find them.


Should the CISO role be split in two?

Over the past three decades, the chief information security officer role has expanded significantly from its strictly technical origins. Today, these professionals are tasked with broad, strategic responsibilities, including data privacy, regulatory compliance, artificial intelligence governance, and overall business risk management. As this heavy workload continues to grow and outpace available resources, some industry observers have debated whether the position should be divided into two distinct roles: one focused purely on technical defense and another dedicated to business risk and organizational resilience. However, leading experts argue clearly against splitting the job. Instead, they recommend confidently maintaining a single executive who holds ultimate accountability for the organization's cyber strategy and risk management. To help manage the immense daily operational demands, larger companies are increasingly relying on a dedicated deputy role, which also directly aids in succession planning. This balanced approach ensures that the primary security leader can successfully focus their energy on executive communication, financial planning, and aligning security measures with core business objectives. Ultimately, the position is maturing along a path very similar to that of the chief information officer. As the role becomes undeniably executive, these professionals must transition from being seen merely as technical experts to functioning as essential business partners.


Exploring AI Observability – Part 1: Why It Matters

Just a year ago, tracking how artificial intelligence operates was hardly a recognized technology field. Today, experts predict that by 2028, a large portion of organizations deploying these systems will rely on dedicated tools to oversee them. This shift is happening because the adoption of intelligent systems has grown much faster than our ability to properly govern them. Employees across companies are using a mix of approved and unapproved tools, while software teams are actively building language models directly into their applications. This rapid expansion creates an urgent need for visibility to understand exactly where these tools are running, how well they perform, what they cost, and if they actually deliver real value to the business. The conversation is no longer just about how fast we can build these systems, but rather whether we can run them reliably in real world settings. Because modern systems can sometimes produce varying results from the exact same input, errors can quickly add up. Proper oversight is necessary right from the development phase to trace interactions, identify failures, and improve accuracy. In production, this oversight ensures that the behavior of intelligent tools connects smoothly with overall application health, resilience, and a solid user experience.


The Platform Engineering Playbook for Production LLMs

According to a case study on an inventory accuracy platform, scaling large language models (LLMs) requires treating the AI stack as platform infrastructure rather than a mere application feature. The engineering team successfully reduced production hallucination rates from fifteen percent down to just 1.5 percent without altering the foundation model itself. They achieved this by implementing an automated retry loop to catch formatting and grounding errors on the fly, alongside an intent-validation gate that defaults to "unclassified" to prevent off-intent responses. Additionally, prompt management was shifted to a history-preserving registry rather than hardcoding instructions, allowing runtime updates with a clear audit trail to prevent silent behavioral breaks. The authors also highlight critical security and observability practices for enterprise AI. They strongly recommend enforcing tool authorization directly at the resource server with a strict default-deny policy, warning that relying solely on API gateways can expose tools due to a single orchestrator bug. Furthermore, since traditional application performance monitoring tools cannot detect semantic degradation or silent output drift, teams must proactively instrument hallucination rates and per-team token costs right at request ingress to avoid costly retrofitting later.


Three questions a hospital CISO should ask a healthcare fintech vendor

In a recent interview with Help Net Security, Drew McCombs, CTO and CISO at Cylerity, discusses his approach to balancing security with development in the healthcare fintech sector. McCombs ensures that security is integrated into every development sprint rather than treated as an afterthought. When conflicts arise, any issue affecting patient data or funds disbursement takes priority. He notes that while Cylerity is not a bank, it must satisfy the compliance expectations of its banking partners without violating HIPAA regulations. To achieve this, the company minimizes data sharing and uses custom identifiers to keep protected health information (PHI) completely separate from financial reporting. When discussing artificial intelligence, McCombs insists that AI models should only recommend or flag information, with a human always making the final decision to prevent errors from gradual model drift. For small medical practices, he emphasizes that turning on multi-factor authentication (MFA) for email is the cheapest and most effective security fix available. Finally, McCombs advises hospital CISOs to scrutinize fintech vendors by asking about their data subprocessors, their protocols for verifying fund destination changes, and their breach response plans, warning that a vendor claiming to be "HIPAA certified" is a major red flag since no such official certification exists.