Showing posts with label DigitalTransformation. Show all posts

Daily Tech Digest - September 05, 2026


Quote for the day:

"Success... seems to be connected with action. Successful people keep moving. They make mistakes, but they don't quit." -- Conrad Hilton

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Why is the Cloud Changing Again?

The rise of artificial intelligence is fundamentally changing how companies store and manage their data, moving the industry away from a one-size-fits-all public cloud model. Traditional cloud setups were excellent for standard web traffic and everyday software, acting like an efficient public transit system. However, artificial intelligence requires processing massive amounts of data at high speeds, which can cause severe delays and soaring costs on shared networks. To handle these heavy workloads, businesses are shifting toward a more specialized, decentralized approach. Additionally, because artificial intelligence learns from the information it processes, companies are increasingly concerned about the security and privacy of their sensitive data. This has driven a strong movement toward bringing data back home to private, local servers. Governments are also introducing stricter privacy laws, requiring companies to keep citizen data within their own national borders rather than storing it in global facilities. As a result, organizations are adopting a flexible strategy where they use public servers for everyday tasks, regional servers to comply with local regulations, and highly secure private servers for their most valuable information. This balanced method allows businesses to use advanced systems while maintaining strict control over their security, legal compliance, and digital assets.


Keeping OT security up to date is more than patching systems

Securing operational technology (OT) in industrial environments involves much more than applying simple software updates. As cyber threats against critical infrastructure like manufacturing and energy continue to rise, protecting these systems requires a fundamentally different approach than traditional IT security. While IT focuses primarily on protecting data, OT security must balance digital defense with real-world safety and continuous physical operations. Because large industrial systems often remain in active use for several decades, they cannot always be patched or upgraded as easily as typical office computers. Rather than relying solely on specialized technical controls, organizations must deeply understand their operational dependencies and gain completely clear visibility into their connected assets and third-party vendor access. Major disruptions frequently stem from basic weaknesses, such as poor network segmentation or compromised IT environments that spill over into industrial operations, rather than highly complex, sophisticated attacks. To build truly effective defenses, companies need strong internal governance that clearly defines responsibilities across engineering, operations, and security teams. Ultimately, organizations should view OT security not just as a narrow technical issue, but as a critical element of overall business resilience. By combining standard cybersecurity practices with deep industrial expertise, companies can protect their vital operations while successfully adapting to ever-evolving security risks.


Your R&D doesn’t need to be flashy

Software development teams often feel pressure to build flashy, highly marketable features to impress users. However, the most valuable research and development work usually happens entirely behind the scenes. While a brand-new interface button might make for a great product demonstration, real long-term user satisfaction depends on foundational elements like speed, reliability, and security. When software performs exactly as expected without delays or glitches, users can focus entirely on their work rather than fighting with the tool itself. Modern professionals, such as architects or engineers, rely on software to handle increasingly complex and automated tasks. If an application fails to execute a command accurately or compromises sensitive project data, the user's trust is instantly broken, and the financial consequences can be severe. This is why development teams must prioritize secure, reliable environments over cosmetic upgrades. By analyzing how people actually use the product, developers can identify the invisible improvements that truly matter, such as open standards that allow seamless collaboration across different platforms. Ultimately, the best software acts as a quiet partner, anticipating a user's needs and handling repetitive work so they can stay immersed in their creative flow.


Querying and Performing Transactions Across Multiple Database Schemas in a Modular Monolith

In a modular monolith, assigning a dedicated database schema to each module establishes strong boundaries but introduces significant challenges for querying data and managing transactions. Because direct database access between modules violates these boundaries, traditional approaches like joining tables across different schemas or relying on single database transactions are no longer viable. To solve querying issues, developers can use several strategies. The simplest method involves direct API calls, where modules communicate through public interfaces, ensuring strict boundaries despite potential performance compromises. For scenarios requiring faster reads, teams can rely on domain events to duplicate and denormalize data across modules, though this requires managing eventual consistency. Alternatively, database views allow developers to join tables across schemas at the database level, which is particularly effective for reporting purposes. Another strong option is the Backend for Frontend pattern, where a dedicated service aggregates data from multiple modules before sending it to the user. Handling transactions across multiple schemas requires a shift away from traditional methods. Instead of relying on a single commit, systems must utilize event driven architectures and patterns like sagas. While this approach ensures loose coupling, scalability, and resilience, it also introduces complexity by requiring compensating transactions and careful error handling to maintain data consistency.


Gmail labels: Your secret weapon against inbox chaos

Gmail labels provide a powerful and flexible alternative to traditional email folders, acting more like customizable tags that allow multiple categories to be applied to a single message. By mastering these tools, users can significantly reduce inbox chaos and streamline their daily communication. A great starting point is creating and color-coding various labels, then grouping them into parent and sublabel hierarchies to maintain a consistently neat sidebar. To save time during everyday tasks, you can proactively apply these labels while composing a new email or assign them simultaneously while archiving a read message. Labels also dramatically improve your ability to find old information; typing specific label operators directly into the search bar instantly narrows down vast results. Furthermore, users can fully automate their workflow by setting up custom Gmail filters. These filters automatically apply specific labels to incoming messages based on criteria like the sender's address or specific subject line keywords. This intelligent automation allows urgent emails to stand out immediately while quietly routing less critical messages away from your main inbox view. Finally, labels can be connected to custom notification settings, ensuring you only receive alerts for the messages that truly matter. By adopting these simple strategies, anyone can transform an overwhelming inbox into a highly organized system.


When cyber capability becomes abundant: Rethinking government cyber resilience

As artificial intelligence rapidly evolves, it is fundamentally changing the economics of cybersecurity for government agencies. Historically, sophisticated cyber operations required scarce, expensive human expertise. Today, AI has significantly reduced these costs, making powerful cyber capabilities widely available to both attackers and defenders. This shift creates unprecedented challenges for government agencies, which protect critical infrastructure and systems essential to national security, public health, and emergency response. Because attackers can now discover and exploit vulnerabilities faster than organizations can fix them, government security leaders are losing confidence in traditional defensive strategies. To adapt to this new reality, governments must rethink their approach to cyber resilience across operational and institutional levels. Operationally, agencies need to move away from trying to fix every single technical flaw. Instead, they must prioritize risks based on their potential impact on public missions. A moderate vulnerability in an emergency response system matters far more than a severe flaw in a low impact network. By translating technical data into real world operational context, governments can better focus their limited resources on protecting what truly matters. Ultimately, success requires agencies to rapidly reduce their exposure, contain breaches driven by artificial intelligence, and actively shape a safer overall cyber ecosystem.


Cyber resilience in the age of AI will be decided in the boardroom

As modern business innovation speeds up due to artificial intelligence, it also provides attackers with powerful new ways to disrupt operations. Companies have spent heavily on defensive software, but having more tools often creates confusing complexity rather than clear protection. Because automated threats move faster than ever, the true test of an organization is not whether it can prevent every single incident, but how well it handles a crisis when it happens. Cybersecurity is no longer just a technical issue meant for the information technology department; it is a fundamental business challenge that belongs in the boardroom. Company leaders must understand their critical digital dependencies and how a failure would impact revenue, reputation, and daily functioning. Security should be woven into every major business decision from the start, prioritizing clear processes over having the most complicated software. True resilience relies heavily on human behavior. An organization must build a culture where employees feel safe reporting mistakes, questioning unusual requests, and practicing response plans before an actual emergency occurs. Ultimately, survival during a digital attack depends on clear communication, decisive leadership, and the ability to keep essential services running smoothly and effectively, ensuring that trust and stability are maintained alongside technological growth.


How Differential Privacy Will Transform Enterprise Data Strategy

Differential privacy is quickly moving from a theoretical concept to a critical component of enterprise data strategy. While previous methods like encryption and de-identification have struggled to protect against re-identification as data volumes grow, differential privacy offers a mathematically proven way to guarantee that an individual's data cannot be reverse-engineered from broader analytical outputs. This technique is already being used successfully by major organizations, including the U.S. Census Bureau, Apple, Google, and Microsoft, and the market is projected to expand significantly by 2030. However, many business leaders mistakenly view this technology merely as a compliance tool. Its true value lies in unlocking data utility, allowing companies to safely share information across internal departments and with partners without exposing sensitive details. To succeed, organizations must understand that differential privacy is not a simple plug-and-play product, nor can it be retrofitted easily into existing pipelines. It requires a fundamental shift in how data is processed and governed. Experts advise companies to start with a single high-value use case, such as customer analytics, and prioritize building strong central governance before focusing on the underlying tooling. Adopting this approach now gives enterprises a significant competitive advantage in responsible data strategy.


What the AI Warning Letter Completely Missed
A recent warning from major technology companies highlights that artificial intelligence will soon make cyberattacks cheaper and more common, urging immediate action to strengthen defenses. While this threat is very real, the proposed solutions overlook the most critical component: the human beings required to do the work. The industry often focuses heavily on advanced tools and theoretical scenarios while ignoring the practical reality that defense depends entirely on skilled people. Every recommendation to improve security, whether it involves fixing weaknesses, reviewing code, or deploying new software, requires a trained operator. The gap in our current readiness is not a lack of software products, but a severe shortage of equipped personnel, especially within smaller organizations and local utilities. To truly prepare for emerging threats, companies must invest directly in the workers already managing these systems, teaching them how to secure their specific environments. Furthermore, technology providers should offer concrete, direct support rather than just access to software models. Defensive tools must be judged by how effectively a small, overworked team can actually use them during an emergency. Ultimately, technology alone will not secure our infrastructure against intelligent threats. True resilience requires betting on motivated, well trained people who are ready to handle the daily work of defense.


Why digital transformations still fail

Digital transformations continue to fail largely because companies let technology, heavily promoted by consulting firms, dictate their strategy rather than focusing on actual business needs. Consultants have consistently sold identical, prepackaged systems to maximize their own profits, completely ignoring the unique requirements of each organization. This approach has resulted in massive budget overruns, delayed timelines, and overly complex systems that fail to perform as promised. Instead of redesigning their processes, companies simply moved their existing problems onto expensive cloud platforms, increasing their costs without gaining any real benefits. Now, as the industry shifts its focus toward artificial intelligence, businesses are repeating these exact same mistakes. Organizations are rushing to add artificial intelligence to everything without a clear reason, while placing unqualified staff into critical design roles. To succeed moving forward, businesses must adopt a much simpler approach. They need to stop overspending on unnecessary computing power and invest heavily in proper foundational training for their internal teams. Ultimately, technology exists solely to serve the business. Any successful change must begin by identifying clear business requirements and working backward to find the most practical, cost-effective solution, rather than blindly purchasing the most complicated or trendy new software option available today.

Daily Tech Digest - August 18, 2026


Quote for the day:

"Be miserable. Or motivate yourself. Whatever has to be done, it's always your choice." -- Wayne Dyer

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI can find zero-days but still can’t reliably write secure code

While artificial intelligence has become highly capable at discovering new vulnerabilities and writing exploits, it still struggles significantly with writing secure code and fixing security flaws. Recent studies highlight a growing imbalance between these offensive and defensive capabilities, showing that a large portion of code generated by artificial intelligence contains known vulnerabilities. This gap poses a serious risk for organizations using these tools to speed up software development, as the models often introduce technical debt and security exposure alongside faster delivery times. Experts note that writing secure code is inherently difficult, and language models lack the necessary organizational context, such as specific architectures, threat models, and internal policies, to do it reliably on their own. Simply improving training data is unlikely to solve this problem entirely. Instead, the software industry is shifting toward using specialized environments that embed strict security checks, context, and validation workflows directly into the development process. These systems provide the necessary constraints to produce safer software. However, automated systems cannot replace human judgment. Traditional testing tools and human oversight remain absolutely essential. Ultimately, experienced human developers must maintain control over reviewing and approving all code changes to ensure the final product is genuinely secure and robust.


A New Paradigm for IT Budgeting

Traditional annual IT budgeting often frustrates organizations because it relies on rigid planning cycles that stifle flexibility and waste valuable time. When companies prioritize individual projects and force them to compete above a funding threshold, they unintentionally encourage padded estimates and a rush to spend remaining funds at the end of the year. This conventional approach measures success by how well teams stick to initial estimates rather than the actual value they deliver, leaving IT departments struggling to keep pace with changing business needs. To resolve these issues, organizations can shift toward an envelope-based portfolio model. Instead of evaluating dozens of isolated projects, leadership allocates funds into broader strategic envelopes, such as improving operational efficiency or enhancing the customer experience. This method simplifies financial management by keeping the focus on outcomes rather than strict plan adherence. Leaders are given the authority to adjust priorities and reallocate resources as conditions change without restarting the entire budgeting process. Artificial intelligence can further assist by streamlining early-stage planning and identifying helpful patterns across initiatives. Ultimately, adopting this envelope approach transforms IT from a constrained, overworked service provider into a responsive partner focused on delivering meaningful results and adapting calmly to new challenges.


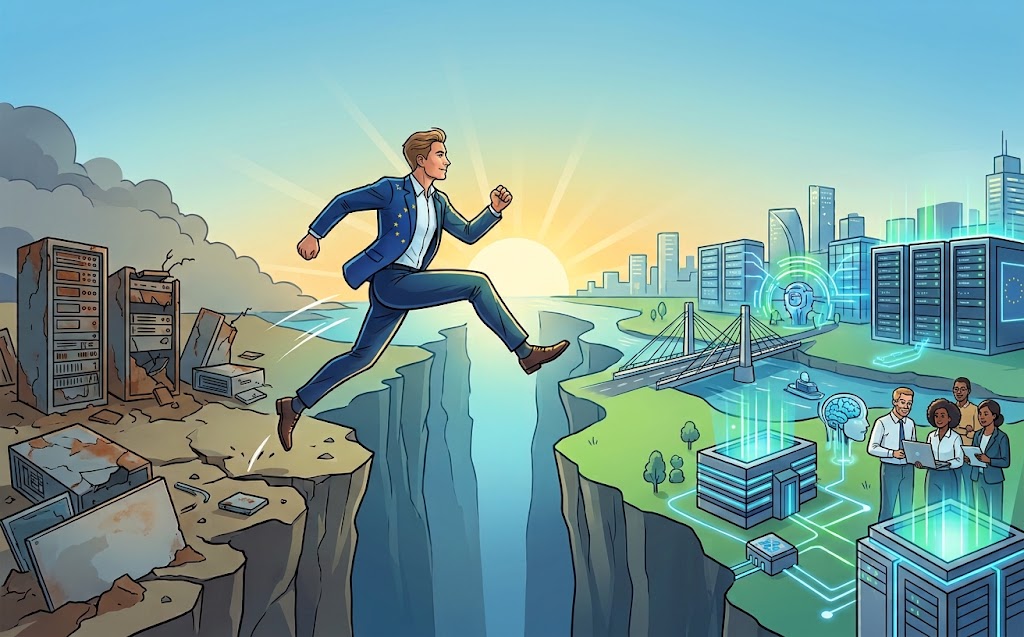
European sovereignty is an opportunity to take a giant leap forward

The conversation around European digital sovereignty is maturing beyond a simple desire to disconnect from American tech giants. Instead, it presents a rare chance to skip over outdated legacy systems and build modern data infrastructure from the ground up. However, achieving this requires more than just new hardware. Currently, many companies struggle because small innovation teams work in isolation while the broader workforce remains stuck on older applications. While European legislation has laid the groundwork for technological independence, the actual services and applications needed to run on these new platforms are still missing. Experts emphasize that successful modernization relies on unifying fragmented data across sectors, much like managing national public works through a single, coordinated system. This level of integration demands deep collaboration across companies rather than isolated efforts. Furthermore, the belief that Europe lacks the necessary talent is a misconception; many major tech platforms were built by small teams with European roots. The actual barriers holding the continent back are a lack of venture capital and stifling regulatory hurdles. To truly succeed, Europe must shift its focus from excessive regulation to creating strong commercial incentives, trusting that the local talent and technology are already fully equipped to manage the transition.


When AI Writes the Code, Specifications Need an Exit Strategy

In the era of AI-generated software, there is a growing temptation to view formal specifications as relics of the past. When artificial intelligence can churn out functional code in seconds, the urge to skip documentation and planning in favor of immediate execution is powerful. Yet, this convenience comes with a hidden cost: a loss of control over the resulting codebase. As the article argues, relying solely on AI to write code without a structured roadmap is a recipe for long-term technical debt. An "exit strategy" is essential. This means maintaining clear, human-readable specifications that act as a blueprint for the system, independent of the tools used to create it. If you cannot understand, modify, or debug your own software without the AI’s help, you have surrendered your agency. True engineering requires foresight, not just rapid output. Specifications provide the necessary guardrails, ensuring that even if an AI writes the initial implementation, the architecture remains grounded in human logic and understandable business requirements. Ultimately, an exit strategy is not about abandoning AI, but about ensuring that developers retain the authority and insight required to manage and evolve their systems effectively over time.


A better approach to generative UI

The article discusses how software developers should approach building dynamic interfaces in applications powered by artificial intelligence. It argues that teams must avoid the common mistake of letting models generate executable code, such as HTML or JavaScript, directly during a live user session. Although having an interface adapt instantly to a user's request sounds appealing, allowing an artificial intelligence to write raw code at run time compromises crucial security, testing, and architectural boundaries. It can lead to unpredictable behaviors and bypass the established rules for user permissions. Instead, the author advocates for a safer method called structured interface intent. With this strategy, the artificial intelligence does not invent the interface code. Rather, it simply chooses from a controlled, pre-defined menu of trusted interface blocks that the core application already knows how to handle. The model returns basic data indicating which visual elements are needed, and the application itself manages the actual display and execution of tasks. By relying on a verified registry of components rather than raw generated code, developers keep absolute control over the application's state, security protocols, and business rules, ensuring that the software system remains dependable, completely safe, and highly predictable while still offering a flexible user experience.


Balancing Sustainable Computing and Computing for Sustainability

The article discusses the critical need to balance two essential goals: making our technology greener and using technology to protect the environment. On one hand, sustainable computing focuses on reducing the heavy environmental toll of our digital lives. As computers become more powerful and data centers grow, they consume massive amounts of energy and produce significant electronic waste. To address this, the industry must develop hardware that uses less energy, improve how computers are manufactured, and create longer lasting devices. On the other hand, computing for sustainability involves using advanced digital tools to solve broad environmental challenges. We can use powerful algorithms and data analysis to optimize power grids, predict climate patterns, and manage natural resources more effectively. However, a conflict arises because the very tools needed to solve these global issues require immense computing power, which in turn increases energy use and carbon emissions. The piece argues that successfully navigating this tension requires a coordinated effort across different fields. Engineers, software developers, and policymakers must work together to ensure that the environmental benefits of new digital solutions outweigh the physical costs of running them. Ultimately, we must design technology that serves the planet without quietly adding to its burdens.


Why people, not technology, drive digital transformation

Akio Ueda argues that digital transformation is fundamentally about people rather than just implementing new tools. Often, companies deploy advanced systems like artificial intelligence or cloud computing but fail to see real, meaningful changes in their daily operations. This happens largely because employees lack the necessary skills to integrate these complex tools into their regular workflows. Ueda emphasizes that technical experts alone cannot drive transformation. True success requires individuals who understand business challenges, focus on customer needs, and can clearly guide organizational change. He points out that a strong talent strategy must align seamlessly with a company's core business goals and be supported by consistent policies across all departments. Training programs alone are not enough; employees must apply their learning practically to bridge the gap between knowing and doing. Furthermore, recognizing and rewarding these efforts through internal and external praise is a practical way to build motivation and confidence. Ultimately, a chief information officer's role is shifting from merely managing technology to developing the people who will execute the strategy. Investing in human potential is the most reliable way to ensure that technological advancements translate into lasting business value, empowering an organization to adapt, grow, and thrive in a constantly changing modern landscape.


How To Build Executive Presence From The Inside Out

True executive presence is not about having a prestigious job title or projecting a polished, charismatic image. Instead, it relies entirely on inner traits and deliberate daily behaviors that build lasting trust and credibility. To develop this presence, you must focus on how you interact with others and manage yourself during stressful situations. It begins with emotional intelligence and the ability to read a room, ensuring you set a calm emotional tone rather than simply reacting to pressure. Small actions like offering a genuine smile and actively listening before you speak go a long way in making your peers feel valued and understood. Furthermore, speaking up with courage to say the hard things, rather than feigning absolute certainty, shows authentic leadership. Another effective but often ignored habit is intentionally pausing before you respond to difficult questions. Taking a brief moment to breathe signals capacity and thoughtfulness rather than anxiety or haste. Real presence also requires you to be fully engaged in every interaction, putting away distractions to focus on the people in front of you. Ultimately, your character, competence, and conduct must align consistently over time. When your actions match your words day after day, you develop a grounded leadership identity that people respect and follow.


Why Some Companies Are Pulling Back on AI Coding

Although artificial intelligence promised to change software development by drastically speeding up code generation, some organizations are now reconsidering their heavy reliance on these tools. The initial enthusiasm is giving way to a more measured approach as engineering teams encounter practical challenges with automated coding. One major concern is the degradation of code review cultures; because AI-generated code often looks correct at first glance, developers may review it less rigorously, allowing subtle bugs and security vulnerabilities to slip into production. Furthermore, companies are noticing structural issues within their software. While these tools can write functional snippets, they often lack the broad context needed to adhere to a project's long-term design patterns, leading to fragmented systems and rising technical debt over time. Data privacy remains another critical issue, as sharing proprietary business logic or sensitive customer information with external language models poses significant security and compliance risks. Finally, leaders are observing a decline in deep system knowledge among their engineering teams. When developers rely too heavily on automated prompts rather than grappling with complex logic themselves, institutional knowledge suffers. Consequently, rather than abandoning these tools entirely, many businesses are pulling back to establish stricter guidelines, ensuring that human judgment and solid engineering practices remain central to their operations.


Why Traditional Data Governance Cannot Secure Business Decisions

Traditional data governance focuses on describing and organizing information through tools like glossaries, catalogs, and data lineage. While these methods help organizations understand what their data means and where it comes from, they often fail to connect that information to the actual business decisions it supports. Organizations do not govern data just to create better catalogs; they do so to ensure they can confidently grant, deny, fund, or authorize actions. The main limitation of traditional models is that they document data without showing how it secures critical operations. To fix this gap, organizations must adopt a decision focused approach. This means treating important business decisions as the central framework for governance. By separating business choices from data management tasks and linking them together, companies can create a clear chain of trust. This chain connects a requirement to a specific decision, the rules that guide it, the data used, the controls that verify it, and the evidence that proves it was handled correctly. Moving forward, governance must go beyond simply adding more descriptions to a database. It requires building a complete system where rules, controls, and error corrections are directly tied to their business consequences. This approach ensures organizations can clearly explain, defend, and trust their decisions.

Daily Tech Digest - April 06, 2026


Quote for the day:

“Victory has a hundred fathers and defeat is an orphan." -- John F. Kennedy


🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


OCSF explained: The shared data language security teams have been missing

The Open Cybersecurity Schema Framework (OCSF) is a transformative open-source initiative designed to standardize how security data is represented across the industry. Traditionally, security operations centers have struggled with a "normalization tax," spending excessive time translating disparate data formats from various vendors into a unified view. OCSF solves this by providing a vendor-neutral schema that allows products from different providers to share telemetry, events, and findings seamlessly. Launched in 2022 by industry giants like AWS and Splunk, the framework has rapidly expanded to include over 200 organizations and now operates under the Linux Foundation. Beyond basic logging, OCSF is evolving to meet the demands of the AI era, incorporating specific updates to track model behaviors, agentic tool calls, and token usage. This standardization is critical as enterprises deploy complex AI systems that generate novel forms of telemetry across product boundaries. By removing the friction of data translation, OCSF enables faster threat detection and more efficient correlation across identity, cloud, and endpoint security layers. Ultimately, it shifts the focus from managing data infrastructure to performing high-level analytics, providing the shared language necessary for modern cybersecurity teams to defend against increasingly sophisticated and automated threats.


What it takes to step into a C-level technology role

Transitioning into a C-level technology role like CIO or CTO requires a fundamental shift from managing specific digital transformation initiatives to taking full accountability for an entire organization’s strategy and operational stability. According to the article, aspiring executives must move beyond being technical experts to becoming influential leaders who can navigate ambiguity and complexity. Utilizing the 70-20-10 learning model is essential; seventy percent of growth should come from high-impact on-the-job experiences, such as collaborating with sales to build business acumen or leading workshops for executive boards. Twenty percent involves social learning through professional networking and peer communities, which are vital for filtering AI hype and developing realistic, data-driven visions. The final ten percent encompasses formal education, including specialized executive courses and continuous reading to stay ahead of rapid innovation. Modern C-suite leaders must prioritize data literacy and AI governance while mastering the ability to listen and pivot when market conditions shift. However, candidates should be prepared for the significant stress associated with these roles, as nearly half of current CIOs report extreme pressure. Ultimately, success at the executive level depends on the capacity to translate complex technical strategies into sustained business value and resilient digital operating models.


Recovery readiness, not backup strategy: The future of enterprise cybersecurity

The article argues that traditional backup strategies are no longer sufficient in the face of modern cyber threats, necessitating a shift toward "recovery readiness" as a strategic priority. With the global average cost of data breaches reaching $4.88 million and attackers dwelling in networks for months, the landscape has evolved; notably, 93% of ransomware attacks now specifically target backup repositories. This trend renders the simple act of storing data inadequate if the ability to restore it is compromised. Organizations must move beyond the question of whether they possess backups and instead evaluate their capacity to recover effectively under coordinated adversarial pressure. Achieving genuine resilience requires treating backup infrastructure as a critical strategic asset rather than an afterthought, utilizing advanced protections like immutable storage, network isolation, and zero-trust architectures to limit blast radii. Furthermore, the piece emphasizes the necessity of regular, high-stakes cyber drills to expose operational gaps and ensure that recovery timelines are realistic. By embedding resilience directly into their architectural design and organizational culture, enterprises can significantly reduce recovery times and costs. Ultimately, the future of cybersecurity lies in incident readiness and tested, enterprise-scale recovery capabilities that allow businesses to navigate sophisticated threats with confidence and credibility.


Getting SOCs Back On The Front Foot With Paranoid Posture Management

The modern security operations center (SOC) faces overwhelming challenges, with mean breach detection times exceeding eight months due to alert fatigue, tool fragmentation, and a worsening cybersecurity skills shortage. In response, Merlin Gillespie introduces "paranoid posture management," a proactive strategy designed to reclaim the initiative from sophisticated threat actors who leverage AI and the cybercrime-as-a-service economy. This approach utilizes intelligent automation and advanced detection logic to correlate numerous low-severity alerts that might otherwise be ignored, effectively uncovering "living-off-the-land" techniques. By implementing nested automated playbooks—potentially running millions of actions daily—SOCs can automate up to 70% of their activity and capture ten times the volume of security events without increasing analyst burnout. This method prioritizes deep contextual enrichment, providing analysts with ready-to-use threat intelligence and entity mapping to accelerate decision-making. While technology is foundational, the human element remains critical; Gillespie suggests that many organizations may benefit from partnering with managed service providers who possess the specialized talent necessary to navigate this high-intensity monitoring environment. Ultimately, paranoid posture management transforms the SOC from a reactive state into a high-fidelity defense machine, ensuring that critical threats are identified and neutralized before they can cause catastrophic damage to the corporate network.


Cloud security turns to identity, access & sovereignty

In honor of World Cloud Security Day, industry experts from Docusign, BeyondTrust, and Saviynt have highlighted a fundamental shift in cybersecurity, where identity, data sovereignty, and access controls now define the modern cloud defense strategy. Moving away from traditional perimeter-based security, organisations are increasingly prioritising the management of digital identities to combat breaches caused by misconfigurations and excessive privileges. Docusign’s leadership emphasizes that trust is built through rigorous security standards and data residency, noting the importance of storing data onshore to meet Australian regulatory requirements. Meanwhile, BeyondTrust points out that identity has become the primary control plane and attack vector, where even simple credential misuse can lead to hyperscale breaches. A significant emerging challenge identified by Saviynt is the rise of non-human identities, such as AI agents, which often operate with high-level access but minimal oversight. To address these risks, experts advocate for a converged security approach that integrates identity governance across all users and machines. By implementing zero-trust principles and just-in-time access, businesses can better protect their sensitive assets in complex, distributed environments. Ultimately, cloud security is no longer just a technical function but a critical business priority essential for maintaining long-term digital trust and regulatory compliance.


The Hidden Cost of Siloed Data in Financial Services

The hidden cost of siloed data in financial services is a multifaceted issue that undermines operational efficiency, strategic decision-making, and customer relationships. When information is trapped in disconnected systems, institutions face significant "decision latency," where gathering and reconciling conflicting data sets stretches timelines and erodes executive confidence. These silos create "blind spots" that lead to missed revenue opportunities—such as failing to identify ideal candidates for cross-selling wealth management or loan products. Beyond internal friction, fragmented data poses serious regulatory and security risks; manual reconciliation increases the likelihood of reporting errors, while inconsistent security protocols across platforms leave vulnerabilities that hackers can exploit. Furthermore, the lack of a unified customer view results in impersonal or irrelevant marketing, damaging client trust. To remain competitive, financial institutions must shift from viewing data integration as a mere IT project to recognizing it as a strategic imperative. By adopting unified platforms and fostering a culture of transparency, firms can transform their data from a stagnant liability into a proactive asset, enabling real-time insights that drive innovation, ensure compliance, and enhance the overall customer journey.


$285 Million Drift Hack Traced to Six-Month DPRK Social Engineering Operation

On April 1, 2026, the Solana-based decentralized exchange Drift Protocol suffered a catastrophic exploit resulting in the theft of $285 million, an event now traced to a meticulously planned six-month social engineering operation by North Korean state-sponsored actors. Attributed with medium confidence to the group UNC4736—also known as Golden Chollima or AppleJeus—the campaign began in late 2025 when hackers posing as legitimate quantitative traders built rapport with Drift contributors at global industry conferences. These attackers established deep professional trust through months of technical dialogue before deploying two primary infection vectors: a malicious Microsoft Visual Studio Code repository weaponizing the "tasks.json" file and a fraudulent wallet app distributed via Apple’s TestFlight. The breach culminated in the compromise of administrative multisig keys, allowing the hackers to bypass security circuit breakers and utilize a fabricated asset called "CarbonVote Token" as collateral to drain protocol vaults in mere minutes. As the largest DeFi hack of 2026 and the second-largest in Solana's history, this incident underscores the evolving sophistication of the DPRK’s "deliberately fragmented" malware ecosystem, which increasingly leverages high-effort human interactions and weaponized developer tools to bypass traditional security perimeters and fund state military ambitions.


How CIOs Can Turn Enterprise Insight Into Action

In the evolving digital landscape, Chief Information Officers (CIOs) are increasingly tasked with transforming vast quantities of enterprise data into tangible business outcomes. The article explores how modern IT leaders bridge the gap between simple data collection and strategic execution. A primary challenge identified is the persistence of data silos, which often hinder a holistic view of the organization. To combat this, CIOs are adopting unified data platforms and leveraging advanced analytics and artificial intelligence to extract meaningful patterns. Beyond technical implementation, the focus is shifting toward fostering a data-driven culture where decision-making is democratized across all levels of the enterprise. By aligning IT initiatives with specific business goals, CIOs ensure that insights lead directly to improved operational efficiency and enhanced customer experiences. Furthermore, the integration of real-time processing allows companies to respond rapidly to market shifts. Ultimately, the role of the CIO has transitioned from a backend service provider to a central strategist who uses technology to catalyze growth. Success in this domain requires a balance of robust infrastructure, clear governance, and a commitment to continuous innovation to ensure that enterprise insights do not remain static but instead drive proactive, value-added actions.


CTEM for Financial Services: A Guide to Continuous Threat Exposure Management

Continuous Threat Exposure Management (CTEM) represents a vital shift for financial institutions navigating a landscape defined by sophisticated threats and strict regulations like DORA. Unlike traditional vulnerability management, which often focuses on reactive patching, CTEM provides a proactive, five-stage framework: scoping, discovery, prioritization, validation, and mobilization. By implementing this iterative process, banks and insurers can map their entire digital attack surface and focus limited resources on risks with the highest exploitability and business impact. Industry experts emphasize that CTEM moves beyond "check the box" compliance, offering fifty percent better visibility into exposures. Gartner predicts that organizations adopting this methodology will be three times less likely to suffer a breach by 2026, highlighting its effectiveness in protecting high-value data and maintaining customer trust. The final stage, mobilization, ensures that security and IT teams collaborate effectively to remediate actionable threats rather than chasing theoretical risks. Ultimately, CTEM enables financial leaders to transition from a static defense to a continuous, risk-based strategy. This evolution is essential for safeguarding payment platforms and trading systems in an environment where downtime is not an option and cyber threats evolve faster than traditional security cycles can manage.


Residential proxies make a mockery of IP-based defenses

The provided article highlights a significant shift in the cyber threat landscape as residential proxies increasingly undermine traditional IP-based security defenses. According to research from GreyNoise Intelligence, which analyzed four billion malicious sessions over a 90-day period, nearly 40% of all IPs targeting enterprise sensors are now residential. This trend weaponizes trusted consumer infrastructure, such as home broadband and mobile connections, making malicious activity nearly indistinguishable from legitimate traffic. Because these residential IPs are short-lived and rotate frequently—often appearing only once before disappearing—static IP reputation lists and geolocation-based filters are becoming largely ineffective. The traffic originates from compromised Windows systems and IoT devices, including routers and cameras, which are recruited into botnets without user knowledge. While these proxies are primarily used for scanning and reconnaissance—specifically targeting enterprise VPN gateways—they serve as a critical precursor to more direct exploitation from hosting environments. Experts describe this evolution as "nightmare fuel" for defenders, as it flips traditional perimeter security models on their head. Even following the disruption of major proxy networks like IPIDEA, attackers quickly adapt by shifting to datacenter infrastructure, proving that organizations must move beyond simple IP reputation to more sophisticated, behavior-based security strategies to remain protected.