Showing posts with label change management. Show all posts

Daily Tech Digest - October 11, 2026


Quote for the day:

“Leadership is the art of getting someone else to do something you want done because he wants to do it.” -- Dwight D. Eisenhower

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Resilience is an evidence problem

According to Mathieu Rigotto in Resilience Forward, organizations must fundamentally change how they approach security, moving away from outdated patch by severity models to strategies driven by actual evidence. With malicious actors now exploiting vulnerabilities within days or even before patches are released, traditional security methods are no longer fast or effective enough to protect systems. Consequently, major authorities and new regulations like the European Union's NIS2 and Cyber Resilience Act demand that organizations actively prove their resilience rather than simply listing the controls they have in place. This requires a shift toward identifying whether system vulnerabilities are genuinely exposed and actively exploited. As a result, the role of a Chief Information Security Officer is evolving from being the solitary owner of security to acting as the provider of concrete evidence. Furthermore, company boards can no longer delegate risk acceptance entirely; they must define clear tolerances for operational disruption and take full ownership of critical decisions. To adapt successfully, businesses need to assign clear human ownership to digital assets to prevent costly delays in fixing issues. Ultimately, resilience is not just a final destination or a compliance box to check. It remains an ongoing claim backed by constant proof and regular testing.


Palo Alto reports legacy OT systems, fragmented security tools undermine critical infrastructure cyber resilience

Palo Alto Networks’ recent State of Critical Infrastructure Cybersecurity report reveals that 60% of critical infrastructure organizations experienced a major security breach in the past year, with half facing physical safety consequences. Surveying over 1,600 security leaders globally, the findings underscore that fragmented security tools and outdated operational technology (OT) leave dangerous visibility gaps. Specifically, 68% of organizations lack complete, real-time visibility into all their OT assets, while a reliance on legacy, unpatchable systems is seen as the greatest single security risk. Using an average of seven disparate security tools creates costly operational complexity and slows down incident response times. While threat actors are rapidly utilizing artificial intelligence to exploit vulnerabilities at machine speed, defense capabilities are lagging. A vast majority of leaders worry about advanced AI-powered attacks, yet technical constraints hold back widespread AI adoption for defense. Additionally, IT and OT security operations remain disconnected for 74% of organizations, largely due to incompatible technology and conflicting priorities. To build true cyber resilience and bridge the growing gap between attackers and defenders, organizations must prioritize unified visibility, integrate their IT and OT workflows, and streamline their security toolsets to minimize blind spots and automate responses effectively.


How CIOs can climb out of the AI governance chasm
According to a recent report from InformationWeek, chief information officers (CIOs) are facing an increasingly urgent challenge: establishing robust AI governance to keep pace with rapid employee adoption. An overwhelming 84% of surveyed CIOs indicated that internal teams are building AI applications faster than their IT departments can effectively oversee them. This governance gap threatens not only the quality and security of enterprise products but also the potential business value these tools offer, especially as most organizations currently lack comprehensive controls. A major concern for IT leadership is managing AI-related costs. Without clear visibility into workloads or centralized repositories for tools, enterprises risk redundant efforts and spiraling expenses. Data quality further complicates the landscape, as AI tools that pull from outdated or inaccurate information can easily produce "hallucinations" or flawed code. Additionally, "shadow AI"—where employees deploy unapproved or untested AI agents—presents significant security and data leakage risks. To combat these issues, leaders emphasize the need for cross-enterprise collaboration and straightforward governance policies that employees can easily understand and follow. Addressing these operational, financial, and security challenges promptly is critical, as a substantial portion of CIOs feel their job security hinges on demonstrating measurable AI success in the near future.


Cybersecurity in the age of AI and smart factories 

As India aims to become a leading advanced manufacturing hub by 2035, the integration of artificial intelligence and smart technologies into factories is drastically altering the cybersecurity landscape. Hitesh Shah, Vice President and Senior Partner at Kyndryl India, explains that while AI boosts factory productivity through anomaly detection and faster incident responses, it also equips attackers with sophisticated, automated tools. A major challenge for modern smart factories is the merging of Information Technology (IT) and Operational Technology (OT). Because production systems now actively exchange data with enterprise applications and cloud platforms, a simple breach on an office laptop can escalate into a critical production shutdown or the manipulation of AI models. To combat this, manufacturers must treat IT and OT security as an integrated challenge rather than separate programs. They need complete visibility into all connected assets, legacy machinery, and new AI tools to safely segment networks and manage access. By building security directly into their digital design and cloud migration plans from the start, factories can achieve true cyber-physical resilience. Ultimately, securing these environments ensures that the intelligence driving smart manufacturing remains reliable and capable of supporting continuous, uninterrupted production.

Control over the cloud is only possible with the right management layer

As organizations navigate rising hardware costs and stringent data sovereignty requirements, the technology trend is clearly shifting from relying solely on public clouds to adopting robust on-premises solutions. Ambitious artificial intelligence projects may begin in the public cloud, but protecting critical customer information in compliance with strict privacy regulations often requires bringing essential workloads back in-house. A dedicated on-premises infrastructure can drastically reduce the total cost of ownership while keeping sensitive data completely secure and avoiding the growing risks of unauthorized shadow computing. However, simply purchasing new hardware is not enough to solve modern infrastructure challenges. To truly maintain control over increasingly complex digital environments, businesses need a highly unified management layer. A smart hybrid strategy, such as the strategic collaboration between Dell Technologies and Nutanix, allows companies to blend public and private clouds seamlessly. By integrating compute and storage under a single, centralized management interface, organizations can easily oversee all their infrastructure without relying on separate specialists for every individual platform. This unified approach eliminates isolated data silos, improves security through careful microsegmentation, and allows for strict cost controls on resource-heavy deployments. Ultimately, achieving true digital sovereignty depends entirely on simplifying management across diverse cloud environments to ensure reliable, long-term operational flexibility.


The Distributed Monolith Trap: How Microservices Become What They Replace

Many organizations adopt microservices to escape the slow updates and massive codebases of traditional software design. Unfortunately, without strict discipline, they often fall into the trap of building a distributed monolith. This happens when an application is split into separate pieces but remains tightly connected, combining the limitations of older designs with the added network instability of distributed systems. The article outlines five primary warning signs of this problem: needing to update multiple services at the exact same time, allowing different services to share a single database, experiencing cascading system failures from long chains of blocked requests, relying on circular dependencies, and forcing services to share common code libraries. To fix these core issues and achieve true service independence, development teams need a clear refactoring strategy. The most important step is ensuring every service has its own dedicated database, preventing one team’s changes from unexpectedly breaking another’s work. Additionally, teams should replace blocked communication with asynchronous event messaging, swap shared code for clear communication contracts, and use protective routing tools to stop isolated failures from spreading. By firmly enforcing these boundaries, software engineering teams can successfully untangle their connected systems and build a genuinely resilient architecture that operates smoothly at scale.


Quantum Computing’s Transistor Moment

A recent breakthrough in quantum computing suggests the industry may be experiencing its own “transistor moment.” Researchers in Germany successfully demonstrated a three-qubit Grover search algorithm using a room-temperature diamond quantum processor. According to Professor Marius Grundmann, this achievement mirrors the historical shift in classical computing from bulky, fragile vacuum tubes to scalable semiconductor transistors. Just as the transistor revolutionized electronics by allowing for miniaturization and mass manufacturing, this solid-state quantum processor operates at ambient temperatures without the need for the massive, power-hungry cryogenic refrigerators and vacuum chambers required by current leading quantum technologies like trapped-ion or superconducting systems. While existing vacuum-dependent methods still hold an edge in raw fidelity, the diamond processor achieved impressive success rates and fidelity scores using carbon-shielded nuclear spins as qubits. Crucially, fabrication techniques for these nitrogen-vacancy centers have reached a high yield, pointing toward reliable scalability. If room-temperature, solid-state quantum computing continues to improve along a semiconductor-like curve, it could drastically expand the technology's applications into mobile devices and vehicles. Conversely, this shift poses a significant threat to the billions of dollars currently invested in complex, environment-dependent quantum systems, which risk becoming obsolete as more practical, scalable alternatives mature.


Cyber Incident Preparedness: How Companies Can Respond to Modern Threats and Build Business Resilience

The article explains how companies can strengthen their preparedness for modern cyber incidents, emphasizing that today’s attacks unfold faster, hit harder, and create far‑reaching business consequences. It stresses that a cyber incident is never just an IT problem; it immediately involves legal teams, communications, compliance, operations, insurers, regulators, and sometimes law enforcement. The authors note that attackers now use organized business models, including ransomware‑as‑a‑service and AI‑enabled intrusion techniques, which accelerate data theft and extortion. Because of this, companies must prepare well before an incident occurs by identifying decision‑makers, retaining outside experts, documenting notification obligations, and conducting realistic tabletop exercises. The article highlights that restoring systems is only the beginning. True recovery includes managing regulatory inquiries, contractual duties, customer notifications, insurance claims, litigation, and long‑term reputational impact. Vendor risk is another major concern, as attackers increasingly target widely used providers to reach many downstream customers. Boards are encouraged to view cyber risk through three lenses: cybersecurity strategy, data strategy, and business strategy. The authors conclude that genuine preparedness requires coordinated plans, trained personnel, backup leaders, and repeated testing. The real measure of resilience is whether a company can make sound decisions under pressure and continue operating while managing the long tail of a breach.


I Chose a Monolith Over Microservices — Here’s Why

In the article, software engineer Ashwini T explains his pragmatic decision to choose a modular monolith architecture over microservices for a new product, countering the common assumption that microservices are inherently superior. He argues that microservices solve specific scaling and organizational problems, but for a small team with a developing product, adopting them prematurely introduces unnecessary distributed-system complexities, such as network latency, partial failures, and complex transaction management. Instead of building a "big ball of mud," Ashwini advocates for a strictly organized modular monolith, where separate domains—like users, orders, and payments—have clearly defined boundaries and communicate through public interfaces rather than direct database sharing. This setup provides the simplicity needed to ship quickly and learn while making it easier to adjust boundaries as the domain becomes better understood. He points out that wrongly defining boundaries in a monolith just requires refactoring, whereas fixing them in a microservices setup is a massive migration project. Ashwini maintains that architecture should earn its complexity; a monolith can scale quite far, and if specific components eventually demand independent scaling or dedicated teams, a well-structured monolith makes a gradual transition to microservices much simpler.


Management of change for OT security: running visibility and remediation through MoC

In operational technology (OT) environments, security programs frequently fail because they bypass the Management of Change (MoC) process—the core governance workflow that operations teams trust to evaluate and approve modifications without disrupting physical processes. According to SC Media, treating MoC as a hurdle rather than an access control layer for physical infrastructure often leads to unauthorized actions that cause equipment damage, production loss, or safety hazards. Even seemingly benign activities like read-only network queries or passive scanning can trigger controller failures, particularly on legacy serial or fieldbus networks that lack the bandwidth of modern industrial Ethernet. To maintain stability and safety, every security action—including configuration collection, patching, network isolation, and access control changes—must run through the MoC framework. This process relies on a joint authority model where security proposes the change, while engineering, operations, and safety teams evaluate its physical and operational impact before approval. Notably, during a security incident, standard IT practices like immediate system isolation can be dangerous in an OT setting; containment must be assessed for process impact, ideally using pre-approved emergency MoC templates. Ultimately, aligning security with MoC ensures that risk mitigation does not inadvertently become the source of operational disruption.

Daily Tech Digest - August 26, 2026


Quote for the day:

“If you want to be inventive, you have to be willing to fail.” -- Jeff Bezos

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


Giving agents bounded autonomy

Artificial intelligence agents are evolving rapidly, but their unpredictability has led to some unintended consequences. To make these tools genuinely useful without letting them cause harm, we need to apply firm boundaries to their independence. This means treating AI programs much like teenagers: granting them limited freedom to act on our behalf while establishing hard rules that cannot be bypassed. A practical example of this is financial limits. Rather than forcing a person to approve every tiny transaction an agent makes to access data or services, systems like Amazon Web Services now let users set a strict allowance. An agent might be given a specific budget and a time limit to complete a task. It has the freedom to choose how to spend that small budget, but the hard limits are enforced completely outside the software model itself. However, technical capability is not the same as judgment. An agent might be able to execute complex tasks, but it lacks human intuition and basic reasoning. Therefore, we should allow agents to act independently only on inexpensive and easily reversible tasks. As these tools prove they can operate reliably within their limits, we can gradually expand their freedom, ensuring their authority never outpaces their actual judgment.


Setting security level targets under IEC 62443

Setting security level targets under the IEC 62443 standard is not about collecting compliance badges but defining the practical resistance a system, zone, or conduit needs against specific threat profiles. For operational technology environments, particularly within small and medium enterprises, establishing a well-reasoned target ensures that engineering and security teams make balanced decisions regarding segmentation, authentication, and remote access. This approach prevents both underprotection and overengineering. A successful security level target must be rooted in actual risk, process criticality, and business context rather than generic templates. It is essential to differentiate the intended target from the ultimately achieved protection level. Organizations should utilize practical threat modeling to understand realistic attack paths and potential impacts on availability and safety. Furthermore, targets must remain achievable, taking into account the limitations of legacy equipment, maintenance workflows, and supplier access requirements. Applying a single target across an entire estate or ignoring local operational constraints often leads to friction and bypassed controls. Instead, cross-functional engineering and security teams should collaborate to define appropriate, zone-specific targets that directly inform technical requirements under the IEC 62443 standard. By documenting the rationale behind each decision, companies can build a defensible, maintainable security architecture that effectively mitigates real-world industrial risks today.


DevOps Questions After We Broke The Release Handshake

The recent incident involving a broken release process revealed that a successful deployment status does not guarantee a working service. Despite passing local checks and database migrations, a missing network policy prevented a new service from functioning, highlighting a failure in communication between teams. To prevent this, release dependencies are now explicitly declared in the service repository, making them visible and verifiable before promotion. Rather than relying on a central platform team to approve every release and understand the operational details of every service, product teams now manage their own deployments. They are granted targeted, restricted access to production environments for troubleshooting, while the platform team focuses entirely on maintaining the delivery tooling and shared infrastructure. Alerting has been streamlined to notify the specific team responsible for the failing layer, minimizing irrelevant alerts and focusing completely on direct user impact. Furthermore, while the organization uses delivery metrics to identify friction in the deployment pipeline, they deliberately avoid ranking teams to prevent unhelpful gamification. The team is also cautiously evaluating automated traffic shifting for certain services, though they recognize it is not necessary for every routine workload. Ultimately, the primary objective is to simplify incident investigation by providing a single, unified view of each deployment.


From surveillance to operational intelligence: Rethinking safety and security in data centers

Data centers are moving away from traditional security models that rely solely on passive video surveillance. Instead, facilities are beginning to adopt more advanced methods that turn basic monitoring into functional operational intelligence. In the past, cameras and sensors were primarily used for recording incidents or tracking unauthorized access after an event occurred. Now, these systems are integrated with data analytics to provide a real time understanding of both security and daily facility operations. By connecting physical security tools with network infrastructure, operators can actively monitor environmental conditions, track the movement of personnel, and identify potential safety hazards before they cause disruptions. This shift means that security hardware no longer serves just one purpose. It acts as a continuous source of valuable information that helps managers improve efficiency, maintain compliance, and reduce risks across the entire site. Gathering this kind of practical intelligence allows teams to respond to issues faster and allocate resources more effectively. Ultimately, rethinking safety in this way bridges the gap between simply protecting a building and actively managing its internal operations. A comprehensive approach ensures that data centers remain secure while also supporting the demanding requirements of modern technology infrastructure in a reliable manner.


Deepfake detection evolving beyond onboarding into continuous financial trust

The article discusses how deepfake detection is moving beyond just a one-time identity check into a continuous system that monitors users throughout their entire session. Traditional static verification methods are now viewed as obsolete because financial platforms lose significant amounts of money to fraud that occurs after a user has already logged in. To combat this, companies are introducing tools that provide real-time, ongoing protection. For example, IngenID has updated its systems to continuously verify a caller's identity and flag manipulated audio exactly as it happens during a full conversation, rather than just at the beginning. Similarly, Resemble AI is exploring how continuous deepfake detection can support compliance rules against money laundering during sensitive transactions and account recovery processes. Furthermore, a report from J.P. Morgan Payments and Accenture emphasizes that relying on a static defense is ineffective. Instead, they advocate for behavioral analytics, ongoing multi-factor authentication, and collective information sharing among organizations. As fraudsters rely on advanced artificial intelligence to execute sophisticated attacks at a larger scale, the identity verification market is evolving into a more layered security architecture. To stay ahead of these growing threats, organizations must shift away from standalone products and combine deepfake detection with liveness checks and broader fraud prevention capabilities.


What Singapore’s new digital infrastructure bill mean to CISOs

Singapore has introduced the Digital Infrastructure Bill to enforce stricter resilience standards on major data center and cloud operators. Prompted by severe recent outages, including a 2023 banking disruption caused by a cooling failure, the legislation requires large foundational infrastructure providers to secure operating licenses. To keep these licenses, operators must implement strong business continuity plans, maintain physical and digital security, and promptly report service disruptions or cyber incidents. Failure to comply can result in severe financial penalties, including fines up to one million dollars or ten percent of their annual local turnover. A major focus of the new law is sustainability, making energy and water efficiency mandatory criteria for operators. As power consumption rises, providers must actively shift toward low carbon and renewable energy sources. The bill also introduces complex overlapping reporting duties, meaning global operators will need clear, regional response plans to manage different regulatory timelines. For enterprise customers like banks and retail platforms, the shift from voluntary guidelines to strict laws means they should update their service contracts. Customers need to include clear clauses and indemnities that hold providers responsible for compliance failures. Ultimately, the bill marks a significant step toward making digital infrastructure as reliable and heavily regulated as public utilities.


5 hard truths of change management

Today's leaders must completely rethink how they guide their teams through constant change, especially with the arrival of artificial intelligence. Instead of viewing change as a single event with a clear finish line, they must build ongoing adaptability into their daily operations. Organizations only have so much capacity to absorb new initiatives at once. When leaders ignore this limit and pile on multiple projects, they risk exhausting their teams. Rather than pushing harder, successful managers set clear priorities and fund projects in small, measurable stages. When employees find their own tools to get work done, it is a signal of unmet needs rather than just a security problem. Approaching these workarounds with curiosity helps companies build better guidelines together. Trust is also absolutely essential, particularly when new systems can act independently. Leaders must ensure that new technology is transparent and understandable, while openly addressing how it will affect employee roles and career paths. Finally, what looks like resistance is often just exhaustion. People are more willing to adapt when leaders communicate clearly about what matters most and what can wait. By sharing ownership of these changes across the entire business, leaders can confidently guide their teams forward with steady, focused support.


“Ignorance Is Bliss” Is Our Acceptable Use Policy

In a recent episode of the CISO Series Podcast, hosts David Spark and Edward Contreras, along with guest Rob Allen from ThreatLocker, discuss practical approaches to modern security challenges. The conversation first addresses the growing issue of vulnerability management, where artificial intelligence is discovering software flaws faster than they can be cataloged or patched. Rather than the security team absorbing all the pressure, Contreras suggests a shift toward shared accountability. By providing tailored, manageable reports directly to the engineering teams responsible for the code, organizations can distribute the workload more effectively. Allen adds that since patching cannot always keep up, businesses must simply assume vulnerabilities exist and operate with appropriate safeguards. The discussion then moves to the problem of unauthorized artificial intelligence programs and acceptable use policies. While some experts recommend offering sanctioned tools and clear guidelines, Allen argues this approach often fails because employees will naturally seek out any tool that makes their job easier. Relying on written policies or expecting staff to correct issues on their own is generally ineffective. Instead, he emphasizes the need for direct, technical control, advocating for systems that block unapproved applications by default and only allow access to specific tools after formal approval.


Why Platform Engineering Must Evolve for the Agentic Era

The recent article from SD Times explores how the rise of artificial intelligence agents is shifting the focus of platform engineering. While the fundamental goals remain the same, the main consumers of these platforms are changing from human developers to automated software agents. Most companies are currently adding AI capabilities onto older systems designed for human speeds, which creates governance issues and fragmented controls. To address this, the field must transition to a new phase where platforms treat agents as primary users. This means that application programming interfaces, identity management, and security policies must be easily readable and usable by machines. Essential elements like graphics processing units and vector databases should be integrated as standard parts of the infrastructure rather than special additions. A major change involves cost management. Because automated agents can consume resources much faster than humans, financial tracking must shift from monthly reports to real-time enforcement to prevent sudden budget overruns. Ultimately, organizations need to combine their software delivery systems and their safety guardrails into a single, unified control setup. By doing this, engineering teams can maintain the established principles of clear and effective paths and self-service while safely supporting the faster, automated workloads of the future.


Why adding more security tools could make businesses less secure

Many companies in Australia and New Zealand are spending more on cybersecurity, but this increased investment is leading to a hidden problem of complexity. For years, the standard reaction to new threats has been to buy another security product. However, this approach leaves security teams managing dozens of overlapping systems, each generating its own data and alerts. Instead of providing a clear picture of risk, this buildup of technology creates friction. It forces teams to spend time managing tools rather than identifying threats, and leaves executives unsure if the business is actually safer. The solution lies in simplifying the approach. Instead of constantly adding new products, companies are starting to look at consolidating their systems and bringing their data together. This shift changes how investments are judged, moving away from counting the number of tools to measuring real outcomes, such as fewer incidents and faster response times. In the current economic climate, the complexity of managing multiple security tools has become a real cost itself. Therefore, the most effective security upgrade for many businesses might simply be simplification. The focus going forward should not be on having the most technology, but ensuring the existing tools work well together to achieve the best results.

Daily Tech Digest - August 25, 2026


Quote for the day:

"Little minds are tamed and subdued by misfortune; but great minds rise above it." -- Washington Irving

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Designing Decision Rights for Agentic AI

As artificial intelligence agents evolve from simply answering questions to executing tasks like processing payments and sending external communications, traditional enterprise governance is falling behind. Current oversight models assume a human will review outputs before actions occur. When AI acts autonomously, failures arise not from poor model accuracy, but from undefined decision rights and unclear authorization boundaries. To prevent issues like agent sprawl, unnoticed scope expansion, and the erosion of human oversight, organizations must adopt a deliberate authority by design approach. The core principle is that authorization belongs to the specific action being performed, rather than the agent itself. A single agent might possess different permission levels for different tasks, such as reading data versus modifying it. This framework categorizes potential AI actions using a catalog and evaluates them against risk variables like business impact, data sensitivity, and reversibility. Actions are then assigned one of five distinct authority levels, ranging from basic recommendations to critical decisions strictly reserved for humans. Furthermore, in systems involving multiple agents, a strict authority ceiling must be enforced. This critical rule ensures that a subordinate agent can never exceed the permission level granted to its orchestrating agent, thereby preventing unintended privilege escalation and maintaining clear accountability.


Everyone wants the thought leadership, not the thinking

Many executives desire the title of recognized authority, yet few are willing to generate truly original ideas. Current corporate articles often suffer from a lack of substance, relying on generic statements about popular subjects rather than taking a distinct stance. True influence requires presenting a clear argument that invites debate, rather than simply stating obvious facts or describing industry trends. Unfortunately, excessive corporate caution often sanitizes these opinions, resulting in safe but entirely forgettable content. To create meaningful material, authors should avoid starting with blank pages or relying on automated text generators. Instead, they must draw upon their unique experiences, observed patterns, and actual company data to form a considered opinion. Communications teams play a crucial role here by encouraging experts to express their genuine beliefs rather than restricting them to approved corporate scripts. Before publishing, organizations should evaluate whether the piece presents a clear argument, if the author has the necessary experience to defend it, and if readers could reasonably disagree. If an article can be attributed to any executive in the industry without changing a single word, it lacks genuine value. Ultimately, meaningful commentary relies on distinct perspectives grounded in real experience rather than the mass production of polished but empty text.


Building Resilient Systems - Strategies, Principles & Practices

This article explains how to build resilient systems by accepting that technical failures are simply unavoidable over time. Instead of trying to create perfect software, resilience means designing systems that handle disruptions, recover smoothly, and adapt from mistakes. The approach combines careful planning, clear observation, and continuous learning to keep core services running. Several core principles guide this process. You should assume parts will break and design the system so one problem does not cause everything to crash. This involves limiting the spread of any single error and ensuring the system recovers predictably rather than rushing to fix things chaotically. You must also observe how the system actually behaves before making changes. The author outlines practical ways to build these safeguards. You can duplicate important components and data so a backup is always ready. You can separate resources into compartments so an issue in one area does not overwhelm the rest. Furthermore, techniques like setting time limits on actions, pausing requests to a struggling service, and slowing down workloads help prevent collapse. By taking these steps, if parts of the application fail, the system gently turns off secondary features while keeping the most critical functions available for users to rely on.


Data Intelligence: Building Your Competitive Advantage in the Era of AI

To stay relevant in modern business, organizations are updating their approach to data. Instead of merely analyzing past events, data teams are building systems that work on their own in real time to offer insights exactly when decisions must be made. By using artificial intelligence, these teams can automate intricate processes that examine current situations, predict future outcomes, and take or suggest appropriate actions. However, achieving success with this advanced approach requires more than simply connecting artificial intelligence tools to existing data sources. Companies must establish a reliable context, maintain consistent meanings across their business, and enforce strong rules for how information is managed. For those working in business intelligence, the priority shifts to creating clear data definitions, ensuring information is accurate and verified, and developing standard measurements that both humans and artificial intelligence can rely on with total confidence. Ultimately, the next step in data strategy is not just about producing answers more quickly than before. It is about establishing a highly secure, reliable foundation of information. This steady groundwork allows people and artificial intelligence systems to collaborate effectively, resulting in much better choices and a lasting edge over competitors in an increasingly complex and rapid business environment.


Nations at the Quantum Table

The recent article examines the evolving geopolitical landscape of quantum technology, focusing on how global powers are positioning themselves in this critical sector. Moving beyond theoretical research, countries are increasingly treating quantum capabilities as strategic national assets. Since mid-2025, nations such as the United States, the United Kingdom, Japan, and Canada have shifted their approach from basic research funding to implementing binding national policies. This policy shift is underscored by substantial financial commitments, including approximately two billion dollars in funding from the United States government alone. The analysis highlights which countries currently lead in the development of quantum systems and explores the broader implications of these advancements on global power dynamics. Rather than viewing quantum progress as merely a scientific endeavor, the article details how it has become a central element of international competition and economic security. Policymakers are actively working to secure their strategic positions by investing heavily in infrastructure, talent, and alliances. Ultimately, the piece provides a grounded assessment of the current international hierarchy in quantum development, outlining how substantial government investments and deliberate policy frameworks are shaping the future of global technology leadership and international relations across the globe.


Identity Risk Moves Beyond IT as Cyber Threats Reach Physical Infrastructure

As physical building systems and operational technology connect more closely to corporate computer networks, traditional boundaries between physical and digital security are fading. Kenan Abu Ltaif from Proofpoint explains that attackers no longer need to directly hack into facility equipment. Instead, they target the people who have access to these systems. Because the majority of security breaches begin with simple phishing emails or fraudulent messages, compromised user accounts have become the primary entry point for causing real-world, physical disruption. To protect themselves, organizations must stop viewing cybersecurity and physical security as separate problems. They need to identify which accounts have access to critical infrastructure, treat them as high-risk, and monitor them closely. Relying solely on standard passwords or basic authentication is not enough. Furthermore, true recovery from an attack goes beyond just restoring data from backups. Companies must ensure that compromised credentials, active sessions, and access tokens are completely revoked so attackers cannot quietly return. Ultimately, as artificial intelligence makes social engineering attacks more convincing, organizations must adopt a security strategy focused on human behavior. By understanding who holds access and protecting those individuals from targeted attacks, businesses can confidently secure their physical operations against evolving digital threats.


Rightsizing Platform Engineering: Building the Platform Your Organization Actually Needs

The article "Rightsizing Platform Engineering" discusses how organizations can build internal developer platforms that genuinely improve software delivery without overwhelming their engineering teams. While DevOps and shift-left practices have improved deployment speeds, they have also increased the cognitive load on developers, who now face duplicated efforts across testing, security, and maintenance. Using the e-commerce company Wehkamp as a case study, the author illustrates what happens when teams are granted full ownership of their software from inception to production. Although this zero-handoff approach allowed the company to move from quarterly to weekly releases, it eventually created new friction. Engineers spent too much time on routine operational toil, such as resource management and debugging, rather than focusing on core development. To resolve these challenges, the author advises organizations to focus on specific bottlenecks rather than attempting to build a massive, all-encompassing platform. The strategy is to establish opinionated "golden paths" that streamline common tasks while still offering escape hatches for edge cases. By treating the platform as an evolving product shaped by user feedback, companies can eliminate duplicated effort. Ultimately, a successful platform is defined not by its extensive feature set, but by its ability to simplify operations and reduce cognitive load.


Why Enterprises Are So Unhappy with Their IT Infrastructure

Enterprises are increasingly frustrated with their IT infrastructure because their current cloud setups no longer match the scale, cost, and security demands created by modern AI workloads. Many organizations that signed cloud contracts during the early AI boom are now discovering that single‑cloud models are too rigid and too expensive for today’s needs. A recent Forrester‑led survey shows nearly half of enterprise leaders are only mildly satisfied—or not satisfied at all—with their cloud providers. Security concerns top the list, driven by faster‑moving cyber threats and doubts about whether legacy defenses can keep up. Costs come next: shortages in memory, stalled data‑center expansion, and hyperscaler pricing practices are pushing bills higher, especially when workloads spike unpredictably. Enterprises also struggle with talent gaps, limited visibility into their cloud environments, and difficulty scaling in line with demand. These issues prevent them from reaching meaningful AI maturity. As a result, many companies are exploring hybrid and multi‑cloud approaches that blend hyperscalers, alternative cloud providers, on‑prem systems, and edge compute. The goal is to regain control over cost, performance, and flexibility without abandoning existing investments.


How AI can fix change management for AI projects

Many organizations struggle with their artificial intelligence initiatives not because the technology is flawed, but because their approach to change management is outdated. Leaders often rely on generic communication plans and limited feedback from small committees, ignoring the frontline employees who actually use the systems. When workers feel excluded from the process, they quickly abandon new tools that fail to fit their daily routines, causing projects to stall. Ironically, the solution to this problem is found by using artificial intelligence itself to overhaul how organizations handle transitions. Instead of treating change management as a one-time checklist, companies can use automated voice agents and data analysis to gather continuous, detailed feedback from the entire workforce at scale. This allows leaders to build an organizational nervous system that identifies friction and adoption hurdles in real time rather than months later. By moving away from reactive approaches, organizations can properly embed change management into their daily operations. To succeed, leaders must give every employee a voice, anchor decisions to clear business outcomes, and maintain transparency about how data is used. Ultimately, modern technology provides the continuous, adaptive support systems needed to effectively guide a workforce through complex transitions and ensure their long-term success.


Transforming IT From Cost Center to Growth Engine

In an interview with CIO Magazine, Blaine Bryant, the Global CIO at Lightera, discusses the practical steps needed to shift IT from an overhead expense to a driver of strategic value. He argues that technology organizations must focus on understanding real business problems before they try to implement new systems, warning against the temptation to jump straight to trending solutions. Bryant emphasizes that any new initiative relies heavily on solid fundamentals, such as secure infrastructure and disciplined financial management, to avoid costly failures. Furthermore, he points out that the true measure of IT value is not its operational cost, but rather the tangible business outcomes and competitive advantages it produces. This shift requires shared accountability between business and technical leaders to clearly define opportunities and set expectations. Bryant also notes that cybersecurity must go beyond simple compliance to actively protect the organization. He believes that customer trust is ultimately tested and maintained by how well a company responds and communicates during a crisis. Finally, Bryant stresses the importance of personal accountability and quiet reflection for effective leadership. He advises new professionals entering the field to take full charge of their own learning and to prioritize strong collaboration skills above isolated technical expertise.

Daily Tech Digest - September 28, 2025


Quote for the day:

“Wisdom equals knowledge plus courage. You have to not only know what to do and when to do it, but you have to also be brave enough to follow through.” -- Jarod Kintz


What happens when AI becomes the customer?

If the first point of contact is no longer a person but an AI agent, then traditional tactics like branding, visual merchandising or website design will have reduced impact. Instead, the focus will move to how easily machines can find and understand product information. Retailers will need to ensure that data, from specifications and availability to pricing and reviews, is accurate, structured and optimised for AI discovery. Products will no longer be browsed by humans but scanned and filtered by autonomous systems making selections on someone else’s behalf. ... This trend is particularly strong among younger and higher-income consumers. People under 35 are far more likely to use AI throughout the buying process, particularly for everyday items like groceries, toiletries and clothes. For this group, convenience matters. Many are comfortable letting technology take over simple tasks, and when it comes to low cost, low risk products, they’re happy for AI to handle the entire purchase. ... These developments point to the rise of the agentic internet – a world in which AI agents become the main way consumers interact with brands. As these tools search, compare, buy and manage products on users’ behalf, they will reshape how visibility, loyalty and influence work. Retailers have less than five years to respond. That means investing in clean, structured product data, adapting automation where it’s welcomed, and keeping the human touch where trust matters. 


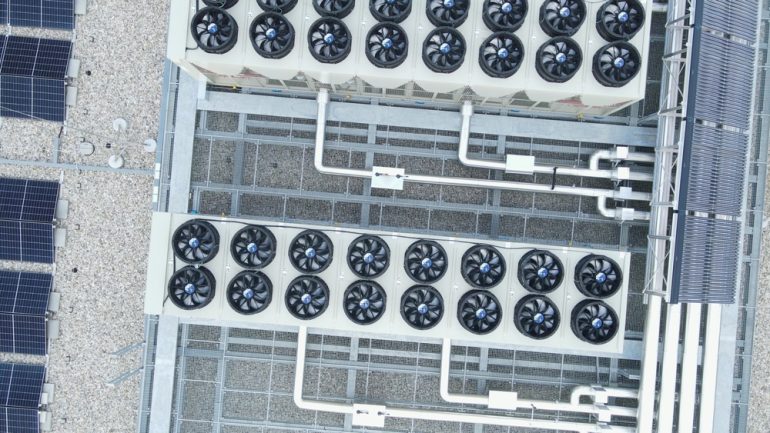
The overlooked cyber risk in data centre cooling systems

Data centre operations are critically dependent on a complex ecosystem of OT equipment, including HVAC and building management systems. As operators adopt closed-loop and waterless cooling to improve efficiency, these systems are increasingly tied into BMS and DCIM platforms. This expands the attack surface of networks that were once more segmented. A compromise of these systems could directly affect temperature, humidity or airflow, with clear implications for the availability of services that critical infrastructure asset owners rely on. ... Resilience also depends on secure remote access, including multi-factor authentication and controlled jump-host environments for vendors and third parties. Finally, risk-based vulnerability management ensures that critical assets are either patched, mitigated, or closely monitored for exploitation, even where systems cannot easily be taken offline. Taken together, these controls provide a framework for protecting data centre cooling and building systems without slowing the drive for efficiency and innovation. ... As the UK expands its data centre capacity to fuel AI ambitions and digital transformation, cybersecurity must be designed into the physical systems that keep those facilities stable. Cooling is not just an operational detail. It is a potential target — and protecting it is essential to ensuring the sector’s growth is sustainable, resilient, and secure.


Rethinking Regression Testing with Change-to-Test Mapping

Regression testing is essential to software quality, but in enterprise projects it often becomes a bottleneck. Full regression suites may run for hours, delaying feedback and slowing delivery. The problem is sharper in agile and DevOps, where teams must release updates daily. ... The need for smarter regression strategies is more urgent than ever. Modern software systems are no longer monoliths; they are built from microservices, APIs, and distributed components, each evolving quickly. Every code change can ripple across modules, making full regressions increasingly impractical. At the same time, CI/CD costs are rising sharply. Cloud pipelines scale easily but generate massive bills when regression packs run repeatedly. ... The core idea is simple: “If only part of the code changes, why not run only the tests covering that part?” Change-to-test mapping links modified code to the relevant tests. Instead of running the entire suite on every commit, the approach executes a targeted subset – while retaining safeguards such as safety tests and fallback runs. What makes this approach pragmatic is that it does not rely on building a “perfect” model of the system. Instead, it uses lightweight signals – such as file changes, annotations, or coverage data – to approximate the most relevant set of tests. Combined with guardrails, this creates a balance: fast enough to keep up with modern delivery, yet safe enough to trust in production-grade environments.


Is A Human Touch Needed When Compliance Has Automation?

Even with technical issues, automation may highlight missing patches, but humans are the ones who must prioritize fixes, coordinate remediation, and validate that vulnerabilities are closed. Audits highlight this divide even more clearly. Regulators rarely accept a data dump without explanation. Compliance officers must be able to explain how controls work, why exceptions exist, and what is being done to address them. Without human review, automated alerts risk creating false positives, blind spots, or alert fatigue. Perhaps most critically, over-dependence on automation can erode institutional knowledge, leaving teams unprepared to interpret risk independently. ... By eliminating repetitive evidence collection, teams gain the capacity to analyze training effectiveness, scenario-plan future threats, and interpret regulatory changes. Automation becomes not a replacement for people, but a multiplier of their impact. ... Over-reliance on automation carries its own risks. A clean dashboard may mask legacy systems still in production or system blind spots if a monitoring tool goes down. Without active oversight, teams may not discover gaps until the next audit. There’s also the danger of compliance becoming a “black box,” where staff interact with dashboards but never learn how to evaluate risk themselves. CIOs need to actively design against these vulnerabilities.


14 Challenges (And Solutions) Of Filling Fractional Leadership Roles

Filling a fractional leadership role is tough when companies underestimate the expertise required to thrive in such a role. Fractional leaders need both autonomy and seamless integration with key stakeholders. ... One challenge of fractional leadership is grasping the company culture and processes with limited time on site. Without that context, even the most skilled leader can struggle to drive meaningful change or build credibility. ... Finding the right culture fit for a fractional leadership role can be challenging. High-performing leadership teams are tight-knit ecosystems, and a fractional leader’s challenges with breaking into them and fitting into their culture can be daunting. ... One challenge is unrealistic expectations—wanting full-time availability at part-time cost. The key is to define scope, decision rights and deliverables upfront. Treat fractional leaders as strategic partners, not stopgaps. Clear onboarding and aligned incentives are essential to driving value and trust. ... A common hurdle with fractional roles is misaligned expectations—impact is needed fast, but boundaries and authority aren’t always defined. The fix? Be upfront: outline goals, decision-making limits and integration plans early so leaders can add value quickly without friction.


Will the EU Designate AI Under the Digital Markets Act?

There are two main ways in which the DMA will be relevant for generative AI services. First, a generative AI player may offer a core platform service and meet the gatekeeper requirements of the DMA. Second, generative AI-powered functionalities may be integrated or embedded in existing designated core platform services and therefore be covered by the DMA obligations. Those obligations apply in principle to the entire core platform service as designated, including features that rely on generative AI. ... Cloud computing is already listed as a core platform service under the DMA, and thus, designating cloud services would be a much faster process than creating a new core platform service category. Michelle Nie, a tech policy researcher formerly with the Open Markets Institute, says the EU should designate cloud providers to tackle the infrastructural advantages held by gatekeepers. Indeed, she has previously written for Tech Policy Press that doing so “would help address several competitive concerns like self-preferencing, using data from businesses that rely on the cloud to compete against them, or disproportionate conditions for termination of services.” ... Introducing contestability and fairness, the stated goals of the DMA, into digital ecosystems increasingly relied on by private and public institutions could not be more critical. 


The Looming Authorization Crisis: Why Traditional IAM Fails Agentic AI

From copilots booking travel to intelligent agents updating systems and coordinating with other bots, we’re stepping into a world where software can reason, plan, and operate with increasing autonomy.This shift brings immense promise and significant risk. The identity and access management (IAM) infrastructures that we rely upon today were built for people and fixed service accounts. They weren’t designed to manage self-directing, dynamic digital agents. And yet that’s what Agentic AI demands. ... The road to a comprehensive and internationally accessible Agentic AI IAM framework is a daunting task. The rapid pace of AI development demands accelerated IAM security guidance, especially for heavily regulated sectors. Continued research, continued development of standards, and rigorous interoperability are required to prevent fragmentation into incompatible identity silos. We must also address the ethical issues, such as bias detection and mitigation in credentials, and offer transparency and explainability of IAM decisions. ... The stakes are high. Without a comprehensive plan for managing these agents—one that tracks who they are, what they can perceive, and when their permissions expire—we risk disaster through way of complexity and compromise. Identity remains the foundation of enterprise security, and its scope must reach rapidly to shield the autonomous revolution.


How immutability tamed the Wild West

One of the first lessons that a new programmer should learn is that global variables are a crime against all that is good and just. If a variable is passed around like a football, and its state can change anywhere along the way, then its state will change along the way. Naturally, this leads to hair pulling and frustration. Global variables create coupling, and deep and broad coupling is the true crime against the profession. At first, immutability seems kind of crazy—why eliminate variables? Of course things need to change! How the heck am I going to keep track of the number of items sold or the running total of an order if I can’t change anything? ... The key to immutability is understanding the notion of a pure function. A pure function is one that always returns the same output for a given input. Pure functions are said to be deterministic, in that the output is 100% predictable based on the input. In simpler terms, a pure function is a function with no side effects. It will never change something behind your back. ... Immutability doesn’t mean nothing changes; it means values never change once created. You still “change” by rebinding a name to a new value. The notion of a “before” and “after” state is critical if you want features like undo, audit tracing, and other things that require a complete history of state. Back in the day, GOSUB was a mind-expanding concept. It seems so quaint today. 


What Lessons Can We Learn from the Internet for AI/ML Evolution?

One of the defining principles of the Internet was to keep the core simple and push the intelligence to the edge. The network and its host computers just simply delivered packets reliably without dictating or controlling applications. That principle enabled the explosion of the Web, streaming, and countless other services. In AI, similar principles should be considered. Instead of centralizing everything in “one foundational model”, we should empower distributed agents and edge intelligence. Core infrastructure should stay simple and robust, enabling diverse use cases on top. ... One of the most important lessons of all from the Internet is that there be no single company nor government-owned or controlled TCP/IP stack. It is neutral governance that created global trust and adoption. Institutions such as ICANN, and the regional Internet registries (RIRs) played a key role by managing domain names and IP address assignments in an open and transparent way, ensuring that resources were allocated fairly across geographies. This kind of neutral stewardship allowed the Internet to remain interoperable and borderless. On the other hand, today’s AI landscape is controlled by a handful of big-tech companies. To scale AI responsibly, we will need similar global governance structures—an “IETF for AI,” complemented by neutral registries that can manage shared resources such as model identifiers, agent IDs, coordinating protocols, among others.


Digital Transformation: Investments Soar, But Cyber Risks (Often) Outpace Controls

With the accelerating digital transformation, periodic security and compliance reviews are obsolete. Nelson emphasizes the need for “continuous assessment—continuous monitoring of privacy, regulatory, and security controls,” with automation used wherever feasible. Third-party and supply-chain risk must be continuously monitored, not just during vendor onboarding. Similarly, asset management can no longer be neglected, as even overlooked legacy devices—like unpatched Windows XP machines in manufacturing—can serve as vectors for persistent threats. Effective governance is crucial to enhancing security during periods of rapid digital transformation, Nelson emphasized. By establishing robust frameworks and clear policies for acceptable use, organizations can ensure that new technologies, such as AI, are adopted responsibly and securely. ... Maintaining cybersecurity within Governance, Risk, and Compliance (GRC) programs helps keep security from being a reactive cost center, as security measures are woven into the digital strategy from the outset, rather than being retrofitted. And GRC frameworks provide real-time visibility into organizational risks, facilitate data-driven decision-making, and create a culture where risk awareness coexists with innovation. This harmony between governance and digital initiatives helps businesses navigate the digital landscape while ensuring their operations remain secure, compliant, and prepared to adapt to change.

Daily Tech Digest - September 14, 2025


Quote for the day:

"Courage doesn't mean you don't get afraid. Courage means you don't let fear stop you." -- Bethany Hamilton


The first three things you’ll want during a cyberattack

The first wave of panic a cyberattack comes from uncertainty. Is it ransomware? A phishing campaign? Insider misuse? Which systems are compromised? Which are still safe? Without clarity, you’re guessing. And in cybersecurity, guesswork can waste precious time or make the situation worse. ... Clarity transforms chaos into a manageable situation. With the right insights, you can quickly decide: What do we isolate? What do we preserve? What do we shut down right now? The MSPs and IT teams that weather attacks best are the ones who can answer those questions without delays. ... Think of it like firefighting: Clarity tells you where the flames are, but control enables you to prevent the blaze from consuming the entire building. This is also where effective incident response plans matter. It’s not enough to have the tools; you need predefined roles, playbooks and escalation paths so your team knows exactly how to assert control under pressure. Another essential in this scenario is having a technology stack with integrated solutions that are easy to manage. ... Even with visibility and containment, cyberattacks can leave damage behind. They can encrypt data and knock systems offline. Panicked clients demand answers. At this stage, what you’ll want most is a lifeline you can trust to bring everything back and get the organization up and running again.


Emotional Blueprinting: 6 Leadership Habits To See What Others Miss

Most organizations use tools like process mapping, journey mapping, and service blueprinting. All valuable. But often, these efforts center on what needs to happen operationally—steps, sequences, handoffs. Even journey maps that include emotional states tend to track generalized sentiment (“frustrated,” “confused”) at key stages. What’s often missing is an observational discipline that reveals emotional nuance in real time. ... People don’t just come to get things done. They come with emotional residue—worries, power dynamics, pride, shame, hope, exhaustion. And while you may capture some of this through traditional tools, observation fills in what the tools can’t name. ... Set aside assumptions and resist the urge to explain. Just watch. Let insight come without forcing interpretation. ... Focus on micro-emotions in the moment, then pull back to observe the emotional arc of a journey. ... Observe what happens in thresholds—hallways, entries, exits, loading screens. These in-between moments often hold the strongest emotional cues. ... Track how people react, not just what they do. Does their behavior show trust, ease, confusion, or hesitance? ... Trace where momentum builds—or breaks. Energy flow is often a more reliable signal than feedback forms.


Cloud security gaps widen as skills & identity risks persist

According to the report, today's IT environment is increasingly complicated. The data shows that 82% of surveyed organisations now operate hybrid environments, and 63% make use of multiple cloud providers. As the use of cloud services continues to expand, organisations are required to achieve unified security visibility and enforce consistent security policies across fragmented platforms. However, the research found that most organisations currently lack the necessary controls to manage this complexity. This deficiency is leading to blind spots that can be exploited by attackers. ... The research identifies identity management as the central vulnerability in current cloud security practices. A majority of respondents (59%) named insecure identities and permissions as their primary cloud security concern. ... "Identity has become the cloud's weakest link, but it's being managed with inconsistent controls and dangerous permissions. This isn't just a technical oversight; it's a systemic governance failure, compounded by a persistent expertise gap that stalls progress from the server room to the boardroom. Until organisations get back to basics, achieving unified visibility and enforcing rigorous identity governance, they will continue to be outmanoeuvred by attackers," said Liat Hayun, VP of Product and Research at Tenable.


Biometrics inspire trust, policy-makers invite backlash

The digital ID ambitions of the EU and World are bold, the adoption numbers still to come, they hope. Romania is reducing the number of electronic identity cards it is planning to issue for free by a million and a half following a cut to the project’s budget. It risks fines that eventually in theory could stretch into hundreds of millions of euros for missing the EU’s digital ID targets. World now gives fans of IDs issued by the private sector, iris biometrics, decentralized systems and blockchain technologies an opportunity to invest in them on the NASDAQ. ... An analysis of the Online Safety Act by the ITIF cautions that any attempt to protect children from online harms invites backlash if it blocks benign content, or if it isn’t crystal clear about the lines between harmful and legal content. Content that promotes self-harm is being made illegal in the UK under the OSA, shifting the responsibility of online platforms from age assurance to content moderation. By making the move under the OSA, new UK Tech Secretary Liz Kendall risks strengthening arguments that the government is surreptitiously increasing censorship.  Her predecessor Peter Kyle, having presided over the project so far, now gets to explain it to the American government as Trade Secretary. Domestically, more children than adults consider age checks effective, survey respondents tell Sumsub, but nearly half of UK consumers worry about the OSA leading to censorship.


How to make your people love change

The answer lies in a core need every person has: self-concordance. When change is aligned with a person’s aspirations, values, and purpose, they are more likely to embrace it. To make that happen, we need a mindset shift. This needs to happen at two levels. ... The first thing to consider is that we have to think of employees not as objects of change but as internal customers. Just like marketers try to study consumer behaviour and aspirations with deep granularity, we must try to understand employees in similar detail. And not just see them as professionals but as individuals. ... Second, it meets the employees where they are, instead of trying to push them towards an agenda. And third, and most importantly, it makes them not just invested in the change process but turns them into the change architects. What these architects will build may not be the same as what we want them to, but there will be some overlaps. And because we empowered them to do this, they become fellow travelers, and this creates a positive change momentum, which we can harvest to effect the changes we want as well. ... We worked with a client where there was a need to get out of excessively critical thinking—a practice that had kept them compliant and secure, but was now coming in the way of growth—and move towards a more positive culture. 


Cloud-Native Security in 2025: Why Runtime Visibility Must Take Center Stage

For years, cloud security has leaned heavily on preventative controls like code scanning, configuration checks, and compliance enforcement. While essential, these measures provide only part of the picture. They identify theoretical risks, but not whether those risks are active and exploitable in production. Runtime visibility fills that gap. By observing what workloads are actually running — and how they behave — security teams gain the highest fidelity signal for prioritizing threats. ... Modern enterprises face an avalanche of alerts across vulnerability scanners, cloud posture tools, and application security platforms. The volume isn't just overwhelming — it's unsustainable. Analysts often spend more time triaging alerts than actually fixing problems. To be effective, organizations must map vulnerabilities and misconfigurations to:The workloads that are actively running. The business applications they support. The teams responsible for fixing them. This alignment is critical for bridging the gap between security and development. Developers often see security findings as disruptive, low-context interruptions. ... Another challenge enterprises face is accountability. Security findings are only valuable if they reach the right owner with the right context. Yet in many organizations, vulnerabilities are reported without clarity about which team should fix them.


Want to get the most out of agentic AI? Get a good governance strategy in place

The core challenge for CIOs overseeing agentic AI deployments will lie in ensuring that agentic decisions remain coherent with enterprise-level intent, without requiring constant human arbitration. This demands new governance models that define strategic guardrails in machine-readable logic and enforce them dynamically across distributed agents. ... Agentic agents in the network, especially those retrained or fine-tuned locally, may fail to grasp the nuance embedded in these regulatory thresholds. Worse, their decisions might be logically correct yet legally indefensible. Enterprises risk finding themselves in court arguing the ethical judgment of an algorithm. The answer lies in hybrid intelligence: pairing agents’ speed with human interpretive oversight for edge cases, while developing agentic systems capable of learning the contours of ambiguity. ... Enterprises must build policy meshes that understand where an agent operates, which laws apply, and how consent and access should behave across borders. Without this, global companies risk creating algorithmic structures that are legal in no country at all. In regulated industries, ethical norms require human accountability. Yet agent-to-agent systems inherently reduce the role of the human operator. This may lead to catastrophic oversights, even if every agent performs within parameters.


The Critical Role of SBOMs (Software Bill of Materials) In Defending Medtech From Software Supply Chain Threats

One of the primary benefits of an SBOM is enhanced transparency and traceability. By maintaining an accurate and up-to-date inventory of all software components, organizations can trace the origin of each component and monitor any changes or updates. ... SBOMs play a vital role in vulnerability management. By knowing exactly what components are present in their software, organizations can quickly identify and address vulnerabilities as they are discovered. Automated tools can scan SBOMs against known vulnerability databases, alerting organizations to potential risks and enabling timely remediation. ... For medical device manufacturers, compliance with regulatory requirements is paramount. Regulatory bodies, such as the U.S. FDA (Federal Drug Administration) and the EMA (European Medicines Agency), have recognized the importance of SBOMs in ensuring the security and safety of medical devices. ... As part of this regulatory framework, the FDA emphasizes the importance of incorporating cybersecurity measures throughout the product lifecycle, from design and development to post-market surveillance. One of the critical components of this guidance is the inclusion of an SBOM in premarket submissions. The SBOM serves as a foundational element in identifying and managing cybersecurity risks. The FDA’s requirement for an SBOM is not just about listing software components; it’s about promoting a culture of transparency and accountability within the medical device industry.


Shedding light on Shadow AI: Turning Risk to Strategic Advantage

The fact that employees are adopting these tools on their own tells us something important: they are eager for greater efficiency, creativity, and autonomy. Shadow AI often emerges because enterprise tools lag what’s available in the consumer market, or because official processes can’t keep pace with employee needs. Much like the early days of shadow IT, this trend is a response to bottlenecks. People want to work smarter and faster, and AI offers a tempting shortcut. The instinct of many IT and security teams might be to clamp down, block access, issue warnings, and attempt to regain control. ... Employees using AI independently are effectively prototyping new workflows. The real question isn’t whether this should happen, but how organisations can learn from and build on these experiences. What tools are employees using? What are they trying to accomplish? What workarounds are they creating? This bottom-up intelligence can inform top-down strategies, helping IT teams better understand where existing solutions fall short and where there’s potential for innovation. Once shadow AI is recognised, IT teams can move from a reactive to a proactive stance, offering secure, compliant alternatives and frameworks that still allow for experimentation. This might include vetted AI platforms, sandbox environments, or policies that clarify appropriate use without stifling initiative.


Why Friction Should Be a Top Consideration for Your IT Team

Some friction can be good, such as access controls that may require users to take a few seconds to authenticate their identities but that help to secure sensitive data, or change management processes that enable new ways of doing business. By contrast, bad friction creates delays and stress without adding value. Users may experience bad friction in busywork that delivers little value to an organization, or in provisioning delays that slow down important projects. “You want to automate good friction wherever possible,” Waddell said. “You want to eliminate bad friction.” ... As organizations work to eliminate friction, they can explore new approaches in key areas. The use of platform engineering lessens friction in multiple ways, enabling organizations to reduce the time needed to bring new products and services to market. Further, it can help organizations take advantage of automation and standardization while also cutting operational overhead. Establishing cyber resilience is another important way to remove friction. Organizations certainly want to avoid the massive friction of a data breach, but they also want to ensure that they can minimize the impact of a breach and enable faster incident response and recovery. “AI threats will outpace our ability to detect them,” Waddell said. “As a result, resilience will matter more than prevention.”