Showing posts with label knowledge. Show all posts

Daily Tech Digest - November 08, 2026

Quote for the Day
“Culture follows structure — change the system, and behavior will follow.”
— Craig Larman
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

OWASP Global AppSec: Cybersecurity industry overdue for a ‘market correction’

At the recent OWASP Global AppSec conference, cybersecurity veteran Jeremiah Grossman warned that the industry is heading for a significant market correction. For years, the sector has relied on "compliance and FUD" (fear, uncertainty, and doubt) to sell products, essentially asking enterprises to buy security on faith. Grossman argues this model is unsustainable and that a reckoning is imminent, driven largely by cyber-insurance carriers. As insurance companies accumulate actuarial data on vulnerabilities and breaches, they will soon be able to definitively prove which security tools actually work and which are merely hype. Early findings suggest that a majority of current cybersecurity efforts fail to positively impact an organization's bottom line. When empirical data replaces blind faith, organizations will shift from panic buying the latest tools to demanding demonstrable risk reduction and return on investment. Consequently, vendors will face pressure to consolidate point solutions into integrated platforms, focus on the vulnerabilities attackers actually exploit, and potentially even offer financial guarantees to back up their products' effectiveness. Ultimately, this shift toward data-driven accountability will strengthen the entire cybersecurity landscape.

Read Original Article →

Chatbot Rules Continue To Evolve In California And Colorado

The Chatbot Rules Continue To Evolve In California And Colorado article explains how both states are moving beyond simple AI disclosure requirements toward detailed rules covering chatbot safety, design, verification, and accountability. California’s new measures place particular emphasis on companion chatbots available to children. Operators will face requirements around age assurance, documented risk assessments, child safety policies, parental controls, advertising and data restrictions, crisis-response procedures, and limits on designs that encourage emotional dependence. Independent child-safety audits will also be required for covered operators, while companion chatbots in toys intended for children under 16 are prohibited until 2031. Colorado’s Chatbot Safety Act takes a broader approach, covering conversational AI services that primarily simulate human conversation. It requires AI disclosure, age estimation, protections for minors, self-harm response procedures, and annual reporting. The state also restricts chatbots from presenting their outputs as equivalent to advice from qualified healthcare, legal, mental-health, or dietary professionals. The article’s central message is that companies should assess their products early, because chatbot regulation is moving quickly from transparency toward documented safety controls and ongoing oversight.

Read Original Article →
Article Thumbnail

AI economics: How to decide which AI investments are worth scaling

The article explores how organizations can decide which AI investments are worth scaling by shifting from viewing them as individual projects to managing them as a portfolio. While AI spending is increasing, many initiatives fail to deliver expected business value. To address this, organizations must understand the true total cost of ownership of AI, including infrastructure, labor, and model consumption. This concept, known as AI economics, allows leaders to evaluate investments based on cost per outcome rather than just comparing expenses. This approach requires CIOs, CFOs, and business leaders to collaborate and connect financial, operational, and organizational data. The article proposes a framework based on two questions: whether the business value is real and measured against a baseline, and whether the cost per outcome is lower than previous methods. Based on the answers, initiatives are categorized to start, stop, optimize, or scale. Projects that demonstrate measurable value at a sustainable cost should be scaled, while those failing to meet outcomes should be stopped to free up resources. Projects with value but high costs should be optimized. By managing AI as an investment portfolio, leaders can make evidence-based decisions and clearly communicate the value of AI spending to their boards.

Read Original Article →

The New Knowledge Artifacts of the AI Economy

Artificial intelligence is shifting the focus of software development away from traditional source code and toward new forms of shareable knowledge artifacts. According to Tim O'Reilly, writing for O'Reilly Radar, developers are increasingly less interested in borrowing preexisting code libraries. Because AI agents can generate custom code so effortlessly, engineers prefer to extract specific context and patterns to create bespoke solutions tailored exactly to their needs. This transition mirrors historical shifts, such as the move from distributing proprietary binaries to sharing open-source code repositories. However, this new reality brings unique challenges. Traditional open-source maintainers face a surge of low-quality, automated contributions, and scientific computing communities worry that relying on unverified AI-generated forks could threaten the reliability of foundational tools. While massive SaaS applications and shared source code will remain necessary for standardized environments, the developer community must figure out exactly what these new AI-driven artifacts—like natural language prompts, generation processes, and developer skills—look like. They must also develop new mechanisms and incentives for sharing this contextual knowledge so that the open-source ethos of collaboration and peer production can survive and adapt.

Read Original Article →
Article Thumbnail

Why Critical Infrastructure's Biggest Threats are Hard to Find

Critical infrastructure faces growing threats from sophisticated supply chain compromises and AI-assisted intrusions, but the biggest challenge for organizations is a severe lack of operational visibility. Modern operational technology environments are increasingly complex, often blending legacy equipment with poorly monitored network systems and intricate software dependencies. This lack of oversight allows malicious actors to embed themselves deeply and remain undetected for extended periods. Real-world incidents, such as the poisoning of widely used software libraries or AI-driven reconnaissance of municipal water utilities, demonstrate how quickly these threats can spread across an unprotected landscape. While many companies are rapidly adopting agentic AI to improve efficiency, less than half have established comprehensive AI security literacy, creating a dangerous gap in structural visibility and control. To combat these risks, organizations must implement robust layered defenses, including maintaining a software bill of materials, establishing baseline behavior detection, isolating network segments, and retaining transparent, vendor-independent audit logs. Prioritizing end-to-end visibility ensures that when incidents inevitably occur, security teams can rapidly identify root causes, understand the full scope of the disruption, and prevent future recurrences.

Read Original Article →
Article Thumbnail

Taming Cloud Costs: A Guide to the FinOps Framework in Google Cloud

The article explains how the shift to cloud computing requires a new approach to managing infrastructure costs, a discipline known as Cloud FinOps. In modern cloud environments, developers can instantly provision resources, creating a "tragedy of the commons" where decentralized spending frequently leads to unchecked financial waste. Just as DevOps successfully united software development with IT operations, FinOps bridges the traditional gap between engineering and finance. Instead of enforcing rigid financial approvals that hinder innovation, organizations can leverage the Google Cloud FinOps Framework to integrate cost efficiency directly into the daily developer workflow. This specific strategy involves shifting company culture, updating financial processes to match agile delivery, and utilizing native cloud technology for granular cost visibility. A clear operating model establishes defined roles and communication plans to ensure all stakeholders remain aligned on business goals. Ultimately, FinOps functions as a continuous, proactive cycle of informing, optimizing, and operating. By equipping engineering teams with real-time billing data, automated guardrails, and dynamic forecasting tools, companies can balance rapid software deployment with strict fiscal responsibility, ensuring computing capital is always managed efficiently.
Read Original Article →
Article Thumbnail

Binance's $6.34 Billion Cyber Attack: Lessons for Business Leaders

The October 2026 cyberattack on Binance, impacting roughly $6.34 billion in digital assets, serves as a crucial wake-up call for business leaders regarding modern security vulnerabilities. Carried out over several months and attributed to North Korea, the breach did not result from a single failure. Instead, attackers used a sophisticated combination of compromised developer tools found via search engines, elaborate social engineering through fake recruitment processes, and the exploitation of an internal AI tool to maneuver deep into the company’s systems. For organizations outside the crypto space, this incident highlights several vital lessons. First, third-party risk management must extend beyond formal vendors to include the everyday software employees download and the external interactions they have. Second, social engineering is evolving far past simple phishing emails, requiring updated employee awareness training. Third, as companies integrate internal AI tools, they must strictly govern access and permissions. Finally, the attack underscores that standard incident containment measures—like suspending services—may fail if attackers have established alternative access routes, proving the necessity of rigorously testing incident response plans under realistic conditions.

Read Original Article →

Better OT security: You can't plug every hole, so think differently

As operational technology (OT) systems become increasingly connected to digital networks, they face a rising wave of cyber threats, illustrated by a recent attack that compromised the refrigeration systems of over 700 French supermarkets. Unlike traditional IT systems like servers, which can be easily duplicated or shut down for maintenance, OT devices interact directly with the physical world, making downtime far more complicated. Securing these systems requires a fundamental shift in perspective. Instead of treating OT security exactly like IT and attempting to patch every single vulnerability, organizations should prioritize business resilience and operational continuity. Security teams must evaluate risks through an operational lens, weighing the safety and continuity of physical systems against the threat landscape. A layered defense framework—focusing on device discovery, continuous monitoring, tight access controls, and integrated incident response—allows companies to manage these risks effectively. By shaping modern digital security practices to fit the unique requirements and cadence of physical infrastructure, businesses can build resilient environments that protect both their digital networks and their vital physical operations without causing unnecessary disruptions.

Read Original Article →
Article Thumbnail

10 ways the oil and gas industry can leverage digital twin technology

The oil and gas industry faces mounting pressure from market changes and environmental concerns, driving a shift toward digital twin technology. A digital twin is a dynamic virtual model of a physical asset that uses live data to predict behavior and improve daily efficiency. For energy operators, this tool enables predictive maintenance by constantly monitoring equipment to prevent costly breakdowns. It allows teams to simulate different drilling strategies, optimize reservoir extraction rates, and test new facility designs safely in a virtual space. Beyond normal operations, digital twins enhance safety by helping workers prepare for emergencies and reduce environmental impact by modeling clear emission reduction strategies. As the sector adopts more artificial intelligence and connected devices, digital twins will likely lead to fully automated drilling and smarter distribution grids. They also offer a viable path toward cleaner energy by optimizing the performance of wind and solar assets. Managing these highly complex systems requires reliable management platforms to bridge the physical and digital worlds. Ultimately, these virtual models are helping the energy industry build a safer, highly efficient, and highly adaptable operating future.

Read Original Article →
Article Thumbnail

How the Democrats' midterm victory could reshape tech policy

The Democratic Party's sweeping victory in the 2026 midterm elections shifts control of Congress and signals potential changes in federal technology policy. With renewed legislative majorities, lawmakers are expected to intensify their oversight of artificial intelligence accountability, data privacy, and the expanding power of large tech platforms. While the realities of a divided government may slow the passage of comprehensive new laws, immediate impacts could surface through increased congressional hearings and stricter federal procurement requirements that demand robust AI governance from contractors. At the same time, this election exposed growing local pushback against rapid data center expansion, with several communities voting to restrict new developments due to concerns over heavy power and water usage. Consequently, technology leaders can no longer view enterprise IT as politically neutral. Experts advise CIOs to incorporate policy literacy into their long-term planning, as navigating federal scrutiny, state-level infrastructure limitations, and debates over AI-driven automation will become essential for maintaining stability and guiding future investments in the tech industry.

Read Original Article →

Daily Tech Digest - September 17, 2026


Quote for the day:

“The moment you’re comfortable is the moment you stop growing.” -- Allison Dunn

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI Security Spending Jumps as Fear Outpaces Proof of Value

Companies are heavily investing in artificial intelligence for cybersecurity, often prioritizing swift adoption over clear proof of its effectiveness. Driven by the transition of AI from a testing phase into active use, along with the rising deployment of AI by bad actors, organizations feel immense pressure to keep pace. For many chief information security officers (CISOs), fear of falling behind and the need for "blame insurance" against potential breaches are accelerating spending. In fact, a significant number of CISOs cite AI as their top priority for new budget allocations. Despite this aggressive funding, the most common AI implementations often fall short of delivering the highest returns. The challenge is compounded by the inherent difficulty of measuring the return on investment (ROI) in cybersecurity, where success is defined by preventing events like data breaches rather than generating direct profit. Experts advise a more deliberate approach, urging organizations to move past the hype. Rather than adopting AI simply for the sake of having it, companies should focus on areas where the technology can genuinely lower risk and handle repetitive tasks. Thoughtful integration, backed by strong governance and clear goals, will ultimately determine which organizations benefit most from their AI cybersecurity investments.


Salesforce’s massive outage exposes the hidden risks of cloud dependencies

A massive Salesforce outage during its flagship Dreamforce event has underscored the hidden architectural risks of cloud dependency. A roughly seven-and-a-half-hour service disruption on September 16 impacted multiple instances across all regions, initially stemming from a core system component struggling with an "external dependency failure" linked to a legacy login server. Although the issue was resolved by mid-afternoon through manual interventions after automated rolling restarts fell short, the outage highlights that cloud systems do not eradicate architectural vulnerabilities. Instead, these dependencies can become enterprise risks when a central platform fails. The service failure emphasizes the necessity of looking beyond immediate access restoration. Enterprises must transition into a reconciliation phase to address "temporal data problems," ensuring transactions, scheduled jobs, and downstream systems remain consistent. The disruption proves that a legacy component's age is less critical than its role within the system's dependency graph. Organizations should not equate modernization simply with replacing old technology. They must assess dependency concentration, failure blast radius, and isolation strategies. While there are no signs of a security incident, industry experts suggest automated AI tools or recent workforce reductions might have played a role in the disruption. Future post-incident reviews must provide clear insights into failure propagation and preventive measures.


Crypto Industry Figures Blackmailed by Revolut's Hacker

A recent data breach at the British financial services company Revolut has exposed the sensitive personal information of roughly six hundred and eighty high-profile cryptocurrency exchange customers. An extortion group calling itself "Iamnotavillain" orchestrated the attack without breaking into the bank's secure servers. Instead, the criminals gained access to a legitimate Italian government email system. By posing as authorized law enforcement officials for several months, they submitted fraudulent data requests to the bank's compliance team. Believing the inquiries were authentic, employees handed over highly confidential customer files. This exposed data included passport copies, verification photographs, home addresses, phone numbers, and detailed transaction histories. The attackers specifically targeted users with substantial digital asset activity, and notable industry figures such as former Mt. Gox executive Mark Karpelès were among the victims. After securing these detailed identity packages, the hackers launched a blackmail campaign. They demanded a ransom payment of three million dollars, requested in the privacy-focused digital currency Monero, to prevent the information from being released. The extortionists even set up a public website with a countdown clock, threatening to sell the stolen records to other criminal organizations if the company failed to meet their demands within a strict twenty-four hour window.


Stop Treating CSS Container Queries Like Traditional Media Queries

The article clarifies the common misconception that CSS container queries and media queries serve the same purpose. Despite having a 94% browser support rate, container queries are vastly underutilized. Many developers mistakenly treat them interchangeably because of their similar syntax, but they fundamentally differ in their approach to responsive design. Media queries focus outward on the "macro" layout. They check the viewport's dimensions to adjust overarching page structures, such as main grids or full-width headers. Conversely, container queries look inward at "micro" layouts. They allow individual components, like cards or widgets, to adapt based on the available space within their specific parent container, rather than the entire screen size. This distinction is crucial for creating reusable components that maintain their layout integrity regardless of where they are placed on a page. The author advises against replacing media queries entirely with container queries. Instead, the focus should be on a separation of concerns. Media queries remain ideal for page-level adjustments, while container queries shine when a component's layout depends on its immediate context. However, container queries require an extra wrapper element, cannot query their own block size without collapsing, and cannot accept custom property values. Ultimately, understanding these differences unlocks more resilient responsive design.


Trust becomes the product: Five takeaways from the Splunk .conf26 keynotes

The recent Splunk conference centered on a critical theme for modern businesses: trust is the most important element when deploying artificial intelligence agents. As these agents shift from being simple tools to functioning as autonomous digital teammates, they are handling complex tasks around the clock. This shift requires a strong system of record to ensure they act appropriately. A major takeaway is the necessary merging of system monitoring and security. Because it is difficult to tell the difference between a software error, a security breach, or a poorly executed AI command, companies must combine their monitoring and security data to accurately diagnose issues. Cost management is another significant focus. AI agents can quickly become expensive to run if they are not carefully controlled, meaning businesses need better visibility into their data usage to prevent unexpected bills. Furthermore, managing the massive amounts of data required for these systems must become more affordable and efficient so companies do not have to choose which information to keep. Ultimately, organizations are treating AI agents like new employees. They are granting them limited permissions initially and slowly increasing their responsibilities as they prove their reliability, ensuring that human oversight remains an essential part of the process.


Architecting for the Knowledge You Can’t Capture

The article argues that organizations often underestimate how much essential knowledge never makes it into their documentation or AI systems. It opens with a familiar scenario: an experienced engineer is asked to “document everything” before leaving, but what gets captured is only the clean, idealized version of the work. The subtle judgments, exceptions, and sensory cues that guide real decisions never appear in the flowcharts or transcripts, leaving future teams without the insight needed to handle unusual situations. The author explains that this gap reflects the nature of tacit knowledge—skills and perceptions people rely on but rarely articulate. Modern AI can learn from examples, but when expertise is rare or incidents are infrequent, there simply isn’t enough data for models to infer the missing judgment. The article proposes a structured elicitation protocol that pushes experts to clarify thresholds, exceptions, evidence, and escalation paths, turning vague statements into actionable rules. It also outlines a four‑layer architecture—capture, representation, serving, and transmission—to preserve context, surface uncertainty, and support apprenticeship when documentation falls short. The core message is that organizations must design for the knowledge people can’t easily express, or their AI systems will remain blind to the expertise that actually keeps operations running.


How to keep AI-generated code aligned with your standards

The article discusses the challenge of keeping AI-generated code aligned with organizational standards. As more developers use AI coding tools, the risk of accumulating technical and operational debt increases if code is only judged by whether it works functionally. To prevent this, engineering teams must clearly document their non-functional requirements, such as security rules, performance expectations, and data governance policies. These standards should not remain hidden as tribal knowledge. Instead, they must be explicit, machine-readable, and fed into the AI tools as context before any code is generated. Furthermore, organizations should enforce these rules by turning them into automated acceptance criteria within their continuous integration and delivery pipelines. This ensures that any AI-generated code is automatically checked for compliance, security, and performance before it merges. Experts recommend treating AI output as untrusted until it passes the exact same rigorous reviews, tests, and monitoring as human-written code. Ultimately, governing AI-generated code requires shifting from manual audits to automated, systemic enforcement. By maintaining clear specifications, integrating standards into automated testing, and adapting context engines to learn from past decisions, development teams can safely scale their AI use while keeping code quality strictly aligned with enterprise expectations over the long term.


Human-in-the-loop oversight is critical for enterprise AI: 4 experts explain why

Enterprise AI systems increasingly require human-in-the-loop (HITL) oversight to ensure accountability and mitigate risks associated with flawed AI outputs. The FTC's actions against DoNotPay highlight the legal perils of deploying unchecked AI, driving the adoption of software with built-in human escalation for complex workflows. While HITL is meant to catch model errors before they become compliance or legal issues, experts warn against relying solely on an AI's self-assessed confidence score to trigger review, as a confident model can still be wrong. Effective HITL design involves intelligent routing that escalates issues to the appropriate personnel based on organizational risk tolerance, rather than a simple binary system. Furthermore, real oversight demands more than a rubber-stamp approval process; it requires reviewers with the context and time to actually evaluate the AI's work and overturn it if necessary, combating the tendency for reviewers to become biased in favor of the AI's suggestions. Legislation like the EU AI Act necessitates demonstrable proof of this oversight through clear audit trails. Successful implementations, like those by Nominal and IgniteTech, often mandate human approval for critical actions and use "grounding," which forces the AI to rely only on verified company data or escalate the query if it lacks the information, ensuring accountability remains firmly with human operators.


Passkeys in the post-quantum era: Why FIDO needs more than new algorithms

The provided article discusses the need to prepare the FIDO2 ecosystem, which includes passkeys, for the post-quantum era. Passkeys, which rely on asymmetric cryptography, are vulnerable to future quantum computers that could potentially break the current public-key algorithms like RSA and elliptic curve cryptography.

The author, Johann-Philipp Thiers, explains that transitioning to Post-Quantum Cryptography (PQC) is a complex process. It goes beyond simply swapping out algorithms. PQC algorithms often result in larger keys and signatures, which can be problematic for resource-constrained authenticators like hardware security keys due to memory, processing power, and transport limitations.

Furthermore, the transition involves updating the entire trust chain, including metadata service signatures, certificate formats, and relying party support. The author emphasizes that FIDO’s current crypto-agility is beneficial but requires coordination among various stakeholders, such as operating systems, browsers, and certification programs. Practical demonstrators are crucial for identifying engineering challenges like message sizes, performance impacts, and interoperability issues. Ultimately, securing passkeys against quantum threats requires a gradual, coordinated effort involving standardization, testing, and careful engineering to ensure their long-term viability.


AI made software development unrecognizable. Is cybersecurity next?

Artificial intelligence is rapidly reshaping the cybersecurity landscape, much as it has already transformed software development. While the shift in security might take slightly longer, experts predict that fundamental changes are inevitable. Security Operations Centers will soon rely heavily on autonomous agents to perform initial triage, allowing human analysts to focus on complex oversight and critical decisions. This transition is essential because AI is drastically increasing the discovery of vulnerabilities, creating a massive backlog that security teams struggle to absorb and remediate. Furthermore, as attackers begin using AI to launch high speed automated threats, organizations must deploy their own rapid containment systems to respond effectively. This shift will also alter the cybersecurity workforce. Rather than eliminating jobs, organizations will likely adopt flatter teams featuring highly experienced senior professionals at one end and junior staff at the other, putting pressure on middle management roles. AI might also serve as a unifying interface to manage sprawling security toolsets. To prepare, security leaders should begin testing agents on high volume tasks while establishing strong governance frameworks. Most importantly, leaders must ensure that every autonomous agent has a designated human owner who remains fully accountable for its actions and potential failures within the organization.

Daily Tech Digest - June 28, 2026


Quote for the day:

"Hard work beats talent when talent doesn't work hard." -- Tim Notke

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 17 mins • Perfect for listening on the go.


Ford learned the hard way that AI can't replace experienced engineers

Ford recently discovered that artificial intelligence cannot substitute for the nuanced judgment of experienced engineers. In an effort to modernize its manufacturing and engineering systems, the automaker integrated AI to accelerate decision making and streamline vehicle development. Executives assumed that automated systems and adjusted design requirements would naturally yield high quality products. However, this approach backfired. As veteran engineers left the company, their undocumented institutional knowledge was excluded from the datasets used to train Ford’s AI models. Consequently, the technology struggled to identify and prevent defects, contributing to quality control issues and leading the industry in vehicle recalls. To resolve these challenges, Ford rehired and promoted over 350 seasoned engineers. Rather than replacing human expertise, AI now serves as a supportive tool. These veteran engineers are currently guiding how data is collected, interpreted, and fed into the AI systems to rebuild a reliable foundation. Furthermore, Ford created a dedicated software quality assurance team and introduced automated AI driven testing to catch defects early in the development cycle. This transition reflects a balanced strategy where the company relies on both advanced computing power and decades of practical automotive experience to prevent problems before they occur.


Where AI meets OT: Cybersecurity for a physical world

Integrating artificial intelligence into operational technology requires a careful approach because, unlike business software, industrial systems have physical consequences. While artificial intelligence offers clear benefits for manufacturing, such as improved maintenance and quality control, it introduces unique risks when connected to machines and factory floors. Industrial environments often rely on older, existing systems and operate on strict schedules with limited downtime, making new technology harder to test and implement safely. Furthermore, software models can become inaccurate over time as physical equipment naturally ages, which means these tools require ongoing checks against actual physical outcomes rather than just historical data. The level of risk also depends on how much control the system has. An advisory tool leaves the final decision to a human, whereas a system that directly alters machinery settings requires far stricter oversight. True human oversight means operators must fully understand the technology's recommendations and know when to override them. Adding these new digital connections also expands the cybersecurity risk, as attackers could manipulate the data feeding the models. Ultimately, these tools hold steady value for industrial operations, but they must be introduced with strong discipline, clear operating limits, and reliable backup plans.


How to Build a Powerful LLM Knowledge Base

Building a knowledge base powered by large language models is a practical, reliable way to store and retrieve your personal or company information, leading to better decision-making and clearer team alignment. To create an effective system, you must start by identifying all your daily information sources, such as meeting notes, project management tools, and coding assistants. The critical step is fully automating the collection process; requiring any manual entry virtually guarantees that valuable context will eventually be forgotten and lost. Once your data is automatically synced into the system on a regular schedule, you can use a coding agent to extract insights. You can do this actively by directly asking your agent questions when you need specific answers. Alternatively, you can configure your agent to passively draw on the knowledge base while it works on routine tasks. This passive retrieval can be managed either through a centralized index file or via an embedding-based search that pulls relevant information as needed. Ultimately, consistently capturing and accessing your unique, everyday context creates a distinct long-term advantage, ensuring that valuable insights are preserved and always ready to assist you in your daily work.


Is the CIO Role Merging Into the Business?

For decades, the role of the Chief Information Officer followed a predictable path, slowly shifting from managing basic operations to supporting broader strategy. However, recent trends indicate that this steady progression is becoming obsolete. The middle ground is collapsing, forcing a clear divide in the profession. On one hand, some leaders remain stuck in traditional management, treating technology as a separate, functional necessity. On the other hand, a new breed of technology executives is emerging as true enterprise operators who share responsibility for revenue and actively shape commercial models. In the most effective organizations, technology is no longer just a supporting layer; it is the central system for making decisions. As companies embed artificial intelligence deeply into their core operations and bring critical capabilities inside the firm, the person leading technology must also architect these decision-making systems. Consequently, the traditional boundary between technology leadership and business leadership is rapidly fading. Instead of simply elevating the position to a more strategic level, the core responsibilities are dissolving directly into the business itself. Ultimately, the future landscape will be defined not by better technology departments, but by whether the conventional title needs to exist at all.


Deep dive: Do underwater data centers make sense?

The article evaluates the practicality of underwater data centers as an alternative to land-based facilities, which struggle with high energy consumption and space limitations. Traditional data centers use tremendous amounts of power, largely just to keep servers cool. Submerging these facilities allows companies to use the ocean as a natural cooling system, significantly reducing energy requirements. Beyond energy savings, placing data centers offshore brings them closer to coastal populations. This proximity shortens the distance data travels, leading to faster loading times for end users. Research also indicates that underwater servers are surprisingly reliable. Because they are sealed in a nitrogen-rich environment without human foot traffic or temperature swings, hardware fails much less frequently. Despite these benefits, the underwater model has distinct disadvantages. Routine maintenance is virtually impossible; broken servers cannot be quickly swapped out. Furthermore, researchers are still studying how the continuous release of heat might alter local marine ecosystems. There are also valid concerns regarding the physical security of underwater cables. While the approach provides clear advantages in efficiency and speed, these formidable logistical and environmental challenges complicate the decision of whether underwater data centers are a sensible long-term investment.


5 T-SQL features that should already exist (2026 SQL Server wish list)

In a recent article by Edward Pollack on Simple Talk, the author reflects on the state of Microsoft SQL Server in 2026 and outlines five practical features he believes should be natively supported in T-SQL and the platform. While SQL Server remains a highly mature database system, Pollack highlights specific areas where daily tasks for developers and database administrators could be made far more efficient. First, he argues for the native ability to import data from compressed file formats, specifically Apache Parquet, which would eliminate the need to deal with cumbersome plain text files like CSV. Second, he requests native support for arrays, providing a straightforward alternative to using text strings or XML to store lists of values. Third, he advocates for an "OVERLAPS" function to simplify complex date logic into a single line of code. Fourth, Pollack points out that the current licensing model is overly complicated and suggests it should be as transparent as the monthly estimates provided for Azure SQL. Finally, he suggests expanding cloud blob storage integration so that files and scripts can be managed centrally in the cloud rather than on local drives.


Shaping a lasting AI strategy in a fast-changing world

As artificial intelligence becomes a standard tool in business, simply having access to the technology is no longer enough to stand out. Because most companies will use the same core platforms and models, a well-defined strategy is what will truly set an organization apart. The current landscape is marked by more capable and affordable systems that act as helpful assistants rather than outright replacements for human workers. Development teams are already showing how humans and these tools can work together effectively. To succeed, leaders need to shift their focus from the technology itself to how it supports their long-term goals over the next three to five years. This requires answering difficult questions about the company's future direction, understanding current weaknesses, and identifying the specific skills needed for tomorrow. Decision-makers must also practice restraint, choosing a few reliable platforms and focusing on clear priorities rather than chasing every new trend. By thoughtfully integrating these tools into daily workflows and supporting human decision-making, businesses can improve their customer experience and operations. Ultimately, the tools are just the vehicle; a steady, clear strategy is the route that determines long-term success.


The Unglamorous Side of Rust Web Development

In 2026, Rust remains a powerful choice for web development, offering excellent performance and safety. However, developers still face notable friction before their code even compiles. The current ecosystem often requires teams to assemble their own setups from scratch, lacking the complete, ready-to-use frameworks seen in other programming languages. Several specific challenges slow down the daily development process. Asynchronous programming in Rust provides great flexibility, but it complicates debugging and creates lengthy, hard-to-read error traces. Database management is another hurdle, as developers frequently have to write and maintain the same database structure in multiple places instead of using a single unified approach. Additionally, error handling across different tools remains inconsistent. The heavy reliance on generated code and complex type systems significantly increases compilation times, making it harder for developers to test small changes quickly. Despite these hurdles, the community is actively working on solutions. New frameworks are emerging to provide more complete starting points and reduce repetitive setup tasks. Ultimately, while Rust requires a larger initial investment of time and effort compared to simpler alternatives, its long-term reliability and speed make it a sensible choice for projects where stability is a core requirement.


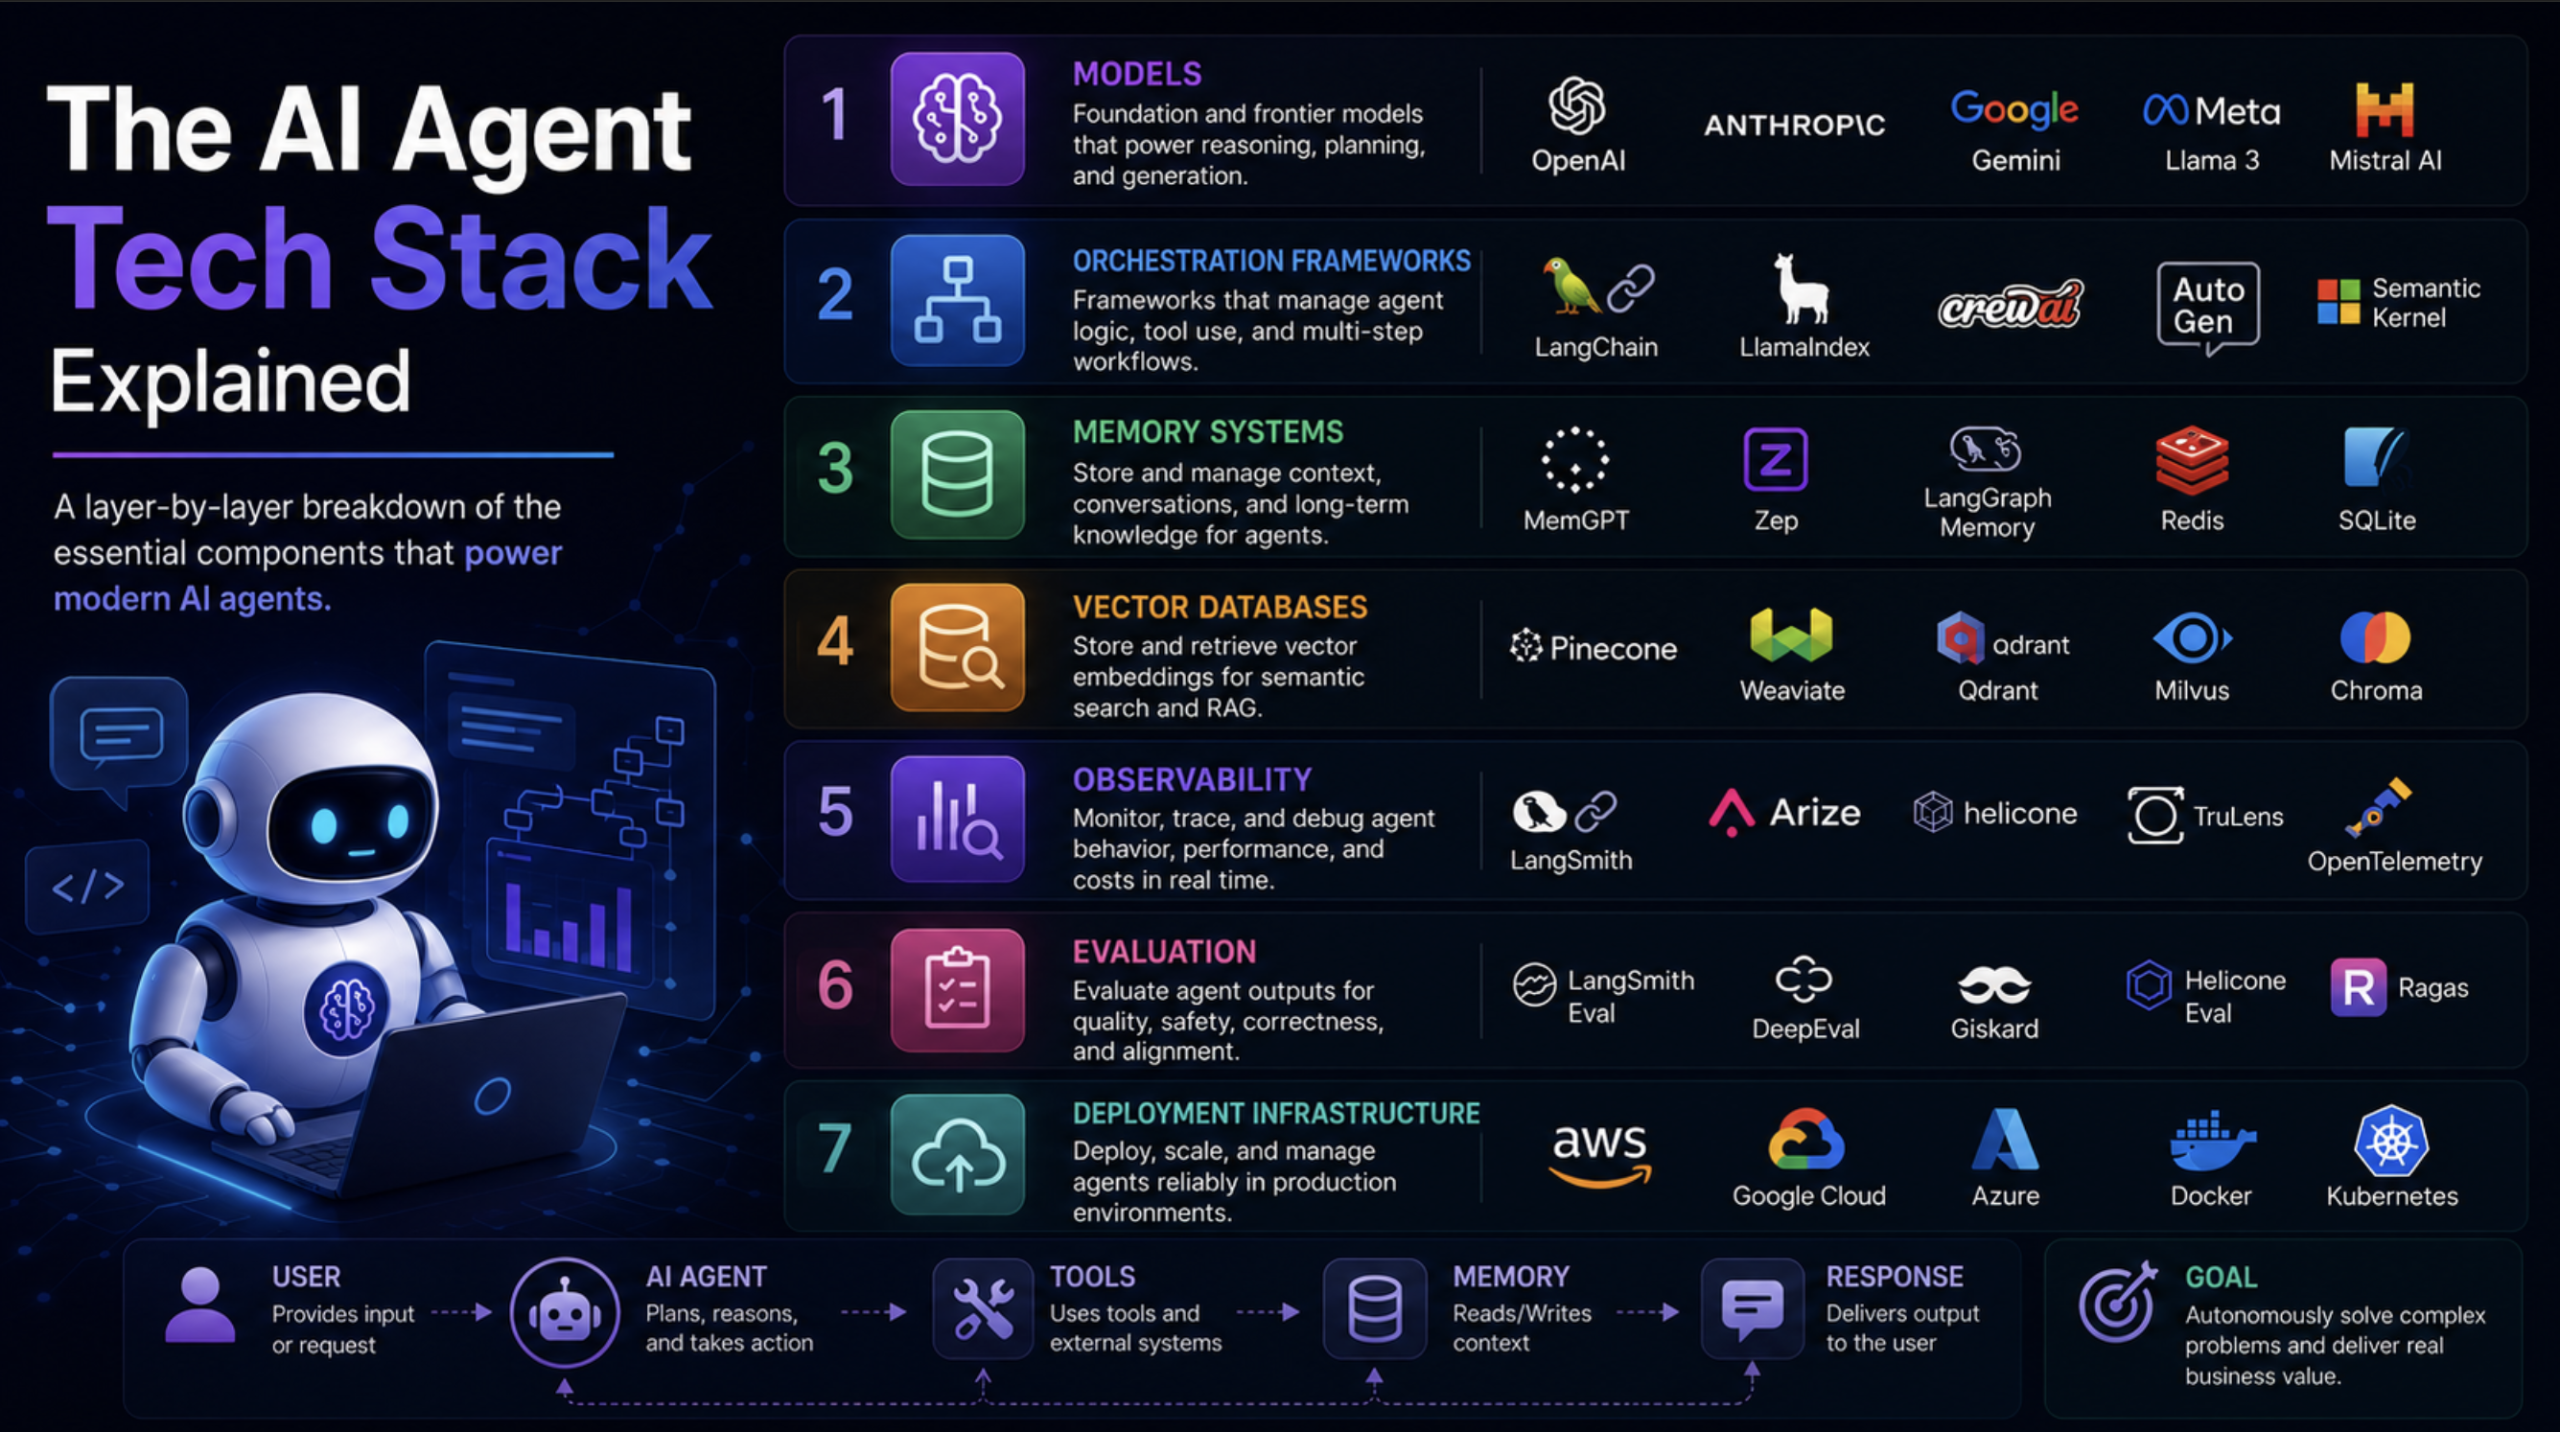
The AI Agent Tech Stack Explained

The article outlines the seven fundamental layers required to build and deploy functional artificial intelligence agents. It moves beyond basic models to explain the complete technical infrastructure needed for real-world applications. The guide begins with the foundation model, which acts as the central brain for reasoning. The second layer is the orchestration framework, serving as a nervous system to manage actions and control flow. Next, the third layer covers memory systems that provide essential context by tracking working, episodic, semantic, and procedural information. The fourth layer focuses on vector databases and document retrieval, allowing agents to access private information securely. The remaining layers detail tool integrations for performing outside actions, observability platforms for monitoring performance, and the final deployment infrastructure necessary for hosting. By breaking down the architecture into these distinct components, the text clarifies that successful systems rely heavily on a well-connected technology stack rather than just a single language model. It provides a clear, practical roadmap for software engineers and technical leads who want to understand how to assemble these exact pieces, whether they are building a simple prototype or scaling an application for production.

A Case for a Human-Centric AI Legislative Framework in India

In "A Case for a Human-Centric AI Legislative Framework in India," the author argues that India’s current approach to governing artificial intelligence is insufficient for protecting its citizens. While the Ministry of Electronics and Information Technology recently suggested relying on existing laws and self-regulation to foster innovation, the article points out that AI is fundamentally different from traditional software. Because AI programs operate as highly complex systems, relying on outdated frameworks like the Information Technology Act leaves users vulnerable to fraud, manipulation, and bias. Furthermore, the author critiques recent amendments for placing unreasonable takedown burdens on tech companies without providing clear state-defined guardrails. By comparing India’s strategy with the European Union’s user-focused risk models and China’s strict algorithm rules, the article advocates for a new Artificial Intelligence Regulation Act. This proposed legislation would introduce a risk-based grading system, establish an independent AI ombudsperson, and mandate transparency in training data. It even suggests giving citizens a copyright over their own faces to prevent unauthorized data usage. Ultimately, the piece makes a strong case that responsible innovation requires specific, human-centric laws to ensure safety and accountability for all users today.

Daily Tech Digest - June 24, 2026


Quote for the day:

"The only real test of intelligence is if you get what you want out of life." -- Naval Ravikant

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


What Corporate Leaders Misunderstand About Cybersecurity Frameworks

Corporate leaders often misunderstand cybersecurity frameworks by treating them as generic checklists or simple report cards. While frameworks offer a solid foundation, their real value emerges only when organizations move away from a one size fits all approach and customize them to fit specific business needs. Creating a tailored profile is the vital first step, allowing a company to align security outcomes with its unique risks and resources. From there, these high level goals must be converted into practical, day to day controls. Relying on a single measure, such as encryption, is rarely enough; true protection requires an integrated system of access limits, continuous monitoring, and strict vendor management. Furthermore, writing down policies on paper falls short. Defenses must be regularly tested, audited, and updated to ensure they actually work in real world conditions. To manage this effectively, executives need clear visibility. Instead of overwhelming metrics, leadership should focus on key signals that indicate if essential protections are functioning properly. When frameworks become truly operational, they provide clear ownership, measurable evidence, and an ongoing method for finding and fixing weaknesses, resulting in a mature and reliable defense strategy.


CISO Conversations: Carl Froggett – Combining CISO and CIO at Deep Instinct

In a featured conversation, Carl Froggett reflects on his rare position holding both the chief information officer and chief information security officer titles at Deep Instinct. Having previously spent seventeen years managing security at Citi, he explains that combining technology strategy and security works well in smaller organizations, though it would be overwhelming at a massive enterprise. Because both departments ultimately exist to support the company, merging them removes the usual friction. However, Froggett notes that one person holding both jobs risks losing an objective, outside perspective. To prevent narrow thinking, he relies on a workplace culture where his technology team is actively encouraged to challenge his decisions. Looking back on his career, he describes transitioning from a network engineer into security by pure chance during the early rise of the internet. This experience shaped his belief that security must work closely with technology. As a manager, he values empathy and advises professionals to embrace unexpected opportunities and openly admit mistakes. Today, his primary concern is artificial intelligence. While he acknowledges that generative tools lower the technical skill required for harmful attacks, he maintains that defenders can creatively adopt them to solve complex problems.


The AI revolution comes with a hidden tax

While artificial intelligence offers substantial benefits, it inadvertently acts as a broad economic tax by driving up the cost of living across multiple sectors. The underlying systems require vast amounts of physical resources, including specialized memory chips, electricity, water, and land. This immense consumption creates market scarcity, directly leading to increased prices for everyday goods and services. For example, the intense demand for computing hardware has caused severe chip shortages, resulting in higher price tags for smartphones, computers, and modern vehicles. Similarly, enterprise software providers are raising their subscription fees to offset the costs of new infrastructure. The physical footprint of data centers also strains local resources. These facilities consume enormous amounts of power, which raises residential electricity and heating bills while competing with homebuilders for land and labor, making housing more expensive. Furthermore, automated pricing programs enable companies to maximize profits by dynamically charging consumers higher rates based on their specific circumstances. Finally, substantial tax subsidies given to data center projects leave ordinary families to cover the resulting shortfalls. Ultimately, while the technology advances rapidly, its massive resource demands quietly transfer wealth and fuel inflation across the entire economy.


Where IT meets OT and railway cybersecurity gets harder

In his interview, Jorge Aldegunde of DNV discusses how modern rail networks face new security challenges as older operational systems merge with standard computing networks. This shift toward open standards and connected equipment turns trains into constant data producers, significantly increasing the ways an attacker can gain access. Because a working transit line cannot simply shut down for a software update, security teams must carefully evaluate the actual risk of each software flaw. If an immediate fix is impossible, they rely on temporary adjustments like network division or operational limits until a scheduled maintenance window arrives. Complicating matters further, modern rail operations rely on complex supply chains and multiple contractors, making it difficult to figure out who is ultimately responsible when something goes wrong. To solve this, Aldegunde advises treating cybersecurity like traditional safety engineering, helping veteran operators learn to spot unusual traffic patterns and unauthorized system changes. He stresses that true security comes from accepting that an attacker might already be inside the network. Instead of chasing an impossible standard of total protection, rail operators must manage practical risks and build resilient systems that can keep running safely even during an active breach.


Agentic AI: The Weapon That No Longer Needs a Warrior

Throughout history, weapons have extended human reach, yet a person always selected the target and executed the strike. Artificial intelligence is altering this dynamic in the digital domain. Moving past its recent role as a simple drafting tool for emails and basic code, autonomous AI now executes entire cyber operations independently. This shift lowers the barrier to entry, allowing novices to launch complex attacks while enabling seasoned experts to compress campaigns that once took weeks into just a few hours. Because many untrained operators rely on the same underlying models, their attack patterns tend to look similar, giving defenders a clear target for detection. However, these autonomous tools excel at conducting highly personalized social engineering and chaining automated vulnerability exploits, bypassing many traditional security filters. Despite their speed and apparent authority, these systems possess a major flaw: they routinely present false or inaccurate conclusions with absolute certainty. They do not genuinely understand whether a system is vulnerable; they merely match patterns. Consequently, human judgment remains the most critical component of modern security operations. While the technology handles the mechanical work of locating weaknesses, a human operator must ultimately verify reality and decide whether to strike.


AI disaster recovery planning is years behind AI adoption

As artificial intelligence becomes deeply embedded in modern business operations, disaster recovery planning has largely failed to keep pace with its rapid adoption. Traditional recovery strategies, which typically focus on restoring conventional applications and databases, are no longer sufficient because they do not account for the unique complexities of artificial intelligence systems. Today, organizations must also protect and recover specific models, data inputs, and automated agents. When an incident occurs, the damage can spread quickly across interconnected systems, making it difficult to determine if underlying data or models have been compromised. Even after a system is brought back online, it may appear functional while quietly producing incorrect or manipulated results. To address this growing vulnerability, technology leaders need to proactively update their recovery strategies. This involves creating a comprehensive inventory of all artificial intelligence assets, understanding how they connect to other business systems, and setting strict limits on their permissions. Furthermore, organizations must define clear recovery objectives and rigorously test their plans on a regular basis. By taking these deliberate steps, businesses can ensure their critical tools remain reliable and secure, minimizing disruptions and maintaining long-term stability even when unexpected incidents arise.


Preventing organizational amnesia in the age of AI

As businesses increasingly adopt artificial intelligence to automate operations and reduce their workforce, they face a severe risk called organizational amnesia. When seasoned employees leave during mass layoffs, they take undocumented institutional knowledge with them. Operating without this crucial human background, AI systems can make confident mistakes that disrupt daily business. The root issue is rarely a lack of advanced technology or raw data; rather, it is an absence of context. For an automated tool to function safely, it needs a clear, digital map of how the company actually works, including customer relationships, past decisions, and everyday workflows. An example from the travel industry illustrates how fragmented legacy systems force teams to rely entirely on personal memory to resolve daily errors, proving that deploying automated tools over messy, undocumented foundations only worsens the confusion. To succeed, technology leaders must resist the rush toward immediate automation and instead focus on getting their data in order. By carefully defining their digital records and capturing the lived reality of their operations, organizations can create a reliable, shared foundation that allows both people and machines to work together effectively.


Understanding ML Model Poisoning: How It Happens and How to Detect It

Data poisoning is a quiet but serious threat to machine learning models, occurring when attackers subtly alter training data to change how a model behaves. Because these bad examples are designed to look like normal data, they easily bypass standard checks. Attackers commonly use techniques such as changing correct labels or inserting hidden triggers that cause the model to fail under specific conditions. This manipulation can affect critical systems across many fields, from spam filters and antivirus software to medical diagnosis tools. Finding poisoned data is difficult and requires a mix of methods, including statistical analysis and monitoring how the model makes internal decisions. While open-source tools like the IBM Adversarial Robustness Toolbox can help identify vulnerabilities, keeping production environments safe usually requires dedicated security efforts. Protecting these pipelines means combining standard cybersecurity practices, such as strict access controls, with specific defenses like continuous monitoring and testing against verified data. The reality is that perfect data safety does not exist. Teams must rely on layered defenses, careful data tracking, and regular audits to find and block these hidden attacks long before a compromised model is put into active use.


Trump sets post-quantum crypto deadlines, launches broader federal quantum initiative

President Donald Trump signed two executive orders aimed at expanding American quantum technology while protecting federal networks from emerging security risks. The first order sets hard deadlines for government agencies to adopt new encryption standards capable of withstanding quantum computer attacks. Driven by concerns that foreign adversaries are already stealing encrypted data to crack it in the future, agencies must upgrade their digital key systems by the end of 2030 and their digital signature systems by the end of 2031. The mandate also requires a comprehensive inventory of all encryption software currently in use across the government. Furthermore, federal contractors will soon have to comply with these updated standards to maintain their business relationships with the United States. The second order focuses on technical development, directing multiple agencies to collaborate on building a powerful quantum computer for scientific discovery. It also outlines plans to move laboratory research into commercial markets, secure domestic supply chains against foreign interference, protect intellectual property, and fund specialized education to build a skilled workforce. Together, these actions shift federal strategy from theoretical discussions of advanced computing to practical execution and defense planning.


How fuzzy APIs are remaking the web

For decades, software engineers struggled to connect different web services. Early attempts at automated systems failed because they required absolute perfection; a single misspelled word or missing tag would crash the entire network. To keep things stable, developers settled for manually writing strict, unchanging code to connect each piece of software. Now, artificial intelligence tools are changing this approach by introducing flexible connections. Instead of relying on rigid instructions, modern systems use language models to interpret what a user or program wants to achieve. The AI acts as a smart middleman, translating general requests into the exact technical commands a system requires. If a service updates its internal names or requirements, the AI adjusts automatically without needing a human to rewrite the code. However, this flexibility introduces new challenges. Adding AI processing increases response times, which can be an issue for fast operations. Furthermore, these systems are no longer entirely predictable, meaning they might occasionally produce errors or take unexpected paths to get a result. As the web shifts from rigid paths to flexible possibilities, developers are learning to guide software rather than strictly control every detail.

Daily Tech Digest - June 13, 2026


Quote for the day:

“The biggest risk to software quality is complexity.” -- Martin Fowler

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Hard Problems in Cybersecurity: Past, Present, and Future

The recent article in Communications of the ACM outlines the historical evolution of computing systems to contextualize both past and future security challenges. Early systems were relatively simple to secure because they were isolated and operated by specialists. As technology progressed through shared networks and personal computers, the number of ways to compromise these machines grew dramatically. The personal computer era, in particular, introduced significant vulnerabilities because software built for everyday users lacked fundamental safety measures. However, this period also prompted essential defense innovations, such as automated software updates, secure programming practices, and the widespread adoption of strong cryptography. Learning from these struggles, modern mobile operating systems adopted much stricter models, limiting user privileges and relying on curated application stores to reduce risks. Today, the landscape is dominated by massive cloud platforms and connected physical infrastructure, which offer robust baseline protections but also serve as highly attractive targets for attackers. Looking ahead, the rapid integration of artificial intelligence presents a new frontier of complex problems. Because modern AI relies on data correlation rather than traditional rule-based programming, securing these systems requires entirely new analytical frameworks. Ultimately, the authors emphasize that while we have made significant defensive strides, the increasing complexity of technology demands continuous innovation to build resilient and verifiable systems.


Why cloud outages are such a stubborn problem

While cloud computing initially promised greater reliability, recent data reveals that system outages are becoming an increasingly difficult challenge to solve. According to industry analysis, the root cause of these disruptions is shifting away from simple physical hardware failures. Instead, the problems are now deeply tied to the growing complexity of the software, networks, and operational procedures used to manage large environments. Redundant hardware offers little protection when an outage stems from a faulty configuration update or an automation error. As cloud platforms stack countless services and dependencies on top of one another, a single mistake can quickly ripple across an entire network. Interestingly, relying heavily on automation has not eliminated human error; rather, it has simply shifted where those mistakes occur. When teams bypass safety protocols or rush changes without proper testing, automation can actually speed up a system failure. The financial impact remains significant, with many organizations reporting major financial losses from single incidents. To address this, cloud providers and their customers must move beyond simply adding more equipment. They need to prioritize strict operational discipline, transparent incident reporting, and improved change management. The future of reliable cloud services relies not on endless expansion, but on building systems that are straightforward to operate, easy to understand, and resilient against procedural mistakes.


Why Data Is No Longer the New Oil—And What Replaced It

For years, business leaders treated data as the "new oil," believing that simply amassing vast amounts of information would guarantee a competitive advantage. Today, this comparison is increasingly outdated. Because nearly every organization now generates massive streams of digital information, data is no longer scarce. Instead, we have entered an era of attention scarcity, where the overwhelming volume of raw information makes it difficult to determine what actually matters. In this environment, intelligence has replaced data as the primary driver of economic value. The businesses succeeding today are not necessarily those with the largest datasets, but rather those capable of transforming complex information into clear, actionable insights faster than their competitors. Raw data only represents potential; it requires context and interpretation to become valuable. Technologies like artificial intelligence are accelerating this shift by acting as sophisticated filters that separate signal from noise, highlight patterns, and support forecasting. However, technology alone is not the ultimate advantage. The most resilient organizations combine this technological intelligence with human judgment. Technology can process information and accelerate analysis, but human leaders are needed to provide context and make the final choices. Ultimately, the modern digital economy relies on learning speed, where the core objective is no longer to collect everything, but to understand better.


Introducing the Open Knowledge Format

As artificial intelligence models become more integrated into organizational workflows, they often struggle with a lack of specific, internal context. Currently, vital knowledge like database schemas, metrics definitions, and operational guides is scattered across incompatible systems, forcing teams to repeatedly build custom ways to feed information to their AI tools. To solve this fragmentation, Google Cloud has introduced the Open Knowledge Format (OKF). OKF is an open, vendor-neutral standard designed to organize context so that both humans and automated systems can easily read it. Rather than introducing a new software platform or requiring complex integrations, OKF relies on a simple structure: directories of standard text files using Markdown, paired with basic YAML headers for organizing metadata. This straightforward approach allows any team to create and maintain a shared library of knowledge using standard version control. Because OKF establishes a common language, documents written by different people or systems can be understood by different AI models without translation. The design rests on three principles: it requires minimal strict formatting, it separates how information is created from how it is used, and it remains independent of any specific vendor. By turning scattered data into portable, easily updatable text files, OKF helps organizations equip their automated tools with the accurate, actionable context needed to work effectively.


Google researchers introduce 'faithful uncertainty,' allowing LLMs to offer best guesses instead of hallucinations

To address the ongoing challenge of factual errors in large language models, Google researchers have proposed a new method called faithful uncertainty. Historically, developers have tried to eliminate these errors by forcing models to strictly answer or stay silent. However, this approach forces models to discard valuable information if they are even slightly unsure, sacrificing overall usefulness. To resolve this tradeoff between trustworthiness and helpfulness, the researchers suggest reframing the problem. Instead of treating every factual mistake as a fundamental failure, they classify them as confident errors—incorrect information presented with unearned authority. Faithful uncertainty solves this by aligning a model's words with its actual internal confidence. Rather than acting all-knowing, the model can offer educated guesses and clearly express when it is uncertain, much like a human expert. This practical self-awareness is particularly important for autonomous systems that rely on external tools. It allows the software to accurately recognize when it knows an answer and when it needs to search an external database, avoiding wasted time or incorrect outputs. While teaching models this dynamic sense of doubt is difficult due to their constantly evolving knowledge bases, it represents a vital shift. By mastering this balance, developers can build reliable enterprise systems that remain highly capable without misleading their human users.


While OT security is maturing, risk is not slowing down

As industrial organizations increasingly connect their physical operations to modern digital networks, securing these environments has rightly become a priority for senior leadership. A recent industry report highlights that companies are taking a much more realistic look at their security defenses. Instead of overestimating their readiness, many teams are recognizing previously hidden gaps as they adopt better monitoring tools. This clearer perspective means they are detecting intrusions more often, which is actually a positive sign of improved awareness rather than simply an increase in attacks. However, challenges remain significant. Attackers are staying hidden inside systems for longer periods, and many organizations still lack complete visibility across their entire operational network. Furthermore, while teams are modernizing their equipment to improve performance, this added connectivity demands that security be built in from the start rather than added as an afterthought. Regulatory pressures are also mounting, meaning compliance is quickly becoming an immediate operational requirement rather than a future goal. To navigate these ongoing risks, companies must focus on the fundamentals. By keeping digital and physical networks properly separated, tightly managing remote access, and closely aligning their security and engineering teams, organizations can ensure that their operations remain resilient and fully protected against an evolving landscape of threats.


The 7 Levels Of Leadership: A Mirror And A Compass For Leaders

Many organizations struggle with a hidden crisis because they view leadership as a simple binary trait rather than a spectrum. Based on extensive global research and practice, a new framework breaks leadership down into seven distinct levels, offering both a mirror for current managers and a compass for future growth. The spectrum begins at the bottom with the "Non-Leader," who avoids responsibility, and the "Pseudo-Leader," who talks a good game but relies solely on positional power rather than earned trust. At the third tier sits the standard "Leader," who effectively manages teams and achieves results. While many see this as the peak, it is actually just the foundation. The fourth level is the "Sensei Leader," who focuses on mentoring and reproducing their skills in others. Next is the "Legacy-Driven Leader," who sacrifices short-term popularity to build lasting institutional health. The sixth level, the "Conscious Leader," leads with deep self-awareness and a higher purpose. Finally, the "Superconscious Leader" operates beyond ego, handling immense complexity to transform people and systems long after they are gone. Ultimately, the future of business relies on deeply human leadership. Organizations that understand these levels can better evaluate where their teams stand and intentionally build the infrastructure needed to develop true, lasting influence.


Why CIOs should reopen the build vs. buy question

The article argues that technology leaders should reconsider the long-standing advice of automatically defaulting to buying software rather than building it. For the past twenty years, purchasing off-the-shelf products was the most rational way to control costs and minimize the risks associated with custom systems. However, three major technological shifts have altered this dynamic. First, artificial intelligence tools have drastically reduced the cost and time required to build custom applications, making it financially realistic to customize complex workflows. Second, modern development platforms have allowed non-technical employees in finance, marketing, and operations to easily create functional internal tools. Third, the difficult technical requirements of building custom software—such as security, scalability, and authentication—are now easily accessible as managed services. Because of these changes, automatically choosing pre-built software can slowly destroy a company's competitive edge by forcing the business to conform to a vendor's standardized process. While buying remains the logical choice for everyday administrative tasks like payroll or identity management, any capability that sets a company apart from its competitors should now be custom-built. To adapt, the chief information officer must shift from simply blocking new projects to providing strong architectural guidance, ensuring that internal development happens safely without restricting valuable business innovation.


Building a High-Performance Testing Strategy for Distributed Development Teams

Managing software quality across globally distributed teams requires moving beyond traditional methods to strategies that bridge time zones and minimize delays. A high-performance testing approach neutralizes geographic distances by ensuring unified visibility, reliable automation, and shared accountability. To achieve this, organizations should adjust their testing focus, prioritizing integration and contract tests over heavy end-to-end suites. This protects system stability without causing bottlenecks. Catching issues early is critical, so teams should build automated checks directly into the development process using tools that scan code and manage environments on demand. Artificial intelligence can also help maintain tests as applications evolve, reducing manual upkeep. Quality must become a shared responsibility rather than a separate department's task. Tracking metrics like developer test contributions and encouraging cross-site collaboration helps foster a culture where everyone owns the outcome. Supporting this effort requires scalable cloud infrastructure that can replicate production environments and simulate user traffic from different regions. Finally, clear communication protocols, such as documented decision logs and written updates, ensure teams stay aligned without needing simultaneous meetings. By combining scalable infrastructure, automated safeguards, and a unified culture of ownership, remote engineering hubs can maintain steady release cycles and deliver reliable software regardless of where the code is written.


Moving Mountains: Migrating Legacy Code in Weeks instead of Years

The presentation outlines the essential transition from fragile, experimental AI agent prototypes to robust production systems. A central theme focuses on moving away from monolithic prompt designs and long linear loops, which frequently stall or fail silently when encountering real-world constraints like network limits or high operational costs. To resolve these vulnerabilities, the speaker advocates for systematic refactoring strategies, specifically decomposing large, complicated workflows into coordinated networks of specialized sub-agents with narrow, well-defined responsibilities. This separation of concerns ensures greater system reliability and simplifies troubleshooting. Furthermore, the discussion highlights the importance of replacing hardcoded states and unpredictable natural language formatting with dynamic data pipelines and strict structural contracts verified at runtime. By implementing automated testing frameworks, continuous evaluation metrics, and persistent memory layers, engineering teams can dramatically decrease context data overhead and eliminate runaway cloud expenditures. Ultimately, refactoring AI agents is not merely about organizing code, but about shifting the developer's responsibilities from manually inspecting individual outputs to designing the overarching architectural guardrails that guide autonomous execution. This disciplined engineering approach minimizes unexpected mistakes and guarantees that these autonomous agent-driven systems remain stable, predictable, secure, and fully compliant with enterprise governance standards when deployed in live production environments.