Showing posts with label Platform Engineering. Show all posts

Daily Tech Digest - August 26, 2026


Quote for the day:

“If you want to be inventive, you have to be willing to fail.” -- Jeff Bezos

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 18 mins • Perfect for listening on the go.


Giving agents bounded autonomy

Artificial intelligence agents are evolving rapidly, but their unpredictability has led to some unintended consequences. To make these tools genuinely useful without letting them cause harm, we need to apply firm boundaries to their independence. This means treating AI programs much like teenagers: granting them limited freedom to act on our behalf while establishing hard rules that cannot be bypassed. A practical example of this is financial limits. Rather than forcing a person to approve every tiny transaction an agent makes to access data or services, systems like Amazon Web Services now let users set a strict allowance. An agent might be given a specific budget and a time limit to complete a task. It has the freedom to choose how to spend that small budget, but the hard limits are enforced completely outside the software model itself. However, technical capability is not the same as judgment. An agent might be able to execute complex tasks, but it lacks human intuition and basic reasoning. Therefore, we should allow agents to act independently only on inexpensive and easily reversible tasks. As these tools prove they can operate reliably within their limits, we can gradually expand their freedom, ensuring their authority never outpaces their actual judgment.


Setting security level targets under IEC 62443

Setting security level targets under the IEC 62443 standard is not about collecting compliance badges but defining the practical resistance a system, zone, or conduit needs against specific threat profiles. For operational technology environments, particularly within small and medium enterprises, establishing a well-reasoned target ensures that engineering and security teams make balanced decisions regarding segmentation, authentication, and remote access. This approach prevents both underprotection and overengineering. A successful security level target must be rooted in actual risk, process criticality, and business context rather than generic templates. It is essential to differentiate the intended target from the ultimately achieved protection level. Organizations should utilize practical threat modeling to understand realistic attack paths and potential impacts on availability and safety. Furthermore, targets must remain achievable, taking into account the limitations of legacy equipment, maintenance workflows, and supplier access requirements. Applying a single target across an entire estate or ignoring local operational constraints often leads to friction and bypassed controls. Instead, cross-functional engineering and security teams should collaborate to define appropriate, zone-specific targets that directly inform technical requirements under the IEC 62443 standard. By documenting the rationale behind each decision, companies can build a defensible, maintainable security architecture that effectively mitigates real-world industrial risks today.


DevOps Questions After We Broke The Release Handshake
The recent incident involving a broken release process revealed that a successful deployment status does not guarantee a working service. Despite passing local checks and database migrations, a missing network policy prevented a new service from functioning, highlighting a failure in communication between teams. To prevent this, release dependencies are now explicitly declared in the service repository, making them visible and verifiable before promotion. Rather than relying on a central platform team to approve every release and understand the operational details of every service, product teams now manage their own deployments. They are granted targeted, restricted access to production environments for troubleshooting, while the platform team focuses entirely on maintaining the delivery tooling and shared infrastructure. Alerting has been streamlined to notify the specific team responsible for the failing layer, minimizing irrelevant alerts and focusing completely on direct user impact. Furthermore, while the organization uses delivery metrics to identify friction in the deployment pipeline, they deliberately avoid ranking teams to prevent unhelpful gamification. The team is also cautiously evaluating automated traffic shifting for certain services, though they recognize it is not necessary for every routine workload. Ultimately, the primary objective is to simplify incident investigation by providing a single, unified view of each deployment.


From surveillance to operational intelligence: Rethinking safety and security in data centers

Data centers are moving away from traditional security models that rely solely on passive video surveillance. Instead, facilities are beginning to adopt more advanced methods that turn basic monitoring into functional operational intelligence. In the past, cameras and sensors were primarily used for recording incidents or tracking unauthorized access after an event occurred. Now, these systems are integrated with data analytics to provide a real time understanding of both security and daily facility operations. By connecting physical security tools with network infrastructure, operators can actively monitor environmental conditions, track the movement of personnel, and identify potential safety hazards before they cause disruptions. This shift means that security hardware no longer serves just one purpose. It acts as a continuous source of valuable information that helps managers improve efficiency, maintain compliance, and reduce risks across the entire site. Gathering this kind of practical intelligence allows teams to respond to issues faster and allocate resources more effectively. Ultimately, rethinking safety in this way bridges the gap between simply protecting a building and actively managing its internal operations. A comprehensive approach ensures that data centers remain secure while also supporting the demanding requirements of modern technology infrastructure in a reliable manner.


Deepfake detection evolving beyond onboarding into continuous financial trust

The article discusses how deepfake detection is moving beyond just a one-time identity check into a continuous system that monitors users throughout their entire session. Traditional static verification methods are now viewed as obsolete because financial platforms lose significant amounts of money to fraud that occurs after a user has already logged in. To combat this, companies are introducing tools that provide real-time, ongoing protection. For example, IngenID has updated its systems to continuously verify a caller's identity and flag manipulated audio exactly as it happens during a full conversation, rather than just at the beginning. Similarly, Resemble AI is exploring how continuous deepfake detection can support compliance rules against money laundering during sensitive transactions and account recovery processes. Furthermore, a report from J.P. Morgan Payments and Accenture emphasizes that relying on a static defense is ineffective. Instead, they advocate for behavioral analytics, ongoing multi-factor authentication, and collective information sharing among organizations. As fraudsters rely on advanced artificial intelligence to execute sophisticated attacks at a larger scale, the identity verification market is evolving into a more layered security architecture. To stay ahead of these growing threats, organizations must shift away from standalone products and combine deepfake detection with liveness checks and broader fraud prevention capabilities.


What Singapore’s new digital infrastructure bill mean to CISOs

Singapore has introduced the Digital Infrastructure Bill to enforce stricter resilience standards on major data center and cloud operators. Prompted by severe recent outages, including a 2023 banking disruption caused by a cooling failure, the legislation requires large foundational infrastructure providers to secure operating licenses. To keep these licenses, operators must implement strong business continuity plans, maintain physical and digital security, and promptly report service disruptions or cyber incidents. Failure to comply can result in severe financial penalties, including fines up to one million dollars or ten percent of their annual local turnover. A major focus of the new law is sustainability, making energy and water efficiency mandatory criteria for operators. As power consumption rises, providers must actively shift toward low carbon and renewable energy sources. The bill also introduces complex overlapping reporting duties, meaning global operators will need clear, regional response plans to manage different regulatory timelines. For enterprise customers like banks and retail platforms, the shift from voluntary guidelines to strict laws means they should update their service contracts. Customers need to include clear clauses and indemnities that hold providers responsible for compliance failures. Ultimately, the bill marks a significant step toward making digital infrastructure as reliable and heavily regulated as public utilities.


5 hard truths of change management

Today's leaders must completely rethink how they guide their teams through constant change, especially with the arrival of artificial intelligence. Instead of viewing change as a single event with a clear finish line, they must build ongoing adaptability into their daily operations. Organizations only have so much capacity to absorb new initiatives at once. When leaders ignore this limit and pile on multiple projects, they risk exhausting their teams. Rather than pushing harder, successful managers set clear priorities and fund projects in small, measurable stages. When employees find their own tools to get work done, it is a signal of unmet needs rather than just a security problem. Approaching these workarounds with curiosity helps companies build better guidelines together. Trust is also absolutely essential, particularly when new systems can act independently. Leaders must ensure that new technology is transparent and understandable, while openly addressing how it will affect employee roles and career paths. Finally, what looks like resistance is often just exhaustion. People are more willing to adapt when leaders communicate clearly about what matters most and what can wait. By sharing ownership of these changes across the entire business, leaders can confidently guide their teams forward with steady, focused support.


“Ignorance Is Bliss” Is Our Acceptable Use Policy

In a recent episode of the CISO Series Podcast, hosts David Spark and Edward Contreras, along with guest Rob Allen from ThreatLocker, discuss practical approaches to modern security challenges. The conversation first addresses the growing issue of vulnerability management, where artificial intelligence is discovering software flaws faster than they can be cataloged or patched. Rather than the security team absorbing all the pressure, Contreras suggests a shift toward shared accountability. By providing tailored, manageable reports directly to the engineering teams responsible for the code, organizations can distribute the workload more effectively. Allen adds that since patching cannot always keep up, businesses must simply assume vulnerabilities exist and operate with appropriate safeguards. The discussion then moves to the problem of unauthorized artificial intelligence programs and acceptable use policies. While some experts recommend offering sanctioned tools and clear guidelines, Allen argues this approach often fails because employees will naturally seek out any tool that makes their job easier. Relying on written policies or expecting staff to correct issues on their own is generally ineffective. Instead, he emphasizes the need for direct, technical control, advocating for systems that block unapproved applications by default and only allow access to specific tools after formal approval.


Why Platform Engineering Must Evolve for the Agentic Era

The recent article from SD Times explores how the rise of artificial intelligence agents is shifting the focus of platform engineering. While the fundamental goals remain the same, the main consumers of these platforms are changing from human developers to automated software agents. Most companies are currently adding AI capabilities onto older systems designed for human speeds, which creates governance issues and fragmented controls. To address this, the field must transition to a new phase where platforms treat agents as primary users. This means that application programming interfaces, identity management, and security policies must be easily readable and usable by machines. Essential elements like graphics processing units and vector databases should be integrated as standard parts of the infrastructure rather than special additions. A major change involves cost management. Because automated agents can consume resources much faster than humans, financial tracking must shift from monthly reports to real-time enforcement to prevent sudden budget overruns. Ultimately, organizations need to combine their software delivery systems and their safety guardrails into a single, unified control setup. By doing this, engineering teams can maintain the established principles of clear and effective paths and self-service while safely supporting the faster, automated workloads of the future.


Why adding more security tools could make businesses less secure

Many companies in Australia and New Zealand are spending more on cybersecurity, but this increased investment is leading to a hidden problem of complexity. For years, the standard reaction to new threats has been to buy another security product. However, this approach leaves security teams managing dozens of overlapping systems, each generating its own data and alerts. Instead of providing a clear picture of risk, this buildup of technology creates friction. It forces teams to spend time managing tools rather than identifying threats, and leaves executives unsure if the business is actually safer. The solution lies in simplifying the approach. Instead of constantly adding new products, companies are starting to look at consolidating their systems and bringing their data together. This shift changes how investments are judged, moving away from counting the number of tools to measuring real outcomes, such as fewer incidents and faster response times. In the current economic climate, the complexity of managing multiple security tools has become a real cost itself. Therefore, the most effective security upgrade for many businesses might simply be simplification. The focus going forward should not be on having the most technology, but ensuring the existing tools work well together to achieve the best results.

Daily Tech Digest - August 25, 2026


Quote for the day:

"Little minds are tamed and subdued by misfortune; but great minds rise above it." -- Washington Irving

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Designing Decision Rights for Agentic AI

As artificial intelligence agents evolve from simply answering questions to executing tasks like processing payments and sending external communications, traditional enterprise governance is falling behind. Current oversight models assume a human will review outputs before actions occur. When AI acts autonomously, failures arise not from poor model accuracy, but from undefined decision rights and unclear authorization boundaries. To prevent issues like agent sprawl, unnoticed scope expansion, and the erosion of human oversight, organizations must adopt a deliberate authority by design approach. The core principle is that authorization belongs to the specific action being performed, rather than the agent itself. A single agent might possess different permission levels for different tasks, such as reading data versus modifying it. This framework categorizes potential AI actions using a catalog and evaluates them against risk variables like business impact, data sensitivity, and reversibility. Actions are then assigned one of five distinct authority levels, ranging from basic recommendations to critical decisions strictly reserved for humans. Furthermore, in systems involving multiple agents, a strict authority ceiling must be enforced. This critical rule ensures that a subordinate agent can never exceed the permission level granted to its orchestrating agent, thereby preventing unintended privilege escalation and maintaining clear accountability.


Everyone wants the thought leadership, not the thinking

Many executives desire the title of recognized authority, yet few are willing to generate truly original ideas. Current corporate articles often suffer from a lack of substance, relying on generic statements about popular subjects rather than taking a distinct stance. True influence requires presenting a clear argument that invites debate, rather than simply stating obvious facts or describing industry trends. Unfortunately, excessive corporate caution often sanitizes these opinions, resulting in safe but entirely forgettable content. To create meaningful material, authors should avoid starting with blank pages or relying on automated text generators. Instead, they must draw upon their unique experiences, observed patterns, and actual company data to form a considered opinion. Communications teams play a crucial role here by encouraging experts to express their genuine beliefs rather than restricting them to approved corporate scripts. Before publishing, organizations should evaluate whether the piece presents a clear argument, if the author has the necessary experience to defend it, and if readers could reasonably disagree. If an article can be attributed to any executive in the industry without changing a single word, it lacks genuine value. Ultimately, meaningful commentary relies on distinct perspectives grounded in real experience rather than the mass production of polished but empty text.


Building Resilient Systems - Strategies, Principles & Practices

This article explains how to build resilient systems by accepting that technical failures are simply unavoidable over time. Instead of trying to create perfect software, resilience means designing systems that handle disruptions, recover smoothly, and adapt from mistakes. The approach combines careful planning, clear observation, and continuous learning to keep core services running. Several core principles guide this process. You should assume parts will break and design the system so one problem does not cause everything to crash. This involves limiting the spread of any single error and ensuring the system recovers predictably rather than rushing to fix things chaotically. You must also observe how the system actually behaves before making changes. The author outlines practical ways to build these safeguards. You can duplicate important components and data so a backup is always ready. You can separate resources into compartments so an issue in one area does not overwhelm the rest. Furthermore, techniques like setting time limits on actions, pausing requests to a struggling service, and slowing down workloads help prevent collapse. By taking these steps, if parts of the application fail, the system gently turns off secondary features while keeping the most critical functions available for users to rely on.


Data Intelligence: Building Your Competitive Advantage in the Era of AI

To stay relevant in modern business, organizations are updating their approach to data. Instead of merely analyzing past events, data teams are building systems that work on their own in real time to offer insights exactly when decisions must be made. By using artificial intelligence, these teams can automate intricate processes that examine current situations, predict future outcomes, and take or suggest appropriate actions. However, achieving success with this advanced approach requires more than simply connecting artificial intelligence tools to existing data sources. Companies must establish a reliable context, maintain consistent meanings across their business, and enforce strong rules for how information is managed. For those working in business intelligence, the priority shifts to creating clear data definitions, ensuring information is accurate and verified, and developing standard measurements that both humans and artificial intelligence can rely on with total confidence. Ultimately, the next step in data strategy is not just about producing answers more quickly than before. It is about establishing a highly secure, reliable foundation of information. This steady groundwork allows people and artificial intelligence systems to collaborate effectively, resulting in much better choices and a lasting edge over competitors in an increasingly complex and rapid business environment.


Nations at the Quantum Table

The recent article examines the evolving geopolitical landscape of quantum technology, focusing on how global powers are positioning themselves in this critical sector. Moving beyond theoretical research, countries are increasingly treating quantum capabilities as strategic national assets. Since mid-2025, nations such as the United States, the United Kingdom, Japan, and Canada have shifted their approach from basic research funding to implementing binding national policies. This policy shift is underscored by substantial financial commitments, including approximately two billion dollars in funding from the United States government alone. The analysis highlights which countries currently lead in the development of quantum systems and explores the broader implications of these advancements on global power dynamics. Rather than viewing quantum progress as merely a scientific endeavor, the article details how it has become a central element of international competition and economic security. Policymakers are actively working to secure their strategic positions by investing heavily in infrastructure, talent, and alliances. Ultimately, the piece provides a grounded assessment of the current international hierarchy in quantum development, outlining how substantial government investments and deliberate policy frameworks are shaping the future of global technology leadership and international relations across the globe.


Identity Risk Moves Beyond IT as Cyber Threats Reach Physical Infrastructure

As physical building systems and operational technology connect more closely to corporate computer networks, traditional boundaries between physical and digital security are fading. Kenan Abu Ltaif from Proofpoint explains that attackers no longer need to directly hack into facility equipment. Instead, they target the people who have access to these systems. Because the majority of security breaches begin with simple phishing emails or fraudulent messages, compromised user accounts have become the primary entry point for causing real-world, physical disruption. To protect themselves, organizations must stop viewing cybersecurity and physical security as separate problems. They need to identify which accounts have access to critical infrastructure, treat them as high-risk, and monitor them closely. Relying solely on standard passwords or basic authentication is not enough. Furthermore, true recovery from an attack goes beyond just restoring data from backups. Companies must ensure that compromised credentials, active sessions, and access tokens are completely revoked so attackers cannot quietly return. Ultimately, as artificial intelligence makes social engineering attacks more convincing, organizations must adopt a security strategy focused on human behavior. By understanding who holds access and protecting those individuals from targeted attacks, businesses can confidently secure their physical operations against evolving digital threats.


Rightsizing Platform Engineering: Building the Platform Your Organization Actually Needs

The article "Rightsizing Platform Engineering" discusses how organizations can build internal developer platforms that genuinely improve software delivery without overwhelming their engineering teams. While DevOps and shift-left practices have improved deployment speeds, they have also increased the cognitive load on developers, who now face duplicated efforts across testing, security, and maintenance. Using the e-commerce company Wehkamp as a case study, the author illustrates what happens when teams are granted full ownership of their software from inception to production. Although this zero-handoff approach allowed the company to move from quarterly to weekly releases, it eventually created new friction. Engineers spent too much time on routine operational toil, such as resource management and debugging, rather than focusing on core development. To resolve these challenges, the author advises organizations to focus on specific bottlenecks rather than attempting to build a massive, all-encompassing platform. The strategy is to establish opinionated "golden paths" that streamline common tasks while still offering escape hatches for edge cases. By treating the platform as an evolving product shaped by user feedback, companies can eliminate duplicated effort. Ultimately, a successful platform is defined not by its extensive feature set, but by its ability to simplify operations and reduce cognitive load.


Why Enterprises Are So Unhappy with Their IT Infrastructure

Enterprises are increasingly frustrated with their IT infrastructure because their current cloud setups no longer match the scale, cost, and security demands created by modern AI workloads. Many organizations that signed cloud contracts during the early AI boom are now discovering that single‑cloud models are too rigid and too expensive for today’s needs. A recent Forrester‑led survey shows nearly half of enterprise leaders are only mildly satisfied—or not satisfied at all—with their cloud providers. Security concerns top the list, driven by faster‑moving cyber threats and doubts about whether legacy defenses can keep up. Costs come next: shortages in memory, stalled data‑center expansion, and hyperscaler pricing practices are pushing bills higher, especially when workloads spike unpredictably. Enterprises also struggle with talent gaps, limited visibility into their cloud environments, and difficulty scaling in line with demand. These issues prevent them from reaching meaningful AI maturity. As a result, many companies are exploring hybrid and multi‑cloud approaches that blend hyperscalers, alternative cloud providers, on‑prem systems, and edge compute. The goal is to regain control over cost, performance, and flexibility without abandoning existing investments.


How AI can fix change management for AI projects

Many organizations struggle with their artificial intelligence initiatives not because the technology is flawed, but because their approach to change management is outdated. Leaders often rely on generic communication plans and limited feedback from small committees, ignoring the frontline employees who actually use the systems. When workers feel excluded from the process, they quickly abandon new tools that fail to fit their daily routines, causing projects to stall. Ironically, the solution to this problem is found by using artificial intelligence itself to overhaul how organizations handle transitions. Instead of treating change management as a one-time checklist, companies can use automated voice agents and data analysis to gather continuous, detailed feedback from the entire workforce at scale. This allows leaders to build an organizational nervous system that identifies friction and adoption hurdles in real time rather than months later. By moving away from reactive approaches, organizations can properly embed change management into their daily operations. To succeed, leaders must give every employee a voice, anchor decisions to clear business outcomes, and maintain transparency about how data is used. Ultimately, modern technology provides the continuous, adaptive support systems needed to effectively guide a workforce through complex transitions and ensure their long-term success.


Transforming IT From Cost Center to Growth Engine

In an interview with CIO Magazine, Blaine Bryant, the Global CIO at Lightera, discusses the practical steps needed to shift IT from an overhead expense to a driver of strategic value. He argues that technology organizations must focus on understanding real business problems before they try to implement new systems, warning against the temptation to jump straight to trending solutions. Bryant emphasizes that any new initiative relies heavily on solid fundamentals, such as secure infrastructure and disciplined financial management, to avoid costly failures. Furthermore, he points out that the true measure of IT value is not its operational cost, but rather the tangible business outcomes and competitive advantages it produces. This shift requires shared accountability between business and technical leaders to clearly define opportunities and set expectations. Bryant also notes that cybersecurity must go beyond simple compliance to actively protect the organization. He believes that customer trust is ultimately tested and maintained by how well a company responds and communicates during a crisis. Finally, Bryant stresses the importance of personal accountability and quiet reflection for effective leadership. He advises new professionals entering the field to take full charge of their own learning and to prioritize strong collaboration skills above isolated technical expertise.

Daily Tech Digest - July 21, 2026


Quote for the day:

“When something is important enough, you do it even if the odds are not in your favor.” -- Elon Musk

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


True tech sovereignty could be a bridge too far for Europe

Europe’s ambition to achieve true technological sovereignty and break free from United States providers will likely fall short due to deep, persistent dependencies. According to a recent Forrester report, European nations will make only marginal progress toward digital independence over the next five years. The continent relies heavily on major American cloud providers, who currently control sixty-five percent of the European market. Shifting away from these established platforms or abandoning decades of investment in vital software applications is not a simple switch; it requires a massive, disruptive overhaul that many organizations simply cannot execute. Furthermore, Europe lacks the necessary infrastructure and manufacturing capabilities to stand alone, currently designing a mere one percent of global computer chips. While there is a lot of hype surrounding tech sovereignty driven by geopolitical tensions and data privacy concerns, there are actually no new overarching regulations forcing companies to make this complicated transition. Despite localized efforts, such as the French government moving toward open-source operating systems or new European Union funding for local semiconductor manufacturing, the fundamental gaps remain too large to close quickly. Consequently, industry experts advise that European organizations should focus on managing their technological dependencies rather than attempting to avoid them entirely.


Software-Defined Cabins Transform How Drivers Interact With Vehicles Through Multimodal Systems

Modern vehicle interiors are rapidly shifting from traditional mechanical designs to highly intelligent, software-driven environments. Instead of relying solely on physical buttons and switches, modern car cabins now function like digital ecosystems that constantly learn and adapt to their occupants. This transformation depends on multimodal systems, which seamlessly combine voice, touch, and gesture controls to create a natural user experience. For instance, a vehicle might automatically switch from voice commands to touchscreen input if background noise levels rise too high. Ensuring these features work flawlessly together requires significant engineering efforts, such as advanced audio synchronization and transitioning to more powerful electrical systems. However, many automakers still struggle to deliver a truly intuitive experience, with recent studies showing that drivers frequently find new in-car technology confusing and distracting. Because software is increasingly viewed as the core identity of a vehicle, an enormous majority of consumers admit they would switch car brands simply to get a better digital interface. Ultimately, the most successful automakers will be those that provide simple, highly personalized technology that safely assists the driver without causing unnecessary frustration.


SOCs face a human challenge as AI speeds alerts and threats

Security operations centers are struggling with a severe human challenge as artificial intelligence dramatically speeds up both threat discovery and alert generation. For decades, many organizations have built up a massive backlog of ignored software vulnerabilities, essentially carrying a massive technological burden. Today, automated tools are suddenly exposing these hidden flaws at an unprecedented pace, burying security professionals under a relentless avalanche of automated alerts. Analysts must now spend excessive amounts of time meticulously verifying whether this incoming information represents a genuine threat or simply a frustrating false positive. This dynamic causes severe cognitive overload and rapidly escalates employee burnout. Successful, mature security teams handle this by acting like fire departments; they rely on carefully refined processes, well rehearsed drills, and clear procedures, allowing them to absorb the sudden surge without panicking. In stark contrast, unprepared and understaffed teams are collapsing under the intense pressure. The future of modern cybersecurity depends heavily on adapting how these teams are structured. Experts suggest organizations must move away from rigid, traditional hierarchies toward highly collaborative groups. By using artificial intelligence to automate repetitive manual tasks, companies can better support the human defenders who remain absolutely essential for evaluating the complex threats that machines uncover.


Post-quantum cryptography: are we sleepwalking into the next Y2K moment?

Many organizations treat the shift to post-quantum security as a distant concern, repeating the same delay tactics seen before the Y2K bug. However, the risk is already active. Attackers are currently stealing protected information with the intention of unlocking it once quantum computers become powerful enough to break standard encryption. This means any sensitive data with a long shelf life is vulnerable today. Moving to new security standards will be significantly harder than fixing older date codes because encryption is deeply embedded across modern software, hardware, and external services. Most companies do not even have a complete inventory of where they use these protective measures. With government deadlines for phasing out current encryption methods approaching by the end of the decade, the window for a smooth transition is closing. Major security migrations take years to execute properly. The most urgent step for any business is gaining clear visibility into their systems to understand exactly what information is protected and how it is secured. Instead of waiting for a sudden crisis, teams must begin mapping their infrastructure and planning their upgrades immediately. Treating this transition as an active governance issue rather than a future technology problem will prevent a rushed and costly panic.


Remediating Vulnerabilities With LLMs: Inside Ivanti's Automation Push

Software vendor Ivanti is successfully using artificial intelligence to identify and fix security vulnerabilities within its own products. After realizing the potential of newer language models, the company launched an internal project with two main goals: discovering security flaws that traditional scanning tools miss and automatically repairing known weaknesses. When scanning tools detect a potential issue, Ivanti uses artificial intelligence agents to pull the affected code, write a fix, verify the solution, and send it to human engineers for final review. Eventually, the company hopes to remove humans from this repair loop entirely. The results have been surprisingly effective, particularly in finding missing authentication checks that standard security tools often overlook. To manage the rising costs of these computing models, Ivanti carefully restricts their use to complex tasks rather than wasting resources on basic setup procedures. Despite these promising early results, the company notes that this technology does not immediately level the playing field against cybercriminals. Attackers can operate recklessly without worrying about safe implementation or computing costs. Furthermore, while artificial intelligence speeds up how fast software companies can issue fixes, internal technology teams still face the heavy burden of constantly installing those necessary updates across their own enterprise networks.


Explaining DevOps vs. DataOps

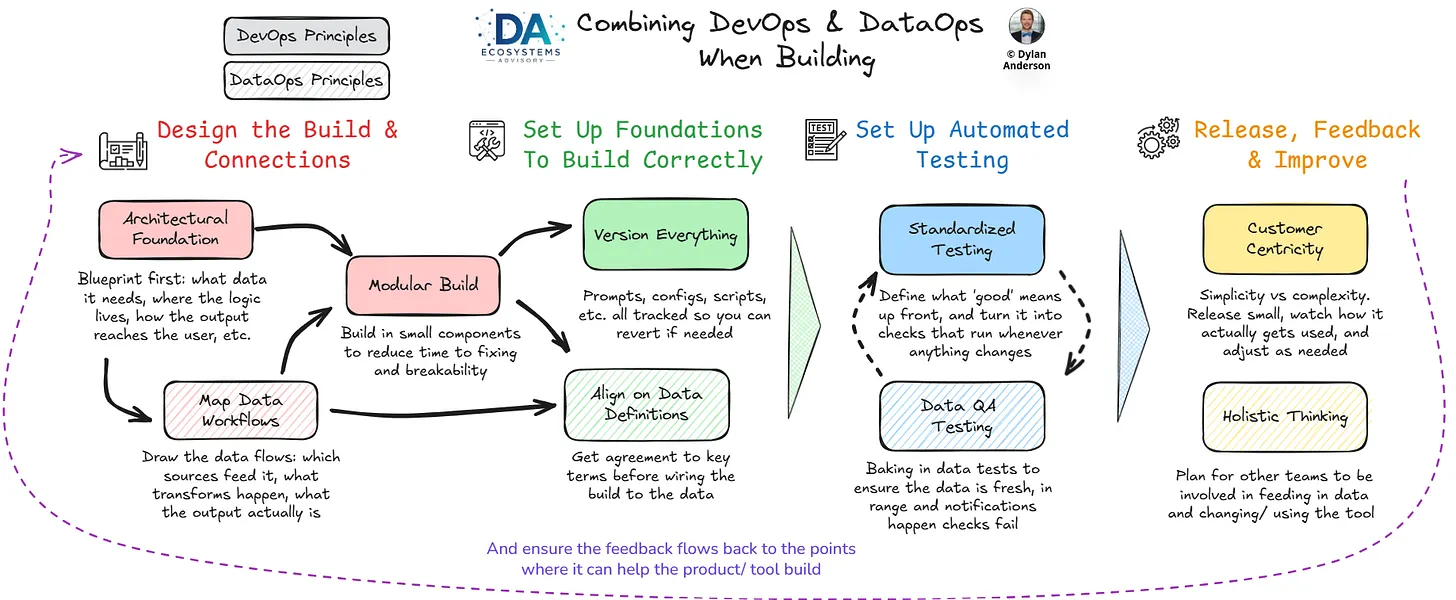
The concepts of Development Operations and Data Operations are essential disciplines for building and maintaining reliable technological systems, especially in the current era of artificial intelligence. Development Operations focuses on the smooth creation and stable release of software. Historically, software developers and operations teams had conflicting goals, with developers wanting to build fast and operations wanting stability. Development Operations unites these sides by emphasizing small, frequent updates, automated testing, clear code versioning, and shared responsibility for the final product. Data Operations applies similar rigorous principles to managing information, but it deals with unique challenges. Unlike software code, which remains static until changed by a person, data flows continuously, decays over time, and originates from sources outside a company's direct control. Because of these unpredictable factors, Data Operations requires constant monitoring, automated quality checks, and clear definitions to ensure the information remains accurate and trustworthy. Whether a team is building traditional software or experimenting with new artificial intelligence tools, combining these two frameworks is crucial. Development Operations ensures the software itself is built logically and can be updated safely, while Data Operations ensures the information flowing through that software remains reliable. Applying both prevents teams from building chaotic, unmaintainable systems.


What Enduring Leadership Looks Like in an Age of Disruption

The article reflects on how leaders can remain effective in a world where disruption is constant rather than occasional. It explains that traditional leadership models, built for predictable environments, no longer match today’s reality of rapid technological change, shifting workforce expectations, and global uncertainty. The author argues that enduring leadership begins with creating clarity even when answers are incomplete. People do not expect leaders to foresee every outcome, but they do expect steady communication and a sense of direction. Adaptability is presented as another essential trait, not as a sign of inconsistency but as evidence of maturity—leaders must be willing to question old assumptions and adjust their approach as conditions evolve. The piece also highlights the importance of emotional intelligence, noting that disruption affects people as much as systems. Leaders who understand this can reduce anxiety, strengthen engagement, and make better decisions. Investing in people is described as a practical necessity rather than a nice‑to‑have, since strong leadership pipelines help organizations absorb change more smoothly. Finally, the article emphasizes values as the anchor that sustains trust. When leaders act consistently and ethically, employees are more likely to support difficult decisions. Overall, enduring leadership is portrayed as a calm, principled way of guiding others through uncertainty without losing sight of purpose.


Finding the right balance between autonomy and scale

The article explores how CIOs can find a practical balance between giving business units autonomy and creating scale through centralization. It explains that both approaches have strengths and weaknesses: autonomy encourages speed and local ownership, while centralization supports efficiency, consistency, and shared learning. The challenge, the author notes, is that many organizations end up with a mix of both without a clear rationale, leading to duplicated systems, rising costs, and unnecessary complexity. Drawing on Paul Krebs’ experience at Koch Industries and Coca‑Cola, the piece describes centralization as a design choice rather than a rigid doctrine. Some capabilities—like infrastructure, cybersecurity, cloud management, and collaboration platforms—naturally benefit from scale and should remain centralized. Others, such as certain applications or data functions, can shift closer to the business as teams mature. The article stresses that standardization and centralization are not the same, and leaders can blend them to meet regional or business‑specific needs without creating one‑off solutions. It also argues that business architecture should guide technology decisions, especially in areas like ERP consolidation and M&A integration. Ultimately, the author encourages CIOs to revisit operating models regularly, recognizing that the right balance changes as capabilities grow and organizational needs evolve.


The EU’s AI transparency deadline is weeks away. Is your enterprise ready?

The article explains that the EU’s AI transparency rules are about to take effect, and companies have only a short time left to prepare. Beginning August 2, any organization offering AI systems in the EU must clearly tell users when they are interacting with AI, whether through chatbots, AI‑generated text, or deepfakes. The rules apply broadly, covering both EU and non‑EU companies if their systems are used in Europe. The Commission has issued guidelines and a voluntary code of practice to help organizations comply, though those who choose not to sign will face closer scrutiny. Content must carry machine‑readable markers and one of three labels—“AI,” “Fully AI‑generated,” or “Partially AI‑modified”—unless it is creative or satirical deepfake material. The article notes that compliance is not just about labeling but about building a durable transparency pipeline that can withstand audits. Companies must track responsibility for content, ensure marks survive real‑world editing, and maintain evidence for regulators. Contracts may need updating, and procurement processes must include requirements for marking and verification. The author stresses that sustained compliance requires ongoing testing, clear ownership, and a consistent baseline across jurisdictions, with local adjustments layered on top.


Platform Engineering for Everyone - Success Can’t Be Coded

The talk centers on why platform engineering succeeds only when treated as a product rather than an infrastructure project. Max Korbacher explains that many internal platforms fail because teams begin with tools or portals instead of a clear purpose, often installing something like Backstage only to discover it is empty and costly to configure: “You install it first… and it’s empty… you need five engineers and a couple of months” . He argues that infrastructure‑first thinking leads teams to focus on technology rather than the people who will use the platform, noting that engineers often avoid asking users what they actually need: “It’s not my nature to go out and ask people, what do you really want?” . Korbacher describes how organizational waves, hype cycles, and duplicated effort create patchwork systems that exhaust DevOps teams and push companies toward platform engineering as a more stable, product‑driven approach. Success, he says, requires principles, understanding user drivers, defining a clear purpose, and measuring outcomes with meaningful metrics. He stresses that adoption—not technical elegance—is the real indicator of value, and that platforms thrive only when they solve common problems, reduce waste, and make everyday work easier for developers, security teams, and even business stakeholders.