Showing posts with label ai roi. Show all posts

Daily Tech Digest - October 05, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale


Data Has No Passport: Why Global Privacy Governance Must Catch Up With AI

At the CruiseCon Privacy and AI 2026 event, Accenture privacy lead Adriana Antunes Winkler highlighted a growing challenge: while data moves globally and instantly, privacy regulations remain fragmented and bound by local jurisdictions. With around eighty percent of the world covered by varying data protection frameworks, companies often struggle to keep up. Winkler advised against building separate privacy programs for every new law, as this causes confusion and conflict. Instead, she recommended a strategy built on a common global foundation with specific local adjustments only where legally necessary. This prevents the burden of simply applying the strictest rules everywhere. Winkler emphasized that operational controls, not just written policies, are what actually protect privacy. These controls require clear ownership, testing, and proof of function. The rise of artificial intelligence complicates this further, as AI often infers new personal details rather than just storing collected information. She suggested focusing on the specific actions AI takes and the systems it accesses, treating it as a data map driven by actions. Ultimately, whether data crosses international borders, runs through AI systems, or eventually processes in orbital satellites, organizations must rely on a unified, adaptable governance system that manages common standards while addressing specific local requirements.


Crypto-Agility Distrust Readiness

When major internet authorities decide to stop trusting a flawed digital certificate, the resulting fallout can cripple the countless services relying on it. While technical bodies like browser developers excel at making the call to pull a failing root certificate, there is currently no coordinated national plan for what happens to the broader economy the morning after. Historically, isolated incidents have been contained, but the dual threats of rapidly advancing artificial intelligence and a forced timeline for quantum-safe encryption mean that widespread disruptions are becoming more likely. The blast radius of a sudden distrust event can vary wildly across different sectors, and responding effectively requires advance preparation rather than improvisation. To survive this accelerating risk, organizations must create reliable certificate inventories, designate clear response liaisons, and run tabletop exercises to test their readiness. On a larger scale, a designated national coordinator is urgently needed to connect technical decision-makers with the sectors facing the consequences. Ultimately, building true resilience requires organizations to eliminate single points of trust by adopting multiple issuing authorities and automating certificate lifecycles, ensuring they can pivot smoothly when a crisis hits instead of scrambling to rebuild.


Measuring AI With the Wrong Ruler

When evaluating artificial intelligence systems, getting caught up in grand labels distracts from what truly matters: reliability, cost, and fitness for the job. The technology industry often assumes that larger, more capable models are inherently better, but deploying a massive system for a straightforward task is wasteful and risky. It is very similar to dropping a race car engine into a riding lawnmower. Raw power without proper control or necessity only creates hazards. Instead of obsessing over raw machine intelligence, which mirrors our flawed fixation on human IQ scores, we should focus on building operational wisdom. This means designing tools that clearly understand context, respect their own boundaries, and know exactly when to seek human intervention. Historical missteps in automotive software, where complex features completely overwhelmed inadequate hardware, prove that mismatched computing power leads to frustrating failures for end users. To make better decisions, organizations need a practical measurement framework that strictly aligns system complexity with the actual criticality of the task. By focusing on calibrated computing, businesses can ensure they deploy software with verifiable competence. This thoughtful approach prioritizes restraint, safety, and hardware capacity over industry hype, ultimately resulting in technology that simply works properly for its intended daily purpose.


Should cybersecurity be nationalised?

The conversation around digital safety is gradually shifting from treating it as a private expense to recognizing it as a public good. While full government ownership is not currently under consideration, experts argue that the traditional model of individual corporate defense is no longer sustainable. Today, private companies are routinely expected to fend off sophisticated attacks from foreign nations, a task for which most lack the necessary resources. Small businesses are particularly vulnerable and they often become the weak link that exposes broader networks to risk. Because hardening the defenses of one company inherently protects the wider community, securing digital infrastructure shares clear parallels with public utilities like street lighting. This shared benefit naturally raises important questions regarding funding and accountability. The emerging consensus suggests a model where the state might fund security measures that are executed by private firms, ensuring broader protection without complete nationalization. As this policy debate unfolds, organizations must adapt by viewing their security practices not merely as an internal budget item, but as a core component of public trust and reputation. Moving forward, businesses should firmly anticipate stricter sector requirements and expect to demonstrate baseline security standards simply to operate within shared modern networks.


IT modernization: Still a make-or-break project for CIOs

IT modernization remains a vital, ongoing mission for CIOs, taking on renewed urgency as artificial intelligence reshapes the technology landscape. The rise of AI and natural language tools means that systems built just a few years ago, such as traditional reporting dashboards and specialized chatbot software, may already be obsolete. IT leaders are now approaching modernization and application rationalization with a business-first strategy, evaluating tools not by their age, but by the tangible value and flexibility they provide. Consolidating software limits wasteful spending, reduces unneeded complexity, and creates a clean data environment essential for advanced technologies. While moving to modern solutions can cut maintenance costs and limit security risks, CIOs face practical challenges, including upfront migration expenses, data extraction difficulties, and internal resistance to letting go of highly customized legacy systems. Some organizations are increasingly weighing whether to build internal tools using advanced coding assistants rather than paying long-term licensing fees for external software. Ultimately, IT modernization is no longer just about retiring old technology; it is a continuous process of aligning the company’s tech stack with fast-evolving business needs to clear a path for meaningful innovation and operational agility.


The Credential Layer Is Expanding Faster Than Security Teams Can See It

As software development accelerates, organizations face an enormous increase in the number of digital keys, passwords, and access tokens they must manage. These credentials now connect people, applications, and artificial intelligence tools to critical data. Because they are often scattered across cloud accounts, internal networks, messaging apps, and developer laptops, it is incredibly difficult for security teams to track them. Recent data shows a sharp rise in leaked secrets, particularly those tied to AI services, which have become a new frontier for access management. At the same time, cybercriminals are using specialized malware to target developer devices, aiming to steal the local access codes stored there. To protect against these threats, security teams cannot rely on outdated, periodic checks. They need constant, clear visibility into every credential across the organization. This means knowing exactly what access each key grants, who owns it, and whether it is still active. Only by building a complete and accurate inventory can teams effectively identify risks, remove exposed secrets, and stop future leaks from happening. Taking control of this expanding environment requires a calm, systematic approach focused on detection first, ensuring that organizations understand their vulnerabilities before attackers can find them.


Should the CISO role be split in two?

Over the past three decades, the chief information security officer role has expanded significantly from its strictly technical origins. Today, these professionals are tasked with broad, strategic responsibilities, including data privacy, regulatory compliance, artificial intelligence governance, and overall business risk management. As this heavy workload continues to grow and outpace available resources, some industry observers have debated whether the position should be divided into two distinct roles: one focused purely on technical defense and another dedicated to business risk and organizational resilience. However, leading experts argue clearly against splitting the job. Instead, they recommend confidently maintaining a single executive who holds ultimate accountability for the organization's cyber strategy and risk management. To help manage the immense daily operational demands, larger companies are increasingly relying on a dedicated deputy role, which also directly aids in succession planning. This balanced approach ensures that the primary security leader can successfully focus their energy on executive communication, financial planning, and aligning security measures with core business objectives. Ultimately, the position is maturing along a path very similar to that of the chief information officer. As the role becomes undeniably executive, these professionals must transition from being seen merely as technical experts to functioning as essential business partners.


Exploring AI Observability – Part 1: Why It Matters

Just a year ago, tracking how artificial intelligence operates was hardly a recognized technology field. Today, experts predict that by 2028, a large portion of organizations deploying these systems will rely on dedicated tools to oversee them. This shift is happening because the adoption of intelligent systems has grown much faster than our ability to properly govern them. Employees across companies are using a mix of approved and unapproved tools, while software teams are actively building language models directly into their applications. This rapid expansion creates an urgent need for visibility to understand exactly where these tools are running, how well they perform, what they cost, and if they actually deliver real value to the business. The conversation is no longer just about how fast we can build these systems, but rather whether we can run them reliably in real world settings. Because modern systems can sometimes produce varying results from the exact same input, errors can quickly add up. Proper oversight is necessary right from the development phase to trace interactions, identify failures, and improve accuracy. In production, this oversight ensures that the behavior of intelligent tools connects smoothly with overall application health, resilience, and a solid user experience.


The Platform Engineering Playbook for Production LLMs
According to a case study on an inventory accuracy platform, scaling large language models (LLMs) requires treating the AI stack as platform infrastructure rather than a mere application feature. The engineering team successfully reduced production hallucination rates from fifteen percent down to just 1.5 percent without altering the foundation model itself. They achieved this by implementing an automated retry loop to catch formatting and grounding errors on the fly, alongside an intent-validation gate that defaults to "unclassified" to prevent off-intent responses. Additionally, prompt management was shifted to a history-preserving registry rather than hardcoding instructions, allowing runtime updates with a clear audit trail to prevent silent behavioral breaks. The authors also highlight critical security and observability practices for enterprise AI. They strongly recommend enforcing tool authorization directly at the resource server with a strict default-deny policy, warning that relying solely on API gateways can expose tools due to a single orchestrator bug. Furthermore, since traditional application performance monitoring tools cannot detect semantic degradation or silent output drift, teams must proactively instrument hallucination rates and per-team token costs right at request ingress to avoid costly retrofitting later.


Three questions a hospital CISO should ask a healthcare fintech vendor

In a recent interview with Help Net Security, Drew McCombs, CTO and CISO at Cylerity, discusses his approach to balancing security with development in the healthcare fintech sector. McCombs ensures that security is integrated into every development sprint rather than treated as an afterthought. When conflicts arise, any issue affecting patient data or funds disbursement takes priority. He notes that while Cylerity is not a bank, it must satisfy the compliance expectations of its banking partners without violating HIPAA regulations. To achieve this, the company minimizes data sharing and uses custom identifiers to keep protected health information (PHI) completely separate from financial reporting. When discussing artificial intelligence, McCombs insists that AI models should only recommend or flag information, with a human always making the final decision to prevent errors from gradual model drift. For small medical practices, he emphasizes that turning on multi-factor authentication (MFA) for email is the cheapest and most effective security fix available. Finally, McCombs advises hospital CISOs to scrutinize fintech vendors by asking about their data subprocessors, their protocols for verifying fund destination changes, and their breach response plans, warning that a vendor claiming to be "HIPAA certified" is a major red flag since no such official certification exists.

Daily Tech Digest - September 27, 2026


Quote for the day:

"The distance between insanity and genius is measured only by success." -- Bruce Feirstein

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Digital Twin Technology: A Comprehensive Guide

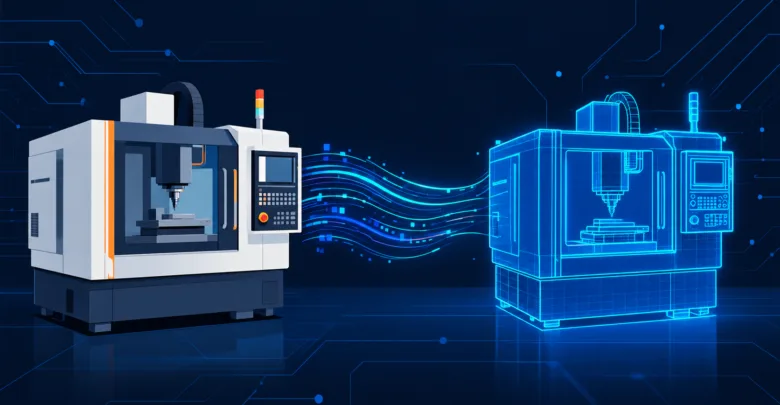
A digital twin is a dynamic, data-driven virtual replica of a physical object, process, or system. Unlike a static 3D model or a traditional one-time simulation, a digital twin continuously receives real-time data from sensors attached to its physical counterpart. This steady flow of information ensures the digital version mirrors the actual, current behavior of the real-world entity rather than just its original design specifications. The technology relies on three core components: the physical entity equipped with sensors, the virtual model, and the continuous data connection linking them. By maintaining this active connection, organizations can run highly accurate simulations, test new scenarios, and predict failures without risking the actual physical asset. The applications are broad and scalable, ranging from tracking a single component like an engine bearing to managing complex networks like a manufacturing production line or an entire modern city's infrastructure. While the technology offers incredibly powerful predictive capabilities, building an effective digital twin comes with several practical challenges. Organizations must manage data quality, handle complex modeling requirements, and navigate security concerns carefully. Because of this inherent complexity, experts recommend starting with a single, well-defined use case before attempting to scale up to larger, interconnected systems.


Three Hidden Traps That Shape Software Engineering Decisions

Engineering leaders face more than just technical challenges; they must also navigate human behaviors and cognitive biases that heavily influence software design and quality. The article outlines three common traps that developers and technical leaders fall into. The first is the "status quo bias," where teams stick to familiar tools or methods simply because "we've always done it this way," often ignoring newer, more suitable options for current requirements. The second trap is "complexity bias," which tempts engineers to overengineer solutions by adding unnecessary layers, abstractions, or services under the false assumption that complex designs are inherently more robust. This often leads to systems that are harder to maintain and prone to failure. Finally, the "broken windows" effect describes how an environment of poor code quality or neglected technical debt silently lowers a team's engineering standards. When developers see messy code or ignored warnings, they are more likely to introduce new shortcuts, gradually degrading the entire system. Recognizing and naming these biases helps teams pause, ask the right questions, and make more deliberate, evidence-based decisions rather than relying on flawed mental shortcuts.


How can boards gain confidence in their organization’s AI adoption?

Many corporate boards believe that establishing policies and risk frameworks is the key to governing artificial intelligence. However, Michael Covington argues that effective AI governance is impossible without first achieving comprehensive visibility into where and how AI is actually being used within the organization. Just as with the adoption of SaaS, cloud computing, and mobile technologies, companies are rushing to implement AI policies while lacking a basic inventory of their AI assets. Currently, over 70% of organizations deploy AI, yet more than 80% feel exposed to AI-related risks because adoption has vastly outpaced governance. This visibility gap is particularly dangerous because AI capabilities are increasingly embedded into routine software updates, meaning new tools can enter the corporate environment without any formal procurement or approval processes. This unchecked expansion poses risks beyond just security, potentially leading to unauthorized data access or widespread system disruptions. To solve this, leadership must treat AI like any other core technology asset. By integrating AI tracking into existing hardware, software, and cloud service inventories, boards can achieve continuous visibility. This foundational step transforms AI from an unmanaged liability into a measurable asset, allowing security, compliance, and finance teams to govern its usage with confidence.


The Factory Can Survive the Cyberattack. Can It Survive the Recovery?

Manufacturers have spent years investing in their ability to detect cyber threats, but detecting an attack is really only the beginning of the battle. In a factory setting, recovering from a cyber incident is far more complex than simply restoring digital assets or standard computer applications. It requires carefully bringing operational technology, such as programmable logic controllers and industrial machinery, back online in the correct sequence to avoid further issues. A technically successful software restoration can still result in operational failure if physical processes are restarted incorrectly or unsafely. To build true recovery readiness, manufacturers must map production dependencies outward from the physical process rather than inward from the network. This means identifying which critical operations must return first and defining the specific utilities, vendors, and human approvals required to support them. Organizations should assign recovery authority across tech, operations, and management teams ahead of time to prevent decision bottlenecks during an emergency. Finally, factories must practice realistic recovery scenarios where ideal conditions, such as the availability of key personnel or clean backups, are deliberately removed. Ultimately, a resilient manufacturer treats operational recovery as a designed and measured production capability, ensuring a safe, controlled return to dependable operations across the entire plant.


Why Enterprise AI ROI Is An Architecture Problem

Many companies struggle to see a positive financial return from their artificial intelligence efforts because of flawed system architecture, rather than the raw cost of the intelligence itself. Most organizations mistakenly build these capabilities by attaching them to disjointed legacy systems, forcing every new project to recreate rules and data connections from scratch. This fragmentation scatters information and makes proving economic value nearly impossible. To solve this and improve financial outcomes, businesses must adopt four core architectural changes. First, they should mandate a shared knowledge foundation to centralize enterprise data, eliminating the need to repeatedly rebuild integrations for each new tool. Second, they need to route tasks to the appropriate model based on complexity; simple tasks should use smaller, less expensive models, reserving advanced systems only for complex, high-value reasoning. Third, companies should prioritize groups of specialized tools over a single, massive program. Breaking tasks down into narrower, focused parts reduces the data processed at each step, significantly cutting costs and improving speed. Finally, organizations must build security and compliance directly into the core platform rather than adding them to individual applications, ensuring controls remain reusable and highly transparent. Ultimately, centralized architecture lowers deployment costs and clarifies actual value for the overall business.


Website Tracking Technologies Face Growing Litigation and Regulatory Scrutiny

Many companies use website tracking technologies like pixels, software development kits, session replay scripts, and chat tools to better understand how visitors interact with their pages. Working quietly behind the scenes, these tools gather data when a person clicks a button, views a product, or fills out a form. They then share this activity with third-party analytics and advertising companies. For years, businesses have relied on these insights to measure website traffic, track the effectiveness of marketing campaigns, and personalize the user experience. However, this routine data collection has recently become the center of a rapidly expanding wave of legal and regulatory action. Because these tools frequently transmit visitor information automatically and often before a user formally agrees to share their data, they have drawn severe scrutiny from privacy advocates and government agencies. Regulators and plaintiffs' attorneys are now scrutinizing exactly what information gets shared, with whom, and whether proper consent was obtained. In many recent lawsuits, these common marketing tools are being classified as wiretapping and eavesdropping devices that unlawfully disclose personal information. Ultimately, while tracking technologies provide businesses with valuable insights into customer behavior, they are now introducing substantial legal risks that demand careful oversight and strict compliance.


Clean Architecture: 5 Layers Every Developer Should Understand in 2026

Clean Architecture provides a structured way to build software by firmly separating core business rules from external details like databases, user interfaces, and frameworks. This approach relies on a central principle called the Dependency Rule, which dictates that source code dependencies must only point inward. The architecture is typically divided into five distinct layers to manage these boundaries. At the very center are Entities, which represent pure, framework-independent business logic that rarely changes. Surrounding them are Use Cases, which define application-specific rules and coordinate data flow without knowing about the database or web framework. Next are Interface Adapters, such as controllers and presenters, which carefully translate data between the inner core and the outside world. Further out is the Infrastructure layer, containing concrete implementations like third-party libraries and database adapters. Finally, the outermost layer consists of Frameworks and Drivers, which act as the basic glue holding the application together at startup. By strictly enforcing this inward dependency throughout the codebase, developers can ensure their applications remain completely testable and highly adaptable over time. This clear structure allows teams to comfortably swap out databases or web interfaces down the line without ever risking the fundamental logic that makes the product work.


The duality nobody priced in: The changing landscape of enterprise tech architecture and Agentic AI era

Enterprise technology is currently undergoing its most significant architectural shift in thirty years, driven primarily by the transition to agentic artificial intelligence. For decades, traditional enterprise systems were designed to standardize business processes, keeping core operations highly structured while placing customizations and early AI tools safely at the outer edges. Generative AI fundamentally breaks this familiar pattern by moving from transaction-driven operations to intent-driven software. Instead of following rigid, pre-defined rules, agentic applications accept a specific goal and determine their own path, effectively shifting business logic into a complex central orchestration layer. While this promises considerably faster software production, it introduces substantial new challenges in data governance, cost management, system testing, and operational oversight. Organizations now face a choice in how to integrate this technology: replacing old automation, layering agents over existing systems, running them in parallel, or embedding them deeply into core frameworks. Ultimately, true success requires much more than just launching rapid prototypes to showcase capabilities. The enterprises that will thrive in the coming decade are those that resist the urge to rush and instead focus on building robust architectural foundations, carefully balancing the speed of new technology with necessary operational reliability and long-term security.


With the Rise of AI Agents, SOC 2 Should Adapt or Risk Irrelevance

The rapid adoption of AI agents is exposing significant blind spots in traditional SOC 2 compliance frameworks. Originally designed with human actors in mind, SOC 2 controls rely on foundational assumptions that do not apply to machine identities. Because the framework does not explicitly mandate treating AI agents as a distinct class of users, organizations can pass audits while harboring unrecognized security risks. Specifically, four core assumptions are now breaking down. First, unlike human users who require formal approval before account creation, agents are often spawned automatically or indirectly. Second, determining the true owner of an agent is frequently a matter of guesswork rather than a clear record. Third, because AI agents often operate using borrowed human credentials, access logs cannot reliably distinguish between human and machine activity. Finally, traditional least-privilege principles limit an agent's reach but fail to explain its actual intended purpose. These gaps weaken critical controls, such as offboarding processes that overlook active agents tied to former employees, and change management where agents bypass genuine segregation of duties. To maintain true security, organizations must look beyond the compliance checklist, intentionally track machine identities, and match an agent's access directly to its specific purpose.


Your architecture diagram is not your resilience

An architecture diagram represents a system as it was intended to be, but it cannot prove whether that system is truly resilient today. Microsoft emphasizes that resilience is no longer a one-time project you can set and forget. Instead, it is an ongoing property you must actively maintain. Over time, architectures drift as systems change. For instance, a database might support failover, but an application's connection string could remain pinned to a single region. Because diagrams lack timestamps and operational reality, they often fail to capture this drift. Furthermore, the nature of dependencies is evolving. While traditional disaster recovery focuses on infrastructure, modern systems increasingly depend on AI models and inference endpoints. These dependencies introduce new risks, as AI can produce varying responses and may become unavailable or capacity-constrained. To manage these shifts, organizations must move beyond relying on static diagrams and adopt a continuous validation approach. Microsoft recommends designing resilience from the beginning, defining clear recovery objectives, and understanding your actual blast radius. Tools like the Azure Infrastructure Resiliency Manager and fault injection through Azure Chaos Studio can help teams test failover paths and measure their posture, ensuring that their intended resilience matches reality.