Showing posts with label AI Slop. Show all posts

Daily Tech Digest - September 23, 2026


Quote for the day:

"Every great story on the planet happened when someone decided not to give up, but kept going no matter what." -- Spryte Loriano

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 26 mins • Perfect for listening on the go.


Observability should start with business outcomes, not infrastructure

The article, "Observability should start with business outcomes, not infrastructure" by Vjacheslav Mikitjuk, argues that technical metrics alone are inadequate for understanding the actual performance of IT systems. The article points out that while an engineering dashboard might show a system running efficiently, it could simultaneously be experiencing a serious customer-facing failure. Therefore, IT teams need to translate technical severity into business severity to provide management with a clear picture of the impact on customers, transaction values, and overall business operations. Mikitjuk suggests that observability needs to follow a chain starting from business outcomes down to telemetry. This approach involves defining service objectives based on user experience rather than just infrastructure metrics. He emphasizes that the translation between technical and business performance should be a shared responsibility across the organization, involving business leadership, product owners, and engineering teams. Furthermore, he advises that business observability must be designed proactively during the service and product design phases, rather than being an afterthought during an incident. The article also highlights that observability priorities should be determined by business criticality, focusing efforts where degradation would have the most significant consequences. Finally, while AI can assist in interpreting data, it requires the foundational context of business goals to be truly effective.


Redefining Cyber Recovery Requirements in the Era of Modern Cyberattacks

Cyber recovery is fundamentally different from traditional disaster recovery, requiring a practical approach to combat modern threats. While disaster recovery focuses on quickly restoring the most recent backup after an outage, cyber recovery prioritizes data integrity. Because attackers often dwell inside networks for days or weeks before causing damage, the newest backup is usually infected. Therefore, IT teams must work backward to find a genuinely clean copy. This process is complicated by the fact that the vast majority of modern intrusions leave no malicious files behind. Instead, attackers use stolen credentials and existing administrative tools to move silently. As a result, standard antivirus scans on powered-off backups are no longer sufficient. To ensure a backup is truly safe, organizations must power it on and carefully observe its behavior over time to detect hidden threats. Because powering on a compromised system risks reinfecting the entire network, this behavioral analysis must happen inside a strictly isolated clean room. Solutions like VMware Cloud Foundation and Advanced Cyber Compliance automate this critical testing environment. By integrating secure, quarantined recovery workflows, organizations can confidently identify uncorrupted data and restore operations safely, moving beyond outdated backup strategies to address the reality of modern fileless attacks.


Data embassies and sovereign dispersion
Data embassies and sovereign dispersion present a new approach to managing the trade-off between data residency and resilience, moving beyond traditional data localization. Driven by geopolitical instability and cyber threats, governments—particularly smaller, highly digitized nations like Estonia—are establishing legally protected digital enclaves on foreign soil. Unlike multi-region cloud backups subject to host nation laws, genuine data embassies operate under bilateral treaties granting them diplomatic immunity. They maintain an active "digital twin" to ensure core civic services, like tax systems and central bank ledgers, run smoothly during domestic crises such as cyberattacks or power failures. Gartner anticipates that by 2029, 15% of nations in unstable regions will have formalized data embassy agreements. Estonia established the first in 2015, partnering with Luxembourg for its Tier IV data centers, setting a precedent that requires specific intergovernmental contracts. Security relies on principles like "encryption as a border," ensuring the origin state retains decryption keys. While replicating this model is challenging for private enterprises, IT leaders can adopt similar technical resilience strategies. By decoupling encryption keys from cloud providers and avoiding over-reliance on a single vendor or location, businesses can enhance their operational continuity and mitigate risks associated with physical data concentration.


How to Handle the Growing Data Complexity Challenge in Cyber Incident Response

The article explains that cyber incident response has become far more complicated than simply handling large volumes of data after a breach. Modern organizations generate information across cloud platforms, collaboration tools, mobile devices, enterprise applications, and third‑party services, creating a sprawling and interconnected data environment. Regulators now expect investigators to identify and analyze a wider range of sensitive information, from traditional personal data to device identifiers, geolocation details, and behavioral patterns. The piece highlights how today’s breaches often involve structured and unstructured data, multimedia files, and systems that store overlapping records, making it difficult to determine what truly matters. Traditional keyword‑based search methods are no longer enough, especially when investigators must uncover “unknown unknowns” hidden across diverse systems. AI‑assisted tools can help by recognizing entities, relationships, and context, but the article stresses that any AI‑driven process must remain legally defensible through documented workflows, validation, and human oversight. Notification decisions—often the hardest part—require consolidating identities, applying jurisdictional rules, and ensuring accuracy at scale. The author concludes that organizations need a disciplined, context‑aware approach to data mining, combining technology, expertise, and defensible processes to understand risk and respond confidently under tight timelines.


7 decisions that make an Azure landing zone enterprise-ready

Creating an effective, enterprise-ready Azure landing zone requires thinking beyond basic reference architectures to build a platform that supports engineering teams rather than hindering them. The article highlights seven key design decisions to achieve this balance between security and developer autonomy. First, treat the landing zone as an operating model—not just a network—by separating platform resources from application workloads using management groups and subscriptions to create clear governance boundaries. Second, opt for Azure Virtual WAN over a self-managed hub-and-spoke setup to simplify cross-region connectivity and route management. Third, integrate your security model, such as a next-generation firewall, directly into the routing architecture from day one rather than bolting it on later. Fourth, implement governance as guardrails that manage risk without turning routine engineering tasks into a constant exception process. Fifth, separate your observability tools for operational health from your SIEM tools for security monitoring to reduce noise and clarify responsibilities. Sixth, treat CI/CD networking as a core platform component, using solutions like private GitHub runners to securely deploy to isolated resources. Finally, ensure an active-active architecture truly works by making both regions fully production-ready and capable of independently supporting the workload during a failure.


AI adoption in OT security accelerates as legacy infrastructure and poor data expose readiness gaps

Many industrial organizations are eager to implement AI for operational technology (OT) security, but their current infrastructure often isn't ready. A recent survey highlights that while nearly 88% of organizations are using or planning to use AI, under 8% have deployed it across multiple functions. The main hurdles are poor data quality and the challenges of integrating AI with legacy systems. Most industrial facilities were built long before AI was a consideration, resulting in control systems that produce inconsistent data. Experts point out that legacy environments frequently lack the necessary identity and access management infrastructure and cloud connectivity required for modern AI models. This gap is especially problematic because AI depends on high-quality data and complete asset context to function accurately. Without these, AI tools can produce incorrect assumptions, leading to false positives or missed threats. Furthermore, poor data quality in OT can have serious physical consequences, including equipment damage or safety incidents. To make AI work effectively and safely in these environments, organizations must first focus on improving their architectural foundations. This includes better data normalization, consistent telemetry, and modernized security architectures that provide a stronger base for AI-enabled tools.


Operational Technology Scope Expands as Security Matures
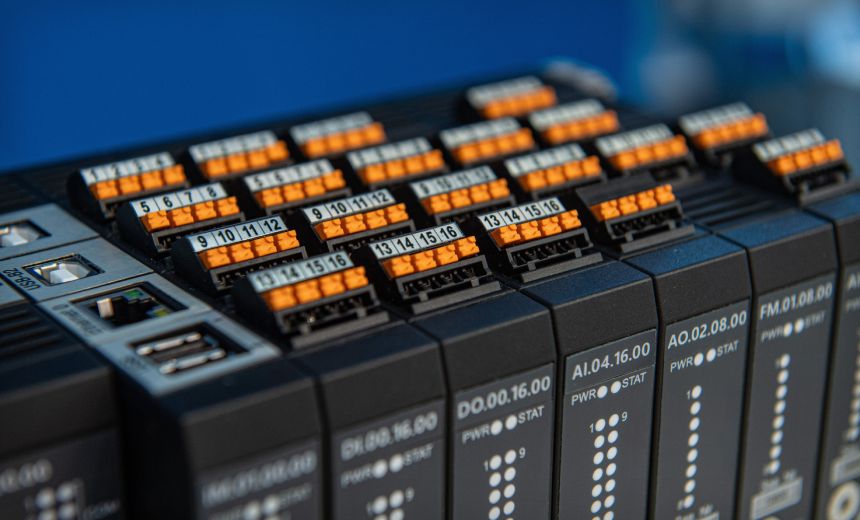
The article describes how operational technology (OT) security has matured as industrial organizations face more frequent and costly cyber incidents. According to Honeywell’s 2026 OT Cybersecurity Benchmark Report, major attacks now cause an average of 16 hours of downtime, with losses reaching up to $500,000 per hour. As a result, companies across energy, manufacturing, healthcare, maritime, and other critical sectors are shifting from a narrow, technology‑centric mindset to a broader focus on business resilience. Leaders increasingly view OT security as essential to safety, uptime, and service continuity, especially as digital connectivity expands across industrial control systems, field devices, building management systems, IoT sensors, and medical equipment. The report shows that organizations with mature programs detect and respond to threats faster, largely because they maintain strong asset inventories and continuous monitoring. Yet visibility remains a major gap: only one‑third have integrated OT systems into a centralized SOC, and just one‑fifth continuously monitor IoT devices. Legacy systems, staffing shortages, and budget constraints add further strain. Many organizations are adopting AI for detection and monitoring, though fully autonomous decision‑making remains rare. The article concludes that resilience depends on extending security across every connected system and closing visibility gaps that still hinder effective response.


I Wasn’t Trying to Predict the Future. I Was Trying to Build One I Could Tolerate

The article is a reflective piece in which the author explains that his work with AI did not begin as an attempt to predict the future but as a practical response to a narrowing set of acceptable options. He frames his journey not as a heroic narrative but as a form of “niche construction,” a security practice focused on shaping an environment that can support more viable futures. Throughout his career in cybersecurity, supply‑chain assurance, information sharing, and industrial systems, he learned that security is rarely about protecting a single object. Instead, it is about maintaining the conditions that allow systems to survive and adapt. He illustrates this through stories of living on self‑built boats, where survival depended on constant maintenance, awareness, and the ability to respond to change. When his own circumstances tightened in 2025, he turned to a large language model as one of the few available tools and began a sustained, iterative collaboration that produced frameworks, documents, code, and new institutional structures. He describes this as building a generative set—an evolving system that creates new possibilities rather than following a fixed plan. The article concludes that meaningful security often comes from constructing environments where better futures can emerge, not from defending the present in isolation.


CISOs can no longer ignore the nation-state threat

The accelerating use of AI by nation-state actors is forcing Chief Information Security Officers (CISOs) to rethink their threat models and treat geopolitical threats as urgent enterprise risks. Historically, CISOs focused on quickly expelling adversaries from networks, while government agencies preferred to monitor them for intelligence. However, AI is now lowering the barrier to entry, allowing even amateur cybercriminals to launch sophisticated attacks that mimic nation-state activity. This shift blurs the line between national security threats and ordinary business risks. A major challenge for organizations is recognizing their own strategic value to foreign adversaries. Companies in seemingly benign industries, such as agriculture, can become targets if they possess valuable intellectual property or supply chain access. AI worsens this by compressing the time between a vulnerability's discovery and its exploitation to mere seconds, making traditional patching processes insufficient. To adapt, security leaders must recognize that AI enables faster, broader pre-positioning by attackers within organizational assets. Experts advise CISOs to prepare for fully autonomous attacks, plan to operate through compromises during major disruptions, and focus on core security controls like zero trust and multi-factor authentication. Crucially, CISOs need board-level support and funding to implement these necessary resilience measures.


AI slop is creating more work, not less. Here’s why

The rise of generative AI in the workplace was promised to boost productivity, but it is increasingly resulting in "AI slop"—low-quality, generic, and often unverified content that shifts the workload onto other employees. In a recent Today in Tech episode, host Keith Shaw and Commvault’s Chris Bevil discussed how tools that instantly generate emails, reports, and presentations create a hidden "review tax." While an executive might save time using AI to summarize a long document or draft a memo, the receiving employees must often spend significant time fact-checking, correcting context, and deciphering vague, polished-but-empty drafts. This disconnect explains why executives frequently report high productivity gains from AI, while non-managers feel bogged down by new verification processes. AI slop resembles a "first draft wearing a tie"—it looks professional and confident on the surface but lacks underlying substance or clear judgment. As this unverified content spreads rapidly across organizations, it risks becoming accepted corporate knowledge. To truly benefit from AI, companies must move beyond simply generating more content and emphasize proper governance, human review, and clear workflows to prevent productivity gains at the top from becoming a burden at the bottom.

Daily Tech Digest - August 29, 2026


Quote for the day:

“You may be disappointed if you fail, but you are doomed if you don’t try.” -- Beverly Sills


🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


Digital twins are evolving from passive virtual mirrors into active decision environments, making their underlying data structures more critical. As artificial intelligence agents are introduced into these environments, they must evaluate complex layers of information such as sensor data, equipment dependencies, and historical records to make sound operational decisions. However, AI agents demand more than standard data access; they require durable, long term memory. Rather than forcing information into prompt windows or attaching separate storage systems, organizations should treat agent memory as primary data within the twin itself. This approach means accurately tracking the source of every fact, its historical context, and its validity over time. Crucially, when new information contradicts an older belief, the system should not simply overwrite the past. Instead, it must retain the original data and link it to the update. Preserving this chain of reasoning creates an essential audit trail that builds trust and supports proper governance. To handle this complexity at scale, unified data foundations are necessary to seamlessly link documents, temporal states, and structured records. Ultimately, the challenge is no longer just building the digital model, but constructing the comprehensive memory around it, ensuring that human operators and machines can act with complete confidence.


AI Slop in the Enterprise: What Happens When Engineers Stop Reviewing AI-Generated Code

AI slop in enterprise software engineering refers to low-quality, AI-generated code that appears functional on the surface but introduces hidden defects, security flaws, and severe maintenance burdens. This phenomenon occurs when developers use AI tools to generate code much faster than teams can responsibly review it. Consequently, pull requests accumulate, and code is frequently merged without thorough human oversight. Because AI-generated code lacks clear human intent, reviewing it requires significantly more effort to identify subtle architectural errors, ultimately doubling review times and placing a heavy burden on senior engineers. This growing review tax leads to burnout and a divide between responsible developers and those who submit AI output without understanding it. The business impact is substantial. Studies show that while AI increases coding volume, it also introduces security vulnerabilities at a vastly accelerated rate, with nearly half of AI-generated samples containing fundamental flaws. Furthermore, unmanaged AI code can quadruple technical debt by the second year, silently embedding architectural mistakes that slow down future development. To solve this problem, enterprises must shift their focus from raw coding speed to strict governance. Solutions involve implementing visible quality metrics, enforcing architectural fit, and applying automated rule sets to verify AI output before human review even begins.


The three layers of agentic AI security: A defense-in-depth architecture for autonomous agents

The VentureBeat article outlines a comprehensive security architecture designed to address the specific risks of autonomous AI agents. Traditional security measures fall short because these agents operate independently and can inadvertently cause data leaks or execute unintended commands. To manage these new risks, the piece proposes a security model built on three distinct layers. First, the infrastructure layer establishes a secure foundation by verifying the physical and digital environments where agents run. By using methods such as hardware level trust and secure isolation, this step ensures that only authorized workloads operate, which is especially important for regulated industries like finance. Second, the network layer manages how agents communicate with other systems and data sources. Because agents generate complex and dynamic traffic patterns, traditional static network rules no longer work. Instead, organizations must adopt dynamic, strict access policies that closely control internal movement and data retrieval. Finally, the control plane acts as the central management hub for permissions and resource allocation. This layer enforces rules consistently across the entire system, preventing agents from using unauthorized tools or consuming excessive computing power. Together, these three layers provide a structured approach to securing independent AI systems, allowing organizations to maintain effective control and continuous oversight.


The Board’s Role in Crisis Management and Scenario Planning

In an era of unpredictable disruptions, a board of directors must shift from merely reacting to crises to actively preparing for them. The core responsibility of the board in crisis management is oversight and strategic guidance, rather than day-to-day execution. While senior management is tasked with implementing response plans when an emergency strikes, the board ensures that robust frameworks, ethical standards, and clear communication channels are already established. A critical tool in this proactive approach is scenario planning. By anticipating potential threats, ranging from financial downturns and operational failures to reputational damage, boards can guide management in developing practical response strategies before a crisis occurs. This involves conducting regular risk assessments and participating in crisis simulations to build organizational resilience. Scenario planning helps uncover hidden vulnerabilities and tests the effectiveness of current policies, allowing companies to respond swiftly and confidently when real challenges arise. Furthermore, effective governance during a crisis requires clear decision-making processes and an unwavering commitment to the company's long-term stability. After a crisis, the board must also lead the review process to identify lessons learned and improve future readiness. Ultimately, strong board leadership transforms crisis management from a frantic scramble into a structured, reliable process that protects the organization and its stakeholders.


Most Organizations Declare Victory Over a Breach Too Early

When dealing with a security incident, business leaders often feel pressured to return to normal operations as quickly as possible. This pressure leads many organizations to declare victory over a breach long before the threat is fully removed. In their rush to restore services, response teams typically address the most obvious signs of an attack, such as isolating a compromised server or resetting user passwords. However, stopping the investigation at this early stage is a critical mistake. Intruders often establish hidden backdoors, create secondary accounts, or move laterally across the network well before the initial detection occurs. If responders fail to conduct a thorough forensic analysis, these hidden footholds remain active, allowing the attackers to quietly regain access days or weeks later. To effectively resolve a cyber incident, organizations must shift their focus from mere speed to complete threat eradication. This requires committing to extended monitoring and ensuring that all affected systems are deeply analyzed for residual threats. Teams should wait until they have clear evidence that the environment is genuinely secure before announcing that the crisis has passed. By taking a careful, methodical approach to recovery, companies can better protect themselves from falling victim to the exact same intruders twice.
Artificial intelligence is fundamentally changing how enterprise software is built, shifting the industry away from large, specialized teams toward smaller, highly skilled groups. At the center of this shift is the IT architect. Rather than simply overseeing design, architects are returning to direct implementation. AI tools allow them to compress the traditional software process into a single, continuous loop that includes analysis, design, coding, testing, and deployment. To succeed today, these architects must combine a deep understanding of business operations with strong technical judgment. By using AI to close the gap between an initial idea and working software, small, architecture-led teams can deliver solid results in a fraction of the time. For instance, a recent legacy system update was finished in just five months instead of the usual two years, without sacrificing basic security, data integrity, or accuracy. This newfound efficiency completely changes the underlying economics of technology development. Traditional systems integrators and major software providers that rely on large staffs and lengthy timelines will face serious market pressure. Highly experienced professionals equipped with modern tools can now build complex systems much faster and more affordably. Consequently, business leaders must rethink their approach to building and buying technology before smaller, more capable competitors outpace them.

In a recent interview at Black Hat USA 2026, Omdia analyst Theresa Lanowitz shared findings on how artificial intelligence is shifting the landscape of cybersecurity. She notes that older methods like standard penetration testing and simulated attacks are no longer enough to keep up with the speed at which threats operate today. Because of this, organizations are rethinking their defense strategies and increasing their investments in offensive security. In fact, research shows that a vast majority of companies are willing to spend more to gain continuous visibility and better track devices across their networks. However, deploying automated tools for defense introduces its own set of challenges. Companies are rightly concerned about the risks of these systems behaving unpredictably, falling victim to manipulative inputs, or simply driving up costs. To manage these risks, experts recommend establishing strict boundaries to limit the potential damage if a system goes off track. Furthermore, securing the software supply chain has become incredibly critical. While nearly all organizations recognize its importance and are investing heavily in it, less than half are documenting their software components during the build process. Ultimately, business leaders are prioritizing overall resilience to ensure they can withstand and recover from unexpected incidents.


CTEM can give your security team a contextual edge

Traditional vulnerability management relies on periodic assessments and patching, but this approach is no longer enough to keep up with fast-moving cyber threats. Many security teams are now turning to continuous threat exposure management (CTEM) to stay ahead. Unlike standard scanners that only flag software flaws, CTEM takes a much broader view of an organization's actual risk. It actively monitors for misconfigurations, identity risks, and excessive permissions across cloud environments, applications, and networks. A major advantage of this continuous model is that it focuses on validation and action. Instead of simply generating long lists of potential issues, it helps teams determine whether a vulnerability is truly exploitable under their current defenses. It also ensures specific people are assigned to fix the most critical problems, shifting the goal from counting flaws to actually closing attack paths. To work well, this approach relies heavily on automation and contextual intelligence, combining technical data with business priorities. However, adopting this new model requires significant cultural shifts. Security leaders must overcome tool fatigue, break down departmental silos, and change their teams' mindsets. Rather than just hunting for every single technical error, the focus must shift toward steadily reducing the overall risk to the core business.

Cybersecurity in manufacturing is no longer just an IT concern; it is a fundamental operational discipline. When a cyber incident strikes a factory, it halts production, impacts product quality, and compromises worker safety. Because modern facilities connect legacy machinery with cloud services, robots, and artificial intelligence, the boundaries of the factory floor have expanded. This creates new vulnerabilities, yet many companies still rely on traditional IT security methods. Standard IT practices, like aggressive scanning and immediate patching, can actually disrupt continuous manufacturing processes. Instead, protecting operational technology requires a different approach focused on system availability, using passive monitoring and protective architecture around older equipment rather than replacing it. A major challenge is the division of responsibility between IT, engineering, and plant operations, which often leaves critical decisions unresolved during an attack. To build real resilience, plant leaders need clear ownership of cyber risks, treating them with the same importance as workplace safety and product quality. By developing specific response plans before an incident occurs, teams can drastically reduce recovery time. Ultimately, manufacturers must merge technical threat knowledge with practical engineering experience to ensure that their facilities run reliably and securely in an increasingly connected world.


Security Readiness Looks Good On Paper. Investigations Say Otherwise

Organizations frequently overestimate their cybersecurity readiness, assuming that purchasing an array of security tools makes them safe. In reality, the true strength of a security program is only revealed during an actual breach, which often exposes a gap between what leaders believe and what is actually happening. Many companies buy defenses like endpoint detection or backup systems but fail to fully implement or monitor them around the clock. Attackers capitalize on these cumulative, minor weaknesses, such as delayed updates or lingering credentials, rather than relying on a single sophisticated exploit. Furthermore, detecting threats has become increasingly difficult as attackers use stealthy methods and artificial intelligence to blend their movements with normal daily operations. Instead of waiting for a breach to happen to secure funding and buy the newest marketed tools, leaders should adopt a proactive mindset. This means asking what protective measures they would wish they had in place if an attack happened tomorrow. By relying on forensic evidence from actual incidents rather than theoretical product demonstrations, companies can focus on battle-tested solutions and practical fixes. Closing the gap between perceived readiness and actual defense capabilities allows organizations to address their vulnerabilities before attackers can exploit them.