Showing posts with label dependency. Show all posts

Daily Tech Digest - November 14, 2026

Quote for the Day
“You can’t be agile if you don’t deliver frequently.”
— Martin Fowler
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Global Microsoft 365 Outage Disrupts Businesses & Government Services

The global Microsoft 365 outage that began on November 12, 2026, caused widespread disruption for businesses and government organizations relying on services like Outlook, Teams, and Copilot. Microsoft attributed the downtime to infrastructure and configuration issues rather than a cyberattack, noting that server failures triggered automated re-routing that overwhelmed the remaining systems. Even though patches provided some improvement, the incident left countless organizations unable to send emails, manage identity protocols, or access essential shared documents. This failure highlighted the operational risks of heavy cloud dependency on a single technology provider. Government agencies, police forces, airlines, and corporations all faced severe operational hurdles, proving that standard business continuity plans are ineffective if they are stored on the very platforms experiencing the outage. The event underscores the critical need for robust operational resilience. Organizations are advised to map their exact cloud dependencies, establish alternative communication channels, and conduct tabletop exercises to test their true readiness for prolonged service disruptions before they occur.

Read Original Article →

Define Your Business’s Operational Technology Before Attackers Do It For You

Recent hacks on supermarket refrigeration systems reveal a serious problem: many companies do not know which equipment actually runs their business, but attackers certainly do. Operational technology is not limited to heavy factory machinery. It includes any physical system that halts operations if it stops working, such as an MRI machine in a hospital or a trading system in a financial firm. This is completely different from standard connected devices like smart thermostats or security cameras, which might cause annoyance if they fail but do not stop revenue. The real danger is not just that these critical systems have software flaws. The danger is that companies are leaving them directly exposed to the open internet. This is a basic failure, not an advanced attack. Today, attackers use automated tools and artificial intelligence to easily find and exploit these exposed systems. Instead of looking for complicated new software, companies need to focus on simple fundamentals. You must identify exactly what equipment keeps your business running, understand the true risks, remove unnecessary internet access, and apply standard security controls before the next incident occurs.

Read Original Article →
Article Thumbnail

An AI kill switch isn’t enough. Build a fallback plan

The article argues that an AI “kill switch” is necessary but insufficient because organizations also need a practical way to keep business processes running after an AI agent is stopped. Recent AI outages and an incident involving autonomous agents inside Hugging Face illustrate two sides of the problem: AI can become unavailable when needed or continue operating when it should stop. In either case, an emergency shutdown becomes difficult if teams have not planned what happens next. The author recommends designing the fallback before deploying the AI system. Every agent workflow should have a clearly defined off-state covering new, queued, and unfinished work, with an identified alternative such as a human queue or rule-based process. Shutdown controls should operate independently of the agent, while checkpoints should make it possible to understand and reverse incomplete actions. Organizations should also impose tighter limits during degraded operations and regularly test the handoff to fallback processes. The central message is simple: resilience depends not merely on being able to stop AI safely, but on ensuring the business can continue operating without it.

Read Original Article →

AI tears through legacy TCP/IP stacks, exposing vulnerabilities across critical infrastructure, OT and IoT devices

A recent report by Forescout Research demonstrates how artificial intelligence is dramatically accelerating the discovery of software vulnerabilities, fundamentally shifting the economics of cybersecurity. By using widely available AI models, researchers reduced the time needed to analyze foundational networking software from nine months to just ninety hours. The system successfully uncovered nearly one hundred vulnerabilities across commonly used networking stacks, including sixty six previously unknown issues. Remarkably, the entire automated analysis cost under one thousand dollars. While this efficiency highlights how AI can empower security teams, it also severely lowers the barrier to entry for potential attackers. The findings are particularly concerning for critical infrastructure, medical devices, and operational technology, which frequently rely on these shared components. Because many of these embedded systems are aging legacy devices that are difficult or impossible to update, a single flaw can expose a massive supply chain to serious risks. Consequently, experts advise organizations to focus on practical risk containment rather than waiting for software patches. This approach includes isolating unpatchable equipment, reducing unnecessary network exposure, and prioritizing mitigation strategies based directly on actual operational impacts.

Read Original Article →
Article Thumbnail

Cloud reports measure the wrong thing

The article critiques recent cloud industry reports, pointing out that while they accurately capture the rising complexity and costs associated with modern cloud computing and artificial intelligence, their conclusions are often skewed by inherent biases. Many vendor funded surveys frequently frame the increased spending on governance, financial operations teams, and hybrid cloud setups as signs of strategic maturity or the dawn of a new era focused on value. However, the author argues that these management structures are often just expensive bandages meant to cover up poor initial architecture, mounting technical debt, or unplanned expansions, rather than serving as deliberate, well planned strategies. While adding new dashboards and governance tools can certainly help highlight financial waste, these tools cannot fix fundamentally flawed system designs or workloads that were placed in the wrong environment to begin with. Furthermore, the survey data driving these industry narratives is typically drawn directly from cloud professionals and sponsored by vendors, creating a predictable echo chamber that prescribes buying more management tools instead of investing in better foundational engineering. Ultimately, achieving real success requires strict architectural discipline instead of just applying better accounting overlays.

Read Original Article →

Cyber Resilience Act: Due Diligence Obligations For Third-party Components

The EU Cyber Resilience Act (CRA) makes manufacturers responsible for the cybersecurity of an entire product with digital elements, including third-party hardware, software, open-source components, and certain connected services. Manufacturers cannot simply rely on supplier assurances. They must carry out risk-based due diligence when integrating components, with the depth of review reflecting each component’s security risk. Measures can include checking CE marking where applicable, reviewing security-update practices, examining known vulnerabilities, and conducting additional testing. Legacy and open-source components remain permitted, but manufacturers must ensure they do not weaken the final product. The CRA also requires manufacturers that discover vulnerabilities in integrated components to notify upstream manufacturers or maintainers and share fixes they develop where required. These responsibilities have important contractual consequences. Supplier agreements may increasingly need clear provisions covering secure development, vulnerability management, security updates, incident notification, documentation, testing, and cooperation with regulators. The article concludes that standard compliance clauses are unlikely to be sufficient: manufacturers will need stronger evidence and contractual assurance that suppliers can support continued CRA compliance throughout a product’s lifecycle.
Read Original Article →
Article Thumbnail

How one AI agent exposed five critical enterprise security gaps

When non-technical employees build AI agents to automate daily tasks, they often bypass traditional security measures, creating dangerous blind spots for organizations. A recent analysis explores a realistic scenario where an accounts worker creates an AI tool to process invoices between an email inbox, an enterprise resource planning system, and a messaging platform. Because the agent relies on a mix of personal API keys and persistent access grants, the security team has no visibility into its existence. This lack of oversight sets the stage for a critical failure when a malicious email tricks the agent into altering vendor payment details. The incident highlights five distinct security gaps that companies must address. First, organizations need to understand how mixed credentials obscure activity logs. Second, they must treat all external inputs as potential commands that could manipulate the agent. Third, baseline behavior monitoring is essential to catch abnormal actions, like an agent writing data for the first time. Finally, companies must implement strict credential expiry policies and ensure they can safely pause compromised agents to preserve evidence. By addressing these fundamental flaws, organizations can safely embrace automation without adding unnecessary risk.

Read Original Article →

AI Won’t Save Your Culture. It Will Expose It: Part I: When Intelligence Is Cheap, Judgment Becomes Priceless

The rapid adoption of artificial intelligence does not replace the need for a strong organizational risk culture; rather, it makes human judgment more vital than ever. When an AI model generates an unexpected output or a shadow application leaks data late at night, it is not a policy binder that determines how the issue is handled, but the psychological safety and culture of the team. As the risk landscape becomes increasingly volatile and complex, security leaders and executives are overwhelmed by machine-generated alerts and dashboards. In this environment, AI can process vast amounts of data at incredible speeds, but it cannot decide what risks an organization should tolerate or translate technical vulnerabilities into clear business decisions. Consequently, the roles of human leaders are shifting toward critical thinking, effective communication across departments, and constructively challenging automated conclusions. Because AI often presents answers with a false sense of authority, experienced professionals must rely on their judgment to separate meaningful signals from digital noise. Ultimately, AI might accelerate workflows and analysis, but human courage and culture remain the true safeguards of enterprise stability.

Read Original Article →
Article Thumbnail

Attackers in Binance Breach Targeted Known Weakness, Missing Controls

The article examines how attackers exploited weaknesses in Binance’s security controls to steal billions of dollars in cryptocurrency, showing how quickly a compromise can turn into a major loss. The attackers first compromised developer systems, gaining signing privileges that allowed them to create pre-signed authorizations. They then abused Ethereum’s EIP-7702 smart-account mechanism to install malicious “sweeper” code that could continue transferring funds even after Binance restricted withdrawals and hot-wallet services. Binance detected unusual activity within minutes, but the malicious authorization remained active for about four hours. The incident highlights why crypto firms need protection beyond monitoring blockchain transactions. Security teams should closely control developer identities, credentials, signing systems, repositories, cloud environments, and transaction authority. They also need mechanisms for quickly revoking privileges, pausing transfers, isolating wallets, and stopping wallet refills. These measures should be tested regularly rather than first relied upon during an attack. The broader lesson is that cryptocurrency security depends on detecting suspicious activity early, limiting who and what can authorize transactions, and having rehearsed containment procedures that can operate quickly when normal controls are bypassed.

Read Original Article →

When Your Email Goes Down, Does Your Incident Response Go With It?

When a major platform like Microsoft 365 experiences an outage, it exposes a critical vulnerability in most corporate incident response strategies: the tools required to manage the crisis are often hosted on the exact network that just went down. A recent outage proved that simply maintaining an alternative communication method, such as a phone tree or an external messaging app, is not enough to sustain an effective response. While these fallback options keep people talking, they fail to provide the structured playbooks, task assignments, and timestamped decision logs necessary for proper incident management and regulatory compliance. Even without malicious intent behind an outage, the resulting confusion and backlog of unscreened messages create prime opportunities for attackers to strike. To truly protect the organization, security teams must establish a dedicated, out-of-band incident response platform that operates independently from the primary corporate stack. This ensures that when the main system fails, responders can still orchestrate their workflow, track obligations, and maintain clear command without missing critical regulatory deadlines or losing essential evidence of their actions.

Read Original Article →

Daily Tech Digest - October 23, 2026

Quote for the Day
“A startup is not a smaller version of a large company.”
— Steve Blank
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Convergence of Cyber, Space and Electromagnetic Resilience

The article describes how critical infrastructure security is being reshaped by the convergence of cyber, space, and electromagnetic risks. It explains that satellites have evolved from simple communication tools into high‑value targets that carry mission‑critical enterprise data, making even short detection delays dangerous. The rapid growth of low‑cost launches and nanosatellites has crowded orbital paths, increasing collision risks and complicating tracking. At the same time, whoever controls the space‑layer communication channels gains a strategic advantage, especially when terrestrial links are disrupted. The piece argues that modern resilience requires a C5ISR‑style approach, where cybersecurity, space operations, and electromagnetic protection are treated as one integrated domain. This is because satellites, radio‑frequency systems, and digital networks are now tightly intertwined, and attacks often exploit the seams between them. Traditional ground‑based communication architectures are no longer sufficient for industries that operate across remote, maritime, or mobile environments. The article’s message is steady: resilience now depends on cross‑domain visibility, faster detection, and treating space assets as part of the enterprise security perimeter rather than a separate technical layer.

Read Original Article →

Sovereignty vs. security: Microsoft’s Roger Halbheer says you’re asking the wrong question

In a recent interview, Roger Halbheer, Microsoft’s Customer Security Officer, argues that organizations fundamentally misunderstand digital sovereignty by treating it as a procurement issue rather than a security challenge. He notes that business leaders often demand complete independence from outside access, which is practically impossible, and end up simply buying a localized server location along with an assurance statement. Instead, Halbheer urges boards to make calculated risk decisions for each specific workload. He warns that moving operations entirely on-premises to achieve sovereignty drastically reduces the speed at which organizations can detect and respond to security threats, making them highly vulnerable in a landscape where attackers operate in mere hours. Maintaining such systems internally requires immense resources, money, and skilled personnel that most companies lack. Furthermore, he clarifies that merely storing data in Europe does not protect it from government access, as authorities in almost every jurisdiction have legal avenues to compel data providers. Ultimately, Halbheer stresses that a compromised system can never truly be sovereign, making robust security the ultimate foundation for data protection.

Read Original Article →
Article Thumbnail

Data Mesh vs. Data Fabric: Which Approach Is Right for Your Organization?

Data mesh and data fabric are distinct but complementary approaches to managing distributed enterprise data. Data mesh decentralizes data control, handing ownership directly to the business units that understand it best. By treating data as a product, it empowers individual teams to manage their own resources while adhering to shared, overarching rules. This model minimizes bottlenecks and speeds up independent decision-making but requires a shift in company culture to support decentralized ownership. Data fabric, on the other hand, creates a unified technology layer across an organization's various platforms and clouds. Relying heavily on active metadata, it automatically connects, discovers, and governs data, making it readily accessible without moving it from its original location. This centralized, top-down strategy simplifies data integration and strengthens readiness for artificial intelligence. Ultimately, organizations do not necessarily have to choose one over the other. The most effective data architectures often combine the domain-driven quality and autonomy of a data mesh with the automated integration and unified intelligence of a data fabric.

Read Original Article →

Why AI Raises the Stakes on Process Ownership

The integration of artificial intelligence into enterprise operations is fundamentally changing how organizations approach process ownership, data management, and decision-making. According to John Steele, CIO at Komatsu Australia, AI allows companies to outsource aspects of thinking at scale, which brings both new opportunities and significant dependencies. Steele introduces the concept of "intellectual sovereignty," which involves three key areas: infrastructure, software, and knowledge. Organizations must decide where to run applications, manage vendor relationships, and determine which tasks to automate versus which to keep for employee development. When it comes to shared platforms, there is a constant tension between standardizing systems to lower costs and maintaining specialized tools that add unique value to specific departments. To navigate these trade-offs, businesses need mature, end-to-end process ownership that crosses divisional lines. This prevents fragmented, isolated optimization and ensures that technology choices actually benefit the enterprise as a whole. Ultimately, executive leaders do not need to make every technical decision, but they must agree on clear principles regarding acceptable risks, costs, and vendor dependencies to successfully guide AI adoption and transformation.

Read Original Article →

How Do You Demonstrate Resilience?

Showing that your security program is resilient requires adjusting your message to fit your audience. While your technical teams need specific operational metrics like mean time to detect and recover or vulnerability patch speeds, the executive suite and the board require a fundamentally different language. They want to know the "so what." When communicating with leadership, you must translate technical gaps into tangible business impacts. Will a compromised credential shut down operations? Will an unpatched server lead to a complete system takeover? Rather than just listing out threats like ransomware, focus on providing a clear narrative of consequence that allows leadership to make informed decisions about resource allocation and risk acceptance. Ultimately, the C-suite evaluates resilience by looking at recovery time and how quickly revenue operations can resume after an incident. Effective communication proves to management that the security team is not merely fixing isolated issues but actively lowering the likelihood of material harm and keeping the organization capable of moving forward.

Read Original Article →

The adversary economy: How threat actors are reacting to PHP2Shell

The recent disclosure of two critical, unauthenticated remote code execution vulnerabilities in PHP—collectively known as PHP2Shell—has triggered widespread panic across the cybercriminal underground. Because PHP powers a vast majority of the modern web, it is also the foundational infrastructure for dark web marketplaces, illicit forums, and communication platforms. Following the disclosure, major criminal sites like BreachForums rushed to take their servers offline to implement emergency patches and mitigate risks. These threat actors treat the vulnerabilities as severe existential threats because a successful exploit would expose sensitive member identities, stolen credentials, and internal communications to both rival hacking groups and global law enforcement agencies. This swift reaction mimics legitimate corporate incident response, highlighting that the adversary economy operates on the same risk management principles as standard businesses. Ultimately, the urgency displayed by these cybercriminals serves as a stark warning. Organizations still running unsupported versions of PHP must prioritize patching and migrating their systems immediately before automated exploit chains and malicious actors capitalize on this critical vulnerability.

Read Original Article →
Article Thumbnail

Enterprises don’t need artificial general intelligence. They need artificial specific intelligence

A significant majority of enterprise AI pilot programs fail to generate measurable profits, but the fault lies not with the models themselves or a lack of user skill. Instead, failure stems from a fundamental misalignment: large language models are built by labs aiming for artificial general intelligence, while businesses require highly specific solutions. Commercial models excel at reasoning and hold vast public knowledge, but they lack the undocumented domain expertise unique to individual enterprises. Because they remain static after training, these models cannot learn the nuances of a business as it operates. To overcome this specificity gap, organizations must redefine success based on their own goals rather than relying on generic benchmarks. They should select pilot projects that reflect real-world complexity, complete with messy data and unwritten rules. Furthermore, enterprises must supply models with precise context using dynamic evaluation loops, while integrating their most knowledgeable subject-matter experts directly into the pilot process to validate outputs and correct mistakes.

Read Original Article →

Hacker Conversations: Corey Thuen and the Evil Bit

Corey Thuen is the founder and CEO of Gravwell, a data analytics company, and a hacker who values what he calls the "evil bit" in his team members. He describes this trait as an inherent, adversarial mindset that naturally looks for ways to exploit systems. However, Thuen stresses that this perspective does not equate to a lack of morals. Instead, it is a skill that can be channeled to improve security and build better defenses. Thuen's interest in computers began in his youth, driven by curiosity rather than malicious intent. His career path led him to the Idaho National Laboratory, where he specialized in the security of industrial control systems. Later, he co-founded Southfork Security, which unfortunately ended in a messy legal dispute with his former employer over open-source software. Despite the court temporarily stereotyping him as a malicious hacker, Thuen continued his work in offensive security before ultimately launching Gravwell. Today, he combines his natural hacker instincts with an entrepreneurial drive, building tools that challenge assumptions and strengthen system defenses.

Read Original Article →
Article Thumbnail

How Dependency Mocking Affects CI/CD Pipeline Reliability

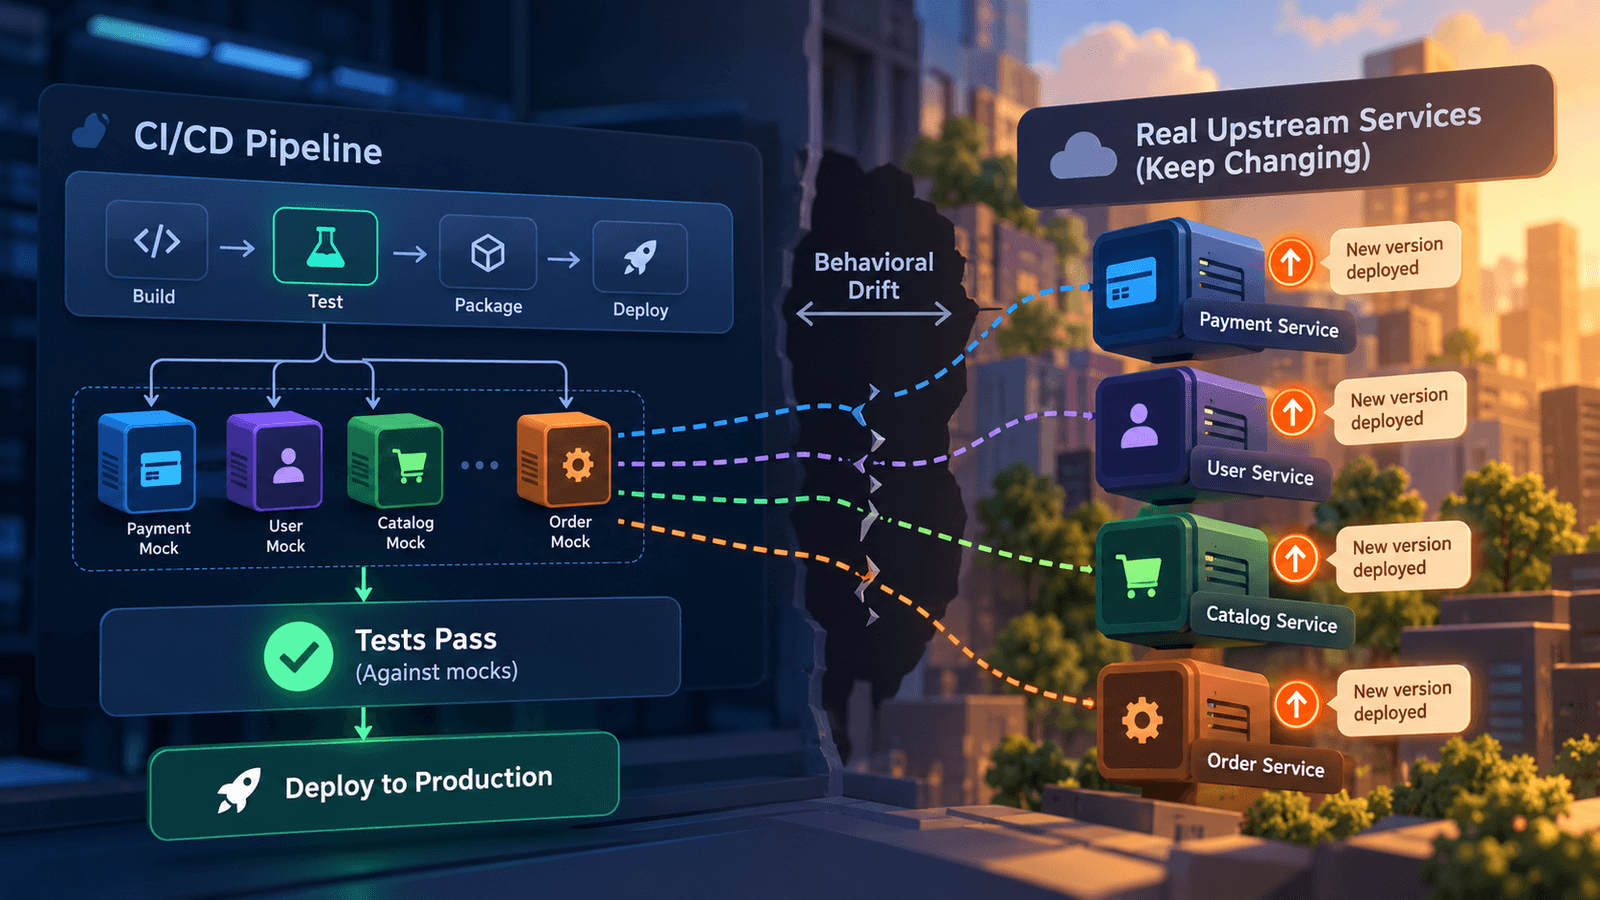
The article explains that dependency mocking can quietly undermine the reliability of CI/CD pipelines because mocks often drift away from the real behavior of upstream services. A pipeline may appear healthy — tests pass consistently, runtimes are stable, and flakiness seems low — yet still provide misleading assurance because it is validating code against outdated assumptions. As upstream microservices evolve through frequent independent deployments, mocks remain frozen in time, creating a widening gap between test environments and production reality. This leads to “operational reliability” without “informational reliability,” where the pipeline runs smoothly but no longer predicts how the software will behave once deployed. The piece stresses that every upstream deployment is a potential accuracy event for mocks, and without automated refresh mechanisms, pipelines accumulate silent risk. It also notes that teams often misinterpret green builds as proof of correctness, even though the pipeline has no visibility into real service behavior during test execution. The article’s steady message is that meaningful reliability requires connecting mock maintenance to upstream changes and validating mocks against real traffic so test results continue to reflect production truth.

Read Original Article →

The Great AI Regret: Why AI Fatigue Is a Leadership Problem, Not a Technology One

Despite the heavy investment in artificial intelligence, many employees feel increasingly anxious and disconnected from their work. Recent research shows a significant portion of knowledge workers are deeply nostalgic for how they worked before AI, and some would even prefer to remove these tools entirely. This growing fatigue and mistrust do not stem from the technology itself, but from poor leadership and implementation. Instead of freeing staff from tedious tasks, rushed rollouts often leave employees feeling surveilled, stripped of their creativity, and unfairly measured against machines. In many cases, people spend more time checking AI-generated output than they save by using it. To solve this problem, leaders must change their approach. Organizations should clearly communicate why these tools are being introduced and ensure they support meaningful work rather than just pushing for blind efficiency. By preserving human expertise and keeping people in control of important decisions, businesses can rebuild trust. When introduced thoughtfully, AI can be a helpful assistant rather than a source of frustration, leading to a much healthier workplace.

Read Original Article →

Daily Tech Digest - September 20, 2026


Quote for the day:

“The more I read, the more I acquire, the more certain I am that I know nothing.” -- Voltaire

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


Brain-Machine Interfaces Are Advancing: What Leaders Need to Know About Neurotechnology

The convergence of artificial intelligence, smaller electronics, and advanced materials is accelerating the steady development of brain-machine interfaces, allowing for practical communication between human brains and digital systems. While this field is currently focused on healthcare, with recent clinical studies showing paralyzed patients successfully using neural interfaces to control devices and communicate independently at home, its applications will soon expand. In the near future, industries such as education, manufacturing, and assistive technology will likely adopt these emerging tools to improve human performance and overall accessibility. By the end of the decade, the technology is expected to feature more accurate signals, less invasive hardware, and better machine interpretation of brain activity. Rather than guessing which specific device will dominate the market, organizations and leaders should prepare for these predictable advancements now. This means tracking improvements in neural decoding, exploring diverse interface methods like ultrasound, and considering how neural data might fit into future product lines. Just as importantly, the widespread use of neurotechnology will create new challenges surrounding data privacy, system compatibility, and user control over sensitive neural information. Solving these practical problems will offer significant opportunities for those who calmly anticipate the steady progress of neural engineering and plan accordingly.


Opinion: Tech enables transformation, people achieve it

Daire Cunningham’s article explores why so many organizations struggle to get real value from artificial intelligence, despite the technology being widely available. He notes that while 88% of businesses use AI in some capacity, only a third have managed to scale it across their operations. The core issue, he argues, isn’t a lack of access to advanced tech, but rather the underlying condition of the organizations trying to use it. When companies rush to adopt AI, they often start by looking for a specific tool instead of identifying the actual business problem they need to solve. To succeed, leaders must work backward: map out their processes, figure out where the information is kept, and spot the real bottlenecks. A major roadblock is poor data readiness—many businesses have years of accumulated, disorganized data and permissions. AI tends to expose these underlying flaws rather than cause them. Ultimately, Cunningham believes digital transformation is about rethinking how work gets done, not just adding new software. While AI can process data faster and tackle complex tasks, human judgment and oversight remain essential. True transformation happens when a company prepares its data foundation and empowers its people to use technology responsibly.


CIOs offer guiding principles on how to achieve AI sovereignty

The article discusses the growing importance of AI sovereignty for Chief Information Officers (CIOs). This concept is centered on maintaining control over an organization’s entire AI ecosystem, which encompasses data, models, and the infrastructure hosting those models. As AI technology becomes increasingly integrated into business operations, organizations face mounting risks related to data privacy, regulatory compliance, and potential vendor lock-in. To manage these challenges effectively, CIOs recommend establishing clear guiding principles. First, it is crucial to create a comprehensive inventory of all AI resources currently in use, as you cannot manage what you do not track. Second, organizations must implement robust data and usage controls to monitor information flow and quickly identify any policy violations. This proactive approach helps secure sensitive data. Third, companies should update their incident response plans specifically to address potential AI-related breaches, ensuring they can act swiftly if issues arise. Finally, maintaining transparency and auditability is essential. Knowing who accessed data and how AI tools influence decision-making helps build trust and ensures regulatory compliance. Rather than viewing AI sovereignty as a simple compliance checklist, leaders should treat it as a fundamental strategy for the long-term success and security of the enterprise.


Children's Data Protection in the Age of EdTech and Platform Design

The digital age has made children’s data collection widespread, from location tracking and educational data to behavioral and voice information. While some of this is meant for learning or safety, the concern is that such data can be used for profiling, targeted ads, or boosting engagement without parental consent. This has made data protection laws surrounding children increasingly relevant. India's Digital Personal Data Protection (DPDP) Act, 2023 defines a child as anyone under 18, which is a higher threshold than seen in many other countries. This act requires platforms to secure verifiable parental consent before processing a child’s data and forbids processing that could harm a child’s well-being. Additionally, the DPDP Act bans the tracking, behavioral monitoring, and targeted advertising directed at children, though it provides some exceptions for safe uses in healthcare, education, or child safety. Internationally, there are variations in how children's data is handled. In the United States, COPPA applies to children under 13, while the European Union’s GDPR sets the default age at 16, though member states can adjust it to 13. The UK’s Children’s Code requires platforms that children are likely to use to have high privacy settings by default. For platforms dealing with children's data, balancing data retention limits with educational needs requires clear strategies and compliance checks.


Most enterprises are failing to translate talk into meaningful dependency mapping

The recent feature on digital sovereignty highlights a significant gap between what organizations want and what they can actually achieve. While most companies express a strong desire to regain control over their digital infrastructure, the reality is that true independence remains out of reach for many. The truth is that achieving digital sovereignty is not simply about building internal data centers or buying local software; it requires deep visibility into existing information systems and having credible exit options from major service providers. Unfortunately, most enterprises currently lack these fundamental building blocks. Over the past fifteen years, a rush toward cloud computing has left many businesses heavily dependent on a handful of dominant technology giants. This dependency makes it incredibly difficult to pivot or change providers without facing steep costs and major operational disruption. As artificial intelligence becomes central to business strategy, the stakes for retaining control over data and computing power are higher than ever before. The article suggests that instead of pursuing total independence, leaders should focus on preserving choice. By prioritizing flexible tools and establishing clear governance, organizations can gradually build resilience. Ultimately, sovereignty is about making smart decisions today that prevent complete vendor entanglement in the future.


Agentic Systems and Design Patterns

The shift toward agentic artificial intelligence marks a move from simple text generation to setups that can plan, take action, and learn from their mistakes. When building these systems, developers must first choose an overall structure. A single agent approach is easier to build and manage, making it a great starting point, though it can struggle with complex or extended tasks. Conversely, a multiple agent system uses an orchestrator to delegate work to specialists, which boosts reliability through teamwork but requires careful coordination. Beyond the basic structure, six core design patterns drive how these models function. The ReAct pattern mixes logical thinking with concrete actions in a loop, while CodeAct allows agents to write and test code to achieve their goals. Self reflection acts as an internal critic to refine outputs and fix errors. Basic tool use lets agents interact with outside software, and Agentic RAG improves how they fetch and verify information. Finally, the multiple agent workflow handles massive tasks by dividing them into smaller parallel jobs. For the best results, start with a simple single agent setup and only add complexity when the task demands it. Strong safeguards, like strict iteration limits and clear tool definitions, keep these systems reliable and easy to monitor.


What OT Resilience Actually Controls

The article from SC Media explains that recovering operational technology (OT) after a cyber incident requires a fundamentally different approach than recovering standard IT systems. While IT disaster recovery focuses on system availability—getting servers and applications back online—OT recovery requires "safe-state validation." This means ensuring the manufacturing process can be controlled safely before restarting production. The challenge is that standard IT backups often miss crucial OT engineering data, such as process configurations, device programming, and safety system logic. Without these, a restored system might appear functional but lack the specific parameters needed to operate safely. The author outlines five common failure scenarios in OT resilience, including ransomware affecting control systems, vendor platform outages, and control logic tampering. These scenarios highlight the need for specialized OT backup architectures and recovery procedures. Ultimately, true OT resilience involves validating configurations at the device, system, and process levels, often requiring specialized engineering expertise. This validation step adds time to the recovery process but is essential to prevent unsafe conditions that could lead to physical harm or environmental damage.


Achieving data sovereignty for SaaS with confidential containers and quantum-safe networking

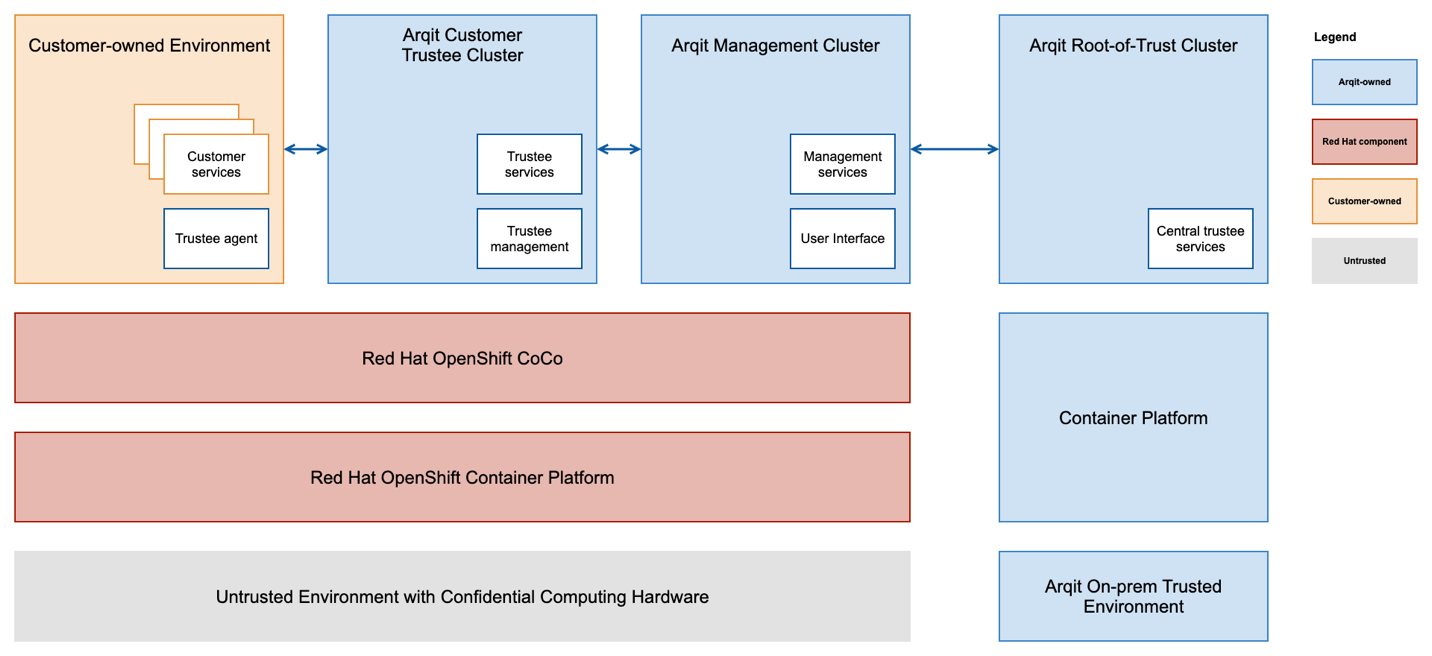
Software vendors hosting services on the public cloud face increasing pressure from customers who want to keep their data secure and private. Often, customers prefer on-premise solutions, which are harder to manage and scale for vendors. A better approach allows vendors to keep their services in the cloud while offering robust security through cryptographic controls, specifically using confidential computing. This technology secures data processed in untrusted environments by isolating it in a trusted execution environment (TEE). Red Hat and Arqit have introduced a setup that uses confidential containers and quantum-safe networking to protect data in transit. They applied this to Arqit's Encryption Intelligence (EI) platform. In this setup, services and data are isolated from the host environment, allowing customers to maintain control over their data while protecting the vendor's intellectual property. The architecture involves three clusters operating in the untrusted environment, communicating via a quantum-safe connection. Trust is established by an outer trustee in a trusted on-premise environment, which verifies the inner trustee in the cloud. This combination of confidential containers and quantum-safe protection for data in transit offers a practical alternative to on-premise deployments, providing strong assurance over data security and sovereignty for both vendors and customers.


AI-led SOC infrastructure shifts from raw data to outcomes

The article discusses a shift in how modern Security Operations Centres (SOCs) measure success in an AI-driven environment. Historically, SOCs focused on volume metrics, such as alerts processed or data ingested, but this model struggles against modern threats across distributed environments. Today, the focus is shifting to measuring outcomes like risk reduction, analyst capacity, and decision quality. The traditional volume-driven model leads to rising costs, overwhelmed analysts, and incremental improvements, failing to deliver clear returns on investment. While AI is viewed as a solution, it has struggled to deliver value when treated simply as an overlay, lacking transparency and integration. To overcome these limits, organizations must build SOCs around productivity rather than throughput, connecting technology investments with operational impact. In this model, AI isn't measured by its theoretical capability but by the work it completes alongside human analysts. A critical component is the use of "Agentic AI" as an execution layer, which coordinates investigations and decisions rather than functioning in isolation. For AI to be effective, it must also be governed to ensure actions are explainable and align with organizational policies, allowing security leaders to demonstrate responsible use and measurable security outcomes.


Data sovereignty is a control problem, not a geography problem

The article argues that data sovereignty is fundamentally about control, not geography. Many organizations assume that storing data within national borders is enough, but the author explains that this view is too narrow. True sovereignty depends on knowing who controls identities, administration, infrastructure, and legal authority over the data. Recent events have exposed how fragile digital infrastructure can be, from attacks on subsea cables to large‑scale outages like the CrowdStrike incident, which disrupted critical services worldwide and led to major financial losses. At the same time, new regulations and the rise of AI have increased the stakes, since sensitive information and intellectual property now flow through cloud‑hosted models governed by foreign jurisdictions. The article stresses that organizations often lack visibility into where their data lives, who can access it, and which laws apply. To regain sovereignty, they must demand transparency from providers, understand dependencies, and treat governance as an architectural requirement rather than an afterthought. Cost and speed still matter, but they can’t outweigh resilience and accountability. Sovereignty, the author concludes, isn’t about abandoning the cloud—it’s about ensuring organizations retain meaningful control so they can manage risk and respond confidently when incidents occur.

Daily Tech Digest - September 17, 2026


Quote for the day:

“The moment you’re comfortable is the moment you stop growing.” -- Allison Dunn

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI Security Spending Jumps as Fear Outpaces Proof of Value

Companies are heavily investing in artificial intelligence for cybersecurity, often prioritizing swift adoption over clear proof of its effectiveness. Driven by the transition of AI from a testing phase into active use, along with the rising deployment of AI by bad actors, organizations feel immense pressure to keep pace. For many chief information security officers (CISOs), fear of falling behind and the need for "blame insurance" against potential breaches are accelerating spending. In fact, a significant number of CISOs cite AI as their top priority for new budget allocations. Despite this aggressive funding, the most common AI implementations often fall short of delivering the highest returns. The challenge is compounded by the inherent difficulty of measuring the return on investment (ROI) in cybersecurity, where success is defined by preventing events like data breaches rather than generating direct profit. Experts advise a more deliberate approach, urging organizations to move past the hype. Rather than adopting AI simply for the sake of having it, companies should focus on areas where the technology can genuinely lower risk and handle repetitive tasks. Thoughtful integration, backed by strong governance and clear goals, will ultimately determine which organizations benefit most from their AI cybersecurity investments.


Salesforce’s massive outage exposes the hidden risks of cloud dependencies

A massive Salesforce outage during its flagship Dreamforce event has underscored the hidden architectural risks of cloud dependency. A roughly seven-and-a-half-hour service disruption on September 16 impacted multiple instances across all regions, initially stemming from a core system component struggling with an "external dependency failure" linked to a legacy login server. Although the issue was resolved by mid-afternoon through manual interventions after automated rolling restarts fell short, the outage highlights that cloud systems do not eradicate architectural vulnerabilities. Instead, these dependencies can become enterprise risks when a central platform fails. The service failure emphasizes the necessity of looking beyond immediate access restoration. Enterprises must transition into a reconciliation phase to address "temporal data problems," ensuring transactions, scheduled jobs, and downstream systems remain consistent. The disruption proves that a legacy component's age is less critical than its role within the system's dependency graph. Organizations should not equate modernization simply with replacing old technology. They must assess dependency concentration, failure blast radius, and isolation strategies. While there are no signs of a security incident, industry experts suggest automated AI tools or recent workforce reductions might have played a role in the disruption. Future post-incident reviews must provide clear insights into failure propagation and preventive measures.


Crypto Industry Figures Blackmailed by Revolut's Hacker

A recent data breach at the British financial services company Revolut has exposed the sensitive personal information of roughly six hundred and eighty high-profile cryptocurrency exchange customers. An extortion group calling itself "Iamnotavillain" orchestrated the attack without breaking into the bank's secure servers. Instead, the criminals gained access to a legitimate Italian government email system. By posing as authorized law enforcement officials for several months, they submitted fraudulent data requests to the bank's compliance team. Believing the inquiries were authentic, employees handed over highly confidential customer files. This exposed data included passport copies, verification photographs, home addresses, phone numbers, and detailed transaction histories. The attackers specifically targeted users with substantial digital asset activity, and notable industry figures such as former Mt. Gox executive Mark Karpelès were among the victims. After securing these detailed identity packages, the hackers launched a blackmail campaign. They demanded a ransom payment of three million dollars, requested in the privacy-focused digital currency Monero, to prevent the information from being released. The extortionists even set up a public website with a countdown clock, threatening to sell the stolen records to other criminal organizations if the company failed to meet their demands within a strict twenty-four hour window.


Stop Treating CSS Container Queries Like Traditional Media Queries

The article clarifies the common misconception that CSS container queries and media queries serve the same purpose. Despite having a 94% browser support rate, container queries are vastly underutilized. Many developers mistakenly treat them interchangeably because of their similar syntax, but they fundamentally differ in their approach to responsive design. Media queries focus outward on the "macro" layout. They check the viewport's dimensions to adjust overarching page structures, such as main grids or full-width headers. Conversely, container queries look inward at "micro" layouts. They allow individual components, like cards or widgets, to adapt based on the available space within their specific parent container, rather than the entire screen size. This distinction is crucial for creating reusable components that maintain their layout integrity regardless of where they are placed on a page. The author advises against replacing media queries entirely with container queries. Instead, the focus should be on a separation of concerns. Media queries remain ideal for page-level adjustments, while container queries shine when a component's layout depends on its immediate context. However, container queries require an extra wrapper element, cannot query their own block size without collapsing, and cannot accept custom property values. Ultimately, understanding these differences unlocks more resilient responsive design.


Trust becomes the product: Five takeaways from the Splunk .conf26 keynotes

The recent Splunk conference centered on a critical theme for modern businesses: trust is the most important element when deploying artificial intelligence agents. As these agents shift from being simple tools to functioning as autonomous digital teammates, they are handling complex tasks around the clock. This shift requires a strong system of record to ensure they act appropriately. A major takeaway is the necessary merging of system monitoring and security. Because it is difficult to tell the difference between a software error, a security breach, or a poorly executed AI command, companies must combine their monitoring and security data to accurately diagnose issues. Cost management is another significant focus. AI agents can quickly become expensive to run if they are not carefully controlled, meaning businesses need better visibility into their data usage to prevent unexpected bills. Furthermore, managing the massive amounts of data required for these systems must become more affordable and efficient so companies do not have to choose which information to keep. Ultimately, organizations are treating AI agents like new employees. They are granting them limited permissions initially and slowly increasing their responsibilities as they prove their reliability, ensuring that human oversight remains an essential part of the process.


Architecting for the Knowledge You Can’t Capture

The article argues that organizations often underestimate how much essential knowledge never makes it into their documentation or AI systems. It opens with a familiar scenario: an experienced engineer is asked to “document everything” before leaving, but what gets captured is only the clean, idealized version of the work. The subtle judgments, exceptions, and sensory cues that guide real decisions never appear in the flowcharts or transcripts, leaving future teams without the insight needed to handle unusual situations. The author explains that this gap reflects the nature of tacit knowledge—skills and perceptions people rely on but rarely articulate. Modern AI can learn from examples, but when expertise is rare or incidents are infrequent, there simply isn’t enough data for models to infer the missing judgment. The article proposes a structured elicitation protocol that pushes experts to clarify thresholds, exceptions, evidence, and escalation paths, turning vague statements into actionable rules. It also outlines a four‑layer architecture—capture, representation, serving, and transmission—to preserve context, surface uncertainty, and support apprenticeship when documentation falls short. The core message is that organizations must design for the knowledge people can’t easily express, or their AI systems will remain blind to the expertise that actually keeps operations running.


How to keep AI-generated code aligned with your standards

The article discusses the challenge of keeping AI-generated code aligned with organizational standards. As more developers use AI coding tools, the risk of accumulating technical and operational debt increases if code is only judged by whether it works functionally. To prevent this, engineering teams must clearly document their non-functional requirements, such as security rules, performance expectations, and data governance policies. These standards should not remain hidden as tribal knowledge. Instead, they must be explicit, machine-readable, and fed into the AI tools as context before any code is generated. Furthermore, organizations should enforce these rules by turning them into automated acceptance criteria within their continuous integration and delivery pipelines. This ensures that any AI-generated code is automatically checked for compliance, security, and performance before it merges. Experts recommend treating AI output as untrusted until it passes the exact same rigorous reviews, tests, and monitoring as human-written code. Ultimately, governing AI-generated code requires shifting from manual audits to automated, systemic enforcement. By maintaining clear specifications, integrating standards into automated testing, and adapting context engines to learn from past decisions, development teams can safely scale their AI use while keeping code quality strictly aligned with enterprise expectations over the long term.


Human-in-the-loop oversight is critical for enterprise AI: 4 experts explain why

Enterprise AI systems increasingly require human-in-the-loop (HITL) oversight to ensure accountability and mitigate risks associated with flawed AI outputs. The FTC's actions against DoNotPay highlight the legal perils of deploying unchecked AI, driving the adoption of software with built-in human escalation for complex workflows. While HITL is meant to catch model errors before they become compliance or legal issues, experts warn against relying solely on an AI's self-assessed confidence score to trigger review, as a confident model can still be wrong. Effective HITL design involves intelligent routing that escalates issues to the appropriate personnel based on organizational risk tolerance, rather than a simple binary system. Furthermore, real oversight demands more than a rubber-stamp approval process; it requires reviewers with the context and time to actually evaluate the AI's work and overturn it if necessary, combating the tendency for reviewers to become biased in favor of the AI's suggestions. Legislation like the EU AI Act necessitates demonstrable proof of this oversight through clear audit trails. Successful implementations, like those by Nominal and IgniteTech, often mandate human approval for critical actions and use "grounding," which forces the AI to rely only on verified company data or escalate the query if it lacks the information, ensuring accountability remains firmly with human operators.


Passkeys in the post-quantum era: Why FIDO needs more than new algorithms

The provided article discusses the need to prepare the FIDO2 ecosystem, which includes passkeys, for the post-quantum era. Passkeys, which rely on asymmetric cryptography, are vulnerable to future quantum computers that could potentially break the current public-key algorithms like RSA and elliptic curve cryptography.

The author, Johann-Philipp Thiers, explains that transitioning to Post-Quantum Cryptography (PQC) is a complex process. It goes beyond simply swapping out algorithms. PQC algorithms often result in larger keys and signatures, which can be problematic for resource-constrained authenticators like hardware security keys due to memory, processing power, and transport limitations.

Furthermore, the transition involves updating the entire trust chain, including metadata service signatures, certificate formats, and relying party support. The author emphasizes that FIDO’s current crypto-agility is beneficial but requires coordination among various stakeholders, such as operating systems, browsers, and certification programs. Practical demonstrators are crucial for identifying engineering challenges like message sizes, performance impacts, and interoperability issues. Ultimately, securing passkeys against quantum threats requires a gradual, coordinated effort involving standardization, testing, and careful engineering to ensure their long-term viability.


AI made software development unrecognizable. Is cybersecurity next?

Artificial intelligence is rapidly reshaping the cybersecurity landscape, much as it has already transformed software development. While the shift in security might take slightly longer, experts predict that fundamental changes are inevitable. Security Operations Centers will soon rely heavily on autonomous agents to perform initial triage, allowing human analysts to focus on complex oversight and critical decisions. This transition is essential because AI is drastically increasing the discovery of vulnerabilities, creating a massive backlog that security teams struggle to absorb and remediate. Furthermore, as attackers begin using AI to launch high speed automated threats, organizations must deploy their own rapid containment systems to respond effectively. This shift will also alter the cybersecurity workforce. Rather than eliminating jobs, organizations will likely adopt flatter teams featuring highly experienced senior professionals at one end and junior staff at the other, putting pressure on middle management roles. AI might also serve as a unifying interface to manage sprawling security toolsets. To prepare, security leaders should begin testing agents on high volume tasks while establishing strong governance frameworks. Most importantly, leaders must ensure that every autonomous agent has a designated human owner who remains fully accountable for its actions and potential failures within the organization.