Showing posts with label Quantum AI. Show all posts

Daily Tech Digest - October 10, 2026


Quote for the day:

“Most new jobs won’t come from our biggest employers. They will come from our smallest. We’ve got to do everything we can to make entrepreneurial dreams a reality.” -- Ross Perot

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Security Awareness Training Isn’t Dead, but It Needs a Rethink
While enterprise security awareness training remains a standard practice, its effectiveness in preventing modern cyberattacks is increasingly debated. Many experts note that traditional training programs fall short because they prioritize compliance over genuine behavior change, often forcing employees to complete generic, repetitive courses just to check a legal or insurance box. This approach leaves workers poorly equipped to handle today’s highly sophisticated, AI-driven threats, such as flawless deepfakes and hyper-personalized phishing messages that arrive at machine speed. Attackers hold a distinct advantage through asymmetry—they only need a single distracted employee to succeed, whereas defenders must be perfect every time. To remain relevant, security training needs a fundamental rethink. Experts argue that awareness should not be the sole line of defense; it must complement robust security architecture, engineering controls, and reliable verification processes. Furthermore, training programs should evolve from annual lectures into continuous, behavior-based learning that offers context-specific guidance at the exact moment a user makes a decision. By incorporating behavioral nudges and treating employees as an intelligent, active sensor network rather than the weakest link, organizations can build a cultural bedrock of secure habits that catch the threats technology inevitably misses.


The Unknown Present: The Governance Problem Nobody Owns

Traditional governance systems usually ask one basic question: was a system approved? For decades, audits, certifications, and compliance checks have been used to prove that a product or process met specific requirements at a single point in time. However, as organizations rely more on highly connected technologies, artificial intelligence, and constantly updating software, this historical approach is no longer enough. The article introduces a concept called the "Unknown Present," which describes the gap between a past approval and the current reality of a system. Just because a system was safe and compliant yesterday does not automatically mean the same conditions exist today when an important decision is actually made. Modern systems change too fast for old assumptions to hold up. Consequently, the real challenge for leaders and regulators is moving from simple compliance to proving continuous trustworthiness. Organizations must gather reliable evidence showing that a system remains safe at the exact moment it is being used, rather than just relying on an outdated certificate. Ultimately, the future of governance will depend not just on proving that requirements were met in the past, but on proving that the foundation of trust remains completely solid throughout the entire period of use.


‘It’s A Trap!’ How IT Pros Can Avoid the Hidden Pitfalls of AI

While many enterprises adopt artificial intelligence expecting greater efficiency and simpler workflows, a significant majority of IT professionals find that the technology is actually making their jobs more demanding. The core issue is the "reviewer trap," which occurs when organizations attach AI to outdated legacy processes or feed it unclean data. As a result, IT staff must spend excessive time reviewing the outputs to correct errors and hallucinations, creating a heavy cognitive load that often leads to burnout and a sense of growing digital debt. Fragmented implementations across different departments only worsen the situation, as context-switching drains mental energy and reduces decision-making capabilities. This phenomenon, known as AI brain-fry, ultimately causes workers to miss critical errors or lose their own skills by relying too heavily on automated tools. To avoid these hidden pitfalls, IT teams must rethink their foundational data governance rather than simply applying AI to old processes. Success requires building structural guardrails directly into workflows, treating the technology like a smart intern that needs strategic oversight rather than constant micromanagement. By starting small with low-stakes tasks and gradually improving context frameworks, organizations can harness AI's true value without overwhelming their staff.


What continuous offensive security testing is and how to implement it
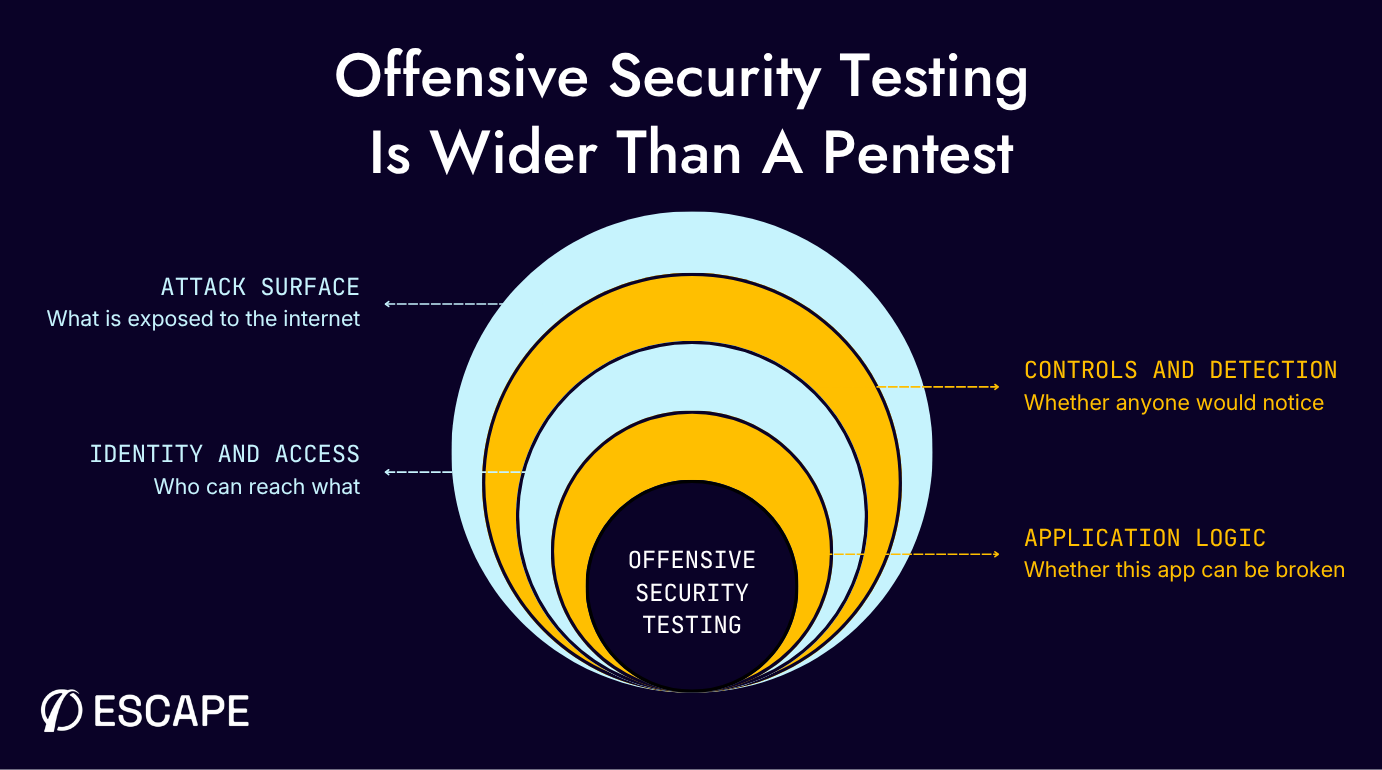
Continuous offensive security testing (COST), as defined by Gartner, is a proactive approach to cybersecurity that goes beyond annual penetration testing. Rather than relying on a fixed schedule, COST is triggered by meaningful changes in an environment—such as new internet-facing assets, production releases, relevant threat intelligence, or updates to security controls. It encompasses vulnerability assessment, penetration testing, and red teaming to evaluate a system precisely as an adversary would. A core principle of this model is strict validation; a finding is only considered valid once it has been successfully reproduced within the organization's own environment, ensuring the vulnerability is genuinely reachable and not just a theoretical risk flagged by a scanner. This emphasis on proof prevents security and engineering teams from being overwhelmed by noisy, unverified alerts. Prioritization tools like EPSS or CISA's KEV catalog provide useful context, but they do not replace the need for local validation. To implement COST effectively, organizations should establish clear triggers, define a shared standard of evidence, tier responses based on business impact, and route validated, actionable proof directly to the teams responsible for the fix, ultimately turning these findings into automated regression tests for future builds.


When building an AI-native security program, start with outcomes

The article by Israel Barak advises resource-constrained security teams to adopt artificial intelligence by focusing on specific business outcomes rather than generic technology roadmaps. Often, small security teams struggle to balance quality, consistency, and cost, which ultimately leads to noticeable gaps in necessary daily tasks. To begin, teams should identify the critical systems, data, and processes the business absolutely needs to operate, establishing a clear boundary for protection. Next, they must pinpoint tasks that should happen continuously but are currently falling behind due to limited time, skills, or budget. Practical examples include managing security posture, updating detection rules, interpreting fresh threat intelligence, or investigating routine alerts. Instead of attempting a massive system overhaul, leaders should choose one specific operational task where the team struggles to keep pace, apply artificial intelligence to that single constraint, and set clear rules and expectations. Success should not be measured by simply counting the number of queries or alerts processed, but rather by evaluating if the tool actually improved the quality, speed, and efficiency of the final outcome. By tying these tools to practical, everyday problems, security teams can effectively reduce manual workload, handle potential threats more consistently, and thoroughly protect the business without needing a massive increase in staff.


Business Intelligence Observability: The Missing Layer of Modern Analytics
While organizations heavily monitor their data infrastructure and pipelines, the business intelligence (BI) layer itself often lacks proper oversight. Traditional monitoring confirms that systems are running and data is delivered, but it fails to answer whether the analytical platform reliably supports sound business decisions. A dashboard might load successfully but perform slower over time, or a report might consume extensive computing power without clear ownership or actual usage. This gap highlights the need for BI observability, a broader operational discipline that continuously measures the health of analytical assets beyond basic technical status. BI observability evaluates five key dimensions: reliability, performance, capacity, adoption, and governance. By shifting the focus from mere technical uptime to actual business impact, data teams can proactively identify deteriorating performance, inefficient resource use, and abandoned reports before users report an issue. This level of transparency is especially critical as organizations adopt enterprise AI, which relies on the exact same governed datasets and semantic models as human decision-makers. Treating business intelligence as a fully observable operational system ensures that both human teams and AI assistants have a trusted, efficient foundation for making timely decisions.


India to release AI regulation consultation paper in 30 days: Vaishnaw

The Indian government plans to release a consultation paper on artificial intelligence regulation within thirty days, focusing on a techno-legal framework rather than relying solely on traditional legislation. Union Minister Ashwini Vaishnaw shared this timeline, highlighting the need to manage AI risks such as deepfakes, financial fraud, and accountability without stifling innovation. This approach combines clear rules with technical safeguards to help organizations monitor AI behavior, restrict unauthorized access, and handle harmful outputs responsibly. A major focus of the upcoming framework is determining accountability when advanced or autonomous AI systems make errors, especially since these systems often rely on multiple technology providers. The government is also looking to streamline how it procures AI services, considering a structured empanelment process for startups and tech companies looking to work on public-sector projects. Alongside these regulatory efforts, India is expanding its domestic AI infrastructure through the IndiaAI Mission, which includes adding thousands of graphics processing units to support computing and inference capabilities. For enterprise technology leaders, this forthcoming regulatory clarity should help establish consistent standards for evaluating AI tools, managing risks, and ensuring proper human oversight as AI adoption expands across public services and business operations.


Why the Chief Data and AI Officer Role Keeps Struggling: Rethinking Executive Leadership for the AI Era

The Chief Data and AI Officer (CDAIO) role frequently struggles because organizations incorrectly treat it as a traditional functional leadership position. Functional executives, like a CFO or COO, are directly accountable for specific departmental operations and outcomes. When the CDAIO is framed this way, their work often devolves into running a technical services department that merely fulfills project requests, delivering disconnected AI models and dashboards rather than driving genuine, widespread business integration. This creates a structural divide between business and technology, making sustainable AI adoption nearly impossible. Instead, the CDAIO should be recognized as a capability leader. Rather than owning a specific business function, their true mission is to build an enterprise-wide capability system—encompassing governance, data literacy, stewardship, and cross-functional coordination. Their goal is to empower every department to effectively leverage data and AI in their daily operations. Success in this role should not be measured by the raw output of AI models or dashboards produced, but by metrics that reflect organizational maturity, such as the number of embedded data experts, active stewards, and the actual utilization rates of AI tools. By shifting from functional ownership to capability building, the CDAIO can truly help the entire enterprise succeed.

Why Tabletop Exercises Expose More Than Technical Weaknesses

While vulnerability scans and penetration tests are excellent at identifying specific security flaws, organizations must conduct tabletop exercises to truly understand how they will respond during an actual cyberattack. These simulated events deliberately expose the nontechnical weaknesses that often go unnoticed on paper, particularly critical gaps in communication, process, and coordination. By throwing untested, unannounced scenarios at decision-makers, organizations can evaluate whether teams agree on incident severity, who actually has the clear authority to shut down systems, and when to involve the board or insurance representatives. A successful exercise is not meant to be flawless; rather, it is designed to create realistic pressure that tests muscle memory and reveals conflicting assumptions across different departments. Executives learn to trust their security teams instead of micromanaging the incident response. To be fully prepared, businesses should run these drills at least annually and conclude each session with a strict action plan that assigns specific owners and concrete deadlines to every identified gap. As threats become more complex due to artificial intelligence, these exercises will also need to adapt dynamically. Ultimately, resolving the deeper governance issues requires ongoing cross-departmental agreement, ensuring the entire organization is genuinely prepared to act quickly and securely.


When AI Meets Quantum: The Next Great Leap in Computing

The article examines three very different ways AI and quantum computing intersect, separating hype from what is actually happening. It first tackles the popular claim that quantum computers will dramatically accelerate AI. The author explains why this is unlikely in the near term: loading real‑world data into quantum states is so costly that it often cancels out any theoretical speedup. While some niche cases in chemistry and materials science show promise, the broader “quantum‑boosted AI” narrative remains mostly aspirational. The second, more grounded convergence runs in the opposite direction—AI is helping quantum hardware mature. Because quantum processors drift, generate noise, and require constant calibration, machine‑learning models are already tuning control pulses, decoding error‑correction signals, and stabilizing qubits more effectively than traditional methods. The third intersection is the most urgent: the cryptographic risk posed by future fault‑tolerant quantum machines. Even though such machines do not exist yet, attackers can harvest encrypted data today and decrypt it later. This threatens AI systems that rely on signatures, secure channels, and provenance trails. The article stresses the need for crypto‑agility, hybrid key exchange, and honest inventories of where cryptography is embedded. It closes with a steady reminder that the real “AI‑quantum leap” is not flashy acceleration but ensuring AI systems remain trustworthy when quantum computers finally arrive.

Daily Tech Digest - September 03, 2026


Quote for the day:

"If you are not embarrassed by the first version of your product, you’ve launched too late." -- Reid Hoffman

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


The Coming Battle Over Machine Identity in Financial Services

As the financial sector increasingly relies on automated systems, a significant challenge is emerging around how these systems identify themselves. While banks have spent decades perfecting how to verify human customers and employees, they now face a much larger volume of non-human actors, such as software applications, cloud services, and automated trading algorithms. These non-human entities outnumber human users by a massive margin and require constant secure connections to function properly. The core issue is that each of these machines needs a verified identity, typically managed through digital certificates and cryptographic keys, to ensure that sensitive financial data is not intercepted or misused. If a system's identity is compromised or allowed to expire, it can lead to severe service disruptions or create vulnerabilities that malicious actors can exploit. Consequently, financial institutions must shift their focus toward establishing rigorous systems for managing machine identities with the same level of strict oversight they apply to human access. This means moving away from fragmented, manual tracking and adopting centralized, automated methods to issue, renew, and secure these digital credentials. By taking control of this hidden infrastructure, financial organizations can maintain operational stability, meet strict regulatory requirements, and protect their vital networks from unauthorized access.


Why Your Critical Skills Should Have to Re-Earn Their Place Every Year

Organizations often treat employee skills frameworks as permanent catalogs, building extensive lists that become outdated before they are even finished. Instead, business leaders and human resources teams should review their critical skills every single year. A skill is only truly critical if a company cannot execute its business plan without it. Rather than listing every useful ability, companies should start with their immediate business goals and work backward to identify the specific capabilities required to achieve them. Even when a skill remains on the list, its practical meaning often changes. For example, critical thinking means something very different today in a workplace using artificial intelligence than it did decades ago on a factory floor. Therefore, managers must consistently update what proficiency actually looks like in practice. Furthermore, looking back at where projects stalled during the previous year helps pinpoint missing capabilities far better than a static inventory. Speed is also absolutely essential. Identifying a gap and building the necessary capability must happen quickly enough to improve performance within the same year. Ultimately, no skill should remain a priority simply by default. Each one must continuously earn its place by proving it drives measurable outcomes and properly aligns with future goals.


Why quantum AI isn’t an IT priority yet

Quantum AI is drawing plenty of attention, but the article makes it clear that it isn’t something IT teams need to prioritize right now. Gartner’s latest analysis shows that no meaningful AI workloads will run on quantum hardware before 2028, and there’s still no peer‑reviewed evidence that quantum systems offer a real advantage for production AI. Most of what’s marketed as “quantum AI” today is either hybrid or quantum‑inspired work running on classical chips, which can be useful but doesn’t require quantum machines. The real concern is budgeting: mixing quantum experiments with day‑to‑day AI spending can pull resources away from projects that already deliver measurable results, like generative and agentic systems. Quantum computing does have promise in areas such as optimization, simulation, and scientific research, but these remain early‑stage pilots rather than operational tools. Post‑quantum security is the one area that deserves near‑term planning, though it sits firmly in the security roadmap rather than AI strategy. For now, the practical approach is to keep quantum exploration in R&D with clear success criteria, while production AI investments stay focused on proven infrastructure, data quality, and governance. Quantum is worth watching, but it shouldn’t distract from what enterprises need to make work today.


Cyber resilience is a very human decision problem, not just a technology one

Cyber resilience is fundamentally a human decision-making challenge, not just a technical one. When a cyber incident occurs, organizations typically face a flood of technical alerts and signals. While tools can detect anomalies and spot patterns, they cannot determine the broader context, such as who is behind an attack or what the legal and reputational impacts might be. Human judgment is required to evaluate these signals, understand the business context, and decide on a proportionate response. The true measure of an organization's resilience is its decision latency—the time it takes to move from identifying a technical signal to making an informed choice about what to do next. Fast but poorly considered decisions can often make a situation worse, so leaders must balance speed with careful judgment. Effective cyber response is a cross-disciplinary effort that extends far beyond the IT department, involving legal, communications, and business operations teams. To navigate these high-pressure situations successfully, companies need a shared decision model and a clear understanding of who is authorized to act. Ultimately, turning threat intelligence into meaningful action requires connecting technical data to real-world consequences, allowing leadership to make critical choices while meaningful response options are still available.


Why Compute Efficiency Is the New Model Architecture

In recent years, the artificial intelligence community has heavily focused on designing novel model architectures to drive progress. We have seen a continuous search for the next big breakthrough in how neural networks are structured. However, a significant shift is currently taking place in the industry. The primary driver of advanced capabilities is no longer just the mathematical arrangement of the model itself, but rather the compute efficiency behind it. As systems scale to unprecedented sizes, the sheer cost and physical limits of hardware have forced a change in priorities. Today, the most meaningful innovations occur at the infrastructure level, focusing on how effectively a system utilizes processing power and manages memory. Optimizing how data moves through hardware has become just as critical as the algorithms processing that data. By maximizing resource utilization, engineering teams can train larger models faster and deploy them more sustainably. This means that designing efficient execution pipelines and hardware integrations is now the true architectural challenge. Ultimately, treating computational efficiency as the core foundation allows organizations to build more capable systems without facing unsustainable costs. Moving forward, the most successful projects will be those that prioritize operational speed and hardware harmony over purely theoretical structural changes.


Cybersecurity for Manufacturing

Modern manufacturing relies heavily on integrating advanced technologies, from cloud platforms and industrial IoT devices to traditional machinery and operational technology (OT). While this digital transformation boosts productivity and automates processes, it significantly expands the cybersecurity attack surface. Cybersecurity for manufacturing involves protecting networks, industrial control systems, and production data from threats while ensuring that safety, quality, and operational continuity are maintained. Because modern facilities often mix legacy systems with advanced automation, cybersecurity in this sector is not solely an IT responsibility; it requires collaboration among IT teams, plant managers, engineers, and executives. The distinction between IT and OT is crucial, as OT focuses on controlling physical processes where downtime can severely disrupt production. The most significant threats include ransomware, phishing, credential theft, and supply-chain attacks. Poorly segmented networks can allow an attack on a simple endpoint to spread to critical operational systems. To defend against these risks, manufacturers must deploy a strategy that includes network segmentation, secure remote access, continuous monitoring, and robust incident response. Organizations also rely on specialized solutions to gain visibility and quickly detect anomalies across these complex, interconnected environments before production is compromised.


The Hidden Technology Keeping Modern Infrastructure Running

Modern infrastructure—such as power grids, water networks, and transportation systems—is increasingly relying on hidden digital technologies to maintain reliability, especially as physical assets age. While concrete, steel, and machinery still form the foundation, a digital layer of sensors, edge computing, and specialized software now continuously monitors their condition. Instead of waiting for periodic manual inspections, operators use technologies like vibration sensors, thermal monitoring, and computer vision to observe infrastructure behavior in real-time. This continuous visibility allows engineers to detect early warning signs, such as a pump consuming extra electricity or a motor changing its vibration signature, before a catastrophic failure occurs. Edge computing processes data locally, sending only essential information to cloud platforms to prevent bandwidth overload. Furthermore, artificial intelligence and machine learning filter massive amounts of operational data to enable predictive maintenance, flagging unusual patterns that require human attention. Digital twins—dynamic digital representations of physical systems—further help engineers compare expected performance with actual behavior. By integrating these tools, operators gain a comprehensive view of their networks, allowing them to prioritize maintenance, target investments efficiently, and keep essential public services running smoothly despite the mounting challenges of aging physical infrastructure.


Seven critical vibe coding mistakes — and how to avoid them

While using artificial intelligence to quickly generate code promises massive productivity gains, it also introduces serious risks if fundamental software engineering practices are ignored. The article highlights seven critical mistakes developers must avoid when relying on AI coding assistants. First, teams must not skip the essential process of defining clear requirements and user stories before generating code. Second, developers should never blindly trust the AI to select software dependencies, as it often chooses outdated or insecure components. Third, foundational architecture and nonfunctional requirements like security must be planned upfront, not bolted on later. Fourth, exposing unmasked production data to AI tools in development environments creates significant compliance risks. Fifth, access controls need to be built directly into the foundation rather than treated as an afterthought. Sixth, relying solely on manual code reviews is highly dangerous; organizations must enforce strict automated testing safeguards before accepting generated code. Finally, teams must ensure complete observability to properly track and understand the automated decisions the AI makes. Ultimately, while coding assistants can dramatically accelerate software delivery, teams must apply the exact same rigorous planning, testing, and quality standards they would use for human-written code to build safe, reliable, and functional applications.


When the patch tsunami meets the maintenance window

Artificial intelligence is drastically accelerating how fast software vulnerabilities are discovered, creating a massive wave of security patches. While standard IT departments can often apply these fixes in days, operational technology environments like factories, water plants, and hospitals face a serious crisis. Finding a flaw now happens at machine speed, but fixing it in physical plants still moves at a crawl. In these settings, you cannot simply reboot a system without risking continuous processes, worker safety, or voiding equipment warranties. Scheduled maintenance windows might only happen once a year, making traditional patching impossible. To manage this growing gap, security teams must stop trying to patch every critical flaw immediately. Instead, they need to prioritize based on actual exposure and the real-world consequences of an attack. If a system cannot be patched safely, operators must focus on strict containment strategies, such as isolating the vulnerable equipment from the main network and closely monitoring it for threats. Furthermore, organizations should proactively negotiate emergency downtime rules with their plant managers and finally set firm retirement dates for aging, unpatchable legacy systems. The speed of vulnerability discovery has changed permanently, and industrial teams must adapt their defenses to strictly match this reality.


The hidden cost of data sovereignty: When governance prevents scaling

Data sovereignty rules require information to remain within specific geographic or legal borders, initially intended to protect user privacy and national interests. However, strictly regulating where and how data is stored creates significant challenges when companies attempt to expand their operations globally. Because organizations must adhere to different local laws, they are frequently forced to construct isolated technology infrastructures for each distinct region. This fragmented approach prevents the smooth flow of information that modern businesses depend on for everyday efficiency. Rather than using a single, unified system, companies maintain multiple parallel environments. This reality duplicates work, consumes valuable technical resources, and drastically increases operating costs. In addition, the administrative burden necessary to manage these varied compliance requirements slows down basic decision-making and delays the introduction of new products or services. While strong governance is absolutely necessary to fulfill legal obligations and maintain customer trust, it can unintentionally form rigid barriers to expansion. Business leaders must find a careful balance between following local mandates and maintaining the operational flexibility required to grow. Without a thoughtful strategy that connects regulatory compliance with sensible infrastructure design, the ambition to enter new markets will ultimately be hindered by the rules designed to keep data secure.