Showing posts with label data security. Show all posts

Daily Tech Digest - September 19, 2026


Quote for the day:

“The only true wisdom is in knowing you know nothing.” -- Socrates

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 20 mins • Perfect for listening on the go.


Building a pre-emptive security architecture — what is it and how can your business adopt one?
With the rise of AI-driven cybersecurity threats, conventional "detect and respond" frameworks are struggling. The speed of attacks has increased, and the volume of vulnerabilities is projected to skyrocket, leading to practitioner burnout. This has prompted a shift toward a pre-emptive security architecture. Instead of waiting to respond to an intrusion, pre-emptive security aims to stop attacks before they cause damage by placing controls directly in the attack path. It's an architectural approach, connecting security across layers—like users, applications, and data—so that a breach in one layer doesn't compromise the whole system. This strategy focuses on anticipating and preventing breaches rather than just limiting the fallout. Key elements of this approach include denying access, deceiving attackers with decoys, and disrupting emerging threats. Techniques like zero trust, secure code development, and confidential computing are central to this model. To implement it, businesses should first identify sensitive data and map out vulnerabilities. This involves understanding potential attack paths and applying the principle of least privilege. Regular penetration testing and continuous monitoring are essential to ensure these controls work without disrupting legitimate business processes. While pre-emptive measures are crucial, they are meant to enhance, not replace, existing security alerts.


Strong fundamentals make next-gen security possible

Instead of constantly chasing the newest security tools, organizations should focus their efforts on mastering five foundational practices to effectively protect their systems. First, businesses must maintain a clear, accurate inventory of all their physical and digital assets across every environment. You simply cannot protect what you do not know exists. Second, carefully managing user identities is critical. Implementing simple but strong measures like multifactor authentication or passkeys significantly lowers the chance of compromised accounts. Third, security strategies should match the specific needs and risk tolerance of the business. By identifying the most valuable data and establishing clear priorities, security teams can focus their resources exactly where they matter most. Fourth, while preventing attacks is important, organizations must also prioritize true resilience. This means keeping secure backups, writing clear recovery plans, and actively practicing those plans so employees know exactly what to do during a crisis. Finally, security professionals and business leaders need to speak the same language. By translating technical risks into clear business impacts, such as potential financial costs, teams can make better decisions together. Mastering these basic, everyday practices may not seem exciting, but it provides a much stronger defense against real threats than simply buying the latest technology.


The cloud outage that should terrify the CIO

A recent Microsoft Azure outage that simultaneously knocked out major AI services, including ChatGPT, Claude, Grok, and Copilot, serves as a stark warning for business leaders. The disruption highlights a growing, hidden vulnerability: concentrated cloud dependency. As organizations increasingly weave artificial intelligence into their core operations, they are inadvertently stacking their critical workflows on the same shared infrastructure. When a major cloud region fails, the impact is no longer limited to a single application going offline. Instead, automated business processes, financial transactions, and customer support pipelines can grind to a sudden halt, leading to massive financial losses. What makes this risk especially dangerous is that many companies are completely unaware of their true exposure. Organizations rely on countless third-party software vendors, who in turn depend on major cloud providers. This creates a chain of invisible dependencies where an outage at a provider you do not directly use can still freeze your business. To protect their operations, technology leaders must actively map their entire software dependency chains, including the artificial intelligence layer. They need to design their critical systems to smoothly switch to backup providers during failures and clearly present the financial risks of cloud downtime to their executive boards.


The Control Plane Is Not the Trust Plane

The article from Security Boulevard, titled "The Control Plane Is Not the Trust Plane," explores the evolving landscape of AI governance. The author argues that while control planes—systems designed to govern what an AI agent is permitted to do—are necessary, they are no longer sufficient. As organizations deploy more AI agents, a critical gap emerges: the need to verify history, provenance, and the actual context of an action. To address this, the author proposes a new conceptual layer: the "trust plane." A control plane answers questions about possibility, such as which identities exist and what policies apply. In contrast, the trust plane answers questions about history, focusing on why a specific action belongs to a legitimate chain of authority. It requires "evidence receipts" to understand the full context—who initiated the request, what identity was used, and what was actually accepted by the receiving system. The article emphasizes that trust should not rely on centralization, which creates single points of failure. Instead, it advocates for a distributed approach where nodes retain local identity while sharing verifiable evidence. Ultimately, as AI systems transition from tools to active participants, securing both control and trust is vital for maintaining accountability and operational integrity.


California child-safety laws expand age checks to addictive feeds, AI chatbots
California has introduced a series of new child safety laws that regulate artificial intelligence chatbots and social media platforms, establishing the state as a leader in digital age verification. These bills aim to create safer online environments for children by making device based age checks the standard. A central piece of this legislation is a new rule requiring independent safety audits and annual risk assessments for companion chatbots. This measure was inspired by a tragic case where a teenager was allegedly influenced by a chatbot to end his life. Major industry players, including the creators of ChatGPT and media advocacy groups, have voiced their support for these rules. In response, artificial intelligence providers are already implementing mandatory safety modes for users under eighteen. Additionally, the new laws ban social media platforms from offering addictive features to children under sixteen. Companies must now verify age before enabling these tools, with severe financial penalties of up to fifty thousand dollars per affected child for those who knowingly violate the rules. Finally, lawmakers clarified how age signals should be shared by operating systems, ensuring that open source developers are not unfairly burdened. As artificial intelligence continues to grow, other states are expected to adopt similar protective measures.


Enabling the next generation of AI data centers
The article describes how AI is forcing a fundamental rethink of data center design, mainly because traditional facilities were built for predictable CPU workloads and steady growth. AI training clusters, by contrast, demand far higher power density, faster deployment timelines, and more complex infrastructure coordination. The author explains that developers are now planning gigawatt‑scale campuses where power, cooling, transmission, water, and long‑term operations must be designed as one integrated system rather than separate components. Site selection has become a balancing act: inexpensive land may lack grid access, while power‑ready sites may come with long interconnection delays or higher costs. To keep projects moving, many operators are turning to hybrid or off‑grid power solutions, including gas generation, batteries, and microgrids, even though these approaches require more capital and careful permitting. Cooling is also shifting toward liquid systems and thermal storage to handle dense AI loads and reduce peak energy use. The article stresses that early permitting work and cross‑discipline alignment are now essential, because regulatory, environmental, and community constraints can shape a project as much as engineering choices. Ultimately, the piece argues that success depends on making early, realistic decisions that translate AI demand into infrastructure that can be delivered at speed and scale.


Is Your Organisation’s Data Secure?
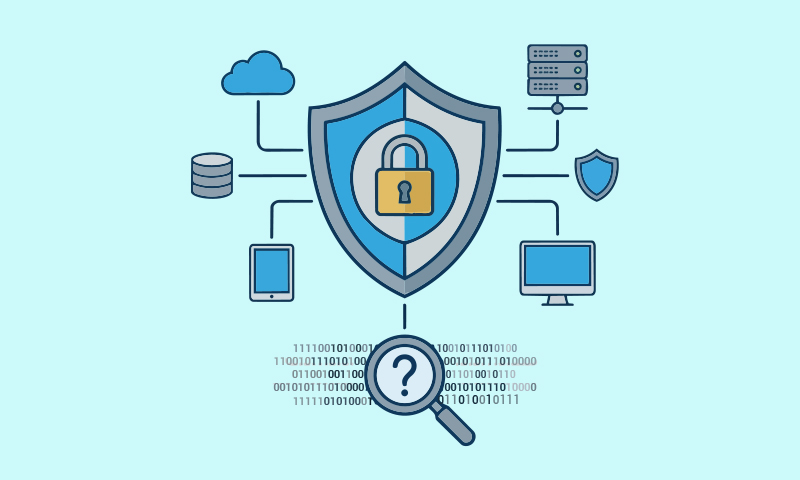
Data security is critical, and many free, open-source tools now offer robust protection, making strong encryption accessible to organizations of all sizes. Encrypting data prevents unauthorized access by converting plaintext into unreadable ciphertext, which requires a specific key to decipher. The transparency of open-source software allows a global community of experts to continuously evaluate the code, often identifying vulnerabilities faster than with closed, proprietary systems. A comprehensive security strategy must address data in two states: at rest and in transit. Data at rest, such as information stored on hard drives or databases, is a high-value target for attackers. Encrypting this data ensures that even if physical devices are stolen, the information remains secure. Data in transit moves between systems over networks like the internet and can be intercepted. Tools like OpenSSL, Let's Encrypt, WireGuard, and OpenSSH provide essential encryption for data in transit, securing web traffic, remote access, and file transfers. Regulatory frameworks worldwide further emphasize the importance of data encryption to protect personal and financial information. By leveraging these open-source tools, organizations can build resilient defenses against data breaches.


Cybersecurity Work-Life Balance Starts With Actually Turning Off

The constant pressure of defending against relentless threats has made it incredibly difficult for cybersecurity professionals to step away from their work. Sam Van Ryder, a veteran in operational technology security, emphasizes that achieving a healthy balance requires individuals to genuinely disconnect, while employers must actively protect their team's downtime. Often, organizations talk about this balance as a benefit without creating the environment necessary for people to log off. With ongoing staffing shortages and constant alerts, the inability to rest is no longer just a personal wellness issue; it is a direct security risk. When security teams are exhausted, their judgment naturally suffers, creating the exact vulnerabilities that attackers actively look to exploit in critical systems. Recognizing this, leaders need to ensure time off is fully respected. This means no emails, no emergency messages, and no checking the daily news. If a team member tries to work on their day off, leaders should send them back to their rest. Furthermore, recovery should not be limited to an annual vacation. Regular breaks throughout the year are completely essential for maintaining a strong and focused workforce. Ultimately, the most effective way to maintain long-term security is for individuals to step back, turn everything off, and simply recharge.


Beyond Age-Gating: Regulating Platform Design for Child Safety

India's approach to child online safety currently relies on basic age restrictions and rapid content removals, but these conventional measures fail to address a much deeper issue: structural platform design. With millions of children accessing the internet daily, the conversation must shift from simply blocking entry to reforming how digital services are actually built from the ground up. Features such as recommendation algorithms, automatic video playback, and default direct messaging settings shape the online experience of a child and their exposure to risk long before content moderation even occurs. Global evidence clearly shows that simple age limits are frequently bypassed, leaving many young users vulnerable to the exact same risks. Furthermore, current safety metrics only track formal complaints rather than measuring the actual frequency of exposure to harmful material. To create a genuinely safer environment, policymakers must begin regulating platform design directly. Rather than treating safety as an afterthought, features that enable direct contact with strangers should be restricted by default. India can utilize its existing consumer protection laws to classify manipulative interfaces as unfair practices. Large digital services should be required to justify structural changes affecting minors, disable behavioral tracking, and publish independently audited data on how often children encounter harmful content online.


The DPDP cross-border transfer rules aren't live yet; so why are contracts being redrafted as if they are?

Many legal teams and companies are prematurely rewriting contracts to comply with the cross-border data transfer rules of India's Digital Personal Data Protection Act. However, these specific rules will not actually take effect until roughly May 2027. Currently, organizations are making the mistake of forcing strict European-style data protection clauses into their Indian contracts. This approach is highly counterproductive because India's legal model is vastly different. While the European system requires strict safeguards for every single transfer, India will use a much more open approach. This means that data can flow freely to any country unless the government explicitly restricts it. Because the government has not yet released a list of restricted countries, there is no solid legal basis to enforce strict transfer mechanisms right now. Including heavy compliance requirements prematurely can easily lock businesses into unnecessary legal burdens and costs. Instead of overcomplicating current agreements, legal teams should draft adaptable clauses that allow for future updates once the rules officially take effect. During this waiting period, companies should focus on understanding their data flows rather than creating rigid compliance structures. Lawyers must also be totally transparent with clients, clarifying that these contract changes are preparations for the future, not immediate legal obligations.

Daily Tech Digest - June 20, 2026


Quote for the day:

"Outstanding leaders go out of their way to boost the self-esteem of their personnel." -- Sam Walton

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 21 mins • Perfect for listening on the go.


Why AI coding debt is different

The rapid adoption of artificial intelligence in software development is generating an entirely new challenge: cognitive debt. Unlike traditional technical debt, which usually involves poorly written or messy code, cognitive debt arises when software works perfectly but no human understands exactly how or why it was built. Because AI tools generate code at unprecedented speeds, developers often bypass the crucial, slower process of thinking through specific scenarios and internalizing the underlying logic. Furthermore, many AI tools operate without essential background knowledge, such as past design choices or specific security rules, resulting in code that may function in isolation but lacks overall coherence. To prevent this accumulation of invisible debt, organizations must shift their focus from merely generating code to rigorously checking it. This involves building strong internal practices that provide AI with necessary historical knowledge before it writes a single line. Most importantly, engineering teams must establish strict human ownership, ensuring a developer takes the time to thoroughly review and comprehend the final product. By balancing the speed of AI generation with careful oversight and deep understanding, companies can maintain healthy, reliable systems without sacrificing their future stability or falling into irreversible complications.


Why Every CISO Needs a Head of AppSec in the Age of Vibecoding

The rise of AI-assisted software development has drastically increased the speed at which code is generated and deployed. While this shift enhances developer productivity, it also introduces subtle flaws and misconfigurations at a scale that outpaces traditional security measures. For a Chief Information Security Officer (CISO), directly overseeing application security is no longer practical. To maintain control without slowing down engineering, organizations must introduce a dedicated Head of Application Security. This role acts as a vital bridge between the security and development teams, turning abstract vulnerabilities into clear, actionable fixes that fit naturally into everyday workflows. Instead of treating security as a roadblock, a capable Head of Application Security enables developers to build safely and efficiently. Furthermore, while automated tools handle known issues, this leader ensures human testers remain focused on uncovering complex attack paths that machines miss. By delegating the daily operational details of application security to a specialized leader, the CISO can step back and focus on broader risk management and strategy. Ultimately, restructuring security leadership is essential for companies wanting to build software quickly without taking on unmanaged risks.


A perfect storm: data centers and tornadoes

The article examines the growing collision between data center expansion and the rising threat of tornadoes. As the demand for digital infrastructure pushes these vital facilities into regions known for volatile weather patterns, operators face a complex challenge. The piece highlights that relying on standard commercial building practices is no longer sufficient to protect critical hardware and ensure uninterrupted operations. Instead, modern data centers must incorporate specialized physical hardening from the ground up. This involves constructing reinforced concrete walls and specialized roofing designed to withstand extreme wind speeds and dangerous flying debris. Beyond structural defenses, the analysis strongly emphasizes the necessity of implementing comprehensive disaster recovery strategies. A key component is building geographic redundancy into the network architecture, ensuring that if one specific facility goes offline, other locations can seamlessly manage the computing load. Maintaining reliable backup power generation and secondary cooling systems is also essential to survive the immediate aftermath of a storm when local utility grids fail. Ultimately, securing digital assets against nature's unpredictability requires a steady, proactive approach, blending structural engineering with thorough contingency planning to keep essential services running smoothly.


OT vs IT Security: Key Differences Explained for Controls Engineers

Operational Technology (OT) security and Information Technology (IT) security serve different purposes and operate under distinct priorities. While IT security safeguards corporate data networks with a primary focus on keeping information confidential, intact, and available, OT security protects industrial control systems like programmable logic controllers and manufacturing lines. Because a failure in these industrial environments can lead to damaged equipment or physical harm, OT flips the traditional model to prioritize availability and safety above all else, often minimizing confidentiality. A major challenge for controls engineers is that standard IT practices do not easily transfer to the plant floor. For example, you cannot simply update an industrial controller the way you patch a laptop. These devices require uninterrupted operation, rigorous testing, and strict vendor approvals, making routine updates costly and disruptive. Furthermore, as enterprise networks increasingly connect with industrial systems to share data—a trend known as IT/OT convergence—traditional boundaries disappear. This connectivity introduces new vulnerabilities to legacy equipment that was never designed for modern internet threats. Bridging this gap requires careful network segmentation and a shared understanding between IT departments and plant engineers to keep production running safely.


AI Governance vs Data Governance: Why They Need Opposite Approaches

The article highlights the distinct but complementary needs of data and artificial intelligence governance within modern organizations. It points out that traditional data management programs often fail within their first year because they rely on rigid, centralized control that internal teams actively resist. To succeed, these data initiatives must instead link directly to specific business goals and decentralize their efforts across departments. Conversely, managing artificial intelligence requires the exact opposite organizational approach. Because AI development usually begins in isolated, scattered teams, it actually requires a centralized strategy to mature effectively and deliver consistent value. To resolve this structural tension, the text advocates for an adaptable framework that thoughtfully balances central standards with flexible, everyday execution. This method adjusts the level of control based on the organization's maturity and the specific risks involved in each project. Furthermore, the rapid adoption of modern AI tools demands a renewed focus on unstructured information, such as plain text documents, which is inherently harder to organize than traditional databases. Companies are strongly advised to systematically discover, tag, and connect this unstructured information to ensure their automated systems remain reliable and safe for long-term enterprise use.


Security considerations for adopting Claude Code and Cowork for SMBs

When small and medium-sized businesses decide to adopt AI tools like Claude, security leaders must carefully balance rapid deployment with essential safety measures. The primary step is understanding the specific plan your organization requires, as advanced security features like single sign-on and compliance tools are restricted to higher-tier subscriptions. Rather than granting broad access, it is safer to control your exposure by selectively assigning licenses for different products—such as Chat, Code, or Cowork—based on actual employee needs. As you introduce these tools, avoid turning on every feature at once. Instead, evaluate the risks of each capability and roll them out gradually. Features like web search or automated skills introduce vulnerabilities, making strict management of API keys and data access critical. Limit the number of people who can generate administrative keys to maintain tight control. Additionally, remember that you cannot outsource your data governance. It is your responsibility to monitor what information flows into the system and verify the accuracy of what comes out. By relying on a phased approach and leveraging existing security vendors, you can confidently integrate new technologies while keeping your business secure.


Every AI Agent Is an Identity. Most Organizations Don't Treat Them That Way

As AI agents evolve from simple productivity tools into powerful actors that can trigger workflows, write code, and update records, they are effectively becoming new digital identities within enterprise networks. However, most organizations are failing to secure them as such. According to the article, security teams traditionally focus on managing the identities of human employees and service accounts, leaving AI agents largely ungoverned. These agents are frequently connected to critical business platforms like Salesforce, GitHub, and production databases, often receiving overly broad permissions just to ensure they work smoothly. This creates a sprawling network of hidden actors with high levels of system access. While much of the AI security conversation has centered on software risks like bad prompts or incorrect outputs, the greater threat lies in what these tools can actually access. An overprivileged AI agent compromised by a malicious plugin can become a dangerous pathway for major data theft or system damage. To safely adopt AI technology, organizations must start treating AI agents exactly like standard network identities. This requires continuous tracking, strictly restricting their permissions to match their exact purpose, and systematically applying the same exact security rules used for human employees.


CIOs: tear down the wall between resilience and data security

For years, organizations have treated keeping systems online and keeping data safe as two separate jobs handled by different teams. However, the rapid adoption of artificial intelligence is proving that this separation is no longer practical. Rather than creating entirely new problems, AI is exposing existing flaws in how companies manage their files and information. When employees use AI assistants, these tools can easily find and share old or sensitive documents that were left unsecured, revealing a severe lack of basic organization and control. To solve this, technology leaders must unite their safety and system recovery efforts. First, companies need to understand exactly what information they have, where it lives, and who should see it before they roll out new tools. Second, they must use automated systems to manage rules and access, because human review simply cannot keep up with the speed of automated requests. Finally, businesses must clearly track what automated programs are doing and why, to ensure they meet future legal standards. Ultimately, attempting to block these new tools will fail. Instead, leaders must safely guide their use by building a unified, trustworthy foundation.


France and Germany Boost Digital Sovereignty Push

France and Germany are strengthening their commitment to European digital sovereignty through a coordinated approach and substantial new funding. To reduce reliance on foreign technology, the French government announced an initial 13 billion euro investment fund, expected to grow to 15 billion euros by the end of the year, aimed at supporting domestic and regional technology firms. Institutional investors, including aerospace and defense partners, are backing this initiative. Half of the capital is dedicated to deep technology sectors such as artificial intelligence, quantum computing, biotechnology, and space exploration. This focus on artificial intelligence is particularly timely given recent United States export controls that restricted European access to advanced models from companies like Anthropic. These restrictions have intensified demands for regional self-sufficiency and highlighted the strategic importance of European developers like France's Mistral AI. The new funding represents the third phase of a broader effort to close the financing gap for scaling tech businesses in the region. Although Germany previously approached such initiatives with caution, shifting geopolitical dynamics and concerns over the reliability of American technology services have united the two nations in their drive to secure technological independence.


Data Observability: Guidance for Data Leaders

Many organizations struggle to ensure their artificial intelligence systems receive reliable information. Although experts recognize the necessity of tracking data as it moves through systems, many leaders still treat this practice as a future goal rather than an immediate requirement. Without a clear view into their data systems, companies are left guessing whether their information is accurate and safe to use. As artificial intelligence shifts from simply providing answers to taking independent actions, relying on guesswork is no longer acceptable. Information pathways are becoming increasingly complicated, making it easier for mistakes to happen or for incorrect details to reach the wrong destination. Proper oversight helps address these complications, including the growing challenge of fragmented systems. Fundamentally, observing your data means proving that the right information arrives exactly when and where it is needed. This practice requires finding and fixing errors before they impact the business. Instead of merely checking if a system is turned on, organizations must validate that the information flowing through it is completely trustworthy. By maintaining a continuous, clear view of their data, organizations can confidently support their advanced technologies and ensure reliable outcomes.