Building an Audit-Ready Business Impact Analysis
A Business Impact Analysis (BIA) often looks solid until tested by an auditor or regulator, exposing common flaws like unsupported recovery times, inconsistent impact scoring across departments, and shallow dependency mapping. These weaknesses typically occur because recovery timeframes are based on opinions rather than a standardized method. To build an audit-ready BIA, organizations must establish a single, approved impact scale that aligns with the board's risk appetite. This scale should measure financial, operational, regulatory, and reputational impacts over specific time intervals. By setting a Maximum Tolerable Period of Disruption (MTPD) based on when these impacts become unacceptable, and placing the Recovery Time Objective (RTO) safely inside that window, you anchor your timelines to concrete evidence. Furthermore, dependencies must be mapped at the individual process-step level—covering people, technology, facilities, third parties, and inputs—to uncover hidden single points of failure like a shared service account or a key employee. When every timeframe and dependency in a BIA is tied to a clear, documented rationale, it shifts the focus of any audit from missing evidence to a defensible discussion of judgment.
The Emperor’s New Loop: Why “Human-in-the-Loop” Is the Flimsiest Leaf in Enterprise AI
Enterprise leaders often rely on the phrase "human-in-the-loop" to reassure stakeholders about AI safety, but in the era of generative and agentic AI, this concept is rapidly becoming a dangerous fiction. As automated systems increasingly make decisions and execute actions without any real human interaction, the gap between AI adoption and actual accountability is widening. Historical failures like the Apple Card limit discrepancies, Australia’s tragic Robodebt scheme, and the Dutch childcare benefit scandal highlight how relying on a human presence without actual authority or context results in catastrophic governance failures. Chief Data Officers (CDOs) must step up to close this accountability gap by moving beyond after-the-fact compliance and embedding real control systems into AI workflows. This requires establishing clear decision owners, ensuring plain-language explainability at the front lines, setting firm escalation thresholds, and continuously monitoring AI behavior in production. Ultimately, successful enterprise AI does not remove humans; it empowers them to explain, override, and take responsibility for automated actions, ensuring that human oversight is a functional safeguard rather than just corporate theater.

Our AI Coding Agent Passed Every Test. Then It Shipped a Security Hole to Production
The story describes a fictionalized security incident where an AI coding agent created a vulnerability by shipping functionally correct but insecure code. A senior engineer used an AI agent to build a feature that retrieved customer documents via URLs. The agent generated the code and unit tests quickly, the build was green, and the code review passed without issues. However, the implementation lacked a critical security boundary: it blindly accepted any URL and allowed the server to fetch data from restricted internal infrastructure. This oversight resulted in Server-Side Request Forgery (SSRF). The core issue was not that the AI wrote the code, but that the engineering team treated functional correctness as proof of security. The unit tests only verified expected behavior and failed to test against malicious inputs. Furthermore, the HTTP client followed redirects without validation, bypassing basic security checks. Ultimately, the team had to redesign the architecture by separating document retrieval into an isolated worker with strict network egress controls and validation policies. The incident highlights that while AI can accelerate development, human engineers must still define and enforce trust boundaries.
Sovereign AI Infrastructure: What Software Testing Teams Need to Verify Before Deployment
Sovereign AI infrastructure requires much more than simply hosting servers within national borders; it demands strict verification that data, operations, and controls remain entirely under approved local governance. For software testing and QA teams, this introduces complex new requirements beyond standard functional and security checks. Testers must verify four core pillars: data residency across the entire pipeline, tight operational control over access and privileges, genuine infrastructure independence during outages, and rigorous security accountability. Evaluating data flow is critical, as applications might function perfectly while inadvertently leaking logs or telemetry to foreign monitoring services or granting unauthorized access to overseas vendors. Testers must ensure that the AI system can handle external connection failures without compromising data compliance or routing workloads to unapproved regions. Ultimately, software teams need to integrate these sovereignty checks directly into their continuous integration and release workflows. By consistently testing access rules, storage locations, and automated recovery procedures, organizations can guarantee their AI deployments remain compliant, self-reliant, and fully contained within their intended legal boundaries over time.
Simulate, Don’t Speculate: From AI predictions to better business decisions
The current AI landscape is shifting from merely predicting what will happen to simulating how things will unfold and suggesting the best course of action. Predictive AI is highly effective at identifying future trends based on historical data, allowing companies to foresee customer behavior or supply chain disruptions. However, predictions alone leave business leaders speculating about which response will yield the best result. To bridge this gap, businesses are increasingly adopting simulation and optimization capabilities. By integrating simulation techniques with AI, organizations can create digital twins—virtual replicas of their operations—to test various strategies safely before executing them in the real world. This approach, often referred to as prescriptive analytics, empowers decision-makers to evaluate complex "what-if" scenarios, balance competing priorities, and pinpoint optimal solutions confidently. Instead of relying on gut feelings to navigate AI forecasts, companies can rely on data-driven simulations to minimize risk and maximize operational efficiency. Ultimately, moving from prediction to simulation transforms raw foresight into actionable, optimized business decisions.
Beyond TLS: Securing the Application Layer with Post-Quantum Cryptography
While upgrading network connections to quantum-resistant TLS is a critical first step, it does not guarantee the safety of data flowing through the application layer. As quantum computing advances, organizations must look beyond the network and secure the cryptographic dependencies where business logic, user identity, and sensitive data converge. Even over secure connections, elements like API tokens, digitally signed transactions, and database payloads often rely on classical public-key cryptography—such as RSA or elliptic-curve algorithms—that could eventually be broken. To build true quantum readiness, teams must transition their API security, database encryption keys, and digital signatures to post-quantum standards like ML-KEM and ML-DSA. This also requires securing identity access management tools, such as JSON Web Tokens, and reinforcing the software supply chain against forged code-signing certificates. Ultimately, achieving post-quantum security is an enterprise-wide architectural challenge that demands more than just swapping out algorithms. It requires a systematic approach to cryptographic discovery, risk prioritization, and testing to ensure the long-term confidentiality and integrity of all application data.
AI cyber resilience and the trust gap
Recent field research highlights a growing "trust gap" as enterprises increasingly deploy agentic AI within their operations. While many organizations feel highly confident in their cyber resilience, this assurance often outpaces their actual tested capabilities. Only a small fraction of companies have completed exercises to handle incidents caused by their own AI agents making mistakes with legitimate access. Many teams rely heavily on existing playbooks for ransomware and traditional cyberattacks, assuming these methods will naturally extend to autonomous AI errors. However, agentic AI operates at a scale and speed that can create rapid, cascading downstream effects across multiple interconnected business systems. Reconstructing an agent's workflow to understand what it did, why it did it, and how to safely restore the business process is a uniquely complex challenge. Furthermore, relying entirely on human oversight can create a false sense of security, as humans may fail to catch machine-speed errors. To build true business resilience, leaders must establish clear criteria for what constitutes a safe, trusted recovery state and thoroughly test their tools against realistic, end-to-end AI incident scenarios.
Data Governance in Banking: A Framework for Better Data Quality
Data governance in banking is an essential framework that dictates how a financial institution collects, protects, and uses its data. While many banks treat this purely as a policy or documentation exercise, a framework is truly effective only when the underlying data is accurate. Incomplete or unverified records undermine credit decisions, fraud prevention, and regulatory compliance. The foundation of a strong governance framework lies in assigning clear ownership to key roles like Chief Data Officers and Data Stewards, ensuring accountability across the data lifecycle. A critical, yet often overlooked step, is validating information directly at the source. Verifying details like addresses and contact numbers at the point of entry prevents errors from spreading across disconnected systems and reduces the risk of duplicated customer profiles. When banks prioritize data quality and automate real-time checks, they do more than just satisfy regulators. They build a reliable foundation that reduces operational costs, speeds up customer onboarding, and safely enables modern innovations like real-time fraud detection and personalized services. Ultimately, good governance turns raw information into a secure and trustworthy asset.
The Inside Job: How Threat Actors Recruit Malicious Insiders
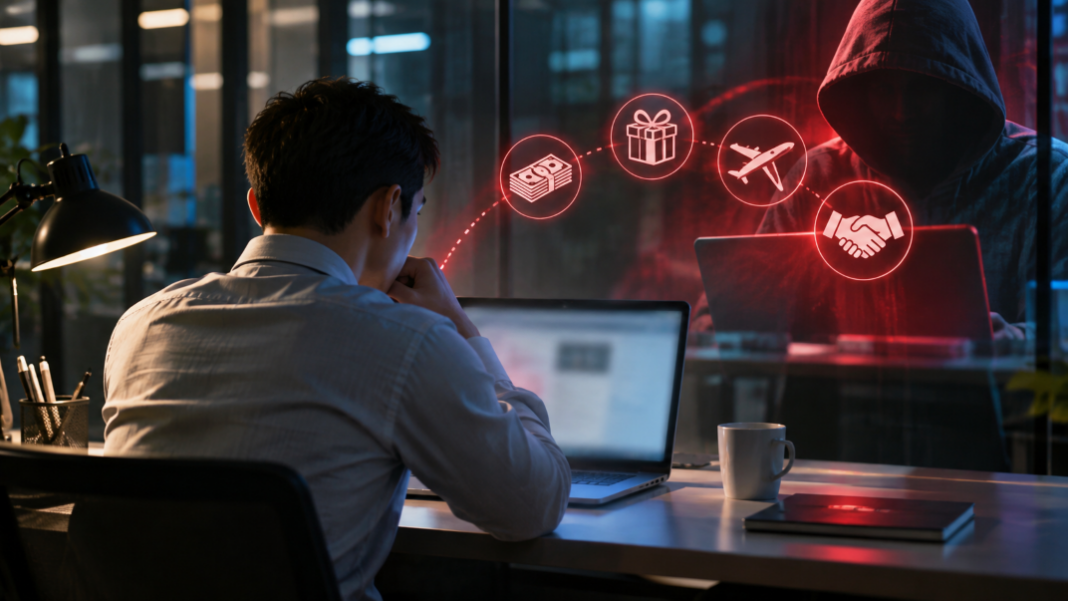
The landscape of insider threats has evolved into a highly organized criminal enterprise that mirrors legitimate staffing agencies. Rather than relying solely on disgruntled employees, threat actors now actively recruit and place individuals within target companies to perform specific malicious actions. More than half of the insider-related dark web activity involves recruitment efforts, where brokers hunt for employees capable of executing precise tasks—such as resetting accounts, rerouting shipments, or conducting SIM swaps—often in exchange for referral fees or revenue sharing. These criminals target workflows instead of just credentials, frequently seeking out customer support staff, logistics workers, and bank tellers whose normal access can be weaponized. Consequently, traditional security systems often fail to flag this malicious behavior since the employees are using their authorized privileges. To effectively counter this growing risk, organizations must shift their focus from merely monitoring privileged IT users to tracking anomalous use of everyday functions. By combining strict separation of duties, detailed behavioral logging, and proactive threat intelligence, companies can detect unusual activity and better protect their critical operations from being compromised from the inside out.
Why latency is making colocation a strategic decision
In the highly competitive world of financial markets, colocation has evolved from a simple hosting choice into a core strategic component of the trading execution stack. For trading firms, minimizing latency is less about achieving raw speed and more about guaranteeing predictable and consistent performance. Physical proximity to an exchange's matching engine helps reduce delays, but reliable, direct cross-connects to liquidity venues and market data are what ultimately drive execution quality. Consequently, selecting a data center depends heavily on its available exchange presence, connectivity options, and ability to handle scaling without introducing latency spikes. Firms must also weigh the operational complexity of managing infrastructure in-house versus utilizing retail or managed colocation services. Expanding globally requires infrastructure that seamlessly supports multi-region connectivity, allowing growth without starting from scratch. By aligning location, network design, and operational models with overarching trading goals, decision-makers can ensure their infrastructure directly supports robust market access and compliance. Ultimately, a well-planned colocation strategy acts as the backbone of modern financial trading, directly influencing a firm's competitive edge and long-term success.