Quote for the day:
"To succeed, high integrity must precede high ambition or high performance. Always do the right thing for the right reasons." -- Vala Afshar
🎧 Listen to the audio debrief on YouTube
▶ Play Audio DigestDuration: 21 mins • Perfect for listening on the go.
Your AI Productivity Gains Are Creating a Talent Crisis
 As companies aggressively adopt artificial intelligence to handle routine tasks,
they are inadvertently creating a hidden talent crisis for the future. While
automating foundational work provides immediate efficiency and saves valuable
time, it quietly dismantles the traditional apprenticeship model that young
employees rely on to build expertise. Historically, doing repetitive tasks
allowed junior professionals to develop the critical judgment and pattern
recognition required to eventually become senior experts. This dynamic leads to
a senior worker paradox. Current experienced professionals can effectively guide
and evaluate artificial intelligence because they built their underlying
knowledge before these tools ever existed. However, the next generation of
workers is expected to supervise complex systems without gaining that identical
practical experience. Consequently, organizations are accumulating a serious
capability debt, where high daily output masks a growing inability among staff
to solve problems independently without technological assistance. To prevent
this looming skill shortage, businesses need to rethink how they implement these
systems. Instead of using artificial intelligence merely as an engine to
generate quick answers, companies should deploy it as a supportive coach. By
designing workflows where the technology challenges assumptions, critiques
reasoning, and highlights weaknesses without simply correcting them,
organizations can help employees develop essential independent judgment.
Data Is Risky Business: Thinking Beyond Systems for Data Governance
Data governance goes far beyond formal frameworks, organizational charts, and
written policies. While audits can evaluate a system by its final outputs,
they rarely explain why well-intentioned employees within well-designed
structures fail to govern data effectively. The true practice of data
governance is shaped continuously by how people interpret their roles and
responsibilities in everyday situations. Employees often rely on inherited
traditions and beliefs when faced with real-world dilemmas, meaning that a
formal rule is less influential than what the employee believes the rule is
actually for. A documented procedure or escalation process only works if team
members feel comfortable using it and believe that flagging an issue
demonstrates competence rather than causes trouble. Effective coordination
among teams, where individuals understand how their actions affect the wider
organization, is crucial for catching anomalies and handling unexpected
disruptions. Furthermore, over-automating these governance processes can be
dangerous. When human reviewers are removed from routine tasks, they lose the
practical experience needed to spot complex or novel failures when automation
inevitably falls short. Ultimately, resilient data governance requires
organizations to intentionally cultivate a culture of collaboration, build
strong communication routines, and maintain the critical human judgment needed
to handle unpredictable data risks.
The BTABoK and Agents
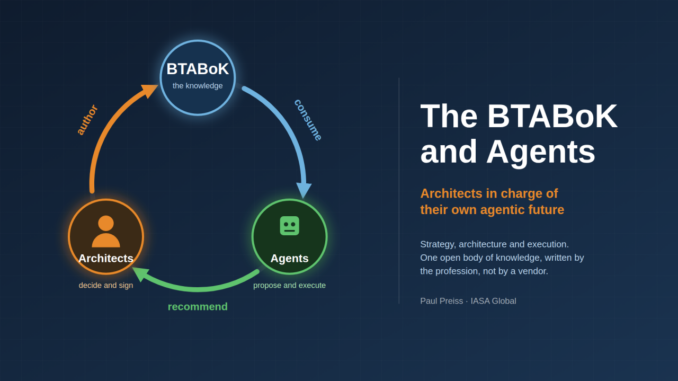 Artificial intelligence agents can generate impressive architectural models in
seconds, but their output is only as good as the knowledge they draw from.
While agents make speed cheap, they can compromise decision quality and shared
understanding if not set up correctly. The Business Technology Architecture
Body of Knowledge offers the most effective foundation for integrating agents
into technology architecture. Unlike vendor specific frameworks that
prioritize product sales or in house wikis that rely on fragmented opinions,
this open framework provides a continuous chain connecting strategy to final
delivery. It treats decisions as the central artifacts, ensuring every choice
has clear trade offs and an accountable human owner. This is crucial because
an agent produces options too quickly for humans to review without structured
decision records. Furthermore, the framework defines specific viewpoints to
answer exact stakeholder concerns and includes a clear competency model,
meaning human architects remain equipped to properly evaluate and approve the
generated work. Ultimately, this approach ensures that human practitioners,
rather than vendors, remain in charge of the knowledge their agents use. By
relying on a structured and practitioner governed foundation, organizations
can safely accelerate their architecture practices without sacrificing
accountability or quality.
Why Cybersecurity Must Become A Truly Professionalised Industry
The cybersecurity industry handles incredibly sensitive data and systems, bearing a level of responsibility similar to the medical or financial fields. However, it still lacks the strict, universal professional standards found in those established sectors. Currently, the quality of services like penetration testing varies significantly between providers, making it difficult for organizations to distinguish true expertise from clever marketing. To build genuine trust, the industry must adopt independent accreditation and verified certifications for both organizations and individual practitioners. Frameworks like the United Kingdom's CHECK scheme or global bodies like CREST offer a reliable baseline, assessing not just technical skills but also ethical conduct and operational maturity. As artificial intelligence makes sophisticated attack tools much more accessible, relying on validated human judgment becomes even more essential. Furthermore, because technology evolves rapidly, professionals must undergo continuous reassessment rather than relying on static, one-time qualifications. Professionalizing cybersecurity is not about adding unnecessary bureaucracy; it is about ensuring accountability, reliability, and consistency across the board. By demanding rigorous, ongoing standards, organizations can confidently partner with security experts, knowing they possess the necessary skills and ethics to protect vital digital infrastructure from increasingly complex and fast-moving threats.Behind every AI inferencing strategy: The storage decision multi-model databases demand
 As businesses rapidly deploy generative AI, the focus is shifting from simply
training models to the critical phase of inferencing—the point where AI
actually analyzes data and generates responses. While powerful processors like
GPUs often grab the headlines, the true bottleneck for successful AI
inferencing usually lies in data storage. Modern AI applications do not just
rely on one type of data; they require a complex mix of text, images,
relationships, and structured information. This complexity has driven the rise
of multi-model databases, which can handle various data types—such as graphs,
documents, and vectors—within a single system. However, these versatile
databases place immense strain on storage infrastructure. To deliver the
real-time, accurate results that enterprise AI demands, storage systems must
provide exceptional speed, massive scalability, and the ability to process
multiple data formats simultaneously without latency. Traditional, siloed
storage setups often struggle to keep pace with these multi-model demands.
Therefore, organizations must carefully evaluate their storage architecture,
prioritizing high-performance solutions that seamlessly support multi-model
databases. Ultimately, a successful AI strategy depends just as much on
selecting the right underlying storage as it does on choosing the most
advanced algorithms or processors.
Inside a Software Factory
The concept of a software factory is evolving from a traditional managed
pipeline into an automation-driven system that transforms how engineering
teams build and ship code. Instead of relying solely on artificial
intelligence as a simple coding assistant within an editor, a modern software
factory integrates automated agents directly into the broader development
lifecycle. This system requires four core properties: standardized inputs,
standardized tooling, measurable outputs, and complete replayability. Work
enters the factory through various signals like bug reports or internal
requests, which are then triaged into clearly scoped tasks. From there,
software development agents take over to plan, execute, test, and review the
code changes. However, humans remain firmly in the loop. The architecture
relies heavily on persistent context, ensuring that security policies,
business rules, and architectural guidelines govern the automated actions at
every step. This shifts the role of software engineers. Rather than writing
every line of code themselves, engineers now manage and supervise the
underlying system, taking responsibility for its safety, governance, and
business outcomes. Ultimately, this approach creates a continuous feedback
loop where the development environment learns and improves over time, enabling
organizations to deliver reliable software with greater consistency and
visibility.
Leverage Code Review for Sustainable AI Coding Development
 As artificial intelligence tools become a standard part of the software
development process, teams are generating code at an unprecedented pace. While
these advanced assistants significantly boost immediate productivity, they
also introduce unique challenges. Without proper oversight, automated code can
easily hide subtle bugs, security vulnerabilities, and structural flaws that
ultimately create massive technical debt. To build applications responsibly,
organizations must leverage rigorous code review practices to ensure lasting
sustainability. Instead of blindly accepting computer suggestions, engineering
teams must adapt their review processes to carefully scrutinize artificial
intelligence contributions. Human oversight remains absolutely essential in
this new landscape. Developers need to act as diligent editors, thoroughly
validating the logic, performance, and security of every generated block of
code before it reaches production. Strong peer review cultures prevent quick
fixes from becoming massive maintenance nightmares. Furthermore, combining
human expertise with modern testing tools ensures that codebases remain clean,
functional, and secure over time. By placing a renewed emphasis on thorough
code reviews, companies can safely harness the incredible speed of modern
development tools. This balanced approach allows teams to innovate rapidly
while maintaining the high standards required for sustainable and reliable
software architecture today.
Why agentic AI is the key to systems integrity
As companies face stricter operational and security regulations, they are
rapidly adopting agentic artificial intelligence systems capable of taking
actions autonomously with minimal human input. While these powerful tools
offer substantial productivity boosts, they also require broad data access and
elevated privileges to function properly. This greatly expands the attack
surface and introduces new vulnerabilities, especially within heavily
regulated industries. Balancing this rapid innovation with strict oversight is
a major challenge, particularly when organizations attempt to scale advanced
tools across older, fragmented technologies. The most effective solution lies
in deploying enterprise-grade platforms that embed security controls directly
into their core design from the very beginning. By weaving identity
management, access limitations, and continuous monitoring directly into the
software development process, well-designed agentic systems actually
strengthen overall integrity rather than weaken it. This proactive approach
standardizes workflows, enforces real-time policy compliance, and prevents
unauthorized internal development. To successfully scale these intelligent
operations, businesses must unify their technology platforms, integrate
security measures much earlier in the planning stages, and provide automated
guardrails that empower teams to explore safely. Ultimately, treating
oversight as a fundamental building block ensures that organizations can
embrace modern automation without sacrificing valuable customer trust or
compromising critical internal data.
 European governments are moving past simply storing sensitive data within
their borders and are now deeply questioning who truly controls their digital
infrastructure. High-profile actions, such as Switzerland avoiding American
cloud services for its national digital identity system and the Netherlands
blocking a U.S. acquisition of a critical local cloud provider, highlight a
growing concern over digital sovereignty. The core issue lies in jurisdiction:
even if data is stored in a European server and heavily encrypted, relying on
foreign-owned companies means the information might still be subject to
outside laws, like the U.S. CLOUD Act. To counter these vulnerabilities,
Europe is expanding its definition of tech sovereignty far beyond mere data
localization. The European Commission has introduced strict new frameworks for
cloud procurement that evaluate strategic, legal, and operational control,
sometimes requiring an entirely European supply chain. Furthermore, the push
for digital autonomy includes developing independent capabilities in
semiconductors, artificial intelligence, and biometrics to reduce reliance on
foreign standards and institutions. By prioritizing decentralization in
projects like digital identity wallets, Europe aims to minimize centralized
data storage altogether, asserting true control over its entire technology
ecosystem rather than just dictating where its data physically resides.
From data residency to tech sovereignty: Europe rethinks control
European governments are moving past simply storing sensitive data within
their borders and are now deeply questioning who truly controls their digital
infrastructure. High-profile actions, such as Switzerland avoiding American
cloud services for its national digital identity system and the Netherlands
blocking a U.S. acquisition of a critical local cloud provider, highlight a
growing concern over digital sovereignty. The core issue lies in jurisdiction:
even if data is stored in a European server and heavily encrypted, relying on
foreign-owned companies means the information might still be subject to
outside laws, like the U.S. CLOUD Act. To counter these vulnerabilities,
Europe is expanding its definition of tech sovereignty far beyond mere data
localization. The European Commission has introduced strict new frameworks for
cloud procurement that evaluate strategic, legal, and operational control,
sometimes requiring an entirely European supply chain. Furthermore, the push
for digital autonomy includes developing independent capabilities in
semiconductors, artificial intelligence, and biometrics to reduce reliance on
foreign standards and institutions. By prioritizing decentralization in
projects like digital identity wallets, Europe aims to minimize centralized
data storage altogether, asserting true control over its entire technology
ecosystem rather than just dictating where its data physically resides.Automated response and SOAR design patterns for security teams
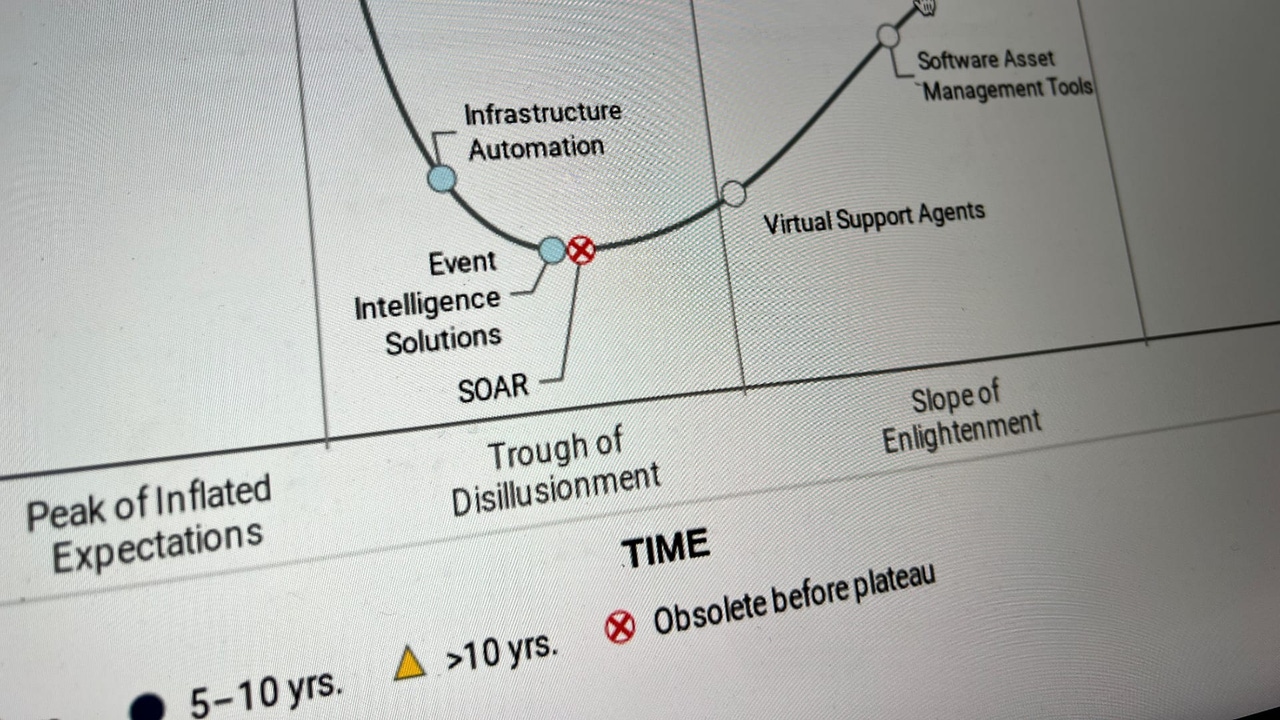
Security Orchestration, Automation, and Response (SOAR) functions as an
essential control layer that connects various security tools and teams,
transforming noisy alerts into consistent, repeatable workflows. Rather than
replacing human judgment or detection engineering, SOAR platforms excel at
tasks like alert enrichment, case creation, and careful incident containment.
A fundamental design principle for safe automation is separating decision
support from direct execution. Playbooks should gather vital context and
recommend actions, but automated responses must always align closely with
technical confidence levels and potential business impact. If underlying
detection quality is poor, reckless automation will simply accelerate bad
decisions and disrupt daily operations. For many organizations, particularly
smaller enterprises, the safest and most valuable initial pattern is automated
alert triage and data enrichment. This approach rapidly improves decision
quality without introducing unnecessary operational risk. When teams do choose
to automate containment actions, such as isolating a compromised endpoint or
forcing a user password reset, these interventions should strictly apply to
high-confidence, reversible scenarios. Identity-focused responses often
provide the cleanest automation targets because they remain centralized and
are easily reversed if necessary. Ultimately, successful automation must
carefully follow reliable detection quality instead of attempting to forcibly
solve ambiguous security threats.