Quote for the day:
“In times of change, learners inherit the earth; while the learned find themselves beautifully equipped to deal with a world that no longer exists.” -- Eric Hoffe
🎧 Listen to the audio debrief on YouTube
▶ Play Audio DigestDuration: 22 mins • Perfect for listening on the go.
Why DBAs are right to be skeptical of AI — and where they’re wrong
 Database management has grown significantly more complex over the past three
decades, turning scalability into an expertise problem rather than a simple
staffing issue. Adding more database administrators (DBAs) to a struggling
system rarely resolves performance problems; instead, organizations need
experienced professionals who can accurately diagnose root causes. However,
skilled DBAs are expensive and increasingly scarce, especially as the demand for
massive databases supporting artificial intelligence and large language models
(LLMs) continues to rise. This is where AI tools can provide meaningful support
without replacing human expertise. While human operators are prone to making
assumptions or taking risky shortcuts under pressure, properly constrained AI
models excel at following defined diagnostic processes consistently. By
providing an LLM with read-only access to monitoring data and clearly structured
instructions, teams can compress hours of manual log analysis into mere minutes.
The key to success is establishing strict guardrails around what the AI can
execute. The model diagnoses the issue and proposes a solution, but a human
administrator retains full control over approving and applying any changes to
the live database. Starting with this low-risk approach allows organizations to
manage growing complexity effectively while the industry slowly builds broader
trust in autonomous operations.
Sovereign cloud is no longer just about where data resides
The concept of a sovereign cloud is evolving far beyond simply keeping data within a country's borders. According to Ravi Jain from IBM India, true digital sovereignty is fundamentally about control rather than just physical location. As artificial intelligence becomes deeply integrated into everyday operations and modern business systems, organizations are asking harder questions about who manages their environments, who holds the encryption keys, and where their AI models actually run. This shift is rapidly moving the conversation from basic data residency to comprehensive AI sovereignty. Regulated sectors in India, such as government, finance, and healthcare, are increasingly viewing this level of operational control as a core architectural requirement. However, Jain notes that not every system needs the same level of strict oversight. Instead of a one-size-fits-all approach, technology leaders should assess their systems individually, applying tighter controls only where data sensitivity and business risks truly demand it. Ultimately, organizations want the freedom to place their systems across various environments without becoming locked into a single technology provider. By focusing on operational independence and transparent governance, businesses can maintain strict control over their most critical assets while still retaining the flexibility needed to operate efficiently and confidently in the future.AI Changed the Exposure Problem. Validation Needs to Change With It
 As artificial intelligence accelerates the discovery of security
vulnerabilities, security teams face a rapidly growing number of reported
exposures. Although published vulnerabilities have increased significantly,
only a small fraction are actually exploited in the real world. This widening
gap means that relying entirely on traditional severity scores is no longer an
effective strategy, as these scores fail to account for a network's unique
environment and active defensive controls. While automated penetration testing
provides valuable insights, it has limitations. It cannot safely test all
critical business systems and requires an existing exploit to function
properly. To adapt, security professionals need a more comprehensive approach
to vulnerability validation. This involves combining exploitability
validation, security control testing, and agentic penetration testing into a
single unified workflow. By integrating these methods, organizations can
accurately determine which vulnerabilities pose a genuine threat to their
specific infrastructure, even when standard exploits are not yet available.
This unified strategy allows security teams to prioritize real risks over
theoretical ones and focus their remediation efforts where they matter most.
Industry leaders will further explore this practical approach to modern
security validation during the upcoming Picus Security Validation Summit,
demonstrating how mature enterprises are adapting to the changing threat
landscape.
What Capital Markets Can Teach Enterprises About Integrated Data Infrastructure
Capital markets can teach enterprises a lot about setting up integrated data infrastructure. For over a decade, capital markets have been combining technology, analytics, and data into a unified structure to give them a competitive edge in pricing and trading. To do this, these firms need to handle large amounts of data very quickly and with high accuracy. They do this by using a centralized data repository where they can clean and manage the data. They establish clear rules on how to manage and use the data. To ensure that everyone works together, they create data teams comprising both technical experts and business leaders. This ensures that the data is not only technically sound but also aligns with the business goals. For an enterprise, this means breaking down silos between departments and viewing data as a unified asset rather than a collection of separate pieces. It also means using new technology like cloud computing to better manage and analyze the data. Doing so can make it easier to adopt newer technologies such as AI and machine learning, which rely on having a solid foundation of data to work effectively.Govern AI agents like workers. Just don’t pretend they’re human
 As artificial intelligence agents become more capable of completing tasks
across corporate systems, IT leaders face a new challenge in managing them.
According to industry experts, the best approach is to borrow management
techniques from human resources without pretending that the AI is actually
human. While it makes sense to handle agents similar to new workers, giving
them specific roles, supervision, and gradually increasing their freedom as
they prove reliable, companies should never give them human names, personas,
or official spots on the organizational chart. Doing so creates a false sense
of trust and blurs the lines of responsibility. Unlike traditional software,
these advanced programs can make their own choices to achieve a goal. This
means they need strict oversight, technical identities for tracking their
actions, and clear boundaries. Some leaders compare them to interns, where
they start with basic tasks and need constant human approval before earning
more independence. However, the most crucial rule is that accountability must
always remain with human employees. An AI agent might have permission to
access data and execute actions, but it lacks human judgment and corporate
values. If a mistake happens, a human or a policy owner must be responsible,
not the software.
Your employees are already using AI tools you never approved
According to a recent report on workplace technology, artificial intelligence
is now widely used across most companies, with nearly three quarters of
organizations adopting it in their daily operations. However, managing this
rapid adoption safely remains a significant challenge for leadership. While
many companies have established basic rules for artificial intelligence, only
a small fraction have fully integrated risk management into their daily
workflow from the very start. This lack of integration leads to frustrating
issues with speed and consistency. A major concern is that employees
frequently use unapproved tools because the official options take entirely too
long to access, leading to unexpected security issues. Furthermore, as
businesses increasingly encourage the use of autonomous programs, internal
oversight struggles to keep pace. Data security, accuracy, and loss are the
most prominent risks, and current review requirements frequently delay new
projects. Despite these hurdles, businesses are actively trying to improve
their safeguards. Teams are spending significantly more time managing these
specific risks than they did just a year ago. To address these growing needs,
nearly all surveyed organizations plan to increase their spending on oversight
technologies in the coming year, focusing heavily on employee training,
clearer rules, and continuous system monitoring.
Applying the roadmap: 3 common M&A scenarios
 Managing physical security during mergers and acquisitions requires careful
preparation and adaptable strategies to succeed over time. Security teams face
different challenges depending on the current stage of the organization in the
acquisition process. If a company expects future acquisitions, security
leaders should begin by clarifying basic risk profiles, setting aside
realistic budgets for system integrations, and organizing their internal teams
to make future transitions easier. When an acquisition is actively happening,
the focus shifts to maintaining clear communication with the planning
committee, identifying key experts within both organizations, and conducting a
thorough inventory of current security assets. For companies that are
constantly acquiring others, achieving true standardization across all systems
might be impossible. Instead, these organizations should focus on maintaining
a strong core incident response plan while managing a variety of everyday
technologies. In this perpetual cycle, it is strictly critical for security
leaders to remain visible, communicate realistic timelines, and ensure their
functional value is well understood. Ultimately, involving physical security
early in the process and building flexible plans helps reduce risks and
ensures that daily operations continue smoothly during any transition. By
staying organized and calm in their approach, security teams can effectively
support the lasting growth of the company and create a unified program.
AI inferencing is headed for the network edge
 Recent advancements in hardware and software are accelerating the shift of AI
inferencing from centralized cloud data centers to the network edge, making
2026 a pivotal year for this transition. As the volume of data generated by
billions of connected devices continues to surge, organizations face mounting
pressure to process information locally. Key drivers for this shift include
the high cost of transporting massive datasets to the cloud, the need for
immediate responses to minimize delays, and strict data privacy rules that
demand localized control over sensitive information. Technological
breakthroughs are making this possible. Smaller AI models and highly efficient
processing chips allow complex operations to run directly on devices without
draining power. Consequently, analysts predict that by 2030, half of all
enterprise AI inference workloads will run on edge nodes. This capability is
unlocking practical applications across industries, from instant quality
control in manufacturing to autonomous agricultural equipment and advanced
pedestrian safety systems. While the industry currently faces hurdles such as
deployment complexity, capital costs, and a fragmented vendor landscape, the
overall trajectory remains clear. The edge AI sector is expected to grow
significantly faster than the broader AI market over the course of the next
few years.
Meta’s smart glasses privacy defense falters when AI can use camera without recording light
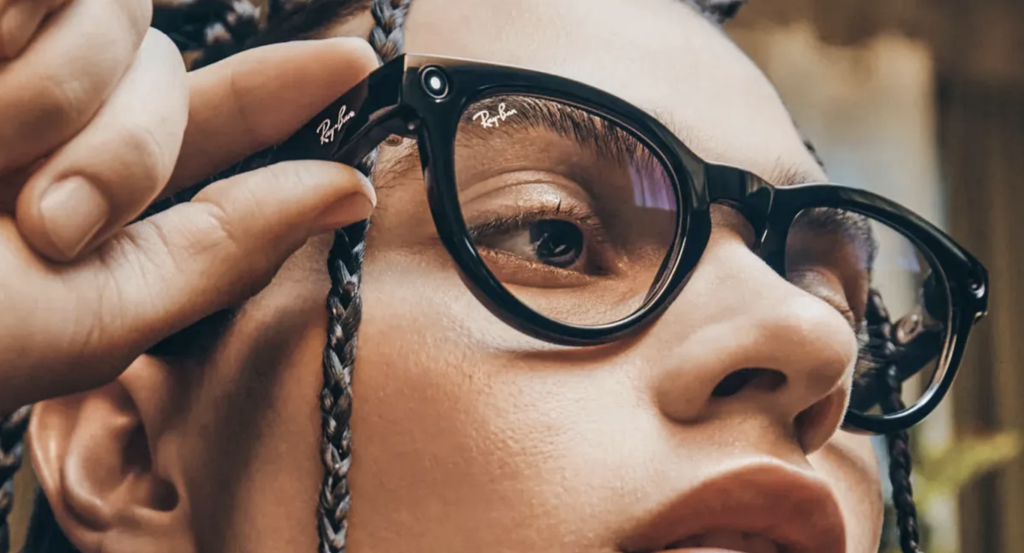 Meta's smart glasses rely on a visible LED light to warn bystanders when a
user takes a photo or records a video. The company defends this safeguard
aggressively, even disabling devices if the light is tampered with. However, a
significant privacy issue has emerged because this indicator does not
illuminate when the glasses use camera-based artificial intelligence features.
According to company documentation, if a wearer asks the AI to identify a
landmark or an object, the camera captures an image for machine analysis
without turning on the warning light. Meta argues these images are processed
by the AI rather than saved to a personal gallery, but this technical
distinction is sparking legal and regulatory pushback. In the United States,
class-action lawsuits have expanded to include bystanders who allege their
information is collected without their consent. Meanwhile, European regulators
are considering stricter rules, including potential bans on public facial
recognition features for consumer eyewear. Additionally, American law
enforcement agencies have issued warnings about the security risks of
civilians using the glasses to secretly record police operations, even as some
departments begin using the technology themselves. Ultimately, the invisible
nature of AI analysis is exposing the limitations of relying solely on visible
recording indicators.
What the 3M ChatGPT case reveals about AI governance
 The Watson Grinding litigation involving 3M highlights a critical but often
overlooked aspect of managing artificial intelligence: the legal
discoverability of everyday user interactions. During the case, an engineering
expert requested that ChatGPT show 3M as entirely blameless, and those prompts
eventually became central to a deposition. This incident shows that
organizations must look beyond simply controlling what data employees put into
AI models and start actively managing the lifespan of the generated records.
Currently, businesses focus heavily on preventing the accidental exposure of
private information. However, AI prompts and chat histories can also preserve
underlying assumptions, rejected alternatives, and lines of reasoning that
never appear in a finished report. While keeping every prompt forever would
create unnecessary security and privacy risks, organizations need practical
rules based on the importance of the work being done. For high-stakes
situations, companies should retain enough of the interaction history to
accurately reconstruct how a specific decision was made. This requires clear
collaboration between IT, legal, and compliance departments to establish
steady retention and ownership protocols. Ultimately, the 3M case serves as a
straightforward warning that companies must deliberately manage their AI
footprints so they can confidently explain the tool's role if their decisions
are later questioned.

