Quote for the day:
“The more I read, the more I acquire, the more certain I am that I know nothing.” -- Voltaire
Brain-Machine Interfaces Are Advancing: What Leaders Need to Know About Neurotechnology
 The convergence of artificial intelligence, smaller electronics, and advanced
materials is accelerating the steady development of brain-machine interfaces,
allowing for practical communication between human brains and digital systems.
While this field is currently focused on healthcare, with recent clinical
studies showing paralyzed patients successfully using neural interfaces to
control devices and communicate independently at home, its applications will
soon expand. In the near future, industries such as education, manufacturing,
and assistive technology will likely adopt these emerging tools to improve
human performance and overall accessibility. By the end of the decade, the
technology is expected to feature more accurate signals, less invasive
hardware, and better machine interpretation of brain activity. Rather than
guessing which specific device will dominate the market, organizations and
leaders should prepare for these predictable advancements now. This means
tracking improvements in neural decoding, exploring diverse interface methods
like ultrasound, and considering how neural data might fit into future product
lines. Just as importantly, the widespread use of neurotechnology will create
new challenges surrounding data privacy, system compatibility, and user
control over sensitive neural information. Solving these practical problems
will offer significant opportunities for those who calmly anticipate the
steady progress of neural engineering and plan accordingly.
Opinion: Tech enables transformation, people achieve it
Daire Cunningham’s article explores why so many organizations struggle to get real value from artificial intelligence, despite the technology being widely available. He notes that while 88% of businesses use AI in some capacity, only a third have managed to scale it across their operations. The core issue, he argues, isn’t a lack of access to advanced tech, but rather the underlying condition of the organizations trying to use it. When companies rush to adopt AI, they often start by looking for a specific tool instead of identifying the actual business problem they need to solve. To succeed, leaders must work backward: map out their processes, figure out where the information is kept, and spot the real bottlenecks. A major roadblock is poor data readiness—many businesses have years of accumulated, disorganized data and permissions. AI tends to expose these underlying flaws rather than cause them. Ultimately, Cunningham believes digital transformation is about rethinking how work gets done, not just adding new software. While AI can process data faster and tackle complex tasks, human judgment and oversight remain essential. True transformation happens when a company prepares its data foundation and empowers its people to use technology responsibly.CIOs offer guiding principles on how to achieve AI sovereignty
 The article discusses the growing importance of AI sovereignty for Chief
Information Officers (CIOs). This concept is centered on maintaining control
over an organization’s entire AI ecosystem, which encompasses data, models,
and the infrastructure hosting those models. As AI technology becomes
increasingly integrated into business operations, organizations face mounting
risks related to data privacy, regulatory compliance, and potential vendor
lock-in. To manage these challenges effectively, CIOs recommend establishing
clear guiding principles. First, it is crucial to create a comprehensive
inventory of all AI resources currently in use, as you cannot manage what you
do not track. Second, organizations must implement robust data and usage
controls to monitor information flow and quickly identify any policy
violations. This proactive approach helps secure sensitive data. Third,
companies should update their incident response plans specifically to address
potential AI-related breaches, ensuring they can act swiftly if issues arise.
Finally, maintaining transparency and auditability is essential. Knowing who
accessed data and how AI tools influence decision-making helps build trust and
ensures regulatory compliance. Rather than viewing AI sovereignty as a simple
compliance checklist, leaders should treat it as a fundamental strategy for
the long-term success and security of the enterprise.
Children's Data Protection in the Age of EdTech and Platform Design
The digital age has made children’s data collection widespread, from location tracking and educational data to behavioral and voice information. While some of this is meant for learning or safety, the concern is that such data can be used for profiling, targeted ads, or boosting engagement without parental consent. This has made data protection laws surrounding children increasingly relevant. India's Digital Personal Data Protection (DPDP) Act, 2023 defines a child as anyone under 18, which is a higher threshold than seen in many other countries. This act requires platforms to secure verifiable parental consent before processing a child’s data and forbids processing that could harm a child’s well-being. Additionally, the DPDP Act bans the tracking, behavioral monitoring, and targeted advertising directed at children, though it provides some exceptions for safe uses in healthcare, education, or child safety. Internationally, there are variations in how children's data is handled. In the United States, COPPA applies to children under 13, while the European Union’s GDPR sets the default age at 16, though member states can adjust it to 13. The UK’s Children’s Code requires platforms that children are likely to use to have high privacy settings by default. For platforms dealing with children's data, balancing data retention limits with educational needs requires clear strategies and compliance checks.Most enterprises are failing to translate talk into meaningful dependency mapping
 The recent feature on digital sovereignty highlights a significant gap between
what organizations want and what they can actually achieve. While most
companies express a strong desire to regain control over their digital
infrastructure, the reality is that true independence remains out of reach for
many. The truth is that achieving digital sovereignty is not simply about
building internal data centers or buying local software; it requires deep
visibility into existing information systems and having credible exit options
from major service providers. Unfortunately, most enterprises currently lack
these fundamental building blocks. Over the past fifteen years, a rush toward
cloud computing has left many businesses heavily dependent on a handful of
dominant technology giants. This dependency makes it incredibly difficult to
pivot or change providers without facing steep costs and major operational
disruption. As artificial intelligence becomes central to business strategy,
the stakes for retaining control over data and computing power are higher than
ever before. The article suggests that instead of pursuing total independence,
leaders should focus on preserving choice. By prioritizing flexible tools and
establishing clear governance, organizations can gradually build resilience.
Ultimately, sovereignty is about making smart decisions today that prevent
complete vendor entanglement in the future.
Agentic Systems and Design Patterns
The shift toward agentic artificial intelligence marks a move from simple text
generation to setups that can plan, take action, and learn from their
mistakes. When building these systems, developers must first choose an overall
structure. A single agent approach is easier to build and manage, making it a
great starting point, though it can struggle with complex or extended tasks.
Conversely, a multiple agent system uses an orchestrator to delegate work to
specialists, which boosts reliability through teamwork but requires careful
coordination. Beyond the basic structure, six core design patterns drive how
these models function. The ReAct pattern mixes logical thinking with concrete
actions in a loop, while CodeAct allows agents to write and test code to
achieve their goals. Self reflection acts as an internal critic to refine
outputs and fix errors. Basic tool use lets agents interact with outside
software, and Agentic RAG improves how they fetch and verify information.
Finally, the multiple agent workflow handles massive tasks by dividing them
into smaller parallel jobs. For the best results, start with a simple single
agent setup and only add complexity when the task demands it. Strong
safeguards, like strict iteration limits and clear tool definitions, keep
these systems reliable and easy to monitor.
What OT Resilience Actually Controls
The article from SC Media explains that recovering operational technology (OT) after a cyber incident requires a fundamentally different approach than recovering standard IT systems. While IT disaster recovery focuses on system availability—getting servers and applications back online—OT recovery requires "safe-state validation." This means ensuring the manufacturing process can be controlled safely before restarting production. The challenge is that standard IT backups often miss crucial OT engineering data, such as process configurations, device programming, and safety system logic. Without these, a restored system might appear functional but lack the specific parameters needed to operate safely. The author outlines five common failure scenarios in OT resilience, including ransomware affecting control systems, vendor platform outages, and control logic tampering. These scenarios highlight the need for specialized OT backup architectures and recovery procedures. Ultimately, true OT resilience involves validating configurations at the device, system, and process levels, often requiring specialized engineering expertise. This validation step adds time to the recovery process but is essential to prevent unsafe conditions that could lead to physical harm or environmental damage.Achieving data sovereignty for SaaS with confidential containers and quantum-safe networking
 Software vendors hosting services on the public cloud face increasing pressure
from customers who want to keep their data secure and private. Often,
customers prefer on-premise solutions, which are harder to manage and scale
for vendors. A better approach allows vendors to keep their services in the
cloud while offering robust security through cryptographic controls,
specifically using confidential computing. This technology secures data
processed in untrusted environments by isolating it in a trusted execution
environment (TEE). Red Hat and Arqit have introduced a setup that uses
confidential containers and quantum-safe networking to protect data in
transit. They applied this to Arqit's Encryption Intelligence (EI) platform.
In this setup, services and data are isolated from the host environment,
allowing customers to maintain control over their data while protecting the
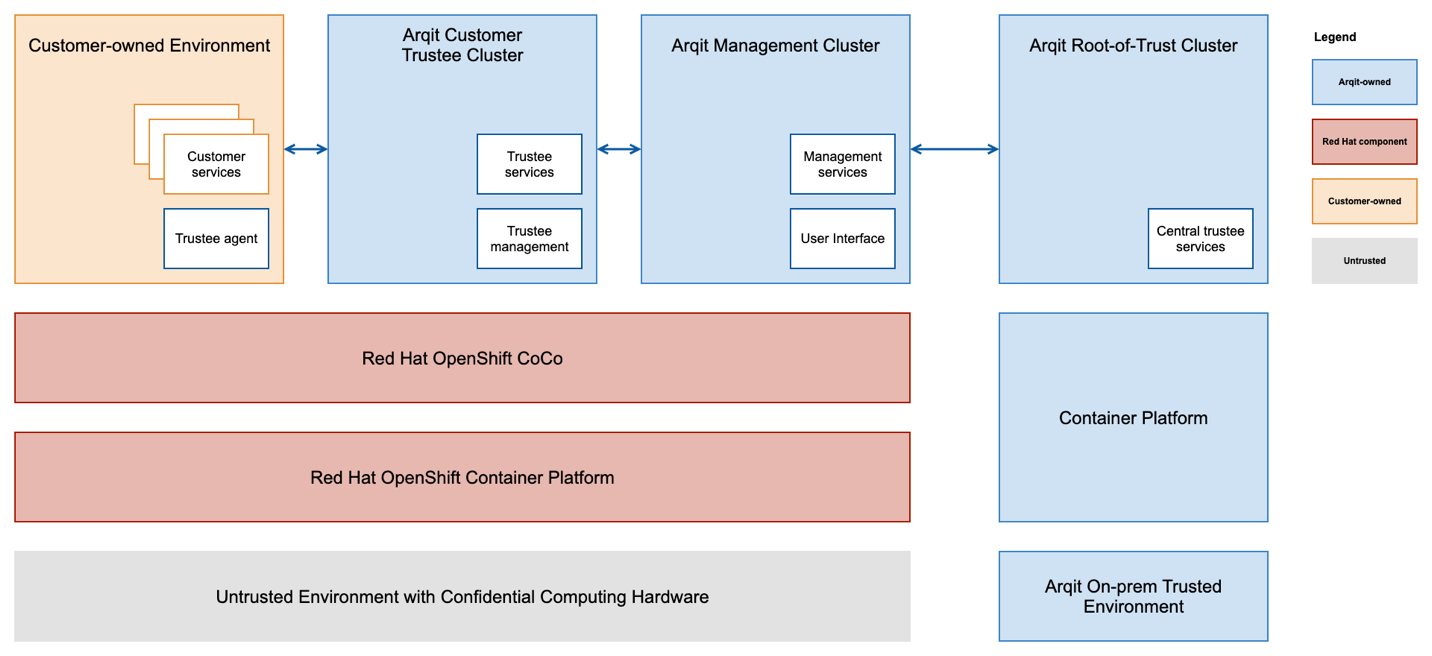
vendor's intellectual property. The architecture involves three clusters
operating in the untrusted environment, communicating via a quantum-safe
connection. Trust is established by an outer trustee in a trusted on-premise
environment, which verifies the inner trustee in the cloud. This combination
of confidential containers and quantum-safe protection for data in transit
offers a practical alternative to on-premise deployments, providing strong
assurance over data security and sovereignty for both vendors and customers.
AI-led SOC infrastructure shifts from raw data to outcomes
 The article discusses a shift in how modern Security Operations Centres (SOCs)
measure success in an AI-driven environment. Historically, SOCs focused on
volume metrics, such as alerts processed or data ingested, but this model
struggles against modern threats across distributed environments. Today, the
focus is shifting to measuring outcomes like risk reduction, analyst capacity,
and decision quality. The traditional volume-driven model leads to
rising costs, overwhelmed analysts, and incremental improvements, failing to
deliver clear returns on investment. While AI is viewed as a solution, it has
struggled to deliver value when treated simply as an overlay, lacking
transparency and integration. To overcome these limits,
organizations must build SOCs around productivity rather than throughput,
connecting technology investments with operational impact. In this model, AI
isn't measured by its theoretical capability but by the work it completes
alongside human analysts. A critical component is the use of "Agentic AI" as
an execution layer, which coordinates investigations and decisions rather than
functioning in isolation. For AI to be effective, it must also be governed to
ensure actions are explainable and align with organizational policies,
allowing security leaders to demonstrate responsible use and measurable
security outcomes.
Data sovereignty is a control problem, not a geography problem
The article argues that data sovereignty is fundamentally about control, not
geography. Many organizations assume that storing data within national borders
is enough, but the author explains that this view is too narrow. True
sovereignty depends on knowing who controls identities, administration,
infrastructure, and legal authority over the data. Recent events have exposed
how fragile digital infrastructure can be, from attacks on subsea cables to
large‑scale outages like the CrowdStrike incident, which disrupted critical
services worldwide and led to major financial losses. At the same time, new
regulations and the rise of AI have increased the stakes, since sensitive
information and intellectual property now flow through cloud‑hosted models
governed by foreign jurisdictions. The article stresses that organizations
often lack visibility into where their data lives, who can access it, and
which laws apply. To regain sovereignty, they must demand transparency from
providers, understand dependencies, and treat governance as an architectural
requirement rather than an afterthought. Cost and speed still matter, but they
can’t outweigh resilience and accountability. Sovereignty, the author
concludes, isn’t about abandoning the cloud—it’s about ensuring organizations
retain meaningful control so they can manage risk and respond confidently when
incidents occur.


No comments:
Post a Comment