Showing posts with label digital trust. Show all posts

Daily Tech Digest - November 10, 2026

Quote for the Day
“Agility is the ability to adapt and respond to change.”
— Jim Highsmith
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

7 tips for achieving defensive agility

The article explains that defensive agility is the ability to detect, adapt to, and respond to changing cyber threats quickly without unnecessarily disrupting business operations. It recommends starting with zero trust, continuously verifying access across users, devices, and applications, while simplifying older, fragmented security infrastructure that can slow containment. Automation and AI can help shorten response times, but autonomous actions should initially focus on areas where confidence is high and mistakes can be easily reversed. The article argues that resilience should also be designed into systems so threats can be isolated without waiting for lengthy human approvals. Security governance must support quick decisions rather than create bureaucracy that gives attackers more time. Automation should handle repetitive work while leaving people responsible for judgment when unusual situations arise. Finally, organizations should regularly rehearse difficult incident scenarios so responsibilities for patching, testing, communication, and taking systems offline are understood before a crisis. The central message is that defensive agility comes less from acquiring more security tools and more from clear authority, adaptable architecture, sensible automation, and repeated practice.
Read Original Article →
Article Thumbnail

NIST: Solo Shouldn't Mean Less Secure

The article examines new NIST cybersecurity guidance designed for solo business owners, who often lack the money, time, and technical support available to larger companies. The guidance translates the Cybersecurity Framework into simpler advice, covering basics such as phishing-resistant authentication, password managers, automatic updates, non-admin accounts, and tested offline backups. Experts welcome the effort but argue that parts remain too technical and demanding for someone running a business alone. Important gaps include protecting domain registrar accounts, setting up email authentication, and having an emergency access plan when the owner is unavailable. The article also questions whether the guidance adequately addresses AI. Solo operators increasingly use AI assistants to access email, run commands, write code, and act through their accounts, yet the document largely treats AI as something passive to inventory and review. Critics also note that the recommendations are not clearly prioritized and that cyber risk depends more on exposed data and business activities than headcount. Overall, the guidance provides a useful baseline, but effective protection for solo businesses requires clearer priorities and stronger attention to autonomous AI and practical operating realities.

Read Original Article →
Article Thumbnail

Cyber Recovery Readiness: The Dark Side of “We Have Backups”

The article argues that having intact backups is not the same as being ready to recover from a cyberattack. Real recovery means rebuilding a trustworthy business service when normal identities, tools, infrastructure, and assumptions may no longer be available. It describes several ways recovery plans can fail: backup data may survive while administrative access or encryption keys do not; the newest backup may already contain compromised data; identity services can create circular dependencies; and recovery priorities may ignore essential technical connections between systems. Organizations may also discover that they have nowhere suitable to restore older applications, or that promised recovery times exclude investigation, access restoration, validation, rebuilding, and business testing. Even successfully restored applications can leave inconsistent transactions across connected systems. The article recommends treating recovery as an evidence-based process, with isolated testing, protected emergency access, dependency mapping, viable rebuild infrastructure, realistic timing measurements, and business-led acceptance checks. Its central message is that recovery readiness should prove an organization can safely resume useful operations, not merely demonstrate that backup files exist or that a test server can be restored.

Read Original Article →

Trust, not technology, is now the speed limit on enterprise AI

The primary obstacle to scaling enterprise artificial intelligence has definitively shifted from technical capability to human trust, according to new Cisco research. While organizations once focused entirely on acquiring the fastest models and infrastructure, many now find their expensive investments underutilized because they neglected cultural adoption. True integration requires calibrated trust, where employees understand exactly when to rely on these systems, when to verify outputs, and when human judgment is absolutely necessary. Blindly accepting generated answers creates errors, while lacking clear boundaries causes hesitant employees to avoid the tools entirely. To overcome this gap, companies must treat deployment as a cultural transformation led by the entire executive team, not just an isolated technology rollout. Starting with visible, low-risk wins helps build practical confidence across the workforce far more effectively than broad company mandates. Furthermore, as organizations move toward autonomous agents, establishing strong network and identity controls is essential. By treating security and clearly defined guardrails as enablers rather than restrictions, companies can empower their employees to experiment safely, ultimately proving that scaling human trust is the true key to scaling technology.

Read Original Article →
Article Thumbnail

5 big Windows headaches and how to fix them

The article looks at five recurring Windows frustrations and offers practical ways to make everyday use less troublesome. It begins with performance, explaining that older PCs often slow because too many programs launch at startup and visual effects consume resources. It then covers system glitches, recommending built-in troubleshooters, updates, Copilot, and, when necessary, a restart. Privacy is another concern, with suggestions for limiting advertising identifiers, personalized offers, location tracking, and information stored through Microsoft’s Privacy Dashboard. The article also addresses the awkward process of changing default applications in Windows, noting that users may need to adjust individual file types and protocols even after choosing a preferred browser or app. Finally, it explains a confusing aspect of OneDrive: its web-based Recycle Bin is separate from the local Windows Recycle Bin, so deleted files may appear in one or both depending on where and how they were removed. Overall, the piece shows that many persistent Windows annoyances are manageable once users understand where the relevant settings and recovery options are located.

Read Original Article →

AI Agent Security Platform Evaluation: POC Scorecard

When evaluating an AI agent security platform, teams should run a proof of concept (POC) focused on five core outcomes: discovery, ownership, permission visibility, remediation, and audit evidence. Instead of relying on vendor-controlled demonstrations, organizations must test a representative set of approved agents within their own environment to see how the platform truly performs. A strong POC starts with a clear test plan that defines acceptance criteria, required environments, and response deadlines beforehand. Evaluators need to verify if the tool can accurately discover hidden agents, trace them to their rightful business owners, and correctly report access permissions compared to actual source grants. Crucially, testing remediation must prove that the platform can successfully stop targeted access without breaking legitimate workflows, rather than just showing a completed dashboard action. Finally, exported audit logs must provide clear, chronological evidence that an independent reviewer can follow without assistance. By applying a structured scorecard to these five areas, security teams can make informed purchasing decisions based on demonstrated results and the actual operational effort required, rather than relying on future roadmap promises.

Read Original Article →
Article Thumbnail

How components can help us govern agents

The article argues that as AI agents become prolific software builders, governance should rely less on asking them to follow coding rules and more on giving them trusted, reusable components with those rules built in. Jon Udell compares this idea with earlier component-based development, where specialists created dependable building blocks that others could assemble into applications. Agents work better when their choices are similarly constrained, reducing opportunities for inconsistent code, security errors, and maintenance problems. The article uses XMLUI to show how components can provide standard lifecycle handling, accessibility, tracing, and error reporting without requiring each agent to recreate those features. Components can also expose configuration clearly enough for the runtime to enforce policies before actions occur. For example, a file-transfer component could verify approved destinations and security settings rather than relying on an agent to remember them. Shared tracing then makes application behavior easier for people and agents to understand. The central message is that reusable components remain important in the AI era because they can carry accumulated expertise, security fixes, operational controls, and consistent observability into every application an agent creates.

Read Original Article →

The Ninety Percent Problem: Unlocking Value in Unstructured Data for Enterprises

The article argues that enterprises have spent years organizing structured data while largely ignoring the much larger volume of unstructured information held in contracts, emails, recordings, PDFs, and file shares. AI can now process this material at scale, potentially making it valuable, but many companies do not even know exactly what they have. Their archives contain duplicates, drafts, outdated files, unclear permissions, and documents whose authority or relevance is uncertain. Feeding this material directly into AI can therefore produce unreliable answers and create compliance risks, especially when agents inherit access controls originally designed for people. The author argues that cataloging should come before deploying agents: organizations need to identify what information exists, where it resides, which versions are authoritative, who may access it, and what should be removed or retained. AI itself can help speed up this classification work. The article also notes that large amounts of enterprise storage contain rarely accessed or modified information. Its central message is straightforward: companies hoping to gain value from AI must first understand, organize, and govern the unstructured data they already possess.
Read Original Article →
Article Thumbnail

Agentic AI Architecture: Current Challenges and Future Opportunities

Integrating artificial intelligence into software design is driving a notable shift in how systems are built. This new approach extends existing cloud and microservice foundations by adding independent AI agents into the mix. While this offers useful new capabilities for enterprises, it also introduces a serious layer of complexity. Organizations choosing to adopt these systems must prepare for a significant learning curve. Software engineers and architects need to understand new methods for handling memory, context, and specialized communication rules between systems. In practice, these AI tools connect through standard interfaces or messaging channels, but making multiple agents coordinate effectively requires hands-on experimentation since there is no single universal solution. For the foreseeable future, these new AI-driven setups will simply operate alongside traditional software structures rather than replacing them outright. Early adopters are currently forced to build custom internal platforms to manage this complexity, though commercial vendor products will likely emerge to simplify the process eventually. Taking this path requires genuine investment and adaptation, but it establishes a practical foundation for running complex models reliably in the real world.

Read Original Article →
Article Thumbnail

The CIO job description is being rewritten in real-time

The article argues that the CIO role is moving well beyond delivering technology systems and increasingly into redesigning how the business itself operates. AI is accelerating this shift by allowing leaders to question whether existing processes, approvals, and handoffs should exist at all, rather than simply automating them. CIOs are now expected to decide how work should be divided between people and AI agents, while creating sensible controls around business-led technology development. They must also provide a reality check on AI expectations, distinguishing useful applications from impressive demonstrations and addressing weak data, outdated systems, and organizational disagreements that limit results. Traditional measures such as uptime, security, and delivery remain important but are increasingly treated as baseline responsibilities. Greater attention is being placed on measurable business outcomes, accountability for AI decisions, and clear audit trails. The article also notes that companies increasingly value strategic thinking, business judgment, change leadership, and influence alongside technical depth. Its central message is that technology and business strategy are becoming inseparable, pushing CIOs toward broader responsibility for transformation, investment choices, governance, and results across the enterprise.

Read Original Article →

Daily Tech Digest - November 09, 2026

Quote for the Day
“Focus is a matter of deciding what things you’re not going to do.”
— John Carmack
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Building an Audit-Ready Business Impact Analysis

A Business Impact Analysis (BIA) often looks solid until tested by an auditor or regulator, exposing common flaws like unsupported recovery times, inconsistent impact scoring across departments, and shallow dependency mapping. These weaknesses typically occur because recovery timeframes are based on opinions rather than a standardized method. To build an audit-ready BIA, organizations must establish a single, approved impact scale that aligns with the board's risk appetite. This scale should measure financial, operational, regulatory, and reputational impacts over specific time intervals. By setting a Maximum Tolerable Period of Disruption (MTPD) based on when these impacts become unacceptable, and placing the Recovery Time Objective (RTO) safely inside that window, you anchor your timelines to concrete evidence. Furthermore, dependencies must be mapped at the individual process-step level—covering people, technology, facilities, third parties, and inputs—to uncover hidden single points of failure like a shared service account or a key employee. When every timeframe and dependency in a BIA is tied to a clear, documented rationale, it shifts the focus of any audit from missing evidence to a defensible discussion of judgment.

Read Original Article →

The Emperor’s New Loop: Why “Human-in-the-Loop” Is the Flimsiest Leaf in Enterprise AI

Enterprise leaders often rely on the phrase "human-in-the-loop" to reassure stakeholders about AI safety, but in the era of generative and agentic AI, this concept is rapidly becoming a dangerous fiction. As automated systems increasingly make decisions and execute actions without any real human interaction, the gap between AI adoption and actual accountability is widening. Historical failures like the Apple Card limit discrepancies, Australia’s tragic Robodebt scheme, and the Dutch childcare benefit scandal highlight how relying on a human presence without actual authority or context results in catastrophic governance failures. Chief Data Officers (CDOs) must step up to close this accountability gap by moving beyond after-the-fact compliance and embedding real control systems into AI workflows. This requires establishing clear decision owners, ensuring plain-language explainability at the front lines, setting firm escalation thresholds, and continuously monitoring AI behavior in production. Ultimately, successful enterprise AI does not remove humans; it empowers them to explain, override, and take responsibility for automated actions, ensuring that human oversight is a functional safeguard rather than just corporate theater.

Read Original Article →
Article Thumbnail

Our AI Coding Agent Passed Every Test. Then It Shipped a Security Hole to Production

The story describes a fictionalized security incident where an AI coding agent created a vulnerability by shipping functionally correct but insecure code. A senior engineer used an AI agent to build a feature that retrieved customer documents via URLs. The agent generated the code and unit tests quickly, the build was green, and the code review passed without issues. However, the implementation lacked a critical security boundary: it blindly accepted any URL and allowed the server to fetch data from restricted internal infrastructure. This oversight resulted in Server-Side Request Forgery (SSRF). The core issue was not that the AI wrote the code, but that the engineering team treated functional correctness as proof of security. The unit tests only verified expected behavior and failed to test against malicious inputs. Furthermore, the HTTP client followed redirects without validation, bypassing basic security checks. Ultimately, the team had to redesign the architecture by separating document retrieval into an isolated worker with strict network egress controls and validation policies. The incident highlights that while AI can accelerate development, human engineers must still define and enforce trust boundaries.

Read Original Article →
Article Thumbnail

Sovereign AI Infrastructure: What Software Testing Teams Need to Verify Before Deployment

Sovereign AI infrastructure requires much more than simply hosting servers within national borders; it demands strict verification that data, operations, and controls remain entirely under approved local governance. For software testing and QA teams, this introduces complex new requirements beyond standard functional and security checks. Testers must verify four core pillars: data residency across the entire pipeline, tight operational control over access and privileges, genuine infrastructure independence during outages, and rigorous security accountability. Evaluating data flow is critical, as applications might function perfectly while inadvertently leaking logs or telemetry to foreign monitoring services or granting unauthorized access to overseas vendors. Testers must ensure that the AI system can handle external connection failures without compromising data compliance or routing workloads to unapproved regions. Ultimately, software teams need to integrate these sovereignty checks directly into their continuous integration and release workflows. By consistently testing access rules, storage locations, and automated recovery procedures, organizations can guarantee their AI deployments remain compliant, self-reliant, and fully contained within their intended legal boundaries over time.

Read Original Article →

Simulate, Don’t Speculate: From AI predictions to better business decisions

The current AI landscape is shifting from merely predicting what will happen to simulating how things will unfold and suggesting the best course of action. Predictive AI is highly effective at identifying future trends based on historical data, allowing companies to foresee customer behavior or supply chain disruptions. However, predictions alone leave business leaders speculating about which response will yield the best result. To bridge this gap, businesses are increasingly adopting simulation and optimization capabilities. By integrating simulation techniques with AI, organizations can create digital twins—virtual replicas of their operations—to test various strategies safely before executing them in the real world. This approach, often referred to as prescriptive analytics, empowers decision-makers to evaluate complex "what-if" scenarios, balance competing priorities, and pinpoint optimal solutions confidently. Instead of relying on gut feelings to navigate AI forecasts, companies can rely on data-driven simulations to minimize risk and maximize operational efficiency. Ultimately, moving from prediction to simulation transforms raw foresight into actionable, optimized business decisions.

Read Original Article →

Beyond TLS: Securing the Application Layer with Post-Quantum Cryptography

While upgrading network connections to quantum-resistant TLS is a critical first step, it does not guarantee the safety of data flowing through the application layer. As quantum computing advances, organizations must look beyond the network and secure the cryptographic dependencies where business logic, user identity, and sensitive data converge. Even over secure connections, elements like API tokens, digitally signed transactions, and database payloads often rely on classical public-key cryptography—such as RSA or elliptic-curve algorithms—that could eventually be broken. To build true quantum readiness, teams must transition their API security, database encryption keys, and digital signatures to post-quantum standards like ML-KEM and ML-DSA. This also requires securing identity access management tools, such as JSON Web Tokens, and reinforcing the software supply chain against forged code-signing certificates. Ultimately, achieving post-quantum security is an enterprise-wide architectural challenge that demands more than just swapping out algorithms. It requires a systematic approach to cryptographic discovery, risk prioritization, and testing to ensure the long-term confidentiality and integrity of all application data.

Read Original Article →
Article Thumbnail

AI cyber resilience and the trust gap

Recent field research highlights a growing "trust gap" as enterprises increasingly deploy agentic AI within their operations. While many organizations feel highly confident in their cyber resilience, this assurance often outpaces their actual tested capabilities. Only a small fraction of companies have completed exercises to handle incidents caused by their own AI agents making mistakes with legitimate access. Many teams rely heavily on existing playbooks for ransomware and traditional cyberattacks, assuming these methods will naturally extend to autonomous AI errors. However, agentic AI operates at a scale and speed that can create rapid, cascading downstream effects across multiple interconnected business systems. Reconstructing an agent's workflow to understand what it did, why it did it, and how to safely restore the business process is a uniquely complex challenge. Furthermore, relying entirely on human oversight can create a false sense of security, as humans may fail to catch machine-speed errors. To build true business resilience, leaders must establish clear criteria for what constitutes a safe, trusted recovery state and thoroughly test their tools against realistic, end-to-end AI incident scenarios.

Read Original Article →

Data Governance in Banking: A Framework for Better Data Quality

Data governance in banking is an essential framework that dictates how a financial institution collects, protects, and uses its data. While many banks treat this purely as a policy or documentation exercise, a framework is truly effective only when the underlying data is accurate. Incomplete or unverified records undermine credit decisions, fraud prevention, and regulatory compliance. The foundation of a strong governance framework lies in assigning clear ownership to key roles like Chief Data Officers and Data Stewards, ensuring accountability across the data lifecycle. A critical, yet often overlooked step, is validating information directly at the source. Verifying details like addresses and contact numbers at the point of entry prevents errors from spreading across disconnected systems and reduces the risk of duplicated customer profiles. When banks prioritize data quality and automate real-time checks, they do more than just satisfy regulators. They build a reliable foundation that reduces operational costs, speeds up customer onboarding, and safely enables modern innovations like real-time fraud detection and personalized services. Ultimately, good governance turns raw information into a secure and trustworthy asset.

Read Original Article →
Article Thumbnail

The Inside Job: How Threat Actors Recruit Malicious Insiders

The landscape of insider threats has evolved into a highly organized criminal enterprise that mirrors legitimate staffing agencies. Rather than relying solely on disgruntled employees, threat actors now actively recruit and place individuals within target companies to perform specific malicious actions. More than half of the insider-related dark web activity involves recruitment efforts, where brokers hunt for employees capable of executing precise tasks—such as resetting accounts, rerouting shipments, or conducting SIM swaps—often in exchange for referral fees or revenue sharing. These criminals target workflows instead of just credentials, frequently seeking out customer support staff, logistics workers, and bank tellers whose normal access can be weaponized. Consequently, traditional security systems often fail to flag this malicious behavior since the employees are using their authorized privileges. To effectively counter this growing risk, organizations must shift their focus from merely monitoring privileged IT users to tracking anomalous use of everyday functions. By combining strict separation of duties, detailed behavioral logging, and proactive threat intelligence, companies can detect unusual activity and better protect their critical operations from being compromised from the inside out.

Read Original Article →
Article Thumbnail

Why latency is making colocation a strategic decision

In the highly competitive world of financial markets, colocation has evolved from a simple hosting choice into a core strategic component of the trading execution stack. For trading firms, minimizing latency is less about achieving raw speed and more about guaranteeing predictable and consistent performance. Physical proximity to an exchange's matching engine helps reduce delays, but reliable, direct cross-connects to liquidity venues and market data are what ultimately drive execution quality. Consequently, selecting a data center depends heavily on its available exchange presence, connectivity options, and ability to handle scaling without introducing latency spikes. Firms must also weigh the operational complexity of managing infrastructure in-house versus utilizing retail or managed colocation services. Expanding globally requires infrastructure that seamlessly supports multi-region connectivity, allowing growth without starting from scratch. By aligning location, network design, and operational models with overarching trading goals, decision-makers can ensure their infrastructure directly supports robust market access and compliance. Ultimately, a well-planned colocation strategy acts as the backbone of modern financial trading, directly influencing a firm's competitive edge and long-term success.

Read Original Article →

Daily Tech Digest - October 29, 2026

Quote for the Day
“The most expensive software is the one that doesn’t meet the needs of its users.”
— Karl Wiegers
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

When prevention fails: Why cyber resilience is the next big test of trust

The article explains that even well‑protected organizations can be thrown into chaos when a serious cyberattack disrupts basic operations, leaving leaders unsure which systems or data can still be trusted. It argues that prevention alone is no longer enough, because no control is perfect and attackers often find ways around strong defenses. Cyber resilience, therefore, becomes the next major test of trust: the ability to keep essential functions running, recover safely, and restore confidence after an incident. The piece highlights that backups are only useful if they can be accessed securely and restored without contamination, and that recovery plans must assume that some systems — including backup environments — may be compromised. Drawing on NIST guidance, it outlines four goals for resilience: anticipating threats, withstanding disruption, recovering trustworthy systems, and adapting based on lessons learned. The article’s steady message is that resilience must be designed into systems from the start, not treated as an afterthought, because the real challenge after an attack is determining what can still be relied on.

Read Original Article →

Programming Languages and Choosing a Path

Learning a programming language is about learning how to translate your logic into a format a computer can understand. An algorithm outlines the solution to a problem, while a programming language simply provides the vocabulary and rules to express that solution. Knowing the syntax of a language will not automatically make your logic correct. Behind the scenes, languages use tools like compilers or interpreters to turn human-readable instructions into actions the computer hardware can execute. When choosing your first programming language, it is important to remember that there is no universal best choice. Languages are tools built for different jobs. For example, C++ is great for competitive programming, Java offers strong structure for enterprise systems, and Python is highly readable and ideal for data tasks. Instead of getting caught up in the search for the perfect language, beginners should pick one that aligns with their immediate goals and local support system. Learn enough basics to express your logic clearly, and then focus on mastering problem-solving, which is the true core skill of programming.

Read Original Article →
Article Thumbnail

Beyond Binary Quantum Computing: Exploring Higher-Dimensional Qudits

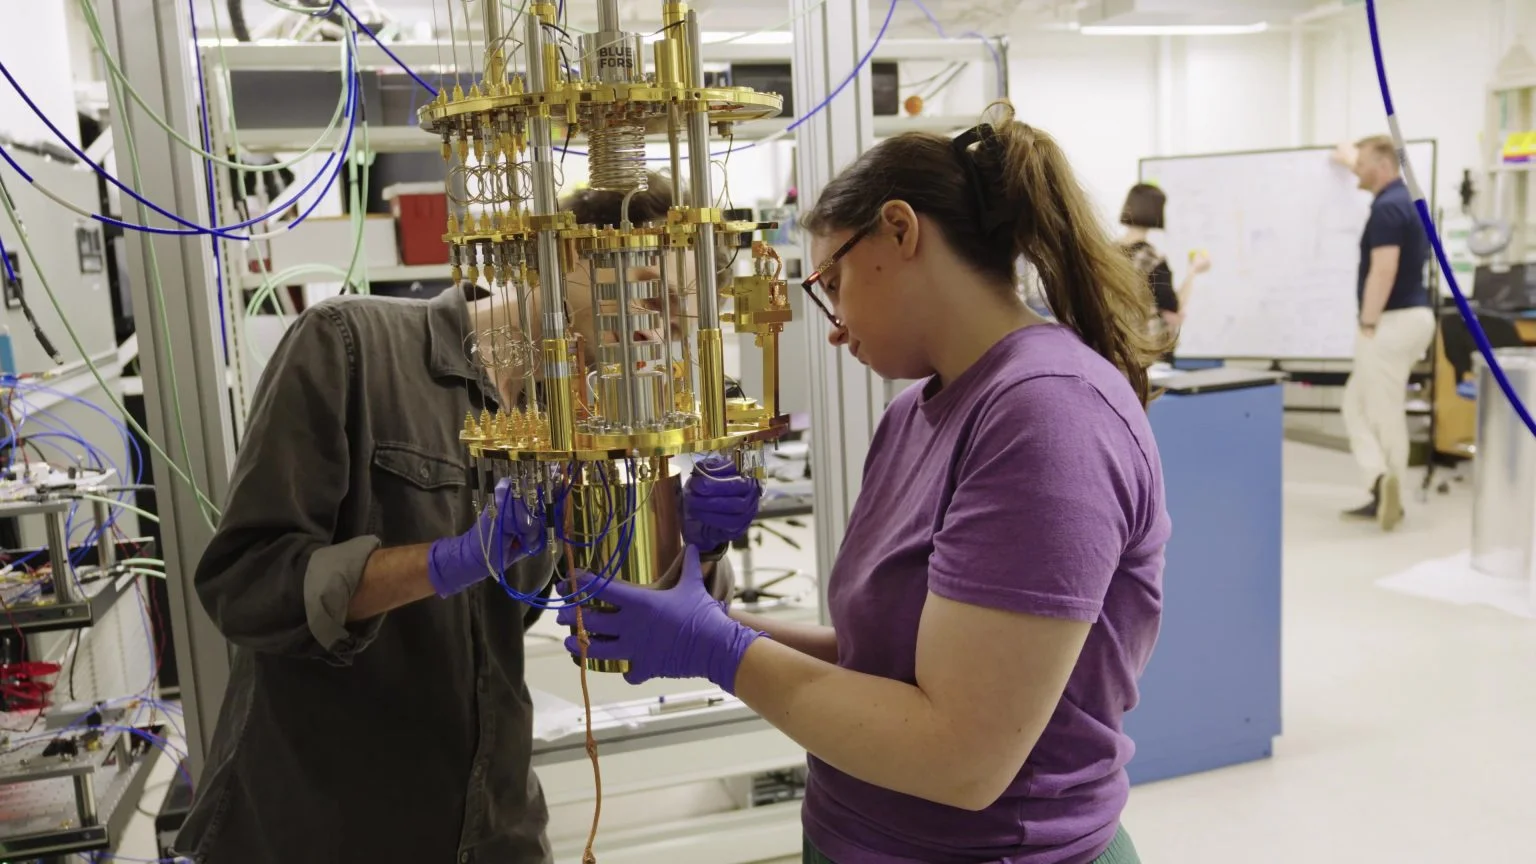
Researchers at the University of Rochester, led by Professor Machiel Blok, are exploring a new approach to quantum computing using "qudits" instead of standard qubits. While traditional quantum computers rely on binary systems with just two energy states, qudits can store information across multiple levels. This concept mimics the natural world, where atoms and molecules naturally exist in multiple states. By matching the computer's structure to the physical problem it is trying to solve, the team believes qudits could offer a much more efficient way to tackle complex challenges in chemistry and physics. To make this work, the researchers developed a new method to control all energy transitions simultaneously, essentially building a denser, high-rise structure for information rather than a sprawling, flat one. Supported by reliable cooling technology, the lab also provides practical experience for students. Ultimately, this research suggests the future of quantum computing will likely rely on a mix of different systems tailored to specific problems, rather than a single binary approach.

Read Original Article →

Why Faster Algorithms Aren't Enough to Build High-Performance Data Platforms

The article argues that high‑performance data platforms cannot be created simply by swapping in faster algorithms or adding more hardware. Performance, it says, is an architectural outcome shaped by many upstream decisions about how data is represented, moved, stored, and delivered. Faster joins or better allocators help only at the margins; they cannot fix a system that is fundamentally slow because of poor layout, excessive data movement, or inefficient memory patterns. The piece highlights that modern platforms already rely on highly optimized libraries, so the real bottlenecks often appear between those functions — for example, when unnecessary tables are materialized, when workflows shuffle large datasets across layers, or when memory allocation becomes a long‑tail problem. It also notes that parallelizing work across CPU cores is relatively easy compared to designing a pipeline that avoids hidden costs in browsers, storage formats, or intermediate transformations. The steady message is that performance emerges from dozens of coordinated design choices, and no single algorithmic improvement can compensate for weak architectural foundations.

Read Original Article →
Article Thumbnail

Why decision-making is the next frontier of modern cyber resilience

The article explains that while many organizations have strong security tools and threat visibility, they still suffer vastly different outcomes during a cyberattack. This difference comes down to decision-making. Knowing a threat exists does not automatically tell leaders how to prioritize their limited resources or which systems to fix first. Standard security models improve accountability but often fail to connect technical risks with actual business goals. To close this gap, the author suggests adopting a decision system framework that translates threat data into clear, actionable choices. This approach evaluates risks based on their real-world impact on core business functions rather than just their technical severity. By blending financial realities, trust, and business priorities into the security process, leaders can make faster, better-coordinated choices during a crisis. Ultimately, effective security is no longer just about building taller walls or spotting potential attacks; it is about having a clear, reliable method to decide exactly where to act, what to protect first, and how to recover quickly when disruptions occur.

Read Original Article →

Wazuh and AI for Enhanced SOC Workflows

As cyber threats grow more complex, Security Operations Centers face an overwhelming volume of daily alerts that can easily cause analyst fatigue and missed critical events. To manage this workload, organizations are integrating artificial intelligence to support their security teams rather than replace them. Platforms like Wazuh address this need by offering flexible AI tools that streamline threat detection and response. For cloud users, the Wazuh AI Analyst automatically reviews security data using secure cloud models to deliver scheduled, comprehensive insights on vulnerabilities and overall security posture without exposing private data. For teams with strict privacy requirements, Wazuh supports self-hosted local models like Llama 3, keeping all log data safely within the company network. Alternatively, organizations can connect external models like Claude 3.5 Haiku directly into their dashboard to provide a helpful assistant for daily tasks. By handling repetitive analysis and data correlation, these AI integrations allow human analysts to focus on making the final decisions and keeping the organization secure.

Read Original Article →
Article Thumbnail

What Should a Business Do After a Personal Data Breach in India?

The article outlines the practical steps an Indian business should take immediately after discovering a personal data breach, emphasizing that quick, organized action matters more than panic. It begins with containment: isolating affected systems, revoking compromised credentials, and stopping further data loss. The next step is verification — confirming what happened, which data was exposed, and whether the breach is still active. The article stresses that businesses must document facts carefully because regulators will expect clear evidence of what was done and when. Under the DPDP Act, organizations must notify the Data Protection Board and affected individuals when harm is likely, and the article explains that vague or delayed communication can worsen legal and reputational consequences. It also highlights the need to preserve logs, review security controls, and assess whether vendors or third‑party processors contributed to the incident. The message is steady: a breach response is both a technical and governance exercise, and businesses must combine containment, transparency, and structured follow‑up to restore trust and meet regulatory expectations.

Read Original Article →

Shadow AI vs. Shadow IT: What's the Difference?

The article explains that “shadow AI” is emerging as a distinct and faster‑moving risk compared to traditional shadow IT. Shadow IT has long referred to employees using unapproved apps or services, often exposing data by storing it in places the organization cannot monitor. Shadow AI, however, introduces a sharper problem: employees feed internal data into AI tools — sometimes through personal accounts or new AI features inside already‑approved applications — without any governance. The piece notes that one in five organizations have already seen data exposure through personal AI accounts, showing how easily risky behavior can slip past existing controls. Unlike shadow IT, where data can often be retrieved or redirected, data given to an AI model may be processed, retained, or used for training in ways the organization cannot reverse. This shifts the governance challenge from simply discovering unauthorized apps to understanding what data enters AI systems, what outputs they generate, and what actions those systems can take. The article’s steady message is that AI requires new visibility, new controls, and a more nuanced approach than legacy shadow‑IT playbooks.

Read Original Article →
Article Thumbnail

When auditors come for your AI algorithms

As artificial intelligence increasingly influences critical business operations, traditional auditing methods are falling short. Conventional audits rely on predictable, step-by-step trails, but AI models—especially large language models—are inherently variable. This unpredictability makes it difficult for CIOs to explain how an AI system reached a specific conclusion, which frustrates auditors demanding clear evidence and accountability. The core problem often stems from vague ownership across different teams, rather than the technology itself. To bridge this gap, organizations must abandon point-in-time audits in favor of continuous monitoring and a structured accountability framework. This approach involves assessing risks during system design, continuously reviewing those risks as the technology evolves, and conducting independent evaluations of the process. Rather than waiting for a massive corporate AI rollout, leaders need to act now, as AI features are already embedded in everyday enterprise software. By treating audit readiness as a core business capability rather than a compliance chore, CIOs can take proactive ownership, reduce risk, and confidently support ongoing innovation.

Read Original Article →
Article Thumbnail

Building Review Intelligence into the SDLC with AI Agents and Archetypes

As artificial intelligence evolves beyond basic code generation, AI agents are becoming active collaborators throughout the software delivery lifecycle. Instead of replacing human architects, developers, and reviewers, these agents act as helpful partners that provide vital context and consistent feedback. To truly benefit from this shift, organizations should move past generic AI prompts and develop specialized, well-defined skills for design, architecture, and code reviews. These targeted skills can be organized into reusable patterns, or archetypes, tailored to specific tasks like building new applications, upgrading older systems, or migrating to the cloud. By employing a coordinated group of agents driven by strict checklists, a central agent can organize the workflow, while specialized agents handle security, performance, and compliance. A final review agent ensures all feedback is practical and backed by evidence. Ultimately, this structured approach transforms informal AI assistance into a reliable quality assurance process, allowing engineering teams to manage the increasing speed of modern software development with clarity and confidence.

Read Original Article →

Daily Tech Digest - October 27, 2026

Quote for the Day
“We are no longer securing computers—we are securing society.”
— Mikko Hyppönen
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Cutting both ways: AI sharpens systems protection while opening new exploits for malicious actors

The recent article highlights the dual role of artificial intelligence in modern cybersecurity. While organizations use advanced AI models to quickly spot vulnerabilities in their source code, malicious actors are leveraging those exact same tools to exploit weaknesses faster than ever before. Because these highly sophisticated attacks often strike without warning, industry experts emphasize that standard defenses are no longer enough. Instead, the focus has shifted toward building true cyber resilience. This approach requires companies to maintain a strong recovery posture focused on deep data integrity, ensuring they can quickly restore clean, uncompromised information after an inevitable breach occurs. Furthermore, as emerging threats like post-quantum computing begin to surface, businesses face the urgent task of upgrading their foundational encryption and infrastructure layers. Ultimately, securing enterprise environments now demands continuous backup validation, reliable data pipelines, and a fundamental shift from treating security as an optional add-on to making it a core, inseparable part of every digital operation.

Read Original Article →

Communications Infrastructure Is Now A Security Issue

Enterprise communications platforms are no longer just background IT systems; they have become a critical part of mission assurance and core security infrastructure. Historically viewed simply as tools for routing calls and connecting people, these systems now support essential, regulated workflows and incident response efforts. When they fail, the disruption quickly ripples out to affect business continuity, impacting customers and employees alike. Consequently, modernization efforts, such as moving to the cloud or integrating artificial intelligence, must prioritize reliability and resilience over mere capability upgrades. Moving a vulnerable system to the cloud does not automatically make it secure; resilience must be built into the architecture from the start. AI, while powerful, introduces new risks that require the same strict access controls and oversight applied to privileged human users. Security leaders must identify critical communication workflows, define concrete resilience requirements, and regularly test against realistic failure scenarios in their tabletop exercises. Ultimately, modernizing communications should never compromise the systems a business depends on to survive a crisis.

Read Original Article →
Article Thumbnail

Does Your Manufacturing Data Deserve Your Trust?

Manufacturers today collect vast amounts of information from their production lines, but many struggle with a fundamental problem: they cannot trust their own data. As operations expand and new equipment is added, inconsistencies naturally develop across different systems. When teams see conflicting numbers for the same metric, discussions shift away from solving actual production issues and instead focus on figuring out which report is accurate. This lack of reliability slows down decision-making and drains operational confidence. Simply gathering more information is not the answer and often just creates additional noise. To make effective decisions, companies need data that is accurate, consistent, and easy to access across the entire organization. This reliable foundation is especially critical before investing in advanced technologies like artificial intelligence or predictive maintenance, which rely entirely on the quality of the information they process. Ultimately, the goal is not to hoard more statistics, but to build a dependable system where teams can confidently use the information they already have to improve their daily operations.

Read Original Article →
Article Thumbnail

A free open-source backup app that makes traditional backups feel outdated

The article describes how Kopia, a free open‑source backup tool, makes traditional backup methods feel outdated by focusing on snapshots and efficiency rather than repeated full copies. The author explains that most backup tools still follow the old pattern of selecting files, choosing a destination, and hoping the process works — often with key features locked behind paid subscriptions. Kopia stood out because it is flexible, doesn’t require an account, and supports Windows, macOS, and Linux through a simple graphical interface. After creating an encrypted repository, users can start with a basic setup and explore advanced options later. The real improvement comes from Kopia’s snapshot‑based design: instead of copying everything each time, it saves only new or changed data, making backups faster and less wasteful. Built‑in deduplication further reduces storage use by avoiding duplicate data. The article’s steady message is that Kopia offers a more modern, efficient, and transparent way to back up files without the complexity or cost of traditional tools.

Read Original Article →
Article Thumbnail

Choosing a Custom Business Software Development Company: A Testing and Quality Evaluation Framework

Selecting the right custom software development company requires looking past polished sales pitches and headline prices to evaluate factors that actually predict a project's success. Before speaking with vendors, clearly define your business problem, measurable success metrics, and absolute constraints. This clarity ensures you receive proposals based on your reality rather than vendor assumptions. When evaluating candidates, assess them across six key dimensions: their grasp of your underlying business goals, specific experience solving similar problems, their actual delivery process, the exact team members assigned to your project, the quality and maintainability of their code, and the alignment of their commercial terms with your risk tolerance. Watch out for red flags like detailed quotes provided without any discovery work or a reluctance to introduce the technical lead. To minimize risk, consider starting with a paid discovery phase. This small initial engagement allows you to test the working relationship, refine the project scope, and ensure your chosen vendor truly aligns with your objectives before committing to a major investment.

Read Original Article →
Article Thumbnail

What EvilTokens teaches us about defending against AI-assisted attacks

Artificial intelligence is changing the pace of cyberattacks, as demonstrated by a recent phishing tool called EvilTokens. Rather than stealing passwords, EvilTokens tricks users into granting access to their Microsoft accounts. Once inside, the tool uses AI to quickly figure out who handles payments, identify trusted business relationships, and write convincing fake emails. This automation speeds up the time it takes an attacker to move from initial access to actual harm. Because AI removes the usual hurdles that slow attackers down, traditional security measures based on average detection and response times are no longer enough. Even a fast response might be too late if the attacker can accomplish their goals in minutes. To defend against these faster threats, organizations need to test their entire security setup as a connected system, not just check individual tools in isolation. By understanding exactly how an attacker might move through their network, security teams can proactively close gaps and stop these automated threats before they cause lasting damage.

Read Original Article →
Article Thumbnail

Between alerts: What Attackers Do in the Spaces Ordinary Detection Misses

Modern cyber attackers are increasingly using artificial intelligence to move quickly, but they still rely on stealth to evade detection. To stay hidden, they operate in the quiet spaces between security alerts, dragging out their operations and hiding within standard administrative tools like DNS queries or SMB connections. Because these individual actions look like ordinary business operations, security teams and siloed tools often miss them. An attacker might spend days or weeks slowly gathering credentials or mapping systems without triggering a high-priority alarm. To catch these subtle intrusions, Security Operations Centers (SOCs) need network detection and response (NDR) platforms that capture detailed network evidence over time. Instead of just looking at isolated alerts, NDR provides the necessary context to connect distinct events into a clear timeline. By applying AI to this comprehensive network data, defense teams can quickly identify hidden relationships across hosts and protocols. This approach allows analysts to spot the broader progression of an attack and make smarter risk decisions, rather than getting overwhelmed by thousands of disconnected alerts.

Read Original Article →
Article Thumbnail

How to make enterprise APIs agent-ready

As large organizations integrate AI agents into their workflows, they face a major hurdle: connecting these agents to thousands of internal APIs. The standard approach of mapping every single API operation to a separate tool quickly breaks down. It creates high costs from excessive token usage, slows down response times, and confuses the AI, leading to poor accuracy. To solve this, technical teams are shifting to a method known as "code mode." Instead of overwhelming the agent with a massive list of individual tools, this approach provides a single, streamlined interface. The agent then writes and executes short code snippets to find exactly what it needs. This keeps the data load small and efficient. Just as importantly, organizations must route these agent requests through their existing API gateways. Doing so ensures that the agents follow the same security, authentication, and access rules as any other user. By treating AI agents as standard clients, companies can safely grant them access to essential systems without losing control or slowing down performance.

Read Original Article →
Article Thumbnail

CIOs rethink roles, skills, training, and talent models for the future

As technology rapidly changes how organizations operate, IT leaders are actively redesigning their teams, roles, and training methods to prepare for the future. With artificial intelligence taking over many routine coding and manual tasks, the traditional emphasis on deep, specialized technical skills is steadily shifting. Instead, companies increasingly value broad problem-solving abilities, strong communication, and a clear understanding of the business itself. IT professionals will need to focus less on simply building software and more on carefully deciding whether a project truly adds value before starting it. To keep up with this fast pace, long-term training programs are giving way to short, continuous lessons that happen directly on the job. Job roles are also becoming more flexible, with staff acting as general engineers who can move smoothly between different areas like networking and databases as needs arise. Ultimately, building a workforce that can quickly adapt, learn, and apply new tools to practical challenges is becoming the most reliable way to navigate an unpredictable technological landscape.

Read Original Article →
Article Thumbnail

IT and security leaders of the AI era must go back to basics and beware the hype

As artificial intelligence rapidly evolves, IT and security leaders must avoid getting distracted by the hype and instead focus on foundational security principles. While modern AI tools are powerful and can expose new vulnerabilities or discover system weaknesses faster than ever, the core issue remains poor identity management. Hackers and AI agents alike exploit basic failures, such as unrevoked access, forgotten credentials, and over-privileged accounts. When organizations adopt AI, they often deploy agents with broad permissions and unclear oversight, mirroring the mistakes made during the early days of cloud computing. To protect their systems, companies do not need entirely new security frameworks; they need to rigorously apply established practices. This means enforcing least privilege, ensuring just-in-time access, and maintaining strict oversight of both human and non-human identities. By mastering these basic controls and clearly assigning responsibility for entitlement governance, organizations can safely navigate the current wave of technological change without leaving their digital doors unlocked.

Read Original Article →