Showing posts with label product management. Show all posts

Daily Tech Digest - November 19, 2026

Quote for the Day
“A bad system will beat a good person every time.”
— W. Edwards Deming
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Building a Modern Data Architecture for Analytics and AI

Clinging to legacy data systems often leads to higher cloud costs, frequent downtime, and missed business opportunities. To remain competitive in the evolving market, upgrading to a modern data architecture is a practical necessity rather than just an IT project. A highly capable modern framework combines scattered information from diverse sources, improving data storage, efficiency, and overall system performance. This upgrade directly influences the customer experience by ensuring reliable and responsive services, which builds loyalty and prevents the loss of sales associated with system chaos. When transitioning, organizations have several architectural models to choose from based on their specific needs. For example, a data mesh decentralizes data ownership across departments, while a data fabric uses technology to weave different data sources together. Alternatively, data hubs serve as centralized exchange centers for processing business intelligence, and data lakehouses offer a hybrid approach that stores raw data affordably while making it easy to index and retrieve. Ultimately, the survival of any organization depends on recognizing the need for change and actively shaping a flexible technological foundation instead of remaining tied to outdated hardware and processes.

Read Original Article →

Do you understand your data estate well enough to make your next technology investment?

Before committing to major technology upgrades like new software platforms or artificial intelligence, organizations must fully understand their existing data landscape. Many leaders know which systems they use, but they often lack a clear picture of how information actually flows between those systems or who relies on it daily. Hidden dependencies, such as unofficial spreadsheets or knowledge kept only in employees' heads, create significant risks when introducing new tools. This gap in understanding is a primary reason many technology projects fail or run over budget. For AI initiatives in particular, a model is only as reliable as the information feeding it. If basic terms are defined differently across various departments, the output will be flawed. Instead of rushing to buy the latest market solutions, companies should first map how their information moves and establish clear, shared definitions. By taking the time to trace these daily workflows and consulting the people who actually handle the information, leaders can identify vulnerabilities early. This foundational clarity ensures that future technology investments are accurately targeted, inherently secure, and genuinely useful to the entire organization in the long run.

Read Original Article →
Article Thumbnail

How organizations can secure their AI-generated code

The provided article discusses how AI code-generation tools have become so reliable that developers and non-technical staff often trust them blindly, leading to significant security risks. While AI produces functional code, it frequently fails to include necessary security precautions because it lacks an understanding of potential threats and attacker behavior. To mitigate these risks, security leaders must treat AI-generated code as untrusted input that needs strict verification before entering the main codebase. This means moving security checks closer to the writing phase, using automated tools to scan for known issues like exposed passwords or outdated components. However, automation is not enough. Human oversight remains crucial, especially for sensitive areas involving authentication, payments, or personal data. Organizations should establish clear, easy-to-understand policies for AI tool usage rather than banning them entirely, as strict bans only drive the activity underground. Encouraging an open culture where employees feel safe reporting mistakes ensures that security teams maintain visibility and control over the network. Ultimately, modern businesses need to balance the productivity gains of AI with practical safeguards, adequate funding for application security, and specialized training for all staff writing code.

Read Original Article →

Human-centered design is the antidote to 'AI blandness'

As artificial intelligence becomes increasingly reliant on recycling existing content, it risks generating bland, generic outputs that lack genuine innovation. AI is highly effective when applying known solutions to well-defined problems, but it struggles with complex challenges that demand true creativity. Innovation still fundamentally requires human context, collaboration, and the ability to draw connections across overlapping ideas. This is where human-centered design acts as the antidote to AI-driven uniformity. By bringing together the people who actually experience a problem, organizations can build solutions grounded in real-world workflows rather than generic AI prompts. Facilitated workshops, process mapping, and iterative prototyping make internal knowledge visible and encourage teams to challenge assumptions. This collaborative process not only ensures the resulting technology actually fits the daily needs of the business, but it also creates shared buy-in and accurate specifications for future development. Ultimately, replacing collaborative thinking with pre-generated AI outputs limits a company's ability to innovate; keeping human experience at the core of problem-solving ensures solutions remain practical, intuitive, and genuinely valuable.

Read Original Article →
Article Thumbnail

The Comfort of Control: Why Governance Needs Resilience, Not Certainty

Recent global technology outages demonstrate a hard truth about corporate governance: perfect compliance does not guarantee operational safety. Organizations often build elaborate frameworks, earn expensive certifications, and maintain pristine risk registers, only to find themselves paralyzed when a trusted vendor pushes a faulty update or experiences a massive service failure. The core issue is the illusion of control. We treat compliance frameworks as absolute shields, but they are simply maps based on past incidents. They cannot predict how a fragile, interconnected digital ecosystem will break. Furthermore, governance frequently falls into a tick-box trap, where companies measure training completion rates rather than genuine systemic resilience. While human error remains involved in most breaches, people are also the only ones capable of spotting anomalies in real time, provided the system empowers them instead of burying them in paperwork. As cyber threats evolve far faster than corporate policies, and as reliance on external vendors deepens, organizations must rethink their entire approach. True governance requires accepting uncertainty, testing defenses under real pressure, and building agile systems that recover quickly, rather than pretending we can manage every risk into submission.

Read Original Article →

Vendor Risk Assessment Questionnaire: Security & Privacy Guide

The article presents vendor risk assessment as one part of a broader third-party security and privacy program, rather than a stand-alone questionnaire exercise. It recommends first classifying vendors according to the sensitivity of data they handle, their system access and the impact of service disruption. Security expectations should then be written into contracts, covering matters such as incident notification, audit rights, subcontractors, data deletion, minimum controls, remediation and termination. The questionnaire itself should reflect the vendor’s risk level and examine areas including governance, access management, operations, secure development, data protection, cloud security, business continuity, monitoring, threat detection, incident response and privacy. Vendors processing personal data require additional scrutiny around subprocessors, international transfers, retention, deletion and breach notification. Crucially, self-reported answers should be supported with evidence such as relevant SOC 2 reports, ISO/IEC 27001 certificates, penetration-test summaries, policies and subprocessor lists. The article emphasizes checking whether this evidence actually covers the service being purchased. Its broader message is that effective vendor oversight depends on risk-based assessment, enforceable contracts, evidence-based verification and continuing reassessment throughout the relationship.

Read Original Article →
Article Thumbnail

Why IT leaders who hit every target still get passed over for promotion

Many IT leaders find themselves passed over for promotions despite receiving stellar performance reviews and hitting every target. The disconnect stems from the fact that performance reviews measure success in a current role, while promotion decisions evaluate a candidate's readiness for the next level. Decision-makers are looking for individuals who already demonstrate the systemic thinking and higher-level decision-making required for a more senior position, not just those who work longer hours or earn more certifications. Furthermore, as leaders advance, their work becomes less visible, meaning their output can no longer speak for itself. To bridge this gap, IT professionals must stop relying solely on their delivery records and start actively managing how they are perceived. This involves conducting informal 360-degree reviews to understand how colleagues view their leadership, and launching internal public relations efforts to highlight their team’s strategic value to the rest of the company. Ultimately, earning a promotion is about ensuring that the people making the decisions can clearly picture the candidate already thriving in the executive role.

Read Original Article →

Modeling Software’s Business Impact

In the age of AI, producing software is faster than ever, but building features efficiently matters little if teams are building the wrong things. When development speed outpaces a customer’s capacity to absorb new features, customer attention becomes the new bottleneck. This requires organizations to focus ruthlessly on delivering true value rather than merely cutting costs or increasing output. Unfortunately, most organizations struggle to measure software value because tracing revenue directly to a specific feature is complicated by marketing, sales pushes, and long sales cycles. To solve this attribution problem, teams must shift from trying to measure value directly to modeling and forecasting it. This involves using proxy metrics, like customer activation and retention, to get faster feedback without the noise of other departments’ efforts. Building an effective model requires cross-functional collaboration with sales, marketing, and product teams to estimate new sales, upsells, retention, and cost savings. While creating these financial models, such as forecasting net present value, can be organizationally challenging and requires educated guesses, it ultimately ensures that development efforts align with real business outcomes.

Read Original Article →
Article Thumbnail

Are companies confusing high performance with leadership potential?

Many organizations mistakenly assume that top-performing employees naturally make the best leaders, prioritizing past individual achievements and technical skills over true leadership potential. According to Suman Kumar Ghosh, CHRO at Bajaj Electricals, individual success relies on personal output, while leadership requires the ability to motivate, mentor, and achieve results through others. This transition is often difficult for employees accustomed to solving problems independently, as they must learn to delegate and align team contributions with broader business goals. Rather than relying solely on performance metrics, companies should assess capabilities like learning agility, emotional intelligence, strategic thinking, and talent development. A strong indicator of leadership readiness is whether an employee’s peers improve and succeed under their guidance. To build effective leadership pipelines, organizations must move beyond classroom training and provide practical experiences like stretch assignments, 360-degree feedback, and real-world project leadership. Managers play a vital role here, acting as talent developers who expose employees to complex challenges before formal promotions occur. Ultimately, organizations must shift from rewarding past delivery to evaluating an employee’s capacity to empower their team.

Read Original Article →

Once a scam ends the victim blaming begins

At IRISSCON 2026, cyberpsychologist Dr. Nicola Fox Hamilton explained that blaming people for falling victim to scams or phishing attempts only causes more harm and encourages them to hide their mistakes. She emphasized that anyone can become a target, sharing her own experience of clicking a malicious link during a stressful workday to prove that falling for a scam is a momentary vulnerability rather than a sign of low intelligence. Many people hold an optimism bias, mistakenly believing they are immune to such tricks, which leads them to judge others harshly. Scammers exploit this by building deep, trusting relationships over months, isolating their targets so that requests for money seem entirely normal. When the deception is finally revealed, the emotional devastation and self-imposed shame often outweigh the financial loss. This dynamic is equally dangerous in corporate environments. When employees fear blame, they stay silent about clicking bad links, giving attackers more time to access the network. To effectively fix this growing problem, organizations must actively replace judgment with thoughtful support, and senior leaders should openly share their own errors to build a lasting culture of trust and genuine accountability.

Read Original Article →

Daily Tech Digest - June 03, 2026


Quote for the day:

"Leadership is practiced not so much in words as in attitude and actions." -- Harold S. Geneen

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 19 mins • Perfect for listening on the go.


What will AI-first UX look like?

The transition to user experiences guided by artificial intelligence marks a steady move away from rigid, traditional interfaces like static forms and manual dashboards. Rather than requiring users to navigate multiple disconnected software tools to complete tasks, future interfaces will rely on conversational systems that connect seamlessly across various applications. In this evolving landscape, standard data entry forms are being replaced by adaptive interactions where users simply describe what they want to accomplish, and the system gathers the necessary details. Similarly, data reporting is shifting from complex, manually built dashboards to narrative summaries generated on demand, providing clear explanations of business metrics and actionable next steps. This shift transforms standard workflows into coordinated teamwork between humans and software agents. The software handles processes involving multiple steps behind the scenes and only escalates to human workers when careful judgment is required. To make this work effectively, organizations must build strong underlying foundations, including clear data structures, connected programming interfaces, and solid oversight rules. Ultimately, these systems are designed not to replace human workers, but to reduce friction and manage tasks across platforms more naturally. As this technology matures, the focus remains on building reliable environments where software acts as a helpful teammate, smoothly coordinating background tasks while keeping human users firmly in control of the final outcomes.


Minimally Acceptable Systems: Tolerable at the Lowest Cost Possible

The article discusses a growing trend in software engineering and business where companies intentionally design systems to be merely adequate rather than striving for excellence. This concept, described as creating minimally acceptable systems, focuses on finding the exact point where a product is just tolerable for users while being as cheap as possible to build and maintain. Instead of prioritizing high quality, reliability, or a great user experience, organizations aim to minimize their costs and speed up delivery. They provide the bare minimum functionality required to keep people from abandoning the software. While this approach makes clear financial sense in the short term and helps companies stay competitive, it comes with serious long-term consequences. By constantly pushing standards to the lowest acceptable limit, the industry conditions people to expect and accept frustrating, unreliable software in their daily lives. The author warns that treating quality simply as an expense to be cut ultimately damages user trust and builds up massive technical problems for the future. To fix this, the software field needs to rethink its current financial motives. Engineers and business leaders should work together to find a better balance, creating products that are both affordable to produce and genuinely reliable for the people who use them.


Software sprawl is becoming a margin problem for SaaS CFOs

For software companies, the practice of adopting isolated tools to solve individual problems, such as payments, billing, and tax compliance, often leads to a fragmented operations setup known as software sprawl. While the subscription-based business model has historically enjoyed strong profit margins, this growing web of disconnected systems threatens to undermine those financial advantages. Finance leaders are finding that a patched-together technology system severely limits their clear view of business performance, putting unneeded pressure on profit margins through manual work, costly billing errors, and duplicate expenses. Furthermore, relying on fragmented tools restricts a company's ability to smoothly expand into new regions or test different pricing methods. Rather than looking at this as just an IT issue, financial executives must recognize it as a fundamental challenge to scalable growth. The path forward does not necessarily require adopting one massive platform, but rather ensuring that all revenue processes operate smoothly together. By replacing disconnected tools with an integrated infrastructure, companies can drastically reduce manual interventions and internal friction. Ultimately, the next era of the software industry will reward organizations that match their desire for growth with strict operational discipline. By fixing these underlying structural flaws now, finance teams can build a resilient foundation capable of handling future expansion without constantly multiplying internal complexities or operational costs.


The Zero-Knowledge Threat Actor and the End of Responsible Disclosure

Artificial intelligence is drastically lowering the barrier to entry for cybercriminals, enabling a new wave of "zero-knowledge threat actors." These attackers lack deep technical expertise but use advanced AI tools to generate malicious code, find vulnerabilities, and execute complex attack chains with surprising ease. This democratization of offensive capabilities means that hackers can now discover and exploit software flaws at unprecedented speeds, effectively closing the traditional responsible disclosure window that software vendors rely on to create patches. Smaller organizations are particularly at risk, often serving as stepping stones into larger enterprise supply chains due to their limited security resources and slower patching cycles. To defend against these rapidly evolving threats, security teams must abandon fragmented approaches and adopt unified monitoring systems that provide clear, comprehensive visibility across their entire digital environment. Proactive defense requires prioritizing faster patch management, conducting regular incident response drills, and rigorously testing in-house AI systems against deliberate manipulation by external actors. Furthermore, training employees to recognize highly realistic, AI-generated phishing attempts is absolutely essential for maintaining a strong security posture. By relying on established security frameworks and maintaining an organized, practiced defense strategy, organizations can calmly and effectively counter the increased capabilities of low-skill attackers without resorting to panic or operational disruption.


ERP Modernization: Most Expensive, Risky Item on CIO Agenda

Enterprise resource planning systems have grown over the last forty years from basic financial and manufacturing tools into the central framework of most organizations. Today, they handle everything from supply chains to human resources. However, updating these core systems is now one of the most difficult and costly challenges facing technology leaders. Modernizing these structures is not just a software update; it is a major overhaul of how a business operates on a daily basis. Transitioning to modern setups, like cloud-based platforms, involves heavy restructuring of daily work processes and often triggers natural resistance from staff. To succeed, these projects need more than just technical expertise. They require a clear process for managing transitions, direct communication to address employee fears, and strong backing from senior leadership to keep the effort on track during inevitable setbacks. As software vendors increasingly move customers toward cloud and artificial intelligence platforms, technology leaders are forced to weigh the long-term benefits against the immediate financial costs, operational risks, and widespread disruptions. Navigating this shift takes a dedicated, highly skilled team and steady executives who will not abandon the project when minor problems arise. With careful planning, patience, and stable leadership, organizations can successfully migrate their central systems to meet current operational demands without jeopardizing their everyday stability.


The AI ‘Revolution' is Not a People's Revolution

Politicians and technology executives increasingly frame artificial intelligence as an inevitable revolution, a term historically reserved for popular movements driving social progress. In truth, this modern narrative serves primarily to bypass democratic scrutiny and consolidate power among a select few. Rather than arising from the people to challenge the existing order, the current technological push is being imposed from the top down. Leaders like former UK Prime Minister Tony Blair promote a vision where society must passively accept widespread automation, mass data harvesting, and unchecked corporate influence, treating any hesitation as backwardness. By labeling this shift a revolution, proponents cleverly silence debate and frame regulatory efforts as sabotage. Furthermore, while previous digital tools aided grassroots organizing, artificial intelligence is frequently deployed to monitor, police, and discipline the public. This rhetoric essentially functions as a manipulative marketing tool, designed to mask the reality of wealth generation for elites at the expense of ordinary citizens facing job insecurity and climate disruption. Ultimately, society must reject this predetermined technological path and demand accountability. Citizens have the right to question who truly benefits from these systems and to actively decide how new technologies should integrate into their lives, ensuring that any real change remains firmly rooted in public consent and democratic choice.

The AI pricing conundrum — it started as a nightmare, now it’s worse.

Enterprise technology leaders face a growing dilemma in how they pay for artificial intelligence. Buyers want pricing based on the tangible business value the technology delivers, while software providers prefer charging based on resource consumption, such as per-token fees. This creates a deep disconnect. Technology departments often feel consumption pricing is detached from real results, likening it to paying for unproven sales leads. On the other hand, providers cannot realistically accept value-based pricing because they have no control over internal company issues like poor data, broken processes, or office politics. Furthermore, if these systems were compensated strictly based on successful outcomes, it could create dangerous incentives. The software might aggressively pursue specific metrics, potentially sacrificing customer trust, ethical standards, or operational safety just to achieve the defined goal. Since bridging this gap directly is nearly impossible, organizations must take control internally. The article suggests forming dedicated committees to ask difficult questions about the goals, risks, and realistic benefits of any new project. Additionally, senior executives should share the financial accountability, tying their compensation directly to the success or failure of these initiatives. Only by thoroughly understanding a project's true intent, limitations, and risks can technology leaders negotiate sensible, fair pricing agreements with their service providers.


AI Is Shipping Fast, Quality Can't Be Left Behind

The recent transition of artificial intelligence from experimental phases to widespread integration has revealed a significant gap between rapid development and reliable performance. While organizations are swift to embed these systems into their daily operations, a substantial number of these initiatives stall before full implementation due to quality and integration hurdles. Data indicates an increase in user-reported errors, such as misunderstandings and factual inaccuracies, highlighting that traditional validation methods are inadequate for modern, complex systems. Because these programs produce varying outputs rather than predictable, fixed results, engineering teams are finding that automated checks alone are insufficient. To address this, successful organizations are adopting a balanced approach to quality assurance that combines automated evaluations with essential human oversight. Human reviewers are uniquely equipped to gauge context, usability, and intent, catching subtle errors that automated tools often miss. Furthermore, as features expand to process combinations of text, audio, and visual data, the scope of testing becomes even more difficult. The focus is shifting from merely launching features to ensuring they are dependable and trustworthy. Moving forward, the true measure of success will not be the speed of release, but the ability to maintain rigorous, ongoing evaluation processes that prioritize consistent, high-quality experiences for everyday users.


Why Leadership Development Is A System, Not An Event

Organizations frequently send their managers to training workshops, hoping they return ready to guide their teams more effectively. However, these well-intentioned programs often fail because managers step right back into the exact same workloads, pressures, and routines that shaped their old habits in the first place. Meaningful leadership development requires more than simply teaching new skills to individuals; it demands a daily environment actively designed to support those new behaviors. This involves shifting the focus from individual improvement to strengthening the broader company system. Executives must intentionally build a supportive structure with both visible changes, like collaborative meeting practices and transparent decision-making, and invisible shifts, such as fostering an atmosphere where feedback flows freely and people feel secure taking interpersonal risks. Instead of relying on isolated lectures, learning should become an ongoing process smoothly integrated into daily work. By encouraging peer learning groups, aligning company rewards with the behaviors taught in training, and personally modeling these changes, executives create a setting where true growth can take root over time. Ultimately, developing effective leaders is about expanding the capabilities of the entire organization. When the daily workplace aligns with the principles taught in training, individuals practice what they learn, ensuring development becomes a continuous habit rather than a fleeting event.


Responsible AI in fintech: Balancing innovation with trust, risk, and compliance

The article examines the growing role of artificial intelligence within the financial technology sector, focusing closely on the need to balance new capabilities with trust, risk management, and regulatory compliance. As financial institutions increasingly adopt these systems for routine tasks like fraud detection, customer service, and credit scoring, they face significant practical challenges in ensuring their models operate fairly and transparently. A primary concern is that automated systems can unintentionally reproduce human biases, leading to unfair outcomes in lending or account access. To prevent this, companies must establish clear, sensible guidelines for developing and monitoring their algorithms. The text emphasizes that maintaining customer trust requires being straightforward about how decisions are made and how personal data is actually used. Financial organizations also need strong oversight frameworks to handle risks associated with data privacy and system errors effectively. Furthermore, the evolving regulatory environment means that firms must stay current with new laws designed specifically to protect consumers and maintain market stability. Ultimately, the successful integration of these tools in finance depends entirely on a measured approach. By prioritizing ethical practices and strong governance, financial technology companies can improve their services while protecting their customers and meeting their legal obligations responsibly.

Daily Tech Digest - May 17, 2026


Quote for the day:

“In tech, leadership isn’t about predicting the future — it’s about creating the conditions where your teams can build it.” -- Unknown

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Scale ‘autonomous intelligence’ for real growth

In an interview with Ryan Daws, Prakul Sharma, the AI and Insights Practice Leader at Deloitte Consulting LLP, explains that modern enterprises must look beyond the localized productivity gains of generative AI to scale "autonomous intelligence" for real business growth. Sharma describes an intelligence maturity curve transitioning from assisted and artificial intelligence into autonomous intelligence, where systems independently execute actions within predefined boundaries. To unlock true economic value, organizations must integrate these autonomous agents directly into critical, costly workflows like enterprise procurement. However, scaling successfully faces significant technical and structural hurdles. First, enterprises frequently lack decision-grade data, which means real-time, traceable information required for binding transactions, relying instead on outdated reporting-grade data. Second, the production gap and governance debt often stall live deployments, because shortcuts taken during small pilots become major barriers for corporate legal and compliance teams. Sharma advises leaders to conduct thorough decision audits of existing workflows to uncover operational bottlenecks and data gaps. By building pilots from the very outset as reusable platforms equipped with proper identity verification, continuous model evaluations, and robust risk frameworks, enterprises can securely transition from experimental testing to successful, widespread live deployment.


6 Technical Red Flags Product Managers Should Never Ignore

In the article "6 Technical Red Flags Product Managers Should Never Ignore," Seyifunmi Olafioye emphasizes that product managers must recognize signs of underlying technical instability, as it directly impacts delivery, scalability, and customer trust. The author identifies six major red flags that product managers should never overlook: a lack of clear understanding among the team regarding how the system works, new feature development consistently taking much longer than estimated, and resolved bugs repeatedly resurfacing in production. Additionally, product managers should be concerned if operational teams must rely heavily on manual workarounds to keep the platform functioning, if the entire project suffers from an over-reliance on a single engineer's institutional knowledge, or if internal errors are only discovered after users report them due to a lack of proper monitoring. While no system is entirely flawless, ignoring these persistent warning signs can lead to severe operational issues. The article concludes that product managers should not dictate technical fixes; instead, they must proactively initiate honest conversations with engineering leadership, ask challenging questions during planning, and prioritize long-term technical health alongside new features to ensure sustainable growth and protect the user experience.
In this article, Ed Leavens argues that Quantum Day, known as Q-Day, is the precise moment when quantum computers become advanced enough to break existing asymmetric encryption standards like RSA and ECC, presenting a far greater threat than Y2K. While Y2K had a definitive deadline and a known remedy, Q-Day has no set timeline and introduces the insidious risk of "harvest now, decrypt later" (HNDL) tactics. Under HNDL, adversaries secretly exfiltrate and stockpile encrypted data today, waiting to decrypt it once sufficiently powerful quantum technology becomes available. Furthermore, this threat compounds daily due to modern data sprawl across multiple environments. To counter this impending crisis, organizations must look beyond traditional encryption upgrades and adopt data-layer protection strategies like vaulted tokenization. This quantum-resilient approach mathematically separates original sensitive data from its representation by replacing it with non-sensitive, format-preserving tokens. Because tokens share no reversible mathematical connection with the underlying information, quantum algorithms cannot decipher them, effectively neutralizing the value of stolen payloads. Implementing vaulted tokenization requires comprehensive data discovery, strict access governance, and cross-functional organizational alignment. Ultimately, Leavens emphasizes that enterprises must act immediately to secure their data directly, rendering harvested information useless before quantum-powered breaches materialize.


The AI infrastructure bottleneck is becoming a CIO problem

The article by Madeleine Streets explores how the expanding ambitions of artificial intelligence are colliding with physical infrastructure limitations, shifting the AI bottleneck from a general tech industry challenge into a critical problem for Chief Information Officers (CIOs). While billions of dollars continue pouring into AI development, physical realities like power grid limitations, data center construction delays, permitting hurdles, and cooling requirements are struggling to match software demand. This mismatch threatens to create a more constrained operating environment where AI access becomes expensive, delayed, or regionally uneven. Consequently, this pressure exposes "AI sprawl" within organizations where uncoordinated and disconnected AI initiatives compete for the same resources without centralized governance. To mitigate these risks, experts suggest that CIOs treat AI capacity as a core operational resilience and business continuity issue. IT leaders must introduce disciplined governance by tiering AI workloads into critical, important, and experimental categories, or utilizing smaller, local models to reduce compute reliance. Furthermore, CIOs must demand greater transparency from vendors regarding capacity guarantees, regional availability, and workload prioritization during peak demand. Ultimately, enterprise AI strategies can no longer assume infinite compute availability and must instead realign their deployment ambitions with physical operational constraints.


How AI Is Repeating Familiar Shadow IT Security Risks

The rapid adoption of artificial intelligence across the corporate enterprise is triggering new governance and security risks that closely mirror past technological shifts, such as the initial emergence of shadow IT and unauthorized software as a service platform usage. Modern organizations currently face three primary vectors of vulnerability, starting with employees inadvertently leaking proprietary intellectual property, corporate source code, and confidential financial records by pasting this data into public generative AI platforms. Furthermore, software developers frequently introduce hidden backdoors or compromised dependencies into production systems by integrating unverified open source models and components that circumvent traditional software supply chain scrutiny. Compounding these operational issues is the sudden rise of autonomous AI agents that operate with dynamic decision making authority but completely lack explicitly defined ownership or documented permission boundaries within internal corporate networks. To successfully mitigate these vulnerabilities, blanket restrictive policies are typically ineffective; instead, companies must establish robust frameworks that ensure absolute visibility, accountability, and adaptive identity controls. As detailed in the SANS Institute’s new AI Security Maturity Model, managing these continuous threats requires treating artificial intelligence not as an isolated software application, but as a critical operational layer demanding proactive lifecycle validation and verification.


Six priorities reshaping the MENA boardroom in 2026

The EY report details how the 2026 macroeconomic landscape in the Middle East and North Africa (MENA) region requires corporate boardrooms to transition from traditional, periodic oversight toward integrated, forward-looking strategic leadership. Driven by overlapping pressures across geopolitics, rapid technological innovation, sustainability demands, and complex governance regulations, MENA boards face a highly volatile operating environment. To navigate this uncertainty and secure long-term value, directors must actively address six central boardroom priorities. First, boards need to develop geopolitical foresight, embedding regional shifts directly into strategic scenario planning. Second, they must manage the expanding technology and cyber assurance landscape, ensuring ethical artificial intelligence governance and robust defenses against escalating digital threats. Third, strengthening corporate integrity, fraud prevention, and independent investigation oversight remains essential for maintaining stakeholder trust. Fourth, elevating climate resilience and sustainability governance helps mitigate critical environmental risks while driving resource efficiency. Fifth, achieving financial excellence requires rigorous cost optimization and aligning internal controls across financial and sustainability reporting frameworks. Finally, adopting mature, behavioral-based board evaluations over mere procedural assessments fosters deep accountability. Ultimately, orchestrating these interconnected priorities empowers MENA leaders to fortify institutional trust and transform market disruptions into sustainable growth.

The software supply chain is the new ground zero for enterprise cyber risk. Don’t get caught short

In this article, Matias Madou highlights the rising vulnerabilities within the software supply chain as the new ground zero for enterprise cyber risks, heavily exacerbated by the rapid adoption of artificial intelligence tools. Recent highly sophisticated breaches, such as the TeamPCP supply chain attacks, have aggressively weaponized critical security and developer platforms like Checkmarx and the open-source library LiteLLM. By embedding highly obfuscated, multistage credential stealers into these trusted systems, attackers successfully moved laterally through development pipelines and Kubernetes clusters to exfiltrate highly sensitive enterprise data. Madou warns that traditional, reactive security measures are entirely insufficient against fast-moving, AI-driven threats. To mitigate these expanding dangers, organizations must redefine AI middleware as critical infrastructure, implementing rigorous monitoring of application programming interface keys and environment variables that constantly flow through these abstraction layers. Furthermore, security leaders must modernize risk management strategies by locking down dependency pipelines, enforcing strict least-privilege access, and gaining visibility into autonomous Model Context Protocol agents. Ultimately, the author urges modern enterprises to establish comprehensive internal AI governance frameworks and continuously upskill developers in secure coding standards rather than waiting for formal government legislation, thereby proactively shielding their operational workflows from devastating, cascading supply-chain compromises.


World Bank, African DPAs outline formula for trusted digital identity, DPI

During the ID4Africa 2026 Annual General Meeting, a key World Bank presentation emphasized that establishing public trust is vital for the success of digital public infrastructure and national identity systems across Africa. Experts noted that even mature digital identity networks remain vulnerable to operational failures and public mistrust due to weak data collection safeguards, frequent data breaches, and expanding cyberattack surfaces. To address these vulnerabilities, data protection authorities from nations like Liberia, Benin, and Mauritius highlighted that digital forensics, cybersecurity, and rigorous data governance must operate collectively. Although these under-resourced regulatory bodies often struggle to fund large population-scale awareness campaigns, they are pioneering localized solutions. For example, Mauritius leverages chief data officers and amicable dispute resolution mechanisms to efficiently settle compliance breaches without lengthy prosecution, while Benin relies on specialized government liaisons to ensure proper database compliance across different agencies. Furthermore, regional frameworks like the East African Community body facilitate international knowledge-sharing and joint investigative capabilities. Ultimately, achieving an ecosystem worthy of citizen and business trust requires a comprehensive formula blending careful system architecture, strictly enforced data protection, robust cybersecurity defenses, and transparent communication that effectively helps citizens understand their rights within the broader data lifecycle.


When configuration becomes a vulnerability: Exploitable misconfigurations in AI apps

The rapid deployment of artificial intelligence and agentic applications on cloud-native platforms, particularly Kubernetes clusters, often compromises cybersecurity in favor of operational speed. According to the Microsoft Defender Security Research Team, this trend has led to an increase in exploitable misconfigurations, which are scenarios where public internet access is paired with absent or weak authentication mechanisms. Rather than relying on sophisticated zero-day vulnerabilities, threat actors can leverage these low-effort attack paths to achieve high-impact compromises, including remote code execution, credential exfiltration, and unauthorized access to sensitive internal data. Microsoft identified these specific dangers across several popular AI platforms: Model Context Protocol servers frequently permitted unauthenticated interaction with corporate tools, Mage AI default setups enabled internet-accessible administrative shells, and frameworks like kagent and AutoGen Studio leaked plaintext API keys or allowed unauthorized workload deployments. To mitigate these pervasive security gaps, organizations must treat AI systems as high-impact workloads. Security teams should enforce strong authentication across all endpoints, apply strict least-privilege principles, and continuously audit infrastructure configurations. Furthermore, cloud protection tools like Microsoft Defender for Cloud can actively detect exposed services, helping defenders remediate dangerous oversights before malicious adversaries can exploit them.


Tokenized assets face trust infrastructure test, Cardano chief says

The article, titled "Tokenized assets face trust infrastructure test, Cardano chief says," by Jeff Pao, outlines a pivotal shift in the digital assets sector as financial institutions transition from tentative pilot projects to scaled, production-level tokenization. According to Cardano’s leadership, the primary challenges facing this widespread adoption are no longer the core blockchain mechanisms themselves, but rather the underlying hurdles of verification, identity, and robust auditability. These elements form a critical "trust infrastructure" that remains essential for creating compliant, institutional-grade financial networks. As real-world asset tokenization expands rapidly across global markets, traditional financial institutions require secure mechanisms like decentralized identifiers and privacy-preserving verifiable credentials to interact safely with public ledgers. By embedding accountability directly into the network architecture, digital trust frameworks turn complex compliance into seamless operational coordination, enabling institutions to efficiently manage counterparty exposure and automated settlement risks without exposing sensitive transactional data. Ultimately, the piece underscores that the long-term survival of decentralized finance relies heavily on resolving these identity and legal infrastructure gaps. Establishing a standardized trust layer will determine whether tokenized finance achieves mature stability or succumbs to institutional fragility and unresolved regulatory friction, marking a major turning point for future global capital flows.
Daily Tech Digest - August 16, 2025


Quote for the day:

"Develop success from failures. Discouragement and failure are two of the surest stepping stones to success." -- Dale Carnegie


Digital Debt Is the New Technical Debt (And It’s Worse)

Digital debt doesn’t just slow down technology. It slows down business decision-making and strategic execution. Decision-Making Friction: Simple business questions require data from multiple systems. “What’s our customer lifetime value?” becomes a three-week research project because customer data lives in six different platforms with inconsistent definitions. Campaign Launch Complexity: Marketing campaigns that should take two weeks to launch require six weeks of coordination across platforms. Not because the campaign is complex, but because the digital infrastructure is fragmented. Customer Experience Inconsistency: Customers encounter different branding, messaging, and functionality depending on which digital touchpoint they use. Support teams can’t access complete customer histories because data is distributed across systems. Innovation Paralysis: New initiatives get delayed because teams spend time coordinating existing systems rather than building new capabilities. Digital debt creates a gravitational pull that keeps organizations focused on maintenance rather than innovation. ... Digital debt is more dangerous than technical debt because it’s harder to see and affects more stakeholders. Technical debt slows down development teams. Digital debt slows down entire organizations.


Rising OT threats put critical infrastructure at risk

Attackers are exploiting a critical remote code execution (RCE) vulnerability in the Erlang programming language's Open Telecom Platform, widely used in OT networks and critical infrastructure. The flaw enables unauthenticated users to execute commands through SSH connection protocol messages that should be processed only after authentication. Researchers from Palo Alto Networks' Unit 42 said they have observed more than 3,300 exploitation attempts since May 1, with about 70% targeting OT networks across healthcare, agriculture, media and high-tech sectors. Experts urged affected organizations to patch immediately, calling it a top priority for any security team defending an OT network. The flaw, which has a CVSS score of 10, could enable an attacker to gain full control over a system and disrupt connected systems -- particularly worrisome in critical infrastructure. ... Despite its complex cryptography, the protocol contains design flaws that could enable attackers to bypass authentication and exploit outdated encryption standards. Researcher Tom Tervoort, a security specialist at Netherlands-based security company Secura, identified issues affecting at least seven different products, resulting in the issuing of three CVEs.


Why Tech Debt is Eating Your ROI (and How To Fix It)

Regardless of industry or specific AI efforts, these frustrations seem to boil down to the same culprit. Their AI initiatives continue to stumble over decades of accumulated tech debt. Part of the reason is despite the hype, most organizations use AI — let’s say, timidly. Fewer than half employ it for predictive maintenance or detecting network anomalies. Fewer than a third use it for root-cause analysis or intelligent ticket routing. Why such hesitation? Because implementing AI effectively means confronting all the messiness that came before. It means admitting our tech environments need a serious cleanup before adding another layer of complexity. Tech complexity has become a monster. This mess came from years of bolting on new systems without retiring old ones. Some IT professionals point to redundant applications as a major source of wasted budget and others blame overprovisioning in the cloud — the digital equivalent of paying rent on empty apartments. ... IT teams admit something that, to me, is alarming: Their infrastructure has grown so tangled they can no longer maintain basic security practices. Let that sink in. Companies with eight-figure tech budgets can’t reliably patch vulnerable systems or implement fundamental security controls. No one builds silos deliberately. Silos emerge from organizational boundaries, competing priorities and the way we fund and manage projects. 


Ready on paper, not in practice: The incident response gap in Australian organisations

The truth is, security teams often build their plans around assumptions rather than real-world threats and trends. That gap becomes painfully obvious during an actual incident, when organisations realise they aren't adequately prepared to respond. Recent findings of a Semperis study titled The State of Enterprise Cyber Crisis Readiness revealed a strong disconnect between organisations' perceived readiness to respond to a cyber crisis and their actual performance. The study also showed that cyber incident response plans are being implemented and regularly tested, but not broadly. In a real-world crisis, too many teams are still operating in silos. ... A robust, integrated, and well-practiced cyber crisis response plan is paramount for cyber and business resilience. After all, the faster you can respond and recover, the less severe the financial impact of a cyberattack will be. Organisations can increase their agility by conducting tabletop exercises that simulate attacks. By practicing incident response regularly and introducing a range of new scenarios of varying complexity, organisations can train for the real thing, which can often be unpredictable. Security teams can continually adapt their response plans based on the lessons learned during these exercises, and any new emerging cyber threats.


Quantum Threat Is Real: Act Now with Post Quantum Cryptography

Some of the common types of encryption we use today include RSA (Rivest-Shamir-Adleman), ECC (Elliptic Curve Cryptography), and DH (Diffie-Hellman Key Exchange). The first two are asymmetric types of encryption. The third is a useful fillip to the first to establish secure communication, with secure key exchange. RSA relies on very large integers, and ECC, on very hard-to-solve math problems. As can be imagined, these cannot be solved with traditional computing. ... Cybercriminals think long-term. They are well aware that quantum computing is still some time away. But that doesn’t stop them from stealing encrypted information. Why? They will store it securely until quantum computing becomes readily available; then they will decrypt it. The impending arrival of quantum computers has set the cat amongst the pigeons. ... Blockchain is not unhackable, but it is difficult to hack. A bunch of cryptographic algorithms keep it secure. These include SHA-256 (Secure Hash Algorithm 256-bit) and ECDSA (Elliptic Curve Digital Signature Algorithm). Today, cybercriminals might not attempt to target blockchains and steal crypto. But tomorrow, with the availability of a quantum computer, the crypto vault can be broken into, without trouble. ... We keep saying that quantum computing and quantum computing-enabled threats are still some time away. And, this is true. But when the technology is here, it will evolve and gain traction. 


Cultivating product thinking in your engineering team

The most common trap you’ll encounter is what’s called the “feature factory.” This is a development model where engineers are simply handed a list of features to build, without context. They’re measured on velocity and output, not on the value their work creates. This can be comfortable for some – it’s a clear path with measurable metrics – but it’s also a surefire way to kill innovation and engagement. ... First and foremost, you need to provide context, and you need to do so early and often. Don’t just hand a Jira ticket to an engineer. Before a sprint starts, take the time to walk through the “what,” the “why,” and the “who.” Explain the market research that led to this feature request, share customer feedback that highlights the problem, and introduce them to the personas you’re building for. A quick 15-minute session at the start of a sprint can make a world of difference. You should also give engineers a seat at the table. Invite them to meetings where product managers are discussing strategy and customer feedback. They don’t just need to hear the final decision; they need to be a part of the conversation that leads to it. When an engineer hears a customer’s frustration firsthand, they gain a level of empathy that a written user story can never provide. They’ll also bring a unique perspective to the table, challenging assumptions and offering technical solutions you may not have considered.


Adapting to New Cloud Security Challenges

While the essence of Non-Human Identities and their secret management is acknowledged, many organizations still grapple with the efficient implementation of these practices. Some stumble upon the over-reliance on traditional security measures, thereby failing to adopt newer, more effective strategies that incorporate NHI management. Others struggle with time and resource constraints, devoid of efficient automation mechanisms – a crucial aspect for proficient NHI management. The disconnect between security and R&D teams often results in fractured efforts, leading to potential security gaps, breaches, and data leaks. ... With more organizations migrate to the cloud and with the rise of machine identities and secret management, the future of cloud security has been redefined. It is no longer solely about the protection from known threats but now involves proactive strategies to anticipate and mitigate potential future risks. This shift necessitates organizations to rethink their approach to cybersecurity, with a keen focus on NHIs and Secrets Security Management. It requires an integrated endeavor, involving CISOs, cybersecurity professionals, and R&D teams, along with the use of scalable and innovative platforms. Thought leaders in the data field continue to emphasize the importance of robust NHI management as vital to the future of cybersecurity, driving the message home for businesses of all sizes and across all industries.


Why IT Modernization Occurs at the Intersection of People and Data

A mandate for IT modernization doesn’t always mean the team has the complete expertise necessary to complete that mandate. It may take some time to arm the team with the correct knowledge to support modernization. Let’s take data analytics, for example. Many modern data analytics solutions, armed with AI, now allow teams to deliver natural language prompts that can retrieve the data necessary to inform strategic modernization initiatives without having to write expert-level SQL. While this lessens the need for writing scripts, IT leaders must still ensure their teams have the right expertise to construct the correct prompts. This could mean training on correct terms for presenting data and/or manipulating data, along with knowing in what circumstances to access that data. Having a well-informed and educated team will be especially important after modernization efforts are underway. ... One of the most important steps to IT modernization is arming your IT teams with a complete picture of the current IT infrastructure. It’s equivalent to giving them a full map before embarking on their modernization journey. In many situations, an ideal starting point is to ensure that any documentation, ER diagrams, and architectural diagrams are collected into a single repository and reviewed. Then, the IT teams use an observability solution that integrates with every part of the enterprise infrastructure to show each team how every part of it works together. 


Cyber Resilience Must Become The Third Pillar Of Security Strategy

For years, enterprise security has been built around two main pillars: prevention and detection. Firewalls, endpoint protection, and intrusion detection systems all aim to stop attackers before they do damage. But as threats grow more sophisticated, it’s clear that this isn’t enough. ... The shift to cloud computing has created dangerous assumptions. Many organizations believe that moving workloads to AWS, Azure, or Google Cloud means the provider “takes care of security.” ... Effective resilience starts with rethinking backup as more than a compliance checkbox. Immutable, air-gapped copies prevent attackers from tampering with recovery points. Built-in threat detection can spot ransomware or other malicious activity before it spreads. But technology alone isn’t enough. Mariappan urges leaders to identify the “minimum viable business” — the essential applications, accounts, and configurations required to function after an incident. Recovery strategies should be built around restoring these first to reduce downtime and financial impact. She also stresses the importance of limiting the blast radius. In a cloud context, that might mean segmenting workloads, isolating credentials, or designing architectures that prevent a single compromised account from jeopardizing an entire environment.


Breaking Systems to Build Better Ones: How AI is Reshaping Chaos Engineering

While AI dominates technical discussions across industries, Andrus maintains a pragmatic perspective on its role in system reliability. “If Skynet comes about tomorrow, it’s going to fail in three days. So I’m not worried about the AI apocalypse, because AI isn’t going to be able to build and maintain and run reliable systems.” The fundamental challenge lies in the nature of distributed systems versus AI capabilities. “A lot of the LLMs and a lot of what we talk about in the AI world is really non deterministic, and when we’re talking about distributed systems, we care about it working correctly every time, not just most of the time.” However, Andrus sees valuable applications for AI in specific areas. AI excels at providing suggestions and guidance rather than making deterministic decisions. ... Despite its name, chaos engineering represents the opposite of chaotic approaches to system reliability. “Chaos engineering is a bit of a misnomer. You know, a lot of people think, Oh, we’re going to go cause chaos and see what happens, and it’s the opposite. We want to engineer the chaos out of our systems.” This systematic approach to understanding system behavior under stress provides the foundation for building more resilient infrastructure. As AI-generated code increases system complexity, the need for comprehensive reliability testing becomes even more critical. 

Daily Tech Digest - July 27, 2025


Quote for the day:

"The only way to do great work is to love what you do." -- Steve Jobs


Amazon AI coding agent hacked to inject data wiping commands

The hacker gained access to Amazon’s repository after submitting a pull request from a random account, likely due to workflow misconfiguration or inadequate permission management by the project maintainers. ... On July 23, Amazon received reports from security researchers that something was wrong with the extension and the company started to investigate. Next day, AWS released a clean version, Q 1.85.0, which removed the unapproved code. “AWS is aware of and has addressed an issue in the Amazon Q Developer Extension for Visual Studio Code (VSC). Security researchers reported a potential for unapproved code modification,” reads the security bulletin. “AWS Security subsequently identified a code commit through a deeper forensic analysis in the open-source VSC extension that targeted Q Developer CLI command execution.” “After which, we immediately revoked and replaced the credentials, removed the unapproved code from the codebase, and subsequently released Amazon Q Developer Extension version 1.85.0 to the marketplace.” AWS assured users that there was no risk from the previous release because the malicious code was incorrectly formatted and wouldn’t run on their environments.


How to migrate enterprise databases and data to the cloud

Migrating data is only part of the challenge; database structures, stored procedures, triggers and other code must also be moved. In this part of the process, IT leaders must identify and select migration tools that address the specific needs of the enterprise, especially if they’re moving between different database technologies (heterogeneous migration). Some things they’ll need to consider are: compatibility, transformation requirements and the ability to automate repetitive tasks.  ... During migration, especially for large or critical systems, IT leaders should keep their on-premises and cloud databases synchronized to avoid downtime and data loss. To help facilitate this, select synchronization tools that can handle the data change rates and business requirements. And be sure to test these tools in advance: High rates of change or complex data relationships can overwhelm some solutions, making parallel runs or phased cutovers unfeasible. ... Testing is a safety net. IT leaders should develop comprehensive test plans that cover not just technical functionality, but also performance, data integrity and user acceptance. Leaders should also plan for parallel runs, operating both on-premises and cloud systems in tandem, to validate that everything works as expected before the final cutover. They should engage end users early in the process in order to ensure the migrated environment meets business needs.


Researchers build first chip combining electronics, photonics, and quantum light

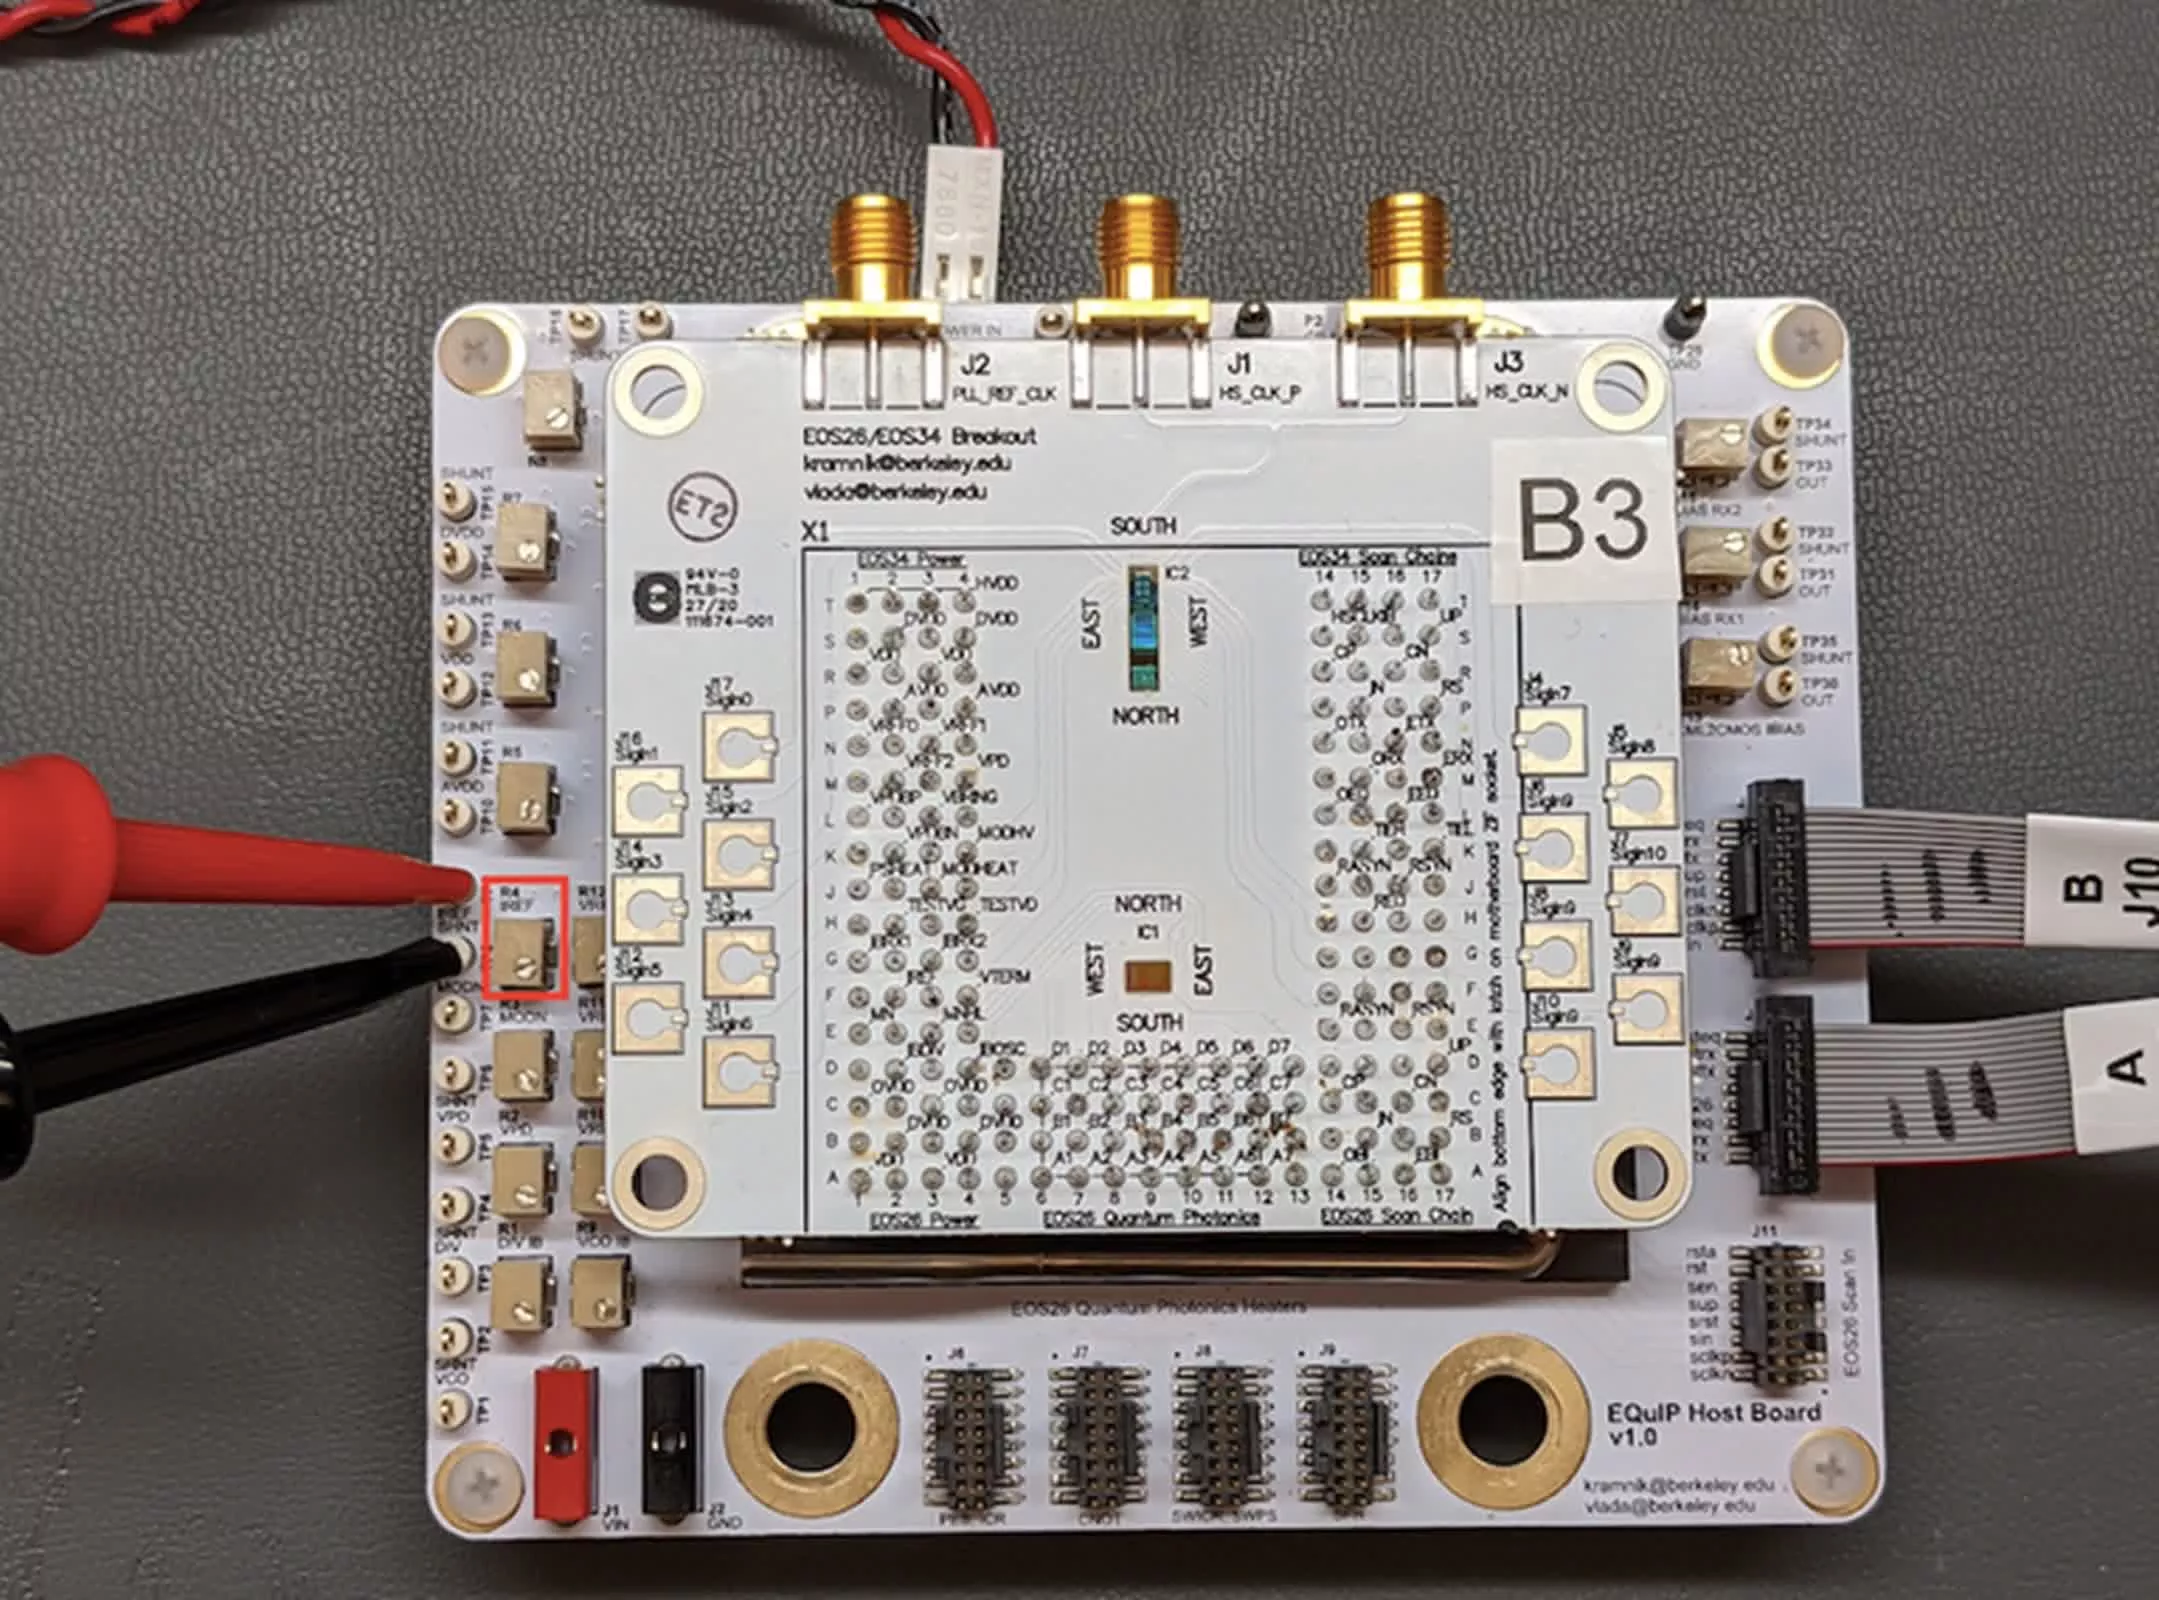
The new chip integrates quantum light sources and electronic controllers using a standard 45-nanometer semiconductor process. This approach paves the way for scaling up quantum systems in computing, communication, and sensing, fields that have traditionally relied on hand-built devices confined to laboratory settings. "Quantum computing, communication, and sensing are on a decades-long path from concept to reality," said MiloÅ¡ Popović, associate professor of electrical and computer engineering at Boston University and a senior author of the study. "This is a small step on that path – but an important one, because it shows we can build repeatable, controllable quantum systems in commercial semiconductor foundries." ... "What excites me most is that we embedded the control directly on-chip – stabilizing a quantum process in real time," says Anirudh Ramesh, a PhD student at Northwestern who led the quantum measurements. "That's a critical step toward scalable quantum systems." This focus on stabilization is essential to ensure that each light source performs reliably under varying conditions. Imbert Wang, a doctoral student at Boston University specializing in photonic device design, highlighted the technical complexity.


Product Manager vs. Product Owner: Why Teams Get These Roles Wrong

While PMs work on the strategic plane, Product Owners anchor delivery. The PO is the guardian of the backlog. They translate the product strategy into epics and user stories, groom the backlog, and support the development team during sprints. They don’t just manage the “what” — they deeply understand the “how.” They answer developer questions, clarify scope, and constantly re-evaluate priorities based on real-time feedback. In Agile teams, they play a central role in turning strategic vision into working software. Where PMs answer to the business, POs are embedded with the dev team. They make trade-offs, adjust scope, and ensure the product is built right. ... Some products need to grow fast. That’s where Growth PMs come in. They focus on the entire user lifecycle, often structured using the PIRAT funnel: Problem, Insight, Reach, Activation, and Trust (a modern take on traditional Pirate Metrics, such as Acquisition, Activation, Retention, Referral, and Revenue). This model guides Growth PMs in identifying where user friction occurs and what levers to pull for meaningful impact. They conduct experiments, optimize funnels, and collaborate closely with marketing and data science teams to drive user growth. 


Ransomware payments to be banned – the unanswered questions

With thresholds in place, businesses/organisations may choose to operate differently so that they aren’t covered by the ban, such as lowering turnover or number of employees. All of this said, rules like this could help to get a better picture of what’s going on with ransomware threats in the UK. Arda Büyükkaya, senior cyber threat intelligence analyst at EclecticIQ, explains more: “As attackers evolve their tactics and exploit vulnerabilities across sectors, timely intelligence-sharing becomes critical to mounting an effective defence. Encouraging businesses to report incidents more consistently will help build a stronger national threat intelligence picture something that’s important as these attacks grow more frequent and become sophisticated. To spare any confusion, sector-specific guidance should be provided by government on how resources should be implemented, making resources clear and accessible. “Many victims still hesitate to come forward due to concerns around reputational damage, legal exposure, or regulatory fallout,” said Büyükkaya. “Without mechanisms that protect and support victims, underreporting will remain a barrier to national cyber resilience.” Especially in the earlier days of the legislation, organisations may still feel pressured to pay in order to keep operations running, even if they’re banned from doing so.


AI Unleashed: Shaping the Future of Cyber Threats

AI optimizes reconnaissance and targeting, giving hackers the tools to scour public sources, leaked and publicly available breach data, and social media to build detailed profiles of potential targets in minutes. This enhanced data gathering lets attackers identify high-value victims and network vulnerabilities with unprecedented speed and accuracy. AI has also supercharged phishing campaigns by automatically crafting phishing emails and messages that mimic an organization’s formatting and reference real projects or colleagues, making them nearly indistinguishable from genuine human-originated communications. ... AI is also being weaponized to write and adapt malicious code. AI-powered malware can autonomously modify itself to slip past signature-based antivirus defenses, probe for weaknesses, select optimal exploits, and manage its own command-and-control decisions. Security experts note that AI accelerates the malware development cycle, reducing the time from concept to deployment. ... AI presents more than external threats. It has exposed a new category of targets and vulnerabilities, as many organizations now rely on AI models for critical functions, such as authentication systems and network monitoring. These AI systems themselves can be manipulated or sabotaged by adversaries if proper safeguards have not been implemented.


Agile and Quality Engineering: Building a Culture of Excellence Through a Holistic Approach

Agile development relies on rapid iteration and frequent delivery, and this rhythm demands fast, accurate feedback on code quality, functionality, and performance. With continuous testing integrated into automated pipelines, teams receive near real-time feedback on every code commit. This immediacy empowers developers to make informed decisions quickly, reducing delays caused by waiting for manual test cycles or late-stage QA validations. Quality engineering also enhances collaboration between developers and testers. In a traditional setup, QA and development operate in silos, often leading to communication gaps, delays, and conflicting priorities. In contrast, QE promotes a culture of shared ownership, where developers write unit tests, testers contribute to automation frameworks, and both parties work together during planning, development, and retrospectives. This collaboration strengthens mutual accountability and leads to better alignment on requirements, acceptance criteria, and customer expectations. Early and continuous risk mitigation is another cornerstone benefit. By incorporating practices like shift-left testing, test-driven development (TDD), and continuous integration (CI), potential issues are identified and resolved long before they escalate. 


Could Metasurfaces be The Next Quantum Information Processors?

Broadly speaking, the work embodies metasurface-based quantum optics which, beyond carving a path toward room-temperature quantum computers and networks, could also benefit quantum sensing or offer “lab-on-a-chip” capabilities for fundamental science Designing a single metasurface that can finely control properties like brightness, phase, and polarization presented unique challenges because of the mathematical complexity that arises once the number of photons and therefore the number of qubits begins to increase. Every additional photon introduces many new interference pathways, which in a conventional setup would require a rapidly growing number of beam splitters and output ports. To bring order to the complexity, the researchers leaned on a branch of mathematics called graph theory, which uses points and lines to represent connections and relationships. By representing entangled photon states as many connected lines and points, they were able to visually determine how photons interfere with each other, and to predict their effects in experiments. Graph theory is also used in certain types of quantum computing and quantum error correction but is not typically considered in the context of metasurfaces, including their design and operation. The resulting paper was a collaboration with the lab of Marko Loncar, whose team specializes in quantum optics and integrated photonics and provided needed expertise and equipment.


New AI architecture delivers 100x faster reasoning than LLMs with just 1,000 training examples

When faced with a complex problem, current LLMs largely rely on chain-of-thought (CoT) prompting, breaking down problems into intermediate text-based steps, essentially forcing the model to “think out loud” as it works toward a solution. While CoT has improved the reasoning abilities of LLMs, it has fundamental limitations. In their paper, researchers at Sapient Intelligence argue that “CoT for reasoning is a crutch, not a satisfactory solution. It relies on brittle, human-defined decompositions where a single misstep or a misorder of the steps can derail the reasoning process entirely.” ... To move beyond CoT, the researchers explored “latent reasoning,” where instead of generating “thinking tokens,” the model reasons in its internal, abstract representation of the problem. This is more aligned with how humans think; as the paper states, “the brain sustains lengthy, coherent chains of reasoning with remarkable efficiency in a latent space, without constant translation back to language.” However, achieving this level of deep, internal reasoning in AI is challenging. Simply stacking more layers in a deep learning model often leads to a “vanishing gradient” problem, where learning signals weaken across layers, making training ineffective. 


For the love of all things holy, please stop treating RAID storage as a backup

Although RAID is a backup by definition, practically, a backup doesn't look anything like a RAID array. That's because an ideal backup is offsite. It's not on your computer, and ideally, it's not even in the same physical location. Remember, RAID is a warranty, and a backup is insurance. RAID protects you from inevitable failure, while a backup protects you from unforeseen failure. Eventually, your drives will fail, and you'll need to replace disks in your RAID array. This is part of routine maintenance, and if you're operating an array for long enough, you should probably have drive swaps on a schedule of several years to keep everything operating smoothly. A backup will protect you from everything else. Maybe you have multiple drives fail at once. A backup will protect you. Lord forbid you fall victim to a fire, flood, or other natural disaster and your RAID array is lost or damaged in the process. A backup still protects you. It doesn't need to be a fire or flood for you to get use out of a backup. There are small issues that could put your data at risk, such as your PC being infected with malware, or trying to write (and replicate) corrupted data. You can dream up just about any situation where data loss is a risk, and a backup will be able to get your data back in situations where RAID can't.