Showing posts with label Human in The Loop. Show all posts

Daily Tech Digest - September 17, 2026


Quote for the day:

“The moment you’re comfortable is the moment you stop growing.” -- Allison Dunn

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


AI Security Spending Jumps as Fear Outpaces Proof of Value
Companies are heavily investing in artificial intelligence for cybersecurity, often prioritizing swift adoption over clear proof of its effectiveness. Driven by the transition of AI from a testing phase into active use, along with the rising deployment of AI by bad actors, organizations feel immense pressure to keep pace. For many chief information security officers (CISOs), fear of falling behind and the need for "blame insurance" against potential breaches are accelerating spending. In fact, a significant number of CISOs cite AI as their top priority for new budget allocations. Despite this aggressive funding, the most common AI implementations often fall short of delivering the highest returns. The challenge is compounded by the inherent difficulty of measuring the return on investment (ROI) in cybersecurity, where success is defined by preventing events like data breaches rather than generating direct profit. Experts advise a more deliberate approach, urging organizations to move past the hype. Rather than adopting AI simply for the sake of having it, companies should focus on areas where the technology can genuinely lower risk and handle repetitive tasks. Thoughtful integration, backed by strong governance and clear goals, will ultimately determine which organizations benefit most from their AI cybersecurity investments.


Salesforce’s massive outage exposes the hidden risks of cloud dependencies

A massive Salesforce outage during its flagship Dreamforce event has underscored the hidden architectural risks of cloud dependency. A roughly seven-and-a-half-hour service disruption on September 16 impacted multiple instances across all regions, initially stemming from a core system component struggling with an "external dependency failure" linked to a legacy login server. Although the issue was resolved by mid-afternoon through manual interventions after automated rolling restarts fell short, the outage highlights that cloud systems do not eradicate architectural vulnerabilities. Instead, these dependencies can become enterprise risks when a central platform fails. The service failure emphasizes the necessity of looking beyond immediate access restoration. Enterprises must transition into a reconciliation phase to address "temporal data problems," ensuring transactions, scheduled jobs, and downstream systems remain consistent. The disruption proves that a legacy component's age is less critical than its role within the system's dependency graph. Organizations should not equate modernization simply with replacing old technology. They must assess dependency concentration, failure blast radius, and isolation strategies. While there are no signs of a security incident, industry experts suggest automated AI tools or recent workforce reductions might have played a role in the disruption. Future post-incident reviews must provide clear insights into failure propagation and preventive measures.


Crypto Industry Figures Blackmailed by Revolut's Hacker
A recent data breach at the British financial services company Revolut has exposed the sensitive personal information of roughly six hundred and eighty high-profile cryptocurrency exchange customers. An extortion group calling itself "Iamnotavillain" orchestrated the attack without breaking into the bank's secure servers. Instead, the criminals gained access to a legitimate Italian government email system. By posing as authorized law enforcement officials for several months, they submitted fraudulent data requests to the bank's compliance team. Believing the inquiries were authentic, employees handed over highly confidential customer files. This exposed data included passport copies, verification photographs, home addresses, phone numbers, and detailed transaction histories. The attackers specifically targeted users with substantial digital asset activity, and notable industry figures such as former Mt. Gox executive Mark Karpelès were among the victims. After securing these detailed identity packages, the hackers launched a blackmail campaign. They demanded a ransom payment of three million dollars, requested in the privacy-focused digital currency Monero, to prevent the information from being released. The extortionists even set up a public website with a countdown clock, threatening to sell the stolen records to other criminal organizations if the company failed to meet their demands within a strict twenty-four hour window.


Stop Treating CSS Container Queries Like Traditional Media Queries

The article clarifies the common misconception that CSS container queries and media queries serve the same purpose. Despite having a 94% browser support rate, container queries are vastly underutilized. Many developers mistakenly treat them interchangeably because of their similar syntax, but they fundamentally differ in their approach to responsive design. Media queries focus outward on the "macro" layout. They check the viewport's dimensions to adjust overarching page structures, such as main grids or full-width headers. Conversely, container queries look inward at "micro" layouts. They allow individual components, like cards or widgets, to adapt based on the available space within their specific parent container, rather than the entire screen size. This distinction is crucial for creating reusable components that maintain their layout integrity regardless of where they are placed on a page. The author advises against replacing media queries entirely with container queries. Instead, the focus should be on a separation of concerns. Media queries remain ideal for page-level adjustments, while container queries shine when a component's layout depends on its immediate context. However, container queries require an extra wrapper element, cannot query their own block size without collapsing, and cannot accept custom property values. Ultimately, understanding these differences unlocks more resilient responsive design.


Trust becomes the product: Five takeaways from the Splunk .conf26 keynotes

The recent Splunk conference centered on a critical theme for modern businesses: trust is the most important element when deploying artificial intelligence agents. As these agents shift from being simple tools to functioning as autonomous digital teammates, they are handling complex tasks around the clock. This shift requires a strong system of record to ensure they act appropriately. A major takeaway is the necessary merging of system monitoring and security. Because it is difficult to tell the difference between a software error, a security breach, or a poorly executed AI command, companies must combine their monitoring and security data to accurately diagnose issues. Cost management is another significant focus. AI agents can quickly become expensive to run if they are not carefully controlled, meaning businesses need better visibility into their data usage to prevent unexpected bills. Furthermore, managing the massive amounts of data required for these systems must become more affordable and efficient so companies do not have to choose which information to keep. Ultimately, organizations are treating AI agents like new employees. They are granting them limited permissions initially and slowly increasing their responsibilities as they prove their reliability, ensuring that human oversight remains an essential part of the process.


Architecting for the Knowledge You Can’t Capture

The article argues that organizations often underestimate how much essential knowledge never makes it into their documentation or AI systems. It opens with a familiar scenario: an experienced engineer is asked to “document everything” before leaving, but what gets captured is only the clean, idealized version of the work. The subtle judgments, exceptions, and sensory cues that guide real decisions never appear in the flowcharts or transcripts, leaving future teams without the insight needed to handle unusual situations. The author explains that this gap reflects the nature of tacit knowledge—skills and perceptions people rely on but rarely articulate. Modern AI can learn from examples, but when expertise is rare or incidents are infrequent, there simply isn’t enough data for models to infer the missing judgment. The article proposes a structured elicitation protocol that pushes experts to clarify thresholds, exceptions, evidence, and escalation paths, turning vague statements into actionable rules. It also outlines a four‑layer architecture—capture, representation, serving, and transmission—to preserve context, surface uncertainty, and support apprenticeship when documentation falls short. The core message is that organizations must design for the knowledge people can’t easily express, or their AI systems will remain blind to the expertise that actually keeps operations running.


How to keep AI-generated code aligned with your standards

The article discusses the challenge of keeping AI-generated code aligned with organizational standards. As more developers use AI coding tools, the risk of accumulating technical and operational debt increases if code is only judged by whether it works functionally. To prevent this, engineering teams must clearly document their non-functional requirements, such as security rules, performance expectations, and data governance policies. These standards should not remain hidden as tribal knowledge. Instead, they must be explicit, machine-readable, and fed into the AI tools as context before any code is generated. Furthermore, organizations should enforce these rules by turning them into automated acceptance criteria within their continuous integration and delivery pipelines. This ensures that any AI-generated code is automatically checked for compliance, security, and performance before it merges. Experts recommend treating AI output as untrusted until it passes the exact same rigorous reviews, tests, and monitoring as human-written code. Ultimately, governing AI-generated code requires shifting from manual audits to automated, systemic enforcement. By maintaining clear specifications, integrating standards into automated testing, and adapting context engines to learn from past decisions, development teams can safely scale their AI use while keeping code quality strictly aligned with enterprise expectations over the long term.


Human-in-the-loop oversight is critical for enterprise AI: 4 experts explain why

Enterprise AI systems increasingly require human-in-the-loop (HITL) oversight to ensure accountability and mitigate risks associated with flawed AI outputs. The FTC's actions against DoNotPay highlight the legal perils of deploying unchecked AI, driving the adoption of software with built-in human escalation for complex workflows. While HITL is meant to catch model errors before they become compliance or legal issues, experts warn against relying solely on an AI's self-assessed confidence score to trigger review, as a confident model can still be wrong. Effective HITL design involves intelligent routing that escalates issues to the appropriate personnel based on organizational risk tolerance, rather than a simple binary system. Furthermore, real oversight demands more than a rubber-stamp approval process; it requires reviewers with the context and time to actually evaluate the AI's work and overturn it if necessary, combating the tendency for reviewers to become biased in favor of the AI's suggestions. Legislation like the EU AI Act necessitates demonstrable proof of this oversight through clear audit trails. Successful implementations, like those by Nominal and IgniteTech, often mandate human approval for critical actions and use "grounding," which forces the AI to rely only on verified company data or escalate the query if it lacks the information, ensuring accountability remains firmly with human operators.


Passkeys in the post-quantum era: Why FIDO needs more than new algorithms

The provided article discusses the need to prepare the FIDO2 ecosystem, which includes passkeys, for the post-quantum era. Passkeys, which rely on asymmetric cryptography, are vulnerable to future quantum computers that could potentially break the current public-key algorithms like RSA and elliptic curve cryptography.

The author, Johann-Philipp Thiers, explains that transitioning to Post-Quantum Cryptography (PQC) is a complex process. It goes beyond simply swapping out algorithms. PQC algorithms often result in larger keys and signatures, which can be problematic for resource-constrained authenticators like hardware security keys due to memory, processing power, and transport limitations.

Furthermore, the transition involves updating the entire trust chain, including metadata service signatures, certificate formats, and relying party support. The author emphasizes that FIDO’s current crypto-agility is beneficial but requires coordination among various stakeholders, such as operating systems, browsers, and certification programs. Practical demonstrators are crucial for identifying engineering challenges like message sizes, performance impacts, and interoperability issues. Ultimately, securing passkeys against quantum threats requires a gradual, coordinated effort involving standardization, testing, and careful engineering to ensure their long-term viability.


AI made software development unrecognizable. Is cybersecurity next?

Artificial intelligence is rapidly reshaping the cybersecurity landscape, much as it has already transformed software development. While the shift in security might take slightly longer, experts predict that fundamental changes are inevitable. Security Operations Centers will soon rely heavily on autonomous agents to perform initial triage, allowing human analysts to focus on complex oversight and critical decisions. This transition is essential because AI is drastically increasing the discovery of vulnerabilities, creating a massive backlog that security teams struggle to absorb and remediate. Furthermore, as attackers begin using AI to launch high speed automated threats, organizations must deploy their own rapid containment systems to respond effectively. This shift will also alter the cybersecurity workforce. Rather than eliminating jobs, organizations will likely adopt flatter teams featuring highly experienced senior professionals at one end and junior staff at the other, putting pressure on middle management roles. AI might also serve as a unifying interface to manage sprawling security toolsets. To prepare, security leaders should begin testing agents on high volume tasks while establishing strong governance frameworks. Most importantly, leaders must ensure that every autonomous agent has a designated human owner who remains fully accountable for its actions and potential failures within the organization.

Daily Tech Digest - August 23, 2026


Quote for the day:

“Motivation comes from working on things we care about. It also comes from working with people we care about.” -- Sheryl Sandberg

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 5 mins • Perfect for listening on the go.


Managing the cyber risk of agentic AI

The UK’s National Cyber Security Centre recently released guidance on how organizations can securely deploy and manage the risks associated with agentic artificial intelligence. Unlike earlier discussions that focused mainly on securing standalone models against common exploits or data leaks, this advice shifts the focus to securing the agent in operation. When an autonomous system can retrieve records, trigger workflows, and interact with external applications, the primary security question becomes what the system is permitted to do, rather than simply what it knows. To safely integrate these tools, the center emphasizes treating them as active participants within your digital environment. A core recommendation is assigning distinct identities to agents, which enables independent monitoring and prevents their activities from blending into human or service accounts. Organizations should apply practical safeguards, including sandboxing, strict permission limits, and targeted access controls tailored to the agent's level of autonomy. Most importantly, the guidance stresses the need for active human oversight and the ongoing ability to intervene if an agent behaves unexpectedly in a production setting. By fostering direct collaboration among developers, operators, and security teams, leaders can adapt traditional security measures to manage these evolving operational risks with clear expectations and steady control.


Building data centers is getting easier. Building trust is not

While the physical construction of data centers has become significantly more streamlined in recent years, securing the confidence of local communities and regulators remains a steep challenge. Technological advancements, modular designs, and standardized construction processes have made it easier than ever to bring new facilities online efficiently. Developers have largely solved the engineering puzzle of deploying vast digital infrastructure at scale. However, this operational efficiency does not automatically translate into public acceptance. As these facilities grow in size and number, they place immense demands on local power grids and water supplies, leading to heightened scrutiny from residents and local governments. People are increasingly concerned about the environmental impact and the strain on public resources. Consequently, the industry is facing a landscape where technical execution is no longer the primary bottleneck for expansion. Instead, the real difficulty lies in navigating complex zoning laws, addressing community anxieties, and proving a genuine commitment to sustainable practices. Building trust requires transparent communication, investments in renewable energy, and a willingness to integrate into the community rather than simply occupying space. Ultimately, developers must realize that while pouring concrete and installing servers is straightforward, earning the social license to operate takes steady, consistent effort.


Surveillance – Everything You Wanted to Know, But Were Afraid to Ask

Surveillance has become an unavoidable reality, with various groups tracking our everyday activities for their own specific benefit rather than ours. Commercial companies monitor us to drive sales through targeted advertisements and complex internet cookies, while employers increasingly track employee behavior, private communications, and daily productivity to maintain control. On the malicious side, criminals use harmful software to quietly steal personal data, passwords, and digital credentials for financial gain. Law enforcement agencies also monitor the general public, often justifying their actions under the banner of public safety. However, this well-intended monitoring can easily overstep its boundaries, capturing far more personal information than necessary and sharing it widely. Across all these distinct groups, the rapid integration of artificial intelligence is accelerating the scale and depth of continuous surveillance, making it much easier to analyze our behaviors, conversations, and habits. These practices carry significant consequences for our personal privacy, individual freedom, bank balances, and even employment status. Despite these growing capabilities, our primary defenses remain largely limited to legal regulations and our own ongoing personal awareness. Ultimately, whether driven by profit, control, theft, or public safety, continuous observation is a fixture of modern life that requires strict accountability and clear boundaries.


The Swivel Chair Problem Holding Back Enterprise AI With Clio

In a recent episode of the Tech Talks Daily podcast, host Neil C. Hughes explores a major barrier to adopting new workplace tools: the swivel chair problem. Speaking with a guest from Clio, the conversation focuses on the hidden problems holding back the effective use of artificial intelligence in modern businesses. The central idea asks listeners to consider how much of their office software relies on employees acting as human bridges between disconnected programs. When systems cannot talk to each other, people are forced to quietly compensate by swiveling between multiple screens and manually copying information from one application to another. This routine manual effort not only wastes valuable time but also creates a messy setup that prevents advanced tools from working as intended. The episode, which runs for about thirty minutes, breaks down why organizations must address these basic communication gaps before expecting new systems to deliver real value. Rather than focusing on complex technical ideas, the discussion highlights a practical reality. Businesses must connect their foundational tools and eliminate repetitive manual entry. By solving the swivel chair problem, companies can build a smooth process where technology actually serves the workforce, ultimately setting the stage for more effective and reliable results.


80% of developers find AI coding more addictive than helpful

AI programming tools help developers write code faster, but they are also introducing new challenges like addiction and burnout. A recent survey revealed that eighty percent of developers feel dependent on these tools rather than simply aided by them. Because AI tools provide an engaging, continuous feedback loop, many programmers find it difficult to stop working. The process of watching an AI agent generate code can trigger cycles of anticipation and reward, which keeps developers hooked long after their normal work hours should end. Beyond the daily struggle to log off, the quality of AI-generated work is creating hidden problems. While adoption continues to climb, overall trust in the accuracy of AI output has dropped significantly. Developers report growing frustration with code that is nearly correct but requires time-consuming debugging. This creates what the industry calls verification debt. The time saved by generating code quickly is often lost because developers still need to carefully review it for security, system compatibility, and overall accuracy. Furthermore, employers routinely expect more output from developers using these tools, which offsets any potential time savings. Ultimately, the integration of AI into software development has become a pressing work-life balance issue, leaving programmers struggling to set clear professional boundaries.


Enterprises winning with AI agents are limiting how much the agents can do alone

Over the past two years, many businesses believed that giving artificial intelligence agents complete freedom to handle complex tasks would automatically boost performance. However, recent real-world applications show that this fully independent approach is largely failing. Capability is currently outpacing control, leading to rising costs, unclear value, and significant risk management issues. In fact, industry forecasts suggest that a large portion of current AI projects will be canceled within a few years due to these exact governance problems. Instead of racing to build the most independent systems, successful organizations are prioritizing trust and reliability. They are actively limiting what their AI tools can do without human oversight. Rather than relying on broad, general-purpose programs, these companies design agents with narrow, highly specific responsibilities. By creating tightly bounded rules and breaking large workflows into smaller tasks, they make errors much easier to audit and fix. Furthermore, they are enforcing strict human verification for any high-risk actions. This approach acknowledges that while AI can greatly reduce manual effort, human judgment remains essential for safety and compliance. The true advantage goes to companies that establish clear boundaries, ensuring their tools operate safely within well-defined limits rather than running unconstrained.


The tug-of-war between AI and traditional cloud services

Major cloud service providers are currently pouring money and attention into artificial intelligence to capture the high revenue it promises, but this intense focus risks leaving their core services behind. Most businesses rely daily on foundational cloud tools like storage, computing power, databases, and networking to keep operations running smoothly. While introducing new artificial intelligence features into these older systems might look impressive on the surface, adding a chatbot or search assistant does not actually improve the underlying reliability, speed, or overall value of the service. If providers neglect the essential updates and maintenance required for these traditional tools, customers will eventually suffer from unresolved bugs, poor support, and frustrating outages. Traditional infrastructure is not an outdated concept; it is the essential bedrock of modern business technology. Customers should not simply accept that all services are improving at the same rate. Instead, they need to closely watch product updates and release notes to verify that the core tools they depend on are receiving genuine upgrades rather than just decorative updates. Furthermore, businesses must use their negotiating power during contract renewals to clearly demand that cloud providers continue investing in the everyday infrastructure that keeps their digital doors safely open.


Beyond Legacy Processes: Engineering the High-Velocity Enterprise

In a recent podcast episode, Isaac Sacolick speaks with Daniel Meyer, the chief technology officer of Camunda, about updating outdated business processes for the modern workplace. Meyer explains that companies can improve older manual workflows by organizing them entirely from start to finish before carefully introducing artificial intelligence. He shares a specific example where this approach made loan underwriting significantly faster. A panel of experts, including Joanne Friedman, Joseph Puglisi, and John Patrick Luethe, joined the conversation to share their perspectives. They highlight the importance of building trust in artificial intelligence gradually over time. The panel emphasizes the need for safety measures, clear observation, and consistent human oversight when adopting these systems. The discussion also explores how to best organize tasks across an organization. Meyer favors a central approach to manage different activities effectively. Looking ahead, the group envisions a future where both customers and employees interact with technology in a more natural, conversational way. Artificial intelligence will likely handle complex tasks across various systems, potentially removing traditional barriers between corporate departments. The conversation touches on maintaining compliance, keeping clear records, and managing systems that learn continuously. Finally, Sacolick notes his upcoming speech in New York City about redesigning work processes.


Ransomware takes aim at enterprise resilience

Ransomware has evolved from a basic encryption threat into a complex strategy aimed at total business disruption. Attackers now routinely bypass encryption entirely, opting to steal sensitive data and threaten public release to extort payments. This shift means the focus for organizations is no longer just restoring systems, but maintaining daily operations and protecting customer trust during an active incident. The rapid adoption of artificial intelligence complicates this landscape by creating new entry points for attackers and accelerating the speed of phishing and extortion campaigns. Furthermore, businesses face growing risks from interconnected third-party vendors, making supply chain security as crucial as internal defenses. Consequently, ransomware has become a top priority for corporate boards, requiring security leaders to step into strategic roles. Security teams must look beyond standard prevention measures to focus on overall operational resilience. Essential practices include keeping offline backups, enforcing strict access controls, and developing thorough response plans that address executive communication and legal obligations. Ultimately, the benchmark for security success is shifting. Organizations must accept that no defense is perfect and focus instead on embedding resilience into their core strategy, measuring success by how effectively they can recover and maintain continuity when an attack inevitably occurs.


From tokenmaxxing to sovereign alpha: Who controls your AI economics?

As companies integrate artificial intelligence into their operations, a critical financial debate is emerging regarding who truly benefits from AI economics. Many enterprises find themselves trapped in "tokenmaxxing," a model where progress is measured by usage metrics like tokens and API calls, heavily favoring vendor revenue. This reliance on expensive third-party frontier models has led to severe financial consequences. For instance, Canva had to lower its revenue growth forecast due to unexpected AI input costs, and Uber reportedly exhausted its annual AI budget in a single quarter. To combat these unsustainable expenses, businesses are shifting toward "sovereign alpha." This approach prioritizes financial sovereignty, allowing organizations to retain the economic value generated by their AI tools. Achieving this control does not require completely abandoning frontier models. Instead, enterprises are adopting a hybrid strategy. They host predictable, steady-state, and sensitive workloads on internal infrastructure using open-weight models, establishing a controlled baseline. Organizations then reserve expensive, third-party frontier models for complex tasks that truly require advanced capabilities, such as deep reasoning. Ultimately, true financial sovereignty means that the enterprise, rather than the vendor, controls the cost curve, data routing, and infrastructure dependencies. By owning the decision of where each workload runs, businesses protect their profit margins and secure their long-term economic independence.

Daily Tech Digest - June 01, 2026


Quote for the day:

“The best architectures, requirements, and designs emerge from self‑organizing teams.” -- Martin Fowler

🎧 Listen to this digest on YouTube Music

▶ Play Audio Digest

Duration: 23 mins • Perfect for listening on the go.


Why AI can’t match human creative work

This Computerworld article explores why AI-generated content struggles to match the real effectiveness of human creativity, despite its overwhelming volume in today's digital marketplace. Recent industry studies in advertising and search engine optimization highlight a clear pattern: even when typical audiences cannot consciously distinguish between human and machine outputs, they consistently prefer human-created work. In advertising, human-made campaigns perform significantly better in driving sales and boosting long-term brand health because they can forge genuine emotional connections and break new ground rather than simply remixing existing data. Similarly, comprehensive data from web search results reveals that human-written articles overwhelmingly secure top rankings compared to those entirely generated by software algorithms. While automated tools have allowed an unprecedented flood of synthetic blogs, music, videos, and social media posts into the mainstream, this automated material rarely captures meaningful audience attention or real engagement. For instance, although AI-produced episodes make up a very substantial share of new podcast uploads, they currently account for less than one percent of actual listening time. Ultimately, the author concludes that while modern technology serves as a practical assistant for formatting, outlining, or brainstorming, standalone human talent remains completely indispensable for producing work that truly resonates, engages readers, and achieves tangible long-term business results.


TSA seeks biometric identity management support

The Transportation Security Administration is looking for industry assistance to modernize and maintain its internal identity management and background check systems. Through a draft work statement issued by its Enrollment Services and Vetting Programs office, the agency intends to upgrade how it processes biographical and biometric information. This initiative does not create new public-facing data collection routines; instead, it optimizes existing programs that screen pilots, commercial flight students, maritime personnel, hazardous materials drivers, and PreCheck applicants. A major focus of this comprehensive update is moving away from traditional, one-time background checks toward continuous, automated tracking. To do this, the agency plans to expand its use of the Federal Bureau of Investigation's recurrent vetting service and automate the evaluation of text-based criminal records. Additionally, the project outlines plans to integrate existing systems more deeply with Department of Homeland Security biometric databases over the next three to five years. To improve data accuracy and operational speed, the selected contractor will use data science tools, including basic machine learning, to detect data anomalies and help staff review cases more efficiently. The proposed contract includes a twelve-month base period followed by four optional one-year extensions, with all services based at the agency's Virginia headquarters.


Why ‘human in the loop’ falls short – and what to do about it

In this SiliconANGLE column, Jason Bloomberg explains why the common practice of keeping a human in the loop to oversee artificial intelligence operations is deeply flawed. While tech companies often pitch human oversight as a safety net against autonomous systems making mistakes, this method struggles to hold up under real-world pressure. On an individual level, people tend to trust automated systems too much, suffer from mental fatigue during repetitive tasks, or simply wave approvals through without checking. In corporate groups, it often leads to finger-pointing, blame-shifting, or superficial compliance. Furthermore, software systems function in mere seconds, whereas human business workflows require meetings and lengthy procedural delays, creating a massive gap in actual response times. To fix these flaws, tech providers usually suggest limiting software capabilities or building detailed tracking tools, but these heavy-handed changes slow down operations and frustrate commercial goals. Bloomberg suggests flipping the entire setup by focusing on automation in the loop instead. Rather than forcing human workers to become cogs inside an automated pipeline, software should exist purely to assist human day-to-day operations. This perspective ensures people retain ultimate responsibility, prevents software from making critical business decisions, and allows systems to grow safely without overwhelming human operators or clashing with long-term strategic plans.


Why Moving Off the Cloud Is the Easy Part and What Comes Next Is Where Things Get Hard

In this article, Eli Lahr explains that while rising costs and unpredictable performance prompt many organizations to move their digital workloads off public cloud providers, the actual migration is rarely the primary challenge. Instead, the real difficulty emerges afterward, during regular day-to-day operations. Moving away from large, centralized cloud platforms forces companies to manage internal infrastructure details that were previously handled automatically by the provider. This structural transition introduces unfamiliar administrative responsibilities, hidden technical skill gaps, and the intricate task of safely running applications across fragmented environments, including a combination of traditional on-premises hardware, local data centers, and remaining cloud components. Rather than treating this shift as a basic technology relocation, successful organizations choose to approach it as a comprehensive corporate strategy revision. They bring together their engineering, security, and financial departments early in the process to determine exactly where each distinct application belongs according to its unique performance needs, actual long-term expenses, and strict data compliance rules. Lahr recommends explicitly whiteboarding critical workloads to map out their exact structural dependencies, real monthly costs, and detailed response plans for late-night system outages or sudden traffic spikes. Ultimately, establishing precise benchmarks for baseline expenses, execution speed, and overall availability helps ensure companies achieve genuine long-term predictability.


6 critical security gaps every CISO must address

The CSO Online article highlights six essential security shortcomings that corporate security leaders need to address. First, a narrow perspective remains common; many leaders treat cybersecurity purely as a technical IT issue instead of focusing on broader business resilience and downstream operational continuity. Second, a noticeable lag exists between the swift automation used by digital attackers and the slower, more traditional response times of corporate defense teams. Similarly, security operations frequently struggle to match the rapid pace of general business changes, adoptions, and market expansions. Internal talent issues have also evolved significantly; the primary challenge is no longer just finding enough individuals to hire, but ensuring that current employees have the specific, updated skills required to handle an evolving environment. This skills gap is heavily compounded by the rapid growth of artificial intelligence, where top-down corporate initiatives and unauthorized employee tools are vastly outstripping proper security frameworks and oversight. Finally, aging tech infrastructure creates a significant vulnerability, as out-of-date systems cannot support modern security controls, leaving them exposed to easy exploitation. Rather than attempting to block every single threat, professionals are advised to use objective, risk-based prioritization to protect core company workflows and preserve long-term stability.


The Pitfalls of Defaulting to a Single Database: Why "Good Enough" Isn't Always a Good Strategy

When building software systems, it is incredibly common for modern engineering teams to default to a single database because it feels familiar, comfortable, and entirely sufficient for early stage development. However, accepting a "good enough" data architecture often introduces severe technical challenges as an organization scales. Forcing highly diverse data workloads, such as rapid transactional processing, complex analytical reporting, and unstructured document storage, into one general purpose engine creates major performance bottlenecks. No single database system can optimally handle every distinct data requirement, which forces teams to make design compromises that ultimately drag down the performance of the entire platform. Furthermore, relying on a single shared repository creates a precarious single point of failure. If that central data layer experiences an unexpected outage or suffers a performance slowdown from a poorly optimized query, every connected application and service grinds to a sudden halt. This structural centralization tightly couples unrelated services, making future software changes cumbersome and risky. Instead of settling for a monolithic database structure out of convenience, organizations achieve far greater resilience by matching distinct operational tasks with appropriate, specialized storage technologies. Choosing targeted databases minimizes resource friction, streamlines backend infrastructure management, and ensures individual services remain completely independent and stable.
The article examines how advanced artificial intelligence systems have dismantled traditional timeline safety margins for enterprise cyber defense. Historically, while AI could exploit known security flaws, it struggled to identify them independently. However, the release of Anthropic’s Claude Mythos Preview changed this dynamic by autonomously discovering thousands of zero-day vulnerabilities across major operating systems and browsers at a minimal compute cost. Consequently, the window between vulnerability disclosure and real-world exploitation has collapsed to less than ten hours, rendering traditional, calendar-based patching schedules obsolete. To address this risk, security teams are advised to replace standard severity scoring with a more dynamic, three-layer prioritization filter that integrates real-time exploitation data from federal databases and predictive scoring systems. Additionally, the proliferation of AI-driven developer platforms creates massive security risks because a single compromised host can easily expose high-value credentials across an entire corporate ecosystem. Because formal safety and authorization standards are still years away from implementation, organizations must move away from human-speed response intervals. Securing modern networks requires implementing event-driven patching for core services, conducting proactive asset discovery scans, and strictly auditing authorization boundaries to match the accelerated operational speed of automated adversaries.


Why Data “Spring Cleaning” Is Critical for AI Execution

In a Dataversity article, Michael Curry explains why enterprise data management must transition from a seasonal chore into a continuous operational discipline to support successful AI deployment. Many organizations today struggle with fragmented sources, redundant datasets, and brittle information pipelines. While these data inefficiencies were manageable during early experimental phases, they now directly block modern automation models from scaling properly. Artificial intelligence systems demand highly reliable, context-rich, and easily accessible internal records; without them, models deliver late insights or inaccurate outputs, which quickly destroys user trust. Survey data indicates that a large majority of technology leaders worry about basic quality and accessibility rather than the structural complexity of the algorithm itself. To resolve these operational bottlenecks, companies must modernize infrastructure and routinely clean their digital environments using automated classification, systematic deduplication, and regular platform profiling. Furthermore, businesses must rethink their legacy core systems, which house highly valuable data, by establishing secure, real time access instead of abandoning those platforms entirely. Ultimately, expanding these tools from isolated test pilots into broad enterprise execution requires strict data governance, clear ownership, and standardized business definitions. Because corporate information landscapes shift constantly, keeping foundations clean is a permanent obligation that directly determines if advanced tech projects succeed or stall.


Digital Twins Are Broken, AI Might Finally Fix Them

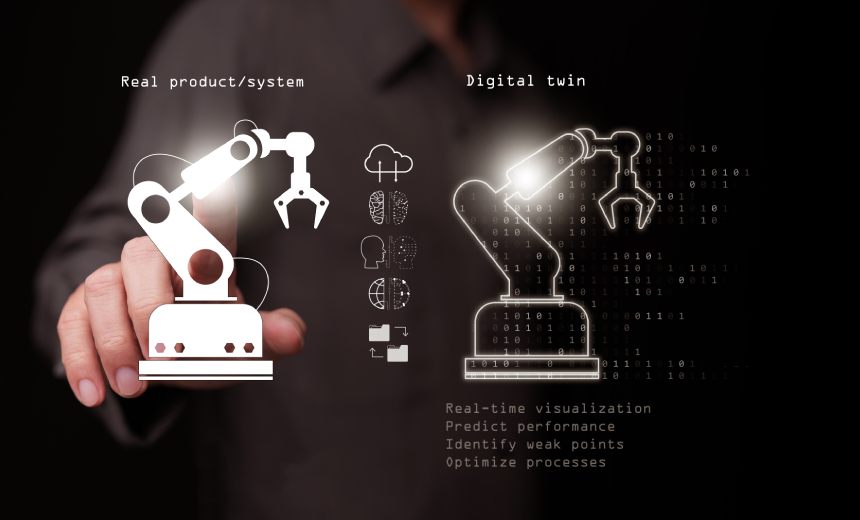
For nearly two decades, digital twins struggled to live up to their initial promises. Most companies used them merely as advanced visualization tools or static engineering models that quickly became disconnected from the physical equipment they represented. Building and maintaining these simulations was highly expensive, and fragmented data across separate corporate departments further limited their actual utility. However, the broader availability of practical artificial intelligence is changing how factories and industrial plants operate. By cleanly integrating live data feeds, modern digital twins can continuously learn from everyday operational events, environmental shifts, and machinery maintenance histories rather than remaining static. This shift allows large companies to simulate factory updates and test potential facility modifications safely without pausing active assembly lines. Beyond basic mirroring, newer setups enable virtual models to accurately predict system failures and automate adjustments directly back into real-world workflows. This ongoing progression also encourages organizations to dismantle the traditional divisions between their plant-floor operational systems and standard corporate IT networks. Ultimately, these tools working together allow manufacturers to bypass previous technical limitations. Instead of managing passive digital replicas, businesses can now run responsive systems that analyze data and optimize physical environments in real time, finally capturing real value from their data investments.


Data discovery gaps that catch enterprises off guard

In an interview with Help Net Security, Schellman CEO Avani Desai highlights a significant disconnect between what organizations believe they know about their own sensitive files and what automated discovery tools actually find. Even companies with advanced compliance dashboards and extensive data catalogs frequently overlook hidden information sitting in abandoned cloud storage, old testing setups, and legacy environments that teams assumed were turned off years ago. This lack of visibility becomes especially problematic during corporate mergers, where overlooked and heavily duplicated files can stall integration work and lead to unexpected, costly cleanups. Desai points out that while synthetic data is currently marketed heavily as a simple shortcut for basic security habits, confidential computing remains underappreciated despite its crucial ability to protect information while it is actively being processed. Interestingly, smaller firms often manage compliance and technical updates much better than large enterprises because they operate with less internal bureaucracy, fewer outdated computer systems, and far clearer lines of individual responsibility. Ultimately, mapping out company information cannot be treated as a fixed, one-off task. Desai suggests the real test of a company's readiness is knowing exactly who is responsible for continuously updating that data map after any routine system change, software update, or cloud migration takes place.