Showing posts with label Cyber Resilience. Show all posts

Daily Tech Digest - September 05, 2026


Quote for the day:

"Success... seems to be connected with action. Successful people keep moving. They make mistakes, but they don't quit." -- Conrad Hilton

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 24 mins • Perfect for listening on the go.


Why is the Cloud Changing Again?

The rise of artificial intelligence is fundamentally changing how companies store and manage their data, moving the industry away from a one-size-fits-all public cloud model. Traditional cloud setups were excellent for standard web traffic and everyday software, acting like an efficient public transit system. However, artificial intelligence requires processing massive amounts of data at high speeds, which can cause severe delays and soaring costs on shared networks. To handle these heavy workloads, businesses are shifting toward a more specialized, decentralized approach. Additionally, because artificial intelligence learns from the information it processes, companies are increasingly concerned about the security and privacy of their sensitive data. This has driven a strong movement toward bringing data back home to private, local servers. Governments are also introducing stricter privacy laws, requiring companies to keep citizen data within their own national borders rather than storing it in global facilities. As a result, organizations are adopting a flexible strategy where they use public servers for everyday tasks, regional servers to comply with local regulations, and highly secure private servers for their most valuable information. This balanced method allows businesses to use advanced systems while maintaining strict control over their security, legal compliance, and digital assets.


Keeping OT security up to date is more than patching systems

Securing operational technology (OT) in industrial environments involves much more than applying simple software updates. As cyber threats against critical infrastructure like manufacturing and energy continue to rise, protecting these systems requires a fundamentally different approach than traditional IT security. While IT focuses primarily on protecting data, OT security must balance digital defense with real-world safety and continuous physical operations. Because large industrial systems often remain in active use for several decades, they cannot always be patched or upgraded as easily as typical office computers. Rather than relying solely on specialized technical controls, organizations must deeply understand their operational dependencies and gain completely clear visibility into their connected assets and third-party vendor access. Major disruptions frequently stem from basic weaknesses, such as poor network segmentation or compromised IT environments that spill over into industrial operations, rather than highly complex, sophisticated attacks. To build truly effective defenses, companies need strong internal governance that clearly defines responsibilities across engineering, operations, and security teams. Ultimately, organizations should view OT security not just as a narrow technical issue, but as a critical element of overall business resilience. By combining standard cybersecurity practices with deep industrial expertise, companies can protect their vital operations while successfully adapting to ever-evolving security risks.


Your R&D doesn’t need to be flashy

Software development teams often feel pressure to build flashy, highly marketable features to impress users. However, the most valuable research and development work usually happens entirely behind the scenes. While a brand-new interface button might make for a great product demonstration, real long-term user satisfaction depends on foundational elements like speed, reliability, and security. When software performs exactly as expected without delays or glitches, users can focus entirely on their work rather than fighting with the tool itself. Modern professionals, such as architects or engineers, rely on software to handle increasingly complex and automated tasks. If an application fails to execute a command accurately or compromises sensitive project data, the user's trust is instantly broken, and the financial consequences can be severe. This is why development teams must prioritize secure, reliable environments over cosmetic upgrades. By analyzing how people actually use the product, developers can identify the invisible improvements that truly matter, such as open standards that allow seamless collaboration across different platforms. Ultimately, the best software acts as a quiet partner, anticipating a user's needs and handling repetitive work so they can stay immersed in their creative flow.


Querying and Performing Transactions Across Multiple Database Schemas in a Modular Monolith

In a modular monolith, assigning a dedicated database schema to each module establishes strong boundaries but introduces significant challenges for querying data and managing transactions. Because direct database access between modules violates these boundaries, traditional approaches like joining tables across different schemas or relying on single database transactions are no longer viable. To solve querying issues, developers can use several strategies. The simplest method involves direct API calls, where modules communicate through public interfaces, ensuring strict boundaries despite potential performance compromises. For scenarios requiring faster reads, teams can rely on domain events to duplicate and denormalize data across modules, though this requires managing eventual consistency. Alternatively, database views allow developers to join tables across schemas at the database level, which is particularly effective for reporting purposes. Another strong option is the Backend for Frontend pattern, where a dedicated service aggregates data from multiple modules before sending it to the user. Handling transactions across multiple schemas requires a shift away from traditional methods. Instead of relying on a single commit, systems must utilize event driven architectures and patterns like sagas. While this approach ensures loose coupling, scalability, and resilience, it also introduces complexity by requiring compensating transactions and careful error handling to maintain data consistency.


Gmail labels: Your secret weapon against inbox chaos

Gmail labels provide a powerful and flexible alternative to traditional email folders, acting more like customizable tags that allow multiple categories to be applied to a single message. By mastering these tools, users can significantly reduce inbox chaos and streamline their daily communication. A great starting point is creating and color-coding various labels, then grouping them into parent and sublabel hierarchies to maintain a consistently neat sidebar. To save time during everyday tasks, you can proactively apply these labels while composing a new email or assign them simultaneously while archiving a read message. Labels also dramatically improve your ability to find old information; typing specific label operators directly into the search bar instantly narrows down vast results. Furthermore, users can fully automate their workflow by setting up custom Gmail filters. These filters automatically apply specific labels to incoming messages based on criteria like the sender's address or specific subject line keywords. This intelligent automation allows urgent emails to stand out immediately while quietly routing less critical messages away from your main inbox view. Finally, labels can be connected to custom notification settings, ensuring you only receive alerts for the messages that truly matter. By adopting these simple strategies, anyone can transform an overwhelming inbox into a highly organized system.


When cyber capability becomes abundant: Rethinking government cyber resilience

As artificial intelligence rapidly evolves, it is fundamentally changing the economics of cybersecurity for government agencies. Historically, sophisticated cyber operations required scarce, expensive human expertise. Today, AI has significantly reduced these costs, making powerful cyber capabilities widely available to both attackers and defenders. This shift creates unprecedented challenges for government agencies, which protect critical infrastructure and systems essential to national security, public health, and emergency response. Because attackers can now discover and exploit vulnerabilities faster than organizations can fix them, government security leaders are losing confidence in traditional defensive strategies. To adapt to this new reality, governments must rethink their approach to cyber resilience across operational and institutional levels. Operationally, agencies need to move away from trying to fix every single technical flaw. Instead, they must prioritize risks based on their potential impact on public missions. A moderate vulnerability in an emergency response system matters far more than a severe flaw in a low impact network. By translating technical data into real world operational context, governments can better focus their limited resources on protecting what truly matters. Ultimately, success requires agencies to rapidly reduce their exposure, contain breaches driven by artificial intelligence, and actively shape a safer overall cyber ecosystem.


Cyber resilience in the age of AI will be decided in the boardroom

As modern business innovation speeds up due to artificial intelligence, it also provides attackers with powerful new ways to disrupt operations. Companies have spent heavily on defensive software, but having more tools often creates confusing complexity rather than clear protection. Because automated threats move faster than ever, the true test of an organization is not whether it can prevent every single incident, but how well it handles a crisis when it happens. Cybersecurity is no longer just a technical issue meant for the information technology department; it is a fundamental business challenge that belongs in the boardroom. Company leaders must understand their critical digital dependencies and how a failure would impact revenue, reputation, and daily functioning. Security should be woven into every major business decision from the start, prioritizing clear processes over having the most complicated software. True resilience relies heavily on human behavior. An organization must build a culture where employees feel safe reporting mistakes, questioning unusual requests, and practicing response plans before an actual emergency occurs. Ultimately, survival during a digital attack depends on clear communication, decisive leadership, and the ability to keep essential services running smoothly and effectively, ensuring that trust and stability are maintained alongside technological growth.


How Differential Privacy Will Transform Enterprise Data Strategy

Differential privacy is quickly moving from a theoretical concept to a critical component of enterprise data strategy. While previous methods like encryption and de-identification have struggled to protect against re-identification as data volumes grow, differential privacy offers a mathematically proven way to guarantee that an individual's data cannot be reverse-engineered from broader analytical outputs. This technique is already being used successfully by major organizations, including the U.S. Census Bureau, Apple, Google, and Microsoft, and the market is projected to expand significantly by 2030. However, many business leaders mistakenly view this technology merely as a compliance tool. Its true value lies in unlocking data utility, allowing companies to safely share information across internal departments and with partners without exposing sensitive details. To succeed, organizations must understand that differential privacy is not a simple plug-and-play product, nor can it be retrofitted easily into existing pipelines. It requires a fundamental shift in how data is processed and governed. Experts advise companies to start with a single high-value use case, such as customer analytics, and prioritize building strong central governance before focusing on the underlying tooling. Adopting this approach now gives enterprises a significant competitive advantage in responsible data strategy.


What the AI Warning Letter Completely Missed
A recent warning from major technology companies highlights that artificial intelligence will soon make cyberattacks cheaper and more common, urging immediate action to strengthen defenses. While this threat is very real, the proposed solutions overlook the most critical component: the human beings required to do the work. The industry often focuses heavily on advanced tools and theoretical scenarios while ignoring the practical reality that defense depends entirely on skilled people. Every recommendation to improve security, whether it involves fixing weaknesses, reviewing code, or deploying new software, requires a trained operator. The gap in our current readiness is not a lack of software products, but a severe shortage of equipped personnel, especially within smaller organizations and local utilities. To truly prepare for emerging threats, companies must invest directly in the workers already managing these systems, teaching them how to secure their specific environments. Furthermore, technology providers should offer concrete, direct support rather than just access to software models. Defensive tools must be judged by how effectively a small, overworked team can actually use them during an emergency. Ultimately, technology alone will not secure our infrastructure against intelligent threats. True resilience requires betting on motivated, well trained people who are ready to handle the daily work of defense.


Why digital transformations still fail

Digital transformations continue to fail largely because companies let technology, heavily promoted by consulting firms, dictate their strategy rather than focusing on actual business needs. Consultants have consistently sold identical, prepackaged systems to maximize their own profits, completely ignoring the unique requirements of each organization. This approach has resulted in massive budget overruns, delayed timelines, and overly complex systems that fail to perform as promised. Instead of redesigning their processes, companies simply moved their existing problems onto expensive cloud platforms, increasing their costs without gaining any real benefits. Now, as the industry shifts its focus toward artificial intelligence, businesses are repeating these exact same mistakes. Organizations are rushing to add artificial intelligence to everything without a clear reason, while placing unqualified staff into critical design roles. To succeed moving forward, businesses must adopt a much simpler approach. They need to stop overspending on unnecessary computing power and invest heavily in proper foundational training for their internal teams. Ultimately, technology exists solely to serve the business. Any successful change must begin by identifying clear business requirements and working backward to find the most practical, cost-effective solution, rather than blindly purchasing the most complicated or trendy new software option available today.

Daily Tech Digest - September 04, 2026


Quote for the day:

“The more you loose yourself in something bigger than yourself, the more energy you will have.” -- Norman Vincent Peale

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 25 mins • Perfect for listening on the go.


The blind spots in business continuity

Business continuity planning has fundamentally shifted from merely ensuring internal operations to mapping out external vulnerabilities. Modern organizations depend heavily on complex networks of third-party suppliers, software providers, and outsourced partners. According to a recent survey by DRI International, a significant 55% of resilience professionals identified outside vendors and supply chains as their biggest blind spot. This highlights that third-party dependency is no longer just an administrative issue but a core operational risk. Disruptions like extreme weather, cyber attacks, and technology outages frequently expose how vulnerable digital supply chains actually are. Meanwhile, 25% of respondents pointed to legacy IT systems as their primary concern. Old hardware and software are often difficult to maintain, susceptible to cyber threats, and lack the speed required for modern recovery targets. While less visible, executive succession planning also remains a quiet continuity risk. Only 14% of professionals flagged it, yet many organizations still lack clear plans for leadership continuity during a crisis. Lastly, remote work is now largely considered business as usual rather than a major blind spot. Ultimately, organizations must move beyond static supplier lists and internal recovery plans to deeply understand and protect the interconnected ecosystems they rely on daily.


Stop playing with the CISO role. Fix cybersecurity leadership

Organizations expect too much from their Chief Information Security Officers, asking them to handle complex technology while also acting as strategic business partners. This creates a structural flaw because the CISO holds accountability for cybersecurity but lacks the authority to influence broader business decisions across the company. Instead of forcing technical experts to become universal executives, companies should establish a distinct, elevated role: the Chief Security Officer. This position should sit above traditional cybersecurity and focus entirely on protecting the organization's ability to operate and compete. The CSO acts as a senior business leader with the mandate to unite conflicting departments, from legal and finance to technology and operations, ensuring that protective strategies align with business goals. Under this model, the CISO can return to their natural area of expertise. They report to the CSO and focus completely on the technical execution of security, managing architecture, engineering, and operations. This clear division of labor solves the long-standing problem of misaligned security efforts. By separating technical delivery from enterprise-level governance, businesses build a healthier management structure. Security stops being an isolated technology issue and naturally becomes a core part of how the company operates, makes decisions, and protects its future.


Risk Has No Department: Building an Enterprise-Wide Risk Ownership Culture Through ESRM

The traditional model where the security department solely owns all organizational risk is no longer sustainable. Today’s business environment is deeply interconnected, with risks spanning physical security, cybersecurity, human capital, and supply chains. As a result, Enterprise Security Risk Management (ESRM) shifts this paradigm by distributing risk ownership to the actual asset owners—the individuals who create, manage, or benefit from the assets. Instead of making all the final decisions, security professionals now act as trusted advisors who facilitate informed choices, while leaders in departments like human resources, operations, and information technology maintain ultimate accountability. To make this transition successful, organizations must establish a formal risk ownership matrix that clearly maps specific risks to their corresponding functions. This eliminates ambiguity and ensures that risk management is integrated directly into daily operational decisions rather than treated as an afterthought. Furthermore, to cement this culture of shared accountability, organizations should tie risk management effectiveness to leadership performance through key performance indicators and formal risk acceptance thresholds. Ultimately, creating an enterprise-wide risk ownership culture requires strong top-down support from executive leadership and boards of directors, ensuring that risk becomes a strategic business consideration rather than just a compliance checkbox.


How to keep your mission-critical cloud workloads running

To ensure that mission-critical cloud workloads stay online, organizations must take proactive control of their infrastructure's resilience. While cloud providers guarantee the availability of their own hardware, the responsibility for keeping specific applications running falls squarely on the user. True application resilience relies on four essential components: clustering, data replication, failover, and disaster recovery. Historically, clustering depended on expensive physical hardware, but modern software-based clusters offer the flexibility needed for hybrid and multi-cloud environments. These modern setups eliminate single points of failure by seamlessly connecting multiple systems together across varied locations. Meanwhile, keeping data consistently synchronized across these nodes through real-time replication ensures that backup systems are always fully prepared to take over. When a disruption occurs, automated failover mechanisms instantly shift workloads to standby resources without requiring manual intervention or new database builds. Furthermore, a strong disaster recovery plan incorporates geographic distance and asynchronous replication to protect against large-scale regional outages. Using these software-driven strategies not only protects against unexpected crashes but also makes planned maintenance and security patching much safer. By embracing this comprehensive approach, businesses can confidently protect their operations, prevent costly downtime, and keep their most important applications running smoothly regardless of unexpected external failures.


Who gets to decide? The CIO and the new architecture of enterprise authority

As artificial intelligence evolves from merely recommending actions to independently executing them, organizations face a critical new challenge. The core issue is no longer just what the technology can do, but who, or what, has the authority to do it. This creates an enterprise authority gap, where intelligent systems act faster than businesses can define or control their boundaries. Because modern AI interprets intent rather than just following rigid rules, it can easily cross organizational boundaries and create unintended risks if decision rights remain ambiguous. To safely manage this shift, Chief Information Officers must lead the creation of a new enterprise authority architecture. This approach requires businesses to clearly define the desired decision before selecting the technology and firmly separate a system's capability from its actual authority. Furthermore, this delegated authority must be technically enforceable through clear limits, approval gates, and continuous monitoring. Leaders also need to evaluate the true economic cost of autonomous decisions, accounting for oversight, error correction, and potential harm. Ultimately, the new mandate for technology leaders is not about maximizing how much artificial intelligence is deployed. Instead, success depends on how wisely and safely the enterprise distributes decision-making authority to these intelligent systems.


Large Enterprises Targeted in Fake Merger & Acquisition Scams

Cybercriminals are using highly sophisticated social engineering tactics to steal massive sums of money from large enterprises through fake merger and acquisition (M&A) schemes. In a recently uncovered campaign dubbed "Phantom Deal," attackers thoroughly researched mid-level employees who might be involved in corporate dealmaking. The scammers then impersonated company executives and external auditors, crafting a plausible but fake acquisition narrative based on real corporate history. To keep the target isolated, the attackers issued fake non-disclosure agreements and insisted all communication remain strictly on personal channels like WhatsApp, keeping the interactions hidden from corporate security monitors. The ultimate goal was to trick the employee into authorizing a massive wire transfer to overseas accounts. Security experts note that these scammers gather extensive, publicly available details—such as job roles and company history—to make their ruses remarkably convincing. However, organizations can protect themselves by emphasizing strict adherence to internal verification and payment controls. Employees should be trained to question whether the requested process is legitimate, rather than just trusting the identity presented on a screen. When something feels off, the safest action is to immediately halt the process and report the suspicious request through official channels.


Enterprise architecture and software architecture as the core CTO model

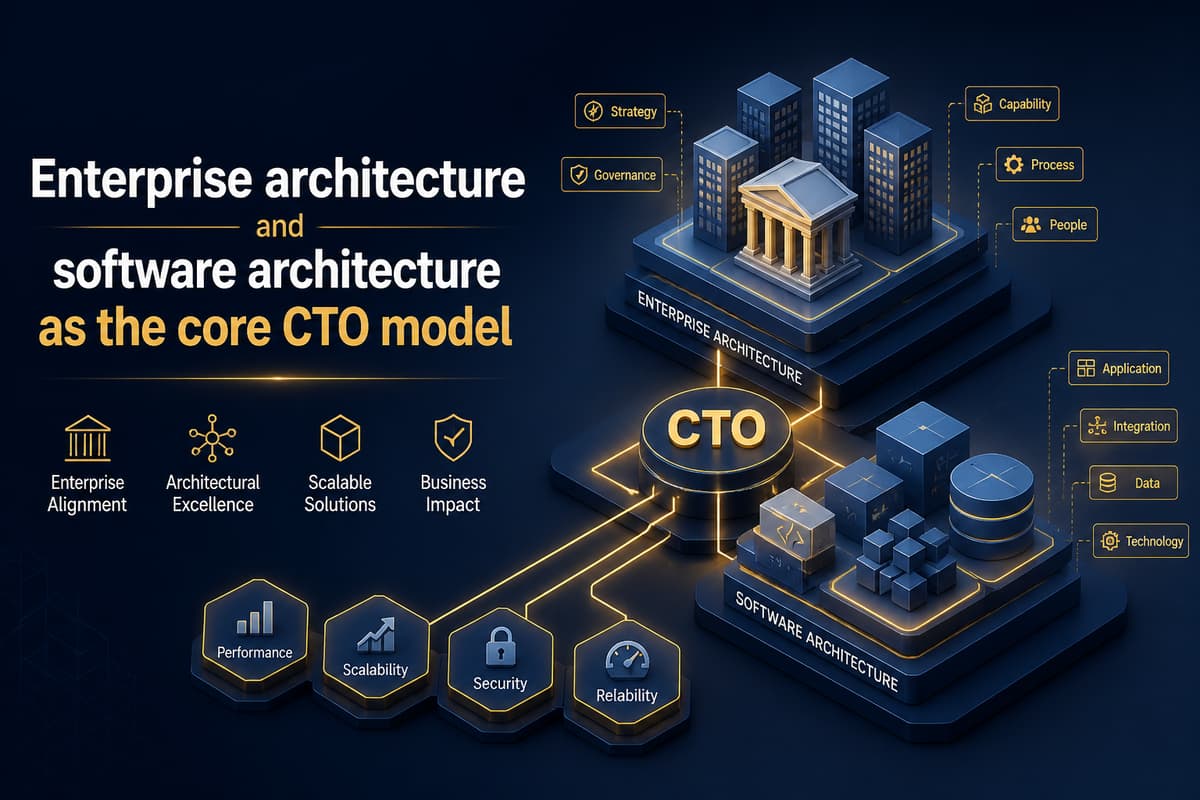
Enterprise architecture and software architecture are not just documentation tasks; they are essential frameworks that allow technology leaders to manage change safely and efficiently. Enterprise architecture maps business capabilities directly to applications, data, and risks, acting as the clear rulebook for technological decisions. Meanwhile, software architecture translates those rules into constraints that development teams can actually code against, ensuring systems perform well under stress and failure. Relying on one without the other leads to immediate problems. Enterprise architecture alone becomes an ignored catalog, while software architecture alone creates disorganized local successes that fail to serve the broader business. To succeed, leaders must adopt a continuous loop of deciding, designing, delivering, and defending their architecture choices. While artificial intelligence speeds up development, it also increases the risk of deploying bad systems quickly, making strong architectural guardrails more critical than ever. Effective leaders treat architecture like a living product rather than a static diagram. They build this practice systematically, starting with a thirty-day inventory of vital systems, followed by a ninety-day framework of automated policies, and finally establishing long-term guiding principles. Ultimately, practical architecture directly improves the four outcomes that matter most to any business: delivery speed, operational costs, system risk, and developer retention.


From IT Security to Business Strategy: Navigating Cyber Risk in Digital India

As India rapidly expands its digital economy, managing cyber risk has fundamentally shifted from a narrow technical concern into a core business strategy. For many years, organizations treated cybersecurity merely as an IT function focused on defending perimeters and protecting data. However, the modern digital landscape, fueled by cloud adoption, artificial intelligence, and complex regulatory changes like the DPDP Act, demands a far more holistic approach. Today, business leaders must carefully balance rapid technological innovation with strong governance, compliance, and resilience to maintain stakeholder trust. Cybersecurity is no longer just about preventing unauthorized access; it is about ensuring that critical operations remain consistently available and that users feel psychologically safe when interacting with digital services. Building this digital trust requires enterprises to integrate risk management across their entire ecosystem, including third party vendor networks and evolving AI models. By shifting their perspective, executives can transform security from a defensive cost center into a strategic enabler of sustainable growth. This proactive mindset allows companies to navigate evolving regulatory obligations effectively while adapting their infrastructure to meet user needs at lightning speed. Ultimately, treating cyber risk as a central business priority ensures that organizations can innovate responsibly and thrive securely in India’s dynamic digital future.


Why cyber resilience fails: 5 obstacles holding orgs back

While most organizations want to achieve strong cyber resilience to withstand attacks and keep operations running, the reality often falls short of their goals. Even when leadership provides adequate support and resources, resilience efforts frequently break down in the space between broad strategy and daily execution. Several major obstacles consistently hold companies back from properly securing their systems. Chief among these are mounting technical debt, persistent shortages in skilled security professionals, and increasingly complex identity risks. When older systems are neglected or vulnerabilities go unreviewed, they quietly compound into technical debt. This creates dangerous operational blind spots that attackers can easily exploit. Furthermore, without enough trained staff to manage these environments, security teams struggle to keep pace with evolving threats. The rapid expansion of user identities across different platforms only adds to the challenge, making it difficult to control who has access to sensitive information. Ultimately, true resilience is not just an idealistic goal or a passing project. It requires bridging the gap between management intentions and actual daily operations. To succeed, businesses must actively address these practical challenges, paying down their technical debt and heavily investing in their workforce to ensure that protective measures are flawlessly integrated into everyday tasks.


The next cyber crisis is already taking shape

The financial sector is currently facing an emerging cybersecurity crisis driven by the convergence of two major technological shifts. First, rapid advances in artificial intelligence are drastically lowering the barriers to entry for threat actors. Cybercriminals can now use sophisticated AI tools to quickly identify hidden vulnerabilities, develop exploits, and launch attacks at an unprecedented scale, making threats faster and harder to predict. Second, banks are undergoing a massive, complex transition to post-quantum cryptography to protect their infrastructure against future computing power that could easily break current encryption standards. Because modern banking relies entirely on deeply embedded cryptographic systems, updating them requires years of careful planning. Unlike the Y2K bug, this transition lacks a strict universal deadline, which can dangerously lead to delayed action and increased exposure for institutions. Together, these dual challenges mean that traditional security playbooks are no longer sufficient. Simply recovering systems after a breach is inadequate when facing AI-accelerated attacks and disruptive infrastructure overhauls. Instead, organizations must embrace a strategy of managed degradation. True enterprise resilience now requires maintaining core financial operations and preserving customer trust even while systems are actively compromised. Financial institutions must proactively address this growing imbalance and begin their extensive security upgrades before time runs out.