Showing posts with label wearables. Show all posts

Daily Tech Digest - October 24, 2026

Quote for the Day
“Design is really an act of communication.”
— Don Norman
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Midmarket AI gap: Small IT teams are being asked to do enterprise-sized jobs

Small and mid-sized companies stand to gain a massive productivity boost from artificial intelligence, but a critical gap is emerging in their ability to secure it. While AI allows leaner teams to operate at the scale of larger competitors, technology adoption is moving at an enterprise pace while IT capacity remains limited to a midmarket budget. Surveys reveal that many organizations lack the dedicated staff or specific tools to monitor shadow AI usage, particularly across mobile devices and software-as-a-service connections. As a result, written safety policies often serve as mere liability documents rather than enforceable technical controls. Without proper governance, businesses face heightened risks of data leaks and compliance violations. Because midmarket IT departments are already stretched thin managing daily operations, expecting them to handle complex AI governance alone is unrealistic. Instead of blocking AI projects entirely—and surrendering the competitive edge it offers—smaller organizations are encouraged to partner with managed service providers. These partners offer the essential continuous monitoring, security enforcement, and round-the-clock support required to adopt AI safely.

Read Original Article →

Attackers Aren’t Looking For Dumb Employees. They’re Looking For Busy Ones

Attackers are increasingly exploiting human psychology rather than technical flaws, targeting busy employees instead of uninformed ones. A notable example involves a contractor who, exhausted by a barrage of multi-factor authentication requests and a spoofed IT message, simply approved a login to stop the notifications. This granted the hacker extensive access without requiring specialized technical knowledge. Traditional security training assumes that educating employees about phishing will prevent these breaches, but generic annual modules fail to address the high-pressure, fast-paced nature of modern work. When policies create too much friction, employees prioritize deadlines over security, often taking shortcuts like pasting sensitive data into unapproved artificial intelligence tools to finish tasks faster. To combat this, companies need to rethink their approach by making secure behavior the easiest option. Security leaders should reduce process friction, integrate training directly into daily workflows, provide role-specific guidance, and foster a culture where reporting mistakes is encouraged rather than punished. Ultimately, building a resilient security culture means designing systems that anticipate human behavior and accommodate it, rather than expecting perfection.

Read Original Article →
Article Thumbnail

A Framework For Evaluating Application Ownership

When managing software, many companies make the mistake of leaving mature applications in the hands of their core engineering team. Over time, tasks like bug fixes and security patches slowly drain away the capacity of top talent. This creates a significant opportunity cost, preventing senior engineers from focusing on modernization, strategy, and complex problem-solving. To solve this, leaders can use a three-step framework to determine who should really maintain an application. First, plot each application on a grid based on its need for core engineering expertise versus the operational friction it causes. This helps decide whether to keep, transition, resolve, or modernize the software. Second, assess the business criticality of the application to understand the risks of handing it off and the necessary service-level agreements. Finally, evaluate the transition economics to confirm whether the benefits outweigh the costs and effort. Using tools like artificial intelligence can speed up the knowledge transfer process, making it easier to hand maintenance to another internal team or an external partner, ultimately freeing up core engineers for high-value work.

Read Original Article →

Quantum Computing’s Next Phase May Be Driven by Compounding Breakthroughs

The global quantum computing industry is entering a critical phase defined by rapid and compounding breakthroughs. Although current conversations often highlight short-term market cooling and geopolitical supply chain concerns, the broader trajectory remains highly optimistic. Stakeholders expect that the time between major milestones will steadily shrink over the next few years. The drive toward fault-tolerant quantum computing—fueled by progress in logical qubits and error correction—is a major focus, as it promises to unlock practical use cases in drug discovery, cryptography, and materials science. Furthermore, the deep convergence of artificial intelligence and quantum technology is expected to create a powerful super-cycle, accelerating research and development. To maintain this momentum, companies must transition from hardware-focused delivery models to sustainable, service-based approaches like compute-as-a-service on cloud platforms. While researchers remain cautious about specific technical hurdles, entrepreneurs and policymakers continue to push for sustained support and cross-industry collaboration. Ultimately, these overlapping innovations aim to bridge the gap between theoretical physics and real-world commercial applications.
Read Original Article →
Article Thumbnail

Multi-Cloud FinOps: An Engineering Framework for Cross-Cloud Cost Optimization

While multi-cloud architectures offer flexibility and better geographic reach, they often introduce hidden costs tied to data movement across provider boundaries. A major source of this expense is egress fees—charges incurred when data leaves a provider's network. In many cases, published transfer rates are just the baseline; actual expenses surge due to hidden charges like cross-zone routing and gateway processing. These expenses accumulate silently and are rarely identified before deployment. The core issue lies in the system architecture rather than negotiated provider rates. Egress costs are fundamentally driven by service placement decisions and how frequently systems communicate across clouds. Instead of reacting to high bills with post-production tuning, organizations must treat cost efficiency as a structural property during the design phase. Adopting an engineering framework like Backend FinOps allows teams to integrate cost governance directly into their workflows. Strategies like replacing continuous data transfer with scheduled synchronization and processing data near its source can significantly reduce expenses without degrading performance, proving that architectural choices are the most effective lever for cost control.

Read Original Article →
Article Thumbnail

How long until wearable brain‑computer interfaces become mainstream?

The article explains that wearable brain‑computer interfaces are advancing quickly, but mainstream adoption is still years away because the technology remains immature and difficult to validate outside controlled research settings. Medical BCIs, which are mostly implantable, already help patients with paralysis communicate or control devices, but consumer wearables face tougher challenges. They rely on weak, noisy brain signals that vary widely between people, environments, and even times of day, making reliability a major hurdle. Companies often market these devices based on small, supervised studies that don’t reflect real‑world use. The article notes that proving consistent benefit is harder than proving basic functionality, especially for neurofeedback systems that require sustained user effort. Neuromodulation devices raise safety and regulatory questions, while passive BCIs introduce concerns about mental privacy as brain signals are combined with contextual data. The author argues that large‑scale, long‑term studies and strong ethical frameworks are essential. With proper investment in validation and ecosystem development, meaningful mainstream progress may be possible within five to ten years.

Read Original Article →
Article Thumbnail

The Connection Between IT Efficiency, Cybersecurity, and Device Management

The article explains that IT efficiency and cybersecurity are tightly connected, and that the foundation for both is something deceptively simple: accurate hardware records. It uses the example of a forgotten laptop with an active VPN certificate to show how easy it is for device inventories to drift from reality. When records decay, every security control built on top of them becomes weaker, because teams cannot patch, monitor, or retire devices they don’t know exist. Unmanaged machines become quiet risks — unenrolled, unscanned, and unmonitored — making them ideal footholds for attackers. The article stresses that patching programs and vulnerability prioritization depend on knowing exactly which devices are in use and who owns them. Good records also make routine work smoother, from onboarding and offboarding to audits and renewals. The core message is steady: treating device inventories as a security control, not clerical work, reduces surprises, shrinks the attack surface, and gives IT teams evidence‑based footing for both efficiency and risk reduction.
Read Original Article →
Article Thumbnail

Exposed to PHP2Shell? Cyber Experts Weigh in With Advice

Organizations are struggling to patch the new "PHP2Shell" vulnerabilities as fast as attackers are exploiting them, with experts noting millions of exploitation attempts within hours of the flaw's disclosure. The slow response stems from the fact that patching these specific vulnerabilities is rarely as simple as clicking an update button. PHP is embedded not just in websites, but also in storage devices, physical access-control systems, and cameras, making it difficult to detect and inventory. Upgrading older, unsupported versions of PHP often requires rewriting applications, which heavily disrupts operations for both large and small enterprises. For companies unable to completely overhaul their software, experts suggest turning off vulnerable systems temporarily or applying backported patches provided by specific operating systems like Ubuntu. Some security leaders also recommend disabling certain session upload features as an interim defense measure. Ultimately, managing this threat requires a comprehensive inventory of all PHP deployments, careful coordination with third-party vendors, and targeted updates rather than assuming a single standard patch will resolve the exposure.

Read Original Article →
Article Thumbnail

Matrix gains ground in Europe’s public sector — but replacing Teams is another matter

Across Europe's public sector, government agencies are increasingly adopting Matrix-based messaging tools to enhance digital sovereignty and reduce reliance on major US technology suppliers. Matrix is an open messaging standard for decentralized communication that gives organizations greater control over their sensitive data. High-profile early adopters include the French and German governments, and the European Commission recently rolled out a Matrix-based app for thousands of employees to ensure business continuity and resilience. Similarly, Swedish agencies are exploring how to link these open platforms so different government departments can securely communicate without needing centralized third-party software. Despite this growing interest, Matrix applications are not expected to entirely replace established platforms like Microsoft Teams overnight. Implementing sovereign communications involves navigating complex change management, employee resistance, and significant prior investments in commercial cloud solutions. Some agencies lack the resources to maintain open-source platforms and run them alongside existing applications rather than committing to a full switch. Ultimately, moving to sovereign digital infrastructure will be a gradual, long-term strategic transition rather than an immediate substitution.

Read Original Article →
Article Thumbnail

Don’t assume resilience from your cloud provider

A recent Google Cloud outage in London highlights a critical reality for businesses: cloud infrastructure will inevitably fail, and the responsibility for keeping applications running rests with the enterprise, not just the provider. While major platforms offer excellent building blocks like multiple regions and automated recovery tools, simply moving an application to the cloud does not automatically make it resilient. Organizations often mistakenly believe they have solved the problem, when they may have only relocated their single point of failure. Modern applications rely on complex, deeply interconnected dependency chains including managed services, third-party APIs, and identity platforms. A failure in just one area can trigger widespread disruptions across seemingly unrelated services. To build true resilience, companies must map out these dependencies, classify workloads by business criticality, and heavily invest in regular, controlled failure testing. Rushing into multicloud setups often adds expensive complexity rather than solving the problem. Ultimately, robust architecture requires deliberate financial investment and a clear understanding that the business must own its operational design.

Read Original Article →

Daily Tech Digest - May 10, 2024

Optimize AI at Scale With Platform Engineering for MLOps

Just as platform engineering emerged from the DevOps movement to streamline app development workflows, so too must platform engineering streamline the workflows of MLOps. To achieve this, one must first recognize the fundamental differences between DevOps and MLOps. Only then can one produce an effective platform engineering solution for ML engineers. To enable AI at scale, enterprises must commit to developing, deploying and maintaining platform engineering solutions that are purpose-built for MLOps. Whether due to data governance requirements or practical concerns about moving vast volumes of data over significant geographical distances, MLOps at scale require enterprises to utilize a spoke-and-wheel approach. Model development and training occurs centrally, trained models are distributed to edge locations for fine-tuning on local data, and fined-tuned models are deployed close to where end users interact with them and the AI applications they leverage. ... Enterprises should hire engineers with MLOps experience to fill platform engineering roles appropriately. According to research from the World Economic Forum, AI is projected to create around 97 million new jobs by 2025. 


The Blockchain Integrity Act: Latest Attempt to Restrict Financial Privacy

In short, the Blockchain Integrity Act would first establish a two‐​year moratorium that prohibits financial institutions from going anywhere near cryptocurrency that has been routed through a mixer. With that two‐​year moratorium in place, the Blockchain Integrity Act would then require the Department of the Treasury to study how people use mixers and other privacy‐​enhancing technology. ... The second half of the legislation—the request for a study—is less concerning if it’s considered alone and without the surrounding context. The request seeks information regarding different types of privacy‐​enhancing technology, illicit and legitimate use history, and an analysis of what the government’s role might be here. Those are all reasonable inquiries. Again, without additional context, it’s an encouraging sign that Representative Casten is interested in learning more about how this technology is used for both better and worse. Yet what isn’t encouraging is that Representative Casten introduced the bill saying that “until we’ve studied [privacy enhancing technologies like mixers] and have a good audit trail, the presumption should be that these are money laundering channels.”


Some strategies for CISOs freaked out by the specter of federal indictments

“Some CISOs feel like they’re the frog that’s in the water that’s starting to boil, and they don’t like that feeling, and they want to make sure that they’re doing the right things to navigate that heat,” Sullivan said during a panel discussion, “CISOs Under Indictment: Case Studies, Lessons Learned, and What’s Next,” at this year’s RSA Conference. The panel of current and former CISOs emphasized that in this environment, CISOs need to document their roles and responsibilities, involve the right people in incident response and decision-making processes, and have the courage to stand up for their convictions to minimize the risk that they will face the same fates as Sullivan and Brown. ... “The heat is up because the reality is you’ve got these entities in government who are responding to a huge rise in cybercrime in a way that no one can hide. It’s not like in the old days when if an incident happened, most people wouldn’t notice when stuff happens. Today, the whole world notices,” he said. Blauner’s bottom-line advice to CISOs to protect themselves is to “take a look at every governance document you’ve got and really make sure that it’s crystal clear about roles and responsibilities, especially around who makes risk management decisions.”


Wearable devices can now harvest our brain data. Australia needs urgent privacy reforms

In a background paper published earlier this year, the Australian Human Rights Commission identified several risks to human rights that neurotechnology may pose, including rights to privacy and non-discrimination. Legal scholars, policymakers, lawmakers and the public need to pay serious attention to the issue. The extent to which tech companies can harvest cognitive and neural data is particularly concerning when that data comes from children. This is because children fall outside of the protection provided by Australia’s privacy legislation, as it doesn’t specify an age when a person can make their own privacy decisions. The government and relevant industry associations should conduct a candid inquiry to investigate the extent to which neurotechnology companies collect and retain this data from children in Australia. The private data collected through such devices is also increasingly fed into AI algorithms, raising additional concerns. These algorithms rely on machine learning, which can manipulate datasets in ways unlikely to align with any consent given by a user.


Cloud environments beyond the Big Three

The resurgence and innovation in edge computing and on-premises technology further support the trend toward diversification as data generation and consumption locations continue to spread geographically. ... Edge computing addresses these limitations by processing data closer to where it is generated. This drastically reduces latency and enhances the user experience in applications such as IoT, retail tech, and smart manufacturing. Although many consider edge computing to be small devices, it also includes entire data centers and smaller server installations that exist to serve a specific business location. Many enterprises don’t see the wisdom of sending their data on a 2,000-mile round trip to the point of presence for a public cloud provider, which happens more often than we understand. Additionally, although the cloud offers good scalability and flexibility, concerns over data sovereignty and security continue to push certain industries towards on-premises solutions. Sensitive data and critical applications in sectors such as finance, government, and healthcare often necessitate keeping data in-house under strict regulatory frameworks.


Controlling chaos using edge computing hardware: Digital twin models promise advances in computing

Using machine learning tools to create a digital twin (a virtual copy) of an electronic circuit that exhibits chaotic behavior, researchers found that they were successful at predicting how it would behave and at using that information to control it. Many everyday devices, like thermostats and cruise control, utilize linear controllers—which use simple rules to direct a system to a desired value. Thermostats, for example, employ such rules to determine how much to heat or cool a space based on the difference between the current and desired temperatures. Yet because of how straightforward these algorithms are, they struggle to control systems that display complex behavior, like chaos. As a result, advanced devices like self-driving cars and aircraft often rely on machine learning-based controllers, which use intricate networks to learn the optimal control algorithm needed to operate efficiently. However, these algorithms have significant drawbacks, the most demanding of which is that they can be extremely challenging and computationally expensive to implement.


Digital recreations of dead people need urgent regulation, AI ethicists say

Such services, which are already technically possible to create and legally permissible, could let users upload their conversations with dead relatives to “bring grandma back to life” in the form of a chatbot, researchers from the University of Cambridge suggest. They may be marketed at parents with terminal diseases who want to leave something behind for their child to interact with, or simply sold to still-healthy people who want to catalogue their entire life and create an interactive legacy. But in each case, unscrupulous companies and thoughtless business practices could cause lasting psychological harm and fundamentally disrespect the rights of the deceased, the paper argues. “Rapid advancements in generative AI mean that nearly anyone with internet access and some basic knowhow can revive a deceased loved one,” said Dr Katarzyna Nowaczyk-BasiÅ„ska, one of the study’s co-authors at Cambridge’s Leverhulme centre for the future of intelligence (LCFI). “This area of AI is an ethical minefield. It’s important to prioritise the dignity of the deceased, and ensure that this isn’t encroached on by financial motives of digital afterlife services, for example.”


How To Take The A-I-M Approach To Leadership

I like to break down the concept of taking aim into three components, which I call the A-I-M approach: appreciation, imagination and motivation. The common thread across all three of these principles is communication—and leaders cannot be effective without it. Showing genuine gratitude is a foundational aspect of effective leadership. Expressing heartfelt encouragement demonstrates empathy and humility. And this simple show of appreciation directly benefits the organization by motivating employees to continue contributing to the company’s success and nurturing their loyalty. ... A leader’s job is not to be the author of all ideas but to inspire team members to tap into their imaginations and present fresh approaches to solving problems, delivering solutions and communicating with clients.  ... One of the responsibilities of a leader is to understand what moves their teams into action. As author and leadership coach John Maxwell famously wrote, “A leader is great not because of his or her power, but because of his or her ability to empower others.” I call that motivation.


Colorado AI legislation further complicates compliance equation

CIOs might struggle with the bill’s language because the focus is on whether AI — in any form — helps make “consequential decisions” that could impact Colorado residents. The bill defines consequential decision as being any decision “that has a material legal or similarly significant effect on the provision or denial to any consumer,” which includes educational enrollment, employment or employment opportunity, financial or lending service, healthcare services, housing, insurance, or a legal service. ... Another provision could prove onerous for CIOs who do not have full knowledge of every AI implementation in use in their environment, as it requires companies to make “a publicly available statement summarizing the types of high-risk systems that the deployer currently deploys, how the deployer manages any known or reasonably foreseeable risks of algorithmic discrimination that may arise from deployment of each of these high-risk systems and the nature, source, and extent of the information collected and used.” ... One especially dicey area in the legislation that should concern CIOs is when AI — especially generative AI — acts on its own. 


AI's Game-Changing Role in Finance and Audit Processes

Auditors can face several risks when using AI. These risks include over-reliance on AI-generated insights, potential biases and quality issues from incomplete or poor-quality data andcybersecurity threats such as consequences in terms of hacking of the confidential data from the AI websites. Thus, it is necessary to ensure compliance and implement safeguarding measures. Following are some of the possible measures that can be implemented to mitigate the above-mentioned risks. Human judgement: While AI is a great tool to be incorporated in the professional world to help auditors and organisations streamline their existing processes, AI work on standard algorithm that can’t be customised on case-to-case basis. Therefore, to ensure the accuracy of the results, a human review can be placed in practice to review from and validate the accuracy of output results. Updating back-end algorithms: The better the algorithms, the better the results. Regular updates to the back-end algorithms can yield more accurate and improved outputs, adapting to changing scenarios and data formats, ultimately mitigating the risk of incorrect or inaccurate results..


Quote for the day:

"Don't find fault, find a remedy." -- Henry Ford

Daily Tech Digest - March 18, 2024

Generative AI will turn cybercriminals into better con artists. AI will help attackers to craft well-written, convincing phishing emails and websites in different languages, enabling them to widen the nets of their campaigns across locales. We expect to see the quality of social engineering attacks improve, making lures more difficult for targets and security teams to spot. As a result, we may see an increase in the risks and harms associated with social engineering – from fraud to network intrusions. ... AI is driving the democratisation of technology by helping less skilled users to carry out more complex tasks more efficiently. But while AI improves organisations’ defensive capabilities, it also has the potential for helping malicious actors carry out attacks against lower system layers, namely firmware and hardware, where attack efforts have been on the rise in recent years. Historically, such attacks required extensive technical expertise, but AI is beginning to show promise to lower these barriers. This could lead to more efforts to exploit systems at the lower level, giving attackers a foothold below the operating system and the industry’s best software security defences.


Get the Value Out of Your Data

A robust data strategy should have clearly defined outcomes and measurements in place to trace the value it delivers. However, it is important to acknowledge the need for flexibility during the strategic and operational phases. Consequently, defining deliverables becomes crucial to ensure transparency in the delivery process. To achieve this, adopting a data product approach focused on iteratively delivering value to your organization is recommended. The evolution of DevOps, supported by cloud platform technology, has significantly improved the software engineering delivery process by automating development and operational routines. Now, we are witnessing a similar agile evolution in the data management area with the emergence of DataOps. DataOps aims to enhance the speed and quality of data delivery, foster collaboration between IT and business teams, and reduce the associated time and costs. By providing a unified view of data across the organization, DataOps enables faster and more confident data-driven decision-making, ensuring data accuracy, up-to-datedness, and security. It automates and brings transparency to the measurements required for agile delivery through data product management.


Exposure to new workplace technologies linked to lower quality of life

Part of the problem is that IT workers need to stay updated with the newest tech trends and figure out how to use them at work, said Ryan Smith, founder of the tech firm QFunction, also unconnected with the study. The hard part is that new tech keeps coming in, and workers have to learn it, set it up, and help others use it quickly, he said. “With the rise of AI and machine learning and the uncertainty around it, being asked to come up to speed with it and how to best utilize it so quickly, all while having to support your other numerous IT tasks, is exhausting,” he added. “On top of this, the constant fear of layoffs in the job market forces IT workers to keep up with the latest technology trends in order to stay employable, which can negatively affect their quality of life.” ... “As IT has become the backbone of many businesses, that backbone is key to the businesses operations, and in most cases revenue,” he added. “That means it’s key to the business’s survival. IT teams now must be accessible 24 hours a day. In the face of a problem, they are expected to work 24 hours a day to resolve it. ...”


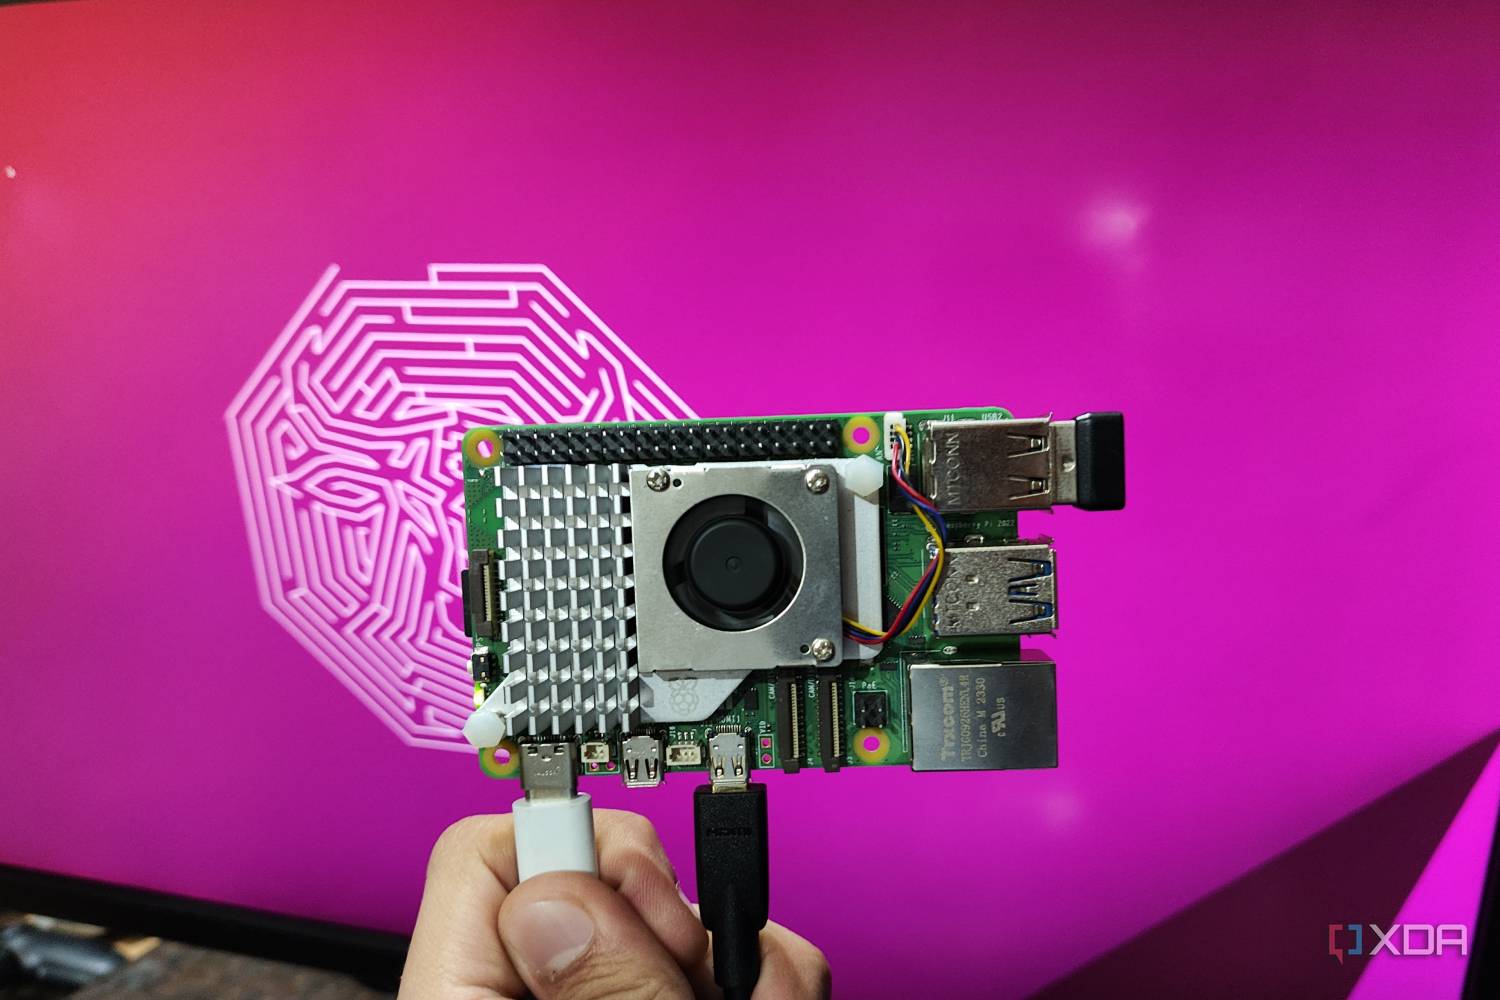
6 best operating systems for Raspberry Pi 5

Even though it has been nearly seven years since Microsoft debuted Windows on Arm, there has been a noticeable lack of ARM-powered laptops. The situation is even worse for SBCs like the Raspberry Pi, which aren’t even on Microsoft’s radar. Luckily, the talented team at WoR project managed to find a way to install Windows 11 on Raspberry Pi boards. ... Finally, we have the Raspberry Pi OS, which has been developed specifically for the RPi boards. Since its debut in 2012, the Raspberry Pi OS (formerly Raspbian) has become the operating system of choice for many RPi board users. Since it was hand-crafted for the Raspberry Pi SBCs, it’s faster than Ubuntu and light years ahead of Windows 11 in terms of performance. Moreover, most projects tend to favor Raspberry Pi OS over the alternatives. So, it’s possible to run into compatibility and stability issues if you attempt to use any other operating system when attempting to replicate the projects created by the lively Raspberry Pi community. You won’t be disappointed with the Raspberry Pi OS if you prefer a more minimalist UI. That said, despite including pretty much everything you need to use to make the most of your RPi SBC, the Raspberry Pi OS isn't as user-friendly as Ubuntu.


Speaking without vocal cords, thanks to a new AI-assisted wearable device

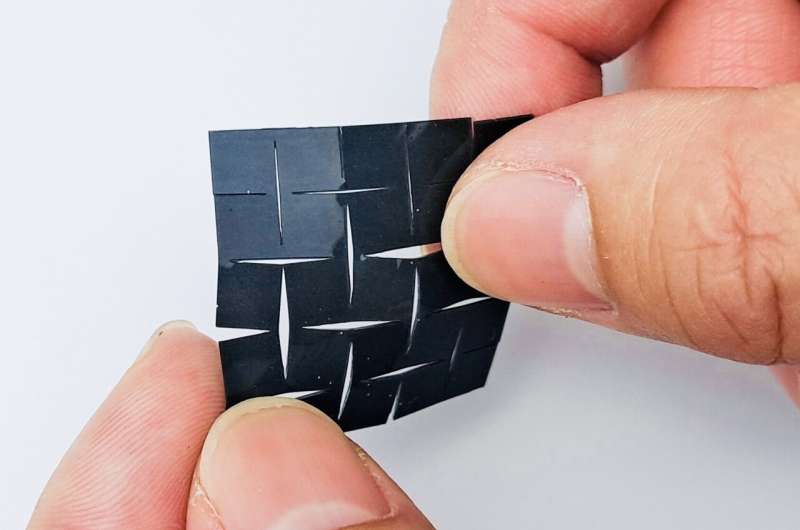
The breakthrough is the latest in Chen's efforts to help those with disabilities. His team previously developed a wearable glove capable of translating American Sign Language into English speech in real time to help users of ASL communicate with those who don't know how to sign. The tiny new patch-like device is made up of two components. One, a self-powered sensing component, detects and converts signals generated by muscle movements into high-fidelity, analyzable electrical signals; these electrical signals are then translated into speech signals using a machine-learning algorithm. The other, an actuation component, turns those speech signals into the desired voice expression. The two components each contain two layers: a layer of biocompatible silicone compound polydimethylsiloxane, or PDMS, with elastic properties, and a magnetic induction layer made of copper induction coils. Sandwiched between the two components is a fifth layer containing PDMS mixed with micromagnets, which generates a magnetic field. Utilizing a soft magnetoelastic sensing mechanism developed by Chen's team in 2021, the device is capable of detecting changes in the magnetic field when it is altered as a result of mechanical forces—in this case, the movement of laryngeal muscles.

We can’t close the digital divide alone, says Cisco HR head as she discusses growth initiatives

At Cisco, we follow a strengths-based approach to learning and development, wherein our quarterly development discussions extend beyond performance evaluations to uplifting ourselves and our teams. We understand that a one-size-fits-all approach is inadequate. To best play to our employees' strengths, we have to be flexible, adaptable, and open to what works best for each individual and team. This enables us to understand individual employees' unique learning needs, enabling us to tailor personalised programs that encompass diverse learning options such as online courses, workshops, mentoring, and gamified experiences, catering to diverse learning styles. As a result, our employees are energized to pursue their passions, contributing their best selves to the workplace. Measuring the quality of work, internal movements, employee retention, patents, and innovation, along with engagement pulse assessments, allows us to gauge the effectiveness of our programs. When it comes to addressing the challenge of retaining talent, it's essential for HR leaders to consider a holistic approach. 


Vector databases: Shiny object syndrome and the case of a missing unicorn

What’s up with vector databases, anyway? They’re all about information retrieval, but let’s be real, that’s nothing new, even though it may feel like it with all the hype around it. We’ve got SQL databases, NoSQL databases, full-text search apps and vector libraries already tackling that job. Sure, vector databases offer semantic retrieval, which is great, but SQL databases like Singlestore and Postgres (with the pgvector extension) can handle semantic retrieval too, all while providing standard DB features like ACID. Full-text search applications like Apache Solr, Elasticsearch and OpenSearch also rock the vector search scene, along with search products like Coveo, and bring some serious text-processing capabilities for hybrid searching. But here’s the thing about vector databases: They’re kind of stuck in the middle. ... It wasn’t that early either — Weaviate, Vespa and Mivlus were already around with their vector DB offerings, and Elasticsearch, OpenSearch and Solr were ready around the same time. When technology isn’t your differentiator, opt for hype. Pinecone’s $100 million Series B funding was led by Andreessen Horowitz, which in many ways is living by the playbook it created for the boom times in tech.


The Role of Quantum Computing in Data Science

Despite its potential, the transition to quantum computing presents several significant challenges to overcome. Quantum computers are highly sensitive to their environment, with qubit states easily disturbed by external influences – a problem known as quantum decoherence. This sensitivity requires that quantum computers be kept in highly controlled conditions, which can be expensive and technologically demanding. Moreover, concerns about the future cost implications of quantum computing on software and services are emerging. Ultimately, the prices will be sky-high, and we might be forced to search for AWS alternatives, especially if they raise their prices due to the introduction of quantum features, as it’s the case with Microsoft banking everything on AI. This raises the question of how quantum computing will alter the prices and features of both consumer and enterprise software and services, further highlighting the need for a careful balance between innovation and accessibility. There’s also a steep learning curve for data scientists to adapt to quantum computing.


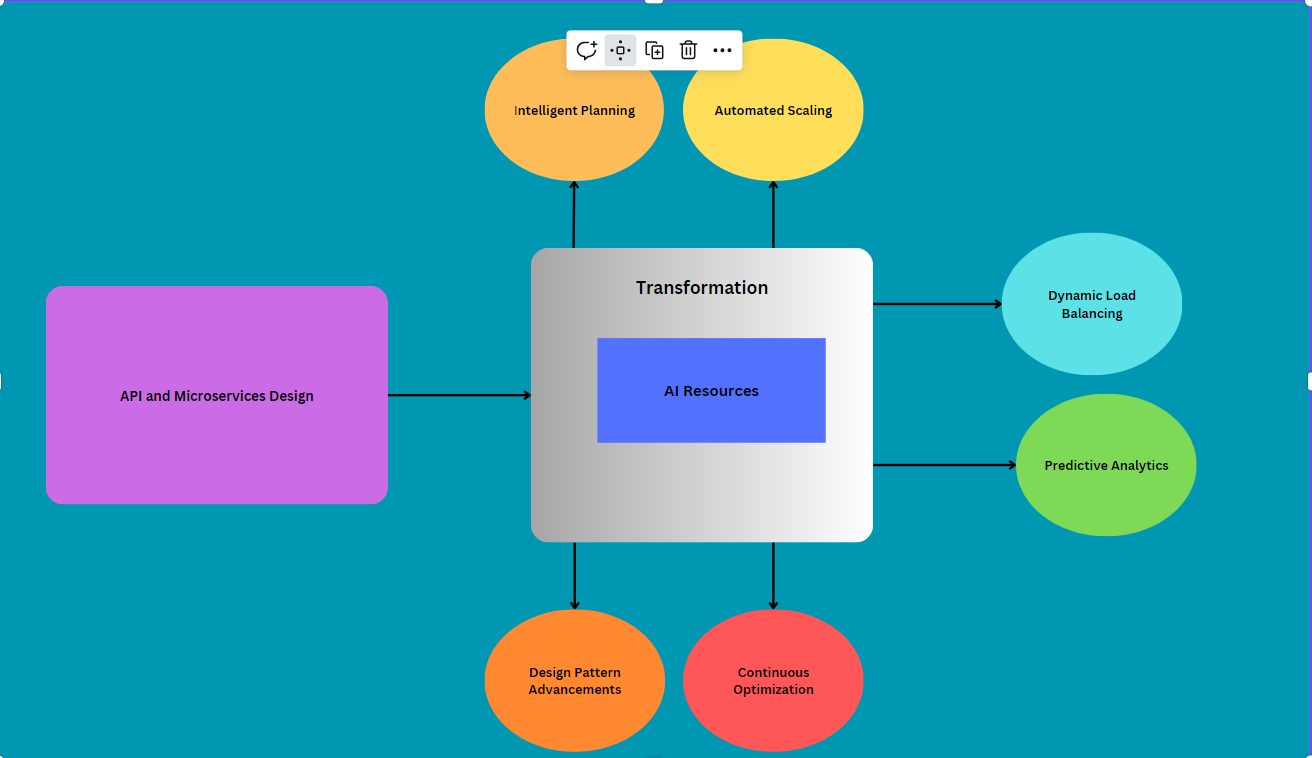
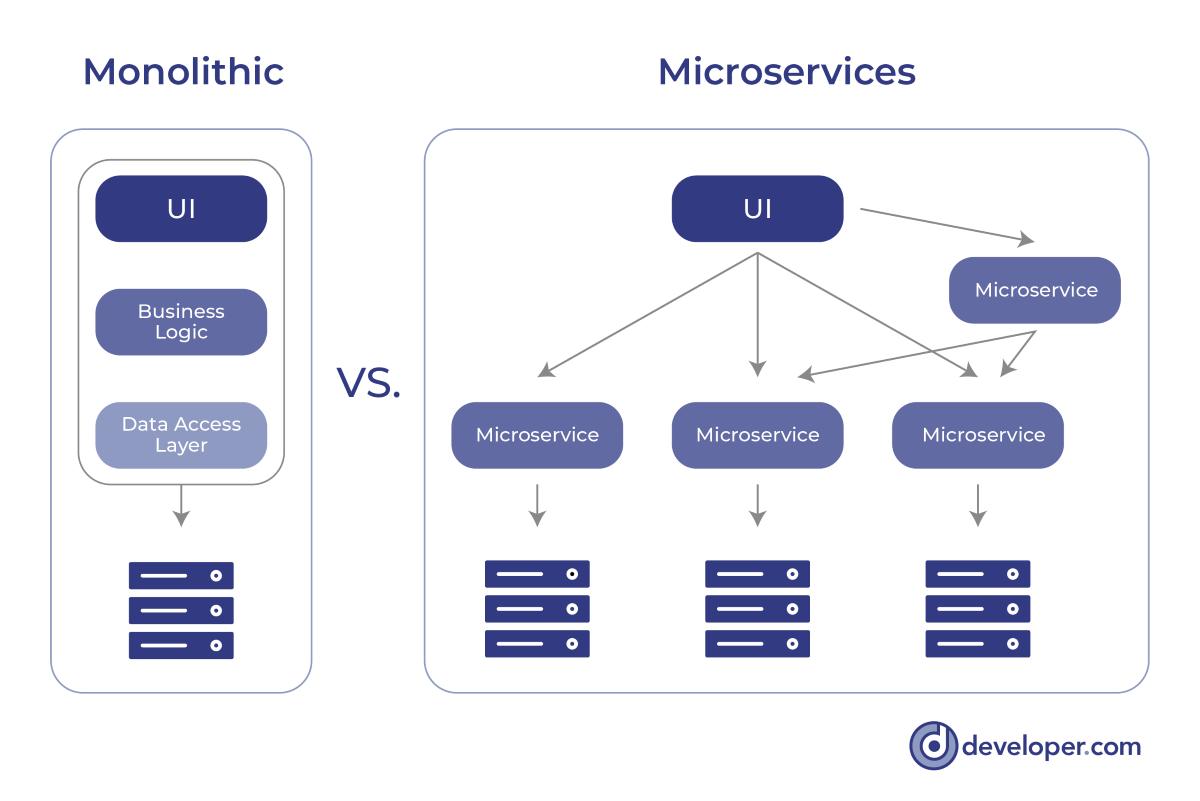
AI-Driven API and Microservice Architecture Design for Cloud

Implementing AI-based continuous optimization for APIs and microservices in Azure involves using artificial intelligence to dynamically improve performance, efficiency, and user experience over time. Here's how you can achieve continuous optimization with AI in Azure:Performance monitoring: Implement AI-powered monitoring tools to continuously track key performance metrics such as response times, error rates, and resource utilization for APIs and microservices in real time. Automated tuning: Utilize machine learning algorithms to analyze performance data and automatically adjust configuration settings, such as resource allocation, caching strategies, or database queries, to optimize performance. Dynamic scaling: Leverage AI-driven scaling mechanisms to adjust the number of instances hosting APIs and microservices based on real-time demand and predicted workload trends, ensuring efficient resource allocation and responsiveness. Cost optimization: Use AI algorithms to analyze cost patterns and resource utilization data to identify opportunities for cost savings, such as optimizing resource allocation, implementing serverless architectures, or leveraging reserved instances.


4 ways AI is contributing to bias in the workplace

Generative AI tools are often used to screen and rank candidates, create resumes and cover letters, and summarize several files simultaneously. But AIs are only as good as the data they're trained on. GPT-3.5 was trained on massive amounts of widely available information online, including books, articles, and social media. Access to this online data will inevitably reflect societal inequities and historical biases, as shown in the training data, which the AI bot inherits and replicates to some degree. No one using AI should assume these tools are inherently objective because they're trained on large amounts of data from different sources. While generative AI bots can be useful, we should not underestimate the risk of bias in an automated hiring process -- and that reality is crucial for recruiters, HR professionals, and managers. Another study found racial bias is present in facial-recognition technologies that show lower accuracy rates for dark-skinned individuals. Something as simple as data for demographic distributions in ZIP codes being used to train AI models, for example, can result in decisions that disproportionately affect people from certain racial backgrounds.


Quote for the day:

"The most common way people give up their power is by thinking they don't have any." -- Alice Walker

Daily Tech Digest - August 03, 2023

When your teammate is a machine: 8 questions CISOs should be asking about AI

There are many potential benefits that can flow from incorporating AI into security technology, according to Rebecca Herold, an IEEE member and founder of The Privacy Professor consultancy: streamlining work to shorten finish times for projects, the ability to make quick decisions, to find problems more expeditiously. But, she adds, there are a lot of half-baked instances being employed and buyers "end up diving into the deep end of the AI pool without doing one iota of scrutiny about whether or not the AI they view as the HAL 9000 savior of their business even works as promised." She also warns that when "flawed AI results go very wrong, causing privacy breaches, bias, security incidents, and noncompliance fines, those using the AI suddenly realize that this AI was more like the dark side of HAL 9000 than they had even considered as being a possibility." To avoid having your AI teammate tell you, "I'm sorry, Dave, I'm afraid I can't do that," when you are asking for results that are accurate, non-biased, privacy-protective, and in compliance with data protection requirements, Herold advises that every CISO ask eight questions


Generative AI needs humans in the loop for widespread adoption

Generative AI by itself has many positives, but it is currently a work in progress and it will need to work with humans for it to transform the world - which it is almost certain to do. This blending of man and machine is best described as “AI with humans in the loop” and it is already being widely adopted by businesses who want to cut operating costs and improve customer services, but also realise that humans will be crucial if these objectives are to be achieved. One of the sectors embracing this new normal is in financial journalism. Reuters managing director Sue Brooks announced that AI will be used to cover news stories and will create a “golden age” of news. Crucially, she also said it was vital there “was always a human in the loop to ensure total accuracy”. Reuters content now has automated time-coded transcripts and translation of many languages into English, part of the Reuters Connect service. Brooks went on to say that this meld would “free up brain power to be creative and put all these tools in your toolbox to create magical experiences for readers”.


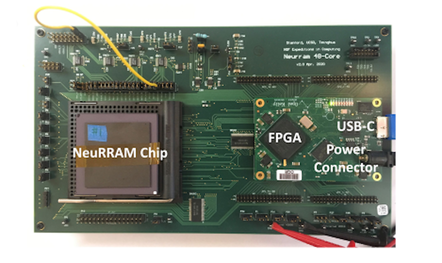
AI chip adds artificial neurons to resistive RAM for use in wearables, drones

According to Weier Wan, a graduate researcher at Stanford University and one of the authors of the paper, published in Nature yesterday, NeuRRAM has been developed as an AI chip that greatly improves energy efficiency of AI inference, thereby allowing complex AI functions to be realized directly within battery-powered edge devices, such as smart wearables, drones, and industrial IoT sensors. "In today's AI chips, data processing and data storage happen in separate places – computing unit and memory unit. The frequent data movement between these units consumes the most energy and becomes the bottleneck for realizing low-power AI processors for edge devices," he said. To address this, the NeuRRAM chip implements a "compute-in-memory" model, where processing happens directly within memory. It also makes use of resistive RAM (RRAM), a memory type that is as fast as static RAM but is non-volatile, allowing it to store AI model weights. 


The CISO role has changed, and CISOs need to change with it

Perhaps the best way to improve security—and make the CISO’s job a little easier—is not reliant on technology. A change in culture is the best way to truly create an organization where security is top of mind. CISOs, part of upper management, but also part of the security team, are uniquely positioned to lead this change – both with other leaders and those they lead. A security-first culture requires embedding security in everything a business does. Developers should be enabled to create secure code that is free from vulnerabilities and resistant to attacks as soon as it is written, as opposed to being a consideration much later in the SDLC. Designated security champions from the developer ranks should lead this charge, acting as both coach and cheerleader. This approach means that security is not being mandated from above, but part of the team’s DNA and backed up by management. This cannot be an overnight change, and may be met with resistance. But the threat landscape is too complex, too advanced and too ubiquitous for any one person or even a small team to handle alone.


Hosting Provider Accused of Facilitating Nation-State Hacks

The allegations, whether true or not, are a reminder that cybercrime doesn't operate in a vacuum. Rather, there's a burgeoning service and support ecosystem. Services include initial access brokers who provide on-demand access to victims, botnet owners who facilitate malware-laden phishing attacks, and repacking services that make malware tougher to spot. They also include ransomware-as-a-service operators who lease their code to business partners, the affiliates who use it to infect victims, and cryptocurrency money laundering services that help criminals - operating online or off - convert their ill-gotten gains into cash. Online attackers require infrastructure for launching their attacks. Some make use of bulletproof service providers, which provide VPS and other types of hosting services in return for a promise, typically for a relatively high fee, that customers can do whatever they like. Halcyon's report alleges that Cloudzy functionally operates in a similar manner, due to a lack of proper oversight, including allowing cryptocurrency-using customers to be able to remain anonymous.


The tug-of-war between optimization and innovation in the CIO’s office

The downside of prioritizing optimization is the risk of overlooking opportunities for innovation that could have long-term impacts on the organization’s growth and relevance. Think game-changing new systems, such as AI, that increase supply chain efficiency, or automating steps in manufacturing that speeds up productivity and reduces costs at the same time. Usually, the value of a business is directly defined by the innovations that can drive it. Think about the services we use now, from food delivery to home sharing, with the draw being better customer experiences through innovation. Emphasizing innovation enables companies to stay ahead of the curve, attracting customers with cutting-edge products and services. ... These mistakes will kill a company. Taking resources away from innovation and spending them on making things work as they should removes business value. I think we’re going to see a great many businesses spend so much money to fix past mistakes that they’ll end up throwing in the towel. 


Flight to cloud drives IaaS networking adoption

IDC describes IaaS cloud networking as a foundational networking layer that allows large enterprises and technology providers to connect data centers, colocation environments, and cloud infrastructure. With IaaS networking, the network infrastructure and services are scalable and available on-demand, provisioned and consumed just like any other cloud service. That makes this infrastructure more scalable and agile than traditional approaches to networking, according to IDC. Direct cloud connects/interconnects is the largest segment of IaaS networking, accounting for more than half of all IaaS networking revenue. The four other major segments of the IaaS networking market are cloud WAN (transit), IaaS load balancing, IaaS service mesh, and cloud VPNs (to IaaS clouds), according to IDC. Cloud WAN, which includes cloud middle-mile and core transit networks, is the fastest-growing segment of IaaS networking, with a forecasted five-year compound annual growth rate of 112%, says IDC. IaaS service meshes are also expected to see strong growth, with a forecasted five-year compound annual growth rate of 68%.


The rise of Generative AI in software development

AI is accelerating the process of going from zero to one – it jumpstarts innovation, releasing developers from the need to start from scratch. But the 1 to n problem remains – they start faster but will quickly have to deal with issues like security, governance, code quality, and managing the entire application lifecycle. The largest cost of an application isn't creating it – it's maintaining it, adapting it, and ensuring it will last. And if organisations were already struggling with tech debt (code left behind by developers who quit, vendors who sunset apps and create monstrous workloads to take care of) now they'll also have to handle massive amounts of AI-generated code that their developers may or may not understand. As tempting as it may be for CIOs to assume they can train teams on how to prompt AI and use it to get any answers they need, it might be more efficient to invest in technologies that help you leverage Gen AI in ways that you can actually see, control and trust. This is why I believe that in the future, fundamentally, everything will be delivered on top of AI-powered low-code platforms. 


Will law firms fully embrace generative AI? The jury is out | The AI Beat

On one hand, gen AI is shaking up the legal industry, with companies like Everlaw adding options to their product portfolio, while Thomson Reuters can integrate with Microsoft 365 Copilot to power legal content generation directly in Word. On the other hand, lawyers tend to be a conservative bunch — and in this case, attorneys would likely be wise to be cautious, with headlines like “New York lawyers sanctioned for using fake ChatGPT cases in legal brief” going viral. Another problem is that their clients may not feel comfortable with law firms using gen AI — a new survey found that one-third of consumer respondents said they’re against any use of gen AI in the legal field. ... But with Everlaw’s new gen AI now available in beta, lawyers can go beyond just clustering data at the aggregate level to querying, summarizing and otherwise extracting details from documents to get what they need. For example, the company says that while it typically takes hours for a legal professional to compose a statement of facts, it can now happen in about 10 seconds, delivering legal teams a rough draft to edit and fact check. 


Vulnerability Management: Best Practices for Patching CVEs

In a perfect world, you would analyze all CVEs first to determine the priority order for patching. But this just isn’t scalable due to the sheer number of vulnerabilities and how frequently CVEs are discovered. In reality, only a handful of CVEs actually affect your software. Of course, there’s no way to know for certain how a CVE affects your application until it has been analyzed, but because there are so many, including those from transitive dependencies, it is nearly impossible to analyze them all before new CVEs are discovered or in the time between a tight release schedule. Instead, we recommend you start by patching all critical and high-severity CVEs without analysis. ... Preventing, detecting and patching CVEs needs to be a shared responsibility between developers and security teams. It is not sustainable for security teams to bear the responsibility of managing and patching CVEs alone. Development teams can often be hesitant to push frequent updates for fear that updates to software libraries will create bugs in their software.


Quote for the day:

"Our greatest battles are with our own minds." -- Jameson Frank

Daily Tech Digest - September 14, 2022

A vision for making open source more equitable and secure

There have been multiple attempts at providing incentive structures, typically involving sponsorship and bounty systems. Sponsorship makes it possible for consumers of open source software to donate to the projects they favor. Only projects at the top of the tower are typically known and receive sponsorship. This biased selection leads to an imbalance: Foundational bricks that hold up the tower attract few donations, while favorites receive more than they need. In contrast, tea will give package maintainers the opportunity to publish their releases to a decentralized registry powered by a Byzantine fault-tolerant blockchain to eliminate single sources of failure, provide immutable releases, and allow communities to govern their regions of the open-source ecosystem, independent of external agendas. Because of the package manager’s unique position in the developer tool stack—it knows all layers of the tower—it can enable automated and precise value distribution based on actual real-world usage.


Cognitive Overload: The hidden cybersecurity threat

Cognitive overload occurs when workers are trying to take in too much information or execute too many tasks. This typically falls under two areas for cybersecurity analysts: intrinsic load, the piecing together of complex technical information to perform incident response activities; and extraneous load, the other 97% of data in a SIEM that they must filter out, while also handling team conversations and sidebar questions. Ultimately, cognitive overload leads to poor performance levels, a lack of focus, and a lack of fulfillment. This can have particularly detrimental consequences within cybersecurity, where ransomware attacks rose 13% year-over-year – more than the past five years combined. To boot, just under half of senior cyber professionals (45%) have considered quitting the industry altogether because of stress. To accommodate the needs of this critical workforce – and fill the 771,000 cyber positions open today – companies must make easing cognitive overload a top priority. Today, it stems from two major issues. First, organizations typically lack direction in cybersecurity, tasking analysts with a broad and daunting: defend our infrastructure. It’s too abstract and leaves them unsure of their roles and responsibilities. 


Medical device vulnerability could let hackers steal Wi-Fi credentials

A vulnerability found in an interaction between a Wi-Fi-enabled battery system and an infusion pump for the delivery of medication could provide bad actors with a method for stealing access to Wi-Fi networks used by healthcare organizations, according to Boston-based security firm Rapid7. The most serious issue involves Baxter International’s SIGMA Spectrum infusion pump and its associated Wi-Fi battery system, Rapid7 reported this week. The attack requires physical access to the infusion pump. The root of the problem is that the Spectrum battery units store Wi-Fi credential information on the device in non-volatile memory, which means that a bad actor could simply purchase a battery unit, connect it to the infusion pump, and quicky turn it on and off again to force the infusion pump to write Wi-Fi credentials to the battery’s memory. Rapid7 added that the vulnerability carries the additional risk that discarded or resold batteries could also be acquired in order to harvest Wi-Fi credentials from the original organization, if that organization hadn’t been careful about wiping the batteries down before getting rid of them.


Four Action Steps for Shoring Up OT Cybersecurity

Having proactive safeguards in place is important, but it’s also critical to have effective reactive procedures ready to respond to intrusions, especially to quickly restore the integrity of operations, applications, data, or any combination of the three. Key ICS and SCADA functions should be backed up with hot standbys featuring immediate failover capabilities should their primary counterparts be disrupted. For data protection, automated and contemporaneous backups are preferable; or at least they should be done at a weekly interval. Ideally, the backup storage will be off-network and, even better, offsite, too. The former protects backup data in case malware, such as ransomware, succeeds in circumventing defense-in-depth and network segmentation measures and locks it up. ... Like plant health, safety and environment (HSE) programs, cybersecurity should be considered alongside them as a required mainstay risk-reduction program with support from executive management, owners, and the board of directors.


The Future of the Web: The good, the bad and the very weird

The rise of big technology companies over the last two decades has made the internet more usable for most people, but has also lead to the creation of a series of 'walled gardens' controlled by them, within which information is held and not easily relocated. As a result, a small number of very large companies control what you search for online, or where you share information with your friends, or even do your shopping. Even worse, these companies have done much to develop what is effectively 'surveillance capitalism' -- taking the information we have shared with them (about what we do, where we go and who we know) to sell to advertisers and others. As smartphones have become one of the key ways we access the web, that surveillance capitalism now follows us wherever we go. And while the rise of social media (the so-called 'Web 2.0' era) promised to make it possible for individuals to produce and share their own content, it was still mostly the big tech companies that remained the gatekeepers. A platform that was once about openness seems to be dominated by big tech.


Authorization Challenges in a Multitenant System

Restricting users to the data that belongs to their tenant is the most fundamental requirement of multitenant authorization. Tenant isolation barriers are needed to prevent users from accessing sensitive information owned by another account. Such a breach would erode trust in your service and, depending on the type of exposure that occurred, could leave you liable to regulatory penalties. Tenant identification usually occurs early in the lifecycle of a request. Your service should authenticate the user, determine the tenant they belong to, and then limit subsequent interactions to data that’s associated with that tenant. ... Another complication occurs when tenants require unique combinations of roles and actions to mirror their organization’s structures. One org might be satisfied by admin and read-only roles; another may need the admin role to be split into five distinct assignments. The most effective multitenant authorization systems will flexibly accommodate customizations on a per-tenant basis. At the application level, granular permission checks will remain the same; however, the system will need to be configurable so tenants can create their own roles by combining different permissions.


Deployment Patterns in Microservices Architecture

The Multiple Service Instances per Host pattern involves provisioning one or more physical or virtual hosts. Each of the hosts then executes multiple services. In this pattern, there are two variants. Each service instance is a process in one of these variants. In another variant of this pattern, more than one service instance might run simultaneously. One of the most beneficial features of this pattern is its efficiency in terms of resources, as well as its seamless deployment. This pattern has the benefit of having a low overhead, making it possible to start the service quickly. This pattern has the major drawback of requiring a service instance to run in isolation as a separate process. The resource consumption of each instance of a service becomes difficult to determine and monitor when several processes are deployed in the same process. The Service Instance per Host pattern is a deployment strategy in which only one microservice instance can execute on a particular host at a specific time. Note that the host can be a virtual machine or a container running just one service instance simultaneously.


Bursting the Microservices Architectures Bubble

The buzz surrounding microservices in recent years doesn't reflect the sudden emergence of the microservices concept at that time, however. Microservices architectures actually have a long history that stretches back decades. But they didn't really catch on and gain mainstream focus until the early-to-mid 2010s. So, why did everyone go gaga over microservices starting about ten years ago? That's a complex question, but the answer probably involves the popularization around the same time of two other key trends: DevOps and cloud computing. You don't need microservices to do DevOps or use the cloud, but microservices can come in handy in both of these contexts. For DevOps, microservices make it easier in certain important respects to achieve continuous delivery because they allow you to break complex codebases and applications into smaller units that are easier to manage and easier to deploy. And in the cloud, microservices can help to consume cloud resources more efficiently, as well as to improve the reliability of cloud apps.


New Survey Shows 6 Ways to Secure OT Systems

A fundamental principle of OT security is the need to create an air gap between ICS and OT systems and IT systems. This basic network cybersecurity design employs an industrial demilitarized zone to prevent threat actors from moving laterally across systems, but the survey finds that only about half of organizations have an IDMZ within their OT architecture, and 8% are working on it. The healthcare, public health and emergency services sectors were especially behind. Nearly 40% of respondents in those sectors don't have plans to implement an IDMZ. Implementing a DMZ is a basic best practice, Ford says. "The risk is lateral movement where breach can move from IT to OT or vice versa, or from low-value network assets to high-value network assets," Ford says. "The more attackers can penetrate your infrastructure, the greater damage and downtime they can cause. Segmentation in DMZ, demilitarized zones, provide an air gap between IT and OT, and additional segmentation can further protect business-critical assets with strong access controls, firewalls and policy rules based on zero trust." 


Wearable devices: invasion of privacy or health necessity?

Dangling a carrot of free technology is a way to engage customers, but protection is vital should wearable technology be compromised. This data isn’t simply name, address and payment details, but potentially highly personal data about an individuals’ wellbeing. The insurance industry will need to develop solutions that help protect the policyholder, and reassure the individual that their data is secure. With GDPR, UK-GDPR and other regulations globally to be highly considered, insurers are spending considerable time and investment in ensuring data is well protected. The ubiquitous nature of wearables has helped increase engagement with insurance, and customers have been introduced to the numerous health benefits of using these devices. If you’ve already got a device tracking your wellbeing, why would you not want a doctor also doing the same? By becoming an extension to the wearable itself, wearable insurance is likely to be generally accepted by customers.


Quote for the day:

"Different times need different types of leadership." -- Park Geun-hye