Showing posts with label CISO. Show all posts

Daily Tech Digest - November 20, 2026

Quote for the Day
“Crisis is the ultimate test of leadership.”
— John Chambers
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

AI coding agents need a safe place to work; Eclipse is building the sandbox to give it to them

As AI coding tools evolve from simple assistants into autonomous agents that execute commands and modify software, they require more freedom to be productive. However, unrestricted access poses significant risks, such as exposing credentials or making unintended changes to systems. To address this problem, the Eclipse Foundation recently introduced Eclipse Enclave 1.0, an open source sandbox that provides a safe, isolated environment for AI coding agents to operate. Instead of forcing developers to supervise every single action, which defeats the entire purpose of automation, Enclave allows these agents to work independently within strictly defined boundaries. Developers can grant access only to the specific files, tools, and web resources needed for a particular task, keeping sensitive information like API keys completely out of reach. The platform even supports running multiple agents in parallel on entirely separate tasks without any interference. Originally built as an internal tool by EclipseSource, this vendor neutral infrastructure successfully shifts the developer role from constant supervision to higher level planning and review. While sandboxing cannot eliminate every risk associated with autonomous code generation, Enclave offers a practical framework to manage those risks while remaining independent.

Read Original Article →

CISO Conversations: Patti Degnan – Part of the Job Is Deciding What Not to Do

Patti Degnan’s journey to becoming the Chief Information Security Officer at Glow, an AI-powered endpoint security firm, began unexpectedly after her identity was stolen in 2006. This personal incident sparked a deep interest in data privacy, leading her through internal audit roles and eventually into senior security leadership positions at companies like Symantec and Notion. Degnan firmly believes that effective cybersecurity leadership requires a strong desire to lead and the ability to align security strategies with overall business goals. While technical knowledge is highly valuable, she argues that a CISO does not need to be a hands-on developer; instead, they must excel at communicating complex technical risks to non-technical stakeholders across the organization. When building her teams, she prioritizes a candidate's ability to take real ownership of problems rather than simply collecting certifications. Addressing the widespread issue of industry burnout, Degnan emphasizes that a crucial part of leadership is deciding what not to do. By setting clear priorities, automating routine tasks with artificial intelligence, and encouraging necessary time off, she helps her team maintain the personal resilience required to manage constant security challenges.

Read Original Article →
Article Thumbnail

Why Visibility Without Action is Failing OT/IoT Security

For years, securing operational technology and connected devices relied on a simple idea: if you can see it, you can secure it. However, simply identifying a vulnerable device creates a dangerous gap between discovering a problem and actually fixing it. Today's automated threats move far too quickly for manual responses. Relying on alerts alone fails because security teams quickly become overwhelmed, and these specialized devices often lack standard operating systems that make updates easy. To close this gap, organizations must move beyond passive monitoring and adopt automated systems that handle routine security tasks like patching, updating passwords, and renewing certificates. These systems can work directly with the devices at scale, effectively blocking threats before they take hold. Yet, because these industrial systems control physical environments where a faulty update could halt production or cause damage, complete automation is too risky. A qualified human professional must always remain in the loop to carefully review and approve these critical changes. Ultimately, simply watching your network is no longer enough; true security requires automated action firmly guided by human judgment to protect physical operations safely.

Read Original Article →

Is Coding with AI Actually Faster and Cheaper?

Recent studies reveal that coding with artificial intelligence indeed accelerates development, though the overall impact on software delivery is more measured than hype suggests. Research tracking over half a million developers shows a massive jump in code commits, but a much smaller increase in actual software releases. While individual programmers generally complete tasks faster using these tools, the time saved during the initial coding phase often shifts into the review, testing, and auditing stages. Consequently, building software feels less stressful and somewhat quicker, but it is not an overnight revolution that drastically slashes production timelines. Regarding costs, the financial benefit largely depends on the capability of the AI model being used. Economic simulations demonstrate that highly capable agents offset the price of their tokens by producing fewer errors and reducing the need for human supervision. In contrast, cheaper but less effective models can quickly become expensive due to the necessary retries and bug fixes. Ultimately, capable AI tools do make coding faster and more cost-effective, yet the full expense of securely delivering and maintaining enterprise software has not dramatically collapsed across the broader tech industry.

Read Original Article →
Article Thumbnail

Why Strong Board Governance Requires Knowing When To Hit The Brakes

Effective board governance comes down to knowing precisely when to accelerate and when to hit the brakes. While many board members default to either cheerleading risky moves to please founders or stalling progress under the guise of risk management, exceptional directors master tempo control. To navigate high-stakes decisions effectively, boards should rely on three key principles: reversibility, information asymmetry, and the difference between trajectory and inflection. If a decision is easily reversible or simply speeds up a proven strategy, the board should accelerate the process. Conversely, if a move represents a permanent pivot or management lacks the necessary on-the-ground expertise, the board must intervene and force a deliberate pause to evaluate risks. For instance, rushing an aggressive international expansion without proper local knowledge can drain capital, whereas a strategic pause for thorough diligence can turn potential failure into a durable revenue stream. Ultimately, a board member’s true value lies not in asking the most questions, but in discerning strategic inflection points from mere noise, protecting capital while ensuring the enterprise scales with confidence and discipline.

Read Original Article →

A game you cannot win unless you have a quantum computer

Google researchers have successfully demonstrated "quantum contextuality" on a large scale, proving that quantum computers can solve specific problems impossible for classical systems. To illustrate this, they use a "magic square" puzzle where two players must fill a grid following contradictory rules. In classical physics, players lose because a pre-determined table cannot satisfy all conditions. However, using entangled qubits on Google's Willow quantum processor, the system won the game 98.3% of the time, easily beating the absolute classical limit of 88.9%. This happens because in quantum mechanics, the answers do not exist before measurement; instead, they are generated at the moment they are observed based on their context. The researchers tested these contextual properties across systems of up to 105 qubits, proving that this phenomenon survives as quantum computers scale up in size. Beyond solving theoretical games, these tests provided a highly sensitive benchmark for identifying subtle hardware errors that standard tests miss. This research confirms that contextuality, rather than just entanglement alone, is a fundamental engine driving the computational advantage of quantum machines, paving the way for more accurate quantum algorithms in fields like chemistry and materials science.
Read Original Article →
Article Thumbnail

How to Secure IT/OT Convergence Without Breaking Operations

As manufacturing environments increasingly connect their information technology and operational technology systems, securing this overlap has become a serious challenge. Most cyberattacks that reach factory floors actually begin in the standard IT network, exploiting pathways created by integrated tools or third-party vendor access. The core issue is that these two environments operate with entirely different priorities and timelines. Standard IT focuses on speed and regular updates, while operational systems prioritize continuous uptime and safety, often relying on legacy equipment that runs for decades and cannot accept modern software patches. Because standard security controls do not translate well to factory floors, companies must adopt frameworks designed specifically for physical operations. This involves prioritizing process safety, implementing strict network segmentation, and managing remote access with time-limited, closely monitored sessions rather than open connections. Using digital certificates helps authenticate connected devices, ensuring only trusted equipment accesses the network. Furthermore, new global compliance standards are shifting how companies buy equipment, requiring manufacturers to embed security features directly into the design phase. By understanding these distinct operational constraints, organizations can better protect their critical infrastructure without disrupting daily production.

Read Original Article →

Chaos, then control: the maturity model most AI rollouts skip over

When engineering teams roll out new artificial intelligence tools, they often notice a strange gap: a few people achieve massive productivity gains, while most just use the tools like a fancy autocomplete. According to a five-stage maturity model, this happens because leaders skip the messy but essential middle steps of a proper rollout. The process should start by letting chaos reign as people experiment, followed by discovering what actually works, codifying those discoveries into shared practices, scaling them across the entire group, and only then reorganizing the team around the new reality. Unfortunately, eager to show quick financial returns, many organizations simply buy the software licenses, wait for the dust to settle, and immediately try to restructure roles based on guesses. To truly succeed, leaders need to pause and closely study their most adventurous engineers during the initial rollout. By identifying their successful habits and translating them into a clear, shared set of daily practices, companies can actively teach the rest of the team how to improve. That unglamorous middle work is the only reliable way to turn scattered individual wins into lasting team-wide success.

Read Original Article →
Article Thumbnail

Your liveness check passed. Was there ever a camera?

Passing a biometric identity check does not always mean a real person is sitting in front of a camera. While many security systems are built to catch someone holding a printed photo or mask up to a lens, criminals are now bypassing cameras entirely. By feeding fake videos or doctored images directly into the verification software, they can open fraudulent accounts with ease. These injection attacks require a different type of testing and defense than traditional physical spoofs. For smaller banks and businesses without dedicated fraud teams, it is crucial to ask technology vendors directly about their specific protections against these camera bypass methods. Instead of relying solely on the facial image, organizations should examine the broader context of the session, such as device data and location signals. Staff should be given clear guidelines on what to look for when a system flags a suspicious entry, rather than being expected to spot artificial images by eye alone. Placing temporary limits on new accounts can also reduce risk. Ultimately, treating a passed facial scan as absolute proof of physical presence is a blind spot that modern security programs must correct.

Read Original Article →

Learning the language of machine learning

MIT Associate Professor Jacob Andreas is working to make artificial intelligence more transparent by teaching machine learning models to explain their own internal processes using everyday human language. Currently, many neural networks operate as "black boxes," meaning their decision-making is difficult to audit or understand. Andreas and his research group are addressing this by developing techniques that allow AI systems to accurately describe what they have learned from their training data. Instead of relying on external tools to decipher a model's behavior, his approach trains the models to talk about themselves and their reasoning directly. His team also focuses on building systems that can learn from simple descriptions rather than millions of examples, similar to how humans learn from a single recipe. Because the field of AI evolves rapidly, often reinventing itself every few years, Andreas continuously updates his courses so students understand the foundational mechanics behind the technology. Ultimately, his research aims to build trustworthy, interpretable AI systems that can honestly communicate their capabilities and limitations, helping to establish a clearer scientific understanding of how models behave in the real world.

Read Original Article →

Daily Tech Digest - October 30, 2026

Quote for the Day
“Scrum is not a methodology; it is a path to agility.”
— Ken Schwaber
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

CISO Problems That Can't Be Solved With Technology

The article highlights a blunt reality: many of the hardest problems CISOs face cannot be solved with technology alone. A panel of security leaders explains that organizations often churn through tools not because the tools are bad, but because they were never properly integrated, funded, or owned. New leaders arrive, priorities shift, and platforms get replaced before they ever reach full value. Several CISOs stress that the real issues are operational — unclear ownership, slow coordination, and misaligned reporting structures. One example describes a critical vulnerability that took an hour to fix technically but three days to close because no one had agreed in advance who should notify teams, approve downtime, or communicate with the business. The panel also criticizes vendors for pushing products without understanding customer needs, and notes that corporate politics often prevent CISOs from having a direct voice with CEOs and boards. The steady message is that security failures often stem from human systems, not technical ones, and solving them requires clearer accountability, better collaboration, and more realistic operating models.

Read Original Article →

Out-of-Band Communication: Your Incident Plan Assumes the Systems You’re Using to Respond Still Work

Most organizations mistakenly assume their standard communication tools will be safe to use during a cyberattack. In reality, when a breach occurs, attackers routinely monitor platforms like Teams, Slack, and corporate email to stay a step ahead of the defense team. If your incident responders are coordinating on compromised systems, they are essentially giving the attackers a live briefing of their recovery strategy. To prevent this, response teams need out-of-band communication—a secure channel entirely separate from the company’s primary network and identity infrastructure. However, simply switching to consumer messaging apps like Signal or WhatsApp is not a reliable backup. These apps lack proper identity verification, make it difficult to maintain accurate team access, and fail to create the secure, defensible audit trails required for regulatory reporting. A genuine out-of-band strategy requires a dedicated, independent environment that is set up and tested long before a crisis hits. By moving the entire response process off the primary network, organizations can confidently manage the incident without tipping off the adversary.

Read Original Article →
Article Thumbnail

Agents are rewriting the book on security. Can your data layer keep up?

The article argues that AI agents are reshaping security in ways that traditional data architectures are not prepared for. These agents don’t just automate tasks — they make decisions, take actions, and interact with multiple systems at once. That shift means the data layer becomes a central security concern rather than a background utility. The piece explains that most organizations still rely on fragmented data stores, inconsistent permissions, and brittle pipelines, all of which create blind spots when agents begin pulling information from many sources simultaneously. If the underlying data is incomplete, stale, or poorly governed, agents can make incorrect or risky choices at machine speed. The article also warns that agents expand the attack surface because they can be manipulated through poisoned data, misleading prompts, or compromised integrations. To keep up, organizations need unified governance, strong lineage tracking, and real‑time visibility into how data flows through agent workflows. The steady message is that AI agents change the tempo and complexity of security, and only a modern, well‑governed data layer can support them safely.

Read Original Article →

Cheap Code, Expensive Confidence

Delegating software development to AI coding assistants might generate code quickly, but building the confidence that this code actually works as intended remains a challenging and time-consuming process. When an AI builds a feature, seeing a number on a screen doesn't prove the underlying math is correct or that the right data was used. Verifying these details requires deep system knowledge and often collaborative discussions with experienced colleagues. Because of this, claiming an AI got a project "eighty percent done" is often misleading. The remaining work involves uncovering where your expectations and the AI's logic diverge, which can take longer than writing the code manually. Furthermore, leaning too heavily on AI can rob newer developers of vital learning opportunities. Working through a problem manually helps them understand how data flows through an application, a skill they need for future troubleshooting. Ultimately, teams must thoughtfully decide when to hand tasks to an AI. This choice should depend on how easily the team can verify the final result and whether a developer needs the experience of solving the problem themselves.

Read Original Article →
Article Thumbnail

The Rise of the Threat Operator: How AI Will Redefine Security Operations and Careers

As artificial intelligence takes over routine security tasks like investigating alerts and gathering evidence, the traditional role of the security analyst is fundamentally changing. Instead of getting bogged down in individual alerts, professionals are transitioning into a new role often called a threat operator. This position requires overseeing the entire defense strategy rather than just monitoring tools. Because AI can handle the repetitive technical work, human experts must now focus on understanding their organization's unique business risks and guiding the AI systems accordingly. They decide how much independence the software should have and step in when complex judgment is needed, such as balancing a security threat against the risk of taking a critical business system offline. This shift means future security professionals will need a different blend of skills. While technical knowledge remains important, the ability to interpret automated decisions, manage overall risk, and maintain accountability over the defense process is becoming essential. Ultimately, security teams are moving from operating individual software tools to managing a comprehensive, AI-supported defense system.

Read Original Article →
Article Thumbnail

A Release Review Checklist for Teams Where One Developer Does Most of the Work

When a single developer handles an entire software project, the usual safety nets of peer reviews and dedicated testing disappear. To prevent bugs from reaching users, teams should implement a straightforward release review process that a senior developer can complete in under an hour. The foundation of this method is a consistent, eight-point checklist applied to every release. First, the reviewer reads the release summary to ensure the code actually solves the requested problem. They then evaluate the structural design rather than just reading lines of code. The reviewer tests the feature from the perspective of both a brand-new user and a long-time user, deliberately trying unexpected inputs that the original developer likely missed. They also check for broken features in other parts of the application, verify that appropriate tests are included, and confirm environment configurations match production settings. Finally, the reviewer records a clear decision to release or hold the code. For this system to work, reviews must be scheduled, reviewers must have authority to halt a release, and common mistakes must be discussed.

Read Original Article →
Article Thumbnail

A JSON schema Is not an AI governance layer

True AI governance happens far below the level of industry regulations and policy debates; it ultimately comes down to the specific code that decides whether an AI agent is allowed to execute an action. While many developers rely on tools like JSON schemas to validate an agent's requests, these schemas only check the shape of the data, not its precise meaning across different systems. This limitation creates a security vulnerability known as a parser differential, where two different components read the exact same payload in slightly different ways. Simple differences in how a system handles whitespace, looks up identifiers, or processes data normalization can inadvertently alter your authorization rules. Furthermore, you cannot rely on an agent to declare its own inputs as trustworthy. Real security requires deriving trust directly at the enforcement boundary by verifying cryptographic signatures against known keys. To truly secure your AI deployments, you must go beyond basic schema validation, strictly enforce specifications, reject ambiguous data shapes, and ensure your system independently verifies the authority behind every requested action.

Read Original Article →

McKinsey's Quantum Road Map Runs Through Q-Day

A recent McKinsey report highlights the rapid advancement of quantum technology and its dual role as a massive economic opportunity and a serious security threat. The focus for security professionals is "Q-Day," the point when quantum computers become capable of breaking today’s standard encryption. This milestone is approaching faster than initially projected, with key hardware developments expected within the next five years. Because attackers are already stealing encrypted data to decode it in the future, organizations cannot afford to wait. The report urges companies to begin upgrading to new, quantum-resistant encryption methods immediately to protect their long-term data. Upgrading this security infrastructure will require significant time and financial investment, marking a shift that is non-negotiable for large enterprises. To prepare, leaders need to take inventory of their current encryption systems, secure multi-year budgets, and require their technology suppliers to provide clear transition plans. Ultimately, updating to quantum-safe security is not a distant concern but an active, ongoing necessity that requires methodical and immediate planning.

Read Original Article →
Article Thumbnail

No One Holds the Key: Threshold ECDSA, Part 1

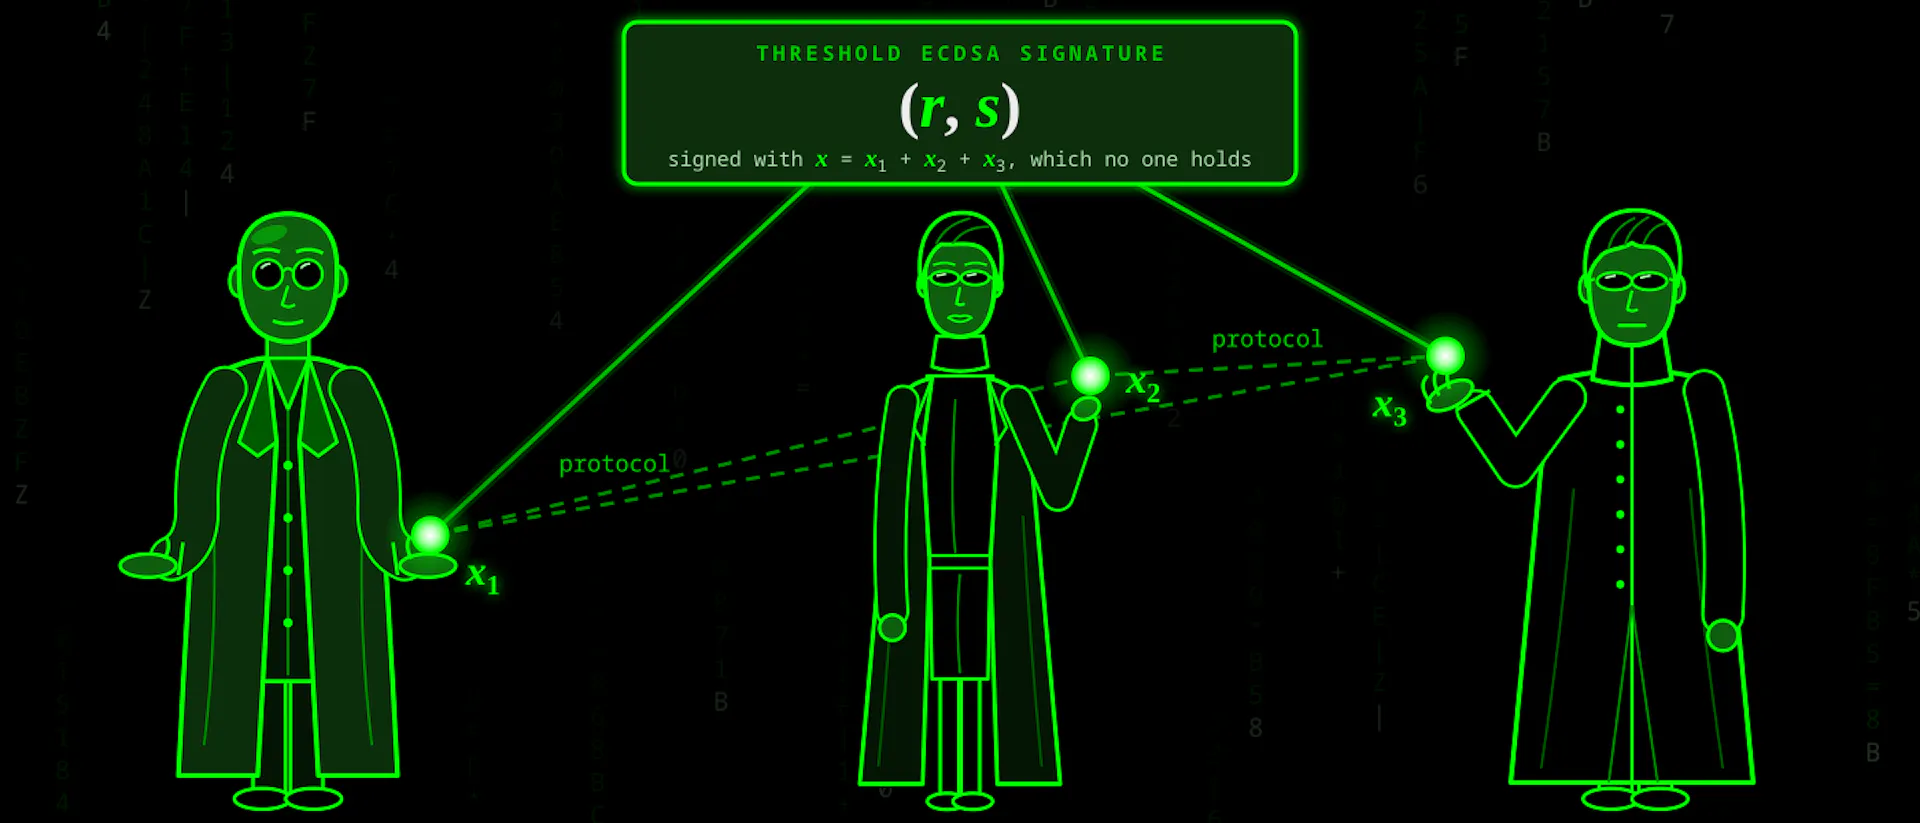
The article introduces threshold ECDSA as a way to remove single points of failure in digital signing systems. Traditional ECDSA relies on one private key held by one party, which creates an obvious risk: if that key is stolen, lost, or misused, the entire system is compromised. Threshold ECDSA changes this model by splitting the private key into multiple independent shares held by different participants. No one ever sees or reconstructs the full key, yet the group can still produce valid ECDSA signatures through a coordinated protocol. The article explains that this approach improves security for wallets, exchanges, and custodial services because attackers can no longer target a single secret. It also reduces operational fragility — losing one device or administrator doesn’t destroy access. The piece highlights that implementing threshold signing is complex, requiring careful cryptographic design to prevent leaks during collaboration. Its steady message is that threshold ECDSA offers a practical path toward stronger, more resilient key management by ensuring that “no one holds the key” in the traditional sense.

Read Original Article →
Article Thumbnail

PHP2Shell will persist in enterprise environments for years

The article explains why the PHP2Shell vulnerabilities will linger in enterprise environments for years, even though patches already exist. PHP is embedded in an enormous range of third‑party products — NAS devices, firewalls, VPN gateways, printers, building‑management systems, industrial controllers, and OT interfaces — many of which run outdated or unsupported PHP versions. Because customers cannot patch these runtimes directly, they must wait for vendors to release updates, and those updates often arrive slowly or not at all. The article shows how inconsistent versioning, backported fixes, and long‑term‑support Linux distributions make it difficult to know whether a system is truly protected. Early scans already reveal widespread exposure, and CISA has confirmed active exploitation. Even when patches are available, organizations still face the challenge of discovering every PHP instance across servers, containers, appliances, and firmware images. Until vendors deliver fixes, teams must rely on temporary mitigations such as isolating devices, tightening firewall rules, and monitoring for signs of compromise. The steady message is that PHP2Shell is less a single vulnerability and more a visibility and lifecycle problem that enterprises will be managing for a long time.

Read Original Article →

Daily Tech Digest - October 25, 2026

Quote for the Day
“The only way to win is to learn faster than anyone else.”
— Eric Ries
Audio Edition — Listen to Today’s Digest
Narrated version of the Daily Tech Digest
Article Thumbnail

Core Concepts in Infrastructure Cost Management

The article revisits how organizations should think about infrastructure cost management by comparing on‑premise and cloud deployment patterns. It notes that a decade ago, cloud was widely seen as the inevitable future, but recent shifts show that on‑premise environments still offer advantages worth reconsidering. On‑premise setups involve not just servers but the full physical ecosystem — racks, networking gear, cooling, power, and security — all of which carry long‑term financial and operational implications. The piece explains that while on‑premise environments are often labeled inflexible, they can be surprisingly adaptable when paired with modern automation frameworks. The real challenges lie in hardware lifespan decisions, sizing development and QA environments, managing shared analytic workloads, and maintaining disaster‑recovery sites that are costly to keep idle. These factors shape both capital and operational expenses over many years. The article’s steady message is that cost management requires understanding the trade‑offs between flexibility, predictability, and long‑term commitments, and that both cloud and on‑premise models have strengths that deserve thoughtful evaluation rather than assumptions.

Read Original Article →

Container Security Checklist for CI/CD Pipelines: 30 Checks From Commit to Runtime

This article presents a practical security checklist containing 30 checks for container images as they move through continuous integration and deployment pipelines. The core message is that actual security comes from enforcing rules, not just listing best practices. The checks span eight stages, from the initial code commit to runtime monitoring. In the early stages, teams should build minimal images, remove all secrets, and lock down third-party actions. Later stages focus on vulnerability scanning that blocks risky deployments, generating software bills of materials, and digitally signing images to guarantee they came from a trusted build. At deployment, admission controllers must verify signatures and restrict permissions so images cannot run with root access or modify the underlying host. Because the pipeline itself is a high-privilege system that can be compromised, securing the build process is just as important as securing the image. Implementing these checks incrementally—starting with basic Dockerfile hygiene—prevents common mistakes and ensures a cleaner, safer production environment.

Read Original Article →
Article Thumbnail

Cloud repatriation: What CISOs need to know

The article explains that cloud repatriation is becoming a practical concern for CISOs, not because enterprises are abandoning the cloud, but because many workloads no longer fit the cloud‑first assumptions of the past decade. Surveys show that while 86% of CIOs plan to move at least some workloads back on‑premises, only about 8–9% intend a full exit, meaning most organizations are simply recalibrating workload placement rather than rejecting cloud altogether. Cost discipline is a major driver, with private cloud often delivering 40–50% lower total cost of ownership for steady‑state workloads. Compliance, data‑gravity issues, and high‑intensity AI workloads also push certain systems back into controlled environments. The article stresses that hybrid infrastructure is becoming the long‑term norm, where each workload “earns” its placement based on economics, performance, and risk. For CISOs, this shift introduces new responsibilities: reassessing threat models, ensuring consistent controls across mixed environments, and preparing for operational risks tied to vendor concentration and geopolitical disruptions. The message is steady — repatriation is about precision, not retreat, and CISOs must adapt security strategies accordingly.

Read Original Article →

The Cybersecurity Reality Check: Ten Myths That Matter

The article challenges ten common assumptions that often mislead leaders about cybersecurity and explains why these misconceptions create real risk. It notes that serious incidents rarely stem from exotic technical failures; instead, they usually begin with flawed beliefs about who attackers target, where responsibility sits, or what “adequate protection” really means. One myth is that small organizations are too insignificant to attract attention, but attackers typically exploit exposed systems using automated tools, making size irrelevant. Smaller firms may even be more vulnerable because they have fewer security resources and weaker monitoring. Another misconception is that cybersecurity is purely an IT function, when governance and accountability actually rest with leadership. The article stresses that regulatory scrutiny in the UK and EU has intensified, and breaches can quickly lead to investigations, litigation, business interruption, and reputational harm. Ultimately, the piece argues that organizations must be able to justify their security measures as proportionate to their risks and abandon assumptions that no longer match today’s threat landscape.

Read Original Article →
Article Thumbnail

When Trust Fails: What the eMudhra Certificate Incident and PHP Vulnerabilities Teach Us About Zero Trust Security

In October 2026, two distinct cybersecurity events—a certificate failure by eMudhra and critical remote code execution flaws in PHP—highlighted a fundamental lesson for software engineers: trust must be constantly verified. The eMudhra incident involved weak intermediate cryptographic keys generated by a flawed process. Even though eMudhra itself was not hacked, the incident proved that secure connections rely on trustworthy underlying processes, not just a padlock icon. Meanwhile, the PHP vulnerabilities demonstrated that securing an application requires patching the entire software stack, not just the core code, because a vulnerable runtime can serve as an easy entry point. Together, these events show why modern systems must move away from assuming that any internal network or familiar request is automatically safe. Instead, engineers should adopt a strict verification approach. This means validating identity, authorization, and context at every boundary, properly handling access tokens, and protecting communication between internal services. Ultimately, security is an ongoing engineering process of continuous verification rather than a single static feature or one-time setup.

Read Original Article →

What OT detection actually reveals

Securing operational technology (OT) environments requires a fundamentally different approach than standard IT security. While conventional IT tools excel at spotting network anomalies, they lack the critical physical process context needed to recognize when otherwise legitimate industrial commands are used for malicious disruption. OT detection platforms solve this by combining industrial protocol awareness with a deep understanding of normal operational behavior and physical constraints. A solid asset inventory is the foundational first step. From there, effective OT security relies on five core capabilities: monitoring industrial protocol anomalies, establishing strict baselines for process behavior, tracking engineering workstation activity, closely managing remote vendor access, and correlating traffic across the IT/OT boundary. Because OT involves physical processes where any disruption can impact safety, detection must be paired with structured, pre-planned response strategies. Automated actions are generally safe only at the IT or DMZ layers. Any direct intervention touching physical plant controllers requires clear authorization from operations teams to ensure production environments remain safe and stable.

Read Original Article →
Article Thumbnail

AI accelerates path from IT compromise to OT targeting

The article explains that AI is accelerating the path from IT compromise to OT targeting, making industrial environments more exposed than before. Attackers can now use AI to quickly analyze stolen IT data, map relationships, and identify the most valuable operational assets to target. This shortens the traditional gap between breaching corporate networks and moving into industrial systems. The piece notes that modern OT environments are increasingly connected to cloud services, remote access tools, and SaaS platforms, creating more entry points and making it harder to maintain clear separation between IT and OT. AI also helps attackers craft more convincing phishing messages, automate reconnaissance, and generate malware tailored to specific environments. At the same time, defenders struggle with legacy systems, inconsistent visibility, and slow patch cycles. The article argues that organizations must rethink OT security by improving asset inventories, tightening identity controls, and preparing for faster, more automated attack chains. Its message is steady: AI has changed the tempo of intrusions, and OT security must adapt to match that speed.

Read Original Article →

The next manufacturing cyber threat is manipulation of AI-driven decisions

As manufacturing becomes increasingly connected, the nature of cybersecurity threats is shifting. According to Pradipta Patro, Chief Information Security Officer at Polycab India Limited, the next major risk isn't just about keeping hackers out of the network. It is about protecting the artificial intelligence systems that influence critical operational decisions. If an attacker manipulates the data feeding an AI model, the system could make unsafe or faulty decisions without triggering traditional alarms. This goes beyond compromised information, directly threatening production quality, equipment reliability, and even worker safety on the factory floor. To address this, security must be built into factories from the ground up rather than added later as an afterthought. Manufacturers need complete visibility into all connected devices, strong network boundaries between IT and operations, and meaningful human oversight of AI decisions. Ultimately, cyber resilience must be treated as a core business continuity issue. The most successful factories will be those that can fully trust their automated systems because they secured the underlying data first.

Read Original Article →
Article Thumbnail

Digital twins in oil and gas: from simulation to real-time optimisation

Digital twins in the oil and gas sector are evolving from isolated engineering studies into practical tools that drive daily operations. Historically, creating a digital twin took months and became outdated as soon as the physical equipment changed. Today, advanced models can be built quickly, update automatically alongside physical wear, and connect across entire systems. A key shift is the use of physics-based modeling rather than just relying on historical data. Purely statistical models struggle when equipment faces new or unobserved conditions. By grounding the software in the actual laws of fluid dynamics and heat transfer, operators receive reliable, real-time recommendations they can trust. This approach accounts for uncertainty, allowing teams to optimize active equipment and reduce waste like methane flaring by safely pushing production closer to its true limits. Solving the challenge of scaling these tools in energy operations also opens the door for similar efficiency gains in other complex, high-demand environments, such as data centers and power grids.

Read Original Article →
Article Thumbnail

Data Sovereignty is Becoming a Design Principle for Enterprise AI

In the past, data sovereignty simply meant knowing the physical location of your company’s servers to meet regional laws. Today, artificial intelligence has fundamentally changed this. Because data now constantly flows through various external applications, language models, and processing tools, maintaining control over it has become much more complex. Instead of trying to lock down an entire organization, companies should focus on individual tasks. For example, processing public marketing information requires far less strict control than handling sensitive medical records. A major challenge is ensuring that safety rules follow the information wherever it goes. When original records are transformed into formats that AI can read, those new formats must inherit the same restrictions. Tracking this movement requires strong underlying data tagging. To manage this effectively, businesses should view sovereignty as a flexible budget. They must calmly weigh the need for strict control against the benefits of using advanced, external technology. Ultimately, building a flexible setup allows teams to continuously adjust their safety measures as rules and technology evolve.

Read Original Article →

Daily Tech Digest - October 16, 2026


Quote for the day:

"Every great story on the planet happened when someone decided not to give up, but kept going no matter what." -- Spryte Loriano

🎧 Listen to the audio debrief on YouTube

▶ Play Audio Digest

Duration: 22 mins • Perfect for listening on the go.


Why AI Confidence Is Not Validation

Artificial intelligence tools are rapidly becoming integrated into digital forensics and incident response, but these systems are growing confident in their outputs faster than human operators can verify them. Without proper validation standards, unverified AI findings can end up in critical legal or forensic reports. To address this, SANS introduced two specialized AI frameworks mapped to industry standards, emphasizing that while AI can speed up investigations, a human examiner must remain the final authority. An AI tool that provides a confident answer without showing its underlying reasoning or sources is essentially unreliable. Practitioners cannot blindly trust an AI claim just because a high confidence score is attached; they must independently confirm the source data. Furthermore, different disciplines require entirely different policies. Incident response teams prioritize speed to detect and contain threats, whereas digital forensics demands strict validation of every file, often making AI use more labor-intensive. Ultimately, the effectiveness of AI depends heavily on the foundational skills of the human practitioner. AI should never automatically execute actions that cannot be reversed, such as collecting evidence or accessing cloud accounts without explicit authority. An inexperienced person relying solely on AI presents a significant risk to the integrity of any investigation.


CISO Conversations: James Robinson – Many Jobs, One Journey to Netskope CISO

James Robinson’s path to becoming the Chief Information Security Officer at Netskope reveals that a successful career in cybersecurity does not always follow a traditional or planned route. Initially focused more on sports than academics, Robinson discovered his passion for networking through a vocational program while in high school. This early exposure led him to acquire advanced certifications and eventually land at State Farm Insurance. When the dot-com crash disrupted his plans to join Cisco, he pivoted into the emerging field of information security, moving through roles at several major organizations and continually advancing his expertise. Throughout his journey, Robinson has relied heavily on the guidance of mentors and emphasizes the importance of building strong professional relationships. He believes that continuous learning, genuine curiosity, and enjoying the process are far more important than just reaching a specific destination or focusing solely on salary. As a leader, his primary focus is on cultivating a supportive team culture and ensuring his team members feel recognized and connected. When hiring, he values persistence, dedication, and the right mindset over formal degrees, proving that resilience and a willingness to put in the hard work are the true cornerstones of security leadership.


No click required: How the ad industry became a pipeline for mercenary spyware

Researchers from The Citizen Lab have discovered that the online advertising ecosystem is being used to deliver zero-click spyware to targeted individuals without requiring them to click on anything. A company known as Discover-Tech successfully posed as a legitimate advertising vendor, gaining approval from major ad networks like Google and IAB Europe. By participating in real-time automated ad auctions, the company accessed detailed user data, such as physical locations and device identifiers, allowing them to precisely profile millions of people worldwide. When Discover-Tech won a bid to display an ad, it mostly delivered harmless banners, which allowed it to pass routine security verification scanners. However, for specific targets, such as journalists at Al Jazeera, the ad silently delivered malicious code in the background. Because the ad auction system automatically shares user data to determine targeting, bad actors can track individuals across various networks undetected. To defend against this invisible threat, security experts advise organizations to implement strict ad-blocking policies at the network level rather than relying on users themselves. They also strongly recommend disabling mobile advertising identifiers on corporate devices and treating all ad networks as untrusted vendors, since every digital ad essentially runs external code on a user's device.


Governance Is Failing: Why Converged Digital Risk Is Outpacing Every Control We Have

Organizations today are struggling to manage modern digital threats because their governance models are outdated. Traditional structures treat cybersecurity, privacy, artificial intelligence, and compliance as separate issues managed by different departments. However, modern risks no longer stay in these neat categories. A single incident, such as a compromised identity, can instantly trigger a massive chain reaction that causes data leaks, disrupts supply chains, corrupts artificial intelligence systems, and results in severe regulatory and reputational damage. This interconnected system of threats is known as Converged Digital Risk, and it moves much faster than isolated governance frameworks can handle. To solve this, businesses must stop treating risk in silos and start viewing it as a unified system. This means shifting focus from merely protecting internal assets to understanding the massive dependencies organizations have on external tools, like cloud providers and third-party models. Ultimately, managing this complexity might require the creation of a new executive role—a Digital Risk Officer—who can oversee the entire landscape, ensure unified visibility, and make rapid decisions when multiple risk areas collide. The organizations that thrive will be those that prioritize system-wide resilience and act quickly before failures cascade.


AI Slop Isn't Just for Social Media; It's Ruining Cyberattacks, Too

Despite the alarmist headlines claiming artificial intelligence is supercharging cyber threats, security researchers are finding that AI is actually making many attackers worse at their jobs. While threat actors are using AI to scale their operations and generate content, the result is often low quality output that exposes their campaigns. Previously sophisticated cybercrime groups and even state funded operations are adopting AI to write code, design phishing lures, and create malware, but these efforts frequently backfire. The attacks are riddled with obvious mistakes, such as broken QR codes, blank emails, mismatched languages, and logical errors in malware that prevent it from functioning properly. Some groups are even exposing their own infrastructure by accidentally leaving their AI generated control panels open to researchers. Ultimately, top tier espionage and hacking operations avoid relying heavily on AI because it is too noisy and unpredictable, which dramatically increases their chances of being caught. Instead of a new era of highly advanced artificial intelligence breaches, the industry is mostly seeing a flood of sloppy, poorly executed attacks. The consensus among researchers is that the most dangerous and effective cyber threats still rely on traditional methods, making the current narrative around automated attacks largely exaggerated and unsupported by real world data.


IT reinvention requires mastering the art of translation

Technology leaders must act as translators who can clearly explain how technical systems directly benefit their companies. Rather than discussing complicated cloud architecture or artificial intelligence setups, a successful executive links technological investments to business outcomes like profitability, risk reduction, and an improved experience for customers. This approach is evident in the transformation of Deluxe Corporation, a business that successfully transitioned from a legacy check manufacturer into a modern digital payments and data company. By framing its strategy around how technology powers profitable growth, the company aligned its entire operation with clear goals like building modern platforms, using artificial intelligence responsibly, and strengthening security. True organizational reinvention requires completely changing processes, talent, and mindsets rather than just adding digital tools to old workflows. Leaders must also learn to separate practical signals from the endless noise surrounding emerging trends. Instead of chasing every new technological development, they should focus on core business functions that rarely change while tracking how shifts in areas like cybersecurity, agentic commerce, and employee roles affect those functions. By continuously learning, challenging their own assumptions, and pressure-testing ideas with peers, technology leaders can guide their organizations through continuous reinvention with confidence.


How Should Security Be Architected for Human Error?

When architecting enterprise cybersecurity, organizations must acknowledge that human error is inevitable and stop building programs that expect perfect behavior. Attackers actively manipulate employees into making mistakes, so relying solely on human judgment or even automated systems acting alone is insufficient. Instead, security programs should blend human oversight with automation, allowing each to audit the other. Security should be treated as an operational capability focused on resilience rather than a mere product feature. Instead of adopting a heavy-handed approach that completely blocks access until users complain, organizations need intelligent "default deny" or allow-listing strategies that preserve usability. Assuming that a malicious link will eventually be clicked, the focus must shift to minimizing the blast radius. This requires aggressive segmentation, strict minimization of privileges, and inline rate limits that act as "speed bumps." For example, systems should flag and pause actions that fall outside the norm, like a user attempting to delete millions of database rows or send tens of thousands of emails simultaneously. Ultimately, companies should routinely practice for failures through tabletop exercises and chaos engineering. By putting guardrails in place and testing recovery protocols before prevention fails, businesses can ensure that a single human mistake doesn't escalate into a massive crisis.


8 insights from LogicMonitor’s Elevate event: AI-driven observability moves toward autonomous IT

At the recent LogicMonitor Elevate event, the focus was on how artificial intelligence is shifting IT monitoring from passive observation to active, autonomous problem-solving. As business infrastructure becomes more complex, traditional alerts and dashboards are no longer enough. To manage this, LogicMonitor is emphasizing AI-driven observability that combines performance data with automated actions and strict governance. The results are significant: GlobalFoundries, for example, used LogicMonitor’s Edwin AI to reduce distracting alert noise by 98% in just six months, allowing them to spot potential failures in their semiconductor manufacturing before they disrupt production. A central theme of the event was the need to build trust in these automated systems. Before organizations let artificial intelligence resolve issues automatically, they need to know the AI operates within strict rules and understands the context of the business. By connecting operational data with clear guardrails, LogicMonitor aims to help IT teams resolve incidents faster and reduce the number of tools they need to manage. Ultimately, the goal is to free up engineering teams to focus on higher-value work, moving operations from simply fixing problems to actively preventing them.


Why Chief Data Officers Need to Go Beyond Data Catalogs to Deliver Value

Chief Data Officers are finding that traditional data catalogs are no longer enough to meet the demands of modern business, especially as artificial intelligence adoption increases. While companies collect vast amounts of data, it often remains locked in departmental silos or stuck in technical tools that everyday employees cannot easily use. This lack of accessible, high-quality information not only frustrates staff but also limits the effectiveness of artificial intelligence models, which require reliable inputs to function properly. To solve this, organizations must shift toward creating data products—packaged, business-focused assets designed for specific needs. However, these products only deliver value if people can easily find and use them. This is driving the adoption of data marketplaces, which function much like e-commerce storefronts, allowing non-technical users to search for, understand, and access reliable information through intuitive interfaces. A successful transition requires more than just new technology; companies must foster a culture of data literacy and trust by ensuring the experience is straightforward and the initial offerings are highly relevant. By moving past reactive data catalogs and embracing user-friendly marketplaces, businesses can effectively share information across teams and artificial intelligence systems, turning their data into tangible, long-term value.


Developers Positive About AI - but Trust Remains Conditional

According to Stack Overflow’s 2026 Developer Survey, while AI adoption in the workplace has reached near saturation, developers remain deeply skeptical of its output. Six in ten developers view artificial intelligence favorably, yet nearly half only trust the technology when they can independently verify its work. A mere seven percent trust AI for critical decisions, highlighting a strong demand for transparency, technical context, and clear source attribution. Most developers actively use coding assistants and find them highly effective for implementation, debugging, and refactoring, but their perceived utility drops significantly for human oriented tasks like design and team communication. Furthermore, organizational governance is lagging, with many companies lacking official policies for AI use. Beyond AI, the survey paints a complex picture of the modern workplace. Almost half of developers feel complacent in their current roles, largely driven by burnout, unclear priorities, and tech fatigue. Despite a push for return to office mandates, remote work remains the preferred arrangement. In terms of technology, familiar foundations like JavaScript and Python continue to dominate the landscape. Interestingly, while OpenAI and Anthropic currently see equal usage among developers, there is a growing preference to use Anthropic models and agents in the coming year.