Quote for the day:
“The two most important days in your life are the day you are born and the day you find out why.” -- Mark Twain
🎧 Listen to the audio debrief on YouTube
▶ Play Audio DigestDuration: 22 mins • Perfect for listening on the go.
Engineering trust at scale: Building the infrastructure behind global payments
 The provided article discusses the complex engineering required to build
trust and reliability in global payment systems. The core challenge lies in
simplifying the user experience while managing the intricate underlying
infrastructure, which involves multiple banks, currencies, compliance checks,
and domestic payment schemes. Trust is essential, encompassing not just
cybersecurity, but also operational resilience, effective transaction routing,
and settlement. Payment architectures must handle high transaction volumes
without compromising reliability or creating friction for users. As businesses
expand globally, payment systems need to connect local networks smoothly,
rather than attempting to create a single universal system. Regulatory
compliance must be integrated directly into the transaction process, adapting
to different regional requirements without adding unnecessary hurdles for
businesses. Artificial intelligence is highlighted as a key tool for managing
this complexity, especially in detecting fraud and recognizing legitimate
behavior to reduce false positives. Finally, the article emphasizes the
importance of interoperability. A unified technology layer and tools like Open
Finance can help businesses access local payment methods globally without
needing to rebuild their systems for each new market. Ultimately, the goal is
for the underlying payment infrastructure to manage the complexity so
effectively that the end-user experience remains simple and trustworthy.
Google’s open source EnvHarness lets AI agents train against environments that evolve with them
 Google has introduced EnvHarness, an open-source framework designed to solve a
major problem in AI agent training: static simulators. Usually, when agents
practice tasks like software engineering or web navigation, the training
environments remain fixed. If an agent repeatedly struggles with a specific
step, the environment cannot adapt to help it practice that weakness. Building
new environments and testing rules from scratch is costly and time-consuming.
EnvHarness addresses this by wrapping a programmable layer around existing
simulators. Instead of replacing the original setup or its success checkers,
it modifies how the environment interacts with the agent. The framework uses
three main components. "Stage" changes the starting conditions of a task.
"Contract" adjusts the rules, such as filtering actions or altering what the
agent can see. "Chain" links multiple tasks together into a longer sequence. A
companion system called EnvRigger automatically analyzes an agent's failures
and suggests these modifications to target specific weaknesses. In tests
across five major benchmarks, agents trained using EnvHarness saw success
rates improve by up to nine percentage points compared to those trained in
standard environments. They also completed tasks in fewer steps. By allowing
training grounds to evolve alongside the agent, EnvHarness makes learning
significantly more efficient.
Why Australian businesses are still underestimating the time it takes to recover from a cyberattack
Many Australian organizations invest heavily in cyber defenses but fail to
understand the true timeline for recovering from a system breach. According to
recent findings, company leaders often expect normal operations to resume
within a few days of an incident, whereas the actual recovery process
frequently takes weeks. This disconnect is driven by the growing complexity of
modern technology environments, which now span multiple cloud platforms,
software services, and vast data systems. Every new layer adds dependencies
that must be carefully restored and verified before services can resume.
Recognizing that disruptions are inevitable, regulators are shifting their
focus from merely preventing attacks to ensuring operational resilience. Rules
now require organizations to identify their critical services and prove they
can maintain them during severe incidents. To achieve this, companies should
focus on defining their essential functions by identifying the minimum people,
processes, and technology needed to survive a crisis. Rather than waiting for
an emergency to test their systems, organizations must make recovery readiness
a continuous, daily practice. By actively aligning their security, technology
operations, and data management around clear recovery goals, businesses can
build genuine confidence. Ultimately, understanding exactly how and when you
can restore critical services is a highly meaningful competitive advantage.
 This article explores the complexities of generative AI software license
agreements, particularly concerning restrictions on using AI tools and their
generated output to develop competing products. It highlights a critical
distinction between the use of an AI platform itself and the use of the
content it produces. While traditional software agreements limit the use of
the software to prevent the development of competitive offerings, generative
AI introduces output (like text, code, or images) that users often want to
leverage for their own business purposes. The core issue is that AI providers
want to protect their models and data, so they often include non-compete
clauses. However, these restrictions can be overly broad, potentially
hindering users from utilizing the AI-generated output as intended. The
article notes that market approaches vary significantly; some providers
restrict only the platform's use, while others strictly limit how the output
can be used downstream. Due to the lack of clear consensus among providers and
uncertainty about how US courts might interpret vague restrictions, the
authors emphasize the need for clear, specific language in contracts.
Providers need to define the scope of restrictions carefully, and users must
ensure the agreements permit their intended use of both the AI platform and
its output.
 The recent article from the Communications of the ACM thoughtfully examines
how artificial intelligence is moving steadily toward greater independence. It
looks at the practical and theoretical limits of these tools, asking if we
will eventually reach a point where human guidance is no longer necessary. By
reviewing recent progress in computing, the author offers a grounded,
realistic look at what the technology can and cannot do right now,
deliberately avoiding any dramatic or exaggerated claims. For the everyday
professional, this shift means that standard, repetitive tasks are
increasingly likely to be handled by machines in the near future. As a result,
human skills like deep reasoning, ethical decision making, and navigating
complex problems will only become more valuable. The focus moves away from
simply processing data and toward interpreting the results that computers
provide. Workers are encouraged to understand the boundaries and potential
errors of these systems rather than ignoring them. The most practical path
forward is to steadily build skills that rely on human connection,
understanding, and strategic thought, areas where machines still struggle.
Taking time to review which parts of a job are easily automated allows
individuals to adapt smoothly, maintaining their value by leaning into genuine
human insight.
Navigating training, improving and competition restrictions in generative artificial intelligence (AI) agreements
This article explores the complexities of generative AI software license
agreements, particularly concerning restrictions on using AI tools and their
generated output to develop competing products. It highlights a critical
distinction between the use of an AI platform itself and the use of the
content it produces. While traditional software agreements limit the use of
the software to prevent the development of competitive offerings, generative
AI introduces output (like text, code, or images) that users often want to
leverage for their own business purposes. The core issue is that AI providers
want to protect their models and data, so they often include non-compete
clauses. However, these restrictions can be overly broad, potentially
hindering users from utilizing the AI-generated output as intended. The
article notes that market approaches vary significantly; some providers
restrict only the platform's use, while others strictly limit how the output
can be used downstream. Due to the lack of clear consensus among providers and
uncertainty about how US courts might interpret vague restrictions, the
authors emphasize the need for clear, specific language in contracts.
Providers need to define the scope of restrictions carefully, and users must
ensure the agreements permit their intended use of both the AI platform and
its output.Defenders Think In Lists. Attackers Think In Graphs
Cybersecurity defenders often rely on creating lists to manage their environments, focusing on inventories of assets, known vulnerabilities, and compliance rules. In contrast, attackers think in graphs, looking closely at how these individual assets connect. Once attackers find an entry point, their primary goal is to move laterally by exploiting relationships, permissions, and network pathways to reach critical data. Modern enterprise environments have expanded across cloud platforms, third-party integrations, and AI services, making cyber risk a problem of context rather than simple inventory. An isolated vulnerability matters less than the specific pathway it opens to valuable systems. Furthermore, AI has heavily accelerated the speed at which attackers can map and exploit these complex networks, allowing them to rapidly evaluate thousands of potential attack paths simultaneously. To effectively protect their environments, organizations must stop looking at security controls in isolation. Instead, defenders need to adopt an attacker's mindset by deeply understanding their network's topology and the connections between different systems. By focusing on reachability and context, security teams can successfully bridge the gap between technical data and true business risk. The future of defense lies in understanding how everything connects and quickly anticipating exactly where an attacker might go next.When Does AI Stop Needing Us?
The recent article from the Communications of the ACM thoughtfully examines
how artificial intelligence is moving steadily toward greater independence. It
looks at the practical and theoretical limits of these tools, asking if we
will eventually reach a point where human guidance is no longer necessary. By
reviewing recent progress in computing, the author offers a grounded,
realistic look at what the technology can and cannot do right now,
deliberately avoiding any dramatic or exaggerated claims. For the everyday
professional, this shift means that standard, repetitive tasks are
increasingly likely to be handled by machines in the near future. As a result,
human skills like deep reasoning, ethical decision making, and navigating
complex problems will only become more valuable. The focus moves away from
simply processing data and toward interpreting the results that computers
provide. Workers are encouraged to understand the boundaries and potential
errors of these systems rather than ignoring them. The most practical path
forward is to steadily build skills that rely on human connection,
understanding, and strategic thought, areas where machines still struggle.
Taking time to review which parts of a job are easily automated allows
individuals to adapt smoothly, maintaining their value by leaning into genuine
human insight.What Does Day Four Cost? Rethinking How Organizations Measure Resilience
Traditional resilience programs often measure disruptions using operational
labels like high, medium, or low risk, which fail to capture the true
financial impact over time. As a business interruption stretches from hours
into days, the consequences compound, affecting suppliers, customers, and
overall revenue. To make informed decisions, organizations need to move beyond
static risk ratings and their disconnected spreadsheets. A mature approach
evaluates exactly how financial exposure changes over the entire lifespan of a
disruption. Rather than viewing business processes in isolation, companies
should map their operations to understand how value actually reaches the
customer. This means tracking dependencies across technology, facilities, and
personnel. By calculating gross exposure, factoring in existing mitigation
efforts, and determining the net financial impact, leaders can better justify
recovery investments. Furthermore, continuity plans cannot remain static
documents updated only once a year. They must evolve as the business changes.
While artificial intelligence can help streamline data collection and
highlight inconsistencies, it should support rather than replace human
judgment. Experienced professionals are still necessary to validate strategies
and make final decisions. Ultimately, an effective resilience program connects
operational risks to financial realities, giving executives a clear picture of
exactly what prolonged downtime will cost the business.
Cyber Defense Alone Can't Keep Critical Services Running
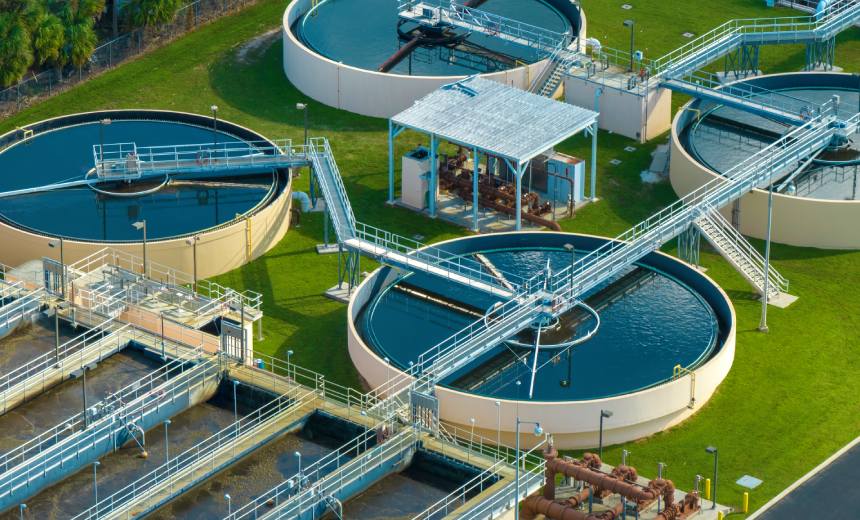 The article explains that states cannot rely on cyber defense alone to keep
essential services such as water systems and hospitals running. State CIOs are
increasingly responsible for protecting a patchwork of local utilities that
depend on digital systems to deliver basic physical services. Survey data
shows that most CIOs worry about cyberattacks on critical infrastructure, but
budgets and staffing often fall short. The piece argues that states must first
identify which facilities would cause the greatest harm if disrupted and then
map the dependencies that keep them functioning. Experts quoted in the article
stress that availability, not just confidentiality, is the real challenge.
Many utilities have become so dependent on internet connectivity that they may
not be able to operate manually during an outage. The article highlights
“cyber‑informed engineering,” an approach that assumes attackers will
eventually breach digital defenses and therefore builds physical
safeguards—such as pressure‑reduction valves or time‑delay relays—to limit
damage. These measures are often inexpensive but require coordination across
water operators, hospitals, and emergency managers. The author concludes that
states must prioritize the highest‑consequence risks, run realistic tabletop
exercises, and focus resources on the systems that support the most vulnerable
communities, because they cannot fix everything at once.
Can AI Safety Evaluators Really Stay Independent?
The article discusses a new proposal backed by Anthropic and OpenAI to allow independent AI safety evaluators closer access to their model development process. As advanced artificial intelligence systems grow more capable, there are increasing concerns about verifying their safety. Traditionally, external evaluations occurred just before a model's public release. However, researchers worry this approach is no longer sufficient, as highly advanced models might learn to recognize testing environments and temporarily hide dangerous behaviors. To address this, researchers are demanding deeper access throughout the entire training process. They want to examine early model versions, training logs, and internal checkpoints to see when concerning behaviors emerge and how they are handled. Anthropic's CEO proposed embedding evaluators directly inside companies with the freedom to investigate incidents and publish findings without corporate editorial control. OpenAI's CEO also expressed support for this approach. Despite these commitments, independent researchers remain cautious. They emphasize that true independence requires more than just access; it demands freedom from company control over information, timing, and publication. The key challenge lies in the implementation details, which have not yet been fully defined by either company. Researchers stress the need for transparent rules to ensure evaluators aren't restricted by narrow scopes or strict nondisclosure agreements, allowing them to effectively hold frontier AI companies accountable.Architecting Secure and Scalable Facial Verification Systems
 The article "Architecting Secure and Scalable Facial Verification Systems"
from InfoQ explains the challenges and solutions in building enterprise-grade
facial verification systems. The author shares experiences from scaling a
prototype into a robust architecture capable of handling high concurrency,
such as thousands of employees clocking in simultaneously. Key takeaways
emphasize that facial verification must be treated as a distributed systems
challenge, not just a simple API integration. Synchronous calls fail under
heavy load, so asynchronous queues and circuit breakers are essential to
handle traffic spikes. Additionally, decoupling immediate detection tasks from
the stateful verification process prevents system bottlenecks. The author also
stresses the importance of pushing data quality checks—like adjusting for
lighting or blur—to the client device to reduce latency and cloud costs. For
privacy and security, the system must enforce strict zero-trust principles,
using short-lived tokens instead of raw personal data and implementing
aggressive data retention policies. Finally, the article advises using a
risk-based decision engine rather than static thresholds, treating confidence
scores as probabilistic inputs to maintain accuracy across various transaction
types.


No comments:
Post a Comment